Complete Technical Paper Content — Secure User Registration And Login System With Bcrypt
Overview & System Context
Secure User Registration And Login System With Bcrypt: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9501 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A password, sometimes called a passcode, is secret data, typically a string of characters, usually used to confirm a user's identity. Traditionally, passwords were expected to be memorized, but the large number of password-protected services that a typical individual accesses can make memorization of unique passwords for each service impractical. Using the terminology of the NIST Digital Identity Guidelines, the secret is held by a party called the claimant while the party verifying the identity of the claimant is called the verifier. When the claimant successfully demonstrates knowledge of the password to the verifier through an established authentication protocol, the verifier can infer the claimant's identity. In general, a password is a sequence of characters including letters, digits, or other symbols. If the permissible characters are constrained to be numeric, the corresponding secret is sometimes called a personal identification number (PIN). Despite its name, a password does not need to be an actual word; indeed, a non-word (in the dictionary sense) may be harder to guess, which is a desirable property of passwords. A memorized secret consisting of a sequence of words or other text separated by spaces is sometimes called a passphrase. A passphrase is similar to a password in usage, but the former is generally longer for added security.
The way in which they secure the passing round of the watchword for the night is as follows: from the tenth maniple of each class of infantry and cavalry, the maniple which is encamped at the lower end of the street, a man is chosen who is relieved from guard duty, and he attends every day at sunset at the tent of the tribune, and receiving from him the watchword—that is a wooden tablet with the word inscribed on it – takes his leave, and on returning to his quarters passes on the watchword and tablet before witnesses to the commander of the next maniple, who in turn passes it to the one next to him. All do the same until it reaches the first maniples, those encamped near the tents of the tribunes. These latter are obliged to deliver the tablet to the tribunes before dark. So that if all those issued are returned, the tribune knows that the watchword has been given to all the maniples, and has passed through all on its way back to him. If any one of them is missing, he makes inquiry at once, as he knows by the marks from what quarter the tablet has not returned, and whoever is responsible for the stoppage meets with the punishment he merits. Passwords in military use evolved to include not just a password, but a password and a counterpassword; for example in the opening days of the Battle of Normandy, paratroopers of the U.S. 101st Airborne Division used a password—flash—which was presented as a challenge, and answered with the correct response—thunder. The challenge and response were changed every three days. American paratroopers also famously used a device known as a "cricket" on D-Day in place of a password system as a temporarily unique method of identification; one metallic click given by the device in lieu of a password was to be met by two clicks in reply. Passwords have been used with computers since the earliest days of computing. The Compatible Time-Sharing System (CTSS), an operating system introduced at MIT in 1961, was the first computer system to implement password login. CTSS had a LOGIN command that requested a user password.
"After typing PASSWORD, the system turns off the printing mechanism, if possible, so that the user may type in his password with privacy." In the early 1970s, Robert Morris developed a system of storing login passwords in a hashed form as part of the Unix operating system. The system was based on a simulated Hagelin rotor crypto machine, and first appeared in 6th Edition Unix in 1974. A later version of his algorithm, known as crypt(3), used a 12-bit salt and invoked a modified form of the DES algorithm 25 times to reduce the risk of pre-computed dictionary attacks. In modern times, user names and passwords are commonly used by people during a log in process that controls access to protected computer operating systems, mobile phones, cable TV decoders, automated teller machines (ATMs), etc. A typical computer user has passwords for multiple purposes: logging into accounts, retrieving e-mail, accessing applications, databases, networks, websites, and even reading the morning newspaper online.
The name of a pet, child, family member, or significant other Anniversary dates and birthdays Birthplace Name of a favorite holiday Something related to a favorite sports team The word "password" The security of a password-protected system depends on several factors. The overall system must be designed for sound security, with protection against computer viruses, man-in-the-middle attacks and the like. Physical security issues are also a concern, from deterring shoulder surfing to more sophisticated physical threats such as video cameras and keyboard sniffers.
Passwords should be chosen so that they are hard for an attacker to guess and hard for an attacker to discover using any of the available automatic attack schemes. Nowadays, it is a common practice for computer systems to hide passwords as they are typed. The purpose of this measure is to prevent bystanders from reading the password; however, some argue that this practice may lead to mistakes and stress, encouraging users to choose weak passwords. As an alternative, users should have the option to show or hide passwords as they type them. Effective access control provisions may force extreme measures on criminals seeking to acquire a password or biometric token. Less extreme measures include extortion, rubber hose cryptanalysis, and side channel attack. Some specific password management issues that must be considered when thinking about, choosing, and handling a password follow.
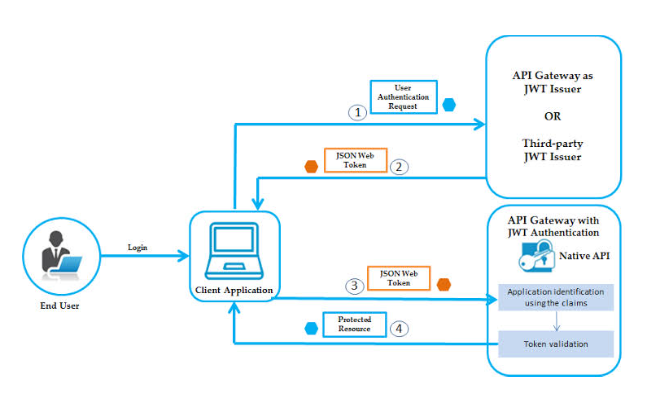
Figure 1: JWT Authentication Guide: How to Create and Implement JSON Web Tokens The risk of interception of passwords sent over the Internet can be reduced by, among other approaches, using cryptographic protection. The most widely used is the Transport Layer Security (TLS, previously called SSL) feature built into most current Internet browsers. Most browsers alert the user of a TLS/SSL-protected exchange with a server by displaying a closed lock icon, or some other sign, when TLS is in use. There are several other techniques in use.
Usually, a system must provide a way to change a password, either because a user believes the current password has been (or might have been) compromised, or as a precautionary measure. If a new password is passed to the system in unencrypted form, security can be lost (e.g., via wiretapping) before the new password can even be installed in the password database and if the new password is given to a compromised employee, little is gained. Some websites include the user-selected password in an unencrypted confirmation e-mail message, with the obvious increased vulnerability. Identity management systems are increasingly used to automate the issuance of replacements for lost passwords, a feature called self-service password reset.
The user's identity is verified by asking questions and comparing the answers to ones previously stored (i.e., when the account was opened). Some password reset questions ask for personal information that could be found on social media, such as mother's maiden name. As a result, some security experts recommend either making up one's own questions or giving false answers.
Not displaying the password on the display screen as it is being entered or obscuring it as it is typed by using asterisks (*) or bullets (•). Allowing passwords of adequate length. (Some legacy operating systems, including early versions of Unix and Windows, limited passwords to an 8 character maximum, reducing security.) Requiring users to re-enter their password after a period of inactivity (a semi log-off policy). Enforcing a password policy to increase password strength and security. Assigning randomly chosen passwords. Requiring minimum password lengths. Some systems require characters from various character classes in a password—for example, "must have at least one uppercase and at least one lowercase letter". However, all-lowercase passwords are more secure per keystroke than mixed capitalization passwords. Employ a password blacklist to block the use of weak, easily guessed passwords Providing an alternative to keyboard entry (e.g., spoken passwords, or biometric identifiers). Requiring more than one authentication system, such as two-factor authentication (something a user has and something the user knows). Using encrypted tunnels or password-authenticated key agreement to prevent access to transmitted passwords via network attacks Limiting the number of allowed failures within a given time period (to prevent repeated password guessing). After the limit is reached, further attempts will fail (including correct password attempts) until the beginning of the next time period. However, this is vulnerable to a form of denial of service attack. Introducing a delay between password submission attempts to slow down automated password guessing programs. Some of the more stringent policy enforcement measures can pose a risk of alienating users, possibly decreasing security as a result.
Multi-factor authentication schemes combine passwords (as "knowledge factors") with one or more other means of authentication to make authentication more secure and less vulnerable to compromised passwords. For example, a simple two-factor login might send a text message, e-mail, automated phone call, or similar alert whenever a login attempt is made, possibly supplying a code that must be entered in addition to a password. More sophisticated factors include such things as hardware tokens and biometric security.
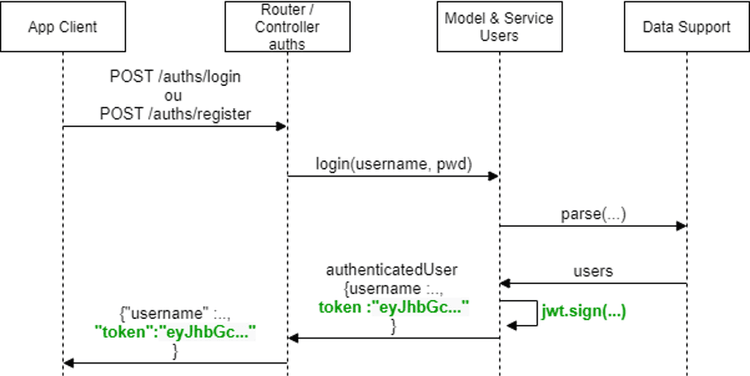
Figure 2: JWT auths API & bcrypt Most organizations specify a password policy that sets requirements for the composition and usage of passwords, typically dictating minimum length, required categories (e.g., upper and lower case, numbers, and special characters), and prohibited elements (e.g., use of one's own name, date of birth, address, telephone number). Some governments have national authentication frameworks that define requirements for user authentication to government services, including requirements for passwords. Many websites enforce standard rules such as minimum and maximum length, but also frequently include composition rules such as featuring at least one capital letter and at least one number/symbol. These latter, more specific rules were largely based on a 2003 report by the National Institute of Standards and Technology (NIST), authored by Bill Burr.
It originally proposed the practice of using numbers, obscure characters and capital letters and updating regularly. In a 2017 article in The Wall Street Journal, Burr reported he regrets these proposals and made a mistake when he recommended them. According to a 2017 rewrite of this NIST report, a number of websites have rules that actually have the opposite effect on the security of their users. This includes complex composition rules as well as forced password changes after certain periods of time. While these rules have long been widespread, they have also long been seen as annoying and ineffective by both users and cybersecurity experts. The NIST recommends people use longer phrases as passwords (and advises websites to raise the maximum password length) instead of hard-to-remember passwords with "illusory complexity" such as "pA55w+rd". A user prevented from using the password "password" may, if required to include a number and uppercase letter, simply choose "Password1". Combined with forced periodic password changes, this can lead to passwords that are difficult to remember but easy to crack. Paul Grassi, one of the 2017 NIST report's authors, further elaborated: "Everyone knows that an exclamation point is a 1, or an I, or the last character of a password. $ is an S or a 5. If we use these well-known tricks, we aren't fooling any adversary. We are simply fooling the database that stores passwords into thinking the user did something good." Pieris Tsokkis and Eliana Stavrou were able to identify some bad password construction strategies through their research and development of a password generator tool. They came up with eight categories of password construction strategies based on exposed password lists, password cracking tools, and online reports citing the most used passwords. These categories include user-related information, keyboard combinations and patterns, placement strategy, word processing, substitution, capitalization, append dates, and a combination of the previous categories.
Attempting to crack passwords by trying as many possibilities as time and money permit is a brute-force attack. A related method, rather more efficient in most cases, is a dictionary attack. In a dictionary attack, all words in one or more dictionaries are tested. Lists of common passwords are also typically tested. Password strength is the likelihood that a password cannot be guessed or discovered, and varies with the attack algorithm used. Cryptologists and computer scientists often refer to the strength or 'hardness' in terms of entropy. Passwords easily discovered are termed weak or vulnerable; passwords difficult or impossible to discover are considered strong. There are several programs available for password attack (or even auditing and recovery by systems personnel) such as L0phtCrack, John the Ripper, and Cain; some of which use password design vulnerabilities (as found in the Microsoft LANManager system) to increase efficiency. These programs are sometimes used by system administrators to detect weak passwords proposed by users. Studies of production computer systems have consistently shown that a large fraction of all user-chosen passwords are readily guessed automatically. For example, Columbia University found 22% of user passwords could be recovered with little effort. According to Bruce Schneier, examining data from a 2006 phishing attack, 55% of MySpace passwords would be crackable in 8 hours using a commercially available Password Recovery Toolkit capable of testing 200,000 passwords per second in 2006. He also reported that the single most common password was password1, confirming yet again the general lack of informed care in choosing passwords among users. (He nevertheless maintained, based on these data, that the general quality of passwords has improved over the years—for example, average length was up to eight characters from under seven in previous surveys, and less than 4% were dictionary words.) Single-use passwords. Having passwords that are only valid once makes a number of potential attacks ineffective. Most users find single-use passwords extremely inconvenient. They have, however, been widely implemented in personal online banking, where they are known as Transaction Authentication Numbers (TANs). As most home users only perform a small number of transactions each week, the single-use issue has not led to intolerable customer dissatisfaction in this case.
Time-synchronized one-time passwords are similar in some ways to single-use passwords, but the value to be entered is displayed on a small (generally pocketable) item and changes every minute or so. Passwordless authentication in which a user can log in to a computer system without entering (and having to remember) a password or any other knowledge-based secret. In most common implementations users are asked to enter their public identifier (username, phone number, email address etc.) and then complete the authentication process by providing a secure proof of identity through a registered device or token. Most of implementations rely on public-key cryptography infrastructure where the public key is provided during registration to the authenticating service (remote server, application or website) while the private key is kept on a user's device (PC, smartphone or an external security token) and can be accessed only by providing a biometric signature or another authentication factor which is not knowledge-based. PassWindow one-time passwords are used as single-use passwords, but the dynamic characters to be entered are visible only when a user superimposes a unique printed visual key over a server-generated challenge image shown on the user's screen. Access controls based on public-key cryptography e.g. ssh.
The necessary keys are usually too large to memorize (but see proposal Passmaze) and must be stored on a local computer, security token or portable memory device, such as a USB flash drive or even floppy disk. The private key may be stored on a cloud service provider, and activated by the use of a password or two-factor authentication. Biometric methods promise authentication based on unalterable personal characteristics, but as of 2008 have high error rates and require additional hardware to scan, for example, fingerprints, irises, etc. They have proven easy to spoof in some famous incidents testing commercially available systems, for example, the gummie fingerprint spoof demonstration, and, because these characteristics are unalterable, they cannot be changed if compromised; this is a highly important consideration in access control as a compromised access token is necessarily insecure. Single sign-on technology is claimed to eliminate the need for having multiple passwords. Such schemes do not relieve users and administrators from choosing reasonable single passwords, nor system designers or administrators from ensuring that private access control information passed among systems enabling single sign-on is secure against attack. As yet, no satisfactory standard has been developed. Envaulting technology is a password-free way to secure data on removable storage devices such as USB flash drives. Instead of user passwords, access control is based on the user's access to a network resource. Non-text-based passwords, such as graphical passwords or mouse-movement based passwords. Graphical passwords are an alternative means of authentication for log-in intended to be used in place of conventional password; they use images, graphics or colours instead of letters, digits or special characters. One system requires users to select a series of faces as a password, utilizing the human brain's ability to recall faces easily. In some implementations the user is required to pick from a series of images in the correct sequence to gain access. Another graphical password solution creates a one-time password using a randomly generated grid of images. Each time the user is required to authenticate, they look for the images that fit their pre-chosen categories and enter the randomly generated alphanumeric character that appears in the image to form the one-time password. So far, graphical passwords are promising, but are not widely used. Studies on this subject have been made to determine their usability in the real world. While some believe that graphical passwords would be harder to crack, others suggest that people will be just as likely to pick common images or sequences as they are to pick common passwords. 2D Key (2-Dimensional Key) is a 2D matrix-like key input method having the key styles of multiline passphrase, crossword, ASCII/Unicode art, with optional textual semantic noises, to create big password/key beyond 128 bits to realize the MePKC (Memorizable Public-Key Cryptography) using fully memorizable private key upon the current private key management technologies like encrypted private key, split private key, and roaming private key. Cognitive passwords use question and answer cue/response pairs to verify identity.
"The password is dead" is a recurring idea in computer security. The reasons given often include reference to the usability as well as security problems of passwords. It often accompanies arguments that the replacement of passwords by a more secure means of authentication is both necessary and imminent. This claim has been made by a number of people at least since 2004. Alternatives to passwords include biometrics, two-factor authentication or single sign-on, Microsoft's Cardspace, the Higgins project, the Liberty Alliance, NSTIC, the FIDO Alliance and various Identity 2.0 proposals. Bonneau et al.
systematically compared web passwords to other technical solutions that were alternatives. They reviewed these in respect of usability, deployability, and security. Their analysis showed that most alternatives do better than passwords on security, some do better and some worse with respect to usability, while every alternative does worse than passwords on deployability. This may be why over 20 years after this recurring idea started, passwords are still being used, despite attempts by technology businesses to change this. Some that highlight this, suggest that the problem is generally not with the system of using passwords and is instead an issue with how humans use and manage their passwords and that "in the age of disparate workforces, home WiFi networks and multiple devices, password use has continued to increase".
Figure 3: GitHub - gautam-Ragnarok/secure_auth: I Secure Django Authentication ... In cryptography, the Salted Challenge Response Authentication Mechanism (SCRAM) is a family of modern, password-based challenge–response authentication mechanisms providing authentication of a user to a server. As it is specified for Simple Authentication and Security Layer (SASL), it can be used for password-based logins to services like LDAP, HTTP, SMTP, POP3, IMAP and JMAP (e-mail), XMPP (chat), or MongoDB and PostgreSQL (databases). For XMPP, supporting it is mandatory.
SaltedPassword = H(password, salt, iteration-count) = PBKDF2(HMAC, password, salt, iteration-count, output length of H). client-first The client-first message consists of a GS2 header (comprising a channel binding flag, and optional name for authorization information), the desired username, and a randomly generated client nonce c-nonce. server-first The server appends to this client nonce its own nonce s-nonce, and adds it to the server-first message, which also contains a salt used by the server for salting the user's password hash, and an iteration count iteration-count. client-final After that the client sends the client-final message containing channel-binding, the GS2 header and channel binding data encoded in base64, the concatenation of the client and the server nonce, and the client proof, proof. server-final The communication closes with the server-final message, which contains the server signature, verifier.
Auth = client-first-without-header + , + server-first + , + client-final-without-proof (concatenated with commas) More concretely, this takes the form: ClientKey = HMAC(SaltedPassword, 'Client Key') ServerKey = HMAC(SaltedPassword, 'Server Key') ClientProof = p = ClientKey XOR HMAC(H(ClientKey), Auth) ServerSignature = v = HMAC(ServerKey, Auth) where the XOR operation is applied to byte strings of the same length, H(ClientKey) is a normal hash of ClientKey. 'Client Key' and 'Server Key' are verbatim strings. The server can authorize the client by computing ClientKey from ClientProof and then comparing H(ClientKey) with the stored value. The client can authorize the server by computing and comparing ServerSignature directly.
This is a non-exhaustive list of reports about data breaches, using data compiled from am news articles. The list includes those involving the theft or compromise of 30,000 or more records, although many smaller breaches occur continually. Note that other sources compile more complete lists. Breaches of large organizations where the number of records is still unknown are also listed. In addition, the various methods used in the breaches are listed, with hacking being the most common. As a result of data breaches, it is estimated that in first half of 2018 alone, about 4.5 billion records were exposed. In 2019, a collection of 2.7 billion identity records, consisting of 774 million unique email addresses and 21 million unique passwords, was posted on the web for sale. In January 2024, a data breach dubbed the "mother of all breaches" was uncovered. Over 26 billion records, including some from Twitter, Adobe, Canva, LinkedIn, and Dropbox, were found in the database. No organization immediately claimed responsibility.
A secure web-based authentication system developed using Python Flask , MariaDB , SQLAlchemy , and bcrypt . This project demonstrates modern authentication techniques, secure password storage, session management, and web security best practices. The Secure Login System is a cybersecurity-focused web application that allows users to register, authenticate, and manage sessions securely. The system implements password hashing using bcrypt and stores user credentials in a MariaDB database.
The primary objective of this project is to demonstrate secure authentication mechanisms while following secure coding principles and protecting against common web-based attacks. Contributions, suggestions, and feedback are always welcome. Feel free to open an issue or submit a pull request. Secure authentication system built using Flask, MariaDB, SQLAlchemy, and bcrypt with secure login, registration, password hashing, and session management.
This project is a simple user registration and authentication system built using Flask, SQLite, and bcrypt for password hashing. The system allows users to register with a unique username and a securely hashed password. Registered users can then log in using their credentials to access user-specific page. The system implements session management to keep track of authenticated users.
Single User Session: The system currently supports only one active session per user at a time. Basic Error Handling: Error handling is implemented at a basic level and may not cover all potential edge cases. 2. System Architecture & Core Working Principles Minimal Frontend: The frontend is simplistic and lacks advanced features like form validation or UI enhancements.
SQLite Limitations: SQLite is used as a lightweight database, suitable for small-scale applications. For larger applications, a more robust database solution might be required. Security Considerations: While bcrypt is used for password hashing, additional security measures like rate limiting, CSRF protection, and HTTPS implementation should be considered for production deployments.
Contributions to enhance the system or improve documentation are welcome. Please submit pull requests or raise issues for discussion. This README.md file provide an overview of the project structure, features, setup instructions, and limitations. Feel free to customize and expand these documents based on your specific project requirements and deployment scenarios.
This project implements a secure user registration system using Flask, SQLite, and JavaScript to handle user registration, login, and logout functionalities. The system ensures robust error handling to gracefully manage invalid inputs and prevent SQL injection attacks. Tired of Boring and insecured Logins ? Let's ditch the basic sign-up and sign-in systems and build a secure, engaging application with a personalized dashboard using PHP! This tutorial will guide you through creating a user management system with a focus on security best practices and user experience.
What You'll Learn: How to handle user registration and login. Securely store passwords using bcrypt hashing. Implement a basic routing system. Leverage a service container to manage dependencies. III IApp III IConfig : config.php , container.php , Database.php III IController : AuthController.php , DashboardController.php III ICore : app.php III IHelper : Autholoader.php , validator.php III IModel : userModel.php III IRoutes : api.php , Router.php III Iservices : AuthService.php , container.php III IView III IDashboard : DashboardView.php III ILogin : Mainview.php , SignInView.php , SignUpView.php Create a config.php file to store your database credentials and other configuration settings: The code defines a class UserModel within the namespace App\Model. The class is designed to interact with a database to perform operations related to user management, specifically creating and validating users. Here's a breakdown of the principal components and functionalities: namespace App\Model; : Declares that the UserModel class is part of the App\Model namespace.
use App\Config\DataBase; : Imports the DataBase class from the App\Config namespace, which presumably handles database connections. use PDOException; : Imports the PDOException class, which is used to catch exceptions thrown by PDO operations. Class Definition : class UserModel: Defines the UserModel class, which encapsulates methods for interacting with the database regarding user data. Constructor and Destructor : The constructor ( __construct ) accepts an instance of DataBase and connects to the database using $this->db::connect(); .
The destructor ( __destruct ) unsets the $db property, effectively closing the database connection when the object is destroyed. Public Methods : create($data) : This method attempts to insert a new user into the users table with the provided data ($data). It uses prepared statements to prevent SQL injection. It checks for a duplicate entry error (code 23000) and returns an error message if the email already exists in the database. On success, it returns an array indicating success and the ID of the newly inserted user.
validateUser($data) (it's inside the class also ): This method queries the database to find a user with the provided email address. It uses a prepared statement to safely query the database. If a user is found, it returns an array indicating success and the user's data. If no user is found, it returns an array indicating failure. Error Handling: Both methods use a try-catch block to catch PDOException exceptions, which are thrown by PDO when there's an error executing a database operation. In the create method, if a PDOException is caught and its code indicates a duplicate entry error, it returns an error message indicating that the email already exists.
This code defines routes for our application, connecting URLs to specific controller actions. It uses a Router class to define how different HTTP requests (GET and POST) to specific URLs are handled. Each route maps a URL to a controller and a method within that controller. For example, a GET request to /login will execute the showLoginForm method of the AuthController. This allows for organized and efficient handling of requests, directing them to the appropriate code based on the URL and HTTP method. This is a common way to manage routing in MVC applications, ensuring clear separation between URL handling and application logic.
In the MVC (Model-View-Controller) architectural pattern, the router acts as a traffic cop, directing incoming requests to the correct controller action. Think of it as the "switchboard" of your application. Definition: The router analyzes the URL of a request and determines which controller and action should handle it. It then passes the request to that controller, allowing the MVC flow to continue. Importance: Organizes Request Handling: Without a router, it would be chaotic to handle different types of requests. The router ensures each request goes to the right place.
Maintainable Code: It keeps the code clean and organized by separating URL mapping from application logic. Flexibility and Scalability: Routers allow for easy addition of new features and functionalities without major restructuring. * SEO-Friendliness: Routers can create clean, descriptive URLs that are beneficial for Search Engine Optimization * (SEO). this is the endspoint of the router : By using a Dependency Injection Container, you can: Decouple components by injecting dependencies instead of hardcoding them. Easily switch implementations of dependencies (e.g., for testing or different environments). Improve code organization and testability.
This code defines a simple Dependency Injection Container in PHP. Here's a breakdown of the important parts: 3. Software Implementation, Frameworks & Protocols 1. Namespace: namespace App\Services; : This line indicates that the code belongs to the namespace App\Services. Namespaces help organize code and prevent naming collisions. 2. Class Definition: class Container { ... } : This defines a class called Container, which will hold and manage dependencies. 3. Bindings Property: private $bindings = []; : This is a private property that stores the dependencies. It's an array where keys are dependency "identifiers" and values are "factories" responsible for creating those dependencies. 4. set Method: public function set(string $id, callable $factory): void : This method registers a dependency. $id : The unique identifier for the dependency (e.g., 'database', 'logger'). $factory : A callable (function or closure) that knows how to create an instance of the dependency. 5. get Method: public function get(string $id) : This method retrieves a dependency by its identifier. It checks if the dependency is registered using isset($this->bindings[$id]) . If found, it retrieves the $factory associated with the $id . It then calls the $factory with the container itself as an argument ($factory($this)) , allowing the factory to potentially access other dependencies from the container. Finally, it returns the created instance of the dependency. If the dependency is not found, it throws an Exception.
explication : 1. Namespace: namespace App\View\Login; : Indicates the code belongs to the namespace App\View\Login, organizing view-related code for login/signup. 2. SignUpView Class: class SignUpView { ... }: Defines a class named SignUpView, likely responsible for rendering the HTML of the signup form. 3. render Method: public static function render($errors) { ... } : This static method generates the HTML content of the signup form. The $errors parameter likely contains an array of validation errors from a controller, similar to the login form example. Key Elements Within the render Method: Output Buffering: ob_start(); and ob_get_clean();: Similar to the login view, utilizes output buffering to capture the generated HTML content before sending it to the browser, allowing potential manipulation or processing. Welcome Message and Login Link: A simple welcome message is displayed, along with a link to the login page (./login). Sign-Up Form: form method="post" action="./register" : Defines a form that uses the POST method to submit data to the ./register URL Input Fields: Creates input fields for user information like "full name," "email," "date of birth," "gender," "password," and "confirm password." Labels are included for clarity.
Navigation Buttons:
_explication : _ ( " almost the same thing in the signUp" 1. Namespace: namespace App\View\Login; : Indicates the code belongs to the App\View\Login namespace, keeping login view code organized. 2. SignInView Class: class SignInView { ... } : Defines a class named SignInView to handle login form rendering. 3. render Method: public static function render($errors) { ... } : This static method generates the HTML for the login form. The $errors parameter is crucial as it likely contains an array of validation errors passed from the controller. Key Elements Within the render Method: Output Buffering: ob_start(); and ob_get_clean(); : These functions utilize output buffering. The HTML content is generated and stored in a buffer instead of being immediately sent to the browser. This allows for manipulation or processing of the content before it's displayed.
Welcome Message and Signup Link: Provides a simple welcome message and a link to the registration page (./register). Login Form: form method="post" action="./login" : Defines a form that uses the POST method to submit data to the ./login URL . Input Fields: Creates input fields for "email" and "password," including labels for user clarity. Error Display: : Uses the null coalescing operator ( ?? ) to display an error message associated with the 'null' key in the $errors array if it exists, otherwise displays nothing. This could be for a general login error. and : Similar to the above, these lines display specific error messages associated with the 'email' and 'password' fields, respectively, if they exist in the $errors array. Sign In Button: : Creates a button for users to submit the form.
This PHP code defines an AuthService class within the App\Services namespace, which is responsible for handling user registration and login processes , including form validation and password hashing with a salt. Here's a brief explanation focusing on form validation and the salt-hashing process: Namespace and Imports: The class is part of the App\Services namespace and imports Validator and UserModel classes from other namespaces. Class Properties and Constructor : The AuthService class has two private properties: $model of type UserModel and $validator of type Validator. These are injected via the constructor, allowing the class to interact with the database and validate data. Form Validation in validateRegistration: The validateRegistration method uses the Validator class to validate the registration data. It sets aliases for form fields for better error messages and defines validation rules for each field: full_name must be required and contain only alphabetic characters. email must be required and in a valid email format. dob (date of birth) must be required and in a valid date format.
gender must be required and a valid gender value. password must be required and meet the criteria defined by the password rule (likely a minimum length and complexity). confirm_password must match the password field. If validation fails, it returns an array with success set to false and the errors collected by the validator. If validation passes, it returns an array with success set to true and the validated data. Password Hashing with Salt in register : Before inserting the user data into the database, the register method generates a random salt using random_bytes(16) and converts it to hexadecimal with bin2hex(). This salt is then concatenated with the plain text password. The concatenated string (salt + password) is hashed using password_hash() with the PASSWORD_ARGON2ID algorithm, which is a strong hashing algorithm suitable for storing passwords securely. The hashed password and the generated salt are stored in the database. This ensures that even if the password is compromised, the attacker cannot reverse-engineer the original password from the hash due to the presence of the unique salt.
This code represents a view that generates a dynamic dashboard page. It highlights several important aspects of views in an MVC application: The code represents a simple view in a PHP MVC application, likely designed for a dashboard. Here's a breakdown: 1. Namespace: namespace App\View\Dashboard; : Similar to the previous example, this indicates the code belongs to the namespace App\View\Dashboard, likely organizing view-related code. 2. SCRIPT_ROOT Constant: define('SCRIPT_ROOT', 'http://localhost/hackathon'); : This defines a constant SCRIPT_ROOT with the base URL of your application. This constant is used throughout the HTML to build paths to resources like CSS files and images. 3. DashboardView Class: class DashboardView { ... } : This defines a class DashboardView, which likely encapsulates the logic for generating the HTML of the dashboard. 4. render Method: public static function render() { ... }: This static method generates the actual HTML content of the dashboard. It's designed to be called from a controller, which would pass any necessary data to populate the view. Key Elements Within the render Method: HTML Structure: The method outputs a standard HTML document structure, including the Et Voila ! , this is our "mini-tutorial" for our "mini-project" to get the full folders and files of our project you can acces to our gitHub : LinkToGithub Congratulations! You've built a basic PHP authentication system! Key Security Considerations: Password Hashing: Always hash passwords using bcrypt (password_hash()) before storing them. Never store passwords in plain text. Input Validation: Thoroughly validate and sanitize user input to prevent vulnerabilities like SQL injection and cross-site scripting (XSS). Session Management: Implement secure session management practices to protect user data. This is a simple starting point. You can expand this system to include password reset functionality, email verification, and more complex authorization rule In this lesson, we will focus specifically on the user login aspect of authentication by using Bcrypt for secure password hashing and verification in a Symfony application. While user registration sets the stage for creating user accounts securely, login ensures that only authorized users can access the application by verifying their credentials.
By completing this lesson, you'll gain a deeper understanding of secure login mechanisms using Bcrypt in Symfony, a key part of building resilient web applications. When verifying user credentials, Bcrypt provides robust security measures that are crucial for safeguarding user data: Through this login implementation, leveraging these capabilities, the application reinforces its security posture against common vulnerabilities.
By considering this material and the previously covered registration process, you now have a comprehensive understanding to safeguard user credentials effectively in Symfony apps. The login functionality is implemented within the UserController to handle authentication requests. Below is a snippet describing the critical sections involved in the login process: This guide demonstrates how to set up and use a register/login service with Bcrypt for secure password hashing. It includes initializing migrations with Alembic, verifying the database setup, and testing the register and login functionality.
Once the containers are running, you need to set up your database schema using Alembic. If successful, you should see the users table along with other tables (e.g., alembic_version ). If everything is set up correctly, you'll see the following results when registering and logging in users. This guide provides a secure foundation for a user authentication system using Flask, SQLAlchemy, Alembic, and Bcrypt. I Simple project to show how to set up and use a register/login service with Bcrypt for secure password hashing. It includes initializing migrations with Alembic, verifying the database setup, and testing the register and login functionality Authentication is one of the most important parts of any web application. It ensures that only authorized users can access protected resources. In this project, we will build a secure authentication system with the following features: We will also connect a frontend using HTML and JavaScript Fetch API to interact with backend APIs.
Figure-1: JWT Token Generation Process I Step 7: Signup API Route app.post("/signup", async (req, res) => { const { username, email, password } = req.body; const hashedPassword = await bcrypt.hash(password, 10); const user = new User({ username, email, password: hashedPassword }); await user.save(); res.send("User Registered Successfully"); }); I Step 8: Login API Route app.post("/login", async (req, res) => { const { email, password } = req.body; const user = await User.findOne({ email }); if (!user) return res.send("User not found"); const isMatch = await bcrypt.compare(password, user.password); if (!isMatch) return res.send("Invalid credentials"); const token = jwt.sign({ id: user._id }, "secretKey", { expiresIn: "1h" }); res.json({ token }); }); II Step 9: Middleware for Protected Routes Middleware checks if user is authenticated before accessing protected routes.
function verifyToken(req, res, next) { const token = req.headers["authorization"]; if (!token) return res.send("Access denied"); try { jwt.verify(token, "secretKey"); next(); } catch { res.send("Invalid token"); } } I Step 10: Frontend Integration (HTML + Fetch API) fetch("http://localhost:5000/login", { method: "POST", headers: { "Content-Type": "application/json" }, body: JSON.stringify({ email: "test@gmail.com", password: "123456" }) }) .then(res => res.json()) .then(data => { localStorage.setItem("token", data.token); }); I Step 11: Token Expiry Handling We set token expiration time to improve security. jwt.sign({ id: user._id }, "secretKey", { expiresIn: "1h" }); After 1 hour, the user must login again. I Step 12: Logout System function logout() { localStorage.removeItem("token"); window.location.href = "/login.html"; } I Real-World Applications E-commerce websites Admin dashboards Online learning platforms SaaS applications Banking systems II Common Mistakes Storing passwords without hashing Not using HTTPS Hardcoding secret keys Not validating user input I FAQs 1. What is JWT? JWT is a token-based authentication system used to securely transmit user data. 2. Why use bcrypt? Bcrypt is used to securely hash passwords before storing them in the database. 3. Is this system production-ready? Yes, but you should add advanced security features for production use. 4. Can I use SQL instead of MongoDB? Yes, you can use MySQL or PostgreSQL as alternatives. 5. What is middleware? Middleware is a function that runs before accessing protected routes. I Conclusion In this tutorial, you learned how to build a complete full-stack authentication system using Node.js, Express, MongoDB, and JWT. This project is a strong foundation for real-world web development and backend engineering. Keep practicing and integrate this system into larger applications to improve your skills. APIs & Web Services Backend Development Full Stack Development In this tutorial, you learned how to build a complete full-stack authentication system using Node.js, Express, MongoDB, and JWT.
This project is a strong foundation for real-world web development and backend engineering. Keep practicing and integrate this system into larger applications to improve your skills. 4. Practical Deployment, Analysis & Case Studies Imagine you’re building a web application that's about to launch. You've carefully designed the user interface, added exciting features, and made sure everything runs smoothly. But as the launch date gets closer, a nagging concern starts to worry you—security. Specifically, how to ensure that only the right users can access the right parts of your application. This is where authentication comes in.
Authentication is the process of verifying who a user is, and it's a critical aspect of web development. In the vast digital landscape, ensuring that users can securely log in and log out of your application is paramount. One slip, and your app could be vulnerable to attacks, putting user data at risk. In this article, we will explore secure authentication in Node.js, using bcrypt.js to hash passwords and JWT tokens to manage user sessions. By the end, you'll have a solid understanding of how to implement a strong login/logout system, keeping your users’ data safe and secure.
So, let’s embark on this journey to build a bulletproof authentication system, starting from setting up our environment to securing our routes with JWT. Ready to lock down your Node.js app? Let’s get started. Next, we'll set up a basic Express server. Create a file named index.js . This code initializes Express and creates an instance of the application. We'll then define a route for the root URL ("/") to handle incoming HTTP GET requests. After that, we'll start the server on port 8000, allowing it to listen for incoming requests.
Now, we will create a folder named 'routes' and in that folder we will make make a new file named authRoute.js and paste the below code to see basics of routes. In this code snippet, we're setting up routes for different authentication endpoints using Express. First, we import the express library and create a new router instance. Then, we define three GET routes: /signup , /login , and /logout , each responding with a JSON object indicating that the respective endpoint was hit. Finally, we export the router instance as the default export, making it available for use in other parts of the application.
Now, you can test it in your browser...but I will use Postman for its convenience. You can test all the end points like this. Now, first ready our mongoDB database. To do that make a folder Model and under that a file User.js and in this file add Mongoose schema and model for a User in a mongoDB database. The schema includes fields for username , fullName , password , and email , each with specified data types and constraints like uniqueness and required status. The password field also has a minimum length of 6 characters.
Now let's connect to our database. We'll create a folder named db and inside it, a file called connectDB.js . In this file, we'll define an asynchronous function connectMongoDB that tries to connect to a MongoDB database using Mongoose. It gets the database connection string from the MONGO_URI environment variable. If the connection is successful, it logs a success message with the host name. If it fails, it logs the error and exits the process with a status code of 1. The function is exported for use in other parts of the application.
Now to use MONGO_URI we have to make it in .env file. Here I have used local mongoDB setup connection string. If you want then you can also use mongoDB atlas. Now make the signup function. For this 1st make a folder controller and there file authController.js First, it extracts fullName , username , email , and password from the request body. It validates the email format using a regular expression, returning a 400 status if the format is invalid.
Next, the function checks if the username or email already exists in the database. If either is taken, a 400 status with an error message is returned. It also ensures the password is at least 6 characters long, sending another 400 status if this condition isn't met. The password is then securely hashed using bcrypt . A new User instance is created with the provided data and saved to the database.
The function uses the jsonwebtoken library to create a JWT. It signs the token with the user's ID and a secret key ( JWT_SECRET from the environment variables), setting it to expire in 15 days. So this function ensures that the user's session is both secure and persistent, making it a crucial part of the authentication process.
Here we have to add another environment variable JWT_SECRET in .env . You can add any type of mix of number and string like this. So. now it’s time to test our signup function in Postman. Let’s see if it’s working or not. Here you can see it’s working properly and you can check it your mongoDB database as well.
Okay. Now the last function i.e. the logout function. Let’s implement this. It’s pretty simple. If you don't want to code everything yourself and want a quick solution, I have created an npm package called auth0_package. You can get it from here . Now your backend application is complete. In the next blog, I will explain how to integrate this with your frontend. So stay tuned for that II.
In conclusion, implementing secure authentication in a Node.js application is crucial for protecting user data and ensuring that only authorized users can access specific parts of your application. By using bcrypt.js for password hashing and JWT tokens for session management, you can create a robust login/logout system. This approach not only enhances security but also provides a seamless user experience. Setting up a MongoDB database and using Express for routing further strengthens the backend infrastructure. With these tools and techniques, you can confidently launch your web application, knowing that it is well-protected against unauthorized access and potential security threats.
Nice article. Even though I use third party libraries for authentication most of the time, it's always nice to come across articles like these explaining the basics to make sure I still understand how it all works under the hood. A little suggestion: when you write code blocks you can specify a language identifier for syntax highlighting like 5. Performance Evaluation & Extended Technical Observations Thank you for your appreciation. I will surely mention the language from next blog. Thank you! In Node.js, secure authentication can be achieved using bcrypt.js for hashing passwords and JWT (JSON Web Tokens) for session management. During registration, hash the password with bcrypt, and on login, compare it with the stored hash. If matched, generate a JWT for authentication. Use middleware to protect routes by verifying the JWT, and on logout, clear the token from the client side. This approach ensures secure password storage and efficient session handling.
A Blowfish-based password hashing scheme designed by Niels Provos & David Mazières (1999). Deliberately slow and adaptive — bcrypt's cost factor lets security scale with hardware improvements. The cost factor is not an arbitrary dial — it is literally an exponent. bcrypt runs Blowfish's key setup, then repeats it 2 cost times, each round re-mixing your password and salt into an 18-word subkey array (the P-array The 18 32-bit subkeys Blowfish derives from its key. In bcrypt these are re-derived every round, so the whole key schedule — not just one hash — is what gets repeated 2^cost times. ) and four 256-entry substitution boxes (the S-boxes Four lookup tables of 256 32-bit words each = 4 KB of state that must be held and rewritten. This size is what makes bcrypt awkward to parallelize on a GPU's small per-core memory. , 4 KB of state). That 4 KB of constantly-rewritten state is what makes bcrypt awkward to run massively-parallel on a GPU.
bcrypt only feeds the first 72 bytes of a password into the key schedule. Everything after byte 72 is silently ignored. Two different passwords that share the same 72-byte prefix therefore produce a hash that verifies against either one . Type two long passwords below that agree for the first 72 bytes but differ afterward, and watch them cross-verify. Enter a password and choose a cost factor. The output is a real bcrypt hash computed in your browser — not simulated.
Hashes the same password at cost factors 8 through 14, sequentially. Each +1 in cost doubles the computation time. This is by design — the slowness IS the security. bcrypt's headline defense is slowness + per-user salt (Exhibits 1 & 3) — that is what survives a database breach. Constant-time comparison, shown here, is a secondary hardening: it stops a subtler leak in how you compare the final hash.
bcrypt.compare() checks a password against a stored hash in constant time, closing a timing oracle An attacker who can measure how long a comparison takes and learn a secret from it. A naive byte-by-byte === returns faster on the first mismatch, so response time leaks how many leading bytes were guessed correctly. . A naive === comparison returns as soon as it hits the first mismatched byte, so it runs longer the more leading bytes an attacker guesses correctly. That duration is a leak. bcrypt.compare() checks every byte regardless, so its time reveals nothing.
Honesty note: a real === leak on a modern CPU is a few nanoseconds — far too small to see on a bar. Choose how to expose it: Not all hashing algorithms are equal. This comparison shows why bcrypt remains a strong choice and when to prefer alternatives.
Hash the same password with bcrypt (cost 12) and PBKDF2 (100,000 rounds via WebCrypto). Three breach scenarios showing what happens when passwords are stored as plaintext, unsalted MD5, or bcrypt hashes. The button below builds a real table: it MD5s every entry in the demo's common-password wordlist, then looks each stored digest up in that table. The cells hold only the digest, so an account whose password is not in the wordlist genuinely cannot be recovered.
The cost-downgrade experiment. Pick the cost the database was hashed at, then run the attack. Same wordlist, same code, same time budget — the only variable is cost. Every hash and every guess below is real bcrypt; nothing is simulated or timer-driven. Securing passwords requires transitioning away from outdated hashing methods toward modern, adaptive standards. This analysis outlines the essential mechanisms of password protection and best practices for implementation.
Password hashing is a fundamental security practice that transforms plaintext passwords into irreversible strings of characters. Unlike encryption, which is designed to be decrypted with a key, a hash is a one-way mathematical function meant to verify user identity without ever exposing the original credentials. This process serves as a cornerstone for maintaining data integrity within any modern digital infrastructure.
Standard algorithms like MD5 or SHA-1 are computationally efficient, which makes them ideal for file integrity checks but dangerous for password storage. Because they are fast, attackers can perform billions of guesses per second to crack stored hashes. Bcrypt distinguishes itself by being intentionally slow, leveraging a modified Blowfish cipher that forces attackers to invest significant time and hardware resources for every single attempt.
Salting introduces a unique, random string to each password before it is processed through the hashing function. This ensures that even if two users choose the same password, their final hashes will look completely different in the database. As emphasized by the Auth0 standard, this simple yet effective layer of protection effectively renders mass-automated attacks against your user database impossible to execute.
Bcrypt utilizes an adaptive parameter known as the work factor, or cost, which determines how many iterations the hashing function performs. This flexibility allows engineers at Inside Deep Tech to future-proof their systems, increasing the cost parameter as hardware performance improves. The mechanism directly correlates the time required to compute a hash with the overall security level provided to the user.
By artificially slowing down the hashing speed, Bcrypt forces a hardware-intensive bottleneck on attackers attempting massive parallelized brute-force attacks. Below is a comparison of how different cost factors impact verification times on standard server hardware: This table illustrates why selecting the correct factor requires balancing user convenience with the security posture of the host system.
Rainbow table attacks rely on pre-computed lists of hashes for every possible input string. By integrating a unique salt per password, Bcrypt forces attackers to recompute these tables specifically for every targeted database. Such methods are essential for preventing the simple reverse-engineering of user credentials. When a new user submits a registration form, the application must immediately capture the password and feed it into the Bcrypt function alongside a randomly generated salt. This ensures that the record is effectively blinded from the moment it is stored. For those managing on-premises software deployments, this process must be part of a larger, strictly controlled data handling pipeline.
Verification works by re-hashing the incoming password attempt using the salt stored from the initial registration record. The system then performs a timing-resistant comparison to see if the resulting hash matches the one in the database. This approach allows organizations to verify credentials safely, even as they evaluate XDR platforms to improve their broader security visibility.
Developers should utilize well-maintained libraries rather than rolling their own implementations. For those working within the Python ecosystem, the pyca/bcrypt library offers a robust interface for handling hashes and managing cost factors natively. Using established code reduces the risk of logic errors and ensures that cryptographic standards remain consistent across your technical stack.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Password • https://en.wikipedia.org/wiki/Salted%20Challenge%20Response%20Authentication%20Mechanism • https://en.wikipedia.org/wiki/List%20of%20data%20breaches • https://github.com/Manjeetkumarr/secure-login-system • https://github.com/1Elaigwu/secure-user-registration-system • https://dev.to/ettalibi02assia/building-a-secured-user-authentication-system-with-php-mysql-pdo-and-hashed-password-4mpj • https://codesignal.com/learn/courses/securing-your-symfony-app/lessons/secure-user-registration-and-login-with-bcrypt • https://github.com/JaocHatter/Login-Register-app-with-Bcrypt • https://code.prasunbarua.com/2026/05/build-complete-full-stack.html • https://dev.to/tuhin114/mastering-secure-authentication-in-nodejs-loginlogout-with-bcryptjs-and-jwt-4kcl
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure User Registration And Login System With Bcrypt.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |