Complete Technical Paper Content — Secure Voice Communication System Using AES Encryption
Overview & System Context
Secure Voice Communication System Using Aes Encryption: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4250 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Secure voice (alternatively secure speech or ciphony) is a term in cryptography for the encryption of voice communication over a range of communication types such as radio, telephone or IP.
Voice over Internet Protocol (VoIP), also known as IP telephony, is a set of technologies used primarily for voice communication sessions over Internet Protocol (IP) networks, such as the Internet. VoIP enables voice calls to be transmitted as data packets, facilitating various methods of voice communication, including voice and video conferencing applications and appliances and VoIP phones. Regular telephones can also be used for VoIP by connecting them to the Internet via an analog telephone adapter (ATA), which converts telephone signals into digital data packets that can be transmitted over IP networks.
The broader terms Internet telephony, broadband telephony, and broadband phone service specifically refer to the delivery of voice and other communication services, such as fax, SMS, and voice messaging, over the Internet, in contrast to the traditional public switched telephone network (PSTN), commonly known as plain old telephone service (POTS). VoIP technology has evolved to integrate with mobile telephony, including Voice over LTE (VoLTE) and Voice over NR (Vo5G), enabling seamless voice communication over mobile data networks. These advancements have extended VoIP's role beyond its traditional use in Internet-based applications. It has become a key component of modern mobile infrastructure, as 4G and 5G networks rely entirely on this technology for voice transmission.
Network and transport – Creating reliable transmission over unreliable protocols, which may involve acknowledging receipt of data and retransmitting data that wasn't received. Session management – Creating and managing a session (sometimes glossed as simply a "call"), which is a connection between two or more peers that provides a context for further communication. Signaling – Performing registration (advertising one's presence and contact information) and discovery (locating someone and obtaining their contact information), dialing (including reporting call progress), negotiating capabilities, and call control (such as hold, mute, transfer/forwarding, dialing DTMF keys during a call [e.g. to interact with an automated attendant or IVR], etc.). Media description – Determining what type of media to send (audio, video, etc.), how to encode/decode it, and how to send/receive it (IP addresses, ports, etc.). Media – Transferring the actual media in the call, such as audio, video, text messages, files, etc. Quality of service – Providing out-of-band content or feedback about the media such as synchronization, statistics, etc. Security – Implementing access control, verifying the identity of other participants (computers or people), and encrypting data to protect the privacy and integrity of the media contents and/or the control messages. VoIP protocols include: Matrix, open standard for online chat, voice over IP, and videotelephony Session Initiation Protocol (SIP), connection management protocol developed by the IETF H.323, one of the first VoIP call signaling and control protocols that found widespread implementation. Since the development of newer, less complex protocols such as MGCP and SIP, H.323 deployments are increasingly limited to carrying existing long-haul network traffic. Media Gateway Control Protocol (MGCP), connection management for media gateways H.248, control protocol for media gateways across a converged internetwork consisting of the traditional PSTN and modern packet networks Real-time Transport Protocol (RTP), transport protocol for real-time audio and video data Real-time Transport Control Protocol (RTCP), sister protocol for RTP providing stream statistics and status information Secure Real-time Transport Protocol (SRTP), encrypted version of RTP Session Description Protocol (SDP), a syntax for session initiation and announcement for multi-media communications and WebSocket transports.
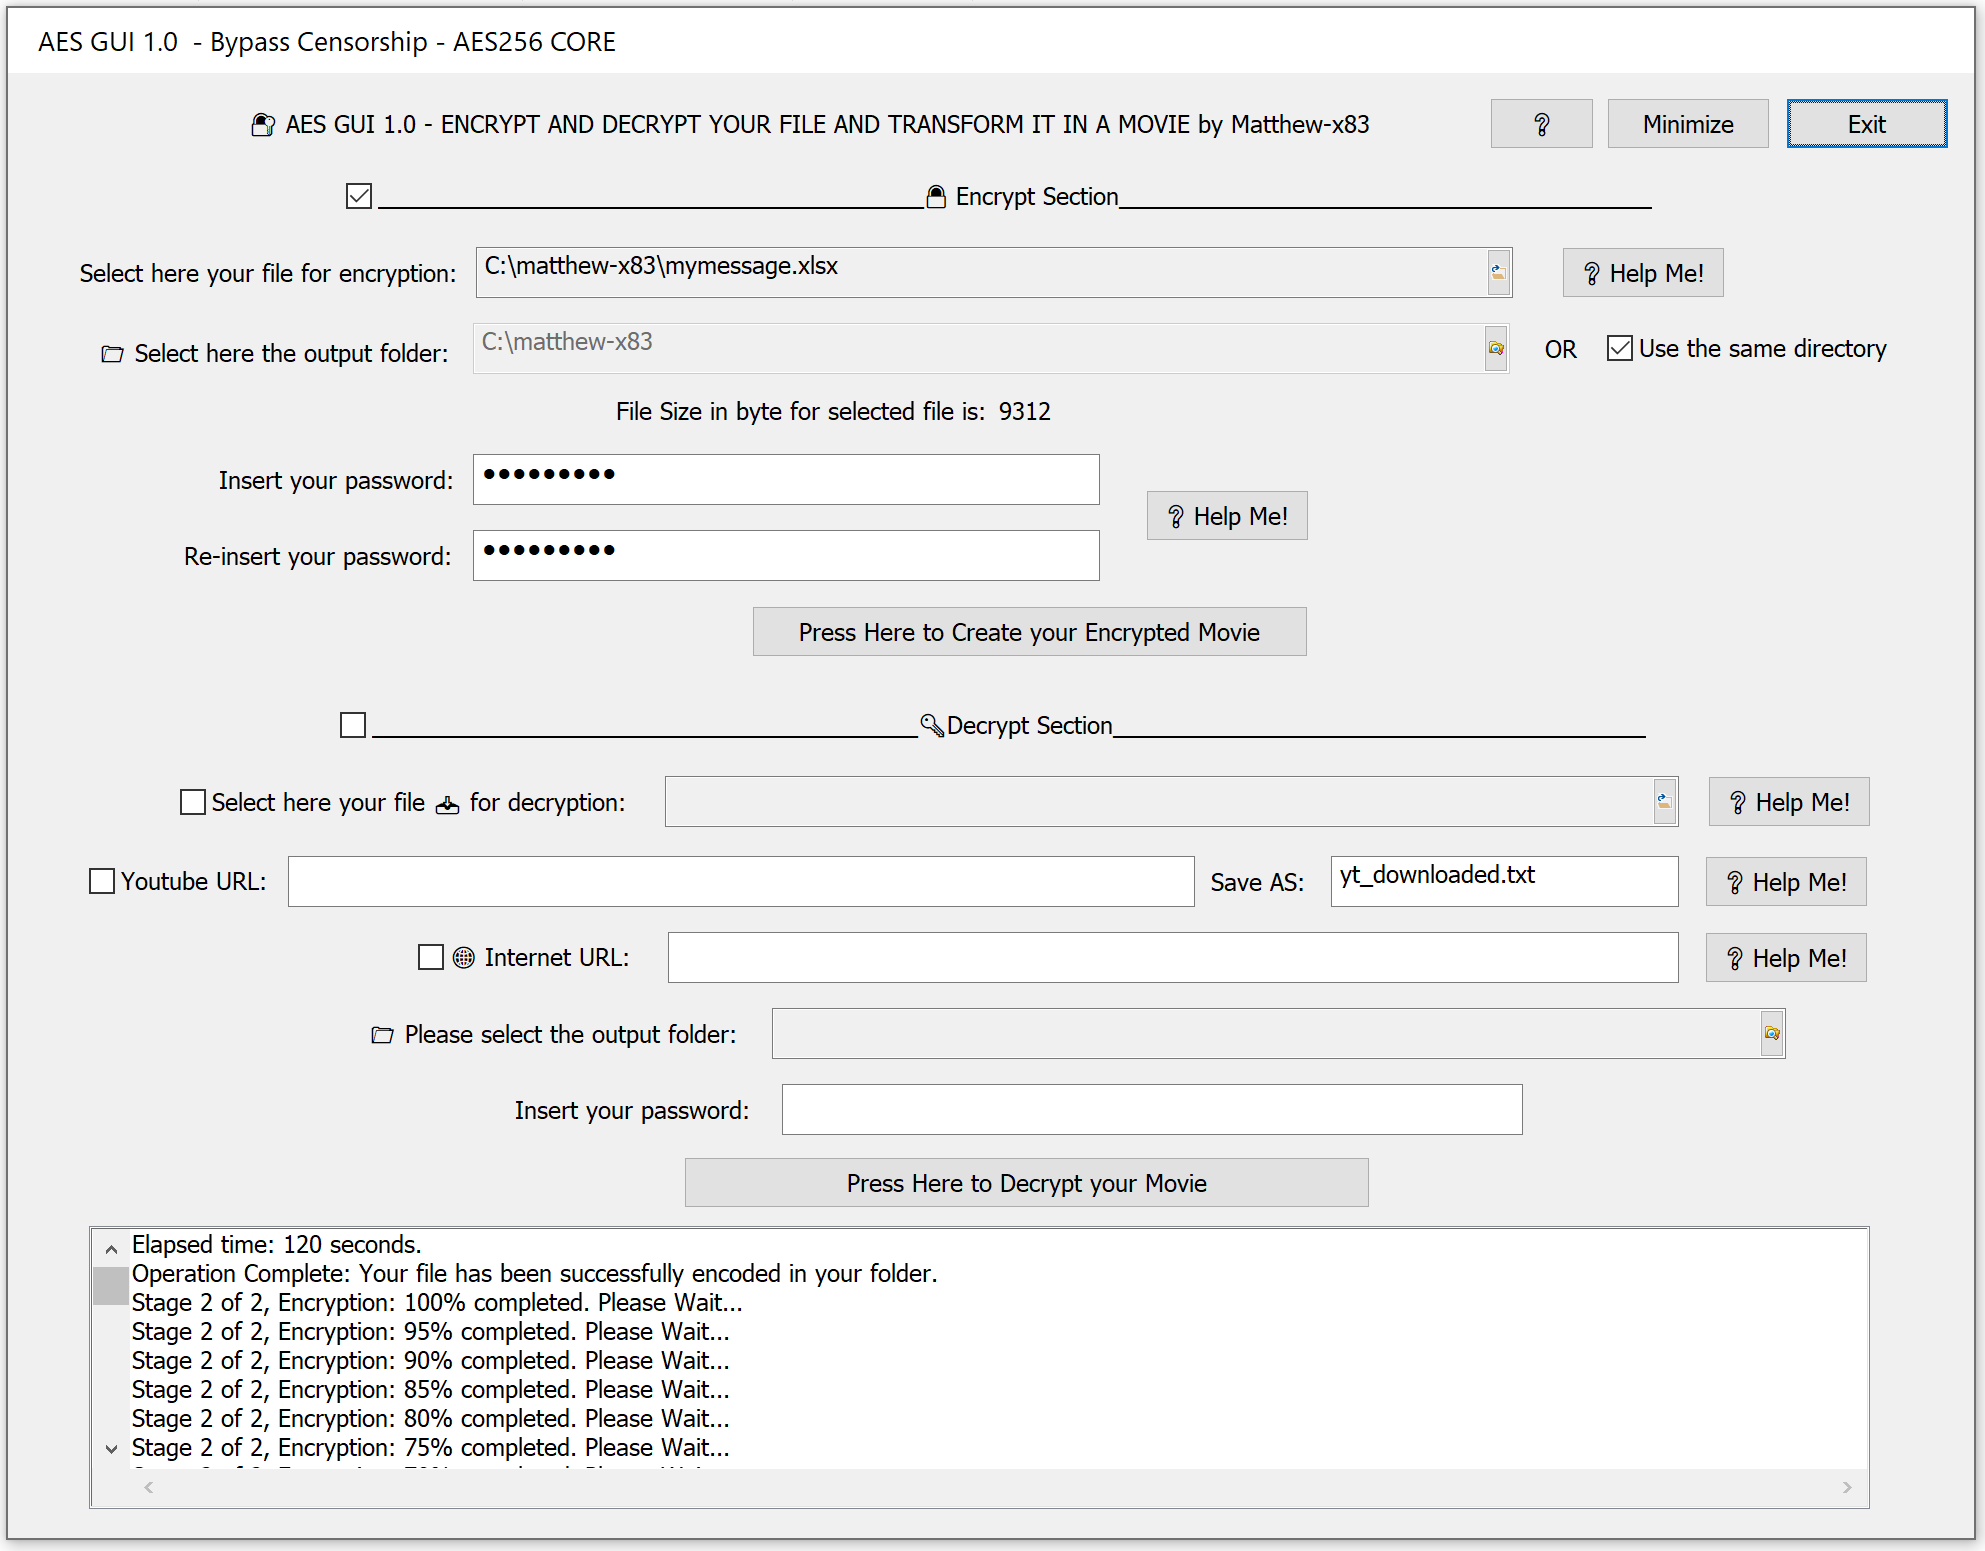
Inter-Asterisk eXchange (IAX), protocol used between Asterisk PBX instances Extensible Messaging and Presence Protocol (XMPP), instant messaging, presence information, and contact list maintenance Jingle, for peer-to-peer session control in XMPP Skype protocol, proprietary Internet telephony protocol suite based on peer-to-peer architecture Figure 1: Matthew-x83 - AES GUI v1.0 Mass-market VoIP services use existing broadband Internet access, by which subscribers place and receive telephone calls in much the same manner as they would via the PSTN. Full-service VoIP phone companies provide inbound and outbound service with direct inbound dialing. Many offer unlimited domestic calling and sometimes international calls for a flat monthly subscription fee. Phone calls between subscribers of the same provider are usually free when flat-fee service is not available.
A VoIP phone is necessary to connect to a VoIP service provider. This can be implemented in several ways: Dedicated VoIP phones connect directly to the IP network using technologies such as wired Ethernet or Wi-Fi. These are typically designed in the style of traditional digital business telephones. An analog telephone adapter connects to the network and implements the electronics and firmware to operate a conventional analog telephone attached through a modular phone jack. Some residential Internet gateways and cable modems have this function built in. Softphone application software installed on a networked computer that is equipped with a microphone and speaker, or headset. The application typically presents a dial pad and display field to the user to operate the application by mouse clicks or keyboard input.
In the case of a private VoIP system, the primary telephony system itself is located within the private infrastructure of the end-user organization. Usually, the system will be deployed on-premises at a site within the direct control of the organization. This can provide numerous benefits in terms of QoS control (see below), cost scalability, and ensuring privacy and security of communications traffic. However, the responsibility for ensuring that the VoIP system remains performant and resilient is predominantly vested in the end-user organization. This is not the case with a Hosted VoIP solution. Private VoIP systems can be physical hardware PBX appliances, converged with other infrastructure, or they can be deployed as software applications.
Generally, the latter two options will be in the form of a separate virtualized appliance. However, in some scenarios, these systems are deployed on bare metal infrastructure or IoT devices. With some solutions, such as 3CX, companies can attempt to blend the benefits of hosted and private on-premises systems by implementing their own private solution but within an external environment. Examples can include data center collocation services, public cloud, or private cloud locations. For on-premises systems, local endpoints within the same location typically connect directly over the LAN. For remote and external endpoints, available connectivity options mirror those of Hosted or Cloud VoIP solutions. However, VoIP traffic to and from the on-premises systems can often also be sent over secure private links. Examples include personal VPN, site-to-site VPN, private networks such as MPLS and SD-WAN, or via private SBCs (Session Border Controllers). While exceptions and private peering options do exist, it is generally uncommon for those private connectivity methods to be provided by Hosted or Cloud VoIP providers.
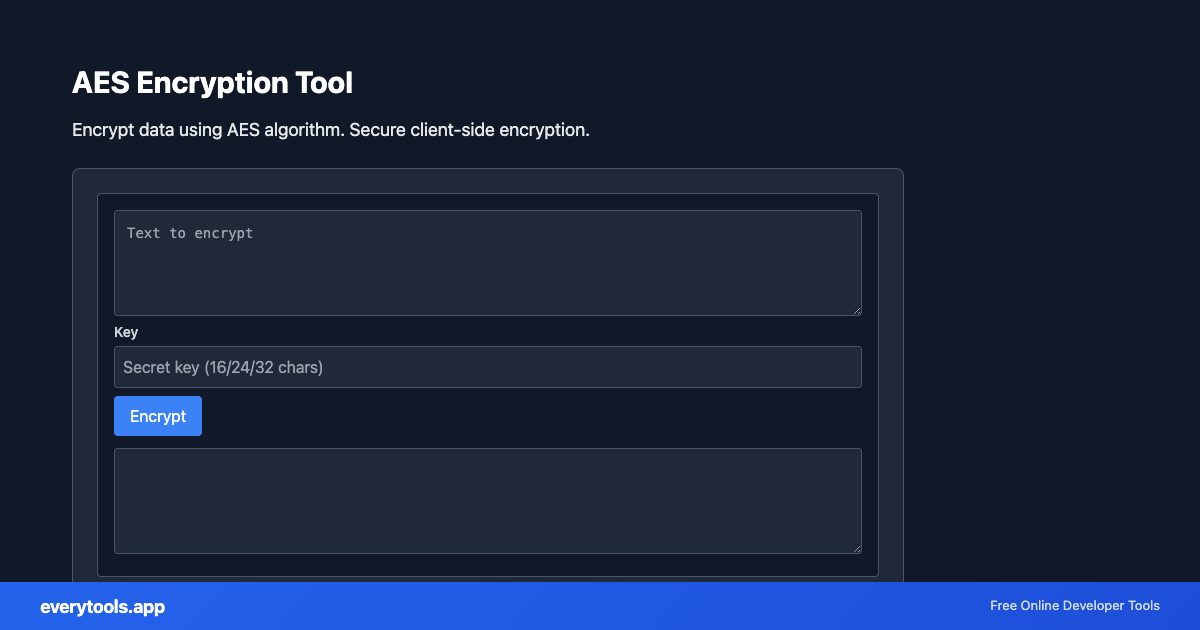
IEEE 802.11e is an approved amendment to the IEEE 802.11 standard that defines a set of quality-of-service enhancements for wireless LAN applications through modifications to the media access control (MAC) layer. The standard is considered of critical importance for delay-sensitive applications, such as voice over wireless IP. IEEE 802.1p defines 8 different classes of service (including one dedicated to voice) for traffic on layer-2 wired Ethernet. The ITU-T G.hn standard, which provides a way to create a high-speed (up to 1 gigabit per second) Local area network (LAN) using existing home wiring (power lines, phone lines and coaxial cables). G.hn provides QoS by means of Contention-Free Transmission Opportunities (CFTXOPs), which are allocated to flows (such as a VoIP call) that require QoS and which have negotiated a contract with the network controllers Figure 2: AES Encryption Tool – Free Online AES Encryption | everytools A VoIP media gateway controller (aka Class 5 Softswitch) works in cooperation with a media gateway (aka IP Business Gateway) and connects the digital media stream, so as to complete the path for voice and data. Gateways include interfaces for connecting to standard PSTN networks. Ethernet interfaces are also included in modern systems, which are specially designed to link calls that are passed via VoIP. E.164 is a global numbering standard for both the PSTN and public land mobile network (PLMN). Most VoIP implementations support E.164 to allow calls to be routed to and from VoIP subscribers and the PSTN/PLMN. VoIP implementations can also allow other identification techniques to be used. For example, Skype allows subscribers to choose Skype names (usernames) whereas SIP implementations can use Uniform Resource Identifier (URIs) similar to email addresses. Often VoIP implementations employ methods of translating non-E.164 identifiers to E.164 numbers and vice versa, such as the Skype-In service provided by Skype and the E.164 number to URI mapping (ENUM) service in IMS and SIP. Echo can also be an issue for PSTN integration. Common causes of echo include impedance mismatches in analog circuitry and an acoustic path from the receive to transmit signal at the receiving end.
As the popularity of VoIP grows, governments are becoming more interested in regulating VoIP in a manner similar to PSTN services. Throughout the developing world, particularly in countries where regulation is weak or captured by the dominant operator, restrictions on the use of VoIP are often imposed, including in Panama where VoIP is taxed, Guyana, where VoIP is prohibited. In Ethiopia, where the government is nationalizing telecommunication service, it is a criminal offense to offer services using VoIP. The country has installed firewalls to prevent international calls from being made using VoIP. These measures were taken after the popularity of VoIP reduced the income generated by the state-owned telecommunications company.
PC to PC; within or outside India PC / a device / Adapter conforming to the standard of any international agencies like ITU or IETF, etc., in India to PSTN/PLMN abroad. Any device / Adapter conforming to standards of International agencies like ITU, IETF etc., connected to ISP node with static IP address to similar device / Adapter; within or outside India. Except whatever is described in condition (ii) above, no other form of Internet Telephony is permitted. In India no Separate Numbering Scheme is provided to the Internet Telephony. Presently the 10-digit Numbering allocation based on E.164 is permitted to the Fixed Telephony, GSM, CDMA wireless service. For Internet Telephony, the numbering scheme shall only conform to IP addressing Scheme of Internet Assigned Numbers Authority (IANA). Translation of E.164 number / private number to IP address allotted to any device and vice versa, by ISP to show compliance with IANA numbering scheme is not permitted. The Internet Service Licensee is not permitted to have PSTN/PLMN connectivity. Voice communication to and from a telephone connected to PSTN/PLMN and following E.164 numbering is prohibited in India.
2. System Architecture & Core Working Principles A secure telephone is a telephone that provides voice security in the form of end-to-end encryption for the telephone call, and in some cases also the mutual authentication of the call parties, protecting them against a man-in-the-middle attack. Concerns about massive growth of telephone tapping incidents led to growing demand for secure telephones. The practical availability of secure telephones is restricted by several factors; notably politics, export issues, incompatibility between different products (the devices on each side of the call have to use the same protocol), and high (though recently decreasing) price of the devices.
The best-known product on the US government market is the STU-III family. However, this system has now been replaced by the Secure Terminal Equipment (STE) and SCIP standards which defines specifications for the design of equipment to secure both data and voice. The SCIP standard was developed by the NSA and the US DOD to derive more interoperability between secure communication equipment. A new family of standard secure phones has been developed based on Philip Zimmermann's VoIP encryption standard ZRTP.
Scramblers were used to secure voice traffic during World War II (1939-1945), but were often intercepted and decoded due to scrambling's inherent insecurity. The first true secure telephone (operational from 1943) was SIGSALY, a massive device that weighed over 50 tons. The NSA, formed in 1952, developed a series of secure telephones, including the STU-I of the 1970s, STU-II and STU-III, as well as voice-encryption devices for military telephones. In 1989 an Irish company called Intrepid developed one of the most advanced secure phones. Called "Milcode", the phone was the first to implement code-excited linear prediction (or CELP) which dramatically improved voice quality and user-operability over previous LPC (Linear Predictive Coding) and LPC-10e versions. Milcode also boasted significantly higher levels of security than previous secure telephones. The base model offered a proprietary encryption algorithm with a key-length of 512 bits, and a more advanced model with a key-length of 1024 bits. Key exchange used a public key, based on Diffie-Hellman, as opposed to a plug-in datakey. A new key was generated for each phone call. Milcode was also able to encrypt fax and data and was electromagnetically shielded to NATO TEMPEST standards. Other products of historical significance are PGPfone and Nautilus (designed as a non-key escrow alternative to Clipper, now officially discontinued, but still available on SourceForge), SpeakFreely, and the security VoIP protocol wrapper Zfone (developed by Phil Zimmermann, who wrote the PGP software).
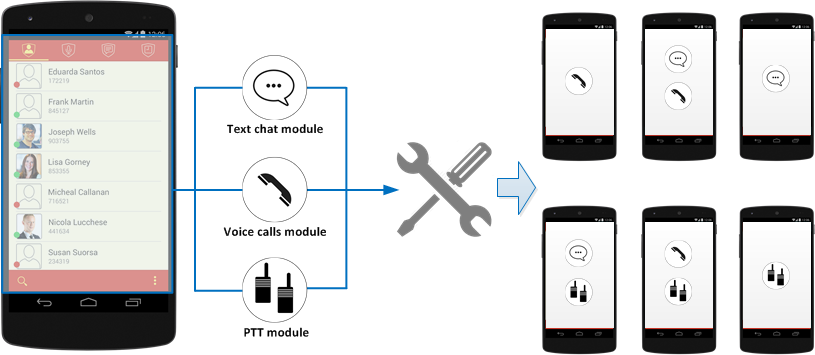
Scrambling, generally using a form of voice inversion, was available from suppliers of electronic hobbyist kits and is common on FRS radios. Analog scrambling is still used, as some telecommunications circuits, such as HF links and telephone lines in the developing world, are of very low quality. Microphone blocker Mobile phone tracking Secure Real-time Transport Protocol (SRTP) SCIP TETRA A5/1 ZRTP Secure voice Figure 3: Voice and text encryption platform UG students, Department of Electronics & Telecommunication Engineering, KITS College of Engineering, Kolhapur, Maharashtra, India Professor, Department of Electronics & Telecommunication Engineering, KITS College of Engineering, Kolhapur, Maharashtra, India Abstract – A secure voice communication system is developed using ESP32 microcontrollers to facilitate real-time, encrypted audio transmission. Digital voice signals are captured via an INMP441 microphone through the I2S protocol and protected using AES encryption to ensure data confidentiality. Transmission is managed by the ESP-NOW protocol, providing a low-latency, peer-to-peer connection that functions independently of external network infrastructure. Integration of a MAX98357A amplifier and a push-to-talk mechanism optimizes audio output quality while maximizing power efficiency during operation. Such a framework provides a robust and cost-effective solution for specialized communication needs in defense, industrial monitoring, and emergency response scenarios.
Rapid advancements in wireless technology have increased the demand for secure and private communication channels, particularly in sensitive sectors such as defense and industrial operations. Conventional analog voice transmission is highly susceptible to eavesdropping and signal interference, making digital encryption a necessity for maintaining data integrity. Modern embedded systems now offer the processing power required to handle real-time audio digitization and complex cryptographic algorithms simultaneously.
The primary objective of this research is to develop a robust, peer-to-peer speech encryption framework using the ESP32 microcontroller. By integrating digital audio interfacing through the I2S protocol and applying AES encryption, the system ensures that voice data remains confidential during transit. Utilizing the ESP-NOW protocol allows for low-latency communication without relying on traditional network infrastructures like Wi-Fi routers. This approach results in a cost-effective, portable, and highly secure solution for short-range voice communication in environments where privacy is paramount.
The hardware integration focuses on high-fidelity digital signal processing to eliminate the noise associated with traditional analog circuits. By employing the I2S (Inter-IC Sound) protocol, the system maintains a direct digital path from the microphone to the encryption engine, preserving audio clarity and reducing the computational overhead of signal conversion. This seamless synchronization between the INMP441 sensor and the ESP32s processing cores allows for the execution of the Advanced Encryption Standard (AES) in real-time, ensuring that the latency remains below the threshold of human perception. Consequently, the project demonstrates that sophisticated cryptographic security can be achieved on low-power, cost-effective embedded hardware without compromising the user experience of a fluid, natural conversation.
The development of secure voice communication systems requires a multidisciplinary approach involving real-time digital signal processing, cryptographic efficiency, and low-latency wireless transmission. The following research works provide the foundational framework for the proposed speech encryption scheme. 3. Software Implementation, Frameworks & Protocols Design and implementation of a real-time AES-256 encrypted audio transmission system on an ARM Cortex-M4 platform.
A significant benchmark in the field was established by Gupta and Chen (2023), who demonstrated the feasibility of implementing AES-256 encryption on an ARM Cortex-M4 platform. Their research proved that high-level encryption standards could be executed on low-power microcontrollers without compromising audio quality or introducing significant latency. This validates the use of the ESP32 in the current project, as it possesses the computational capacity to handle complex cryptographic A lightweight hybrid cryptography scheme for secure voice communication in IoT devices. Internet of Things and Cyber-Physical Systems. Another study titled A Lightweight Hybrid Cryptography Scheme for Secure Voice Communication in IoT Devices by K. Sharma, P. Patel, and R. Kumar (Internet of Things and Cyber-Physical Systems, 2023) explores hybrid encryption methods combining 14 symmetric and asymmetric algorithms for secure IoT-based voice applications. The paper highlights that hybrid methods can enhance key management and strengthen overall data confidentiality. While our project focuses on symmetric AES encryption for simplicity and speed, this study provides insight into future improvements such as key exchange mechanisms and hybrid encryption for multi-node communication systems.
Wang et al. in their paper Efficient HardwareSoftware Co-Design for Voice Data Encryption on Edge Devices (Microprocessors and Microsystems, 2023) proposed the use of DMA (Direct Memory Access) and buffer management techniques to optimize real time performance in embedded encryption systems. Their results demonstrate that offloading repetitive data transfers to DMA significantly reduces latency and processor load. This concept has been applied in our project to enable simultaneous data sampling, encryption, and transmission, ensuring smooth voice streaming without delays. with phrases like "Welcome"thereby enhancing the mascots interactivity and making it more engaging and lifelike.
Sharma and colleagues demonstrated in their research on Real-Time Secure Voice Transmission for Embedded Systems that implementing AES in CTR mode (Counter mode) provides a balanced trade-off between computational efficiency and security. Unlike CBC mode, which requires sequential block processing, CTR mode allows parallel encryption of blocks, enabling faster processing suitable for streaming audio applications. This insight influenced the selection of AES-CTR mode in this project to maintain real time encryption with minimal delay.
Kumar et al. presented their work on Real-Time Audio Processing using Embedded Microcontrollers, where they highlighted the capabilities of the ESP32-WROOM-32 in handling high-speed data processing and wireless communication simultaneously. Their research demonstrated that ESP32 can efficiently manage real-time audio streams with minimal delay. This finding supported the selection of ESP32 as the core processing unit in this project.
Developing an end-to-end encrypted link, this system utilizes the ESP32 microcontroller to facilitate secure, real-time wireless voice communication. High-fidelity digital audio is captured via the I2S protocol using an INMP441 microphone and protected with robust AES encryption to ensure data confidentiality. The framework leverages the connectionless ESP-NOW protocol for low-latency, peer-to-peer transmission, effectively bypassing the need for traditional network infrastructure. Final audio reconstruction is managedby a MAX98357A amplifier, while a push-to-talk mechanism optimizes operational power efficiency.
This integrated hardware-software approach provides a compact and cost-effective solution for secure communication in defense, industrial, and emergency sectors. Establishing a secure channel for voice data begins with the seamless integration of digital hardware and cryptographic firmware. The process initiates at the transmitter, where acoustic signals are captured by an INMP441 digital microphone and converted into 24-bit audio data via the I2S protocol. This digitized stream is fed into the ESP32 microcontroller, where it is partitioned into discrete packets and subjected to Advanced Encryption Standard (AES) processing. By utilizing the dual-core capabilities of the ESP32, the system ensures that high-speed data acquisition and intensive encryption tasks occur simultaneously, preventing any latency that could disrupt the natural flow of human speech.
Once the audio packets are encrypted, they are dispatched across a 2.4 GHz wireless link using the connectionless ESP-NOW protocol. This method of transmission is specifically chosen to bypass the time-consuming handshakes and network overhead associated with traditional Wi-Fi or Bluetooth protocols. By communicating directly through MAC addresses, the system achieves a peer-to-peer connection that is both high-speed and infrastructure-independent. This localized approach not only ensures low-latency performance essential for real-time conversation but also adds a layer of physical security by keeping the The communication cycle concludes at the receiver unit, where the incoming ciphertext is decrypted using a pre-shared secret key to restore the original digital audio values. These restored signals are then routed through a MAX98357A I2S Class-D amplifier, which converts the digital data back into a high-fidelity analog output to drive a speaker. Throughout this process, a push-to-talk mechanism manages the activation of the radio frequency components, ensuring that the system remains power-efficient and only occupies the wireless spectrum during active speech. This comprehensive hardware-software co-design results in a robust and portable solution for secure communication in sensitive industrial or tactical environments.
The system employs ESP-NOW, a connectionless communication protocol operating at the Data Link Layer (OSI Layer 2), which eliminates the need for the TCP/IP stack and traditional Wi-Fi association, enabling direct device-to-device communication with latency below 10ms. Reliable and secure point-to-point transmission is achieved through MAC address-based authentication, where each ESP32s unique 48-bit hardware address is predefined to establish a dedicated communication link while filtering out unrelated traffic at the hardware level. To ensure data confidentiality, the system integrates AES-256 encryption in Cipher Block Chaining (CBC) mode, utilizing a 16-byte Initialization Vector (IV) generated from the ESP32s internal True Random Number Generator (TRNG) for each packet, ther eby preventing pattern leakage and enhancing security even during repetitive or silent transmissions. The receiver reconstructs the original 16-bit PCM audio using the shared key and transmitted IV. By combining low-latency ESP-NOW communication, hardware-level filtering, and strong cryptographic protection, the system establishes a secure, efficient, and zero-trust wireless communication framework where intercepted data remains computationally infeasible to decode in real time.
4. Practical Deployment, Analysis & Case Studies The secure voice communication system achieves high-quality audio transmission with minimal delay. The use of the I2S protocol improves signal clarity by reducing noise compared to analog communication. The ESP32 efficiently handles AES encryption and decryption, maintaining real-time performance. ESP-NOW ensures stable and reliable wireless communication over moderate distances. The system also demonstrates good power efficiency, especially with push-to-talk functionality.
Security is enhanced as encrypted data prevents unauthorized access. Overall, the system provides a low-cost and effective solution for secure voice communication. Successful Implementation of Secure Audio: The project successfully demonstrates a functional end-to-end encrypted voice link using the ESP32, proving that Real-Time Performance and Low Latency: By utilizing the dual-core processing of the ESP32 and the connectionless ESP-NOW protocol, the system maintains real-time audio transmission with latency levels below the threshold of human perception.
Infrastructure Independence: The system operates as a reliable peer-to-peer network without the need for external Wi-Fi routers or internet connectivity, making it ideal for deployment in remote or tactically sensitive environments. Optimized Resource Management: Integration of a push-to-talk mechanism and I2S digital interfacing ensures high audio clarity while significantly reducing power consumption for portable, battery-operated use.
Multi-Node Mesh Networking: Transitioning from a point-to-point link to a mesh network architecture would allow multiple users to communicate simultaneously across a wider area, with each device acting as a signal repeater. Dynamic Key Exchange Protocols: Implementing asymmetric encryption (like Elliptic Curve Diffie-Hellman) for initial handshaking would allow the system to generate unique session keys for every conversation, enhancing security against long-term key compromise.
Voice Activity Detection (VAD): Integrating AI-based VAD algorithms could replace the manual push-to-talk button, automatically triggering transmission only when human speech is detected to further optimize bandwidth and power. Biometric Authentication: Adding a fingerprint sensor or voice-print recognition to the ESP32 hardware would ensure that only authorized personnel can access the encrypted channel, adding a layer of physical security.
Advanced Audio Compression: Utilizing lightweight codecs (like Opus or Speex) could compress the digital audio data before encryption, allowing for longer transmission ranges and better performance in environments with high signal interference. GPS and Metadata Integration: Future iterations could include the transmission of encrypted metadata alongside voice, such as GPS coordinates or device ID, providing real-time location tracking for search and rescue or tactical teams.
5. Performance Evaluation & Extended Technical Observations Solar-Powered Integration: Developing a specialized power management circuit for solar charging would make the device entirely self-sustaining for long-term deployment in remote areas where traditional power sources are unavailable. Sharma, K., Patel, P., & Kumar, R. (2023). A lightweight hybrid cryptography scheme for secure voice communication in IoT devices. Internet of Things and Cyber-Physical Systems, 3, 180191.
Gupta, A., & Chen, S. Y. (2023). Design and implementation of a real-time AES-256 encrypted audio transmission system on an ARM Cortex-M4 platform. 2023 IEEE International Conference on Consumer Electronics (ICCE), 15. Wang, C., Li, H., & Zhng, Z. (2023). Efficient hardwaresoftware co-design for voice data encryption on edge devices. Microprocessors and Microsystems, 96, 104752.
Al-Asadi, M., Ahmed, N. A., & Saad, T. J. (2023). Enhancing security in wireless voice communication using a chaos-based encryption algorithm. Journal of Information Security and Applications, 76, 103525. of Embedded Systems and Applications, 12(3), 4552. SecureVoiceComms-Pro is an encrypted voice communication system designed for secure and reliable voice transmissions.
Leveraging modern encryption techniques, it provides a robust solution for confidential and clear audio communication. Ideal for users requiring secure communication channels in various domains, including business, remote work, and confidential discussions. Versatile for scenarios like remote meetings, secure business conversations, and any situation where encrypted voice communication is crucial.
You can use a crontab entry or create a systemd service for automatically running your scripts at startup. Using Crontab: Add the following line to the crontab file, replacing /path/to/your/main.py with the full path to your main.py script: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Secure%20voice • https://en.wikipedia.org/wiki/Voice%20over%20IP • https://en.wikipedia.org/wiki/Secure%20telephone • https://www.ijert.org/speech-encryption-scheme-for-secure-voice-communication-ijertv15is043839 • https://github.com/Unlimited-Research-Cooperative/SecureVoiceComms-Pro
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Voice Communication System Using AES Encryption.
[*] Metasploit Scan Running on Target Subnet for Secure Voice Communication System Using AES Encryption... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |