Complete Technical Paper Content — Security Audit Checklist Automation
Overview & System Context
Security Audit Checklist Automation: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9509 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background ISO/IEC 27001, titled Information security, cybersecurity and privacy protection — Information security management systems — Requirements, is an information security standard. It specifies the requirements for establishing, implementing, maintaining and continually improving an information security management system (ISMS) within the context of the organization, and includes requirements for the assessment and treatment of information security risks. The requirements are generic and are intended to be applicable to all organizations, regardless of type, size or nature. The requirements are set out in clauses 4 to 10, covering the context of the organization, leadership, planning, support, operation, performance evaluation and improvement; an annex to the standard lists a reference set of information security controls, for which ISO/IEC 27002 supplies the purpose and implementation guidance. An organization may implement the standard for its own purposes, or have its ISMS certified as conforming to it by an independent certification body following successful completion of an audit.
Certification is optional unless it is required by law, by a contract or by another scheme, and it applies only within the scope stated on the certificate. Certification bodies are commonly accredited by a national accreditation body, although accreditation is not compulsory. A systematic review of the academic literature published in 2021 found that few studies had examined the outcomes of certification empirically. It was originally published jointly by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC) in October 2005, with revised editions in 2013 and 2022. The 2022 edition was supplemented in February 2024 by ISO/IEC 27001:2022/Amd 1:2024, Climate action changes, which added one requirement, in the clause on the organization's context, that the organization determine whether climate change is a relevant issue, and one note, in the clause on interested parties, observing that interested parties can have requirements related to climate change.
assess its information security risks systematically, taking account of the potential consequences and likelihood of loss of confidentiality, integrity and availability of information; select risk treatment options and determine the controls necessary to implement them, controls being one form of treatment alongside others such as avoiding a risk or sharing it with another party; and operate, monitor, review and continually improve the management system, so that it continues to meet the organization's information security requirements. Other standards in the ISO/IEC 27000 family provide additional guidance on certain aspects of designing, implementing and operating an ISMS, for example on information security risk management (ISO/IEC 27005).
Clause 4, on the context of the organization, requires the organization to understand its context and the needs and expectations of interested parties, to determine the scope of the ISMS and to establish the management system itself. The organization has to determine which of the requirements of those interested parties are relevant to the ISMS; such requirements can include legal and regulatory requirements and contractual obligations, which are therefore dealt with within the management system rather than being specified by the standard itself. Clause 5 concerns leadership, requiring commitment from top management, an information security policy, and the assignment of roles, responsibilities and authorities. Clause 6, on planning, contains the requirements for information security risk assessment and risk treatment and for information security objectives. Risks identified in the risk assessment must be assigned to risk owners, and the risk treatment process requires the organization to formulate a risk treatment plan and to obtain the approval of the risk owners both for that plan and for the acceptance of the residual information security risks, so that those decisions rest with the management that owns the risks rather than with the auditors or with the staff carrying out the assessment. The information security objectives must be consistent with the information security policy, be measurable if that is practicable, take account of applicable information security requirements and of the results of risk assessment and risk treatment, and be monitored, communicated and updated as appropriate; the organization must also determine what will be done to achieve them, what resources will be required, who will be responsible, when they are to be achieved and how the results will be evaluated.
Clause 7 covers support, including resources, competence, awareness, communication and documented information, and clause 8 covers the operation of the processes planned under clause 6. The clauses follow the harmonized structure for management system standards set out in Annex SL of the ISO/IEC Directives, from which the standard takes its high-level structure, identical sub-clause titles, identical text, common terms and core definitions. The standard says that this maintains compatibility with other management system standards that have adopted Annex SL, and is useful for organizations that choose to operate a single management system meeting the requirements of two or more such standards. The terms and definitions used are those of ISO/IEC 27000, which is the standard's only normative reference. The standard requires a range of documented information to be created and retained, including the scope of the ISMS, the information security policy, the information security risk assessment and risk treatment processes, the Statement of Applicability, the risk treatment plan and the information security objectives, together with records of competence, of the results of monitoring and measurement, of the internal audit programme and its results, of management reviews, and of nonconformities and the actions taken in response.
Clauses 9 and 10 require the organization to monitor, measure, analyse and evaluate the performance of the ISMS, to carry out internal audits and management reviews at planned intervals, to react to nonconformities and take corrective action, and to continually improve the suitability, adequacy and effectiveness of the management system. A software review is "a process or meeting during which a software product is examined by a project personnel, managers, users, customers, user representatives, or other interested parties for comment or approval". In this context, the term "software product" means "any technical document or partial document, produced as a deliverable of a software development activity", and may include documents such as contracts, project plans and budgets, requirements documents, specifications, designs, source code, user documentation, support and maintenance documentation, test plans, test specifications, standards, and any other type of specialist work product.
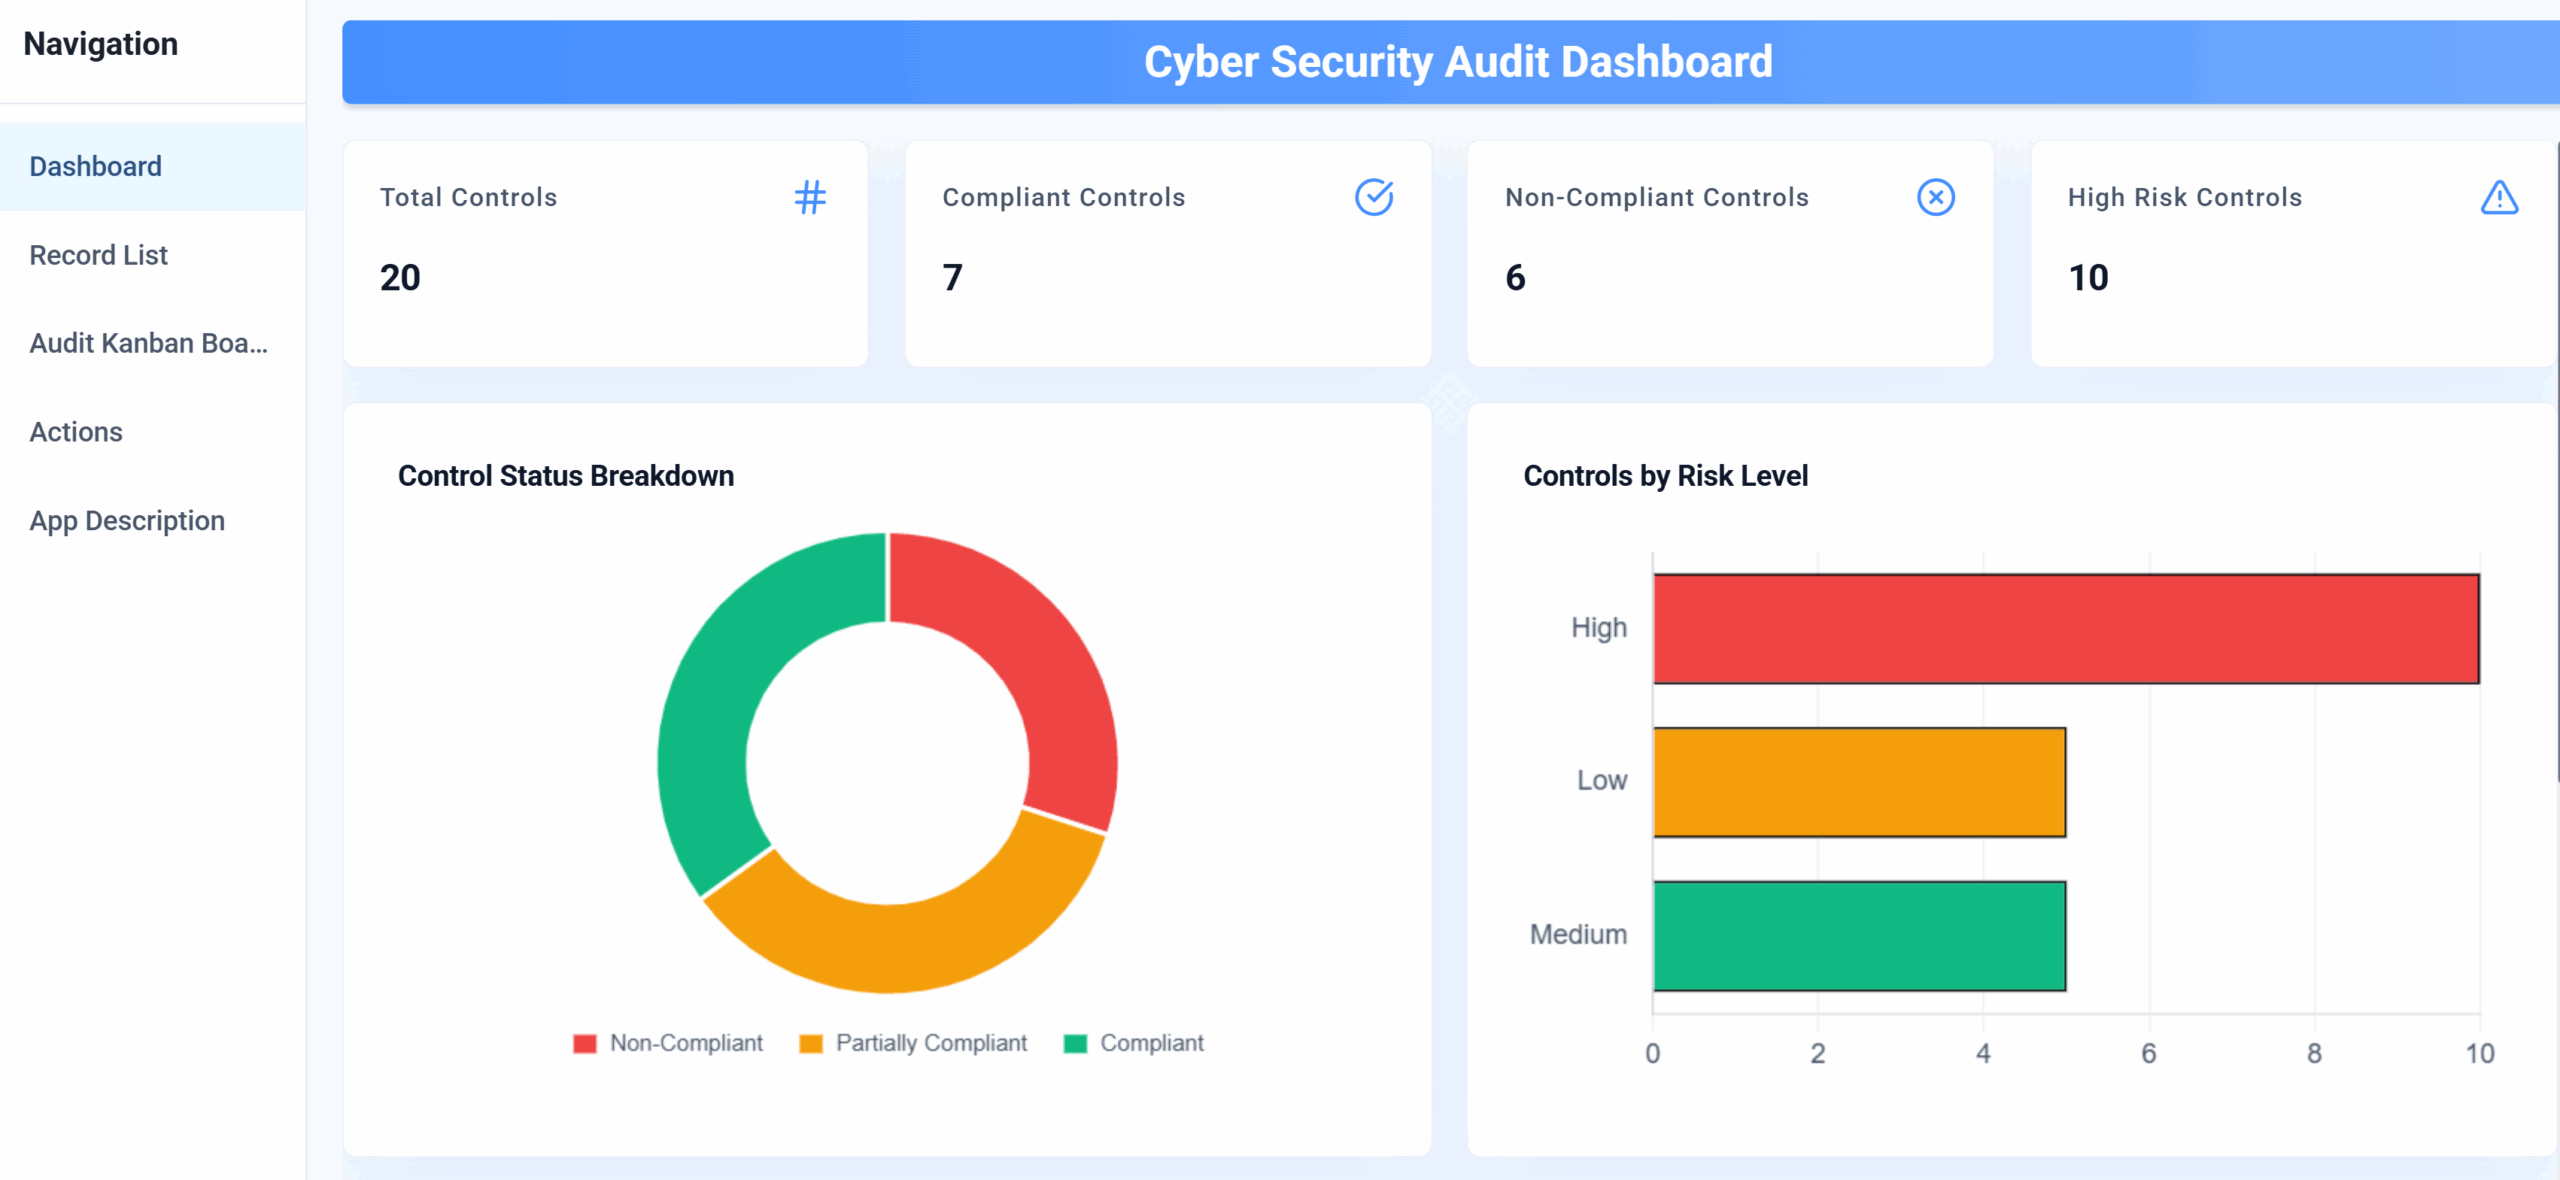
Figure 1: AI Driven Data Compliance & Audit Automation Software App Software peer reviews are conducted by one or more colleagues of the author, to evaluate the technical content and/or quality of the work. Software management reviews are conducted by management representatives to evaluate the status of work done and to make decisions regarding downstream activities. Software audit reviews are conducted by personnel external to the software project, to evaluate compliance with specifications, standards, contractual agreements, or other criteria.
0. [Entry evaluation]: The review leader uses a standard checklist of entry criteria to ensure that optimum conditions exist for a successful review. 1. Management preparation: Responsible management ensure that the review will be appropriately resourced with staff, time, materials and tools, and will be conducted according to policies, standards or other relevant criteria. 2. Planning the review: The review leader identifies or confirms the objectives of the review, organises a team of reviewers and ensures that the team is equipped with all necessary resources for conducting the review. 3. Overview of review procedures: The review leader, or some other qualified person, ensures (at a meeting if necessary) that all reviewers understand the review goals, the review procedures, the materials available to them and the procedures for conducting the review. 4. [Individual] Preparation: The reviewers individually prepare for group examination of the work under review, by examining it carefully for "anomalies" (potential defects), the nature of which will vary with the type of review and its goals. 5.
[Group] Examination: The reviewers meet at a planned time to pool the results of their preparation activity and arrive at a consensus regarding the status of the document (or activity) being reviewed. 6. Rework/follow-up: The author of the work product (or other assigned person) undertakes whatever actions are necessary to repair defects or otherwise satisfy the requirements agreed to at the examination meeting. The review leader verifies that all action items are closed. 7. [Exit evaluation]: The review leader verifies that all activities necessary for successful review have been accomplished and that all outputs appropriate to the type of review have been finalized.
Business continuity may be defined as "the capability of an organization to continue the delivery of products or services at pre-defined acceptable levels following a disruptive incident", and business continuity planning (or business continuity and resiliency planning) is the process of creating systems of prevention and recovery to deal with potential threats to a company. In addition to prevention, the goal is to enable ongoing operations before and during execution of disaster recovery. Business continuity is the intended outcome of proper execution of both business continuity planning and disaster recovery. Several business continuity standards have been published by various standards bodies to assist in checklisting ongoing planning tasks. Business continuity requires a top-down approach to identify an organisation's minimum requirements to ensure its viability as an entity. An organization's resistance to failure is "the ability ... to withstand changes in its environment and still function". Often called resilience, resistance to failure is a capability that enables organizations to either endure environmental changes without having to permanently adapt, or the organization is forced to adapt a new way of working that better suits the new environmental conditions.
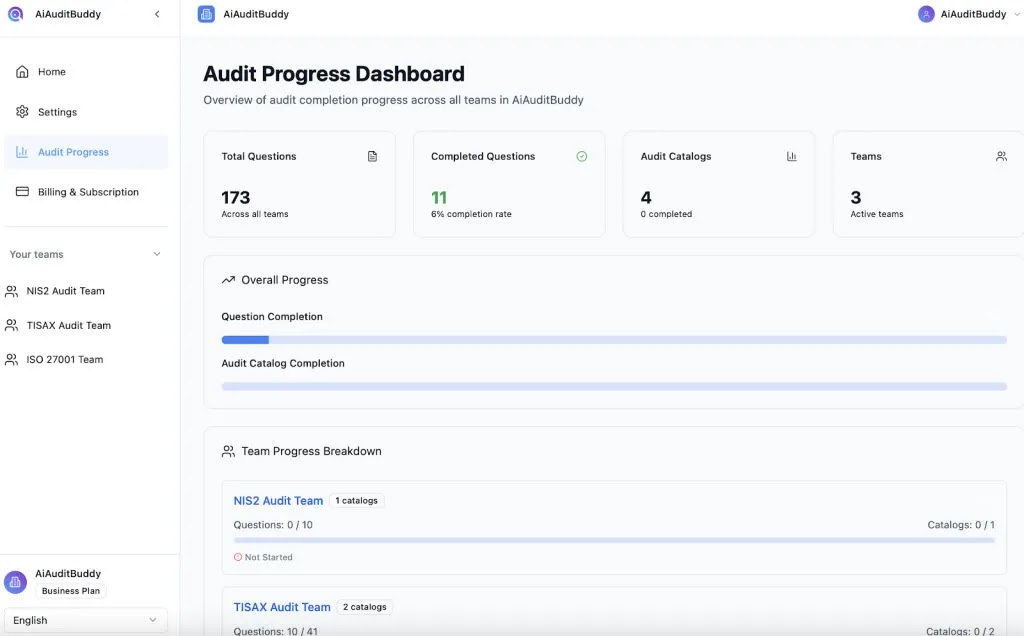
Equipment People (roles and responsibilities) Suppliers and Partners Technology (IT Systems, Communication) Locations, including other offices and backup/work area recovery (WAR) sites Documents and documentation, including which have off-site backup copies: Business documents Procedure documentation Figure 2: AI-Powered Free Security-Audit Checklist 2026 Impact analysis Threat and risks analysis Impact scenarios Quantifying of loss ratios must also include "dollars to defend a lawsuit." It has been estimated that a dollar spent in loss prevention can prevent "seven dollars of disaster-related economic loss." Recovery point objective (RPO) – the acceptable latency of data that will not be recovered. For example, is it acceptable for the company to lose 2 days of data? The recovery point objective must ensure that the maximum tolerable data loss for each activity is not exceeded. Recovery time objective (RTO) – the acceptable amount of time to restore the function Maximum tolerable period of disruption (MTPoD) Maximum tolerable downtime (MTD) Maximum tolerable outage (MTO) Maximum acceptable outage (MAO) According to ISO 22301 the terms maximum acceptable outage and maximum tolerable period of disruption mean the same thing and are defined using exactly the same words. Some standards use the term maximum downtime limit.
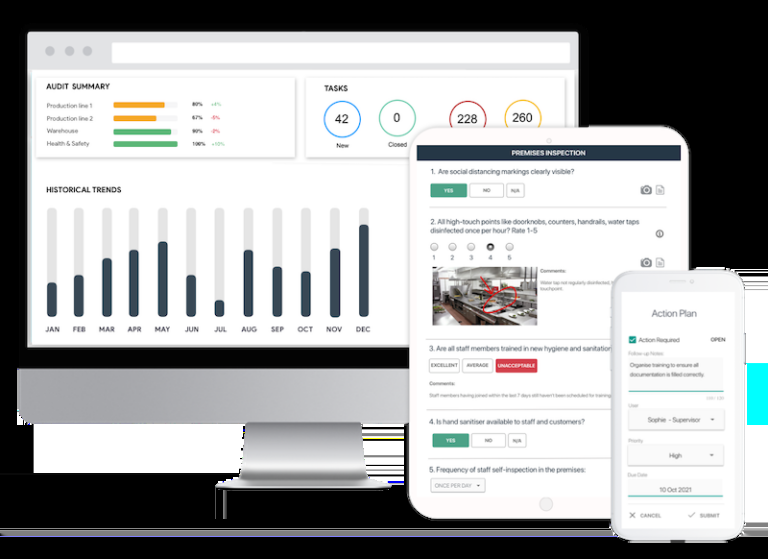
RCO = 1 − ( number of inconsistent entities ) n ( number of entities ) n {\displaystyle {\text{RCO}}=1-{\frac {({\text{number of inconsistent entities}})_{n}}{({\text{number of entities}})_{n}}}} Figure 3: Security Audit Checklist Template The above areas can cascade: Responders can stumble. Supplies may become depleted. During the 2002–2003 SARS outbreak, some organizations compartmentalized and rotated teams to match the incubation period of the disease. They also banned in-person contact during both business and non-business hours. This increased resiliency against the threat.
need for medical supplies need for transportation options civilian impact of nuclear disasters need for business and data processing supplies These should reflect the widest possible damage. Tier 0 – No off-site data • Businesses with a Tier 0 Disaster Recovery solution have no Disaster Recovery Plan. There is no saved information, no documentation, no backup hardware, and no contingency plan. Typical recovery time: The length of recovery time in this instance is unpredictable. In fact, it may not be possible to recover at all. Tier 1 – Data backup with no Hot Site • Businesses that use Tier 1 Disaster Recovery solutions back up their data at an off-site facility. Depending on how often backups are made, they are prepared to accept several days to weeks of data loss, but their backups are secure off-site.
However, this Tier lacks the systems on which to restore data. Pickup Truck Access Method (PTAM). Tier 2 – Data backup with Hot Site • Tier 2 Disaster Recovery solutions make regular backups on tape. This is combined with an off-site facility and infrastructure (known as a hot site) in which to restore systems from those tapes in the event of a disaster. This tier solution will still result in the need to recreate several hours to days worth of data, but it is less unpredictable in recovery time.
Examples include: PTAM with Hot Site available, IBM Tivoli Storage Manager. Tier 3 – Electronic vaulting • Tier 3 solutions utilize components of Tier 2. Additionally, some mission-critical data is electronically vaulted. This electronically vaulted data is typically more current than that which is shipped via PTAM. As a result, there is less data recreation or loss after a disaster occurs. Tier 4 – Point-in-time copies • Tier 4 solutions are used by businesses that require both greater data currency and faster recovery than users of lower tiers. Rather than relying largely on shipping tape, as is common in the lower tiers, Tier 4 solutions begin to incorporate more disk-based solutions. Several hours of data loss is still possible, but it is easier to make such point-in-time (PIT) copies with greater frequency than data that can be replicated through tape-based solutions. Tier 5 – Transaction integrity • Tier 5 solutions are used by businesses with a requirement for consistency of data between production and recovery data centers. There is little to no data loss in such solutions; however, the presence of this functionality is entirely dependent on the application in use. Tier 6 – Zero or little data loss • Tier 6 Disaster Recovery solutions maintain the highest levels of data currency. They are used by businesses with little or no tolerance for data loss and who need to restore data to applications rapidly. These solutions have no dependence on the applications to provide data consistency. Tier 7 – Highly automated, business-integrated solution • Tier 7 solutions include all the major components being used for a Tier 6 solution with the additional integration of automation. This allows a Tier 7 solution to ensure consistency of data above that of which is granted by Tier 6 solutions. Additionally, recovery of the applications is automated, allowing for restoration of systems and applications much faster and more reliably than would be possible through manual Disaster Recovery procedures.
For IT: the minimum application and data requirements and the time in which they must be available. Outside IT: preservation of hard copy (such as contracts). A process plan must consider skilled staff and embedded technology. This phase overlaps with disaster recovery planning. The solution phase determines: Crisis management command structure Telecommunication architecture between primary and secondary work sites Data replication methodology between primary and secondary work sites Backup site with applications, data and work space ISO 22300:2021 Security and resilience – Vocabulary (Replaces ISO 22300:2018 Security and resilience - Vocabulary and ISO 22300:2012 Security and resilience - Vocabulary.) ISO 22301:2019 Security and resilience – Business continuity management systems – Requirements (Replaces ISO 22301:2012.) ISO 22313:2020 Security and resilience – Business continuity management systems – Guidance on the use of ISO 22301 (Replaces ISO 22313:2012 Security and resilience - Business continuity management systems - Guidance on the use of ISO 22301.) ISO/TS 22317:2021 Security and resilience – Business continuity management systems – Guidelines for business impact analysis - (Replaces ISO/TS 22315:2015 Societal security – Business continuity management systems – Guidelines for business impact analysis.) ISO/TS 22318:2021 Security and resilience – Business continuity management systems – Guidelines for supply chain continuity (Replaces ISO/TS 22318:2015 Societal security — Business continuity management systems — Guidelines for supply chain continuity.) ISO/TS 22330:2018 Security and resilience – Business continuity management systems – Guidelines for people aspects on business continuity (Current as of 2022.) ISO/TS 22331:2018 Security and resilience – Business continuity management systems – Guidelines for business continuity strategy - (Current as of 2022.) ISO/TS 22332:2021 Security and resilience – Business continuity management systems – Guidelines for developing business continuity plans and procedures (Current as of 2022.) ISO/IEC/TS 17021-6:2014 Conformity assessment – Requirements for bodies providing audit and certification of management systems – Part 6: Competence requirements for auditing and certification of business continuity management systems.
ISO/IEC 24762:2008 Information technology — Security techniques — Guidelines for information and communications technology disaster recovery services (withdrawn) ISO/IEC 27001:2022 Information security, cybersecurity and privacy protection — Information security management systems — Requirements. (Replaces ISO/IEC 27001:2013 Information technology — Security techniques — Information security management systems — Requirements.) ISO/IEC 27002:2022 Information security, cybersecurity and privacy protection — Information security controls. (Replaces ISO/IEC 27002:2013 Information technology — Security techniques — Code of practice for information security controls.) ISO/IEC 27031:2011 Information technology – Security techniques – Guidelines for information and communication technology readiness for business continuity. ISO/PAS 22399:2007 Societal security - Guideline for incident preparedness and operational continuity management (withdrawn) IWA 5:2006 Emergency Preparedness (withdrawn) BS 7799-1:1995 - peripherally addressed information security procedures. (withdrawn) BS 25999-1:2006 - Business continuity management Part 1: Code of practice (superseded, withdrawn) BS 25999-2:2007 Business Continuity Management Part 2: Specification (superseded, withdrawn) 2008: BS 25777, Information and communications technology continuity management.
Code of practice. (withdrawn) Within the UK, BS 25999-2:2007 and BS 25999-1:2006 were being used for business continuity management across all organizations, industries and sectors. These documents give a practical plan to deal with most eventualities—from extreme weather conditions to terrorism, IT system failure, and staff sickness. In 2004, following crises in the preceding years, the UK government passed the Civil Contingencies Act of 2004: Businesses must have continuity planning measures to survive and continue to thrive whilst working towards keeping the incident as minimal as possible. The Act was separated into two parts: Part 1: civil protection, covering roles & responsibilities for local responders Part 2: emergency powers. In the United Kingdom, resilience is implemented locally by the Local Resilience Forum.
Tabletop exercises - a small number of people concentrate on a specific aspect of a BCP. Another form involves a single representative from each of several teams. Medium exercises - Several departments, teams or disciplines concentrate on multiple BCP aspects; the scope can range from a few teams from one building to multiple teams operating across dispersed locations. Pre-scripted "surprises" are added. Complex exercises - All aspects of a medium exercise remain, but for maximum realism no-notice activation, actual evacuation and actual invocation of a disaster recovery site is added. While start and stop times are pre-agreed, the actual duration might be unknown if events are allowed to run their course.
Confirmation of information in the manual, roll out to staff for awareness and specific training for critical individuals. Testing and verification of technical solutions established for recovery operations. Testing and verification of organization recovery procedures. Issues found during the testing phase often must be reintroduced to the analysis phase. A series of checklists Job descriptions, skillsets needed, training requirements Documentation and document management Definitions of terminology to facilitate timely communication during disaster recovery, Distribution lists (staff, important clients, vendors/suppliers) Information about communication and transportation infrastructure (roads, bridges) Virus definition distribution Application security and service patch distribution Hardware operability Application operability Data verification Data application The tiers of Disaster Recovery and TSM. Charlotte Brooks, Matthew Bedernjak, Igor Juran, and John Merryman. In, Disaster Recovery Strategies with Tivoli Storage Management. Chapter 2. Pages 21–36. Red Books Series. IBM. Tivoli Software.
2002. SteelStore Cloud Storage Gateway: Disaster Recovery Best Practices Guide. Riverbed Technology, Inc. October 2011. Disaster Recovery Levels. Robert Kern and Victor Peltz. IBM Systems Magazine. November 2003. Business Continuity: The 5-tiers of Disaster Recovery. Archived 2018-09-26 at the Wayback Machine Recovery Specialties. 2007. Continuous Operations: The Seven Tiers of Disaster Recovery. Mary Hall. The Storage Community (IBM). 18 July 2011. Retrieved 26 March 2013. Maximum Tolerable Period of Disruption (MTPOD) Maximum Tolerable Period of Disruption (MTPOD): BSI committee response Wayback Machine Janco Associates Business Continuity Plan Department of Homeland Security Emergency Plan Guidelines CIDRAP/SHRM Pandemic HR Guide Toolkit Archived 2013-05-18 at the Wayback Machine Adapt and respond to risks with a business continuity plan (BCP) Learn what a software security audit entails, its significance, key objectives, types of audits, the report structure, and best practices. Gain insights into the complete auditing process.
With the enhancement of digital systems, software security audit plays a significant role in preventing the leakage of information and avoiding hefty fines. In mid-2024, around 22,254 CVEs were noted, which is 30% higher than that of 2023. It is thus important to scan software for vulnerabilities or misconfigurations that can be exploited to facilitate such a surge. In this guide, we will discuss what auditing is, why it is important, and how to audit software for security issues in a systematic manner.
We will start with the meaning of software security audits and demonstrate the dangers that a defective system can present. Then, we will briefly discuss the goals of the audit, the types of audits, and the weaknesses that may be identified during an audit. We will also be explaining how to write the software security audit report, the general steps, and the use of cyber security audit software as well as network security audit software.
Last but not least, the article will include an analysis of the best practices and the issues that may arise in this process, as well as the steps that can be taken to establish a positive audit culture. Software security audit can be described as a systematic analysis of software applications, libraries, and related infrastructure in order to identify security weaknesses and compliance with set norms. In fact, 83% of the applications that are scanned for the first time are likely to have one or more security vulnerabilities. The audit can focus on the source code, observe the behavior of the code during runtime, and verify compliance with best practices. Sometimes, the audit goes even further and focuses on such aspects as deployment pipelines and security settings.
Using an audit, organizations can detect misconfigurations, unpatched vulnerabilities, and even potentially malicious code. This final step guarantees that the final product meets the user requirements for safety and complies with regulations, hence strengthening the security of the organization. Since the early-stage Software Composition Analysis (SCA) is now being performed in 37% more organizations to counter open-source component risks, auditing from the first day is crucial. However, apart from searching for weaknesses, a software security audit strengthens the credibility of the stakeholders, demonstrates adherence to the law, and saves on data leakage expenses.
In the following section, we explain why auditing is so crucial to contemporary software development cycles: Security assessment does not only identify coding vulnerabilities. It is intended to ensure that each aspect of the application: user identification, database connectivity, and customization – complies with the best standards of security. There are five primary objectives of software security audit engagement, which guarantee a strong defense line as follows: Not all security audits are the same – some are focused on certain aspects, while others are general security audits. An appreciation of these different types helps to avoid a mismatch between the organization’s needs and the extent of the assessment.
In the following sections, we describe different methods in the software security audit frameworks: When conducted comprehensively, a software security audit reveals a range of risks. These could be as basic as individual errors to even structural issues. This section examines five common security weaknesses that audits usually uncover, which illustrates why the checks are necessary.
While a detailed report of the software security audit presents the results of the audit to the concerned parties, it provides technical information as well as practical recommendations. This document not only lists issues but also describes fixes for them and provides compliance information. Carrying out a systematic software security audit requires following a certain set of steps. Each stage is different depending on the scope and environment, but every step guarantees that no weaknesses are missed.
The following is a five-step audit plan, which describes the general process of an auditing mission, starting from the planning phase and ending with the closeout phase: Manual inspection of large code or logs may be very time-consuming and often may result in missing some of the information. Specifically, cyber security audit software performs the act of scanning, logging as well as generating consistent results.
Now, let us look at the way such specialized solutions enhance the whole process of audit, including efficiency and reliability. 2. System Architecture & Core Working Principles Still, software auditing has not always been a perfectly smooth process, even though its benefits are evident. Some of the challenges that are faced by the teams include limited staff expertise, false positives, and many others.
Here are five significant obstacles to timely and accurate software security audit results below: While every environment is different, there are certain best practices that will guarantee a repeatable and successful audit at every turn. Through integration, transparency, and constant learning, the teams develop a strong culture of code safety. Here are five tested strategies that can help in creating a good software security audit cycle: Elevate your security posture with real-time detection, machine-speed response, and total visibility of your entire digital environment.
A software security audit combines code review, penetration testing, and configuration testing to expose vulnerabilities that are not easily discernible. With more software using third-party components, microservices, and temporary cloud resources, this approach of simply scanning software is not possible. On the contrary, regular audits build credibility, address legal requirements, and minimize the risk of spectacular violations. Even though there are issues with false positives, lack of expertise, etc., tried and true strategies and powerful scanning tools guarantee efficient audits. Having a checklist of the software security audit and proper cross-team collaboration, each phase of SDLC can maintain a high level of security.
Given the increased number of vulnerabilities every year, it is more advisable to integrate security audits into regular processes. Supporting these standards and employing effective scanning or network security audit software promotes a layered security approach. By optimizing the audit cycles, checking the fixes, and identifying the lessons to be learned, organizations can always improve their security status.
Software security audit can be described as a systematic assessment of an application and its code and the runtime environment for possible vulnerabilities or non-conformity. It may include vulnerability scanning, code reviewing, and penetration testing. In this way, an audit checks that the most important functions of each layer of the software correspond to the determined security requirements. They allow addressing the issues and identifying risks that should be prioritized and avoided in future development.
Typically, a software security audit checklist may include aspects such as checking whether the input validation is in place, the encryption settings, and the least privileged access. It also includes issues related to patches, sessions, and third-party libraries. Auditors often cover such elements as firewalls or SSL certificates in their work. This way, each audit is equally comprehensive, and all the crucial steps are accounted for in the checklist.
Software security audit certifications like ISO 27001, SOC 2, or PCI DSS are often sought by many organizations to ensure that their organization adheres to the set industry standard. Another indication of competence in securing hosted services is specific vendor or product certifications such as those for cloud platforms. Some auditors possess CISSP as their certification in information systems security. Altogether, these accomplishments provide assurance that the auditing team is in conformity with the set standards.
An ordinary software security audit report begins with an executive summary that features key findings and risk assessment. It then expands on each of the mentioned risks to describe the level of risk, supporting evidence, and measures to mitigate them. Details of the scope, method, and tools applied are given in the subsequent sections of the report to show how the results were derived. Last but not least, logs, code snippets, or other related information can be added to the appendixes for additional context and for research purposes.
The frequency can be determined by regulatory requirements, changes in code, or new threats that are identified. Some businesses carry out regular checks with automated solutions and have periodic manual checks at least once a year. As a rule, after significant changes in the architecture or new releases of large features, it is useful to check with network security audit software or code scanners. It is common to have regular software security audit engagements because the threats in cyberspace evolve rapidly.
A hands-on repository for cybersecurity audit checklists, automation scripts, and tooling guidance across cloud, web apps, open-source packages, and PCI DSS compliance. Designed for auditors, solution architects, and freelance consultants. This repository contains checklists, tools, templates, and automation scripts for conducting cybersecurity audits across cloud-native systems, APIs, web applications, open-source components, and compliance domains like PCI DSS and ISO 27001.
I Designed to assist consultants, internal security teams, and freelance auditors in rapidly evaluating and strengthening security postures. A hands-on repository for cybersecurity audit checklists, automation scripts, and tooling guidance across cloud, web apps, open-source packages, and PCI DSS compliance. Designed for auditors, solution architects, and freelance consultants.
In today’s digital world, cyber threats are increasing every day. Whether you’re building an ASP.NET Core application, Flutter app, Node.js backend, Java application, or enterprise ERP software, security should never be an afterthought . A Security Audit is a systematic examination of your application’s code, infrastructure, APIs, databases, authentication mechanisms, and deployment environment to identify vulnerabilities before attackers do.
A well-maintained project not only performs better but also gains user trust, complies with security standards, and ranks higher in enterprise procurement processes. A software security audit helps development teams identify vulnerabilities in application code, APIs, databases, authentication, dependencies, and infrastructure before they become serious security incidents. This guide explains a practical security audit of software projects with real examples, checklists, tools, and secure development practices.
A software security audit is a structured review of an application’s code, configuration, dependencies, APIs, data protection, authentication, authorization, and deployment environment. The goal is to identify security weaknesses, assess their risk, and define practical remediation steps. At least once every quarter, after major releases, and whenever significant infrastructure or application changes are introduced.
No. A security audit reviews policies, configurations, code, and infrastructure, while penetration testing actively attempts to exploit vulnerabilities to demonstrate real-world risk. The most critical issues generally include SQL Injection, Broken Authentication, Broken Access Control, Remote Code Execution (RCE), Server-Side Request Forgery (SSRF), and Sensitive Data Exposure.
Yes. Small businesses are frequently targeted because they often have fewer security controls. Regular audits help reduce risk and improve customer confidence. A security audit is one of the most valuable investments for any software project. By regularly reviewing authentication, authorization, APIs, databases, infrastructure, dependencies, and coding practices, organizations can identify vulnerabilities before attackers do.
Well-maintained projects not only improve security but also enhance performance, reliability, customer trust, and long-term maintainability. Integrating security into every stage of the Software Development Life Cycle (SDLC) ensures that applications remain resilient against evolving cyber threats. Include these as outbound links in your blog to improve credibility (use rel="noopener noreferrer" and target="_blank" where appropriate): Enterprise security teams face mounting pressure to demonstrate continuous compliance while managing increasingly complex IT environments. Traditional manual audit approaches consume valuable resources, create documentation bottlenecks, and often miss critical vulnerabilities until it’s too late. This comprehensive security audit checklist guide addresses these challenges by providing structured frameworks, automated solutions, and actionable implementation strategies that transform compliance from a reactive burden into a strategic enabler of business growth.
A security audit is a comprehensive, systematic evaluation of an organization’s information systems, security policies, and procedures to assess their effectiveness against established security standards and regulatory requirements. Unlike basic vulnerability scans, security audits examine both technical controls and operational processes, providing a holistic view of an organization’s security posture.
Modern security audits evaluate multiple layers of protection, from network infrastructure and access controls to data governance and incident response capabilities. They assess whether security measures are not only implemented but also functioning effectively to protect against current threat landscapes. Security audits can be conducted internally by the organization’s security team or externally by independent third-party auditors, depending on regulatory requirements and organizational needs.
The NIST Cybersecurity Framework provides foundational guidance for conducting comprehensive security audits, emphasizing the importance of continuous assessment and improvement. This framework helps organizations structure their audit processes around five core functions: Identify, Protect, Detect, Respond, and Recover. Security audits differ from compliance audits in scope and purpose, though they often overlap. While compliance audits focus on meeting specific regulatory requirements, security audits take a broader risk-based approach to evaluating organizational security effectiveness across all business operations.
Security audits serve as critical checkpoints that validate whether implemented security measures actually protect against real-world threats. In today’s rapidly evolving threat landscape, organizations cannot rely solely on initial security implementations without ongoing validation and improvement. Regulatory Compliance Requirements : Most industries face mandatory security audit requirements through regulations like SOC 2, ISO/IEC 27001 , HIPAA, or PCI DSS. These regulations require regular security assessments to maintain certification and avoid significant financial penalties.
Risk Management and Threat Detection : Security audits identify vulnerabilities and weaknesses before they can be exploited by malicious actors. This proactive approach enables organizations to address security gaps during controlled maintenance windows rather than during emergency incident response scenarios. Business Continuity Protection : Effective security audits evaluate business continuity and disaster recovery capabilities, ensuring organizations can maintain operations during security incidents or system failures. This assessment becomes increasingly critical as businesses rely more heavily on digital operations.
Stakeholder Confidence and Trust : Regular security audits demonstrate organizational commitment to protecting customer data and business assets. This transparency builds trust with customers, partners, and investors who increasingly prioritize security in their business relationships. Modern Best Security Audit Software to Ensure Compliance & Mitigate Risk platforms automate many audit processes, reducing the time and resources required while improving accuracy and consistency of results.
A security audit checklist is a structured document that outlines specific items, controls, and procedures that auditors must evaluate during a security assessment. It serves as a roadmap ensuring comprehensive coverage of all security domains and provides consistent evaluation criteria across different audit cycles. Effective security audit checklists transform complex security frameworks into actionable evaluation points that audit teams can systematically review and validate. They bridge the gap between high-level security policies and detailed implementation requirements, making audit processes more efficient and thorough.
Standardization and Consistency : Security audit checklists ensure that all auditors evaluate the same controls using consistent criteria, reducing variability in audit results and improving the reliability of security assessments across different time periods and audit teams. Comprehensive Coverage : Well-designed checklists ensure that auditors address all aspects of organizational security, from technical infrastructure to administrative procedures. This comprehensive approach prevents security gaps that might be overlooked in less structured audit approaches.
3. Software Implementation, Frameworks & Protocols Documentation and Evidence Management : Security audit checklists provide templates for documenting findings, collecting evidence, and tracking remediation efforts. This structured documentation supports compliance reporting and provides historical records for trend analysis and continuous improvement initiatives.
Integration with Automated Tools : Modern security audit checklists integrate with automated assessment tools and platforms, enabling continuous monitoring and real-time compliance reporting. Transilience AI’s autonomous compliance platform exemplifies this integration, providing automated evidence collection and gap identification across multiple compliance frameworks.
A comprehensive cyber security audit checklist must address multiple security domains to provide thorough protection assessment. Based on leading frameworks and industry best practices, enterprise security audit checklists should include the following core categories: Technical infrastructure security forms the foundation of any effective security audit checklist. This category evaluates the configuration and management of technology components that support organizational operations.
Asset Inventory and Discovery represents the starting point for effective security audits. Organizations must maintain comprehensive inventories of all IT assets, including servers, workstations, network devices, cloud services, and applications. This foundational requirement enables security teams to understand their attack surface and ensure all systems receive appropriate security attention. Asset discovery tools should automatically identify and catalog systems, providing real-time visibility into infrastructure changes.
Network Security Assessment evaluates network architecture, segmentation, firewall configurations, and monitoring capabilities. Effective network security requires proper segmentation to limit breach impact, correctly configured firewall rules that are regularly reviewed, and comprehensive monitoring of network traffic for suspicious activities. The CIS Controls provide detailed guidance for implementing robust network security controls.
Vulnerability Management encompasses regular vulnerability scanning, penetration testing, and timely patch management processes. Organizations must implement systematic approaches to identifying security weaknesses, prioritizing remediation efforts based on risk, and tracking resolution progress. Transilience AI’s vulnerability prioritization capabilities use intelligent scoring algorithms to help security teams focus on threats that pose actual risk to organizational operations.
Endpoint Protection and Management addresses the security of user devices, including deployment of antivirus software, endpoint detection and response tools, device encryption, and mobile device management solutions. Modern endpoint security requires unified visibility across all device types and automated response capabilities for detected threats. Access control and identity management security ensures that only authorized individuals can access organizational systems and data at appropriate privilege levels.
User Account Management evaluates processes for creating, modifying, and deleting user accounts throughout the user lifecycle. This includes proper approval workflows for account changes, regular account reviews to identify inactive or inappropriate accounts, and automated provisioning and deprovisioning processes that reduce administrative overhead while maintaining security.
Authentication Mechanisms assess password policies, multi-factor authentication implementations, and single sign-on solutions. Strong authentication requires enforcing complex password requirements, implementing multi-factor authentication for privileged accounts and remote access, and integrating authentication systems with centralized identity management platforms.
Authorization and Privilege Management examines role-based access control implementations, least privilege enforcement, and segregation of duties. Effective authorization ensures users receive only the minimum access necessary for their job functions while preventing conflicts of interest through appropriate separation of responsibilities. Access Monitoring and Auditing focuses on logging and reviewing user access activities to detect suspicious behavior.
Comprehensive access monitoring generates audit logs for all system access attempts, implements automated alerting for unusual access patterns, and provides regular access reviews to identify potential security violations. Data protection and privacy controls address the identification, classification, and protection of sensitive information throughout its lifecycle.
Data Discovery and Classification involves systematically identifying and categorizing data assets based on sensitivity and regulatory requirements. Organizations must understand what types of data they possess, where it resides, and what protection requirements apply to different data categories. Encryption Implementation ensures protection of data at rest, in transit, and in use through proper cryptographic controls. This includes implementing appropriate encryption algorithms, managing encryption keys securely, and ensuring consistent encryption application across all systems containing sensitive data.
Data Access Control restricts access to sensitive data based on business need and monitors for unauthorized data exfiltration. Data loss prevention systems, access monitoring, and data sharing agreements help organizations maintain control over sensitive information. Privacy Compliance addresses implementation of privacy notices, consent management, and data subject request handling to meet GDPR, CCPA, and other privacy regulations. Organizations must demonstrate compliance through documented processes and regular privacy impact assessments.
Incident response and business continuity preparations ensure organizations can effectively handle security incidents and maintain operations during disruptions. Incident Response Planning involves developing and maintaining comprehensive response plans covering detection, containment, eradication, recovery, and post-incident review processes. Effective incident response requires clear role definitions, communication procedures, and coordination mechanisms with external partners.
Business Continuity and Disaster Recovery planning ensures organizational resilience through backup systems, recovery procedures, and regular testing of continuity capabilities. Organizations must define recovery objectives and implement systems that meet these requirements during various disruption scenarios. Security audits consistently reveal several categories of gaps that organizations struggle to address effectively. Understanding these common weaknesses helps security teams prioritize improvement efforts and allocate resources more effectively.
AI Security Governance represents an emerging gap as organizations increasingly deploy artificial intelligence systems without formal governance frameworks. Many organizations lack processes for assessing AI system risks, monitoring AI-driven decisions, and ensuring AI applications comply with regulatory requirements. Transilience AI addresses this gap through specialized governance capabilities that provide automated risk assessment and monitoring for AI implementations.
Supply Chain Risk Management continues to challenge organizations as third-party relationships create cascading risk exposures. Traditional security audits often focus primarily on internal controls while giving insufficient attention to vendor security postures and supply chain vulnerabilities. Effective supply chain risk management requires regular third-party assessments, continuous monitoring of supplier security status, and contractual requirements for security standards.
Continuous Monitoring Capabilities remain underdeveloped in many organizations that still rely primarily on point-in-time assessments rather than ongoing security validation. Modern threat landscapes require real-time threat detection and response capabilities that traditional periodic audits cannot provide. Comprehensive Cyber Risk Management approaches integrate continuous monitoring with traditional audit processes to provide comprehensive security oversight.
Configuration Management and Drift Detection represent significant challenges in dynamic cloud environments where system configurations change frequently. Many organizations lack automated tools to detect configuration changes that might introduce security vulnerabilities or compliance violations. Privileged Access Management gaps frequently appear in audit findings, particularly around the management of administrative accounts, service accounts, and emergency access procedures. Organizations often struggle to implement least privilege principles consistently across all systems and applications.
Different types of security audits require specialized checklists tailored to specific technology domains and risk profiles. Understanding these variations helps organizations select appropriate audit approaches for their environments. IT security audit checklists provide comprehensive coverage of general information technology security controls across enterprise environments. These checklists address traditional security domains including network security, system hardening, access controls, and data protection without focusing on specific compliance frameworks.
Key components include infrastructure security assessments, application security evaluations, database security reviews, and operational security procedures. IT security audits typically examine security architectures, technical implementations, and security management processes to identify vulnerabilities and improvement opportunities. Website security audit checklists focus specifically on web application security, addressing vulnerabilities and threats unique to internet-facing applications and services. These specialized checklists evaluate web application firewalls, content management system security, SSL/TLS implementations, and input validation controls.
Website security audits examine authentication mechanisms, session management, data validation, and protection against common web application vulnerabilities identified in the OWASP Top 10. They also assess website infrastructure security, including web server configurations, database security, and third-party integration security. Network security audit checklists concentrate on network infrastructure components, protocols, and security controls. These assessments evaluate firewall configurations, network segmentation, intrusion detection systems, and network monitoring capabilities.
Network security audits examine router and switch configurations, wireless network security, VPN implementations, and network access control systems. They also assess network topology design, traffic analysis capabilities, and incident response procedures specific to network security events. Cloud security audit checklists address the unique security requirements of cloud computing environments, including public, private, and hybrid cloud deployments. These checklists evaluate shared responsibility models, cloud service provider security controls, and customer-implemented security measures.
Cloud security audits examine identity and access management in cloud environments, data encryption and protection, cloud configuration management, and monitoring capabilities. They also assess cloud governance processes, vendor management, and data sovereignty considerations. Industry-specific security audit checklists incorporate regulatory requirements and industry best practices relevant to particular sectors. Healthcare organizations require PCI DSS Compliance Calendar – Activities and Checklist assessments, while financial services organizations focus on regulatory requirements specific to their industry.
These specialized checklists address sector-specific threats, compliance requirements, and operational considerations that general security audits might not adequately cover. Implementing an effective security audit process requires systematic execution of key steps that ensure comprehensive coverage and reliable results. These steps provide a framework for conducting thorough security assessments regardless of organizational size or industry.
Step 1: Define Audit Scope and Objectives – Establish clear boundaries for the audit, identifying systems, processes, and compliance requirements to be assessed. Document specific audit objectives and success criteria to guide the assessment process. Step 2: Gather Preliminary Information – Collect existing documentation including security policies, network diagrams, system inventories, and previous audit reports. This preparation enables more efficient audit execution and helps identify potential focus areas.
Step 3: Conduct Risk Assessment – Evaluate current threat landscape and organizational risk factors to prioritize audit activities. Focus audit attention on areas with highest risk exposure and business impact potential. Step 4: Review Security Policies and Procedures – Examine documented security policies, standards, and procedures to ensure they address current requirements and provide adequate guidance for implementation.
4. Practical Deployment, Analysis & Case Studies Step 5: Assess Technical Controls – Evaluate implementation and effectiveness of technical security controls including access controls, encryption, network security, and endpoint protection measures. Step 6: Test Security Controls – Perform hands-on testing of security controls to validate their effectiveness under realistic conditions. This includes vulnerability scanning, penetration testing, and configuration reviews.
Step 7: Evaluate Compliance Status – Compare current implementation against applicable compliance requirements and industry standards to identify gaps and areas for improvement. Step 8: Document Findings and Evidence – Record all audit findings with supporting evidence, including screenshots, log excerpts, and configuration details that substantiate identified issues.
Step 9: Develop Remediation Recommendations – Provide specific, actionable recommendations for addressing identified vulnerabilities and compliance gaps, including implementation guidance and timelines. Step 10: Create Audit Report and Present Results – Compile comprehensive audit results into executive and technical reports that communicate findings effectively to different stakeholder audiences.
Performing effective security audits requires structured methodologies that ensure comprehensive coverage while managing resource constraints and operational impacts. Modern security audit approaches leverage automation and risk-based assessment techniques to maximize efficiency and effectiveness. Transilience AI’s automated evidence collection capabilities streamline the audit process by continuously gathering compliance evidence and identifying gaps in real-time, reducing manual effort while improving audit accuracy and timeliness.
The frequency of security audits depends on multiple factors including regulatory requirements, organizational risk tolerance, system complexity, and business criticality. Most organizations benefit from implementing layered audit approaches that combine different assessment frequencies and methodologies. Modern approaches increasingly favor continuous monitoring supplemented by periodic comprehensive assessments rather than relying solely on annual audit cycles. This approach provides better security visibility while reducing the resource burden of large-scale audit projects.
Successful security audits require careful planning, skilled execution, and effective communication to deliver valuable results that drive meaningful security improvements. Organizations can improve audit outcomes by implementing proven best practices and leveraging advanced assessment techniques. Security audit checklists provide valuable frameworks for systematic security assessment, but they cannot guarantee complete protection against all possible threats. Understanding the capabilities and limitations of audit checklists helps organizations develop realistic expectations and implement comprehensive security strategies.
Checklist Benefits and Capabilities include providing structured assessment methodologies, ensuring comprehensive coverage of security domains, establishing consistent evaluation criteria, and facilitating compliance reporting. Well-designed checklists help organizations identify and address many common security vulnerabilities and compliance gaps. Cybersecurity Compliance: What It Is & Why It Matters emphasizes the importance of combining audit checklists with broader security strategies that address both current and emerging threats.
Practical examples of security audit implementations help organizations understand how to apply audit checklists effectively in different scenarios and environments. These examples demonstrate both successful implementations and common challenges that organizations encounter. These examples demonstrate the importance of tailoring audit approaches to specific organizational contexts, regulatory requirements, and risk profiles rather than applying generic audit checklists universally.
In today’s rapidly evolving cybersecurity landscape, traditional manual audit processes fall short of meeting the dynamic compliance needs of modern enterprises. Network Intelligence, leveraging breakthrough innovations from Transilience AI, transforms how organizations approach security audit checklists and compliance management through autonomous, AI-powered solutions.
Network Intelligence’s comprehensive Audit Services | Digital Security approach combines over two decades of cybersecurity expertise with cutting-edge AI capabilities to deliver unprecedented automation and accuracy in security assessments. The integration with Transilience AI represents a paradigm shift from reactive compliance checking to proactive, continuous security validation that adapts in real-time to changing threat landscapes and regulatory requirements.
Network Intelligence’s proven track record of successful implementations across banking, technology, energy, and aviation industries demonstrates the real-world effectiveness of AI-enhanced security audit approaches. Organizations working with Network Intelligence and Transilience AI typically see 70% cost reductions, 2+ month timeline accelerations, and 100% resource reallocation from compliance firefighting to strategic business initiatives.
Ready to transform your organization’s security audit process from a reactive burden into a strategic enabler? Talk to an Expert to discover how Network Intelligence and Transilience AI can deliver guaranteed compliance outcomes tailored to your specific industry requirements and business objectives. Get a personalized assessment of your operational efficiency and accelerate growth for your business.
I often think of software systems as living, breathing organisms. They're intricate, ever-changing, and without regular upkeep, they can easily become bloated and outdated. As your organization grows, the software becomes increasingly complex, with multiple integrations, updates, security patches, and other enhancements.
Ultimately, performance starts to slip, and you find yourself wondering, ‘Why doesn’t this software work like it used to?’ A thorough software audit can help you avoid compliance issues , spot security vulnerabilities, and optimize performance. It can also help you identify the areas where modernization will have the greatest impact. But when’s the right time for an audit? How do you actually go about it? And who should lead the process? In this guide, we’ll walk you through everything you need to know about software audits.
A software audit is a detailed review of your organization’s software products, processes, code, and infrastructure. It helps ensure everything meets compliance standards & regulations, stays secure, runs efficiently, and performs at its best. The scope of a software audit can vary. It might focus on license compliance or go deeper into code quality and technical debt.
A license compliance audit helps prevent legal issues by ensuring your organization’s software usage aligns with vendor licensing agreements and legal requirements. These audits can uncover discrepancies such as unauthorized installations, expired licenses, or exceeding license limits. This proactive approach helps you avoid penalties, contract disputes, and potential litigation.
For example , if your team installs a design tool on more computers than you’re licensed for, a compliance audit will flag it before it leads to costly fines. A security audit identifies vulnerabilities, assesses the effectiveness of data protection, and verifies whether your organization is adhering to relevant security standards.
The goal is to protect your systems from potential threats, reduce risk exposure, and build long-term security resilience. These audits also help prevent the financial and reputational damage associated with breaches. For example , a security audit might reveal that your customer database still uses outdated encryption protocols. This would prompt a timely update before any data is compromised.
A quality audit evaluates your development processes, code, and documentation to ensure your software meets high standards and performs reliably. Conducting these audits regularly encourages a culture of continuous improvement. They result in software that is more stable, secure, and scalable as your organization grows and technology advances.
Usability audits focus on the intuitiveness and ease of use of your software. Accessibility audits ensure the product can be used by everyone, including individuals with disabilities. These audits often uncover issues such as confusing onboarding flows, poor UI or UX design, or barriers that make it difficult for some users to navigate the product.
For example , an accessibility audit might reveal that your app’s color scheme makes text difficult to read for users with visual impairments. Whether manual, automated, or a mix of both, code reviews carefully analyze your source code for bugs, security flaws, and adherence to industry best practices.
This process helps you catch issues early, improve code quality, and make your software easier to maintain and scale. 5. Performance Evaluation & Extended Technical Observations For example , a code audit might reveal that a function is vulnerable to SQL injection, allowing you to address the issue before it reaches production.
It focuses on identifying unresolved issues, inefficient code, or outdated components that could hinder future development or compromise system performance. By addressing technical debt, you maintain your software's agility and reduce the risk of costly rework in the future. For instance , you might discover old modules that are difficult to update, prompting you to refactor them for smoother future releases.
Once you understand what kind of audit your organization needs, the next question is: who should perform it? Software audits can be done by the company’s internal group of software experts, or you can have an external partner do it for you. Internal audits are ideal for routine checks, early risk detection, and ongoing improvements.
External audits are essential for regulatory compliance, independent validation, and when an objective perspective is required. 62% of organizations reported being audited by a major software vendor in the past year (2024), up from 40% in 2023. ( Source ) Your team may be skilled, but there are situations where external expertise can make a significant difference.
Your team may be familiar with the product but may not have in-depth knowledge in areas such as compliance standards, emerging technologies, or secure coding practices. External auditors bring that niche expertise. If your internal team is stretched thin, an in-depth audit can feel impossible without affecting daily operations. External auditors help you avoid burnout and keep projects on track.
Familiarity can create blind spots. An external expert offers a new set of eyes, helping identify issues your team may have missed due to routine exposure. When investors, board members, or partners want objective proof of software quality or compliance, an independent audit builds trust and transparency.
If the same issues keep resurfacing, even after internal audits, it’s a sign that deeper problems exist. External specialists can delve in, identify root causes, and provide lasting solutions. When capacity and credibility are in question, external audit services can fill the gap and deliver meaningful, lasting value. As an operational leader, your priorities include reducing costs, managing risk, staying compliant, improving productivity, and ensuring your technology investments deliver strong returns.
You might not realize it, but different regional branches could be using different communication tools. Centralizing on a single platform reduces costs and streamlines vendor management. Without an audit, these unnecessary expenses continue unnoticed and drain your budget. For instance, you may find operations using outdated time-tracking software that doesn't meet labor compliance standards.
Consolidating overlapping tools reduces costs and streamlines workflows, improving software ROI. An audit might reveal inefficient approval steps (with too many manual handoffs) that can be redesigned for speed. Software audits don’t just fix issues. They prepare your systems for growth and transformation, directly benefiting operational leaders.
They take a close look at your software’s architecture, code, and workflows to uncover bottlenecks and waste. These are the hidden blockers that limit your ability to scale. You might uncover slow algorithms or inefficient queries that quietly raise your infrastructure costs. Over time, these issues drag down performance and drain your budget.
Audits also help improve the communication between your systems. Maybe your ERP and CRM aren’t syncing customer data. That causes errors, delays, and missed opportunities. Integration reviews identify broken APIs and unreliable data flows before they escalate into larger issues. Code reviews matter just as much. Auditors look for outdated libraries, legacy modules, and messy code that’s hard to manage. This is what we refer to as technical debt. If left unchecked, it continues to grow and consumes your time, budget, and team’s energy.
Refactoring the legacy code now helps speed up future releases. It makes your system easier to update, easier to scale, and ready for what’s next. By addressing these issues, integration gaps, technical debt, and messy code, you prepare your systems for growth, innovation, and what’s next.
This could mean eliminating 100% of technical debt, enhancing security, or achieving full license compliance. Document everything to keep your team and audit partners aligned. This step helps identify redundant or underutilized tools and provides a clear view of your technology landscape before diving deeper.
For example , you may find different teams using separate tools for the same task, opening up opportunities for consolidation. Now that your software inventory is in place, validate whether you're using it legally and within scope. Manually review critical applications to find risks that automated tools may miss, such as hardcoded credentials or weak configurations.
Utilize automated tools, such as static code analyzers, to identify bugs, code smells, deprecated functions, and risky dependencies. Assess technical debt, legacy modules, hard-to-maintain code, or shortcuts that now hinder progress. Analyze how your software performs from the user’s perspective. Is the interface intuitive and easy to navigate? For example, software with a dashboard that lags during peak hours may need optimization to maintain productivity.
Create a comprehensive audit report that outlines key issues, risks, opportunities, and recommended improvements. Use visuals and summaries to make it easier for stakeholders to understand the information. Work with stakeholders to prioritize fixes and create a roadmap for remediation. Set up regular reviews to track progress and adjust as needed.
Here’s a comprehensive software audit checklist to help ensure your software environment is secure, compliant, efficient, and ready to scale. Each section focuses on a key audit area and provides actionable items you can implement with clarity. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/ISO/IEC%2027001 • https://en.wikipedia.org/wiki/Software%20review • https://en.wikipedia.org/wiki/Business%20continuity%20planning • https://www.sentinelone.com/cybersecurity-101/cybersecurity/software-security-audit/ • https://github.com/Suumitjoshi/cybersecurity-audit • https://blog.vigplanet.com/security-audit-software-project-guide/ • https://www.networkintelligence.ai/blogs/security-audit-checklist/ • https://imaginovation.net/blog/software-audit-guide/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Security Audit Checklist Automation.
[*] Metasploit Scan Running on Target Subnet for Security Audit Checklist Automation... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |