Complete Technical Paper Content — Security Information And Event Management Tool Using Wazuh
Overview & System Context
Security Information And Event Management Tool Using Wazuh: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9514 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Security information and event management (SIEM) is a field within computer security that combines security information management (SIM) and security event management (SEM) to enable real-time analysis of security alerts generated by applications and network hardware. SIEM systems are central to security operations centers (SOCs), where they are employed to detect, investigate, and respond to security incidents. SIEM technology collects and aggregates data from various systems, allowing organizations to meet compliance requirements while safeguarding against threats. NIST's definition for a SIEM tool is an application that provides the ability to gather security data from information system components and present that data as actionable information via a single interface. SIEM tools can be implemented as software, hardware, or managed services. SIEM systems log security events and generate reports to meet regulatory frameworks such as the Health Insurance Portability and Accountability Act (HIPAA) and the Payment Card Industry Data Security Standard (PCI DSS). The integration of SIM and SEM within SIEM provides organizations with a centralized approach for monitoring security events and responding to threats in real-time. First introduced by Gartner analysts Mark Nicolett and Amrit Williams in 2005, the term SIEM has evolved to incorporate advanced features such as threat intelligence and behavioral analytics, which allow SIEM solutions to manage complex cybersecurity threats, including zero-day vulnerabilities and polymorphic malware. In recent years, SIEM has become increasingly incorporated into national cybersecurity initiatives. For instance, Executive Order 14028 signed in 2021 by U.S. President Joseph Biden mandates the use of SIEM technologies to improve incident detection and reporting in federal systems. Compliance with these mandates is further reinforced by frameworks such as NIST SP 800-92, which outlines best practices for managing computer security logs. Modern SIEM platforms are aggregating and normalizing data not only from various Information Technology (IT) sources, but from production and manufacturing Operational Technology (OT) environments as well.
Log management: Focus on simple collection and storage of log messages and audit trails. Security information management (SIM): Long-term storage as well as analysis and reporting of log data. Security event manager (SEM): Real-time monitoring, correlation of events, notifications and console views. Security information and event management (SIEM): Combines SIM and SEM and provides real-time analysis of security alerts generated by network hardware and applications. Managed Security Service: (MSS) or Managed Security Service Provider: (MSSP): The most common managed services appear to evolve around connectivity and bandwidth, network monitoring, security, virtualization, and disaster recovery. Security as a service (SECaaS): These security services often include authentication, anti-virus, anti-malware/spyware, intrusion detection, penetration testing and security event management, among others. In practice many products in this area will have a mix of these functions, so there will often be some overlap – and many commercial vendors also promote their own terminology.
Oftentimes commercial vendors provide different combinations of these functionalities which tend to improve SIEM overall. Log management alone doesn't provide real-time insights on network security, SEM on its own won't provide complete data for deep threat analysis. When SEM and log management are combined, more information is available for SIEM to monitor. A key focus is to monitor and help manage user and service privileges, directory services and other system-configuration changes; as well as providing log auditing and review and incident response.
SIEM architectures may vary by vendor; however, generally, essential components comprise the SIEM engine. The essential components of a SIEM are as follows: A data collector forwards selected audit logs from a host (agent based or host based log streaming into index and aggregation point) An ingest and indexing point aggregation point for parsing, correlation, and data normalization A search node that is used for visualization, queries, reports, and alerts (analysis take place on a search node) A basic SIEM infrastructure is depicted in the image to the right.
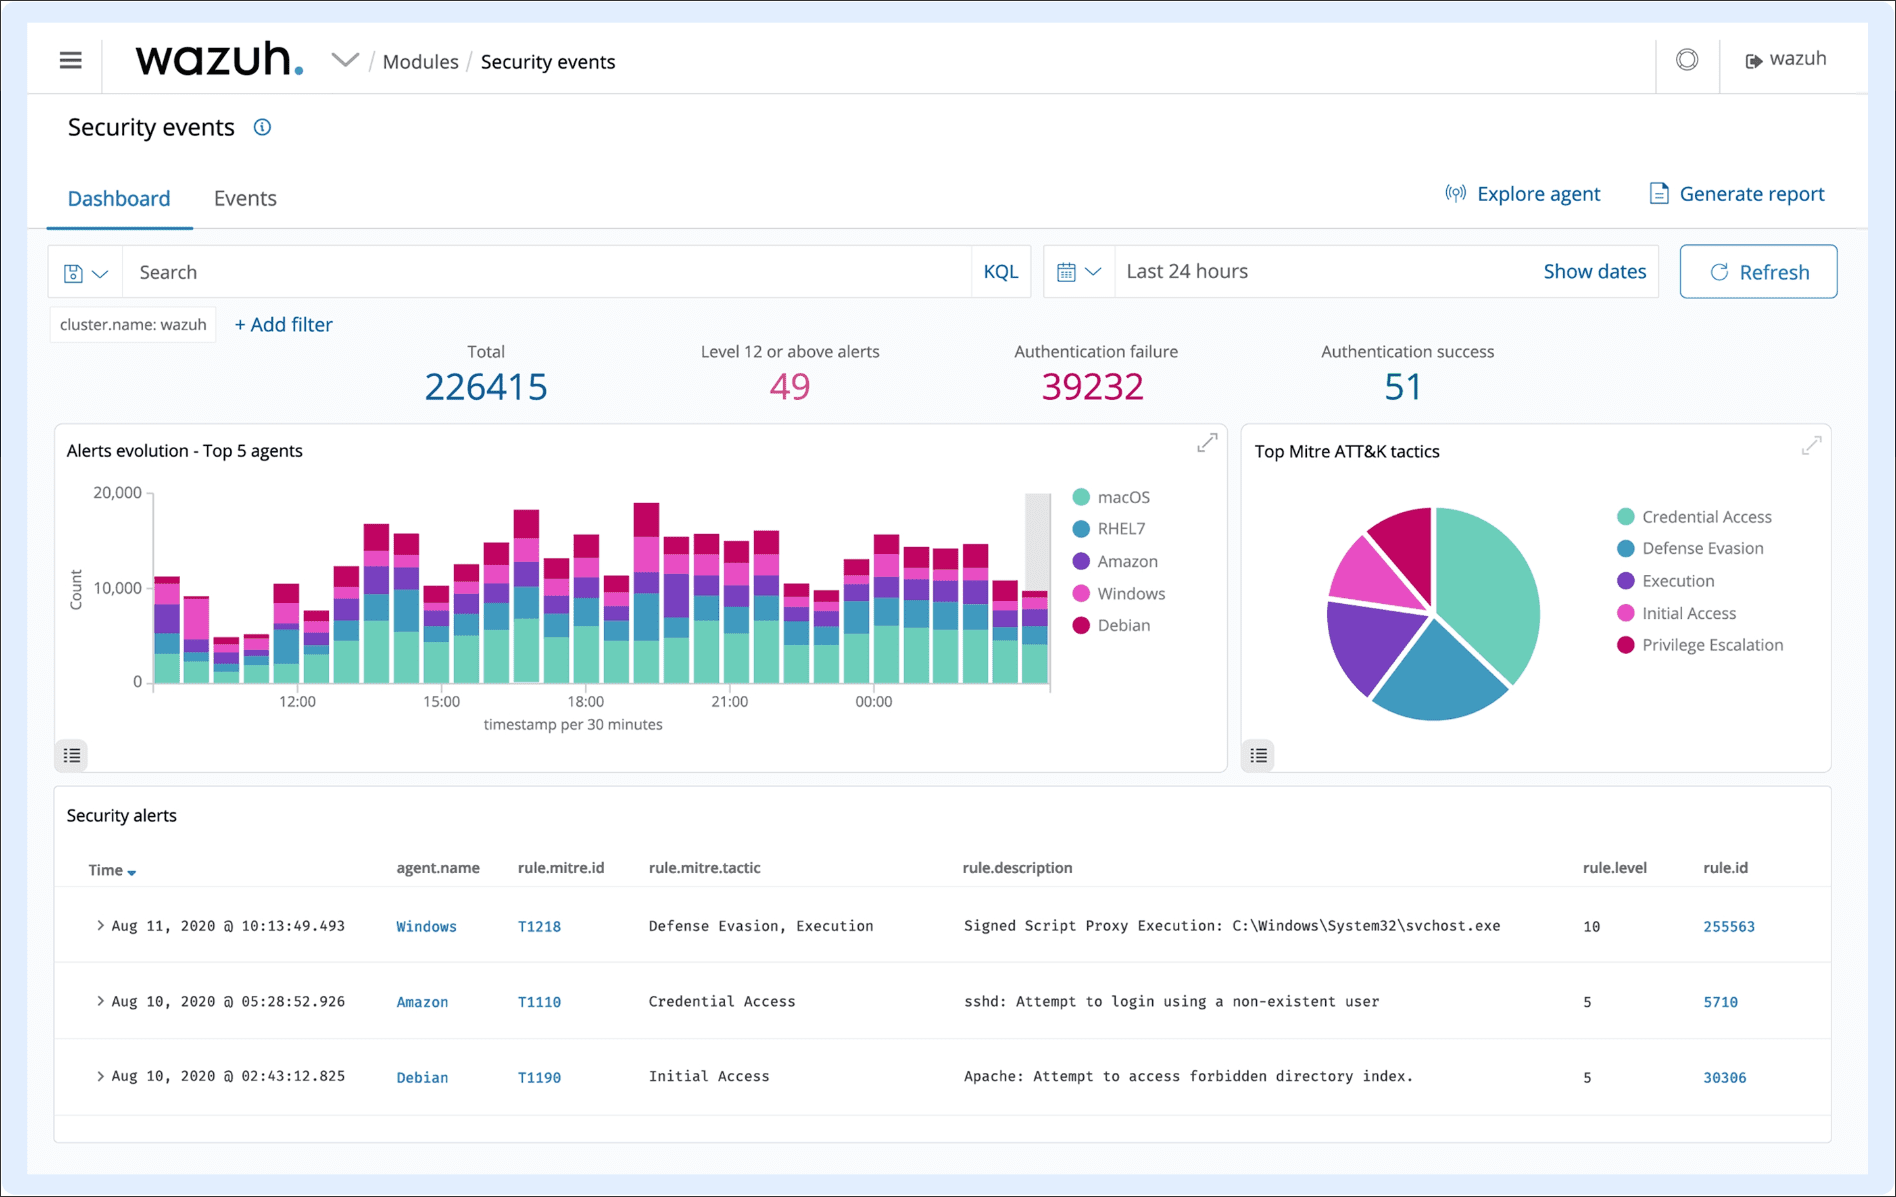
Figure 1: Wazuh Open Source SIEM: XDR for Enterprise and Home Lab ... SIEM visibility and anomaly detection could help detect zero-days or polymorphic code. Primarily due to low rates of anti-virus detection against this type of rapidly changing malware. Parsing, log normalization and categorization can occur automatically, regardless of the type of computer or network device, as long as it can send a log. Visualization with a SIEM using security events and log failures can aid in pattern detection. Protocol anomalies that can indicate a misconfiguration or a security issue can be identified with a SIEM using pattern detection, alerting, baseline and dashboards. SIEMS can detect covert, malicious communications and encrypted channels. Cyberwarfare can be detected by SIEMs with accuracy, discovering both attackers and victims. Modern SIEM platforms support not only detection, but response too. The response can be manual or automated including AI based response.
SIEM systems can have hundreds and thousands of correlation rules. Some of these are simple, and some are more complex. Once a correlation rule is triggered the system can take appropriate steps to mitigate a cyber attack. Usually, this includes sending a notification to a user and then possibly limiting or even shutting down the system. Wazuh is a free and open source security platform that unifies XDR and SIEM capabilities. It protects workloads across on-premises, virtualized, containerized, and cloud-based environments.
Wazuh helps organizations and individuals to protect their data assets against security threats. It is widely used by thousands of organizations worldwide, from small businesses to large enterprises. Figure 2: Wazuh Open Source SIEM: XDR for Enterprise and Home Lab ... Check this Getting Started for an overview of the Wazuh platform components , architecture , and common use cases .
Wazuh has one of the largest open source security communities in the world. You can become part of it to learn from other users, participate in discussions, talk to our development team, and contribute to the project. The following resources are easily available: Slack channel : Join our community channel to chat with our developers and technical team in a close to real-time experience.
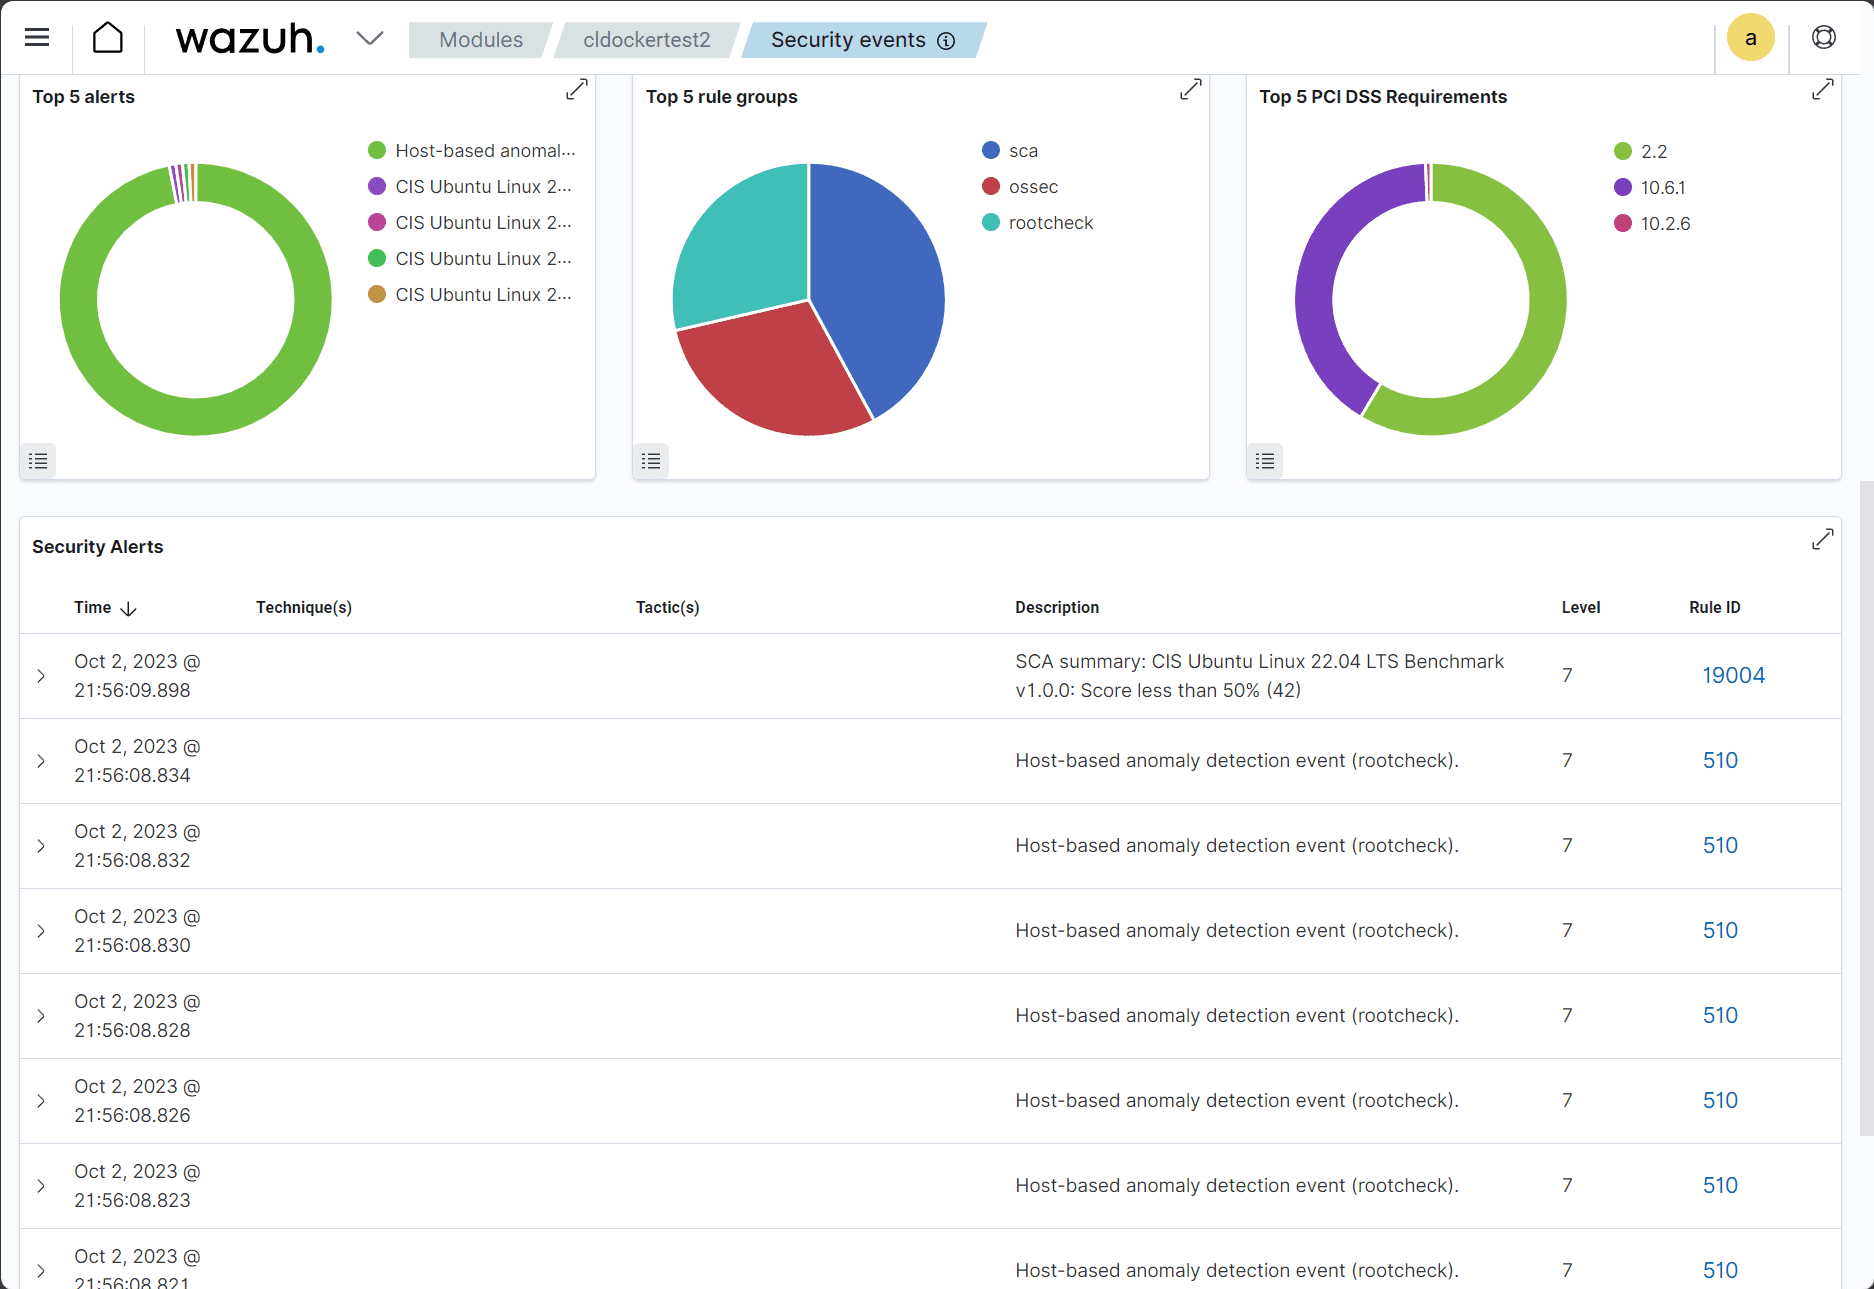
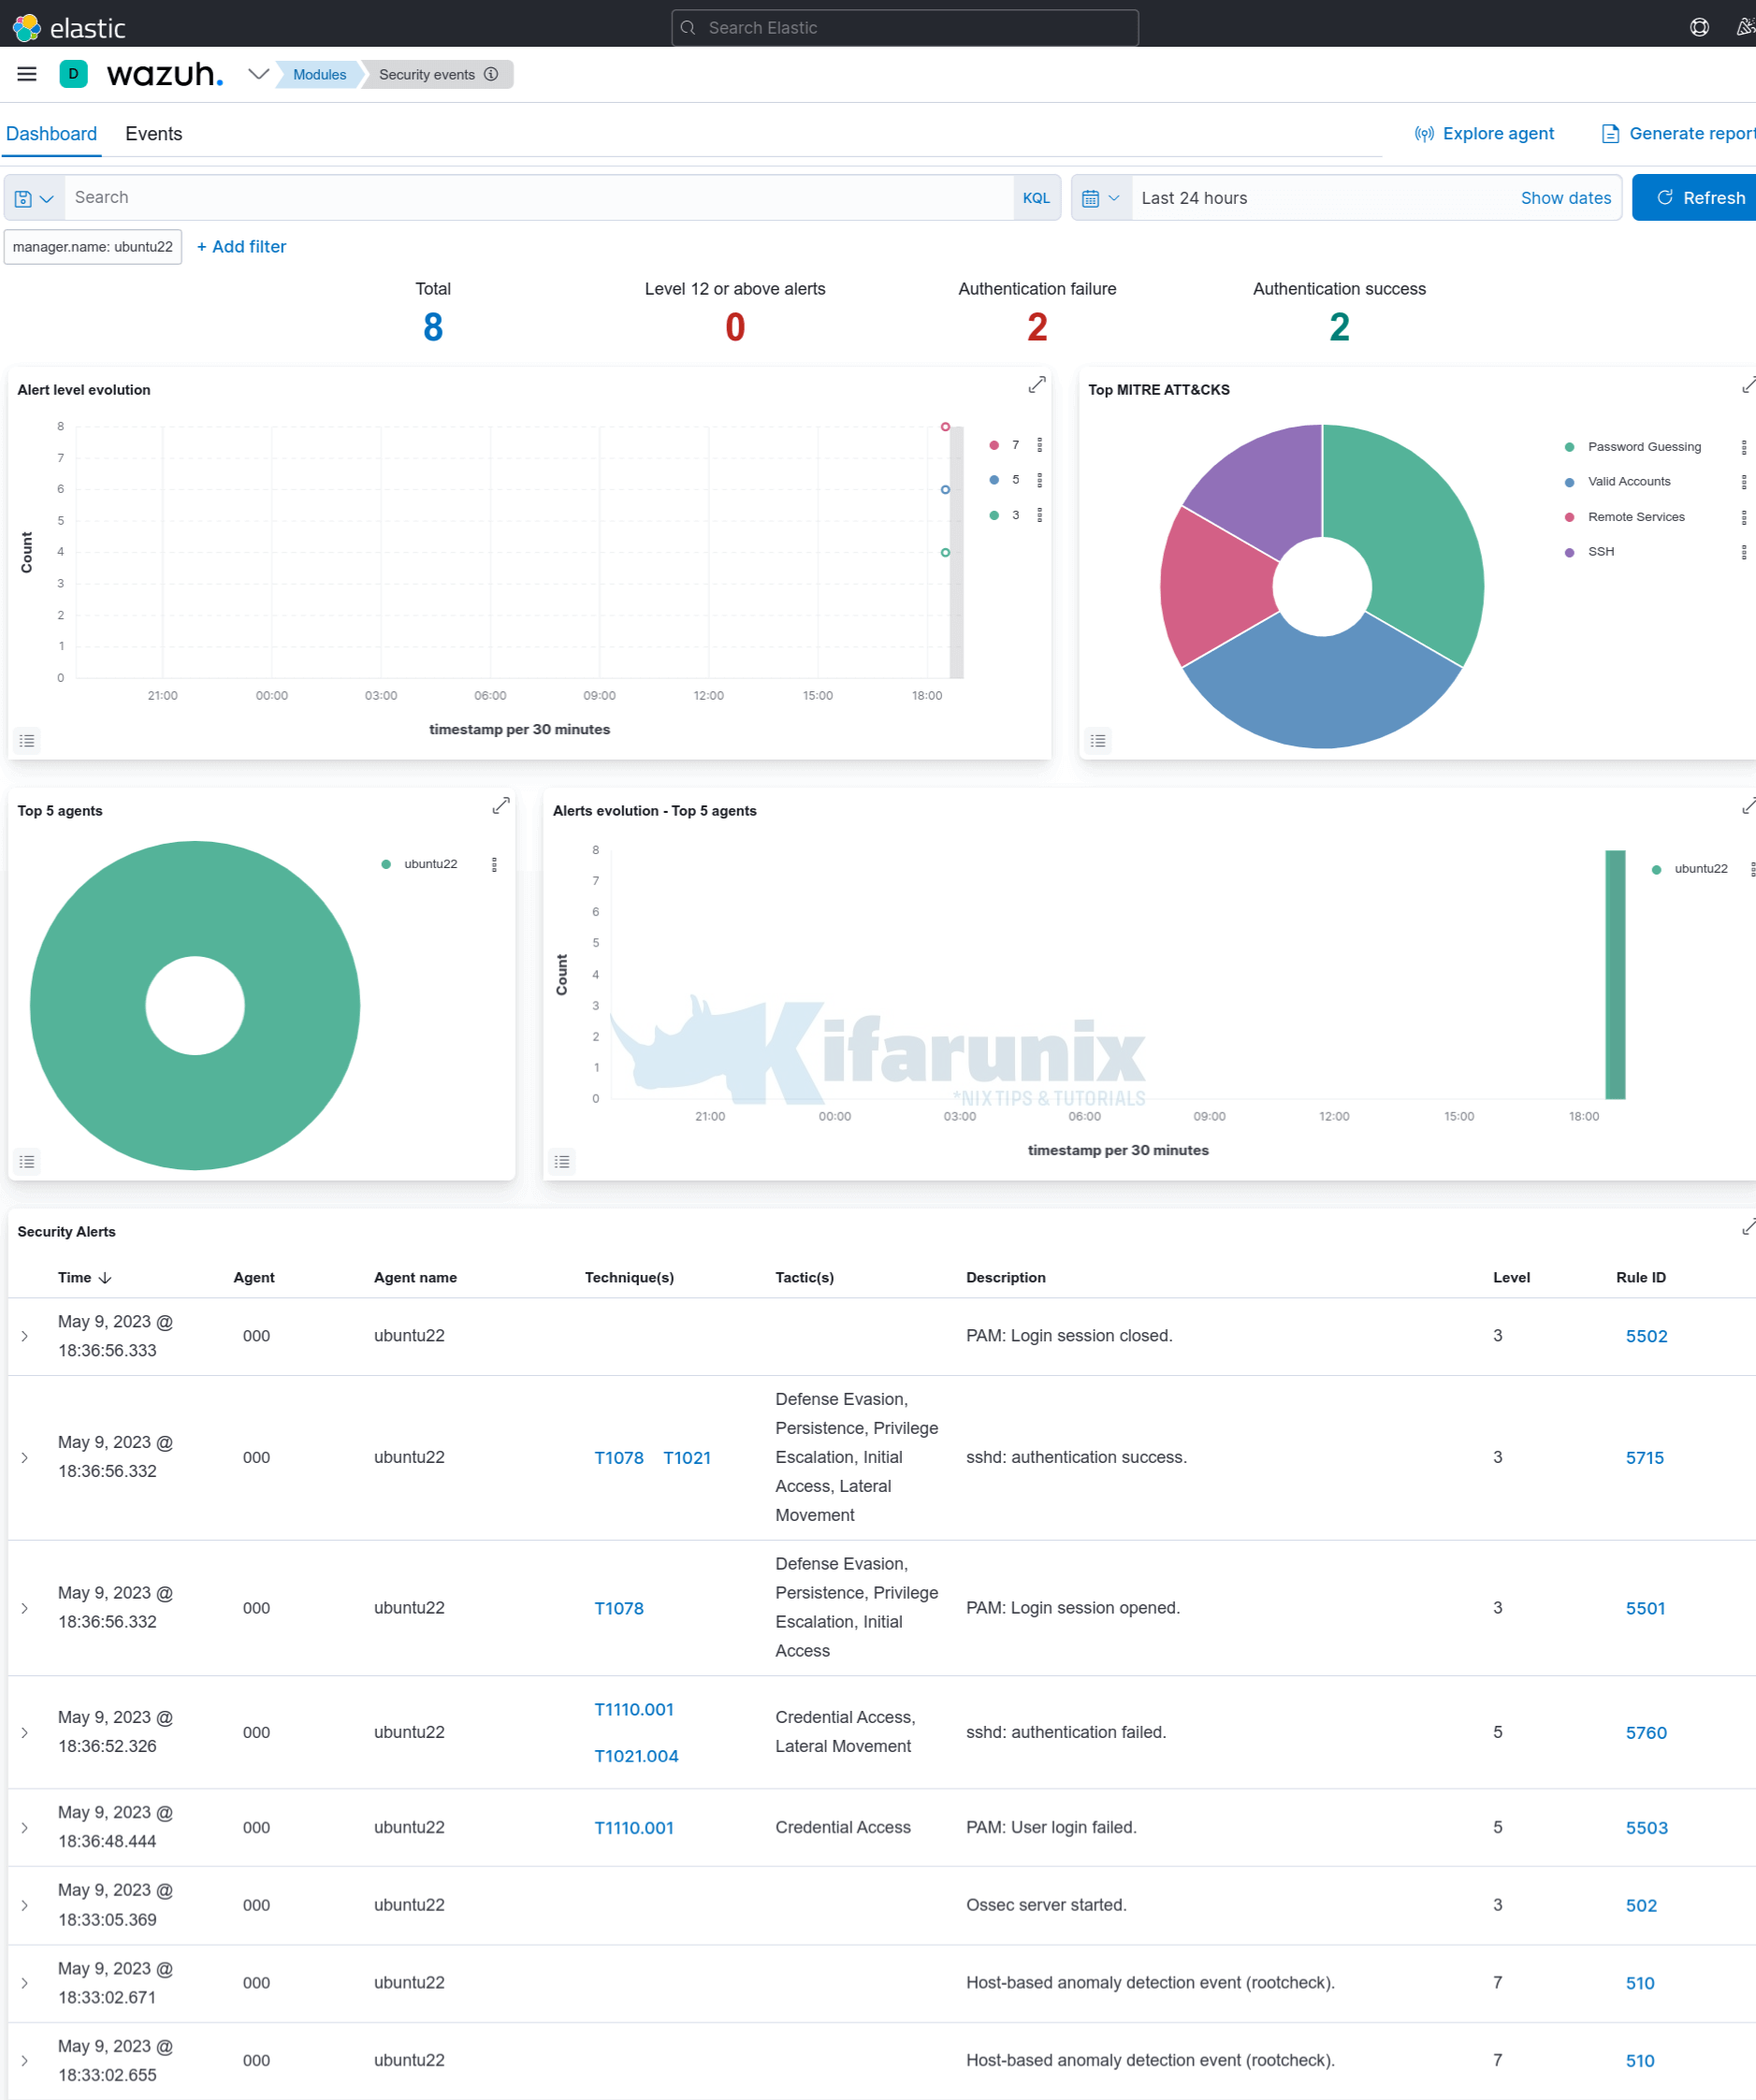
GitHub repositories : Get access to the Wazuh source code, report issues, and contribute to the project. We happily review and accept pull requests. Figure 3: Install and Configure Wazuh Manager on Ubuntu 22.04 - kifarunix.com Discord : Engage with our community in dynamic discussions and collaborations on the latest security trends and Wazuh developments.
Reddit : Join our subreddit to share insights, ask questions, and discuss security issues with fellow users. X : Follow us on X for real-time updates, news, and quick tips from our development team and security experts. LinkedIn : Stay updated with our professional network and industry news by connecting with us on LinkedIn. In addition, we also provide professional support, training, and consulting services .
The Wazuh solution is composed of three central platform components and a single universal agent . For installing Wazuh in your infrastructure, you can check the following sections of our documentation: The Installation guide provides instructions on how to install each central component and how to deploy the Wazuh agents. The Wazuh Cloud is our software as a service (SaaS) solution. We provide a 14-day free trial for you to create a cloud environment and get the best out of our SaaS solution. Check the Cloud service documentation for more information.
You can use large language models (LLMs) to assist in building, managing, and troubleshooting your Wazuh deployment. To support accurate and efficient AI-assisted workflows, Wazuh provides plain text documentation and machine-readable guidance optimized for LLM consumption. You can access most of the Wazuh documentation as plain text Markdown files by replacing .html with .md in the URL of any documentation page.
Cleaner content : Complete documentation text with minimal formatting noise and no navigation elements. Full visibility : Content hidden behind tabs or expandable sections in the web UI is rendered linearly. Structural clarity : Headings, lists, and code blocks preserve document hierarchy for better parsing. Efficient context sharing : You can copy and paste entire guides into an LLM without losing structure or meaning.
Wazuh hosts an /llms.txt file at the root of the documentation domain. This file follows an emerging standard to guide AI tools and agents on how to retrieve and prioritize Wazuh documentation content. It also instructs agents to prefer the current documentation version unless another version is explicitly required. Welcome to the Wazuh user manual. Use it as your reference library once your basic Wazuh installation is ready. In this section, you will find content on topics such as Wazuh server administration, Wazuh agent enrollment, Wazuh capabilities, and many others that are listed below.
Modern organizations generate enormous volumes of security telemetry from endpoints, servers, cloud platforms, firewalls, applications, and network devices. Without a centralized security platform, detecting threats, investigating incidents, and maintaining compliance quickly becomes difficult.
Wazuh has become one of the most popular open-source Extended Detection and Response (XDR) and Security Information and Event Management (SIEM) platforms because it combines log analysis, endpoint security, vulnerability detection, file integrity monitoring, threat detection, compliance monitoring, and incident response into a single platform. Unlike many commercial SIEM solutions that require expensive licensing, Wazuh provides enterprise-grade security monitoring while remaining fully open source.
It supports both small deployments with a handful of servers and large enterprise environments consisting of thousands of endpoints spread across multiple regions. Whether you’re deploying Wazuh for the first time or designing a production-ready security monitoring platform, proper installation is the foundation for long-term stability, scalability, and performance.
Configuration mistakes made during deployment often lead to issues such as disconnected agents, dashboard failures, indexing problems, certificate errors, and high resource usage later. This comprehensive Wazuh Installation Guide walks through every major deployment decision before you install your first component.
Whether you’re installing Wazuh in a home lab, a corporate datacenter, Kubernetes, or the cloud, the deployment principles remain largely the same. Throughout this guide, we’ll also reference specialized installation tutorials for Windows agents, Linux endpoints, Docker deployments, indexer clustering, and agent upgrades so you can continue learning each topic in greater depth.
Planning your architecture, infrastructure, networking, and security requirements upfront significantly reduces deployment issues later. Organizations that invest time in deployment planning typically experience fewer operational problems after going live. Wazuh supports several deployment architectures depending on your environment, scale, and operational requirements.
Most organizations begin with a single-node deployment before expanding into clustered architectures. Organizations monitoring hundreds or thousands of endpoints should strongly consider this deployment model. Containerized deployments have become increasingly popular for development environments and cloud-native infrastructure. Improper Docker configuration is one of the most common causes of deployment failures.
Virtualized deployments provide flexibility while simplifying backups, scaling, snapshots, and disaster recovery. The Wazuh documentation includes deployment recommendations for multiple cloud platforms. Understanding how each Wazuh component interacts makes installation significantly easier and simplifies future troubleshooting.
Nearly every event collected by Wazuh passes through the Manager before being indexed. Storage sizing is one of the most important planning considerations because security logs grow rapidly. The Dashboard communicates with the Indexer rather than directly processing endpoint events. The agent performs lightweight local monitoring before securely forwarding events to the Manager.
After events are analyzed and enriched, the Manager forwards them to the Wazuh Indexer. This separation improves scalability and allows analysts to search large datasets efficiently. Preparation is often the difference between a deployment that succeeds in one afternoon and one that requires days of troubleshooting.
Organizations frequently underestimate storage growth, making capacity planning especially important. Wazuh Compatibility Matrix – https://documentation.wazuh.com/current/installation-guide/index.html Reliable networking is critical for stable communication between all Wazuh components. All Wazuh components should synchronize against reliable Network Time Protocol (NTP) servers to prevent misleading timelines during incident investigations.
Installing security software securely is just as important as installing it correctly. Avoid using self-signed certificates in long-term production environments whenever possible. Administrative access should be limited to authorized personnel and protected using strong authentication policies. Regular backups dramatically reduce recovery time following hardware failures or configuration mistakes.
According to the U.S. National Institute of Standards and Technology (NIST) , organizations should integrate backup and recovery planning into overall system security and resilience strategies rather than treating backups as an afterthought. Expert Insight: The Wazuh engineering team consistently recommends separating production components, using TLS for all inter-component communication, and planning cluster architecture before onboarding large numbers of agents. These practices significantly reduce operational issues as deployments scale.
Once you’ve planned your deployment architecture and prepared your infrastructure, you’re ready to install the core Wazuh platform. Although the installation process varies slightly depending on whether you’re deploying a single server, a production cluster, or containers, every installation includes the same primary components: For first-time users, a single-node deployment is the easiest way to become familiar with the platform before expanding into a clustered production environment.
Because all services run on the same machine, installation is straightforward and requires fewer infrastructure resources. The official installation assistant automates much of this process, reducing manual configuration and minimizing deployment errors. The Wazuh Manager is the central component responsible for processing security events received from monitored endpoints.
After installation, administrators should verify that the manager service starts automatically and is listening on the expected ports. It is also good practice to review the manager logs immediately after installation to identify configuration warnings before enrolling production systems.
The Wazuh Indexer stores all processed security events and makes them searchable through OpenSearch. The Indexer generally consumes the most CPU, memory, and disk resources in a deployment, making proper resource allocation critical for long-term performance. Administrators should confirm cluster health after installation before sending production traffic.
Once configured, the Dashboard should display the platform status, connected agents, and security alerts after data begins flowing into the Indexer. If the Dashboard cannot connect to the Indexer, review authentication settings, certificates, and network connectivity before proceeding.
After all three core components are installed, perform several post-installation tasks before onboarding endpoints. Taking time to validate these settings now can prevent difficult troubleshooting later. You should also confirm that the Dashboard can retrieve data from the Indexer and that internal communication between services is functioning normally.
As environments grow, architecture decisions have a significant impact on reliability and performance. Removing single points of failure ensures security monitoring continues even during hardware failures or maintenance windows. Rather than continually upgrading one large server, many organizations scale horizontally by adding additional Manager and Indexer nodes.
Storage often becomes the first infrastructure bottleneck in mature Wazuh deployments. Using fast SSD storage significantly improves indexing performance and dashboard responsiveness compared to traditional spinning disks. Large deployments frequently place load balancers in front of Manager nodes or Dashboard servers.
Load balancing also simplifies future expansion because additional nodes can be introduced with minimal disruption. Expert Insight: Large enterprise SOCs often separate ingestion, indexing, and visualization onto dedicated servers instead of scaling a single machine. This architecture improves fault isolation and allows each layer to scale independently as log volume increases.
Agents act as sensors distributed throughout your infrastructure, continuously collecting telemetry and securely forwarding it to the Wazuh Manager. Wazuh Agents provide deep visibility into operating system activity that cannot be obtained through network monitoring alone. Each installed agent expands the organization’s ability to detect suspicious activity across its infrastructure.
This visibility helps security teams identify malicious behavior before it spreads throughout the environment. One of the primary responsibilities of the agent is collecting operating system and application logs. 2. System Architecture & Core Working Principles File Integrity Monitoring (FIM) detects unauthorized modifications to important files.
FIM helps identify ransomware activity, unauthorized configuration changes, and persistence mechanisms used by attackers. Wazuh Agents collect software inventory information that enables vulnerability detection. This information allows security teams to prioritize remediation efforts based on actual exposure. Wazuh provides native agents for the most commonly deployed enterprise operating systems.
It integrates with Windows Event Logs, Defender, Sysmon, and numerous security-related event providers. This allows organizations to maintain consistent visibility across mixed operating system environments. Ongoing management ensures that endpoints remain healthy, correctly configured, and capable of detecting new threats. Every endpoint must register with the Wazuh Manager before it begins sending security events.
Administrators should periodically review registered agents to remove inactive or unauthorized systems. Agent Groups allow administrators to apply different configurations to different classes of systems. Grouping simplifies large-scale policy management and reduces administrative overhead. Assigning policies through Agent Groups makes configuration changes consistent across hundreds or thousands of systems.
Monitoring dashboards and automated alerts help detect unhealthy agents before visibility is lost. Rolling upgrades are generally safer than updating every endpoint simultaneously, particularly in large enterprise environments. Expert Insight: Security teams managing thousands of endpoints often automate agent deployment, grouping, and upgrades using configuration management tools such as Ansible, Puppet, or Microsoft Intune. Automation reduces configuration drift while ensuring consistent security policies across the environment.
Many organizations begin with a single-node Wazuh deployment, but as infrastructure grows, so do the demands placed on the platform. Increasing numbers of endpoints, higher log ingestion rates, longer data retention periods, and more concurrent analysts all place additional pressure on the Wazuh Indexer and Manager.
Designing for scalability from the outset makes future expansion significantly easier and reduces the risk of performance bottlenecks. A standalone Indexer works well for small deployments, but there comes a point where clustering becomes necessary. As your environment grows, distributing workloads across multiple Indexer nodes improves both performance and reliability.
In a clustered environment, the failure of a single Indexer node does not necessarily interrupt security monitoring or dashboard access. This is especially important for organizations operating around the clock or supporting multiple business units. If one node becomes unavailable due to hardware failure, software corruption, or network issues, replicated data remains accessible from other nodes.
Search queries are distributed across multiple nodes rather than relying on a single server. Instead of upgrading a single server indefinitely, clustered deployments allow organizations to scale horizontally by adding additional nodes. Avoid designing a cluster solely for current requirements. Planning for expected growth over the next several years can reduce future migrations and infrastructure redesign.
Expert Insight: The OpenSearch project recommends deploying an odd number of cluster manager-eligible nodes (such as three) to maintain quorum and improve cluster stability during node failures or maintenance. This helps prevent split-brain scenarios and improves cluster resilience. Containerized deployments have become increasingly popular because they simplify installation, automate configuration, and integrate well with modern DevOps workflows.
Docker allows administrators to deploy Wazuh quickly while maintaining consistent environments across development, testing, and production systems. However, containerization also introduces operational considerations that differ from traditional package-based installations. Containerized deployments make it easier to reproduce environments, automate provisioning, and standardize deployments across multiple teams.
For large enterprise production environments, many organizations still choose dedicated virtual machines or bare-metal servers to maximize performance and simplify long-term storage management. These containers communicate through Docker networking while using persistent volumes to retain: Most deployments are orchestrated using Docker Compose, allowing administrators to start or stop the entire platform with a single command.
Although Docker simplifies deployment, several common issues regularly affect new installations. Many Dashboard and Indexer connectivity issues originate from networking or volume configuration rather than Wazuh itself. Monitoring container logs during deployment can significantly reduce troubleshooting time. Proper post-installation configuration ensures the platform collects meaningful security data, detects threats accurately, and remains reliable over time.
After deploying the core platform, work through the following configuration tasks before placing Wazuh into production. The first validation step is confirming that endpoints successfully connect to the Wazuh Manager. Offline agents should be investigated before continuing with additional configuration. Organizations should also review default detection rules to reduce unnecessary alert noise while ensuring critical threats receive immediate attention.
Enable Vulnerability Detection so Wazuh can correlate installed software with known Common Vulnerabilities and Exposures (CVEs). Regular vulnerability scanning helps prioritize remediation efforts based on actual exposure. File Integrity Monitoring (FIM) should be configured to monitor sensitive operating system and application files.
Administrators should carefully tune monitoring paths to balance visibility with resource consumption. Collecting only relevant logs helps reduce storage consumption while improving investigation quality. Active Response allows Wazuh to automatically react when predefined threats are detected. Automation should be introduced gradually and thoroughly tested before enabling it in production to avoid unintended disruptions.
Finally, confirm that the Dashboard provides complete visibility into your environment. A fully functioning Dashboard confirms that communication between the Manager, Indexer, and Dashboard has been successfully established. Expert Insight: Experienced SOC teams often perform a controlled validation exercise immediately after deployment by generating known security events, such as failed logins or test detection rules to verify that alerts flow correctly from the endpoint to the Manager, are indexed successfully, and appear in the Dashboard before onboarding production systems.
Completing the installation does not necessarily mean your Wazuh deployment is ready for production. Before onboarding additional endpoints or relying on the platform for threat detection, verify that every core component is operating correctly and communicating as expected. A structured validation process helps identify configuration issues early, preventing gaps in monitoring and reducing future troubleshooting.
The Wazuh Manager is responsible for processing security events, evaluating detection rules, and coordinating communication with agents. Review the Manager log files for warnings or repeated errors that may indicate configuration problems. If you’re using multiple Indexer nodes, ensure cluster synchronization completes successfully before enrolling large numbers of endpoints.
The Dashboard should load without errors and successfully communicate with the Indexer. If the Dashboard reports connection errors, review Indexer connectivity, authentication settings, and TLS certificate configuration. After enrolling a test endpoint, verify that communication between the agent and Manager functions correctly.
Testing communication before deploying hundreds or thousands of agents prevents widespread enrollment issues. This end-to-end validation ensures the entire detection pipeline is functioning correctly. Unexpected gaps in log collection often indicate configuration issues rather than infrastructure failures. Monitoring ingestion rates during the first several days after deployment helps establish performance baselines and detect anomalies early.
Whether deploying Wazuh in a small lab or a global enterprise, following established best practices helps improve security, reliability, and long-term maintainability. Testing changes before production reduces operational risk and minimizes unexpected outages. Strong TLS configurations protect sensitive security telemetry from interception and unauthorized access.
The Manager, Indexer, Dashboard, and Agents should remain on compatible software versions. Manual installation may be practical for a handful of systems, but automation becomes essential as environments grow. Automation improves consistency while reducing deployment time and configuration drift. Well-maintained documentation also accelerates troubleshooting and onboarding of new administrators.
Expert Insight: The Center for Internet Security (CIS) emphasizes secure configuration management, asset inventory, and continuous monitoring as foundational cybersecurity practices. Applying these principles during a Wazuh deployment results in a more resilient and maintainable security monitoring platform. Even experienced administrators occasionally encounter deployment issues caused by avoidable configuration mistakes.
Understanding these common pitfalls can save hours of troubleshooting and improve long-term platform stability. Running unsupported operating systems or incompatible software versions often leads to unexpected behavior. Always consult the official compatibility documentation before deploying or upgrading production systems. Provision hardware based on expected long-term workloads rather than minimum installation requirements.
Mixing incompatible versions of the Manager, Dashboard, Indexer, and Agents can produce difficult-to-diagnose issues. Plan upgrades carefully and avoid skipping major versions unless explicitly supported. Storage shortages often appear months after deployment rather than during installation. Regularly review storage consumption and adjust retention policies as infrastructure evolves.
Some administrators begin onboarding production systems immediately after installation without validating the deployment. Always perform comprehensive validation before considering the deployment production-ready. Expert Insight: Many experienced Wazuh administrators treat deployment as an iterative process rather than a one-time task. They validate each layer. Manager, Indexer, Dashboard, networking, certificates, and agents before progressing to the next stage. This incremental approach significantly reduces troubleshooting complexity and leads to more reliable production deployments.
Even well-planned Wazuh deployments can fail or behave unpredictably due to a small number of recurring configuration mistakes. These issues are especially common in first-time installations and often manifest as connectivity problems, missing alerts, degraded performance, or broken dashboards.
Understanding these pitfalls helps ensure a stable and production-ready deployment from the start. One of the most frequent deployment issues comes from using unsupported operating systems or mismatched Wazuh component versions. These mismatches can lead to API failures, missing features, or complete service incompatibility.
Always verify compatibility before installation and ensure all components belong to the same supported release family. Wazuh Compatibility and Installation Requirements – https://documentation.wazuh.com/current/installation-guide/ Under-provisioning infrastructure is a common cause of long-term performance degradation. 3. Software Implementation, Frameworks & Protocols Wazuh performance is heavily dependent on indexing capacity, so storage speed, memory allocation, and CPU availability must be sized based on expected ingestion rates, not just minimum installation guidelines.
These issues often present as “service running but no data flowing,” making them difficult to diagnose without systematic network validation. Ensure that firewall rules explicitly allow required internal communication paths and restrict external exposure of administrative services.
Because Wazuh relies heavily on encrypted communication, even minor certificate errors can break communication between core components. Running mismatched versions of Wazuh components creates subtle and hard-to-diagnose failures. Storage miscalculations are often discovered after deployment, when log volume begins to accumulate.
Because Wazuh generates continuous telemetry, storage growth is predictable, but often underestimated. A structured validation phase ensures the platform is fully operational before onboarding production workloads. A structured checklist helps ensure consistency across deployments and reduces the risk of configuration drift or missed setup steps.
This section can be used as a final validation framework before moving into production. At this stage, the goal is to eliminate environmental uncertainty before installation begins. Installation issues are easiest to resolve when caught immediately rather than after full deployment. Expert Insight: Mature SOC environments typically treat deployment validation as a formal “go-live gate,” requiring sign-off from security engineering, infrastructure, and operations teams before production onboarding begins. This prevents premature exposure to incomplete or misconfigured monitoring pipelines.
This section addresses common questions that arise during Wazuh installation and early deployment. These answers reflect typical real-world scenarios encountered during small, medium, and enterprise-scale implementations. Most delays come not from installation itself, but from prerequisites such as networking, certificates, and storage configuration.
Production environments typically require significantly more resources, especially for the Indexer. Wazuh Installation Requirements – https://documentation.wazuh.com/current/installation-guide/index.html Many organizations use Docker for experimentation and native deployments for production. However, single-node setups are not recommended for large-scale production due to limited scalability and lack of fault tolerance.
Clusters become essential in enterprise-scale environments with sustained ingestion workloads. After installation, endpoints are added by installing and registering the Wazuh Agent. A full end-to-end test (agent → manager → indexer → dashboard) is the most reliable validation method. In most cases, installation issues are not caused by Wazuh itself but by environment configuration problems.
Deploying Wazuh successfully requires more than simply running an installation script. It is a structured process that begins with careful planning, continues through architecture selection, and ends with rigorous validation of every component in the stack. A key takeaway is that successful Wazuh deployments are not defined by installation speed, but by correctness and validation.
Every component must be verified individually and as part of the full event pipeline before the system is considered production-ready. For deeper implementation details, you should continue with the specialized guides referenced throughout this article. These cover practical, step-by-step instructions for installing agents, building clusters, upgrading components, and troubleshooting real-world issues.
A properly deployed Wazuh platform becomes significantly more powerful once it is tuned, integrated, and scaled according to organizational needs. In the last edition of the SIEM series , we discussed EFK (Elasticsearch, Fluentd, and Kibana), which included a general overview of the technology stack before diving into a hands-on practice. As a reminder, this blog series is not meant to replace course training but rather to introduce the audience to what is involved with SIEM and explain how it works at a basic level.
Additionally, I also wanted to help users create easy sandbox environments where they can practice while they learn. Wazuh is an opensource complete SIEM (Security Information and Event Management) and XDR (Extended Detection and Response) platform. It was created as a fork from Ossec in 2015 and was intended to modernize and extend the latter’s capabilities. Its goal is to become a unified security monitoring solution.
It has tried to address some of the complexities that we witnessed in ELK and make it easier to create your own monitoring system. Wazuh is a powerful open-source security platform that integrates threat detection, integrity monitoring, incident response, and compliance management. Its architecture is modular, comprising several key components: Wazuh can be deployed as a single-node or multi-node architecture depending on scalability and performance needs.
As we covered earlier in this series, raw syslog messages aren’t ideal for building dashboards or triggering alerts. To make them useful, we need to break them down into structured, readable data. In simple terms, creating clear key-value pairs is essential—especially when working with visualization tools like Kibana or the Wazuh Dashboard. Logstash and Fluentd are general purpose log processing engines and are designed for flexibility. However, often flexibility requires complexity. During our walk-through example of grok parsing it was evident that this is an acquired skill and requires time and effort to gain expertise in.
Wazuh chose a slightly different path and uses two stages to process the logs. The first stage leverages decoders while the second one uses the rules. Wazuh attempts to make it easier to parse logs for security purposes by leveraging decoders and regulations with built-in security parsers. In a nutshell, this is how we can compare what we saw with Logstash/Fluentd to Wazuh Decoders and Rules: Just like in our previous posts in this SIEM series, we’re all about hands-on learning. In this exercise, we’ll be working with an Ubuntu virtual machine to install Wazuh directly on the operating system—no Docker this time. For our test lab setup, Wazuh offers a convenient installation script that makes the process quick and straightforward.
3. At this point, you should be able to open a browser and navigate to the IP address or DNS name of your Wazuh VM. If everything is set up correctly, the Wazuh dashboard will load, giving you access to your SIEM environment. 4. Log in using the username admin and the password that appeared in your terminal after completing the installation script. Once logged in, Wazuh will present a rich dashboard full of options to explore.
We’ve created a GitHub repository with simple decoders and rules tailored for Object First’s Ootbi (Out-of-the-Box Immutability) syslog forwarding. You can download them using: No Ootbi yet? No problem. We’ll simulate syslog messages to demonstrate how Wazuh processes them. Instead of modifying the default local_decoder.xml and local_rules.xml, we recommend creating separate files for better organization, especially if you plan to manage multiple event types.
1. Ensure Wazuh is listening for incoming syslog connections by adding the following section to In the Wazuh dashboard, open the top-left menu and click on “Explore” then “Discover.” 5. Subsequently, click on the “Ootbi Dashboard.” You’ll see the events you sent earlier displayed. Since Wazuh is functioning as a SIEM, this is a great opportunity to test Ootbi's new Honeypot feature.
3. If your Honeypot is running on a static IP (mine, for example, is 192.168.0.44), scan it using Zenmap. 5. You should see events lighting up in the Ootbi dashboard and corresponding entries in your Wazuh SIEM dashboard. This blog served as a hands-on introduction to Wazuh, an open-source SIEM and XDR platform designed to simplify security monitoring and threat detection. We explored its modular architecture—covering agents, the server, analysis engine, indexer, and dashboard—and walked through a single-node installation on Ubuntu using Wazuh’s streamlined setup script. From there, we demonstrated how to configure decoders and rules for syslog integration, simulate events, and visualize them in the Wazuh dashboard.
We also showcased how to import a custom dashboard and test Ootbi's Honeypot feature, giving readers a practical look at how Wazuh can be used in real-world scenarios. Whether you're new to SIEM tools or looking for a more security-focused alternative to traditional log processors, Wazuh offers a powerful and approachable solution. For further exploration, I’d highly recommend checking Wazuh’s official documentation .
The Wazuh Security Information and Event Management (SIEM) solution is a centralized platform for aggregating and analyzing telemetry in real time for threat detection and compliance. Wazuh collects event data from various sources like endpoints, network devices, cloud workloads, and applications for broader security coverage. Protect your infrastructure and meet regulatory compliance by monitoring and auditing endpoint activity. Wazuh aggregates, stores, and analyzes security event data to identify anomalies or indicators of compromise. The SIEM platform adds contextual information to alerts to expedite investigations and reduce average response time.
Detect vulnerabilities on monitored endpoints where you deploy the Wazuh agent. Wazuh prioritizes identified vulnerabilities to speed up your decision-making and remediation process. The Wazuh vulnerability detection capability ensures you meet regulatory compliance requirements while reducing your attack surface. Leverage the Wazuh SCA capability to identify misconfigurations and security flaws in your infrastructure. Wazuh scans your systems against the Center for Internet Security (CIS) benchmark to allow you to identify and remediate vulnerabilities, misconfigurations, or deviations from best practices and security standards.
Simplify the process of meeting regulatory compliance requirements by using Wazuh. Wazuh helps you track and demonstrate compliance with various regulatory frameworks such as PCI DSS, NIST 800-53, GDPR, TSC SOC2, and HIPAA. Receive real-time alerts and notifications when security incidents occur. Wazuh correlates events from multiple sources, integrates threat intelligence feeds, and provides customizable dashboards and reports. You can customize alerts to meet specific requirements. This allows security teams to respond quickly to threats and minimize the impact of security incidents.
Generate insightful reports that provide high-level analysis of security events. Wazuh allows you to generate comprehensive, actionable information that meets your unique needs. You can use Wazuh reports to demonstrate compliance with various regulations and standards. Installing Wazuh is only the first step toward building an effective security monitoring platform.
Once the platform is running, the real work begins: configuring it to collect the right data, detect meaningful threats, automate responses, and scale reliably across your infrastructure. Every environment is different, so there is no single configuration that works for every deployment. Without customization, you may miss important security events, collect excessive amounts of unnecessary logs, consume more storage than expected, or generate overwhelming numbers of false-positive alerts.
Well-configured deployments improve detection accuracy, reduce operational overhead, and make investigations significantly faster . It’s also important to understand the difference between installing Wazuh and configuring it. Installation focuses on deploying the software components and ensuring they communicate correctly. Configuration focuses on determining what data should be collected, how alerts should be generated, when automated responses should execute, and how the platform should operate in production.
In this comprehensive guide, you’ll learn how Wazuh’s configuration system works, which configuration files control each component, and the best practices for safely modifying them. You’ll also discover how to configure core features such as File Integrity Monitoring (FIM), Active Response, centralized syslog collection, log retention, custom detection rules, and rule testing.
Throughout the guide, we’ll link to detailed tutorials that walk through each configuration topic step by step. Whether you’re deploying Wazuh for the first time or optimizing an existing deployment, this guide is designed to serve as your complete configuration reference. Before modifying configuration files, it’s important to understand how Wazuh is structured.
Rather than relying on a single configuration file, Wazuh distributes configuration across multiple components, each responsible for a different part of the platform. Together, these files determine how data is collected, analyzed, stored, visualized, and acted upon. Understanding which component controls which functionality helps you troubleshoot problems faster and avoid making unnecessary or conflicting configuration changes.
If you’re managing Windows endpoints, see our guide on How to Install a Wazuh Agent on Windows Server . For Linux environments, you may also find How to Add Linux Endpoints to Wazuh helpful. Most production environments spend the majority of their configuration effort on the manager. If Filebeat cannot communicate with the indexer, alerts will stop appearing in the dashboard.
Wazuh can act as a centralized syslog server for routers, switches, firewalls, Linux servers, and network appliances. Different files control different subsystems, making it easier to manage large deployments without editing a single monolithic configuration file. Sections are organized into logical blocks, making it relatively easy to identify and modify individual features without affecting unrelated services.
Agents maintain their own configuration that determines what data they collect before forwarding it to the manager. Agent groups allow administrators to assign different configurations based on server role. Rather than modifying the default file directly, administrators should place overrides in: When troubleshooting parsing issues, remember that rules cannot match fields that decoders never extracted.
Following a few best practices before making modifications helps reduce downtime, simplifies troubleshooting, and prevents accidental data loss. This allows you to quickly restore a working configuration if a mistake causes services to fail or alerts to stop processing. A common approach is to maintain timestamped backups or use a version control system to track changes over time.
Always validate configuration files before restarting services whenever possible, and carefully review service logs after applying changes. The official Wazuh documentation provides guidance on validating configurations and safely restarting services. This practice aligns with modern Infrastructure as Code (IaC) and DevSecOps workflows.
Whenever possible, validate new rules, integrations, and configuration changes in a staging environment before deploying them to production. 4. Practical Deployment, Analysis & Case Studies The Wazuh developers also recommend testing custom rules using wazuh-logtest before enabling them in production.
Good documentation significantly reduces troubleshooting time during future incidents. Understanding these relationships makes troubleshooting much faster and prevents unnecessary configuration changes in the wrong component. Industry guidance from organizations such as the National Institute of Standards and Technology (NIST) emphasizes secure configuration management and controlled change management as foundational cybersecurity practices, particularly in production environments.
Following these principles reduces operational risk while improving system reliability. While Wazuh offers dozens of configurable features, there are several settings that every deployment should review before moving into production. These core configurations ensure that the platform collects meaningful security data, organizes monitored systems efficiently, delivers actionable alerts, and protects administrative access.
Whether you’re managing ten endpoints or several thousand, the following configurations should be considered the foundation of a healthy Wazuh deployment. If important events are not being collected, they cannot be analyzed, correlated, or used to generate alerts. Before enabling advanced features such as custom detection rules or automated responses, verify that Wazuh is ingesting logs from all critical systems.
Monitoring these files provides visibility into authentication attempts, privilege escalation, software changes, and system errors. Windows endpoints rely heavily on Event Viewer channels rather than traditional log files. Collecting Windows Event Logs enables Wazuh to detect failed logins, privilege abuse, malware activity, PowerShell attacks, and lateral movement.
Many network devices, firewalls, switches, routers, storage appliances, and Unix systems transmit logs using the Syslog protocol. Centralizing Syslog collection provides a single location for monitoring infrastructure events and simplifies incident investigations.
Modern Linux distributions often use systemd-journald instead of traditional log files. Many organizations monitor both Journald and traditional log files to maximize coverage. Business applications often produce proprietary log formats that contain valuable security information. Wazuh supports monitoring virtually any text-based log source. Custom decoders and detection rules can then transform those logs into meaningful security alerts.
As environments grow, managing every endpoint individually quickly becomes impractical. Agent groups allow administrators to organize endpoints based on their purpose and assign shared configurations to entire collections of systems. Grouping endpoints keeps configuration organized while reducing administrative effort.
Rather than maintaining hundreds of separate configuration files, shared settings can be applied to entire groups. When requirements change, administrators only need to update the group configuration instead of every individual endpoint. This centralized approach is especially valuable in enterprise environments where hundreds or thousands of endpoints share similar security requirements.
A poorly tuned deployment can generate thousands of low-value alerts every day, making it difficult to identify genuine threats. Wazuh assigns each rule a severity level based on the potential impact of the detected event. Organizations often customize these severities to better reflect their own risk tolerance and security policies. Critical alerts should receive immediate attention, while informational events may simply be retained for auditing purposes.
Security researchers at the SANS Institute have long emphasized that reducing alert fatigue is one of the most effective ways to improve security operations center performance. Although many organizations rely on dashboards, SIEM integrations, or messaging platforms, email notifications remain an important alerting mechanism for high-priority security events.
Proper configuration ensures that critical alerts reach administrators even when they are not actively monitoring the dashboard. This prevents important notifications from being buried beneath low-priority messages. The Wazuh Dashboard provides access to alerts, endpoint data, threat investigations, and administrative settings.
Because it contains sensitive security information, protecting access should be a top priority. Role-based access control (RBAC) allows organizations to grant permissions based on job responsibilities. The principle of least privilege recommends granting users only the permissions necessary to perform their responsibilities. The Cybersecurity and Infrastructure Security Agency (CISA) identifies least privilege as one of the core practices for reducing the impact of compromised accounts.
File Integrity Monitoring (FIM) is one of Wazuh’s most valuable security capabilities. It continuously monitors files and directories for unauthorized modifications, allowing organizations to quickly identify potential compromises, configuration drift, ransomware activity, or insider threats. Instead of waiting for attackers to execute malicious actions, FIM detects one of the earliest indicators of compromise: unexpected changes to critical files.
Wazuh’s FIM engine, powered by the Syscheck module, periodically scans configured directories and compares file metadata against previously recorded baselines. Many deployments also enable real-time monitoring so changes are detected almost immediately rather than waiting for scheduled scans.
Many regulatory frameworks require organizations to monitor critical system files for unauthorized modifications. FIM helps demonstrate that important operating system files, security configurations, and application binaries are continuously monitored. Although FIM cannot prevent encryption by itself, it can rapidly detect abnormal file modification patterns and generate alerts before an attack spreads further across the environment.
Combined with Active Response, these alerts can trigger automated containment actions. These audit trails simplify troubleshooting, incident response, and compliance reporting. Choosing the right monitoring scope is important. Monitoring every file on every system may generate unnecessary alerts and increase resource consumption.
For a complete step-by-step implementation guide, including recommended exclusions, real-time monitoring, and performance tuning, see: In many situations, organizations also want Wazuh to respond automatically before an attacker can continue exploiting a compromised system.
Active Response enables Wazuh to execute predefined actions whenever specific detection rules are triggered, reducing response times from minutes to seconds. Instead of waiting for an analyst to investigate every alert manually, Wazuh can immediately perform defensive actions based on your security policies.
Active Response is particularly valuable for events that require immediate containment. Automating these responses helps reduce attacker dwell time while allowing analysts to focus on investigation rather than repetitive manual tasks. Wazuh includes several built-in response scripts while also allowing organizations to create their own custom actions.
Many organizations integrate Active Response with external security tools to build more comprehensive incident response pipelines. Although automation provides significant security benefits, it should be introduced carefully. Security experts generally recommend starting with monitoring mode before gradually enabling automated enforcement for trusted detection rules.
For a complete implementation guide covering configuration, supported commands, custom scripts, and deployment recommendations, continue with: Alerts, endpoint inventories, vulnerability findings, File Integrity Monitoring events, authentication logs, and application logs quickly accumulate, especially in medium and large environments.
Without a well-planned log retention strategy, storage costs can grow rapidly, searches may become less efficient, and important forensic evidence may be lost. Log retention is the practice of determining how long security events should be stored before they are archived or deleted. The ideal retention period depends on your organization’s regulatory requirements, operational needs, storage capacity, and incident response objectives.
Many security and privacy frameworks require organizations to retain security logs for defined periods. The required retention period varies depending on the regulation and industry, making it important to understand the requirements that apply to your organization. Proper retention planning helps maintain predictable storage utilization as your environment expands.
Attackers may remain inside an environment for weeks or even months before being discovered. Historical logs often provide the evidence needed to reconstruct attack timelines, identify affected systems, and understand the scope of a compromise. Maintaining sufficient log history simplifies these activities while demonstrating mature security operations.
Instead, most deployments adopt tiered retention policies based on business requirements. Many organizations also retain different categories of logs for different lengths of time. For example, authentication logs may be stored longer than low-priority informational events because they provide greater investigative value.
Planning ahead helps prevent expensive storage upgrades while ensuring that critical security data remains available when needed. The National Institute of Standards and Technology (NIST) recommends establishing formal log retention policies as part of an organization’s broader logging and incident response strategy, ensuring that security events remain available for monitoring, investigations, and compliance activities.
For a complete walkthrough covering index lifecycle management, retention policies, storage optimization, and configuration examples, continue with: Firewalls, routers, switches, load balancers, storage appliances, printers, and numerous network devices generate security logs exclusively through the Syslog protocol.
By configuring Wazuh as a centralized Syslog server, these devices can forward their logs to a single location where they are analyzed alongside endpoint telemetry. This provides significantly better visibility across the entire infrastructure while reducing the complexity of monitoring multiple independent logging systems.
Centralized Syslog collection is often one of the first capabilities organizations enable after deploying Wazuh. Syslog is a standardized protocol supported by thousands of operating systems, security appliances, and enterprise applications. Once configured, devices transmit messages to the Wazuh manager over the network, where they are: This allows Wazuh to correlate events from multiple sources rather than analyzing each device independently.
Many organizations also configure cloud services and virtualization platforms to forward Syslog events into Wazuh. In smaller deployments, devices often send Syslog messages directly to the Wazuh manager. This architecture is simple to deploy and works well for organizations with relatively low log volume. Larger environments frequently introduce dedicated Syslog collectors or load balancers before forwarding logs to Wazuh.
Some organizations also separate external-facing network devices from internal infrastructure by using multiple Syslog collection tiers. Aggregating infrastructure logs into a single platform provides several operational advantages: When combined with custom detection rules and threat intelligence integrations, centralized Syslog becomes a powerful source of actionable security intelligence.
For detailed configuration steps, supported architectures, network requirements, and troubleshooting guidance, see: Wazuh includes thousands of built-in detection rules covering common operating systems, applications, and attack techniques. While these default rules provide excellent baseline coverage, every organization has unique infrastructure, business applications, security policies, and operational requirements.
Custom detection rules allow administrators to extend Wazuh beyond its default capabilities by creating alerts tailored specifically to their environment. 5. Performance Evaluation & Extended Technical Observations Rather than relying solely on generic detections, organizations can identify suspicious behaviors that are meaningful within their own networks.
Custom rules enable Wazuh to recognize these events and generate actionable alerts that would otherwise be ignored. This layered approach preserves the value of the default rules while adapting them to local operational needs. Many organizations also write custom rules to support regulatory compliance reporting and internal security audits. Testing before deployment is especially important because poorly written rules can generate excessive alerts or miss genuine attacks.
Experts from MITRE encourage organizations to continuously evolve detections as attackers adopt new techniques, using frameworks such as ATT&CK to identify gaps in defensive coverage. For a complete tutorial covering rule syntax, XML structure, matching conditions, practical examples, testing, and troubleshooting, continue with: Even a small mistake in rule syntax, decoder logic, or matching conditions can prevent alerts from triggering or generate excessive false positives that overwhelm analysts.
It also helps confirm that logs are being decoded correctly, the appropriate fields are available, and the resulting alerts match your organization’s expectations. Treating rule testing as a mandatory step in your deployment workflow significantly improves detection quality while reducing operational risk.
Testing before deployment allows administrators to identify these issues early when they are much easier to fix. Many mature security teams follow a detection engineering workflow in which every new or modified rule is tested before being approved for production. This interactive tool allows administrators to submit sample log entries and observe each stage of processing, including: Because it simulates the manager’s rule engine, wazuh-logtest is usually the fastest way to troubleshoot detection logic.
Large organizations frequently maintain staging environments that closely resemble production. If the incoming log was parsed incorrectly, or not parsed at all, the rule may never execute. Organizations such as MITRE encourage continuously improving detections as adversaries evolve their techniques rather than relying solely on static rule sets.
For detailed examples of testing custom rules, interpreting wazuh-logtest output, and troubleshooting failed matches, continue with: Once the core components of Wazuh have been configured, organizations can begin implementing more advanced capabilities that improve scalability, automation, integrations, and operational efficiency.
Many of these settings become increasingly valuable as deployments grow beyond a few dozen endpoints. Large deployments often contain multiple server roles, operating systems, business units, and geographical locations. Rather than managing every endpoint individually, administrators can use agent groups to apply consistent policies across entire categories of systems.
Labels provide additional context that makes searching, filtering, and reporting much easier. This metadata allows analysts to quickly isolate affected systems during investigations. Single-node deployments work well for smaller organizations, but enterprise environments often require clustering to improve scalability and resilience.
Proper cluster design improves uptime while supporting thousands of monitored endpoints. Because remote command execution introduces additional risk, organizations should enable it only when necessary and restrict usage through strong access controls. Wazuh becomes significantly more powerful when integrated with other security platforms.
Deliver security notifications into collaboration channels where analysts already work. Use API tokens or other supported authentication mechanisms instead of embedding administrator credentials within automation scripts. Follow role-based access principles by granting applications only the permissions they require.
As deployments expand, optimizing detection performance becomes increasingly important. Fine-tuning rules improves alert quality by suppressing known benign activity while preserving meaningful detections. The Open Worldwide Application Security Project (OWASP) recommends continuously tuning security monitoring systems to improve signal quality while minimizing operational overhead.
Even experienced administrators occasionally make configuration mistakes that reduce detection quality, introduce unnecessary downtime, or complicate troubleshooting. Understanding these common pitfalls can help you build a more stable and maintainable Wazuh deployment. Although this may seem convenient, updates can overwrite these changes during upgrades.
Failure to do so often leads administrators to believe their configuration is incorrect when the new settings simply have not been loaded. Small syntax errors, especially within XML files, can prevent services from starting correctly. Taking a few extra minutes to verify syntax can prevent lengthy troubleshooting sessions later.
Making untested configuration changes directly on production systems increases operational risk. Automated remediation can dramatically reduce response times, but excessive automation can also disrupt legitimate business activity. Organizing systems by role, operating system, or business function simplifies long-term administration.
Regularly reviewing log coverage helps ensure that important security events are not overlooked. The Center for Internet Security (CIS) emphasizes maintaining complete and accurate log collection as a foundational cybersecurity control because organizations cannot detect threats that are never recorded. Because Wazuh is highly configurable and tightly integrated across multiple components, even small changes can impact log ingestion, alert generation, or system stability.
Planning reduces accidental misconfigurations and helps ensure that changes align with security objectives. Backups allow you to quickly restore a working state if a change causes service disruption or unexpected behavior. Wazuh relies heavily on XML-based configuration files. Even minor syntax errors can prevent services from starting or cause silent misconfigurations.
After applying and validating configuration changes, restart the affected Wazuh services. Monitoring ensures that configuration changes do not introduce unintended side effects. Before considering a Wazuh deployment production-ready, verify that all critical configuration areas are properly implemented and tested.
Confirm that all expected agents are connected to the manager and reporting correctly. Ensure custom detection rules have been tested and do not generate excessive false positives. Ensure all network devices, firewalls, and external systems are forwarding logs correctly. Confirm retention policies are properly defined and aligned with compliance requirements.
Check that alerts are meaningful, properly categorized, and not generating excessive noise. Wazuh configuration files are typically located under the /var/ossec/etc/ directory on Linux systems. Key files include ossec.conf , rule files, and decoder files. Agent configurations are also stored locally on each endpoint. Yes. Most configuration changes require restarting or reloading the affected services, such as the Wazuh manager, agents, or related components, for changes to take effect.
Yes. Wazuh supports centralized configuration management using agent groups. This allows you to apply consistent settings across multiple endpoints without manually configuring each one. No. Default rules should not be modified. Instead, create custom rules in local rule files to ensure changes are preserved during upgrades.
You can validate configuration files using XML validation tools and Wazuh’s built-in testing utilities. Always validate before restarting services to avoid startup failures. This usually occurs when services have not been restarted after changes, or when configuration files contain syntax errors that prevent proper loading.
Some configurations can be managed through the Wazuh dashboard or APIs, but advanced configuration still typically requires direct XML file editing. Configuration should be reviewed regularly, typically during system upgrades, infrastructure changes, or when tuning detection rules and log sources. Many organizations also perform quarterly audits.
Proper Wazuh configuration is the foundation of an effective security monitoring and detection system. While installation gets the platform running, configuration determines how well it performs in real-world conditions. Wazuh becomes significantly more powerful when configured correctly, transforming it from a basic monitoring tool into a full-scale security operations platform.
To continue building your deployment, explore the detailed cluster guides linked throughout this pillar page for step-by-step configuration instructions across all major Wazuh components. Stable version: 4.14.8 Level: Beginner → Intermediate Last verified: 11 October 2026 Primary lab OS: Ubuntu 24.04 LTS This course teaches you how to use Wazuh from scratch, including deployment, endpoint monitoring, threat detection, vulnerability assessment, incident investigation, and security automation.
The tutorials are built around a single working lab, so you progressively develop a functional security monitoring environment rather than completing unrelated demonstrations. Version verification: Wazuh 4.14.8 was released on September 23, 2026, and is the latest stable release verified in the official release listings. Wazuh 5.0 remains in beta, so this guide uses the stable 4.x architecture and commands.
The 3-hour schedule is an accelerated practical lesson. Completing every optional cross-platform installation, deeper exercise, and troubleshooting scenario in this reference guide will require additional study time. Wazuh officially recommends the server resources shown above for its all-in-one quickstart deployment with 1–25 agents. These are example private network addresses, not addresses discovered on your equipment. Replace them with your actual lab addresses.
Wazuh is an open-source security monitoring platform combining two important security disciplines: Collects, analyzes, stores, and correlates security events from multiple systems, helping security teams identify suspicious activity. Combines security telemetry from different environments to help detect, investigate, and respond to potential threats.
For example, imagine an organization has 100 Linux servers, 50 Windows systems, and multiple cloud workloads. Without a centralized security monitoring system, administrators would need to inspect different machines and logs separately. The server may record unsuccessful authentication attempts in system logs, but an administrator might not notice those entries immediately.
Wazuh can collect authentication events, analyze them against predefined security rules, and create alerts for suspicious authentication activity. Notice that Wazuh does not automatically prevent every threat. Detection depends on available telemetry, enabled monitoring capabilities, rules, configuration, and any response mechanisms you deliberately configure.
Tools such as Prometheus and Datadog can also collect logs and offer security capabilities, but traditional infrastructure monitoring and security investigation have different primary objectives. A practical DevSecOps architecture can use Falco for runtime threat detection and Wazuh for centralized investigation and other security capabilities.
Wazuh is not a complete replacement for antivirus, endpoint prevention, vulnerability remediation tools, firewalls, or human incident response. It cannot reliably detect activity it has no visibility into, and a generated alert does not necessarily prove that a security incident occurred.
Practical exercise: Identify three events on a Linux server that security monitoring should detect, such as repeated login failures, unexpected configuration modifications, and a vulnerable software package. A: No. Its primary purpose is security monitoring, detection, investigation, and response. A: No. Wazuh provides visibility and controls, but the operating system, network, applications, and security processes still require appropriate hardening.
The availability of specific files depends on the Linux distribution and logging services installed. For example, a minimal Ubuntu installation may use journald without providing a traditional /var/log/auth.log . Expected result: You should see timestamped system or SSH events if those services have produced journal records. A single failed login can be normal. Repeated failures, multiple targeted accounts, or suspicious source behavior may warrant investigation.
Wazuh rules can include MITRE ATT&CK mappings to provide additional investigation context. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Security%20information%20and%20event%20management • https://documentation.wazuh.com/current/getting-started/index.html • https://documentation.wazuh.com/current/user-manual/index.html • https://softstrix.com/the-complete-wazuh-installation-and-deployment-guide/ • https://objectfirst.com/blog/siem-series-wazuh/ • https://wazuh.com/platform/siem/ • https://softstrix.com/the-ultimate-wazuh-configuration-guide/ • https://www.devopsschool.com/tutorials/wazuh-the-complete-tutorial/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Security Information And Event Management Tool Using Wazuh.
[*] Metasploit Scan Running on Target Subnet for Security Information And Event Management Tool Using Wazuh... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |