Complete Technical Paper Content — Serverless Application Vulnerability Testing Tool Aws Lambda
Overview & System Context
Serverless Application Vulnerability Testing Tool Aws Lambda: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9521 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Serverless computing is "a cloud service category where the customer can use different cloud capability types without the customer having to provision, deploy and manage either hardware or software resources, other than providing customer application code or providing customer data. Serverless computing represents a form of virtualized computing", according to ISO/IEC 22123-2. Serverless computing is a broad ecosystem that includes the cloud provider, function as a service (FaaS), managed services, tools, frameworks, engineers, stakeholders, and other interconnected elements.
Google Cloud is a suite of cloud computing services offered by Google that provides a series of modular cloud services including computing, data storage, data analytics, and machine learning, alongside a set of management tools. It runs on the same infrastructure that Google uses internally for its end-user products, such as Google Search, Gmail, and Google Docs, according to Verma et al. Registration requires a credit card or bank account details. Google Cloud provides infrastructure as a service, platform as a service, and serverless computing environments. In April 2008, Google announced App Engine, a platform for developing and hosting web applications in Google-managed data centers, which was the first cloud computing service from the company. The service became generally available in November 2011. Since the announcement of App Engine, Google added multiple cloud services to the platform. Google Cloud includes Google Cloud public cloud infrastructure, as well as Google Workspace (G Suite), enterprise versions of Android and ChromeOS, and application programming interfaces (APIs) for machine learning and enterprise mapping services. Since at least 2022, Google's official materials have stated that "Google Cloud" is the new name for "Google Cloud Platform," which may cause naming confusion.
For those familiar with other notable cloud service providers, a comparison of similar services may be helpful in understanding Google Cloud Platform's offerings. April 2008 – Google App Engine announced in preview May 2010 – Google Cloud Storage launched May 2010 – Google BigQuery and Prediction API announced in preview October 2011 – Google Cloud SQL is announced in preview June 2012 – Google Compute Engine is launched in preview May 2013 – Google Compute Engine is released to GA August 2013 – Cloud Storage begins automatically encrypting each Storage object's data and metadata under the 128-bit Advanced Encryption Standard (AES-128), and each encryption key is itself encrypted with a regularly rotated set of master keys February 2014 – Google Cloud SQL becomes GA May 2014 – Stackdriver is acquired by Google June 2014 – Kubernetes is announced as an open source container manager June 2014 – Cloud Dataflow is announced in preview October 2014 – Google acquires Firebase November 2014 – Alpha release Google Kubernetes Engine (formerly Container Engine) is announced January 2015 – Google Cloud Monitoring based on Stackdriver goes into Beta March 2015 – Google Cloud Pub/Sub becomes available in Beta April 2015 – Google Cloud DNS becomes generally available April 2015 – Google Dataflow launched in beta July 2015 – Google releases v1 of Kubernetes; Hands it over to The Cloud Native Computing Foundation August 2015 – Google Cloud Dataflow, Google Cloud Pub/Sub, Google Kubernetes Engine, and Deployment Manager graduate to GA November 2015 – Bebop is acquired, and Diane Greene joins Google February 2016 – Google Cloud Functions becomes available in Alpha September 2016 – Apigee, a provider of application programming interface (API) management company, is acquired by Google September 2016 – Stackdriver becomes generally available November 2016 – Qwiklabs, an EdTech company is acquired by Google February 2017 – Cloud Spanner, highly available, globally-distributed database is released into Beta March 2017 – Google acquires Kaggle, world's largest community of data scientists and machine learning enthusiasts April 2017 – MIT professor Andrew Sutherland breaks the record for the largest ever Compute Engine cluster with 220,000 cores on Preemptible VMs. May 2017 – Google Cloud IoT Core is launched in Beta November 2017 – Google Kubernetes Engine gets certified by the CNCF February 2018 – Google Cloud IoT Core becomes generally available February 2018 – Google announces its intent to acquire Xively February 2018 – Cloud TPUs, ML accelerators for Tensorflow, become available in Beta May 2018 – Google Cloud Memorystore becomes available in Beta April 2019 – Google Cloud Run (fully managed) Beta release April 2019 – Google Anthos announced November 2019 – Google Cloud Run (fully managed) General availability release March 2020 – Due to the COVID-19 pandemic, Google Cloud postponed the online streaming version of its Google Cloud Next mega-conference, two weeks after it canceled the in-person version. October 2020 – Google Cloud announced that it will become a block producer candidate for the EOS network and EOS.IO protocol. Currently the top block producers are cryptocurrency exchanges like OKEx and Binance. February 2021 – Google Kubernetes Engine Autopilot is introduced. May 2021 – Vertex AI announced at Google.io June 2021 – In 2021, Apple was Google Cloud's biggest customer. April 2022 – MobiledgeX acquired and joins Google Cloud. March 2023 – Google brings generative AI capabilities to Google Cloud. May 2024 Google Cloud partnered with Airtel. April 2025 – At Google Cloud Next 2025 in Las Vegas, Google announced the seventh-generation Tensor Processing Unit, named Ironwood, claiming 3,600 times better performance than its first publicly available TPU. Google also announced Cloud Wide Area Network (Cloud WAN), making its private global network available to enterprise customers, and introduced Gemini 2.5 and Gemini 2.5 Flash reasoning models.
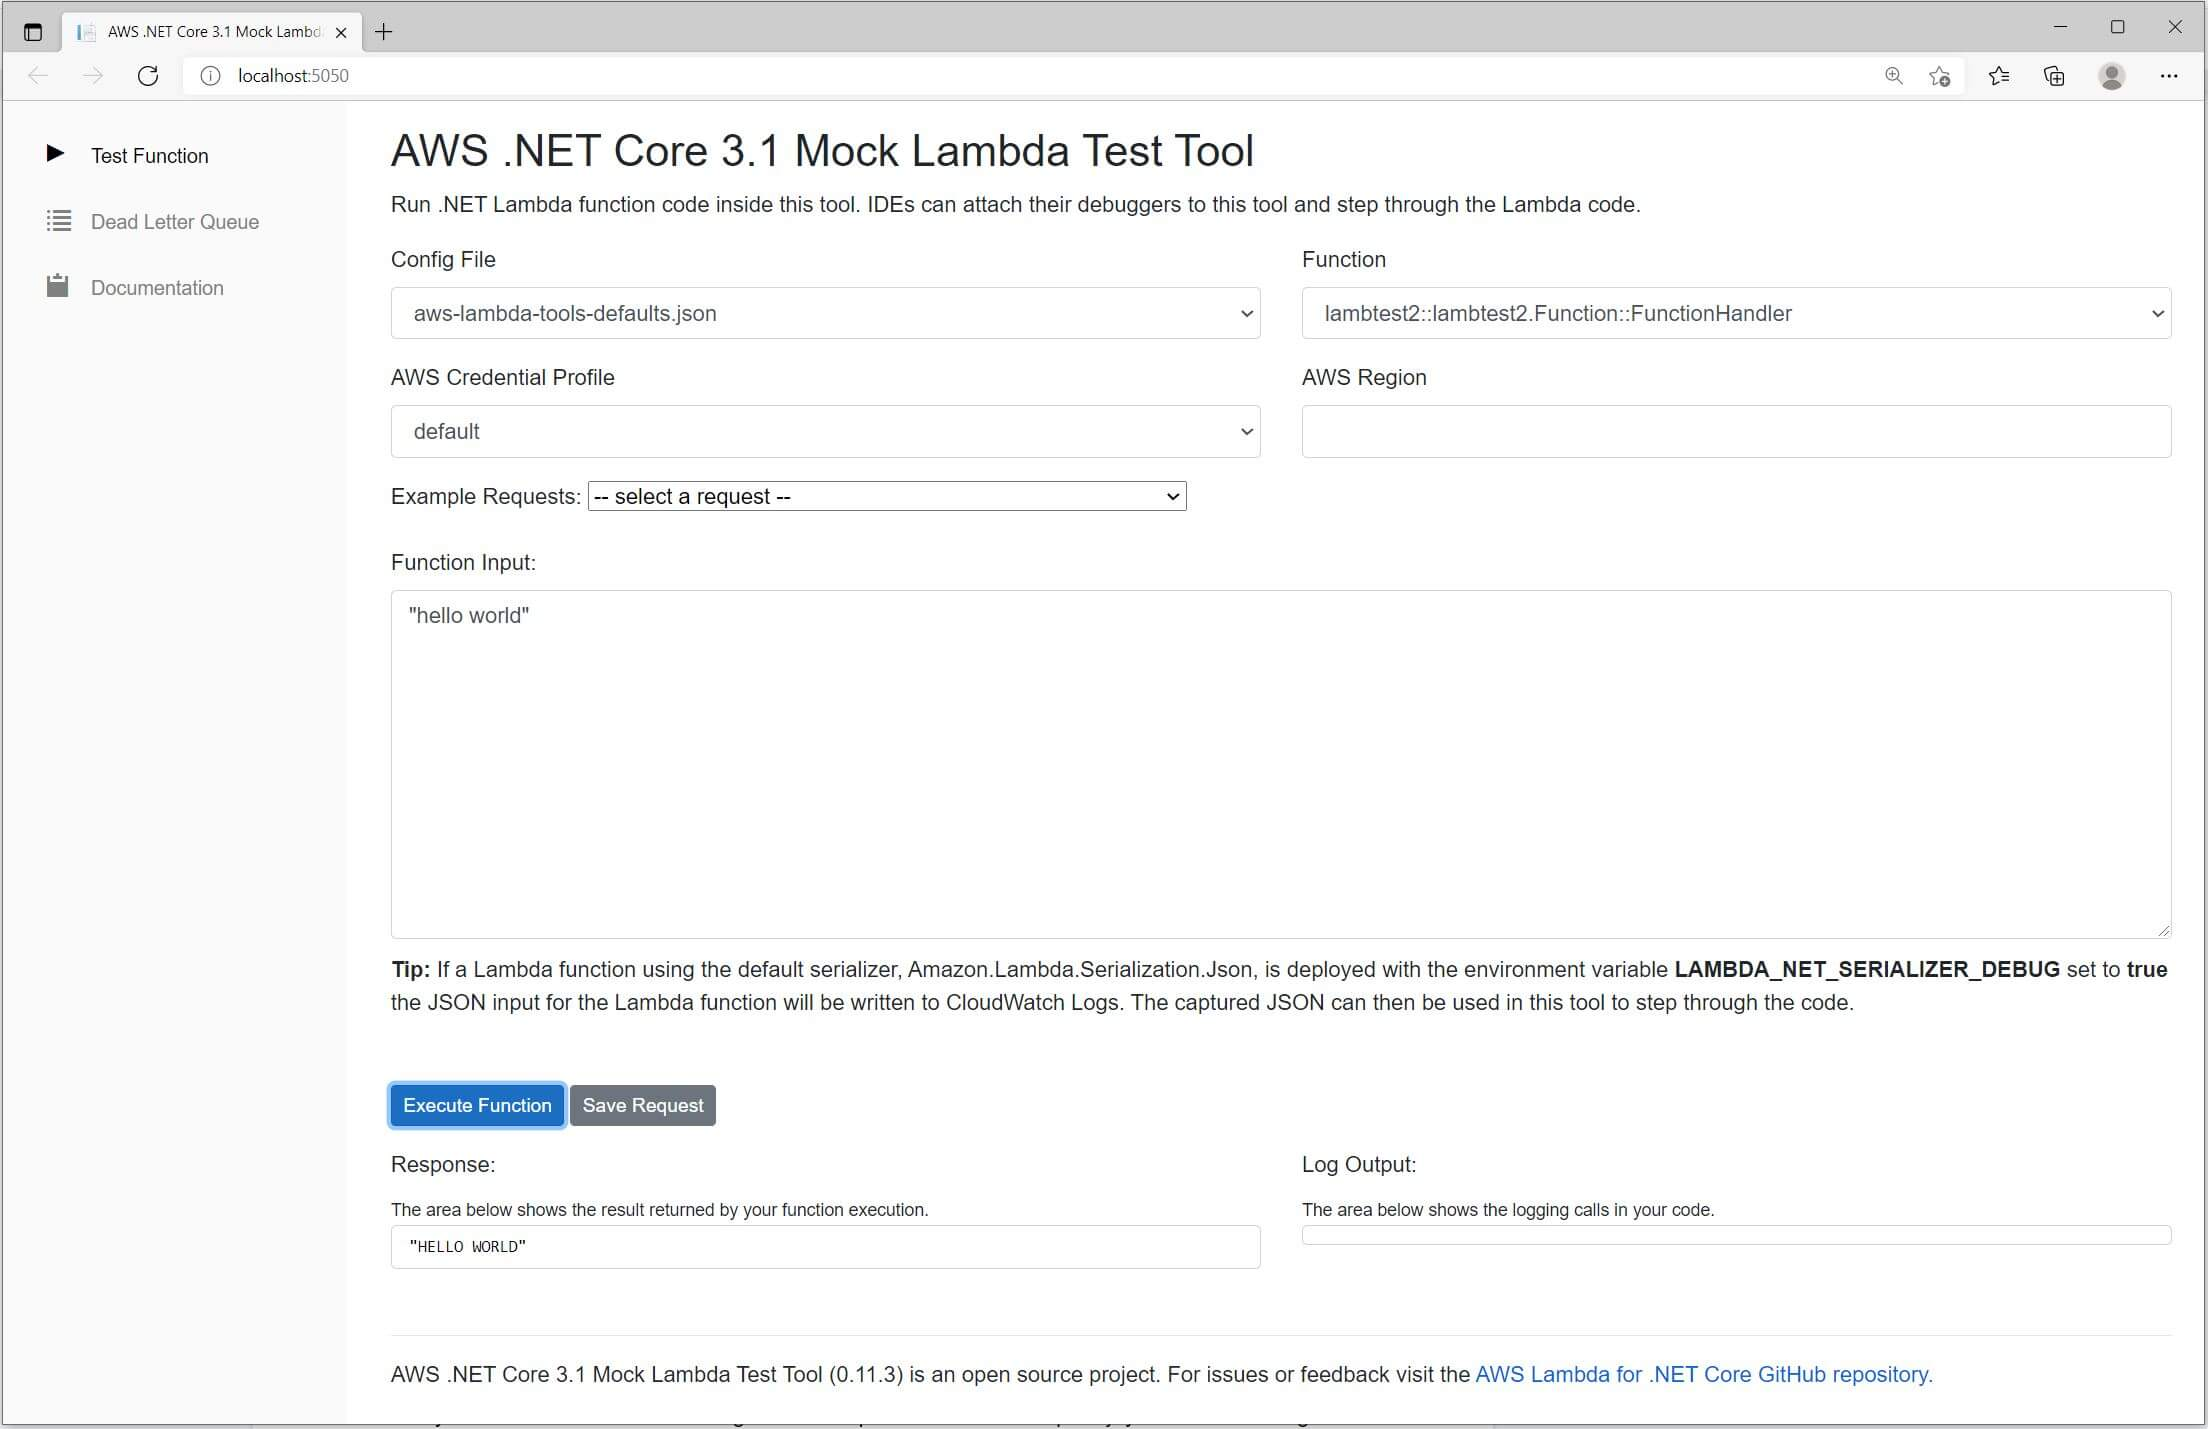
April 2026 – At Google Cloud Next '26, Sundar Pichai announced expanded AI infrastructure investments, including the introduction of Trillium TPUs (8th generation) and the Gemini Enterprise Agent Platform, with Google reporting that 75% of new internal code was AI-generated. Figure 1: Building Serverless Web App Blazor Chart—AWS Lambda Function Testing serverless functions uses traditional test types and techniques, but you must also consider testing serverless applications as a whole. Cloud-based tests provide the most accurate measure of quality of both your functions and serverless applications.
A serverless application architecture includes managed services that provide critical application functionality through API calls. For this reason, your development cycle should include automated tests that verify functionality when your function and services interact. If you do not create cloud-based tests, you could encounter issues due to differences between your local environment and the deployed environment. Your continuous integration process should run tests against a suite of resources provisioned in the cloud before promoting your code to the next deployment environment, such as QA, Staging, or Production.
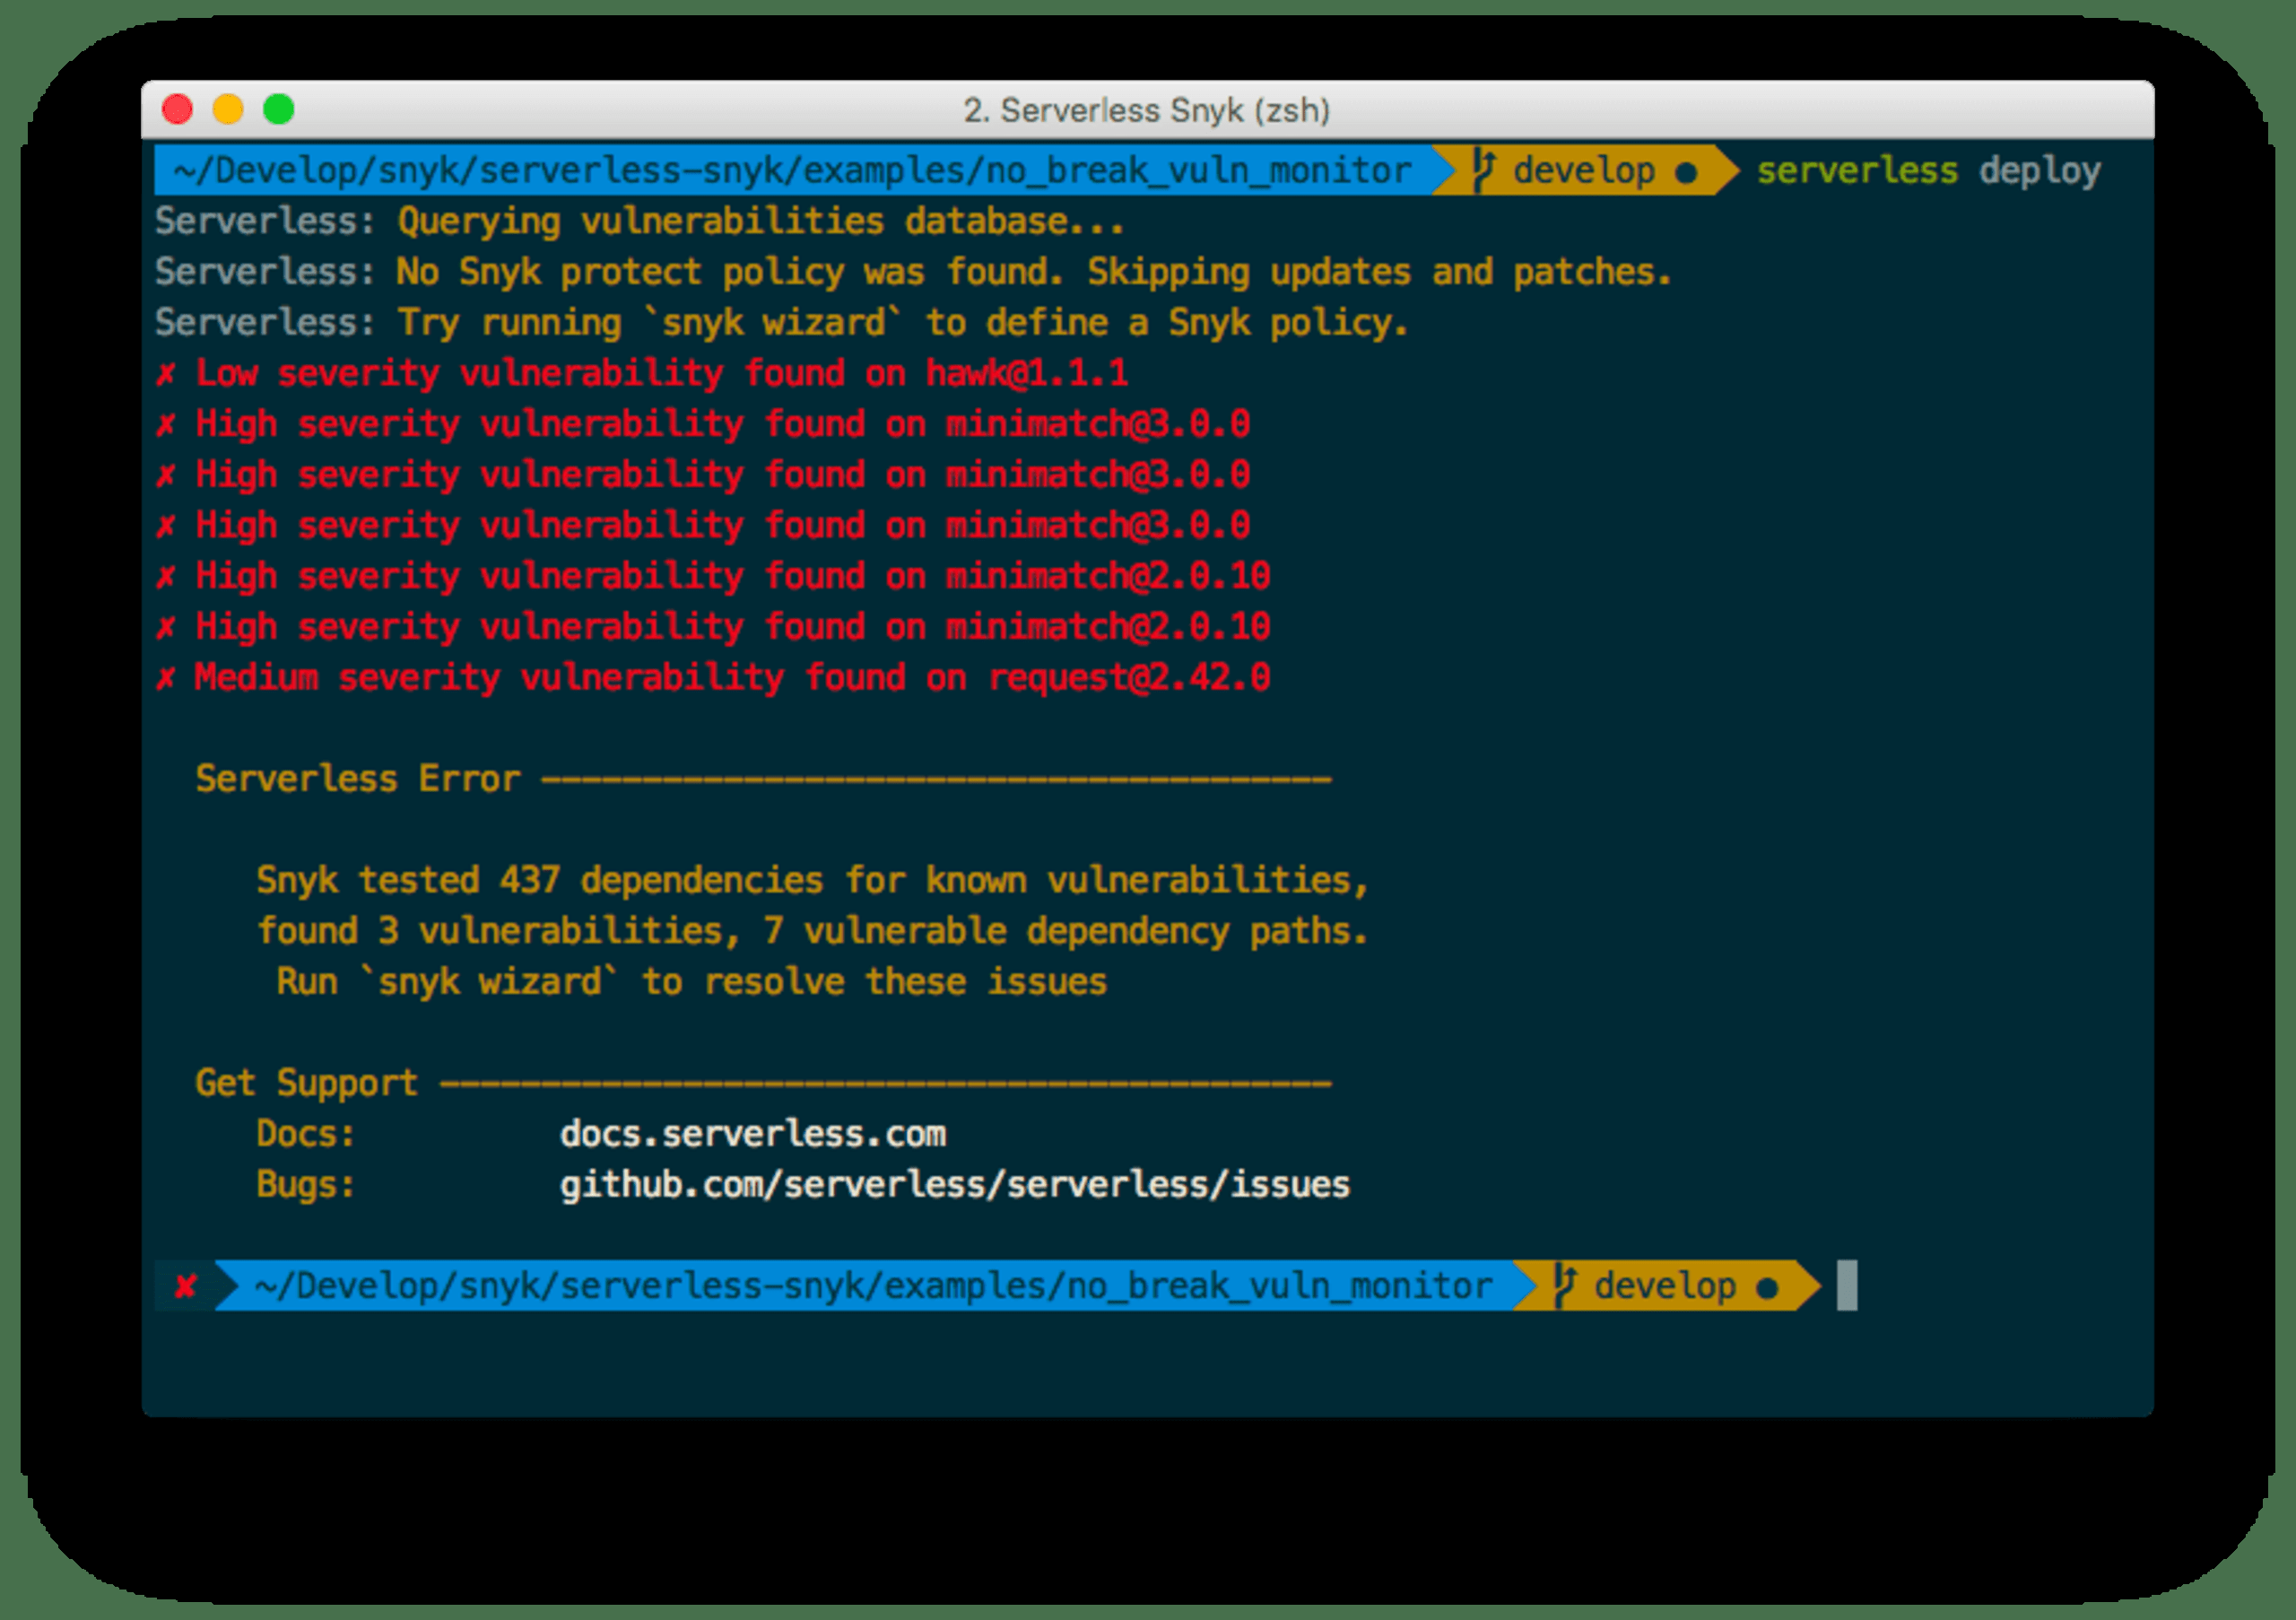
Continue reading this short guide to learn about testing strategies for serverless applications, or visit the Serverless Test Samples repository to dive in with practical examples, specific to your chosen language and runtime. Figure 2: Serverless is great, but what about the security of my AWS Lambda ... Unit tests - Tests that run against an isolated block of code. For example, verifying the business logic to calculate the delivery charge given a particular item and destination.
Integration tests - Tests involving two or more components or services that interact, typically in a cloud environment. For example, verifying a function processes events from a queue. End-to-end tests - Tests that verify behavior across an entire application. For example, ensuring infrastructure is set up correctly and that events flow between services as expected to record a customer's order.
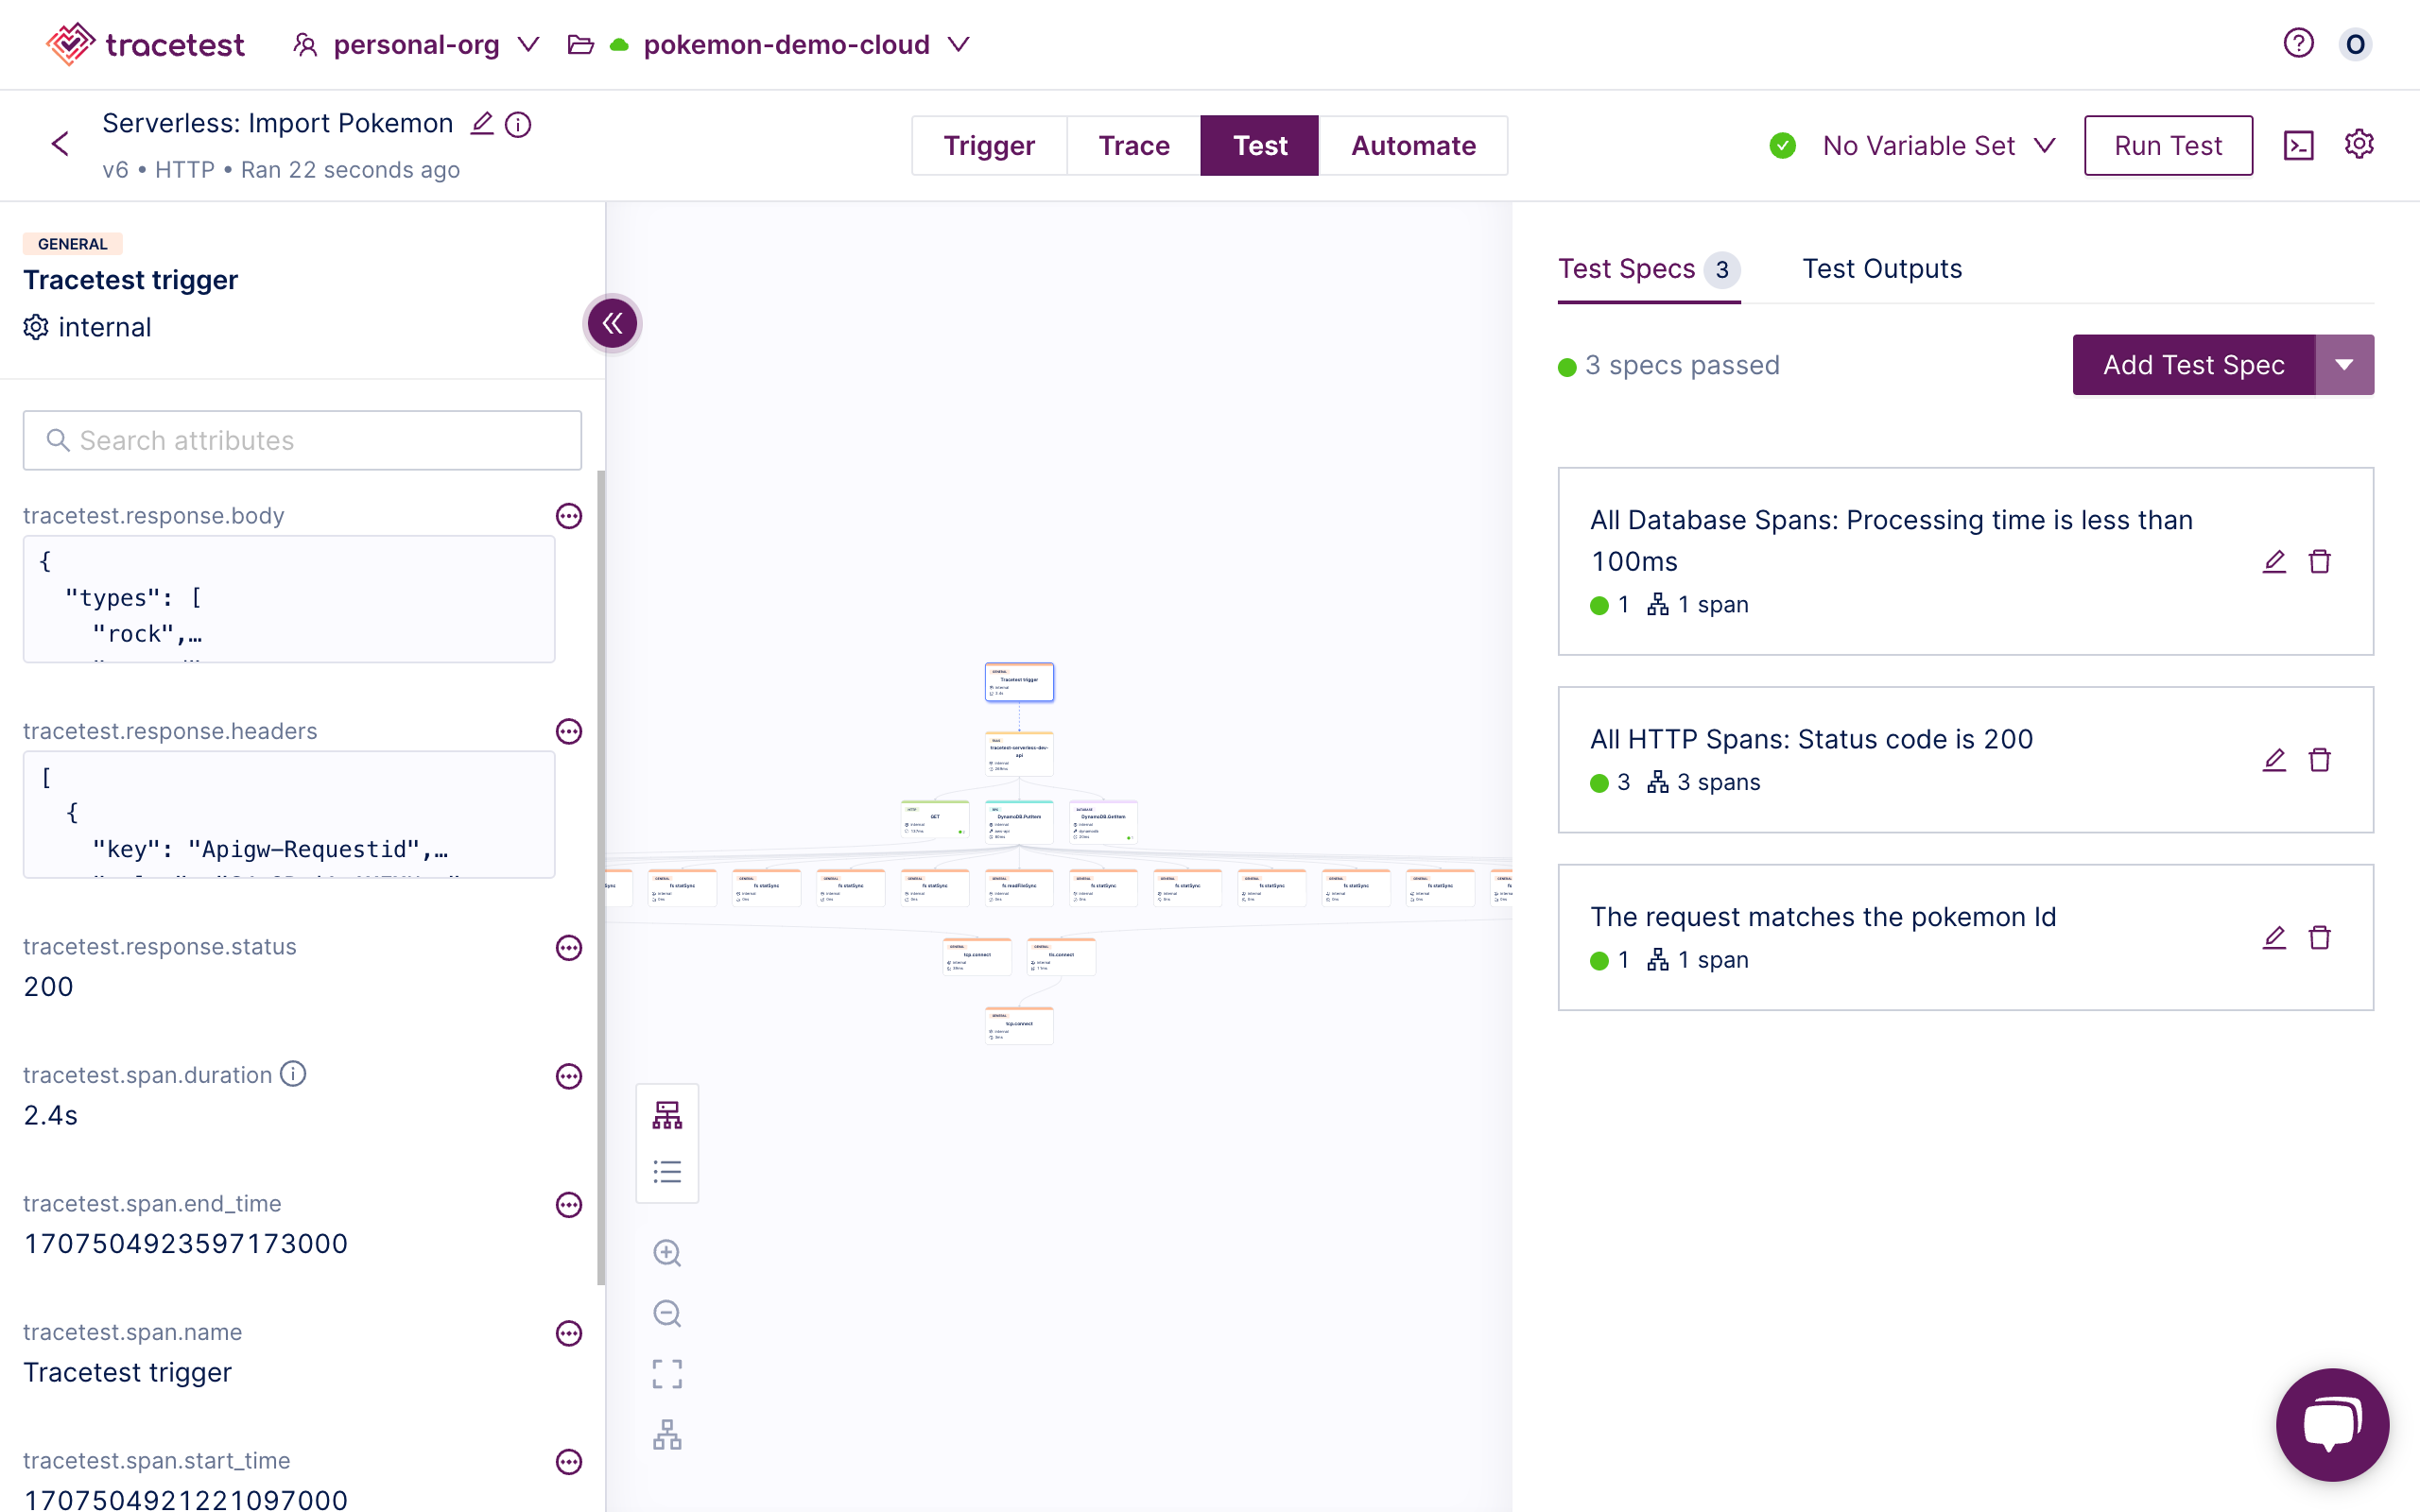
Testing serverless solutions might take more time to set up. You must verify event-driven interactions between services. Keep these practical business reasons in mind as you read this guide: Figure 3: Testing AWS Lambda Functions (Serverless Framework) with OpenTelemetry ... The quality of an application depends on testing many scenarios. Consider your business scenarios and automate tests to run against cloud services. This raises the quality of your application.
Bugs and configuration problems cost less when caught early in the development cycle. Issues that go undetected until production take more effort and more people to fix. A good serverless testing strategy improves software quality and speeds up iterations. It verifies that your Lambda Event Functions and applications work as expected in the cloud.
We recommend a testing strategy that tests managed service behaviors , cloud configuration, security policies, and integration with your code. Behavior testing , also known as black box testing, verifies that a system works as expected without knowing the internals. In traditional server-based architecture, teams often test only the code that runs on the application server. They consider other components, services, or dependencies as external and out of scope.
Serverless applications consist of small units of work. Examples include Lambda functions that retrieve products from a database, process items from a queue, or resize an image in storage. Each component runs in its own environment. Teams manage many of these small units within a single application. Some functionality can be handled entirely by managed services such as Amazon S3, or built without custom code. You don't need to test these managed services. However, you must test how your code integrates with them.
You probably know how to test applications deployed locally. You write tests against code on your desktop or inside containers. For example, you might call a local web service and then check the response. Serverless solutions use your function code and cloud-based managed services, such as queues, databases, event buses, and messaging systems. These components connect through an event-driven architecture , where messages, called events , flow from one resource to another. Some interactions are synchronous, like a web service that returns results right away.
Others are asynchronous, like placing items in a queue or starting a workflow step. Your testing strategy must cover both types and test the interactions between services. For asynchronous interactions, you might need to detect side effects in downstream components that aren't immediately visible. You cannot fully replicate a cloud environment locally. This includes queues, database tables, event buses, and security policies. Differences between local and cloud environments cause issues. These differences increase the time to reproduce and fix bugs.
In serverless applications, components exist entirely in the cloud. Testing against cloud code and services is needed to develop features and fix bugs. Your testing strategy likely includes a mix of techniques. You use quick interactive tests to debug functions in the console. You write automated unit tests to check business logic. You verify calls to external services with mocks. You might also test against emulators that mimic a service.
Testing in the cloud : You deploy infrastructure and code to test with actual services, security policies, and configurations. Cloud-based tests provide the most accurate measure of your code quality. Debugging a function in the console is a quick way to test in the cloud. You can choose from sample test events or create a custom event. You can also share test events with your team through the console.
To automate testing in the development and build lifecycle, test outside of the console. See the language-specific testing sections in this guide for automation strategies. Testing with mocks : Mocks are objects in your code that simulate an external service. They provide pre-defined behavior to verify service calls and parameters. A fake is a mock that takes shortcuts to simplify or speed up testing. For example, a fake data access object might return data from an in-memory datastore. Mocks can simplify complex dependencies, but might lead to more mocks to replace nested dependencies.
Testing locally using AWS SAMÂ CLI : Use AWS SAM CLI to locally invoke Lambda functions in Docker containers that use the same runtime environment as AWS Lambda. You can test function logic and event processing without deploying to the cloud. Testing with emulation : Use the LocalStack integration in VS Code to emulate multiple AWS services locally for testing service integrations.
Testing in the cloud is valuable for all phases of testing: unit tests, integration tests, and end-to-end tests. Tests that run against cloud-based code and services give the most accurate measure of your code quality. A simple way to run a Lambda function in the cloud is with a test event in the AWS Management Console. A test event is a JSON input to your function. If your function needs no input, the event can be an empty JSON document ( { }) . The console provides sample events for many service integrations. You can share events with your team to make testing easier.
Although running functions in the console is a quick way to debug, automating your test cycles is essential to increase application quality and development speed. Test automation samples are available in the Serverless Test Samples repository . The following command line runs an automated Python integration test example : Although the test runs locally, it talks to cloud-based resources. These resources were deployed using the AWS Serverless Application Model and AWS SAM command line tool. The test code first retrieves the deployed stack outputs, such as the API endpoint, function ARN, and security role.
Then, it sends a request to the API endpoint. The response contains a list of Amazon S3 buckets. This test runs against cloud-based resources to verify they are deployed, secured, and working. For cloud-native application development, testing in the cloud provides the following benefits: Tests can cover security policies, service quotas, configurations and infrastructure specific parameters.
Testing in the cloud does have some downsides. Cloud deployments typically take longer than local desktop deployments. Tools such as AWS Serverless Application Model (AWS SAM) Accelerate , AWS Cloud Development Kit (AWS CDK) watch mode , and SST (3rd party) reduce this latency. These tools monitor your infrastructure and code, then deploy updates to your cloud environment automatically.
See how to create infrastructure as code in the Serverless Developer Guide to learn more about AWS Serverless Application Model, CloudFormation, and AWS Cloud Development Kit (AWS CDK). Unlike local testing, cloud testing uses resources that might incur costs. Isolated testing environments might add work for your DevOps teams, especially in organizations with strict account controls. Even so, the developer time to set up a complex local environment can cost more than using disposable cloud environments built with Infrastructure as Code tools.
Testing in the cloud, even with these considerations, is still the best way to guarantee the quality of your serverless solutions. Testing with mocks is a technique where you create replacement objects in your code to simulate the behavior of a cloud service. For example, you could write a test that uses a mock of the Amazon S3 service. The mock returns a set response whenever the CreateObject method is called. It does not call Amazon S3 or any other service endpoints.
Mock frameworks often generate mock objects for you. Some frameworks are generic. Others target AWS SDKs, such as Moto , a Python library for mocking AWS services. Mock objects differ from emulators. Developers create mocks as part of the test code. Emulators are standalone applications that expose the same functionality as the systems they mimic.
Mocks can simulate third-party services that are beyond the control of your application, such as APIs and software as a service (SaaS) providers, without needing direct access to those services. Mocks are useful for testing failure conditions, especially when such conditions are hard to simulate, like a service outage. 2. System Architecture & Core Working Principles Mocks can provide substitute behavior for virtually any kind of object, so mocking strategies can create coverage for a wider variety of services than emulators.
When new features or behaviors become available, mock testing can react more quickly. By using a generic mock framework, you can simulate new features as soon as the updated AWS SDK become available. Mocks generally require a non-trivial amount of setup and configuration effort, specifically when trying to determine return values from different services to properly mock responses.
Mocks are written, configured, and must be maintained by developers, increasing their responsibilities. You might need to have access to the cloud to understand the APIs and return values of services. Mocks can be difficult to maintain. When mocked cloud API signatures change, or return value schemas evolve, you need to update your mocks. Mocks also require updates if you extend your application logic to make calls to new APIs.
Tests that use mocks might pass in desktop environments but fail in the cloud. Results might not match the current API. Service configuration and quotas cannot be tested. Mock frameworks are limited in testing or detecting AWS Identity and Access Management (IAM) policy or quota limitations. Although mocks are better at simulating when authorization fails or a quota is exceeded, testing cannot determine which outcome actually occurs in a production environment.
Use AWS SAMÂ CLI to test your functions in Docker containers using the same runtime environment as AWS Lambda. You can test function logic and event processing locally without deploying to the cloud. If your function makes API calls to other AWS services, those calls reach real AWS resources. AWS service calls from your function interact with real AWS resources, which might incur costs and affect production data.
Emulators are locally running applications that mimic AWS services by providing similar APIs and return values. LocalStack is a popular emulation tool that provides a complete local development environment for testing service integrations. LocalStack is an AWS Cloud emulator that you can use to test serverless applications locally. You can test Lambda functions that integrate with services like DynamoDB, Amazon S3, and Amazon SQS without connecting to actual AWS services. You can use LocalStack in the AWS Toolkit for VS Code .
Emulators provide a familiar environment for developers used to developing code in a local environment. For example, if you're familiar with the development of an n -tier application, you might have a database engine and web server, similar to those running in production, running on your local machine to provide quick, local, isolated test capability. Emulators do not require any changes to cloud infrastructure (such as developer cloud accounts), so it's easy to implement with existing testing patterns.
Because emulators don't use actual AWS resources, you won't get unexpected charges when starting multiple services or for letting some resources run for extended periods of time. Emulators can be difficult to set up and replicate, especially when used in CI/CD pipelines. This can increase the workload of IT staff or developers who manage their own software.
Emulated features and APIs typically lag behind service updates. This can lead to errors because tested code does not match the actual API, and impede the adoption of new features. Emulators require support, updates, bug fixes, and feature parity enhancements. These are the responsibility of the emulator author, which could be a third-party company.
Tests that rely on emulators might provide successful results locally, but fail in the cloud due to production security policies, inter-service configurations, or exceeding Lambda quotas. The following sections provide recommendations for successful serverless application testing. You can find practical examples of tests and test automation in the Serverless Test Samples repository .
Testing in the cloud provides the most reliable, accurate, and complete test coverage. Performing tests in the context of the cloud comprehensively tests not only business logic but also security policies, service configurations, quotas, and the most up to date API signatures and return values. Simplify your tests and Lambda functions by separating Lambda-specific code from your core business logic.
Your Lambda function handler should be a slim adapter that takes in event data and passes only the details that matter to your business logic method(s). With this strategy, you can wrap comprehensive tests around your business logic without worrying about Lambda-specific details. Your AWS Lambda functions should not require setting up a complex environment or large amount of dependencies to create and initialize the component under test.
Generally speaking, you should write a handler that extracts and validates data from the incoming event and context objects, then sends that input to methods that perform your business logic. There are tools and techniques to accelerate development feedback loops. For example, AWS SAM Accelerate and AWS CDK watch mode both decrease the time required to update cloud environments.
The samples in the GitHub Serverless Test Samples repository explore some of these techniques. We also recommend that you create and test cloud resources as early as possible during developmentâIInot only after a check-in to source control. This practice enables quicker exploration and experimentation when developing solutions. In addition, automating deployment from a development machine helps you discover cloud configuration problems more quickly and reduces wasted effort for updates and code review processes.
When building applications with Lambda, testing components together is a best practice. Tests that run against two or more architectural components are called integration tests . The goal of integration tests is to understand not only how your code executes across components, but how the environment hosting your code behaves. End-to-end tests are special types of integration tests that verify behaviors across an entire application.
To build integration tests, deploy your application to a cloud environment. This can be done from a local environment or through a CI/CD pipeline. Then, write tests to exercise the system under test (SUT) and validate expected behavior. For example, the system under test could be an application that uses API Gateway, Lambda and DynamoDB. A test could make a synthetic HTTP call to an API Gateway endpoint and validate that the response included the expected payload. This test validates that the AWS Lambda code is correct, and that each service is correctly configured to handle the request, including the IAM permissions between them. Further, you could design the test to write records of various sizes to verify your service quotas, such as max record size in DynamoDB, are set up correctly.
Testing in the cloud typically requires isolated developer environments, so that tests, data, and events do not overlap. One approach is to provide each developer a dedicated AWS account. This avoids conflicts with resource naming that can occur when multiple developers working in a shared code base, attempt to deploy resources or invoke an API. Automated test processes should create uniquely named resources for each stack. For example, you can set up scripts or TOML configuration files so that AWS SAM CLI sam deploy or sam sync commands automatically specify a stack with a unique prefix.
In some cases, developers share an AWS account. This might be because of having resources in your stack that are expensive to operate, or to provision and configure. For example, a database might be shared to make it easier to set up and seed the data properly If developers share an account, you should set boundaries to identify ownership and eliminate overlap. One way to do this is by prefixing stack names with developer user IDs. Another popular approach is to set up stacks based on code branches .
With branch boundaries, environments are isolated, but developers can still share resources, such as a relational database. This approach is a best practice when developers work on more than one branch at a time. Testing in the cloud is valuable for all phases of testing, including unit tests, integration tests, and end-to-end tests. Maintaining proper isolation is essential; but you still want your QA environment to resemble your production environment as closely as possible. For this reason, teams add change control processes for QA environments.
For pre-production and production environments, boundaries are typically drawn at the account level to insulate workloads from noisy neighbor problems and implement least privilege security controls to protect sensitive data. Workloads have quotas. You don't want your testing to consume quotas allocated for production (noisy neighbor) or have access to customer data. Load testing is another activity you should isolate from your production stack.
In all cases, environments should be configured with alerts and controls to avoid unnecessary spending. For example, you can limit the type, tier, or size of resources that can be created, and set up email alerts when estimated costs exceed a given threshold. Mock frameworks are a valuable tool for writing fast unit tests. They are especially beneficial when tests cover complex internal business logic, such as mathematical or financial calculations or simulations. Look for unit tests that have a large number of test cases or input variations, where those inputs do not change the pattern or the content of calls to other cloud services.
Code that is covered by unit tests with mocks should also be covered by testing in the cloud. This is recommended because a developer laptop or build machine environment could be configured differently than a production environment in the cloud. For example, your Lambda functions could use more memory or time than allocated when run with certain input parameters. Or your code might include environment variables that are not configured in the same way (or at all), and the differences could cause the code to behave differently or fail.
The benefit of mocks is less for integration tests, because the level of effort to implement the necessary mocks increases with the number of connection points. End-to-end testing should not use mocks, because these tests generally deal with states and complex logic that cannot be easily simulated with mock frameworks. Lastly, avoid using mocked cloud services to validate the proper implementation of service calls. Instead, make cloud service calls in the cloud to validate behavior, configuration, and functional implementation.
Emulators can be convenient for some use cases, for example, for a development team with limited, unreliable, or slow internet access. But, in most circumstances, choose to use emulators sparingly. By avoiding emulators, you can build and innovate with the latest service features and up to date APIs. You are not stuck waiting on vendor releases to achieve feature parity. You reduce your upfront and ongoing expenses for purchasing and configuration on multiple development systems and build machines. Moreover, you avoid the problem that many cloud services simply do not have emulators available. A testing strategy that depends on emulation makes it impossible to use those services (leading to potentially more expensive workarounds) or produce code and configurations that aren't well tested.
When you do use emulation for testing, you must still test in the cloud to verify configuration and to test interactions with cloud services that can only be simulated or mocked in an emulated environment. When you use emulators and mocked calls to test on your local desktop you might experience testing inconsistencies as your code progresses from environment to environment in your CI/CD pipeline. Unit tests to validate your application's business logic on your desktop might not accurately test critical aspects of the cloud services.
The following examples provide cases to watch out for when testing locally with mocks and emulators: If a Lambda function's logic depends on creating an S3 bucket, a complete test should confirm that Amazon S3 was called and the bucket was successfully created. 3. Software Implementation, Frameworks & Protocols In a mock testing setup, you might mock a success response and potentially add a test case to handle a failure response.
In an emulation testing scenario, the CreateBucket API might be called, but you need to be aware that the identity making the local call does not originate from the Lambda service. The calling identity does not assume a security role as it would in the cloud, so a placeholder authentication is used instead, possibly with a more permissive role or user identity that is different when run in the cloud.
The mock and emulation setups test what the Lambda function does if it calls Amazon S3; however, those tests do not verify that the Lambda function, as configured, is capable of successfully creating the Amazon S3 bucket. You must make sure the role assigned to the function has an attached security policy that allows the function to perform the s3:CreateBucket action. If not, the function likely fails when deployed to a cloud environment.
If an Amazon SQS queue is the source of a Lambda function, a complete test should verify that the Lambda function is successfully invoked when a message is put in a queue. Emulation testing and mock testing are generally set up to run the Lambda function code directly, and to simulate the Amazon SQS integration by passing a JSON event payload (or a deserialized object) as the function handler's input.
Local testing that simulates the Amazon SQS integration tests what the Lambda function does when it's called by Amazon SQS with a given payload, but the test does not verify that Amazon SQS successfully invokes the Lambda function when it is deployed to a cloud environment. Some examples of configuration problems you might encounter with Amazon SQS and Lambda include the following: Amazon SQS visibility timeout is too low, resulting in multiple invocations when only one was intended.
The Lambda function's execution role doesn't allow reading messages from the queue (through sqs:ReceiveMessage , sqs:DeleteMessage , or sqs:GetQueueAttributes ). The sample event that is passed to the Lambda function exceeds the Amazon SQS message size quota. Therefore, the test is invalid because Amazon SQS would never be able to send a message of that size.
As these examples show, tests that cover business logic but not the configurations between cloud services are likely to provide unreliable results. I have a Lambda function that performs calculations and returns a result without calling any other services. Do I really need to test it in the cloud? Yes. Lambda functions have configuration parameters that could change the outcome of the test. All Lambda function code has a dependency on timeout and memory settings, which could cause the function to fail if those settings are not set properly.
Lambda policies also enable standard output logging to Amazon CloudWatch . Even if your code does not call CloudWatch directly, permission is needed to enable logging. This required permission cannot be accurately mocked or emulated. How can testing in the cloud help with unit testing? If it's in the cloud and connects to other resources, isn't that an integration test? We define unit tests as tests that operate on architectural components in isolation, but this does not prevent tests from including components that might call other services or use some network communication.
Many serverless applications have architectural components that can be tested in isolation, even in the cloud. One example is a Lambda function that takes input, processes the data, and sends a message to an Amazon SQS queue. A unit test of this function would likely test whether input values result in certain values being present in the queued message. Arrange : Allocate resources (a queue to receive messages, and the function under test).
A mock testing approach would involve mocking the queue with an in-process mock object, and creating an in-process instance of the class or module that contains the Lambda function code. During the Assert phase, the queued message would be retrieved from the mocked object. In a cloud-based approach, the test would create an Amazon SQS queue for the purposes of the test, and would deploy the Lambda function with environment variables that are configured to use the isolated Amazon SQS queue as the output destination. After running the Lambda function, the test would retrieve the message from the Amazon SQS queue.
The cloud-based test would run the same code, assert the same behavior, and validate the application's functional correctness. However, it would have the added advantage of being able to validate the settings of the Lambda function: the IAM role, IAM policies, and the function's timeout and memory settings. The Serverless Test Samples repository on GitHub contains concrete examples of tests that follow the patterns and best practices described in this guide. The repository contains sample code and guided walkthroughs of the mock, emulation, and cloud testing processes described in previous sections. Use this repository to get up to speed on the latest serverless testing guidance from AWS.
Visit Serverless Land to access the latest blogs, videos, and training for AWS serverless technologies. AWS Lambda is designed to invoke your code when needed, and scales to support the rate of incoming requests. AWS Lambda runs on AWS infrastructure, with AWS managing fault tolerance across multiple Availability Zones and Regions. AWS Lambda is designed to support application resilience and progress preservation through AWS Lambda durable functions, which are designed to provide error handling, retries, and recovery after failures AWS Lambda is designed to integrate with security, observability, and compliance services, enabling alerts or remediation of security threats. AWS Lambda provides monitoring capabilities by capturing and sending logs, metrics, and traces to AWS monitoring and observability services.
With Application Signals, AWS Lambda offers an application performance monitoring (APM) tool designed to track throughput, availability, latency, faults, and errors in your serverless applications. Additionally, AWS Lambda supports integration with third-party monitoring tools through Lambda extensions. AWS Lambda is designed with tools and features for the local development experience. You can bring your code from the console to your local environment. You can use dedicated toolkits for IDEs to author, build, debug, test, and deploy Lambda functions from your IDE. AWS Lambda also supports remote debugging and local testing of cloud functions.
AWS Lambda enables you to build applications through AI-assisted tools and capabilities. The Model Context Protocol (MCP) Server for AWS Lambda enables generative AI models to access and run Lambda functions as tools, and is designed for secure interaction with private resources and AWS services. AWS Lambda is designed to execute functions using virtual machines providing compute resources. With tenant isolation mode enabled, Lambda is designed to isolate request processing for individual tenants or end-users invoking a function.
These execution environments are designed to operate within network-isolated Amazon VPCs managed by Lambda, where network ingress is limited to Lambda-owned services and accounts. This isolation is designed to create boundaries and reduce potential security vulnerabilities and unauthorized access. AWS Lambda is designed to offer provisioned concurrency to keep Lambda functions initialized and ready to support start-up performance.
Provisioned Mode for Lambda Event Source Mappings (ESM) enables you to configure throughput for event source connectors. AWS Lambda offers flexibility in choosing between processor architectures. You can switch between architectures without code changes.
AWS Lambda Managed Instances is designed to run functions on a range of EC2 compute instances. It is designed to manage infrastructure tasks from instance lifecycle, OS and runtime patching to built-in routing, load balancing, and auto scaling based on your selected scaling parameters. You are enabled to keep the familiar Lambda programming model and focus on code.
For additional information about service controls, security features and functionalities, including, as applicable, information about storing, retrieving, modifying, restricting, and deleting data, please see https://docs.aws.amazon.com/index.html . This additional information does not form part of the Documentation for purposes of the AWS Customer Agreement available at http://aws.amazon.com/agreement , or other agreement between you and AWS governing your use of AWS’s services.
Serverless computing has fundamentally changed how organizations build and deploy applications. AWS Lambda, the dominant force in this space, lets developers run code without provisioning or managing servers. But this architectural shift has not eliminated security risks. It has redistributed them, buried them deeper into IAM policies, environment variables, event triggers, and ephemeral execution contexts.
For penetration testers, attacking serverless environments requires a different playbook. Traditional network-based techniques fall short when there is no persistent server to pivot through. This guide walks through the core techniques used in AWS Lambda pentesting, the commands that deliver results, and the misconfigurations that organizations consistently overlook.
If your organization needs a professional assessment of its serverless infrastructure, Redfox Cybersecurity offers specialized cloud pentesting services built specifically for modern AWS environments. Lambda functions inherit permissions from IAM roles, process untrusted input from event sources, and store secrets in ways that are often poorly audited. Unlike traditional server environments, defenders rarely apply the same scrutiny to function-level access controls as they do to EC2 instances or RDS databases.
From an attacker's perspective, a single over-permissioned Lambda function can become the pivot point for cross-account data access, secret exfiltration, privilege escalation, and lateral movement across an entire AWS organization. Before exploiting anything, you need a complete picture of the Lambda environment. This phase focuses on discovering functions, understanding their configurations, and mapping their permissions.
Start with a broad enumeration of all Lambda functions in the target account. If you have compromised AWS credentials with read access, the following commands give you an immediate inventory: Once you have a target function, pull its full configuration. This reveals the runtime, handler, memory allocation, timeout, and most critically, the IAM execution role: The IAM role attached to a Lambda function is often the most exploitable element in the entire serverless stack. Extract its policies with: Organizations frequently attach AdministratorAccess or overly broad S3 and DynamoDB permissions to Lambda roles without understanding the blast radius. A single function with iam:PassRole and lambda:CreateFunction permissions is enough to escalate privileges to full account compromise.
Redfox Cybersecurity's penetration testing team routinely finds critical privilege escalation paths through Lambda execution roles during cloud security assessments. Environment variables in Lambda are a goldmine. Developers commonly store database URIs, third-party API keys, internal service tokens, and even AWS credentials inside function environment variables.
If you have lambda:GetFunction permissions, extract the environment variables directly: If the function processes user-supplied input and reflects output, you can attempt to exfiltrate environment variables by injecting payloads through the event source. A simple Python-based Lambda exfiltration payload looks like this when injected via an API Gateway parameter: When code execution is possible through a deserialization flaw or server-side template injection in the function's runtime, this pattern allows full environment extraction over outbound HTTP.
4. Practical Deployment, Analysis & Case Studies Lambda functions are triggered by event sources. Each event source introduces a distinct injection surface. API Gateway is the most common Lambda trigger. If the function passes query parameters or request body fields directly into database queries, shell commands, or template renderers, standard injection techniques apply.
A response containing 49 confirms SSTI in a Jinja2 or Twig runtime context. From there, remote code execution is a few payload iterations away. Lambda functions triggered by S3 uploads often process file content without sufficient validation. Malicious file uploads can trigger path traversal, XML external entity (XXE) injection, or command injection inside the processing logic.
If the Lambda function parses this XML without disabling external entity resolution, the contents of /etc/passwd (or any accessible file in the ephemeral container) will appear in the function's response or logs. Lambda-based privilege escalation is one of the most powerful attack paths in AWS environments. The key techniques exploit the ability to create or update Lambda functions with an existing over-permissioned role.
If a compromised user has iam:PassRole and lambda:CreateFunction , they can create a new Lambda function using a high-privilege execution role and invoke it to perform actions as that role: This yields new administrative credentials. The attack requires no CVE, no malware, and leaves minimal forensic traces in environments without CloudTrail alerting.
This overwrites the existing function code with an attacker-controlled payload while preserving the original execution role, which may carry higher privileges than the attacker currently holds. Professional red team engagements conducted by Redfox Cybersecurity regularly demonstrate this exact escalation path in client AWS accounts, often within the first hour of a cloud penetration test.
Once you have code execution inside a Lambda function, the post-exploitation phase focuses on expanding access across the AWS environment. Lambda functions running in a VPC can query the Instance Metadata Service to retrieve temporary credentials associated with the execution role. From within function code: These credentials can then be used outside the Lambda environment for lateral movement.
Lambda functions attached to a VPC can reach internal services that are not exposed to the internet, including RDS instances, ElastiCache clusters, and internal microservices. Use the function's network access to port-scan internal CIDR ranges: This converts the compromised Lambda function into an internal network probe, exposing database endpoints, internal APIs, and administrative services.
Attackers who want to maintain access after a Lambda function is cleaned up will abuse CloudFormation, EventBridge schedules, or Lambda layers to maintain persistence. If the compromised role has CloudTrail permissions, an attacker can suppress logging for specific services: Every offensive technique described here maps to a concrete defensive control. Organizations should: Apply least-privilege IAM roles to every Lambda function, enforce resource-based policies on function invocation, enable AWS CloudTrail for all Lambda data events, use AWS Secrets Manager instead of environment variables for sensitive credentials, implement runtime security monitoring with tools like AWS GuardDuty and third-party CNAPP solutions, and conduct regular serverless-specific penetration tests to validate these controls before attackers do.
The techniques covered in this guide represent a fraction of what a skilled attacker can accomplish inside a misconfigured AWS Lambda environment. Real-world engagements go further, including cross-account trust exploitation, supply chain attacks through Lambda layers, and chaining multiple low-severity misconfigurations into full organizational compromise. The most effective defense is proactive testing. Understanding exactly how your Lambda functions would fail under attack, and remediating those gaps before they become incidents, is the standard that modern security programs are held to.
Redfox Cybersecurity offers comprehensive cloud penetration testing services covering AWS Lambda, API Gateway, IAM, S3, and the full serverless attack surface. Their assessments produce actionable findings mapped to real exploitation paths, not just compliance checkboxes. If your organization runs workloads on AWS and has not had a dedicated serverless security assessment, reach out to Redfox Cybersecurity to understand your actual exposure before someone else does.
Discover the most dangerous AWS IAM permissions that attackers abuse to escalate privileges, exfiltrate data, and persist in cloud environments. Learn real-world exploitation techniques and defensive strategies. Explore a hands-on AWS enumeration lab with real-world commands, tools like Pacu, ScoutSuite, and AWS CLI, and step-by-step techniques used by cloud penetration testers to map attack surfaces and identify misconfigurations.
Learn how attackers exploit unauthenticated access in AWS environments. This in-depth guide covers real-world enumeration techniques, misconfigured services, and command-level exploitation used in AWS penetration testing engagements. Implementation of AWS-native vulnerability management pipeline using Amazon Inspector for continuous security assessment and automated remediation of serverless application vulnerabilities.
Amazon Inspector configured for continuous vulnerability assessment with Lambda function scanning coverage. Amazon Inspector identifying CVE-2023-32681 in Python requests package with detailed severity analysis and impacted resource mapping. Integration with NIST National Vulnerability Database for detailed CVE analysis, CVSS scoring, and vulnerability characteristics.
Lambda function requirements.txt update from requests==2.20.0 to requests (latest), removing vulnerable package version. Vulnerability status transition from Active → Closed, confirming successful remediation and reduced attack surface. aws inspector2 update-configuration --scan-type STANDARD --auto-enable ec2=false ecr=false lambda=true AWS-native vulnerability assessment & remediation using Amazon Inspector and Lambda security hardening Serverless functions have become a core building block for modern cloud and AI-native applications. With AWS Lambda, developers build and scale applications faster without managing underlying infrastructure. But as Lambda functions increasingly process sensitive data, connect to APIs, invoke AI services, and power critical workflows, securing the code and dependencies running inside them matters just as much as securing their configurations.
Securing Lambda functions is fundamentally different from securing VMs or containers. There’s no persistent infrastructure to monitor, no fixed runtime to instrument, and functions spin up and tear down in seconds. Each function also requires its own IAM role, meaning permissions are managed individually across potentially hundreds of functions — making misconfigurations easy to miss.
The result is a widening blind spot: organizations can see that a function exists and whether its configuration looks healthy, but not what’s inside it — the vulnerable packages, outdated libraries, and transitive dependencies attackers can exploit. This blind spot is especially dangerous for AI-native applications, where Lambda functions may retrieve sensitive data, call model endpoints, process prompts and responses or trigger downstream business logic. A vulnerable dependency here can expose risk across the entire AI pipeline, not just the function itself.
Today, Qualys is closing that gap by expanding serverless workload security with automated vulnerability scanning for AWS Lambda, giving security teams deeper insight into the vulnerabilities that matter most. With this enhancement, organizations can move beyond serverless discovery and CSPM posture checks to understand the vulnerable packages and dependencies running inside their Lambda functions.
Serverless simplifies infrastructure management, but it doesn’t eliminate security responsibility. While AWS manages the underlying infrastructure, organizations remain responsible for securing the code, dependencies, permissions, configurations, and data that power their Lambda functions. These checks identify misconfigurations, but they don’t reveal whether a function contains vulnerable open-source packages or outdated libraries that attackers can exploit. To secure modern serverless applications, organizations need visibility into both configuration risks and software vulnerabilities.
With automated Lambda function scanning , Qualys helps security teams close a key visibility gap in serverless security. Lambda functions are automatically discovered and scanned during deployment. As functions are created or updated, event-driven scanning keeps vulnerability insights current — continuously assessing serverless workloads without manual intervention.
The capability supports both same-account and cross-account AWS configurations and deploys using provided CloudFormation templates. Once configured, it runs with minimal manual effort — a practical answer for teams asking how to secure AWS Lambda functions at scale. Serverless applications move fast. AI-native applications move even faster. A Lambda function may sit between sensitive data, APIs, cloud services, and AI models. If that function contains vulnerable dependencies — especially combined with excessive permissions or external exposure — the risk can extend far beyond the function itself.
By combining vulnerability insights with cloud security context, Qualys capabilities help teams identify the highest-risk functions, understand where they’re deployed, and prioritize remediation based on exposure and impact, including automated TruRisk Scoring, which combines business and exposure impact with the latest vulnerability intel. By combining zero-day vulnerabilities with unified attack path prioritization — which merges CSPM and real-time detections including threats, overly permissive identities, and exposure — Qualys enables hyper-prioritization and remediation of the serverless attack paths that are truly remediation-worthy. This is Qualys Lambda scan for AI applications in practice: connecting code-level risk to business impact.
Serverless has helped developers build faster and scale more easily. Now, as serverless becomes a key execution layer for AI-native applications, security needs to keep pace. With serverless workload vulnerability management built into the platform, Qualys extends serverless security from discovery and posture to deeper workload risk visibility — helping organizations secure the functions powering modern cloud and AI applications.
Security should not slow down serverless innovation. It should move at the same speed. Don’t let vulnerable code hide in your serverless functions. See Qualys for AWS Lambda in actio n → It closes the visibility gap between serverless posture management (CSPM) and actual software vulnerabilities inside Lambda function code and dependencies.
5. Performance Evaluation & Extended Technical Observations Automatically and continuously, via event-driven scanning that runs when Lambda functions are created or updated — no manual intervention is needed. No. It complements CSPM by adding vulnerability and dependency visibility on top of existing configuration and posture checks.
Both same-account and cross-account AWS configurations, with coverage across multiple regions. Lambda functions in AI workflows often sit between sensitive data, APIs, and model endpoints — a vulnerable dependency here can expose risk across the entire AI pipeline, not just the function itself. By correlating vulnerability findings with cloud context like permissions and exposure, teams can focus on the highest-risk functions first rather than treating all vulnerabilities equally.
Amazon Inspector is a vulnerability management service that continually scans workloads for known software vulnerabilities and unintended network exposure. Amazon Inspector creates a finding that describes the vulnerability, identifies the affected resource, rates the severity of the vulnerability, and provides remediation guidance. Amazon Inspector support provides continuous, automated security vulnerability assessments for Lambda functions and layers. Amazon Inspector provides two scan types for Lambda: Lambda standard scanning (default): Scans application dependencies within a Lambda function and its layers for package vulnerabilities .
Lambda code scanning : Scans the custom application code in your functions and layers for code vulnerabilities . You can either activate Lambda standard scanning or activate Lambda standard scanning together with Lambda code scanning. To enable Amazon Inspector, navigate to the Amazon Inspector console , expand the Settings section, and choose Account Management . On the Accounts tab, choose Activate , and then select one of the scan options.
You can enable Amazon Inspector for multiple accounts and delegate permissions to manage Amazon Inspector for the organization to specific accounts while setting up Amazon Inspector. While enabling, you need to grant Amazon Inspector permissions by creating the role: AWSServiceRoleForAmazonInspector2 . In the Amazon Inspector console, you can create this role using a one-step option.
For Lambda standard scanning, Amazon Inspector initiates vulnerability scans of Lambda functions in the following situations: When you deploy an update to the application code or dependencies of an existing Lambda function or its layers. Whenever Amazon Inspector adds a new common vulnerabilities and exposures (CVE) item to its database, and that CVE is relevant to your function.
For Lambda code scanning, Amazon Inspector evaluates your Lambda function application code using automated reasoning and machine learning that analyzes your application code for overall security compliance. If Amazon Inspector detects a vulnerability in your Lambda function application code, Amazon Inspector produces a detailed Code Vulnerability finding. For a list of possible detections, see the Amazon CodeGuru Detector Library .
To view the findings, go to the Amazon Inspector console . On the Findings menu, choose By Lambda function to display the security scan results that were performed on Lambda functions. To exclude a Lambda function from standard scanning, tag the function with the following key-value pair: To exclude a Lambda function from code scans, tag the function with the following key-value pair: For example, as shown in following image, Amazon Inspector automatically detects vulnerabilities and categorizes the findings of type Code Vulnerability , which indicates that the vulnerability is in the code of the function, and not in one of the code-dependent libraries. You can check these details for a specific function or multiple functions at once.
You can dive further into each of these findings and learn how to remediate the issue. While working with your Lambda functions, ensure that you comply with the naming conventions for your Lambda functions. For more information, see Working with Lambda environment variables . You are responsible for the remediation suggestions that you accept. Always review remediation suggestions before accepting them. You might need to make edits to remediation suggestions to ensure that your code does what you intended.
Amazon Inspector is a vulnerability management service that continually scans workloads for known software vulnerabilities and unintended network exposure. Amazon Inspector creates a finding that describes the vulnerability, identifies the affected resource, rates the severity of the vulnerability, and provides remediation guidance. Amazon Inspector support for AWS Lambda functions provides continuous, automated security vulnerability assessments for Lambda functions and layers. Amazon Inspector provides two scan types for Lambda: To enable Amazon Inspector, you can navigate to the Amazon Inspector console, expand the Settings section, and choose Account Management. On the Accounts tab, choose Activate, and then select one of two scan options provided.
You can enable Amazon Inspector for multiple accounts and delegate permissions to manage Amazon Inspector for the organization to specific accounts while setting up Amazon Inspector. While enabling, you need to grant Amazon Inspector permissions by creating the Role: AWSServiceRoleForAmazonInspector2 . The Amazon Inspector console allows you to create this role using a one-click option.
For Lambda standard scanning, Amazon Inspector initiates vulnerability scans of Lambda functions in the following situations: For Lambda code scanning, Amazon Inspector evaluates your Lambda function application code using automated reasoning and machine learning that analyzes your application code for an overall security compliance. If Amazon Inspector detects a vulnerability in your Lambda function application code, Amazon Inspector produces a detailed Code Vulnerability type finding.
For a list of possible detections, see the CodeGuru Detector Library . To view the findings, go to the Amazon Inspector console and then on the Findings menu, choose âIIBy Lambda functionâII to display the security scan results that were performed on Lambda functions. To exclude a Lambda function from Lambda standard scanning, tag the function with the following key-value pair: To exclude a Lambda function from Amazon Inspector, Lambda code scans tag the function with the following key-value pair: For example, as shown in below image, Amazon Inspector automatically detects the vulnerabilities and categorizes the findings of type Code Vulnerability, which indicates that the vulnerability is in the code of the function, and not in one of the code-dependent libraries. You can check these details for a specific function or across multiple functions at once.
You can further dive deep into each of these findings and learn how to remediate the issue. While working with your Lambda functions, ensure that you comply with the naming conventions for your Lambda functions. Refer the Lambda environment variables best practices here . You are responsible for the remediation suggestions that you accept. Always review remediation suggestions before accepting them. You may need to make edits to remediation suggestions to ensure that your code does what you intended.
WARNING : The purpose of the workshop is to provide a starter API which does NOT follow many security best practices on purpose. The tutorial modules guide you to identify security gaps in the starter app, and implement protection measures for them. Furthermore, the modules do not cover ALL the security measures that should be applied. After completing all modules, we recommend you to explore additional protections, such as ensuring the principle of least privilege. See the Extra Credit section for more details.
In this workshop, you will learn techniques to secure a serverless application built with AWS Lambda, Amazon API Gateway and RDS Aurora. We will cover AWS services and features you can leverage to improve the security of a serverless applications in 5 domains: LICENSE file.
The sample within this documentation is made available under a modified MIT license. See the LICENSE-SAMPLECODE file. In this workshop, you will learn techniques to secure a serverless application built with AWS Lambda, Amazon API Gateway and RDS Aurora. We will cover AWS services and features you can leverage to improve the security of a serverless applications in 5 domains: identity & access management, code, data, infrastructure, logging & monitoring.
A deliberately vulnerable serverless application for learning AWS Lambda security testing. Maps to the OWASP Serverless Top 10 . Deploy with OSLS (open-source Serverless Framework — no licensing or dashboard sign-up required). Do not deploy this in a production environment. For training, CTF, and authorized security testing only. Full step-by-step guide, with verified commands for every endpoint, is in WALKTHROUGH.md .
This deletes the CloudFormation stack, Lambda function, API Gateway, and associated IAM roles. Verify with: Anjali is a seasoned cloud security engineer, experienced in DevSecOps and Kubernetes security (EKS/GKE) as well as AWS, Azure, and GCP security. She is the founder of Container Security Village and Kubernetes Village, communities dedicated to enhancing cloud-native security. As the project lead for OWASP EKS Goat, she focuses on AWS EKS security research and hands-on exploitation paths. Anjali is a recognized AWS Community Builder and actively shares her research through her YouTube channel, @peachycloudsecurity. Her extensive speaking history includes Blackhat USA, Black Hat Spring USA, Black Hat Europe, Nullcon, Seasides Goa, BSides Bangalore, CSA Bangalore, and C0c0n. She has also contributed to the community by volunteering at Cloud Village at DEF CON and various BSides events globally. Reach out at peachycloudsecurity[dot]com Divyanshu is a senior security engineer, experienced in Cloud Security, Kubernetes Security, DevSecOps, Web Application Pentesting, and Threat Modelling. Reported multiple vulnerabilities to companies like Airbnb, Google, Microsoft, AWS, Apple, Amazon, Samsung, Zomato, Xiaomi, Alibaba, Opera, Protonmail, Mobikwik, etc, and received CVE-2019-8727, CVE-2019-16918, CVE-2019-12278, CVE-2019-14962 for reporting issues. Currently co-lead of OWASP EKS Goat, OWASP GKE Goat, Author of Burp-o-mation and very-vulnerable-serverless. Also part of AWS Community Builder for security and Defcon Cloud Village crew member 2020/2021/2022. Delivered talks at events like Blackhat USA, Europe, Seasides, C0c0n, Nullcon, Brucon, BSides Bangalore and BSides Ahmedabad. Also winner of "Cybersecurity Samurai 2023" at BSides Bangalore 2023 & "Cloud Security Champion" at CSA Bangalore 2023. Reach out at peachycloudsecurity[dot]com The information, commands, and demonstrations presented in this lab are intended strictly for educational purposes. Under no circumstances should they be used to compromise or attack any system outside the boundaries of this educational session unless explicit permission has been granted.
Usage of Training Material : The training material is provided without warranties or guarantees. Participants are responsible for applying the techniques or methods discussed during the training. The trainers and their respective employers or affiliated companies are not liable for any misuse or misapplication of the information provided. Liability : The trainers, their employers, and any affiliated companies are not responsible for any direct, indirect, incidental, or consequential damages arising from the use of the information provided. No responsibility is assumed for any injury or damage to persons, property, or systems as a result of using or operating any methods, products, instructions, or ideas discussed during the training.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Serverless%20computing • https://en.wikipedia.org/wiki/Google%20Cloud%20Platform • https://docs.aws.amazon.com/lambda/latest/dg/testing-guide.html • https://aws.amazon.com/documentation-overview/lambda/ • https://www.redfoxsec.com/blog/serverless-security-testing-guide • https://github.com/SilentVeil/AWS-vulnerability-management-lab • https://blog.qualys.com/product-tech/2026/07/27/aws-lambda-vulnerability-scanning-serverless-security • https://docs.aws.amazon.com/lambda/latest/dg/governance-code-scanning.html • https://serverlessland.com/content/service/lambda/guides/governance/6-code-scanning • https://github.com/aws-samples/aws-serverless-security-workshop
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Serverless Application Vulnerability Testing Tool Aws Lambda.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Serverless Application Vulnerability Testing Tool Aws Lambda... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |