Complete Technical Paper Content — Session Hijacking Detection And Prevention System Project
Overview & System Context
Session Hijacking Detection And Prevention System Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9519 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Data center security is the set of policies, precautions and practices adopted at a data center to avoid unauthorized access and manipulation of its resources. The data center houses the enterprise applications and data, hence why providing a proper security system is critical. Denial of service (DoS), theft of confidential information, data alteration, and data loss are some of the common security problems afflicting data center environments. Data security issues can be harmful to many companies sometimes, so it is very important to know what are the issues and find useful solutions for them. The purpose of data security is to protect digital information from unauthorized access. It is also important to note that data security is different from data privacy. There are many situations where data center security would be threatened, especially for cloud-based data.
39% of companies say negligence was the primary cause of data breaches Malicious or criminal attacks account for 37 percent of total breaches. The average cost of a breach is $5.5 million. Many big companies nowadays are using the cloud to store their and their customers' data, but the risks of saving data in the cloud can be enormous. Cyber attacks can be very harmful to many companies. There were 64% of companies worldwide that had troubles with cyber attacks in the year 2020 alone. Some cyber attacks targeting personal information such as identity theft ,can hurt someone's credits with life-changing influences.
DoS (Denial of Service) Data theft or alteration Unauthorized use of computing resources Identity theft
Implementation
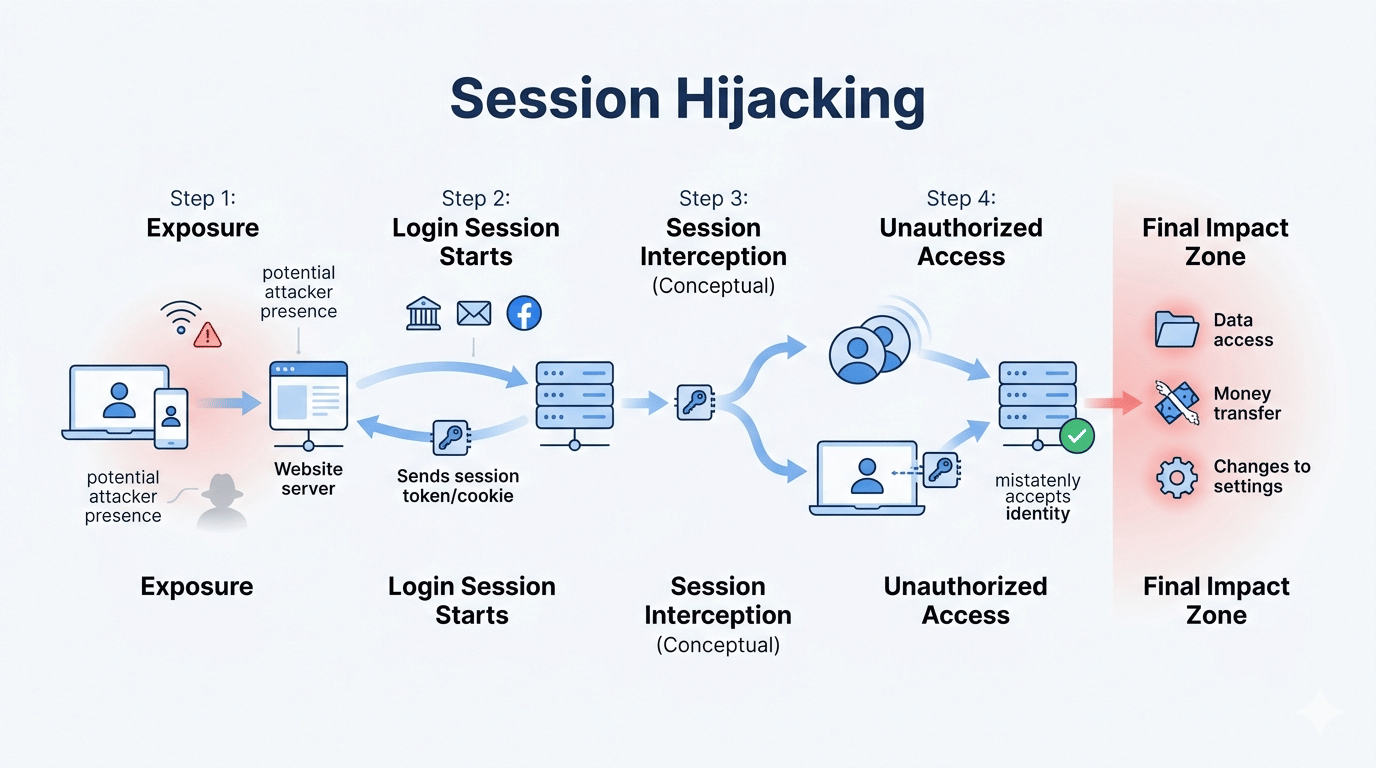
Software design and protocol flaws, coding errors, and incomplete testing Configuration: Use of defaults, elements inappropriately configured Figure 1: Session Hijacking in Cybersecurity: Types and Prevention Scanning or probing: One example of a probe- or scan-based attack is a port scan - whereby "requests to a range of server port addresses on a host" are used, to find "an active port" and then cause harm via "a known vulnerability of that service.".
Implementation Synonym
This reconnaissance activity often precedes an attack; its goal is to gain access by discovering information about a system or network. DoS (Denial of service): A denial-of-service attack occurs when legitimate users are unable to access information systems, devices, or other network resources due to the actions of a malicious cyber threat actor. This type of attack generates a large volume of data to deliberately consume limited resources such as bandwidth, CPU cycles, and memory blocks. Distributed Denial of Service (DDoS): This kind of attack is a particular case of DoS where a large number of systems are compromised and used as source or traffic on a synchronized attack. In this kind of attack, the hacker does not use only one IP address but thousands of them. Unauthorized access: When someone other than an account owner uses privileges associated to a compromised account to access to restricted resources using a valid account or a backdoor. Eavesdropping: Etymologically, Eavesdropping means secretly listening to a conversation. In the networking field, it is an unauthorized interception of information (usernames, passwords) that travels on the network. User logons are the most common signals sought. Viruses and worms: These are malicious code that, when executed produce undesired results. Worms are self-replicating malware, whereas viruses, which also can replicate, need some kind of human action to cause damage.
Implementation Meaning
Internet infrastructure attacks: This kind of attack targets the critical components of the Internet infrastructure rather than individual systems or networks. Trust exploitation: These attacks exploit the trust relationships that computer systems have to communicate. Session hijacking also known as cookie hijacking: Consists of stealing a legitimate session established between a target and a trusted host. The attacker intercepts the session and makes the target believe it is communicating with the trusted host. Buffer overflow attacks: When a program allocates memory buffer space beyond what it had reserved, it results in memory corruption affecting the data stored in the memory areas that were overflowed. Layer 2 attacks: This type of attack exploit the vulnerabilities of data link layer protocols and their implementations on layer 2 switching platforms. SQL injection: Also known as code injection, this is where input to a data-entry form's, due to incomplete data validation, allows entering harmful input that causes harmful instructions to be executed.
Implementation Science
Sensors: Appliances and software agents that analyze the traffic on the network or the resource usage on end systems to identify intrusions and suspicious activities. IDS management: Single- or multi-device system used to configure and administer sensors and to additionally collect all the alarm information generated by the sensors. The sensors are equivalent to surveillance tools, and IDS management is the control center watching the information produced by the surveillance tools.
Implementation Specialist
The process of securing a data center requires both a comprehensive system-analysis approach and an ongoing process that improves the security levels as the Data Center evolves. The data center is constantly evolving as new applications or services become available. Attacks are becoming more sophisticated and more frequent. These trends require a steady evaluation of security readiness. A key component of the security-readiness evaluation is the policies that govern the application of security in the network including the data center. The application includes both the design best practices and the implementation details. As a result, security is often considered as a key component of the main infrastructure requirement.
Implementation Definition
Since a key responsibility of the data centers is to make sure of the availability of the services, data center management systems often consider how its security affects traffic flows, failures, and scalability. Due to the fact that security measures may vary depending on the data center design, the use of unique features, compliance requirements or the company's business goals, there is no set of specific measures that cover all possible scenarios. There exist in general two types of data center security: physical security and virtual security.
Implementation Manager
CCTV security network: locations and access points with 90-day video retention. 24×7 on-site security guards, Network operations center (NOC) Services and technical team Anti-tailgating/Anti-pass-back turnstile gate. Only permits one person to pass through after authentication. Single entry point into co-location facility. Minimization of traffic through dedicated data halls, suites, and cages. Further access restriction to private cages Three-factor authentication SSAE 16 compliant facilities.
Implementation Consultant
Checking the provenance and design of hardware in use Reducing insider risk by monitoring activities and keeping their credentials safe Monitoring of temperature and humidity Fire prevention with zoned dry-pipe sprinkler Natural disaster risk-free locations The coming "dark" data centers will present new challenges as developers and operators look for new ways to reduce staffing needs at the data centers. New automated modular security entrance control booth systems allow for the reduction of security staff per data center, by creating automated security booths or portals that process staff and visitors through tailgate detection, biometric authentication, body scanning, and video security employing a variety of optional integrated security technologies (automatic locking doors, smart intercoms, electronic lockers and smart visitor management systems) managed and monitored by a remote SOC on the campus. The result is an ROI in terms of reduced staff needs.
Implementation Intentions
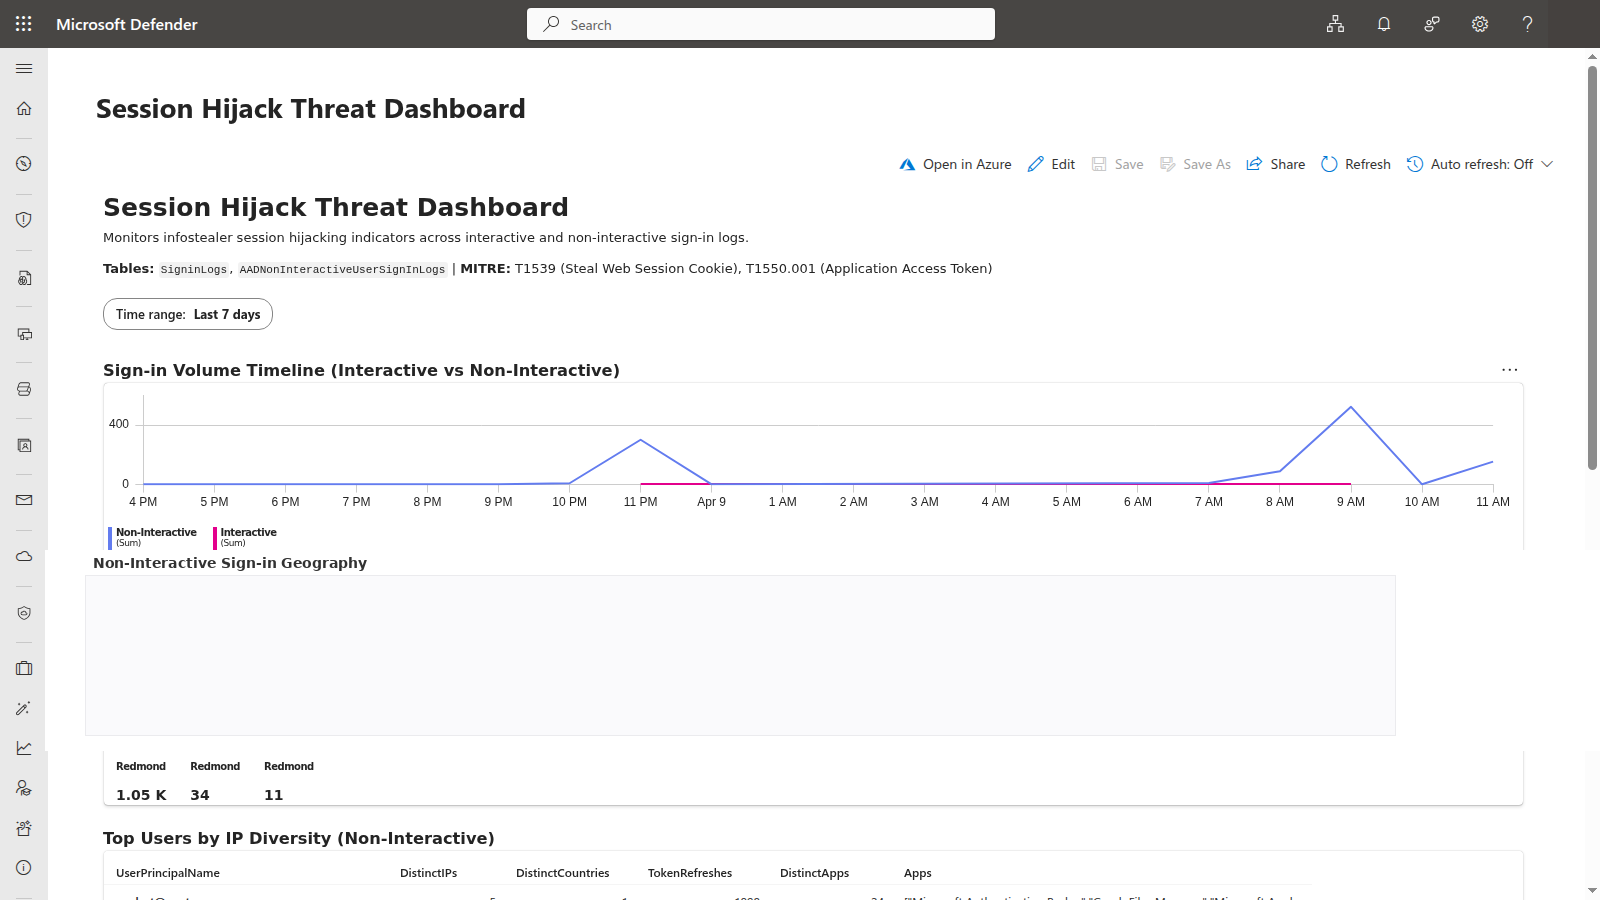
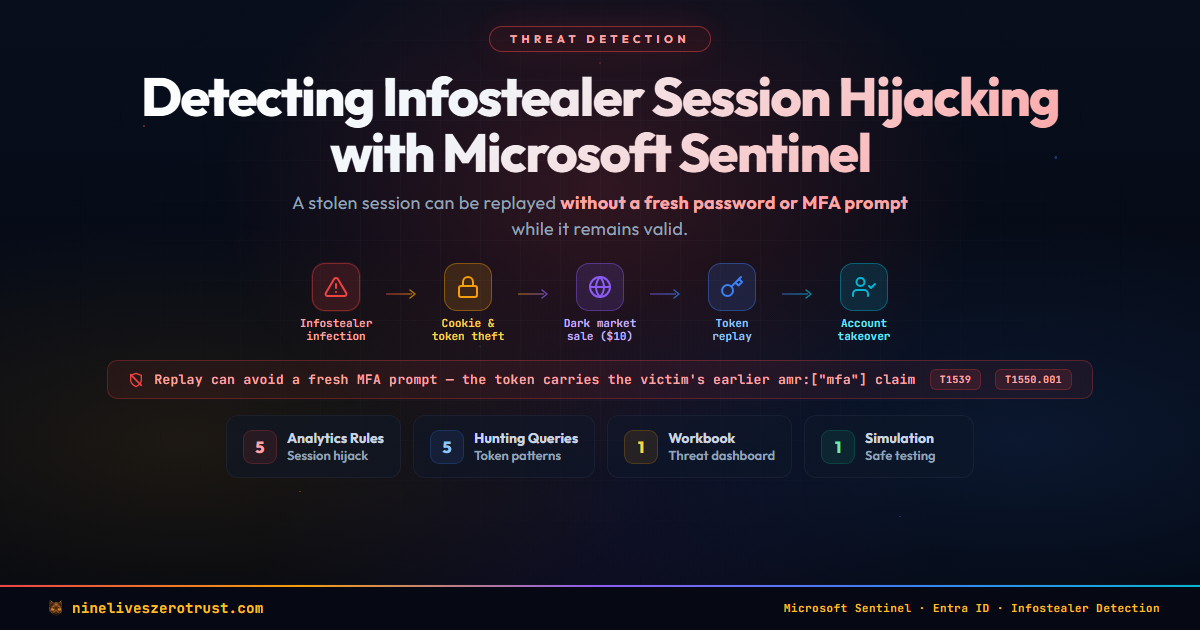
Figure 2: Detecting Infostealer Session Hijacking with Microsoft Sentinel | Nine ... Heavy data encryption during transfer or not: 256-bit SSL encryption for web applications.1024-bit RSA public keys for data transfers. AES 256-bit encryption for files and databases. Logs auditing activities of all users. Secured usernames and passwords: Encrypted via 256-bit SSL, requirements for complex passwords, set up of scheduled expirations, prevention of password reuse. Access based on the level of clearance. AD/LDAP integration. Control based on IP addresses. Encryption of session ID cookies in order to identify each unique user. Two-factor authentication availability. Third party penetration testing performed annually Malware prevention through firewalls and automated scanner Determine the risks. Find all the tools that may store the data such as computers and databases, and make sure everything is stored in a compliant manner. Review current data security systems. Check for any updates in the current data security system if there are one. Sometimes, the stale data should be removed and it is also helpful to have cleanup software installed to help the company delete the unused or unneeded data. Gather a data security team. Build a professional internal security team that can help the company to secure its data and save money on hiring other security teams. The security team must have a recovery plan just in case something unexpected may happen. Update data security approach. Make sure only the authorized people can access the system. Encryption software is needed because it can protect the data from people who decrypt the system. If the proper key was not provided, the software can make the data seem useless to other people. Data masking software is another software that is helpful since it can hide some sensitive information from being seen. The last software is risk assessment software, which is a tool that helps users to monitor and check their network securities.
Implementation Engineers
DNS spoofing, also referred to as DNS cache poisoning, is a form of computer security hacking in which corrupt Domain Name System data is introduced into the DNS resolver's cache, causing the name server to return an incorrect result record, e.g. an IP address. This results in traffic being diverted to any computer that the attacker chooses. Put simply, a hacker makes the device think it is connecting to the chosen website, when in reality, it is redirected to a different website by altering the IP address associated with the domain name in the DNS server.
A Domain Name System server translates a human-readable domain name (such as example.com) into a numerical IP address that is used to route communications between nodes. Normally if the server does not know a requested translation it will ask another server, and the process continues recursively. To increase performance, a server will typically remember (cache) these translations for a certain amount of time. This means if it receives another request for the same translation, it can reply without needing to ask any other servers, until that cache expires. When a DNS server has received a false translation and caches it for performance optimization, it is considered poisoned, and it supplies the false data to clients. If a DNS server is poisoned, it may return an incorrect IP address, diverting traffic to another computer (often an attacker's).
Figure 3: Detecting Infostealer Session Hijacking with Microsoft Sentinel | Nine ... A vulnerable server would cache the additional A-record (IP address) for ns.target.example, allowing the attacker to resolve queries to the entire target.example domain. A vulnerable server would cache the unrelated authority information for target.example's NS-record (nameserver entry), allowing the attacker to resolve queries to the entire target.example domain.
Trusteer is a suite of enterprise security software sold by IBM that allows businesses to verify their customers and prevent fraud and cyberattacks across their online platforms. It was originally developed by Trusteer, Inc., a software company founded by Mickey Boodaei and Rakesh K. Loonkar, in Israel in 2006. Trusteer was acquired in September 2013 by IBM for $1 billion. Trusteer's products aimed to block online threats from malware and phishing attacks and to support regulatory compliance requirements. Trusteer's malware research team aimed to analyze information received from the installed base of 30,000,000 user endpoints and hundreds of organizations. Trusteer had a presence in North America, South America, Europe, Africa, Japan and China.
See how to govern AI agents & third-party risk with Obsidian. Live on Tuesdays. Register Learn how session hijacking bypasses MFA by stealing post-authentication tokens. Discover detection methods and prevention strategies for SaaS security teams. The attack works because modern web applications maintain user sessions through bearer tokens. These tokens function like physical keys: whoever holds the token can access the application without proving they're the rightful owner. When an attacker obtains your session token, they inherit your authenticated state, permissions, and access level across connected SaaS applications.
Why session hijacking surged in 2026: As organizations adopted passwordless authentication and enforced stricter MFA policies, attackers pivoted their tactics. Instead of trying to guess or steal passwords, they now target the session tokens created after users successfully authenticate. This represents a fundamental shift in the threat landscape; authentication security threat research shows session hijacking attacks increased 127% year-over-year, with a 200%+ spike in post-authentication token targeting.
Identity-related issues now drive nearly 90% of all incident response investigations, with identity explicitly implicated in 87% of intrusions. Browser-based activity featured in 48% of investigations, up from 44% in 2024, reflecting widespread exposure through routine web sessions where tokens are stored and transmitted. For security teams, this creates a critical blind spot. Your SSO and MFA protect the initial login, but they don't stop attackers who steal the session token created after that login succeeds. The session operates independently of your authentication controls.
Session hijacking follows a predictable attack pattern that exploits the gap between authentication and session management. Network interception captures unencrypted session tokens transmitted over insecure connections. While HTTPS has reduced this vector, misconfigurations and downgrade attacks still create opportunities. Once acquired, attackers import the stolen session token into their own browser. Because the token is a bearer credential, the application accepts it without requiring re-authentication. The attacker now appears to the server as the legitimate user.
The real damage begins when attackers leverage the compromised session to access connected systems. OAuth tokens often grant permissions across multiple integrated applications. An attacker who hijacks a session in one SaaS app can ride those trusted connections straight into customer environments, connected data repositories, and downstream systems. This SaaS-to-SaaS lateral movement represents one of the most dangerous aspects of session hijacking. The attacker inherits not just the user's direct permissions but also the inherited permissions from OAuth integrations, service accounts, and API connections that extend trust across your SaaS supply chain.
Understanding the specific techniques attackers use helps security teams build targeted defenses. In session fixation attacks, adversaries trick users into authenticating with a session ID the attacker already knows. The attacker sets a specific session identifier (often through a malicious link), then waits for the victim to log in using that predetermined session. Once authentication completes, the attacker uses the known session ID to hijack the now-authenticated session.
XSS vulnerabilities allow attackers to inject malicious scripts into trusted websites. These scripts execute in victims' browsers and extract session tokens, which are then sent to attacker-controlled servers. The attack succeeds because the malicious script runs within the security context of the legitimate application. Man-in-the-middle attacks position the adversary between the user and the application server. The attacker intercepts all traffic, including session tokens, as it flows between endpoints. This technique often combines with AiTM phishing, where the phishing site proxies the real application while capturing authentication tokens.
OAuth tokens and refresh tokens present particularly attractive targets. Refresh tokens are especially dangerous because they operate outside traditional login flows and can generate new access tokens for extended periods. Many refresh tokens remain valid for weeks or months, giving attackers persistent access long after the initial compromise. Most SaaS apps implement OAuth tokens as bearer tokens, something like a key. Whoever has this key can use it. This design choice prioritizes user experience over security, creating the exact vulnerability that session hijacking exploits.
For a deeper understanding of how attackers leverage these tokens, see our guide on identifying and mitigating SaaS session hijacking . Session hijacking enables attackers to accomplish objectives that credential theft alone cannot achieve. Immediate access without detection: Because the hijacked session was already validated through legitimate authentication, security systems see normal user activity. The attacker bypasses login monitoring, failed authentication alerts, and impossible travel detection.
Privilege inheritance across integrated systems: OAuth integrations create trust relationships between SaaS applications. When attackers hijack a session in one application, they often inherit permissions in connected systems. This SaaS supply chain risk turns a single compromised session into a multi-application breach. Data exfiltration at scale: With an active session, attackers can download sensitive data, export customer lists, access confidential documents, and extract intellectual property, all while appearing as the legitimate user performing normal business activities.
Account takeover and persistence: Attackers use hijacked sessions to modify account settings, add additional authentication methods, create new service accounts, and establish backdoor access that survives even after the original session expires. Lateral movement to high-value targets: Initial access through a low-privilege user's session provides a foothold for reconnaissance. Attackers map the environment, identify high-value accounts, and use the compromised session to launch targeted attacks against administrators or sensitive systems.
The Lapsus$ group demonstrated these techniques in high-profile breaches, using session hijacking to bypass MFA and gain access to source code repositories, customer data, and internal systems at major technology companies. Static security tools struggle to identify session hijacking because the stolen token is technically valid. Detection requires behavioral analysis that identifies anomalous patterns invisible to traditional controls.
Sudden IP address changes during an active session indicate potential hijacking. When a user authenticates from New York, then the same session appears in Russia five minutes later, behavioral detection systems flag the impossible travel scenario. ASN (Autonomous System Number) deviation provides more precise detection than simple IP geolocation. When a session suddenly originates from a different internet service provider or hosting provider, it suggests token theft and replay from an attacker-controlled system.
Browser and device fingerprint changes mid-session reveal token theft. If a session begins on Chrome/Windows then continues on Firefox/Linux without re-authentication, the session was likely hijacked and replayed from a different device. Operating system inconsistencies provide similar detection signals. Sessions that jump between iOS, Android, and Windows devices without logical explanation indicate token compromise.
Access pattern changes compared to historical behavior reveal compromised sessions. When a user who typically accesses three specific applications suddenly queries sensitive databases they've never touched, behavioral analytics flag the anomaly. Time-of-day violations identify suspicious activity. Sessions active during hours when the legitimate user never works, especially combined with geographic anomalies, strongly indicate hijacking.
Data access volume spikes reveal exfiltration attempts. When a session downloads 1,000 customer records in five minutes after months of normal activity averaging five records per day, the behavioral deviation triggers alerts. Unexpected OAuth scope expansion indicates attackers modifying permissions. When an existing integration suddenly requests additional scopes or permissions it didn't previously require, it suggests compromise.
New integration approvals from suspicious locations reveal consent phishing or token theft. Behavioral systems correlate the approval location, time, and requested permissions against the user's normal patterns. 2. System Architecture & Core Working Principles Obsidian Security's behavioral detection platform uses these signals to identify session hijacking that bypasses traditional security controls. Learn more about stopping token compromise through behavioral analysis.
Effective session hijacking prevention requires layered controls that address both token acquisition and token replay. Contextual risk assessment evaluates every session action against behavioral baselines. When risk signals accumulate, such as an IP change, unusual data access, or off-hours activity, the system requires re-authentication before allowing sensitive operations.
Device binding for high-risk actions forces re-verification when users attempt privileged operations. Even with a valid session token, accessing admin panels or downloading bulk data triggers additional authentication challenges. Continuous session validation monitors sessions throughout their lifecycle rather than only at login. This approach makes stolen sessions "hit a contextual wall" when they exhibit suspicious behavior, even if the token itself remains technically valid.
Aggressive session expiration limits the window attackers have to exploit stolen tokens. Reducing session lifetimes from hours to minutes significantly constrains attack opportunities, though this must balance against user experience requirements. Refresh token rotation invalidates old tokens when issuing new ones. This prevents attackers from maintaining persistent access through long-lived refresh tokens stolen weeks earlier.
Automatic logout on risk signals immediately terminates sessions when behavioral anomalies are detected, preventing attackers from completing their objectives even if they successfully steal tokens. Endpoint detection and response (EDR) identifies and blocks info-stealer malware before it can exfiltrate session tokens from browser storage.
Login notifications for new devices or locations allow users to detect unauthorized session activity immediately. When users receive alerts about sessions they didn't initiate, they can revoke access before attackers cause damage. Concurrent session limits prevent attackers from maintaining access while the legitimate user is also active. When a second session appears from a different location, the system can require re-authentication or terminate the suspicious session.
Session activity logging creates audit trails that support forensic investigation after compromise. Detailed logs of session actions, IP addresses, and accessed resources help security teams understand breach scope and impact. OAuth scope minimization limits the permissions granted to integrations. When applications request only the specific scopes they actually need, compromised integrations provide less access to attackers.
Integration behavioral monitoring identifies when legitimate integrations begin exhibiting suspicious behavior: accessing new data types, operating at unusual times, or exfiltrating data at abnormal volumes. Third-party app governance maintains visibility into all OAuth-connected applications. Security teams need to know what's talking to their Salesforce, what permissions those connections have, and when those integrations deviate from normal behavior.
For comprehensive guidance on securing your SaaS environment against session-based attacks, explore our zero trust security framework for SaaS applications . Session hijacking becomes exponentially more dangerous when OAuth integrations create trust relationships between SaaS applications. This is where the attack moves from a single compromised session to a SaaS supply chain breach.
OAuth tokens function as bridges between applications. When a user authorizes an integration between Salesforce and a marketing automation platform, they create a persistent OAuth connection. That connection operates through tokens that grant the integrated application ongoing access, often with broad permissions. Attackers ride these trusted connections. A session hijacked in one application provides access to that app's OAuth tokens.
Those tokens then grant access to every connected system, allowing attackers to move laterally across your SaaS environment without triggering additional authentication. The real exposure sits one integration away. Most organizations believe their biggest SaaS risk lives inside the applications they manage directly. In reality, the real exposure often sits one integration away, in the third-party applications connected through OAuth, the service accounts that operate across multiple systems, and the API keys that grant programmatic access.
Inherited permissions multiply the blast radius. When an attacker hijacks a session that has OAuth connections to five other applications, they don't just compromise one user account. They inherit the permissions of every integration that user has authorized, potentially accessing customer data across multiple platforms. Stale integrations with admin permissions create toxic combinations. Security teams often discover OAuth integrations they didn't know existed: connections authorized years ago that still maintain write and delete permissions to critical systems.
These forgotten integrations become high-value targets for attackers who hijack sessions and exploit the overprivileged access. Obsidian Security's behavioral detection identifies these SaaS-to-SaaS lateral movement patterns by monitoring the relationships between applications, tracking OAuth token usage, and alerting when sessions begin accessing connected systems in unexpected ways. Learn more about SaaS integration risks and how to govern them effectively.
Security teams often conflate session hijacking with traditional credential theft, but the distinction matters for defense strategy. Credential theft targets passwords and usernames. Attackers use phishing, keyloggers, password dumps, or brute force attacks to obtain login credentials. Once acquired, they attempt to authenticate as the victim. Session hijacking targets post-authentication tokens. Attackers steal the session identifier created after successful login. They bypass the authentication process entirely because they already have proof of authentication.
MFA stops credential theft but not session hijacking. Multi-factor authentication prevents attackers from logging in with stolen passwords because they can't complete the second factor. But MFA doesn't protect the session token created after the legitimate user successfully authenticates. Two-factor authentication does not stop already-stolen session tokens, though it makes re-entry harder by forcing attackers to re-authenticate with stolen credentials if the session expires.
Passwordless authentication shifts the attack surface. As organizations adopt passkeys and eliminate passwords, credential theft becomes less viable. Attackers respond by focusing exclusively on session tokens, the one artifact that survives the move to passwordless authentication. Detection requirements differ fundamentally. Credential theft generates failed login attempts, impossible travel alerts during authentication, and new device notifications. Session hijacking generates none of these signals because the session was already authenticated. Detection requires behavioral analysis of session activity, not authentication monitoring.
For security teams, this means your authentication security controls, including SSO, MFA, and passwordless login, protect the front door. But session hijacking attacks come through the window after the legitimate user already unlocked the door. You need behavioral detection that monitors what happens after authentication succeeds. Static security tools fail against session hijacking because they evaluate credentials and authentication events, not session behavior. Behavioral detection provides the visibility and response capabilities that traditional controls miss.
Behavioral baselines establish normal patterns. Machine learning models analyze months of user activity to understand typical behavior: which applications they access, when they work, where they connect from, what data they touch, and how they interact with integrated systems. Anomaly detection identifies deviations that indicate compromise. When a session deviates from established baselines, such as accessing new systems, downloading unusual data volumes, or operating from unexpected locations; behavioral detection flags the activity for investigation or automatic response.
Contextual risk scoring weighs multiple signals. Individual anomalies might be benign, but combinations reveal compromise. A session from a new IP address might be explained by travel. But a new IP address plus a new device plus access to sensitive data the user never previously touched creates a high-confidence compromise signal. Automated response contains threats before damage occurs. When behavioral detection identifies high-risk session activity, automated workflows can require re-authentication, terminate the session, revoke OAuth tokens, or alert security teams, all before attackers complete their objectives.
Knowledge Graph correlation reveals attack paths. Behavioral detection platforms that understand relationships between users, applications, integrations, and data can identify lateral movement patterns that single-point monitoring misses. When a hijacked session begins exploring OAuth connections and accessing integrated systems, the Knowledge Graph reveals the attack path.
Obsidian Security's platform combines behavioral detection with deep visibility into SaaS integrations, OAuth tokens, and service accounts to identify session hijacking that bypasses traditional security controls. Explore how Identity Threat Detection and Response (ITDR) stops attacks targeting SaaS environments. The session hijacking threat landscape continues to evolve as attackers adopt new technologies and techniques.
AI-generated phishing campaigns increased 347% year-over-year , with adversaries using large language models to create convincing phishing content at scale. These campaigns often lead to AiTM attacks that capture session tokens after victims authenticate. Voice phishing (vishing) attacks using deepfake voice cloning rose 89% , allowing attackers to impersonate executives and request that IT teams approve OAuth integrations or share session tokens.
QR code phishing (quishing) surged 412% , with attackers embedding malicious QR codes in emails that direct victims to credential harvesting sites designed to steal session tokens. MFA fatigue attacks increased 218% year-over-year , with attackers bombarding authenticator apps with repeated login requests until frustrated users approve unauthorized access. Once approved, the attacker obtains a valid session token that bypasses all authentication controls.
AI agents introduce new session hijacking vectors. As organizations deploy autonomous AI agents with API access and OAuth permissions across SaaS environments, these non-human identities become attractive targets. Compromising an AI agent's session token provides persistent, automated access that operates continuously without human intervention. Learn more about AI agent security risks and how to protect these emerging identities.
Mobile and IoT device vulnerabilities expand the attack surface. Session tokens stored on mobile devices and IoT endpoints often receive less security scrutiny than desktop browsers. Attackers increasingly target these devices to steal tokens that grant access to enterprise SaaS applications. Regulatory violations and compliance failures occur when attackers use hijacked sessions to access protected data. GDPR, HIPAA, PCI-DSS, and other frameworks require organizations to protect personal information. Session hijacking that leads to data breaches triggers notification requirements, regulatory investigations, and potential fines.
Financial services face heightened scrutiny. The NYDFS Cybersecurity Regulation requires financial institutions to implement multi-factor authentication and monitor for unauthorized access. Session hijacking attacks that bypass MFA create compliance gaps that regulators increasingly scrutinize. Review our NYDFS cybersecurity compliance checklist for specific requirements.
Economic costs compound quickly. The average cost of a data breach reached $4.91 million in 2025, with SaaS supply chain breaches carrying additional costs for customer notification, legal defense, regulatory fines, and reputation damage. Customer trust erosion follows public disclosure of session hijacking incidents. When customers learn that attackers accessed their data through compromised sessions, they question the organization's security practices and may terminate relationships.
Insurance implications affect coverage and premiums. Cyber insurance policies increasingly require specific security controls including session monitoring and behavioral detection. Organizations that experience session hijacking breaches without these controls may face coverage denials or premium increases. Board-level accountability makes session hijacking a governance issue. Security leaders must explain to boards how attackers bypassed MFA, what data was accessed, and what controls will prevent recurrence. The technical complexity of session hijacking makes these conversations challenging.
3. Software Implementation, Frameworks & Protocols When behavioral detection or user reports indicate session hijacking, immediate response limits damage. Immediately terminate the compromised session. Revoke the stolen session token to prevent continued attacker access. Most SaaS platforms allow administrators to force logout specific sessions or all sessions for a user.
Revoke associated OAuth tokens and refresh tokens. If the hijacked session had OAuth integrations, revoke those tokens to prevent lateral movement into connected applications. Reset credentials and require re-authentication. Even though session hijacking bypasses passwords, force a password reset to ensure attackers can't re-establish access if they also obtained credentials.
Audit session activity to determine breach scope. Review logs to identify what data the attacker accessed, what actions they performed, and what systems they touched. This audit determines notification requirements and remediation scope. Identify the initial access vector. Determine how the attacker obtained the session token: info-stealer malware, phishing, XSS vulnerability, or network interception. This analysis guides remediation to prevent recurrence.
Scan for additional compromised sessions. If one user's session was hijacked, attackers may have compromised multiple accounts. Behavioral detection platforms can identify other sessions exhibiting similar anomalous patterns. Notify affected users and stakeholders. Depending on the data accessed and regulatory requirements, you may need to notify customers, partners, or regulators about the breach.
Implement additional monitoring. Increase scrutiny on the affected user's account and related systems. Attackers often attempt to re-establish access after initial detection. For comprehensive incident response guidance, see our SaaS Security Threat Report 2025 which includes detailed playbooks for responding to session-based attacks.
Protecting against session hijacking requires a comprehensive program that addresses technology, process, and governance. Establish session security as a strategic priority. With 87% of successful cyberattacks involving session hijacking after valid MFA logins, this threat deserves executive attention and dedicated resources. Deploy behavioral detection that monitors post-authentication activity. Traditional security tools stop at authentication. Modern threats require visibility into what happens after login succeeds.
Implement contextual authentication for sensitive operations. Even with a valid session, require re-verification when users access high-value data, modify security settings, or perform administrative actions. Govern OAuth integrations and third-party connections. Maintain a complete inventory of all SaaS integrations, the permissions they hold, and the data they access. Monitor these connections for behavioral anomalies that indicate compromise.
Reduce session lifetime and rotate tokens aggressively. Shorter session windows limit attacker opportunities. Balance security requirements against user experience through risk-based policies. Enable comprehensive session logging and forensics. You can't investigate what you can't see. Ensure all session activity generates detailed audit trails that support incident response.
Educate users about session-based threats. Most security awareness training focuses on password protection and phishing recognition. Expand training to cover session hijacking, token theft, and the importance of reporting suspicious session notifications. Test detection capabilities through adversary simulation. Red team exercises that include session hijacking techniques validate whether your behavioral detection actually identifies these attacks before damage occurs.
Integrate session security into broader identity threat detection. Session hijacking is one component of identity-based attacks. Comprehensive protection requires visibility across credentials, sessions, OAuth tokens, service accounts, and API keys. Obsidian Security provides the behavioral detection, OAuth governance, and SaaS-to-SaaS visibility that security teams need to identify and stop session hijacking before attackers accomplish their objectives. Get a demo to see how behavioral analysis detects the session anomalies that traditional tools miss.
In the wake of the Salesloft breach, we’re offering a free risk assessment of your Salesforce environment to help identify potential exposure. Click here to request yours. Take a breather! In under 6 minutes, our demo breaks down the risks AI agents bring to your SaaS environment and how you can get ahead of them.
The biggest SaaS breach of 2025 started with a compromised third-party app. Attackers then exploited Salesloft-Drift OAuth tokens, which granted them access to hundreds of downstream environments. Obsidian researchers found the blast radius of this supply chain attack was 10x greater than previous incidents, where attackers infiltrated Salesforce directly. Start in minutes and secure your critical SaaS applications with continuous monitoring and data-driven insights.
Understand session hijacking prevention, common attack types, detection signals, and technical controls to protect web, mobile, and SaaS sessions. See how Bureau has helped industry leaders defend against networked Industrial-scale frauds âII Once an attacker gets access to a valid session token, they may not need to break the login flow, bypass MFA, or guess credentials. The application may already trust the session, which is what makes session hijacking so difficult to catch after authentication succeeds.
Session hijacking prevention focuses on protecting the full session lifecycle: how tokens are created, transmitted, stored, rotated, expired, and revoked. Strong session token security also needs real-time monitoring so teams can spot suspicious changes in device, location, behavior, or token usage before a valid session turns into an account takeover. In this guide, weâIIll explain how session hijacking works, the most common attack methods, how to detect suspicious sessions, and how to prevent session hijacking.
Session hijacking is a cyberattack where an attacker takes over a valid user session by stealing, predicting, fixing, or reusing a session token. Once the attacker has that token, the application may treat them as the authenticated user. This is why session hijacking is so risky: the login may already be complete, but the session is no longer under the userâIIs control.
Session hijacking works by abusing the token that an application uses to remember that a user is already authenticated. The application uses the token to recognize the user without asking them to log in again. The application may treat the attacker as the real user until the token expires, is revoked, or suspicious activity is detected. Session tokens work like bearer credentials, which means anyone holding a valid token may be treated as authenticated.
Long-lived sessions increase the attack window, and passing session IDs in URLs can expose tokens through browser history, logs, referrers, shared links, and support workflows. In fact, according to Microsoft's 2025 Digital Defense Report , 80% of MFA-bypass breaches are attributed to session-token theft, meaning attackers are increasingly winning after authentication, not during it.
According to the 2026 Fortinet Web Application Security Report , credential stuffing has become the top bot-attack concern for 68% of security professionals, reflecting how rapidly attackers are scaling session abuse tactics and why defenses need to keep pace. Session sniffing is when attackers monitor network traffic and capture session data as it moves between the user and the application.
Cross-site scripting allows malicious scripts to run in a userâIIs browser. If session tokens are accessible to JavaScript, attackers may be able to steal them and reuse them elsewhere. Session fixation happens when an attacker forces or tricks a user into authenticating with a session ID that the attacker already knows. If the application does not issue a fresh session ID after login, the attacker may reuse that known session to impersonate the user.
The key control is simple: regenerate session identifiers after trust level changes. That includes: Man-in-the-middle attacks intercept communication between the user and the application. Weak transport security, missing HSTS, insecure redirects, mixed content, or certificate issues can make session tokens easier to expose. If a trusted account suddenly shows up somewhere risky, thatâIIs a signal. When something looks off, revoke the session or trigger step-up authentication to contain the risk without blocking everyone.
Even strong session security cannot eliminate every risk, especially when phishing, malware, or endpoint compromise is involved. Session hijacking detection helps teams identify when a valid session token is being used in a context that no longer looks like the real user. Technical indicators usually show up in session logs, authentication events, API activity, and user complaints. The goal is to catch cases where the token is still valid, but the surrounding session behavior looks wrong.
For better visibility, log every session creation, rotation, refresh, expiry, and revocation event. Track whether session IDs regenerate after login, privilege changes, password resets, MFA resets, and account recovery events. Teams should also alert on session reuse after logout or revocation. High-risk endpoints deserve closer monitoring, especially payout changes, password changes, email changes, admin actions, beneficiary updates, and API key creation.
IBM's 2024 Cost of a Data Breach Report found that breaches involving stolen or compromised credentials took an average of 292 days to identify and contain, underscoring why passive session monitoring cannot wait for a user complaint or a failed login to trigger an investigation. Some hijacked sessions look technically valid but fail the context test. The token works, but the device, location, or behavior does not match the accountâIIs normal pattern.
4. Practical Deployment, Analysis & Case Studies These signals should not automatically block every user. Real users travel, switch devices, change networks, and use privacy tools. The better approach is risk-based response: allow low-risk activity, challenge risky sessions, restrict sensitive actions, or revoke the session when risk is high.
Behavioral biometrics can help here by comparing session behavior such as typing patterns, navigation flow, touchscreen gestures, and interaction rhythm against historical patterns. It allows teams to detect suspicious post-login activity without relying only on static login checks. Related Read: How Businesses Can Stop AI Identity Fraud With Connected Risk Intelligence Session hijacking prevention relies on secure session management and continuous risk monitoring.
Bureau ID adds an extra layer by helping teams verify whether an active session still matches the real user through device, identity, and behavioral signals. According to Verizon's 2025 Data Breach Investigations Report , stolen credentials were involved in 32% of all breaches globally, and 88% of basic web application attacks relied on stolen credentials, making token and session security a central control.
For JWT and OAuth flows, use short-lived access tokens, rotate refresh tokens, and always validate signatures and expiry. This reinforces that verifying identity is only part of the equation and that protecting the session that follows is just as important. Bureau IDâIIs Device ID helps teams identify suspicious access from new, spoofed, or risky devices. Instead of blocking every new device, teams can use device intelligence to trigger step-up authentication when the token is valid but the device context looks risky.
Session hijacking often becomes visible after login because the attacker behaves differently from the real user. Teams should monitor typing speed, mouse movement, touchscreen gestures, navigation behavior, and session rhythm. For example, a user usually logs in from a known mobile device, checks their balance, and exits. Later, the same account shows a valid session from a new desktop environment, moves directly to payout settings, changes beneficiary details, and attempts a large withdrawal. The token is valid, but the behavior is wrong.
Behavioral biometrics should work as a continuous authentication signal alongside MFA. These signals also support broader account takeover prevention strategies , especially when session activity changes after login. Strong session hijacking attack prevention should avoid interrupting every user. Step-up verification should trigger when risk increases.
Depending on risk, teams can use passkeys, MFA, re-authentication, or additional verification. When possible, restrict only the sensitive action instead of terminating the full session. This helps contain the risk before session hijacking escalates into account takeover, where account takeover protection becomes critical. Session controls need ongoing review, so log all session creation, refresh, rotation, revocation, and expiry events. Revoke sessions after suspicious activity, password resets, MFA resets, and account recovery events.
Users should also be able to view and terminate active sessions. Confirmed incidents should feed back into risk rules, timeout policies, and response logic. With a unified risk decisioning platform like Bureau ID, teams can combine device, identity, behavior, and transaction signals into one workflow. That makes it easier to decide whether to allow, challenge, restrict, or terminate a session based on real risk.
When the attacker is already past the login checkpoint, session hijacking prevention depends on two things working together: secure application-layer controls and continuous session risk monitoring. For security and fraud teams, the next step is to review where session risk can still slip through. That means checking how tokens are generated, stored, rotated, expired, and revoked, then layering in device and behavioral signals to detect when an active session no longer looks like the real user.
Bureau ID helps teams add that post-login risk intelligence layer. By combining device intelligence, behavioral biometrics, identity signals, and transaction context, Bureau ID can help identify suspicious sessions, trigger step-up authentication, restrict risky actions, and reduce account takeover exposure without adding friction to every user. Session hijacking is when an attacker takes over a valid user session by stealing or misusing a session token. Once they have the token, the application may treat them as the logged-in user without asking for the password again.
Common signs include sudden location changes, user-agent changes, multiple active sessions from unlikely places, session reuse after logout, sensitive actions right after login, unusual API calls, unexpected logouts, and device or behavior patterns that do not match the real user. MFA helps reduce account compromise, but it may not stop session hijacking if the attacker steals a valid session token after authentication. That is why teams also need secure token handling, session expiry, token revocation, and post-login session monitoring.
Yes. JWT tokens can be hijacked if they are stolen, stored insecurely, exposed through XSS, or kept valid for too long. Use short-lived access tokens, refresh token rotation, strict claim validation, secure storage, and revocation controls where possible. Once an attacker gets access to a valid session token, they may not need to break the login flow, bypass MFA, or guess credentials. The application may already trust the session, which is what makes session hijacking so difficult to catch after authentication succeeds.
Session hijacking prevention focuses on protecting the full session lifecycle: how tokens are created, transmitted, stored, rotated, expired, and revoked. Strong session token security also needs real-time monitoring so teams can spot suspicious changes in device, location, behavior, or token usage before a valid session turns into an account takeover. In this guide, weâIIll explain how session hijacking works, the most common attack methods, how to detect suspicious sessions, and how to prevent session hijacking.
Session hijacking is a cyberattack where an attacker takes over a valid user session by stealing, predicting, fixing, or reusing a session token. Once the attacker has that token, the application may treat them as the authenticated user. This is why session hijacking is so risky: the login may already be complete, but the session is no longer under the userâIIs control.
Session hijacking works by abusing the token that an application uses to remember that a user is already authenticated. The application uses the token to recognize the user without asking them to log in again. The application may treat the attacker as the real user until the token expires, is revoked, or suspicious activity is detected. Session tokens work like bearer credentials, which means anyone holding a valid token may be treated as authenticated.
Long-lived sessions increase the attack window, and passing session IDs in URLs can expose tokens through browser history, logs, referrers, shared links, and support workflows. In fact, according to Microsoft's 2025 Digital Defense Report , 80% of MFA-bypass breaches are attributed to session-token theft, meaning attackers are increasingly winning after authentication, not during it.
According to the 2026 Fortinet Web Application Security Report , credential stuffing has become the top bot-attack concern for 68% of security professionals, reflecting how rapidly attackers are scaling session abuse tactics and why defenses need to keep pace. Session sniffing is when attackers monitor network traffic and capture session data as it moves between the user and the application.
Cross-site scripting allows malicious scripts to run in a userâIIs browser. If session tokens are accessible to JavaScript, attackers may be able to steal them and reuse them elsewhere. Session fixation happens when an attacker forces or tricks a user into authenticating with a session ID that the attacker already knows. If the application does not issue a fresh session ID after login, the attacker may reuse that known session to impersonate the user.
The key control is simple: regenerate session identifiers after trust level changes. That includes: Man-in-the-middle attacks intercept communication between the user and the application. Weak transport security, missing HSTS, insecure redirects, mixed content, or certificate issues can make session tokens easier to expose. If a trusted account suddenly shows up somewhere risky, thatâIIs a signal. When something looks off, revoke the session or trigger step-up authentication to contain the risk without blocking everyone.
Even strong session security cannot eliminate every risk, especially when phishing, malware, or endpoint compromise is involved. Session hijacking detection helps teams identify when a valid session token is being used in a context that no longer looks like the real user. Technical indicators usually show up in session logs, authentication events, API activity, and user complaints. The goal is to catch cases where the token is still valid, but the surrounding session behavior looks wrong.
For better visibility, log every session creation, rotation, refresh, expiry, and revocation event. Track whether session IDs regenerate after login, privilege changes, password resets, MFA resets, and account recovery events. Teams should also alert on session reuse after logout or revocation. High-risk endpoints deserve closer monitoring, especially payout changes, password changes, email changes, admin actions, beneficiary updates, and API key creation.
IBM's 2024 Cost of a Data Breach Report found that breaches involving stolen or compromised credentials took an average of 292 days to identify and contain, underscoring why passive session monitoring cannot wait for a user complaint or a failed login to trigger an investigation. Some hijacked sessions look technically valid but fail the context test. The token works, but the device, location, or behavior does not match the accountâIIs normal pattern.
These signals should not automatically block every user. Real users travel, switch devices, change networks, and use privacy tools. The better approach is risk-based response: allow low-risk activity, challenge risky sessions, restrict sensitive actions, or revoke the session when risk is high. Behavioral biometrics can help here by comparing session behavior such as typing patterns, navigation flow, touchscreen gestures, and interaction rhythm against historical patterns. It allows teams to detect suspicious post-login activity without relying only on static login checks.
Related Read: How Businesses Can Stop AI Identity Fraud With Connected Risk Intelligence Session hijacking prevention relies on secure session management and continuous risk monitoring. 5. Performance Evaluation & Extended Technical Observations Bureau ID adds an extra layer by helping teams verify whether an active session still matches the real user through device, identity, and behavioral signals.
According to Verizon's 2025 Data Breach Investigations Report , stolen credentials were involved in 32% of all breaches globally, and 88% of basic web application attacks relied on stolen credentials, making token and session security a central control. For JWT and OAuth flows, use short-lived access tokens, rotate refresh tokens, and always validate signatures and expiry.
This reinforces that verifying identity is only part of the equation and that protecting the session that follows is just as important. Bureau IDâIIs Device ID helps teams identify suspicious access from new, spoofed, or risky devices. Instead of blocking every new device, teams can use device intelligence to trigger step-up authentication when the token is valid but the device context looks risky.
Session hijacking often becomes visible after login because the attacker behaves differently from the real user. Teams should monitor typing speed, mouse movement, touchscreen gestures, navigation behavior, and session rhythm. For example, a user usually logs in from a known mobile device, checks their balance, and exits. Later, the same account shows a valid session from a new desktop environment, moves directly to payout settings, changes beneficiary details, and attempts a large withdrawal. The token is valid, but the behavior is wrong.
Behavioral biometrics should work as a continuous authentication signal alongside MFA. These signals also support broader account takeover prevention strategies , especially when session activity changes after login. Strong session hijacking attack prevention should avoid interrupting every user. Step-up verification should trigger when risk increases.
Depending on risk, teams can use passkeys, MFA, re-authentication, or additional verification. When possible, restrict only the sensitive action instead of terminating the full session. This helps contain the risk before session hijacking escalates into account takeover, where account takeover protection becomes critical. Session controls need ongoing review, so log all session creation, refresh, rotation, revocation, and expiry events. Revoke sessions after suspicious activity, password resets, MFA resets, and account recovery events.
Users should also be able to view and terminate active sessions. Confirmed incidents should feed back into risk rules, timeout policies, and response logic. With a unified risk decisioning platform like Bureau ID, teams can combine device, identity, behavior, and transaction signals into one workflow. That makes it easier to decide whether to allow, challenge, restrict, or terminate a session based on real risk.
When the attacker is already past the login checkpoint, session hijacking prevention depends on two things working together: secure application-layer controls and continuous session risk monitoring. For security and fraud teams, the next step is to review where session risk can still slip through. That means checking how tokens are generated, stored, rotated, expired, and revoked, then layering in device and behavioral signals to detect when an active session no longer looks like the real user.
Bureau ID helps teams add that post-login risk intelligence layer. By combining device intelligence, behavioral biometrics, identity signals, and transaction context, Bureau ID can help identify suspicious sessions, trigger step-up authentication, restrict risky actions, and reduce account takeover exposure without adding friction to every user. Session hijacking is when an attacker takes over a valid user session by stealing or misusing a session token. Once they have the token, the application may treat them as the logged-in user without asking for the password again.
Common signs include sudden location changes, user-agent changes, multiple active sessions from unlikely places, session reuse after logout, sensitive actions right after login, unusual API calls, unexpected logouts, and device or behavior patterns that do not match the real user. MFA helps reduce account compromise, but it may not stop session hijacking if the attacker steals a valid session token after authentication. That is why teams also need secure token handling, session expiry, token revocation, and post-login session monitoring.
Yes. JWT tokens can be hijacked if they are stolen, stored insecurely, exposed through XSS, or kept valid for too long. Use short-lived access tokens, refresh token rotation, strict claim validation, secure storage, and revocation controls where possible. Learn how mobile app attestation works on Android and iOS, what Play Integrity and App Attest verify, and where runtime protection fits.
Learn how mobile app attestation works on Android and iOS, what Play Integrity and App Attest verify, and where runtime protection fits. Compare deepfake detection software for identity fraud, voice cloning, synthetic media, and enterprise workflows across leading platforms.
Compare deepfake detection software for identity fraud, voice cloning, synthetic media, and enterprise workflows across leading platforms. Understand mobile app security, common threats, testing methods, OWASP guidance, app hardening, and runtime protection for Android and iOS apps.
Understand mobile app security, common threats, testing methods, OWASP guidance, app hardening, and runtime protection for Android and iOS apps. Leave behind fragmented tools. Stop fraud rings, cut false declines, and deliver secure digital journeys at scale Leave behind fragmented tools. Stop fraud rings, cut false declines, and deliver secure digital journeys at scale Session Hijacking falls under the OWASP Top 10 category A07: Identification and Authentication Failures. Despite being a well-documented threat with straightforward mitigation strategies, it remains a common attack vector. The impact is severe because successful hijacking grants attackers complete access to the victim's account, allowing them to perform any action the legitimate user could, often without triggering security alerts or leaving obvious audit trails.
The server receives requests containing the stolen session token and validates it against its session store. Because the session ID is valid and still active, the server cannot distinguish between the legitimate user's requests and the attacker's requests. The application treats the attacker as the authenticated user. With the hijacked session, the attacker can now perform any action the legitimate user could: view sensitive data, modify account settings, make transactions, or escalate privileges. The attack often goes undetected because the session appears legitimate to the application's logging and monitoring systems.
When applications use weak random number generators or predictable patterns for session ID creation, attackers can predict valid session tokens without stealing them. Sequential session IDs like SID001, SID002, SID003 or timestamp-based tokens allow attackers to enumerate valid sessions. Insufficient entropy in session generation enables brute-force attacks. Modern applications must use cryptographically secure random number generators (CSRNG) with at least 128 bits of entropy for session tokens.
Successful session hijacking gives attackers the same access level as the legitimate user, enabling a wide range of malicious activities. The severity depends on the privileges of the compromised account and the sensitivity of accessible data. Attackers gain full access to the victim's account, including the ability to view private messages, personal information, financial data, and transaction history. They can act as the legitimate user across the entire application without needing to know the password.
With hijacked sessions, attackers can perform actions on behalf of the user: making financial transactions, changing account settings, deleting data, sending messages, or initiating password resets to permanently lock out the legitimate user. If the hijacked session belongs to an administrator or privileged user, attackers gain elevated access to system functions, user management, configuration settings, and sensitive business operations, potentially compromising the entire application and its data.
Session hijacking often goes unnoticed because the attacker's activity appears as legitimate user actions in logs. Unlike password theft, victims may not realize their account is compromised until unusual activity occurs. Attackers can maintain access for the entire session lifetime, often hours or days if sessions don't expire properly. Configure both idle timeouts (15-30 minutes of inactivity) and absolute timeouts (maximum session lifetime regardless of activity). Short timeouts minimize the window of opportunity for attackers to exploit stolen sessions. Balance security with user experience by implementing sliding session renewal for active users.
Generate session IDs using cryptographically secure random number generators (CSRNG) with at least 128 bits of entropy. Never use predictable patterns, sequential numbers, or weak algorithms. Most modern frameworks (Express.js, Spring, Django) provide secure session ID generation by default; do not implement custom session ID generators. Store the user's IP address and User-Agent string at session creation and validate them on every request. If they change, invalidate the session as it likely indicates hijacking. Be aware of legitimate scenarios where these might change (mobile users switching networks, VPNs) and implement appropriate tolerance or multi-factor re-authentication.
Implement session fixation protection by generating a new session ID after successful login. This prevents attackers from setting a known session ID before authentication and then using it after the victim logs in. Most web frameworks provide built-in session fixation protection; ensure it's enabled. A third-party Snapchat app failed to implement proper session security, allowing attackers to hijack user sessions and download over 200,000 private photos and videos. The breach occurred because the app used predictable session tokens and didn't bind sessions to device identifiers, enabling mass account compromise through session replay attacks.
Put what you have learned into practice. Try identifying and fixing Session Hijacking vulnerabilities in our interactive coding challenges, or explore more security guides to deepen your understanding. Continue exploring the SecureCodingHub guide library for adjacent vulnerabilities and defenses. Gain higher-level permissions by exploiting flaws in role checks, admin endpoints, or function-level authorization.
Extract API keys, passwords, and tokens embedded directly in source code, configuration files, or compiled binaries. Access unauthorized resources by manipulating object identifiers in API requests or URLs. Exploit weak authentication mechanisms including credential stuffing, brute force, and session management flaws. Exploit timing windows in concurrent operations to bypass limits, duplicate transactions, or corrupt data.
Redirect users to malicious websites by manipulating URL parameters trusted by the application. Compromise software dependencies, build pipelines, or package registries to inject malicious code at scale. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Data%20center%20security • https://en.wikipedia.org/wiki/DNS%20spoofing • https://en.wikipedia.org/wiki/Trusteer • https://www.obsidiansecurity.com/blog/session-hijacking-how-it-works-how-to-stop-it • https://bureau.id/resources/blog/session-hijacking-prevention • https://www.securecodinghub.com/guides/session-hijacking • https://securecodingpractices.com/preventing-session-hijacking-techniques/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Session Hijacking Detection And Prevention System Project.
[*] Metasploit Scan Running on Target Subnet for Session Hijacking Detection And Prevention System Project... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |