Complete Technical Paper Content — Shadow It Discovery Using DNS Logs
Overview & System Context
Shadow It Discovery Using Dns Logs: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9530 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In the Domain Name System (DNS) hierarchy, a subdomain is a domain that is a part of another (main) domain. For example, if a domain offered an online store as part of their website example.com, it might use the subdomain shop.example.com.
A fully qualified domain name (FQDN) consists of multiple parts. For example, take the English Wikipedia domain en.wikipedia.org. The en is a subdomain of wikipedia.org. Although wikipedia.org is usually considered to be the domain name, wikipedia is actually a sub-domain of the org TLD (top level domain). Any fully qualified domain name can be a host or a subdomain. A domain name that does not include any subdomains is known as an apex domain, root domain, or bare domain. For example, wikipedia.org is the apex domain of Wikipedia, which redirects to the subdomain www.wikipedia.org.
Subdomains are often used by Internet service providers (ISPs) supplying web services. They allocate one (or more) subdomains to their clients who do not have their own domain name. This allows independent administration by the clients over their subdomain. Subdomains are also used by organizations that wish to assign a unique name to a particular department, function, or service related to the organization. For example, a university might assign "cs" to the computer science department, such that a number of hosts could be used inside that subdomain, such as www.cs.example.edu. There are some widely recognized subdomains such as WWW and FTP. This allows for a structure where the domain contains administrative directories and files including the FTP directories and webpages. The FTP subdomain could contain logs and the web page directories, while the WWW subdomain contains the directories for the webpages. Independent authentication for each domain provides access control over the various levels of the domain.
.ac.uk: academic (tertiary education, further education colleges and research establishments) and learned societies .co.uk: general use (usually commercial) .gov.uk: government (central and local) .judiciary.uk: courts (to be introduced in the near future) .ltd.uk: limited companies .me.uk: general use (usually personal) .mod.uk: Ministry of Defence and HM Forces public sites .net.uk: ISPs and network companies (unlike .net, use is restricted to these users) .nhs.uk: National Health Service institutions .nic.uk: network use only (Nominet UK) .org.uk: general use (usually for non-profit organisations) .parliament.uk: parliamentary use (only for the UK Parliament and the Scottish Parliament) .plc.uk: public limited companies .police.uk: police forces .sch.uk: Local Education Authorities, schools, primary and secondary education, community education Figure 1: Intune vs. JumpCloud for Discovering Shadow IT - JumpCloud Depending on application, a record inside a domain, or subdomain might refer to a hostname, or a service provided by a number of machines in a cluster. Some websites use different subdomains to point to different server clusters. For example, www.example.com points to Server Cluster 1 or Datacentre 1, and www2.example.com points to Server Cluster 2 or Datacentre 2 etc.
Google Cloud is a suite of cloud computing services offered by Google that provides a series of modular cloud services including computing, data storage, data analytics, and machine learning, alongside a set of management tools. It runs on the same infrastructure that Google uses internally for its end-user products, such as Google Search, Gmail, and Google Docs, according to Verma et al. Registration requires a credit card or bank account details. Google Cloud provides infrastructure as a service, platform as a service, and serverless computing environments. In April 2008, Google announced App Engine, a platform for developing and hosting web applications in Google-managed data centers, which was the first cloud computing service from the company. The service became generally available in November 2011. Since the announcement of App Engine, Google added multiple cloud services to the platform. Google Cloud includes Google Cloud public cloud infrastructure, as well as Google Workspace (G Suite), enterprise versions of Android and ChromeOS, and application programming interfaces (APIs) for machine learning and enterprise mapping services. Since at least 2022, Google's official materials have stated that "Google Cloud" is the new name for "Google Cloud Platform," which may cause naming confusion.
For those familiar with other notable cloud service providers, a comparison of similar services may be helpful in understanding Google Cloud Platform's offerings. April 2008 – Google App Engine announced in preview May 2010 – Google Cloud Storage launched May 2010 – Google BigQuery and Prediction API announced in preview October 2011 – Google Cloud SQL is announced in preview June 2012 – Google Compute Engine is launched in preview May 2013 – Google Compute Engine is released to GA August 2013 – Cloud Storage begins automatically encrypting each Storage object's data and metadata under the 128-bit Advanced Encryption Standard (AES-128), and each encryption key is itself encrypted with a regularly rotated set of master keys February 2014 – Google Cloud SQL becomes GA May 2014 – Stackdriver is acquired by Google June 2014 – Kubernetes is announced as an open source container manager June 2014 – Cloud Dataflow is announced in preview October 2014 – Google acquires Firebase November 2014 – Alpha release Google Kubernetes Engine (formerly Container Engine) is announced January 2015 – Google Cloud Monitoring based on Stackdriver goes into Beta March 2015 – Google Cloud Pub/Sub becomes available in Beta April 2015 – Google Cloud DNS becomes generally available April 2015 – Google Dataflow launched in beta July 2015 – Google releases v1 of Kubernetes; Hands it over to The Cloud Native Computing Foundation August 2015 – Google Cloud Dataflow, Google Cloud Pub/Sub, Google Kubernetes Engine, and Deployment Manager graduate to GA November 2015 – Bebop is acquired, and Diane Greene joins Google February 2016 – Google Cloud Functions becomes available in Alpha September 2016 – Apigee, a provider of application programming interface (API) management company, is acquired by Google September 2016 – Stackdriver becomes generally available November 2016 – Qwiklabs, an EdTech company is acquired by Google February 2017 – Cloud Spanner, highly available, globally-distributed database is released into Beta March 2017 – Google acquires Kaggle, world's largest community of data scientists and machine learning enthusiasts April 2017 – MIT professor Andrew Sutherland breaks the record for the largest ever Compute Engine cluster with 220,000 cores on Preemptible VMs. May 2017 – Google Cloud IoT Core is launched in Beta November 2017 – Google Kubernetes Engine gets certified by the CNCF February 2018 – Google Cloud IoT Core becomes generally available February 2018 – Google announces its intent to acquire Xively February 2018 – Cloud TPUs, ML accelerators for Tensorflow, become available in Beta May 2018 – Google Cloud Memorystore becomes available in Beta April 2019 – Google Cloud Run (fully managed) Beta release April 2019 – Google Anthos announced November 2019 – Google Cloud Run (fully managed) General availability release March 2020 – Due to the COVID-19 pandemic, Google Cloud postponed the online streaming version of its Google Cloud Next mega-conference, two weeks after it canceled the in-person version. October 2020 – Google Cloud announced that it will become a block producer candidate for the EOS network and EOS.IO protocol. Currently the top block producers are cryptocurrency exchanges like OKEx and Binance. February 2021 – Google Kubernetes Engine Autopilot is introduced. May 2021 – Vertex AI announced at Google.io June 2021 – In 2021, Apple was Google Cloud's biggest customer. April 2022 – MobiledgeX acquired and joins Google Cloud. March 2023 – Google brings generative AI capabilities to Google Cloud. May 2024 Google Cloud partnered with Airtel. April 2025 – At Google Cloud Next 2025 in Las Vegas, Google announced the seventh-generation Tensor Processing Unit, named Ironwood, claiming 3,600 times better performance than its first publicly available TPU. Google also announced Cloud Wide Area Network (Cloud WAN), making its private global network available to enterprise customers, and introduced Gemini 2.5 and Gemini 2.5 Flash reasoning models.
April 2026 – At Google Cloud Next '26, Sundar Pichai announced expanded AI infrastructure investments, including the introduction of Trillium TPUs (8th generation) and the Gemini Enterprise Agent Platform, with Google reporting that 75% of new internal code was AI-generated. Figure 2: How To Discover Unauthorized Apps via SSO Logs (Entra ID) Instagram is an American photo and short-form video sharing social networking service owned by Meta Platforms. It allows users to upload media that can be edited with filters, be organized by hashtags, and be associated with a location via geographical tagging. Posts can be shared publicly or with preapproved followers. Users can browse other users' content by tags and locations, view trending content, like photos, and follow other users to add their content to a personal feed. A Meta-operated image-centric social media platform, it is available on iOS, Android, Windows, and the Web. Users can take photos and edit them using built-in filters and other tools, then share them on other social media platforms like Facebook. It supports 33 languages including English, Hindi, Spanish, French, Japanese, and Korean. Instagram was originally distinguished by allowing content to be framed only in a square (1:1) aspect ratio of 640 pixels to match the display width of the iPhone at the time. In 2015, this restriction was eased with an increase to 1080 pixels. It also added messaging features, the ability to include multiple images or videos in a single post, and a Stories feature—similar to its main competitor at the time, Snapchat, which allowed users to post their content to a sequential feed, with each post accessible to others for 24 hours. As of January 2019, Stories was used by 500 million people daily.
Instagram was launched for iOS in October 2010 by Kevin Systrom and the Brazilian software engineer Mike Krieger. It rapidly gained popularity, reaching 1 million registered users in two months, 10 million in a year, and 1 billion in June 2018. In April 2012, Facebook acquired the service for approximately US$1 billion in cash and stock. The Android version of Instagram was released in April 2012, followed by a feature-limited desktop interface in November 2012, a Fire OS app in June 2014, an app for Windows 10 in October 2016, and an app for iPadOS in September 2025. Although often admired for its success and influence, Instagram has also been criticized for negatively affecting teens' mental health, its policy and interface changes, its alleged censorship, and illegal and inappropriate content uploaded by users.
Instagram began development in San Francisco as Burbn, a mobile check-in app created by Kevin Systrom and Mike Krieger. On March 5, 2010, Systrom closed a $500,000 (equivalent to $700,000 in 2024) seed funding round with Baseline Ventures and Andreessen Horowitz while working on Burbn. Realizing that it was too similar to Foursquare, they refocused their app on photo-sharing, which had become a popular feature among its users. They renamed it Instagram, a portmanteau of instant camera and telegram.
Josh Riedel joined the company in October as Community Manager, Shayne Sweeney joined in November as an engineer, and Jessica Zollman joined as a Community Evangelist in August 2011. The first Instagram post was a photo of South Beach Harbor at Pier 38, posted by Mike Krieger at 5:26 p.m. on July 16, 2010. On October 6, 2010, the Instagram iOS app was officially released through the App Store. In February 2011, it was reported that Instagram had raised $7 million (equivalent to $9,601,662 in 2024) in Series A funding from a variety of investors, including Benchmark Capital, Jack Dorsey, Chris Sacca (through Capital fund), and Adam D'Angelo. The deal valued Instagram at around $20 million. In April 2012, Instagram raised $50 million (equivalent to $67,320,000 in 2024) from venture capitalists with a valuation of $500 million (equivalent to $673,200,000 in 2024). Joshua Kushner was the second largest investor in Instagram's Series B fundraising round, leading his investment firm, Thrive Capital, to double its money after the sale to Facebook.
Figure 3: Shadow IT Discovery : Detect & Eliminate Hidden SaaS Risks ... In November 2012, Instagram launched website profiles, allowing anyone to see user feeds from a web browser with limited functionality, as well as a selection of badges, and web widget buttons to link to profiles. Since the app's launch it had used the Foursquare API technology to provide named location tagging. In March 2014, Instagram started to test and switch the technology to use Facebook Places.
In June 2015, the desktop website user interface was redesigned to become more flat and minimalistic, but with more screen space for each photo and to resemble the layout of Instagram's mobile website. Furthermore, one row of pictures only has three instead of five photos to match the mobile layout. The slideshow banner on the top of profile pages, which simultaneously slide-showed seven picture tiles of pictures posted by the user, alternating at different times in a random order, has been removed. In addition, the formerly angular profile pictures became circular.
In April 2016, Instagram released a Windows 10 Mobile app, after years of demand from Microsoft and the public to release an app for the platform. The platform previously had a beta version of Instagram, first released on November 21, 2013, for Windows Phone 8. The new app added support for videos (viewing and creating posts or stories, and viewing live streams), album posts and direct messages. Similarly, an app for Windows 10 personal computers and tablets was released in October 2016. In May, Instagram updated its mobile website to allow users to upload photos, and to add a "lightweight" version of the Explore tab.
On May 11, 2016, Instagram revamped its design, adding a black-and-white flat design theme for the app's user interface, and a less skeuomorphistic, more abstract, "modern" and colorful icon. Rumors of a redesign first started circulating in April, when The Verge received a screenshot from a tipster, but at the time, an Instagram spokesperson simply told the publication that it was only a concept. On December 6, 2016, Instagram introduced comment liking. However, unlike post likes, the user who posted a comment does not receive notifications about comment likes in their notification inbox. Uploaders can optionally decide to deactivate comments on a post.
The mobile website allows uploading pictures since May 4, 2017. Image filters and the ability to upload videos were not introduced then. On April 30, 2019, the Windows 10 Mobile app was discontinued, though the mobile website remains available as a progressive web application (PWA) with limited functionality. The app remains available on Windows 10 computers and tablets, also updated to a PWA in 2020.
In April 2024, Instagram announced that they would start testing new tools "within weeks" to fight sextortion, a form of blackmail involving intimate pictures sent online. On August 2, 2024, Turkey blocked Instagram after the platform deleted posts from users offering condolences for the death of Hamas leader Ismail Haniyeh. In December 2024, Instagram and MTA collaborated and sold Metrocards ft. creators such as New York Nico, Overheard in New York, and SubwayTakes. On September 3, 2025, Instagram launched a native iPadOS app, which before relied on the iOS app and did not utilize the larger screen size of tablets. In February 2026, Meta announced a new safety feature on Instagram that will alert parents if their teenage children repeatedly search for content related to suicide or selfIharm, as part of expanded parental supervision tools amid legal scrutiny of its impact on youth. Meta scheduled an end of support for end-to-end encryption in Instagram direct messaging in May 2026. Following this change, messages are no longer protected by end-to-end encryption and are not exclusively accessible only to the communicating users. As a result, the level of confidentiality in direct messages is reduced compared to fully encrypted communications, and message content may be accessible under certain conditions, depending on applicable policies and regulatory frameworks. The change prompted concerns among privacy researchers and digital rights commentators regarding reduced message confidentiality and broader implications for messaging privacy and data protection. In August 2026, Instagram updated its wordmark for the first time in about a decade, replacing its previous script-style lettering with a redesigned typeface that combines script and print elements. The camera icon remained unchanged.
Users can upload photographs and short videos, follow other users' feeds, and geotag images with the name of a location. Users can set their account as "private", thereby requiring that they approve any new follower requests. Users can connect their Instagram account to other social networking sites, enabling them to share uploaded photos to those sites. In September 2011, a new version of the app included new and live filters, instant tilt–shift, high-resolution photographs, optional borders, one-click rotation, and an updated icon. Photos were initially restricted to a square, 1:1 aspect ratio; since August 2015, the app supports portrait and widescreen aspect ratios as well. Users could formerly view a map of a user's geotagged photos.
The feature was removed in September 2016, citing low usage. Since December 2016, posts can be "saved" into a private area of the app. The feature was updated in April 2017 to let users organize saved posts into named collections. Users can also "archive" their posts in a private storage area, out of visibility for the public and other users. The move was seen as a way to prevent users from deleting photos that don't garner a desired number of "likes" or are deemed boring, but also as a way to limit the "emergent behavior" of deleting photos, which deprives the service of content. In August, Instagram announced that it would start organizing comments into threads, letting users more easily interact with replies. Since February 2017, up to ten pictures or videos can be included in a single post, with the content appearing as a swipeable carousel. The feature originally limited photos to the square format, but received an update in August to enable portrait and landscape photos instead. In April 2018, Instagram launched its version of a portrait mode called "focus mode", which gently blurs the background of a photo or video while keeping the subject in focus when selected. In November, Instagram began to support Alt text to add descriptions of photos for the visually impaired. They are either generated automatically using object recognition (using existing Facebook technology) or manually specified by the uploader. On March 1, 2021, Instagram launched a new feature named Instagram Live Rooms, which lets four people go live together. In May 2021, Instagram announced a new accessibility feature for videos on Instagram Reels and Stories to allow creators to place closed captions on their content.
IGTV was a vertical video application launched by Instagram in June 2018. Basic functionality is also available within the Instagram app and website. IGTV allows uploads of up to 10 minutes in length with a file size of up to 650 MB, with verified and popular users allowed to upload videos of up to one hour in length with a file size of up to 5.4 GB. The app automatically begins playing videos as soon as it is launched, which CEO Kevin Systrom contrasted to video hosts where one must first locate a video. In March 2022, the application was shut down.
Instagram Reels is the short-form section of the American social media platform Instagram. Reels focuses on vertical videos that are less than 90 seconds of duration and various features for user interaction. As of November 2024, Reels averages at 150 billion views a day. Creators earn money based on the amount of views they receive, or through ad revenue. In November 2019, it was announced that Instagram would start to roll out a new feature to Brazil known as Instagram Reels. It would then expand to France and Germany. Instagram Reels was officially launched in Pakistan in August 2022, two years after its global rollout in August 2020. It functions similarly to the Chinese video service TikTok, focusing on allowing users to create short videos already set to existing sounds from other clips. Users could make up to 15 (later 30) second videos using this feature. Reels also uses existing Instagram filters and editing tools. In July 2020, Instagram rolled out Reels to India after TikTok was banned in the country. Then, the following month, Reels officially launched in 50 countries including the United States, Canada and United Kingdom. Then in August of that year, Instagram introduced a reels button on the home page. On June 17, 2021, Instagram launched full-screen advertisements in Reels. The ads are similar to regular reels and can run up to 30 seconds. They are distinguished from regular content by the "sponsored" tag under the account name. Despite the "TikTokification" of Reels and the parent company Meta spending millions on courting content creators, user engagement continued to lag way behind TikTok as of 2022. Then Instagram started rolling out a new feature with made Reels up to 90 seconds long beginning in June 2022. After a period of testing, a duration of up to three minutes was announced in January 2025. On February 26, 2025, Instagram Reels came under fire after numerous users reported a sudden surge in violent and graphic content appearing in their feeds. Meta issued a public apology, stating that a technical error led to the unintended recommendation of such content. A Meta spokesperson explained, "We have fixed an error that caused some users to see content in their Instagram Reels feed that should not have been recommended. We apologize for the mistake." Since its inception in 2020, the usage of Instagram Reels has continuously increased. In September 2022, Instagram Reels generated over 140 billion views daily. The number of monthly users also increased from 1.5 billion in 2022 to 1.8 billion as of 2024.
Researchers from the Guizhou University of Finance and Economics and Western Michigan University found that short-form videos like YouTube Shorts, TikTok, and Instagram Reels may make it easier for young adults and children to develop addictive behavior because short-form videos provide "short bursts of thrills". These researchers found that college students in the U.S. and China watch short-form videos for entertainment, knowledge, and to build social identities. The Wall Street Journal reported that some parents are concerned about the effects of short-form videos on their children, as there is no way to disable Instagram or set limits. When children watch short-form videos, they learn to expect continual stimulation and fast-paced changes, which can cause problems when engaging in activities that require greater focus, such as reading.
Recent studies highlighted the connection between short-form videos such as Instagram Reels and the brain's reward system, specifically dopamine release. According to Dr. Anna Lembke, a psychiatrist and chief of Stanford University's dual diagnosis addiction clinic, brief attention-grabbing videos act as powerful stimuli triggering dopamine surges akin to other addictive behaviors. The rapid and easily consumable nature of short-form videos can elicit high levels of dopamine; since dopamine serves as a motivator rather than a direct source of pleasure, individuals are compelled to seek rewarding activities and become addicted to them. Such neurochemical responses lead to addictive patterns and behaviors, entering a vicious cycle.
Digital addiction can lead to shorter attention spans and slower cognitive processing. In August 2016, Instagram launched Instagram Stories, a feature that allows users to take photos, add effects and layers, and add them to their Instagram story. Images uploaded to a user's story expire after 24 hours. The media noted the feature's similarities to Snapchat. In response to criticism that it copied functionality from Snapchat, CEO Kevin Systrom told Recode that "Day One: Instagram was a combination of Hipstamatic, Twitter [and] some stuff from Facebook like the 'Like' button. You can trace the roots of every feature anyone has in their app, somewhere in the history of technology". Although Systrom acknowledged the criticism as "fair", Recode wrote that "he likened the two social apps' common features to the auto industry: Multiple car companies can coexist, with enough differences among them that they serve different consumer audiences".
Systrom further stated that "When we adopted [Stories], we decided that one of the really annoying things about the format is that it just kept going and you couldn't pause it to look at something, you couldn't rewind. We did all that, we implemented that." He also told the publication that Snapchat "didn't have filters, originally. They adopted filters because Instagram had filters and a lot of others were trying to adopt filters as well." In November, Instagram added live video functionality to Instagram Stories, allowing users to broadcast themselves live, with the video disappearing immediately after ending. In January 2017, Instagram launched skippable ads, where five-second photo and 15-second video ads appear in-between different stories. In April 2017, Instagram Stories incorporated augmented reality stickers, a "clone" of Snapchat's functionality.
In May 2017, Instagram expanded the augmented reality sticker feature to support face filters, letting users add specific visual features onto their faces. Later in May, TechCrunch reported about tests of a Location Stories feature in Instagram Stories, where public Stories content at a certain location are compiled and displayed on a business, landmark or place's Instagram page. A few days later, Instagram announced "Story Search", in which users can search for geographic locations or hashtags and the app displays relevant public Stories content featuring the search term. In June 2017, Instagram revised its live-video functionality to allow users to add their live broadcast to their story for availability in the next 24 hours, or discard the broadcast immediately. In July, Instagram started allowing users to respond to Stories content by sending photos and videos, complete with Instagram effects such as filters, stickers, and hashtags. Stories were made available for viewing on Instagram's mobile and desktop websites in late August 2017. On December 5, 2017, Instagram introduced "Story Highlights", also known as "Permanent Stories", which are similar to Instagram Stories, but don't expire. They appear as circles below the profile picture and biography and are accessible from the desktop website as well. In June 2018, the daily active story users of Instagram had reached 400 million users, and monthly active users had reached 1 billion active users. In December 2024, Instagram announced that it was trialing a feature designed to help users reconnect with content they may have missed from their mutual followers. This new functionality showcases unseen Story Highlights at the end of the Stories tray, which is situated at the top of the feed. By doing so, users can easily access curated Stories from the past week that they might not have seen previously.
Importantly, this feature will only display Story Highlights—curated collections of Stories saved by users—rather than standard Stories that disappear after 24 hours. Users will only be able to view these Highlights after they have gone through all current Stories in their tray, meaning that those who follow many accounts may find it challenging to see these updates. 2. System Architecture & Core Working Principles Sharenting is when parents post content, including images, about their children. Instagram is one of the main sites for sharenting. The hashtag #letthembelittle contains over 10 million images related to children on Instagram. Bare 2020 analysed 300 randomly selected images under the hashtag and found they tended to contain children's personal information, including name, age and location.
After being released in October 2010, Instagram had one million registered users in December 2010. In June 2011, it announced that it had 5 million users, which increased to 10 million in September. This growth continued to 30 million users in April 2012, 80 million in July 2012, 100 million in February 2013, 130 million in June 2013, 150 million in September 2013, 300 million in December 2014, 400 million in September 2015, 500 million in June 2016, 600 million in December 2016, 700 million in April 2017, and 800 million in September 2017. In June 2011, Instagram passed 100 million photos uploaded to the service.
This grew to 150 million in August 2011, and by June 2023, there were over 50 billion photos uploaded to the service. In October 2016, Instagram Stories reached 100 million active users, two months after launch. This increased to 150 million in January 2017, 200 million in April, surpassing Snapchat's user growth, and 250 million active users in June 2017. In April 2017, Instagram Direct had 375 million monthly users.
Like many social media sites, Instagram employs a combination of automated algorithms, user reports and human review to identify and remove illegal content such as child abuse and encouragement of terrorism. The system also aims to identify cyberbullying, hate speech and misinformation. Although the U.S. government has little direct power to force social media sites to remove specific content, Instagram has on occasion done so voluntarily, especially to avoid being seen as aiding the spread of fake news. On October 30, 2020, Instagram temporarily removed the "recent" tab on hashtag pages to prevent the spread of misinformation regarding the 2020 United States presidential election. On January 7, 2021, following the attack on the U.S. Capitol by supporters of then-President Donald Trump, Trump was banned from Instagram "indefinitely". Zuckerberg stated "We believe the risks of allowing the President to continue to use our service during this period are simply too great." Instagram has been criticized in India for not taking steps to counter homophobic and transphobic contents. According to the LGBT activist Indrajeet Ghorpade, "Hateful homophobic content in English is removed but the same in Indian languages is allowed to remain on the platform... despite flagging the hateful and homophobic content to Instagram, no action has been taken." In 2023, a 16-year-old queer artist allegedly died by suicide after receiving thousands of hate comments on Instagram.
Instagram has a clear set of rules about what is and isn't allowed on the site. We encourage people who come across illegal or inappropriate content to report it to us using the built-in reporting tools next to every photo, video or comment, so we can take action. People can't buy things on Instagram, we are simply a place where people share photos and videos. However, new incidents of illegal drug trade have occurred in the aftermath of the 2013 revelation, with Facebook, Inc., Instagram's parent company, asking users who come across such content to report the material, at which time a "dedicated team" reviews the information. In 2019, Facebook announced that influencers are no longer able to post any vape, tobacco products, and weapons promotions on Facebook and Instagram.
Instagram has been blocked by China following the 2014 Hong Kong protests as many confrontations with police and incidents occurring during the protests were recorded and photographed. Hong Kong and Macau were not affected as they are part of special administrative regions of China. Sometimes the phrase "Chinese Instagram" is used to refer to Xiaohongshu, a competitor social media app.
Instagram was one of the last freely available global social media sites in Iran. According to the IFJ, Instagram is popular among Iranians because it is seen as an outlet for freedom and a "window to the world". Still, Iran has sentenced citizens to prison for posts made on their Instagram accounts. The Iranian government blocked Instagram periodically during anti-government protests in 2019-20. In July 2021, Instagram temporarily censored videos with the phrase "death to Khamenei". As of September 2022, it was blocked permanently, along with WhatsApp, with an exception made for tourists and corporations who request its use.
A few days after a fire incident that happened in the Koryo Hotel in North Korea on June 11, 2015, authorities blocked Instagram to prevent photos of the incident from being spread. In May 2017, a survey conducted by the United Kingdom's Royal Society for Public Health, featuring 1,479 people aged 14–24 and asking them to rate social media platforms depending on anxiety, depression, loneliness, bullying and body image, concluded that Instagram was the "worst for young mental health". Some have suggested it may contribute to digital dependence, whilst this same survey noticed its positive effects, including self-expression, self-identity, and community building. In response to the survey, Instagram said that "Keeping Instagram a safe and supportive place for young people was a top priority". The company filters out the reviews and accounts. If some of the accounts violate Instagram's community guidelines, it will take action, which could include banning them. In 2017, researchers from Harvard University and University of Vermont demonstrated a machine learning tool that successfully outperformed general practitioners' diagnostic success rate for depression. The tool used color analysis, metadata components, and face detection of users' feeds. In 2019, Instagram began to test the hiding of like counts for posts made by its users, with the feature later made available to everyone.
In 2021, Instagram announced that like counts would return to be publicly viewable by default. Users can choose to switch them off for their whole feed or on a per-post basis. Correlations have been made between Instagram content and dissatisfaction with one's body, as a result of people comparing themselves to other users. In a recent survey, half of the applicants admitted to photo editing behavior which has been linked with concerns over body image. In October 2021, CNN published an article and interviews on two young women, Ashlee Thomas and Anastasia Vlasova, saying Instagram endangered their lives due to it having toxic effects on their diets. In October 2023, 42 U.S. states filed a lawsuit against Instagram and parent company Meta, accusing them of contributing to a youth mental health crisis due to the addictive nature of the platforms. The lawsuit claimed that Meta and its Instagram unit repeatedly misled the public about the dangers of its platforms and knowingly induced young children and teenagers into addictive and compulsive social media use. Meta representatives replied that they were disappointed with the lawsuit and were hoping instead to continue working with other companies from the industry to create new and better standards for applications teens use.
To help us deliver interesting paid or sponsored content or promotions, you agree that a business or other entity may pay us to display your username, likeness, photos (along with any associated metadata), and/or actions you take, in connection with paid or sponsored content or promotions, without any compensation to you. There was no option for users to opt out of the changed Terms of Service without deleting their accounts before the new policy went into effect on January 16, 2013. The move garnered severe criticism from users, prompting Instagram CEO Kevin Systrom to write a blog post one day later, announcing that they would "remove" the offending language from the policy. Citing misinterpretations about its intention to "communicate that we'd like to experiment with innovative advertising that feels appropriate on Instagram", Systrom also stated that it was "our mistake that this language is confusing" and that "it is not our intention to sell your photos".
Furthermore, he wrote that they would work on "updated language in the terms to make sure this is clear". The policy change and its backlash caused competing photo services to use the opportunity to "try to lure users away" by promoting their privacy-friendly services, and some services experienced substantial gains in momentum and user growth following the news. On December 20, Instagram announced that the advertising section of the policy would be reverted to its original October 2010 version. The Verge wrote about that policy as well, however, noting that the original policy gives the company right to "place such advertising and promotions on the Instagram Services or on, about, or in conjunction with your Content", meaning that "Instagram has always had the right to use your photos in ads, almost any way it wants. We could have had the exact same freakout last week, or a year ago, or the day Instagram launched". The policy update also introduced an arbitration clause, which remained even after the language pertaining to advertising and user content had been modified.
The most-liked photo on Instagram is a carousel of photos from footballer Lionel Messi celebrating winning the 2022 FIFA World Cup, The post has over 76 million likes. In 2022, Instagram was the second most downloaded mobile app of the year. Criticism of Facebook Dronestagram Instagram face – Beauty standard based on digitally altered photographs Instagram husband – Unacknowledged photographer behind another's social media posts Internet celebrity – Person who has become famous through their use of the InternetPages displaying short descriptions of redirect targets List of social networking services Pheed – Pay-per-view social media platform Pixnet – Taiwanese social media service Social media and suicide Timeline of social media Official website Rose, Kevin (May 30, 2013). "A #Nofilter Conversation with the founders of Instagram" (podcast).
Commonwealth Club. "Instagram: Kevin Systrom and Mike Krieger" (podcast). How I Built This. NPR. September 19, 2016. BBC News Hindi (July 2, 2026). Instagram III IIII II IIIII IIIIII II IIIIIIIII - BBC Eye II II IIIIIIIIIIIII (BBC Hindi) [A terrifying world hidden within Instagram exposed]. Retrieved July 5, 2026 – via YouTube.
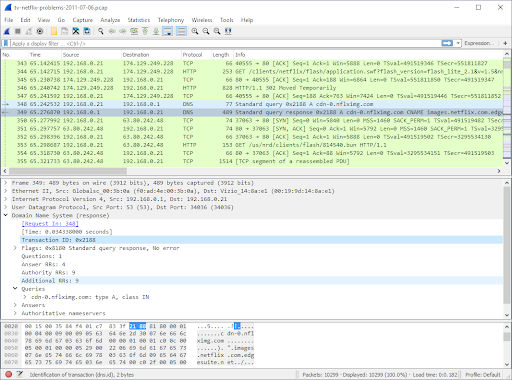
If you run IT or security, some of the apps your staff relies on have never crossed your desk. That is shadow IT, the unsanctioned tools and services running without sign-off, and it matters because those tools are where sensitive data quietly ends up and compliance gaps open. Every app has to look up a domain before it loads, so it shows up in your DNS data before a connection is even made. That record tells you the app and the device that reached for it.
DNS does not tell you everything, though. This guide covers what DNS analytics finds, what it misses, and what to do once you spot unauthorized technology on your network. DNS analytics detects shadow IT because every app resolves a domain before it loads, and DNS filtering tools like Control D log those requests. That single record is enough to reveal an unsanctioned tool and the device using it.
When someone opens an unsanctioned app, their device asks a resolver to turn the app's domain into an IP address. Control D logs that query with three details: This is why DNS analytics casts such a wide net. It catches anything that touches the internet, whether it is installed software, a browser-based tool, or a site someone just opened in a tab, because all of them resolve a domain first.
That holds whether someone bought the tool or is testing its free tier, got it approved or not, or signed up with a personal email. DNS resolution happens on every connection. Control D can run at both the resolver and the endpoint, so the record follows users off-network instead of stopping at the office door.
You spot shadow IT by filtering your DNS logs for a handful of patterns that separate unsanctioned tools from ordinary traffic. The evidence is already there. The problem is volume: organizations routinely discover more SaaS applications and cloud usage than they expected, often several times what IT departments officially manage.
3. Software Implementation, Frameworks & Protocols Most of that is noise: ad trackers, CDNs, and vendor telemetry resolving all day, unusual destinations and unfamiliar subdomains mixed in with the tools employees actually use. Categorization is what makes the log readable. Control D sorts every domain into a Filter category and tracks over 1,000 individual Services , from Dropbox to TeamViewer to ChatGPT, so you read app names instead of raw hostnames.
From there, four patterns tell you where to look. None is proof on its own; each is a place to start. Filter the log by a specific Service and ask a direct question, like which devices have reached a file-hosting or remote-access tool. You get named apps back, which you can cross-reference against your approved application list to make the unauthorized tools stand out.
Anomaly detection catches unusual increases in lookups to a Service. Watch for a cloud storage app climbing over a week, or one team's devices all converging on the same domain. This is the anchor signal. Filter by a category like File Hosting or Artificial Intelligence to see the unapproved footprint and which devices it belongs to.
Filter by result code to pull NXDOMAIN responses, which in unusual volume can flag a misconfigured or evasive device. The VPN & DNS category Filter covers tools built to skirt DNS policy. All of this sits in Control D's Analytics view and Activity Log , filterable by category, Service, and result code, and the same data streams to your SIEM so you can line it up with identity or endpoint logs.
DNS discovery is wide, but partial. It shows you which app and which device, but not who signed in or what data moved. Three limits are worth knowing. When a personal cloud drive resolves from a work laptop, DNS tells you the app is in use and on which device. It does not tell you: DNS reads the domain, not the session or the data, so on its own, DNS analytics does not give you detailed user activity. It can flag that sensitive data may be leaving through an unapproved app, but it cannot confirm what left.
For a regulated team, that gap is where compliance violations hide , since sensitive customer data can land in an app nobody reviewed. Fully protecting sensitive data takes a layer beyond DNS. DNS pointed at a third-party encrypted resolver ( DoH or DoT ) never reaches yours, so those queries stay invisible. On-premises firewall logs go dark the moment a device leaves the building. This gap is the one you can close for managed devices, because Control D also runs as an endpoint agent that logs their queries on any network they connect to, which you can deploy at scale via your RMM/MDM tool .
Historic investigation needs Full Analytics switched on, so if you want to trace a past incident rather than only watch live traffic, turn it on before you need it. No single method sees everything, so effective shadow IT discovery benefits from combining multiple data sources, with network-level data as the base.
DNS analytics is the widest, lowest-effort first net, so pair it with one identity or endpoint signal to answer the account question DNS cannot. CASBs use network traffic analysis to inspect cloud traffic and often assign each app a risk score, which is useful once you know an app exists.
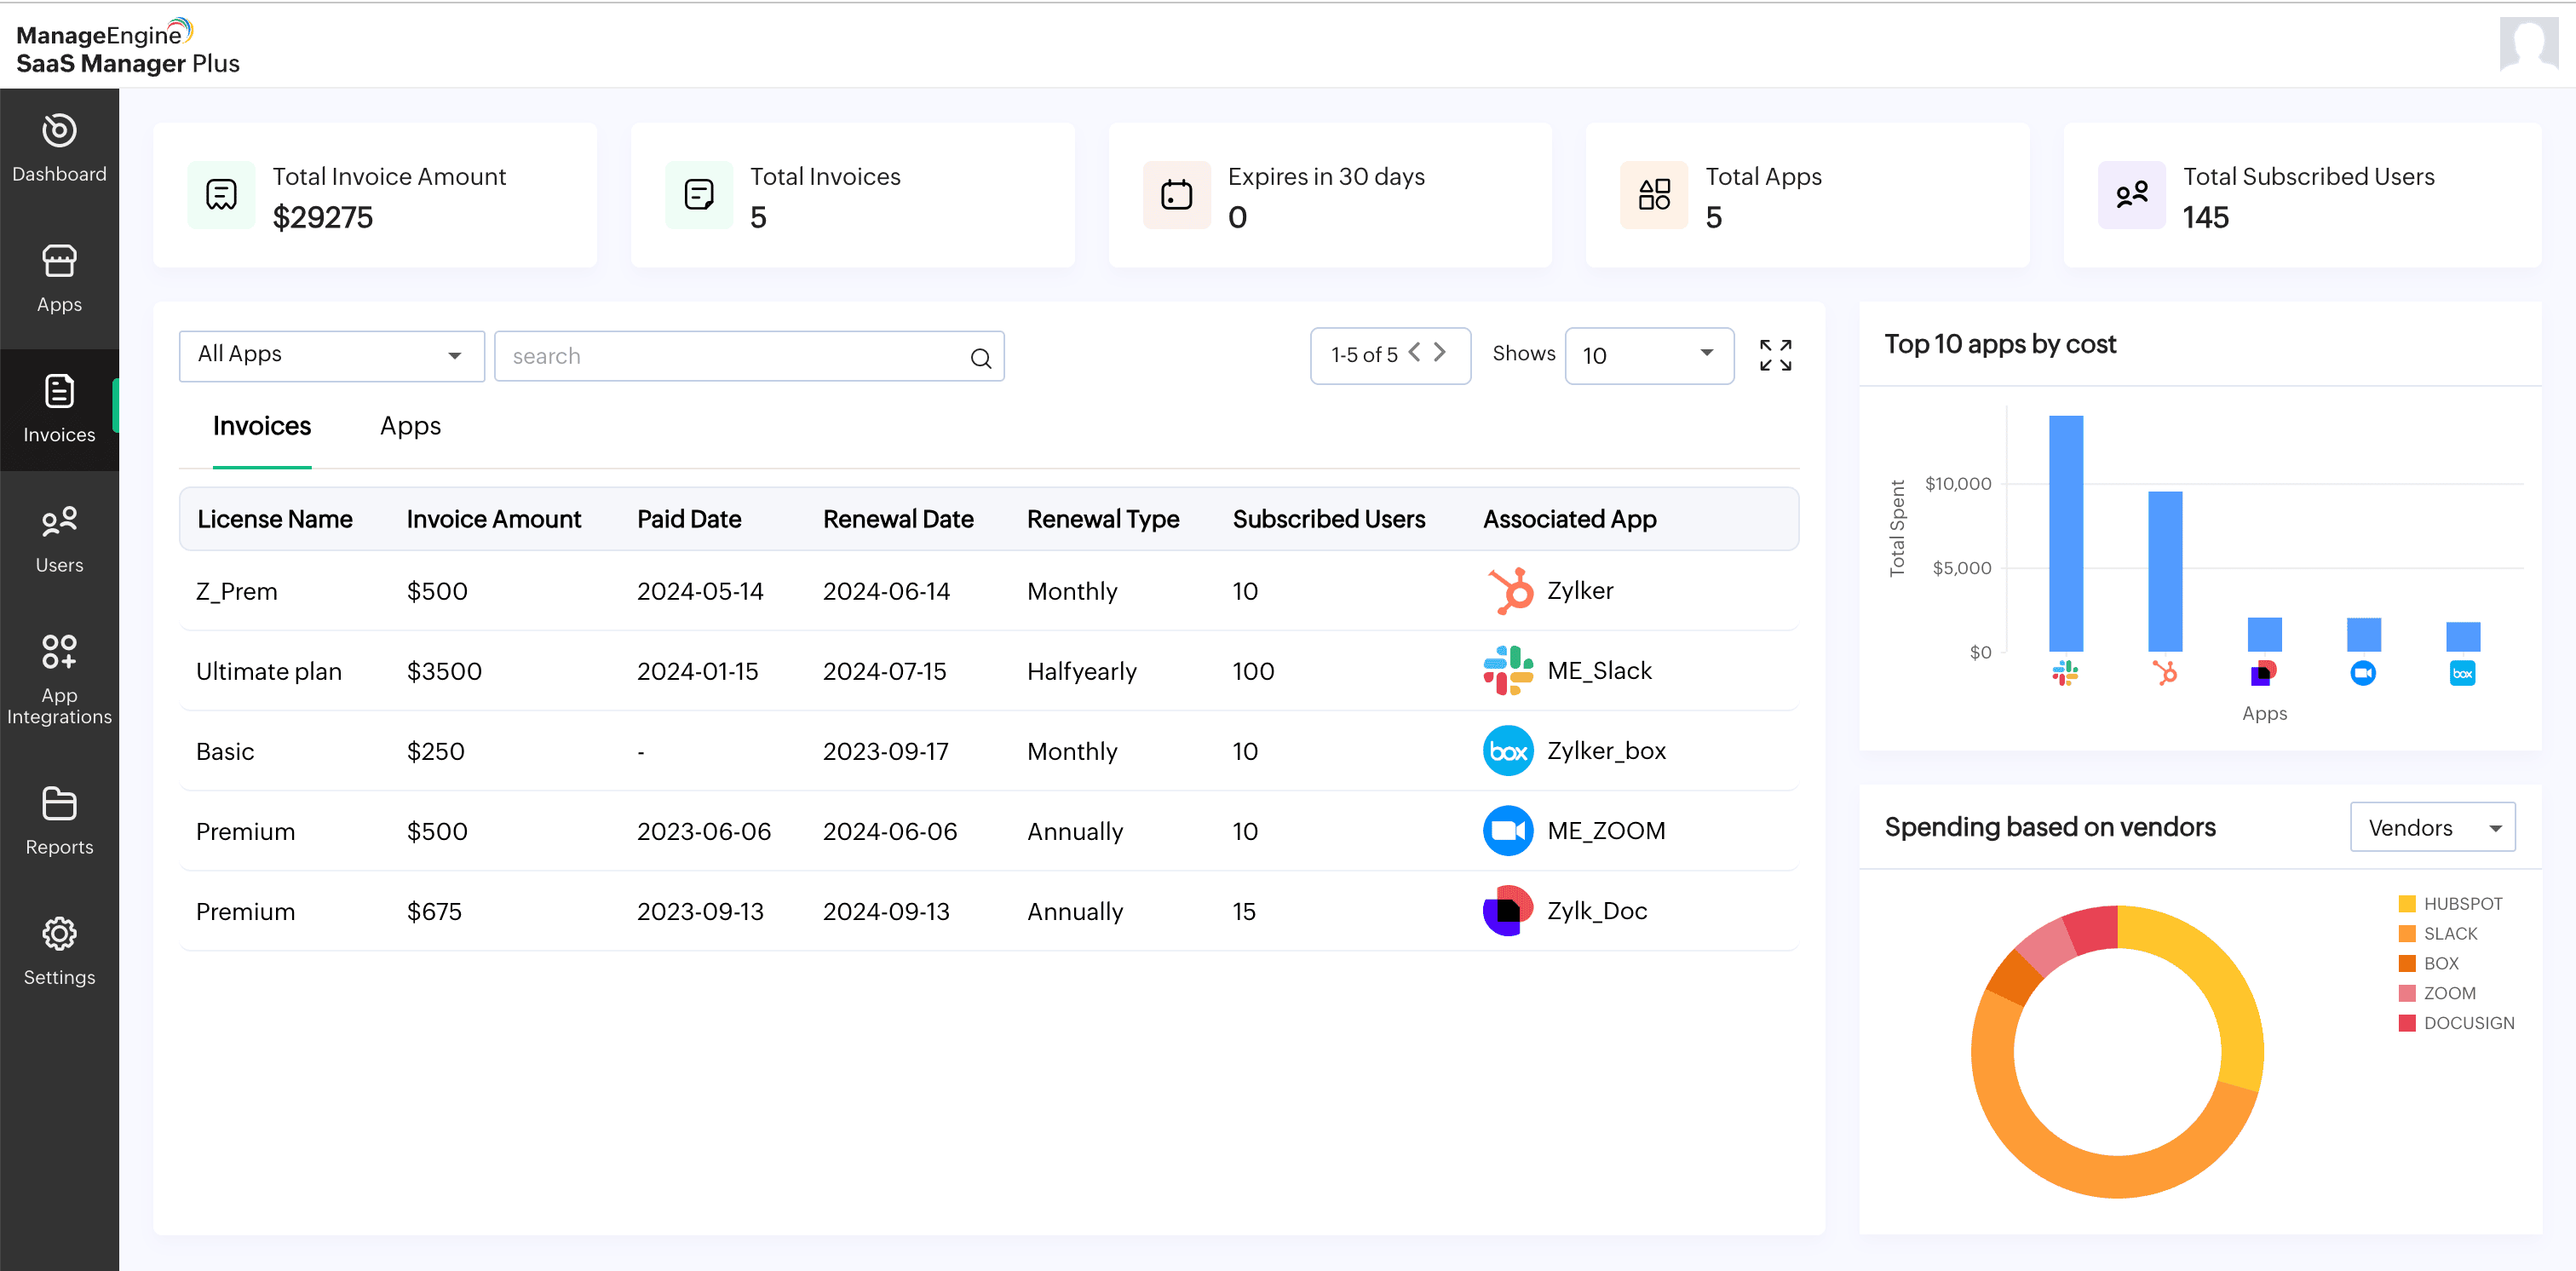
SaaS management platforms are good at spend and licenses, but a tool someone signed up for today hasn't generated either yet. DNS sees it the moment it resolves a domain. There are plenty of detection tools and security solutions in this space, but network monitoring at the DNS layer sees the broadest set of apps, which is why it belongs at the base of the discovery process.
Discovering shadow AI is close to a perfect case for DNS, because DNS analytics can detect employee use of generative AI tools even when nobody rolled them out. Almost every AI tool is a cloud service that resolves a provider domain before it runs, so it leaves a DNS record where other discovery methods see nothing. A browser-based assistant slips past: That is how shadow AI tools surface. Control D tracks the major providers (ChatGPT, Gemini, Claude, Copilot) as named Services under the Artificial Intelligence category, so you filter by that category and get a direct list of which AI tools are in use and where.
4. Practical Deployment, Analysis & Case Studies On Control D's Full Metal Packet podcast , ISO 27001 lead auditor John Verry said most SaaS products now ship AI features and that a typical thousand-person company already runs over a hundred AI use cases, almost none reviewed. Those are his figures, not a verified benchmark, but they track with what security teams are seeing.
Although DNS cannot read the prompts or the sensitive information leaked inside, it shows you the usage and helps find the exposure. The Corporation of Massey Hall and Roy Thomson Hall runs IT for two of Toronto's busiest concert venues, covering public Wi-Fi and a hybrid workforce across both sites.
After moving its DNS filtering to Control D, the team gained real-time insight into DNS activity across the internal network, and that visibility surfaced apps and services departments were using without IT approval. IT manager Neil Bowen was clear about the intent. The team was not trying to invade privacy. DNS analytics showed which apps were in use at the device and network level, without the keystroke tracking that turns discovery into surveillance.
Once you find an unsanctioned app, decide whether to block it, approve it, or replace it, and enforce that in the same DNS layer that surfaced it. Most discovery tools stop at the report and leave enforcement to something else. The tool that found the app can also act on it. Keeping discovery and control together removes that handoff, which is how DNS analytics helps organizations gain control over their shadow IT environment.
Shadow IT usually points to a gap in your approved tools stack. People reach for outside apps when the sanctioned ones fall short, so treating what you find as feedback rather than a list of violations tends to build a healthier process than blocking everything and bracing for the next workaround. It also gives you tighter access controls, since every tool you bring in through the front door is one you can actually govern.
For how discovery and enforcement fit into a wider program, see our enterprise DNS security guide . Shadow IT is not going away, and AI tools are only adding to it, but you don't need a heavy new platform to get a handle on it. Because every app resolves a domain, your DNS data already holds the widest view of what is actually running on your network, including the free and browser-based tools that slip past everything else.
DNS will not tell you what data moved, so pair it with an identity or endpoint signal where that matters. Start with the logs you already have, and turn what you find into action in the same layer. If you want to see what shadow IT is already running on your network, try Control D free for 14 days (no credit card required) . No. DNS finds any app that resolves a domain, which is most of them, but it cannot tell whether someone used a company or personal account, and it cannot see what was uploaded. Encrypted DNS sent to a third-party resolver can also route around it.
Pair it with an identity or endpoint signal to cover those gaps. A CASB goes deep on cloud apps you already sanctioned and can inspect the data inside them. DNS analytics goes wide across everything that touches the internet, including the free unauthorized SaaS applications a CASB misses because they sit outside your tenant. They do different jobs and often run together.
It shows apps and domains at the device and network level, not keystrokes or activity timelines, so it can stay on the visibility side rather than surveillance. That is the line the Massey Hall and Roy Thomson Hall team drew when they found unsanctioned tools without tracking individual behavior. Yes. AI tools resolve their provider's domain before they load, so they show up even when nobody set them up. Control D tracks the major ones as named Services so security teams can filter for AI usage directly.
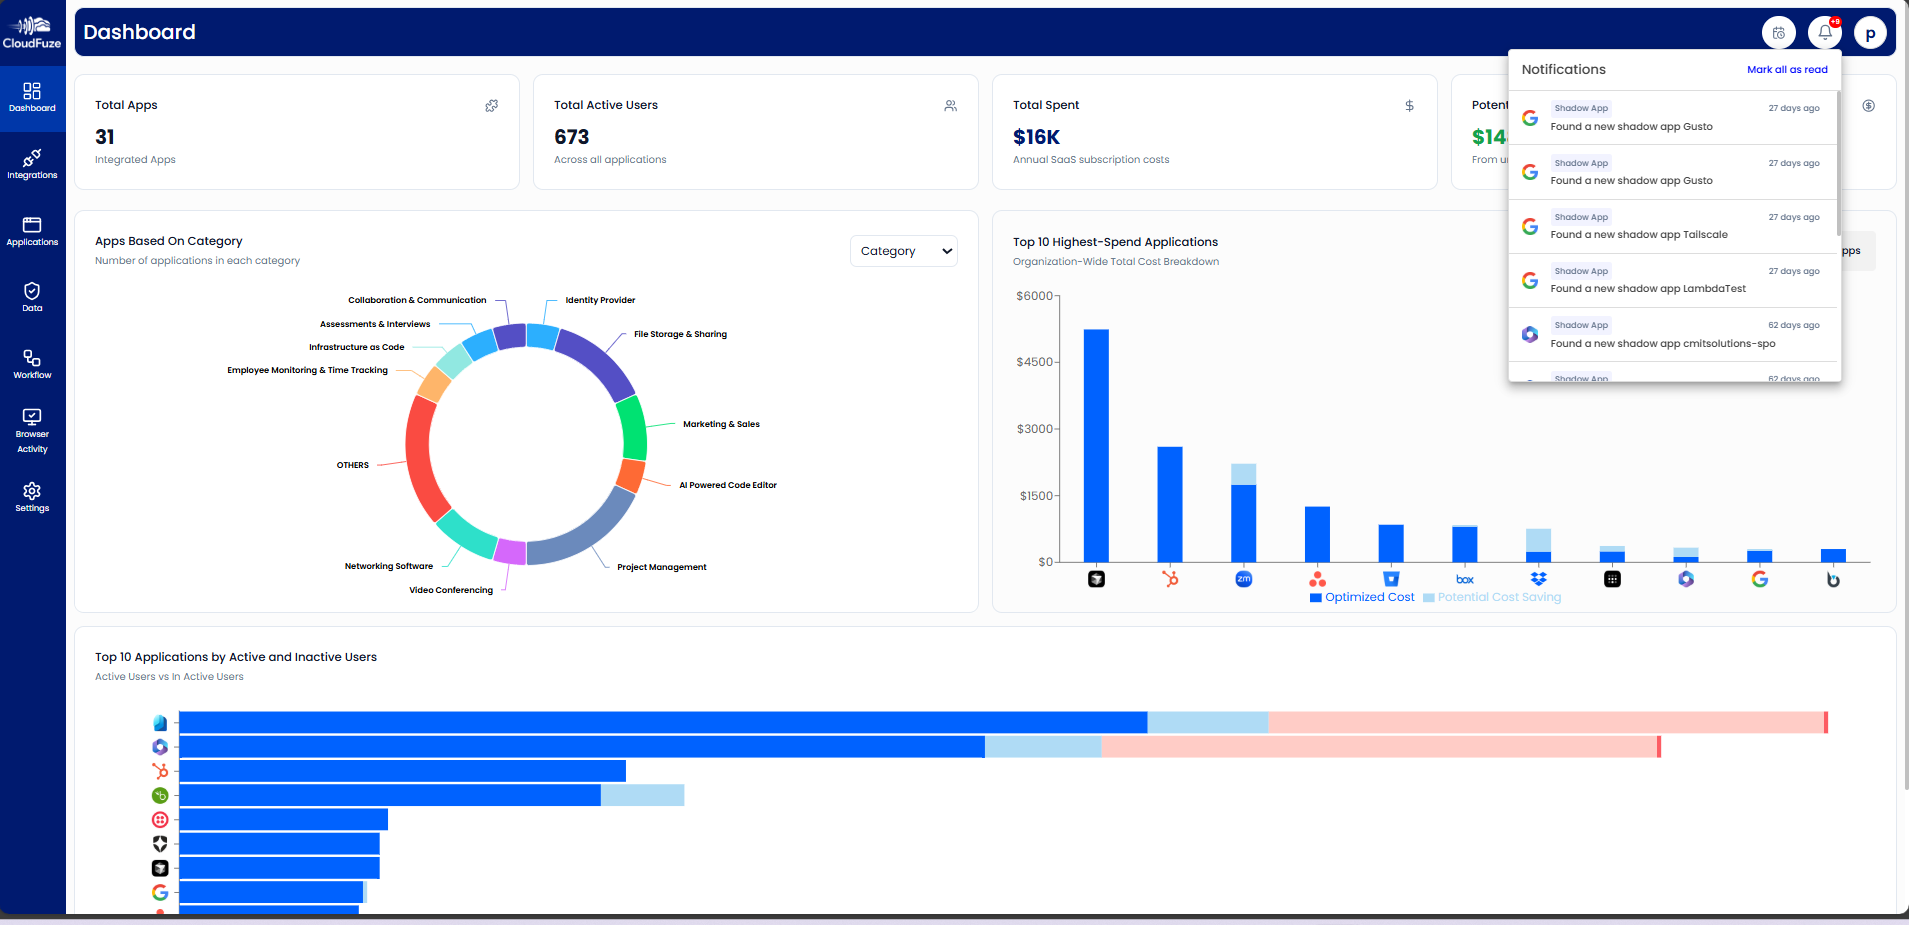
Assess the risk, then block it, approve it, or replace it with a sanctioned alternative, and keep the record for your audit trail. Because discovery and enforcement sit in the same DNS layer, you can act without switching tools. Access to this page requires authorization. You can try signing in or changing directories . When IT admins are asked how many cloud apps they think their employees use, on average they say 30 or 40, when in reality, the average is over 1,000 separate apps being used by employees in your organization. Shadow IT helps you know and identify which apps are being used and what your risk level is. 80% of employees use non-sanctioned apps that no one has reviewed, and may not be compliant with your security and compliance policies. And because your employees can access your resources and apps from outside your corporate network, it's no longer enough to have rules and policies on your firewalls.
In this tutorial, you'll learn how to use cloud discovery to discover which apps are being used, explore the risk of these apps, configure policies to identify new risky apps that are being used, and to unsanction these apps in order to block them natively using your proxy or firewall appliance To see Defender for Cloud Apps data for an app that's not currently in the catalog, we recommend that you check our roadmap or create a custom app .
5. Performance Evaluation & Extended Technical Observations Discover Shadow IT : Identify your organization's security posture by running cloud discovery in your organization to see what's actually happening in your network. For more information, see Set up cloud discovery . This can be done using any of the following methods: Get up and running quickly with cloud discovery by integrating with Microsoft Defender for Endpoint . This native integration enables you to immediately start collecting data on cloud traffic across your Windows 10 and Windows 11 devices, on and off your network.
For coverage on all devices connected to your network, it's important to deploy the Defender for Cloud Apps log collector on your firewalls and other proxies to collect data from your endpoints and send it to Defender for Cloud Apps for analysis. Integrate Defender for Cloud Apps with your proxy. Defender for Cloud Apps natively integrates with some third-party proxies, including Zscaler .
Because policies are different across user groups, regions, and business groups, you might want to create a dedicated Shadow IT report for each of these units. For more information, see Create custom continuous reports . Now that cloud discovery is running on your network, look at the continuous reports that are generated and look at the cloud discovery dashboard to get a full picture of what apps are being used in your organization. It's a good idea to look at them by category, because you'll often find that non-sanctioned apps are being used for legitimate work-related purposes that weren't addressed by a sanctioned app.
Identify the risk levels of your apps : Use the Defender for Cloud Apps catalog to dive deeper into the risks that are involved with each discovered app. The Defender for cloud app catalog includes over 31,000 apps that are assessed using over 90 risk factors. The risk factors start from general information about the app (where are the app's headquarters, who is the publisher), and through security measures and controls (support for encryption at rest, provides an audit log of user activity). For more information, see Working with risk score , In the Microsoft Defender Portal , under Cloud Apps , select Cloud Discovery . Then go to the Discovered apps tab. Filter the list of apps discovered in your organization by the risk factors you're concerned about. For example, you can use Advanced filters to find all apps with a risk score lower than 8.
You can drill down into the app to understand more about its compliance by selecting the app name and then selecting the Info tab to see details about the app's security risk factors. Evaluate compliance : Check whether the apps are certified as compliant with your organization's standards, such as HIPAA or SOC2.
In the Microsoft Defender Portal , under Cloud Apps , select Cloud Discovery . Then go to the Discovered apps tab. Filter the list of apps discovered in your organization by the compliance risk factors you're concerned about. For example, use the suggested query to filter out non-compliant apps. You can drill down into the app to understand more about its compliance by selecting the app name and then selecting the Info tab to see details about the app's compliance risk factors.
Analyze usage : Now that you know whether or not you want the app to be used in your organization, you want to investigate how and who is using it. If it's only used in a limited way in your organization maybe it's ok, but maybe if the use is growing you want to be notified about it so you can decide if you want to block the app. In the Microsoft Defender Portal , under Cloud Apps , select Cloud Discovery . Then go to the Discovered apps tab, and then drill down by selecting the specific app you want to investigate. The Usage tab lets you know how many active users are using the app and how much traffic it's generating. This can already give you a good picture of what's happening with the app. Then, if you want to see who, specifically, is using the app, you can drill down further by selecting Total active users . This important step can give you pertinent information, for example, if you discover that all the users of a specific app are from the Marketing department, it's possible that there's a business need for this app, and if it's risky you should talk to them about an alternative before blocking it.
Dive even deeper when investigating use of discovered apps. View subdomains and resources to learn about specific activities, data access, and resource usage in your cloud services. For more information, see Deep dive into Discovered apps and Discover resources and custom apps . Identify alternative apps : Use the cloud app catalog to identify safer apps that achieve similar business functionality as the detected risky apps, but do comply with your organization's policy. You can do this by using the advanced filters to find apps in the same category that meet with your different security controls.
Manage cloud apps : Defender for Cloud Apps helps you with the process for managing app use in your organization. After you identified the different patterns and behaviors used in your organization, you can create new custom app tags in order to classify each app according to its business status or justification. These tags can be then used for specific monitoring purposes, for example, identify high traffic that is going to apps that are tagged as risky cloud storage apps. App tags can be managed under Settings > Cloud Apps > Cloud Discovery > App tags . These tags can then be used later for filtering in the cloud discovery pages and creating policies using them.
Manage discovered apps using Microsoft Entra Gallery : Defender for Cloud Apps also uses its native integration with Microsoft Entra ID to enable you to manage your discovered apps in Microsoft Entra Gallery. For apps that already appear in the Microsoft Entra Gallery, you can apply single sign-on and manage the app with Microsoft Entra ID. To do so, on the row where the relevant app appears, choose the three dots at the end of the row, and then choose Manage app with Microsoft Entra ID .
Continuous monitoring : Now that you've thoroughly investigated the apps, you might want to set policies that monitor the apps and provide control where needed. Now it's time to create policies so you can be automatically alerted when something happens that you're concerned about. For example, you might want to create an App discovery policy that lets you know when there's a spike in downloads or traffic from an app you're concerned about. To achieve this, you should enable Anomalous behavior in discovered users policy , Cloud storage app compliance check , and New risky app . You should also set the policy to notify you by email. For more information, see policy template reference , more about cloud discovery policies and Configure App discovery policies .
Look at the alerts page and use the Policy type filter to look at app discovery alerts. For apps that were matched by your app discovery policies, it's recommended that you do an advanced investigation to learn more about the business justification for using the app, for example, by contacting the users of the app. Then, repeat the steps in Phase 2 to evaluate the risk of the app. Then determine next steps for the application, whether you approve use of it in the future or want to block it the next time a user accesses it, in which case you should tag it as unsanctioned so it can be blocked using your firewall, proxy, or secure web gateway. For more information, see Integrate with Microsoft Defender for Endpoint , Integrate with Zscaler , Integrate with iboss , and Block apps by exporting a block script .
In addition to the reporting options available in Defender for Cloud Apps, you can integrate cloud discovery logs into Microsoft Sentinel for further investigation and analysis. Once the data is in Microsoft Sentinel, you can view it in dashboards, run queries using Kusto query language, export queries to Microsoft Power BI, integrate with other sources, and create custom alerts. For more information, see Microsoft Sentinel integration .
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Subdomain • https://en.wikipedia.org/wiki/Google%20Cloud%20Platform • https://en.wikipedia.org/wiki/Instagram • https://controld.com/blog/shadow-it-dns-discovery/ • https://learn.microsoft.com/en-us/defender-cloud-apps/tutorial-shadow-it
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Shadow It Discovery Using DNS Logs.
[*] Metasploit Scan Running on Target Subnet for Shadow It Discovery Using DNS Logs... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |