Complete Technical Paper Content — Shamir Secret Sharing Scheme Implementation In Python
Overview & System Context
Shamir Secret Sharing Scheme Implementation In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7470 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Shamir's secret sharing (SSS) is an efficient secret sharing algorithm for distributing private information (the "secret") among a group, first developed by Adi Shamir in 1979. The secret cannot be revealed unless a minimum number of the group's members act together to pool their knowledge. To achieve this, the secret is mathematically divided into parts (the "shares") from which the secret can be reassembled only when a sufficient number of shares are combined. SSS has the property of information-theoretic security, meaning that even if an attacker steals some shares, it is impossible for the attacker to reconstruct the secret unless they have stolen a sufficient number of shares. Shamir's secret sharing is used in some applications to share the access keys to a master secret.
share a key for decrypting the root key of a password manager, recover a user key for encrypted email access, share the passphrase used to recreate a master secret, which is in turn used to access a cryptocurrency wallet and recover the combination to a physical safe. Secure: The scheme has information-theoretic security. Minimal: The size of each piece does not exceed the size of the original data. Extensible: For any given threshold, shares can be dynamically added or deleted without affecting existing shares Dynamic: Security can be enhanced without changing the secret, but by changing the polynomial occasionally (keeping the same free term) and constructing a new share for each of the participants. Flexible: In organizations where hierarchy is important, each participant can be issued different numbers of shares according to their importance inside the organization. For instance, with a threshold of 3, the president could unlock the safe alone if given three shares, while three secretaries with one share each must combine their shares to unlock the safe. Weaknesses include: No verifiable secret sharing: During the share reassembly process, SSS does not provide a way to verify the correctness of each share being used. Verifiable secret sharing aims to verify that shareholders are honest and not submitting fake shares.
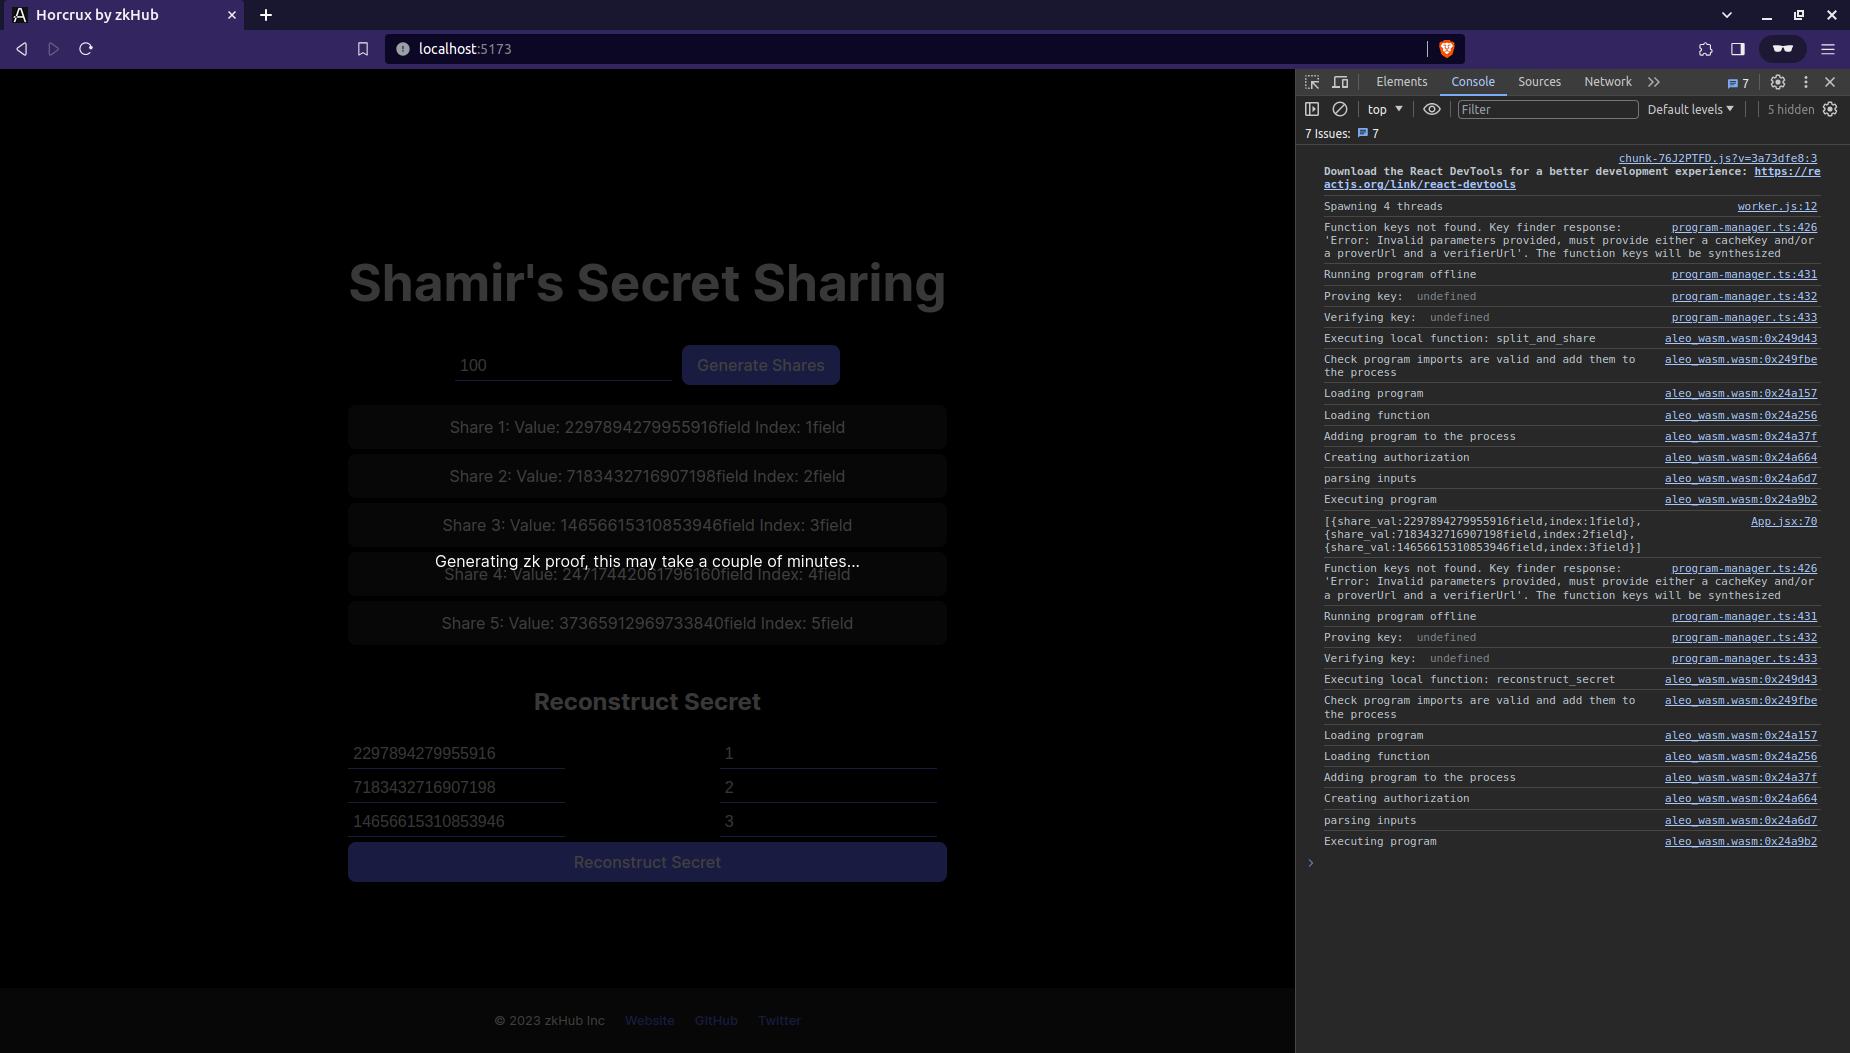
Single point of failure: The secret must exist in one place when it is split into shares, and again in one place when it is reassembled. These are attack points, and other schemes including multisignature eliminate at least one of these single points of failure. Figure 1: Horcrux - Shamir Secret Sharing in Aleo | Devpost Knowledge of any k {\displaystyle k} or more shares S i {\displaystyle S_{i}} makes S {\displaystyle S} computable. That is, the entire secret S {\displaystyle S} can be reconstructed from any combination of k {\displaystyle k} shares. Knowledge of any k − 1 {\displaystyle k-1} or fewer shares S i {\displaystyle S_{i}} leaves S {\displaystyle S} completely undetermined, in the sense that the possible values for S {\displaystyle S} remain as likely with knowledge of up to k − 1 {\displaystyle k-1} shares as with knowledge of 0 {\displaystyle 0} shares. The secret S {\displaystyle S} cannot be reconstructed with fewer than k {\displaystyle k} shares. If n = k {\displaystyle n=k} , then all of the shares are needed to reconstruct the secret S {\displaystyle S} . Assume that the secret S {\displaystyle S} can be represented as an element a 0 {\displaystyle a_{0}} of a finite field G F ( q ) {\displaystyle \mathrm {GF} (q)} (where q {\displaystyle q} is greater than the number n {\displaystyle n} of shares being generated). Randomly choose k − 1 {\displaystyle k-1} elements, a 1 , I , a k − 1 {\displaystyle a_{1},\cdots ,a_{k-1}} , from G F ( q ) {\displaystyle \mathrm {GF} (q)} and construct the polynomial f ( x ) = a 0 + a 1 x + a 2 x 2 + a 3 x 3 + I + a k − 1 x k − 1 {\displaystyle f\left(x\right)=a_{0}+a_{1}x+a_{2}x^{2}+a_{3}x^{3}+\cdots +a_{k-1}x^{k-1}} . Compute any n {\displaystyle n} points out on the curve, for instance set i = 1 , … , n {\displaystyle i=1,\ldots ,n} to find points ( i , f ( i ) ) {\displaystyle \left(i,f\left(i\right)\right)} . Every participant is given a point (a non-zero input to the polynomial, and the corresponding output).
Given any subset of k {\displaystyle k} of these pairs, a 0 {\displaystyle a_{0}} can be obtained using interpolation, with one possible formula for doing so being a 0 = f ( 0 ) = ∑ j = 0 k − 1 y j ∏ m = 0 m ≠ j k − 1 x m x m − x j {\displaystyle a_{0}=f(0)=\sum _{j=0}^{k-1}y_{j}\prod _{\begin{smallmatrix}m\,=\,0\\m\,\neq \,j\end{smallmatrix}}^{k-1}{\frac {x_{m}}{x_{m}-x_{j}}}} , where the list of points on the polynomial is given as k {\displaystyle k} pairs of the form ( x i , y i ) {\displaystyle (x_{i},y_{i})} . Note that f ( 0 ) {\displaystyle f(0)} is equal to the first coefficient of polynomial f ( x ) {\displaystyle f(x)} . More generally, any value f ( α ) {\displaystyle f(\alpha )} , where α ∈ G F ( q ) {\displaystyle \alpha \in \mathrm {GF} (q)} , may be used as the secret instead of f ( 0 ) {\displaystyle f(0)} . The leading coefficient a k − 1 {\displaystyle a_{k-1}} may similarly be interpreted as the value f ( ∞ ) {\displaystyle f(\infty )} on the projective line and can also be used as the secret.
These are precisely the polynomial-derived quantities that remain perfectly hidden from every coalition of fewer than k {\displaystyle k} participants. In contrast, other linear combinations of the polynomial coefficients, including the intermediate coefficients, a 1 , … , a k − 2 {\displaystyle a_{1},\ldots ,a_{k-2}} , may be determined by some coalitions of fewer than k {\displaystyle k} participants.
This yields coefficients ( a 0 = 1234 ; a 1 = 166 ; a 2 = 94 ) , {\displaystyle (a_{0}=1234;a_{1}=166;a_{2}=94),} where a 0 {\displaystyle a_{0}} is the secret The polynomial to produce secret shares (points) is therefore: f ( x ) = 1234 + 166 x + 94 x 2 {\displaystyle f(x)=1234+166x+94x^{2}} Six points D x − 1 = ( x , f ( x ) ) {\displaystyle D_{x-1}=(x,f(x))} from the polynomial are constructed as: Figure 2: GitHub - Blake-Haydon/Shamir-Secret-Sharing: Shamir's Secret Sharing ...
D 0 = ( 1 , 1494 ) ; D 1 = ( 2 , 1942 ) ; D 2 = ( 3 , 2578 ) ; D 3 = ( 4 , 3402 ) ; D 4 = ( 5 , 4414 ) ; D 5 = ( 6 , 5614 ) {\displaystyle D_{0}=(1,1494);D_{1}=(2,1942);D_{2}=(3,2578);D_{3}=(4,3402);D_{4}=(5,4414);D_{5}=(6,5614)} Each participant in the scheme receives a different point (a pair of x {\displaystyle x} and f ( x ) {\displaystyle f(x)} ). Because D x − 1 {\displaystyle D_{x-1}} is used instead of D x {\displaystyle D_{x}} the points start from ( 1 , f ( 1 ) ) {\displaystyle (1,f(1))} and not ( 0 , f ( 0 ) ) {\displaystyle (0,f(0))} . This is necessary because f ( 0 ) {\displaystyle f(0)} is the secret.
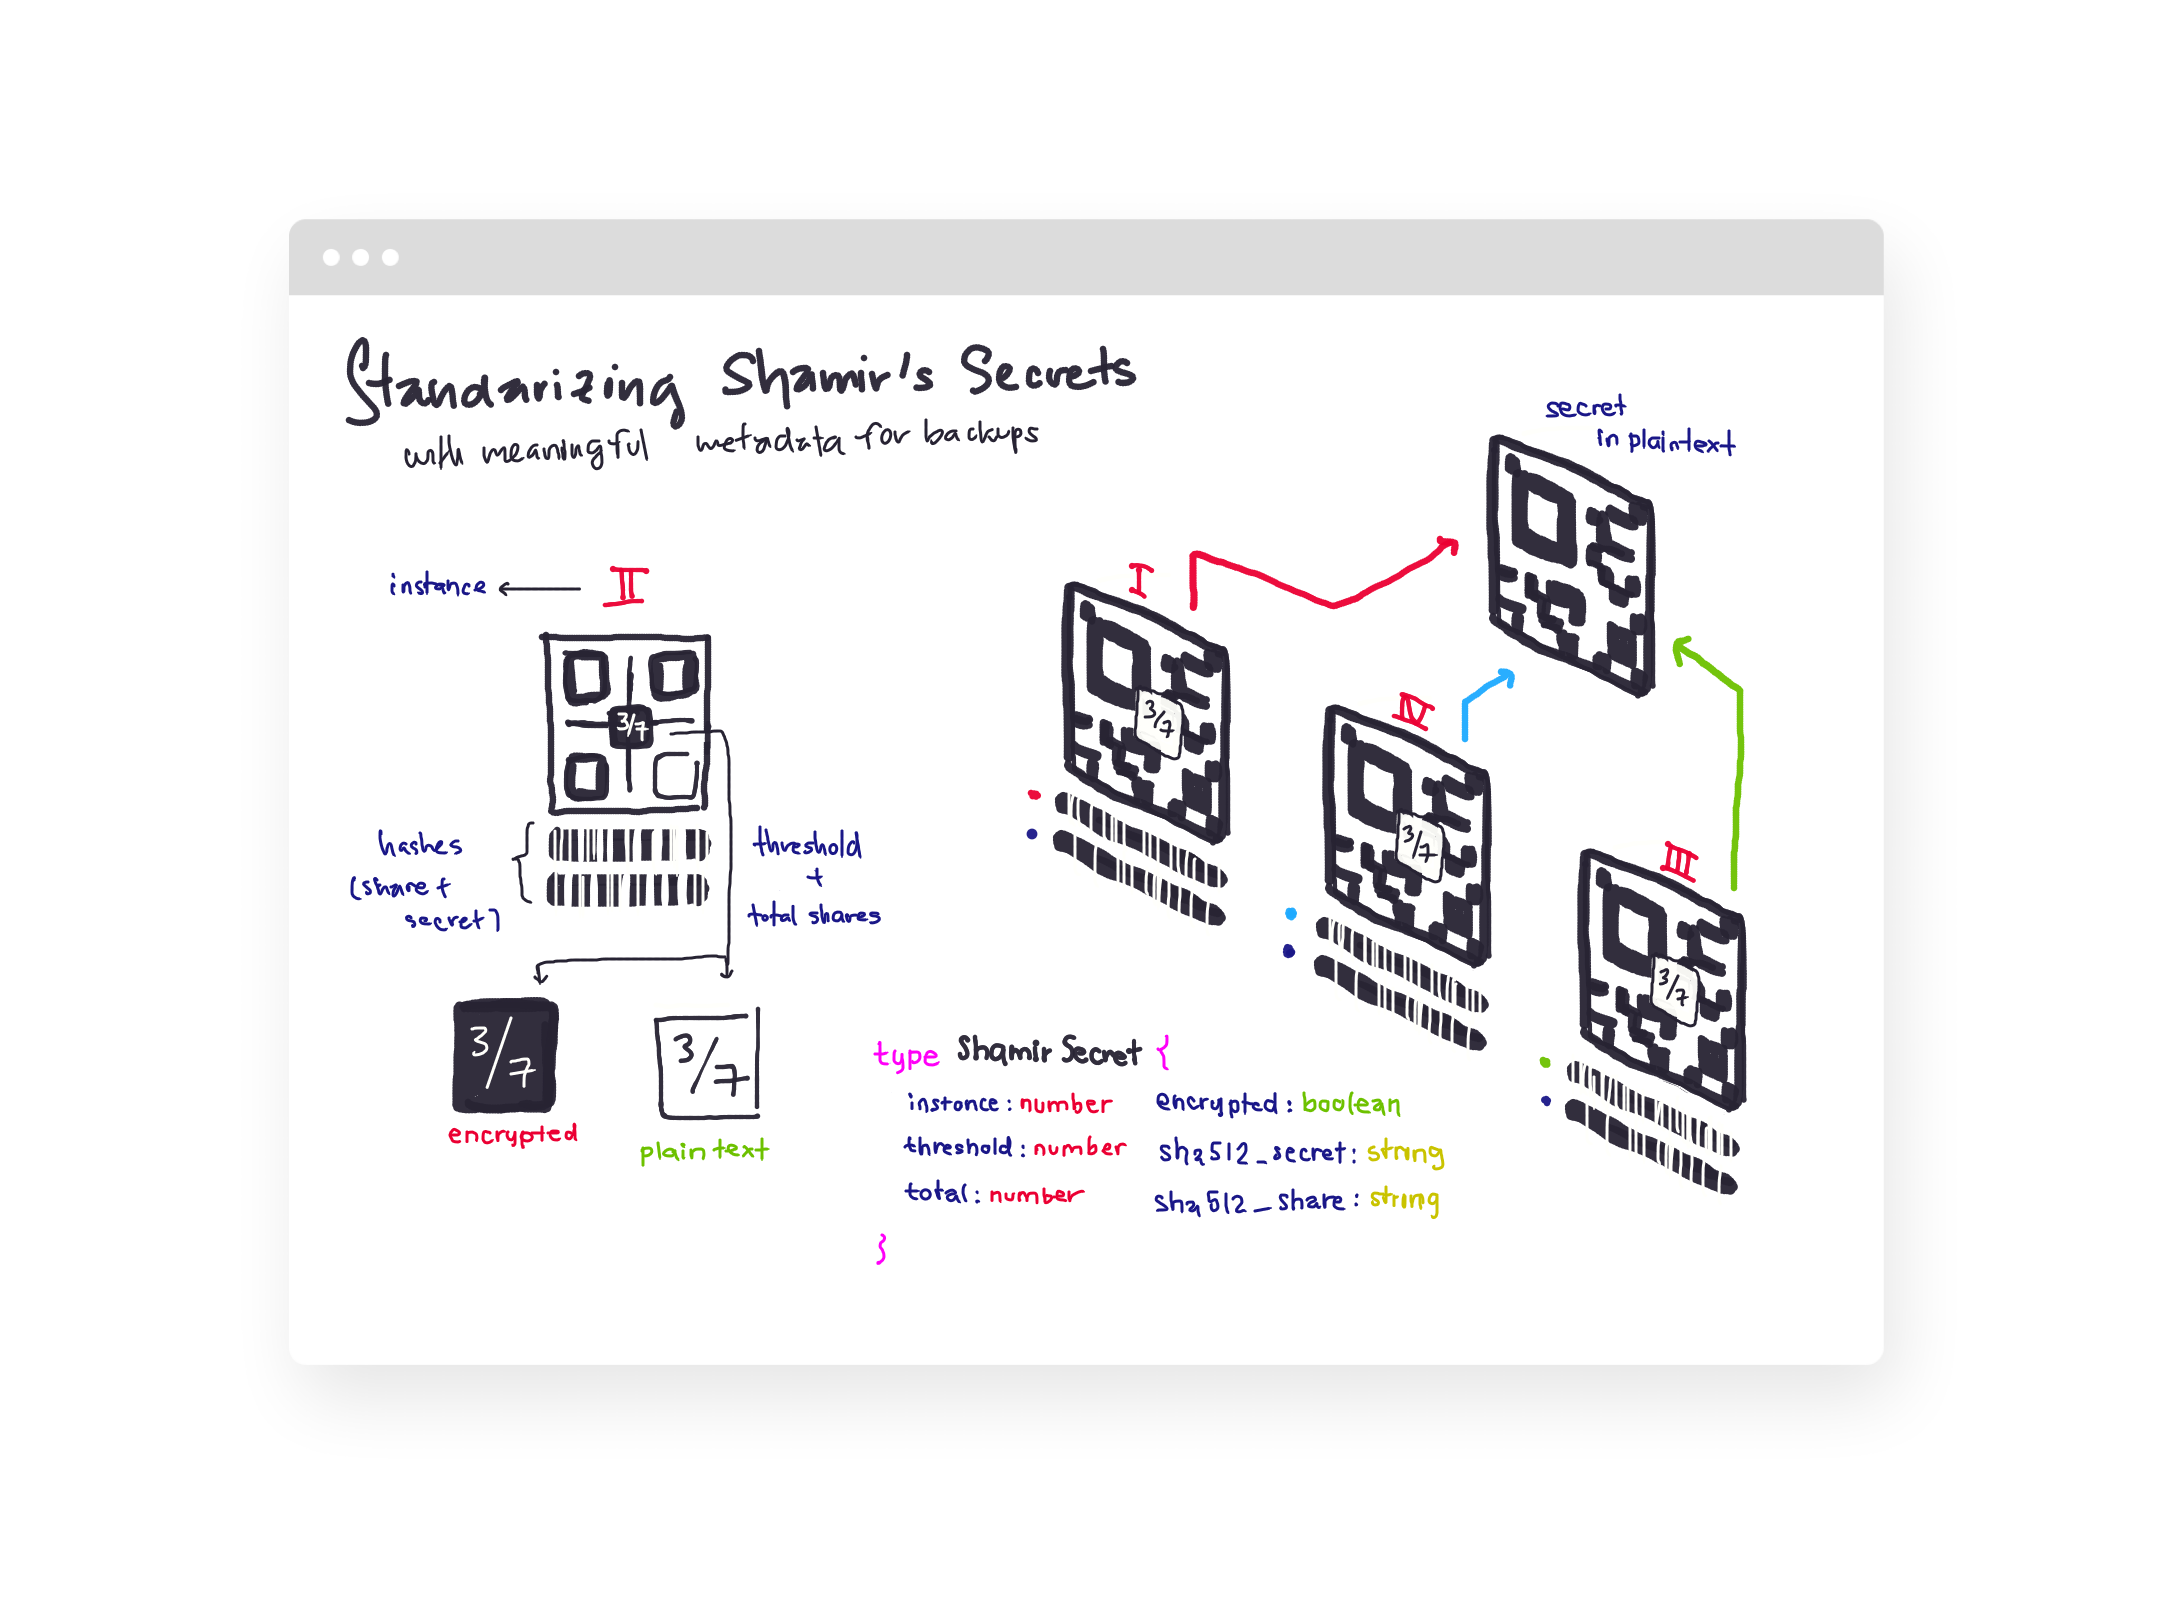
I 0 ( x ) = x − x 1 x 0 − x 1 ⋅ x − x 2 x 0 − x 2 = x − 4 2 − 4 ⋅ x − 5 2 − 5 = 1 6 x 2 − 3 2 x + 10 3 {\displaystyle \ell _{0}(x)={\frac {x-x_{1}}{x_{0}-x_{1}}}\cdot {\frac {x-x_{2}}{x_{0}-x_{2}}}={\frac {x-4}{2-4}}\cdot {\frac {x-5}{2-5}}={\frac {1}{6}}x^{2}-{\frac {3}{2}}x+{\frac {10}{3}}} I 1 ( x ) = x − x 0 x 1 − x 0 ⋅ x − x 2 x 1 − x 2 = x − 2 4 − 2 ⋅ x − 5 4 − 5 = − 1 2 x 2 + 7 2 x − 5 {\displaystyle \ell _{1}(x)={\frac {x-x_{0}}{x_{1}-x_{0}}}\cdot {\frac {x-x_{2}}{x_{1}-x_{2}}}={\frac {x-2}{4-2}}\cdot {\frac {x-5}{4-5}}=-{\frac {1}{2}}x^{2}+{\frac {7}{2}}x-5} Figure 3: GitHub - 0xjjpa/shamir-secret-sharing-store: TypeScript library to ...
I 2 ( x ) = x − x 0 x 2 − x 0 ⋅ x − x 1 x 2 − x 1 = x − 2 5 − 2 ⋅ x − 4 5 − 4 = 1 3 x 2 − 2 x + 8 3 {\displaystyle \ell _{2}(x)={\frac {x-x_{0}}{x_{2}-x_{0}}}\cdot {\frac {x-x_{1}}{x_{2}-x_{1}}}={\frac {x-2}{5-2}}\cdot {\frac {x-4}{5-4}}={\frac {1}{3}}x^{2}-2x+{\frac {8}{3}}} Using the formula for polynomial interpolation, f ( x ) {\displaystyle f(x)} is: f ( x ) = ∑ j = 0 2 y j ⋅ I j ( x ) = y 0 I 0 ( x ) + y 1 I 1 ( x ) + y 2 I 2 ( x ) = 1942 ( 1 6 x 2 − 3 2 x + 10 3 ) + 3402 ( − 1 2 x 2 + 7 2 x − 5 ) + 4414 ( 1 3 x 2 − 2 x + 8 3 ) = 1234 + 166 x + 94 x 2 {\displaystyle {\begin{aligned}f(x)&=\sum _{j=0}^{2}y_{j}\cdot \ell _{j}(x)\\[6pt]&=y_{0}\ell _{0}(x)+y_{1}\ell _{1}(x)+y_{2}\ell _{2}(x)\\[6pt]&=1942\left({\frac {1}{6}}x^{2}-{\frac {3}{2}}x+{\frac {10}{3}}\right)+3402\left(-{\frac {1}{2}}x^{2}+{\frac {7}{2}}x-5\right)+4414\left({\frac {1}{3}}x^{2}-2x+{\frac {8}{3}}\right)\\[6pt]&=1234+166x+94x^{2}\end{aligned}}} Recalling that the secret is the free coefficient, which means that S = 1234 {\displaystyle S=1234} , and the secret has been recovered.
f ( 0 ) = ∑ j = 0 k − 1 y j ∏ m = 0 m ≠ j k − 1 x m x m − x j {\displaystyle f(0)=\sum _{j=0}^{k-1}y_{j}\prod _{\begin{smallmatrix}m\,=\,0\\m\,\neq \,j\end{smallmatrix}}^{k-1}{\frac {x_{m}}{x_{m}-x_{j}}}} Fill the formula for f ( x ) {\displaystyle f(x)} with S {\displaystyle S} and the value of k : f ( x ) = S + a 1 x + I + a k − 1 x k − 1 ⇒ f ( x ) = S + a 1 x + a 2 x 2 {\displaystyle k:f(x)=S+a_{1}x+\cdots +a_{k-1}x^{k-1}\Rightarrow {}f(x)=S+a_{1}x+a_{2}x^{2}} Fill (1) with the values of D {\displaystyle D} 's x {\displaystyle x} and f ( x ) : 1942 = S + a 1 2 + a 2 2 2 ⇒ S = 1942 − 2 a 1 − 4 a 2 {\displaystyle f(x):1942=S+a_{1}2+a_{2}2^{2}\Rightarrow {}S=1942-2a_{1}-4a_{2}} The above attack exploits constraints on the values that the polynomial may take by virtue of how it was constructed: the polynomial must have coefficients that are integers, and the polynomial must take an integer as value when evaluated at each of the coordinates used in the scheme. This reduces its possible values at unknown points, including the resultant secret, given fewer than k {\displaystyle k} shares. This problem can be remedied by using finite field arithmetic. A finite field always has size q = p r {\displaystyle q=p^{r}} , where p {\displaystyle p} is a prime and r {\displaystyle r} is a positive integer. The size q {\displaystyle q} of the field must satisfy q > n {\displaystyle q>n} , and that q {\displaystyle q} is greater than the number of possible values for the secret, though the latter condition may be circumvented by splitting the secret into smaller secret values, and applying the scheme to each of these. In our example below, we use a prime field (i.e. r = 1). The figure shows a polynomial curve over a finite field. In practice this is only a small change. The order q of the field (i.e. the number of values that it has) must be chosen to be greater than the number of participants and the number of values that the secret a 0 = S {\displaystyle a_{0}=S} may take. All calculations involving the polynomial must also be calculated over the field (mod p in our example, in which p = q {\displaystyle p=q} is taken to be a prime) instead of over the integers. Both the choice of the field and the mapping of the secret to a value in this field are considered to be publicly known. For this example, choose p = 1613 {\displaystyle p=1613} , so the polynomial becomes f ( x ) = 1234 + 166 x + 94 x 2 mod 1613 {\displaystyle f(x)=1234+166x+94x^{2}{\bmod {1613}}} which gives the points: ( 1 , 1494 ) ; ( 2 , 329 ) ; ( 3 , 965 ) ; ( 4 , 176 ) ; ( 5 , 1188 ) ; ( 6 , 775 ) {\displaystyle (1,1494);(2,329);(3,965);(4,176);(5,1188);(6,775)} This time Eve doesn't gain any information when she finds a D x {\displaystyle D_{x}} (until she has k {\displaystyle k} points).
Suppose again that Eve finds D 0 = ( 1 , 1494 ) {\displaystyle D_{0}=\left(1,1494\right)} and D 1 = ( 2 , 329 ) {\displaystyle D_{1}=\left(2,329\right)} , and the public information is: n = 6 , k = 3 , p = 1613 , f ( x ) = a 0 + a 1 x + I + a k − 1 x k − 1 mod p , a 0 = S , a i ∈ N {\displaystyle n=6,k=3,p=1613,f(x)=a_{0}+a_{1}x+\dots +a_{k-1}x^{k-1}\mod {p},a_{0}=S,a_{i}\in \mathbb {N} } . Attempting the previous attack, Eve can: Fill the f ( x ) {\displaystyle f(x)} -formula with S {\displaystyle S} and the value of k {\displaystyle k} and p {\displaystyle p} : f ( x ) = S + a 1 x + I + a 3 − 1 x 3 − 1 mod 1613 {\displaystyle f(x)=S+a_{1}x+\dots +a_{3-1}x^{3-1}\mod 1613} Fill (1) with the values of D 0 {\displaystyle D_{0}} 's x {\displaystyle x} and f ( x ) : 1494 ≡ S + a 1 1 + a 2 1 2 ( mod 1613 ) ⇒ 1494 ≡ S + a 1 + a 2 ( mod 1613 ) {\displaystyle f(x):1494\equiv S+a_{1}1+a_{2}1^{2}{\pmod {1613}}\Rightarrow {}1494\equiv S+a_{1}+a_{2}{\pmod {1613}}} Fill (1) with the values of D 1 {\displaystyle D_{1}} 's x {\displaystyle x} and f ( x ) : 1942 ≡ S + a 1 2 + a 2 2 2 ( mod 1613 ) ⇒ 1942 ≡ S + 2 a 1 + 4 a 2 ( mod 1613 ) {\displaystyle f(x):1942\equiv S+a_{1}2+a_{2}2^{2}{\pmod {1613}}\Rightarrow {}1942\equiv S+2a_{1}+4a_{2}{\pmod {1613}}} 2. System Architecture & Core Working Principles Subtract (3)-(2): ( 1942 − 1494 ) ≡ ( S − S ) + ( 2 a 1 − a 1 ) + ( 4 a 2 − a 2 ) ( mod 1613 ) ⇒ 448 ≡ a 1 + 3 a 2 ( mod 1613 ) {\displaystyle (1942-1494)\equiv (S-S)+(2a_{1}-a_{1})+(4a_{2}-a_{2}){\pmod {1613}}\Rightarrow {}448\equiv a_{1}+3a_{2}{\pmod {1613}}} and rewrite this as a 1 ≡ 448 − 3 a 2 ( mod 1613 ) {\displaystyle a_{1}\equiv 448-3a_{2}{\pmod {1613}}} There are p {\displaystyle p} possible values for a 1 {\displaystyle a_{1}} . She knows that [ 448 , 445 , 442 , … ] {\displaystyle [448,445,442,\ldots ]} always decreases by 3, so if p {\displaystyle p} were divisible by 3 {\displaystyle 3} she could conclude a 1 ∈ [ 1 , 4 , 7 , … ] {\displaystyle a_{1}\in [1,4,7,\ldots ]} . However, p {\displaystyle p} is prime, so she can not conclude this.
Thus, using a finite field avoids this possible attack. Also, even though Eve can conclude that S ≡ 1046 + 2 a 2 ( mod 1613 ) {\displaystyle S\equiv 1046+2a_{2}{\pmod {1613}}} , it does not provide any additional information, since the "wrapping around" behavior of modular arithmetic prevents the leakage of "S is even", unlike the example with integer arithmetic above. In cryptography, a ring signature is a type of digital signature that can be performed by any member of a set of users that each have keys. Therefore, a message signed with a ring signature is endorsed by someone in a particular set of people. One of the security properties of a ring signature is that it should be computationally infeasible to determine which of the set's members' keys was used to produce the signature. Ring signatures are similar to group signatures but differ in two key ways: first, there is no way to revoke the anonymity of an individual signature; and second, any set of users can be used as a signing set without additional setup. Ring signatures were invented by Ron Rivest, Adi Shamir, and Yael Tauman Kalai, and introduced at ASIACRYPT in 2001. The name, ring signature, comes from the ring-like structure of the signature algorithm.
Suppose that a set of entities each have public/private key pairs, (P1, S1), (P2, S2), ..., (Pn, Sn). Party i can compute a ring signature σ on a message m, on input (m, Si, P1, ..., Pn). Anyone can check the validity of a ring signature given σ, m, and the public keys involved, P1, ..., Pn. If a ring signature is properly computed, it should pass the check. On the other hand, it should be hard for anyone to create a valid ring signature on any message for any set without knowing any of the private keys for that set.
In the original paper, Rivest, Shamir, and Tauman described ring signatures as a way to leak a secret. For instance, a ring signature could be used to provide an anonymous signature from "a high-ranking White House official", without revealing which official signed the message. Ring signatures are right for this application because the anonymity of a ring signature cannot be revoked, and because the group for a ring signature can be improvised. Another application, also described in the original paper, is for deniable signatures. Here the sender and the recipient of a message form a group for the ring signature, then the signature is valid to the recipient, but anyone else will be unsure whether the recipient or the sender was the actual signer. Thus, such a signature is convincing, but cannot be transferred beyond its intended recipient. There were various works, introducing new features and based on different assumptions: Threshold ring signatures Unlike standard "t-out-of-n" threshold signature, where t of n users should collaborate to sign a message, this variant of a ring signature requires t users to cooperate in the ring signing protocol. Namely, t parties S1, ..., St ∈ {P1, ..., Pn} can compute a (t, n)-ring signature, σ, on a message, m, on input (m, S1, ..., St, P1, ..., Pn). Linkable ring signatures The property of linkability allows one to determine whether any two signatures have been produced by the same member (under the same private key). The identity of the signer is nevertheless preserved. One of the possible applications can be an offline e-cash system. Traceable ring signature In addition to the previous scheme the public key of the signer is revealed (if they issue more than one signatures under the same private key). An e-voting system can be implemented using this protocol.
C k , v ( y 1 , y 2 , … , y n ) = E k ( y n ⊕ E k ( y n − 1 ⊕ E k ( I ⊕ E k ( y 1 ⊕ v ) … ) ) ) {\displaystyle C_{k,v}(y_{1},y_{2},\dots ,y_{n})=E_{k}(y_{n}\oplus E_{k}(y_{n-1}\oplus E_{k}(\dots \oplus E_{k}(y_{1}\oplus v)\dots )))} It outputs a single value z {\displaystyle z} which is forced to be equal to v {\displaystyle v} . The equation v = C k , v ( y 1 , y 2 , … , y n ) {\displaystyle v=C_{k,v}(y_{1},y_{2},\dots ,y_{n})} can be solved as long as at least one y i {\displaystyle y_{i}} , and by extension x i {\displaystyle x_{i}} , can be freely chosen.
Under the assumptions of RSA, this implies knowledge of at least one of the inverses of the trap door functions g i − 1 {\displaystyle g_{i}^{-1}} (i.e. a private key), since g i − 1 ( y i ) = x i {\displaystyle g_{i}^{-1}(y_{i})=x_{i}} . Calculate the key k = H ( m ) {\displaystyle k={\mathcal {H}}(m)} , using a cryptographic hash function. This step assumes a random oracle for H {\displaystyle {\mathcal {H}}} , since k {\displaystyle k} will be used as key for E k {\displaystyle E_{k}} .
Pick a random glue value v {\displaystyle v} . Pick random x i {\displaystyle x_{i}} for all ring members but yourself ( x s {\displaystyle x_{s}} will be calculated using the signer's private key), and calculate corresponding y i = g i ( x i ) {\displaystyle y_{i}=g_{i}(x_{i})} . Solve the ring equation for y s {\displaystyle y_{s}} Calculate x s {\displaystyle x_{s}} using the signer's private key: x s = g s − 1 ( y s ) {\displaystyle x_{s}=g_{s}^{-1}(y_{s})} The ring signature now is the ( 2 n + 1 ) {\displaystyle (2n+1)} -tuple ( P 1 , P 2 , … , P n ; v ; x 1 , x 2 , … , x n ) {\displaystyle (P_{1},P_{2},\dots ,P_{n};v;x_{1},x_{2},\dots ,x_{n})} Apply the public key trap door on all x i {\displaystyle x_{i}} : y i = g i ( x i ) {\displaystyle y_{i}=g_{i}(x_{i})} . Calculate the symmetric key k = H ( m ) {\displaystyle k={\mathcal {H}}(m)} . Verify that the ring equation holds C k , v ( y 1 , y 2 , … , y n ) = v {\displaystyle C_{k,v}(y_{1},y_{2},\dots ,y_{n})=v} .
Visual cryptography is a cryptographic technique which allows visual information (pictures, text, etc.) to be encrypted in such a way that the decrypted information appears as a visual image. One of the best-known techniques has been credited to Moni Naor and Adi Shamir, who developed it in 1994. They demonstrated a visual secret sharing scheme, where a binary image was broken up into n shares so that only someone with all n shares could decrypt the image, while any n − 1 shares revealed no information about the original image. Each share was printed on a separate transparency, and decryption was performed by overlaying the shares. When all n shares were overlaid, the original image would appear. There are several generalizations of the basic scheme including k-out-of-n visual cryptography, and using opaque sheets but illuminating them by multiple sets of identical illumination patterns under the recording of only one single-pixel detector, which exposed the image. Using a similar idea, transparencies can be used to implement a one-time pad encryption, where one transparency is a shared random pad, and another transparency acts as the ciphertext. Normally, there is an expansion of space requirement in visual cryptography. But if one of the two shares is structured recursively, the efficiency of visual cryptography can be increased to 100%. Some antecedents of visual cryptography are in patents from the 1960s. Other antecedents are in the work on perception and secure communication. Visual cryptography can be used to protect biometric templates in which decryption does not require any complex computations.
In this example, the binary image has been split into two component images. Each component image has a pair of pixels for every pixel in the original image. These pixel pairs are shaded black or white according to the following rule: if the original image pixel was black, the pixel pairs in the component images must be complementary; randomly shade one II, and the other II. When these complementary pairs are overlapped, they will appear dark gray. On the other hand, if the original image pixel was white, the pixel pairs in the component images must match: both II or both II. When these matching pairs are overlapped, they will appear light gray. So, when the two component images are superimposed, the original image appears. However, without the other component, a component image reveals no information about the original image; it is indistinguishable from a random pattern of II / II pairs. Moreover, if you have one component image, you can use the shading rules above to produce a counterfeit component image that combines with it to produce any image at all.
Sharing a secret with an arbitrary number of people, n, such that at least 2 of them are required to decode the secret is one form of the visual secret sharing scheme presented by Moni Naor and Adi Shamir in 1994. In this scheme we have a secret image which is encoded into n shares printed on transparencies. The shares appear random and contain no decipherable information about the underlying secret image, however if any 2 of the shares are stacked on top of one another the secret image becomes decipherable by the human eye. Every pixel from the secret image is encoded into multiple subpixels in each share image using a matrix to determine the color of the pixels. In the (2, n) case, a white pixel in the secret image is encoded using a matrix from the following set, where each row gives the subpixel pattern for one of the components: {all permutations of the columns of} : C 0 = [ 1 0 . . . 0 1 0 . . . 0 . . . 1 0 . . . 0 ] . {\displaystyle \mathbf {C_{0}=} {\begin{bmatrix}1&0&...&0\\1&0&...&0\\...\\1&0&...&0\end{bmatrix}}.} While a black pixel in the secret image is encoded using a matrix from the following set: {all permutations of the columns of} : C 1 = [ 1 0 .
{\displaystyle \mathbf {C_{1}=} {\begin{bmatrix}1&0&...&0\\0&1&...&0\\...\\0&0&...&1\end{bmatrix}}.} For instance in the (2,2) sharing case (the secret is split into 2 shares and both shares are required to decode the secret) we use complementary matrices to share a black pixel and identical matrices to share a white pixel. Stacking the shares we have all the subpixels associated with the black pixel now black while 50% of the subpixels associated with the white pixel remain white.
2×2 subpixels can also encode a binary image in each component image. For example, each white pixel of each component image could be represented by two black subpixels, while each black pixel represented by three black subpixels. When overlaid, each white pixel of the secret image is represented by three black subpixels, while each black pixel is represented by all four subpixels black. Each corresponding pixel in the component images is randomly rotated to avoid orientation leaking information about the secret image.
This library provides functions and data structures for computing secret shares given an integer input value and for reassembling an integer from its corresponding secret shares via Lagrange interpolation over finite fields (according to Shamir’s secret sharing scheme ). The built-in secrets.randbelow function is used to generate random coefficients. The lagrange library is used for Lagrange interpolation.
The library provides the function shares for transforming a nonnegative integer plaintext into a number of secret shares and the function interpolate for reassembling those shares back into the plaintext they represent: Individual secret shares are represented using the share class. This class is derived from the tuple type and can have either two integer components (the share index and the share value that together determine the coordinates of a point on a polynomial curve) or three integer components (also including the modulus). One advantage of the two-component variant is that the memory footprint of share objects is reduced. These components can be accessed either directly via their indices or via named attributes: The shares function accepts an optional boolean argument compact , making it possible to create secret shares that do not include the modulus component: It is also possible to extend a two-component share object with a modulus using the built-in modulus operator (thanks to the __mod__ method): Addition of share objects and multiplication of share objects by a scalar are both supported via special methods such as __add__ and __mul__ that correspond to Python’s built-in addition and multiplication operators : When creating secret shares for a given plaintext, the modulus can be specified explicitly or omitted. When the modulus is omitted, the default is the 128-bit modulus (2 ** 127) - 1 : When using interpolate to reconstruct a plaintext from compact share objects, the modulus must be specified explicitly: 3. Software Implementation, Frameworks & Protocols The reconstruction threshold can also be specified explicitly or omitted. When it is omitted, the default threshold is the number of secret shares requested: The threshold argument is never required when invoking interpolate , but it can reduce the number of arithmetic operations performed when reconstructing a plaintext: To facilitate rapid prototyping and assembly of concise tests, the add and mul helper functions are provided for performing addition and scalar multiplication operations involving collections of shares: These methods can also be used instead of built-in arithmetic operators when working with share objects that have no modulus component: In addition, conversion methods for bytes-like objects and Base64 strings are included to support encoding and decoding of share objects: All installation and development dependencies are fully specified in pyproject.toml . The project.optional-dependencies object is used to specify optional requirements for various development tasks. This makes it possible to specify additional options (such as docs , lint , and so on) when performing installation using pip : All unit tests are executed and their coverage is measured when using pytest (see the pyproject.toml file for configuration details): Alternatively, all unit tests are included in the module itself and can be executed using doctest : In order to contribute to the source code, open an issue or submit a pull request on the GitHub page for this library.
Beginning with version 1.0.0, the version number format for this library and the changes to the library associated with version number increments conform with Semantic Versioning 2.0.0 . This library can be published as a package on PyPI via the GitHub Actions workflow found in .github/workflows/build-publish-sign-release.yml that follows the recommendations found in the Python Packaging User Guide .
Ensure that the correct version number appears in pyproject.toml , and that any links in this README document to the Read the Docs documentation of this package (or its dependencies) have appropriate version numbers. Also ensure that the Read the Docs project for this library has an automation rule that activates and sets as the default all tagged versions. To publish the package, create and push a tag for the version being published (replacing ?.?.? with the version number): PyCryptodome is a self-contained Python package of low-level cryptographic primitives, for Python 3.9 and newer. It needs no system libraries: install it with pip install pycryptodome .
For instance, this is how to encrypt and authenticate a message with AES in GCM mode, and then decrypt it: This library provides functions and data structures for computing secret shares given an integer input value and for reassembling an integer from its corresponding secret shares via Lagrange interpolation over finite fields (according to Shamir’s secret sharing scheme ). The built-in secrets.randbelow function is used to generate random coefficients. The lagrange library is used for Lagrange interpolation.
The library provides the function shares for transforming a nonnegative integer plaintext into a number of secret shares and the function interpolate for reassembling those shares back into the plaintext they represent: Individual secret shares are represented using the share class. This class is derived from the tuple type and can have either two integer components (the share index and the share value that together determine the coordinates of a point on a polynomial curve) or three integer components (also including the modulus). One advantage of the two-component variant is that the memory footprint of share objects is reduced. These components can be accessed either directly via their indices or via named attributes: The shares function accepts an optional boolean argument compact , making it possible to create secret shares that do not include the modulus component: It is also possible to extend a two-component share object with a modulus using the built-in modulus operator (thanks to the __mod__ method): Addition of share objects and multiplication of share objects by a scalar are both supported via special methods such as __add__ and __mul__ that correspond to Python’s built-in addition and multiplication operators : When creating secret shares for a given plaintext, the modulus can be specified explicitly or omitted. When the modulus is omitted, the default is the 128-bit modulus (2 ** 127) - 1 : When using interpolate to reconstruct a plaintext from compact share objects, the modulus must be specified explicitly: The reconstruction threshold can also be specified explicitly or omitted. When it is omitted, the default threshold is the number of secret shares requested: The threshold argument is never required when invoking interpolate , but it can reduce the number of arithmetic operations performed when reconstructing a plaintext: To facilitate rapid prototyping and assembly of concise tests, the add and mul helper functions are provided for performing addition and scalar multiplication operations involving collections of shares: These methods can also be used instead of built-in arithmetic operators when working with share objects that have no modulus component: In addition, conversion methods for bytes-like objects and Base64 strings are included to support encoding and decoding of share objects: 4. Practical Deployment, Analysis & Case Studies All installation and development dependencies are fully specified in pyproject.toml . The project.optional-dependencies object is used to specify optional requirements for various development tasks. This makes it possible to specify additional options (such as docs , lint , and so on) when performing installation using pip : All unit tests are executed and their coverage is measured when using pytest (see the pyproject.toml file for configuration details): Alternatively, all unit tests are included in the module itself and can be executed using doctest : In order to contribute to the source code, open an issue or submit a pull request on the GitHub page for this library.
Beginning with version 1.0.0, the version number format for this library and the changes to the library associated with version number increments conform with Semantic Versioning 2.0.0 . This library can be published as a package on PyPI via the GitHub Actions workflow found in .github/workflows/build-publish-sign-release.yml that follows the recommendations found in the Python Packaging User Guide .
Ensure that the correct version number appears in pyproject.toml , and that any links in this README document to the Read the Docs documentation of this package (or its dependencies) have appropriate version numbers. Also ensure that the Read the Docs project for this library has an automation rule that activates and sets as the default all tagged versions. To publish the package, create and push a tag for the version being published (replacing ?.?.? with the version number): For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation .
Provenance describes where a file came from. On PyPI, provenance is shared via attestations , which provide a verifiable record of the build or publishing details. View details, limitations and caveats. PyPI verified that this artifact, at this checksum, originated from the publisher listed below. Provenance describes where a file came from. On PyPI, provenance is shared via attestations , which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI verified that this artifact, at this checksum, originated from the publisher listed below. This library provides functions and data structures for computing secret shares given an integer input value and for reassembling an integer from its corresponding secret shares via Lagrange interpolation over finite fields (according to Shamir’s Secret Sharing scheme ). The built-in secrets.token_bytes function and rejection sampling are used to generate random coefficients. The lagrange library is used for Lagrange interpolation.
The library provides functions for transforming a nonnegative integer value into a number of secret shares and for reassembling those shares back into the value they represent: All installation and development dependencies are fully specified in pyproject.toml . The project.optional-dependencies object is used to specify optional requirements for various development tasks. This makes it possible to specify additional options (such as docs , lint , and so on) when performing installation using pip : All unit tests are executed and their coverage is measured when using pytest (see the pyproject.toml file for configuration details): Alternatively, all unit tests are included in the module itself and can be executed using doctest : In order to contribute to the source code, open an issue or submit a pull request on the GitHub page for this library.
Beginning with version 1.0.0, the version number format for this library and the changes to the library associated with version number increments conform with Semantic Versioning 2.0.0 . This library can be published as a package on PyPI by a package maintainer. First, install the dependencies required for packaging and publishing: Ensure that the correct version number appears in pyproject.toml , and that any links in this README document to the Read the Docs documentation of this package (or its dependencies) have appropriate version numbers. Also ensure that the Read the Docs project for this library has an automation rule that activates and sets as the default all tagged versions. Create and push a tag for this version (replacing ?.?.? with the version number): Remove any old build/distribution files. Then, package the source into a distribution archive: Uses Mersenne prime field (2¹²I-1) for cryptographic operations. Resistant to brute-force attacks.
Polynomial Generation : Creates a (t-1)-degree polynomial with the secret as the constant term. Share Distribution : Evaluates the polynomial at n distinct points to generate shares. Secret Sharing schemes are used in the distribution of a secret value among multiple participants ( shareholders ) by dividing the secret into fragments ( shares ) . This is done in a manner that prevents a single shareholder from having any useful knowledge of the original secret at all. The only way to retrieve the original secret is to combine the shares, distributed among the participants. Hence, the control of the secret is distributed . These schemes are examples of Threshold Cryptosystems , which involve the division of secrets among multiple parties such that several parties (more than some threshold number) must cooperate to reconstruct the secret.
In general, a secret may be split into n shares (for n shareholders), out of which, a minimum of t , (t < n) shares are required for successful reconstruction. Such a scheme is referred to as a (t, n) sharing-scheme. From the n participants, any subset of shareholders, of size greater or equal to t , can regenerate the secret. Importantly, even with any k (k < t) shares, no new information about the original secret is learned.
5. Performance Evaluation & Extended Technical Observations Shamir Secret Sharing ( SSS ) is one of the most popular implementations of a secret sharing scheme created by Adi Shamir , a famous Israeli cryptographer, who also contributed to the invention of RSA algorithm. SSS allows the secret to be divided into an arbitrary number of shares and allows an arbitrary threshold (as long as it is less than the total participants). SSS is based on the mathematical concept of polynomial interpolation which states that a polynomial of degree t-1 can be reconstructed from the knowledge of t or more points, known to be lying on the curve. For instance, to reconstruct a curve of degree 1 (a straight line), we require at least 2 points that lie on the line. Conversely, it is mathematically infeasible to reconstruct a curve if the number of unique points available is less than (degree-of-curve + 1). One can imagine having infinite possible straight lines that could be formed as a result of just one point in 2D space.
The concept of polynomial interpolation can be applied to produce a secret sharing scheme by embedding the secret into the polynomial. A general polynomial of degree p can be expressed as follows: In the expression of P(x), the values a_{1}, a_{2}, a_{3}, ..., a_{n} represent the coefficients of the polynomial. Thus, construction of a polynomial requires the selection of these coefficients. Note that no values are actually substituted in for x; every term in the polynomial acts as a "placeholder" to store the coefficient values. Once the polynomial is generated, we can essentially represent the curve by just p+1 points that lie on the curve. This follows from the polynomial interpolation principle.
For example, a curve of degree 4 can be reconstructed if we have access to at least 5 unique points lying on it. To do this, we can run Lagrange's interpolation or any other similar interpolation mechanism. Consequently, if we conceal the secret value into such a polynomial and use various points on the curve as shares, we arrive at a secret sharing scheme. More precisely, to establish a (t, n) secret sharing scheme, we can construct a polynomial of degree t-1 and pick n points on the curve as shares such that the polynomial will only be regenerated if t or more shares are pooled. The secret value ( s ) is concealed in the constant term of the polynomial (coefficient of 0-degree term or the curve's y-intercept) which can only be obtained after the successful reconstruction of the curve.
Shamir's Secret Sharing uses the polynomial interpolation principle to perform threshold sharing in the following two phases: Phase I: Generation of Shares This phase involves the setup of the system as well as the generation of the shares. Phase II: Reconstruction of Secret For reconstruction of the secret, a minimum of t participants are required to pool their shares.
Secret sharing schemes are widely used in cryptosystems where trust is required to be distributed instead of centralized. Prominent examples of real world scenarios where secret sharing is used include: This library provides functions and data structures for computing secret shares given an integer input value and for reassembling an integer from its corresponding secret shares via Lagrange interpolation over finite fields (according to Shamir's secret sharing scheme ). The built-in secrets.randbelow function is used to generate random coefficients. The lagrange library is used for Lagrange interpolation.
The library provides the function shares for transforming a nonnegative integer plaintext into a number of secret shares and the function interpolate for reassembling those shares back into the plaintext they represent: Individual secret shares are represented using the share class. This class is derived from the tuple type and can have either two integer components (the share index and the share value that together determine the coordinates of a point on a polynomial curve) or three integer components (also including the modulus). One advantage of the two-component variant is that the memory footprint of share objects is reduced. These components can be accessed either directly via their indices or via named attributes: The shares function accepts an optional boolean argument compact , making it possible to create secret shares that do not include the modulus component: It is also possible to extend a two-component share object with a modulus using the built-in modulus operator (thanks to the __mod__ method): Addition of share objects and multiplication of share objects by a scalar are both supported via special methods such as __add__ and __mul__ that correspond to Python's built-in addition and multiplication operators : When creating secret shares for a given plaintext, the modulus can be specified explicitly or omitted. When the modulus is omitted, the default is the 128-bit modulus (2 ** 127) - 1 : When using interpolate to reconstruct a plaintext from compact share objects, the modulus must be specified explicitly: The reconstruction threshold can also be specified explicitly or omitted. When it is omitted, the default threshold is the number of secret shares requested: The threshold argument is never required when invoking interpolate , but it can reduce the number of arithmetic operations performed when reconstructing a plaintext: To facilitate rapid prototyping and assembly of concise tests, the add and mul helper functions are provided for performing addition and scalar multiplication operations involving collections of shares: These methods can also be used instead of built-in arithmetic operators when working with share objects that have no modulus component: In addition, conversion methods for bytes-like objects and Base64 strings are included to support encoding and decoding of share objects: All installation and development dependencies are fully specified in pyproject.toml . The project.optional-dependencies object is used to specify optional requirements for various development tasks. This makes it possible to specify additional options (such as docs , lint , and so on) when performing installation using pip : All unit tests are executed and their coverage is measured when using pytest (see the pyproject.toml file for configuration details): Alternatively, all unit tests are included in the module itself and can be executed using doctest : In order to contribute to the source code, open an issue or submit a pull request on the GitHub page for this library.
Beginning with version 1.0.0, the version number format for this library and the changes to the library associated with version number increments conform with Semantic Versioning 2.0.0 . This library can be published as a package on PyPI via the GitHub Actions workflow found in .github/workflows/build-publish-sign-release.yml that follows the recommendations found in the Python Packaging User Guide .
Ensure that the correct version number appears in pyproject.toml , and that any links in this README document to the Read the Docs documentation of this package (or its dependencies) have appropriate version numbers. Also ensure that the Read the Docs project for this library has an automation rule that activates and sets as the default all tagged versions. To publish the package, create and push a tag for the version being published (replacing ?.?.? with the version number): Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Shamir%27s%20secret%20sharing • https://en.wikipedia.org/wiki/Ring%20signature • https://en.wikipedia.org/wiki/Visual%20cryptography • https://shamirs.readthedocs.io/ • https://pycryptodome.readthedocs.io/en/latest/src/protocol/ss.html • https://pypi.org/project/shamirs/ • https://shamirs.readthedocs.io/en/2.1.0/index.html • https://team-hype.github.io/shamir-secret-sharing/ • https://www.geeksforgeeks.org/python/implementing-shamirs-secret-sharing-scheme-in-python/ • https://github.com/lapets/shamirs
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Shamir Secret Sharing Scheme Implementation In Python.
[*] Metasploit Scan Running on Target Subnet for Shamir Secret Sharing Scheme Implementation In Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |