Complete Technical Paper Content — Smart Building Environmental Sensor Tampering Detection
Overview & System Context
Smart Building Environmental Sensor Tampering Detection: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9545 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Tamperproofing is a methodology used to hinder, deter or detect unauthorised access to a device or circumvention of a security system. Since any device or system can be foiled by a person with sufficient knowledge, equipment, and time, the term "tamperproof" is a misnomer unless some limitations on the tampering party's resources is explicit or assumed.
Tamper resistance is resistance to intentional malfunction or sabotage by either the normal users of a product, package, or system or others with physical access to it. Tamper resistance ranges from simple features like screws with special drives and tamper-evident seals to more complex devices that render themselves inoperable or encrypt all data transmissions between individual chips, use of materials needing special tools and knowledge. Tamper-resistant devices or features are common on packages to deter package or product tampering or enable its detection. Anti-tamper devices have one or more components: tamper resistance, tamper detection, tamper response, and tamper evidence. In some applications, devices are only tamper-evident rather than tamper-resistant.
Identify who a potential tamperer might be: average user, child, person under medical care, misguided joker, prisoner, saboteur, organized criminals, terrorists, corrupt government. What level of knowledge, materials, tools, etc. might they have? Identify all feasible methods of unauthorized access into a product, package, or system. In addition to the primary means of entry, also consider secondary or "back door" methods. Control or limit access to products or systems of interest. Improve the tamper resistance to make tampering more difficult, time-consuming, etc. Add tamper-evident features to help indicate the existence of tampering. Educate people to watch for evidence of tampering.
A user who breaks equipment by modifying it in a way not intended by the manufacturer might deny they did it, in order to claim the warranty or (mainly in the case of PCs) call the helpdesk for help in fixing it. Tamper-evident seals may be enough to deal with this. However, they cannot easily be checked remotely, and many countries have statutory warranty terms that mean manufacturers may still have to service the equipment. Tamper proof screws will stop most casual users from tampering in the first place. In the US, the Magnuson-Moss Warranty Act prevents manufacturers from voiding warranties solely due to tampering. A warranty may be dishonored only if the tampering actually affected the part that has failed, and could have caused the failure.
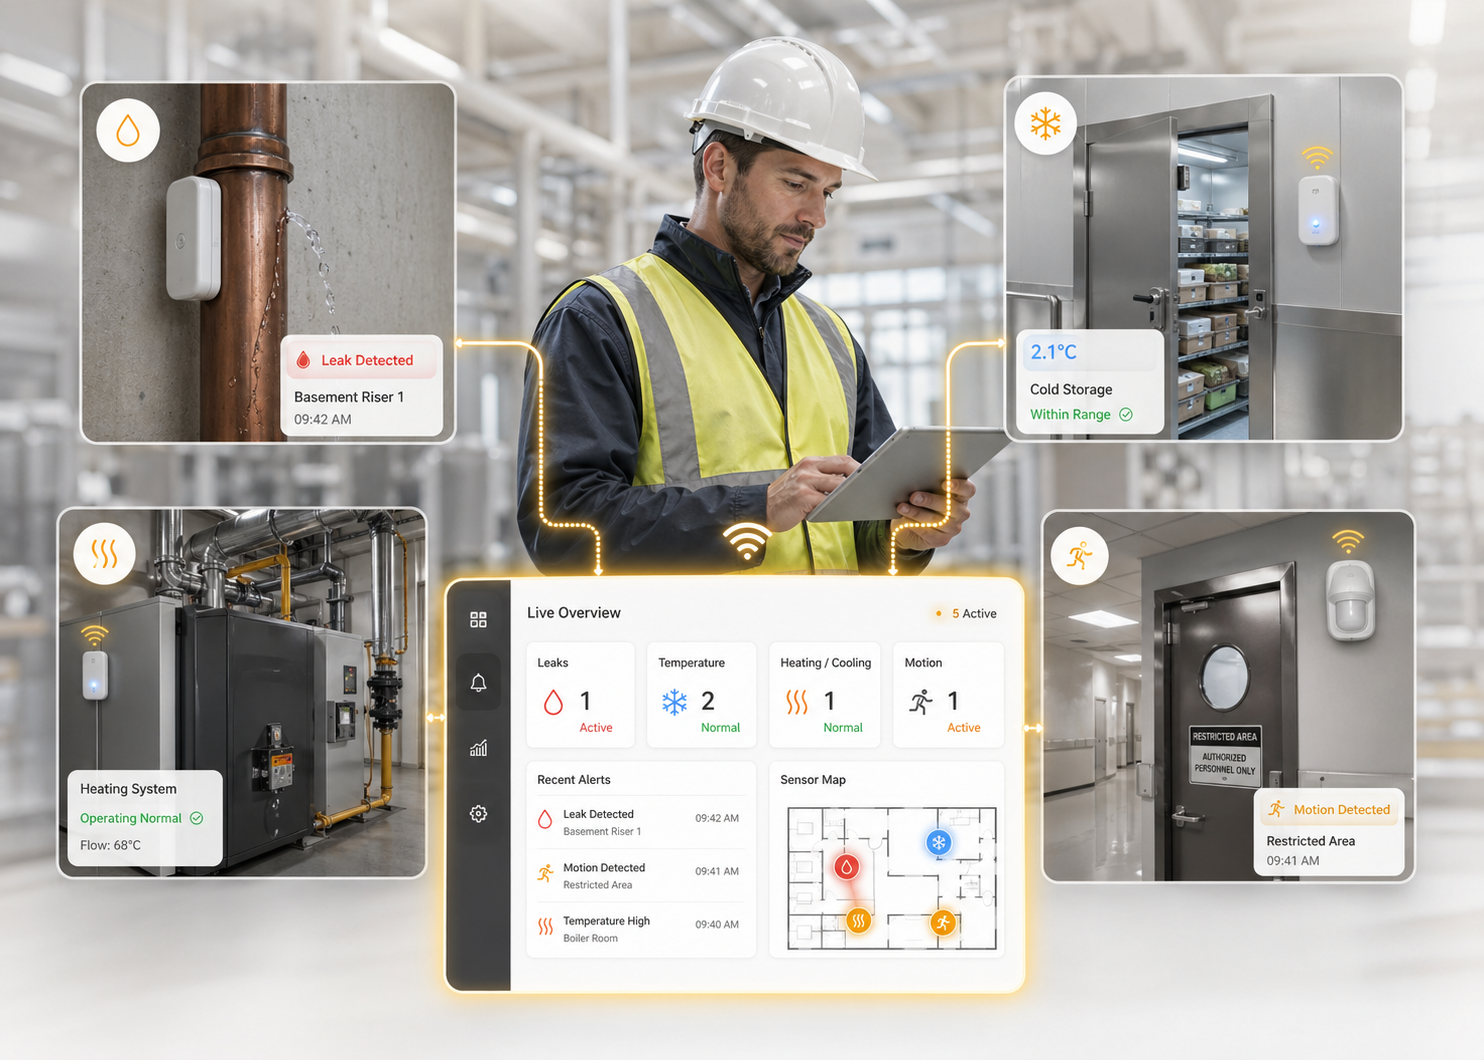
Figure 1: Smart IoT Sensors - Live Building Monitoring, Alerts & Dashboards physical attack of various forms (microprobing, drills, files, solvents, etc.) freezing the device applying out-of-spec voltages or power surges applying unusual clock signals inducing software errors using radiation (e.g., microwaves or ionising radiation) measuring the precise time and power requirements of certain operations (see power analysis) Tamper-resistant chips may be designed to zeroise their sensitive data (especially cryptographic keys) if they detect penetration of their security encapsulation or out-of-specification environmental parameters. A chip may even be rated for "cold zeroisation", the ability to zeroise itself even after its power supply has been crippled. In addition, the custom-made encapsulation methods used for chips used in some cryptographic products may be designed in such a manner that they are internally pre-stressed, so the chip will fracture if interfered with. Nevertheless, the fact that an attacker may have the device in their possession for as long as they like, and perhaps obtain numerous other samples for testing and practice, means that it is impossible to totally eliminate tampering by a sufficiently motivated opponent. Because of this, one of the most important elements in protecting a system is overall system design. In particular, tamper-resistant systems should "fail gracefully" by ensuring that compromise of one device does not compromise the entire system. In this manner, the attacker can be practically restricted to attacks that cost more than the expected return from compromising a single device. Since the most sophisticated attacks have been estimated to cost several hundred thousand dollars to carry out, carefully designed systems may be invulnerable in practice.
In the United States, purchasing specifications require anti-tamper (AT) features on military electronic systems. Regulations for some pharmaceuticals require it. High value products may be subject to theft. Evidence needs to remain unaltered for possible legal proceedings. Resistance to tampering can be built in or added to packaging. Examples include: Extra layers of packaging (no single layer or component is "tamper-proof") Packaging that requires tools to enter Extra-strong and secure packaging Packages that cannot be resealed Tamper-evident seals, security tapes, and features Software is also said to be tamper-resistant when it contains measures to make reverse engineering harder, or to prevent a user from modifying it against the manufacturer's wishes (such as removing a restriction on how it can be used). One commonly used method is code obfuscation. However, effective tamper resistance in software is much harder than in hardware, as the software environment can be manipulated to near-arbitrary extent by the use of emulation. If implemented, trusted computing would make software tampering of protected programs at least as difficult as hardware tampering, as the user would have to hack the trust chip to give false certifications in order to bypass remote attestation and sealed storage.
However, the current specification makes it clear that the chip is not expected to be tamper-proof against any reasonably sophisticated physical attack; that is, it is not intended to be as secure as a tamper-resistant device. That has the side effect that software maintenance gets more complex because software updates need to be validated, and errors in the upgrade process may lead to a false-positive triggering of the protection mechanism.
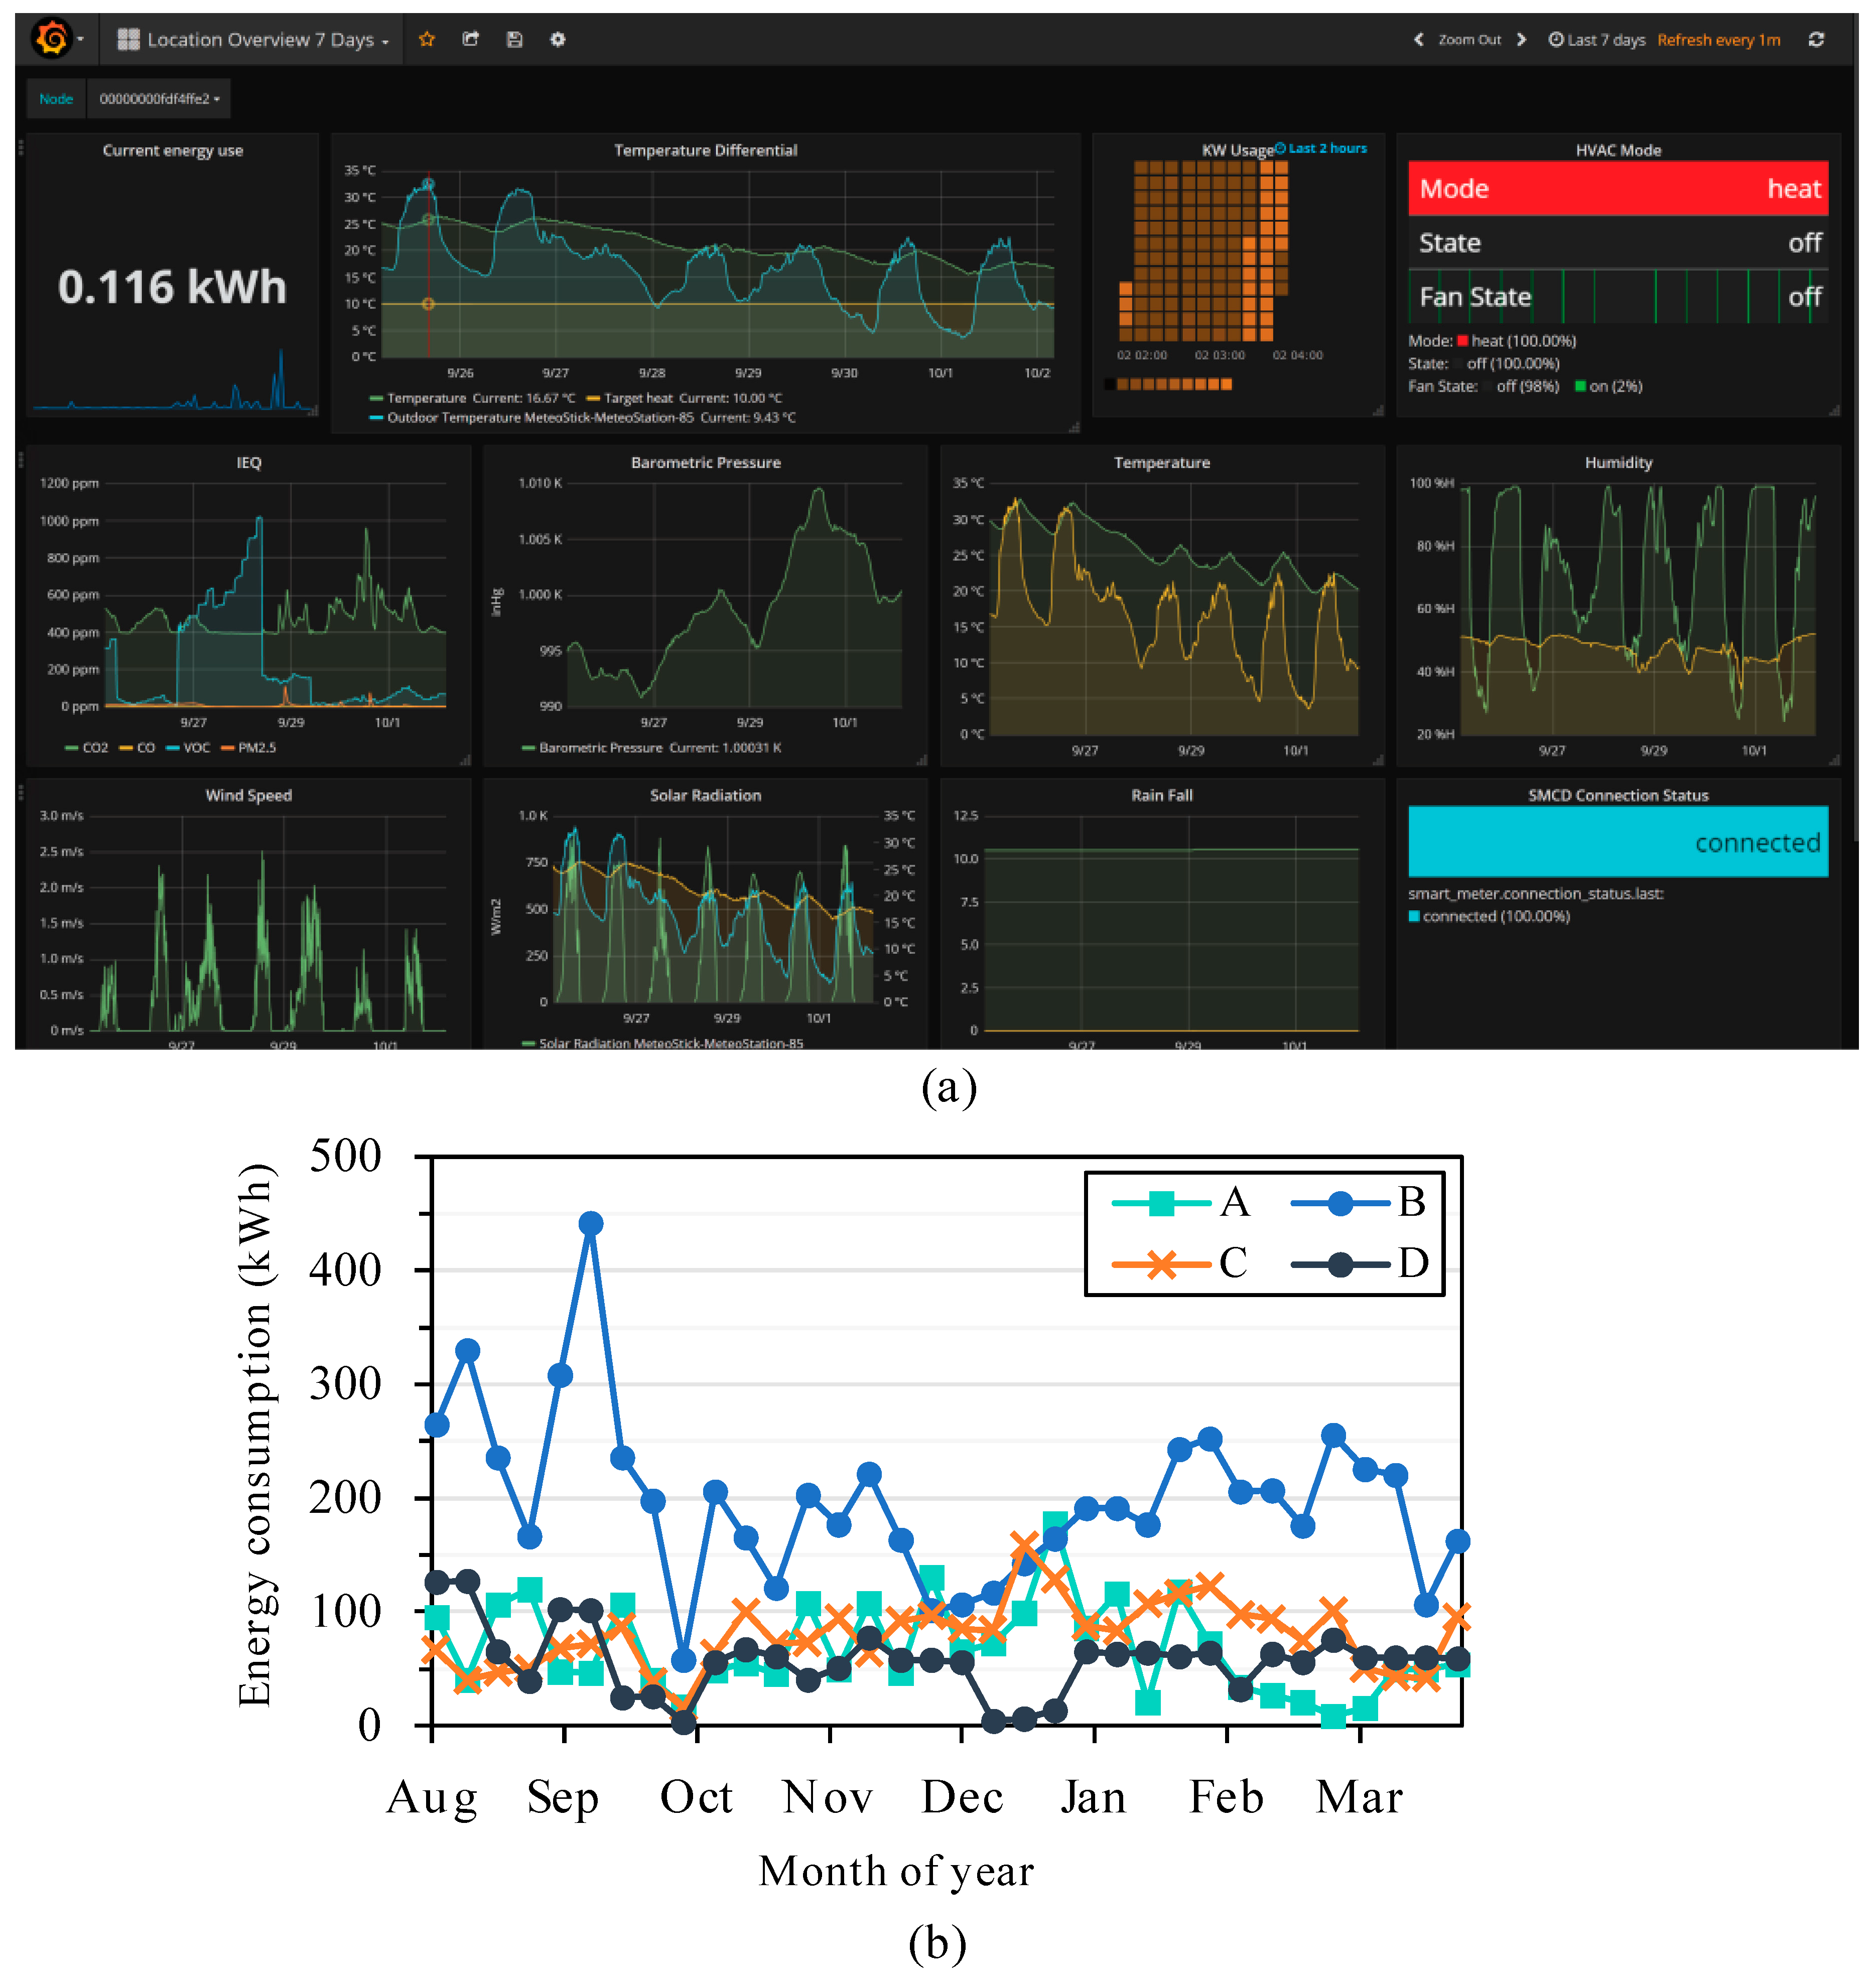
Figure 2: Elemental: An Open-Source Wireless Hardware and Software Platform for ... A security alarm is a system designed to detect intrusions, such as unauthorized entry, into a building or other areas, such as a home or school. Security alarms protect against burglary (theft) or property damage, as well as against intruders. Examples include personal systems, neighborhood security alerts, car alarms, and prison alarms. Some alarm systems serve a single purpose of burglary protection; combination systems provide fire and intrusion protection. Intrusion-alarm systems are combined with closed-circuit television surveillance (CCTV) systems to record intruders' activities and interface to access control systems for electrically locked doors. There are many types of security systems. Homeowners typically have small, self-contained noisemakers. These devices can also be complicated, multirole systems with computer monitoring and control.
It may even include a two-way voice which allows communication between the panel and monitoring station. The most basic alarm consists of at least one sensor to detect trespassers and an alerting device to indicate the intrusion. However, a typical premises security alarm employs the following components: Alarm control panel (ACP), or simply panel: The panel reads sensor inputs, tracks arm/disarm status, and signals intrusions.
In a modern device, there are typically one or more computer circuit boards inside a metal enclosure. Many newer networks often use sealed plastic boxes. Some also have their control units built-into the keypad or other human-machine interface. Sensors: In a security alarm, some sensors detect intrusions. Sensors' locations are at the perimeter of the protected area, within it, or both. Sensors can detect intruders by different methods. Alerting devices indicate an alarm condition. Most commonly, these are bells, sirens, and/or flashing lights. Alerting devices serve the dual purpose of warning occupants of intrusion and potentially scaring off burglars. Keypads: Keypads are devices that function as the human-machine interface to the system. In addition to buttons, keypads typically feature indicator lights, a small multi-character display, or both. In addition to the system itself, security alarms often offer a monitoring service. In the event of an alarm, the premises control unit contacts a central monitoring station. Operators at the station take appropriate action, such as contacting property owners, notifying the police, or dispatching private security forces. Such alerts transmit via dedicated alarm circuits, telephone lines, or the internet.
The passive infrared (PIR) motion detector is one of the most common sensors found in household and small business environments. This sensor does not generate or radiate energy; it works entirely by detecting the heat energy given off by other objects. PIR sensors identify abrupt changes in temperature at a given point. As an intruder walks in front of the sensor, the temperature at that point will rise from room temperature to body temperature and then back again. This quick change triggers the detection. PIR sensors designed to be wall- or ceiling-mounted come in various fields of view. PIRs require a power supply in addition to the detection signaling circuit.
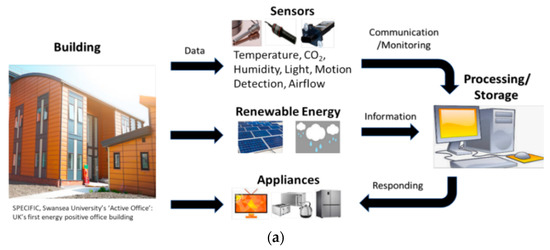
Figure 3: The State-of-the-Art of Sensors and Environmental Monitoring ... If a potential intruder tries to enter into a house, they test whether it is closed and locked, uses tools on openings, and/or applies pressure, creating low-frequency sound vibrations. Before the intruder breaks in, the infrasound detector automatically detects the intruder's actions. The purpose of such a system is to detect burglars before they enter the house to avoid both theft and vandalism. The sensitivity is dependent on the size of a home and the presence of animals.
Microwave detectors respond to a Doppler shift in the frequency of the reflected energy, by a phase shift, or by a sudden reduction of the level of received energy. Any of these effects may indicate motion of an intruder. Microwave detectors are low cost, easy to install, have an invisible perimeter barrier, and are not affected by fog, rain, snow, sand storms, or wind. May be affected by the presence of water dripping on the ground. Typically need a sterile clearance area to prevent partial blocking of the detection field.
In the last decades, many technological progresses have been made in this area and MEMS accelerometers are used in high-reliability environments and are starting to replace other established technologies. MEMS accelerometer can be applied as a sensor in the earthquake disaster prevention, since one of the main characteristics of MEMS accelerometers is the linear frequency response to DC to about 500 Hz, and this capability offers an improvement in measuring ground motion at lower-frequency band. Another practical application of MEMS accelerometers is in machine condition monitoring to reduce machines' maintenance. Wireless and embedded technologies such as Micro-electro Mechanical system sensors offer a wireless smart vibration measurement of machine's condition. Moving to the defence field, it can be applied in fence-mounted intrusion detection systems. Since MEMS sensors are able to work in a wide temperature range, they can prevent intrusions in outdoors and very spread-off perimeters.
Microphonic systems vary in design (for example, time-domain reflectrometer or piezo-electric) but each is generally based on the detection of an intruder attempting to cut or climb over a fence. Usually the microphonic detection systems are installed as sensor cables attached to rigid chain-wire fences, however, some specialized versions of these systems can also be installed buried underground. Depending on the type, it can be sensitive to different frequencies or levels of noise or vibration. The system is based on coaxial or electro-magnetic sensor cable with the controller having the ability to differentiate between signals from the cable or chain-wire being cut, an intruder climbing the fence, or bad weather conditions. The systems are designed to detect and analyze incoming electronic signals received from the sensor cable, and then to generate alarms from signals which exceed pre-set conditions. The systems have adjustable electronics to permit installers to change the sensitivity of the alarm detectors to the suit specific environmental conditions. The tuning of the system is usually done during commissioning of the detection devices. Microphonic systems are relatively inexpensive compared to other systems and easy to install, but older systems may have a high rate of false alarms caused by wind and other distances. Some newer systems use DSP to process the signal and reduce false alarms.
This system employs an electromagnetic field disturbance principle based on two coaxial cables. The transmitter emits continuous radio frequency (RF) energy along one cable and the energy is received by the other cable. When the change in field strength weakens due to the presence of an object and reaches a preset lower threshold, an alarm condition is generated. The system is covert after installation. The surrounding soil must offer good drainage in order to avoid nuisance alarms. Ported coaxial cables are concealed as a buried form but can be affected by RF noise and is difficult to install.
Security electric fences consist of wires that carry pulses of electric current to provide a non-lethal shock to deter potential intruders. Tampering with the fence also results in an alarm that is logged by the security electric fence energiser, and can also trigger a siren, strobe, and/or notifications to a control room or directly to the owner via email or phone. In practical terms, security electric fences are a type of sensor array that acts as a (or part of a) physical barrier, a psychological deterrent to potential intruders, and as part of a security alarm system. Electric fences are less expensive than many other methods, less likely to give false alarms than many other alternative perimeter security methods, and have highest psychological deterrent of all methods, but there is a potential for unintended shock.
The trigger signal from sensors are transmitted to one or more control units either through wires or wireless means, such as radio, line carrier, and infrared. Wired systems are convenient when sensors, such as passive infrared motion sensors and smoke detectors require external power to operate correctly; however, they may be more costly to install. Basic wired systems utilize a star network topology, where the panel is at the center logically, and all devices home run their line wires back to the panel. More complex panels use a Bus network topology where the wire basically is a data loop around the perimeter of the facility, and has drops for the sensor devices which must include a unique device identifier integrated into the sensor device itself. Wired systems also have the advantage, if wired properly for example by dual loop, of being tamper-evident. Wireless systems, on the other hand, often use battery-powered transmitters which are easier to install and have less expensive start-up costs, but may fail if the batteries are not maintained. Depending on distance and construction materials, one or more wireless repeaters may be required to bring the signal to the alarm panel reliably. A wireless system can be moved to a new property easily. An important wireless connection for security is between the control panel and the monitoring station.
Wireless monitoring of the alarm system protects against a burglar cutting cables or from failures of an internet provider. This setup is commonly referred to as fully wireless. Hybrid systems use both wired and wireless sensors to achieve the benefits of both. Transmitters can also be connected through the premises' electrical circuits to transmit coded signals to the control unit (line carrier). The control unit usually has a separate channel or zone for burglar and fire sensors, and more advanced systems have a separate zone for every different sensor, as well as internal trouble indicators, such as mains power loss, low battery, and broken wires.
An electricity meter, electric meter, electrical meter, energy meter, kilowatt-hour meter, or power meter is a device that measures the amount of electric energy consumed by a residence, a business, or an electrically powered device over a time interval. Electric utilities use electric meters installed at customers' premises for billing and monitoring purposes. They are typically calibrated in billing units, the most common one being the kilowatt hour (kWh). They are usually read once each billing period. When energy savings during certain periods are desired, some meters may measure demand, the maximum use of power in some interval. "Time of day" metering allows electric rates to be changed during a day, to record usage during peak high-cost periods and off-peak, lower-cost, periods. Also, in some areas meters have relays for demand response load shedding during peak load periods.
Many experimental types of meter were developed. Thomas Edison at first worked on a direct current (DC) electromechanical meter with a direct reading register, but instead developed an electrochemical metering system, which used an electrolytic cell to totalise current consumption. At periodic intervals the plates were removed and weighed, and the customer billed. The electrochemical meter was labor-intensive to read and not well received by customers. DC meters often measured charge in ampere hours. Since the voltage of the supply should remain substantially constant, the reading of the meter was proportional to actual energy consumed. For example, if a meter recorded that 100 ampere hours had been consumed on a 200-volt supply, then 20 kilowatt-hours of energy had been supplied. In 1885 Ferranti offered a mercury motor meter with a register similar to gas meters; this had the advantage that the consumer could easily read the meter and verify consumption. Another early electromagnetic meter with visible readouts was a DC meter by Hermann Aron, who patented it in 1884. Hugo Hirst of the British General Electric Company introduced it commercially into Great Britain from 1888. Aron's power meter (later adapted for AC power) recorded the total charge used over time, and showed it on a series of clock dials.
Electrochemical meters were also improved to be directly read out, such as the Bastian electrolytic meter invented in 1897, and the Wright electrolytic meter or 'Reason' meter which was patented in 1900. The Wright meter, used mainly in the United Kingdom, consisted of a vertically mounted glass structure with a mercury reservoir at the top of the meter. As current was drawn from the supply, electrochemical action transferred the mercury to the bottom of the column. The height of the mercury indicated the total charge. The meter had to be reset to zero before the reserve of mercury ran out. Reset was performed by inverting the meter, restoring the mercury to the reservoir.
The most common unit of measurement on the electricity meter is the kilowatt hour [kWh], which is equal to the amount of energy used by a load of one kilowatt over a period of one hour, or 3,600,000 joules. Some electricity companies use the SI megajoule instead. Demand is normally measured in watts, but averaged over a period, most often a quarter- or half-hour. Reactive power is measured in "thousands of volt-ampere reactive-hours", (kvarh). By convention, a "lagging" or inductive load, such as a motor, will have positive reactive power. A "leading", or capacitive load, will have negative reactive power.
Volt-amperes measures all power passed through a distribution network, including reactive and actual. This is equal to the product of root-mean-square volts and amperes. Distortion of the electric current by loads is measured in several ways. Power factor is the ratio of resistive (or real) power to volt-amperes. A capacitive load has a leading power factor, and an inductive load has a lagging power factor. A purely resistive load (such as a filament lamp, heater or kettle) exhibits a power factor of 1.
Current harmonics are a measure of distortion of the wave form. For example, electronic loads such as computer power supplies draw their current at the voltage peak to fill their internal storage elements. This can lead to a significant voltage drop near the supply voltage peak which shows as a flattening of the voltage waveform. This flattening causes odd harmonics which are not permissible if they exceed specific limits, as they are not only wasteful, but may interfere with the operation of other equipment. Harmonic emissions are mandated by law in EU and other countries to fall within specified limits. In addition to metering based on the amount of energy used, other types of metering are available. Meters which measured the amount of charge (coulombs) used, known as ampere hour meters, were used in the early days of electrification. These were dependent upon the supply voltage remaining constant for accurate measurement of energy usage, which was not a likely circumstance with most supplies. The most common application was in relation to special-purpose meters to monitor charge / discharge status of large batteries. Some meters measured only the length of time for which charge flowed, with no measurement of the magnitude of voltage or current being made. These are only suited for constant-load applications and are rarely used today.
Electricity meters operate by continuously measuring the instantaneous voltage (volts) and current (amperes) to give energy used (in joules, kilowatt-hours etc.). Meters for smaller services (such as small residential customers) can be connected directly in-line between source and customer. For larger loads, more than about 200 ampere of load, current transformers are used, so that the meter can be located somewhere other than in line with the service conductors. The meters fall into two basic categories, electromechanical and electronic.
The disc is supported by a spindle which has a worm gear which drives the register. The register is a series of dials which record the amount of energy used. The dials may be of the cyclometer type, an odometer-like display that is easy to read where for each dial a single digit is shown through a window in the face of the meter, or of the pointer type where a pointer indicates each digit. With the dial pointer type, adjacent pointers generally rotate in opposite directions due to the gearing mechanism. The amount of energy represented by one revolution of the disc is denoted by the symbol Kh which is given in units of watt-hours per revolution. The value 7.2 is commonly seen. Using the value of Kh one can determine their power consumption at any given time by timing the disc with a stopwatch.
P = 3600 ⋅ K h t {\displaystyle P={{3600\cdot Kh} \over t}} . Where: t = time in seconds taken by the disc to complete one revolution, P = power in watts. For example, if Kh = 7.2 as above, and one revolution took place in 14.4 seconds, the power is 1800 watts. This method can be used to determine the power consumption of household devices by switching them on one by one. Most domestic electricity meters must be read manually, whether by a representative of the power company or by the customer. Where the customer reads the meter, the reading may be supplied to the power company by telephone, post or over the internet. The electricity company will normally require a visit by a company representative at least annually in order to verify customer-supplied readings and to make a basic safety check of the meter. In an induction type meter, creep is a phenomenon that can adversely affect accuracy, that occurs when the meter disc rotates continuously with potential applied and the load terminals open circuited. A test for error due to creep is called a creep test. Two standards govern meter accuracy, ANSI C12.20 for North America and IEC 62053.
Electronic meters display the energy used on an LCD or LED display, and some can also transmit readings to remote places. In addition to measuring energy used, some electronic meters can also record other parameters of the load and supply such as instantaneous and maximum rate of usage demands, voltages, power factor and reactive power used etc. They can also support time-of-day billing, for example, recording the amount of energy used during on-peak and off-peak hours. The meter has a power supply, a metering engine, a processing and communication engine (i.e. a microcontroller), and other add-on modules such as a real time clock (RTC), a liquid crystal display, infra red communication ports/modules and so on. The metering engine is given the voltage and current inputs and has a voltage reference, samplers and quantisers followed by an analog to digital conversion section to yield the digitised equivalents of all the inputs. These inputs are then processed using a digital signal processor to calculate the various metering parameters. The largest source of long-term errors in the meter is drift in the preamp, followed by the precision of the voltage reference. Both of these vary with temperature as well, and vary wildly when meters are outdoors. Characterising and compensating for these is a major part of meter design. The processing and communication section has the responsibility of calculating the various derived quantities from the digital values generated by the metering engine. This also has the responsibility of communication using various protocols and interface with other addon modules connected as slaves to it. RTC and other add-on modules are attached as slaves to the processing and communication section for various input/output functions. On a modern meter most if not all of this will be implemented inside the microprocessor, such as the RTC, LCD controller, temperature sensor, memory and analog to digital converters.
EN 62053-31 (formerly DIN 43864) defines the S0 interface, which is a galvanically isolated open collector output. Voltage and current are limited to 27 V and 27 mA, respectively. Each metered amount of electrical energy produces one impulse with a length of 32-100 ms. The meter constant (pulses per kWh) is programmable on some meters, but often fixed to 1000-10000 pulses per kWh. Other meters implement a similar pulse interface, but with an infrared LED instead of an electrical connection. The interface is also used on other kinds of meters, like water meters. Some EU countries install meters with a DSMR 5.0.2 P1 Open metering system port (wired serial interface). Many meters designed for semi-automated reading have a serial port that communicates by infrared LED through the faceplate of the meter. In some multi-unit buildings, a similar protocol is used, but in a wired bus using a serial current loop to connect all the meters to a single plug. The plug is often near a more easily accessible point. In the European Union, the most common infrared and protocol is "FLAG", a simplified subset of mode C of IEC 61107. In the United States and Canada, the favored infrared protocol is ANSI C12.18. Some industrial meters use protocols for programmable logic controllers, like Modbus or DNP3. One protocol proposed for this purpose is DLMS/COSEM which can operate over any medium, including serial ports. The data can be transmitted by Zigbee, Wi-Fi, telephone lines or over the power lines themselves. Some meters can be read over the internet. Other more modern protocols are also becoming widely used, like OSGP (Open Smart Grid Protocol). Electronic meters now also use low-power radio, GSM, GPRS, Bluetooth, IrDA, as well as RS-485 wired link. The meters can store the entire usage profiles with timestamps and relay them at the click of a button. The demand readings stored with the profiles accurately indicate the load requirements of the customer. This load profile data is processed at the utilities for billing and planning purposes. AMR (Automatic Meter Reading) and RMR (Remote Meter Reading) describe various systems that allow meters to be checked remotely, without the need to send a meter reader. An electronic meter can transmit its readings by telephone line or radio to a central billing office.
2. System Architecture & Core Working Principles A potentially powerful means to reduce household energy consumption is to provide convenient real-time feedback to users so they can change their energy using behaviour. Recently, low-cost energy feedback displays have become available, that may be able to measure energy (Watt-hours), momentary power (wattage), and may additionally be able to measure the MAINS voltage, current, uptime, apparent power, capturing peak wattage and peak current, and have a manually set clock.
The display may indicate the power consumption over the week graphically. A study using a consumer-readable meter in 500 Ontario homes by Hydro One showed an average 6.5% drop in total electricity use when compared with a similarly sized control group. Hydro One subsequently offered free power monitors to 30,000 customers based on the success of the pilot. Projects such as Google PowerMeter, take information from a smart meter and make it more readily available to users to help encourage conservation.
Plug-in electricity meters (or plug load meters) measure energy used by individual appliances. There are a variety of models available on the market today but they all work on the same basic principle. The meter is plugged into an outlet, and the appliance to be measured is plugged into the meter. Such meters can help in energy conservation by identifying major energy users, or devices that consume excessive standby power. Web resources can also be used, if an estimate of the power consumption is enough for the research purposes. A power meter can often be borrowed from the local power authorities or a local public library.
Electricity retailers may wish to charge customers different tariffs at different times of the day to better reflect the costs of generation and transmission. Since it is typically not cost effective to store significant amounts of electricity during a period of low demand for use during a period of high demand, costs will vary significantly depending on the time of day. Low cost generation capacity (baseload) such as nuclear can take many hours to start, meaning a surplus in times of low demand, whereas high cost but flexible generating capacity (such as gas turbines) must be kept available to respond at a moment's notice (spinning reserve) to peak demand, perhaps being used for a few minutes per day, which is very expensive. Some multiple tariff meters use different tariffs for different amounts of demand. These are usually industrial meters. Domestic variable-rate meters generally permit two to three tariffs ("peak", "off-peak" and "shoulder") and in such installations a simple electromechanical time switch may be used. Historically, these have often been used in conjunction with electrical storage heaters or hot water storage systems. Multiple tariffs are made easier by time of use (TOU) meters which incorporate or are connected to a time switch and which have multiple registers. Switching between the tariffs may happen via ripple control, or via a radio-activated switch. In principle, a sealed time switch can also be used, but is considered more vulnerable to tampering to obtain cheaper electricity.
Radio-activated switching is common in the UK, with a nightly data signal sent within the longwave carrier of BBC Radio 4, 198 kHz. The time of off-peak charging is usually seven hours between midnight and 7:00am GMT/BST, and this is designed to power storage heaters and immersion heaters. In the UK, such tariffs are typically branded Economy 7, White Meter or Dual-Rate. The popularity of such tariffs has declined in recent years, at least in the domestic market, because of the (perceived or real) deficiencies of storage heaters and the comparatively much lower cost of natural gas per kWh (typically a factor of 3-5 times lower). Nevertheless, a sizeable number of properties do not have the option of gas, with many in rural areas being outside the gas supply network, and others being expensive upfront to upgrade to a radiator system. An Economy 10 meter is also available, which gives 10 hours of cheap off-peak electricity spread out over three timeslots throughout a 24-hour period. This allows multiple top-up boosts to storage heaters, or a good spread of times to run a wet electric heating system on a cheaper electricity rate. Most meters using Economy 7 switch the entire electricity supply to the cheaper rate during the 7 hour night time period, not just the storage heater circuit. The downside of this is that the daytime rate per kWh is significantly higher, and that standing charges are sometimes higher. For example, as of July 2017, normal ("single rate") electricity costs 17.14p per kWh in the London region on the standard default tariff for EDF Energy (the post-privatisation incumbent electricity supplier in London), with a standing charge of 18.90p per day. The equivalent Economy 7 costs are 21.34p per kWh during the peak usage period with 7.83p per kWh during the off-peak usage period, and a standing charge of 18.90p per day. Timer switches installed on washing machines, tumble dryers, dishwashers and immersion heaters may be set so that they only switch on during the off-peak usage period.
Smart meters go a step further than simple AMR (automatic meter reading). They offer additional functionality including a real-time or near real-time reads, power outage notification, and power quality monitoring. They allow price setting agencies to introduce different prices for consumption based on the time of day and the season. Another type of smart meter uses nonintrusive load monitoring to automatically determine the number and type of appliances in a residence, how much energy each uses and when. This meter is used by electric utilities to do surveys of energy use. It eliminates the need to put timers on all of the appliances in a house to determine how much energy each uses.
The standard business model of electricity retailing involves the electricity company billing the customer for the amount of energy used in the previous month or quarter. In some countries, if the retailer believes that the customer may not pay the bill, a prepayment meter may be installed. This requires the customer to make advance payment before electricity can be used. If the available credit is exhausted then the supply of electricity is cut off by a relay. In the UK, mechanical prepayment coin meters used to be common, both in private rented accommodation and residential customers of the electricity boards, the nationalised electricity sector. Disadvantages of these included the need for regular visits to remove the cash, and risk of theft of the cash in the meters by both customers and burglars. The first automated pre-payment meters were introduced by London Electricity, in conjunction with the Schlumberger Metering based in Felixstowe, UK. They were initially called Key Meters and later renamed Budget Meters. They avoided the 60,000 disconnections for non-payment per annum and the many disadvantages of cash prepayment. They were also popular with customers who wanted a convenient payment method, especially in short term tenancies. Well over 1 million such meters were installed across the UK in the first few years after introduction. Modern solid-state electricity meters, in conjunction with smart cards, have removed these disadvantages and such meters are commonly used for customers considered to be a poor credit risk. In the UK, customers can use organisations such as the Post Office Limited or PayPoint network, where rechargeable tokens (Quantum cards for natural gas, or plastic "keys" for electricity) can be loaded with whatever money the customer has available. In Indonesia, Northern Ireland, South Africa and Sudan, prepaid meters are recharged by entering a unique, encoded twenty digit number using a keypad. This makes the tokens, which may be electronically delivered or printed on a slip of paper at point of purchase, very cheap to produce. Around the world, experiments are going on, especially in developing countries, to test pre-payment systems. In some cases, prepayment meters have not been accepted by customers. There are various groups, such as the Standard Transfer Specification (STS) association, which promote common standards for prepayment metering systems across manufacturers. Prepaid meters using the STS standard are used in many countries.
Many electricity customers are installing their own electricity generating equipment, whether for reasons of economy, redundancy or environmental reasons. When a customer is generating more electricity than required for his own use, the surplus may be exported back to the power grid. Customers that generate back into the "grid" usually must have special equipment and safety devices to protect the grid components (as well as the customer's own) in case of faults (electrical short circuits) or maintenance of the grid (say voltage on a downed line coming from an exporting customers facility). This exported energy may be accounted for in the simplest case by the meter running backwards during periods of net export, thus reducing the customer's recorded energy usage by the amount exported. This in effect results in the customer being paid for his/her exports at the full retail price of electricity. Unless equipped with a ratchet or equivalent, a standard meter will accurately record power flow in each direction by simply running backwards when power is exported. Where allowed by law, utilities maintain a profitable margin between the price of energy delivered to the consumer and the rate credited for consumer-generated energy that flows back to the grid. Lately, upload sources typically originate from renewable sources (e.g., wind turbines, photovoltaic cells), or gas or steam turbines, which are often found in cogeneration systems. Another potential upload source that has been proposed is plug-in hybrid car batteries (vehicle-to-grid power systems). This requires a "smart grid," which includes meters that measure electricity via communication networks that require remote control and give customers timing and pricing options. Vehicle-to-grid systems could be installed at workplace parking lots and garages and at park and rides and could help drivers charge their batteries at home at night when off-peak power prices are cheaper, and receive bill crediting for selling excess electricity back to the grid during high-demand hours.
The location of an electricity meter varies with each installation. Possible locations include on a utility pole serving the property, in a street-side cabinet (meter box) or inside the premises adjacent to the consumer unit / distribution board. Electricity companies may prefer external locations as the meter can be read without gaining access to the premises but external meters may be more prone to vandalism. Current transformers permit the meter to be located remotely from the current-carrying conductors. This is common in large installations. For example, a substation serving a single large customer may have metering equipment installed in a cabinet, without bringing heavy cables into the cabinet.
Electricity meters are governed by various standards worldwide to ensure accuracy, reliability, and interoperability. These standards vary by region and are often based on national or international regulations. Below are the key standards used in different regions. European Standards In Europe, electricity meters are primarily regulated under the Measuring Instruments Directive (MID), established by the European Union. MID ensures that electricity meters meet specific technical and operational criteria for accurate billing. Key standards include: EN 50470-1 to EN 50470-3: These standards specify general requirements, particular requirements, and tests for active energy meters. IEC 62052 and IEC 62053 series: Commonly applied for the functional and accuracy performance of electricity meters. American Standards In the United States, the standards are developed by the American National Standards Institute (ANSI) and the Institute of Electrical and Electronics Engineers (IEEE). Key standards include: ANSI C12 Series: Covering meter accuracy, testing, and performance for residential, commercial, and industrial meters. IEEE 1708: Provides guidelines for testing the cybersecurity of smart meters. Chinese Standards In China, electricity meter standards are governed by the China National Standards (GB), which align with international practices but also reflect specific local requirements: GB/T 17215: Sets the requirements for static electricity meters for active energy. DL/T 645: Specifies the communication protocol for multi-function electricity meters, ensuring interoperability.
Australian Standards In Australia, electricity meters adhere to the standards set by Standards Australia and the National Measurement Institute (NMI): AS 62052.11 and AS 62053.21: Align with IEC standards for general requirements and accuracy classes of electricity meters. NMI M 6: Specifies the metrological requirements for electricity meters used for billing.
Energy management software Energy monitoring and targeting Meter operator Utility submeter Zellweger off-peak Multimeter Hover, tap, or focus any component on the drawing (or a circuit below it) for details. Click to pin; move away or click again to clear. Every component in the diagram above, grouped by section, with its role and the relevant standard.
The owner's stated comfort, energy, and indoor-air-quality (IAQ) goals — the starting requirements that every downstream design decision, from HVAC control sequences to sensor selection, has to satisfy. Architectural floor plans and mechanical/electrical/plumbing drawings that establish zone boundaries, ceiling space, and equipment locations — the physical layout every BAS point list and cable route is built against.
Mechanical and electrical equipment schedules and submittals (AHUs, VAV boxes, chillers, boilers, panels) that define exactly which points, I/O counts, and controller types the BAS design must accommodate. Target Energy Use Intensity (EUI), sustainability commitments, and the capital and operating budget the project has to work within — the numbers that size the energy-management and analytics scope.
The applicable codes, standards, and owner design standards — ASHRAE Guideline 36, BACnet (Standard 135), energy codes, and any internal owner-specific control and naming conventions — that bound the design from day one. The existing building automation system, its point database, and its network topology — critical for retrofit and expansion projects where new controllers must integrate with (or migrate off of) legacy infrastructure.
Occupant comfort expectations and the owner's broader business objectives — space utilization, hybrid-work scheduling, wellness certification — that shape control strategy beyond pure energy performance. The end deliverable of the workflow: a fully installed, commissioned, and operating building automation system controlling HVAC, lighting, and other building subsystems to the design sequences.
Live trend logs, alarm and event feeds, and operator dashboards that give the operations team real-time visibility into every controlled zone and piece of equipment. Recurring energy reports and Energy Use Intensity benchmarking against ENERGY STAR Portfolio Manager and ASHRAE 90.1 baselines — the evidence the sustainability goals set in Project Inputs were actually met.
Operations & maintenance manuals and as-built drawings handed to facility staff at closeout — the reference set that keeps the system maintainable long after the commissioning team leaves. Ongoing performance optimization — setpoint reset tuning, fault detection and diagnostics (FDD) findings, and demand-response participation — that keeps squeezing energy and comfort gains out of the installed system.
The bottom-line outcome the entire smart-building engineering workflow exists to deliver: measurably lower energy use and demand alongside better, more consistent occupant comfort. 3. Software Implementation, Frameworks & Protocols The workflow opens with a site assessment & audit, a baseline energy (EUI) measurement, defining control objectives, an initial risk & cyber assessment, and an ROI & lifecycle analysis to justify the project.
System design locks in the BAS architecture, the control strategy (sequence of operations at a high level), network & topology planning, point list & I/O sizing, and the OT security design. Detailed engineering: writing the sequence of operations, control diagrams, network diagrams, panel & rack layouts, and the specifications & bill of quantities that get issued for construction.
Controller & device selection, vendor coordination, submittal review, factory acceptance testing, and material procurement — turning the design into ordered, staged hardware. Field execution: panel fabrication, field installation, device integration, network configuration, and power & grounding — the phase that physically builds the system on site.
Pre-functional checks, functional performance testing, trend & alarm validation, sequence verification, and MBCx/TAB coordination — proving the installed system actually does what the sequences say. Post-occupancy optimization: energy analysis & EUI tracking, fault detection & diagnostics, setpoint optimization, demand response participation, and digital twin modeling.
The sustaining phase: 24/7 monitoring, alarm management, preventive maintenance, firmware updates, and continuous improvement that keeps the system performing over its full service life. The dashed feedback loop closing the workflow: monitoring, analysis, and lessons learned from Optimization & Analytics and Operate & Maintain flow back into Assess & Plan, so the building keeps improving after commissioning instead of standing still.
The core BAS signal chain: field sensors & actuators (temperature, humidity, CO2, lighting, valves, fans) wire into a DDC controller, which exchanges data with I/O modules and reports up to the BAS server/front end for supervisory monitoring. Direct Digital Controllers (DDC) run the equipment directly; the supervisory layer adds scheduling, trending, and alarming on top. Supports HVAC, lighting, pumps, fans, elevators, and more, and local control continues even during a network outage.
Key output: reliable, automated system operation. A typical Air Handling Unit (AHU) feeds conditioned air to VAV boxes that modulate zone airflow. Supply air temperature reset, static pressure reset, economizer control & free cooling, demand-controlled ventilation, and VAV terminal box control are the core ASHRAE Guideline 36 sequences shown here.
HVAC control covers supply air temperature reset, static pressure reset, economizer control & free cooling, demand-controlled ventilation (DCV), and VAV terminal box control — all written to ASHRAE Guideline 36 high-performance sequences. Key output: comfort with minimum energy. A workstation/operator interface connects through a network switch to BACnet/IP (Ethernet) and BACnet MS/TP (twisted-pair) device chains, which route through gateways to third-party systems — fire alarm, metering, lighting, and elevators.
Protocol scope: BACnet (ANSI/ASHRAE 135), BACnet/IP & MS/TP plus Wi-Fi, Modbus TCP/RTU and OPC UA for third-party integration, secure networking & VLAN segmentation, and NTP time sync with scheduled backups. Key output: interoperable, secure communication. Smart meters (electric, gas, water) feed a data historian & cloud platform, which drives the analytics & dashboards that surface energy trends and anomalies back to the facility and energy-management teams.
Energy management covers Energy Use Intensity (EUI) tracking, ENERGY STAR Portfolio Manager benchmarking, load profiling & demand response, Fault Detection & Diagnostics (FDD), and digital twin & predictive maintenance. Key output: lower energy and operating cost. Users authenticate through a firewall before reaching the BAS network, which is segmented down to controllers, servers, cameras, and workstations — keeping the operational-technology (OT) layer isolated from general IT traffic.
Security scope: network segmentation & access control, role-based access & MFA, encryption/patching & vulnerability management, and monitoring, logging & incident response for the OT environment. Key output: secure and resilient operations. The Computerized Maintenance Management System (CMMS) that tracks work orders and asset maintenance history, integrated into the BAS ecosystem through the middleware layer so alarms can auto-generate tickets.
The enterprise resource planning and finance system, connected so energy costs, capital projects, and maintenance spend tracked in the BAS ecosystem can roll up into corporate financial reporting. The Integrated Workplace Management System (IWMS) that tracks space utilization and occupancy — increasingly fed by BAS occupancy sensor data to right-size HVAC scheduling to actual space use.
The fire alarm and life-safety system, integrated at the enterprise level so a fire event can trigger coordinated building-wide responses — smoke control sequences, elevator recall, and door unlock — through the BAS platform. The API and middleware integration layer that mediates data exchange between enterprise systems (CMMS, ERP, IWMS, fire alarm) and the BAS platform — the piece that keeps the architecture from becoming a set of disconnected silos.
The alarming module of the BAS platform — prioritizes, routes, and logs alarms from every connected controller and field device so operators see the events that actually need a response first. The trending module that logs point values over time — the raw time-series data behind every energy report, FDD rule, and commissioning trend graph.
The scheduling module that drives occupied/unoccupied setback schedules, holiday calendars, and optimal start/stop — one of the single biggest energy-savings levers in the whole architecture. The graphics module that renders floor plans, AHU schematics, and equipment mimics for the operator front end — turning raw BACnet objects into a navigable visual interface.
The analytics module that applies rules and statistical models to trend and alarm data — the engine behind Fault Detection & Diagnostics (FDD) and energy-anomaly detection. 4. Practical Deployment, Analysis & Case Studies The reporting module that packages energy, alarm, and performance data into scheduled reports for facility managers, energy managers, and ENERGY STAR benchmarking submissions.
The Fault Detection & Diagnostics module that continuously compares actual equipment behavior against expected rules-based or model-based performance and flags degrading or faulty equipment before it fails outright. The user-management module controlling operator accounts, role-based permissions, and audit logging of who changed what setpoint and when — a core piece of BAS cyber hygiene.
HVAC equipment — AHUs, VAV boxes, chillers, boilers — as one of the field systems reporting up through the BAS platform to enterprise and analytics layers. Lighting controls — dimming, occupancy sensing, and daylight harvesting — integrated as a field system alongside HVAC under the same BAS platform for unified scheduling and energy reporting.
Electric, gas, and water sub-meters feeding usage data directly into the BAS platform and, from there, into the smart-meter and data-historian chain for EUI tracking. Access control readers and door controllers integrated as a field system — allowing occupancy-driven HVAC and lighting responses tied to actual badge-in activity per zone.
CCTV cameras integrated as a field system, correlating video with BAS and access events for unified incident review across security and building-operations teams. Elevator controllers integrated as a field system — enabling coordinated fire-alarm recall sequences and destination-dispatch tie-ins with occupancy and access data.
Fire alarm and suppression systems integrated as a field system so life-safety events can drive coordinated building-wide responses through the same BAS platform. Domestic water, irrigation, and leak-detection systems integrated as a field system, feeding consumption and leak-alarm data into the same energy and facility dashboards.
The cloud or on-prem historian that stores long-term time-series data from the BAS platform — the archive that feeds trend analysis, EUI benchmarking, and year-over-year performance comparisons. A data lake aggregating raw BAS, IoT, and enterprise data at scale — the staging ground for the machine-learning and analytics workloads that need more than a simple historian can offer.
A digital twin — a live virtual model of the building fed by real-time BAS and sensor data — used to simulate control changes, forecast loads, and visualize performance before touching the real equipment. The machine-learning/AI engine that turns historian and data-lake volumes into predictive insight — forecasting loads, detecting anomalies, and driving predictive-maintenance recommendations back into the BAS platform.
The camera-coverage design checklist: identify assets & critical areas, define fields of view & coverage, avoid dead zones & glare, install height & angle, night performance (IR/low-light), privacy masking where required, bandwidth & storage planning, retention policy (days), and record resolution & FPS. A typical building coverage layout: a perimeter bullet camera along the ground-level approach, a corner dome covering the roof area, a door camera at the entrance, and a panoramic camera overlooking the parking lot — the standard zone-by-zone camera plan integrated with the building's security field systems.
The topmost IoT/sensor stack layer: AI-driven insight, operator dashboards, and automated reports — where raw sensor readings finally become decisions people and algorithms act on. The data layer: historian and cloud storage that persists every sensor reading over time — the foundation the application layer's dashboards and AI models are built on.
The network layer: BACnet/IP, Wi-Fi, and LoRaWAN transports that move readings from edge gateways up to the data layer — the layer where bandwidth, latency, and protocol choice matter most. The edge layer: gateways and controllers that aggregate, filter, and locally pre-process device data before it hits the network — reducing bandwidth and giving the system a fallback if the wide-area link drops.
The device layer: the physical sensors (temperature, humidity, CO2, occupancy) and actuators at the very source of every measurement and control action — where the whole IoT stack begins. The Niagara Framework (Tridium) is one of the most widely deployed BAS integration platforms — a vendor-neutral software framework that normalizes BACnet, Modbus, LonWorks, and other protocols under one supervisory layer.
Johnson Controls' METASYS is a full-stack BAS platform spanning field controllers through enterprise-level supervisory software, common in large commercial and institutional portfolios. EcoStruxure Building Operation, offered under the Siemens brand, is a cloud-connected building management platform combining BAS supervisory control with energy analytics and IoT integration.
Siemens Desigo CC is a unified management station that integrates HVAC, fire, security, and energy management into a single operator interface across multi-building portfolios. Honeywell's integrated building management software suite spans BAS, fire, and security integration for commercial and industrial facilities.
Facility Explorer is a mid-market BAS platform aimed at smaller commercial buildings, offering scaled-down DDC control and web-based supervisory access. AVEVA's Unified Operations Center brings SCADA/historian-grade operations visibility and analytics into building and industrial-facility management, often paired with the BAS platform for enterprise reporting.
5. Performance Evaluation & Extended Technical Observations Autodesk design and BIM tools (Revit, AutoCAD) supply the as-designed and as-built building models that increasingly feed a building's digital twin and O&M documentation. Energy Use Intensity — total annual energy use per square foot (kBtu/ft²/yr) — is the headline metric for comparing a building's energy performance against ENERGY STAR and ASHRAE 90.1 benchmarks.
Total metered energy consumption by fuel type — electricity in kWh, natural gas in therms — the raw utility-bill data behind every EUI and cost calculation. Peak electrical demand (kW) — the maximum instantaneous draw the building hits, which drives demand charges on the utility bill and is the target metric for demand-response and load-shedding strategies.
HVAC system efficiency expressed in kW per ton of cooling — the standard metric for tracking chiller plant performance against design and part-load efficiency targets. Alarm rate and average response time — a high nuisance-alarm rate signals a poorly tuned BAS, while slow response time signals an understaffed or poorly prioritized operations team.
The volume of occupant comfort complaints (too hot, too cold, stuffy) — a direct, if noisy, signal of whether the control sequences are actually delivering on the comfort requirements set at the start of the project. The count of Fault Detection & Diagnostics issues detected, trended against a baseline — shows whether ongoing FDD is catching and resolving equipment problems faster than they accumulate.
System uptime percentage — how reliably the BAS platform, network, and controllers stay online — the baseline reliability metric every other KPI depends on being measured accurately. Core technical skills: HVAC systems & sequences of operation, DDC controller configuration & programming, BACnet networking & protocol setup, low-voltage cabling & power, and energy modeling & EUI analysis.
Delivery and analytics skills: data analytics & visualization, FDD & predictive maintenance, cybersecurity for OT systems, commissioning & MBCx, and documentation & as-built deliverables. BICSI's Electronic Safety & Security (ESS) Engineer credential covers the low-voltage design skills — structured cabling, device integration — directly relevant to smart-building field-system wiring.
ASIS International's Certified Protection Professional (CPP) credential — relevant where a smart-buildings engineer also owns integrated security scope (access control, CCTV) alongside the BAS. ASIS International's Physical Security Professional (PSP) credential, focused on physical security assessment and system design — relevant to the security & cyber resilience discipline shown in this diagram.
The LEED Accredited Professional credential from USGBC — the standard accreditation for engineers designing toward LEED energy, IAQ, and sustainability credits, closely tied to the energy-management scope of this diagram. ASHRAE Guideline 36 (High-Performance Sequences of Operation), Standard 135 (BACnet), and Guideline 13 (Specifying DDC Control Systems) — the three standards that most directly govern how BAS sequences are written and how controllers talk to each other.
ASHRAE Standard 90.1 (Energy Standard for Buildings), Standard 62.1 (Ventilation & IAQ), ENERGY STAR Portfolio Manager benchmarking, and Title 24/IECC energy codes — the baseline energy and IAQ requirements every design has to meet or beat. TIA-568/TIA-569 (structured cabling) and NFPA 70 (National Electrical Code, low-voltage power) — the standards governing the physical cabling and low-voltage wiring that every field device in this diagram ultimately connects through.
The signal and data flows that tie the diagram together — each shown as a colored line in the legend above. The solid arrows that carry the project through the 8-step end-to-end smart building engineering workflow, in order, from Assess & Plan through Operate & Maintain. The dashed loop beneath the 8-step workflow: monitoring, analysis, and optimization data flow back from Optimization & Analytics and Operate & Maintain into Assess & Plan, closing the loop instead of ending at commissioning.
The solid arrows in the Integrated Smart Building Architecture diagram — data flowing from enterprise systems through the integration layer to the BAS platform, out to field systems, and up into the cloud/historian, data lake, digital twin, and ML/AI engine. Implementing robust sensor security is essential in connected systems. Compromised sensors can feed corrupt, inaccurate data directly into operational systems, leading to devastating real-world failures, catastrophic physical damage, safety concerns, and compromised decision-making.
The increasing number of sensors in modern systems and the diversity of sensor types across applications like machine learning (ML) and automation present an expanding attack surface that can be invaded by bad actors. Sensors are used in a variety of critical systems, from the electric grid to autonomous vehicles and pacemakers. Corrupted data can create life-threatening conditions. Corrupted data can also result in an AI application that makes incorrect predictions, resulting in unsafe actions. Adding to the challenges, sensors are often resource-constrained devices, making it difficult to integrate significant levels of security directly into the sensor.
The growing complexity of sensor networks further expands the attack surface, making implementing sensor security complex as well as critical. That necessitates implementing a defense-in-depth approach that embraces hardware, network, and software layers ( Figure 1 ). Hardware considerations for sensor security include tamper detection using physical switches, accelerometers, or other tools to monitor for unauthorized physical access. Unused ports should be physically sealed and secure boot implemented.
Network isolation can be important, including the use of virtual LANs to limit outbound sensor communication and block all unauthorized inbound connections. Use of a zero-trust architecture to verify all communication provides an additional level of security. A well-regulated and controlled patch management process for the delivery of encrypted firmware updates is essential. ML tools can be used to identify anomalous sensor data that may indicate a sensor that’s been physically compromised or subjected to environmental manipulation.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Tamperproofing • https://en.wikipedia.org/wiki/Security%20alarm • https://en.wikipedia.org/wiki/Electricity%20meter • https://engineersuniverse.com/studios/smart-buildings/system-architecture • https://www.sensortips.com/sensor-security/how-to-implement-sensor-security-in-connected-systems/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Smart Building Environmental Sensor Tampering Detection.
[*] Metasploit Scan Running on Target Subnet for Smart Building Environmental Sensor Tampering Detection... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |