Complete Technical Paper Content — Smart Contract Automated Audit Framework Using Python
Overview & System Context
Smart Contract Automated Audit Framework Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8530 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A smart contract is a computer program or a transaction protocol that is intended to automatically execute, control or document events and actions according to the terms of a contract or an agreement. The objectives of smart contracts are the reduction of need for trusted intermediators, arbitration costs, and fraud losses, as well as the reduction of malicious and accidental exceptions. Smart contracts are commonly associated with cryptocurrencies, and the smart contracts introduced by Ethereum are generally considered a fundamental building block for decentralized finance (DeFi) and non-fungible token (NFT) applications. The original Ethereum white paper by Vitalik Buterin in 2014 describes the Bitcoin protocol as a weak version of the smart contract concept as originally defined by Nick Szabo, and proposed a stronger version based on the Solidity language, which is Turing complete. Since then, various cryptocurrencies have supported programming languages which allow for more advanced smart contracts between untrusted parties. A smart contract should not be confused with a smart legal contract, which is a traditional, natural-language, legally binding agreement that has selected terms expressed and implemented in machine-readable code.
A smart contract does not typically constitute a valid binding agreement at law. Proposals exist to regulate smart contracts. Smart contracts are not legal agreements, but instead transactions which are executed automatically by a computer program or a transaction protocol, such as technological means for the automation of payment obligations such as by transferring cryptocurrencies or other tokens. Some scholars have argued that the imperative or declarative nature of programming languages would impact the legal validity of smart contracts. In some jurisdictions, legal scholars have examined how the rigidity of smart contracts interacts with traditional doctrines such as contractual unforeseeability. For instance, Colombian legal scholarship has proposed adapting the theory of supervening onerousness (teoría de la imprevisión) to account for the high economic and systemic costs of reversing smart contract effects through judicial intervention, emphasizing the need to internalize these costs and develop new procedural mechanisms for digital environments. Since the 2015 launch of the Ethereum blockchain, the term "smart contract" has been applied to general purpose computation that takes place on a blockchain. The US National Institute of Standards and Technology describes a "smart contract" as a "collection of code and data (sometimes referred to as functions and state) that is deployed using cryptographically signed transactions on the blockchain network". In this interpretation a smart contract is any kind of computer program which uses a blockchain. A smart contract also can be regarded as a secured stored procedure, as its execution and codified effects (like the transfer of tokens between parties) cannot be manipulated without modifying the blockchain itself. In this interpretation, the execution of contracts is controlled and audited by the platform, not by arbitrary server-side programs connecting to the platform. In 2018, a US Senate report said: "While smart contracts might sound new, the concept is rooted in basic contract law. Usually, the judicial system adjudicates contractual disputes and enforces terms, but it is also common to have another arbitration method, especially for international transactions. With smart contracts, a program enforces the contract built into the code." States in the US which have passed legislation on the use of smart contracts include Arizona, Iowa, Nevada, Tennessee, and Wyoming. In April 2021, the UK Jurisdiction Taskforce (UKJT) published the Digital Dispute Resolution Rules (the Digital DR Rules), which were intended to enable the rapid resolution of blockchain and crypto legal disputes in Britain. In 2021, the Law Commission of England and Wales advised that smart legal contracts are capable of being recognized and enforced under existing English law.
Processes on a blockchain are generally deterministic in order to ensure Byzantine fault tolerance. Nevertheless, real world application of smart contracts, such as lotteries and casinos, require secure randomness. In fact, blockchain technology reduces the costs for conducting of a lottery and is therefore beneficial for the participants. Randomness on blockchain can be implemented by using block hashes or timestamps, oracles, commitment schemes, special smart contracts like RANDAO and Quanta, as well as sequences from mixed strategy Nash equilibria.
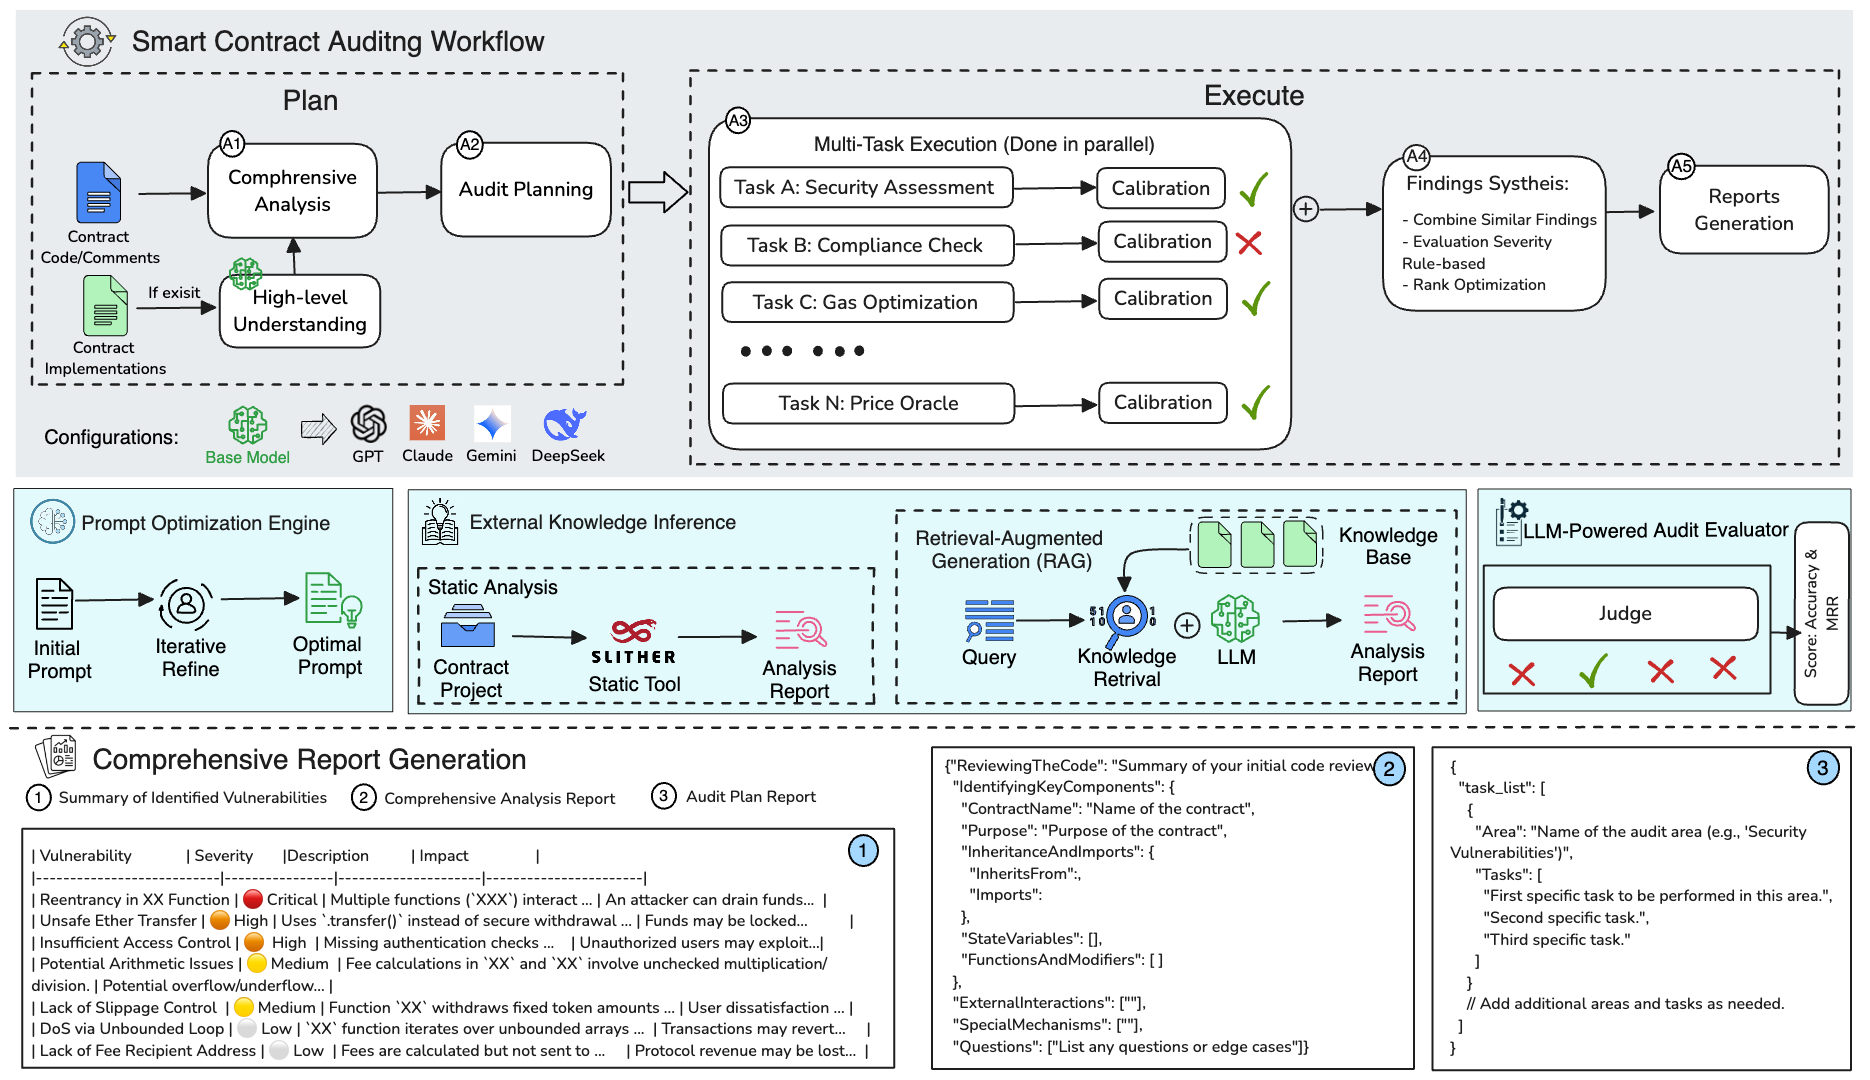
Code and Other Laws of Cyberspace Decentralized application Ethereum Regulation by algorithms Regulation of algorithms Ricardian contract (a design pattern to capture the intent of the agreement of parties) Loan Secure multiparty computation Transparency Figure 1: [2505.15242] Adaptive Plan-Execute Framework for Smart Contract ...
A smart meter is an electronic device that records information—such as consumption of electric energy, voltage levels, current, and power factor—and communicates the information to the consumer and electricity suppliers. Advanced metering infrastructure (AMI) differs from automatic meter reading (AMR) in that it enables two-way communication between the meter and the supplier.
Power-line communication for Smart Metering Power Line Communication (PLC) stands out among smart metering connectivity technologies because it leverages existing electrical power infrastructure for data transmission. Unlike cellular, radio-frequency (RF), or Wi-Fi-based solutions, PLC does not require building or maintaining separate communication networks, making it inherently more cost-effective and easier to scale. Two major PLC standards in smart metering are G3-PLC and the PRIME Alliance protocol. G3-PLC supports IPv6-based communications and adaptive data rates, providing robust performance even in noisy environments, while PRIME (PoweRline Intelligent Metering Evolution) focuses on efficient, high-speed communication with low-cost implementation. PLC-based smart metering is deployed extensively in regions like Europe, South America, and parts of Asia where dense infrastructure supports its use. Utilities favor PLC for its reliability in urban environments and for connecting large numbers of meters within smart grid networks.
An important feature of G3-PLC and PRIME is their ability to enable mesh networking (also called multi-hop), where smart meters act as repeaters for other meters in the network. This functionality allows meters to relay data from neighboring meters to ensure that the information reaches the Data Concentrator Unit (DCU), even if direct communication is not possible due to distance or signal obstructions. This approach enhances network reliability and coverage, particularly in dense urban environments or geographically challenging areas. Cellular Network (GPRS, NB-IoT, LTE-M): "Cellular technologies are highly scalable and secure. With national coverage, cellular connectivity can support a large number of meters in densely populated areas as well as reach those in remote locations." Wireless mesh network (e.g. Wirepas and Wi-Sun): Ideal for urban areas, where devices can relay data to optimize coverage and reliability. It is mostly used for Water Meter and Gas Meter Short-range: such as Wireless M-Bus (WMBUS) are commonly used in smart metering applications to enable reliable, low-power communication between utility meters and local data collectors within buildings or neighborhoods. Hybrid PLC/RF PRIME and G3-PLC standards defines an integrated approach for seamless integration of PLC and wireless communication, enhancing reliability and flexibility in smart grids. The challenges faced by rural utilities differ significantly from those of urban counterparts or utilities in remote, mountainous, or poorly serviced areas. Smart meters often extend their functionality through integration into Home Area Networks (HANs). These networks enable communication within the household and may include: In-Premises Displays: Providing real-time energy usage insights for consumers. Hubs: Interfacing multiple meters with the central head-end system. Technologies used in HANs vary globally but typically include PLC, wireless ad hoc networks, and Zigbee. By leveraging appropriate connectivity solutions, smart meters can address environmental and infrastructural needs while delivering communication and enhanced functionality.
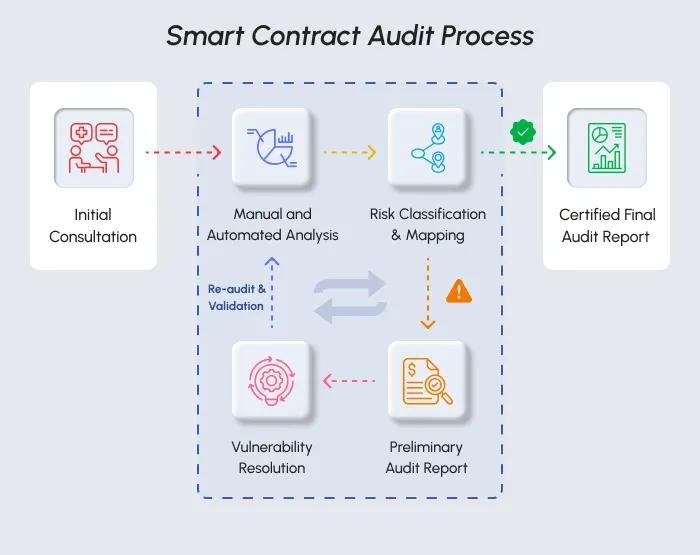
Figure 2: Smart Contract Auditing Services for Secure Blockchain Apps Integrated within the meter: a smart meter includes its own communication module (e.g.: cellular, RF-Mesh, PLC) and transmits data directly (or through a data concentrator) to utility servers. These meters can also form a local mesh network and act as relays for nearby devices without direct WAN access. Handled by an external local gateway next to the meter: in this architecture, the meter is limited to basic metrology and uses a local interface (e.g.: RS-485, Ethernet, or Wireless M-Bus) to forward data to a nearby gateway device. This gateway, often referred to as a smart meter gateway (SMGW) performs protocol translation, encryption, and handles upstream communication to utility systems via WAN technologies such as LTE, Ethernet or Wi-Fi.
IEC 62056 "IEC 62056 is the most widely adopted protocol" for smart meter communication, enabling reliable, two-way data exchange within Advanced Metering Infrastructure (AMI) systems. It encompasses the DLMS/COSEM protocol for structuring and managing metering data. "It is widely used because of its flexibility, scalability, and ability to support different communication media such as Power Line Communication (PLC), TCP/IP, and wireless networks.". It also supports data transmission over serial connections using ASCII or binary formats, with physical media options such as modulated light (via LED and photodiode) or wired connections (typically EIA-485).
ANSI C12.18 ANSI C12.18 is an ANSI Standard that describes a protocol used for two-way communications with a meter, mostly used in North American markets. The C12.18 Standard is written specifically for meter communications via an ANSI Type 2 Optical Port, and specifies lower-level protocol details. ANSI C12.19 specifies the data tables that are used. ANSI C12.21 is an extension of C12.18 written for modem instead of optical communications, so it is better suited to automatic meter reading. ANSI C12.22 is the communication protocol for remote communications.
OSGP The Open Smart Grid Protocol (OSGP) is a family of specifications published by the European Telecommunications Standards Institute (ETSI) used in conjunction with the ISO/IEC 14908 control networking standard for smart metering and smart grid applications. Millions of smart meters based on OSGP are deployed worldwide. On July 15, 2015, the OSGP Alliance announced the release of a new security protocol (OSGP-AES-128-PSK) and its availability from OSGP vendors.
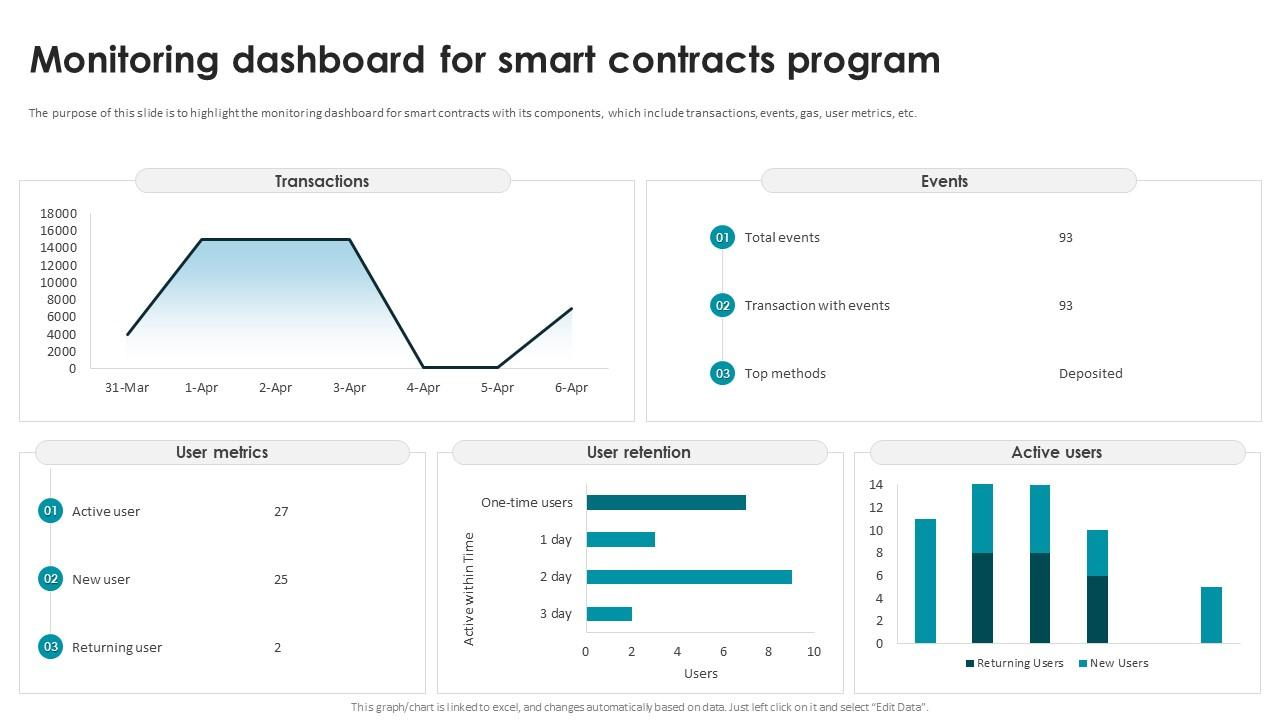
This deprecated the original OSGP-RC4-PSK security protocol which had been identified to be vulnerable. Figure 3: Smart Contracts Implementation Plan Monitoring Dashboard For Smart ... Meters and More "Meters and More was created in 2010 from the coordinated work between Enel and Endesa to adopt, maintain and evolve the field-proven Meters and More open communication protocol for smart grid solutions." . In 2010, the Meters and More Association was established to promote the protocol globally, ensuring interoperability and efficiency in power line communication (PLC)-based smart metering systems. Meters and More is an open communication protocol designed for advanced metering infrastructure (AMI). It facilitates reliable, high-speed data exchange over PLC networks, focusing on energy monitoring, demand response, and secure two-way communication between utilities and consumers.
Unlike DLMS/COSEM, which is a globally standardized and versatile protocol supporting multiple utilities (electricity, gas, and water), Meters and More is tailored specifically for PLC-based systems, emphasizing efficiency, reliability, and ease of deployment in electricity metering. There is a growing trend toward the use of TCP/IP technology as a common communication platform for Smart Meter applications, so that utilities can deploy multiple communication systems, while using IP technology as a common management platform. A universal metering interface would allow for development and mass production of smart meters and smart grid devices prior to the communication standards being set, and then for the relevant communication modules to be easily added or switched when they are. This would lower the risk of investing in the wrong standard as well as permit a single product to be used globally even if regional communication standards vary.
Data Concentrator A Data Concentrator Unit (DCU) aggregates data from multiple smart meters within a localized area (e.g., a neighborhood or building) before transmitting it to the central server. Data concentrators reduce the communication load on the network and help overcome connectivity challenges by acting as intermediaries between smart meters and the head-end system (HES). They typically support communication protocols like IEC 62056, DLMS/COSEM Head-End System (HES) The HES is responsible for collecting, validating, and managing data received from data concentrators and smart meters. It serves as the central communication hub, facilitating two-way communication between the smart meters and the utility's central servers. The HES supports meter configuration, firmware updates, and real-time data retrieval, ensuring data integrity and security. Meter Data Management System (MDMS) The MDMS is a specialized software platform that stores and processes large volumes of meter data collected by the HES. Key functions of the MDMS include data validation, estimation, and editing, as well as billing preparation, load analysis, and anomaly detection. The MDMS integrates with other utility systems, such as billing, customer relationship management (CRM), and demand response systems, to enable efficient energy management.
It also is essential for smart grid implementations that power line communication (PLC) technologies used within the home over a Home Area Network (HAN), are standardized and compatible. The HAN allows HVAC systems and other household appliances to communicate with the smart meter, and from there to the utility. Currently there are several broadband or narrowband standards in place, or being developed, that are not yet compatible. To address this issue in the United States, the National Institute for Standards and Technology (NIST) established the PAP15 group, which studies and recommends coexistence mechanisms with a focus on the harmonization of PLC Standards for the HAN. The objective of the group is to ensure that all PLC technologies selected for the HAN coexist as a minimum. The two leading broadband PLC technologies selected are the HomePlug AV / IEEE 1901 and ITU-T G.hn technologies. Technical working groups within these organizations are working to develop appropriate coexistence mechanisms. The HomePlug Powerline Alliance has developed a new standard for smart grid HAN communications called the HomePlug Green PHY specification. It is interoperable and coexistent with the widely deployed HomePlug AV technology and with the latest IEEE 1901 global Standard and is based on Broadband OFDM technology. ITU-T commissioned in 2010 a new project called G.hnem, to address the home networking aspects of energy management, built upon existing Low Frequency Narrowband OFDM technologies.
TIA Smart Utility Networks – U.S. Standardization Process. Archived 2014-02-10 at the Wayback Machine Demand Response and Advanced Metering Coalition. Definitions. Tridium Inc. is an American engineering hardware and software company based in Richmond, Virginia, whose products facilitate and integrate the automation of building and other engineering control systems. Since November 2005, the company has operated as an independent business entity of Honeywell International Inc.
SmartAuditFlow is a dynamic and adaptive framework for automated smart contract auditing, leveraging Large Language Models (LLMs) and workflow-driven strategies to deliver reliable, precise, and scalable security analysis. SmartAuditFlow addresses key limitations in smart contract auditing by orchestrating LLMs within a structured, multi-stage workflow, enabling: This framework is inspired by the Plan-and-Solve paper as well as the Baby-AGI project.
This compares to a typical ReAct style agent where you think one step at a time. The advantages of this "plan-and-execute" style agent are: Explicit long term planning (which even really strong LLMs can struggle with) Ability to use smaller/weaker models for the execution step, only using larger/better models for the planning step SmartAuditFlow is an AI-powered framework for automated smart contract security auditing. It combines Large Language Models (LLMs) with dynamic workflow orchestration to detect vulnerabilities through adaptive planning, iterative refinement, and integration with static analyzers.
A smart contract audit is a detailed, line-by-line analysis of blockchain code that identifies security vulnerabilities, logic flaws, and inefficient coding practices before deployment. It combines automated testing with manual expert review to reduce exploit risk and protect user funds. A contract audit is an expert analysis of every line of code in a smart contract, detecting bugs and recommending fixes. That is the core definition used by CertiK , and it remains the practical benchmark for Web3 security teams. Because blockchain code is open source and immutable after deployment, an audit serves as a pre-launch gate that combines code review, testing, and documentation.
Chainlink defines the same process as a detailed analysis intended to preemptively identify security vulnerabilities, remove inefficient coding practices, and find solutions that prevent exploits by malicious actors. The emphasis on preemptive detection matters: once a contract is deployed to Ethereum, BNB Chain, Avalanche, or another network, updating it is expensive and sometimes impossible without complex upgrade patterns.
Audits are not limited to finding bugs. They also examine logic, architecture, and security measures. A strong audit checks whether the code matches the whitepaper, whether access controls are correct, and whether the contract could be manipulated by flash loans or frontrunning. A this type of audit is a formal security assessment of smart contract code and its surrounding architecture. It covers the codebase, technical documentation, and deployment configuration. According to CertiK, the process includes a comprehensive manual review by experienced security experts, with automated AI-powered review as an additional layer.
Scope typically includes the smart contract code itself, but many providers also review bridges, stablecoins, DEX/AMM modules, lending and leverage protocols, and options/perps/derivatives. ChainSecurity publishes public audit reports for the WBTC Solana Bridge, Pendle Boros Markets, and MakerDAO Liquidations 2.0, showing how audits span ecosystems. In traditional applications, developers can push patches and roll back faulty updates. In blockchain systems, a deployed smart contract executes exactly as coded. Hedera frames this as “code is law”: there is no room for error because the contract runs only as the coding dictates. Once deployed, developers cannot fix it. They must create a new version and redeploy, which can be costly and time-consuming.
This immutability is why a this kind of audit must happen before deployment. The auditor’s job is to find the error while the code can still be changed cheaply. A post-deploy fix often requires migration, emergency pauses, or complex proxy logic, and user funds may already be at risk. A standard application code review may focus on maintainability, style, and general bugs. A smart contract is adversarial: it assumes that any exposed function can be called by anonymous users, bots, or well-funded attackers. The auditor thinks about economic incentives, price manipulation, frontrunning, reentrancy, and cross-contract callbacks.
contract audits also produce a public-facing report in many cases. The report is a risk disclosure document that classifies findings by severity and often becomes part of a protocol’s security credentials. That public dimension is unique to Web3 and changes the expectations around thoroughness and accuracy. A this type of audit is not a luxury. It is a security control for protocols that hold billions of dollars in value. According to Chainlink, over $5 billion has been lost to hacks in DeFi to date, with the total reaching $5.13 billion as of February 20, 2023.
These losses are largely irreversible because blockchain transactions cannot be reversed by a central party. Without a pre-deployment audit, a protocol may ship code that passes basic unit tests but contains a logic flaw only visible to an adversarial reviewer. The audit’s purpose is to find those flaws before launch, when remediation is still practical. According to Cyfrin , the total value stolen from DeFi protocols in 2023 decreased significantly to $1.8 billion , a 51.4% drop from the previous year. However, 2024 reversed that trend, with stolen funds rising 21.07% year-over-year to $2.2 billion .
These numbers show that while security practices improved at times, exploit activity remains high and adaptive. Hacken’s Q2 2026 Security and Compliance Report counted 67 incidents and $764 million in losses, with 88% of losses attributed to operational failures rather than isolated code bugs. That finding broadens the definition of audit risk: operational controls, access management, and incident response are now part of the security picture.
Once a smart contract is deployed, no bank, exchange, or protocol team can simply reverse a malicious transaction. If a vulnerability leads to loss of user funds, those funds cannot be retrieved in most cases. This is a core reason why Hedera says bug-free code is not a nicety but a necessity. The audit process helps ensure that the code is sound before it becomes permanent public infrastructure.
Even upgradeable contracts do not remove the need for audits. Proxy patterns and migration logic introduce their own risks, and every upgrade requires a new security review. An audit of the initial implementation is only one part of a continuous security posture. A completed this kind of audit is a trust signal. It tells users that a third party has reviewed the code, classified vulnerabilities, and provided remediation guidance. CertiK notes that projects completing an audit earn a spot on the Skynet Leaderboard, which gives the Web3 community a visible demonstration of security commitment.
For institutional participants and DAO governance voters, an audit report can be a prerequisite for capital allocation. The absence of an audit, or a report with unresolved critical findings, often leads to reduced liquidity and reputational damage. 2. System Architecture & Core Working Principles The standard smart contract process follows a repeatable sequence: collect documentation, run automated tests, conduct manual review, classify errors, and draft an initial report. Chainlink, CertiK, Hedera, and others describe similar steps, with variations in tooling and formality. The numbered sequence below synthesizes the common workflow.
Step 1. Collect Documentation. The project freezes its code and provides auditors with technical documentation, including the codebase, whitepaper, architecture, and deployment details. The documentation gives auditors a high-level guide to intended behavior and exact implementation. Step 2. Automated Testing. Automated tools check the contract for known vulnerabilities, run unit tests on individual functions, and may perform integration and penetration testing. Chainlink notes that automated testing can check every possible state of a smart contract and raise alerts around issues that could undermine functionality or security. Automated tools mostly detect pattern-level bugs, not logic errors.
Step 3. Manual Review. Security experts examine each line of code to identify errors and vulnerabilities. Manual review is more capable of detecting problems with contract logic, architecture, poor coding practices that pass automated tests, gas optimization opportunities, and weak points for common attacks such as frontrunning. Step 4. Classification of Contract Errors. Each finding is assigned a severity level. Chainlink’s schema uses Critical, Major, Medium, Minor, and Informational. CertiK similarly classifies vulnerabilities from Critical to Informational. This shared vocabulary helps teams prioritize remediation.
Step 5. Initial Report. Auditors draft a report summarizing code flaws and feedback on how the project team can fix them. Some providers have experts who help fix issues directly, while others return the report to the client for remediation. After fixes, the auditor may re-review the code and confirm that vulnerabilities are resolved. The final report becomes a record of the audit. In many cases, it is published publicly. Unresolved issues are described alongside their potential effects and the project team’s justification, ensuring that users can evaluate residual risk.
Severity classification is the way contract audit reports communicate risk. A clear severity scale prevents teams from treating a style issue the same way they treat a critical exploit. It also lets investors and users quickly understand the protocol’s security posture. CertiK and Chainlink both use a five-tier severity model. Critical findings impact the safe functioning of a protocol. Major findings include centralization and logical errors that can lead to loss of user funds or protocol control. Medium findings affect performance or reliability. Minor findings are inefficient code that does not put application security at risk. Informational findings relate to style or industry best practices.
Hacken’s portfolio data shows how findings are distributed in real audits. Out of 16,257 vulnerabilities found across 2,138 audits, 483 were Critical, 1,471 were High, 2,799 were Medium, 4,555 were Low, and 6,950 were Observations. That distribution reflects the reality that many findings are lower severity, while a small number carry catastrophic risk. A final audit report is a comprehensive, transparent record of identified vulnerabilities, their severity, and suggested remediation. CertiK describes reports as freely available to the public, with resolved issues marked as resolved and acknowledged but unresolved issues accompanied by a description of potential effects and the project team’s justification.
The report typically includes an executive summary, scope, methodology, tooling used, detailed findings, and a remediation roadmap. Some reports also include gas optimization notes and recommendations for ongoing monitoring. Public audit reports create accountability. Investors and users can review the exact findings and decide whether a protocol’s residual risk is acceptable. CertiK’s Skynet Leaderboard publishes audited projects to demonstrate commitment to security, and ChainSecurity maintains a public audit report archive covering bridges, stablecoins, DEXs, and lending protocols.
Not every client publishes the report. Veridise notes that confidentiality is available upon request, while many clients find value in publishing it. The decision to publish influences how the market perceives security maturity. A this type of audit is strongest when manual review and automated tooling work together. Automated tools scale and cover large codebases quickly, while manual review catches logic flaws and architecture issues. The most credible audit providers are explicit about combining both.
Automated vulnerability scanners detect known patterns such as unchecked return values, reentrancy, and integer overflow. They tend to miss contract-specific logic errors, flawed economic assumptions, and permission misconfigurations. Chainlink emphasizes that human engineers are more capable of detecting problems with contract logic or architecture and poor coding practices that are technically correct and pass automated tests.
Automation is not a replacement for expert judgment. It is a triage layer that helps auditors focus manual effort on the highest-risk code paths. Knowing what auditors look for helps developers write safer code from the start. The most frequently exploited vulnerability classes include reentrancy attacks, where an external contract calls back into the vulnerable function before state is updated; integer overflow and underflow, which Solidity 0.8+ mitigates natively but older contracts still expose; access control misconfigurations, where privileged functions lack proper role checks; and oracle manipulation, where price feeds can be distorted within a single transaction using flash loans.
Frontrunning is another common target. Because mempool transactions are publicly visible before confirmation, a well-timed bot can insert a transaction ahead of a user’s trade to extract value. Auditors specifically probe for these economic attack vectors, not just syntactic bugs. Formal verification is a mathematical process that proves a program satisfies specific properties. In a smart contract audit, formal verification goes beyond testing by certifying smart contract behavior with respect to custom function specifications.
CertiK reports 1,233+ formally verified projects and 2,636+ formally verified contracts, demonstrating that formal methods have scaled beyond academic use. This approach provides mathematical guarantees about functionality, not just the absence of known test failures. CertiK describes formal verification as providing mathematical proofs that Web3 projects are bug-free, though the guarantees are only as strong as the specification written for them.
“While traditional testing approaches merely attempt to detect vulnerabilities, CertiK’s formal verification provides mathematical proofs that Web3 projects are bug-free. This is one of the main reasons that convinced us to go with CertiK for our smart contract security audit.” – Sebastien Borge, COO and Co-founder Veridise illustrates the growing importance of specialized tooling. Its in-house tools include OrCa , a specification-guided fuzzer; Vanguard , a static analysis tool for smart contracts and ZK circuits; and Picus , a zero-knowledge proof auditing tool that finds bugs in arithmetic circuits. These tools target bug classes that manual review may miss.
HackenProof also markets AI-powered smart contract audits as automated tools for detecting security vulnerabilities and ensuring the safety of smart contracts. This AI-assisted layer is becoming common, but providers still pair it with human review to avoid false confidence. Smart contract audit pricing is not standardized. The cost depends on code size, complexity, protocol type, and the provider’s methodology. According to Hedera, smart contract auditors typically charge $5,000 to $15,000 , but might charge more depending on the size and complexity of the contract. Hedera also estimates that creating and deploying a smart contract can cost about $7,000 to $45,000 , with large organizations potentially paying around $100,000 .
Industry sources quote different ranges because audit scope varies widely. A simple ERC-20 token with standard functionality may fall at the lower end, while a complex DeFi protocol with multiple modules, cross-chain bridges, and upgradeable contracts can exceed $100,000. The Hedera estimate of $5,000 to $15,000 is a useful baseline for straightforward engagements, but large enterprises should expect higher fees.
Some providers also offer retainer arrangements, bug bounty integration, and post-audit monitoring. These add-ons change the total price and may be necessary for protocols with continuous development. Several factors influence smart contract audit pricing: the number of contracts, lines of code, complexity of state transitions, use of external oracles, cross-chain interactions, and whether formal verification is requested. A project with custom math or ZK circuits will require specialized tools like Veridise’s Picus, increasing cost.
Timeline also matters. Faster onboarding and expedited reviews command premium pricing. CertiK notes that faster onboarding options depend on project code size, and large teams can handle any job no matter how big or small. When compared with the potential loss from a single exploit, an audit fee is small. Cyfrin reports that DeFi protocols lost $2.2 billion in 2024. A typical audit fee is a fraction of a percent of that total per project. The economic argument for a smart contract audit is straightforward: the cost of prevention is far lower than the cost of a critical vulnerability discovered after launch.
Selecting a smart contract audit provider is a security decision, not just a checkbox. Teams should evaluate track record, methodology, tooling, public reports, and ecosystem coverage. The competitor landscape includes established firms, specialized research teams, and competitive audit platforms. CertiK is one of the largest providers, reporting 6,198+ audited projects and 92,944+ security audit findings. It is recommended by exchanges like Binance, OKEx, and Huobi, and supports Ethereum, BNB Chain, Polygon, and more than a dozen other Layer 1 blockchains. ChainSecurity has worked since 2017 with top-tier DeFi protocols, research institutions, central banks, and large organizations, with published reports for MakerDAO, Curve, Enzyme, and Pendle.
Other well-known names appear in Cyfrin’s top 10 list: Cyfrin, OpenZeppelin, Spearbit, TrailOfBits, Guardian Audits, Sigma Prime, ChainSecurity, Hashlock, Code4rena, and CodeHawks. The list is a useful starting point, but due diligence should go beyond brand recognition. Competitive audit platforms such as Code4rena and CodeHawks crowd-source security review from multiple auditors. These platforms can surface a wider range of findings than a single team, though they may require more coordination and remediation effort. They are often used alongside a traditional audit for defense in depth.
A competitive audit is not a replacement for a formal report. The output, process, and accountability differ. Projects with regulatory or institutional requirements may need a provider that can produce a formal, confidential, or legally defensible report. The evaluation criteria should include whether the provider uses formal verification, in-house tooling, public report templates, and severity classifications. Veridise emphasizes that many clients find value in publishing reports, but confidentiality and ownership terms vary. Some providers surrender full report ownership upon completion, while others retain publication rights.
A strong provider will explain its methodology before the audit begins. Ask what tools will be used, who will manually review the code, how findings will be classified, and whether remediation support is included. The answers reveal whether the engagement is a rigorous review or a shallow scan. “Veridise helped our protocols avoid very critical mistakes when other audit firms signed off and issued reports. As the regular retainer of Ankr, Veridise has done an amazing job.” – Ryan Fang, Co-Founder of Ankr The smart contract audit market is evolving toward deeper automation, mathematical proof, and specialized tooling. As DeFi and institutional Web3 adoption grow, audit standards are becoming more outcome-focused and less reliant on manual checklists alone.
AI-assisted code review is now advertised by providers including HackenProof, whose AI-powered smart contract audits are positioned as automated tools for detecting security vulnerabilities and ensuring safety. CertiK also mentions automated AI-powered review as an additional layer of security. As of 2026, AI currently augments rather than replaces expert manual review, especially for protocol-specific logic and economic attacks.
Formal verification is moving from optional extra to core differentiator. CertiK’s formal verification statistics show meaningful adoption across thousands of projects. Veridise’s Picus targets zero-knowledge proof circuits specifically, which matters because ZK rollups and privacy protocols introduce arithmetic circuit bugs that traditional Solidity scanners miss. 3. Software Implementation, Frameworks & Protocols As zero-knowledge applications grow, specialized audit tooling for ZK circuits, transient storage, and new EVM features will become standard. ChainSecurity has already written about EIP-1153 transient storage and the Cancun hardfork, indicating that auditors must track protocol upgrades to stay current.
Institutions and central banks are entering the space. ChainSecurity’s client base includes central banks and large organizations, and Hedera frames audits as essential for organizations that rely on smart contracts for essential functions. This institutional pressure is likely to push audit standards toward more consistent severity frameworks, public reporting norms, and post-deployment monitoring requirements.
A smart contract audit is a detailed code review that identifies security vulnerabilities, logic flaws, and inefficient coding before blockchain deployment. It typically combines automated testing with manual expert analysis and may include formal verification for mathematical guarantees. Typical smart contract audit fees range from $5,000 to $15,000, according to Hedera. Complex DeFi protocols or enterprise deployments can cost significantly more depending on code size, scope, and whether formal verification is included.
Yes. DeFi hacks caused $2.2 billion in losses in 2024 alone, according to Cyfrin. An audit costs far less than a critical exploit and provides a public trust signal that users and investors actively look for before committing capital. The standard process includes collecting documentation, running automated tests, performing manual review, classifying errors by severity, and drafting an initial report. Formal verification can be added for mathematical guarantees about contract behavior.
Formal verification is a mathematical method that proves a smart contract satisfies specified properties. It goes beyond testing by providing stronger guarantees about contract behavior, though it depends on accurate specifications provided by the development team. Severity levels typically include Critical, Major, Medium, Minor, and Informational. Critical findings can compromise protocol safety and require immediate remediation, while Informational findings relate to style and best practices with no direct security impact.
Ready to build on a foundation that takes security seriously? Apply to the Genesis Cohort at Digital Blockchains and work with a team that treats audits as a starting point, not a finish line. Weekly technical analysis on blockchain infrastructure, protocol design, and Web3 architecture. No hype — just engineering insights.
Founder of Digital Blockchains & Amin Ferdowsi Holding. Building protocol-layer infrastructure for the decentralized future. Venture studio operator, full-stack architect, AI automation engineer. Solid documentation is the cornerstone of any successful smart contract audit. It illuminates the design, functionality, and attack surface of a smart contract system, which lets auditors and external contributors evaluate it efficiently. Accessible documentation saves money, since new developers and auditors reach the point of contributing sooner, and it guides the implementation of future features toward more secure choices.
Every smart contract system solves a specific problem. High-level documentation starts with a problem description covering why the problem matters and how the system addresses it, then introduces the low-level components and their role in the whole. That progression carries the design rationale and the assumptions made during development. Graphics built during the system design process pair naturally with both halves.
With the moving parts described, the interactions and controls between components need documenting. Every meaningful interaction calls for four clarifications: Documentation is unpopular with developers and project managers, because its benefits arrive late and indirectly. High-level documentation is written by hand, while low-level technical documentation is annotated directly in the codebase. These documentation comments can be specified on a contract- and a function level. When written in a standard format like NatSpec , tools like solidity-docgen can parse the code base and automatically generate HTML and PDF documentation. The technical documentation can be generated during the CI and testing workflow and automatically uploaded to a free hosting service such as Github Pages .
The following code snippet taken from the Solidity docs (v0.8.20) is an example of NatSpec notation: To make the automated documentation accessible for auditors and new developers, the smart contract project's README file should elaborate on installing the system's dependencies and generating the documentation. Alternatively, when documentation is automatically generated and hosted, the respective pages for the detailed technical documentation should be referenced wherever possible to help contributors contextualize the system's components more quickly.
The solidity-docgen project's documentation and the tool's help page carry further information, and both change frequently while the tool is under active development. The official OpenZeppelin contracts and documentation can be consulted for detailed syntax since they also adhere to the NatSpec standard and leverage specific features provided by solidity-docgen . When smart contract infrastructure is designed for integration with other systems, a well-documented system provides clear guidance to developers, aiding in a smooth and efficient integration process.
For that purpose, developers need to know the locations of the most recent smart contract deployment. An excellent example of good practice in this area can be seen in the documentation provided by the Compound docs . The Compound developers list their deployments on each chain in their documentation. This practice significantly reduces the risk of developers mistyping an address or accidentally initializing their system to a deprecated contract version. Moreover, with new addresses published on partial updates, this aids in maintaining the consistency and reliability of the system.
An excellent addition for even quicker analysis is that the docs provide links adjacent to each address, directing users to the respective blockchain explorer. Reading, validating, and interacting with the contract then takes minimal effort, which cuts the time developers spend on contract analysis. The deployment documentation outlines every step leading toward production deployment, ensuring the operations' sequence and outcomes are well understood. Providing and referencing helper scripts within the documentation enhances usability, allowing developers to automate or semi-automate parts of the deployment process. Furthermore, the documentation should comprehensively list system environment variables and smart contract constructor parameters, elucidating their roles in the deployment process and overall system functioning.
State every external contract the system interacts with explicitly. System behavior varies with the blockchain environment, and a contract it integrates with on one chain does not necessarily behave the same on another. An explicit warning that deployment on a different blockchain yields different results gives developers the context they need to plan a multi-chain deployment.
Establishing clear contribution guidelines is crucial for fostering an inclusive and secure development environment. The guidelines should outline the process for submitting changes and code review and acceptance standards. This clarity enhances community collaboration, reducing the potential for misunderstanding or disputes. Running a bug bounty program or having a systematic vulnerability reporting procedure encourages responsible disclosure of any discovered security issues. More details are in the dedicated bug bounty program section .
The documentation should include any previously conducted audits and their corresponding published reports. These provide valuable insights into the system's security posture and demonstrate transparency and dedication to quality, boosting user confidence and trust in the system. How to audit a smart contract is no longer a niche skill. It is a specialized security discipline that blends software engineering, cryptography, and adversarial thinking. The stakes are high because smart contracts often hold significant value, are transparent to attackers, and can be difficult or costly to change once deployed. Industry reporting from Immunefi and Chainalysis has consistently documented billions of dollars in annual losses, with a large share attributed to smart contract vulnerabilities and protocol logic flaws. That reality has made smart contract audits a baseline expectation for serious DeFi launches, NFT marketplaces, and enterprise blockchain deployments.
This guide presents a practical, research-driven workflow, the core tools used by professional auditors, and the best practices that help teams reduce risk before and after an audit. As blockchain adoption continues to grow, organizations increasingly need professionals who can identify vulnerabilities before they become costly exploits. A Certified Smart Contract Auditor credential helps build practical expertise in security analysis, vulnerability assessment, testing methodologies, and blockchain risk management, providing a strong foundation for conducting effective smart contract reviews.
Smart contract audits differ from typical application security reviews in several important ways: Immutability and upgrade risk : vulnerabilities can be permanent or require complex migrations to fix. Direct financial impact : many issues convert immediately into fund loss, governance takeover, or protocol insolvency. Attacker visibility : contracts are public, allowing attackers to simulate every execution path.
Composability : risks propagate across interconnected protocols, bridges, oracles, and liquidity venues. Smart contract security also benefits from a broader understanding of software engineering, cloud infrastructure, cybersecurity, and modern development practices. A Tech Certification helps professionals strengthen these complementary technical skills, making it easier to evaluate blockchain applications within larger enterprise technology environments.
Modern audits therefore combine threat modeling, automated analysis, deep manual review, and operational security validation rather than relying on code scanning alone. Methodologies vary by firm, but most professional audits follow a consistent sequence. Use the workflow below as a repeatable blueprint for internal reviews or third-party engagements.
The fastest, highest-signal audits happen when the project team prepares the codebase and provides context upfront. Code cleanliness : remove dead code, maintain a clear folder structure, add comments for non-obvious assumptions, and enforce consistent style with tools like solhint for Solidity. Specifications and invariants : document functional intent, security assumptions, and invariants such as supply conservation, access boundaries, and parameter constraints.
Robust tests : ship unit and integration tests that cover edge cases, revert paths, and critical invariants. Add fuzz or invariant tests for core components. 4. Practical Deployment, Analysis & Case Studies Ops readiness : prepare deployment scripts, upgrade mechanisms, admin role documentation, and incident response procedures, including pause or circuit breaker logic where applicable.
Auditors begin by defining what is being audited, under what assumptions, and what a realistic threat model looks like. Business and protocol understanding : identify which assets are at risk, map the user flows, and define what failure looks like in practice. Threat model : assess likely adversaries, capital requirements, MEV capabilities, governance influence, and attack motivations.
Dependencies : catalog oracles, DEX integrations, bridges, external protocols, and off-chain components. Known issue research : reviewers consult public vulnerability databases and prior audit reports to identify recurring pitfalls in similar modules. Deliverables at this stage typically include a written scope, list of contracts and commit hashes, environment versions, and an agreed communication process.
Automation improves coverage and catches common issues, but it does not replace human reasoning. A standard tool-assisted phase includes static analysis, fuzzing, and dependency checks. Static tools scan source code or bytecode without executing the contract. Common options include: Slither for Solidity vulnerability patterns, dangerous code smells, and design anti-patterns.
Mythril or MythX for symbolic execution and vulnerability discovery covering reentrancy and authorization issues. For non-EVM ecosystems, the equivalents are typically language toolchains combined with specialized rulesets, such as Clippy and cargo-audit for Rust (common in Solana and CosmWasm), alongside chain-specific frameworks like Anchor for Solana.
Fuzzers generate large volumes of inputs to expose unexpected states and invariant violations. Widely used tools include: Effective fuzzing depends on meaningful properties such as conservation of balances, monotonic parameter bounds, and correct access control under adversarial input sequences. Not all security issues involve code bugs. Some stem from economics or runtime limits: Gas profiling to detect gas griefing and denial-of-service risks from expensive loops or unbounded operations.
Simulations using tools like Tenderly to model abnormal flows, failure scenarios, and adversarial transaction ordering. MEV and oracle stress testing to examine sandwich attacks, price manipulation, and flash-loan-driven conditions. This is the core of how to audit a smart contract properly. Automated tools flag patterns, but human reviewers validate protocol intent, cross-contract interactions, and economic edge cases.
State transitions : check lifecycle steps such as initialization, pausing, liquidation, settlement, and upgrade flows. Cross-function interactions : verify that calling sequences cannot bypass intended checks. Invariant reasoning : validate properties such as supply conservation and correct accounting across all functions. Many firms require at least two independent reviewers to reduce blind spots, then reconcile findings and validate hypotheses through targeted tests.
Flash loan and MEV surfaces , including governance manipulation and atomic price moves. Math and precision issues , rounding errors, overflow or underflow in unchecked contexts, and fee distribution mistakes. When protocols use signatures, commitments, randomness, or advanced cryptographic flows, auditors validate: Cryptographic mistakes can be subtle and catastrophic, particularly in bridges, authentication systems, and meta-transaction implementations.
Even a thoroughly reviewed contract can be compromised through operational failures. A holistic audit examines: Deployment integrity : reproducible builds, verifiable bytecode, and confirmation that deployed contracts match the audited commit. Key management : multisig usage, key storage practices, rotation and revocation plans, and monitoring of admin actions.
Upgrade and migration : governance processes, timelocks, upgrade authorization, and rollback strategies. Emergency response : tested pause mechanisms, incident runbooks, and clear team responsibilities. Supply chain security : pinned dependencies, regular dependency scanning via npm audit or cargo-audit, and controlled CI/CD pipelines.
Professional audit reports categorize issues by severity and provide exploit narratives alongside recommended fixes. Informational : improvements, style guidance, monitoring recommendations, and gas suggestions. After the team patches issues, auditors perform a focused retest and issue a final status update showing what was fixed, what changed in scope, and what remains as accepted risk.
Shift left : conduct design-time threat modeling and security reviews before implementation begins. Use battle-tested libraries : prefer well-reviewed components like OpenZeppelin for standards and access control. Secure coding standards : apply checks-effects-interactions, minimize external calls, and guard them carefully. Least privilege : enforce role separation, timelocks, and multisigs for sensitive operations.
Continuous security : re-audit after significant changes and periodically as dependencies and integrations evolve. 5. Performance Evaluation & Extended Technical Observations Stay current : exploit patterns evolve quickly; public post-mortems and vulnerability databases should continuously feed checklists.
Scenario thinking : attackers chain small issues into large exploits, especially in composable systems. Repeatable process plus creativity : structured methodology reduces misses, while custom scripts and targeted fuzzing handle novel logic. Clear communication : explain impact, recommended fixes, and prevention strategies to raise the team's long-term security maturity.
Responsible disclosure : coordinate timelines so critical issues are not made public before mitigations are in place. More automation : static analysis and symbolic tooling continue to improve, including ML-assisted triage, though human judgment remains essential for economic and protocol reasoning. Formal verification : increasingly applied to high-risk components such as bridges and stablecoin mechanics, though it remains specialized and resource-intensive.
Security standards : the ecosystem is converging on more consistent verification standards, similar in spirit to established web security baselines. Runtime monitoring : on-chain alerting and automated protective responses are becoming part of ongoing security operations, not just pre-launch checks.
Cross-chain focus : bridges and messaging layers remain high-impact targets and require specialized review approaches. Knowing how to audit a smart contract means combining structured methodology with adversarial creativity. A strong audit workflow starts with clear specifications and tests, moves through automated analysis and fuzzing, relies heavily on manual logic review, and extends into deployment, key management, and lifecycle controls. Reports and retests then close the loop so fixes are validated rather than merely suggested.
Audits reduce risk but do not eliminate it. Teams that pair audits with secure design practices, recurring reviews, dependency hygiene, and runtime monitoring consistently build more resilient protocols. For professionals seeking to develop deeper expertise in this area, structured learning in smart contract development and blockchain security provides a strong foundation for advancing in this field.
Technical expertise is only one part of successful blockchain adoption. A Marketing & Business Certification helps professionals develop stronger strategic planning and communication skills, enabling them to explain security risks clearly, support informed business decisions, and align blockchain security initiatives with broader organizational goals. A smart contract audit is a detailed security review of blockchain smart contract code to identify vulnerabilities, logic errors, inefficiencies, and compliance issues before deployment. The goal is to reduce security risks and improve contract reliability.
A smart contract audit helps prevent exploits, financial losses, protocol failures, and reputational damage. Since blockchain transactions are immutable, fixing vulnerabilities after deployment can be difficult and expensive. A smart contract should be audited before mainnet deployment, after major code updates, before protocol upgrades, and whenever significant changes are introduced to the application's logic.
Smart contract audits are conducted by blockchain security firms, independent security researchers, and experienced blockchain developers with expertise in Solidity, Rust, or other smart contract programming languages. The first step is understanding the protocol's architecture, business logic, contract interactions, and intended functionality before reviewing the source code.
Manual code review helps auditors identify complex logic flaws, insecure design patterns, and business logic issues that automated security tools may not detect. Automated security tools quickly scan contracts for known vulnerabilities, coding issues, and insecure patterns, making the audit process faster and more comprehensive.
Static analysis examines smart contract source code without executing it to identify vulnerabilities, coding errors, and security weaknesses. Dynamic testing executes the smart contract in simulated environments to evaluate its behavior under different conditions and identify runtime vulnerabilities.
Fuzz testing automatically generates random and unexpected inputs to discover hidden vulnerabilities, crashes, and edge cases that standard testing may overlook. Formal verification uses mathematical methods to prove that a smart contract behaves according to its intended specifications under every possible scenario.
Auditors review ownership functions, administrator permissions, role based access controls, and authorization logic to ensure only approved users can execute sensitive functions. Gas optimization focuses on reducing transaction costs by improving code efficiency while maintaining security and functionality.
Business logic verification ensures the contract behaves as intended and prevents users from exploiting logical flaws that could bypass protocol rules. Dependency analysis evaluates third party libraries, imported contracts, and external integrations to identify vulnerabilities that may affect the overall application.
Developers should fix all identified issues, perform regression testing, request a follow up review if necessary, and verify that vulnerabilities have been successfully resolved before deployment. No. An audit significantly reduces risk but cannot guarantee that a smart contract is completely free from vulnerabilities or future attack methods.
The duration depends on project complexity. Small projects may take several days, while large decentralized finance or enterprise blockchain applications can require several weeks. Audit costs vary based on contract size, code complexity, blockchain platform, audit scope, and the experience of the auditing firm.
Professional smart contract audits improve security, strengthen user trust, reduce financial risks, support regulatory compliance, enhance protocol reliability, and increase confidence among investors, developers, and the broader blockchain community. A practical smart contract security guide covering principles, tools, lifecycle best practices, real incidents, audits, testing, and monitoring.
A practical guide to the best smart contract development tools for Solidity, testing, fuzzing, auditing, formal verification, and monitoring. Smart contract best practices for secure design, testing, audits, AI-assisted review, monitoring, and Web3 team security workflows.
Explore the leading decentralized finance platforms and what makes each one unique in the evolving DeFi landscape. Understand how blockchain technology is being applied to protect the integrity and security of AI training data. Discover Claude AI tools for productivity to streamline tasks, manage workflows, and improve efficiency. A smart contract audit is a comprehensive security review of a smart contract’s code, designed to catch vulnerabilities, logical errors, and inefficiencies before deployment. Founders, developers, and project leaders across Web3, DeFi, and AI-driven crypto rely on this process to protect digital assets and earn user trust. This guide breaks down exactly what a smart contract audit involves, how much it costs, and how to choose the right auditor for your project.
A smart contract audit is a systematic review of blockchain-based smart contract code to identify security vulnerabilities, logic issues, and implementation risks before the contract is deployed or used in production. The audit examines how the contract handles transactions, permissions, assets, and predefined business rules. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Smart%20contract • https://en.wikipedia.org/wiki/Smart%20meter • https://en.wikipedia.org/wiki/Tridium • https://github.com/JimmyLin-afk/SmartAuditFlow • https://digitalblockchains.com/smart-contract-audit-guide/ • https://scsfg.io/developers/documentation/ • https://www.blockchain-council.org/smart-contracts/how-to-audit-a-smart-contract-tools-best-practices-workflow/ • https://blocsys.com/smart-contract-auditing/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Smart Contract Automated Audit Framework Using Python.
[*] Metasploit Scan Running on Target Subnet for Smart Contract Automated Audit Framework Using Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |