Complete Technical Paper Content — Smart Contract Vulnerability Detection Tool Using Slither
Overview & System Context
Smart Contract Vulnerability Detection Tool Using Slither: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5454 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Slither is a Solidity & Vyper static analysis framework written in Python3. It runs a suite of vulnerability detectors, prints visual information about contract details, and provides an API to easily write custom analyses. Slither enables developers to find vulnerabilities, enhance their code comprehension, and quickly prototype custom analyses.
This is the preferred option if your project has dependencies as Slither relies on the underlying compilation framework to compile source code. Note Slither requires Python 3.10+. If you're not going to use one of the supported compilation frameworks , you need solc , the Solidity compiler; we recommend using solc-select to conveniently switch between solc versions.
The -e flag installs in editable mode, meaning changes to the source code are immediately reflected without reinstalling. Figure 1: How DeFi Insurance Protocols Use Smart Contract Audits to Reduce ... Use the eth-security-toolbox docker image. It includes all of our security tools and every major version of Solidity in a single image. /home/share will be mounted to /share in the container.
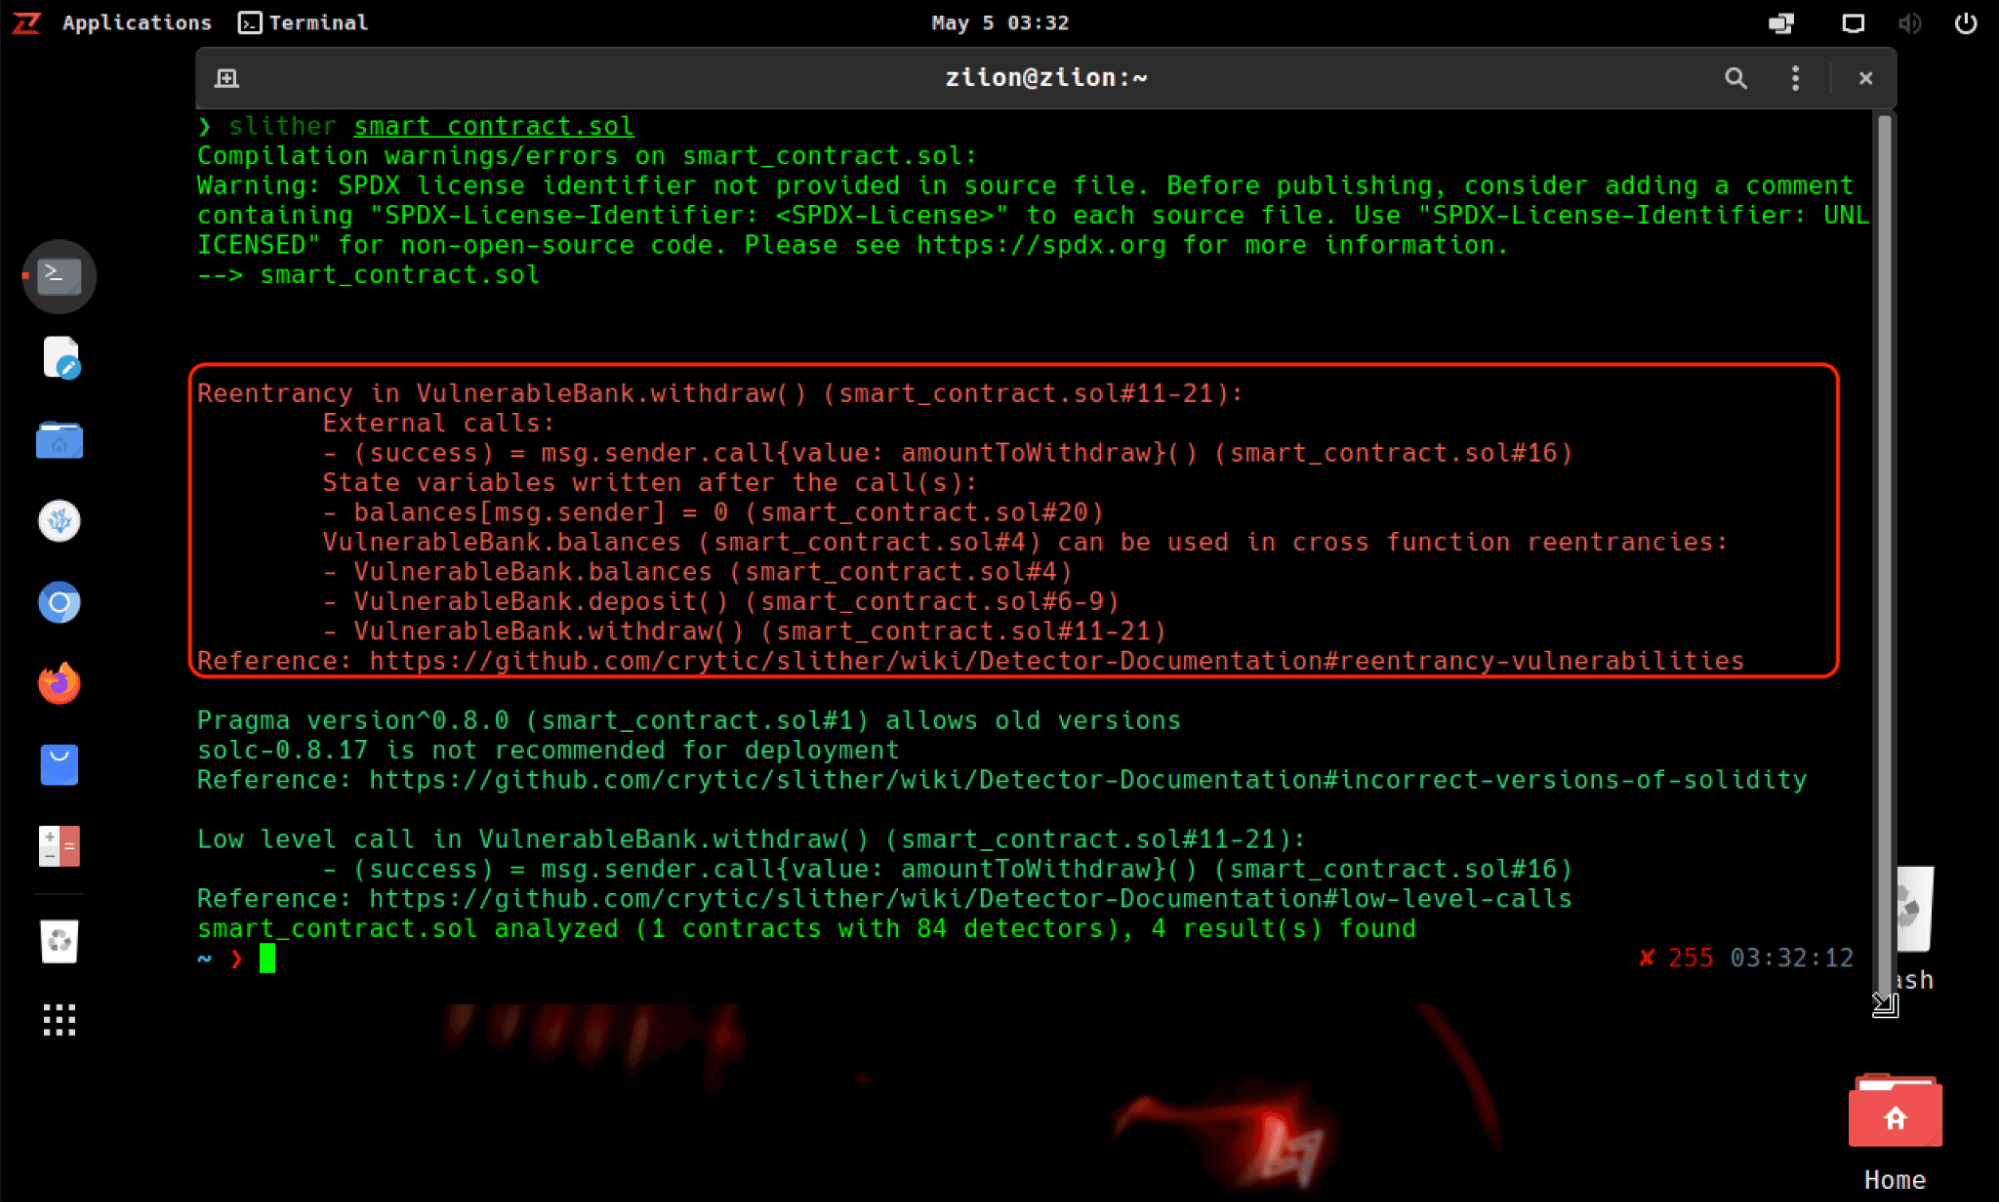
Feel free to stop by our Slack channel (#ethereum) for help using or extending Slither. The Printer documentation describes the information Slither is capable of visualizing for each contract. The API documentation describes the methods and objects available for custom analyses. Figure 2: ZIION - How to Detect Reentrancy Attacks Using ZIION Tools Slither is licensed and distributed under the AGPLv3 license. Contact us if you're looking for an exception to the terms.
If you are using Slither on an academic work, consider applying to the Crytic $10k Research Prize . Slither is a Solidity & Vyper static analysis framework written in Python3. It runs a suite of vulnerability detectors, prints visual information about contract details, and provides an API to easily write custom analyses. Slither enables developers to find vulnerabilities, enhance their code comprehension, and quickly prototype custom analyses.
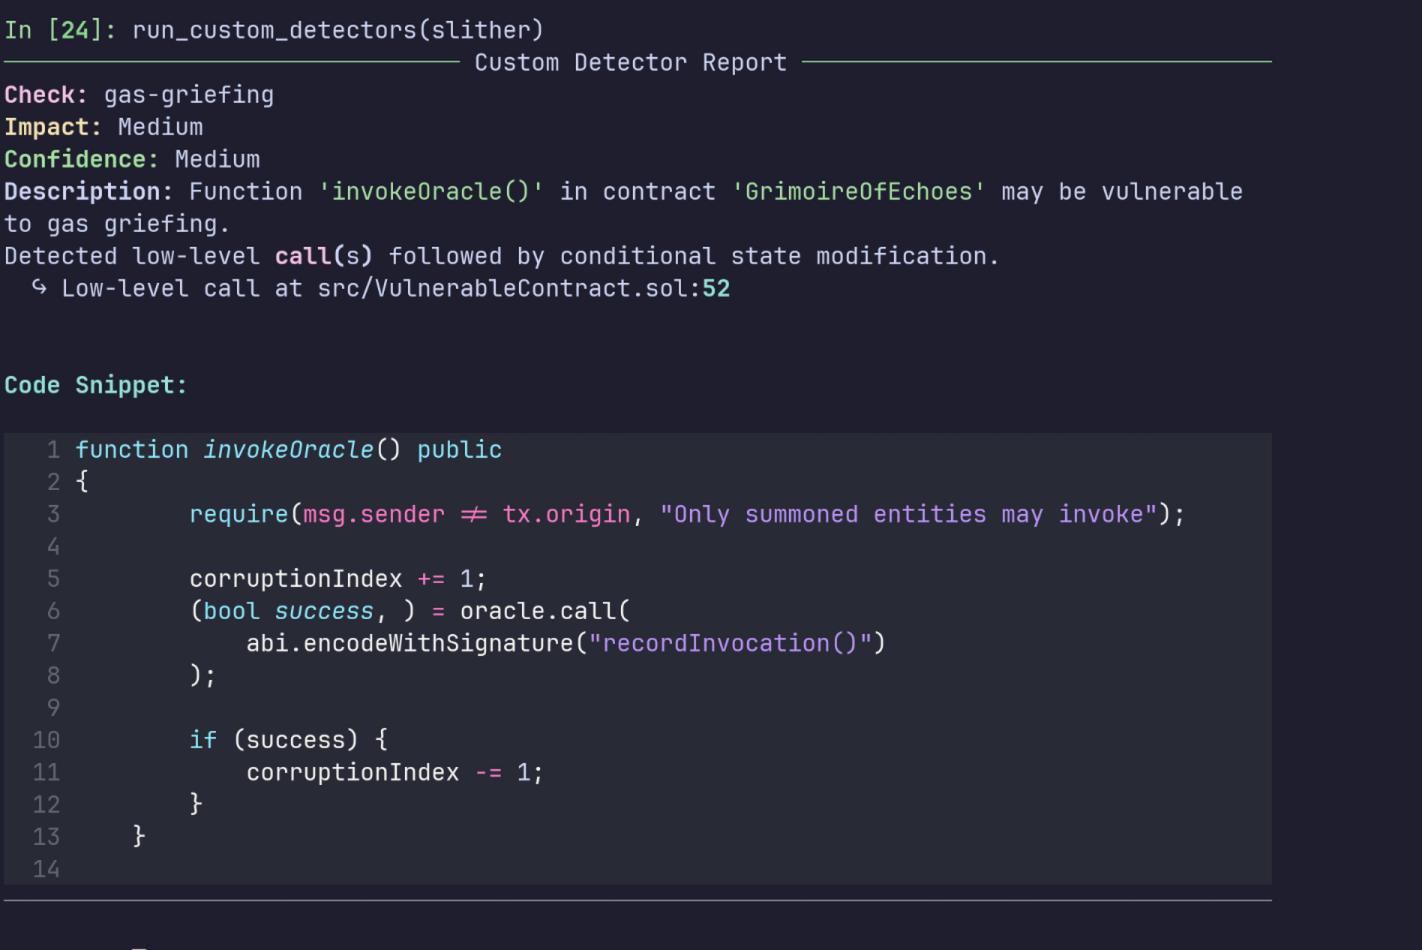
This is the preferred option if your project has dependencies as Slither relies on the underlying compilation framework to compile source code. Figure 3: Beyond the CLI: Hacking Smart Contracts with the Slither API Note Slither requires Python 3.10+. If you're not going to use one of the supported compilation frameworks , you need solc , the Solidity compiler; we recommend using solc-select to conveniently switch between solc versions.
The -e flag installs in editable mode, meaning changes to the source code are immediately reflected without reinstalling. Use the eth-security-toolbox docker image. It includes all of our security tools and every major version of Solidity in a single image. /home/share will be mounted to /share in the container. Feel free to stop by our Slack channel (#ethereum) for help using or extending Slither.
The Printer documentation describes the information Slither is capable of visualizing for each contract. The API documentation describes the methods and objects available for custom analyses. Slither is licensed and distributed under the AGPLv3 license. Contact us if you're looking for an exception to the terms. If you are using Slither on an academic work, consider applying to the Crytic $10k Research Prize .
Slither is a Solidity & Vyper static analysis framework written in Python3. It runs a suite of vulnerability detectors, prints visual information about contract details, and provides an API to easily write custom analyses. Slither enables developers to find vulnerabilities, enhance their code comprehension, and quickly prototype custom analyses. Slither is a Solidity & Vyper static analysis framework written in Python3. It runs a suite of vulnerability detectors, prints visual information about contract details, and provides an API to easily write custom analyses. Slither enables developers to find vulnerabilities, enhance their code comprehension, and quickly prototype custom analyses.
This is the preferred option if your project has dependencies as Slither relies on the underlying compilation framework to compile source code. Note Slither requires Python 3.10+. If you're not going to use one of the supported compilation frameworks , you need solc , the Solidity compiler; we recommend using solc-select to conveniently switch between solc versions.
The -e flag installs in editable mode, meaning changes to the source code are immediately reflected without reinstalling. Use the eth-security-toolbox docker image. It includes all of our security tools and every major version of Solidity in a single image. /home/share will be mounted to /share in the container. Feel free to stop by our Slack channel (#ethereum) for help using or extending Slither.
2. System Architecture & Core Working Principles The Printer documentation describes the information Slither is capable of visualizing for each contract. The API documentation describes the methods and objects available for custom analyses. Slither is licensed and distributed under the AGPLv3 license. Contact us if you're looking for an exception to the terms.
If you are using Slither on an academic work, consider applying to the Crytic $10k Research Prize . For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation . Provenance describes where a file came from. On PyPI, provenance is shared via attestations , which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI verified that this artifact, at this checksum, originated from the publisher listed below. Provenance describes where a file came from. On PyPI, provenance is shared via attestations , which provide a verifiable record of the build or publishing details. View details, limitations and caveats. PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Slither is a Solidity static analysis framework written in Python 3. It runs a suite of vulnerability detectors, prints visual information about contract details, and provides an API to easily write custom analyses. Slither enables developers to find vulnerabilities, enhance their code comprehension, and quickly prototype custom analyses. For GitHub action integration, see slither-action . For additional configuration, see the usage documentation.
We recommend using a Python virtual environment, as detailed in the Developer Installation Instructions , if you prefer to install Slither via git. Use the eth-security-toolbox docker image. It includes all of our security tools and every major version of Solidity in a single image. /home/share will be mounted to /share in the container.
Feel free to stop by our Slack channel (#ethereum) for help using or extending Slither. The Printer documentation describes the information Slither is capable of visualizing for each contract. The API documentation describes the methods and objects available for custom analyses. Slither is licensed and distributed under the AGPLv3 license. Contact us if you're looking for an exception to the terms.
If you are using Slither on an academic work, consider applying to the Crytic $10k Research Prize . Slither is a Solidity static analysis framework based on Python 3. It is one of the most popular tools for smart contracts auditing. Slither has a wide range of vulnerability detectors, printers for visualization of the contract details, and API for custom analyses. It supports Solidity 0.4+ contracts and the audit time is fewer than 1 second per contract.
You should also install the solc-select. It is used for quick installation and switching between Solidity compiler versions. After the solc and solc-select are installed with no errors, we can proceed to the Slither installation. It can be done in three ways: We can check the installation by running slither - -version in your terminal. If the tool is installed properly, you’ll see the latest version – 0.9.2.
After you defined a contract that you want to check, the easiest way is just to run slither [target]. The target can be specified in several ways: Let’s explore a smart contract that’s vulnerable to re-entrancy attacks. The tutorial contracts can be found in this GitHub repo. The easiest way to scan the local copy of a smart contract is to run slither with a contract name. Within seconds you will receive the results: The colorized output highlights the most valuable audit findings. Slither also provides a detailed description of the vulnerability: Technically, you can even exclude medium and high-impact issues. But who’d be really interested in it? 3. Software Implementation, Frameworks & Protocols Detectors are used when you search for a specific type of vulnerability. There are 83 vulnerability detectors. You can find a full list of the detectors in this GitHub repo or by typing slither -h. To use a detector of your choice, run slither –detect [detector_name].
Instead of automatic analysis, printers can help you quickly extract crucial contract information. This may be helpful in manual analysis, audit reports, etc. You can check the full list of the available printers by running slither –list-printers. Running slither SecureContract.sol –print contract-summary, function-summary, modifiers will give us information about each function of the contract, its visibility, modifiers, internal and external calls.
Also, there’s a printer to build graphs to visualize the functions interactions inside the contract. Just run slither SecureContract.sol –print call-graph and the tool will generate a dot file that can be opened with any online dot viewer. Here’s an example of the mentioned graphs: That’s it! Now we can run some basic checks of the smart contract, scan for the most popular vulnerabilities and extract important information for manual audits. You can try your new skills on our public smart contract programs to find valid bugs with a high bounty for them. But keep in mind that reports without a detailed Proof of Concept are out of scope, so do not forget to attach the PoC to your report.
Welcome to the Slither-Detector-101 tutorial series. This repository is designed to teach you how to write custom static analysis detectors for Ethereum Smart Contracts using the Slither framework. Before diving into the levels, it is essential to understand the hierarchy Slither uses to represent a contract. Your detectors will navigate this tree: This outline moves from basic metadata filtering to complex data-flow and dependency analysis.
A 10-level hands-on guide to building custom Slither detectors for smart contract auditing. From basic metadata filtering to advanced data-flow and taint analysis. You have just deployed a Solidity contract that passed all your unit tests. Two weeks later, $3.4 million is drained through a reentrancy attack your test suite never even considered. This is not a hypothetical. Smart contract exploits have resulted in over $15 billion in cumulative losses since 2020, with $2.8 billion stolen from cross-chain bridges alone in 2024. The gap between “my tests pass” and “this contract is secure” is enormous, and traditional testing approaches will not bridge it. What will is a three-layer automated security pipeline: static analysis to catch known vulnerability patterns, fuzzing to explore untested state spaces, and invariant testing to verify your core business logic under adversarial conditions.
I wrote this for engineers building or evaluating DeFi protocols, settlement systems, or tokenized asset platforms. You know Solidity well enough to write contracts and run tests, but you have not yet formalized your security toolchain. Maybe you are coming from traditional capital markets infrastructure where you had decades of battle-tested tooling and now find yourself in a world where a single unchecked external call can empty a protocol. This guide is also for engineering leads evaluating whether these tools belong in their CI pipeline, which they absolutely do.
I am assuming you have a Solidity project running and a basic test harness. Everything else I will walk through step by step. How to integrate Slither directly into your development workflow so it catches vulnerabilities before you even open a pull request. How to write Echidna properties that systematically torture-test your contract’s assumptions. How Foundry’s forge fuzz and invariant testing gives you Solidity-native testing without the JavaScript dependency. And most importantly, how to stack these three tools so they complement rather than duplicate each other.
The security tooling landscape for Solidity splits into three approaches that map directly to how bugs actually manifest in production. Slither, developed by Trail of Bits and written in Python, converts your Solidity source code into an intermediate representation called SlithIR and runs 30+ built-in vulnerability detectors against it. Version 0.11.0, released in February 2025, added seven new detectors including ones for deprecated Pyth oracle functions, unchecked Chronicle price feeds, Chainlink feed registry issues, and Optimism deprecation patterns. Slither is static analysis — it finds what is structurally wrong with your code without ever executing it. Think of it as a compiler warning system on steroids.
Echidna, also from Trail of Bits and written in Haskell, is a grammar-based fuzzer that uses your contract’s ABI to generate randomized transaction sequences that attempt to falsify invariants you define. Version 2.1.0 introduced on-chain contract retrieval and multicore fuzzing. Echidna does not just find obvious crashes; it minimizes failing transaction sequences down to the shortest reproducing input through a process called shrinking, so you are not debugging a hundred-transaction trace when the real bug triggers on step four.
Foundry, developed by Paradigm and written in Rust, hit its 1.0 milestone in February 2025 after seven thousand commits. The forge component handles compilation, testing, and deployment entirely in Solidity — no JavaScript, no Hardhat, no waffle. It supports native fuzz testing, invariant testing, fork testing, and EIP-7702 account abstraction. The built-in gas reporter alone makes it worth the install.
If you prefer a single Docker image that includes all three plus additional analysis tools, Trail of Bits maintains the eth-security-toolbox image at trailofbits/eth-security-toolbox . I use this in CI because it pins known compatible versions and avoids pip version conflicts. Slither runs on compiled Solidity output. You point it at your contract and it prints findings grouped by severity.
Out of the box, Slither detects reentrancy, unused state variables, uninitialized storage pointers, shadowed inheritance, locked ether, and a dozen other common vulnerability classes. Each detector includes a confidence score and a reference to the vulnerable code path. The action fails the PR if Slither detects vulnerabilities above a configurable severity threshold. This catches issues like the Ronin bridge vulnerability pattern that Slither’s check-upgradeability module was specifically updated to detect in version 0.10.3.
Static analysis finds what is structurally wrong. Fuzzing finds what is behaviorally wrong. Echidna generates random transaction sequences against your contract and checks whether user-defined predicates hold. An Echidna invariant for this contract checks that total ether in the contract always equals the sum of all user balances: Echidna will rapidly find that the withdraw() function lets an attacker drain the contract because the balance is zeroed after the external call rather than before. It will output the minimal transaction sequence that triggers the failure — typically three to four transactions instead of the dozens a human tester would try.
The critical insight with Echidna is that your invariants are only as good as your understanding of the protocol. I have found my most valuable invariants by writing down exactly what I want to be true about the system state and then encoding those statements as echidna_test functions. If you cannot articulate an invariant for a function, you probably do not fully understand what that function is supposed to guarantee.
Foundry’s invariant testing overlaps with Echidna but operates inside the forge test runner, making it more practical for day-to-day development. You write invariants directly in Solidity as test functions prefixed with invariant_ : 4. Practical Deployment, Analysis & Case Studies The --invariant-depth flag controls how many calls forge makes per test run before checking your invariant. I start at depth 20 during development and push to 100 before deployment. Foundry also supports targeted fuzzing where you specify the range and distribution of input values: Foundry’s fork testing is invaluable for protocols that integrate with existing deployments. You can fork mainnet state and run invariant tests against real liquidity pools, oracle feeds, and token balances: A security toolchain that you do not trust is useless. Here is how I validate that these tools are actually catching real bugs.
Run Slither against a known-weak contract from the Damn Vulnerable DeFi suite and confirm it flags the intended vulnerabilities. Run Echidna against the same contract and verify it generates a failing transaction sequence. Then introduce a deliberate vulnerability into your own production contract — a reentrancy or a missing access control — and confirm each tool catches it at its layer. When all three produce findings and the findings differ in kind rather than redundancy, you have a layered defense.
I also track metrics: how many Slither findings per PR, how many Echidna sequences per invariant, and whether forge invariant tests find anything during the fuzz run that unit tests miss. Over three months on one protocol I worked with, this pipeline caught eight vulnerabilities that survived manual code review. I block merges on Slither high-severity findings and Echidna invariant failures. Forge invariant failures are reviewed case by case — some indicate real vulnerabilities, others indicate test setup issues. Over time, your invariants stabilize and the noise drops to zero.
Related: Read more about smart contract security — Smart Contract Security: Lessons from DeFi’s $15 Billion Exploits For a deeper look at cross-chain bridge vulnerabilities and how these tools apply to multi-chain architectures, see our earlier article: Cross-Chain Bridge Security: Preventing Multi-Billion Dollar Exploits . If you are building settlement or trading infrastructure on blockchain rails and need expert review of your architecture, we can help. See our Trading & Market Systems Engineering services page.
Disclaimer: The code snippets and testing commands in this article are for demonstration purposes only. Always perform thorough security audits before deploying smart contracts to production. Your smart contract just drained someone's wallet faster than a teenager with a credit card at the mall. Sound familiar? Welcome to the wild world of smart contract vulnerabilities, where one missing line of code can cost millions.
Slither smart contract analysis saves developers from these expensive nightmares. This static analysis tool catches security vulnerabilities before they reach production, protecting both your reputation and your users' funds. This guide shows you exactly how to use Slither for comprehensive security testing. You'll learn installation, configuration, vulnerability detection, and advanced analysis techniques that professional auditors use daily.
Slither is a static analysis framework for Solidity smart contracts. Created by Trail of Bits, it examines your code without executing it, identifying potential security vulnerabilities and code quality issues. Smart contracts handle billions of dollars in cryptocurrency. Unlike traditional software, you cannot easily patch deployed contracts. Vulnerability detection before deployment prevents: This configuration excludes naming convention warnings while maintaining all security-focused detectors.
Slither smart contract analysis transforms security testing from reactive damage control to proactive vulnerability prevention. This powerful static analysis tool catches critical security issues before they reach production, protecting both developers and users. Start securing your smart contracts today. Install Slither, run your first security scan, and join thousands of developers who trust static analysis for blockchain security.
Ready to level up your smart contract security? Check out our comprehensive smart contract audit checklist and learn about advanced Solidity security patterns. This blog is a compilation of security ideas from Erik Elbieh. For questions or comments about this blog, please contact Erik . If you’ve spent any amount of time researching solidity security or doing security reviews on smart contract code, you’ve heard of or used the tool Slither from Trail of Bits. Most Slither tutorials I’ve seen don’t provide step-by-step instructions for using the tool from a security auditor’s perspective. Most tutorials only cover the basics of using Slither. But this tutorial attempts to provide a more in-depth view of how Slither fits into my security testing workflow.
Slither is a static analysis tool that often requires no setup on the security tester’s part. If the code compiles with hardhat or several other frameworks, Slither can be used. The lack of any setup process is a key part of why Slither has become so widely used. Fuzzing tools are great, but setup effort is required, so static analysis tools like Slither keep life simple. Unlike other solidity static analysis tools, Slither is regularly updated and maintained, which has played a large part in why it has superceded most (all?) other solidity static analysis tools at the time of writing.
The first step to using Slither is to install Slither. There are several installation options , and using a Python virtual environment is a good practice, but the lazy way of installing with pip is to use pip3 install slither-analyzer . Next, make sure the solidity version you have installed is the same one required by the contracts. Compare the solc version you have installed to the pragma version in the .sol contract files you want to test. If you don’t have a project that you want to analyze of your own, you can follow along using a well-known public project .
If the solc version doesn’t match the version number of the contracts, you can get the correct solc version either with the solc-select tool , by keeping separate Docker images for different solidity versions like Scott Bigelow describes here , or by downloading the proper version of solc binary from the solidity github repository and copying it over your existing solc binary using: To confirm Slither is installed, print the Slither help message with slither -h . If the output shows a long list of Slither command options (as opposed to an error), Slither should be installed properly. The latest version of Slither at the time of writing was 0.8.2.
Now that you have Slither installed and solc is the correct version, you need to make sure you can compile the contracts without any errors. Normally a project will require the installation of JavaScript dependencies before it can be built. These dependencies can be installed with either npm or yarn. The best approach is to read the project documentation and use the build instructions provided. If there are no instructions, I use a simple rule of thumb. If there is a yarn.lock file in the project directory, use yarn install to install the dependencies. If there is only a package.json file but no yarn.lock file, then use npm install to install the dependencies.
5. Performance Evaluation & Extended Technical Observations The command used for compiling the project depends on the development toolchain used. If hardhat is used, you should find a hardhat.config.ts or hardhat.config.js file in the top level directory. Make sure you are in the same directory as the hardhat.config.js file when you run npx hardhat compile .
If another development toolchain is used, such as truffle , waffle , dapptools , foundry , etc., refer to the project’s documentation or visit the official website for the proper development toolchain and read the toolchain documentation on how to compile a project with that tool. If brownie or foundry are the build frameworks, you’re out of luck as of early 2022 - see the upcoming section about that .
After you have the project compiling without errors using its native framework, it’s time to run Slither. The easiest way to run all 76 Slither detectors is by navigating to the top level directory of your project and running slither . . If all goes well, you should see colorful output like the screenshot below. Many examples online have more arguments in the command, but you don’t need them for Slither to run successfully. There are many old issues in the Slither repository where users try running Slither with slither ./contracts , but this is incorrect because Slither expects to receive the top level directory of the project, not the contracts directory. By default, Slither will compile the contracts when it is run. If you just finished compiling your contract with npx hardhat compile or a similar command, there is no need for Slither to waste time repeating the compilation, so you can run Slither with slither .
--hardhat-ignore-compile to tell Slither to skip compiling the code and save some time. The slither -h help message shows there is a similar flag to skip compilation with waffle, dapptools, etc. Slither will sometimes encounter an error. If you are testing a project that uses brownie or foundry, skip to the end to this section for an explanation on known open issues. Sometimes reading the Slither error message will guide you on how to solve the error, but sometimes it’s not very helpful. In these cases, I start by checking whether the program compiles by testing: For some deeper background, crytic-compile is what Slither uses to compile the contracts before it begins static analysis, and sometimes crytic-compile doesn’t like the code you try to compile. If the three steps above don’t solve the issue for me, I take some keywords from the error messages I received from Slither and crytic-compile and search for Slither past issues and crytic-compile past issues . It can help to search both projects because sometimes the issue can get posted to the wrong project. If your searches don’t yield fruit, and searching on Google and Stack Overflow doesn’t help either, it might be time to post a new issue to the Slither GitHub.
If you’ve used Slither before, you may have been annoyed by findings concerning dependencies in the node_modules folder. A Slither config file can simplify your output and remove these findings. The full list of config file options is on the project page , but I normally filter out the node_modules folder at a minimum. This config file can have any name, but Slither will require the --config-file NewFileName argument to specify where the config file is if the default name is not used. For this reason, I find it easier to always use the default config file name, which is “slither.config.json”. Copy the filter_paths statement below into a file named “slither.config.json” located in the top level directory of your project (the same location where you run slither . ) and Slither will use this config file for your project.
The config file data above is will remove findings from the node_modules directory. You can go further and remove multiple paths from Slither results. For example, if you wanted to remove the “contract/Interfaces” and the “contract/Math” directories from Slither analysis, you could use the following config file. Be aware that Slither documentation as of April 2022 suggests separating filter path values with a , instead of a | , which is incorrect .
Another useful config file option is to filter out findings of a certain risk level. For example, if we wanted to remove optimization, informational, and low risk findings, which often have some false positives that clutter the results output, we could use this config file. The output of slither --help lists the optional flags you can add to the slither . command. Adding flags will give the same results as a config file. I prefer storing the config data in a config file, but that is my personal choice. For example, to duplicate the config file result above, you can use slither . --filter-paths "node_modules" --exclude-optimization --exclude-informational --exclude-low .
In February 2022, the Slither GitHub action was published. This can run Slither automatically each time a PR or commit is added to your project. Whether you would find Slither output after each commit to be useful is your choice, but filtering out the low risk issues using the config file above may help reduce the noise in the results. There’s a few quirks with Slither that are minor and understandable for an automated tool with no setup required. It is worth mentioning these in case you encounter the same quirks.
The first quirk is that Slither doesn’t consider the modifiers involved when checking for findings like reentrancy. For example, Slither might identify a function as vulnerable to reentrancy even though there is a “nonReentrant” or “lock” modifier on the function. In other places, it might flag a function such as “selfdestruct” when the “onlyOnly” modifier exists on the function. It is always mandatory to check the output of any automated security tool, but I have learned to expect to see “nonReentrant” modifiers on most functions that Slither highlights as potentially vulnerable to reentrancy.
There is still plenty of room to grow for automated solidity security tools of the future. Several detectors could be added to handle Open Zeppelin dependencies alone to make sure they are used properly, let along other libraries. Possible checks could include: 1. checking for an initializer modifier on any function containing the letters “initialize” or “initialization” to prevent the possibility of multiple initializations 2.
validating that inherited contracts are initialized properly if openzeppelin-contracts-upgradeable imports exist 3. checking the package.json for outdated versions of Open Zeppelin contracts with known security issues .
I first saw the Slither printer feature demoed in this talk by Scott Bigelow . This feature is well documented . Printers are a way to visualize the functions in the project in different ways. There are 18 different printers, each providing a different view on the project code. To list the different printers, use slither --list-printers . Here are some examples of using the printers, and remember that adding the --hardhat-ignore-compile argument can speed up the process by skipping compilation: The main difficulty I have had using these printers is sizing the output properly so the table renders neatly while the text is still large enough to be legible. I personally prefer the layout provided by VS Code extensions that serve a similar purpose.
Slither’s static analyzer may be the most commonly used part of Slither, but wait, there’s more! Slither also includes the following CLI tools: Not all of these tools have much official documentation . I will only mention a few here. The slither-check-erc tool is the tool I have used the most, besides the main static analyzer. Any time I encounter a contract that implements a common ERC token, I run this tool as a sanity check. If you’re really lazy, check the output of slither . --print human-summary and look for the ERCs output line to see what is automatically detected. The output of slither-check-erc lists whether all the functions required by the ERC specification are implemented. The output contains optional functions for the ERC too, pointing out possible areas for improvement even if the minimum requirements are met. Using slither-check-erc is very similar to running Slither, but the contract name must be provided as an input argument. The command to run this tool on an ERC20 token contract, which is the default ERC for the tool, is shown below.
slither-check-erc supports the following tokens: ERC20,ERC223,ERC165,ERC721,ERC1820,ERC777,ERC1155. To test a token other than ERC20, include the --erc argument. The slither-flat tool flattens a codebase. What this means in practice is that all contracts for a project are reorganized into a single folder. This process is most useful to prepare the contracts for another tool like mythx that might encounter problems with external contract imports. You can see the results yourself using slither-flat . , which will store the output files in a new directory named “crytic-export/flattening”.
The slither-check-upgradeability tool automatically checks contracts that use the delegatecall proxy pattern . Because of the evolving nature of proxy architecture and strategies, I haven’t used this tool as much as expected, but if you do encounter this scenario, the tool is definitely worth using. It can be run with slither-check-upgradeability ContractName.sol ContractName . Here’s one custom code example that prints out the contract name and function name if a function match the criteria 1. the function is public or external 2. state variables are modified in the function 3. there is no onlyOwner modifier on the function.
Save this code in a Python .py file in the same top level directory where you run slither . . This python script is run like any other python script, using python3 filename.py . There are open issues that brownie and foundry don’t currently play nice with Slither (technically the issue is with crytic-compile, which Slither relies upon), so what is the workaround? My simple hack is to create a new hardhat project, copy the contracts over, fix dependencies as needed, make sure the code compiles, and run Slither on the hardhat project. Here are my steps to doing this.
First, check that you have hardhat installed globally on your system by viewing the help message from npx hardhat --help . If you see the hardhat help message, then setting up a fresh hardhat project is as simple as running npx hardhat in the directory where you want to store the project, selecting the “Create a basic sample project” option when asked, and answering the prompts (usually by tapping enter to accept the defaults until no more prompts appear).
A few final steps are needed to copy over the original project to the blank hardhat template. Harvested Online Documentation & Reference Sources • https://github.com/crytic/slither • https://crytic.github.io/slither/slither.html • https://secure-contracts.com/program-analysis/slither/docs/src/index.html • https://pypi.org/project/slither-analyzer/ • https://github.com/Surendra-Patil/slither-smart-contract-scanner • https://hackenproof.com/blog/how-to-use-slither-for-auditing-smart-contracts • https://github.com/oswaldblockdev/slither-detector-101 • https://cloudlogic.dev/2026/06/09/automated-smart-contract-security-testing-with-slither-echidna-and-foundry/ • https://markaicode.com/slither-smart-contract-security-analysis/ • https://security.erikelbieh.com/using-slither
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Smart Contract Vulnerability Detection Tool Using Slither.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Smart Contract Vulnerability Detection Tool Using Slither... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |