Complete Technical Paper Content — Software Bill Of Materials Generation And Vulnerability Tool
Overview & System Context
Software Bill Of Materials Generation And Vulnerability Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9512 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A software supply chain is the components, libraries, tools, and processes used to develop, build, and publish a software artifact. This collection of dependencies is called a software supply chain, by analogy with supply chains of physical goods required for manufacturing. Companies with products that rely on complex software supply chains may implement strategies for supply chain risk management to try to improve supply chain security. A software bill of materials (SBOM) declares the inventory of components used to build a software artifact, including any open source and proprietary software components. It is the software analogue to the traditional manufacturing bill of materials (BOM), which is used as part of supply chain management. SBOMs are a strategy for improving transparency in the software supply chain.
Grype is an open-source vulnerability scanner designed to identify known security vulnerabilities in container images, filesystems, and software artifacts. It is commonly used in DevOps and cloud-native environments to detect vulnerabilities in operating system packages and language-specific dependencies prior to deployment. Grype scans container images and filesystems by comparing installed packages against vulnerability databases, and supports scanning images stored locally or in remote registries, as well as extracted file systems and software bill of materials (SBOMs). Grype is developed and maintained by Anchore and is distributed as a command-line interface (CLI) tool. It can be used for periodic scanning of deployed containers to identify newly introduced vulnerabilities, as well as for automated scanning within development pipelines to detect vulnerabilities before containers are promoted to production. Grype supports multiple Linux distributions, including Alpine, Debian, Ubuntu, Red Hat Enterprise Linux (RHEL), and Amazon Linux, as well as language-specific ecosystems such as Java, Python, JavaScript, Ruby, and Go.
React (also known as React.js or ReactJS) is a free and open-source front-end JavaScript library that aims to make building user interfaces based on components more "seamless". It is maintained by Meta (formerly Facebook) and a community of individual developers and companies. According to the 2025 Stack Overflow Developer Survey, React is one of the most commonly used web technologies. React can be used to develop single-page, mobile, or server-rendered applications with frameworks like Next.js and React Router. Because React is only concerned with the user interface and rendering components to the DOM, React applications often rely on libraries for routing and other client-side functionality. A key advantage of React is that it only re-renders those parts of the page that have changed, avoiding unnecessary re-rendering of unchanged DOM elements. React is used by an estimated 6% of all websites.
"Only call hooks at the top level" — do not call hooks from inside loops, conditions, or nested statements so that the hooks are called in the same order each render. "Only call hooks from React functions" — do not call hooks from plain JavaScript functions so that stateful logic stays with the component. Although these rules cannot be enforced at runtime, code analysis tools such as linters can be configured to detect many mistakes during development. The rules apply to both usage of Hooks and the implementation of custom Hooks, which may call other Hooks.
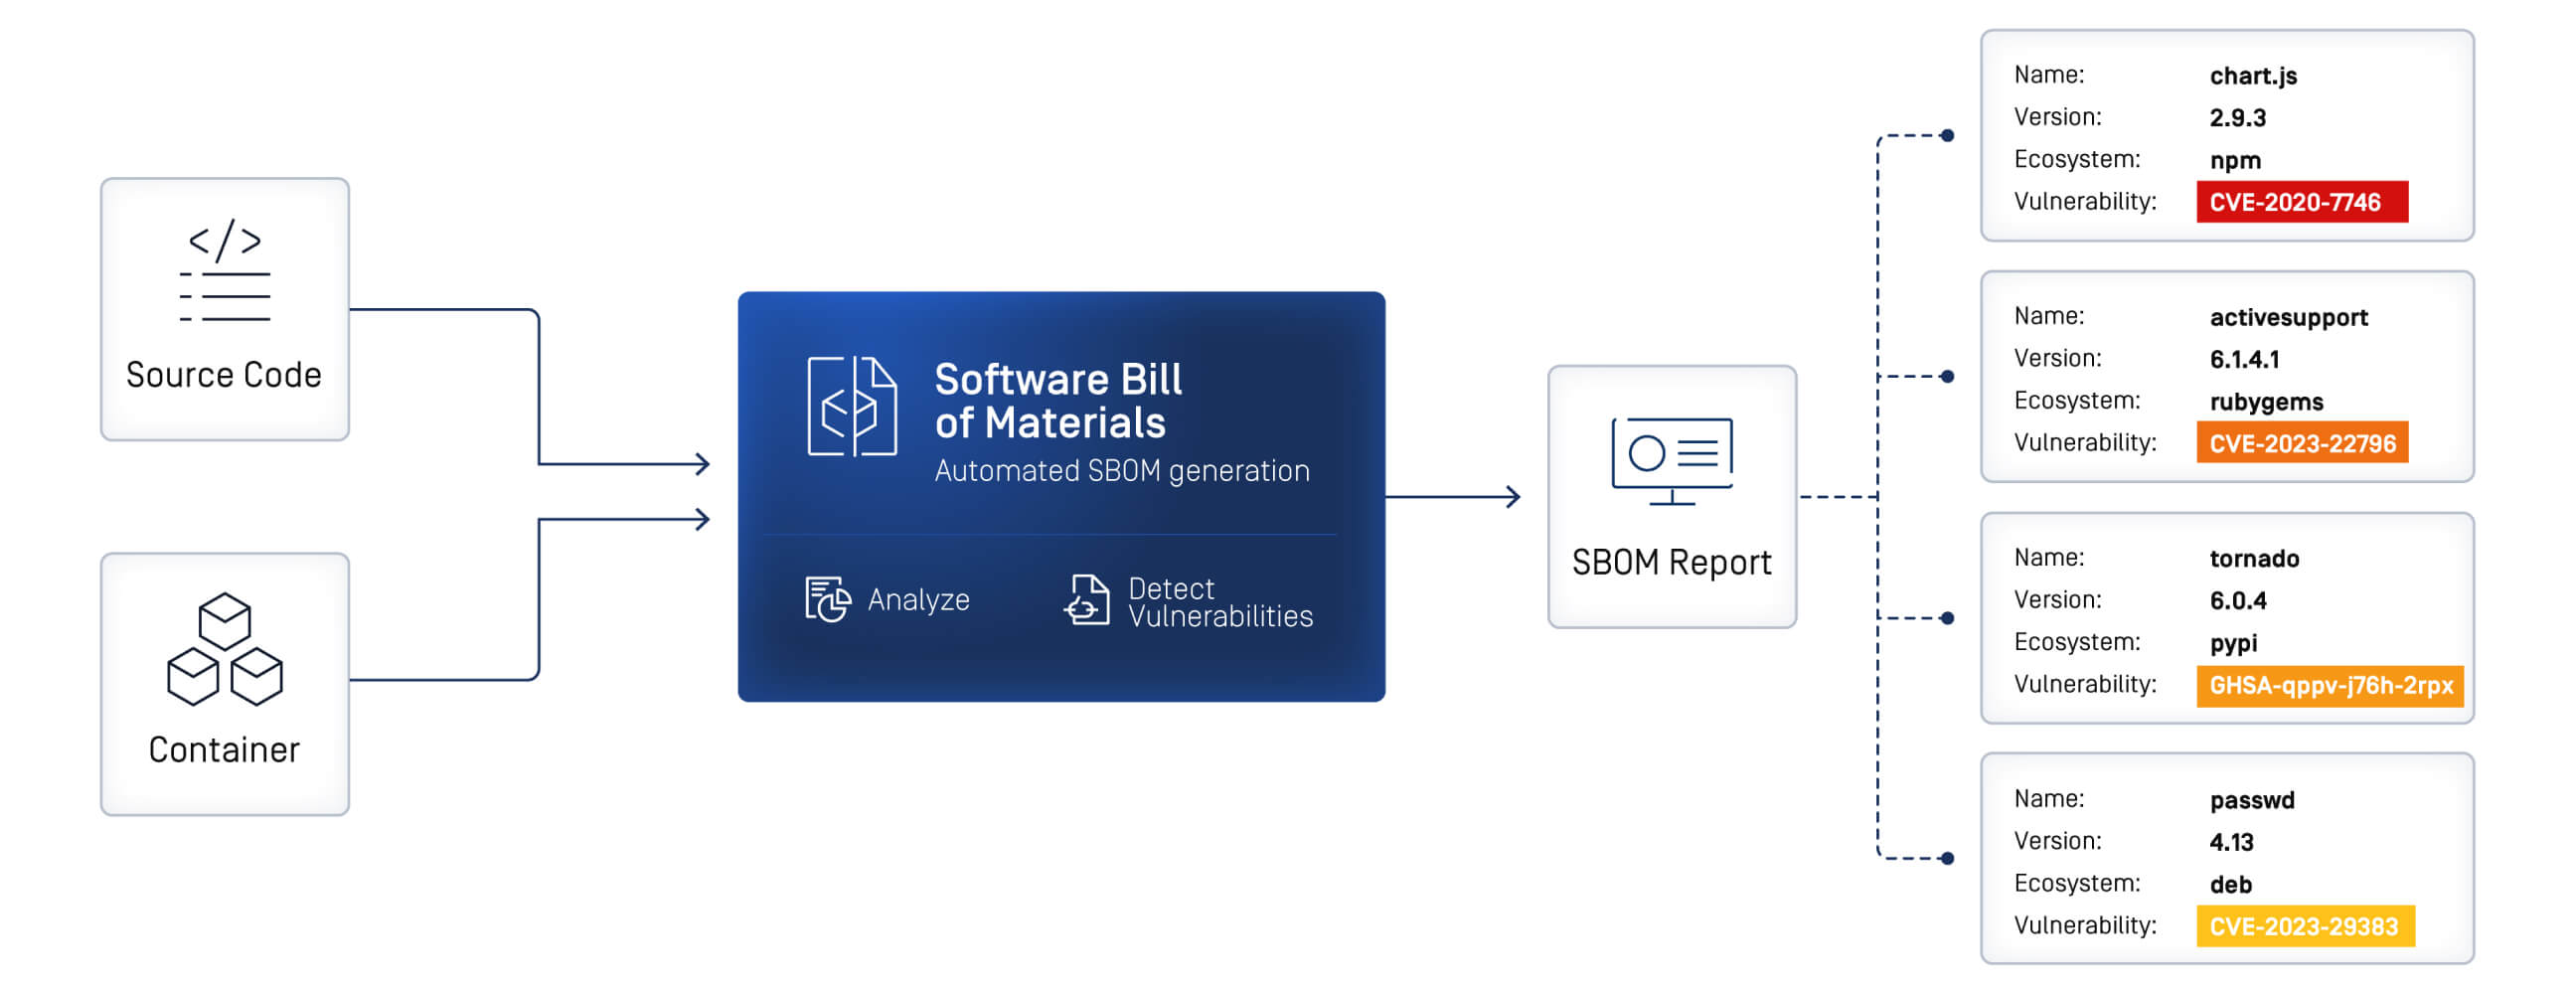
Figure 1: Software Bill of Materials - Automated SBOM Generation - OPSWAT ShouldComponentUpdate allows the developer to prevent unnecessary re-rendering of a component by returning false if a render is not required. componentDidMount is called once the component has "mounted" (the component has been created in the user interface, often by associating it with a DOM node). This is commonly used to trigger data loading from a remote source via an API. componentDidUpdate is invoked immediately after updating occurs. componentWillUnmount is called immediately before the component is torn down or "unmounted". This is commonly used to clear resource-demanding dependencies to the component that will not simply be removed with the unmounting of the component (e.g., removing any setInterval() instances that are related to the component, or an "eventListener" set on the "document" because of the presence of the component) render is the most important lifecycle method and the only required one in any component. It is usually called every time the component's state is updated, which should be reflected in the user interface.
JSX, or JavaScript XML, is an extension to the JavaScript language syntax. Similar in appearance to HTML, JSX provides a way to structure component rendering using syntax familiar to many developers. React components are typically written using JSX, although they do not have to be (components may also be written in pure JavaScript). During compilation, JSX is converted to JavaScript code. JSX is similar to another extension syntax created by Facebook for PHP called XHP. An example of JSX code: To support React's concept of unidirectional data flow (which might be contrasted with AngularJS's bidirectional flow), the Flux architecture was developed as an alternative to the popular model–view–controller architecture. Flux features actions which are sent through a central dispatcher to a store, and changes to the store are propagated back to the view. When used with React, this propagation is accomplished through component properties. Since its conception, Flux has been superseded by libraries such as Redux and MobX. Flux can be considered a variant of the observer pattern. A React component under the Flux architecture should not directly modify any props passed to it, but should be passed callback functions that create actions which are sent by the dispatcher to modify the store. The action is an object whose responsibility is to describe what has taken place: for example, an action describing one user "following" another might contain a user id, a target user id, and the type USER_FOLLOWED_ANOTHER_USER. The stores, which can be thought of as models, can alter themselves in response to actions received from the dispatcher. This pattern is sometimes expressed as "properties flow down, actions flow up". Many implementations of Flux have been created since its inception, perhaps the most well-known being Redux, which features a single store, often called a single source of truth. In February 2019, useReducer was introduced as a React hook in the 16.8 release. It provides an API that is consistent with Redux, enabling developers to create Redux-like stores that are local to component states.
The license granted hereunder will terminate, automatically and without notice, if you (or any of your subsidiaries, corporate affiliates or agents) initiate directly or indirectly, or take a direct financial interest in, any Patent Assertion: (i) against Facebook or any of its subsidiaries or corporate affiliates, (ii) against any party if such Patent Assertion arises in whole or in part from any software, technology, product or service of Facebook or any of its subsidiaries or corporate affiliates, or (iii) against any party relating to the Software. [...] A "Patent Assertion" is any lawsuit or other action alleging direct, indirect, or contributory infringement or inducement to infringe any patent, including a cross-claim or counterclaim. The Apache Software Foundation considered this licensing arrangement to be incompatible with its licensing policies, as it "passes along risk to downstream consumers of our software imbalanced in favor of the licensor, not the licensee, thereby violating our Apache legal policy of being a universal donor", and "are not a subset of those found in the [Apache License 2.0], and they cannot be sublicensed as [Apache License 2.0]". In August 2017, Facebook dismissed the Apache Foundation's downstream concerns and refused to reconsider their license. The following month, WordPress decided to switch its Gutenberg and Calypso projects away from React. On September 23, 2017, Facebook announced that the following week, it would re-license Flow, Jest, React, and Immutable.js under a standard MIT License; the company stated that React was "the foundation of a broad ecosystem of open source software for the web", and that they did not want to "hold back forward progress for nontechnical reasons". On September 26, 2017, React 16.0.0 was released with the MIT license. The MIT license change has also been backported to the 15.x release line with React 15.6.2.
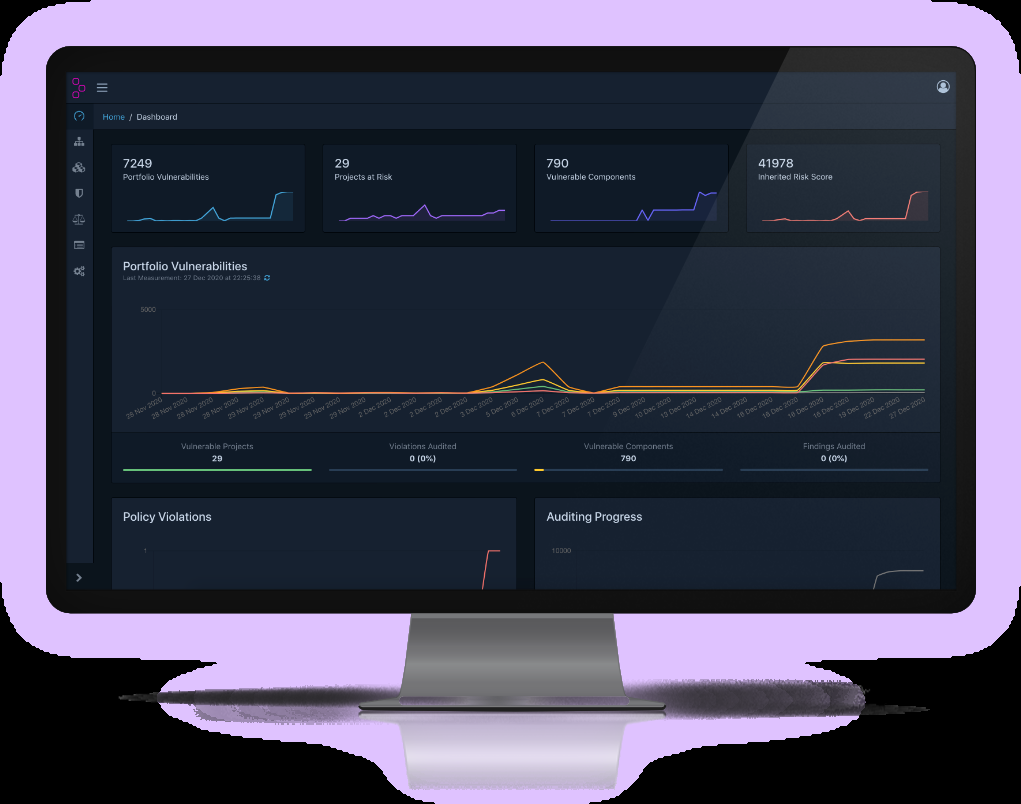
Figure 2: Dependency-Track | Software Bill of Materials (SBOM) Analysis | OWASP Angular (web framework) Backbone.js Ember.js Gatsby (JavaScript framework) Next.js TypeScript Svelte Vue.js Comparison of JavaScript-based web frameworks Web Components Official websites use .gov A .gov website belongs to an official government organization in the United States.
Secure .gov websites use HTTPS A lock ( ) or https:// means you’ve safely connected to the .gov website. Share sensitive information only on official, secure websites. A “software bill of materials” (SBOM) has emerged as a key building block in software security and software supply chain risk management. An SBOM is a nested inventory, a list of ingredients that make up software components. While not a brand new concept, the ideas and implementation have advanced since 2018 through a number of collaborative community effort, including National Telecommunications and Information Administration’s (NTIA) multistakeholder process .
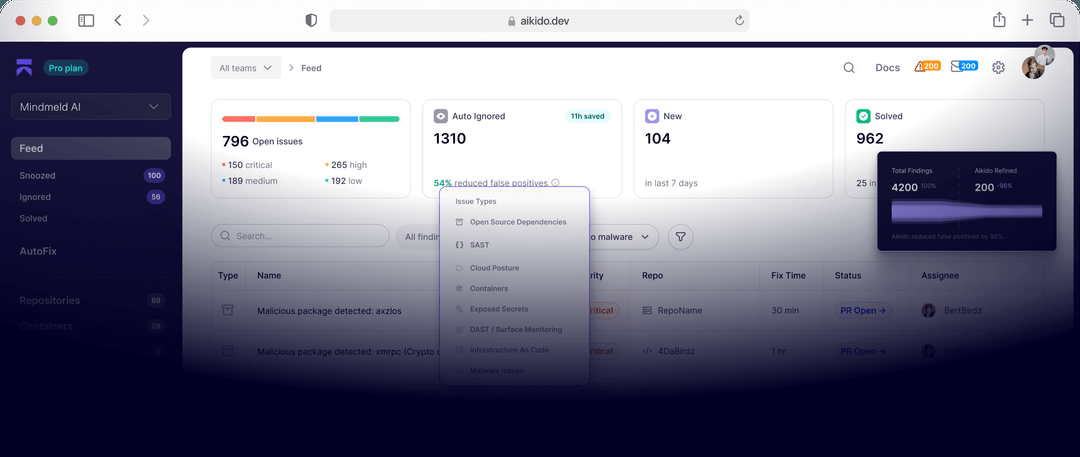
Figure 3: SBOM Generator: Software Bill of Materials | Aikido Security CISA is advancing the SBOM adoption and practices by facilitating community-led work, with a focus on scaling and operationalization, as well as tools, new technologies, and new use cases. This website will also be a nexus for the broader set of SBOM resources across the digital ecosystem and around the world.
An SBOM-related concept is the Vulnerability Exploitability eXchange (VEX). A VEX document is an attestation, a form of a security advisory that indicates whether a product or products are affected by a known vulnerability or vulnerabilities. CISA also advances the SBOM work by facilitating community engagement to advance and refine SBOM, coordinating with international, industry, inter-agency partners on SBOM implementation, and promoting SBOM as a transparency tool across the broader software ecosystem, the U.S. government, and the world. If you have any questions, please reach out to us at SBOM@cisa.dhs.gov This joint guidance includes new SBOM data fields, practices, and processes to reflect stakeholder feedback and tooling advancements driven by the growing number of organizations using SBOMs worldwide.
This guidance helps public and private sector stakeholders improve transparency in their super intelligence systems and supply chains. 2025 Minimum Elements for a Software Bill of Materials (SBOM) Guidance and Request for Comment Updated draft SBOM guidance outlines current best practices for software transparency and supply chain security. Open for public comment until October 3, 2025.
This document, further defines and clarifies SBOM Attributes from the 2021 Framing Software Component Transparency document , offering descriptions of the minimum expected, recommended practices, and aspirational goal for each Attribute. This guide provides information on the benefits of SBOM, common misconceptions and concerns, creation of an SBOM, distributing and sharing an SBOM, and role specific guidance.
Acknowledging key differences between SaaS and non-SaaS software, this paper discusses the value of SBOM-driven transparency for SaaS and offers recommendations for advancing transparency in SaaS software. This document provides examples of how software bill of materials (SBOM) can be shared between different actors across the software supply chain. The examples demonstrate SBOM sharing methods currently in use, ranging from proprietary software vendor Building on the SBOM Sharing Lifecycle Report, this document defines the three roles (SBOM Author, SBOM Consumer, and SBOM Distributor) of the SBOM sharing lifecycle and the factors they should keep in mind or be aware of when engaging in the three p Software producers, such as product manufacturers and integrators, often need to assemble and test a set of products together before delivering to their customers. This set of products may contain components that undergo version changes over time and This document seeks to explain the circumstances and events that could lead an entity to issue Vulnerability Exploitability eXchange (VEX) information and describes the entities that create or consume VEX information. Whether, and when, to issue VEX CISA advances the SBOM work by facilitating community engagement to advance and refine SBOM, coordinating with international, industry, inter-agency partners on SBOM implementation, and promoting SBOM as a transparency tool across the broader software ecosystem, the U.S. government, and the world.
For any questions or to receive updates on CISA’s SBOM work, please email SBOM@cisa.dhs.gov . Official websites use .gov A .gov website belongs to an official government organization in the United States. Secure .gov websites use HTTPS A lock ( ) or https:// means you’ve safely connected to the .gov website. Share sensitive information only on official, secure websites.
CISA, the National Security Agency, the Federal Bureau of Investigation, and international partners released joint guidance, 2026 Minimum Elements for a Software Bill of Materials (SBOM) , that updates and replaces the minimum elements for an SBOM published by the National Telecommunications and Information Administration (NTIA) in 2021. The new guidance incorporates stakeholder feedback from a 2025 public comment period and reflects current SBOM tools and needs while preserving the core principles of the original NTIA document.
An SBOM serves as an “ingredients list” for software and is a key building block of software security and supply chain risk management. Organizations can use SBOM data to better understand the makeup of their software components and supply chains and make more risk-informed decisions. Minimum elements for an SBOM describe the baseline technologies and practices that an SBOM should include.
While the minimum elements for an SBOM apply to all software, some software types—such as artificial intelligence and software as a service in cloud environments—may require additional elements. Any effort to improve software transparency, regardless of the software type, should begin with the application of minimum elements. Official websites use .gov A .gov website belongs to an official government organization in the United States.
Secure .gov websites use HTTPS A lock ( ) or https:// means you've safely connected to the .gov website. Share sensitive information only on official, secure websites. A “Software Bill of Materials” (SBOM) is a nested inventory for software, a list of ingredients that make up software components. The following documents were drafted by stakeholders in an open and transparent process to address transparency around software components, and were approved by a consensus of participating stakeholders. More information about the NTIA multistakeholder process on software component transparency is available here .
SBOM at a Glance (2021) This resource provides an introduction to the practice of SBOM, supporting literature, and the pivotal role SBOMs play in providing much-needed transparency for the software supply chain. ( Japanese translation ) SBOM FAQ (2021 ) This document outlines detailed information, benefits, and commonly asked questions. SBOM Myths vs. Facts (2021) This document is intended to help the reader to understand and dispel common, often sincere myths and misconceptions about SBOM.
SBOM Explainer Videos on YouTube (2020-2021) This collection of videos provides a wide range of information about SBOM including introductory concepts, technical webinars, and proof of concept presentations. Framing Software Component Transparency: Establishing a Common Software Bill of Materials (SBOM) – (2021) This resource serves as the detailed foundation of SBOM. It defines SBOM concepts and related terms, offers an updated baseline of how software components are to be represented, and discusses the processes around SBOM creation. (prior 2019 edition ) SBOM Options and Decision Points (2021 ) This resource frames the dimensions of SBOM creation and delivery, to support more consistent and effective articulation of needs between requesters and suppliers of SBOMs.
Use Cases: Roles and Benefits for SBOM Across the Supply Chain (2019) This resource summarizes the use cases and benefits of having an SBOM from the perspective of those who make software, those who choose or buy software, and those who operate it. It characterizes the security, quality, efficiency, and other organizational benefits, as well as the potential for the broader ecosystem across the supply chain.
SBOM Tool Classification Taxonomy (2021) This resource offers a categorization of different types of SBOM tools. It can help tool creators and vendors to easily classify their work, and can help those who need SBOM tools understand what is available. Survey of Existing SBOM Formats and Standards (2021) This resource summarizes existing standards, formats, and initiatives as they apply to identifying the external components and shared libraries used in the construction of software products for SBOMs, highlighting three key formats of SPDX, CycloneDX, and SWID. The group analyzed efforts already underway by other groups related to communicating this information in a machine-readable manner. (prior 2019 edition ) Software Suppliers Playbook: SBOM Production and Provision (2021 ) This resource outlines workflows for the production of Software Bills of Materials (SBOM) and their provision by software suppliers, including software vendors supplying a commercial product, contract software developers supplying a software deliverable to clients, and open source software (OSS) development projects making their capabilities publicly available.
2. System Architecture & Core Working Principles Software Consumers Playbook: SBOM Acquisition, Management, and Use (2021 ) This resource outlines workflows for the acquisition, management, and use of SBOM by software consumers, including commercial and non-commercial entities acquiring third-party software capabilities from a supplier.
How-To Guide for SBOM Generation (2021) This resource offers instructions and guidance on how to generate an SBOM based on the experiences of the Healthcare Proof-of-Concept working group. Sharing and Exchanging SBOMs (2021) This resource describes how SBOM data can flow down the supply chain, and provides a small set of SBOM discovery and access options to support flexibility while minimizing the burden of implementation.
Software Identity: Challenges and Guidance (2021) This resource reviews the challenges of identifying software components for SBOM implementation with sufficient discoverability and uniqueness. It offers guidance to functionally identify software components in the short term and converge multiple existing identification systems in the near future. SBOM Tool Classification Taxonomy (2021) This resource offers a categorization of different types of SBOM tools. It can help tool creators and vendors to easily classify their work, and can help those who need SBOM tools understand what is available.
Vulnerability-Exploitability eXchange (VEX) - An Overview (2021 ) This resource offers a brief introduction to VEX, which allows a software supplier to clarify whether a specific vulnerability actually affects a product. How-To Guide for SBOM Generation in Healthcare (2021) This resource offers instructions and guidance on how to generate an SBOM based on the experiences of the Healthcare Proof-of-Concept working group.
Healthcare SBOM Proof of Concept – Phase II Summary (2021) Phase II confirmed the value of providing SBOM information, proving the viability of the baseline elements, expanding use cases and participants, developing a how-to guide, and exploring the use of VEX. Healthcare Proof of Concept Report (2019) This resource documents the successful execution and lessons learned of a proof-of-concept exercise led by medical device manufacturers (MDMs) and healthcare delivery organizations (HDOs). The exercise examined the feasibility of SBOMs being generated by MDMs and used by HDOs as part of operational and risk management approaches to medical devices at their hospitals.
Software Bill of Materials Related Efforts (2021) A collection of initiatives, guidance, models, frameworks, and reports that explicitly or implicitly highlight the value of SBOM. Software Identity: Challenges and Guidance (2021) This resource reviews the challenges of identifying software components for SBOM implementation with sufficient discoverability and uniqueness. It offers guidance to functionally identify software components in the short term and converge multiple existing identification systems in the near future.
SBOM Two-Page Overview (2020 ) This document provides high-level information on SBOM’s background and ecosystem-wide solution, the NTIA process, and an example of an SBOM. For upcoming and archived meeting details, please visit the NTIA Software Component Transparency page . TL;DR: Three SBOM standards serve different purposes. CycloneDX prioritizes vulnerability tracking with native VEX support.
SPDX focuses on licensing compliance and has broader tool adoption. SWID is an IT asset management term used only for specific federal requirements. Most teams need CycloneDX for security work and SPDX for legal review. The format your team chooses determines whether your SBOM becomes a security tool or sits unused in an artifact repository. FDA reviewers have rejected submissions over format mismatches, and federal contractors often receive format specifications without a clear rationale. This gap between compliance and utility is where most SBOM initiatives fail.
Most teams can generate SBOMs, but without processes to interpret and apply that data, the output rarely delivers real security value. In this guide, you’ll see what each standard captures, which tools generate clean output versus SBOMs that technically validate but lack meaningful data, and how to use SBOM data for dependency risk management.
SBOM standards define how you document the components, dependencies, and metadata in a software product. The standards specify which fields are required and how relationships get structured, including the formats tools should output. The main problem: three competing standards exist, each with different strengths, and most tools implement them inconsistently. Your build pipeline might generate an SBOM that validates against the schema but lists every component as “NOASSERTION” for licensing or omits the CPE identifiers that vulnerability scanners need.
Schema validation alone proves nothing about data quality. An SBOM can pass every validation check while containing zero actionable information because the generator filled the required fields with placeholder values. The three primary SBOM standards are: CycloneDX : Built by the Open Worldwide Application Security Project (OWASP) community specifically for security use cases, with strong support for vulnerability data and dependencies SPDX : Created by the Linux Foundation for open source licensing compliance, now used for broader supply chain transparency WID : Developed by the National Institute of Standards and Technology (NIST) for IT asset management, required for some federal systems but rarely used elsewhere Each standard made different design choices about what matters most, which affects what you can actually do with the SBOM after you generate it.
Additionally, White House Executive Order 14028 on cybersecurity required SBOMs but didn’t mandate a specific standard. Different federal agencies made different choices, leading medical device manufacturers to see FDA 510(k) submissions bounce because they generated SPDX in JSON format, while the FDA’s tools only parsed tag-value format. Six weeks get lost to format conversion that adds no technical value.
CycloneDX was purpose-built for application security. When you need to track whether CVE-2024-1234 affects your production services, CycloneDX makes that correlation straightforward because the standard was designed for that workflow. The architecture reflects security priorities. Where SPDX evolved from licensing concerns and later added security fields, CycloneDX started with vulnerability tracking as its primary use case.
Component inventory with versions, hashes, and package URLs (PURLs) that precisely identify what you’re using. The PURL specification standardizes how packages are named across ecosystems, ensuring tools recognize that “jackson-databind” in your Maven build is the same component in vulnerability databases. Dependency graphs show which components rely on others, important when a vulnerable transitive dependency sits five layers deep. The graph structure lets you trace exactly which direct dependencies pulled in the problematic component.
VEX data is embedded directly in the SBOM documents, indicating whether your code actually calls the vulnerable function. This separates theoretical exposure from operational risk. VEX documents that analysis and prevents false-positive alerts. Service definitions for microarchitectures track external APIs and data flows, extending beyond traditional dependency tracking.
Using an older version might mean being stuck on 1.4 for 6 months, since upgrading to 1.6 could break existing steps for vulnerability correlation. The reason is that the schema changes weren’t backward-compatible. You’ll see it when a scan shows “0 components detected” for container images built with an outdated plugin. The SBOM technically validates, but the missing container-layer metadata makes every image look empty to the scanner.
To avoid that mismatch, use the current generation plugins that natively support CycloneDX across major build tools: The dependency graph and PURL identifiers let vulnerability scanners automatically match CVEs to your deployments, eliminating the need for manual lookups. Container registries like Harbor, Amazon ECR, and GitHub Container Registry now accept SBOM uploads directly, but most only support CycloneDX or SPDX in JSON format. SWID is rarely accepted because it lacks container-layer metadata. Using CycloneDX ensures registries can automatically associate SBOMs with stored images for vulnerability scanning.
SPDX was developed nearly a decade before CycloneDX to identify which open-source licenses apply to components inside a product. Legal teams encounter the problem regularly: a library marked “MIT” contains a single GPL file deep in its tree. SPDX lets legal see that file before it becomes a compliance issue. Originally focused purely on licensing and open-source compliance, SPDX has expanded significantly with versions 2.3 and 3.0 to include vulnerability tracking and security use cases.
Detailed license information, including SPDX license identifiers, custom license text, and license expression parsing. The SPDX License List provides standardized identifiers for hundreds of open-source licenses. File-level analysis documents which licenses apply to which source files, key for legal review. This granularity catches edge cases where a primarily MIT-licensed project includes GPL-licensed test utilities.
Package relationships identify which packages include or depend on others, modeling relationships like “CONTAINS,” “DEPENDS_ON,” and “BUILD_TOOL_OF.” Security identifiers (CPEs, PURLs) were added in versions 2.3 and 3.0 to support vulnerability tracking, though not always populated by tools.
When legal reviews your software, they need to know whether the MIT-licensed library you’re using actually contains files under the GNU General Public License (GPL) that trigger copyleft requirements. SPDX documents this at file granularity. SPDX supports multiple formats: RDF/XML, JSON, YAML, tag-value, and spreadsheets. This flexibility causes practical problems because every format requires different parsing code.
SPDX 2.2 : Widely adopted, stable, focuses exclusively on licensing with limited security metadata SPDX 2.3 : Added external references for security identifiers, bridging licensing and vulnerability tracking SPDX 3.0 : Complete redesign with expanded security capabilities, making it more competitive with CycloneDX for vulnerability management, but limited tool adoption as of 2024 3. Software Implementation, Frameworks & Protocols Version fragmentation creates practical issues. Teams generate SPDX 2.3 but find their legal team’s review tools only parse 2.2, requiring conversion that strips security fields.
You would use SPDX when your legal department requires SBOMs for open source license compliance and already has workflows built around the SPDX format. Changing to CycloneDX or another SBOM standard means retraining and potentially new tooling. Another instance is when you’re shipping software to customers who specifically request SPDX, which is common in the automotive and industrial sectors, where SPDX adoption happened early.
SWID tags were designed for IT asset management, tracking what software is installed on enterprise devices. The standard was developed by NIST and gained traction in federal systems. The use case differs fundamentally: SWID answers “what software is on these 10,000 endpoints,” while CycloneDX and SPDX answer “what components are in this application.” SWID rarely appears in development workflows, but is required under federal requirements that require compliance tracking to match installed software against approved baselines.
Use SWID when your organization already uses SWID tags for IT asset management, you’re selling software to federal agencies that mandate SWID tags per NIST guidelines, or your IT operations team needs software inventory data for thousands of endpoints. SWID uses XML in accordance with ISO/IEC 19770-2. The format is verbose and primarily consumed by enterprise asset management tools rather than security scanners or vulnerability databases.
For organizations with existing ITAM infrastructure, SWID integration is often already in place via tools such as ServiceNow, Flexera, or Snow Software. Few development tools generate SWID natively, which creates a gap between DevOps workflows and enterprise asset management. Organizations that need SWID for compliance typically use specialized software to create tags from existing package manifests, adding manual overhead compared to automated generation of SPDX or CycloneDX tags during builds.
For modern DevSecOps workflows focused on vulnerability management and dependency tracking, CycloneDX or SPDX is a more practical choice. SWID’s limited adoption in security tooling and CI/CD pipelines makes it less suitable for development-centric SBOM use cases. Generating accurate SBOMs requires integration across your build pipeline. They must be generated during the build process and validated to ensure they contain usable, complete data.
These native integrations are more accurate than external scanning tools because they understand the build system’s dependency resolution logic. When Maven resolves version conflicts through dependency management, the SBOM reflects what actually got compiled, not what the original pom.xml requested. The limitation is that each build tool outputs in a single format, typically CycloneDX. Organizations that need SPDX for legal review must run separate tooling or convert formats, risking inconsistencies.
Tools like Syft and Trivy scan built artifacts to extract component information. Artifact scanning catches components that build tools miss, particularly OS packages in container-based images. The tradeoff is accuracy. Scanners make educated guesses about versions based on file signatures. For production use, combine both approaches: generate SBOMs during build with native tools, then re-scan final artifacts to catch anything the build process didn’t document.
SBOM generation belongs to continuous integration and continuous delivery CI/CD, running automatically on every build. A practical implementation flow looks like this: SBOM generation adds 23 minutes per build. This is time well spent for the visibility you gain. Teams running 50+ builds daily invest about 2.5 hours in pipeline time, but that’s far less than the hours spent manually hunting affected services when the next CVE drops You’ll see the impact immediately once the SBOM generation runs in CI. Every build starts producing a CycloneDX file alongside the artifact, and those SBOMs feed straight into your vulnerability management platform. The next morning, the system compares yesterday’s SBOMs to today’s and flags new CVEs introduced through dependency updates. The deployment pipeline blocks the build until the issue clears. Over time, you’ll stop dozens of vulnerable components before they ever reach production.
A schema-valid SBOM isn’t necessarily usable. Data quality matters more than format compliance. Common issues include component names missing ecosystem identifiers, versions listed as “latest” instead of fixed values, license fields set to “NOASSERTION,” missing PURL or CPE identifiers breaking vulnerability matching, and no dependency relationships, leaving a flat list instead of a graph.
A complete SBOM covers declared and transitive dependencies, OS packages in container images, statically linked libraries, and vendored code . Your package.json lists 20 packages, but npm installed 500. A complete SBOM documents all 500. Accuracy drifts when the SBOM no longer matches the deployed code. Regenerate SBOMs on every build , compare against runtime scans, and audit artifact repositories to confirm SBOM-to-artifact mappings.
Most organizations generate SBOMs because procurement requires them. The SBOM data becomes part of your security workflow when it blocks vulnerable builds and flags outdated components. When a supply chain compromise hits, like the xz backdoor or log4shell, SBOMs tell you immediately whether you’re affected and where. Query all SBOMs for the compromised component and get a list of every service that needs patching. Without SBOMs, teams spend days searching code repositories. With SBOMs, the answer is a database query that runs in seconds.
Use CycloneDX when your primary need is vulnerability management and security scanning, you’re building security automation that ingests SBOM data, or container images and dependency graphs are core to your architecture. Opt for SPDX when legal teams require detailed license compliance documentation, you’re shipping software that requires file-level analysis of copyleft obligations, or your industry has already standardized on SPDX.
Pick SWID when federal procurement explicitly requires SWID tags per NIST guidelines, or when your organization already has asset management infrastructure that consumes SWID. Most teams end up generating multiple SBOM formats because security tools, legal teams, and federal partners consume data through different systems. Syft and similar tools output multiple formats from a single scan, keeping formats synchronized.
Multi-format generation is straightforward when build tools support it. Syft and similar tools output multiple formats from a single scan. This keeps formats synchronized and prevents version skew between the CycloneDX your security team uses and the SPDX legal reviews. SBOM generation makes sense when it fits naturally into existing workflows rather than requiring separate processes.
Kiuwan Insights generates complete SBOMs as part of continuous software composition analysis. When you scan third-party components for vulnerabilities and license compliance, the platform simultaneously builds accurate component inventories with the metadata that vulnerability matching and legal review actually need. You get one-click SBOM export in CycloneDX or SPDX formats, with confidence that component versions, licenses, and identifiers reflect what’s actually in your code. Scanning happens automatically throughout your development lifecycle, keeping SBOMs up to date without manual regeneration.
Schedule a free trial and discover how SBOM standards support security operations instead of just checking compliance boxes. An SBOM standard defines the format and required fields for documenting software components, dependencies, and metadata. The three primary standards each serve different purposes: CycloneDX, SPDX, and SWID. CycloneDX prioritizes security and vulnerability tracking, SPDX focuses on licensing compliance, and SWID handles IT asset management.
Standards ensure SBOMs can be generated by different tools and consumed by vulnerability scanners, legal review platforms, and compliance systems. Kiuwan generates SBOMs directly from dependency-resolution data rather than inferring components from post-build scans. This eliminates common issues like missing transitive dependencies or “NOASSERTION” license fields. The platform continuously updates SBOMs as code changes, tracks component age and obsolescence, and ensures identifiers such as PURL and CPE are populated for reliable vulnerability matching. The result is SBOM output that’s both schema-compliant and operationally useful for security and compliance teams.
Use CycloneDX for security operations, vulnerability management, and DevSecOps workflows. Use SPDX when legal teams need file-level license analysis or when partners specifically require SPDX format. Use SWID only if federal procurement explicitly mandates it. Many organizations generate both CycloneDX and SPDX from the same build, using CycloneDX for security scanning and SPDX for legal review.
CycloneDX supports JSON and XML. SPDX supports JSON, YAML, RDF/XML, tag-value text format, and spreadsheets. SWID uses XML only. JSON is most common for automated processing. Format choice affects tool compatibility. Some vulnerability scanners only parse specific formats, and conversion between formats can lose information. Maven CycloneDX plugin, Gradle CycloneDX plugin, npm @cyclonedx/cyclonedx-npm, .NET built-in SBOM generation, Syft for container and filesystem scanning, and Tern for container layer analysis all generate SBOMs automatically. Kiuwan Insights generates CycloneDX or SPDX SBOMs during software composition analysis. Native build tool integration is more accurate than post-build scanning because build tools know exactly what the dependency manager resolved.
NTIA defined minimum elements required for an SBOM: supplier name, component name, version, unique identifier, dependency relationships, SBOM author, and timestamp. These elements can be satisfied by CycloneDX, SPDX, or SWID formats. However, minimum elements represent baseline compliance. Useful SBOMs include additional metadata, such as license information, vulnerability references, and component hashes, beyond the minimum elements.
CycloneDX and SPDX both include fields for vulnerability identifiers (CVE, CPE, PURL) that enable automated correlation against vulnerability databases. CycloneDX’s dependency graph shows which components are transitive dependencies, helping prioritize direct dependencies for updates. VEX data in CycloneDX documents whether vulnerable code is actually exploitable in your context. Automated SBOM generation feeds vulnerability platforms with current component inventories, replacing manual tracking with continuous monitoring.
Cybersecurity Awareness Month: Securing the Future Starts With Critical Infrastructure Supply chain attacks now target dependencies as aggressively as application code, making visibility into every component non-negotiable for secure deployments. When you need to SBOM: Generate a Software Bill of Materials , you are creating a machine-readable inventory that maps libraries, versions, licenses, and known vulnerabilities across your entire stack. This guide walks through generating standards-compliant SBOMs using open-source tooling integrated directly into modern CI workflows, ensuring audit readiness without slowing delivery.
An SBOM (Software Bill of Materials) is effectively a nutritional label for software. It lists every direct and transitive dependency, including metadata like version hashes, supplier information, and licensing data. In 2026, regulatory frameworks like the U.S. Executive Order 14028 and EU CRA have moved from voluntary guidelines to mandatory enforcement for many sectors. For teams pursuing SOC 2 Type II or ISO 27001 certification, having an up-to-date SBOM is often the primary evidence artifact requested during vendor risk assessments.
Beyond compliance, the operational value is immediate. When a zero-day vulnerability like Log4Shell hits, querying an SBOM database takes seconds compared to days of manual grep searches across repositories. If you are already practicing Infrastructure as Code with Terraform , treating your dependency inventory as code follows the same immutable, version-controlled philosophy. You cannot secure what you cannot see, and the SBOM provides that foundational visibility layer.
Syft has emerged as the industry-standard open-source generator due to its broad ecosystem support and accuracy. Unlike older tools that relied solely on package manager manifests, Syft performs deep inspection of container layers, filesystems, and binary artifacts to identify embedded dependencies that manifests miss. This is critical when you containerize applications where multi-stage builds might obscure runtime dependencies.
Install Syft via the official install script or package manager. Avoid downloading random binaries; verify checksums against the GitHub release page to maintain supply chain integrity for the tool itself. Both formats are NTIA-approved minimum elements compliant. SPDX (Linux Foundation) excels at license compliance and detailed provenance, making it preferred for legal-heavy industries. CycloneDX (OWASP) was designed specifically for security use cases, with native fields for vulnerability exploitation data and service definitions. In practice, I recommend generating both if storage allows, but default to CycloneDX for DevSecOps pipelines focused on risk reduction.
4. Practical Deployment, Analysis & Case Studies Generating an SBOM locally is useful for debugging, but value comes from automation. Every build should produce a fresh SBOM attached to the artifact. This aligns with the principles discussed in CI/CD pipeline guides : shift left, fail fast, and treat metadata as a first-class deliverable. The SBOM should be signed (using Sigstore/cosign) and stored alongside the container image in your registry or artifact store.
The tooling landscape has consolidated around a few high-quality options. Choosing depends on whether your priority is pure generation speed, vulnerability correlation, or enterprise platform integration. Below is a comparison based on real-world usage in 2026 across cloud-native environments. A common mistake is relying solely on Trivy because it is popular. While excellent, Syft often identifies 10–15% more packages in complex multi-language containers due to specialized catalogers for Go binaries, Python wheels, and Java archives. For compliance-critical workloads, I frequently run both and merge results to maximize coverage.
Generating an SBOM is a point-in-time activity; security requires continuous validation. An SBOM created at build time becomes stale the moment a new CVE is published. This is where the distinction between generation and monitoring matters. Tools like Dependency-Track ingest SBOMs and automatically correlate them against NVD, OSV, and commercial vulnerability databases daily.
Validation also means verifying the SBOM itself. Use sbom-utility or cyclonedx-cli to validate schema conformance before ingestion. Invalid SBOMs silently fail in monitoring platforms, creating false confidence. Additionally, implement VEX (Vulnerability Exploitability eXchange) documents alongside your SBOM. A VEX statement clarifies whether a vulnerable component is actually exploitable in your specific context, reducing alert fatigue by 60–80% in mature organizations.
Implementing SBOM: Generate a Software Bill of Materials is no longer optional for teams handling sensitive data or operating in regulated markets. Start by integrating Syft into your existing CI pipeline today, even if initially just for visibility. Once baseline inventories exist, add Grype for policy enforcement and Dependency-Track for continuous monitoring. Remember that the SBOM is a living artifact; its value compounds only when kept current and actionable. If your team needs help designing a compliant supply chain strategy or preparing for SOC 2 audits with proper SBOM evidence, reach out to discuss your infrastructure security posture .
Generating a software bill of materials (SBOM) as part of your DevSecOps process is an essential step to secure your software supply chain. SBOMs are becoming critical due to the growing prominence of catastrophic supply chain attacks like XZ Utils , Log4j and CUPS . SBOMs are a comprehensive record of every software component in an application—along with critical metadata such as supplier, licensing, and security details. SBOMs serve as the foundational data structure for security, OSS licensing compliance, risk management use cases—and many more across a DevSecOps organization.
Importantly, SBOMs are needed to comply with the White House Executive Order (EO) 14028 and the recently ratified Cyber Resilience Act in the European Union. Fortunately, there are a number of free, open source tools that generate SBOMs. Generating your first one only takes a few simple steps: If you need instant gratification, check out our one-minute tutorial for how to generate an SBOM wih Syft. It covers generating an SBOM and scanning it for vulnerabilities: There are many tools available for generating SBOMs, so the first thing you’ll need to do is pick one to use. Below is a TL;DR of the most impactful evaluation criteria: A full-length discussion of each of these points can be found at the end of this article.
For this article, we’ll focus on Syft. It is easy to use in many different scenarios and supports a variety of ecosystems. Syft runs on your desktop, in CI systems, or as a Docker container, and it scans ecosystems ranging from Linux distributions to build dependency specifications. Additionally, Syft is the recommended software composition analysis (SCA) tool for generating SBOMs in NVIDIA’s AI Blueprint for Vulnerability Analysis .
Enough with the prelude! Let’s get into the meat of how to generate an SBOM. We’ll walk you through the process below: You can directly download Syft binaries for many platforms, including Windows, from the GitHub releases page . There is also a Syft Docker image with every release: anchore/syft , which can be run like this: Once you have Syft installed, creating your first SBOM is simple. Syft supports multiple sources to scan when generating an SBOM using both the local filesystem and container images.
To generate an SBOM for a Docker or OCI image—even without a Docker daemon—simply run: Syft can generate SBOMs from a variety of other sources, such as scanning the filesystem by directory or specific file, Podman, tar archives, or directly from an OCI registry when Docker is not available. Check out the full list of sources . By default, the SBOM you’ll see will be a nicely formatted table rather than any standardized SBOM format, which leads us to… Depending on your use case, it may be important to use a particular SBOM format. The most popular ones are Software Package Data Exchange (SPDX) and CycloneDX, both of which Syft supports. Syft also has a lossless intermediate format that interoperates with Anchore’s open source vulnerability scanner, Grype . If you’re looking for more detailed information on SBOM formats, standards, and examples, follow the link.
While Syft supports these different formats, they have slightly different goals and features. It may be important to pick SPDX or CycloneDX for interoperability with other tools or as a standardized format to distribute to downstream consumers. If your use case requires an SBOM in SPDX format, Syft has you covered. SPDX has been around the longest of all the formats mentioned here. There are multiple variants of SPDX. Syft supports SPDX Tag-Value ( spdx-tag-value ) and SPDX JSON ( spdx-json ). For SPDX JSON, simply add the -o spdx-json argument. For example, run: You’ll see there is a lot more data than the table view allows! You should see something resembling: Not only does this format contain the package names, but also Package URLs , license information, and a host of additional metadata, such as the location of associated files Syft identified within the package .
Similarly, if you need to generate an SBOM in CycloneDX format, use a CycloneDX format option. Syft supports CycloneDX XML ( cyclonedx-xml ) and JSON ( cyclonedx-json ). For CycloneDX XML: Again, there is a lot more data than the table allows, but a different set of data than the SPDX format, because there simply is not a one-to-one mapping of properties between the two.
The last format we’ll talk about is Syft’s own format. If there isn’t a need to provide an SBOM to other tools or you’re using a tool that supports Syft’s lossless intermediate format (e.g., Grype), then the Syft JSON format will deliver the highest fidelity data. Both SPDX and CycloneDX prune data fields from the metadata that Syft’s scan generates, while the Syft lossless format does not.
Although Grype works great with SPDX and CycloneDX, there could be a situation where data was lost converting to one of these formats that Grype’s matching uses. This impairs Grype’s ability to detect vulnerabilities, which is why we recommend the Syft lossless format. To use the Syft JSON format, use the -o json argument. Now that you’ve got an SBOM, what’s next? A logical next step would be to integrate with your build pipeline to have SBOMs generated automatically. In fact, there could be more than one location where it makes sense to generate SBOMs, such as build time and after a container is built or during a release process.
The SBOMs could then be scanned for license compliance and continuously for vulnerabilities. In fact, if you are using GitHub Actions, there are a couple of actions to do just that: sbom-action to generate SBOMs using Syft and scan-action to perform vulnerability scanning. For a few repositories, it’s very simple to set these up but might be challenging when there are a lot of repositories to keep track of.
As we’ve talked about, using SBOMs as a central part of securing your software supply chain is increasingly important. Integrating automated SBOM generation into your DevOps process is vital. Storing, managing, and analyzing those SBOMs to inform security measures should be an important consideration for you and your organization. For more comprehensive SBOM management , an enterprise-level solution like Anchore Enterprise will enable you to generate comprehensive SBOMs with every build, detect drift from one build to the next, share SBOMs internally or externally, and quickly identify risk such as vulnerabilities, secrets, malware, and misconfigurations.
As promised at the beginning of this article, below is a detailed discussion of the criteria to choose the best SBOM generation tool for your organization. When choosing from the array of SBOM generation tools in the market, it is important to frame your decision with the outcome(s) that you are trying to achieve. If your goal is to improve the response time/mean time to remediation when the next Log4j -style incident occurs—and be sure that there will be a next time—an SBOM tool that excels at correctly identifying open source licenses in a code base won’t be the best solution for your use case (even if you prefer its CLI ;-D).
It can be tempting to prioritize an SBOM generator that is best suited to our preferences and workflows; after all, we are the ones who will be using the tool regularly—shouldn’t we prioritize what makes our lives easier? If we prioritize our needs above the goal of the initiative, we might end up putting ourselves into a position where our choice in tools impedes our ability to recognize the desired outcome. Using the correct framing, in this case by focusing on the use cases, will keep us focused on delivering the best possible outcome.
SBOMs can be utilized for numerous purposes: security incident response, open source license compliance, proactive vulnerability management, compliance reporting or software supply chain risk management. We won’t address all use cases/outcomes in this blog post, but you can find a more comprehensive outline of potential SBOM use cases here . Pro tip: While you will inevitably leave many SBOM use cases out of scope for your current project, keeping secondary use cases in the back of your mind while making a decision on the right SBOM tool will set you up for success when those secondary use cases eventually become a priority in the future.
Does the SBOM generator support your organization’s ecosystem of programming languages, etc? SBOM generators aren’t just tools to ingest data and reformat it into a standardized format. They are typically paired with a software composition analysis (SCA) tool that scans an application/software artifact for metadata that will populate the final SBOM.
Support for the complete array of programming languages, build artifacts, and operating system ecosystems is essentially an impossible task. This means that support varies significantly depending on the SBOM generator that you select. An SBOM generator’s ability to help you reach your organizational goals is directly related to its support for your organization’s software tooling preferences. This will likely be one of the most important qualifications when choosing between different options and will rule out many that don’t meet the needs of your organization.
This is one of the most important criteria when evaluating different SBOM tools. An SBOM generator may claim support for a particular programming language, but after testing the scanne,r you may discover that it returns an SBOM with only direct dependencies—honestly not much better than a package.json or go.mod file that your build process spits out. Two different tools might both generate a valid SPDX SBOM document when run against the same source artifact, but the content of those documents can vary greatly. This variation depends on what the tool can inspect, understand, and translate.
Being able to fully scan an application for both direct and transitive dependencies as well as navigate non-ideomatic patterns for how software can be structured end up being the true differentiators between the field of SBOM generation contenders. Imagine using two SBOM tools on a Debian package. One tool recognizes Debian packages and includes detailed information about them in the SBOM. The latter can’t fully parse the Debian .deb format and omits critical information. Both produce an SBOM, but only one provides the data you need to power use-case-based outcomes like security incident response or proactive vulnerability management. Let’s make this example more concrete by simulating this difference with Syft, Anchore’s open source SBOM generation tool: 5. Performance Evaluation & Extended Technical Observations In this example, we first generate an SBOM using Syft then run it through Grype—our vulnerability scanning tool. Syft + Grype uncover 4 critical vulnerabilities.
Now let’s try the same thing but “simulate” an SBOM generator that can’t fully parse the structure of the software artifact in question: In this case, we are returned none of the critical vulnerabilities found with the former tool. This highlights the importance of careful evaluation of the SBOM generator that you decide on. It could mean the difference between effective vulnerability risk management and a security incident.
If the SBOM generator is packaged as a self-contained binary with a command line interface (CLI) then it should tick this box. CI/CD build tools are most amenable to this deployment model. If the SBOM generation tool in question isn’t a CLI, then it should at least run as a server with an API that can be called as part of the build process. Integrating with an organization’s DevSecOps pipeline is key to enabling a scalable SBOM generation process. By implementing SBOM creation directly into the existing build tooling, organizations can leverage existing automation tools to ensure consistency and efficiency, which are necessary for achieving the desired outcomes.
Using an open source SBOM tool is considered an industry best practice. This is because it guards against the risks associated with vendor lock-in. As a bonus, the ecosystem for open source SBOM generation tooling is very healthy. OSS will always have an advantage over proprietary in regard to ecosystem coverage and data quality because it will get into the hands of more users, which will create a feedback loop that closes gaps in coverage or quality.
Finally, even if your organization decides to utilize a software supply chain security product that has its own proprietary SBOM generator, it is still better to create your SBOMs with an open source SBOM generator, export to a standardized format (e.g., SPDX or CycloneDX), then have your software supply chain security platform ingest these non-proprietary data structures. All platforms will be able to ingest SBOMs from one or both of these standards-based formats.
Now that you understand the many reasons to generate SBOMs (whether for compliance or vulnerability analysis) using Syft to generate SBOMs is a flexible and simple process with many options to tailor SBOMs to your specific use cases. If you’d like to explore using Anchore Enterprise for its robust features like continuous visibility, SBOM monitoring, drift detection, and policy enforcement, then access a free 15 day trial here.
Save your developers time with Anchore Enterprise. Get instant access with a 15-day free trial. Generate your first Software Bill of Materials in under 10 minutes. Step-by-step guide with examples for all major programming languages. Learn the basics of Software Bill of Materials, why they're essential for modern software security, and how they fit into your development workflow.
Compare CycloneDX, SPDX, and SWID Tags formats. Understand the differences and choose the right format for your use case. Navigate industry standards and regulatory requirements including EU Cyber Resilience Act and US Executive Order on cybersecurity.
Follow our step-by-step guide to create your first Software Bill of Materials in under 10 minutes. Jump straight to implementation guides for your preferred programming language and package manager. Dependency-Track is the open source platform that over 20,000 organizations use to inventory components, find vulnerabilities, and enforce policy across the software supply chain.
Built around the software bill of materials, it tracks every component in every version of every project, and surfaces risk the moment it emerges. Ingest CycloneDX SBOMs and track libraries, containers, operating systems, firmware, and services across every version of every project in your portfolio.
Continuously match every component against multiple vulnerability sources, verify upstream integrity, and prioritize what matters with EPSS. Codify policy in an expression engine, auto-triage findings, break the build on a fail, and route alerts to everywhere your teams work.
A continuous pipeline from SBOM production to intelligent response, with no step left to chance. SBOMs are published to Dependency-Track via the REST API, CI plugins, or the web interface. Components are evaluated for security, operational, and license risk against live intelligence. The entire portfolio is continuously re-analyzed as new vulnerabilities and policy changes land.
Actionable findings flow to the tools teams already use through webhooks, chat-ops, and email. Track libraries, frameworks, applications, containers, operating systems, firmware, hardware, and services across every project. Full-stack traceability for the cloud, the enterprise, smart devices, and IoT. Bring vulnerable components to light with multiple sources of vulnerability intelligence, including the NVD, Sonatype OSS Index, GitHub Advisories, Snyk, and OSV.
Security, operational, and license policies surface risk quickly across development teams, suppliers, and partners in the supply chain. Codenamed Hyades, v5 rebuilds how Dependency-Track scales, survives failure, and reasons about risk: horizontal scaling and active/active high availability, durable processing that resumes after a crash, supply chain integrity verification, and an expression-based policy engine.
Build a complete, continuously updated record of everything you ship, from one SBOM standard. Surface vulnerabilities, integrity failures, and risk the moment they emerge, not on a periodic scan. Turn your standards into enforceable policy and the machine-readable evidence regulators now expect. The v5 redesign rebuilt the engine to stay up, never silently lose work, and run from one team to an enterprise portfolio.
Spin up a full deployment with Docker Compose. Dependency-Track 5.2 ships as separate API server and frontend container images from Docker Hub and the GitHub Container Registry. Upgrading from 4.x? v5 does not upgrade in place. Plan a maintenance window and follow the v4 to v5 migration guide . Dependency-Track is free and open source. Join the teams across more than 20,000 organizations who help shape the project.
In the rapidly evolving landscape of software development, ensuring security and compliance is paramount. A Software Bill of Materials (SBOM) has emerged as a critical tool in DevSecOps , enabling organizations to manage software components, track vulnerabilities, and ensure regulatory compliance. This tutorial provides a detailed exploration of SBOM, its integration into DevSecOps workflows, and practical guidance for implementation.
An SBOM is a structured, machine-readable inventory of all software components, libraries, and dependencies used in a software application or system. It includes metadata such as component names, versions, licenses, and origins, providing a transparent view of the software supply chain. The concept of an SBOM originated in the early 2000s as software supply chain complexity grew. Key milestones include: DevSecOps integrates security into every phase of the software development lifecycle (SDLC). SBOMs are critical because they: Flow : Code commit → CI/CD triggers SBOM generation → SBOM stored → Vulnerability scan → Alerts to DevSecOps teams.
Let’s set up Syft to generate an SBOM for a Node.js project and integrate it into a GitHub Actions pipeline. 7. Automate in CI/CD : Push the code to GitHub, and the workflow will generate and store the SBOM. A fintech company uses a Node.js application with multiple dependencies. By generating an SBOM with Syft and scanning it with Grype, the team identifies a critical CVE in an outdated Express version. They update the dependency and re-run the pipeline, ensuring no vulnerabilities before deployment.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Software%20supply%20chain • https://en.wikipedia.org/wiki/Grype • https://en.wikipedia.org/wiki/React%20%28software%29 • https://www.cisa.gov/topics/information-communications-technology-supply-chain-security/sbom • https://www.cisa.gov/resources-tools/resources/2026-minimum-elements-software-bill-materials-sbom • https://www.ntia.gov/page/software-bill-materials • https://www.kiuwan.com/blog/sbom-standards/ • https://khimananda.com/blog/sbom-generate-a-software-bill-of-materials • https://anchore.com/sbom/how-to-generate-an-sbom-with-free-open-source-tools/ • https://sbomgenerator.com/learn
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Software Bill Of Materials Generation And Vulnerability Tool.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Software Bill Of Materials Generation And Vulnerability Tool... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |