Complete Technical Paper Content — Ssh Honeypot For Credential Harvesting Detection Cowrie
Overview & System Context
Ssh Honeypot For Credential Harvesting Detection Cowrie: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5036 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Cowrie is a medium to high interaction SSH and Telnet honeypot designed to log brute force attacks and the shell interaction performed by the attacker. In medium interaction mode (shell) it emulates a UNIX system in Python, in high interaction mode (proxy) it functions as an SSH and telnet proxy to observe attacker behavior on another system. In LLM mode, it uses large language models to generate dynamic responses to attacker commands.
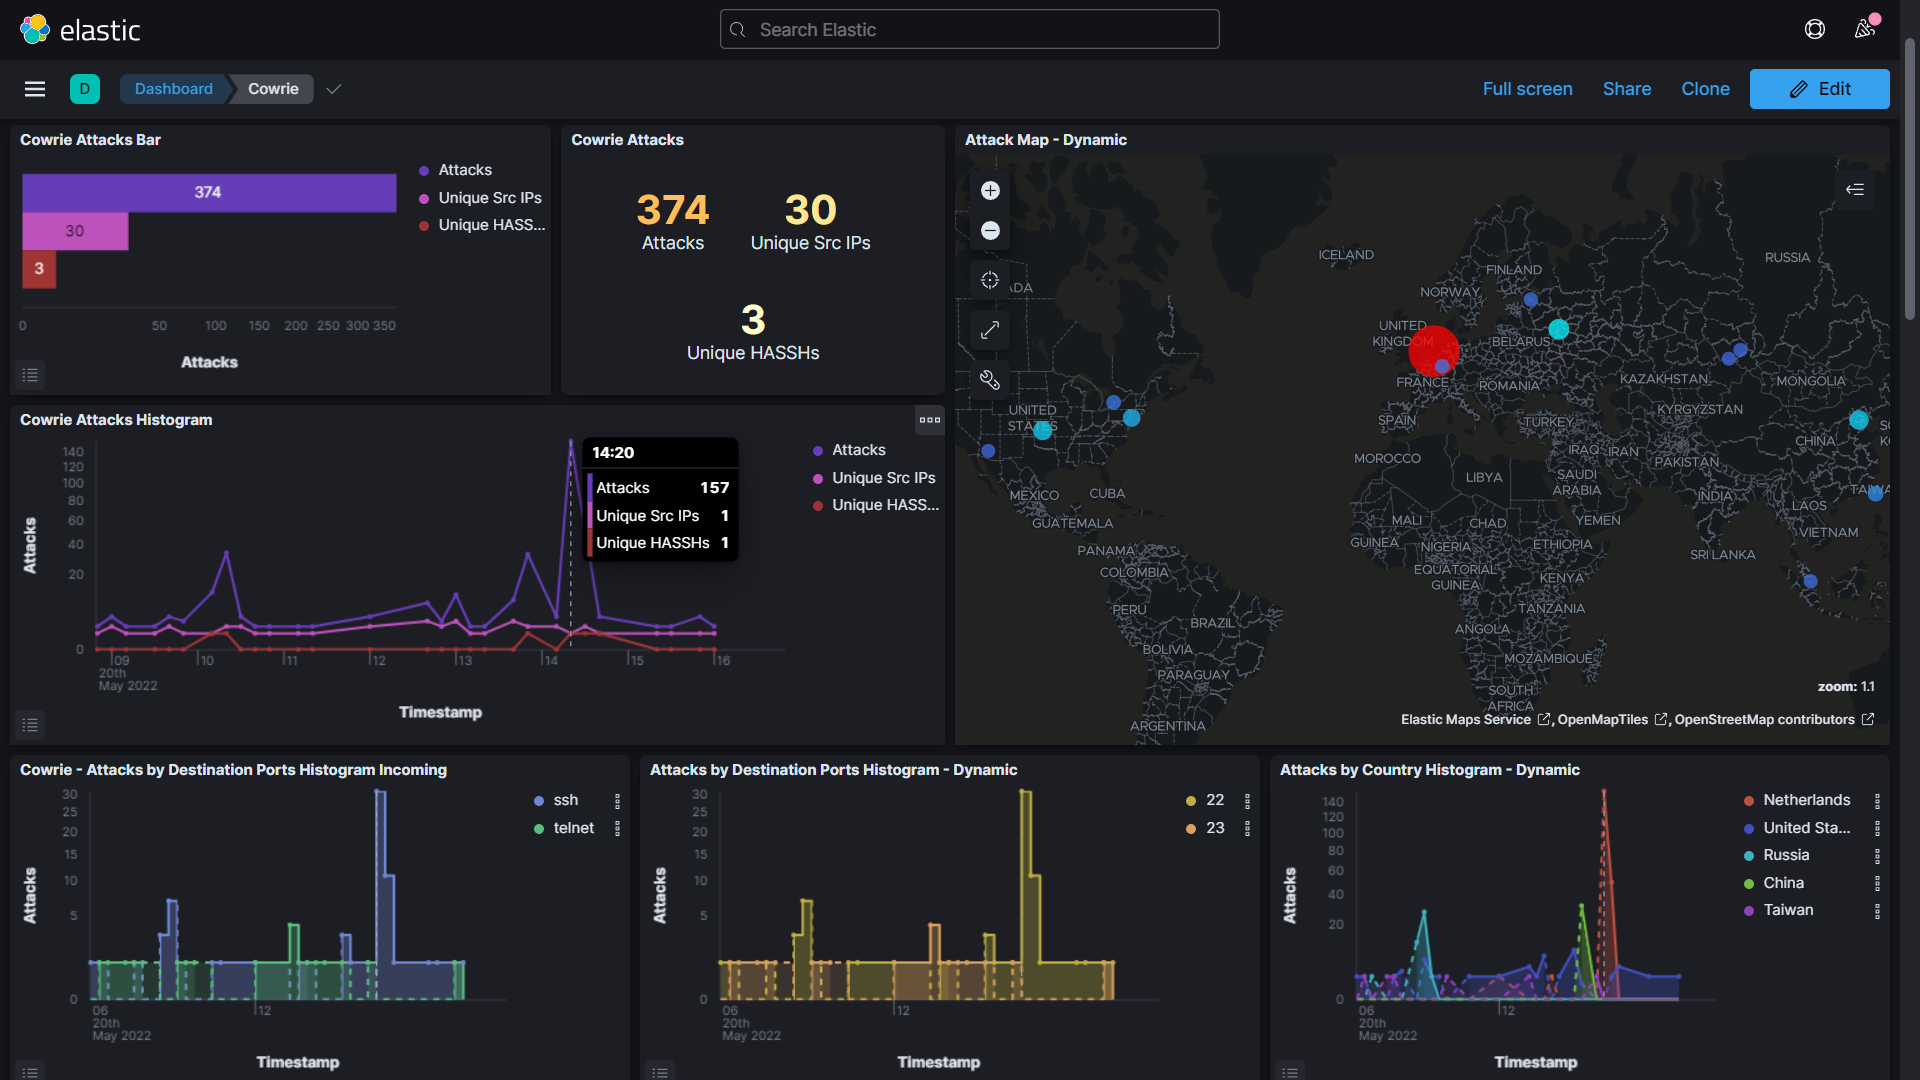
Fake filesystem with the ability to add/remove files. A full fake filesystem resembling a Debian 5.0 installation is included Possibility of adding fake file contents so the attacker can cat files such as /etc/passwd . Only minimal file contents are included Cowrie saves files downloaded with wget/curl or uploaded with SFTP and scp for later inspection Figure 1: Cybersecurity Update and Honeypot Project – Ur Tempo! Or let Cowrie manage a pool of QEMU emulated servers to provide the systems to login to Use large language models (e.g., OpenAI GPT) to dynamically generate realistic shell responses Session logs are stored in a User Mode Linux compatible format for easy replay with the playlog utility.
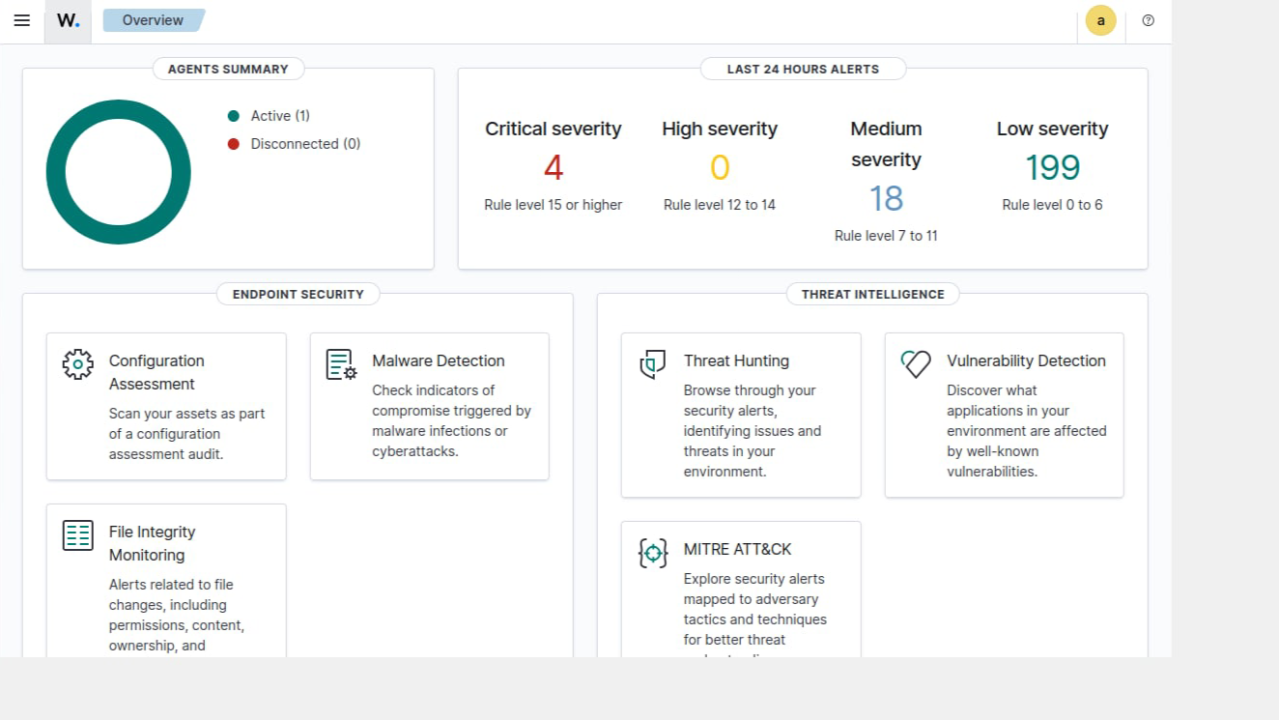
There are three ways to install Cowrie: pip , Docker, and a git checkout. For your first honeypot, pip and Docker are the easiest paths. Use a git checkout for development or advanced scenarios where you want to modify Cowrie itself. Full instructions for all three are in the installation guide . Figure 2: Security Monitoring: Building a SIEM integrated with a Cowrie SSH ...
cowrie init writes the configuration file etc/cowrie.cfg in the current directory; logs and downloads land under var/ . etc/cowrie.cfg - Cowrie’s configuration file (operator-owned). Created by cowrie init . src/cowrie/data/etc/cowrie.cfg.dist - bundled defaults, edit your etc/cowrie.cfg instead src/cowrie/data/fs.pickle - fake filesystem; carries both metadata (path, uid, gid, size, mode) and the embedded contents ( A_CONTENTS bytes) for the small files attackers commonly cat. Edit via fsctl ; rebuild via make build-fs-pickle .
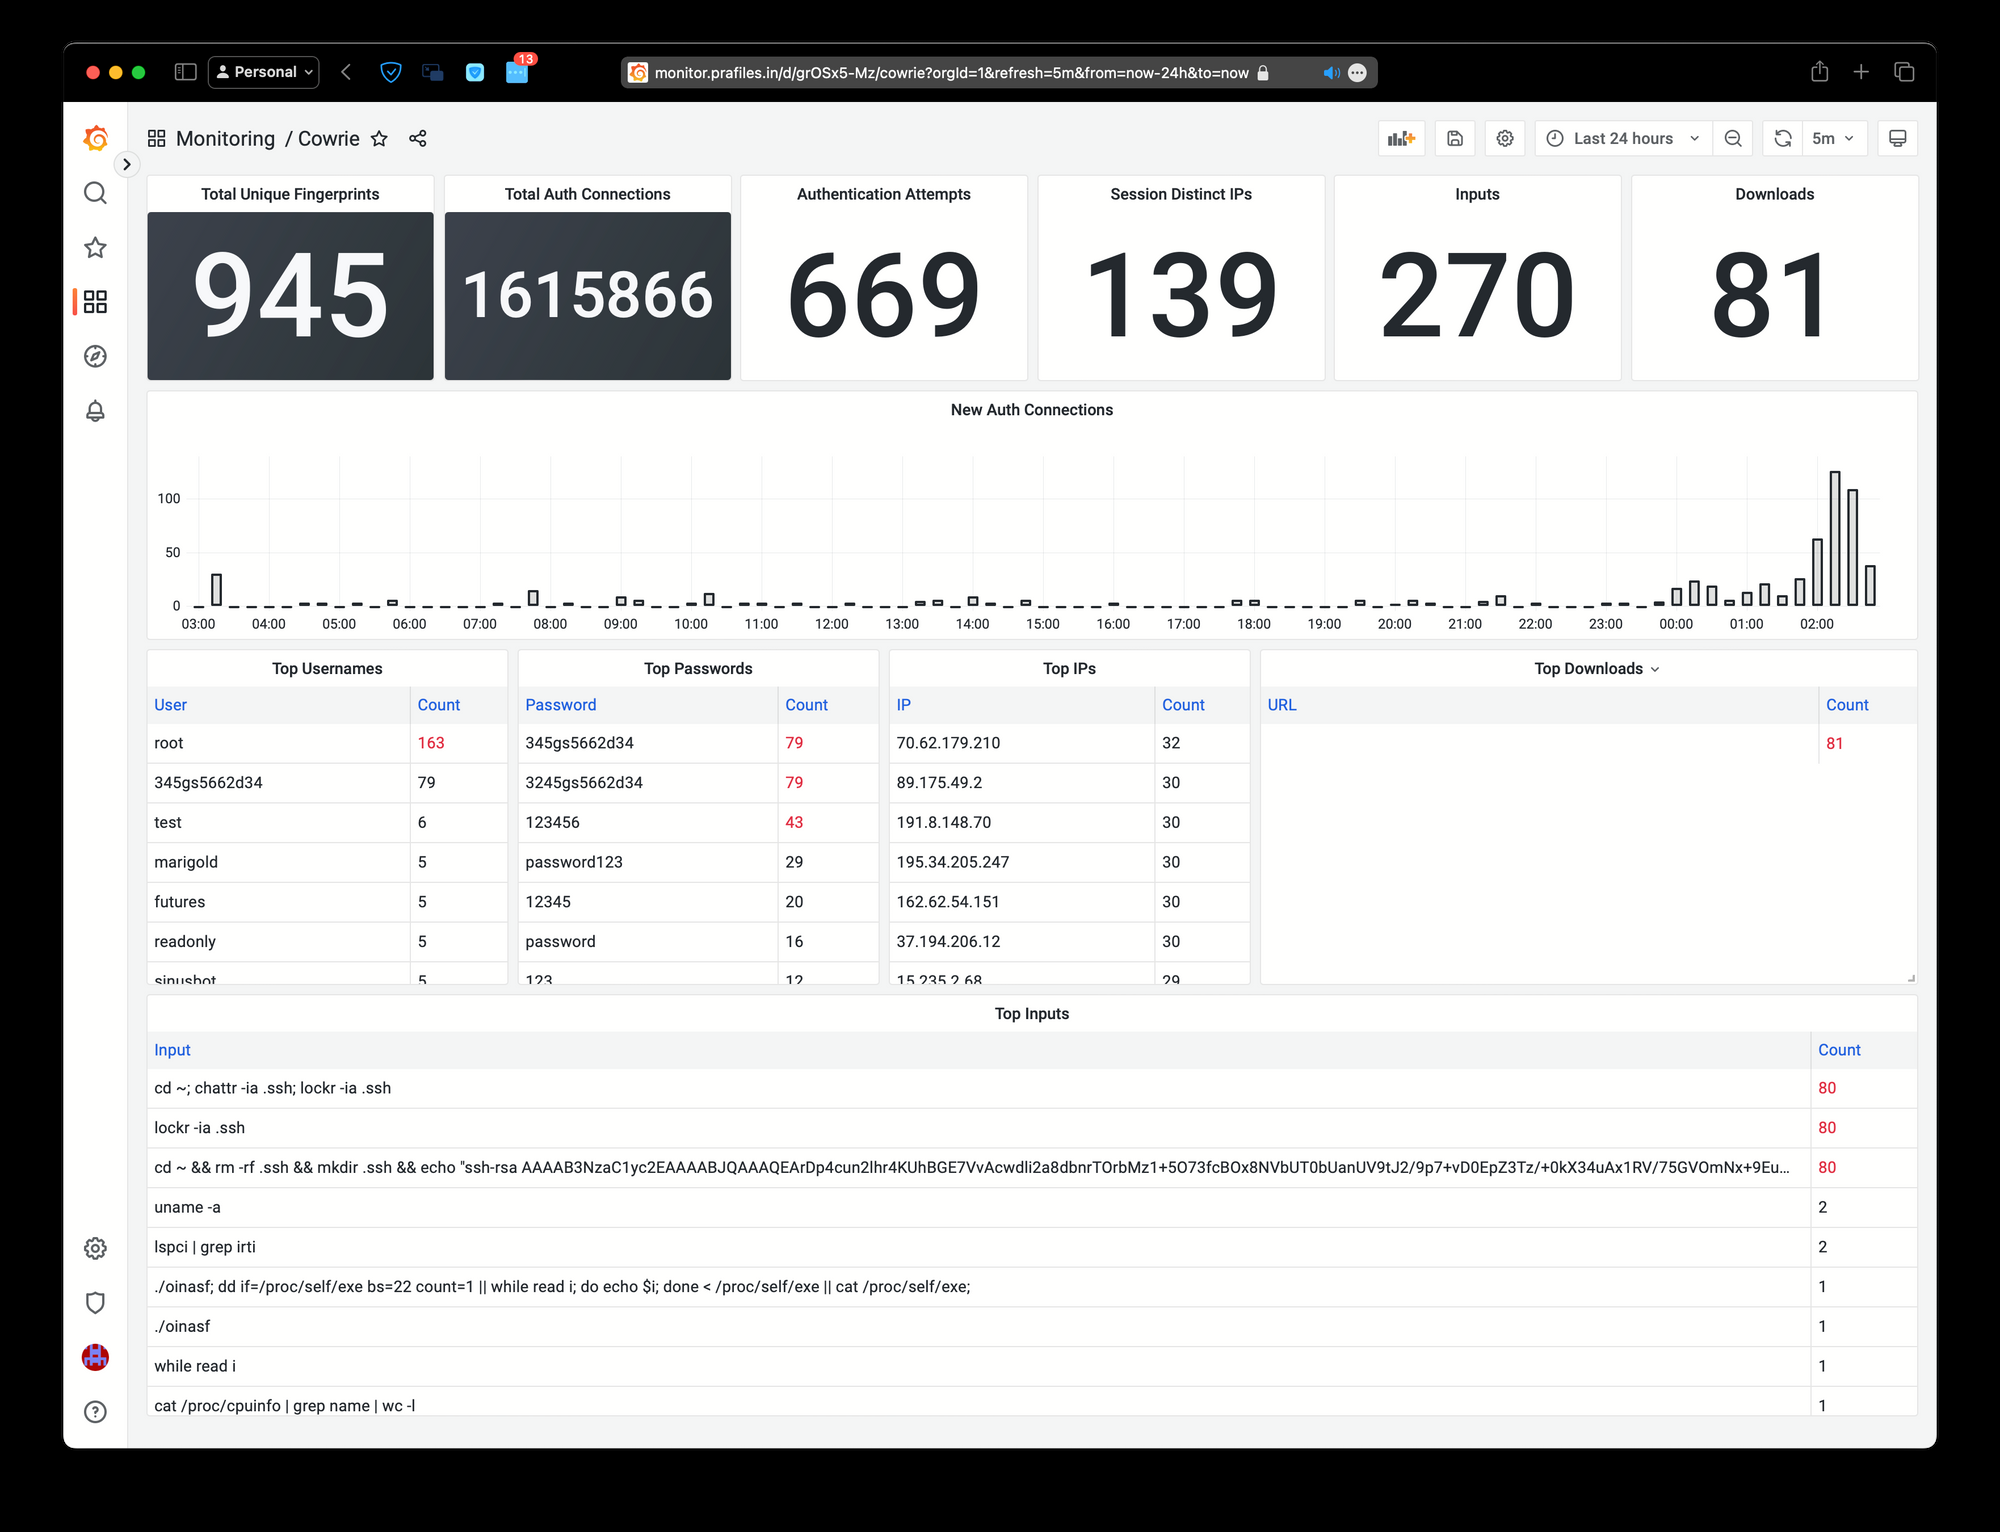
Figure 3: Cowrie as HoneyPot on my Router var/lib/cowrie/downloads/ - files transferred from the attacker to the honeypot are stored here Cowrie is a medium to high interaction SSH and Telnet honeypot designed to log brute force attacks and the shell interaction performed by the attacker. In medium interaction mode (shell) it emulates a UNIX system in Python, in high interaction mode (proxy) it functions as an SSH and telnet proxy to observe attacker behavior on another system. In LLM mode, it uses large language models to generate dynamic responses to attacker commands.
There are three ways to install Cowrie: pip , Docker, and a git checkout. For your first honeypot, pip and Docker are the easiest paths. Use a git checkout for development or advanced scenarios where you want to modify Cowrie itself. Full instructions for all three are in the installation guide . cowrie init writes the configuration file etc/cowrie.cfg in the current directory; logs and downloads land under var/ .
Cowrie pretends to be a vulnerable server. It logs brute-force logins, records every command attackers type, saves the malware they upload, and sends it all to your analysis tools as JSON. Cowrie is a medium to high interaction honeypot. It gives attackers enough to keep going and gives you a complete record of what they did.
Attackers land in an emulated shell with a fake filesystem. ls, cat, wget, busybox and dozens of other commands are imitated; nothing real is touched. Every keystroke and every byte of output is stored with timing. Replay a session later and watch exactly what the attacker saw.
Files fetched with wget or curl, or pushed with scp and sftp, are kept on disk and named by SHA-256 so duplicates collapse. Login attempts, commands, downloads, TCP forwards and session metadata are all emitted as JSON lines. Easy to grep, easy to ship. Send events straight to Elasticsearch, Splunk, MISP, Microsoft Sentinel, Graylog, MySQL, Slack and more. Enable a plugin in cowrie.cfg and restart.
Listens on SSH and Telnet. In proxy mode Cowrie forwards the session to a real backend and records it. In LLM mode a language model from OpenAI, Anthropic or a local server writes the shell output. Pip install (recommended for operators). Install the published package, cowrie init a state directory, edit etc/cowrie.cfg , start. No source checkout required.
Source checkout (developers and contributors). Clone the repo and install in editable mode. The venv lives inside the honeypot directory alongside etc/ and var/ , keeping each honeypot self-contained. The pip-install workflow described here requires Cowrie 3.0.0 or later (or the current main branch). Earlier releases need the source checkout path below.
2. System Architecture & Core Working Principles cowrie init writes ./etc/cowrie.cfg from the bundled template. On first cowrie start cowrie creates the rest of the state layout ( var/log/cowrie/ , var/lib/cowrie/ , var/run/ ) under the same directory and generates SSH host keys. Pick the directory you want state to live in before running init .
Cowrie itself is pure Python, but several of its dependencies have native components ( cryptography , cffi , bcrypt , optional mysqlclient / libvirt-python ). On most distros you need build-essential plus the OpenSSL and libffi headers for these to compile during pip install . ( docker.io is only needed if you want to rebuild fs.pickle from a Debian container via make build-fs-pickle .) Pick the directory you want cowrie state (logs, downloads, host keys, ttylogs) to live in, create the venv inside it, and install: If you plan to modify Cowrie or run against unreleased code, you also need the development extras (mypy, ruff, pre-commit, tox, sphinx, etc.) and a few extra system packages for native builds: docker.io is only required if you want to use make build-fs-pickle to regenerate the bundled filesystem from a Debian container. The [dev] extra brings in the typecheckers, linters, test runner, and docs toolchain that match what CI uses.
In source-checkout mode, the repo root is the state directory. cowrie start detects this and skips the cowrie init step. cowrie init writes ./etc/cowrie.cfg from the bundled template and creates the var/ skeleton so the first cowrie start has somewhere to write logs and a PID file. SSH host keys are generated on first start. If the config already exists, cowrie init refuses with a non-zero exit code rather than overwriting your edits — re-running cowrie init is not idempotent.
Configuration lives in ./etc/cowrie.cfg relative to the directory you run Cowrie from. The full set of available settings and their defaults are documented in the bundled cowrie.cfg.dist (also materialized by cowrie init for browsing). Later layers override earlier ones for any keys they set. Your etc/cowrie.cfg only needs to contain the keys you want to change.
Cowrie runs in the current working directory. Logs land in ./var/log/cowrie/ and the PID file is ./var/run/cowrie.pid . cowrie start refuses to run from a directory that has not been initialized. If you see ERROR: cowrie is not initialized you are probably in the wrong directory — cd into your state directory first, or run cowrie init . The SSH daemon runs on port 22 by default. Cowrie defaults to port 2222. To collect most traffic, you need Cowrie listening on 22. This requires two changes: relocate any existing SSH server, then expose Cowrie on the lower port.
Port redirection is system-wide and runs as root. A firewall redirect can make your existing SSH server unreachable — move it to a different port first. To let QEMU use disk images and snapshots, edit /etc/libvirt/qemu.conf and set both user and group to the user running the pool (typically cowrie ).
Cowrie automatically outputs event data to text and JSON log files in ./var/log/cowrie . Additional output plugins can record the data elsewhere: every [output_*] section in the bundled cowrie.cfg.dist is one plugin, covering SQL databases, SIEMs, chat notifications, threat intelligence services, and more. Setup guides for several of them are in the documentation at docs.cowrie.org (the docs/ directory of the source tree): Datadog, ELK (Elastic) Stack, Graylog, Prometheus, Azure Sentinel, Splunk, SQL (MySQL/PostgreSQL), and VirusTotal.
You ran cowrie start from a directory that does not look like a cowrie state directory. Either cd to your state directory first, or run cowrie init to set up the current directory. Two possibilities. If there is a Python stack trace, a dependency is missing or broken. Without a stack trace, double-check that you activated the right virtualenv.
Check the log file ./var/log/cowrie/cowrie.log (relative to wherever you started Cowrie). Cowrie commands operate on the current working directory — the PID file, log paths, and state files are all relative to wherever you ran cowrie start from. Stop and start commands must be issued from the same directory. If you use the SQL/Splunk/ELK output plugins, also upgrade their optional dependencies: The simulated filesystem and the default file contents that attackers see ( /etc/passwd , /etc/hostname , /proc/cpuinfo , etc.) ship inside the bundled fs.pickle . Three customization paths: Set contents_path in etc/cowrie.cfg to a directory of your choice, and drop a file at the matching path inside it: Files present in this directory override the bundled defaults at matching paths. Anything not overridden continues to come from the pickle. Only files that already exist in the pickle are visible to attackers via cat ; adding a brand-new path requires editing the pickle itself.
The bundled fs.pickle lives inside the installed Cowrie package and is read-only from an operator’s perspective. To edit it, copy it out first and point [shell] filesystem at your local copy: To regenerate the bundled filesystem from a fresh Debian container with custom packages, see bin/build-fs-pickle.sh and the make build-fs-pickle target. Paths listed in createfs.py ’s EMBED_PATHS have their bytes baked into the pickle during the build.
3. Software Implementation, Frameworks & Protocols If authentication fails, check etc/userdb.txt and confirm an allow rule exists. Rules are processed top-to-bottom and stop at the first match. Logs land in ./var/log/cowrie/cowrie.log — all recorded activity, login attempts, and shell commands.
The internet never sleeps, and neither do the armies of bots probing every exposed port they can find. To see just how noisy the background really is, I decided to spin up a honeypot ; a decoy service designed to attract attackers and record their behavior. A honeypot is a security mechanism that deliberately exposes a fake or emulated service to attackers. Instead of providing real access, it records every interaction for later analysis. The goal is not to stop attacks, but to learn from them: what credentials attackers try, which tools they use, and what payloads they attempt to deliver once they believe they’ve gained access.
For this experiment I deployed Cowrie , an SSH/ Telnet honeypot, on a VPS . Cowrie simulates an SSH/Telnet service with a working login prompt and fake shell environment. From the attacker’s perspective it looks real, but everything they type or attempt is logged safely without risk to the host system. Cowrie writes structured events to cowrie.json . With Compose named volumes , Docker prefixes the volume name with the project (e.g., root_cowrie-var ). Tail it directly on the host: Between August 24th and September 3rd, 2025 (11 days), the Cowrie honeypot recorded an onslaught of 89,109 events across 20,683 sessions , originating from 2,123 unique IP addresses .
To put that in perspective, that's nearly 1,900 connection attempts per day on average, or ~78 per hour; the "background noise" of the internet. And remember, this server wasn't advertising any services or doing anything high-profile, it was just a default SSH port open to the world, which is enough to attract constant attention from bots. SSH vs Telnet: Interestingly, even though SSH attacks were more common, a significant minority of attackers also targeted Telnet on port 23. Out of the 20,683 sessions, about 75.6% were SSH and 24.4% were Telnet. This shows that even now, some IoT malware and scanners still prod old-school Telnet services in addition to SSH. Many Mirai -like IoT botnets will cycle through both ports 22 and 23 when looking for vulnerable devices.
Each session corresponds to an attacker connecting and interacting (or not) with the honeypot. Each session can generate multiple events (e.g. login attempts, commands). Not all IP addresses were equally aggressive. Some hosts tried a handful of sessions, others barraged the honeypot non-stop. The top IPs by number of sessions initiated are listed below: Once a connection is made, the attacker’s next step is usually to attempt a login. Since Cowrie presents a fake login prompt, we get to see all the username/password combinations attackers try. Over the 11 days, the honeypot logged 12,199 login attempts in total (across those 20k sessions). These can be broken down into: Cowrie’s default behavior is to pretend that the login succeeds for some common usernames (like “root” or “admin”), which is how we ended up with thousands of successful logins. In reality, none of these are real logins to a real system, but from the attacker’s perspective they’ve hit they gained shell access, at which point Cowrie continues to record their activity. Failed attempts simply mean the honeypot told the attacker “login incorrect” and the session often ends shortly after or the attacker tries another credential.
Top Usernames and Passwords: Attackers don’t try random strings for credentials (at least not usually); they use lists of common usernames and passwords (a mix of default device credentials and popular weak passwords). Here were the top 20 usernames and passwords observed: All in all, not very surprising. On the username side, we see a lot of default account names for various systems and applications: admin , root , oracle , ftpuser , ubnt , pi , postgres , nagios, git , apache , tomcat , etc. Attackers are clearly hoping the target is some misconfigured device or application left with a default login.
On the password side, “123456” is by far the most attempted password, which sadly reflects how many real systems must still have that as a password. Other very common ones include root , abc123 , password , 1234 , 12345 , qwerty – essentially the worst passwords that any password policy would forbid, but which still appear in countless password dumps and hacker wordlists. We also see some service-specific defaults in the password list: raspberry , postgres , tomcat , etc. Attackers mix these in with generic weak passwords.
Top Username+Password Combinations: It’s interesting to look at which exact pairs of username and password are most popular. Here are the top 10 credential pairs the attackers tried (out of thousands of unique combos): Default credentials are heavily attempted. The list is dominated by identical username=password pairs (root/root, admin/admin, user/user, ubnt/ubnt, etc.) and other well-known defaults (pi/raspberry for Raspberry Pi, admin/password, etc).
Attackers are absolutely banking on the chance that the target might be an IoT device or software appliance left with factory logins. In fact, I counted at least 18 distinct username-password pairs in the dataset that were obvious vendor defaults (including the ones above). In total, about 2,475 login attempts (roughly 20% of all attempts) used some kind of default credentials (same user and pass or known default combo). The remaining ~9,700 attempts (~80%) were more general weak passwords (the dictionary approach, e.g. trying “root” with a bunch of common passwords like 123456, password, etc., or trying those weak passwords on various usernames). So there was roughly a 1:4 ratio of default-credential attacks to broader dictionary attacks. This shows a strong preference for dictionary-style brute forcing over strictly trying default logins. Attackers apparently assume that even if the device isn’t on default creds, it might have a weak user-chosen password they can guess.
The fact that root:root is still the #1 combo (211 attempts) and admin:admin not far behind tells us that, even in 2025, bots are still routinely trying the classics. This likely still pays off for them when encountering older equipment or unmaintained systems. It’s a reminder that using any of these credentials on an internet-facing system is basically guaranteeing a compromise.
When an SSH client connects, it identifies itself with a version string (like SSH-2.0-OpenSSH_8.4 or SSH-2.0-PuTTY etc.). Cowrie logged these version banners and also the cryptographic handshake fingerprints (called HASSH – a hash of the SSH client's handshake parameters). These give insight into what software or libraries the attackers are using for their SSH connections.
The vast majority of connections were not human users running OpenSSH from a terminal, but automated scripts and malware. Here were the most common SSH client identifiers seen: We can conclude that over 80-90% of the traffic was automated and tool-driven, not real interactive users. This aligns with the idea that botnets and scanners account for the bulk of internet background noise.
Corroborating this, if we look at the HASSH fingerprints (which uniquely identify an SSH client’s handshake patterns), we saw a few fingerprints dominate across many IPs: The key takeaway from these fingerprints is that the attacks are homogeneous. The same few tools (or malware families) are launching most of the attacks, just from a variety of IP addresses. This is exactly what you'd expect from botnets: each bot is an infected machine, but they all run the same attack code, hence they have identical SSH fingerprints and behaviors. It's not 2,123 independent actors with unique techniques, it's likely a handful of malware campaigns accounting for the lion’s share of the noise.
Once attackers successfully "logged in" (into the Cowrie fake shell), what did they do? Typically, the pattern is to run a series of commands to recon the system and possibly download malware. Because Cowrie emulates a shell, it captured every command issued. Across all sessions, thousands of commands were attempted. Many were repeated across different attackers, indicating automated scripts. Here were some of the most common commands or actions executed by attackers: And so on. Nearly all of these commands are automation and reconnaissance . There was very little in the way of interactive, manual exploration (which would look like a human typing different things, editing files, etc.). The attackers basically log in, the script runs a flurry of info-gathering commands within a few seconds, and then often tries to download something malicious (which we’ll cover next). If the download or further exploit succeeds (or fails), often the session just ends.
4. Practical Deployment, Analysis & Case Studies It’s interesting that none of the top commands are things like cd or vi or any manual admin tasks; it’s all "what are you" and then presumably "here's my malware payload". After recon, the logical next step for an automated attack is often to fetch a malware binary or script that will turn the compromised machine into a bot (for DDoS, cryptomining, etc). Our honeypot caught many such attempts. Cowrie intercepts and logs file download commands (like wget or curl attempts), and can even save a copy of the file (which is great for later analysis).
In the 11-day period, there were 129 file download events recorded. Many of these were repeated attempts to fetch the same files. Only a handful of unique URLs were involved – the bots were largely trying to download a few specific payloads. You can tell just by the names, these are not benign files: bins.sh , adb.sh , 1.sh , d.sh – they look like installer scripts for malware. Often, botnets use a shell script to pull down the correct binary for the infected machine’s architecture (hence the term “bins” as in binaries). For example, a script might download multiple binaries for x86, ARM , MIPS, etc., and run whichever works – this is a common tactic for IoT malware like Mirai variants.
Cowrie saved copies of some of these files. One particularly popular file had an SHA-256 hash of 1b20a210fe96e5a8abc... (truncated for brevity) and was attempted 71 times. The first time it was seen, Cowrie downloaded it (likely one of the above URLs corresponds to this hash), and thereafter for the next 70 attempts, Cowrie didn’t re-download (it marked them as duplicate attempts). This is why we had many NaN (not-a-number) entries for URL in the log; those were repeated attempts of a known file, which the honeypot handled by not pulling it again.
From an external threat intelligence perspective, at least one of these URLs was known bad. The URL 178.16.54.252/bins.sh was reported to threat databases during this timeframe as a malware distribution site threatfox.abuse.ch . In fact, it was first seen on Aug 25, 2025 and tagged as payload_delivery in ThreatFox feeds, associated with honeypot reports. This aligns perfectly with our observation, as my honeypot saw it 17 times in that period. In other words, the VPS directly witnessed an active malware campaign that researchers worldwide were also tracking.
The content of these scripts and binaries is beyond the scope of this post (and running them is dangerous), but based on naming and behavior, we can guess: The honeypot logs show these download attempts often tried to save files into directories like /tmp/ or used names like trying to drop in wget and chmod +x commands. For instance, one typical sequence (from combining log events) was an attacker doing something like: Which would, on a real system, fetch the script and execute it to infect the machine. In our case, Cowrie faked the download (even saved the file for us) and if the script ran, it would operate in Cowrie’s sandbox (likely failing to contact its C2 since outbound Internet from the container was disabled by my setup).
These were active exploitation attempts aiming to deliver malware. The presence of those specific URLs in our logs shows how quickly an exposed system gets pulled into the sights of botnets. The fact that some payloads were attempted dozens of times means either many different bots tried the same thing, or some bots retried repeatedly. On a related note, Cowrie also recorded file upload attempts (where the attacker tries to upload a file via SCP or similar).
There were a few of those in the logs as well (though far fewer than downloads). Most attackers stick to the target pulling from a URL, since it’s simpler and bypasses firewall issues. Attack volume wasn't uniform over time. Some days and hours were heavier than others. Here’s how events were distributed by day and by hour of day: Events per day: Events captured per day by the honeypot (Aug 24 – Sep 3, 2025). There was a steady drumbeat of activity each day, with a massive spike on September 1st and 2nd.
As shown above, most days saw on the order of 5,000–8,000 events. But on September 1, the honeypot logged 14,527 events , and September 2 wasn’t far behind with 13,954 . These two days saw roughly double the traffic of a typical day. This corresponds to about ~3,500 sessions on Sep 1 and ~3,300 on Sep 2, compared to ~1,000–1,500 sessions on a normal day. Something ramped up at the start of September; likely a new botnet campaign or an existing one that expanded its reach or intensified its scans at that time.
It's not uncommon, botnets often operate in cycles or when new malware variants drop, there’s a burst of scanning. The data suggests Sep 1–2 spike was a coordinated scanning wave, possibly related to the payloads we saw (maybe the bins.sh or others were part of a new malware version that started propagating then). After Sep 2, the activity came down a bit to ~10k events on Sep 3, which is still higher than the previous week’s average. It’s possible the campaign was winding down or my IP fell off the target list of some bots.
Events by hour of day (UTC): Aggregate distribution of events by hour of the day (UTC), across the entire 11-day period. Attacks happened constantly, but there was a noticeable peak in the late afternoon UTC (around 15:00), and relative lull in the early morning hours. In any case, the main point is the attacks were continuous . Even at “low” times, the server was getting hit multiple times every minute. And at peak, it could be dozens of events per minute. There was never an hour with zero attacks.
After crunching all this data, here are some of the most important lessons and insights: Running this honeypot for just 11 days provided a an in-depth look into the the internet’s constant attacks. This "background radiation" of the internet is composed of botnets crawling every IP, trying to log in with the weakest of credentials and, if successful, rope the machine into the next wave of attacks. It's frankly astonishing, though not surprising to security folks, how quickly and how widely a new server will be probed.
This project demonstrates the deployment of a Cowrie SSH honeypot in a controlled lab environment, along with attack simulation, network traffic capture, and log analysis . The goal is to observe real-world attacker behavior and gain hands-on blue-team experience. SSH services are a frequent target for brute-force and credential-stuffing attacks. Standard system logs often provide limited insight into attacker behavior and techniques.
To deploy an SSH honeypot that mimics a real server, capture attacker interactions, and analyze authentication attempts and network traffic patterns. This project is for educational and ethical cybersecurity research only . Do not deploy honeypots on production or unauthorized networks.
This project demonstrates step-by-step how to set up a Honeypot using Cowrie, an SSH and Telnet Honeypot designed to capture and log malicious activities. The purpose is to analyze attackers' behaviors in a controlled environment. Document your findings in a report and share it along with the project documentation on your GitHub. For more comprehensive analysis, integrate Honeypot logs with a SIEM platform like Splunk or QRadar.
I developed a Python script that analyzes Windows Security logs to detect suspicious login attempts. This tool filters… 5. Performance Evaluation & Extended Technical Observations I Just completed my SOC Automation Project! I In this project, I set up a Security Operations Center (SOC) with pfSense, Splunk and Kali.
https://github.com/cesursular/Soc_1_Analyst/tree/main/SOC%20Automation%20Project # SOC Automation Project ## Overview… Project Description This project demonstrates the use of popular password-cracking tools, Hashcat and John the Ripper… This project demonstrates a production-grade SSH honeypot deployment using Cowrie on Ubuntu Server 22.04, engineered to emulate a legitimate corporate file server. The honeypot systematically captures attacker behaviour, forensically documents credential-based attacks, and integrates findings into a Splunk SIEM pipeline with real-time alerting.
Key Achievement: Built a deception technology system that captured 65 events, 9 successful logins, and 7 post-login commands across 5 MITRE ATT&CK techniques — demonstrating the complete attack lifecycle from brute force to credential harvesting to malware staging in under one second. Cowrie is a medium to high interaction SSH and Telnet honeypot designed to log brute force attacks and the shell interaction performed by the attacker. In medium interaction mode (shell) it emulates a UNIX system in Python, in high interaction mode (proxy) it functions as an SSH and telnet proxy to observe attacker behavior to another system.
For more detailed instructions on using Docker in Cowrie, check :ref:`Building Docker Images
There are three ways to install Cowrie: pip , Docker, and a git checkout. For your first honeypot, pip and Docker are the easiest paths. Use a git checkout for development or advanced scenarios where you want to modify Cowrie itself. Full instructions for all three are in the installation guide . cowrie init writes the configuration file etc/cowrie.cfg in the current directory; logs and downloads land under var/ .
A honeypot is only useful if attackers believe it and you can read what they did. Cowrie is built for both. Cowrie listens on SSH and Telnet. Any login attempt is recorded; the ones you allow get a shell. The attacker sees a Debian system with a real-looking filesystem and dozens of working commands. Logins, commands, downloads, TCP forwards and the raw terminal stream are written as JSON and tty logs.
Output plugins deliver each event to your SIEM, database, chat or threat-sharing platform. Attackers get a shell inside a fake filesystem that mirrors a Debian install. Common commands are emulated in Python; ls, cat, cd, wget, curl, busybox, uname, ps and many more behave as expected. Nothing they run touches the real host. The hostname, kernel version, CPU details and file contents are all configurable, so the machine can look like whatever you want attackers to find.
A small text file controls which usernames and passwords get in. Reject the obvious ones so scanners keep guessing, accept the rest so you see what they do once inside. Every attempt, successful or not, is logged with the credentials used. Over time this is a free feed of the passwords currently being sprayed at the internet.
Cowrie stores the full terminal stream of every session with timing information. The playlog tool replays it in real time, pauses included, so you can watch a session exactly as it happened. Each command is also logged as its own event, which is what you want for searching and statistics. Files fetched with wget or curl, or pushed in over scp and sftp, are saved to disk and named by their SHA-256 hash. The same payload arriving a thousand times is stored once.
The VirusTotal output plugin can submit each new sample automatically and record the verdict alongside the session. Every event is a line of JSON with a stable eventid, the session it belongs to, the source address and a timestamp. Grep it, load it into a notebook, or let an output plugin ship it. Plugins exist for Elasticsearch, Splunk, Microsoft Sentinel, MISP, hpfeeds, MySQL, SQLite, MongoDB, Slack, Discord and more. Enable as many as you like in cowrie.cfg.
Cowrie speaks SSH and Telnet on any ports you choose. The emulated shell is the default and is safe to expose anywhere. For attackers who need more than an emulation, proxy mode forwards the session to a real system, typically a disposable VM, while Cowrie sits in the middle and records everything. Install from source, or use the official Docker image. A single small VM is enough; many people run a fleet of them and aggregate the JSON centrally.
Harvested Online Documentation & Reference Sources • https://docs.cowrie.org/en/latest/README.html • https://github.com/cowrie/cowrie • https://cowrie.org/ • https://docs.cowrie.org/en/latest/INSTALL.html • https://ambientnode.uk/running-a-cowrie-honeypot-data-and-findings • https://github.com/cyberginny/cowrie-honeypot-lab • https://www.linkedin.com/pulse/honeypot-setup-cowrie-cesur-sular-opqbe • https://github.com/MozB-lab/honeypot-ssh-cowrie-lab • https://github.com/bmnizar98/cowrie-honeypot-lab • https://github.com/micheloosterhof/cowrie-dev
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Ssh Honeypot For Credential Harvesting Detection Cowrie.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |