Complete Technical Paper Content — SSL Certificate Validation And Expiry Monitoring Tool
Overview & System Context
Ssl Certificate Validation And Expiry Monitoring Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9540 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In cryptography, a certificate authority or certification authority (CA) is an entity that stores, signs, and issues digital certificates. A digital certificate certifies the ownership of a public key by the named subject of the certificate. This allows others (relying parties) to rely upon signatures or on assertions made about the private key that corresponds to the certified public key. A CA acts as a trusted third party—trusted both by the subject (owner) of the certificate and by the party relying upon the certificate. The format of these certificates is specified by the X.509 or EMV standard.
One particularly common use for certificate authorities is to sign certificates used in HTTPS, the secure browsing protocol for the World Wide Web. Another common use is in issuing identity cards by national governments for use in electronically signing documents. The clients of a CA are server supervisors who call for a certificate that their servers will bestow to users. Commercial CAs charge money to issue certificates, and their customers anticipate the CA's certificate to be contained within the majority of web browsers, so that safe connections to the certified servers work efficiently out-of-the-box. The quantity of web browsers, other devices, and applications which trust a particular certificate authority is referred to as ubiquity. Mozilla, which is a non-profit business, issues several commercial CA certificates with its products. While Mozilla developed their own policy, the CA/Browser Forum developed similar guidelines for CA trust. A single CA certificate may be shared among multiple CAs or their resellers. A root CA certificate may be the base to issue multiple intermediate CA certificates with varying validation requirements.
In addition to commercial CAs, some non-profits issue publicly-trusted digital certificates without charge, for example Let's Encrypt. Some large cloud computing and web hosting companies are also publicly-trusted CAs and issue certificates to services hosted on their infrastructure, for example IBM Cloud, Amazon Web Services, Cloudflare, and Google Cloud Platform.
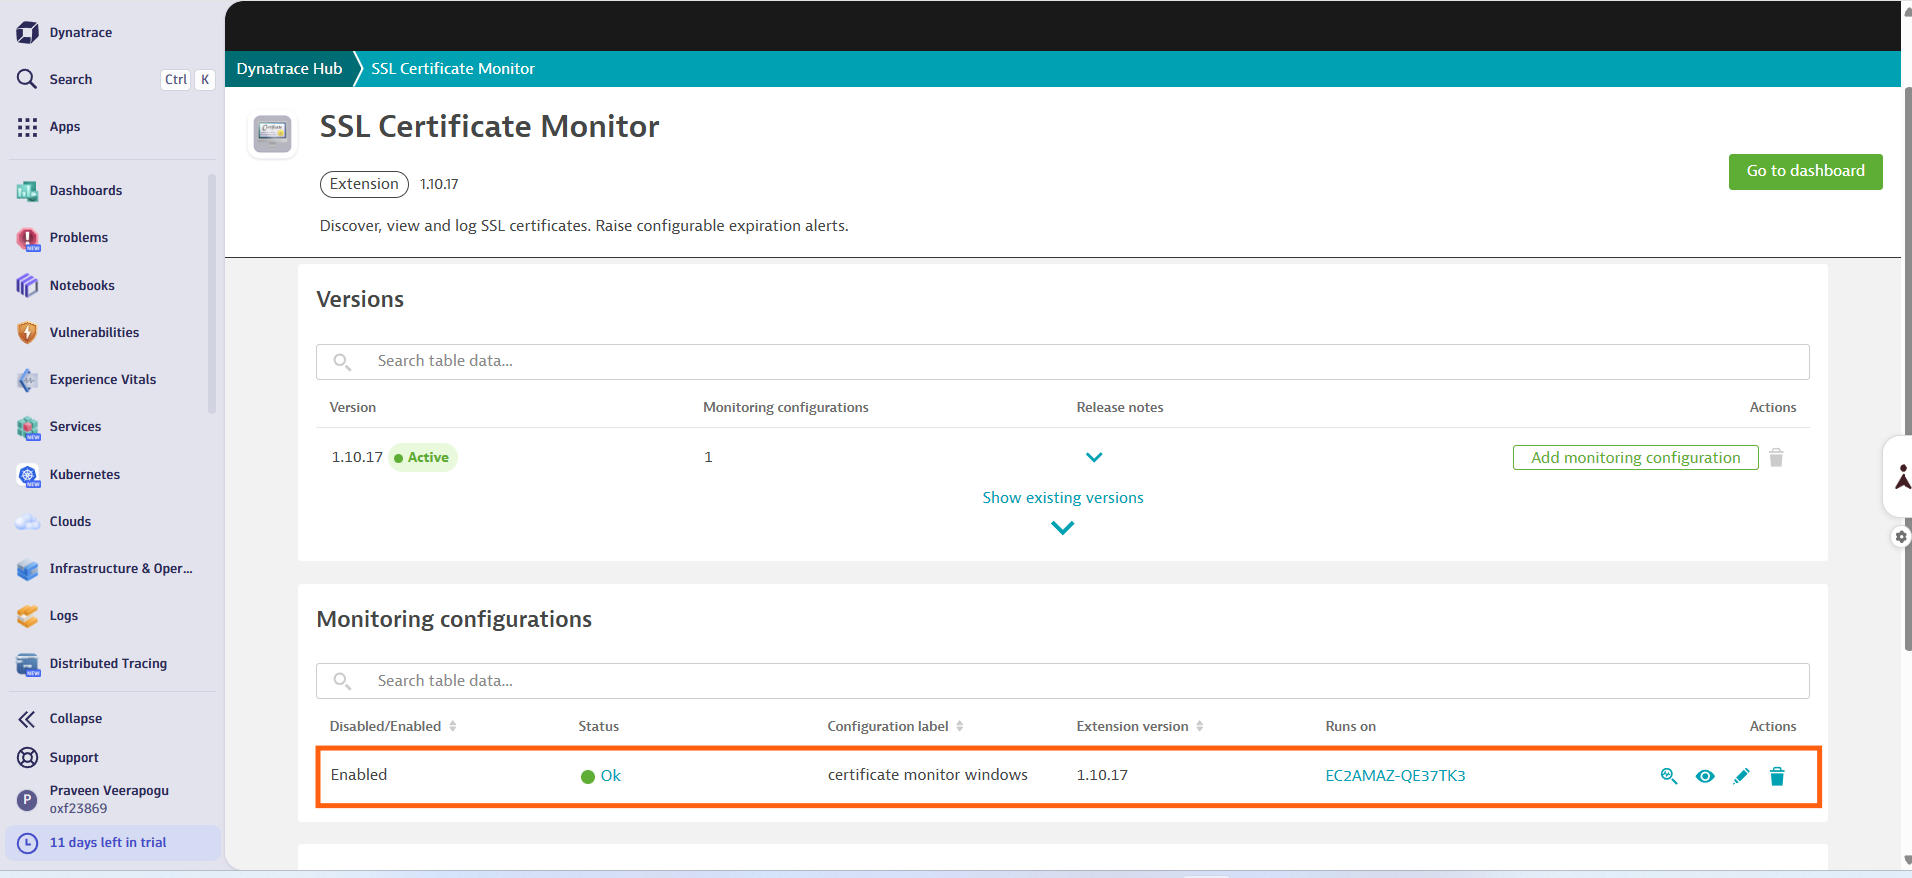
Figure 1: SSL Certificate Monitoring in Dynatrace: A Complete Guide Large organizations or government bodies may have their own PKIs (public key infrastructure), each containing their own CAs. Any site using self-signed certificates acts as its own CA. Commercial banks that issue EMV payment cards are governed by the EMV Certificate Authority, payment schemes that route payment transactions initiated at Point of Sale Terminals (POS) to a Card Issuing Bank to transfer the funds from the card holder's bank account to the payment recipient's bank account. Each payment card presents along with its card data also the Card Issuer Certificate to the POS. The Issuer Certificate is signed by EMV CA Certificate. The POS retrieves the public key of EMV CA from its storage, validates the Issuer Certificate and authenticity of the payment card before sending the payment request to the payment scheme.
Browsers and other clients of sorts characteristically allow users to add or do away with CA certificates at will. While server certificates regularly last for a relatively short period, CA certificates are further extended, so, for repeatedly visited servers, it is less error-prone importing and trusting the CA issued, rather than confirm a security exemption each time the server's certificate is renewed.
Less often, trustworthy certificates are used for encrypting or signing messages. CAs dispense end-user certificates too, which can be used with S/MIME. However, encryption entails the receiver's public key and, since authors and receivers of encrypted messages, apparently, know one another, the usefulness of a trusted third party remains confined to the signature verification of messages sent to public mailing lists.
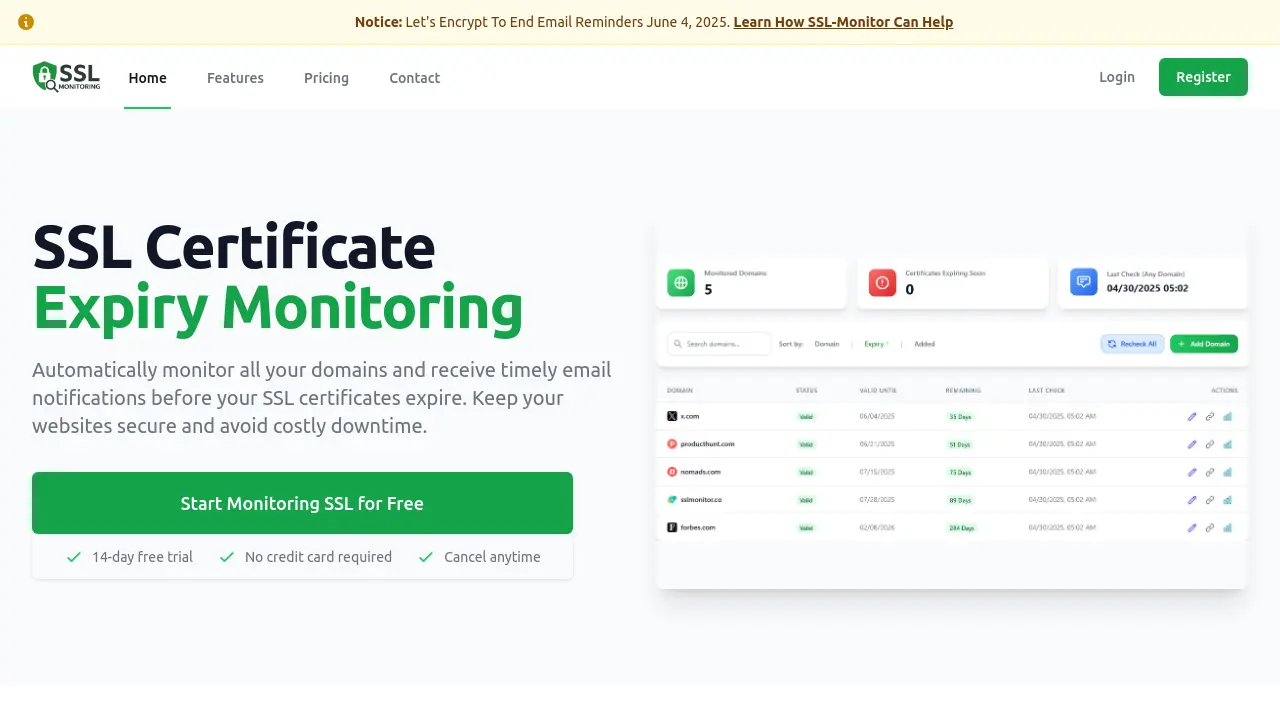
Figure 2: SSL Monitor - Effortless SSL Certificate Expiry Monitoring and Alerts However, the market for globally trusted TLS/SSL server certificates is largely held by a small number of multinational companies. This market has significant barriers to entry due to the technical requirements. While not legally required, new providers may choose to undergo annual security audits (such as WebTrust for certificate authorities in North America and ETSI in Europe) to be included as a trusted root by a web browser or operating system.
As of 24 August 2020, 147 root certificates, representing 52 organizations, are trusted in the Mozilla Firefox web browser, 168 root certificates, representing 60 organizations, are trusted by macOS, and 255 root certificates, representing 101 organizations, are trusted by Microsoft Windows. As of Android 4.2 (Jelly Bean), Android currently contains over 100 CAs that are updated with each release.
On November 18, 2014, a group of companies and nonprofit organizations, including the Electronic Frontier Foundation, Mozilla, Cisco, and Akamai, announced Let's Encrypt, a nonprofit certificate authority that provides free domain validated X.509 certificates as well as software to enable installation and maintenance of certificates. Let's Encrypt is operated by the newly formed Internet Security Research Group, a California nonprofit recognized as federally tax-exempt.
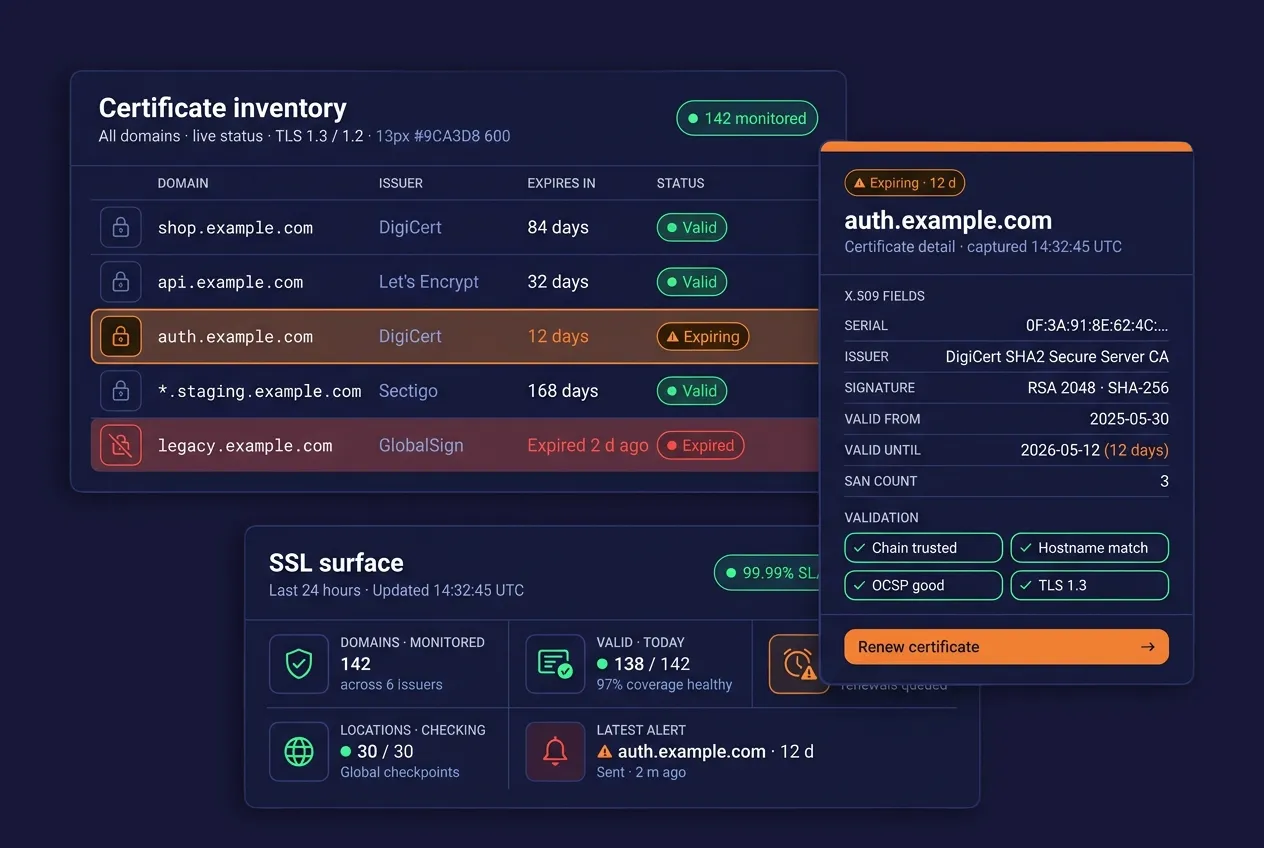
According to Netcraft in May 2015, the industry standard for monitoring active TLS certificates, "Although the global [TLS] ecosystem is competitive, it is dominated by a handful of major CAs — three certificate authorities (Symantec, Comodo CA, GoDaddy) account for three-quarters of all issued [TLS] certificates on public-facing web servers. The top spot has been held by Symantec (or VeriSign before it was purchased by Symantec) ever since [our] survey began, with it currently accounting for just under a third of all certificates. To illustrate the effect of differing methodologies, amongst the million busiest sites Symantec issued 44% of the valid, trusted certificates in use — significantly more than its overall market share." Figure 3: SSL Certificate Expiration Monitoring Tool | Dotcom-Monitor As of July 2024 the survey company W3Techs, which collects statistics on certificate authority usage among the Alexa top 10 million and the Tranco top 1 million websites, lists the five largest authorities by absolute usage share as below.
The commercial CAs that issue the bulk of certificates for HTTPS servers typically use a technique called "domain validation" to authenticate the recipient of the certificate. The techniques used for domain validation vary between CAs, but in general domain validation techniques are meant to prove that the certificate applicant controls a given domain name, not any information about the applicant's identity.
Many Certificate Authorities also offer Extended Validation (EV) certificates as a more rigorous alternative to domain validated certificates. Extended validation is intended to verify not only control of a domain name, but additional identity information to be included in the certificate. Some browsers display this additional identity information in a green box in the URL bar. One limitation of EV as a solution to the weaknesses of domain validation is that attackers could still obtain a domain validated certificate for the victim domain, and deploy it during an attack; if that occurred, the difference observable to the victim user would be the absence of a green bar with the company name. There is some question whether users would be likely to recognize this absence as indicative of an attack being in progress: a test using Internet Explorer 7 in 2009 showed that the absence of IE7's EV warnings were not noticed by users, however Microsoft's newer browser, Edge Legacy, shows a significantly greater difference between EV and domain validated certificates, with domain validated certificates having a hollow, gray lock.
Domain validation suffers from certain structural security limitations. In particular, it is always vulnerable to attacks that allow an adversary to observe the domain validation probes that CAs send. These can include attacks against the DNS, TCP, or BGP protocols (which lack the cryptographic protections of TLS/SSL), or the compromise of routers. Such attacks are possible either on the network near a CA, or near the victim domain itself.
One of the most common domain validation techniques involves sending an email containing an authentication token or link to an email address that is likely to be administratively responsible for the domain. This could be the technical contact email address listed in the domain's WHOIS entry, or an administrative email like admin@, administrator@, webmaster@, hostmaster@ or postmaster@ the domain. Some Certificate Authorities may accept confirmation using root@, info@, or support@ in the domain. The theory behind domain validation is that only the legitimate owner of a domain would be able to read emails sent to these administrative addresses.
Domain validation implementations have sometimes been a source of security vulnerabilities. In one instance, security researchers showed that attackers could obtain certificates for webmail sites because a CA was willing to use an email address like ssladmin@domain.com for domain.com, but not all webmail systems had reserved the "ssladmin" username to prevent attackers from registering it.
Prior to 2011, there was no standard list of email addresses that could be used for domain validation, so it was not clear to email administrators which addresses needed to be reserved. The first version of the CA/Browser Forum Baseline Requirements, adopted November 2011, specified a list of such addresses. This allowed mail hosts to reserve those addresses for administrative use, though such precautions are still not universal. In January 2015, a Finnish man registered the username "hostmaster" at the Finnish version of Microsoft Live and was able to obtain a domain-validated certificate for live.fi, despite not being the owner of the domain name.
A CA issues digital certificates that contain a public key and the identity of the owner. The matching private key is not made available publicly, but kept secret by the end user who generated the key pair. The certificate is also a confirmation or validation by the CA that the public key contained in the certificate belongs to the person, organization, server or other entity noted in the certificate. A CA's obligation in such schemes is to verify an applicant's credentials, so that users and relying parties can trust the information in the issued certificate. CAs use a variety of standards and tests to do so. In essence, the certificate authority is responsible for saying "yes, this person is who they say they are, and we, the CA, certify that".
If the user trusts the CA and can verify the CA's signature, then they can also assume that a certain public key does indeed belong to whoever is identified in the certificate. The rest of the communication then proceeds using the new (disposable) symmetric key, so when the user enters some information to the bank's page and submits the page (sends the information back to the bank) then the data the user has entered to the page will be encrypted by their web browser. Therefore, even if someone can access the (encrypted) data that was communicated from the user to www.bank.example, such eavesdropper cannot read or decipher it.
This mechanism is only safe if the user can be sure that it is the bank that they see in their web browser. If the user types in www.bank.example, but their communication is hijacked and a fake website (that pretends to be the bank website) sends the page information back to the user's browser, the fake web-page can send a fake public key to the user (for which the fake site owns a matching private key). The user will fill the form with their personal data and will submit the page. The fake web-page will then get access to the user's data.
This is what the certificate authority mechanism is intended to prevent. A certificate authority (CA) is an organization that stores public keys and their owners, and every party in a communication trusts this organization (and knows its public key). When the user's web browser receives the public key from www.bank.example it also receives a digital signature of the key (with some more information, in a so-called X.509 certificate). The browser already possesses the public key of the CA and consequently can verify the signature, trust the certificate and the public key in it: since www.bank.example uses a public key that the certification authority certifies, a fake www.bank.example can only use the same public key. Since the fake www.bank.example does not know the corresponding private key, it cannot create the signature needed to verify its authenticity.
a signature, contract or other record relating to such transaction may not be denied legal effect, validity, or enforceability solely because it is in electronic form; and a contract relating to such transaction may not be denied legal effect, validity or enforceability solely because an electronic signature or electronic record was used in its formation. Despite the security measures undertaken to correctly verify the identities of people and companies, there is a risk of a single CA issuing a bogus certificate to an imposter. It is also possible to register individuals and companies with the same or very similar names, which may lead to confusion. To minimize this hazard, the certificate transparency initiative proposes auditing all certificates in a public unforgeable log, which could help in the prevention of phishing.
In large-scale deployments, Alice may not be familiar with Bob's certificate authority (perhaps they each have a different CA server), so Bob's certificate may also include his CA's public key signed by a different CA2, which is presumably recognizable by Alice. This process typically leads to a hierarchy or mesh of CAs and CA certificates. A certificate may be revoked before it expires, which signals that it is no longer valid. Without revocation, an attacker would be able to exploit such a compromised or misissued certificate until expiry. Hence, revocation is an important part of a public key infrastructure. Revocation is performed by the issuing CA, which produces a cryptographically authenticated statement of revocation.
For distributing revocation information to clients, timeliness of the discovery of revocation (and hence the window for an attacker to exploit a compromised certificate) trades off against resource usage in querying revocation statuses and privacy concerns. If revocation information is unavailable (either due to accident or an attack), clients must decide whether to fail-hard and treat a certificate as if it is revoked (and so degrade availability) or to fail-soft and treat it as unrevoked (and allow attackers to sidestep revocation).
Due to the cost of revocation checks and the availability impact from potentially-unreliable remote services, Web browsers limit the revocation checks they will perform, and will fail-soft where they do. Certificate revocation lists are too bandwidth-costly for routine use, and the Online Certificate Status Protocol presents connection latency and privacy issues. Other schemes have been proposed but have not yet been successfully deployed to enable fail-hard checking.
The CA/Browser Forum publishes the Baseline Requirements, a list of policies and technical requirements for CAs to follow. These are a requirement for inclusion in the certificate stores of Firefox and Safari. On April 14, 2025, the CA/Browser Forum passed a ballot to reduce SSL/TLS certificates to 47 day maximum term by March 15, 2029.
If the CA can be subverted, then the security of the entire system is lost, potentially subverting all the entities that trust the compromised CA. For example, suppose an attacker, Eve, manages to get a CA to issue to her a certificate that claims to represent Alice. That is, the certificate would publicly state that it represents Alice, and might include other information about Alice. Some of the information about Alice, such as her employer name, might be true, increasing the certificate's credibility. Eve, however, would have the all-important private key associated with the certificate. Eve could then use the certificate to send a digitally signed email to Bob, tricking Bob into believing that the email was from Alice. Bob might even respond with encrypted email, believing that it could only be read by Alice, when Eve is actually able to decrypt it using the private key.
A notable case of CA subversion like this occurred in 2001, when the certificate authority VeriSign issued two certificates to a person claiming to represent Microsoft. The certificates have the name "Microsoft Corporation", so they could be used to spoof someone into believing that updates to Microsoft software came from Microsoft when they actually did not. The fraud was detected in early 2001. Microsoft and VeriSign took steps to limit the impact of the problem.
In 2008, Comodo CA reseller Certstar sold a certificate for mozilla.com to Eddy Nigg, who had no authority to represent Mozilla. In 2011 fraudulent certificates were obtained from Comodo CA and DigiNotar, allegedly by Iranian hackers. There is evidence that the fraudulent DigiNotar certificates were used in a man-in-the-middle attack in Iran.
In 2012, it became known that Trustwave issued a subordinate root certificate that was used for transparent traffic management (man-in-the-middle) which effectively permitted an enterprise to sniff SSL internal network traffic using the subordinate certificate. In 2012, the Flame malware (also known as SkyWiper) contained modules that had an MD5 collision with a valid certificate issued by a Microsoft Terminal Server licensing certificate that used the broken MD5 hash algorithm. The authors thus was able to conduct a collision attack with the hash listed in the certificate.
In 2015, a Chinese certificate authority named MCS Holdings and affiliated with China's central domain registry issued unauthorized certificates for Google domains. Google thus removed both MCS and the root certificate authority from Chrome and have revoked the certificates. CAs sometimes use a key ceremony when generating signing keys, in order to ensure that the keys are not tampered with or copied.
This issue is the driving impetus behind the development of the DNS-based Authentication of Named Entities (DANE) protocol. If adopted in conjunction with Domain Name System Security Extensions (DNSSEC) DANE will greatly reduce if not eliminate the role of trusted third parties in a domain's PKI. Chung, Taejoong; Lok, Jay; Chandrasekaran, Balakrishnan; Choffnes, David; Levin, Dave; Maggs, Bruce M.; Mislove, Alan; Rula, John; Sullivan, Nick; Wilson, Christo (2018). "Is the Web Ready for OCSP Must-Staple?" (PDF). Proceedings of the 53223350. Larisch, James; Choffnes, David; Levin, Dave; Maggs, Bruce M.; Mislove, Alan; Wilson, Christo (2017). "CRLite: A Scalable System for Pushing All TLS Revocations to All Browsers". 2017 IEEE Symposium on Security and Privacy (SP). pp.
Thomas (November 2022). Recommendations for Secure Use of Transport Layer Security (TLS) and Datagram Transport "Let's Revoke: Scalable Global Certificate Revocation". Proceedings 2020 Network and Distributed System Security Everything you need to understand, operate, and respond to certificate failures, from expiration tracking through incident response, organized into a single reference.
Every TLS certificate has an expiration date, and every public-facing service depends on that certificate being valid when clients connect. When expiration slips past, the failure is total and instant: browser warnings, API errors, mail server handshake failures. Certificate outages are the most scheduled failure in infrastructure, and they continue to take down production services at major companies every year.
This guide is a curated reference covering the full lifecycle: how certificate monitoring works, what to watch for besides expiration dates, how renewal operations should run, how to recover when something slips through, and where the industry is headed with shorter certificate lifetimes. The articles below are organized by stage. Start at the top if certificate management is new to you, or skip directly to the section that matches what you are dealing with right now.
Start here for the concepts, timelines, and failure modes that make certificate monitoring necessary. 2. System Architecture & Core Working Principles Expired certificates cause predictable, avoidable outages. Here is how SSL certificate expiration monitoring works and how to set alerts that fire in time.
The CA/Browser Forum has mandated a phased reduction in TLS certificate validity, reaching a 47-day maximum by 2029. Here's the timeline and impact. A working checklist for renewing TLS certificates without causing an outage. Covers planning, validation, and post-deployment verification.
Most certificate outages stem from certificates the ops team didn't know existed. Build a complete inventory using DNS, CT logs, and internal discovery. Let's Encrypt and ACME automation make certificate management nearly frictionless. But automation can fail silently, and you won't know until you're down.
A certificate just expired in production. Here's the triage order, the fastest ways to restore service, and what to document before the incident closes. Every publicly trusted certificate is logged to CT logs, so any certificate issued for your domain is public. Here's how to monitor for unauthorized issuance.
Reading about certificate failures is useful; continuous monitoring is what prevents the outage. Between automated renewal (which fails silently often enough to matter) and the certificates on internal infrastructure that external tools cannot see, the practical requirement is a monitoring layer that validates every certificate, every chain, every backend, on a schedule. Generator Labs Certificate Monitoring tracks expiration, chain integrity, hostname matching, revocation status, CA trust, and fingerprint changes across public and internal infrastructure. Configurable alert thresholds give you lead time before any certificate causes a visible failure. On-premise agents extend the same coverage inside private networks without exposing anything externally.
For the numbers behind all of this, the white paper When Certificates Expire collects seven years of public expiry incidents and the 47-day lifetime schedule, and the case study Automated, and Still Expired shows what happens when renewal automation runs without a backstop. Both are free PDFs. Monitor every certificate across your infrastructure, automatically. Pay-per-host pricing starts at $0.01 per host per day. No contracts, no minimums.
As browsers push for universal encryption, SSL/TLS certificates have become the foundation of internet trust. However, installation is only the first step. Without a robust lifecycle strategy, organizations face service outages, security vulnerabilities, and a sharp decline in search engine rankings. This guide explores the essential components of SSL certificate management, the risks of negligence, and how to implement a strategy that ensures your site remains secure and accessible.
SSL/TLS certificate management is the continuous process of overseeing a certificate’s entire lifecycle—from the initial Certificate Signing Request (CSR) and CA issuance to deployment, expiration tracking, and renewal. Effective management ensures every certificate in your infrastructure remains valid, correctly configured, and compliant with modern security standards.
Historically, SSL certificates were valid for several years, but validity periods have been steadily decreasing. Since September 2020, major browsers have limited certificate validity to 398 days (13 months), down from the previous 825-day (27-month) limit established in March 2018. Industry discussions continue around further reducing validity periods to encourage automation and improve security posture.
This shift has significantly increased renewal frequency – organizations managing certificates that previously lasted 2-3 years now face renewal cycles roughly every 13 months, increasing administrative overhead by 2-3x. If you manage dozens or hundreds of domains, the probability of a “human error” leading to an expired certificate increases exponentially. An expired certificate results in the dreaded ‘Your connection is not private’ warning. This warning creates a major obstacle for users, causing most to abandon the site, which severely impacts traffic, conversions, and user trust.
To manage SSL certificates effectively, it is vital to understand that they do not exist in a vacuum. They are the visible “end-entity” of a broader system known as Public Key Infrastructure (PKI) . PKI is the framework of hardware, software, and policies required to create, manage, and revoke digital certificates. Understanding the hierarchy of trust is essential for troubleshooting “untrusted connection” errors that often plague poorly managed environments.
Every SSL/TLS certificate relies on a Chain of Trust to be validated by a browser. This chain typically consists of three layers: Effective SSL certificate management requires managing this entire chain. A common point of failure in manual management is forgetting to install the Intermediate Certificate on the web server. While some browsers may attempt to fetch missing intermediate certificates through AIA (Authority Information Access), this behavior is inconsistent and unreliable. All clients – including browsers, API clients, and security scanners – should receive the complete certificate chain from the server to ensure reliable validation. Missing intermediate certificates will cause these clients to report the connection as untrusted.
While most discussions around SSL certificate management focus on public-facing websites, enterprises must also manage a vast “hidden” ecosystem of internal certificates. Understanding the distinction between Public and Private PKI is critical for a holistic security strategy. These are certificates issued by a publicly trusted Certificate Authority (CA) like DigiCert, Sectigo, or Let’s Encrypt.
These are issued by an internal CA, such as Microsoft Active Directory Certificate Services (AD CS) or an internal HashiCorp Vault. Managing both types simultaneously creates a “visibility gap.” Public-facing monitoring tools can effectively monitor external certificates accessible from the internet, but internal certificates require monitoring solutions deployed within the network perimeter to access internal endpoints and services.
Effective SSL certificate management requires a unified view that monitors both public endpoints and internal infrastructure to ensure no link in your security chain is forgotten. To manage certificates effectively, you must treat them as a continuous cycle rather than a “set it and forget it” task. This begins with generating a Certificate Signing Request (CSR) and choosing the right validation level (Domain Validated, Organization Validated, or Extended Validation). Once issued, the certificate must be correctly installed on the web server, ensuring the intermediate chain is intact to prevent “untrusted” errors.
A major hurdle in SSL certificate management is ensuring the certificate format matches the destination server’s requirements. Different operating systems and web servers use specific file extensions and encoding styles. Effective management requires knowing the “home” of every certificate in your infrastructure. Common storage locations include: By tracking not just the expiration dates, but also the format and server type , your team can reduce “Mean Time to Recovery” (MTTR) if a certificate needs to be re-issued or moved during an emergency.
You cannot manage what you cannot see. A centralized inventory records metadata for every certificate, including its expiration date, issuing CA, and server location. Crucially, it should also track information *about* the associated private key—such as its storage location and cryptographic strength—but should **never** store the private key itself. This is the most critical phase. Renewal should ideally happen 30 days before expiration. This buffer allows for troubleshooting if the validation process hits a snag or if there are configuration issues on the server.
Management also involves ensuring that all certificates use modern cryptographic standards (such as RSA 2048-bit or ECC keys) and that legacy, insecure protocols like TLS 1.0 or 1.1 are disabled across your environment. Organizations typically choose between manual and automated workflows depending on their scale. While certificate management platforms handle issuance and deployment, external monitoring services provide validation from the end-user perspective. Evaluating the best SSL certificate monitoring tools allows organisations to detect issues like incomplete certificate chains, hostname mismatches, and server misconfigurations that might not be apparent from internal systems.
Manual management involves using spreadsheets or calendar reminders to track expiration dates and manually updating server files. Automation uses protocols like ACME (Automated Certificate Management Environment) to handle the entire lifecycle without human intervention.
Cloud providers like AWS (ACM), Google Cloud, and Azure offer integrated certificate management for resources within their ecosystems. Ideal for organizations that are “all-in” on a specific cloud provider and want to reduce the friction of certificate deployment. These tools often only manage certificates used within that specific cloud environment, potentially creating a blind spot for on-premise servers or other cloud providers.
Dotcom-Monitor serves as a robust SSL certificate monitoring tool and safety net, ensuring your website always stays trusted and accessible from dozens of locations worldwide. While internal tools handle the background updates, we watch your site from the outside, exactly as your customers see it. We monitor your security from dozens of locations worldwide to catch small setup errors before they turn into “Not Secure” warnings. Instead of waiting for a visitor to find a problem, you’ll get an alert the moment your site isn’t fully protected. It’s the easiest way to prevent downtime and keep your brand safe without the headache of manual checks.
Matthew Schmitz is Director of Load and Performance Testing at Dotcom-Monitor, where he leads the team developing LoadView’s cloud-based load testing platform. He joined Dotcom-Monitor in 2012 and has worked in software engineering and performance testing since 2004. His work focuses on realistic load testing, capacity planning and preparing applications for peak traffic.
The best network monitoring software depends on where you need to see from. For switch, router and interface data, use an SNMP and flow tool A 200 response does not mean your PDF loaded. See how to monitor embedded PDF viewers with scripted checks, content assertions, and smart alerting.
Your cloud provider’s monitoring runs inside the failure domain it watches. Here’s what to test before you pick a monitoring tool. Prevent silent phone line outages. Learn how operations teams use SIP checks and inward-dialing tests to keep customer lines running smoothly.
How external synthetic monitoring meets DORA’s detection and availability obligations, mapped requirement by requirement. 3. Software Implementation, Frameworks & Protocols At 08:00, the certificate renewal job reports success, but the public endpoint still serves an expired certificate from one region. SSL monitoring catches that mismatch before browsers begin blocking customers, while basic uptime checks continue reporting “up.” This guide explains how certificate checks work, which TLS details matter, and how to build alerts that distinguish real expiry risks from harmless configuration changes.
You will learn how to monitor certificate validity, chain trust, hostname coverage, protocol behavior, and renewal workflows. You will also see how to combine certificate checks with response time, port, DNS, and multi-location tests without creating an alert stream nobody trusts. SSL monitoring is the automated checking of a TLS-enabled service to confirm that its certificate remains valid, trusted, correctly configured, and available to intended clients.
A useful check does more than compare the certificate’s expiration date with today’s date. It connects to the endpoint, performs a TLS handshake, validates the presented chain, checks the hostname, records certificate details, and reports remaining validity time. For example, suppose payments.example.com uses a certificate that expires in 18 days. A simple expiry reminder may report no problem. A deeper check could find that the server omits an intermediate certificate, one load balancer still serves the previous certificate, or a certificate covers www.example.com but not the payment hostname.
These checks overlap, but none replaces the others. A server can accept connections on port 443 while presenting an expired certificate. It can also have a valid certificate while returning a slow or broken application response. The TLS handshake itself follows standards described in RFC 8446 , while browser-facing certificate behavior depends on X.509 and public trust rules. In practice, teams should treat SSL monitoring as one layer within external service monitoring, not as a substitute for exploring server health monitoring .
The monitoring service resolves the target domain through DNS before connecting. This matters because different records may send users to different addresses, regions, or providers. If the name resolves to the wrong host, later certificate results may describe an unintended system. Skipping this step hides DNS failover problems and stale records. A certificate can look correct on one address while another address serves an expired or unrelated certificate.
The checker connects to the configured port, usually 443 for HTTPS. It may also test other TLS services, such as SMTPS, IMAPS, APIs, or custom application ports. The port matters because one service can expose several certificates. If the monitoring target uses the wrong port, the check may pass against a management service while the customer-facing endpoint remains broken.
Modern hosting commonly uses Server Name Indication, or SNI. The checker must send the intended hostname during the TLS handshake so a shared server returns the correct certificate. A check that omits SNI may receive a default certificate. That creates a false failure, but it can also reveal a real problem for older clients or misconfigured integrations.
The service checks the certificate’s dates, hostname coverage, signature, issuer chain, and trust path. It should report whether the chain works from the monitoring environment, not merely whether a certificate file exists on a server. Skipping chain validation misses a common deployment failure: the leaf certificate is fresh, but the intermediate certificate is absent or incorrect.
A complete monitor may check supported TLS versions, handshake errors, redirects, HTTP status, and response time. For an API, it can request a health endpoint instead of downloading a full page. If you only inspect certificate metadata, you can miss a service that has a valid certificate but fails after the handshake. That distinction matters during incidents.
The monitoring system stores certificate identity, expiration, issuer, chain details, and response behavior. It then applies warning and critical thresholds. Without history, teams cannot tell whether a new certificate was expected, whether only one location changed, or whether a renewal process has repeatedly failed. Historical data turns a raw alert into an actionable incident.
Consider a realistic deployment. A company renews its certificate through an automated certificate authority. The primary load balancer updates correctly, but an older regional node keeps the previous certificate. A single-location check may pass. Multi-location SSL monitoring exposes the split state, while certificate fingerprints and endpoint addresses help engineers find the stale node.
For background on certificate structure and browser validation, MDN’s TLS documentation is a practical reference. The X.509 overview on Wikipedia also explains the certificate model, though operational decisions should follow current vendor and standards documentation. The strongest monitoring systems focus on failure modes that affect users, not just fields displayed in a certificate viewer.
Why: Renewal jobs fail for mundane reasons: missing permissions, rate limits, incorrect challenge records, or a stopped service. A 30-day warning gives teams time to investigate. A one-day warning often becomes an emergency. Practical tip: Use different thresholds for public websites, internal services, and certificates requiring manual approval. We typically set an early warning around 30 days and a higher-priority alert around seven days, then adjust for the organization’s renewal process.
What: The check verifies that the requested hostname appears in the certificate’s Subject Alternative Name list. Why: A wildcard certificate for *.example.com does not normally cover example.com , and it does not cover deeper names such as api.eu.example.com . Practical tip: Monitor every customer-facing hostname separately. Do not assume that monitoring the apex domain proves coverage for API, checkout, admin, or regional domains.
What: The monitor validates the complete chain from the server certificate to a trusted root. Why: Developers often deploy only the leaf certificate. Some desktop browsers may recover through cached intermediates, while mobile clients, Java applications, or embedded devices fail immediately. Practical tip: Test from outside the issuing network and include the actual client trust requirements. A chain trusted by one operating system may fail on another.
What: The monitor records changes to serial numbers, fingerprints, issuers, or public keys. Why: Certificate replacement can be legitimate, but unexpected changes may indicate a failed deployment, an incorrect load balancer, or a security incident. Practical tip: Alert on unexpected identity changes, but provide a maintenance process for planned renewals. Fingerprint alerts without change management quickly become noise.
What: The monitor tests whether the endpoint negotiates acceptable TLS versions and detects handshake failures. Why: A certificate may be valid while the server supports only obsolete protocols or incompatible cipher suites. Conversely, a security hardening change may break older clients. Practical tip: Separate certificate alerts from protocol-policy alerts. The owner and response path may differ.
Why: DNS, CDNs, geolocation, and regional load balancers can produce different results. One location passing does not prove global correctness. Practical tip: Use locations that reflect real users and infrastructure boundaries. A check from one cloud region cannot validate every traffic path.
What: The monitoring workflow connects certificate expiry to the renewal and rollout process. Why: Renewal and deployment are separate operations. A certificate can be renewed successfully on disk while the running proxy continues serving the old file. Practical tip: Pair external checks with server performance monitoring and service logs. External evidence shows customer impact; internal evidence shows why it occurred.
SSL monitoring is most valuable when certificate failure creates customer impact, contractual risk, or difficult diagnosis. A team with a single disposable development endpoint may not need a dedicated certificate monitor. A local test service can often rely on the deployment pipeline and a manual check, provided it cannot affect production users. Early warnings create time for investigation and replacement. The concrete outcome is fewer incidents where customers see browser security errors before an engineer knows the certificate expired.
A business with manual approval steps may need more lead time than a team using fully automated renewal. The right threshold follows the slowest part of the process. Certificate checks separate TLS failures from application failures. When HTTP monitoring reports an outage, engineers can quickly determine whether the issue involves DNS, port access, the handshake, certificate trust, or the application itself.
That reduces the common mistake of restarting application servers when the real issue sits on a proxy or certificate chain. Multi-location results show whether a problem affects every user or only one traffic path. This matters for teams using CDNs, geo-based DNS, or regional load balancers. 4. Practical Deployment, Analysis & Case Studies A single failing location may indicate routing drift rather than a global certificate failure. That changes both urgency and the team responsible.
Historical certificate data reveals whether renewals complete on schedule and whether deployments reach every node. Teams can measure the time between replacement and external verification rather than trusting a local job log. This is especially useful for managed services with many domains and different customer owners. A well-designed policy can group repeated failures, delay escalation during transient errors, and notify the correct team. The result is fewer duplicate messages and better attention to confirmed incidents.
Zuzia.app describes intelligent notification filtering as part of its monitoring approach; teams should still define ownership, severity, and escalation rules before enabling alerts. Organizations that promise uptime or secure transport need evidence from outside the production environment. External records support incident reviews, service reports, and conversations with customers.
This does not prove every user had the same experience, but it gives a defensible record of observed endpoint behavior. Compare monitoring services against operational behavior, not the number of checks listed on a feature page. A five-minute interval may suit ordinary certificate expiry. High-risk payment or API endpoints may need faster detection for handshake and response failures.
Ask whether the advertised interval applies to every monitor, every location, and every plan. “Real time” often means event processing after a check, not continuous connection testing. A useful service should support more than one certificate type and endpoint pattern. Confirm support for HTTPS, custom TLS ports, mail services, APIs, IP-based targets, SNI, redirects, and wildcard-related hostname checks.
Do not assume that a website monitor performs complete certificate validation. Read the provider’s check documentation. Look for email, mobile notifications, SMS, voice calls, chat tools, incident systems, and webhooks when your team needs them. Confirm whether recurring notifications stop after acknowledgement or continue until recovery. The important question is not how many integrations exist. It is whether an alert reaches the person who can renew or deploy the certificate.
The provider should document probe locations, source addresses, allowlisting needs, and maintenance behavior. This matters when firewalls permit only known monitoring IPs. A location-specific failure can be caused by blocked probes rather than a service outage. Clear probe information makes that distinction easier.
At minimum, results should show expiration, issuer, hostname coverage, chain errors, handshake errors, status code, response time, and observed location. A red “down” state without diagnostic detail forces engineers to repeat the investigation manually. An API helps teams create monitors from infrastructure definitions, review certificate inventory, and connect events to existing workflows. Export options help during audits and incident analysis.
Verify authentication, rate limits, event history, and whether changes can be made safely through automation. Free tiers and monitor counts can be useful for evaluation, but count more than domains. One service may need separate monitors for web, API, mail, regions, ports, and certificate identity. Also check seats, notification recipients, retention, and location limits. Exact allowances vary by provider, so read current service documentation before planning an estate.
The following values are starting points, not universal rules. Adjust them to match renewal lead time, ownership, and customer impact. A solid production setup typically includes one monitor for each important hostname, at least two external locations, a certificate warning threshold, a critical threshold, and an HTTP check after TLS negotiation. It also has a named owner, a renewal runbook, and a test renewal performed before the first emergency.
For internal hosts, you may need allowlisting or a private probe. Do not expose an administrative endpoint publicly just to make external monitoring possible. Where internal visibility matters, pair an agent with external monitoring for the public boundary. Teams managing the underlying machines should also review guidance on Linux server monitoring and server resource monitoring . Certificate failures often surface during resource, disk, permission, or service problems.
False positives usually come from a mismatch between the test and the real client path. First, retry a failed check from the same location. A single failed handshake should normally create a pending event, not an immediate major incident. The retry delay should be long enough to avoid repeating the same packet loss, but short enough to detect a real outage.
Second, confirm from another location. Two independent failures provide stronger evidence than one probe reporting an error. However, do not require every location to fail before alerting. A regional outage can be serious even when the primary region works. Third, separate alert types. Expiry, chain trust, hostname mismatch, protocol failure, HTTP status, and response time should not all produce the same message. Each has a different likely owner and recovery action.
Fourth, preserve evidence. Store the resolved address, location, certificate subject, issuer, serial number, fingerprint, expiration, TLS version, HTTP status, and response time. Without these details, engineers cannot tell whether the service changed or the monitor behaved differently. Finally, verify recovery. An alert should close only after a successful check meets the same conditions that caused the failure.
Do not clear a certificate incident merely because the port accepts connections again. For high-value services, run a controlled certificate replacement in a staging or canary environment. Confirm that the monitor detects the expected change, reports the new expiration date, and does not alert incorrectly during the rollout. This test validates the monitor and the runbook together.
Mistake: Monitoring only the main website and ignoring API or checkout hostnames. Consequence: The homepage works while logins, payments, or integrations fail. Fix: Inventory every public TLS hostname and assign separate checks where behavior differs. Mistake: Treating certificate expiry as the only certificate risk. Consequence: Missing intermediates, hostname mismatches, and regional certificate drift cause unexpected failures. Fix: Enable chain, hostname, handshake, and multi-location validation.
Mistake: Alerting at one day before expiration. Consequence: A failed renewal becomes an emergency with little time for approval or propagation. Fix: Start with a 30-day warning and a seven-day critical alert, then tune from actual recovery times. Mistake: Running checks from one location. Consequence: Regional load-balancer and DNS problems remain invisible. Fix: Use multiple independent locations and compare resolved addresses.
Mistake: Sending every failure directly to the whole team. Consequence: Repeated alerts create fatigue, and important incidents receive less attention. Fix: Separate severity, assign owners, retry transient failures, and escalate only when conditions persist. Mistake: Trusting the renewal job log without checking the public endpoint. Consequence: The certificate updates on disk but not in the running proxy or every node. Fix: Verify externally after deployment and record certificate identity from each serving path.
Mistake: Ignoring custom TLS services. Consequence: Mail, database, VPN, or partner integration endpoints expire without warning. Fix: Include non-HTTP TLS ports where certificate failure affects operations. Mistake: Suppressing alerts during every deployment. Consequence: A genuine certificate or routing failure can hide inside a long maintenance window. Fix: Keep windows narrow, document expected changes, and verify recovery immediately afterward.
Monitor the user-facing hostname, not only the server address. The hostname controls SNI, certificate selection, DNS routing, and the client-visible result. Treat renewal and deployment as separate controls. A certificate authority may issue a new certificate, but the proxy still needs to load it. Validate both events.
Keep certificate alerts separate from uptime alerts. This preserves useful diagnosis and sends the issue to the right owner. Use two or more external locations for important services. Location diversity reveals routing and regional failures that one probe cannot see. Record certificate identity changes. Issuer, serial number, fingerprint, and public key changes deserve review when they were not planned.
Test the alert path, not just the monitor. A perfect check is useless if the message goes to a retired mailbox or an unmonitored chat channel. Pair external checks with internal resource data. Disk exhaustion, stopped proxy processes, and failed renewal hooks often explain external certificate symptoms. For Linux environments, teams can also review how to monitor server performance .
5. Performance Evaluation & Extended Technical Observations Document the fastest safe rollback. During a certificate incident, engineers need to know which proxy, secret, ingress object, or load balancer requires correction. SSL monitoring checks certificate expiration, hostname coverage, chain trust, TLS handshake behavior, and often HTTP response health. It can also record issuer, serial number, fingerprint, protocol, location, and response time. The exact checks depend on the provider and monitor type.
A certificate expiry alert should usually fire at least 30 days before expiration for production services. Teams with manual approvals, external vendors, or long change windows may need 45 or 60 days. A second critical alert near seven days provides escalation when the recovery window becomes short. Yes, a properly configured SSL monitoring check can detect a missing or invalid intermediate certificate during chain validation. This matters because some clients recover through cached intermediates while others reject the connection.
Always test from external locations and required client environments. No, SSL monitoring validates TLS identity and trust, while website monitoring primarily checks application responses. A website can return an HTTP response through a broken or untrusted path for some clients, and a valid certificate can protect a site that returns a server error. Production services usually need both checks.
Yes, multi-location SSL monitoring is recommended when DNS, CDNs, regional load balancers, or multiple hosting providers serve the domain. Different locations may receive different IP addresses or certificates. At least two independent locations provide a stronger view than one probe. Many monitoring services can check APIs and custom TLS ports, but support varies by provider. Confirm SNI handling, hostname validation, protocol support, authentication needs, and whether the service can test ports beyond standard HTTPS.
A port check alone does not prove certificate correctness. No, monitoring detects risk while renewal automation performs the replacement. You need both because automated renewal can fail, deploy to only one node, or update a file without reloading the proxy. External verification confirms that users receive the intended certificate.
Use retries, multiple locations, clear thresholds, maintenance windows, and separate alert categories. Preserve diagnostic details such as the resolved address, certificate identity, handshake error, and HTTP response. Alert policies should reflect business impact rather than every transient probe failure. SSL monitoring works best when it supports renewal automation rather than pretending to replace it. It should sit beside website, port, DNS, response-time, cron, and Server Health Check s, giving engineers enough evidence to act without repeating the same investigation.
If you are looking for a reliable uptime and monitoring solution, visit zuzia.app to learn more. SSL certificate monitoring checks more than just expiry dates - it validates the full certificate chain, hostname match, TLS protocol version, and issuer changes. An expired or broken cert triggers a full-page browser warning that blocks every visitor and breaks API connections. Included on all PingPing plans, no add-on needed.
SSL certificate monitoring is the practice of automatically tracking the health, validity, and expiration of your siteâIIs SSL/TLS certificates, alerting you before something breaks. It checks whether your certificates are properly configured, havenâIIt expired, and are actually trusted by browsers and devices. Think of it this way. YouâIIve got a certificate that encrypts traffic between your server and your visitors. That certificate has an expiration date. When it expires, or when something goes wrong with the certificate chain, browsers throw up a full-screen warning that says âIIYour connection is not private.âII Visitors leave. Revenue drops. Google notices the bounce rate spike. And if youâIIre running a SaaS or an e-commerce store, you might not even know it happened until a customer tweets about it.
At PingPing , we check your SSL certificates daily and notify you via email, SMS, Slack, or webhooks when something needs attention. The monitoring runs on autopilot. You configure it once and forget about it until thereâIIs actually something to fix. The second your cert expires, every visitor to your site sees a browser warning. Not a subtle one - a full-page interstitial that actively discourages them from proceeding. Chrome, Firefox, Safari, Edge. They all do it. On Chrome, the warning includes the text âIIAttackers might be trying to steal your information.âII ThatâIIs what your customers read instead of your landing page.
HereâIIs what happens next. Conversion rates go to zero on affected pages. Users who were mid-checkout abandon their carts. API integrations that rely on your SSL certificate start failing: payment webhooks, third-party data syncs, anything that validates your certificate before connecting. If youâIIre processing payments, youâIIre now violating PCI DSS compliance requirements, which is a whole separate problem.
And then thereâIIs the SEO angle. HTTPS has been a Google ranking factor since 2014. When your certificate expires, your site effectively becomes HTTP in the eyes of the browser. The cost of that downtime compounds fast. Lost rankings take weeks to recover, not hours. The irony? All of this is preventable with a monitoring tool that starts at âI¬6/month.
Not all SSL monitoring is created equal. A basic check just looks at the expiration date. A proper SSL monitor examines the full stack: Certificate expiration dates. The obvious one. You configure how far in advance you want to be warned: 14 days, 7 days, 3 days or 1 day before expiry, or on expiration day. PingPing lets you pick the threshold that matches your renewal workflow.
Certificate chain completeness. This one catches people off guard. Your SSL certificate doesnâIIt work alone. ItâIIs part of a chain that goes from your certificate, through one or more intermediate certificates, up to a trusted root certificate authority. If an intermediate cert is missing, your site works fine on most browsers but breaks on some mobile devices and older systems. You wonâIIt see the problem from your laptop. Your users on Android 8 will.
Domain name matching. The certificate needs to cover the exact domain being served. That includes wildcard certificates ( *.example.com ) and Subject Alternative Name (SAN) certificates that cover multiple domains. A mismatch triggers NET::ERR_CERT_COMMON_NAME_INVALID and blocks access completely. TLS protocol version. TLS 1.0 and 1.1 are deprecated. Major browsers dropped support for them in 2020. If your server still negotiates on an old protocol, a growing number of connections will fail.
Certificate issuer changes. If your certificate authority suddenly changes without you initiating a renewal, thatâIIs a potential indicator of compromise. Monitoring flags unexpected issuer changes so you can investigate. Checks run daily - SSL certificates change rarely, so daily cadence catches every issue with days of lead time. The mechanics are straightforward. A monitoring service connects to your server on port 443 (or whatever port you specify) and performs a TLS handshake, the same process your visitorâIIs browser does when loading your site.
During that handshake, the monitor pulls the complete certificate chain and inspects each certificate in it. It checks the validity period, verifies the chain of trust up to the root CA, confirms the domain matches, and evaluates the cipher suites and protocol versions offered by the server. SSL certificates are long-lived and rarely change within a single day. ThatâIIs why daily checks are the right cadence for certificate monitoring. Unlike uptime monitoring where 30-second intervals matter because a server can go down at any moment, certificate status doesnâIIt shift minute to minute. Daily checks catch every issue with plenty of lead time for you to act.
When a check finds something wrong - expiration approaching, broken chain, protocol issue - the system fires a notification through whichever channels youâIIve configured. You fix the problem before your visitors ever encounter it. SSL expiry alerts warn you before a certificate lapses, usually at several thresholds (14, 7, 3, and 1 day out), so one missed email never turns into an outage. Strong monitoring adds status-change alerts on top. A new issuer, a changed chain, or a swapped certificate each fire a notification the moment they appear, not days later.
Why stagger the reminders? Picture a renewal that quietly fails on a Friday. A single âIIexpires todayâII alert lands while youâIIre offline for the weekend, and by Monday every visitor is staring at a security warning. Spread the warnings across two weeks and you get caught the first time, with room to act. ThatâIIs the whole point of expiry monitoring: lead time. Status-change alerts cover what an expiry date canâIIt predict. If your certificateâIIs issuer changes when you didnâIIt request a renewal, thatâIIs worth a look. It might be a misconfigured ACME client, or a certificate someone issued for your domain without your knowledge. A chain that changes shape, a certificate reissued early, a serial number you donâIIt recognize: all of it is signal. PingPing watches for these and tells you the same day it sees them.
Running more than one domain? You donâIIt want to log in and eyeball each certificate by hand. A weekly verification sweep across every domain youâIIve added, with a single alert stream for expiry and status changes, keeps the whole portfolio honest. Pair it with the step-by-step expiry setup and youâIIve got both the early warning and the recovery path covered.
SSL monitoring and uptime monitoring answer different questions. Uptime monitoring checks whether your server responds; SSL monitoring checks whether your certificate is valid and trusted. A site can report 100% uptime while showing a browser security warning because its certificate expired overnight. You need both for full coverage. Uptime monitoring answers the question: âIIIs my server responding?âII It checks HTTP status codes, verifies response times, and confirms that expected content appears on the page. It runs frequently, every 30 seconds with PingPing, because servers can go down without warning.
SSL certificate monitoring answers a different question: âIIIs my connection trustworthy?âII A site can be fully operational from a server perspective while showing a scary browser warning because the SSL certificate expired last night. Your uptime monitor will report 100% uptime. Your visitors will see a security wall. The reverse is true too. A valid certificate doesnâIIt help if the server behind it is down.
PingPing bundles both uptime monitoring and SSL certificate monitoring on every plan. You also get response time tracking and status pages included. No add-on fees for SSL checks like some tools require. Step 1: Add your website URL in the PingPing dashboard. Just paste your domain. PingPing automatically detects your SSL certificate. No need to upload cert files or specify ports.
Step 2: Configure your expiration alert threshold. Choose when you want to be notified before your certificate expires: 14 days, 7 days, 3 days, or 1 day, or on expiration day. If you use auto-renewal through LetâIIs Encrypt or your hosting provider, 3 days is usually plenty. If you renew manually, go with 14 days to give yourself a comfortable window. Step 3: Set up your notification channels. Pick from email, SMS, Slack, or webhooks. You can configure multiple channels.
We recommend at least two, because the one time your cert actually expires will be the one time you didnâIIt check your email. ThatâIIs it. PingPing runs daily SSL checks alongside your uptime monitoring from that point forward. Both are included on all plans starting at âI¬6/month.
For a deeper walkthrough including notification channel setup and renewal recovery, see our step-by-step guide on monitoring SSL certificate expiration . Choosing an SSL monitoring tool depends on what else you need it to do. HereâIIs how four popular options compare for SSL certificate monitoring specifically: PingPing is built for solo founders and small dev teams who want monitoring that covers the essentials without complexity.
SSL monitoring is part of every plan. ThereâIIs no separate SSL add-on or higher tier to unlock it. You get uptime checks every 30 seconds, daily SSL validation, response time tracking, and status pages, all bundled together from âI¬6/month. If you run a SaaS, a web app, or a client site and you want to know the moment somethingâIIs off, this is the straightforward option.
TrackSSL does one thing: SSL certificate monitoring. ItâIIs the specialist. If you manage dozens or hundreds of certificates and you donâIIt need uptime monitoring (because you handle that elsewhere), TrackSSLâIIs per-domain pricing makes sense. It also monitors certificate transparency logs, which is unique. The free plan covers 2 certificates. But if you need uptime monitoring too, youâIIll need a second tool.
UptimeRobot is the free-tier incumbent. The free plan gives you 50 monitors with 5-minute intervals, and SSL monitoring comes bundled into the HTTP check. For basic SSL expiration alerts, it works. The trade-off: SSL checks on the free plan are less configurable, you wonâIIt get chain validation or issuer change detection, and the check intervals for uptime are slower than what PingPing offers. See our detailed PingPing vs UptimeRobot comparison for a full breakdown.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Certificate%20authority • https://generatorlabs.com/guides/ssl-certificate-monitoring • https://www.dotcom-monitor.com/blog/ssl-certificate-management/ • https://zuzia.app/learn/ssl-monitoring/ • https://pingping.io/guides/ssl-certificate-monitoring
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for SSL Certificate Validation And Expiry Monitoring Tool.
[*] Metasploit Scan Running on Target Subnet for SSL Certificate Validation And Expiry Monitoring Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |