Complete Technical Paper Content — Static Application Security Testing Tool Using Python Ast
Overview & System Context
Static Application Security Testing Tool Using Python Ast: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8557 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In computer science, static program analysis (also known as static analysis or static simulation) is the analysis of computer programs performed without executing them, in contrast with dynamic program analysis, which is performed on programs during their execution in the integrated environment. The term is usually applied to analysis performed by an automated tool, with human analysis typically being called "program understanding", program comprehension, or code review. In the last of these, software inspection and software walkthroughs are also used. In most cases the analysis is performed on some version of a program's source code, and, in other cases, on some form of its object code.
Two leading approaches to resource certification have been Static Analysis (SA) and Implicit Computational Complexity (ICC). SA is algorithmic in nature: it focuses on a broad programming language of choice, and seeks to determine by syntactic means whether given programs in that language are feasible. In contrast, ICC attempts to create from the outset specialized programming languages or methods that delineate a complexity class. Thus, SA's focus is on compile time, making no demand on the programmer; whereas ICC is a language-design discipline." Linting is a lightweight form of static analysis that typically checks source code for programming errors, suspicious constructs, and style issues.
Medical software: The US Food and Drug Administration (FDA) has identified the use of static analysis for medical devices. Nuclear software: In the UK the Office for Nuclear Regulation (ONR) recommends the use of static analysis on reactor protection systems. Aviation software (in combination with dynamic analysis). Automotive & Machines (functional safety features form an integral part of each automotive product development phase, ISO 26262, section 8). A study in 2012 by VDC Research reported that 28.7% of the embedded software engineers surveyed use static analysis tools and 39.7% expect to use them within 2 years. A study from 2010 found that 60% of the interviewed developers in European research projects made at least use of their basic IDE built-in static analyzers. However, only about 10% employed an additional other (and perhaps more advanced) analysis tool. In the application security industry the name static application security testing (SAST) is also used. SAST is an important part of Security Development Lifecycles (SDLs) such as the SDL defined by Microsoft and a common practice in software companies.
Unit Level Analysis that takes place within a specific program or subroutine, without connecting to the context of that program. Technology Level Analysis that takes into account interactions between unit programs to get a more holistic and semantic view of the overall program in order to find issues and avoid obvious false positives. System Level Analysis that takes into account the interactions between unit programs, but without being limited to one specific technology or programming language. A further level of software analysis can be defined.
Figure 1: ProSAST Scanner: AI-Powered Static Application Security Testing Mission/Business Level Analysis that takes into account the business/mission layer terms, rules and processes that are implemented within the software system for its operation as part of enterprise or program/mission layer activities. These elements are implemented without being limited to one specific technology or programming language and in many cases are distributed across multiple languages, but are statically extracted and analyzed for system understanding for mission assurance. Many static analysis tools use intermediate representations of programs to examine the structure of source code without executing the program. For this purpose, abstract syntax trees (ASTs) are commonly used, since they provide a structured representation of a program's syntactic elements.
Formal methods is the term applied to the analysis of software (and computer hardware) whose results are obtained purely through the use of rigorous mathematical methods. The mathematical techniques used include denotational semantics, axiomatic semantics, operational semantics, and abstract interpretation. By a straightforward reduction to the halting problem, it is possible to prove that (for any Turing complete language), finding all possible run-time errors in an arbitrary program (or more generally any kind of violation of a specification on the final result of a program) is undecidable: there is no mechanical method that can always answer truthfully whether an arbitrary program may or may not exhibit runtime errors. This result dates from the works of Church, Gödel and Turing in the 1930s (see: Halting problem and Rice's theorem). As with many undecidable questions, one can still attempt to give useful approximate solutions. Some of the implementation techniques of formal static analysis include: Abstract interpretation, to model the effect that every statement has on the state of an abstract machine (i.e., it 'executes' the software based on the mathematical properties of each statement and declaration). This abstract machine over-approximates the behaviours of the system: the abstract system is thus made simpler to analyze, at the expense of incompleteness (not every property true of the original system is true of the abstract system). If properly done, though, abstract interpretation is sound (every property true of the abstract system can be mapped to a true property of the original system). For analysis in a domain with infinite ascending chains, widening can be used to achieve convergence at a fixed point. This loses precision, but can improve performance significantly. Data-flow analysis, a lattice-based technique for gathering information about the possible set of values; Hoare logic, a formal system with a set of logical rules for reasoning rigorously about the correctness of computer programs. There is tool support for some programming languages (e.g., the SPARK programming language (a subset of Ada) and the Java Modeling Language—JML—using ESC/Java and ESC/Java2, Frama-C WP (weakest precondition) plugin for the C language extended with ACSL (ANSI/ISO C Specification Language) ). Model checking, considers systems that have finite state or may be reduced to finite state by abstraction; Symbolic execution, as used to derive mathematical expressions representing the value of mutated variables at particular points in the code. Nullable reference analysis Veracode is an application security company based in Burlington, Massachusetts. Founded in 2006, it provides SaaS application security that integrates application analysis into development pipelines. The company provides multiple security analysis technologies on a single platform, including static analysis (or white-box testing), dynamic analysis (or black-box testing), and software composition analysis. Veracode serves over 2,500 customers worldwide and, as of February 2021, has assessed over 25 trillion lines of code.
Figure 2: What Is SAST (Static Application Security Testing)? II Guide. This is a list of notable tools for static program analysis (program analysis is a synonym for code analysis). CodePeer ConQAT Fluctuat LDRA Testbed MALPAS Polyspace SofCheck Inspector Squore Understand Astree Axivion Suite (Bauhaus) BLAST Clang Coccinelle Coverity CPAchecker Cppcheck Cppdepend Cpplint ECLAIR Eclipse Fluctuat Frama-C GCC Helix QAC Facebook Infer Klocwork Lint LDRA Testbed Parasoft C/C++test PC-lint Plus Polyspace PVS-Studio SLAM project Sparse SonarQube Splint Understand Visual Studio Axivion Suite (Bauhaus) Code Dx CodeScene CodeQL Coverity Fluid Attacks Kiuwan Klocwork .NET Compiler Platform PVS-Studio SonarQube Sotoarc StyleCop Squore Understand Visual Studio Figure 3: SAST Explained: Benefits, Challenges & Top Security Testing Tools Coverity Facebook Infer Fluid Attacks Klocwork LDRA Testbed PMD RIPS Semgrep SourceMeter Understand Axivion Suite (Bauhaus) Code Dx CodeScene PMD SofCheck Inspector SonarQube SourceMeter Understand Astrée – finds all potential runtime errors by abstract interpretation, can prove the absence of runtime errors and can prove functional assertions; tailored towards safety-critical C code (e.g. avionics). CodePeer – Statically determines and documents pre- and post-conditions for Ada subprograms; statically checks preconditions at all call sites. ECLAIR – Uses formal methods-based static code analysis techniques such as abstract interpretation and model checking combined with constraint satisfaction techniques to detect or prove the absence of certain run time errors in source code. ESC/Java and ESC/Java2 – Based on Java Modeling Language, an enriched version of Java Frama-C – An open-source analysis framework for C, based on the ANSI/ISO C Specification Language (ACSL). Its main techniques include abstract interpretation, deductive verification and runtime monitoring. KeY – analysis platform for Java based on theorem proving with specifications in the Java Modeling Language; can generate test cases as counterexamples; stand-alone GUI or Eclipse integration MALPAS – A formal methods tool that uses directed graphs and regular algebra to prove that software under analysis correctly meets its mathematical specification. Polyspace – Uses abstract interpretation, a formal methods based technique, to detect and prove the absence of certain run time errors in source code for C/C++, and Ada SPARK Toolset including the SPARK Examiner – Based on the SPARK language, a subset of Ada.
Application security testing (AST) is how teams find and fix security vulnerabilities in software before attackers exploit them. It is no longer a single scan run before release - it is a set of complementary techniques that run continuously across the software development lifecycle, covering your custom code, your open-source dependencies, and your running applications. This complete guide explains what application security testing is, the five core types you need to know ( SAST , DAST, IAST, SCA, and RASP), how they compare in a single tools table, where each one fits in the SDLC, and how to choose the right approach for your team.
Application security testing is the practice of evaluating an application for security weaknesses throughout its lifecycle - from the first line of code to production runtime. The goal is simple: find exploitable vulnerabilities early, prioritize the ones that matter, and fix them before they reach attackers. Modern applications are assembled, not just written. A typical service combines first-party code, dozens or hundreds of open-source packages, container images, infrastructure-as-code, and third-party APIs. No single test can cover all of that surface area, which is why mature application security programs layer multiple testing techniques together.
The application security testing landscape is built on five foundational techniques. Understanding what each one does - and what it misses - is the key to building coverage that does not leave gaps. What it is: SAST analyzes source code, bytecode, or binaries without running the application . It is white-box testing, meaning it has full access to the code and inspects it line by line and across data flows.
What it finds: Injection flaws (SQL injection, command injection), cross-site scripting patterns, insecure deserialization, hardcoded secrets, weak cryptography, path traversal, and unsafe API usage. SAST is the backbone of shift-left security. For a deeper dive, see our SAST vs DAST comparison and our roundup of the best SAST tools . AI-native engines like Corgea AI SAST extend traditional SAST by reasoning about code context to catch logic flaws and cut false positives. For the broader category, see our guide to AI code security and how to choose an AI vulnerability scanner .
What it is: DAST tests a running application from the outside, with no access to source code. It is black-box testing that behaves like an attacker, sending malicious inputs and observing how the app responds. What it finds: Runtime and configuration issues - broken authentication, session management flaws, server misconfigurations, exposed endpoints, and injection vulnerabilities that only manifest at runtime.
DAST pairs naturally with SAST. Learn more in our DAST tools guide and how to choose a DAST tool . What it is: IAST instruments a running application with agents or sensors that observe code execution from the inside while the app is exercised by tests, QA, or DAST traffic. It is gray-box testing - it combines code-level insight with runtime context. What it finds: Vulnerabilities confirmed along real execution paths - injection, SSRF, insecure data handling - with the precise code location and proof the path is reachable.
IAST is a strong fit for teams with mature automated testing who want higher-confidence findings than DAST alone. What it is: SCA scans your application’s open-source and third-party dependencies for known vulnerabilities (CVEs), license risks, and outdated components. Since most modern code is dependency code, SCA is non-negotiable. What it finds: Vulnerable packages, transitive dependency risks, license-policy violations, and unmaintained or malicious components.
The fix for SCA noise is reachability analysis. Corgea dependency scanning traces whether a vulnerable function is actually called, so teams fix the dependencies that matter instead of every CVE. Container images are part of this surface too. See container scanning and the container security tools buyer guide. To go deeper on tooling, see software composition analysis tools and best SCA tools .
What it is: RASP embeds protection inside the running application. Rather than just detecting vulnerabilities, it monitors execution in production and can block exploitation attempts in real time. What it finds and stops: Active attacks - injection attempts, suspicious runtime behavior, and exploitation of zero-day or unpatched flaws - by intercepting them at the point of execution.
RASP is often grouped with WAFs (web application firewalls), but RASP runs inside the app with deeper context, while a WAF sits at the network edge. The table below summarizes how the core methods compare, so you can see where each fits at a glance. A practical rule: SAST + SCA give you early, broad coverage; DAST or IAST validate the running app; RASP protects what is live; and penetration testing stress-tests the whole thing periodically.
Application security testing works best as a continuous practice woven through development, not a release-day gate. Mapping each method to its ideal phase is how teams shift left without losing runtime coverage. The earlier a vulnerability is caught, the cheaper it is to fix - a flaw caught in the IDE costs a fraction of one caught in production. But “shift left” does not mean “shift only left”: runtime methods (DAST, IAST, RASP) catch issues that static analysis fundamentally cannot. The goal is coverage at every phase. Embedding these checks into your pipeline is covered in our CI/CD security guide .
The “best” application security testing strategy is the one that produces trusted signal and fits your engineers’ workflow. Use this framework. Map your stack honestly. A dependency-heavy app needs strong SCA with reachability. A public-facing web app needs DAST and API testing. A regulated environment needs SBOMs and penetration testing for compliance.
A tool developers will not use provides zero security value. Check that it runs in the IDE and CI, surfaces findings in pull requests where decisions happen, and explains why something is a risk and how to fix it. See how developer experience shapes adoption. 2. System Architecture & Core Working Principles In 2026, AI-generated fixes are common - but a fast wrong fix is worse than a slow correct one. Ask vendors how they validate findings and patches before they reach developers.
The biggest shift in application security testing is the move from pattern matching to contextual reasoning. Traditional tools generated enormous backlogs of low-confidence findings, and teams drowned in triage. AI changes the equation in three ways: Corgea brings this approach across the stack - AI SAST for higher-signal code analysis, reachability-aware dependency scanning , container and IaC scanning , and secrets scanning - in one developer-first workflow.
Application security testing is not a single tool or a one-time scan - it is a layered, continuous discipline. The five core methods each cover a distinct gap: SAST and IAST inspect your code, DAST tests the running app, SCA covers your dependencies, and RASP protects production. Combine them across the SDLC, prioritize by real exploitability, and keep remediation inside the developer workflow.
Get the layering right and you catch more real vulnerabilities, earlier, with less noise - which is the entire point of application security testing. See how Corgea helps teams do exactly that. To validate what an attacker could actually exploit at runtime, explore the best AI pentesting tools , learn how autonomous pentesting works, and weigh AI pentest vs traditional pentest .
Application security testing (AST) is the process of finding and fixing security vulnerabilities in software across its lifecycle. It combines methods such as static analysis (SAST), dynamic analysis (DAST), interactive analysis (IAST), software composition analysis (SCA), and runtime protection (RASP) to catch flaws in custom code, dependencies, and running applications before attackers do.
The five core types are SAST (analyzes source code at rest), DAST (tests a running application from the outside), IAST (instruments a running app to combine code and runtime context), SCA (finds vulnerable and risky open-source dependencies), and RASP (protects applications at runtime by blocking exploitation attempts). Most programs also add penetration testing, secrets scanning, and infrastructure-as-code scanning.
SAST is white-box testing that scans source code without running it, so it works early but cannot see runtime behavior. DAST is black-box testing that attacks a running app from the outside, so it finds runtime and configuration issues but later in the lifecycle. IAST is gray-box testing that instruments a running application to combine code-level visibility with runtime context, reducing false positives but requiring a running, instrumented environment.
Application security testing should be continuous, not a single gate. Run SAST and secrets scanning in the IDE and on pull requests, SCA whenever dependencies change, DAST and IAST in staging or QA environments, and penetration testing plus RASP around release and in production. Shifting testing left lowers remediation cost without removing the need for runtime coverage.
Start by naming your biggest bottleneck: too much noise, slow remediation, or coverage blind spots. Match tools to your stack and SDLC, prioritize accuracy (low false positives) and developer-friendly remediation over the longest feature list, and run a proof-of-value on your own codebase measuring time-to-triage and fix acceptance rather than raw finding counts. No. Penetration testing is one technique within application security testing, usually a periodic, human-led assessment that simulates real attacks. AST is the broader discipline that also includes automated, continuous methods such as SAST, DAST, IAST, SCA, and RASP that run throughout development and operations.
Helps us understand site usage, performance, and session recordings with Google Analytics and PostHog. Supports ad attribution and audience measurement with LinkedIn and consent-aware tags managed through Google Tag Manager. The Future Starts at Current: Where real-time data and AI come together | Register now Static Application Security Testing (SAST) , is a method that checks for security flaws in code before it reaches production. It is a security method used to analyze source code for vulnerabilities at an early stage of the SDLC. It’s different from dynamic testing, which focuses on running applications, SAST is performed without executing code. This makes this testing a “white-box” approach where testers have access to the internal structure of the application.
At this point it helps the organization to not only help protect against future breaches but also prevents costly remediation efforts down the line. Further, when we integrate this process into the CI/CD pipeline , SAST becomes part of DevSecOps (an approach that ensures security is considered at every stage of development). SAST tools perform code scanning without executing an application. This static code analysis searches for patterns that may lead to attacks, such as SQL injection, command injection, and server-side-injection attack.
SAST tools are easily integrated with CI/CD pipelines, thereby allowing continuous security checks. SAST tools identify potential vulnerabilities such as SQL injection and cross-site scripting by checking the structure and logic of the code. Results are fed back to developers real time so that they can address issues at the time of coding.
In choosing the proper SAST tool, a team needs to select one that will work with their development environment and security requirements. The tool should support as many programming languages and frameworks as possible to allow for seamless fitment in all the existing workflows of your development pipelines.
SAST tools should handle large and complex codebases efficiently without compromising performance, allowing for fast scans and feedback. It also allows the fine-tuning of the scanning process, which completely fits your project's needs. Detailed, real-time reports that help developers prioritize vulnerabilities and provide fixing guidance.
By identifying issues during the development phase, you can reduce the risk of releasing insecure software. The cost of fixing vulnerabilities gets cheaper earlier on, rather than trying to fix them after deployment. SAST tools could also be used to enforce the use of coding standards and best practices that result in more secure and maintainable code.
Many regulatory frameworks require security testing, and SAST helps you meet such standards through vulnerability detection and suggesting improvements. False Positives: SAST tools may flag non-issues, overwhelming developers with unnecessary alerts. Initial Setup and Integration: Setting up SAST in a large environment can be resource-intensive.
Limited Dynamic Context: Since SAST doesn’t run the application, it may miss runtime issues. Complexity in Large Codebases: For big projects, SAST tools can struggle with performance and accuracy. To overcome these challenges, it’s important to tune SAST tools to focus on critical vulnerabilities and use other security methods like DAST (Dynamic Application Security Testing) to cover runtime issuesI.
Security teams should work closely with developers to prioritize and resolve vulnerabilities. Use SAST alongside DAST (Dynamic Application Security Testing) and IAST (Interactive Application Security Testing) for a comprehensive coverage. Select a SAST tool that aligns with your specific technology stack and integrates well with your existing processes for seamless operation.
For event-driven applications like those built on Kafka, integrating SAST into CI/CD ensures that security vulnerabilities are caught early in the data pipeline. Encourage developers to provide feedback on the SAST process and tools used, allowing for continuous improvement and better alignment with their workflow needs.
SAST plays an important role in the Confluent ecosystem , especially within event-driven architectures like those based on Apache Kafka . These systems process large amounts of real-time data, making them attractive targets for security threats. By implementing SAST, organizations can ensure that the code running within these Kafka-based applications is secure, as it helps detect vulnerabilities early in the development lifecycle.
Additionally, SAST is crucial for securing real-time data pipelines , ensuring that data flows remain protected from potential threat. By addressing these aspects, SAST plays an important role in maintaining the integrity and security of data streams within the Confluent ecosystem. 3. Software Implementation, Frameworks & Protocols SAST is a critical component of a comprehensive security strategy, but it should be considered alongside other testing methods. Here’s how SAST compares to two key approaches: SAST vs. DAST: While SAST analyzes code statically without executing it, Dynamic Application Security Testing (DAST) evaluates applications in real-time during runtime. DAST identifies vulnerabilities that may not be apparent in static code analysis, such as those that emerge only when the application is executed. This makes DAST particularly effective for catching runtime-specific issues that SAST may miss.
SAST vs. IAST: Interactive Application Security Testing (IAST) operates within a running application, providing real-time feedback on vulnerabilities as they are detected. IAST integrates components of both SAST and DAST , providing more comprehensive insights into an application's security posture. By integrating SAST with IAST , organizations can achieve a more comprehensive view of their application’s security, utilizing the strengths of both methodologies.
The choice of testing method often depends on the specific phase of the development lifecycle and the type of vulnerabilities being targeted. SAST is ideal for early-stage development to catch issues before deployment, while DAST is effective for assessing runtime behavior in production environments. IAST can be beneficial when continuous testing is needed throughout the application’s lifecycle.
Fortify Static Code Analyzer: Fortify is particularly well-suited for developers aiming to integrate SAST directly into their CI/CD pipelines. It facilitates the prioritization of vulnerabilities and provides actionable guidance for remediation, ensuring a more secure development process. SonarQube and Semgrep: These open-source tools offer flexible integration capabilities and support a wide range of programming languages, making them accessible for various development environments.
While these tools are valuable, it's important to focus on scanning code that interacts with data streaming—specifically, applications and microservices that have access to data streams. If this code is compromised, it poses a risk to your data streams. So, developers should ensure that the security of the code handling data streams is robust, as issues in this area can lead to significant risks.
In modern development environments, microservices and real-time data systems (like Kafka) become more important and prevalent. So, SAST plays an important role in these settings by catching vulnerabilities early and ensuring security throughout the development process. SAST integrates into CI/CD workflows, automating security checks as code is committed. This real-time monitoring helps developers address vulnerabilities early, reducing risks and costs. For example, a financial services company may use SAST in its CI/CD pipeline to secure applications handling sensitive transactions, ensuring compliance and security from development to deployment.
In microservices architectures , each service operates independently, creating potential security gaps. SAST helps secure these services individually, identifying vulnerabilities before deployment. For example, e-commerce and healthcare systems can use SAST to protect services handling payment data or patient records. For real-time data systems like Kafka, SAST ensures secure code in event-driven architectures. By scanning code in real-time data pipelines, SAST helps protect sensitive information and operational integrity, such as in retail environments using Kafka for inventory and sales tracking.
By integrating SAST into CI/CD and microservices workflows, organizations can secure their real-time applications and minimize security risks efficiently. The future of SAST lies in its ability to adapt to real-time data and emerging threats. As event-driven architectures continue to grow, SAST will become more sophisticated, leveraging technologies like Generative AI for enhanced analysis and detection.
SAST tools will become more intelligent and automated, with GenAI enhancing their ability to analyze code. GenAI will help predict potential vulnerabilities and provide more precise improvement advice, making security more proactive. As real-time data streaming grows, securing dynamic pipelines will be important. SAST tools will evolve to better handle the complexities of distributed, real-time systems, identifying vulnerabilities before they can cause disruption.
SAST will become a more integrated part of DevSecOps workflows, providing automatic, real-time security feedback for developers throughout the development process. New threats to streaming data will demand more advanced SAST capabilities. With GenAI capabilities , future SAST tools will detect and respond to new vulnerabilities in real-time, securing event-driven architectures from emerging risks.
The future of SAST depends on its ability to adapt to real-time environments , leverage AI-powered insights , and ensure seamless security in DevSecOps workflows. SAST (Static Application Security Testing) remains an integral part of any security strategy, especially for event-driven, real-time data applications. By integrating SAST into CI/CD pipelines and using best practices, organizations can reduce vulnerabilities, improve code quality, and stay ahead of emerging security threats.
Implement SAST in your development workflow today to secure your applications and protect against future vulnerabilities. Master Application Security Testing: learn core methods, CI/CD integration, and best practices to catch vulnerabilities before they become breaches. Application Security Testing identifies vulnerabilities in software before attackers exploit them, across code, dependencies, and runtime configurations. You weave automated and manual checks into every stage of your software development life cycle so flaws are discovered while they're still cheap to fix.
Attackers move faster than release cycles. A vulnerability discovered today gets weaponized within hours and exploited at scale before your next sprint planning meeting. AST finds exploitable weaknesses while code is still in your environment, not in production where breaches cost millions. Every unpatched SQL injection or misconfigured API becomes an entry point. When you integrate security testing into each commit, you stop attacks before they start instead of cleaning up breaches after the damage spreads. Teams without continuous testing ship vulnerabilities that sit dormant until an attacker scans your public endpoints and finds them first.
AST spans every workload you ship. Web application security has become critical as organizations depend on browser-based systems to handle sensitive data. Web applications, mobile apps, APIs, and containerized cloud services all carry business-critical data and need their own testing layer. During static analysis you review source code for predictable errors, while dynamic tests probe the running application from the outside. Dependency scanners inspect open-source libraries, and agent-based tools watch live traffic for suspicious behavior that escaped earlier gates. Together, these techniques reveal familiar injection bugs (SQL injection, cross-site scripting , and other issues highlighted in the OWASP Top 10) along with misconfigurations that only appear under real load.
Following structured frameworks like OWASP Testing Guide (OTG) management principles helps teams systematically cover attack surfaces and maintain consistent test coverage. Secure delivery is a team sport, so AST responsibility spreads across roles. Developers receive automated scan results in their pull requests. Security engineers tune test policies and investigate complex findings. QA testers fold security checks into functional test suites, and compliance officers verify that processes align with internal or regulatory standards. When these stakeholders share a single testing pipeline, vulnerabilities get caught early, fixes merge quickly, and production incidents become the exception rather than the rule.
Modern teams have shifted from finding bugs to systematically preventing exploitable weaknesses. By integrating AST into every commit, organizations cut breach risk, accelerate release velocity, and satisfy regulatory demands, making continuous security testing a non-negotiable element of contemporary software development. Effective application security testing requires three essential components: comprehensive coverage, automated tooling, and continuous feedback loops.
Coverage means testing every layer of your application stack, from source code and dependencies to runtime behavior and infrastructure configuration. Automated tooling executes repetitive scans without human intervention, while feedback loops deliver findings directly to developers when context is fresh. Start with a complete asset inventory that maps every application, API, and service you deploy. Without knowing what exists, you cannot secure it. Next, define clear ownership so each component has a responsible team that receives findings and tracks remediation. Testing tools must integrate with your development workflow, triggering scans on commits, pull requests, and deployments so security checks become automatic quality gates rather than manual bottlenecks.
Establish severity thresholds that block releases when critical vulnerabilities appear. Set service-level agreements for remediation based on risk: When these components work together, security testing becomes a predictable, measurable control that catches vulnerabilities before they reach production.
Application security testing analyzes code, dependencies, and runtime behavior through automated scans and targeted probes. The process begins when developers commit code, triggering static analysis that reviews source files for insecure functions, hard-coded credentials, and logic flaws. These early checks catch predictable mistakes before code compiles. During build stages, dependency scanners inventory every library and framework, cross-referencing them against vulnerability databases to flag known CVEs . Container images get scanned for outdated packages and misconfigurations before they reach registries. Integration testing adds dynamic scans that probe deployed applications from the outside, sending malicious input to test how the application handles attacks.
Once applications reach staging or production, interactive testing instruments the runtime environment to watch how requests flow through code paths. Agents embedded in the application track suspicious behavior and block exploits immediately. Meanwhile, continuous monitoring correlates security events with application telemetry, linking attacks to specific code changes or deployment events.
Security teams triage findings, validate exploitability, and set remediation priorities. This cycle repeats with every code change, creating a continuous loop that finds and fixes vulnerabilities faster than attackers can exploit them. Application security testing finds the injection attacks, broken authentication, and misconfigurations that account for most successful breaches. SQL injection and cross-site scripting top the list because they exploit how applications handle untrusted input. When user data reaches databases or browsers without proper validation, attackers inject malicious code that steals credentials, exfiltrates data, or takes over sessions.
Broken authentication surfaces through weak password policies, missing multi-factor requirements, and session tokens that never expire. Testing tools probe login flows, password reset functions, and session management to find these weaknesses before attackers do. Security misconfigurations appear across every layer: Dependency vulnerabilities stem from outdated libraries bundled into applications. A single vulnerable component can compromise an entire application when attackers exploit known CVEs in popular frameworks. Insecure deserialization lets attackers execute arbitrary code by manipulating serialized objects, while insufficient logging obscures attacks until damage spreads.
Testing also catches authorization flaws where users access resources they should not see, and XML external entity attacks that expose file systems through crafted XML input. When these vulnerabilities reach production, they become the entry points attackers exploit first. No single test finds every flaw. Mature programs layer multiple methods across the development lifecycle so teams see the same code, component, or workload from several angles and catch issues a single scan would miss. This principle echoes how unified security platforms already correlate endpoint , cloud, and identity telemetry to close visibility gaps across an environment.
4. Practical Deployment, Analysis & Case Studies Security teams adopting this layered strategy drastically reduce exploitable surface area. When multiple methods overlap across the development lifecycle, each test reinforces the others, closing blind spots no single tool could ever address alone. Breaches happen because vulnerable code reaches production before anyone tests it. Continuous AST runs security checks at every pipeline stage, finding exploitable flaws hours after they're written instead of weeks after deployment.
Consolidating tools into a comprehensive security platform mitigates these issues by providing centralized threat analysis and streamlined alerts. This integration helps security teams focus on high-priority vulnerabilities, ultimately preventing breaches and maintaining compliance. Security testing belongs in your CI/CD pipeline alongside linting and unit tests. Shift-left testing catches vulnerabilities when developers still have the code context to fix them, turning security into a quality gate instead of a bottleneck.
By maintaining a single security context from commit to production, teams embed security testing directly into CI/CD workflows, reduce alert fatigue, and deliver actionable findings while code remains fresh in developers' minds. Most testing programs fail by checking security once per year, trusting one scanner, and skipping internal services. These gaps let attackers exploit the 364 days between audits and pivot through untested APIs once they breach your perimeter.
Effective security testing requires layered methods, risk-based prioritization, and stakeholder involvement across development, security, and operations. Success starts by embedding tests early, running scans at each commit, build, and integration stage, so flaws surface while the code is still fresh. Continuous analysis keeps vulnerability windows short and remediation costs low.
Finally, keep everyone in the conversation. Developers need instant feedback, security engineers tune policies, and ops teams verify that mitigations don't break production. When all three groups share context and collaborate on remediation, vulnerabilities get fixed faster and stay fixed. Elevate your security posture with real-time detection, machine-speed response, and total visibility of your entire digital environment.
Security testing works when you run it continuously, not annually. Testing at every commit finds vulnerabilities while developers still remember the code, making fixes faster and cheaper. No single scanner catches every flaw, so successful programs combine static analysis, live application probing, dependency tracking, and runtime monitoring. Focus your remediation efforts on exploitable weaknesses in production systems first. When security checks integrate directly into your development pipeline, testing becomes an automated quality gate instead of a bottleneck. Teams that embed security into every stage from code commit through production ship secure applications faster and stop breaches before they start.
Application Security Testing identifies security vulnerabilities in software applications before deployment. AST scans source code, dependencies, and running applications to find exploitable weaknesses like SQL injection, cross-site scripting, and insecure configurations. You run these tests throughout development to catch flaws early when fixes cost less than post-breach remediation.
The main types are Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), Interactive Application Security Testing (IAST), Software Composition Analysis (SCA), and Runtime Application Self-Protection (RASP). SAST reviews source code before execution, DAST attacks running applications from outside, IAST monitors applications during runtime, SCA tracks vulnerable dependencies, and RASP blocks exploits inside live applications. Teams layer these methods throughout development to catch vulnerabilities that single approaches miss.
AST prevents breaches by finding vulnerabilities before attackers exploit them. Without continuous testing, vulnerable code reaches production and sits exposed until the next security audit. Attackers scan public endpoints constantly, exploiting known weaknesses within hours. Teams that integrate AST into every commit catch exploitable flaws while developers still have code context, making fixes faster and cheaper while stopping attacks before they start.
SAST inspects source code or binaries before an application runs, flagging issues such as insecure functions or hard-coded secrets early in the pipeline. DAST probes a live application from the outside to uncover runtime flaws such as SQL injection, cross-site scripting, and configuration errors that only appear in deployed environments. Run lightweight SAST and Software Composition Analysis on every commit, schedule DAST and IAST for each build that reaches staging, and maintain continuous RASP monitoring in production. Match your testing cadence to your release cycle: daily deployments require daily automated tests.
No, automated testing excels at breadth while skilled penetration testers bring creative, context-aware attacks that pentesting test suites cannot replicate. Use annual or quarterly pen tests to validate business logic and probe chained exploits after automated scanners have reduced obvious vulnerabilities. Focus first on exploitable flaws in internet-facing, mission-critical systems, then tackle issues with available patches or well-known exploits. Platforms that score vulnerabilities by exploitability and exposure help teams cut through alert overload and fix what matters most.
DevSecOps embeds security checks inside CI/CD workflows by triggering scanners on commits, blocking merges that introduce high-risk flaws, and surfacing results in developer tools. This makes continuous security testing an automated quality gate that provides instant feedback without derailing delivery speed.
Static Application Security Testing (SAST) is a critical practice in modern software development, particularly within the DevSecOps framework, which integrates security into every phase of the software development lifecycle (SDLC). This tutorial provides an in-depth exploration of SAST, its role in DevSecOps, and practical guidance for implementation. Designed for developers, security engineers, and DevOps professionals, it covers core concepts, setup, use cases, benefits, limitations, and best practices.
SAST is a security testing methodology that analyzes source code, bytecode, or binaries without executing the application. It identifies vulnerabilities early in the development process by scanning code for patterns, insecure coding practices, or potential weaknesses. SAST emerged in the early 2000s as software security gained prominence. Early tools like Fortify (introduced in 2003) and Checkmarx (2006) popularized static code analysis for security. The rise of DevSecOps in the 2010s, driven by agile and CI/CD adoption, amplified SAST’s importance by embedding security into rapid development cycles.
DevSecOps emphasizes “shifting left” — addressing security early in the SDLC. SAST aligns perfectly by: SAST is a cornerstone of DevSecOps, enabling teams to secure code early, automate security checks, and meet compliance requirements. By integrating SAST into CI/CD pipelines, organizations can reduce risks and foster collaboration between development and security teams. Future trends include AI-driven SAST for smarter false-positive filtering and deeper cloud integrations.
#Automation #CareerGrowth #CICD #CI_CD #CloudAutomation #CloudComputing #CloudDevOps #CloudNative #DataScience #DevOps #DevOpsAutomation #DevOpsCareer #DevOpsCareers #DevOpsSkills #DevOpsTools #DevOpsTraining #DevSecOps #EnterpriseDevOps #InfrastructureAsCode #ITTraining #Kubernetes #MachineLearning #Microservices #Observability #SiteReliabilityEngineering #SoftwareDelivery #SoftwareDevelopment #SRE #TechSkills #TechTraining Static Application Security Testing (SAST) scans your source code — not the running app — to find insecure coding patterns before they reach production. It’s one of the earliest and most effective security tools you can add to a development workflow because it catches errors when they’re cheapest to fix: while you’re writing code.
SAST analyzes source files, looking for patterns that indicate a vulnerability: unsanitized user input used in SQL queries, improper cryptography , unsafe authentication flows , and more. Because it inspects code statically (without executing it), SAST excels at flagging insecure coding practices early in the SDLC. Traditional SAST tools are predominantly rule-based : an engine parses code and applies thousands of rules that match known insecure patterns. This approach is efficient and precise for many classes of flaws because the patterns are well understood.
Some vendors are pushing AI-driven detection, but raw LLM scanning tends to be noisy and computationally expensive — the famous analogy applies: it’s like mowing your lawn with a Ferrari. Instead, the most effective use of AI so far is not scanning per se, but adding project-wide context to improve triage and fix suggestions. Open-source SAST tools are great starting points because they separate the scanning engine from the rule set. The engine performs parsing and matching; the rules, often community-maintained, define what “bad” looks like.
Rule-based SAST often casts a wide net. That’s good for recall — you find more potential problems — but it also pulls in a lot of noise. Many flagged issues aren’t reachable in production or are safe in a particular project context, so teams spend time investigating alerts that don’t matter. Rather than replacing rule-based scanning, modern SAST tooling combines static rules with AI-powered layers that add context and reduce noise: SAST is still one of the most cost-effective ways to reduce security risk because it finds code-level issues early. Rule-based engines remain the workhorses for detection, while AI is proving most valuable as a contextual layer that prioritizes findings, explains reachability, and proposes fixes.
Start small with open-source SAST to discover what issues exist in your code. When noise or scale becomes a problem, add AI-enabled triage and autofix to get to real vulnerability remediation — faster and with less friction for developers. Try out Aikido Security today! Jason Haddix on why manual pentesting can't keep up, what disappears first, and why human methodology is what makes AI pentesting work Most of a container's vulnerabilities come from the base image. How to harden Docker images, why hardening is ongoing, and how to patch the base you already run.
Tyro's CISO: Being the "Einstein of cybersecurity" isn't enough if developers don't trust you Tyro CISO Arun Singh on developer trust as a finite resource, and what happens when supply chain attacks force teams to spend it Secure your code, cloud, and runtime in one central system. Connect a repo to discover what the reasoning agents find in your codebase.
5. Performance Evaluation & Extended Technical Observations Benchmark and evaluation framework for static application security testing (SAST) and vulnerability analysis agents. SastBench ( Feiglin and Dar, 2026 ) is a framework for evaluating automated SAST (Static Application Security Testing) triage agents. It provides a benchmark to help advance agents that can analyze security tool findings, assist with the triage process (i.e., identifying true and false positive vulnerability reports), and support secure development workflows.
The evaluator groups findings by (repo_url, commit_hash) , checks out that commit, runs preprocess once per commit, then calls analyze once per finding, passing finding["to_analyzer"] as finding_data . The agent must return a prediction ( true_positive / false_positive / error ) and a confidence (confidence is saved in the logs, but it usually isn't very useful -- it can be set to a constant value); correctness is computed against ground_truth .
to_analyzer is intentionally generic: it can be any JSON object your agent understands. The bundled dataset uses a shape like: Agents can interpret this as they like; the only contract is that analyze(processed_data_path, finding_data) returns an AnalysisResult with prediction and confidence .
Install dependencies (for the evaluation CLI and workers; agents have their own in each agents/
What usually stays the same: The docker-compose setup and the preprocess step are typically left as-is (or with minimal changes). All bundled agents use the same pattern: preprocess copies the repository into output_path/source_files so the container has the code at the right commit; the compose file just builds the image and mounts your code and the shared analyzer_interface . You only need to change these if your agent needs extra services, different env vars, or a different way to prepare the repo.
What you change: The analyze logic is where agents differ. You implement (or replace) the analyze(processed_data_path, finding_data) method in analyzer.py : it receives the preprocessed data and one finding’s to_analyzer payload and returns an AnalysisResult . That’s the part that defines your agent’s behavior (e.g. ReAct vs single-shot LLM vs tool-using agent). You may also add or adjust arguments in agent_schema.json if your analyzer needs new options (model, API key, etc.).
The evaluator discovers the agent via --agent-dir and uses agent_schema.json to build the run command and config for the container. No changes to the evaluation CLI are required when you add a new agent. Benchmark and evaluation framework for static application security testing (SAST) and vulnerability analysis agents. Application security testing explained — SAST, DAST, IAST, SCA and penetration testing compared, where each fits in the SDLC, and how to build an AppSec programme in 2026.
The application layer is where most breaches now begin. Injection flaws, broken access control, vulnerable dependencies, and leaked secrets do not need a network foothold — they are reachable directly from the internet, at the speed of a single HTTP request. Application security testing (AST) is the discipline of finding those flaws before an attacker does. The problem is that "application security testing" has fractured into an alphabet soup of methods — SAST, DAST, IAST, SCA, RASP, ASPM — each with a different vantage point, a different set of findings, and a different cost. Buy the wrong combination and you get thousands of false positives and a blind spot where the real risk lives. Buy the right combination and you catch the bug in the IDE, three weeks before it would have shipped to production.
This guide is the practical map. We define what application security testing actually is, walk through every major testing type, compare them head to head, show where each fits in the software development lifecycle (SDLC), and lay out how to build a programme that reduces real risk rather than generating noise. By the end, engineering leaders, AppSec owners, and CISOs will know exactly which method solves which problem in their environment.
Application security testing (AST) is the practice of analysing software — its source code, its dependencies, and its running behaviour — to find security vulnerabilities before they are exploited. It spans the whole software development lifecycle, from a developer's first commit to the live production application. There is no single AST tool. Instead there are complementary methods: SAST reads your code, SCA inspects your open-source dependencies, IAST instruments the app while tests run, and DAST plus manual penetration testing attack the running application from the outside.
The goal is not "zero findings". It is defensible coverage : every class of risk that matters to your application is being looked at by the right method, the findings are triaged and fixed, and the same bug does not keep reappearing in the next release. APIs, single-page apps, and SaaS integrations expose business logic directly to the internet. There is no firewall in front of a broken authorisation check.
The majority of a modern codebase is open-source dependencies. A single vulnerable transitive package — the Log4Shell pattern — can expose every application that pulls it in. AI coding assistants generate code (and bugs) at scale, while attackers use AI to weaponise exploits in hours. The window between disclosure and exploitation has collapsed. See our analysis of the CERT-In 2026 AI Cybersecurity Blueprint .
The economics reinforce the urgency. A flaw caught by a developer's IDE costs a few minutes to fix. The same flaw caught in production can cost up to 100× more — incident response, emergency patching, regulatory notification, and reputational damage. This cost curve is the entire argument for "shift-left" security, and AST is how you shift left in practice. Each method has a distinct vantage point. Understanding what each one sees — and what it is blind to — is the key to assembling a programme with no gaps and minimal overlap.
Static Application Security Testing. Analyses source code, bytecode, or binaries without running them. Catches injection patterns, hard-coded secrets, and insecure APIs early — directly in the IDE or pull request. Dynamic Application Security Testing. Attacks the running application from the outside, with no view of the code. Finds real, exploitable issues — injection, misconfiguration, authentication flaws — the way an attacker would.
Interactive Application Security Testing. Instruments the application with sensors and watches it from the inside while functional or QA tests exercise it. Combines code-level context with runtime confirmation, so accuracy is high. Software Composition Analysis. Inventories every open-source and third-party component, flags known CVEs and risky licences, and underpins your SBOM. Essential because most of your codebase is code you did not write.
The takeaway: these methods are complementary, not competing . SAST and SCA catch problems early and cheaply but generate noise and miss runtime context. DAST and penetration testing confirm what is actually exploitable but only late, on a running app. IAST bridges the two. A mature programme uses all of them, each at the stage where it is cheapest and most accurate.
Application security testing is most effective when it is woven through the entire lifecycle rather than bolted on at the end. The principle is "shift left, test right" : catch as much as possible early (cheap), and still validate the running system (real). This is the essence of DevSecOps and a secure SDLC : security testing is automated into the pipeline, owned jointly by engineering and security, and treated as part of "done" rather than a pre-launch gate.
You cannot test what you cannot see. Catalogue every app and API, then rank by data sensitivity and exposure. Internet-facing apps handling PII or payments get the deepest testing. These give the fastest, cheapest coverage. Begin in "report-only" mode to baseline noise, tune the rules, then introduce blocking gates on critical, confirmed findings only. Our SAST and SCA implementation services cover the tuning that makes or breaks adoption.
Once code-level scanning is stable, validate the running application. DAST and IAST confirm which findings are genuinely exploitable, cutting the triage burden. Automated tools never find business-logic flaws or chained exploits. Schedule periodic web , API , and mobile penetration tests and secure code reviews for your crown-jewel applications.
Track mean-time-to-remediate, recurrence rate, and coverage — not raw finding counts. An AppSec maturity assessment benchmarks where you are and what to fix next. A single SAST licence covers one vantage point. Without SCA you are blind to dependency risk; without DAST or pen testing you never confirm exploitability. Coverage comes from a layered set, not one product.
An untuned scanner that floods the pull request with low-severity noise trains developers to ignore it. Tuning, severity gating, and de-duplication are what turn a scanner into a programme people trust. A single annual penetration test satisfies a checkbox but finds problems when they are most expensive to fix. Continuous, shift-left testing catches the same issues for a fraction of the cost.
A backlog of 10,000 unaddressed findings is worse than no scanner — it is documented, un-remediated risk. Prioritisation, ownership, and SLAs matter more than scan volume. For Indian banks, NBFCs, fintechs, and SaaS providers, application security testing is increasingly the practical way to evidence software-side compliance. RBI 's Master Direction on IT Governance expects application security testing and VAPT for critical systems; the DPDP Act demands reasonable security safeguards for personal data, which begins at the application; and CERT-In 's 2026 blueprint compresses remediation windows for exploitable, internet-facing flaws to hours. A documented AST programme — scans, pen-test reports, SBOMs, and remediation evidence — turns "we follow secure development" into auditable proof. See our RBI cybersecurity beginner's guide and Cloud Security for Fintech & NBFC for the regulatory map.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Static%20program%20analysis • https://en.wikipedia.org/wiki/Veracode • https://en.wikipedia.org/wiki/List%20of%20tools%20for%20static%20code%20analysis • https://corgea.com/learn/application-security-testing-complete-guide • https://www.confluent.io/learn/sast/ • https://www.sentinelone.com/cybersecurity-101/cybersecurity/application-security-testing/ • https://devsecopsschool.com/blog/static-application-security-testing-sast-in-devsecops-a-comprehensive-tutorial/ • https://www.aikido.dev/blog/ultimate-sast-guide-static-application-security-testing • https://github.com/RivalSecurity/sastbench • https://www.adayptus.com/blog/application-security-testing-complete-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
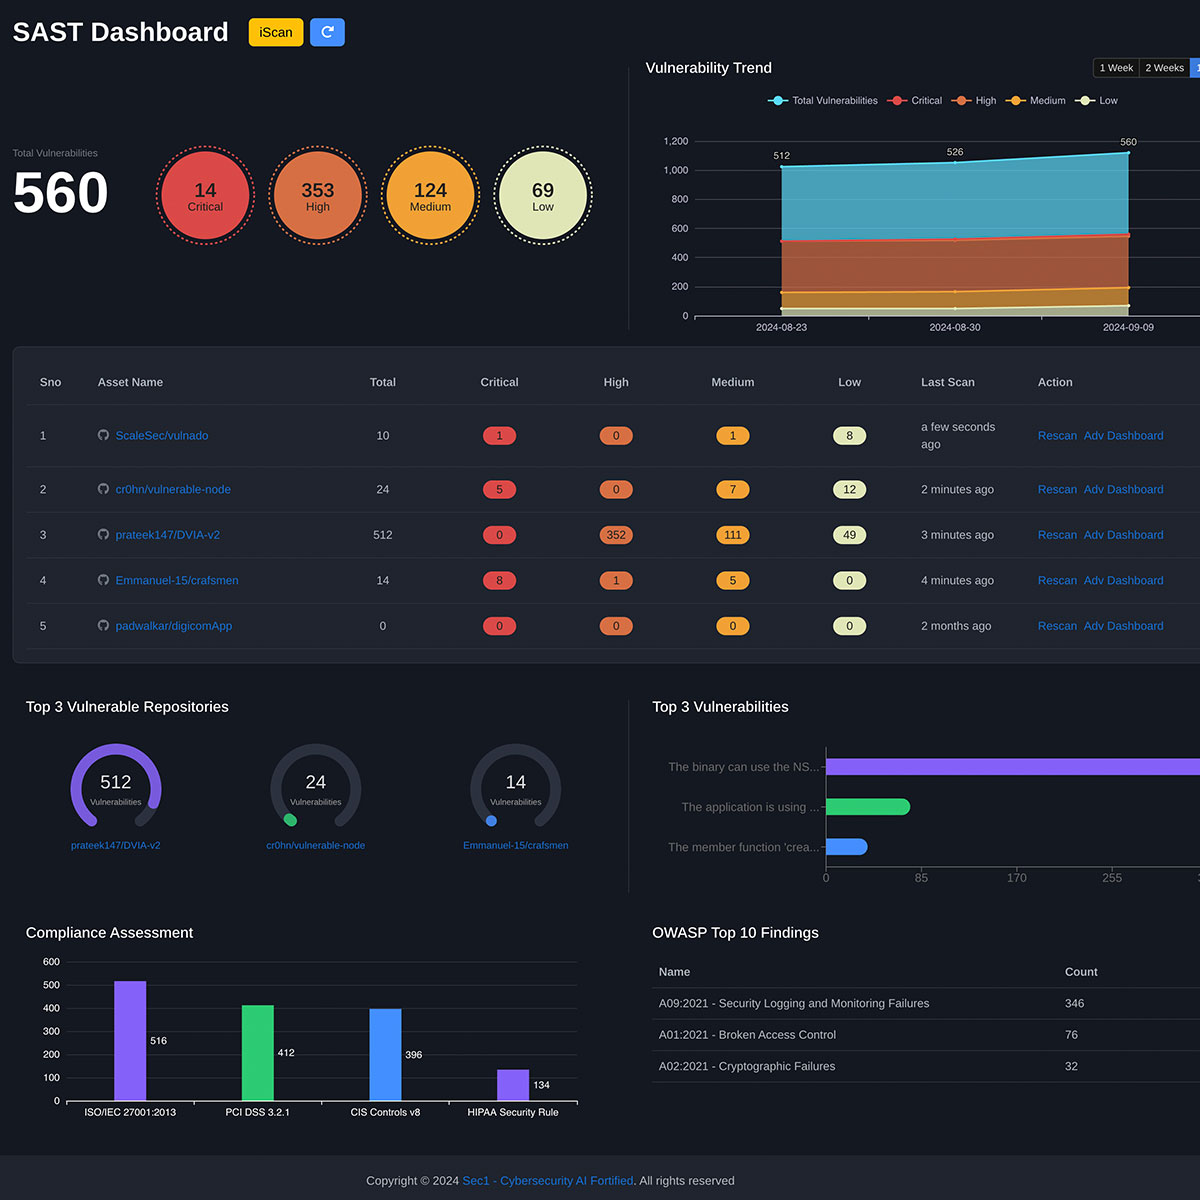
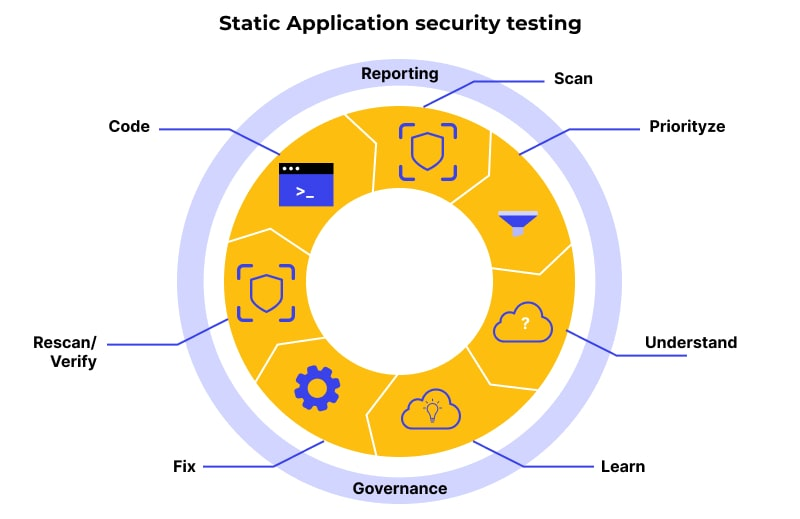
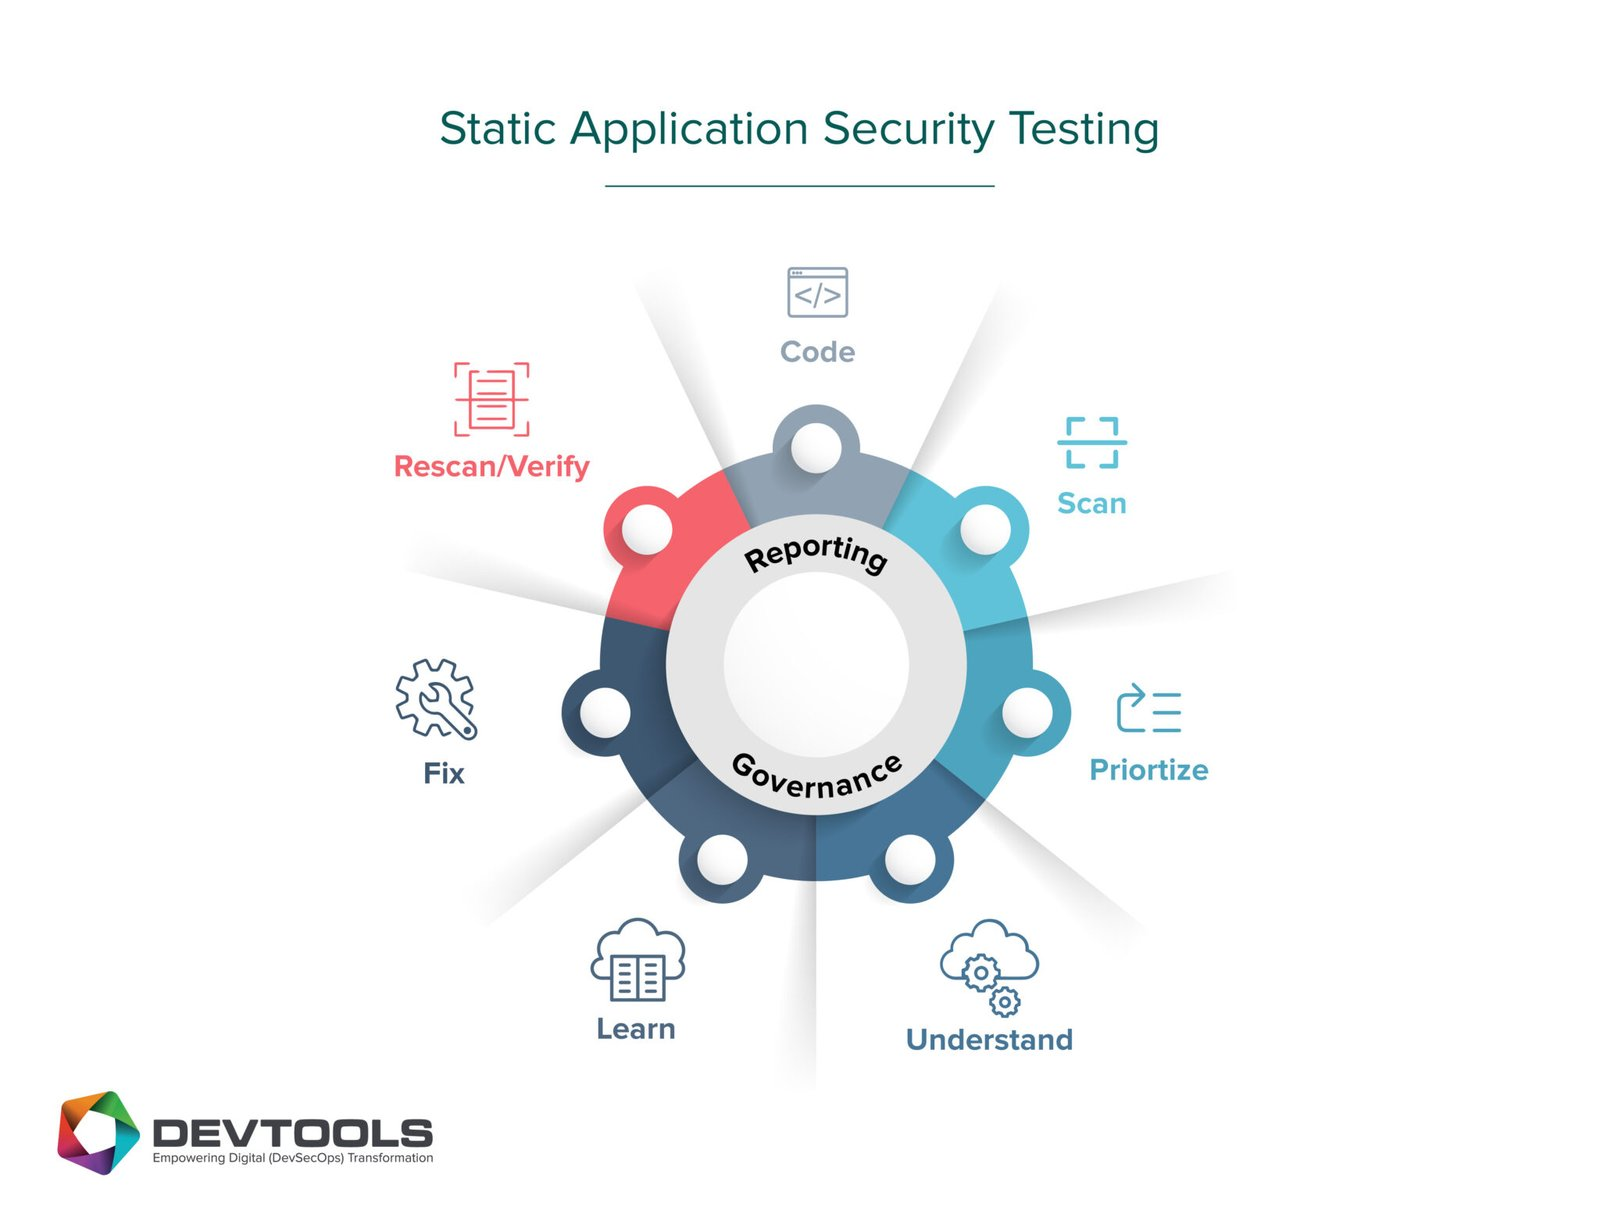
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Static Application Security Testing Tool Using Python Ast.
[*] Metasploit Scan Running on Target Subnet for Static Application Security Testing Tool Using Python Ast... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |