Complete Technical Paper Content — Steganography Detection In Digital Images Using Deep Learning
Overview & System Context
Steganography Detection In Digital Images Using Deep Learning: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4301 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Steganography ( , STEG-I-NOG-rI-fee) is the practice of representing information within another message or physical object, in such a manner that the presence of the concealed information would not be evident to an unsuspecting person's examination. In computing and electronic contexts, a computer file, message, image, or video is concealed within another file, message, image, or video. Generally, the hidden messages appear to be (or to be part of) something else: images, articles, shopping lists, or some other cover text. For example, the hidden message may be in invisible ink between the visible lines of a private letter. Some implementations of steganography that lack a formal shared secret are forms of security through obscurity, while key-dependent steganographic schemes try to adhere to Kerckhoffs's principle. The word steganography comes from Greek steganographia, which combines the words steganós (στεγανIς), meaning "covered or concealed", and -graphia (γραφI) meaning "writing". The first recorded use of the term was in 1499 by Johannes Trithemius in his Steganographia, a treatise on cryptography and steganography, disguised as a book on magic. The advantage of steganography over cryptography alone is that the intended secret message does not attract attention to itself as an object of scrutiny. Plainly visible encrypted messages, no matter how unbreakable they are, arouse interest and may in themselves be incriminating in countries in which encryption is illegal. Whereas cryptography is the practice of protecting the contents of a message alone, steganography is concerned with concealing both the fact that a secret message is being sent and its contents. Steganography includes the concealment of information within computer files. In digital steganography, electronic communications may include steganographic coding inside a transport layer, such as a document file, image file, program, or protocol. Media files are ideal for steganographic transmission because of their large size. For example, a sender might start with an innocuous image file and adjust the color of every hundredth pixel to correspond to a letter in the alphabet. The change is so subtle that someone who is not looking for it is unlikely to notice the change.
The first recorded uses of steganography can be traced back to 440 BC in Greece, when Herodotus mentions two examples in his Histories. Histiaeus sent a message to his vassal, Aristagoras, by shaving the head of his most trusted servant, "marking" the message onto his scalp, then sending him on his way once his hair had regrown, with the instruction, "When thou art come to Miletus, bid Aristagoras shave thy head, and look thereon." Additionally, Demaratus sent a warning about a forthcoming attack to Greece by writing it directly on the wooden backing of a wax tablet before applying its beeswax surface.
Wax tablets were in common use then as reusable writing surfaces, sometimes used for shorthand. Greek writer Aeneas Tacticus also devised a method of steganography now known as the pinhole cipher. He tells of a method where you are to write a letter and mark specific characters inside the letter with a dot-shaped hole. The recipient of said letter will simply note down all letters below the holes and string them together to form a message. He also suggested writing down a message and whitening it, making it invisible, so that when soaked in water the message would be revealed. He suggests many other hiding methods, such as hiding a message in leaves, in the foot of a messenger's sandal, and even in animal bladders. In his Compendium of Mechanics, Philo of Byzantium describes a recipe for invisible ink. He says to write down a message with crushed gallnuts dissolved in water. Then it could be revealed by being soaked by a sponge of ferrous sulfate. This recipe was inspired by the recipe for gall ink. Ferrous sulfate and crushed gallnuts dissolved in water both react to make ink so when they combine the message is revealed. In his Ars Amatoria, Roman poet Ovid noted of a primitive form of invisible ink using milk to be used in writing love letters. Naturalist Pliny the Elder also wrote of the tithymalus plant in his Natural History, and how its milk could be used for invisible ink. The first recorded use of the term steganography was by Johannnes Trithemius with his Steganographia, a book seemingly about summoning angels to hide messages. In reality however, the book was about steganography, the angel summoning being a cover text. Every angel corresponded to a different method of steganography.
He had written a letter to Arnold Bostius about his book, how it contained many methods of secret writing, how it could be used to communicate without speaking, signing or even nodding and much more. Bostius had died before he could receive the letter, however his colleagues had read and published it, accusing him of conversing with demons. Trithemius had also invited Charles de Bovelles to read his book before de Bovelles threw it away, claiming Trithemius was a magician. This situation led Trithemius to quit the book, not however, his interest in steganography. In his work Polygraphiae, Trithemius developed his Ave Maria cipher, a polyalphabetic substitution cipher and form of steganography that can hide information in a Latin praise of God. It consists of around 384 alphabets of 24 letters corresponding to 24 words to praise God. To encode a message, take the first letter of your message and replace that letter with the corresponding word in the first alphabet. Do that for the second, the third, and so on. "Conservator magnus conservans cuncta iuftis fuis in felicitatibus amen", for example, contains the concealed word SECRET. In the year 1606, Book I and II of the Steganographia were printed in Frankfurt, along with an incomplete Book III, and the Clavis Steganographie. The Clavis explained how to extract the secret of the Steganographia from Book I and II. Simply select an incantation to summon an "angel" and extract every other letter of every other word to find the secret steganographic method associated with that angel. With this publication came a slew of books vindicating Trithemius by explaining the steganography, acquitting him of magic. However, Book III was still widely regarded as a work of magic, with no clear way to extract its secrets. It would take until the late 1990s when Jim Reeds and Thomas Ernst independently discovered that it too, was secretly a work of steganography.
Numerous techniques throughout history have been developed to embed a message within another medium. Hiding a message in the title and context of a shared video or image. Misspelling names or words that are popular in the media in a given week, to suggest an alternative meaning. Hiding a picture that can be traced by using Paint or any other drawing tool.
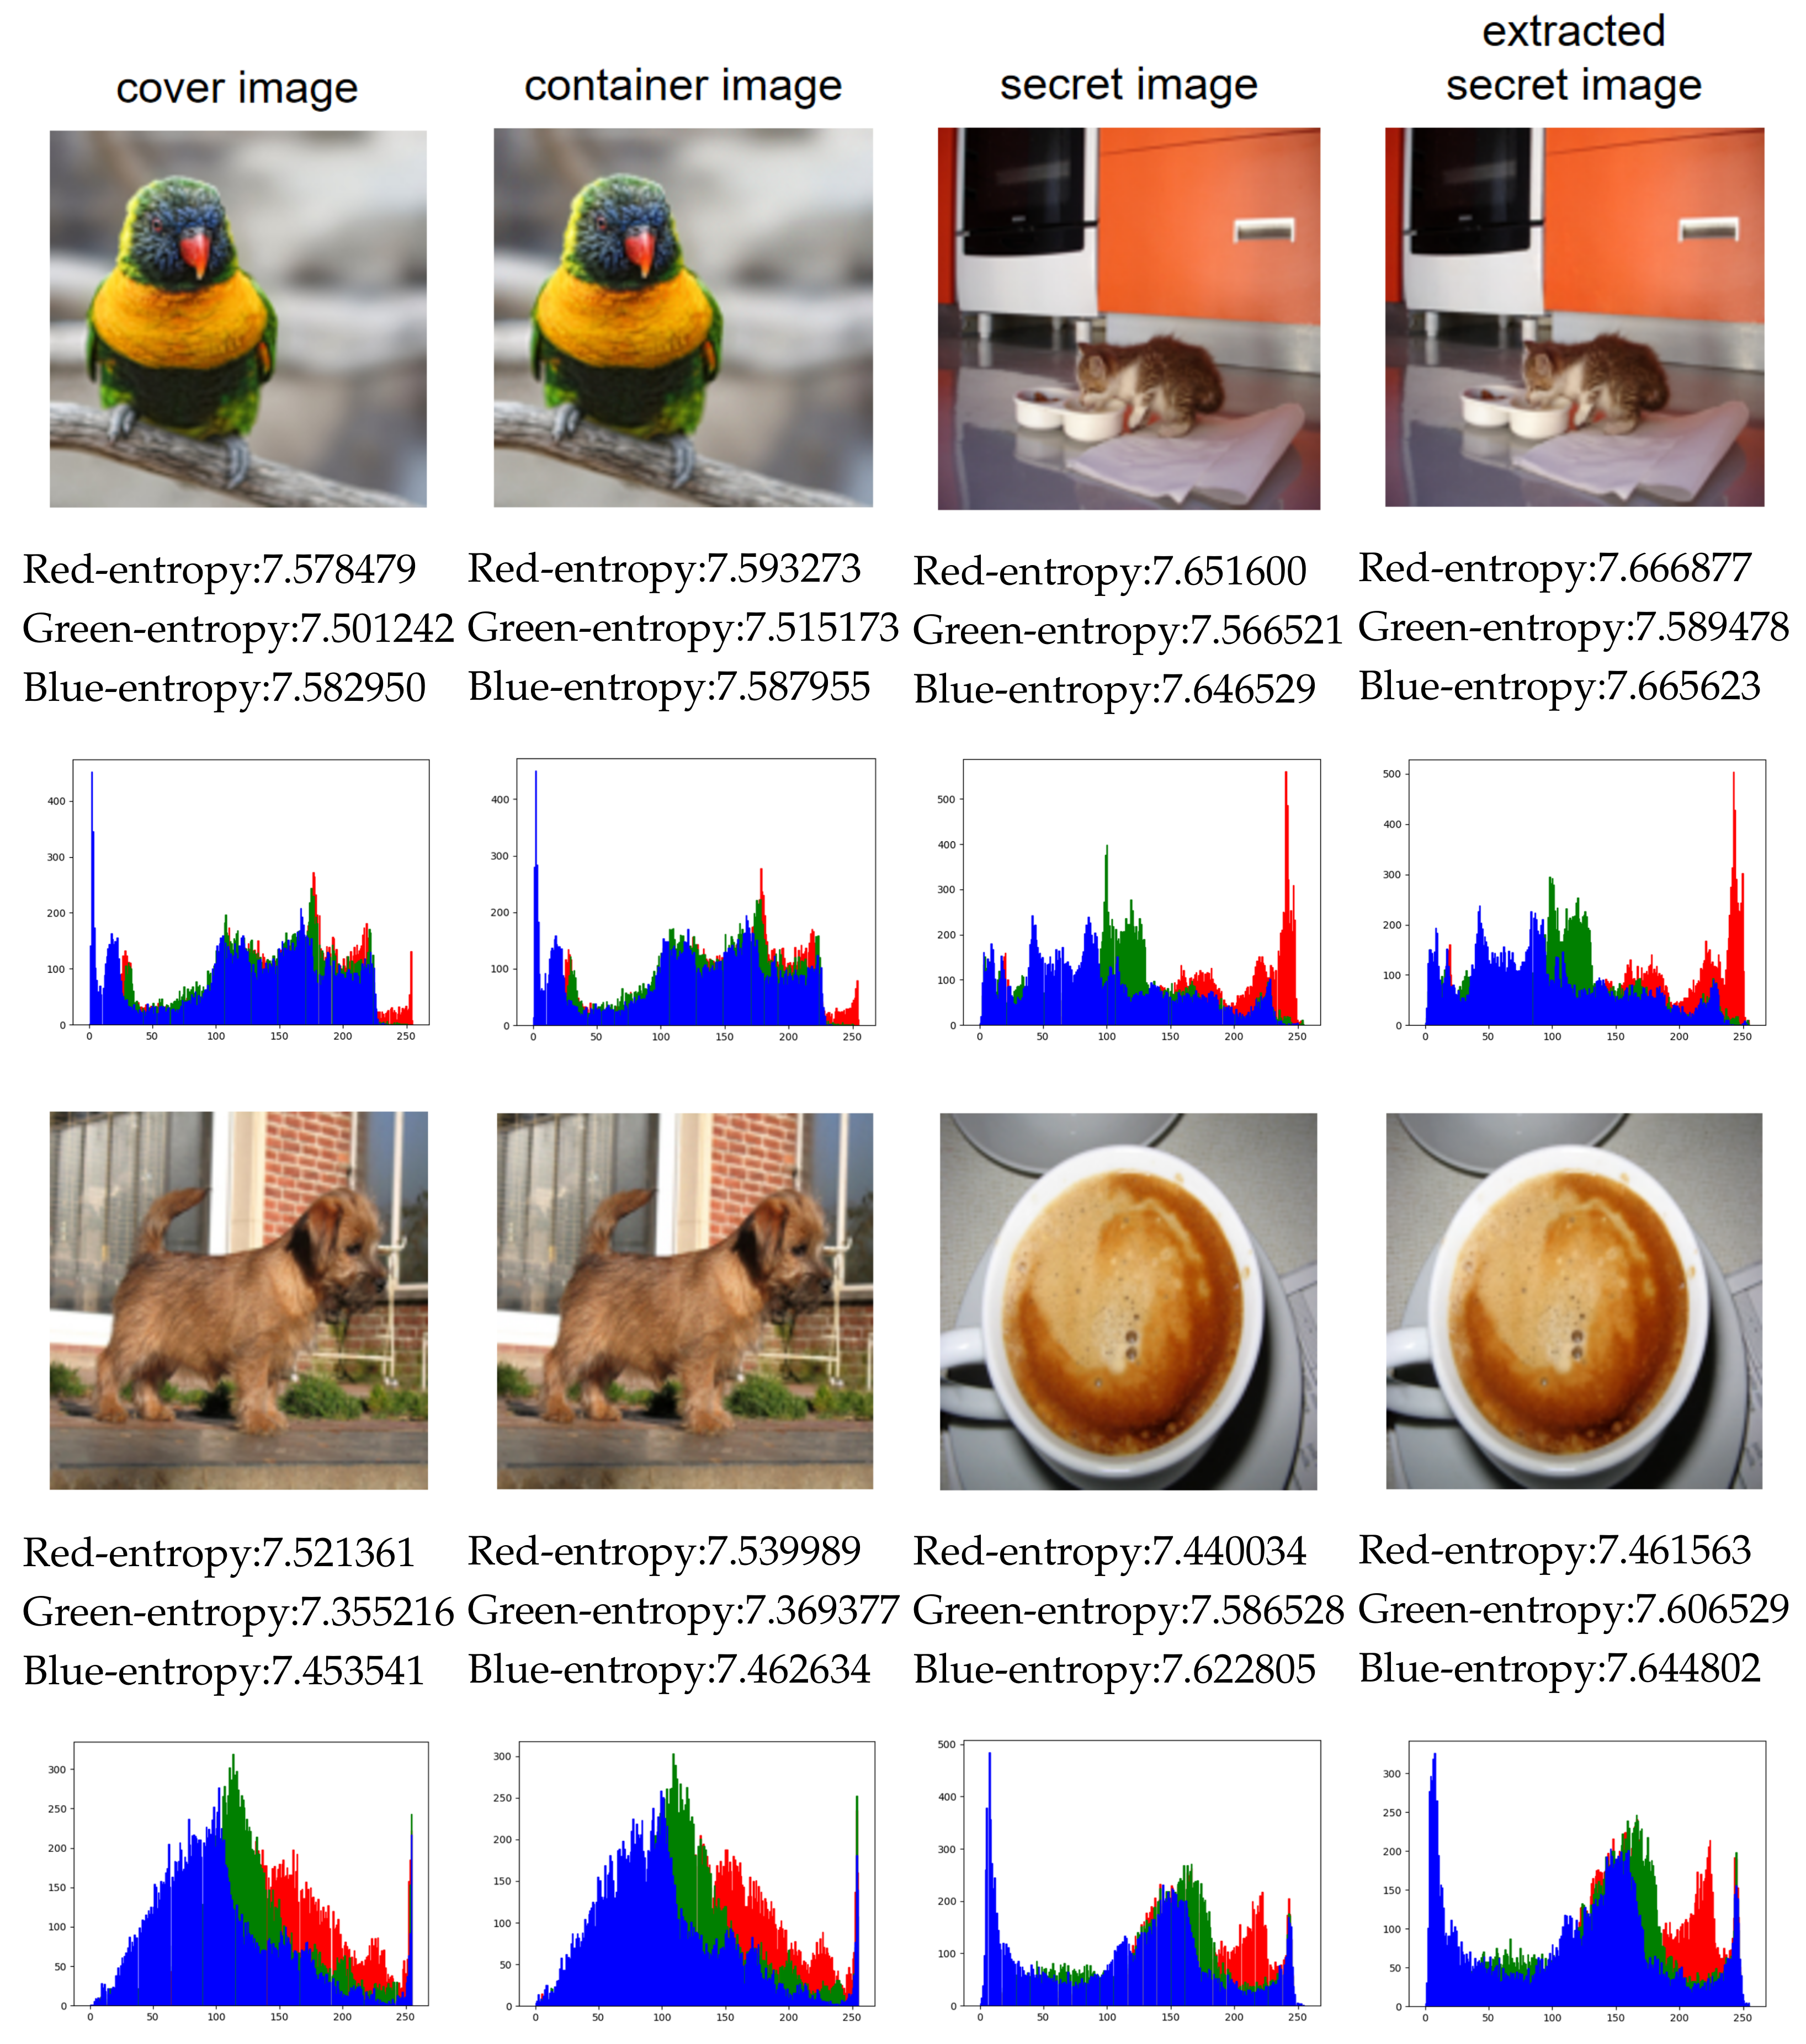
Figure 1: Deep Image Steganography Using Transformer and Recursive Permutation Since the dawn of computers, techniques have been developed to embed messages in digital cover mediums. The message to conceal is often encrypted, then used to overwrite part of a much larger block of encrypted data or a block of random data (an unbreakable cipher like the one-time pad generates ciphertexts that look perfectly random without the private key).
Examples of this include changing pixels in image or sound files, properties of digital text such as spacing and font choice, chaffing and winnowing, mimic functions, modifying the echo of a sound file (echo steganography), and including data in ignored sections of a file. Although not classic steganography, some types of modern color laser printers integrate the model, serial number, and timestamps on each printout for traceability reasons using a dot-matrix code made of small, yellow dots not recognizable to the naked eye (see: Printer tracking dots, for details).
Steganophony – the concealment of messages in Voice-over-IP conversations, e.g. the employment of delayed or corrupted packets that would normally be ignored by the receiver (this method is called LACK – Lost Audio Packets Steganography), or, alternatively, hiding information in unused header fields. WLAN Steganography – transmission of steganograms in Wireless Local Area Networks. A practical example of WLAN Steganography is the HICCUPS system (Hidden Communication System for Corrupted Networks) Discussions of steganography generally use terminology analogous to and consistent with conventional radio and communications technology. However, some terms appear specifically in software and are easily confused. These are the most relevant ones to digital steganographic systems: The payload is the data covertly communicated. The carrier is the signal, stream, or data file that hides the payload, which differs from the channel, which typically means the type of input, such as a JPEG image. The resulting signal, stream, or data file with the encoded payload is sometimes called the package, stego file, or covert message. The proportion of bytes, samples, or other signal elements modified to encode the payload is called the encoding density and is typically expressed as a number between 0 and 1. In a set of files, the files that are considered likely to contain a payload are suspects. A suspect identified through some type of statistical analysis can be referred to as a candidate.
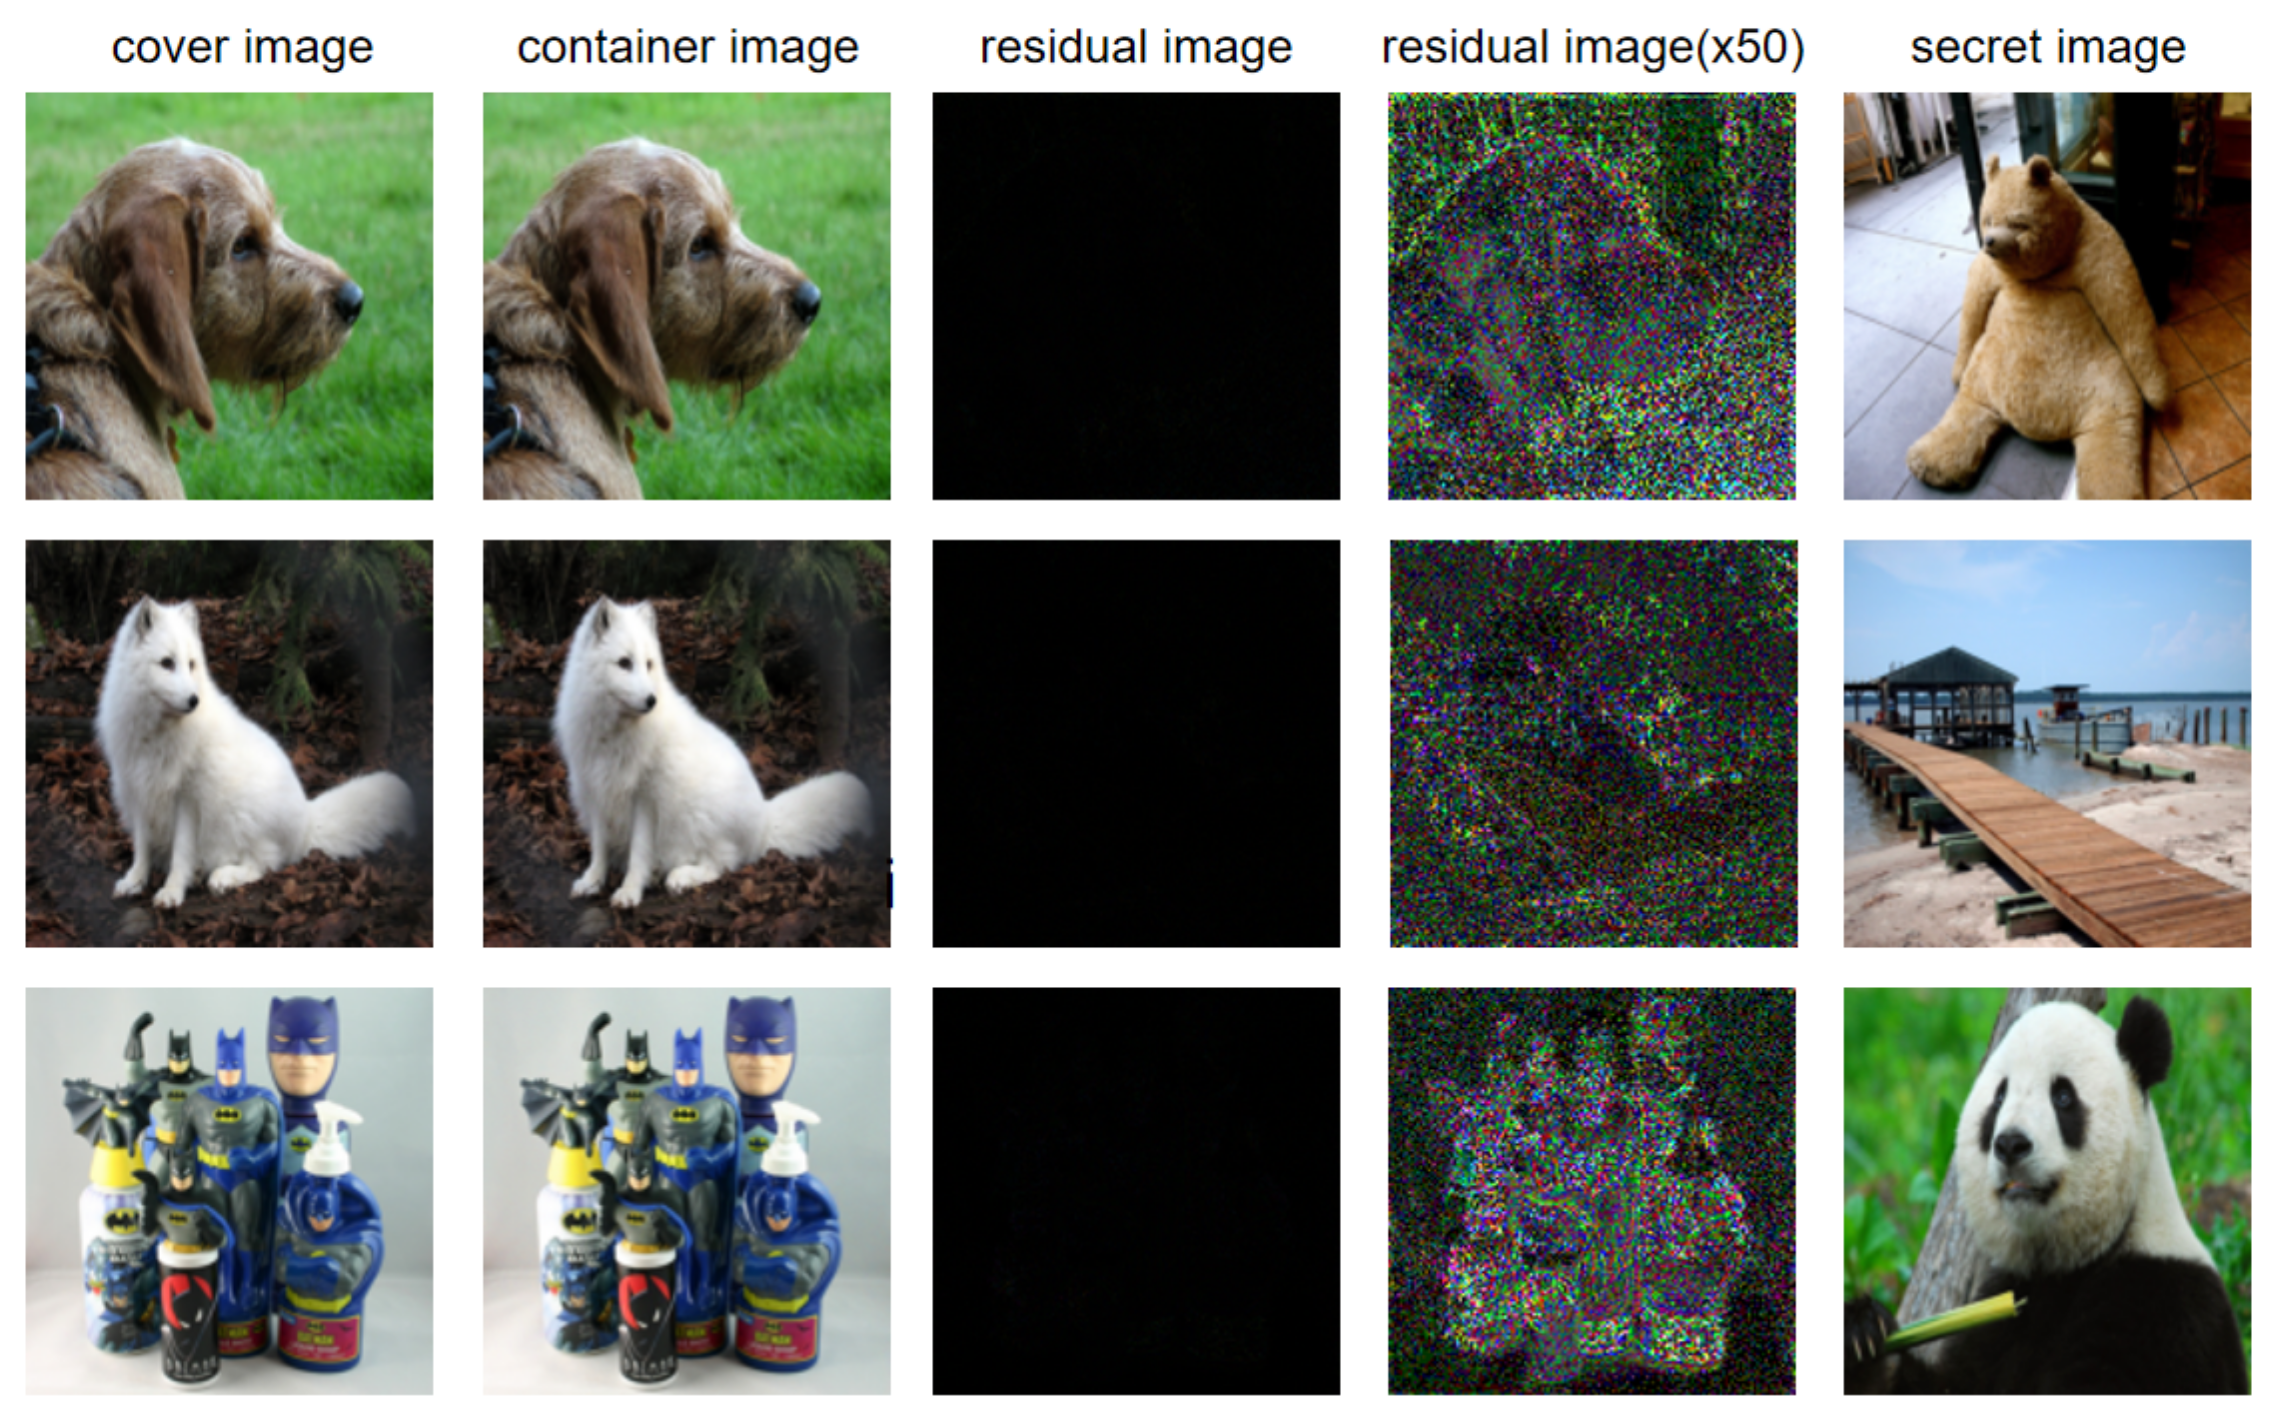
Figure 2: Deep Image Steganography Using Transformer and Recursive Permutation Some modern computer printers use steganography, including Hewlett-Packard and Xerox brand color laser printers. The printers add tiny yellow dots to each page. The barely visible dots contain encoded printer serial numbers and date and time stamps. The Electronic Frontier Foundation confirmed the marks are a forensic tracking tool, reportedly part of a secret agreement between printer manufacturers and governments to help track counterfeiters.
It is possible to steganographically hide computer malware into digital images, videos, audio and various other files in order to evade detection by antivirus software. This type of malware is called stegomalware. It can be activated by external code, which can be malicious or even non-malicious if some vulnerability in the software reading the file is exploited. Stegomalware can be removed from certain files without knowing whether they contain stegomalware or not. This is done through content disarm and reconstruction (CDR) software, and it involves reprocessing the entire file or removing parts from it. Various methods can be employed within CDR software to counter stegomalware with varying levels of mitigation relative to visual integrity disruption. Actually detecting stegomalware in a file can be difficult and may involve testing the file behaviour in virtual environments or deep learning analysis of the file.
Chosen stego attack: the stegoanalyst perceives the final target stego and the steganographic algorithm used. Known cover attack: the stegoanalyst comprises the initial conductive target and the final target stego. Known stego attack: the stegoanalyst knows the initial carrier target and the final target stego, in addition to the algorithm used. Stego only attack: the stegoanalyst perceives exclusively the stego target. Chosen message attack: the stegoanalyst, following a message selected by him, originates a stego target. Known message attack: the stegoanalyst owns the stego target and the hidden message, which is known to them.
2. System Architecture & Core Working Principles Passive steganalysis: does not alter the target stego, therefore, it examines the target stego in order to establish whether it carries hidden information and recovers the hidden message, the key used or both. Active steganalysis: changes the initial stego target, therefore, it seeks to suppress the transfer of information, if it exists.
An overview of digital steganography, particularly within images, for the computationally curious by Chris League, Long Island University, 2015 Examples showing images hidden in other images Information Hiding: Steganography & Digital Watermarking. Papers and information about steganography and steganalysis research from 1995 to the present. Includes Steganography Software Wiki list. Dr. Neil F. Johnson. Detecting Steganographic Content on the Internet. 2002 paper by Niels Provos and Peter Honeyman published in Proceedings of the Network and Distributed System Security Symposium (San Diego, CA, 6–8 February 2002). NDSS 2002. Internet Society, Washington, D.C. Covert Channels in the TCP/IP Suite Archived 23 October 2012 at the Wayback Machine – 1996 paper by Craig Rowland detailing the hiding of data in TCP/IP packets. Network Steganography Centre Tutorials Archived 16 December 2017 at the Wayback Machine. How-to articles on the subject of network steganography (Wireless LANs, VoIP – Steganophony, TCP/IP protocols and mechanisms, Steganographic Router, Inter-protocol steganography). By Krzysztof Szczypiorski and Wojciech Mazurczyk from Network Security Group. Invitation to BPCS-Steganography. Steganography by Michael T. Raggo, DefCon 12 (1 August 2004) File Format Extension Through Steganography by Blake W. Ford and Khosrow Kaikhah Computer steganography. Theory and practice with Mathcad (Rus) 2006 paper by Konakhovich G. F., Puzyrenko A. Yu. published in MK-Press Kyiv, Ukraine Stegomalware is a form of malicious software that leverages steganography techniques to conceal its code, configuration data, or command-and-control (C&C) communications within seemingly benign digital media such as images, audio files, videos, documents, or network traffic. It typically embeds encrypted or obfuscated payloads into digital media and only extracts and executes them at runtime, which makes traditional signature-based and sandbox-based detection significantly more difficult. Stegomalware has been observed in attacks ranging from advanced persistent threats (APTs) to financially motivated cybercrime, and is now the subject of dedicated academic surveys, research projects, and international law-enforcement initiatives. The key distinction between stegomalware and traditional obfuscated malware lies in the encoding location. After obfuscation, malicious code remains present within the executable and can theoretically be discovered through static analysis. In contrast, stegomalware hides the payload entirely within a cover medium (image, audio, etc.), remaining invisible until the malware dynamically extracts and executes it at runtime.
Stegotext (R): An innocent-looking digital asset (image, audio file, etc.) into which the malicious payload is embedded. Secret key (sk): A key used by the embedding and extraction algorithms, typically hardcoded into the malware. Payload (p): The actual malicious code, configuration data, or C&C commands hidden within the stegotext. The malware extracts the payload at runtime using the secret key and either executes it directly or uses it to download additional stages of the attack.
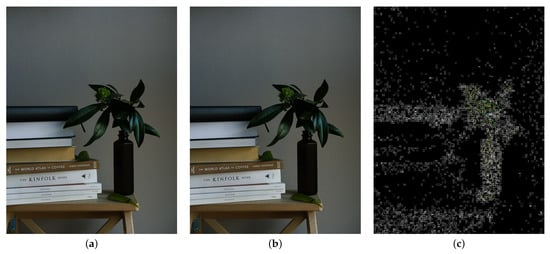
Stegomalware can be classified into several types based on deployment method: Figure 3: Detection of Image Steganography Using Deep Learning and Ensemble ... Type 0 (Autonomous): Both the stegotext and extraction algorithm are embedded within the malware application itself. The malicious payload is extracted and executed locally without external communication. Type I (Update): The stegotext and secret key are downloaded from a remote server at runtime; only the extraction algorithm is included in the malware. This variant is more flexible, allowing attackers to push updated payloads. Type II (External Algorithm): Neither the stegotext nor the extraction algorithm are distributed with the malware; both are fetched from an attacker-controlled infrastructure, providing maximum flexibility and evasion.
HUGO (High Undetectable steGO) (2010): Minimizes detectable distortion by distributing the payload across multiple pixels, achieving embedding capacity with reduced statistical footprint. WOW (Wavelet Obtained Weights) (2012): Embeds data preferentially in textured regions of images where modifications are less perceptually noticeable. UNIWARD (Universal Wavelet Relative Distortion) (2014): Uses a universal distortion function applicable to multiple image formats, balancing payload capacity with undetectability. HILL (2014): Applies high-pass and low-pass filters to identify robust embedding regions. MiPOD (Minimizing the Power of Optimal Detector) (2016): Designed to minimize the power of theoretical optimal steganalysis detectors.
Embedding in DCT coefficients (used in JPEG compression) Embedding in DWT coefficients (used in lossless formats) Spread spectrum techniques, which distribute the payload across many frequency components Transform domain methods are generally more resistant to noise, compression, and image transformations than spatial methods. SGAN (Steganographic GAN) (2017): First GAN applied to steganography, using a generator, discriminator, and steganalysis network. ASDL-GAN (2017): Performs automatic steganographic distortion learning at the pixel level. SteganoGAN (2019): Improves upon earlier GAN models, achieving higher embedding capacity and robustness. HiGAN (Hiding Images GAN) (2020): Enables hiding one image within another while maintaining visual plausibility. GAN-based approaches are more resilient to standard steganalysis attacks but remain an emerging threat requiring further research.
Stegomalware has been documented in numerous high-profile cyber attacks and campaigns. Notable examples include: Operation Shady RAT (2011): Used digital images to hide command-and-control server addresses in targeted espionage. Duqu (2011): Embedded victim data into JPEG files to exfiltrate industrial control system information. Zeus/Zbot (2014): Masked banking configuration data inside JPEG files exploited via malvertising. Gatak/Stegoloader (2015): Hid shellcode in PNG files for software licensing attacks and bot command execution. TeslaCrypt (2015): Embedded C&C commands and ransomware keys in JPEG images. Cerber (2016): Concealed executable ransomware code in JPEG files distributed via phishing. DNSChanger (2016): Embedded malicious code in PNG files for DNS hijacking campaigns. Sundown Exploit Kit (2017): Distributed exploit code in PNG files via malvertising. AdGholas (2017): Used JPEG steganography to distribute ransomware via malvertising. Synccrypt (2017): Hidden ransomware components in JPEG-steganographic encrypted archives. ZeroT/PlugX (2017): Hid Remote Access Trojan payloads in BMP files for espionage. Loki Bot (2018): Concealed malware installers in JPEG and video files. Waterbug (APT28) (2019): Injected malicious DLLs into WAV audio files. Shlayer (macOS adware) (2019): Hid malicious URLs in JPEG files via malvertising.
Phishing emails with malicious attachments or links Malvertising campaigns using malicious banner advertisements Exploit kits through compromised or malicious websites Legitimate application vulnerabilities (e.g., watering-hole attacks) Fake software distribution (cracked software, keygen tools) 3. Software Implementation, Frameworks & Protocols Payload delivery: Stego images contain full executable code or shellcode. C&C communication: Hidden data contains server addresses or command instructions. Data exfiltration: Stolen data encoded into images to evade network inspection. Update mechanism: New malware versions delivered via stegomalware.
A variety of publicly available steganography tools can be repurposed for stegomalware creation: Steghide (2003): Open-source; LSB-based; supports JPEG, BMP, WAV, AU formats OpenPuff (2004): Java-based; multi-format support (BMP, JPEG, GIF, PNG, video) Xiao (2006): Simple Windows GUI; basic LSB embedding in BMP and WAV OpenStego (2015): Open-source; user-friendly interface; supports multiple formats StegExpose: Detection tool; statistical analysis for finding embedded data Binwalk: Firmware analysis and data extraction; useful for forensics Aperi'Solve: Web-based steganalysis tool combining multiple detection methods Advanced algorithms such as UNIWARD, HILL, WOW, and MiPOD require implementation from research papers rather than ready-to-use tools.
Detecting stegomalware is challenging because modifications are designed to be statistically invisible. Traditional antivirus solutions struggle since they primarily analyze executable files and network traffic, not embedded multimedia. Visual steganalysis: Human inspection for anomalies (rarely effective for modern techniques) Statistical steganalysis: Analysis of pixel distributions and histograms Signature-based steganalysis: Matching known tool signatures or patterns Rich model steganalysis: Domain-specific feature extraction with ensemble classifiers Deep learning-based steganalysis: Convolutional neural networks to distinguish natural from stego images Universal (blind) steganalysis: General-purpose detection regardless of embedding algorithm Very low embedding rates Adversarial training or GAN-based steganography Mixed file formats in datasets Encrypted payloads File-level analysis: Scanning for steganography signatures using tools like StegExpose or binwalk Dynamic behavior analysis: Using sandboxes to observe payload extraction and execution Network monitoring: Detecting suspicious patterns in traffic indicating exfiltration Machine learning models: Deploying trained classifiers to identify stego images Detection frameworks have been proposed for datacenters, cloud (AWS, Azure), and multi-cloud environments.
Raising awareness among law enforcement and the public about steganography threats Sharing threat intelligence on information hiding misuse Tracking emerging steganographic techniques in cybercrime Training law enforcement and forensic professionals Supporting investigations involving steganography CUIng's threat assessment identified steganography in diverse crimes including child sexual abuse material (CSAM), industrial espionage, enterprise cyberattacks, credit card fraud, and backdoor injection.
Analysis and cataloging of existing steganographic tools Development and validation of state-of-the-art steganalysis detectors Creation of a unified online platform for forensic analysis Field validation with law enforcement use cases Training and capacity building for agencies and institutes Legal frameworks for court admissibility across European jurisdictions UNCOVER demonstrated that operational steganalysis improves with metadata or partial information about the original media, such as JPEG steganalysis using leaked cover thumbnails.
Limited public datasets: Only the proprietary MalJPEG dataset (157,000 samples) exists; inaccessible to researchers. Lack of real-payload evaluation: Most research uses generic steganographic images, not actual malware-embedded images. Adversarial robustness: Attackers use adversarial training and GANs to evade detectors. Multi-format detection: Methods specialize in single formats (JPEG) and struggle with mixed datasets. Audio/video steganography: Limited research on detecting steganography in WAV, MP3, and video files. Stegomalware in neural networks: Emerging threat of embedding payloads in pre-trained deep learning model weights. Scalability in enterprises: Large-scale deployment introduces computational and false-positive challenges. Emerging techniques: Novel GAN-based and context-aware steganography may outpace detection. Future research priorities include: Developing public stegomalware datasets and benchmarks Evaluating detectors against real malware payloads Cross-domain and cross-format steganalysis methods Integrating cryptanalysis with steganographic detection Harmonizing legal frameworks for cross-border investigations 4. Practical Deployment, Analysis & Case Studies A copy detection pattern (CDP) or graphical code is a small random or pseudo-random digital image which is printed on documents, labels or products for counterfeit detection. Authentication is made by scanning the printed CDP using an image scanner or mobile phone camera. It is possible to store additional product-specific data into the CDP that will be decoded during the scanning process. A CDP can also be inserted into a 2D barcode to facilitate smartphone authentication and to connect with traceability data.
CDPs have also been described as a type of optical physical unclonable function. While they have been cited as a "powerful tool to detect copies", it is noted however that CDPs "require an extensive knowledge of printing technologies" because the printing process introduces variation that is foundational to copy detection. In, practical recommendations on printing stability, taking into account scanning quality of the detector, and managing the security of printing facilities. In, a decision theoretic-model is developed to determine optimality properties of CDPs in idealised conditions. Based on an additive Gaussian noise assumption for the print channel and an attacker who takes optimal decisions, it is shown that the most effective decision function is a correlation function. In, different new CDP detection metrics are proposed and confirmed a significant improvement of copy detection accuracy. In, the impact of multiple printed observations of the same CDP is studied, and it is shown that the noise due to the printing process can be reduced but not completely removed, due to deterministic printing artefacts. In, a theoretical comparison is made between the performance of CDPs and natural randomness. In and, deep learning methods are used to recover portions of the digital CDP, and it is shown that these can be used to launch clonability attacks. In, quality control challenges are reviewed, and an inline verification system of secure graphics is proposed for high security printing applications. In, different attack methods based on restoration of the scanned CDP are tested. and show that a classifier based on support vector domain description outperforms other classification methods.
As a means of providing a product authentication service using the Internet of Things. For securing identification documents, in combination with digital watermarks and 2D barcodes. They were used in 2006 to protect identification badges during the FIFA World Cup. Integrated into QR Codes to enable consumers to check product authenticity with a smartphone application. For authenticating pharmaceutical packaging.
This repository made for an AI-powered steganography detection system using deep learning. The project includes training a Convolutional Neural Network (CNN) on stego images and detecting hidden information inside digital images. This project can be a great starting component of a Security Operations Center (SOC), Endpoint Detection & Response (EDR), or Security Orchestration, Automation, and Response (SOAR) system, by giving it an automated layer of anti-malware analysis in context of a security framework.
The dataset consists of clean and stego images, which must be correctly organized into separate folders before training. If the dataset is not structured properly, use the organize_data.py script to arrange the files. Make sure to manually edit the code, especially the part with the condition coefficent, cause it really varies based on the training proccess.
Ensure that Python 3.10+ is installed. Use the following command to install dependencies: If you want to find out more about the usage of CNNs, feel free to checkout our article . AI steganography Detection project can be a great starting component of a Security Operations Center (SOC), Endpoint Detection & Response (EDR), or Security Orchestration, Automation, and Response (SOAR) system, by giving it an automated layer of anti-malware analysis in context of a security framework.
A Hybrid Machine Learning & Cryptography Project > Hiding data in images using LSB Steganography and detecting it using a custom SRNet Deep Learning model. 5. Performance Evaluation & Extended Technical Observations Stego-SRNet is a project designed to explore the boundaries of digital forensics. It consists of two main components: While standard CNNs focus on image content (objects, colors), this model is designed to suppress content and focus on noise residuals , allowing it to spot the statistical anomalies introduced by steganography.
Due to GPU hardware limitations during the training phase, the SRNet model was trained on and is optimized for images of size 150x150 pixels . The model detects LSB artifacts. Converting images to lossy formats (like JPEG ) acts as a filter that "cleans" these artifacts, causing the model to classify the image as "Clean" (False Negative). Always use PNG or BMP .
We take a secret text message, encrypt it (optional), convert it to binary, and replace the least significant bit of the image pixels with these bits. To the human eye, the change is invisible. The dataset used to train this model was custom generated to ensure a perfect 50/50 balance: The model was evaluated on a held-out test set containing equal numbers of Cover and Stego images.
This system is designed to be straightforward to use for research and testing purposes. The workflow is divided into two main phases: Data Hiding and Detection. To test the model or create new training data, you first need to generate "Stego-images." Contributions are welcome, especially those that address the current resolution limitations! Deep Learning–based steganalysis system using TensorFlow and SRNet to detect hidden payloads in lossless images with high accuracy.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Steganography • https://en.wikipedia.org/wiki/Stegomalware • https://en.wikipedia.org/wiki/Copy%20detection%20pattern • https://github.com/7megaumka7/AI-steganography-detection • https://github.com/deepanshu160105/Steganograph_DL_deep • https://github.com/asaishivanand-design/steganography-detection-cnn
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Steganography Detection In Digital Images Using Deep Learning.
[*] Metasploit Scan Running on Target Subnet for Steganography Detection In Digital Images Using Deep Learning... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |