Complete Technical Paper Content — Stride Threat Modeling Tool
Overview & System Context
Stride Threat Modeling Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9541 Words · Real Software Screenshots: 1 1. Executive Overview & Technical Background STRIDE (Spoofing, Tampering, Repudiation, Information disclosure, Denial of service, Elevation of privilege) is a threat model for identifying computer security threats. Developed by Praerit Garg and Loren Kohnfelder at Microsoft, it provides a mnemonic for security threats in six categories. Each STRIDE category corresponds to a core principle of information security: Authenticity, Integrity, Non-repudiability, Confidentiality, Availability and Authorization.
Threat modeling is a process by which potential threats, such as structural vulnerabilities or the absence of appropriate safeguards, can be identified and enumerated, and countermeasures or controls prioritized. Threat modeling provides defenders with a systematic analysis of what controls or defenses needed to be included, given the nature of the system, the probable attacker's profile, the most likely attack vectors, and the most likely assets to be attacked by an attacker. Threat modeling answers questions like "Where am I most vulnerable to attack?", "What are the most relevant threats?", and "What do I need to do to safeguard against these threats?". Similar to threat modeling, risk assessments and threat attack modeling can be used informally in our day to day lives to address risks such as bullies, or even to prioritize military defensive preparations as since antiquity.
Most threat modeling approaches use data flow diagrams (DFD). DFDs were developed in the 1970s as tool for system engineers to communicate, on a high level, how an application caused data to flow, be stored, and manipulated by the infrastructure upon which the application runs. Traditionally, DFDs utilize only four unique symbols: data flows, data stores, processes, and interactors. In the early 2000s, an additional symbol, trust boundaries, were added to improve the usefulness of DFDs for threat modeling. Once the application-infrastructure system is decomposed into its five elements, security experts consider each identified threat entry point against all known threat categories. Once the potential threats are identified, mitigating security controls can be enumerated or additional analysis can be performed.
In computer security, a threat is an action or event that would result in an unwanted or negative impact to a computer system, software, data, or other IT resources. Many cyber threats are enabled by vulnerabilities. A threat can be either a negative "intentional" event like hacking or an "accidental" negative event or otherwise a circumstance, capability, action, or event (incident is often used as a blanket term). A threat actor who is an individual or group that can perform the threat action, such as exploiting a vulnerability to actualise a negative impact. An exploit is a vulnerability that a threat actor used to cause an incident.
Figure 1: Figure 1: Verified System Architecture & Pipeline Workflow The term "threat" relates to some other basic security terms as shown in the following diagram: A resource (both physical or logical) can have one or more vulnerabilities that can be exploited by a threat agent in a threat action. The result can potentially compromise the confidentiality, integrity or availability properties of resources (potentially different than the vulnerable one) of the organization and others involved parties (customers, suppliers). The so-called CIA triad is the basis of information security. The attack can be active when it attempts to alter system resources or affect their operation: so it compromises Integrity or Availability. A "passive attack" attempts to learn or make use of information from the system but does not affect system resources: so it compromises Confidentiality.
OWASP (see figure) depicts the same phenomenon in slightly different terms: a threat agent through an attack vector exploits a weakness (vulnerability) of the system and the related security controls causing a technical impact on an IT resource (asset) connected to a business impact. A set of policies concerned with information security management, the Information security management systems (ISMS), has been developed to manage, according to risk management principles, the countermeasures in order to accomplish to a security strategy set up following rules and regulations applicable in a country.
Countermeasures are also called security controls; when applied to the transmission of information are named security services. The overall picture represents the risk factors of the risk scenario. The widespread of computer dependencies and the consequent raising of the consequence of a successful attack, led to a new term cyberwarfare. Nowadays the many real attacks exploit Psychology at least as much as technology. Phishing and Pretexting and other methods are called social engineering techniques. The Web 2.0 applications, specifically Social network services, can be a mean to get in touch with people in charge of system administration or even system security, inducing them to reveal sensitive information. One famous case is Robin Sage. The most widespread documentation on computer insecurity is about technical threats such as a computer virus, trojan and other malware, but a serious study to apply cost effective countermeasures can only be conducted following a rigorous IT risk analysis in the framework of an ISMS: a pure technical approach will let out the psychological attacks that are increasing threats.
Types of threats: Physical damage: fire, water, pollution Natural events: climatic, seismic, volcanic Loss of essential services: electrical power, air conditioning, telecommunication Compromise of information: eavesdropping, theft of media, retrieval of discarded materials Technical failures: equipment, software, capacity saturation Compromise of functions: error in use, abuse of rights, denial of actions Note that a threat type can have multiple origins.
Deliberate: aiming at information asset spying illegal processing of data Accidental equipment failure software failure Environmental natural event loss of power supply Negligence: Known but neglected factors, compromising the network safety and sustainability Computer viruses Trojan horses Worms Rootkits Spyware Adware Ransomware Fileless malware Spoofing of user identity Tampering Repudiation Information disclosure (privacy breach or Data leak) Denial of Service (D.o.S.) Elevation of privilege Microsoft previously rated the risk of security threats using five categories in a classification called DREAD: Risk assessment model. The spread over a network of threats can lead to dangerous situations. In military and civil fields, threat level has been defined: for example INFOCON is a threat level used by the US. Leading antivirus software vendors publish global threat level on their websites.
Threat intelligence is the practice of collecting and analyzing information about potential and current threats to a system. This information can include indicators of compromise, attack techniques, and threat-actor profiles. Information security audit Penetration test Many organizations perform only a subset of these methods, adopting countermeasures based on a non-systematic approach, resulting in computer insecurity. Information security awareness is a significant market. There has been a lot of software developed to deal with IT threats, including both open-source software and proprietary software.
Manual and automated intelligence gathering and threat analytics Comprehensive methodology for real-time monitoring including advanced techniques such as behavioral modelling Use of advanced analytics to optimize intelligence, generate security intelligence, and provide Situational Awareness Technology and skilled people leveraging situational awareness to enable rapid decisions and automated or manual actions Cyber threat hunting Emergency management – Dealing with all humanitarian aspects of emergencies, i.e. societal threats Internet Engineering Task Force (IETF) Information security audit Information security Intrusion detection system IT risk Physical security Vulnerability management Ever pushed code feeling pretty darn good about it, only to have that sinking feeling when a security issue pops up later? Yeah, me too. 13 years in this industry, and I can tell you, surprises in security are rarely the good kind. We build complex systems, juggling features, deadlines, and performance, and sometimes, just sometimes, security feels like this mystical thing we bolt on at the end, hoping for the best. But hope, as they say, isn’t a strategy, especially not in cybersecurity.
That’s where threat modeling comes in. Threat modeling is a practical, engineering discipline. It’s about proactively looking at your system before the bad guys do, figuring out where the weaknesses might be, and fixing them before they become headlines. It’s about shifting security left, making it part of the design conversation, not just an afterthought during a frantic incident response.
Now, there are various ways to approach threat modeling, but one framework that’s stood the test of time, especially for folks building software, is STRIDE that helps us systematically brainstorm how things could go wrong. It gives us a common language and a structured way to think about potential attacks. We are going to ditch the overly academic jargon and get practical. We will break down what STRIDE is, walk through how to actually use it with three different real-world-ish scenarios (think APIs, IoT, and cloud platforms), share some hard-won tips from the trenches, and even suggest some ways you could visualize this stuff later on.
My goal here isn’t just to define STRIDE, but to show you how it can become a valuable tool in your engineering toolkit. It’s about making security less scary and more systematic. So, grab a coffee, settle in, and let’s talk about how to stride confidently towards more secure systems. The magic of STRIDE lies in its acronym, which covers six key categories of security threats. When you are looking at a system component – whether it’s a user logging in, data moving across a network, or a file being saved – you ask yourself: how could someone mess with this using one of the STRIDE methods? S - Spoofing: This is all about impersonation. An attacker pretends to be someone or something they’re not. Think fake login pages trying to steal your credentials, or a malicious server mimicking a legitimate one to intercept data. The security property being violated here is Authenticity . Are you really talking to who you think you are talking to? Is that user really who they claim to be? T - Tampering: This one’s about unauthorized modification. Attackers mess with data – maybe changing values in a database, altering code as it runs, or modifying data packets flying across the network. Imagine someone changing the amount on a financial transaction or tweaking configuration files to gain an advantage. The property under attack is Integrity . Can you trust that your data and your system haven’t been illicitly changed? R - Repudiation: This is the “I didn’t do it!” threat. An attacker performs some malicious action and then tries to deny having done it. Or, perhaps more commonly, the system simply lacks the ability to prove who did what. If you can’t prove a user placed that order or deleted that critical file, you have a repudiation problem. The violated property here is **Non-** repudiability . Can you trace actions back to the actor responsible? I - Information Disclosure: This is about confidentiality breaches. Sensitive information gets exposed to people who shouldn’t see it. This could be anything from error messages revealing system internals, to attackers accessing private user data, to sniffing unencrypted network traffic. The property at stake is Confidentiality . Is your sensitive data kept secret from unauthorized eyes? D - Denial of Service (DoS): Pretty self-explanatory – making a system or service unavailable to legitimate users. This could be by overwhelming it with traffic (like a classic flood attack), crashing a service, or locking out user accounts. The violated property is Availability . Can authorized users access the system and its data when they need to? E - Elevation of Privilege: This is when someone gains more permissions than they should have. A regular user somehow gets admin rights, or one application component manages to execute code with the privileges of another, more trusted component. This is often the goal that enables other attacks. The violated property is Authorization . Are users and components restricted to only the actions and data they are explicitly allowed to access? So if I were to summarize all of these in a single table, it would be something like this: Ideally, you want to apply STRIDE during the design phase of the software development lifecycle (SDLC). Finding a flaw on a whiteboard is infinitely cheaper and easier to fix than finding it in production code. However, it’s never too late. You can apply STRIDE to existing systems, new features, or even specific changes to understand the security implications.
Before we go deep into this novel approach, let me summarize the overall process from this article in a simplistic diagram. Before we go deep into process, let’s look at the high level process how does it look like: Okay, we know the what (the STRIDE categories) and the why (proactive security!). Now, let’s get into the how. How do you actually do a STRIDE analysis? It’s not just about chanting the acronym; it’s a process. Here’s a typical flow, keeping in mind this can be adapted: You can’t find threats in something you don’t understand. The first step is always to visualize the system you are analyzing.
The most common way to do this in threat modeling is using Data Flow Diagrams (DFDs) . A DFD is just a structured way to show how data moves through your system. Key symbols you will use are: This is where the STRIDE mnemonic shines. Go through your DFD, element by element (each process, data store, data flow, and even external entity interaction). For each element, systematically ask the STRIDE questions: That’s a useful starting point but it leaves you asking the same six questions over and over, without telling you how to think about where the gaps actually live or why an attacker would exploit them. You end up with a bullet list of “possible threats” rather than a rich map of all the angles you need to sweep.
To fill that gap, I have developed a 360° thinking blueprint for each STRIDE category, four complementary “lenses” you can peer through, a mini-checklist of red-flags, and reflective prompts to spark concrete scenarios. Use it against any DFD element, at any level (1/2), and you will move from rote questions to real insight: precisely where your system is vulnerable, how an attacker might work their way in, and what defenses belong at each step.
Below you will find the full blueprint your new go-to process whenever you sit down with a whiteboard or a DFD. Run the Four-Lens Sweep for Each STRIDE Category For each category you have marked, work through the four lenses in order: As you identify potential threats, document them! A simple list or spreadsheet works fine. Include: For the threats you have decided are worth addressing (usually the higher-risk ones), brainstorm countermeasures. What security controls, design changes, or coding practices can prevent or mitigate this threat? Document these proposed mitigations alongside the threats. Walk through your findings with teammates developers, architects, testers, ops.Confirm that your mitigation ideas line up with real-world constraints and that no new gaps emerge.Make this four-lens sweep part of design reviews or “definition of done” for major stories.
Review the identified threats and proposed mitigations. Do the mitigations actually address the threats? Are there any gaps? Does implementing one mitigation introduce another threat? This is often an iterative process. Keep your threat register live and revisit it whenever designs change. This might seem like a lot, but starting small and focusing on critical parts of your system makes it manageable. Now, let’s see this process in action with a few scenarios.
Theory is great, but let’s see STRIDE in action. Imagine we are building a core piece of an e-commerce platform: the Checkout API. This is a backend REST API, likely written in something like Python, Java, or Node.js. Its job is to handle the final stage of a purchase. It receives details from the customer’s frontend (web or mobile app), including: Repeat for every STRIDE category - Do this in turn for Spoofing, Tampering, Repudiation, Information Disclosure, DoS, Elevation of Privilege for each DFD element in your scope.
Threat Scenario (TAMP-01): Attacker modifies totalAmount in the JSON payload (e.g. 100 → 1) before TLS termination on a misconfigured segment, causing under-priced order. This demonstrates the exact four-lens STRIDE approach from your document, applied end-to-end to the Checkout API scenario.
2. System Architecture & Core Working Principles Likewise once you complete this activity end-to-end for both diagrams and entire feature/functionality, your final threat register would look something like below: I will give you two scenarios with Level 1 and Level 2 DFD diagrams and you have to now work on the above STRIDE lens and apply it strategically as a part of your homework exercise.
Let’s shift gears from pure web APIs to the interconnected world of the Internet of Things (IoT). Consider a common smart home device: a Smart Lock. Users can lock/unlock their door using a mobile app, grant temporary access to guests, and check the lock’s status remotely. For our final scenario, let’s tackle something bigger and more complex: a multi-tenant, cloud-based data analytics platform.
Think of a service where different companies (tenants) can upload their datasets, run complex analysis jobs, and visualize the results through dashboards. This platform likely involves numerous microservices running in a cloud environment (like AWS, Azure, or GCP). Alright, we have seen STRIDE applied to a few different systems. But knowing the theory and making it work smoothly within a busy team are two different things. After 13 years wrestling with security in real-world projects, here are some practical tips – the stuff you learn by doing (and sometimes by messing up).
Yes, there are tools in the market! OWASP also has resources, and other commercial tools exist. But remember: the tool supports the process, it doesn’t replace the thinking. A fancy tool won’t help if you don’t understand the system or the STRIDE categories. Honestly, the biggest challenge often isn’t technical; it’s cultural. Threat modeling works best when it’s a collaborative effort .
Get developers, testers, architects, and security folks in a room (virtual or physical). Developers know the code inside out, testers know how things break, architects see the big picture, and security brings the threat landscape perspective. Don’t let it become a security team throwing findings over the wall. Make it a shared responsibility, a learning opportunity for everyone involved. When developers understand the why behind a security requirement, they’re much more likely to implement it effectively. Foster a culture where asking “What could go wrong here?” is a normal part of building software.
Ultimately, STRIDE is a means to an end: building more secure, resilient systems. It provides structure and helps ensure you are not missing entire categories of threats. Use it pragmatically, adapt it to your team’s workflow, and focus on the collaborative process of identifying and mitigating real risks. So, the next time you are designing a new feature or system, give it a try. Sketch out a quick DFD, run through the STRIDE categories, and see what you uncover. You might be surprised at how this simple framework can help you build more robust and resilient software. Keep learning, keep questioning, and stride on! Introduction In today’s cloud-native world, APIs are the backbone of digital ecosystems connecting microservices, external partners, and end-users alike. But with … Introduction Think of DNS like the Internet’s phone book: it turns names you understand into addresses computers use. In this guide, we’ll walk through four simple views … Threat modeling is one of the most powerful and misunderstood practices in cybersecurity. You’ve probably seen it treated as a compliance checkbox, or as an abstract exercise disconnected from real engineering. But when done properly, threat modeling becomes a design superpower.
Among all threat modeling frameworks, STRIDE remains the most widely taught and globally adopted. Originally developed at Microsoft in 1999, STRIDE gives you a structured way to think about how systems can fail securely, and how attackers might exploit those failures. This guide covers STRIDE: what it is, how to apply it, where it excels, where it struggles in modern systems, and how it adapts to AI and agentic architectures.
The STRIDE threat model is a threat classification framework originally created by Loren Kohnfelder and Praerit Garg at Microsoft in 1999. It was later formalized within Microsoft’s Security Development Lifecycle (SDL) and popularized in Adam Shostack’s 2014 book Threat Modeling: Designing for Security . STRIDE is an acronym representing six categories of threats, each mapped to a violated security property: Rather than listing specific attacks, STRIDE provides a structured lens through which to analyze systems. It is typically applied by: Although originally designed for traditional, human-written software with predictable control flows, STRIDE remains the foundation of threat modeling education worldwide.
Here’s what each of the six STRIDE categories look like in practice and in modern systems. Spoofing occurs when an attacker impersonates a legitimate user, service, or system component to gain unauthorized access. Classic examples are: If you’re running distributed systems, watch the service-to-service authentication; that’s where spoofing hits the hardest in microservices.
In agentic systems, spoofing looks different: one AI agent impersonating another, forged tool execution identities, or malicious plugins claiming legitimate trust levels. Tampering involves unauthorized modification of data, in transit, at rest, or during processing. Examples include: Tampering often overlaps with injection vulnerabilities. AI systems add new forms of tampering: prompt injection altering agent instructions mid-execution, model poisoning attacks modifying training data, and context window manipulation in LLM applications. Prompt injection maps to Tampering, but STRIDE’s original categories don’t capture the specifics of AI threats very well.
Repudiation is when someone does something, denies it, and you can’t prove otherwise. Repudiation is often overlooked because it does not directly “break” the system, but it destroys accountability. Common issues include: The AI angle makes this worse. Autonomous agents produce untraceable reasoning chains, make decisions without clear provenance, and often have incomplete logging of tool calls. If an AI agent makes a financial decision or a security change, how do you prove why it happened? Information Disclosure is what it sounds like; sensitive data gets exposed to people who shouldn’t see it. Examples include: AI applications introduce new disclosure risks: context window leaks revealing prior user data, system prompt leakage, training data memorization exposure, and inference attacks. In LLM systems, the attack surface for confidential data expands beyond storage and transmission into model behavior.
Denial of Service is resource exhaustion. The goal is to make your system unavailable. Examples include: In AI and agentic systems, recursive agent loops consume unbounded compute, prompt amplification spikes token usage, and tool chaining triggers runaway execution paths. Availability threats today are inflating your operational costs. Elevation of Privilege (EoP) occurs when a user or process gains access rights beyond what was intended. Examples include: Authorization boundaries are significantly more complex in autonomous architectures. Modern AI context in agentic systems includes: An injected prompt only matters if the agent can do something with it. Trent maps what each agent can read, write and run.
Threat modeling an entire platform at once often becomes overwhelming. Start small with a feature, service, or workflow. Clarify: Large language models break assumptions that STRIDE was built on. Traditional software has predictable control flows; LLMs respond differently to the same input depending on context, temperature, and prior conversation. That makes threat identification harder because the attack surface isn’t static.
The OWASP Top 10 for LLM Applications 2025 provides the closest structured mapping between STRIDE categories and LLM-specific vulnerabilities: If you’re building with LLMs, STRIDE still gives you the right questions. But you’ll need these LLM-specific categories to get useful answers.
STRIDE and DREAD are complementary. STRIDE identifies threats. DREAD scores them. If your team is new to threat modeling or works with DFD-based architectures, STRIDE is the place to start. PASTA covers both and adds business objectives, technical profiling, and attack simulation on top. If you need business-aligned threat analysis, PASTA is better suited. Microsoft deprecated DREAD internally due to subjective and inconsistent scoring, though it remains in widespread industry use.
Note: Microsoft deprecated DREAD internally due to scoring inconsistencies, but it remains widely used. Trent builds a threat model from your architecture documents, so vendor-built systems get reviewed too. In microservices architectures, the number of trust boundaries and data flows increases dramatically compared to monoliths, multiplying the STRIDE attack surface.
Serverless functions introduce ephemeral execution contexts that require different observability patterns than traditional host-based systems. Standard host-level logging doesn’t apply, but cloud-native alternatives (CloudWatch, X-Ray, structured logging) address many tracing needs. The STRIDE-relevant challenge is that Repudiation and Denial of Service analysis requires deliberate instrumentation that doesn’t come by default.
Your IaC templates are threat model targets. A tampered IaC template can deploy insecure infrastructure at scale. Scan for misconfigurations, sign your infrastructure policies, and implement drift detection. Modern teams embed STRIDE into CI/CD. Integrating STRIDE into CI/CD pipelines means automating threat identification at pull request time, not as a one-time workshop artifact .
3. Software Implementation, Frameworks & Protocols If you’re shipping fast and want a lightweight starting point, our threat modeling checklist for developers walks through the same thinking before code goes live. In Agile environments, threat modeling shifts from a waterfall gating activity to an incremental process. Each user story that changes data flows or trust boundaries triggers a STRIDE review of affected components.
STRIDE provides six broad threat categories, but it was never intended as an exhaustive taxonomy. It emerged in the context of traditional, human-written software with predictable control flows, and its categories reflect that. AI systems introduce non-deterministic behavior; outputs vary based on input context, training data, and model state. Traditional STRIDE assumes predictable input-output relationships, but AI systems are non-deterministic . STRIDE is necessary, but insufficient for AI-native architectures.
Agentic AI systems add autonomous decision-making, multi-step execution, and dynamic tool access, creating threat vectors that require new threat categories extending beyond the original six. While many agentic threats can be mapped to STRIDE categories (as shown below), the mapping loses critical nuance around intent misalignment, autonomous scope creep, and multi-agent trust dynamics. While AI threats can map to STRIDE categories, the mapping often loses nuance.
Teams building agentic AI security systems need threat modeling approaches that account for: Trent AI ‘s Agentic Threat Assessor extends traditional STRIDE analysis to agentic systems, mapping threats across both classical and AI-specific categories using your actual architecture as context. There are many tools out there, and modern tools extend STRIDE to AI-specific threats using architecture-aware automation.
Here are some tools to check out: Trent AI’s Agentic Threat Assessor : Contextual, agentic STRIDE analysis grounded in your specific codebase, architecture, and CI/CD pipeline. Extends STRIDE to AI-native threats automatically. For teams wanting to move beyond manual STRIDE workshops, Trent AI’s Threat Assessor automates the process using your actual system architecture, not generic templates.
Threat model documentation generated through STRIDE analysis serves as evidence for audit trails in regulated industries. STRIDE endures because it simplifies a complex problem: How can this system fail securely? It does not predict every attack. It does not replace risk management. It does not eliminate human judgment. But it provides structure, in a world of microservices, cloud-native deployments, CI/CD pipelines, and AI agents making autonomous decisions; structure is invaluable.
STRIDE remains the most accessible gateway into systematic security thinking; and when extended thoughtfully, it continues to serve modern engineering teams more than 25 years after its creation. The key is not to treat STRIDE as a checklist. Treat it as a lens, and use that lens early, when architecture decisions are still cheap to change. That’s where real security lives. Upload your design docs and Trent returns findings and security requirements before the first commit.
The STRIDE threat model is a threat classification framework developed at Microsoft circa 1999. It identifies six threat categories: Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege. Each category maps to a violated security property, giving teams a structured way to analyze how systems can fail. STRIDE stands for Spoofing (violates Authentication), Tampering (violates Integrity), Repudiation (violates Non-repudiation), Information Disclosure (violates Confidentiality), Denial of Service (violates Availability), and Elevation of Privilege (violates Authorization).
STRIDE is a threat identification framework that classifies threats into six categories. DREAD is a risk scoring model that rates identified threats on five factors: Damage, Reproducibility, Exploitability, Affected Users, and Discoverability. They are complementary. STRIDE identifies threats, DREAD scores them. Microsoft deprecated DREAD internally due to inconsistent scoring, but it remains in widespread industry use.
STRIDE can be adapted for AI systems, but traditional categories map imperfectly. Prompt injection maps to Tampering, excessive agency maps to Elevation of Privilege, and unbounded compute consumption maps to Denial of Service. Teams building agentic AI systems often combine STRIDE with OWASP Top 10 for LLM Applications 2025 to cover threats that STRIDE’s original six categories don’t fully capture.
Popular STRIDE tools include Microsoft Threat Modeling Tool (free, Windows, STRIDE-per-element automation), OWASP Threat Dragon (open-source, cross-platform), and Threagile (threat modeling as code, YAML-based). For AI-native threat modeling, Trent AI’s Agentic Threat Assessor extends STRIDE analysis to agentic systems using your actual architecture as context.
Discover how STRIDE threat modelling empowers CTOs and VPs of Engineering to build secure-by-design architectures with proactive risk management and robust cybersecurity measures. This document explores the STRIDE framework in depth, detailing its components, real-world applications, comparative methodologies, and strategic implementation guidelines. It is crafted for senior technical leaders who are looking to embed security deeply into their product development cycles.
STRIDE is a threat modeling framework developed by Microsoft that helps security teams identify six categories of threats: Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege. Modern software development is characterized by rapid iterations, continuous integration, and frequent deployments. In this dynamic environment, waiting until post-deployment to address vulnerabilities can be both costly and risky. Threat modelling —using frameworks such as STRIDE—allows organizations to identify design flaws at the earliest possible stage. This “security-by-design” approach not only minimizes the window of exposure but also reduces remediation costs, as vulnerabilities are addressed before code is written.
By integrating threat modelling into your SDLC, you are investing in a proactive posture that continuously assesses the security posture of your systems. This not only protects critical assets but also instills a culture of security awareness across engineering, development, and operations teams. Threat modelling is not just a technical exercise; it is a collaborative process that involves stakeholders from across the organization. Bringing together developers, architects, security experts, and even product managers ensures that multiple perspectives are considered, leading to more comprehensive security solutions. This cross-functional collaboration enhances overall security literacy, ensuring that every team member—from the front lines of development to executive leadership—is aware of potential risks and best practices.
The STRIDE framework is built around six core threat categories. Each category addresses specific attack vectors and vulnerabilities that can compromise an application’s integrity, confidentiality, and availability. Definition & Mechanism: Spoofing involves impersonating a legitimate entity to gain unauthorized access to systems or data. Attackers can use spoofing to trick systems into accepting malicious requests by faking identity credentials. In many cases, this is achieved through techniques like phishing, where the attacker sends emails or messages that appear to be from trusted sources.
Real-World Example: A notorious example is the rise of AI-powered phishing attacks. Traditional phishing emails are increasingly being automated, allowing attackers to craft personalized, convincing messages that mimic legitimate correspondence. In 2020, several large organizations reported phishing campaigns that successfully bypassed conventional spam filters by leveraging machine learning to create more authentic-looking emails. These attacks not only jeopardized sensitive data but also eroded trust in communication channels.
Definition & Mechanism: Tampering refers to the unauthorized modification of data, configuration files, or system logs. Attackers may alter data to hide their tracks, introduce vulnerabilities, or manipulate system behavior for malicious purposes. Real-World Example: Consider a scenario in which a cyber attacker gains access to a configuration file within an enterprise application. By modifying the configuration, the attacker could disable critical security settings, opening the door for further exploitation. In 2018, a major financial institution faced a data breach where tampering with logs obscured the trail of unauthorized access. This incident highlighted the need for robust file integrity monitoring (FIM) systems.
Definition & Mechanism: Repudiation occurs when an actor performs an unauthorized operation and then denies involvement, making it difficult to trace the action back to the perpetrator. This is often due to insufficient logging or weak audit trails. Real-World Example: In environments where outbound communications are not thoroughly validated, an attacker might perform malicious operations and later deny responsibility. A notable instance was observed in email systems where a lack of proper logging allowed attackers to send fraudulent messages without any traceable digital footprint. This type of attack not only impairs accountability but also complicates forensic investigations.
Definition & Mechanism: Information disclosure involves the unintentional leakage of sensitive data. This can occur through insecure configurations, error messages, or even improperly secured backups. The disclosure of such data can lead to significant privacy breaches and competitive disadvantages. Real-World Example: One prominent example occurred when an e-commerce company inadvertently exposed database details through overly verbose error messages. This incident allowed attackers to gather critical information about the system architecture and vulnerabilities, ultimately leading to a targeted data breach. In another case, misconfigured cloud storage led to millions of records being accessible publicly, emphasizing the risk of information leakage in modern digital environments.
Definition & Mechanism: Denial of Service attacks aim to disrupt the normal functioning of a service by overwhelming it with traffic or requests, thereby denying legitimate users access. These attacks can target network resources, application endpoints, or backend systems. Real-World Example: One of the most infamous DoS incidents occurred in 2017 when Google was targeted by an attack that involved spoofed traffic across 180,000 servers. The attacker managed to generate up to 167 million packets per second (Mpps), showcasing the potential scale of modern DoS attacks. According to industry reports, 2020 saw around 12.5 million DDoS-capable devices, and a 2022 study indicated a 133% increase in DoS incidents over the previous year. These statistics underscore the persistent and growing threat posed by DoS attacks.
Definition & Mechanism: Elevation of privilege occurs when a user or process gains access to functionalities or data beyond their authorization. This can happen due to missing authorization checks, configuration errors, or vulnerabilities in the application’s logic. Real-World Example: A common instance involves a minor oversight in the implementation of access controls. For example, in 2019, a software vendor discovered that a flaw in their authentication system allowed regular users to perform administrative actions simply by manipulating URL parameters. This seemingly small vulnerability had the potential to lead to a full-scale system compromise if exploited further.
While STRIDE offers a solid foundation for threat analysis, it is important for senior technical leaders to be aware of alternative frameworks that might better suit specific use cases. Each methodology has its own strengths and focus areas: Each of these methodologies can be tailored to address specific organizational needs. For many enterprises, a hybrid approach—leveraging STRIDE alongside elements from these frameworks—can provide a more comprehensive view of the threat landscape.
To integrate STRIDE effectively into your development process, it is essential to adopt a systematic approach: Empirical evidence underscores the business case for proactive threat modelling. Consider the following statistics and incidents: These real-world examples and statistics highlight that the cost of not investing in comprehensive threat modelling is far higher than the cost of integrating it into the SDLC. For senior leaders, the message is clear: proactive threat modelling is not just about technical risk reduction—it is about safeguarding the organization’s reputation, customer trust, and overall business continuity.
For CTOs and VPs of Engineering, implementing STRIDE threat modelling is as much about strategic vision as it is about technical execution. Here are some key recommendations: When the internal expertise or resources for comprehensive threat modelling are limited, engaging professional services can be a game-changer. Organizations facing complex security challenges or undergoing significant digital transformation may benefit from the specialized skills offered by external experts. Software Secured Threat Modelling Services provide an experienced team to conduct in-depth analyses, tailor methodologies like STRIDE to your specific environment, and offer actionable insights to bolster your security posture. Leveraging their expertise can accelerate the identification of vulnerabilities, ensure industry best practices are followed, and ultimately safeguard your business from evolving cyber threats.
4. Practical Deployment, Analysis & Case Studies Comparing STRIDE to other frameworks like DREAD and PASTA? See our STRIDE vs DREAD vs PASTA comparison → STRIDE threat modeling is applied by reviewing system components and mapping potential threats across spoofing, tampering, repudiation, information disclosure, denial of service, and elevation of privilege. This structured approach helps teams identify threats, evaluate security risks, and align security controls with real attack scenarios inside software systems.
The STRIDE methodology stands out because it categorizes security threats by attacker goals rather than assets alone. Unlike other threat modeling methodologies, it provides a consistent lens for threat identification, helping teams reason about potential security threats across trust boundaries and understand how threats exist within application workflows. Using the STRIDE model, each element applies threat modeling at the level of individual system components, data flows, and trust boundaries. This improves threat identification by revealing potential security risks tied to privileged access, attack surface expansion, and component interactions. It helps teams identify threats earlier and prioritize remediation more accurately.
The STRIDE framework integrates well with broader security strategy efforts, including risk assessment, threat intelligence, and secure design reviews. STRIDE threat modeling methodology complements other threat modeling approaches by providing a clear taxonomy that supports layered defenses, aligns with security controls, and adapts to emerging threats over time.
STRIDE threat modeling should be used early in the threat modeling process and revisited throughout the software development lifecycle. It is especially effective during design changes, architecture reviews, and feature expansion, when potential security risks increase and threat modeling helps teams proactively identify threats before they reach production. Adopting STRIDE threat modelling is essential for proactive, secure-by-design software development. By integrating continuous threat analysis into your SDLC, you not only reduce potential risks but also foster a culture of security awareness across your organization. In an era of increasing cyber threats, combining in-house efforts with professional services like Software Secured Threat Modelling can ensure your defenses remain robust and effective. STRIDE gives you the framework to think systematically about your attack surface but applying it well to a real architecture requires experience across the threat categories that actually show up in practice, not just the ones in the textbook. If your team is working through a new system design, a significant feature, or an acquisition and wants an experienced team to run the STRIDE process alongside you, see how Software Secured approaches threat modelling engagements including how we work with your architects and engineers.
Sherif Koussa is a cybersecurity expert and entrepreneur with a rich software building and breaking background. In 2006, he founded the OWASP Ottawa Chapter, contributed to WebGoat and OWASP Cheat Sheets, and helped launch SANS/GIAC exams. Today, as CEO of Software Secured, he helps hundreds of SaaS companies continuously ship secure code. Threat modeling is an effective way to help secure your systems, applications, networks, and services. It's a systematic approach that identifies potential threats and recommendations to help reduce risk and meet security objectives earlier in the development lifecycle.
Example of these phases is covered in the threat modelling example. More details about these phases can be found at Threat Modeling Security Fundamentals. Here is an example of a threat modeling document which talks about the architecture and different phases involved in the threat modeling. This document can be used as reference template for creating threat modeling documents.
Add at least one visual dataflow diagram that shows process flows between different entities in the system If additional information is needed to understand the flow, include additional diagrams or information here. The goal of this section is to capture the documentation needed to accomplish building a successful threat model. If it is discovered later that additional information is required, ensure the “What are we working on?” section is updated with the latest information.
To complete the STRIDE table below, apply the questions above to each of the interactions in the data flow diagram between different entities. There should be at least one issue identified for each of S, T, R, I, D, and E. Make sure to uniquely identify them, so they are easier to track in the next step. To complete the table below, design or identify mitigations that can address each of the issues identified. Alternatively, the risk may be documented and corporately accepted by the business.
Did the STRIDE model uncover any new design issues or concerns that had not been previously addressed or thought of? Did the treatments identified in the “What are we going to do about it” section adequately address the issues identified? Any additional thoughts or insights on the threat modeling process that could help improve it next time? STRIDE is one of the most widely used threat modeling frameworks. This guide walks through the six categories, the STRIDE-per-element chart, and a worked example you can copy. For the short definition, see the STRIDE glossary entry .
STRIDE is an acronym. Each letter is a category of threat that maps to a security property it violates: Steps 1 and 2 rely on a data flow diagram and trust boundaries — the foundation every STRIDE analysis builds on. You don't need to consider all six threats for every element. STRIDE-per-element maps each threat to the diagram element types it typically affects: (S = Spoofing, T = Tampering, R = Repudiation, I = Information Disclosure, D = Denial of Service, E = Elevation of Privilege.) Take a simple web app: a user (external entity) sends requests to a web service (process), which reads and writes a database (data store). A trust boundary sits between the user and the service. Applying STRIDE: Running STRIDE by hand in workshops doesn't scale to every release. With automated threat modeling , an agent infers the data flow diagram from your code, applies STRIDE per element automatically, and delivers prioritized findings — so STRIDE runs continuously instead of occasionally. See also STRIDE vs PASTA and the full threat modeling guide .
Virantis runs STRIDE (and PASTA) automatically with agentic AI — no diagrams to draw. Request early access. Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege. Each maps to a security property: authentication, integrity, non-repudiation, confidentiality, availability, and authorization respectively. Diagram the system as a data flow diagram, mark trust boundaries, then go element by element asking which STRIDE threats apply. The STRIDE-per-element chart tells you which categories are relevant to external entities, processes, data stores, and data flows.
STRIDE-per-element is a shortcut that maps each STRIDE threat to the data flow diagram element types it typically affects, so you don't have to consider all six threats for every element. For example, processes are susceptible to all six, while data flows are mainly susceptible to Tampering, Information Disclosure, and Denial of Service. Yes. Tools — increasingly agentic AI — can infer the data flow diagram from code, apply STRIDE per element automatically, and produce prioritized findings, so STRIDE can run on every change instead of in occasional manual workshops.
Security defects are cheaper the earlier you find them — this is an industry iron rule. If a vulnerability is found after production release, the cost is unlimited: investigation, fix, redeploy, and in some cases responding to information leakage. On the other hand, find it on a diagram at the design stage and it's just an erase with an eraser. The systematic method for this "building security in at the design stage" is threat modeling. This article, rather than how to use abstruse tools, explains a thinking type a team can run right away , faithful to official information (the Threat Modeling Manifesto , Microsoft's STRIDE , OWASP Threat Modeling ), and finally goes all the way to the implementation of managing threats "as code." The positioning of this article: of a security engineer's core skills, this deeply explores the "Identify" in NIST CSF 2.0 terms — the ability to surface risk at the design stage. For the roadmap of the role overall, see how to become a security engineer , and for the technique of crushing the surfaced threats in implementation, secure-coding practices .
When you hear threat modeling, you tend to imagine a dedicated tool or abstruse notation, but the essence is answering, as a team, the four questions the Threat Modeling Manifesto raises. Running these four questions for an hour in a design-review setting is already valuable. The Manifesto says — "a valuable model over a perfect model," "people and collaboration over checklists." Threat modeling isn't a "ritual" but a collaborative activity to think one level deeper about the design.
Listing "what can go wrong" by "feel" will surely leave gaps. So use STRIDE , systematized by Microsoft. It divides threats into six categories, each corresponding to which security property it breaks. STRIDE's strength is that you can mechanically ask the six "is there spoofing for this element? tampering? …" Exhaustiveness beats person-dependent intuition.
The best tool to share "what we're working on" is a Data Flow Diagram (DFD). More than perfect notation, what matters is seeing where data flows from and to, and where the 'premise of trust' changes. The trust boundary is the very heart of threat modeling. Data flows that cross the boundary — user input, external-API responses, calls from another microservice — are all "the moment something untrusted enters the inside." This coincides with where validation, authentication, and authorization should take effect. Once the boundary is visible on the diagram, "where to protect" becomes self-evident.
Apply STRIDE's six categories to each element of the DFD. For example, about the "user → API server" data flow (crossing the boundary): In this way, just filling in the "element × STRIDE" matrix makes the threat enumeration astonishingly exhaustive. You don't need to crush everything perfectly. Being "aware of it" is decisively more important than not being aware.
The biggest reason threat modeling becomes a formality is "writing it in a document once and letting it rot as-is." The design keeps changing, but the diagram fossilizes as a PNG somewhere on a wiki. The best way to prevent this is to manage the threat model as code, in the repository (Threat Modeling as Code). Next, write a verification that "if a high-risk threat has no mitigation / unimplemented, fail CI." This makes the threat model a "living contract." Place this script in CI and you can mechanically detect the divergence between "threats raised in design" and "implemented mitigations." The threat model changes from a "rotting document" into an "unbreakable contract" — this is a security-engineer-like design practice. The thinking on type-safe boundary validation connects to secure-coding practices .
Even if you raise 100 threats, resources are finite. Prioritize by risk = likelihood × impact. What's important is that "acceptance" is also a legitimate option. You can't zero every risk. A state where you can record "this risk is accepted, with a reason" is far healthier than unwittingly leaving it. This is also a decision that management should be responsible for, and the METI Cybersecurity Management Guidelines also position grasping risk and decision-making as a management responsibility.
5. Performance Evaluation & Extended Technical Observations "Light, frequent" is the principle. Rather than doing heavy threat modeling once a year, continuously running lightweight threat modeling per feature keeps up with change and takes root in the team as a culture. Threat modeling is, not special talent or an expensive tool, a collaborative activity to think one level deeper about the design.
Whether you can build security in at the design stage most greatly affects a product's safety. "Building fast" and "building safely" can be reconciled in the first 30 minutes of design — that's the essence of threat modeling. If you want to build threat modeling into your product's design review, or take inventory of the "vertical risks" of an existing design once, feel free to consult me.
Developer of a METI Minister's Award–winning product. With TypeScript + Python + AWS, I deliver SaaS, industry DX, and production-grade generative AI (RAG) end to end — from requirements to infrastructure and operations — single-handedly. Design reviews via threat modeling, correct implementation of crypto and authn/authz, log design and detection (detection engineering), and building an incident-response capability. With experience building — solo × generative AI — a METI Minister's Award B2B SaaS and a payments platform with zero double charges in production, I help get your product to a state where it ships fast and can be defended. Vertical risks that only design can address, I also take on as an audit.
Available for both project-based (contract) and advisory engagements. Start with a free 30-minute consult. How to become a security engineer [2026 complete roadmap]: a skill map, certifications, and the fastest route from no experience, drawn with official frameworks A complete roadmap to becoming a security engineer. With primary sources — the NIST NICE Framework, CSF 2.0, IPA ITSS+, and METI guidelines — as the map, it systematically explains, with real code: the big picture of the role, a skill map to build from no experience, a certification strategy including Japan's national 'Registered Security Specialist,' and differentiation in the AI era.
Incident-response practical guide [2026 edition]: CSIRT, Runbooks, and automated containment aligned with NIST SP 800-61 Rev.3 (CSF 2.0) A practical guide to designing security incident response (IR) at production quality. Centered on the new framework of NIST SP 800-61 Rev.3 (the CSF 2.0 Community Profile) revamped in 2025, it explains the CSIRT structure, severity triage, idempotent containment Runbooks, blameless postmortems, and SOAR automation, with real code faithful to official information.
A practical applied-cryptography guide [2026 edition]: using password hashing (Argon2id), encryption (AES-GCM), and key management correctly A practical guide for app developers to 'use cryptography correctly.' Faithful to official sources, it explains, in type-safe code: the difference between hashing, encryption, and encoding; Argon2id password hashing with OWASP-recommended parameters; the latest NIST 800-63B-4 password policy; authenticated encryption with AES-256-GCM; and key management and rotation.
Practical secure-coding guide [2026 edition]: become an engineer who 'builds safely' with NIST SSDF and OWASP ASVS A complete guide to practicing secure coding by 'mechanism,' not 'willpower.' With NIST's official framework SSDF (SP 800-218) and OWASP ASVS 5.0 as a map, it explains validation at the trust boundary, server-enforced authorization, output encoding, secret management, and dependency measures with real code, and finally shows how to auto-enforce these in CI.
Does the app you built with AI need a human security review? — who needs one, who doesn't, and what it costs, when to do it and how to ask Should you pay a person to review the app you built with Claude Code, Cursor or Lovable? A decision table based on the data you hold, what an AI self-check covers and what it can't, when in the launch cycle to ask, typical prices and what drives them, and how to get a review without handing over keys or customer data.
Security governance for rolling Claude Code out to an organization — permission modes, managed settings, sandboxing and CI What to decide before handing Claude Code to a team: which of the six permission modes to allow, the deny→ask→allow evaluation order, delivering managed settings and the keys users can't override, the sandbox that is off by default, hook governance, and the CI trust trap, per the official docs as of October 2026.
Using third-party MCP servers safely with Claude Code — trust decisions, allowlists and managed-mcp.json Before you connect a third-party MCP server to Claude Code: local servers run outside the sandbox, and Anthropic does not audit MCP servers. Covers .mcp.json approval, writing allowlists and denylists correctly, managed-mcp.json, and a vetting checklist, per the official docs.
Most security reviews happen after the architecture is already built, when moving a trust boundary means rewriting three services instead of redrawing a box on a whiteboard. Threat modeling exists specifically to happen before that point — and STRIDE, a framework Microsoft published in 1999, is still the fastest way to run one without buying anything or waiting for a specialist’s calendar to open up.
If your organization does security reviews only after code is written — a pentest before launch, a code review before merge — you’re finding architectural flaws at the most expensive possible point to fix them. Threat modeling during design catches the class of bug that a pentest finds anyway, except before it’s built into three dependent services and a database schema. The value isn’t the mnemonic itself — it’s that six categories are small enough to actually apply exhaustively to a real system in a working session, unlike open-ended “what could go wrong here” brainstorming, which tends to converge on whatever the loudest person in the room already worried about.
STRIDE isn’t applied to a system in the abstract — it’s applied to a data flow diagram (DFD) , a deliberately simple representation with four element types: The DFD doesn’t need to be polished. A whiteboard photo is a perfectly valid input. What matters is that every trust boundary is marked explicitly — that’s where STRIDE analysis actually happens, because a threat that doesn’t cross a trust boundary usually isn’t worth modeling at that level of detail.
The room needs both roles represented — a developer who understands the actual implementation and someone who thinks like an attacker — because STRIDE questions asked by only one side tend to either miss implementation-specific details or miss realistic attacker behavior entirely. Take a simple case: a browser (external entity) sends credentials across a trust boundary to a login API (process), which checks them against a user database (data store) and returns a session token.
Six questions, one trust boundary, six concrete findings — none of which required a pentest, a scanner, or specialized tooling. That’s the entire value proposition of the method. The temptation in any design review is to skip the structure and just ask “what could go wrong?” That works for the first five minutes and then reliably degrades — the discussion drifts toward whatever risk someone already had in mind, quieter voices in the room stop contributing, and entire categories of threat (repudiation and denial of service are the most commonly skipped) never come up at all because nobody happened to think of them unprompted.
STRIDE’s actual job is forcing coverage: six questions per trust boundary, asked every time, regardless of what feels intuitively risky. The categories that feel “boring” to ask about — repudiation, in particular — are often exactly the ones that get skipped in free-form discussion and then turn into the finding nobody can explain in an incident review six months later. A whiteboard and a spreadsheet are sufficient for most sessions, but two free, actively maintained OWASP tools cover the next step up: Neither replaces the actual thinking the session requires — they just remove friction from documenting and maintaining the output once you’re doing this regularly enough that a spreadsheet stops scaling.
Each STRIDE category corresponds to real, observed attacker technique families in MITRE ATT&CK — useful for showing a skeptical stakeholder that this isn’t an abstract design exercise: How attackers turn GitHub Actions' shared build cache into a supply chain weapon — real cases, attack mechanics, detection logic, and mitigations.
GitHub says an employee device was compromised through a poisoned third-party VS Code extension and internal repositories were exfiltrated. Here is the fact-checked breakdown for defenders. CISA lists GitLab CVE-2026-85706 as exploited. Self-managed administrators must upgrade to 19.3.2, 19.2.6, or 19.1.8 or later, hunt the repository commits API, and treat readable secrets as potentially compromised.
In the fast-paced world of Agile software development, security is often bolted on at the very end of the cycle—usually after a penetration tester finds a critical flaw a week before the launch date. Fixing architectural flaws at the end of the development lifecycle is incredibly expensive and highly disruptive. The solution to this problem is Threat Modeling . Threat modeling is the process of identifying, understanding, and mitigating security risks before a single line of code is written. It is the cornerstone of "shifting security left." In this post, we will explore how to conduct a practical threat modeling session using the industry-standard STRIDE methodology.
At its core, threat modeling seeks to answer four simple questions about a system or application: You cannot secure a system you do not understand. The first step in threat modeling is gathering the architects, developers, and security engineers in a room (or on a whiteboard) to draw a Data Flow Diagram (DFD) . Once the DFD is drawn, you systematically analyze every process, data flow, and data store across trust boundaries using STRIDE .
Developed by Microsoft, STRIDE is an acronym that categorizes six distinct types of security threats: Can an unprivileged user execute commands or access functions reserved for higher-level accounts? As the team uncovers STRIDE threats on the whiteboard, they are documented as actionable tickets in the engineering backlog (Jira, DevOps, etc.).
For every threat identified, a mitigation strategy must be assigned. If a threat is too difficult to fix immediately, the business must formally accept the risk, ensuring that security is a documented business decision, not an afterthought. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/STRIDE%20model • https://en.wikipedia.org/wiki/Threat%20model • https://en.wikipedia.org/wiki/Threat%20%28computer%20security%29 • https://chintangurjar.com/posts/stride/ • https://trent.ai/blog/stride-threat-model/ • https://www.softwaresecured.com/post/stride-threat-modelling • https://microsoft.github.io/code-with-engineering-playbook/security/threat-modelling/ • https://developers.stellar.org/docs/build/security-docs/threat-modeling/STRIDE-template • https://virantis.com/how-to-do-stride-threat-modeling • https://tomodahinata.com/en/blog/threat-modeling-stride-data-flow-diagram-secure-design-practical-guide
Extracted Research Figures & Simulation Topologies
Total 1 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
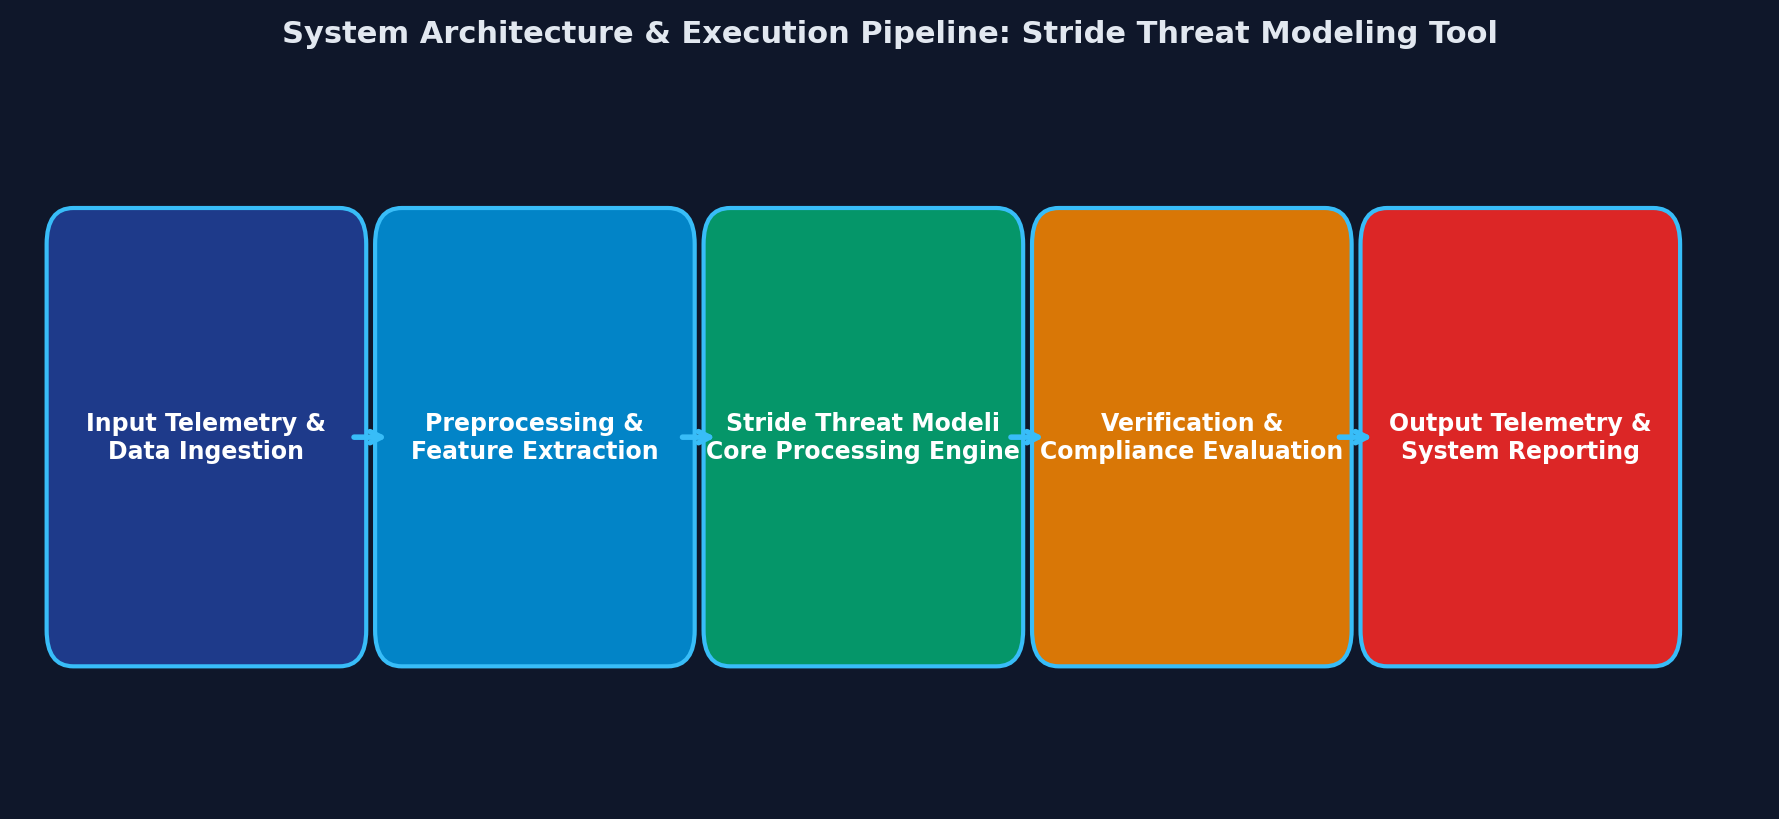
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Stride Threat Modeling Tool.
[*] Metasploit Scan Running on Target Subnet for Stride Threat Modeling Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |