Complete Technical Paper Content — Supply Chain Code Tampering Detection
Overview & System Context
Supply Chain Code Tampering Detection: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9527 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A supply chain attack is a cyber-attack that seeks to damage an organization by targeting less secure elements in the supply chain. A supply chain attack can occur in any industry, from the financial sector, oil industry, to a government sector. A supply chain attack can happen in software or hardware. Cybercriminals typically tamper with the manufacturing or distribution of a product by installing malware or hardware-based spying components. Symantec's 2019 Internet Security Threat Report states that supply chain attacks increased by 78 percent in 2018. A supply chain is a system of activities involved in handling, distributing, manufacturing, and processing goods in order to move resources from a vendor into the hands of the final consumer. A supply chain is a complex network of interconnected players governed by supply and demand. Although supply chain attack is a broad term without a universally agreed upon definition, in reference to cyber-security, a supply chain attack can involve physically tampering with electronics (computers, ATMs, power systems, factory data networks) in order to install undetectable malware for the purpose of bringing harm to a player further down the supply chain network. Alternatively, the term can be used to describe attacks exploiting the software supply chain, in which an apparently low-level or unimportant software component used by other software can be used to inject malicious code into the larger software that depends on the component. In a more general sense, a supply chain attack may not necessarily involve electronics. In 2010 when burglars gained access to the pharmaceutical giant Eli Lilly's supply warehouse, by drilling a hole in the roof and loading $80 million worth of prescription drugs into a truck, they could also have been said to carry out a supply chain attack. However, this article will discuss cyber attacks on physical supply networks that rely on technology; hence, a supply chain attack is a method used by cyber-criminals.
At the end of 2013, Target, a US retailer, was hit by one of the largest data breaches in the history of the retail industry. Between 27 November and 15 December 2013, Target's American brick-and-mortar stores experienced a data hack. Around 40 million customers' credit and debit cards became susceptible to fraud after malware was introduced into the POS system in over 1,800 stores. The data breach of Target's customer information saw a direct impact on the company's profit, which fell 46 percent in the fourth quarter of 2013. Six months prior the company began installing a $1.6 million cyber security system.
Target had a team of security specialists to monitor its computers constantly. Nonetheless, the supply chain attack circumvented these security measures. It is believed that cyber criminals infiltrated a third party supplier to gain access to Target's main data network. Although not officially confirmed, investigation officials suspect that the hackers first broke into Target's network on 15 November 2013 using passcode credentials stolen from Fazio Mechanical Services, a Pennsylvania-based provider of HVAC systems. Ninety lawsuits have been filed against Target by customers for carelessness and compensatory damages. Target spent around $61 million responding to the breach, according to its fourth-quarter report to investors.
Stuxnet is a computer worm that is widely believed to be a joint U.S.-Israeli cyber operation, though neither government has officially confirmed involvement. The worm specifically targets industrial control systems, particularly those that automate electromechanical processes, such as factory machinery and nuclear enrichment equipment. Stuxnet was designed to manipulate programmable logic controllers (PLCs), disrupting industrial equipment by issuing unauthorized commands while simultaneously feeding falsified operations data to monitoring systems to conceal its activity. Stuxnet is widely believed to have been developed to disrupt Iran's enriched uranium programs. Kevin Hogan, Senior Director of Security Response at Symantec, stated that most infections occurred in Iran. Analysts suggest that its primary target was the Natanz uranium enrichment facility. Stuxnet was initially introduced into Iran's Natanz facility via infected USB flash drives, requiring physical access to the target network. According to reports, engineers or maintenance workers, either knowingly or unknowingly, facilitated its entry into the plant. Once inside, the worm spread autonomously, exploiting multiple zero-day vulnerabilities in Windows systems to propagate across networked machines running Siemens industrial control software.
In June 2017, the financial software M.E.Doc, widely used in Ukraine, was identified by security researchers as a likely initial vector for the spread of the NotPetya malware. Security researchers, including those from Microsoft, indicated that NotPetya infections may have originated from a compromised update issued through M.E.Doc. Some analysts described this as a supply chain attack, though the exact method of compromise was not definitively identified. The software's developers denied the claim but later deleted their statement and stated that they were cooperating with investigators. NotPetya was initially identified as ransomware because it encrypted hard drives and displayed a ransom demand in bitcoin. However, the email account used to provide decryption keys was shut down, leaving victims without a way to recover their files. Unlike WannaCry, NotPetya had no built-in kill switch, making it harder to stop. The attack affected multiple industries in Ukraine, including banks, an airport, the Kyiv Metro, pharmaceutical companies, and Chernobyl's radiation detection systems. It also spread globally, impacting organizations in Russia, the United Kingdom, India, and the United States. NotPetya spread using EternalBlue, a vulnerability originally developed by the U.S. National Security Agency (NSA) and later leaked. EternalBlue had previously been used in the WannaCry cyberattack in May 2017. This exploit enabled NotPetya to spread through the Windows Server Message Block (SMB) protocol. The malware also used PsExec and the Windows Management Instrumentation (WMI) to spread within networks. Due to these exploits, once a device on a network was infected, the malware could rapidly spread to other connected systems. Ukrainian police stated that M.E.Doc employees could face criminal liability for negligence, citing repeated warnings from antivirus firms about security vulnerabilities in the company's cybersecurity infrastructure. The head of Ukraine's CyberPolice, Colonel Serhiy Demydiuk, alleged that M.E.Doc had been repeatedly warned by security firms about weaknesses in its systems but failed to act, stating, "They knew about it." Authorities later reported that M.E.Doc cooperated with investigators.
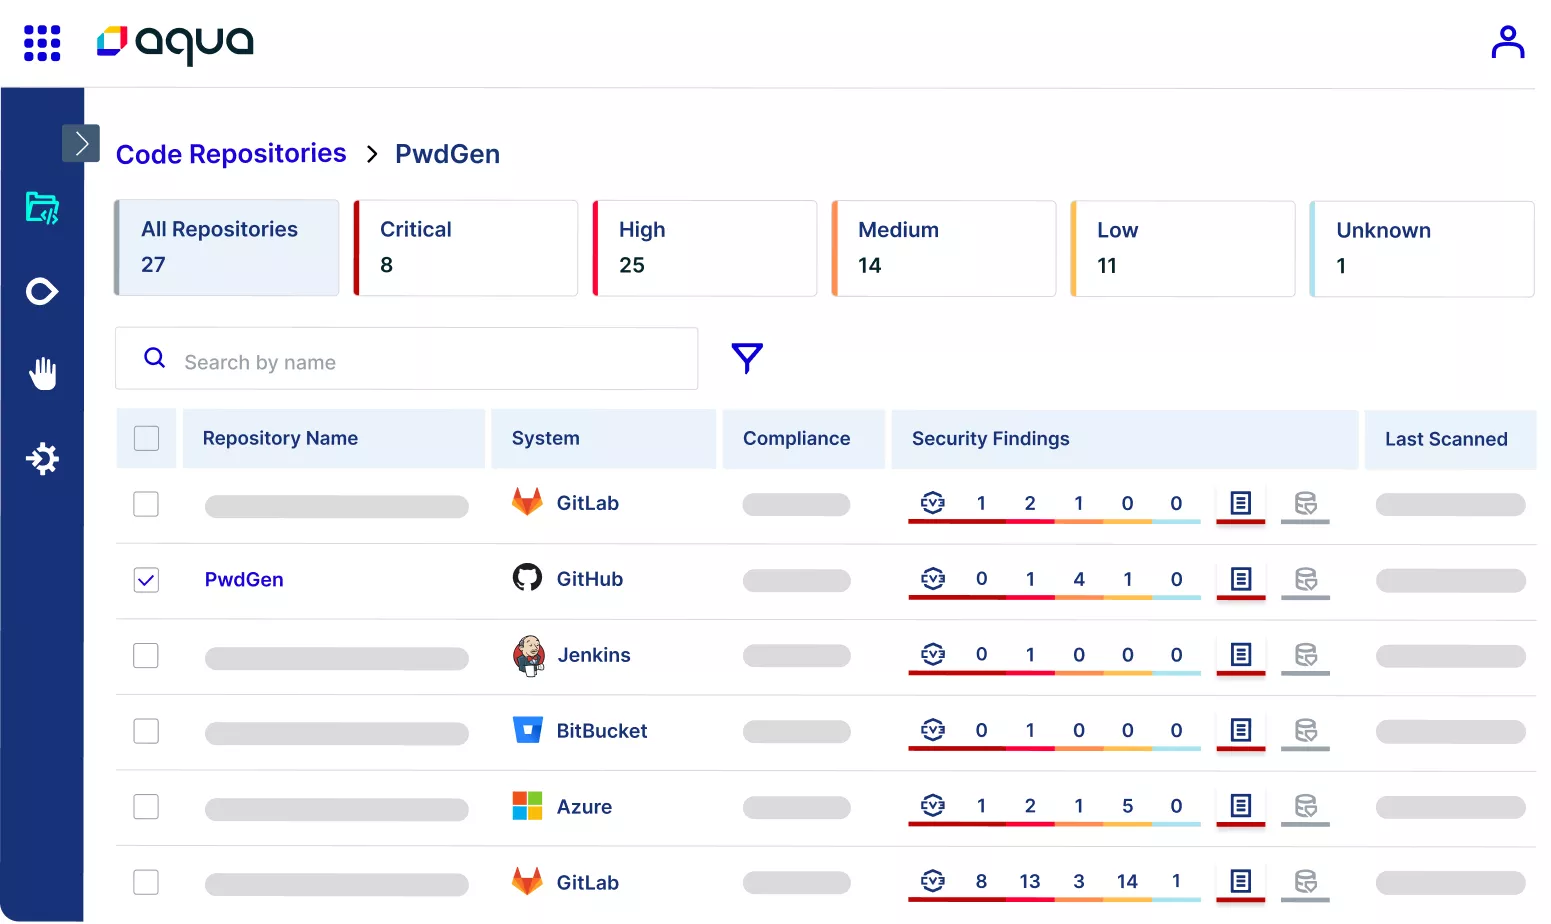
Figure 1: Software Supply Chain Security - Aqua The 2020 SolarWinds cyberattack was linked to a supply chain compromise targeting the IT infrastructure company SolarWinds, which provided software used by multiple U.S. federal institutions, including networks within the National Nuclear Security Administration (NNSA). Russian hackers compromised Orion, a widely used network management software developed by SolarWinds, by injecting malicious code into software updates. This allowed them to gain unauthorized access to numerous organizations, including multiple U.S. government agencies that relied on Orion for IT monitoring and management. On December 13, 2020, the U.S. Department of Homeland Security issued Emergency Directive 21-01, "Mitigate SolarWinds Orion Code Compromise", requiring affected federal agencies to disconnect compromised Windows host OS instances from their enterprise domain and rebuild those hosts using trusted sources. These compromised systems had been running SolarWinds Orion. In December 2020, FireEye identified a cyber breach involving the SolarWinds Orion software, which had been compromised prior to its discovery. Microsoft was among the organizations affected, detecting and removing malicious files linked to the breach. Microsoft has since collaborated with FireEye as part of an ongoing investigation into the incident. The cyberattack targeted supply chain software used across various industries, including government, consulting, technology, telecommunications, and extractive sectors in North America, Europe, Asia and the Middle East. On January 5, 2021, a joint statement from the Federal Bureau of Investigation (FBI), the Cybersecurity and Infrastructure Security Agency (CISA), the Office of the Director of National Intelligence (ODNI), and the National Security Agency (NSA) indicated that, while approximately 18,000 public and private sector entities were affected by the SolarWinds breach, fewer than ten U.S. government agencies were confirmed to have been compromised.
In February 2021 Microsoft determined that the attackers had downloaded a few files "(subsets of service, security, identity)" apiece from "a small subset of Azure components" "a small subset of Intune components" "a small subset of Exchange components" None of the Microsoft repositories contained production credentials. The repositories were secured in December, and those attacks ceased in January. However, in March 2021 more than 20,000 US organizations were compromised through a back door that was installed via flaws in Exchange Server. The affected organizations use self-hosted e-mail (on-site rather than cloud-based) such as credit unions, town governments, and small businesses. The flaws were patched on 2 March 2021, but by 5 March 2021 only 10% of the compromised organizations had implemented the patch; the back door remains open. The US officials are attempting to notify the affected organizations which are smaller than the organizations that were affected in December 2020. Microsoft has updated its Indicators of Compromise tool and has released emergency mitigation measures for its Exchange Server flaws. The attacks on SolarWinds and Microsoft software are currently thought to be independent, as of March 2021. The Indicators of Compromise tool allows customers to scan their Exchange Server log files for compromise.
At least 10 attacking groups are using the Exchange Server flaws. Web shells can remain on a patched server; this still allows cyberattacks based on the affected servers. As of 12 March 2021 exploit attempts are doubling every few hours, according to Check Point Research, some in the name of security researchers themselves. By 14 April 2021 the FBI had completed a covert cyber operation to remove the web shells from afflicted servers and was informing the servers' owners of what had been done. In May 2021 Microsoft identified 3000 malicious emails to 150 organizations in 24 countries, that were launched by a group that Microsoft has denoted 'Nobelium'. Many of those emails were blocked before delivery. 'Nobelium' gained access to a Constant Contact "email marketing account used by the US Agency for International Development (USAID)".
Security researchers assert that 'Nobelium' crafts spear-phishing email messages which get clicked on by unsuspecting users; the links then direct installation of malicious 'Nobelium' code to infect the users' systems, making them subject to ransom, espionage, disinformation, etc. The US government has identified 'Nobelium' as stemming from Russia's Federal Security Service. By July 2021 the US government is expected to name the initiator of the Exchange Server attacks: "China's Ministry of State Security has been using criminal contract hackers". In September 2021 the Securities and Exchange Commission (SEC) enforcement staff have requested that any companies which have downloaded any compromised SolarWinds updates, voluntarily turn over data to the SEC if they have installed the compromised updates on their servers. In July 2022 SessionManager, a malicious module hosted by IIS (installed by default on Exchange Servers), was discovered to have infected Exchange Servers since March 2021; SessionManager searches memory for passwords, and downloads new modules, to hijack the server.
In May 2021, a ransomware attack on Colonial Pipeline forced a temporary shutdown of a major fuel distribution network, disrupting the supply of gasoline, diesel, and jet fuel to the U.S. East Coast. The Biden administration invoked emergency powers to prevent shortages, while experts described the incident as the worst-ever cyberattack on U.S. infrastructure. The attack, attributed to the Russian-linked cybercriminal group DarkSide, raised concerns about vulnerabilities in critical energy systems, as fuel traders sought alternative supply routes and fears of price spikes emerged. On June 16, 2021, President Biden stated to President Putin that cyberattacks on 16 critical infrastructure sectors were off-limits and said that the U.S.
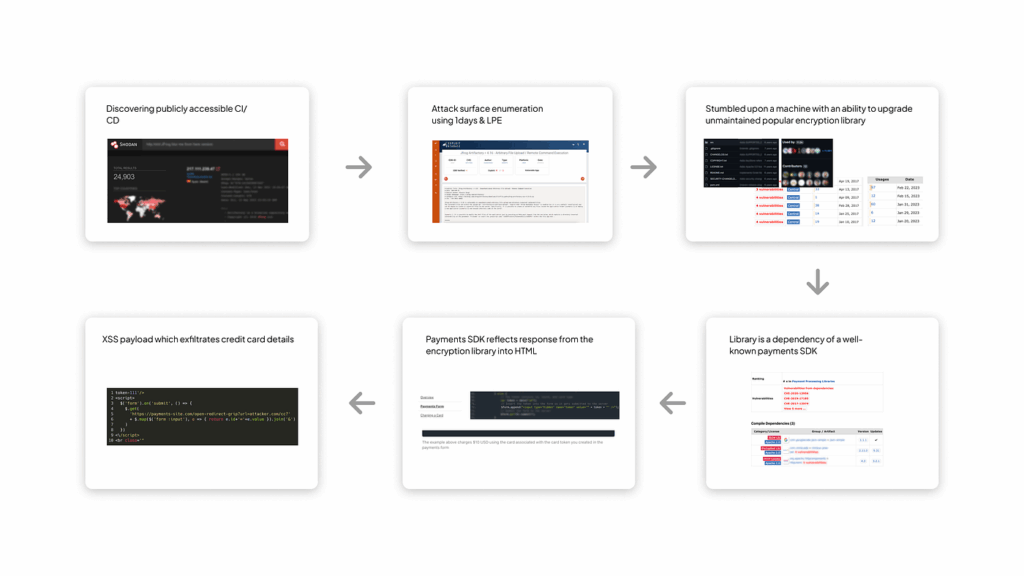
would respond to future cyber threats. The 16 critical infrastructure sectors, as designated by the U.S. Cybersecurity and Infrastructure Security Agency (CISA), include energy, food and agriculture, emergency services, healthcare, and other essential industries such as financial services, communications, and transportation systems. Figure 2: Tampering Detection AI Engine — How to Prevent the Next Software Supply ...
In March 2024, a backdoor in xz/liblzma in XZ Utils was suspected, with malicious code known to be in version 5.6.0 and 5.6.1. While the exploit remained dormant unless a specific third-party patch of the SSH server is used, under the right circumstances this interference could potentially enable a malicious actor to break sshd authentication and gain unauthorized access to the entire system remotely. The list of affected Linux distributions includes Debian unstable, Fedora Rawhide, Kali Linux, and OpenSUSE Tumbleweed. Most Linux distributions that followed a stable release update model were not affected, since they were carrying older versions of xz. Arch Linux issued an advisory for users to update immediately, although it also noted that Arch's OpenSSH package does not include the common third-party patch necessary for the backdoor. FreeBSD is not affected by this attack, as all supported FreeBSD releases include versions of xz that predate the affected releases and the attack targets Linux's glibc.
Day 30: solicit input Day 45: define 'critical software' Day 60: EO task 4i, 4r: user guidance, and vendor testing Day 180: EO task 4c: guidelines for enhancing supply chain software security Day 270: EO task 4e, 4s, 4t, 4u: guidelines for enhancing supply chain software Day 360: EO task 4d: guidelines for review and update procedures of supply chain software Day 365: EO task 4w: summary support of the pilot In a 2014 PwC report, titled "Threat Smart: Building a Cyber Resilient Financial Institution", the financial services firm recommends the following approach to mitigating a cyber attack: "To avoid potential damage to a financial institution's bottom line, reputation, brand, and intellectual property, the executive team needs to take ownership of cyber risk. Specifically, they should collaborate up front to understand how the institution will defend against and respond to cyber risks, and what it will take to make their organization cyber resilient.
A small supplier base: This allows a firm to have tighter control over its suppliers. Stringent vendor controls: Imposing stringent controls on suppliers in order to abide by lists of an approved protocols. Also conducting occasional site audits at supplier locations and having personnel visiting the sites on a regular basis for business purposes allows greater control. Security built into design: Security features, such as check digits, should be designed into the software to detect any previous unauthorized access to the code. An iterative testing process to get the code functionally hardened and security-hardened is a good approach.
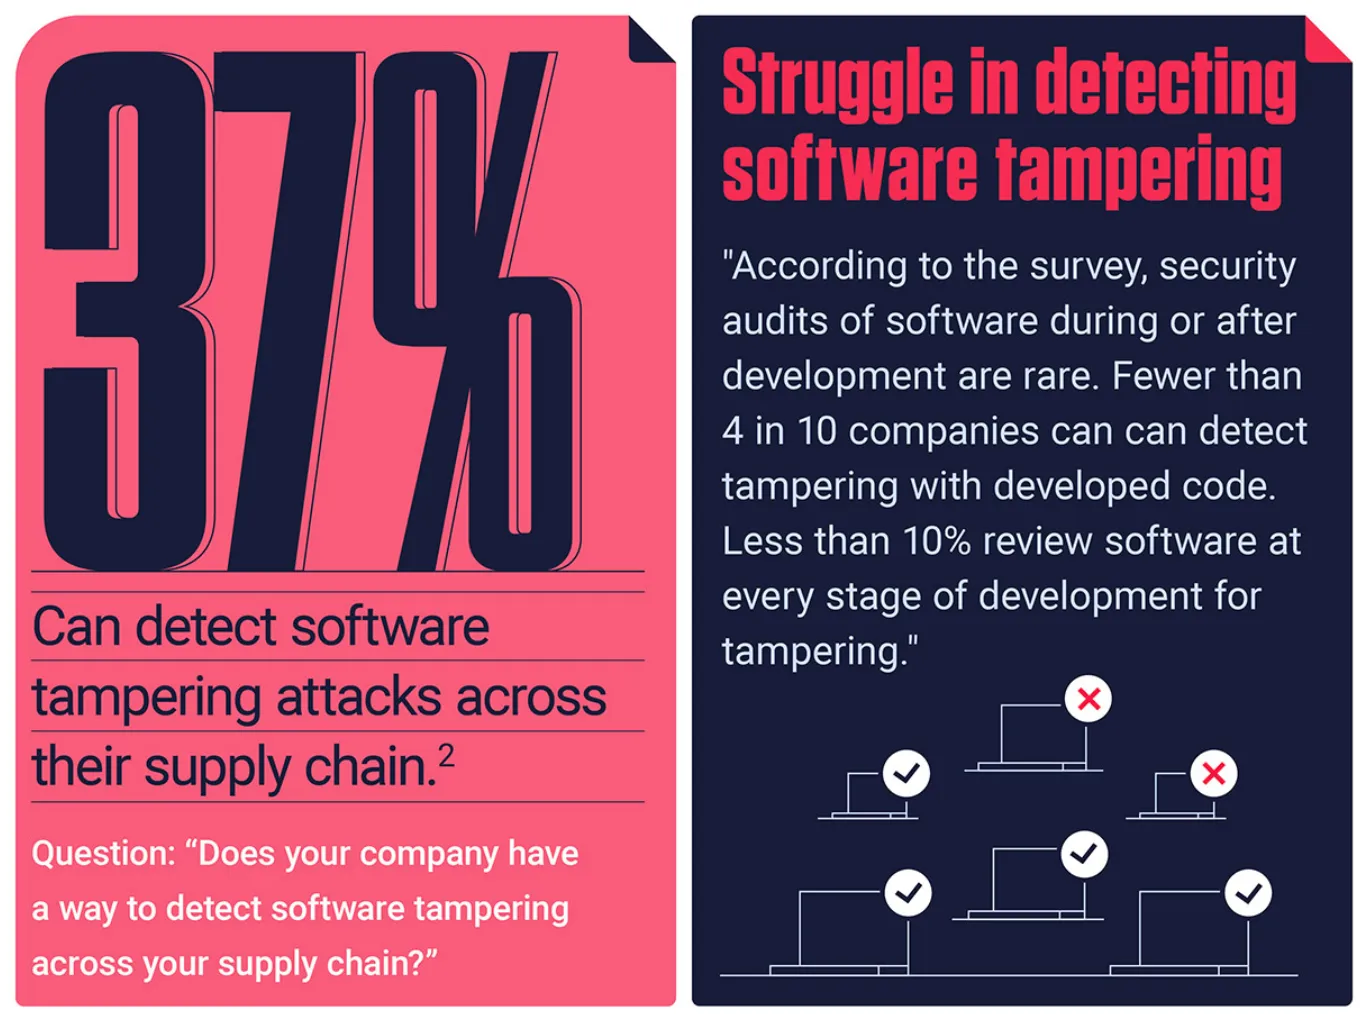
Figure 3: Survey finds software supply chain security top of mind for dev teams ... On 27 April 2015, Sergey Lozhkin, a Senior Security Researcher with GReAT at Kaspersky Lab, spoke about the importance of managing risk from targeted attacks and cyber-espionage campaigns, during a conference on cyber security he stated: "Mitigation strategies for advanced threats should include security policies and education, network security, comprehensive system administration and specialized security solutions, like... software patching features, application control, whitelisting and a default deny mode."In 2025, a study by the Austrian Chamber of Commerce (WKO) and AV-Comparatives identified what cybersecurity firms should do to assure their customers about supply chain security. This includes disclosing a software bill of materials, maintaining transparent data storage practices, providing detailed incident reports, and offering facilities where customers can inspect source codes and updates for the cybersecurity product. Only 3 of the 14 vendors examined provided such assurances.
Supply chain security (also "supply-chain security") activities aim to enhance the security of the supply chain or value chain, the transport and logistics systems for the world's cargo and to "facilitate legitimate trade". Their objective is to combine traditional practices of supply-chain management with the security requirements driven by threats such as terrorism, piracy, and theft. A healthy and robust supply chain absent from security threats requires safeguarding against disturbances at all levels such as facilities, information flow, transportation of goods, and so on. A secure supply chain is critical for organizational performance. Typical supply-chain security activities include: Credentialing of participants in the supply chain Screening and validating of the contents of cargo being shipped Advance notification of the contents to the destination country Ensuring the security of cargo while in transit, for example through the use of locks and tamper-proof seals Inspecting cargo on entry Theft and shrinkage can take place anywhere in the logistics chain: from the shipper, carrier, or consignee. It may be packages, pallet loads, and full truck loads. It can involve individuals with an opportunity to take cargo or can involve organized crime. Security systems involving surveillance systems, tracking systems, and broader corporate security are needed to reduce the theft of material.
The European Union's regulation on the Community Customs Code (2008) includes reference to supply chain security in its outline of the mission of each EU customs authority:Customs authorities shall be primarily responsible for the supervision of the Community's international trade, thereby contributing to ... overall supply chain security. In February 2021 US President Joe Biden made supply chain security one of his administration's priorities.
The Customs Trade Partnership against Terrorism (C-TPAT), a voluntary compliance program for companies to improve the security of their corporate supply chains. Operation Safe Commerce (OSC), a U.S. federal program designed to test and evaluate practices, policies and procedures aimed at improving the security of international containerized shipping. The World Customs Organization (WCO) adopted the Framework of Standards to Secure and Facilitate Global Trade in 2005, which consists of supply-chain security standards for Customs administrations including authorized economic operator (AEO) programs. The Container Security Initiative (CSI), a program led by U.S. Customs and Border Protection in the Department of Homeland Security (DHS) focused on screening containers at foreign ports. The Global Container Control Programme (CCP), a joint United Nations Office on Drugs and Crime (UNODC)/World Customs Organization (WCO) initiative working to establish effective container controls at select ports across the globe with the aim to prevent trafficking of drugs, chemicals and other contraband and to facilitate trade by strengthening cooperation between the customs, trade and enforcement communities.
The Global Trade Exchange, a DHS data-mining program designed to collect financial information about shipments, with the objective of determining the safety of cargo shipments. Pilot initiatives by companies in the private sector to track and monitor the integrity of cargo containers moving around the world using technologies such as RFID and GPS. The BSI Group undertakes an annual survey of supply chain risk exposure, identifying and updating the main supply chain security concerns.
In its 2020 report, drug smuggling, cargo theft of pharmaceuticals and medical supplies and increasing warehouse and facility theft were identified as particular concerns. The International Organization for Standardization (ISO) has released a series of standards for the establishment and management of supply-chain security. ISO/PAS 28000 Specification for Security Management Systems for the Supply Chain, offers public and private enterprise an international high-level management standard that enables organizations to utilize a globally consistent management approach to applying supply-chain security initiatives. ISO/IEC 20243 is The Open Trusted Technology Provider Standard (O-TTPS) (Mitigating Maliciously Tainted and Counterfeit Products) that addresses supply-chain security and secure engineering. The EU-US Summit held in Lisbon in November 2010, highlighting the need for their international "partnership to bring greater prosperity and security" for citizens on both sides of the Atlantic, provided a foundation for the Transatlantic Economic Council to build on, announcing at its December 2010 meeting an agreement "to deepen transatlantic cooperation in supply chain security policies". The Common Criteria offers with EAL 4 an opportunity to include necessary evaluations that assure supply chain security for IT products Supply chain cyber security is a subset of supply chain security which focuses on the digital aspects of the traditional supply chain as well as the supply chain for electronic and digital goods.
ICAO-WCO: Moving Air Cargo Globally - Air Cargo and Mail Secure Supply Chain and Facilitation Guidelines IMO FAQ on the ISPS Code MIT Project on Supply Chain Response to Terrorism Supply Chain Risk Management Maturity Model Stanford Global Supply Chain Management Forum Supply chain security: adding to a complex operational and institutional environment, A Grainger (2007) World Customs Journal: special issue on supply chain security Port and Maritime Security Online Chain of Perils: Hardening the Global Supply Chain and Strengthening America's Resilience ISO 28002 supply chain security and resilience CSA Cargo Security Information Global Supply Chain Security, James Giermanski, Scarecrow Press, 2012 - 218 Pages Implementing a Robust Supply Chain Security & Risk Management Authentication (from Greek: αIθεντικIς authentikos, "real, genuine", from αIθIντης authentes, "author") is the act of proving an assertion, such as the identity of a computer system user. In contrast with identification, the act of indicating a person or thing's identity, authentication is the process of verifying that identity. Authentication is relevant to multiple fields. In art, antiques, and anthropology, a common problem is verifying that a given artifact was produced by a certain person, or in a certain place (i.e. to assert that it is not counterfeit), or in a given period of history (e.g. by determining the age via carbon dating). In computer science, verifying a user's identity is often required to allow access to confidential data or systems. It might involve validating personal identity documents.
Authentication can be considered to be of three types: The first type of authentication is accepting proof of identity given by a credible person who has first-hand evidence that the identity is genuine. When authentication is required for art or physical objects, this proof could be a friend, family member, or colleague attesting to the item's provenance, perhaps by having witnessed the item in its creator's possession. With autographed sports memorabilia, this could involve someone attesting that they witnessed the object being signed. A vendor selling branded items implies authenticity, while they may not have evidence that every step in the supply chain was authenticated. The second type of authentication is comparing the attributes of the object itself to what is known about objects of that origin. For example, an art expert might look for similarities in the style of painting, check the location and form of a signature, or compare the object to an old photograph. An archaeologist, on the other hand, might use carbon dating to verify the age of an artifact, do a chemical and spectroscopic analysis of the materials used, or compare the style of construction or decoration to other artifacts of similar origin. The physics of sound and light, and comparison with a known physical environment, can be used to examine the authenticity of audio recordings, photographs, or videos. Documents can be verified as being created on ink or paper readily available at the time of the item's implied creation.
Attribute comparison may be vulnerable to forgery. In general, it relies on the facts that creating a forgery indistinguishable from a genuine artifact requires expert knowledge, that mistakes are easily made, and that the amount of effort required to do so is considerably greater than the amount of profit that can be gained from the forgery. In art and antiques, certificates are of great importance for authenticating an object of interest and value. Certificates can, however, also be forged, and the authentication of these poses a problem. For instance, the son of Han van Meegeren, the well-known art-forger, forged the work of his father and provided a certificate for its provenance as well. Criminal and civil penalties for fraud, forgery, and counterfeiting can reduce the incentive for falsification, depending on the risk of getting caught. Currency and other financial instruments commonly use this second type of authentication method. Bills, coins, and cheques incorporate hard-to-duplicate physical features, such as fine printing or engraving, distinctive feel, watermarks, and holographic imagery, which are easy for trained receivers to verify. The third type of authentication relies on documentation or other external affirmations. In criminal courts, the rules of evidence often require establishing the chain of custody of evidence presented. This can be accomplished through a written evidence log, or by testimony from the police detectives and forensics staff that handled it. Some antiques are accompanied by certificates attesting to their authenticity. Signed sports memorabilia is usually accompanied by a certificate of authenticity. These external records have their own problems of forgery and perjury and are also vulnerable to being separated from the artifact and lost.
Taggant fingerprinting – uniquely coded microscopic materials that are verified from a database Encrypted micro-particles – unpredictably placed markings (numbers, layers and colors) not visible to the human eye Holograms – graphics printed on seals, patches, foils or labels and used at the point of sale for visual verification Micro-printing – second-line authentication often used on currencies Serialized barcodes UV printing – marks only visible under UV light Track and trace systems – use codes to link products to the database tracking system Water indicators – become visible when contacted with water DNA tracking – genes embedded onto labels that can be traced Color-shifting ink or film – visible marks that switch colors or texture when tilted Tamper evident seals and tapes – destructible or graphically verifiable at point of sale 2d barcodes – data codes that can be tracked RFID chips NFC chips A difficult-to-reproduce physical artifact, such as a seal, signature, watermark, special stationery, or fingerprint. A shared secret, such as a passphrase, in the content of the message. An electronic signature; public-key infrastructure is often used to cryptographically guarantee that a message has been signed by the holder of a particular private key. The opposite problem is the detection of plagiarism, where information from a different author is passed off as a person's own work. A common technique for proving plagiarism is the discovery of another copy of the same or very similar text, which has different attribution. In some cases, excessively high quality or a style mismatch may raise suspicion of plagiarism.
The ways in which someone may be authenticated fall into three categories, based on what is known as the factors of authentication: something the user knows, something the user has, and something the user is. Each authentication factor covers a range of elements used to authenticate or verify a person's identity before being granted access, approving a transaction request, signing a document or other work product, granting authority to others, and establishing a chain of authority. Security research has determined that for a positive authentication, elements from at least two, and preferably all three, factors should be verified. The three factors (classes) and some of the elements of each factor are: Knowledge: Something the user knows (e.g., a password, partial password, passphrase, personal identification number (PIN), challenge–response (the user must answer a question or pattern), security question). Ownership: Something the user has (e.g., wrist band, ID card, security token, implanted device, cell phone with a built-in hardware token, software token, or cell phone holding a software token). Inherence: Something the user is or does (e.g., fingerprint, retinal pattern, DNA sequence (there are assorted definitions of what is sufficient), signature, face, voice, unique bio-electric signals, or other biometric identifiers). Historically, fingerprints have been used as the most authoritative method of authentication, but court cases in the US and elsewhere have raised fundamental doubts about fingerprint reliability. Outside of the legal system as well, fingerprints are easily spoofable, with British Telecom's top computer security official noting that "few" fingerprint readers have not already been tricked by one spoof or another. Hybrid or two-tiered authentication methods offer a compelling solution, such as private keys encrypted by fingerprint inside of a USB device.
Multi-factor authentication involves two or more authentication factors (something you know, something you have, or something you are). Two-factor authentication is a special case of multi-factor authentication involving exactly two factors. For example, using a bank card (something the user has) along with a PIN (something the user knows) provides two-factor authentication. Business networks may require users to provide a password (knowledge factor) and a pseudorandom number from a security token (ownership factor). Access to a very-high-security system might require a mantrap screening of height, weight, facial, and fingerprint checks (several inherence factor elements) plus a PIN and a day code (knowledge factor elements), but this is still a two-factor authentication.
2. System Architecture & Core Working Principles Enrollment – an individual applies to a credential service provider (CSP) to initiate the enrollment process. After successfully proving the applicant's identity, the CSP allows the applicant to become a subscriber. Authentication – After becoming a subscriber, the user receives an authenticator e.g., a token and credentials, such as a user name. He or she is then permitted to perform online transactions within an authenticated session with a relying party, where they must provide proof that he or she possesses one or more authenticators. Life-cycle maintenance – the CSP is charged with the task of maintaining the user's credential over the course of its lifetime, while the subscriber is responsible for maintaining his or her authenticator(s).
The authentication of information can pose special problems with electronic communication, such as vulnerability to man-in-the-middle attacks, whereby a third party taps into the communication stream, and poses as each of the two other communicating parties, in order to intercept information from each. Extra identity factors can be required to authenticate each party's identity.
In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection. The SolarWinds compromise was executed by modifying the build process to inject malicious code into signed, legitimate software updates. The XZ Utils backdoor was injected by a contributor who gained maintainer trust over years. Both attacks demonstrate the same principle: the source code repository and the published artifact are two different things, and the gap between them -- the build pipeline -- is an attack surface that traditional application security controls do not cover. SLSA provides a framework for closing this gap by requiring that build pipelines produce verifiable provenance, that builds run in isolated environments, and that source code changes undergo review before being built. This guide covers the SLSA framework requirements, how to implement provenance generation in GitHub Actions, and how to verify provenance in your deployment pipeline.
SLSA 1.0 defines three build levels with progressively stronger guarantees about build integrity. Each level builds on the previous -- reaching L3 requires meeting all L1 and L2 requirements as well. SLSA Build L1 requires that the build process produces a provenance document containing the builder identity, source repository, and output artifact digest. No requirements are made about the trustworthiness of the build platform or the provenance generation process. An attacker who controls the build environment could produce forged provenance. L1 provides a documented build audit trail and enables tooling to read provenance, but does not provide strong security guarantees. It is the easiest level to achieve and a prerequisite for L2 and L3.
SLSA Build L2 requires that the build runs on a hosted, managed build platform (GitHub Actions hosted runners, Google Cloud Build, AWS CodeBuild) and that provenance is generated by the platform itself -- not by user-controlled build scripts. This means the provenance cannot be forged by modifying the build script: the platform signs the provenance with its own identity, which the build script cannot access. L2 prevents a compromised build script from producing false provenance claims. GitHub Actions with SLSA GitHub Generator meets L2.
SLSA Build L3 adds requirements for build environment isolation and hardening. The build runs in an ephemeral, isolated environment with no shared state between builds. The build cannot access the network during execution (hermetic). The build environment cannot be influenced by user-controlled pipeline code. Source code must have undergone two-party review (branch protection with required reviewers) before being built. L3 provides the strongest supply chain guarantee: even if an attacker compromises a developer account, they cannot get malicious code built without passing two-party review.
For internal applications, SLSA Build L2 is a practical target: it provides non-forgeable provenance from a managed build platform and can be achieved in GitHub Actions today with the SLSA GitHub Generator. SLSA Build L3 is appropriate for artifacts distributed to external consumers (open-source libraries, vendor-distributed software, platform binaries). Start with L1 (provenance generation) to enable tooling, upgrade to L2 when feasible, and plan for L3 on critical artifacts distributed externally.
The SLSA GitHub Generator provides reusable GitHub Actions workflows that generate SLSA provenance for multiple artifact types (generic binaries, Go binaries, container images, Maven/Gradle artifacts). It is the practical implementation of SLSA provenance generation in GitHub Actions. To generate provenance for any artifact type, call the generic generator workflow: in your release workflow, after building the artifact, add a job that calls slsa-framework/slsa-github-generator/.github/workflows/generator_generic_slsa3.yml@v2 with inputs hash (SHA-256 hash of your artifact) and filename. The generator runs in a separate job, produces a signed .intoto.jsonl provenance file, and uploads it alongside the release artifact. The generator job uses a distinct OIDC identity from your build job, meeting SLSA L3 requirements.
For container images, use the container image generator: generator_container_slsa3.yml. Pass the image digest (from the docker push output) as input. The generator produces provenance attesting that the image at that digest was built by your GitHub Actions workflow from the specified source repository and commit. The provenance is stored as an OCI artifact in the registry alongside the image, discoverable via the OCI referrers API.
The SLSA generator requires the SHA-256 hash of your artifact as input. In your build job: HASH=$(sha256sum myapp-binary | awk '{print $1}') and pass it to the generator via job output. For multiple artifacts, compute a single JSON hash file: sha256sum artifact1 artifact2 > hashes.txt, base64-encode it, and pass the encoded value as the hash input. The generator will verify each artifact against its expected hash in the provenance.
SLSA provenance attests to build integrity. cosign (Sigstore) attests to artifact identity by signing the artifact itself. Together they provide a complete chain: provenance proves the build process was legitimate, and the cosign signature proves the artifact has not been modified since the provenance was generated. After building the artifact and generating SLSA provenance, sign the artifact with cosign using keyless signing: cosign sign-blob --yes --output-certificate artifact.pem --output-signature artifact.sig myapp-binary. The OIDC token from the GitHub Actions runner is used to obtain a Fulcio certificate. The signature and certificate are uploaded alongside the binary. The signing event is logged in the Rekor transparency log, providing an immutable audit trail.
For container images: cosign sign --yes myregistry/myapp@sha256:
cosign attest integrates SLSA provenance with OCI images: cosign attest --yes --predicate provenance.json --type slsaprovenance myregistry/myapp@sha256:
Generating provenance is only half of the SLSA model -- the other half is verifying provenance at the point of consumption before an artifact is deployed or used. Without verification, provenance generation is a logging exercise rather than a security control. Install slsa-verifier (go install github.com/slsa-framework/slsa-verifier/v2/cli/slsa-verifier@latest). To verify a binary: slsa-verifier verify-artifact myapp-binary --provenance-path myapp-binary.intoto.jsonl --source-uri github.com/myorg/myrepo.
To additionally verify a specific tag: add --source-versioned-tag v1.2.3. Integrate this command into your deployment pipeline as a mandatory step that fails the pipeline if verification does not succeed. A failed verification means the artifact cannot be traced to a trusted build of the specified source. For container images, use Sigstore Policy Controller (admission webhook for Kubernetes) to enforce that all images deployed to specific namespaces have valid SLSA provenance attestations and cosign signatures. Create a ClusterImagePolicy resource specifying the expected OIDC issuer and subject pattern for the provenance signer. Images without valid attestations matching the policy are rejected at admission time before the pod is created.
For Go modules and npm packages, verification tooling is still maturing but available. npm has experimental provenance support: packages published from GitHub Actions with SLSA provenance show a 'Provenance' badge on the npm registry. Go's vulnerability database integrates with supply chain tooling. For Java artifacts published to Maven Central, slsa-verifier supports JAR verification via the Maven Central provenance API. Check the SLSA tools ecosystem page for the current state of language-specific verification.
SLSA and SBOMs are frequently mentioned together because both address software supply chain security, but they answer different questions. Understanding their complementary relationship helps organizations deploy both effectively. SLSA provenance answers: was this binary built from the source code I can inspect? Was it built by a trusted, isolated build platform? Did the source code undergo required review? It does not tell you what is in the artifact -- only that the artifact came from a specific, verifiable build process. An artifact can have perfect SLSA L3 provenance and still contain a vulnerable dependency that needs patching.
An SBOM (in CycloneDX or SPDX format) enumerates the components, libraries, and their versions included in an artifact, along with their licenses and known vulnerability identifiers. It answers: does this artifact contain Log4j 2.14.1? Is this dependency licensed under a GPL license that requires source disclosure? SBOMs enable vulnerability management -- you can query an SBOM against a CVE database to find vulnerable components. They do not prove how the artifact was built.
The complete supply chain security posture requires both. Generate SLSA provenance in the build pipeline to prove build integrity. Generate an SBOM using syft, Trivy, or your build tool's SBOM plugin at build time to document components. Attach both to the release artifact. Verification at deployment time checks the SLSA provenance (was it built from the right source?) and scans the SBOM against a vulnerability database (does it contain known-vulnerable dependencies?). EO 14028 and NIST SP 800-218 (SSDF) both require SBOM generation; SLSA provides the build integrity complement that SBOMs do not cover.
SLSA implementation is a maturity journey: start with Build L1 by integrating the SLSA GitHub Generator into your release workflows to generate provenance for your most critical artifacts -- the overhead is a single reusable workflow call. Upgrade to L2 by ensuring builds run on hosted GitHub Actions runners rather than self-hosted ones. Plan for L3 on externally distributed artifacts by enabling branch protection with required reviewers and hermetic dependency management. Pair SLSA provenance with cosign signing and integrate slsa-verifier into deployment pipelines as a mandatory gate. Add SBOM generation alongside SLSA to cover the component risk surface that provenance does not address. Together, these controls implement the supply chain security requirements of EO 14028 and NIST SSDF and provide verifiable defense against build process compromise attacks.
A SLSA provenance attestation is a JSON document in the in-toto attestation format that contains: the builder identity (e.g., the GitHub Actions runner with its OIDC identity), the source repository URL and commit SHA, the build trigger (the workflow file that initiated the build), build parameters (any inputs that affected the build), the invocation ID (a unique build run identifier), and the output artifact digest (SHA-256 hash of the built artifact). The provenance is signed by the build platform -- in GitHub Actions with SLSA GitHub Generator, it is signed using Sigstore's keyless signing with the runner's OIDC identity.
The signature is stored in the Rekor transparency log. Build L1 requires provenance to exist and be available, but makes no requirements about the trustworthiness of the build platform. An attacker who controls the build platform could produce fake provenance. Build L2 requires that the build platform is a hosted, managed service (not a self-managed runner) and that the provenance is generated by the platform itself rather than by user-controlled code in the build. This means the provenance cannot be forged by the build script. Build L3 additionally requires that the build runs in an isolated, ephemeral environment that cannot be influenced by previous builds or external input during the build, that the build environment is hardened against tampering, and that the source code underwent two-party review before being built.
3. Software Implementation, Frameworks & Protocols A hermetic build has no network access during the build execution and resolves all dependencies from a locked, pre-fetched set of inputs. Non-hermetic builds fetch dependencies at build time from the internet, which means the artifact is influenced by whatever version of the dependency was available at that moment -- an attacker who controls a package registry can inject a malicious version into a non-hermetic build even without modifying the source code. Hermetic builds prevent this: all inputs are fixed before the build starts, the build runs without network access, and the output is fully determined by the fixed inputs.
SLSA provenance attestations use the in-toto attestation framework as their underlying specification. in-toto is a framework for defining supply chain policies and producing link metadata that documents steps in the supply chain. SLSA uses the in-toto Attestation Framework's envelope format (predicateType and predicate fields) for provenance documents, specifically with predicateType 'https://slsa.dev/provenance/v1'. You can think of in-toto as providing the vocabulary and format and SLSA as providing the specific requirements and trust levels for build provenance.
The SLSA GitHub Generator is a reusable GitHub Actions workflow maintained by the SLSA team that generates SLSA provenance for build artifacts. Your workflow calls the generator as a reusable workflow, passing the artifact and its hash. The generator runs in a separate workflow job with its own OIDC identity (distinct from the build job's identity), produces a signed SLSA provenance attestation, and uploads it as a release asset alongside the artifact. Because provenance generation runs in a separate job controlled by the generator (not your build script), the provenance meets SLSA Build L3 requirements when using GitHub's hosted runners.
SLSA provenance answers 'How was this artifact built and by whom?' -- it proves build integrity and chain of custody. An SBOM (Software Bill of Materials) answers 'What components are in this artifact?' -- it lists all dependencies, their versions, and their licenses. They are complementary, not alternatives. SLSA provenance tells you the artifact was built from a specific commit by a verified build platform. The SBOM tells you what libraries are included so you can check for known CVEs. Supply chain security requires both: provenance to verify build integrity and SBOM to assess component risk.
Use the slsa-verifier CLI tool. For a binary artifact: slsa-verifier verify-artifact myapp-binary --provenance-path provenance.intoto.jsonl --source-uri github.com/myorg/myrepo --source-versioned-tag v1.2.3. This verifies that the provenance signature is valid (checking the Rekor transparency log), the artifact digest in the provenance matches the artifact you have, the source repository matches what you expect, and the build platform meets the claimed SLSA level. Integrate this verification step into your deployment pipeline as a mandatory gate before any artifact is deployed.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. A software supply chain attack turns trusted software into a delivery path for malware. Attackers compromise a vendor, dependency, CI/CD pipeline, or update mechanism and use that trusted channel to reach downstream endpoints. Because the malicious code may carry legitimate trust signals, runtime behavior monitoring is essential to detect it after execution.
A software supply chain malware attack occurs when attackers compromise a trusted software vendor, open-source dependency, development tool, CI/CD pipeline, or software update mechanism to deliver malicious code to downstream users. MITRE ATT&CK classifies this activity as T1195: Supply Chain Compromise , where adversaries manipulate software or its delivery mechanisms before it reaches the intended consumer.
MITRE ATT&CK divides T1195: Supply Chain Compromise into two sub-techniques based on where attackers compromise the software supply chain: The key difference is where the attacker enters the supply chain. T1195.001 typically targets dependencies and development environments, while T1195.002 focuses on software vendors and distribution mechanisms. Both can ultimately result in malicious code executing on downstream endpoints.
Attackers first compromise a trusted part of the supply chain, such as software maintainer accounts, source code repositories, CI/CD systems (GitHub Actions, Jenkins, CircleCI), package registry accounts and API tokens, or vendor build and signing infrastructure. Attackers introduce malicious code through source code commits, malicious dependencies, build pipeline scripts, or package lifecycle scripts such as npm's preinstall , postinstall , or install hooks.
The compromised software is distributed through legitimate channels such as npm, PyPI, or a vendor's official update server. Because it comes through trusted infrastructure, it may retain legitimate signatures, domains, and software management workflows. The compromised software reaches downstream systems through normal installation or update processes. Malicious code may execute during package installation or when the legitimate application loads the compromised component.
After execution, attackers can pursue familiar objectives such as credential theft, persistence, C2 communication, lateral movement, and data exfiltration. The challenge is that the activity may originate from a trusted application rather than an obviously malicious executable. Software supply chain attacks can occur at almost any stage of the development and deployment lifecycle. NIST SP 800-161r1 identifies broader supply chain risk across development, build, packaging, distribution, and deployment.
Attackers modify a legitimate software update and distribute it through the vendor's trusted channel. Because the update appears legitimate, victims may install the malware as part of routine maintenance. Attackers create malicious packages and publish them to public registries. These packages may appear functional while executing a malicious payload during installation.
Attackers steal a legitimate maintainer's credentials or session tokens and use them to publish malicious versions of trusted packages. Existing users may then receive the compromised version through routine updates. Dependency confusion exploits how package managers resolve package names. An attacker publishes a malicious package with the same name as an internal dependency, often with a higher version number, causing the package manager to install the malicious public version instead.
Attackers publish packages with names that closely resemble legitimate libraries, such as reqeusts instead of requests . Developers or automated pipelines can accidentally install these malicious packages. Package ecosystems such as npm support lifecycle hooks that can execute code automatically during installation. Hooks such as preinstall and postinstall can trigger malicious code without requiring the application to import or call the compromised package.
4. Practical Deployment, Analysis & Case Studies CI/CD systems often have access to source code, dependencies, build artifacts, signing infrastructure, and production registries. Compromising a pipeline or build agent can allow attackers to inject malicious code during the build process. Attackers modify a legitimate software installer to include a malicious component. The application may work normally while silently installing malware alongside it.
Attackers can compromise build or signing infrastructure and inject malicious functionality before an application is digitally signed. The resulting binary may therefore carry a valid signature even though its contents have been compromised. A compromised software update may come from a legitimate vendor, carry a valid digital signature, arrive through an official distribution channel, and behave like familiar software. Static security checks may therefore find nothing obviously malicious.
This is why detecting supply chain malware requires more than checking what software looks like before execution. Runtime behavioral monitoring and process telemetry are critical for identifying what trusted software actually does after it runs. Rather than relying on a single signal, effective detection correlates events such as package installation, lifecycle-script execution, process activity, and outbound network connections.
Software supply chain attacks are not new, but their scale, automation, and sophistication have increased. Three trends stand out. Stolen developer credentials can now turn a single compromised package into a propagation mechanism. Malware uses those credentials to spread across every other package the attacker can reach—multiplying the blast radius from one account.
Attackers increasingly harvest cloud credentials, repository tokens, and package-publishing keys stored in developer environments and build pipelines—providing a path from a single package compromise into production environments. Supply chain compromise has become a preferred technique for nation-state actors. A single compromised dependency or vendor can give adversaries simultaneous access to thousands of downstream organizations with minimal per-target effort.
The SolarWinds attack remains one of the most significant examples of software supply chain compromise. Attackers compromised the SolarWinds Orion build process and inserted the SUNBURST backdoor into legitimate software updates. Because the compromised updates were distributed through SolarWinds' legitimate update mechanism and digitally signed, customers installed the malware as part of a routine software update. MITRE ATT&CK classifies the attack under T1195.002: Compromise Software Supply Chain .
Key lesson: A trusted and digitally signed update is not necessarily safe if the software was compromised before it reached the customer. The 3CX compromise demonstrated how one supply chain attack can enable another. Attackers compromised the 3CX build environment and distributed a trojanized version of the 3CX Desktop App to downstream users. The malicious installer used DLL side-loading to execute the payload while appearing to be a legitimate application.
The campaign combined T1195.002: Compromise Software Supply Chain with T1574.002: DLL Side-Loading . Key lesson: When trusted software is compromised upstream, tracing the original point of entry can become extremely difficult. In March 2026, attackers compromised the npm publishing credentials of the axios project and released malicious versions of the widely used JavaScript HTTP client library. The compromised releases contained a malicious dependency with a postinstall script that executed automatically when affected projects installed the package. The malware targeted developer and CI/CD credentials and deployed a cross-platform backdoor.
This is a strong example of T1195.001: Compromise Software Dependencies and Development Tools . Key lesson: A trusted package can become a powerful attack vector when its publishing credentials are compromised. The ChainDrop campaign demonstrated a more aggressive evolution of npm supply chain attacks. After compromising a maintainer account, the malware harvested npm, GitHub, cloud, and other credentials from infected environments. It then used stolen publishing credentials to identify other packages it could modify and propagate itself across them, transforming a single compromised account into a mechanism for distributing malicious releases at scale.
The campaign also used blockchain based infrastructure for command and control, making traditional domain based blocking more difficult. Key lesson: Supply chain malware can now use stolen developer credentials not only to maintain persistence, but also to propagate through the software ecosystem actively.
In May 2026, Microsoft's Defender for Cloud Security Research team identified a campaign involving malicious npm packages designed to mimic legitimate OpenSearch, Elasticsearch, DevOps, and configuration libraries. The packages used install-time scripts to execute a credential harvesting payload targeting cloud, GitHub, Vault, and npm credentials. Key lesson: Typosquatting remains effective because it exploits a simple weakness in the supply chain: developers and automated build systems can install malicious packages before their legitimacy is fully verified.
Detecting supply chain malware requires more than static file analysis or digital signature validation. Security teams need visibility into what software does after execution. npm, pip, or other package processes spawning cmd.exe , PowerShell , or bash during installation can indicate malicious lifecycle scripts. This is one of the highest fidelity signals available.
Install scripts executing encoded commands or downloading additional payloads can indicate an obfuscated dropper. Look for Base64-encoded arguments or -EncodedCommand flags in process telemetry. A trusted application making a new or unusual outbound connection after installation can indicate C2 activity. Correlate network events with the installation timeline.
5. Performance Evaluation & Extended Technical Observations An update process dropping and executing previously unseen binaries particularly from user-writable locations, is a strong behavioral signal requiring immediate investigation. CI/CD systems making outbound connections that fall outside their normal behavior can indicate pipeline compromise or credential theft. Baseline normal CI/CD network activity to identify anomalies.
Supply chain malware such as ChainDrop has used blockchain infrastructure for C2, making traditional domain-based detection less effective. Behavioral and memory-based detection is essential for these cases. No single security control can prevent every software supply chain attack. Effective protection requires multiple layers across the software lifecycle.
Maintain an up-to-date inventory of commercial software, open-source dependencies, and internal packages across development, build, and production environments. A Software Bill of Materials (SBOM) provides a machine readable inventory of software components, helping organizations quickly identify whether a compromised component is present. Pin versions and use lockfiles to prevent unexpected package updates. Use private registries or proxies to control which packages reach development and build environments. Disable install time scripts where possible, particularly in CI/CD environments, and continuously scan dependencies against vulnerability and threat intelligence sources.
Apply least privilege to build agents and service accounts. Enforce MFA on developer, package registry, and CI/CD accounts. Store API keys, cloud credentials, and publishing tokens in dedicated secret-management systems, and monitor changes to CI/CD workflows and build scripts. Standards and tools such as SLSA, Sigstore/cosign, in-toto, and OpenSSF Scorecard can help organizations verify software provenance, artifact integrity, and the security posture of open-source dependencies.
Upstream controls reduce the likelihood of compromised software reaching an endpoint, but cannot eliminate the risk entirely. When malicious software does execute, runtime behavioral monitoring, EDR, process telemetry, network monitoring, and memory visibility can detect suspicious activity. ManageEngine Malware Protection Plus provides behavioral and reputation-based detection to give security teams visibility into suspicious process activity, persistence, and endpoint state after a supply chain compromise.
An attack where malicious code is introduced into legitimate software or its delivery process and distributed to downstream users. The attacker compromises a trusted component such as a vendor's build system, an open-source package, or a CI/CD pipeline to deliver malware through channels the victim already trusts. Attackers compromise a trusted component, insert malicious code, and use the legitimate software or distribution channel to deliver it downstream. The malicious code then executes on the victim's system during installation, update, or normal application use potentially before anyone notices the software was compromised.
Common vectors include malicious packages published to npm or PyPI, account hijacking of legitimate maintainers, typosquatting, dependency confusion attacks, compromised CI/CD pipelines, trojanized software installers, and compromised software update mechanisms. An attack where an attacker publishes a malicious public package that mimics the name of an internal private dependency.
Package managers may install the malicious public version instead of the intended internal one, particularly when the attacker uses a higher version number. T1195.001 covers the compromise of software dependencies and development tools such as npm packages, build tools, and IDE plugins. T1195.002 covers broader software supply chain compromise, including vendor software and distribution mechanisms such as update servers and installers.
Yes. Malicious code inserted into software before signing by compromising the build environment, can result in a compromised application carrying a valid digital signature. The SolarWinds SUNBURST attack is the clearest example: the malicious update was signed with a legitimate SolarWinds certificate. A Software Bill of Materials (SBOM) is a machine readable inventory of a software application's components and dependencies. When a supply chain compromise is discovered, an SBOM allows organizations to quickly determine whether a compromised component is present in their environments.
Yes. Runtime behavioral monitoring can detect suspicious activity from compromised software after it executes such as trusted applications spawning unexpected processes, making unusual network connections, or establishing persistence even when the software passed signature validation at install time. ðIII Updated September 12, 2026 âII added the Nuclei signature-verification bypass (CVE-2024-43405): what happens when the verifier and the executor are different parsers.
A defender’s reference for software supply chain risks âII threat model across the SDLC, package-registry attack patterns, CI/CD hardening, artifact provenance and signing, SBOMs, dependency scanning, case studies, and a checklist. Draws on published advisories and incident write-ups. A software supply chain attack compromises a dependency, tool, build system, or distribution channel that the target trusts, rather than attacking the target directly. The malicious payload rides in on a routine npm install , pip install , docker pull , or CI build âII bypassing perimeter defenses because the artifact appears legitimate.
Growth: Supply chain attacks on package registries surged 73% in 2025âII2026. Sonatype tracked a 742% increase between 2019 and 2022. OSSF and Bastion 2026 reports attribute the spike to nation-state actors (notably DPRK clusters publishing ~1,700 malicious packages across npm, PyPI, Go, and Rust), credential-stealing worms, and industrialized typosquatting.
Map threats to lifecycle stages. Each stage has distinct actors, assets, and controls. STRIDE per stage: Every stage maps to Spoofing (forged provenance), Tampering (injected code), Repudiation (missing attestations), Information disclosure (leaked secrets via install scripts), DoS (dependency deletion à la left-pad), and Elevation (signing-key theft).
Reduce any factor. Release-age gates attack window_before_detection ; ignore-scripts attacks privilege(install_context) ; pinning attacks trust_score drift. Occurs when a package manager prefers public registries over private ones for a name used both internally and publicly. Avoid --extra-index-url âII it merges indices and picks highest version. Use --index-url to a repository-manager virtual registry that proxies public content behind policy.
LLMs regularly hallucinate plausible-sounding package names. Attackers squat those names. Defensive verification before installing any AI-suggested package: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Supply%20chain%20attack • https://en.wikipedia.org/wiki/Supply%20chain%20security • https://en.wikipedia.org/wiki/Authentication • https://www.decryptiondigest.com/blog/slsa-software-supply-chain-framework-guide • https://www.manageengine.com/malware-protection/articles/software-supply-chain-malware.html • https://chs.us/guides/supply-chain/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Supply Chain Code Tampering Detection.
[*] Metasploit Scan Running on Target Subnet for Supply Chain Code Tampering Detection... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |