Complete Technical Paper Content — Sybil Attack Detection In Decentralized Peer Networks
Overview & System Context
Sybil Attack Detection In Decentralized Peer Networks: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9530 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A Sybil attack is a type of attack on a computer network service in which an attacker subverts the service's reputation system by creating a large number of pseudonymous identities and uses them to gain a disproportionately large influence. It is named after the subject of the book Sybil, a case study of a woman diagnosed with dissociative identity disorder. The name was suggested in or before 2002 by Brian Zill at Microsoft Research. The term pseudospoofing had previously been coined by L.
Detweiler on the Cypherpunks mailing list and used in the literature on peer-to-peer systems for the same class of attacks prior to 2002, but this term did not gain as much influence as "Sybil attack". Tor is a free overlay network for enabling anonymous communication. It is built on free and open-source software run by over seven thousand volunteer-operated relays worldwide, as well as by millions of users who route their internet traffic via random paths through these relays. This technique is called onion routing. Using Tor makes it more difficult to trace a user's internet activity by preventing any single point on the internet (other than the user's device) from being able to view both where traffic originated from and where it is ultimately going to at the same time. This conceals a user's location and usage from anyone performing network surveillance or traffic analysis from any such point, protecting the user's freedom and ability to communicate confidentially.
In 2004, the Naval Research Laboratory released the code for Tor under a free license, and the Electronic Frontier Foundation (EFF) began funding Dingledine and Mathewson to continue its development. In 2006, Dingledine, Mathewson, and five others founded The Tor Project, a Massachusetts-based 501(c)(3) research-education nonprofit organization responsible for maintaining Tor. The EFF acted as The Tor Project's fiscal sponsor in its early years, and early financial supporters included the U.S. Bureau of Democracy, Human Rights, and Labor and International Broadcasting Bureau, Internews, Human Rights Watch, the University of Cambridge, Google, and Netherlands-based Stichting NLnet. Over the course of its existence, various Tor vulnerabilities have been discovered and occasionally exploited. Attacks against Tor are an active area of academic research that is welcomed by The Tor Project itself.
Tor enables its users to surf the Internet, chat and send instant messages anonymously, and is used by a wide variety of people for both licit and illicit purposes. Tor has, for example, been used by criminal enterprises, hacktivism groups, and law enforcement agencies at cross purposes, sometimes simultaneously; likewise, agencies within the U.S. government variously fund Tor (the U.S. State Department, the National Science Foundation, and – through the Broadcasting Board of Governors, which itself partially funded Tor until October 2012 – Radio Free Asia) and seek to subvert it. Tor was one of a dozen circumvention tools evaluated by a Freedom House-funded report based on user experience from China in 2010, which include Ultrasurf, Hotspot Shield, and Freegate. Tor is not meant to completely solve the issue of anonymity on the web. Tor is not designed to completely erase tracking but instead to reduce the likelihood for sites to trace actions and data back to the user. Tor can also be used for illegal activities. These can include censorship circumvention, as well as distribution of child abuse content, drug sales, or malware distribution. Tor has been described by The Economist, in relation to Bitcoin and Silk Road, as being "a dark corner of the web". It has been targeted by the American National Security Agency and the British GCHQ signals intelligence agencies, albeit with marginal success, and more successfully by the British National Crime Agency in its Operation Notarise. At the same time, GCHQ has been using a tool named "Shadowcat" for "end-to-end encrypted access to VPS over SSH using the Tor network". Tor can be used for anonymous defamation, unauthorized news leaks of sensitive information, copyright infringement, distribution of illegal sexual content, selling controlled substances, weapons, and stolen credit card numbers, money laundering, bank fraud, credit card fraud, identity theft and the exchange of counterfeit currency; the black market utilizes the Tor infrastructure, at least in part, in conjunction with Bitcoin. It has also been used to brick IoT devices. In its complaint against Ross William Ulbricht of Silk Road, the US Federal Bureau of Investigation acknowledged that Tor has "known legitimate uses". According to CNET, Tor's anonymity function is "endorsed by the Electronic Frontier Foundation (EFF) and other civil liberties groups as a method for whistleblowers and human rights workers to communicate with journalists". EFF's Surveillance Self-Defense guide includes a description of where Tor fits in a larger strategy for protecting privacy and anonymity. In 2014, the EFF's Eva Galperin told Businessweek that "Tor's biggest problem is press. No one hears about that time someone wasn't stalked by their abuser. They hear how somebody got away with downloading child porn." The Tor Project states that Tor users include "normal people" who wish to keep their Internet activities private from websites and advertisers, people concerned about cyber-spying, and users who are evading censorship such as activists, journalists, and military professionals. In November 2013, Tor had about four million users. According to the Wall Street Journal, in 2012 about 14% of Tor's traffic connected from the United States, with people in "Internet-censoring countries" as its second-largest user base. Tor is increasingly used by victims of domestic violence and the social workers and agencies that assist them, even though shelter workers may or may not have had professional training on cyber-security matters. Properly deployed, however, it precludes digital stalking, which has increased due to the prevalence of digital media in contemporary online life. Along with SecureDrop, Tor is used by news organizations such as The Guardian, The New Yorker, ProPublica and The Intercept to protect the privacy of whistleblowers. In March 2015, the Parliamentary Office of Science and Technology released a briefing which stated that "There is widespread agreement that banning online anonymity systems altogether is not seen as an acceptable policy option in the U.K." and that "Even if it were, there would be technical challenges." The report further noted that Tor "plays only a minor role in the online viewing and distribution of indecent images of children" (due in part to its inherent latency); its usage by the Internet Watch Foundation, the utility of its onion services for whistleblowers, and its circumvention of the Great Firewall of China were touted. Tor's executive director, Andrew Lewman, also said in August 2014 that agents of the NSA and the GCHQ have anonymously provided Tor with bug reports. The Tor Project's FAQ offers supporting reasons for the EFF's endorsement: Figure 1: Sybil Attack Detection in Vehicular Network Projects - YouTube Criminals can already do bad things. Since they're willing to break laws, they already have lots of options available that provide better privacy than Tor provides... Tor aims to provide protection for ordinary people who want to follow the law. Only criminals have privacy right now, and we need to fix that...
So yes, criminals could in theory use Tor, but they already have better options, and it seems unlikely that taking Tor away from the world will stop them from doing their bad things. At the same time, Tor and other privacy measures can fight identity theft, physical crimes like stalking, and so on. Tor aims to conceal its users' identities and their online activity from surveillance and traffic analysis by separating identification and routing. It is an implementation of onion routing, which encrypts and then randomly bounces communications through a network of relays run by volunteers around the globe. These onion routers employ encryption in a multi-layered manner (hence the onion metaphor) to ensure perfect forward secrecy between relays, thereby providing users with anonymity in a network location. That anonymity extends to the hosting of censorship-resistant content by Tor's anonymous onion service feature. Furthermore, by keeping some of the entry relays (bridge relays) secret, users can evade Internet censorship that relies upon blocking public Tor relays. Because the IP address of the sender and the recipient are not both in cleartext at any hop along the way, anyone eavesdropping at any point along the communication channel cannot directly identify both ends. Furthermore, to the recipient, it appears that the last Tor node (called the exit node), rather than the sender, is the originator of the communication.
Tor can also provide anonymity to websites and other servers. Servers configured to receive inbound connections by connecting to Tor are called onion services (formerly, hidden services). Rather than revealing a server's IP address (and thus its network location), an onion service is accessed through its onion address, usually via the Tor Browser or some other software designed to use Tor. The Tor network understands these addresses by looking up their corresponding public keys and introduction points from a distributed hash table within the network. It can route data to and from onion services, even those hosted behind firewalls or network address translators (NAT), while preserving the anonymity of both parties. Tor is necessary to access these onion services. Because the connection never leaves the Tor network, and is handled by the Tor application on both ends, the connection is always end-to-end encrypted. Onion services were first specified in 2003 and have been deployed on the Tor network since 2004. They are unlisted by design, and can only be discovered on the network if the onion address is already known, though a number of sites and services do catalog publicly known onion addresses. Popular sources of .onion links include Pastebin, Twitter, Reddit, other Internet forums, and tailored search engines. While onion services are often discussed in terms of websites, they can be used for any TCP service, and are commonly used for increased security or easier routing to non-web services, such as secure shell remote login, chat services such as IRC and XMPP, or file sharing. They have also become a popular means of establishing peer-to-peer connections in messaging and file sharing applications. Web-based onion services can be accessed from a standard web browser without client-side connection to the Tor network using services like Tor2web, which remove client anonymity. In 2023, the Tor Project unveiled a new defense mechanism to safeguard onion services against denial-of-service (DoS) attacks. With the release of Tor 0.4.8, this proof-of-work (PoW) defense promises to prioritize legitimate network traffic while deterring malicious attacks.
Figure 2: Sybil Attack Detection in Blockchain | What is Sybil attack | How is ... Tor makes no attempt to conceal the IP addresses of exit relays, or hide from a destination server the fact that a user is connecting via Tor. Operators of Internet sites therefore have the ability to prevent traffic from Tor exit nodes or to offer reduced functionality for Tor users. For example, Wikipedia generally forbids all editing when using Tor or when using an IP address also used by a Tor exit node, and the BBC blocks the IP addresses of all known Tor exit nodes from its iPlayer service. Apart from intentional restrictions of Tor traffic, Tor use can trigger defense mechanisms on websites intended to block traffic from IP addresses observed to generate malicious or abnormal traffic. Because traffic from all Tor users is shared by a comparatively small number of exit relays, tools can misidentify distinct sessions as originating from the same user, and attribute the actions of a malicious user to a non-malicious user, or observe an unusually large volume of traffic for one IP address. Conversely, a site may observe a single session connecting from different exit relays, with different Internet geolocations, and assume the connection is malicious, or trigger geo-blocking. When these defense mechanisms are triggered, it can result in the site blocking access, or presenting captchas to the user.
In July 2014, the Tor Project issued a security advisory for a "relay early traffic confirmation" attack, disclosing the discovery of a group of relays attempting to de-anonymize onion service users and operators. A set of onion service directory nodes (i.e., the Tor relays responsible for providing information about onion services) were found to be modifying traffic of requests. The modifications made it so the requesting client's guard relay, if controlled by the same adversary as the onion service directory node, could easily confirm that the traffic was from the same request. This would allow the adversary to simultaneously know the onion service involved in the request, and the IP address of the client requesting it (where the requesting client could be a visitor or owner of the onion service). The attacking nodes joined the network on 30 January, using a Sybil attack to comprise 6.4% of guard relay capacity, and were removed on 4 July. In addition to removing the attacking relays, the Tor application was patched to prevent the specific traffic modifications that made the attack possible. In November 2014, there was speculation in the aftermath of Operation Onymous, resulting in 17 arrests internationally, that a Tor weakness had been exploited. A representative of Europol was secretive about the method used, saying: "This is something we want to keep for ourselves. The way we do this, we can't share with the whole world, because we want to do it again and again and again." A BBC source cited a "technical breakthrough" that allowed tracking physical locations of servers, and the initial number of infiltrated sites led to the exploit speculation. A Tor Project representative downplayed this possibility, suggesting that execution of more traditional police work was more likely. In November 2015, court documents suggested a connection between the attack and arrests, and raised concerns about security research ethics. The documents revealed that the FBI obtained IP addresses of onion services and their visitors from a "university-based research institute", leading to arrests.
Reporting from Motherboard found that the timing and nature of the relay early traffic confirmation attack matched the description in the court documents. Multiple experts, including a senior researcher with the ICSI of UC Berkeley, Edward Felten of Princeton University, and the Tor Project agreed that the CERT Coordination Center of Carnegie Mellon University was the institute in question. Concerns raised included the role of an academic institution in policing, sensitive research involving non-consenting users, the non-targeted nature of the attack, and the lack of disclosure about the incident.
The main implementation of Tor is written primarily in C. Starting in 2020, the Tor Project began development of a full rewrite of the C Tor codebase in Rust. The project, named Arti, was publicly announced in July 2021. Standard: All website functions supported by Tor Browser, such as JavaScript, fonts, and multimedia, are enabled. Safer: Some features known to be common attack vectors are disabled. JavaScript is disabled on all websites not secured by TLS; some fonts and mathematical symbols are disabled; videos and audio are click-to-play. Safest: Only features necessary for static websites and basic services are enabled. JavaScript is disabled globally; some fonts, icons, math symbols, and images are disabled; videos and audio are click-to-play. To allow download from places where accessing the Tor Project URL may be risky or blocked, a GitHub repository is maintained with links for releases hosted in other domains.
Figure 3: Figure 1. Topology of Attack Model : Performance and Analysis of Sybil ... Tor has been praised for providing privacy and anonymity to vulnerable Internet users such as political activists fearing surveillance and arrest, ordinary web users seeking to circumvent censorship, and people who have been threatened with violence or abuse by stalkers. The U.S. National Security Agency (NSA) has called Tor "the king of high-secure, low-latency Internet anonymity", and BusinessWeek magazine has described it as "perhaps the most effective means of defeating the online surveillance efforts of intelligence agencies around the world". Other media have described Tor as "a sophisticated privacy tool", "easy to use" and "so secure that even the world's most sophisticated electronic spies haven't figured out how to crack it". Advocates for Tor say it supports freedom of expression, including in countries where the Internet is censored, by protecting the privacy and anonymity of users. The mathematical underpinnings of Tor lead it to be characterized as acting "like a piece of infrastructure, and governments naturally fall into paying for infrastructure they want to use". The project was originally developed on behalf of the U.S. intelligence community and continues to receive U.S. government funding, and has been criticized as "more resembl[ing] a spook project than a tool designed by a culture that values accountability or transparency". As of 2012, 80% of The Tor Project's $2M annual budget came from the United States government, with the U.S. State Department, the Broadcasting Board of Governors, and the National Science Foundation as major contributors, aiming "to aid democracy advocates in authoritarian states". Other public sources of funding include DARPA, the U.S. Naval Research Laboratory, and the Government of Sweden. Some have proposed that the government values Tor's commitment to free speech, and uses the darknet to gather intelligence. Tor also receives funding from NGOs including Human Rights Watch, and private sponsors including Reddit and Google. Dingledine said that the United States Department of Defense funds are more similar to a research grant than a procurement contract. Tor executive director Andrew Lewman said that even though it accepts funds from the U.S. federal government, the Tor service did not collaborate with the NSA to reveal identities of users. Critics say that Tor is not as secure as it claims, pointing to U.S. law enforcement's investigations and shutdowns of Tor-using sites such as web-hosting company Freedom Hosting and online marketplace Silk Road. In October 2013, after analyzing documents leaked by Edward Snowden, The Guardian reported that the NSA had repeatedly tried to crack Tor and had failed to break its core security, although it had had some success attacking the computers of individual Tor users. The Guardian also published a 2012 NSA classified slide deck, entitled "Tor Stinks", which said: "We will never be able to de-anonymize all Tor users all the time", but "with manual analysis we can de-anonymize a very small fraction of Tor users".
When Tor users are arrested, it is typically due to human error, not to the core technology being hacked or cracked. On 7 November 2014, for example, a joint operation by the FBI, ICE Homeland Security Investigations and European Law enforcement agencies led to 17 arrests and the seizure of 27 sites containing 400 pages. A late 2014 report by Der Spiegel using a new cache of Snowden leaks revealed, however, that as of 2012 the NSA deemed Tor on its own as a "major threat" to its mission, and when used in conjunction with other privacy tools such as OTR, Cspace, ZRTP, RedPhone, Tails, and TrueCrypt was ranked as "catastrophic," leading to a "near-total loss/lack of insight to target communications, presence..." "No adversary is truly global, but no adversary needs to be truly global," he says. "Eavesdropping on the entire Internet is a several-billion-dollar problem. Running a few computers to eavesdrop on a lot of traffic, a selective denial of service attack to drive traffic to your computers, that's like a tens-of-thousands-of-dollars problem." At the most basic level, an attacker who runs two poisoned Tor nodes—one entry, one exit—is able to analyse traffic and thereby identify the tiny, unlucky percentage of users whose circuit happened to cross both of those nodes. In 2016 the Tor network offers a total of around 7,000 relays, around 2,000 guard (entry) nodes and around 1,000 exit nodes. So the odds of such an event happening are one in two million (1⁄2000 × 1⁄1000), give or take." Tor does not provide protection against end-to-end timing attacks: if an attacker can watch the traffic coming out of the target computer, and also the traffic arriving at the target's chosen destination (e.g. a server hosting a .onion site), that attacker can use statistical analysis to discover that they are part of the same circuit. A similar attack has been used by German authorities to track down users related to Boystown.
Proof of personhood (PoP) is a means of resisting malicious attacks on peer-to-peer networks, particularly attacks that use multiple fake identities, otherwise known as a Sybil attack. Decentralized online platforms are particularly vulnerable to such attacks by their very nature, as notionally democratic and responsive to large voting blocks. In PoP, each unique human participant obtains one equal unit of voting power, and any associated rewards. The term is used in Cryptocurrency and Blockchains as a parallel to proof of work, proof of stake, and other consensus mechanisms which attempt to distribute voting power and rewards to participants proportionately to an investment of resources.
A technical guide for developers to build systems that identify clusters of wallets controlled by a single entity, using transaction graph analysis, behavior similarity, and integration with proof-of-personhood protocols. Sybil attacks threaten decentralized systems by allowing a single entity to control multiple fake identities. This guide explains how to identify and mitigate these attacks.
A Sybil attack occurs when a single malicious actor creates and controls a large number of pseudonymous identities within a peer-to-peer network. In blockchain and Web3 contexts, these fake identities can be used to manipulate governance votes , drain liquidity mining rewards , spam airdrop claims , or distort decentralized reputation systems . The core challenge is distinguishing between a genuine, diverse user base and a coordinated swarm of sybils controlled by one party. Unlike traditional systems with central authorities, decentralized networks must rely on cryptographic and economic signals for detection.
Implementing a detection system requires analyzing on-chain and off-chain data for patterns indicative of sybil behavior. Common technical signals include: transaction graph analysis to identify clusters of addresses funding each other, temporal analysis of address creation and activity bursts, and similarity detection in contract interactions or metadata. For example, hundreds of addresses created in a short timeframe, all interacting with the same DeFi pool to farm tokens, then withdrawing to a common destination, form a strong sybil cluster. Tools like Chainalysis and Nansen use these heuristics, but open-source libraries like tensorflow and networkx allow you to build custom detectors.
A practical detection pipeline involves three stages: data collection , feature extraction , and classification . First, collect transaction history and event logs for addresses in question via an RPC provider or indexer like The Graph. Next, extract features such as: first-seen timestamp, gas usage patterns, overlap in transaction counterparties, and token transfer motifs. Finally, apply a classification model—a simple rule-based engine (e.g., flagging addresses funded from the same source) or a machine learning model trained on known sybil datasets. The Ethereum Foundation's Anti-Sybil Blog Post provides a foundational framework for this analysis.
It's crucial to understand that sybil resistance is probabilistic, not absolute. Systems often employ a combination of techniques: proof-of-human protocols like Worldcoin, social graph analysis , and stake-weighted mechanisms. Your implementation should be iterative: flag suspected clusters, apply a scoring mechanism, and allow for manual review or appeals. Avoid false positives by setting conservative thresholds initially and analyzing the economic cost of an attack versus the reward. The goal is to increase the cost and complexity for an attacker to a prohibitive level, thereby securing your protocol's incentives and governance.
This guide outlines the technical prerequisites and initial setup required to build a system for identifying Sybil attacks in decentralized networks. A Sybil attack occurs when a single entity creates and controls multiple fake identities to gain disproportionate influence in a network. This undermines consensus mechanisms, governance voting, and airdrop distributions. To build a detection system, you need a foundational understanding of on-chain data analysis , graph theory , and machine learning concepts. Familiarity with a blockchain's data structure, such as Ethereum's account-based model or UTXOs, is essential for tracing transaction flows between suspected addresses.
Your development environment requires specific tools. For data ingestion, you'll need access to a blockchain node (like Geth or Erigon for Ethereum) or a reliable node provider API (such as Alchemy or Infura). For analysis, Python is the dominant language due to its data science libraries: use web3.py for on-chain interactions, pandas for data manipulation, and networkx or igraph for constructing and analyzing transaction graphs. Setting up a local database (PostgreSQL or TimescaleDB) is recommended for storing historical address and transaction data.
The first implementation step is data collection . You must extract all transactions for a target protocol or timeframe. Focus on capturing the from , to , value , and timestamp fields. For ERC-20 tokens and NFTs, you also need to parse event logs to trace asset movements. This raw data forms the transaction graph , where addresses are nodes and transfers are edges. Batch processing and efficient storage are critical here to handle datasets containing millions of transactions.
Next, you must define Sybil heuristics to flag suspicious clusters. Common indicators include: - High velocity funding : Multiple addresses funded from a single source in a short time. - Circular transactions : Tokens moving in loops between a cluster of addresses. - Common behavioral patterns : Identical transaction amounts, timings, or interaction with the same smart contracts. Implementing these as initial filters helps narrow down the address space for more complex analysis.
2. System Architecture & Core Working Principles For advanced detection, integrate graph analysis algorithms . Calculate metrics like clustering coefficient to find tightly-knit groups, or use community detection algorithms like Louvain to partition the graph. Addresses with high betweenness centrality might be coordination points. Combining these graph features with supervised machine learning (using labeled historical Sybil data) or unsupervised anomaly detection can significantly improve accuracy. Start with simple rules and iteratively add complexity.
Finally, establish a pipeline for continuous monitoring . Your system should periodically scan new blocks, update the transaction graph, and re-run detection models. Tools like Apache Airflow or Prefect can orchestrate this. Remember that Sybil attackers adapt, so your heuristics and models will require regular updates. Always validate findings with on-chain sleuthing before taking action, as false positives can harm legitimate users.
A practical guide to building a system that identifies and mitigates Sybil attacks by analyzing on-chain and off-chain identity signals. A Sybil attack occurs when a single entity creates and controls multiple fake identities to gain disproportionate influence in a decentralized system, such as a governance vote, airdrop, or liquidity mining program. The core methodology for detection involves creating a behavioral graph from blockchain data. This graph models interactions between addresses, treating them as nodes and their transactions (e.g., token transfers, contract calls) as edges. By analyzing this graph's structure—looking for clusters of addresses with highly similar transaction patterns, shared funding sources, or circular token flows—you can identify likely Sybil clusters that act in coordination rather than as independent actors.
The first technical step is data collection. You need to index and query historical blockchain data. For Ethereum and EVM chains, tools like The Graph subgraphs or direct node RPC calls via libraries like ethers.js or web3.py are essential. You'll collect transaction histories, token transfers (ERC-20/ERC-721), and interactions with specific smart contracts (e.g., DeFi pools, governance contracts). A simple query to get recent transfers for an address might look like using Etherscan's API: https://api.etherscan.io/api?module=account&action=tokentx&address=0x... . Store this data in a structured format (like a PostgreSQL or Neo4j database) for graph analysis.
Once you have the data, construct the graph and apply detection algorithms. Graph analysis libraries like NetworkX (Python) or Neo4j's Cypher queries are used to calculate key metrics. Look for: - High clustering coefficients : Dense interconnections within a suspected cluster. - Common funding sources : Many addresses receiving initial ETH from a single "seed" address. - Transaction temporal patterns : Bursts of identical actions performed in quick succession. A basic Python snippet using NetworkX might start a community detection analysis: import networkx as nx communities = list(nx.community.louvain_communities(G)) . This partitions the graph into groups of densely connected nodes.
To reduce false positives, you must incorporate off-chain and stake-based signals . These are orthogonal data points that are costly for an attacker to fake at scale. Key signals include: - Proof-of-Humanity : Integration with verification protocols like Worldcoin's Orb or BrightID. - Staked Assets : Requiring a meaningful, non-transferable stake (like locked tokens) that would be economically prohibitive to replicate across hundreds of fake identities. - Social Graph Analysis : Checking for established, non-sybil social connections on platforms like Twitter (via X API) or GitHub. Combining these with on-chain graph analysis creates a robust, multi-layered defense.
Finally, implement a scoring and flagging system. Assign each address or cluster a Sybil risk score based on the weighted sum of your detected signals. For example, a cluster with a common funding source (+50 points), identical transaction timing (+30), and no off-chain verification (+20) might score 100, triggering a flag. This system should run continuously, updating scores as new on-chain activity occurs. The output is a list of flagged addresses that can be used to filter participants in a governance snapshot or exclude them from a reward distribution, thereby preserving the integrity of the decentralized application.
A Sybil attack identification system combines on-chain data analysis with behavioral heuristics to detect and mitigate coordinated fake identities. These techniques are essential for securing airdrops, governance, and incentive programs. Map wallet interactions into a graph data structure where nodes are addresses and edges are transactions. Use algorithms like Louvain community detection to identify tightly-knit clusters of addresses that may represent a single entity. Key signals include: Create a profile for each address based on its on-chain behavior. This involves analyzing patterns that are difficult for Sybils to mimic consistently across hundreds of wallets.
Trace the origin of funds for a set of addresses. Sybil attacks often rely on a limited number of funding sources to distribute capital to many wallets. Implement sybil-resistance through cost by requiring users to stake assets or build a reputation over time. This makes large-scale attacks economically prohibitive.
Train a model to classify addresses as "organic" or "suspicious" using labeled on-chain data. This is a more advanced, proactive technique. Build a dashboard or alert system that continuously scans for Sybil attack patterns. This operationalizes the detection techniques.
A practical guide to building a system that identifies Sybil attack patterns by analyzing on-chain transaction graphs. A Sybil attack occurs when a single entity creates and controls a large number of pseudonymous identities to subvert a network's reputation or governance system. In blockchain contexts, this is often done to manipulate token airdrop eligibility, voting outcomes, or liquidity mining rewards. Transaction Graph Analysis (TGA) is a powerful method for detecting these coordinated clusters by modeling wallets as nodes and the transactions between them as edges . The core hypothesis is that Sybil clusters exhibit distinct graph patterns—such as high internal connectivity and low external connectivity—that differ from organic user behavior.
To implement a basic Sybil detection system, you first need to construct the graph. Using a node provider like Alchemy or QuickNode, you can fetch transaction history for a set of addresses. In Python, you can use networkx to build a directed graph. The following code snippet shows how to add edges based on transaction data: This creates a graph where each transfer is a connection. For more nuance, you can weight edges by transaction value, frequency, or timestamp.
Once the graph is built, you apply community detection algorithms to identify tightly-knit groups. The Louvain method is effective for finding high-modularity communities, which are candidates for Sybil clusters. Using the python-louvain package, you can partition the graph: This assigns each node a community ID. You then analyze these communities using graph metrics : - Internal/External Edge Ratio : Sybil clusters often have far more transactions within the group than with outside addresses. - Degree Centrality : Identifies hub addresses that connect to many others within the cluster. - Clustering Coefficient : Measures how interconnected a node's neighbors are, which is typically high in Sybil groups.
To reduce false positives, you must filter out legitimate high-connectivity patterns. Legitimate DeFi power users or exchange hot wallets may also show dense transaction graphs. Incorporate on-chain heuristics to refine detection: filter addresses interacting with known centralized exchange deposit contracts, exclude contracts themselves, and consider time-based patterns (e.g., all transactions in a Sybil cluster may occur in a short, coordinated burst). Combining TGA with machine learning classifiers trained on labeled data (e.g., past known airdrop farms) can significantly improve accuracy by learning subtle feature combinations.
For production systems, scalability is critical. Processing transaction data for millions of addresses requires efficient data pipelines. Consider using graph databases like Neo4j or Amazon Neptune for persistent storage and querying, and implement batch processing with Apache Spark for large-scale graph computations. Regularly update your detection models as Sybil attackers evolve their tactics, such as using mixers or cross-chain bridges to obscure links. Open-source tools like EigenPhi offer analytics that can benchmark your system's findings.
Implementing Transaction Graph Analysis provides a robust, data-driven foundation for Sybil defense. By moving beyond simple rule-based filters to analyze the underlying structure of relationships , developers and protocol teams can more effectively protect their ecosystems from manipulation. The key is to start with a simple model, validate it against known attack data, and iteratively add complexity and heuristics to balance detection precision with recall.
This guide explains how to build a system that identifies Sybil attacks by analyzing and clustering on-chain transaction behavior patterns. A Sybil attack occurs when a single entity creates and controls multiple fake identities to subvert a network's reputation or governance system. In blockchain, this often manifests as a cluster of addresses controlled by one user, artificially amplifying voting power or farming airdrops. Traditional identity verification is impossible on pseudonymous chains, so detection must rely on behavioral analysis . By examining transaction patterns, timing, and interaction graphs, we can identify addresses that act in suspiciously similar ways, flagging them as potential Sybil clusters.
3. Software Implementation, Frameworks & Protocols The core technical approach involves feature extraction from raw blockchain data. For each address, you compute a vector of behavioral features. Key features include: transaction frequency and time patterns, common counterparties or interaction clusters, gas price preferences, smart contract interaction signatures, and token transfer flow patterns. For example, two addresses that always interact with the same DeFi pools, use identical gas strategies, and transfer funds between each other in a circular pattern are likely related. These features are normalized and used to calculate a similarity score between address pairs.
With feature vectors prepared, you apply a clustering algorithm to group similar addresses. Hierarchical Density-Based Spatial Clustering of Applications with Noise (HDBSCAN) is often effective for this task, as it doesn't require pre-defining the number of clusters and can identify outliers. The algorithm uses the pairwise similarity scores to group addresses where members have high mutual similarity. The output is distinct clusters where intra-cluster behavioral similarity is high and inter-cluster similarity is low. Each cluster is a candidate Sybil group requiring further investigation.
Implementation requires querying data from a node or indexer like The Graph. Using ethers.js or viem, you can fetch transaction histories. A simplified code snippet for feature calculation might look like this: The complexity scales with the number of addresses analyzed, requiring efficient data pipelines for large-scale monitoring. After clustering, post-analysis is crucial to reduce false positives. Legitimate user groups (like exchange hot wallets or DAO treasuries) may also show similar behavior. Investigate cluster centroids: do they interact with known Sybil-related contracts? Is there a common funding source from a centralized exchange? Tools like EigenPhi for MEV analysis or Chainalysis for illicit finance patterns can provide additional risk signals. The final output is a risk-scored list of address clusters, which can be used to filter governance proposals, adjust airdrop allocations, or alert security teams.
This system should be part of a broader defense-in-depth strategy. Combine behavioral clustering with graph analysis (mapping the complete transaction network) and consensus-based reputation systems like Gitcoin Passport. Continuously retrain your model with newly labeled data (confirmed Sybil clusters from past incidents) to improve accuracy. By automating the detection of coordinated fake identities, projects can protect their token distribution and governance processes from manipulation, ensuring resources go to legitimate, diverse participants.
A comparison of open-source libraries and frameworks for building Sybil detection systems. A technical guide for developers on integrating proof-of-personhood and reputation data to detect and mitigate Sybil attacks in decentralized applications. A Sybil attack occurs when a single entity creates and controls multiple fake identities to subvert a system's reputation or governance. In decentralized networks, these attacks threaten token airdrops, voting mechanisms, and social graphs.
Implementing a Sybil identification system involves analyzing on-chain and off-chain data to detect coordinated behavior and assign a Sybil risk score to each address. This guide outlines a modular approach using existing protocols like Gitcoin Passport , Worldcoin , and on-chain analytics to build a robust defense. The first step is to collect identity attestations from proof-of-personhood (PoP) providers. Instead of building your own, integrate with established services via their APIs. For example, you can query Gitcoin Passport for a user's aggregated stamp score or verify a WorldID proof of uniqueness. Store these attestations, along with the user's primary Ethereum address, in your application's database. This creates a foundational layer of verified identity data that is difficult to spoof at scale.
Consider using a registry contract or EAS (Ethereum Attestation Service) schemas for on-chain, portable attestations. Next, implement on-chain behavior analysis to identify Sybil clusters. Analyze transaction patterns between addresses, such as: - Token transfer rings (circular payments) - Funding from common sources (e.g., centralized exchange withdrawal addresses) - Identical activity timing (batch interactions with contracts) Tools like the Chainalysis oracle or subgraphs from Dune Analytics can provide this data. Calculate metrics like the Jaccard similarity of transaction histories or use graph analysis libraries to detect tightly-knit address groups that likely belong to a single actor.
Combine the PoP attestations and on-chain analysis to calculate a composite Sybil Score . Assign weights to each signal based on your application's risk tolerance. For a high-stakes governance vote, you might weight WorldID verification heavily. For an airdrop, on-chain cluster analysis may be more relevant. A simple scoring function could be: Sybil Score = (PoP_Score * W1) + (OnChain_Trust_Score * W2) - (Cluster_Risk_Score * W3) . Scores can be updated periodically or in real-time via oracle updates or indexer listeners.
Integrate this scoring system into your application's logic. For a voting contract, you can use a gatekeeper pattern where only addresses with a Sybil score below a certain threshold can submit proposals or cast votes. For an airdrop, filter out high-risk addresses from the eligibility merkle tree. Make the scoring parameters and thresholds upgradeable via governance to adapt to new attack vectors. Transparency is key: consider publishing the scoring methodology and allowing users to query their own risk score and the evidence affecting it.
Continuously monitor and iterate on your system. Sybil attackers constantly evolve their tactics, using techniques like slow-farming reputation or simulated organic behavior . Participate in communities like EthResearch to stay updated on new PoP protocols like BrightID or Idena . Regularly audit your cluster detection algorithms for false positives that could penalize legitimate users in shared communities or payroll contracts. A well-designed Sybil system balances security with inclusivity, protecting your application's integrity without creating excessive barriers to entry.
Practical tools, protocols, and research papers you can use to design and implement a Sybil attack identification system in production Web3 environments. Gitcoin Passport is a composable Sybil resistance framework used by major airdrops and grant programs. It aggregates multiple identity signals into a single onchain score, allowing applications to define custom thresholds.
Gitcoin Passport is most effective when used as one layer in a defense-in-depth Sybil mitigation system. BrightID is a decentralized identity system that uses social graph verification to detect Sybil behavior. Instead of financial cost or biometrics, BrightID relies on the structure of human relationships. BrightID is useful when you want Sybil resistance without KYC or biometrics, especially for governance and quadratic voting.
Proof of Humanity (PoH) is an Ethereum-based registry of verified humans using video submission and peer dispute resolution. PoH is not suitable for high-throughput onboarding but works well as a gold-standard identity anchor in layered systems. SybilRank is a foundational academic algorithm for ranking nodes by likelihood of being Sybil based on graph trust propagation.
Reading the original paper helps you design detection systems that scale without relying on identity or capital costs. NetworkX is a Python library widely used to prototype graph-based Sybil detection techniques. 4. Practical Deployment, Analysis & Case Studies While NetworkX is not suitable for large-scale production graphs, it is ideal for research, feature engineering, and validating detection assumptions.
Common technical questions and solutions for developers implementing on-chain sybil detection systems. A sybil attack occurs when a single entity creates and controls a large number of pseudonymous identities (sybils) to subvert a network's reputation, governance, or incentive system. In Web3, this is a critical vulnerability for: The core challenge is distinguishing between unique humans and sybil-controlled wallets using only on-chain data, as blockchain addresses are inherently pseudonymous.
Detection relies on analyzing transaction graphs and behavioral patterns. Key methodologies include: High false positives often stem from overfitting heuristics to specific attack patterns, misclassifying legitimate user behaviors. Common causes and fixes: Set thresholds based on statistical analysis of known good actor sets, not theoretical models.
Prevention requires careful eligibility design and post-claim analysis. Follow this multi-layered approach: Reference : The Uniswap and Hop Protocol airdrops used combinations of these techniques effectively. Key Overlap : A sybil attack is often executed by bots . Therefore, a robust system should integrate both: Tools like Forta Network bots are specialized for real-time bot detection on transactions.
False negatives are sophisticated sybils that evade initial heuristics. Mitigate them with continuous system evolution. You have now explored the core components for building a Sybil attack identification system. This guide covered data collection, analysis techniques, and mitigation strategies. Implementing a Sybil defense is an ongoing process, not a one-time setup. Your system should continuously ingest on-chain and off-chain data—transaction history, governance votes, social graphs, and attestations from services like Ethereum Attestation Service (EAS) or Gitcoin Passport . This data forms the foundation for your analysis. Regularly update your data sources and parsers to adapt to new chain deployments and user behavior patterns.
The analysis layer is where you apply heuristics and models to identify suspicious clusters. Start with simple rules: flagging addresses with near-identical transaction timing , common funding sources, or circular token transfers. For more advanced detection, consider deploying machine learning models like graph neural networks (GNNs) to identify tightly-knit subgraphs that human heuristics might miss. Tools like The Graph for indexing or Covalent for unified data can accelerate this phase.
Your mitigation strategy must be proportional and transparent. Common actions include: - Down-weighting votes in governance. - Applying rate-limits to interactions. - Requiring stricter identity verification for high-value actions. Always provide users with a clear appeal process. Smart contracts for governance or airdrops should integrate with your Sybil detection module via oracles or off-chain checks to enforce these rules transparently.
For next steps, consider contributing to or auditing open-source Sybil detection frameworks like BrightID 's analysis tools or Gitcoin Passport 's scorer. Test your system against known Sybil clusters from past airdrops or governance attacks. Finally, document your methodology and publish your findings (where possible) to contribute to the collective security of the Web3 ecosystem. Continuous iteration is key as attackers constantly evolve their tactics.
Production systems our engineers design, build and run, scoped to what you are working on. Smart contracts, DeFi, wallets, tokenization and infrastructure across the ecosystems teams choose today, plus other networks on request. Imagine you are running a community vote to decide where the next local festival should be held. Suddenly, one person shows up with fifty different costumes and fifty different names, casting fifty votes instead of one. The result is rigged, not by force, but by deception. In the world of Sybil attacks are a type of network attack where a single entity creates multiple fake identities (nodes) to gain disproportionate influence over a decentralized system , named after the dissociative identity disorder case study from the 2002 research paper 'The Sybil Attack' by Brian Neil Levine and Clay Shields. This isn't just a theoretical nightmare; it’s a daily threat to blockchain networks that rely on trustless consensus. If you are building or securing a blockchain application, understanding how to detect these phantom nodes is no longer optional-it is survival.
The core problem with blockchain networks are decentralized digital ledgers that use distributed consensus mechanisms to validate transactions without a central authority . is their pseudoanonymous nature. Unlike your bank account, which requires a passport and a signature, joining a peer-to-peer network often only requires downloading software. Attackers exploit this openness to spawn hundreds of nodes from a single server rack. These Sybil nodes are malicious entities controlled by a single attacker that mimic legitimate network participants to manipulate consensus, voting, or resource allocation . can then manipulate consensus mechanisms, drain governance treasuries, or even launch 51% attacks. The Ethereum Classic network learned this the hard way in January 2019 when a Sybil attack paved the way for a successful chain reorganization, stealing millions in value. Detecting these nodes before they cause damage is the primary job of modern blockchain security.
You might think that firewalls and IP bans would stop this. They don’t. The beauty of a Sybil attack is its simplicity and low barrier to entry. Creating a new node in many networks costs nothing more than electricity and bandwidth. If you run a DeFi protocol offering an airdrop, an attacker doesn’t need to hack your code; they just need to create 10,000 wallets, interact minimally with your contract, and claim rewards meant for real users. Formo’s 2023 report documented 37 Sybil attacks on DeFi protocols in 2022 alone, with each incident costing an average of $2.8 million. The damage isn't always financial theft; sometimes it's the erosion of trust. When users see bots dominating governance votes, they lose faith in the decentralization promise.
The challenge lies in the definition of 'identity.' In traditional web systems, we use email addresses or phone numbers. In blockchain, identity is cryptographic-a public key. Anyone can generate a new key pair in seconds. Therefore, detecting a Sybil node isn't about checking if a user exists; it's about determining if multiple keys belong to the same physical actor. This requires moving beyond simple authentication into behavioral analysis and economic incentives.
There is no silver bullet. Dr. Ari Juels, former Chief Scientist at Chainlink, noted that no purely technical solution eliminates Sybil attacks entirely. Instead, effective defense relies on a multi-layered approach. Here are the five primary methodologies currently used in the industry: Note the trade-off here. Bitcoin’s PoW is resistant because attacking it costs millions in hardware and electricity. But if you are running a lightweight IoT blockchain, you can’t demand 51% of global hashrate. That’s why context matters. Monero, which prioritizes anonymity, suffered a Sybil attack in 2021 where attackers controlled 42% of network nodes because its privacy features made it difficult to distinguish unique actors.
If you are a developer tasked with protecting your DAO or DeFi protocol, where do you start? According to Consensys Academy, implementing a basic detection system takes 3-5 weeks. Advanced systems require 8-12 weeks. Here is a realistic roadmap: 5. Performance Evaluation & Extended Technical Observations A common pitfall is relying solely on one method. A robust system combines economic stakes (if applicable), behavioral heuristics, and social graph analysis. For instance, if a node has a high reputation score but suddenly connects to a known Sybil cluster, flag it for manual review rather than immediate ban.
The landscape is shifting. The EU’s MiCA regulations, effective June 2024, now mandate robust Sybil prevention for networks operating in Europe. By 2026, the SEC’s proposed framework will make these capabilities standard. But regulation is only part of the driver; technology is evolving faster. Zero-knowledge proofs (ZKPs) are emerging as a game-changer. zkSync reported a 99.2% accuracy rate in identifying Sybil wallets while preserving user privacy in their October 2023 testnet. This allows users to prove they are unique humans without revealing their identity. Similarly, Worldcoin’s Orb biometric verification aims to establish a "one-person-one-identity" system, having verified 2.3 million unique users by August 2023. While controversial due to privacy concerns, these technologies address the root cause: the ability to easily clone digital identities.
Vitalik Buterin highlighted in his January 2023 blog post that Proof-of-Stake fundamentally changes the landscape by making identity acquisition expensive rather than merely difficult. As networks move toward sub-second finality, like Avalanche’s metastable consensus which detects clusters in 800 milliseconds, the window for Sybil exploitation shrinks. The future belongs to systems that combine economic disincentives with cryptographic proof of uniqueness.
A Sybil attack occurs when a single malicious actor creates multiple fake identities (nodes or wallets) in a decentralized network to gain disproportionate influence. Think of it as one person buying fifty tickets to a raffle to increase their chances of winning, except in blockchain, this can allow them to control voting outcomes or disrupt consensus. Proof-of-Stake (PoS) prevents Sybil attacks by requiring participants to lock up a significant amount of cryptocurrency as collateral. For example, Ethereum requires 32 ETH per validator. Since creating thousands of validators would require billions of dollars in capital, it becomes economically irrational for an attacker to attempt controlling the network through sheer volume of nodes.
Yes, but they are extremely expensive. Bitcoin uses Proof-of-Work, so a Sybil attack would require controlling 51% of the network's computational power. As of July 2023, this would cost approximately $1.4 million per hour in energy and hardware. While technically possible, the economic barrier makes it highly unlikely compared to smaller, less secure chains. Popular tools include SybilRank for graph-based analysis, Chainalysis for enterprise-level tracking, and specialized libraries like Formo for DeFi airdrop protection. For developers building custom solutions, integrating behavioral analysis APIs and zero-knowledge proof verifiers like those from zkSync provides advanced detection capabilities.
It can, depending on the method. Identity verification (KYC) requires personal data, which raises privacy concerns. However, newer methods like Zero-Knowledge Proofs (ZKPs) allow users to prove they are unique individuals without revealing their actual identity, achieving high detection accuracy (up to 99.2%) while maintaining privacy compliance. Implementation costs vary. Basic behavioral analysis might take 3-5 weeks of developer time. Advanced systems with AI integration and ZKP verification can take 8-12 weeks. Enterprise solutions from firms like Chainalysis or CertiK involve annual licensing fees, often ranging from tens to hundreds of thousands of dollars, depending on network size and transaction volume.
Stop pretending this is a 'security' issue when it's really just an economic one. You don't need fancy AI or ZKPs to stop Sybils, you just need to make it expensive enough that no sane person would do it. The whole point of blockchain is that money talks and bullshit walks. If you have to rely on KYC or social graphs, you've already failed as a decentralized system because you're reintroducing central points of failure. It's not about detection, it's about incentives. Fix the economics and the bots go away.
I actually found this incredibly insightful! It’s so easy to get lost in the code and forget that behind every node is a human decision-or a lack thereof. The part about reputation systems really resonated with me because trust is such a fragile thing online. We spend so much time building walls when we could be building bridges of verified identity. I hope more projects look into those ZKP solutions; they sound like the perfect balance of safety and privacy. It gives me so much hope for the future of decentralized governance! I The Ethereum Classic hack was a disaster but honestly? Good riddance to weak chains. If your consensus mechanism can be broken by a guy with a server rack and a grudge, you deserve to lose your money. Bitcoin doesn't have this problem because it costs millions to attack. Everything else is just gambling with extra steps. Stop crying about decentralization if you're running on PoS with low stakes. It's not a bug, it's a feature of being cheap.
This entire guide is propaganda designed to push centralized control under the guise of security. Who benefits from KYC? Not the user. The banks and the governments want you to verify your identity so they can track your transactions. They call it 'Sybil detection' but it is really just surveillance capitalism wrapped in crypto jargon. The real threat isn't fake nodes; it's the erosion of anonymity. Once you accept that you must prove you are human to participate, you have surrendered your freedom. The deep state wants you to use Worldcoin. Don't fall for it.
i mean... its kinda complicated lol. i tried setting up a neo4j graph database last week and my brain just melted. like, who has time for this stuff? maybe just stick to bitcoin tbh. less headache. You people are so naive thinking tech can solve human greed I. Look at Formo data again. 37 attacks in ONE YEAR. Your 'detection' tools are always three steps behind. Every time you patch a hole, they find a new way. It is a rat race. And guess what? The rats always win because they have infinite resources and zero morals. You think your little heuristic filters will save you? Cute. Keep dreaming while your treasury gets drained. II Average dev trying to copy paste this garbage. Real engineers know that behavioral analysis adds latency that kills UX. You talk about 8-12% latency like its nothing. In high freq trading that is death. Also your table is wrong. Monero isn't vulnerable to Sybil in the way you describe, it's about mining pools. Show some respect for actual cryptography before posting this mediocre summary. Typical US tech bro ignorance. I The concept of identity is fluid, yet we try to pin it down with rigid algorithms. Is a Sybil attack truly malicious if the network accepts it? Or is the network flawed for accepting it? We create these digital avatars and then fear them when they multiply.
Perhaps the solution lies not in restriction, but in acceptance of multiplicity. But then again, I am just a philosopher watching the machine eat itself. I Let's break this down for everyone who feels overwhelmed. First, start small. Don't try to build the perfect detector overnight. Focus on one pillar-maybe economic staking if you can, or simple behavioral flags. Remember, progress over perfection. If you are building a DAO, talk to your community about what kind of verification they are comfortable with. Collaboration is key here. You don't have to do it alone. There are great open source tools out there. Just take that first step! You got this! II Actually, none of this matters if you aren't using enterprise grade solutions. Free tools are for hobbyists. If you are handling real value, you pay for Chainalysis or CertiK. Stop trying to DIY your security. It's embarrassing.
This guide details architectural patterns and cryptographic techniques for building Sybil-resistant decentralized communication protocols, covering PoW, PoS, social trust, and attestations. Sybil attacks, where a single entity creates many fake identities to subvert a network, are a fundamental threat to decentralized systems. This guide explains how to architect protocols with built-in resistance.
A Sybil attack occurs when a single adversary creates and controls a large number of pseudonymous identities—Sybil nodes—to gain disproportionate influence over a network. In decentralized systems like blockchains, DAOs, or decentralized storage networks, this can undermine governance, consensus, and resource allocation. The core challenge is establishing costly identity in a permissionless environment where creating a new public key is essentially free. Without Sybil resistance, mechanisms like one-token-one-vote or one-IP-one-vote are easily manipulated.
Effective Sybil resistance imposes a cost on identity creation that is asymmetric for attackers. The goal is to make the cost of creating enough Sybil identities to sway the system economically prohibitive. Common mechanisms include Proof of Work (costly computation), Proof of Stake (costly capital), and Proof of Personhood (costly verification of human uniqueness). The choice depends on the protocol's threat model and desired properties; a DeFi governance system may use token-weighted voting, while a decentralized social network might explore biometric verification.
When architecting a protocol, integrate Sybil resistance at the incentive layer . For example, a peer-to-peer network might use a stake-weighted bandwidth allocation system, where nodes bond tokens to earn the right to serve data. An attacker would need to lock substantial capital to spam the network with malicious nodes. Similarly, airdrop or grant distribution can use retroactive public goods funding models that rely on existing, reputable community members to nominate recipients, creating a web-of-trust barrier to Sybils.
Implementation often involves on-chain verification of the resistance mechanism. For a staking-based system, a smart contract can manage deposits and slashing. Consider this simplified Solidity snippet for a stake-weighted voting contract: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Sybil%20attack • https://en.wikipedia.org/wiki/Tor%20%28network%29 • https://en.wikipedia.org/wiki/Proof%20of%20personhood • https://chainscorelabs.com/guides/ai-llms-and-machine-learning-in-web3/ai-for-on-chain-data-analysis/how-to-implement-a- sybil-attack-identification-system • https://psrseed.com/how-to-detect-sybil-nodes-in-blockchain-a-practical-guide-for-developers • https://chainscorelabs.com/guides/decentralized-social-media-and-communication/decentralized-communication-protocols/h ow-to-architect-a-protocol-resistant-to-sybil-attacks
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
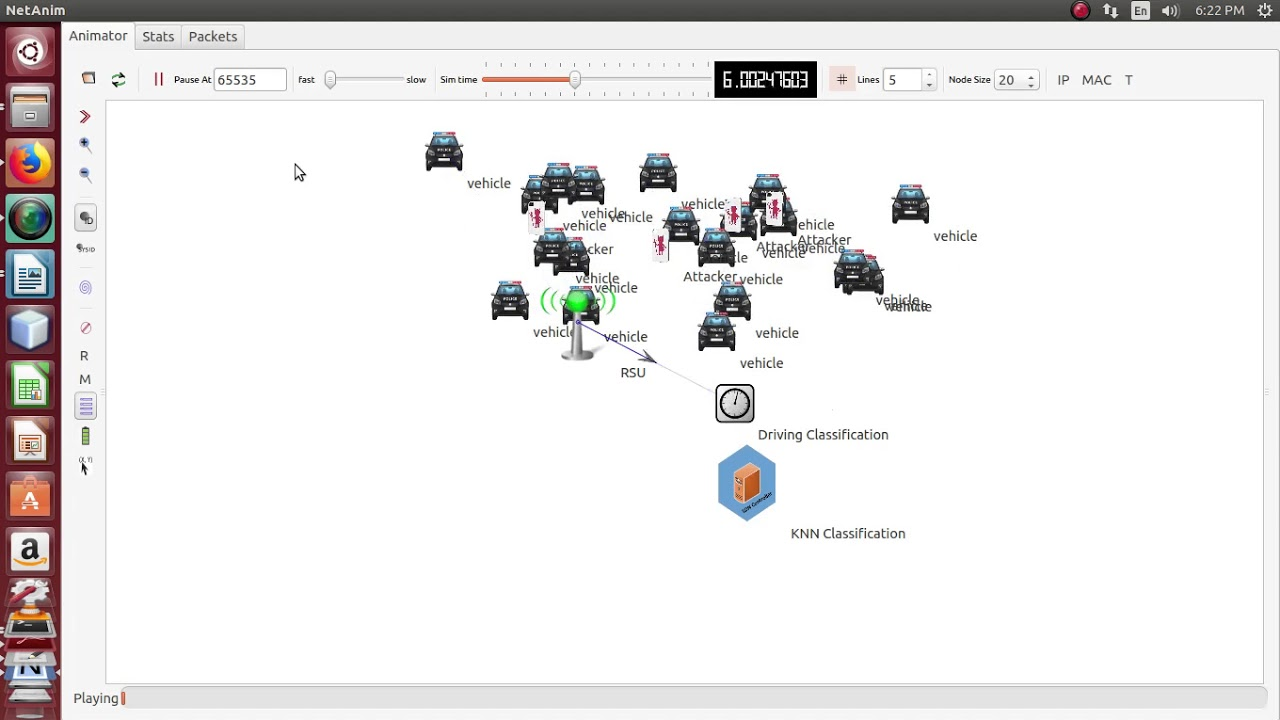
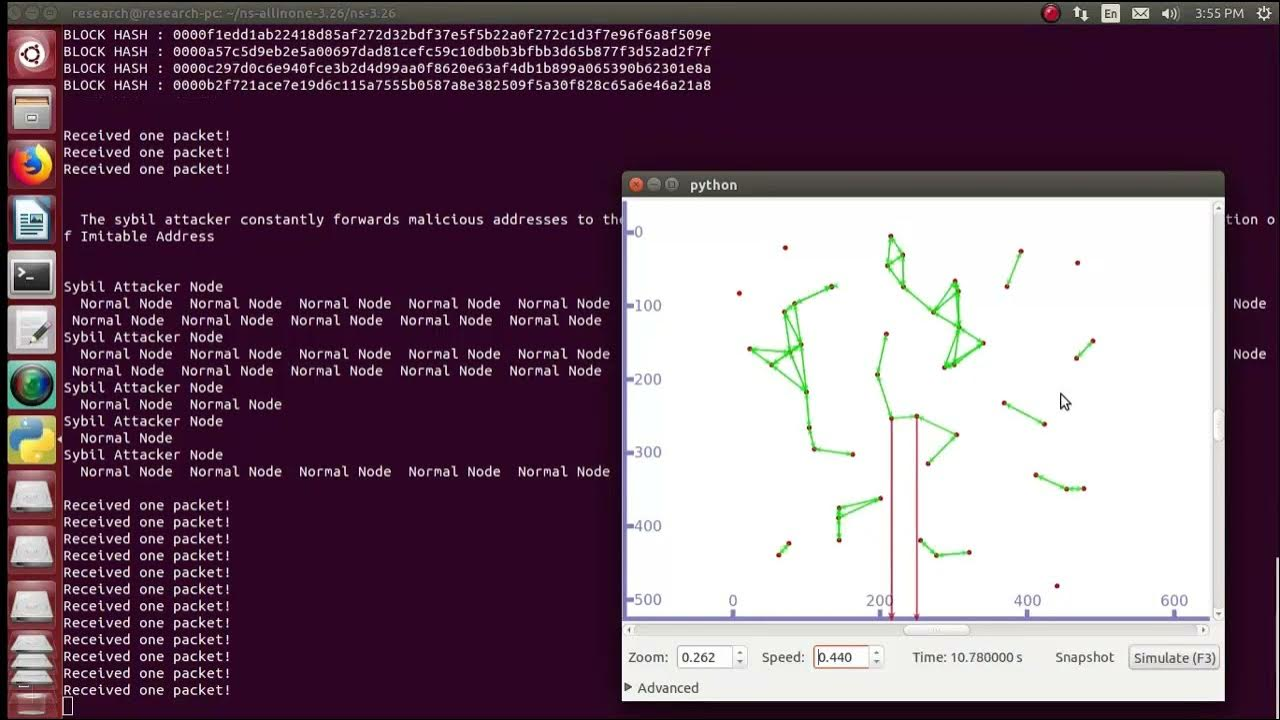
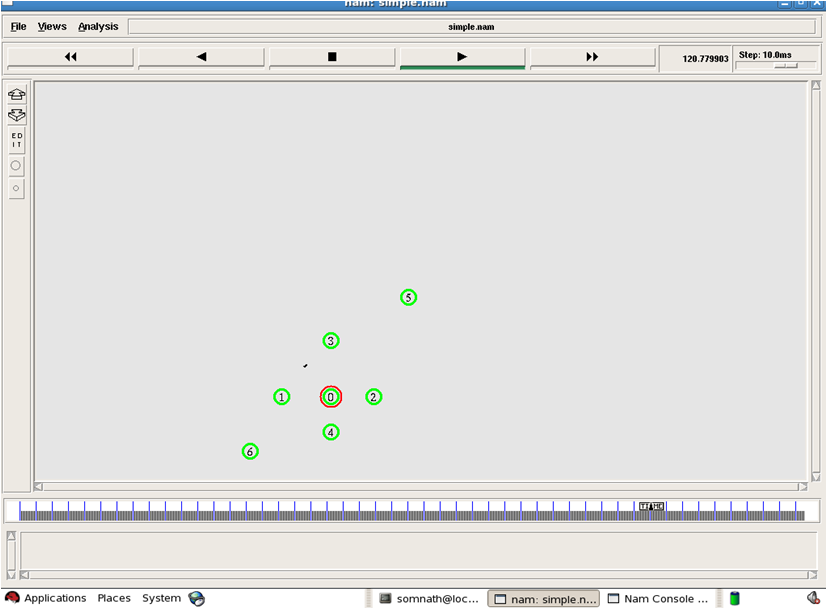
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Sybil Attack Detection In Decentralized Peer Networks.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |