Complete Technical Paper Content — Terraform Misconfiguration Detection Tool In Python
Overview & System Context
Terraform Misconfiguration Detection Tool In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8594 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This repository contains the hands-on technical component of a master’s research project focused on evaluating the effectiveness and limitations of automated cloud security controls in AWS environments.
The project examines how Infrastructure as Code (Terraform) and Python-based automation can be used to detect common cloud misconfigurations, while also highlighting where automation alone is insufficient. The emphasis is on evidence-based analysis rather than assumptions about secure-by-default cloud configurations. This repository represents the practical implementation that supports a graduate-level research paper.
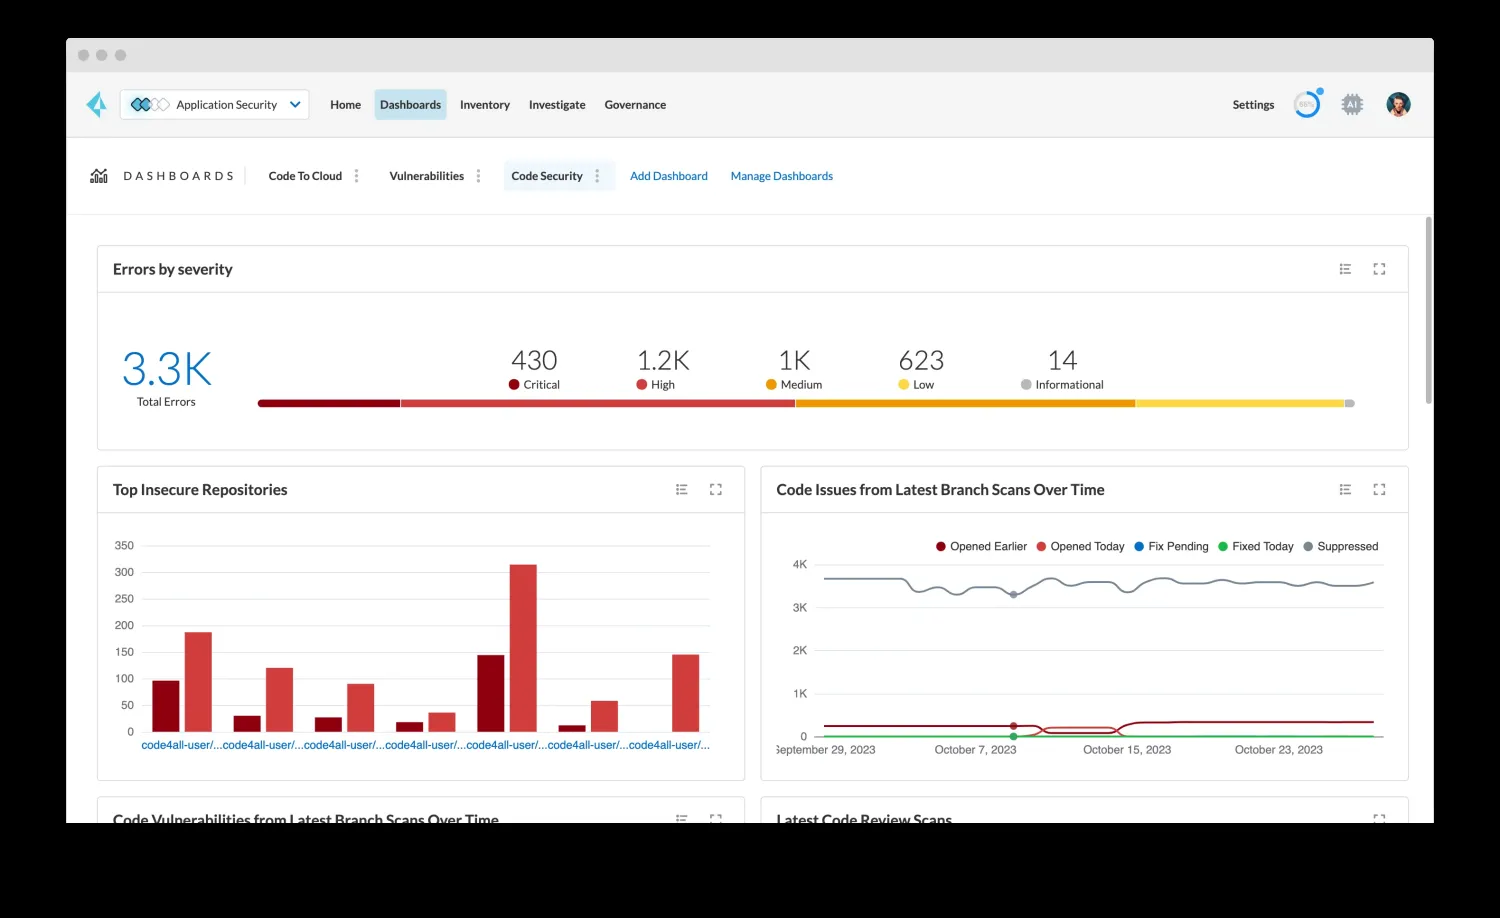
All misconfigurations are intentional, isolated, and created solely for research and learning purposes. Figure 1: Best IaC Security Tools for Terraform (2026) | AppSec Santa Results demonstrate that automation reliably detects common misconfigurations, while reinforcing that context and architectural intent still require human judgment.
This repository supports a master’s research paper examining cloud misconfiguration risk, automation bias in security tooling, and the role of Infrastructure as Code in cloud security governance. Automation improves visibility and consistency, but it does not eliminate cloud security risk. Automated controls must be evaluated using evidence to understand both their strengths and their limitations.
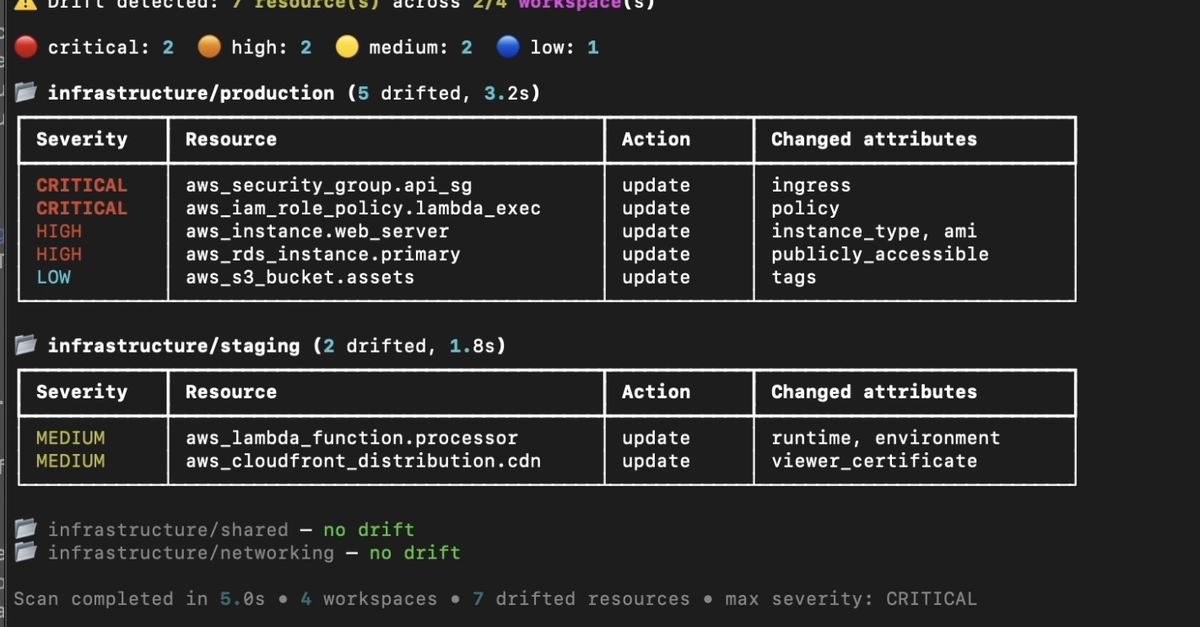
Terraform + Python (Boto3) project that provisions insecure AWS resources and programmatically detects cloud misconfigurations. Figure 2: I Built tfdrift Free Terraform Drift Detection With Severity Alerts ... A CLI tool that scans Terraform .tf files and flags security risks before they reach production, built after reviewing the infrastructure of 45+ cloud applications and seeing the same misconfigurations surface repeatedly.
Terraform is how most teams manage AWS infrastructure. It's fast and repeatable, but that speed cuts both ways: a single misconfigured resource block, such as an open SSH port, a public S3 bucket, or a wildcard IAM policy, gets deployed just as easily as a correct one. Most tools catch these issues after deployment, during a cloud security audit or an incident. This tool catches them at the source, before terraform apply is ever run.
Point it at a .tf file or a project folder. It finds every resource block, runs it through a trained ML model, and tells you what's risky and why. Figure 3: Open-source Tools for detecting drift in Terraform-managed ... 1. Parse: the tool reads the .tf file and splits it into individual resource blocks using brace-balanced tokenization.
2. Extract: each block is checked against 17 security indicators across common AWS resource types (open CIDR ranges, exposed ports, unencrypted storage, hardcoded secrets, and more). Each indicator is a 1 or 0. The block becomes a row of 17 numbers. 3. Classify: that row goes into a trained Random Forest model, which outputs Low, Medium, or High risk along with a per-class confidence score.
4. Explain: whichever indicators fired are translated into a plain-English reason, so engineers know exactly what to fix. Three classifiers were trained and compared on a balanced dataset of 300 labeled Terraform snippets: Random Forest is the default, providing per-class confidence scores and never misclassifying a High-risk resource as Low. Logistic Regression achieves the highest raw accuracy, which makes sense: the binary feature space is largely linearly separable.
This launches an interactive menu where you can choose to scan a file, scan a directory, train the models, or run demo predictions. The Cloud Development Kit for Terraform is deprecated as of December 10, 2025. HashiCorp no longer supports or maintains the Cloud Development Kit for Terraform.
A video tutorial on Terraform Misconfiguration scans can be found on the Aqua Open Source YouTube account. A note to tfsec users We have been consolidating all of our scanning-related efforts in one place, and that is Trivy. You can read more on the decision in the tfsec discussions. Terraform configuration scanning is available as part of the trivy config command. This command scans all configuration files for misconfiguration issues. You can find the details within misconfiguration scans in the Trivy documentation.
Command structure: trivy config
Git clone the tutorial and cd into the directory: git clone git@github.com:Cloud-Native-Security/trivy-demo.git cd bad_iac/terraform In this case, the folder only contains Terraform configuration files. However, you could scan a directory that contains several different configurations e.g. Kubernetes YAML manifests, Dockerfile, and Terraform. Trivy will then detect the different configuration files and apply the right rules automatically.
The --output flag specifies the file location in which the scan result should be saved: If you are presented with lots and lots of misconfiguration across different files, you might want to filter or the misconfiguration with the highest severity: You can pass terraform values to Trivy to override default values found in the Terraform HCL code. More information are provided in the documentation.
We have lots of examples in the documentation on how you can write and pass custom Rego checks into terraform misconfiguration scans. The trivy config command does not perform secret and vulnerability checks out of the box. However, you can specify as part of your trivy fs scan that you would like to scan your Terraform files for exposed secrets and misconfiguration through the following flags: The trivy config command is a sub-command of the trivy fs command. You can learn more about this command in the documentation.
Instead of scanning your different Terraform resources individually, you could also scan your Terraform Plan file before it is deployed for misconfiguration. This will give you insights into any misconfiguration of your resources as they would become deployed. Here is the link to the documentation. Similar to tfsec, Trivy can be used either on local developer machines or integrated into your CI/CD pipeline. There are several steps available for different pipelines, including GitHub Actions, Circle CI, GitLab, Travis and more in the tutorials section of the documentation: https://trivy.dev/docs/latest/tutorials/integrations/ A video tutorial on Terraform Misconfiguration scans can be found on the Aqua Open Source YouTube account.
A note to tfsec users We have been consolidating all of our scanning-related efforts in one place, and that is Trivy. You can read more on the decision in the tfsec discussions. Terraform configuration scanning is available as part of the trivy config command. This command scans all configuration files for misconfiguration issues. You can find the details within misconfiguration scans in the Trivy documentation.
Command structure: trivy config
Install Trivy on your local machines. The documentation provides several different installation options. This tutorial will use this example Terraform tutorial for terraform misconfiguration scanning with Trivy. Git clone the tutorial and cd into the directory: git clone git@github.com:Cloud-Native-Security/trivy-demo.git cd bad_iac/terraform In this case, the folder only containes Terraform configuration files. However, you could scan a directory that contains several different configurations e.g. Kubernetes YAML manifests, Dockerfile, and Terraform. Trivy will then detect the different configuration files and apply the right rules automatically.
The --output flag specifies the file location in which the scan result should be saved: If you are presented with lots and lots of misconfiguration across different files, you might want to filter or the misconfiguration with the highest severity: You can pass terraform values to Trivy to override default values found in the Terraform HCL code. More information are provided in the documentation.
We have lots of examples in the documentation on how you can write and pass custom Rego checks into terraform misconfiguration scans. The trivy config command does not perform secrete and vulnerability checks out of the box. However, you can specify as part of your trivy fs scan that you would like to scan you terraform files for exposed secrets and misconfiguraction through the following flags: The trivy config command is a sub-command of the trivy fs command. You can learn more about this command in the documentation.
Instead of scanning your different Terraform resources individually, you could also scan your Terraform Plan file before it is deployed for misconfiguration. This will give you insights into any misconfiguration of your resources as they would become deployed. Here is the link to the documentation. Similar to tfsec, Trivy can be used either on local developer machines or integrated into your CI/CD pipeline. There are several steps available for different pipelines, including GitHub Actions, Circle CI, GitLab, Travis and more in the tutorials section of the documentation: https://aquasecurity.github.io/trivy/latest/tutorials/integrations/ In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Terraform code that provisions an S3 bucket with public access, an RDS instance without encryption, or a security group with 0.0.0.0/0 ingress on all ports will create exactly that infrastructure when applied. Security scanning in CI/CD catches these before apply runs. This guide covers how to set up tfsec and Checkov in a GitHub Actions pipeline, the top misconfiguration patterns each tool catches, and how to handle suppression for legitimate exceptions without creating a blanket ignore policy.
This shows only High and Critical findings, giving you the most impactful starting point without overwhelming the team with hundreds of Medium and Low findings at once. These resource types produce the highest-frequency high-severity findings across AWS, Azure, and GCP: Set soft_fail: false once the existing finding backlog is resolved. With soft_fail: false , any High or Critical finding blocks the PR merge. Upload SARIF to the GitHub Security tab so findings are tracked as code scanning alerts alongside SAST results.
Some findings are intentional. A public S3 bucket hosting a static website, a security group allowing 443 from the world for a load balancer, or a non-encrypted bucket for cost optimization in a staging environment. Suppression must be documented and scoped. For custom organization rules that the public scanners do not cover (e.g., required tags on all resources, specific naming conventions), tfsec supports custom rule YAML files placed in a .tfsec/ directory in the repo.
Trivy is a broader security scanner that covers IaC, container images, and secrets in a single tool. For Terraform, Trivy replicates most tfsec and Checkov checks and adds secrets detection (hardcoded API keys, passwords, AWS access keys in Terraform variable files). Trivy is particularly useful for detecting hardcoded secrets in .tfvars files and in resource arguments that should reference variable inputs: For secrets in Terraform state files (a separate problem): Terraform state can contain sensitive values in plaintext. Always use remote state with encryption at rest (S3 + SSE, Terraform Cloud, or Azure Backend with customer-managed keys). Add state file locations to your .gitignore and run Trivy on your repository to ensure no .tfstate files are committed.
Every terraform apply without a prior security scan is a production deployment with no code review for the security properties that matter most. Add tfsec or Checkov to your CI/CD pipeline at the PR level, upload results as SARIF to the Security tab, set a policy that High and Critical findings block merge, and require ticket references for every suppression. The scanning takes 30-60 seconds per run and prevents the kind of S3 bucket public access exposure that shows up in breach post-mortems.
They overlap significantly on core rule coverage. tfsec is Terraform-specific and fast, with good HCL parsing. Checkov covers more frameworks (Terraform, Kubernetes, Dockerfiles, Ansible) and has a larger rule library including compliance framework mappings (CIS, SOC 2, PCI). Trivy adds secrets detection on top of misconfiguration scanning. Many teams run two tools in parallel: tfsec for fast PR feedback and Checkov for compliance-mapped reporting. Running all three is not unreasonable in high-compliance environments and takes under 2 minutes in CI.
Can IaC scanning detect runtime misconfigurations that are applied outside of Terraform? No. IaC scanners analyze the Terraform code; they cannot see what exists in cloud accounts that was deployed manually, through another tool, or that drifted from the Terraform state after apply. For runtime misconfiguration detection, use a CSPM tool (Defender for Cloud, Wiz, Prisma Cloud, AWS Security Hub). IaC scanning and CSPM are complementary: IaC scanning prevents new misconfigurations from being deployed; CSPM detects existing misconfigurations regardless of how they were created.
When tfsec or Checkov scans a root module that calls a public registry module, findings in the module code are typically surfaced with the module source path. You cannot modify the module source, but you can: (1) pass variables to the module that enable secure configuration, (2) fork the module and apply fixes in your fork, (3) suppress the finding with a documented justification, or (4) switch to a different module with better security defaults. Check the module's GitHub issues first -- many popular modules have accepted PRs for security fixes that are not yet in a released version.
Start with report-only mode (soft_fail: true) for the first 4-6 weeks to let the team understand the finding volume and resolve the existing backlog. Then switch Critical findings to blocking, then High findings. Medium and Low findings should remain advisory for most teams. The goal is to make the path of least resistance a secure one: if every PR fails due to 50 findings, engineers will configure blanket suppressions to unblock themselves, defeating the purpose.
Use inline suppression comments (tfsec, Checkov, and Trivy all support suppression directives with a reason field) for one-time exceptions. Enforce a policy that every suppression must include a reason string and a Jira or issue tracker reference. In your CI pipeline, run a script that counts active suppressions per repository and outputs a suppression inventory as a build artifact. Route suppressions beyond a defined threshold for mandatory security review. Set suppression expiry by convention: if the reason references a ticket, the ticket closure should trigger suppression removal. Review the suppression inventory quarterly as part of your IaC security posture assessment.
Terraform state files contain plaintext values for all resource attributes, including secrets, passwords, and private keys that were passed to resources during provisioning. Never store state locally on developer machines or in version control. Use remote state backends with encryption at rest and access controls: Terraform Cloud, AWS S3 with server-side encryption and a DynamoDB lock table, Azure Blob Storage with encryption, or GCS with a customer-managed key. Restrict state file access via IAM so only the CI/CD role and designated operators can read or write state. Enable state locking to prevent concurrent applies. For particularly sensitive state (containing database credentials or certificate private keys), consider using external secret references rather than passing secrets directly to resource arguments.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. A misconfigured aws_s3_bucket resource or an 0.0.0.0/0 security group rule is cheap to fix in a pull request and expensive to fix once terraform apply has already created the resource — at that point it's a live incident, not a diff. That's the core argument for scanning Terraform before deployment rather than after. The tooling landscape shifted meaningfully in February 2023, when Aqua Security folded tfsec into Trivy: the standalone tfsec repository now only accepts dependency bumps, and all new Terraform misconfiguration rules ship through trivy config , which also covers CloudFormation, Kubernetes manifests, Helm charts, and Dockerfiles under one scanner. Legacy tfsec rule IDs still map onto Trivy's AVD (Aqua Vulnerability Database) rule IDs, so existing CI configs don't break outright, but teams still pinning tfsec as a standalone binary are running a project that's effectively frozen. Meanwhile HashiCorp's own Sentinel policy engine, built into Terraform Cloud and Enterprise's Team & Governance tier, runs after terraform plan and before apply , with direct access to the plan, state, and config data — a different enforcement point than a pre-commit scanner. This post walks through where each layer fits and how to chain them into one pipeline.
A Terraform misconfiguration is a resource definition that's syntactically valid HCL but creates an insecure or non-compliant cloud resource — the plan succeeds, apply succeeds, and the vulnerability ships. The recurring categories across every major scanner's rule set are the same: security groups or NACLs open to 0.0.0.0/0 on ports like 22 or 3389, storage resources (S3 buckets, Azure Storage accounts, GCS buckets) provisioned without encryption-at-rest or with public-read ACLs, IAM policies using wildcard Action: "*" or Resource: "*" statements, logging and monitoring left disabled on resources like CloudTrail or VPC flow logs, and databases provisioned without encryption or with public endpoints exposed. None of these trip a syntax error or a terraform validate failure — HCL doesn't know your security group is dangerous, it only knows the block parses. That's the gap static IaC scanners are built to close: they parse the resource graph the way terraform plan does, then evaluate each resource against a rule set that encodes what "insecure" looks like for that provider and resource type.
All three parse .tf files (or plan JSON) and flag misconfigurations without ever touching cloud credentials, but they differ in maintenance status and rule scope. Trivy's trivy config
Sentinel adds an enforcement gate at the point where a plan is about to become real infrastructure, which a pre-commit or CI scanner can't fully replicate because it doesn't see the finalized plan output. Available on Terraform Enterprise and Cloud's Team & Governance tier and above, Sentinel policies run automatically after terraform plan and before apply , with read access to the plan, the resulting state, and the configuration itself — so a policy can inspect the actual resource values Terraform is about to create, not just the source HCL. HashiCorp's documentation defines three enforcement levels: hard-mandatory, which blocks the run with no override; soft-mandatory, which blocks by default but lets an authorized user override it; and advisory, which surfaces a warning without blocking anything. That tiering matters operationally — a team can run new rules as advisory to gather data on how many existing workspaces would fail, then promote proven rules to soft-mandatory, and reserve hard-mandatory for the small set of non-negotiable controls, like blocking public S3 ACLs outright.
Run Tasks are Terraform Cloud/Enterprise's webhook-based integration point for external checks — cost estimation, drift detection, and third-party security scanning — that report a pass/fail result back into the run and display it inline in the run details, alongside the plan output and any Sentinel policy results. Unlike Sentinel, which is HashiCorp's own proprietary policy engine, Run Tasks let a team plug in whatever scanner they already run in CI — Trivy, Checkov, or an internal tool — so the same misconfiguration checks that gate a pull request also gate the Terraform Cloud run itself, rather than relying on CI alone and hoping nobody applies a plan generated outside that pipeline. This closes a real gap: a scanner wired only into GitHub Actions never sees runs triggered by the Terraform Cloud UI, the API, or a scheduled run, so teams that want one consistent gate regardless of trigger source pair Run Tasks with their CI-stage scanner rather than choosing one over the other.
3. Software Implementation, Frameworks & Protocols Open Policy Agent and its Rego policy language matter beyond Terrascan because they're the leading open-source alternative to Sentinel for teams that don't have (or don't want to pay for) Terraform Enterprise's governance tier, and because Rego policies written for Terraform plan JSON can be reused against Kubernetes admission control, CI/CD gates, and other systems that already speak OPA. A team can run terraform show -json to produce plan JSON, then evaluate that JSON against Rego policies with the standalone conftest tool or OPA directly — achieving a Sentinel-like plan-time gate without an Enterprise license, at the cost of building and maintaining the policy library yourself rather than relying on HashiCorp's built-in policy set.
Safeguard doesn't run a dedicated Terraform policy-as-code engine the way Sentinel or Terrascan do, so the misconfiguration checks described above still belong in a scanner like Trivy, Checkov, or Sentinel wired into your plan-time gate. Where Safeguard is directly relevant is the adjacent risk that IaC repositories routinely carry alongside misconfigurations: secrets. Safeguard's secrets scanning runs across your repositories the same way it does for application code, catching hardcoded database passwords, API keys, and cloud credentials that get pasted into .tf files or .tfvars during a rushed provisioning change — a common source of exposure that a misconfiguration-focused scanner like tfsec or Checkov isn't purpose-built to catch with the same depth. Pairing a dedicated IaC policy scanner for misconfigurations with Safeguard's secrets scanning across the same repositories gives you coverage for both failure modes without treating either as a substitute for the other.
Users in Germany and the UK who reached Microsoft 365 through Global Secure Access lost Outlook, Teams and more for about 11 hours. What the status updates say, and what they leave out. One regional fault took down many services in October 2025, and UK regulators now oversee four cloud providers. What concentration risk means for your own stack.
Three first party post-mortems show how routing and name resolution fail, and why recovery is slow when your tools depend on the thing that broke. Lightweight DevSecOps tool that scans Terraform IaC for critical AWS misconfigurations, tracks risk findings, and exposes results through a FastAPI backend and Streamlit dashboard.
Cloud breaches often start as boring misconfigs. This project turns static Terraform review into a repeatable scan → API → dashboard workflow a security engineer can demo. Useful for cloud security , DevSecOps , and shift-left reviews before infrastructure reaches production. II Lightweight, native Python DevSecOps tool that parses Terraform infrastructure-as-code files, checks for critical cloud misconfigurations (AWS), tracks risks, and exposes findings via a FastAPI backend and interactive Streamlit web dashboard.
Checkov scans cloud infrastructure configurations to find misconfigurations before they're deployed. Checkov uses a common command line interface to manage and analyze infrastructure as code (IaC) scan results across platforms such as Terraform, CloudFormation, Kubernetes, Helm, ARM Templates and Serverless framework. Checkov supports developers using Terraform, Terraform plan, CloudFormation, Kubernetes, ARM Templates, Serverless, Helm, and AWS CDK.
Scan cloud resources in build-time for misconfigured attributes with a simple Python policy-as-code framework. Analyze relationships between cloud resources using Checkov’s graph-based YAML policies. Execute, test, and modify runner parameters in the context of a subject repository CI/CD and version control integrations. Prevent misconfigurations from being deployed by embedding it into existing developer workflows.
Checkov can be integrated with custom support for platforms, build processes, and release systems. The transition from manual infrastructure provisioning to Infrastructure as Code (IaC) has fundamentally altered the DevOps landscape. By treating infrastructure with the same rigor as application code, organizations have achieved unprecedented levels of repeatability and scalability. However, this paradigm shift has also centralized risk. A single line of misconfigured HashiCorp Configuration Language (HCL) in a Terraform template can inadvertently expose a database to the public internet, disable encryption at rest, or create a massive cost explosion through unconstrained resource scaling.
As infrastructure complexity grows, manual peer reviews of Terraform plans become mathematically impossible to sustain. To maintain a robust security posture without throttling engineering velocity, organizations must move beyond "human-in-ability" and implement automated, multi-layered misconfiguration detection within their CI/CD pipelines. Detecting these requires more than simple regex-based searching. Effective detection requires tools that understand the structural relationship between resources, variables, and modules.
Effective automation is not achieved with a single tool, but through a layered defense strategy involving Linting, Static Analysis, and Policy-as-Code. The first line of defense is linting. Tools like `tflint` go beyond checking for syntax errors; they validate that the configuration is logically sound according to the specific provider's constraints. For example, `tflint` can detect if an AWS instance type is invalid for a specific region, a check that standard Terraform syntax validation would miss.
Key Benefit: Catching provider-specific errors before the `terraform plan` phase, reducing the feedback loop for developers. Static Analysis Security Testing (SAST) tools, such as Checkov , tfsec (now integrated into Aqua), and Terrascan , scan the HCL files or the generated Terraform Plan JSON. These tools utilize a set of predefined policies to identify known security anti-patterns.
Unlike a simple linter, these tools perform graph-based analysis. They don't just look at an S3 bucket in isolation; they evaluate the relationship between the bucket, its policy, and the IAM roles that have access to it. A tool like Checkov, when run against this code, will trigger a high-severity failure because it identifies two distinct issues: the absence of `aws_s3_bucket_server_side_encryption_configuration` and the explicit disabling of public access blocks.
While SAST tools cover "known unknowns," Policy-as-Code (PaC) allows you to define "known knowns"-your specific organizational guardrails. Using Open Policy Agent (OPA) and the Rego language, you can write complex, context-aware policies that are decoupled from the infrastructure code itself. PaC is most powerful when applied to the `terraform plan` output in JSON format. By analyzing the plan, OPA can evaluate the resultant state of the infrastructure, accounting for variables, locals, and module outputs that are only resolved during the planning phase.
To be effective, these checks must be embedded in the CI/CD workflow. A common implementation pattern involves a "Pre-merge" check in a GitHub Actions or GitLab CI pipeline. As shown across "The Anatomy of an IaC Security Failure", "A Multi-Layered Approach to Detection", "Implementing the Automated Pipeline", a secure implementation for automating misconfiguration detection in terraform iac templates depends on execution discipline as much as design.
The practical hardening path is to enforce deterministic identity policy evaluation with deny-by-default semantics, admission-policy enforcement plus workload isolation and network policy controls, and behavior-chain detection across process, memory, identity, and network telemetry. This combination reduces both exploitability and attacker dwell time by forcing failures across multiple independent control layers.
Operational confidence should be measured, not assumed: track false-allow rate and time-to-revoke privileged access and mean time to detect and remediate configuration drift, then use those results to tune preventive policy, detection fidelity, and response runbooks on a fixed review cadence. 63% of cloud incidents trace back to misconfiguration -- and most are catchable in code. This guide covers Terraform security scanning with Checkov and Trivy, state file hardening, and CI/CD integration patterns.
This issue has been assessed as high severity. Review affected configurations immediately. Infrastructure as Code promised repeatable, auditable deployments. It delivered — but it also codified every misconfiguration at scale. A single vulnerable Terraform module applied across 200 environments becomes 200 exposed resources simultaneously. 63% of cloud security incidents trace to misconfiguration, and the majority of those originate in IaC. The good news: problems caught in a pull request cost almost nothing to fix. Problems caught in a production incident cost millions.
Over-permissive IAM is the most common path to privilege escalation. Terraform makes it easy to grant wildcard permissions and easy to forget to remove them. Public-facing storage — S3, Azure Blob, GCS — defaults have improved but misconfiguration remains common when block_public_acls is explicitly disabled.
Encryption at rest disabled, logging not configured, and security groups with 0.0.0.0/0 ingress on sensitive ports round out the top issues. Checkov is the dominant open-source IaC scanner with 2,500+ built-in policies for AWS, Azure, GCP, and Kubernetes. Install and run against a Terraform directory: 4. Practical Deployment, Analysis & Case Studies Trivy (which replaced tfsec as of 2024) provides IaC scanning alongside container and dependency scanning: Terraform state files contain sensitive data — resource IDs, IP addresses, and sometimes secrets passed as variables. State files stored insecurely are a frequent source of credential exposure.
The shift-left value of IaC scanning only materialises if it blocks merges. Here’s a GitHub Actions workflow that fails the PR on critical findings: Drift occurs when someone makes a manual change in the console that diverges from the IaC state. Undetected drift creates shadow configurations that scanners never see. Integrate terraform plan outputs into your CI pipeline and alert on non-empty plans in production: If you’re starting from a messy baseline: run Checkov in --soft-fail mode to inventory your existing violations, suppress the lower-severity findings with documented justifications, and set the pipeline to hard-fail only on CRITICAL severity. Expand the critical list over successive sprints. Getting the pipeline in place with imperfect coverage beats waiting for perfect coverage before enabling it.
IaC security scanning with Checkov is one of the fastest ways to catch Terraform misconfigurations before they ever reach production. Public S3 buckets, permissive security groups, unencrypted volumes, and overly broad IAM policies are all the kind of drift that turns into a breach headline, and most of them are trivial to catch in a pull request if you have the right scanner wired in. This guide walks through a hands-on Checkov terraform scan tutorial: installing the tool, running your first scan, reading the output, suppressing noise responsibly, and wiring the whole thing into CI so misconfigurations get blocked before merge instead of found during an audit. By the end, you'll have a repeatable IaC misconfiguration detection workflow you can drop into any Terraform repo, plus a sense of how a platform like Safeguard extends this into an organization-wide control.
Terraform makes infrastructure changes fast and repeatable, which is exactly why a single bad module can replicate a misconfiguration across dozens of environments in minutes. A hardcoded 0.0.0.0/0 ingress rule or a storage bucket without encryption doesn't just affect one resource — it becomes the default pattern every engineer copies into the next module. Checkov is an open-source static analysis tool built specifically for infrastructure-as-code. It parses Terraform (along with CloudFormation, Kubernetes manifests, Helm charts, ARM templates, and more) into a graph representation and checks it against hundreds of built-in policies mapped to frameworks like CIS Benchmarks, NIST, PCI-DSS, and SOC 2. Because it works statically against your .tf files, it catches problems before terraform apply ever touches a cloud account — which is a much cheaper place to fix a misconfiguration than after it's live.
Checkov is a Python package and installs cleanly with pip, Homebrew, or as a Docker image. Pip is the most common path for local development and CI runners: If you'd rather avoid polluting your local Python environment, the Docker image works identically and is often the better choice for CI: For teams standardizing tool versions across a monorepo, pinning the Checkov version in a requirements-dev.txt or your CI image avoids "it worked on my machine" drift when new checks ship upstream.
Navigate to the root of your Terraform configuration and point Checkov at the directory: Checkov will recursively scan every .tf file, build a resource graph, and evaluate each resource against its policy set. Output looks like this for a passed and failed check: Each finding includes the specific resource, the exact file and line range, and a link to remediation guidance — enough context to fix the issue without leaving your editor. For a single Terraform module, this is a five-minute scan; for a large monorepo it's still typically under a minute since the analysis is static, not a live cloud API scan.
If you only care about a specific check ID or want to scope the scan to one directory, both are supported: A fresh Checkov terraform scan tutorial run against an existing codebase will often surface fifty or more findings on the first pass — don't try to fix everything at once. Triage by severity and blast radius first: Export results as JSON or SARIF if you want to feed them into a dashboard or ticketing system instead of reading raw terminal output: SARIF is worth calling out specifically since GitHub, GitLab, and most code-scanning dashboards ingest it natively, which turns your Checkov output into inline PR annotations rather than a wall of terminal text someone has to go look up.
Not every finding applies to your environment. A public-facing load balancer in front of a static marketing site isn't the same risk as a public database. Checkov supports inline suppression with an explicit reason, which keeps the suppression auditable instead of silent: You can also suppress at the run level with a .checkov.yaml config file checked into the repo, which is the better option for team-wide policy decisions rather than one-off exceptions: Treat every skip as a decision that needs a reviewer's sign-off in the PR — an unexplained skip-check list is exactly how misconfigurations quietly become permanent. This is also where a documented Terraform security best practices standard pays off: agree once, as a team, on which categories of findings are always blocking versus context-dependent, and write it down so triage doesn't get re-litigated in every PR.
Built-in checks cover the common cloud misconfigurations, but every organization has internal standards that no public ruleset knows about — required tags, approved AMI sources, naming conventions tied to cost allocation. Checkov lets you write custom policies in Python or a simplified YAML format: Point Checkov at the directory containing your custom policies alongside the built-in set: This is the step that turns Checkov from "a generic scanner" into an enforcement layer for your organization's actual Terraform security best practices — the accumulated lessons from past incidents, compliance requirements, and architecture reviews, codified as something a machine checks on every PR instead of something that lives in a wiki nobody reads.
A scan that only runs on a developer's laptop only catches misconfigurations that developer happens to run it against. The real value of IaC misconfiguration detection comes from making it a required, automated gate. A minimal GitHub Actions job: Start with soft-fail: true (or the action's equivalent) so the team gets visibility without blocking every open PR on day one, then flip specific high-severity checks to hard-fail once the existing findings are triaged and the backlog is under control. Trying to hard-fail everything on day one is the single most common reason a Checkov rollout gets disabled by a frustrated team a week later.
Checkov reports zero resources scanned. This usually means it's being pointed at a directory without .tf files, or a .terraform cache directory is confusing the parser. Run with --compact off and check the file list, or scope the -d flag directly to the module root. A check fails but the Terraform is already correct. Confirm you're not scanning a stale plan file or an outdated module version.
Also check whether the resource uses a variable or module output Checkov can't statically resolve — in those cases, --var-file pointing at your terraform.tfvars can help Checkov resolve values it would otherwise treat as unknown. Custom policies aren't being picked up. Verify the --external-checks-dir path is correct relative to where the command runs (CI working directories are a common culprit), and that the YAML or Python file follows Checkov's expected schema — a malformed custom check fails silently rather than throwing a hard error in some versions.
CI passes locally but fails in the pipeline. Compare Checkov versions between local and CI. New releases regularly add checks, so a version pinned in CI but not locally (or vice versa) will produce different results. Pin the version in both places. To verify your setup end to end, intentionally introduce a known-bad resource (an open security group is a good, safe test case), confirm Checkov flags it locally, push the branch, and confirm the same finding shows up as a CI failure or PR annotation. If all three match, your detection pipeline is wired correctly.
Checkov is an excellent foundation for IaC security scanning, but a single open-source scanner in one repo's CI pipeline only tells you about that repo. Safeguard extends the same underlying idea — static, policy-driven detection of infrastructure misconfigurations — across your entire software supply chain, correlating Terraform findings with the artifacts, containers, and pipelines those resources actually deploy.
Instead of triaging Checkov output repo by repo, Safeguard aggregates IaC misconfiguration detection results across every codebase your organization owns, maps findings to the services and teams that own them, and tracks remediation over time so a fixed issue doesn't quietly reappear in the next module someone copies. Custom policy exceptions get the audit trail compliance teams need for SOC 2 and similar frameworks, instead of living as unreviewed #checkov:skip comments scattered across dozens of files. And because Safeguard sits at the supply chain layer, it can tie a Terraform misconfiguration back to the commit, the pull request, and the engineer who introduced it — turning a scanner finding into an actionable, ownable fix rather than another item in a spreadsheet nobody closes.
If your team is ready to move from ad hoc Checkov runs to an organization-wide IaC security scanning Checkov program with enforced Terraform security best practices, Safeguard can plug directly into the CI workflow you already have. Checkov, Trivy and KICS are the maintained open source Terraform scanners. tfsec has merged into Trivy and Terrascan is archived. Compare and choose.
You remove a vendor's IP from an allowlist and the firewall updates immediately. It does not update every client that already resolved the hostname and cached the answer, some of which will keep connecting to the old address for as long as their TTL says they may. Less hardening, unfinished code, no monitoring, real credentials, and often production's network reachability. An attacker choosing between your two environments will frequently prefer this one.
The research studies an LLM-assisted Terraform repair pipeline evaluated under zero-shot, few-shot, and RAG prompting for generating patch candidates that satisfy targeted Checkov policy checks on misconfigured Terraform HCL configurations. Four LLMs are compared (Claude Sonnet, GPT-4o, DeepSeek V3, Qwen3-Coder) on a benchmark of 79 cases spanning AWS, Azure, and Databricks infrastructure.
The methodology is inspired by LAURA (Zhang et al., ASE 2025) and evaluated using the pass@1 protocol from TerraFormer (Jana et al., 2026). The LAURA adaptation is partial: this thesis uses LAURA's exemplar-retrieval idea and CodeT5+ embedding setup, while omitting broader repository-context augmentation and structured chain-of-thought guidance because outputs must be machine-checkable raw HCL patches.
5. Performance Evaluation & Extended Technical Observations Verbeek, S. (2026). Raw Checkov Findings — LLM-Assisted Terraform Misconfiguration Repair (1.0.0). Zenodo. https://doi.org/10.5281/zenodo.19608763 Download them and place in data/raw/ before running dataset construction scripts. Alternatively, follow the reproduction instructions in data/raw/README.md to regenerate them from scratch.
The benchmark ( data/final/unified_benchmark.json ) contains 79 Terraform misconfiguration cases structured as a 2×3 design: Raw Checkov findings can be regenerated with the commands in data/raw/README.md . The Phase 1 construction scripts are retained for auditability, but the recommended thesis rerun starts from the committed unified benchmark so the generation/evaluation pipeline is exactly reproducible.
This validates generated fixes inside temporary synthetic Terraform modules. It is useful for detecting HCL/provider-schema problems, but it is not a deployment safety proof and does not replace the primary Checkov pass@1 metric. Embedding model: Salesforce/codet5p-110m-embedding (CodeT5+, 256-dim), following Zhang et al. (2025). Research code — MIT. Dataset sources retain their original licenses: TerraGoat (Apache 2.0), terraform-databricks-examples (Apache 2.0), TerraDS (see Zenodo record).
Research artifacts for a benchmark study on LLM-assisted Terraform misconfiguration repair under strict targeted Checkov pass@1 evaluation. Raw Checkov static analysis scan outputs used as input to the dataset construction pipeline in the thesis "LLM-Assisted Terraform Misconfiguration Repair for Databricks Infrastructure".
Contains findings from TerraGoat, terraform-databricks-examples, and a TerraDS sample (Azure/terraform, antonputra/tutorials, ministryofjustice/modernisation-platform).
Infrastructure as code moves the power to build and destroy cloud estates into state files, pipeline credentials and reusable modules, and each of those becomes a target in its own right. A Terraform state file can hold database passwords in plain text, the identity that runs terraform apply is often the most privileged account in the cloud, and a single shared module can push a weak setting into hundreds of deployments. This guide goes deeper than the general misconfiguration picture: it covers Terraform state security, secrets in templates, plan and apply privilege, module and provider governance, IaC scanning and policy as code, and drift detection, with notes for OpenTofu, CloudFormation, Azure Bicep and ARM templates, and Pulumi. For the wider picture see the Cloud Misconfiguration Guide . It is written for platform engineers, cloud security teams and the people who review infrastructure pull requests.
Infrastructure as code (IaC) describes cloud resources in declarative files that a tool reconciles with reality. It removes console click-ops but adds assets that need as much protection as the infrastructure itself. MITRE ATT&CK lists configuration files containing passwords as a target of T1552.001 Credentials In Files, and state files, plan files and .tfvars files fit that description exactly.
HashiCorp's documentation is direct: state and plan files hold resource attributes that can include secrets such as initial database passwords and API tokens, and local state is a plaintext file. Values marked sensitive are redacted in CLI output but are still stored in state and plan, and terraform output -json or -raw prints them in plain text. Treat the state file as a credential store.
Encryption limits who can read state; ephemeral values keep secrets out of it. From Terraform 1.10, ephemeral variables, module outputs and resource blocks exist during a run and are omitted from state and plan. From Terraform 1.11, write-only arguments (a _wo suffix, such as password_wo , with a _wo_version argument to trigger updates) send a value to the provider without persisting it. Provider support varies. The target pattern: read the secret from a vault through an ephemeral resource and pass it to a write-only argument.
OpenTofu can encrypt state and plan files itself, in any backend, using the aes_gcm method with key providers such as aws_kms , gcp_kms , azure_vault or pbkdf2 . Set enforced = true once migrated, and back up keys first: encrypted state is unrecoverable without them. Every IaC tool can keep secrets out of source and logs; leaks happen when teams skip it or forget outputs.
The identity that applies infrastructure can usually create users, open network rules and delete databases: a non-human identity with standing administrative power that attackers on a CI runner look for first. Modules and providers are third-party code that runs with your cloud credentials. Treat them as part of the software supply chain.
Infrastructure as code scanning works at two levels. Static IaC scanners read source templates and flag known misconfiguration patterns. Policy-as-code engines evaluate the machine-readable plan (for Terraform, terraform show -json on a saved plan), which contains resolved values and the exact create, update and delete actions. HashiCorp describes configuration drift as changes "made outside Terraform's regular process": someone bypassed review, or an emergency fix never reached code.
NIST SP 800-204D's strategies for supply chain security in CI/CD pipelines apply directly to infrastructure pipelines. Related NHI Mgmt Group resources: Cloud Misconfiguration Guide · CI/CD Pipeline Identity Security Guide · Secrets Management Guide · Software Supply Chain Security Guide · CNAPP Guide The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week.
The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week. Learn how to write automated security tests for Terraform configurations to catch misconfigurations like open ports, missing encryption, and overly permissive IAM policies. Security misconfigurations in Terraform are among the most common causes of cloud breaches. An overly permissive security group, an unencrypted database, or a wildcard IAM policy can expose your entire infrastructure. The good news is that most of these issues are detectable before deployment through automated testing. This guide walks through practical approaches to testing Terraform for security best practices.
Before writing tests, know what you are looking for. The most frequent Terraform security issues include: Trivy (which absorbed tfsec) is the fastest way to scan Terraform for security issues. It knows about hundreds of security rules out of the box. For organization-specific security rules, write custom tests against the resources in your module.
IAM policies deserve special attention because overly permissive policies are a top attack vector. Not every security finding is actionable. Some resources legitimately need public access (like a public-facing load balancer). Use inline comments to suppress specific checks: Document why each suppression exists. Security scanners flag things for a reason, and a suppression without context looks like a shortcut.
Security best practices evolve. New vulnerabilities are discovered, cloud providers add new security features, and compliance requirements change. Keep your security tests current: Automated security testing catches the low-hanging fruit that causes most breaches. It is not a replacement for security reviews, penetration testing, or threat modeling, but it prevents the obvious mistakes from ever reaching production.
For related topics, see How to Test Terraform for Compliance Requirements and How to Use Conftest with Terraform for Policy Testing . Every OneUptime blog post is open source. Found a typo, an inaccuracy, or have a clearer way to explain something? Anyone can contribute — your edits make this post better for everyone who reads it next.
Your complete reliability stack unified: infrastructure monitoring, incident management, status pages, and APM. Open-source and self-hostable. In July 2019, a former Amazon Web Services engineer exploited a misconfigured web application firewall to pull temporary credentials from an EC2 instance's metadata service, then used those credentials to read more than 700 S3 buckets and exfiltrate records on 106 million Capital One customers. The instance's IAM role had far broader permissions than the WAF actually needed — the kind of default-open access pattern that gets written into a Terraform module once and then copy-pasted into a dozen environments. Terraform's declarative model makes provisioning fast and repeatable, but that same repeatability means a single insecure default — a security group open to 0.0.0.0/0 , an unencrypted S3 bucket, an IAM policy with "Action": "*" — gets replicated everywhere the module is reused. Gartner predicted back in 2019 that through 2025, 99% of cloud security failures would trace back to customer misconfiguration, not the cloud provider. Six years later that prediction still holds. Here is how Terraform misconfigurations happen, why they're hard to catch, and what actually stops them before they reach production.
A Terraform misconfiguration is any resource block in a .tf file that provisions infrastructure with weaker security controls than the environment requires — an AWS security group with SSH open to the internet, an Azure Storage account with public blob access enabled, a GCS bucket with allUsers granted objectViewer . Unlike an application vulnerability, a Terraform misconfiguration usually isn't a bug in the traditional sense — the code runs exactly as written and terraform apply succeeds cleanly. The problem is that "succeeds cleanly" and "secure" are different properties, and Terraform's provider defaults have historically favored the former. For example, the aws_s3_bucket resource in the AWS provider did not block public ACLs by default until HashiCorp split that behavior into a separate aws_s3_bucket_public_access_block resource in provider v4 (released April 2022) — meaning any module written before that change, and never revisited, can silently allow public objects.
Multiply that by every team that forked a Stack Overflow snippet or a public registry module in 2019 or 2020 and never re-ran the code against a current baseline, and you get an estate full of infrastructure that was "correct" the day it was written and wrong every day since. Harvested Online Documentation & Reference Sources • https://github.com/jeremiahhale793/Cloud-Security-Misconfiguration-Detection-AWS • https://github.com/NarahariRaghava/Pre-Deployment-Detection-of-Terraform-Security-Misconfigurations-Using-Machine-Le arning • https://developer.hashicorp.com/terraform/cdktf/api-reference/python • https://trivy.dev/docs/latest/tutorials/misconfiguration/terraform/ • https://trivy.dev/docs/v0.54/tutorials/misconfiguration/terraform/ • https://www.decryptiondigest.com/blog/terraform-iac-security-scanning-tfsec-checklist • https://safeguard.sh/resources/blog/terraform-iac-security-scanning-guide • https://github.com/KingLinux24/cloud-misconfig-detector • https://www.checkov.io/ • https://www.cyberask.co.uk/posts/automating-misconfiguration-detection-in-terraform-iac-templates.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Terraform Misconfiguration Detection Tool In Python.
[*] Metasploit Scan Running on Target Subnet for Terraform Misconfiguration Detection Tool In Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |