Complete Technical Paper Content — Theharvester Wrapper Tool For Automated Reconnaissance
Overview & System Context
Theharvester Wrapper Tool For Automated Reconnaissance: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~2617 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background As part of my Cybersecurity & Ethical Hacking internship with Networkwalks , I performed a Footprinting and Reconnaissance exercise using theHarvester 4.10.1 on Kali Linux.
The exercise focused on Open-Source Intelligence (OSINT) and passive reconnaissance to understand how publicly available information can reveal aspects of an organization's digital footprint. II Note: This documentation focuses on reconnaissance methodology and learning outcomes. No exploitation, authentication testing, or vulnerability verification was performed.
The output contained hostname entries, mappings, wildcard records and repeated representations. Proper normalization would be required before treating the results as a unique asset inventory. Figure 1: Cyber Security Project Presentation : Essential Reconnaissance Tools ... Several integrations were affected by missing or invalid API credentials, including sources such as Shodan, Censys, VirusTotal, GitHub, SecurityTrails, FOFA and LeakIX.
This demonstrates how publicly discoverable DNS and indexed information can provide insight into an organization's digital footprint. These results provide candidate information about infrastructure associated with the target. However, the exercise did not independently verify whether each address was active, publicly accessible, or directly controlled by the target.
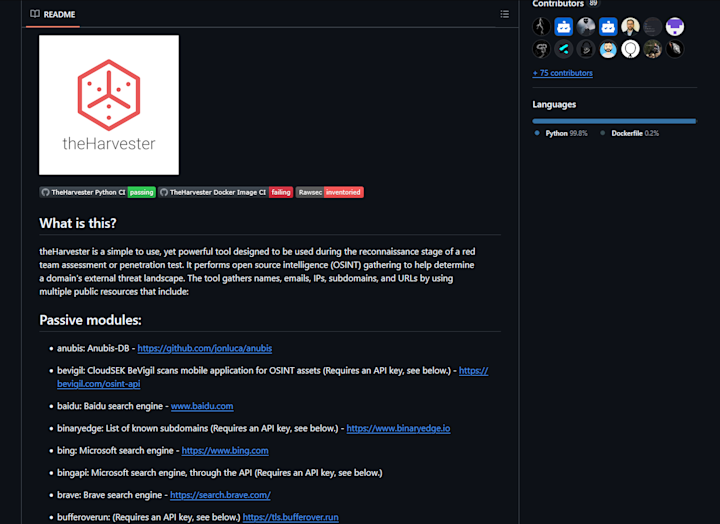
Figure 2: Beginner's Guide to Passive Reconnaissance Tools in Cyber Security ... Publicly available email addresses may potentially be useful in phishing or social-engineering scenarios. However, discovering an email address does not establish that an account is compromised or vulnerable. Multiple ASNs can indicate that an organization's externally visible infrastructure is associated with different network environments.
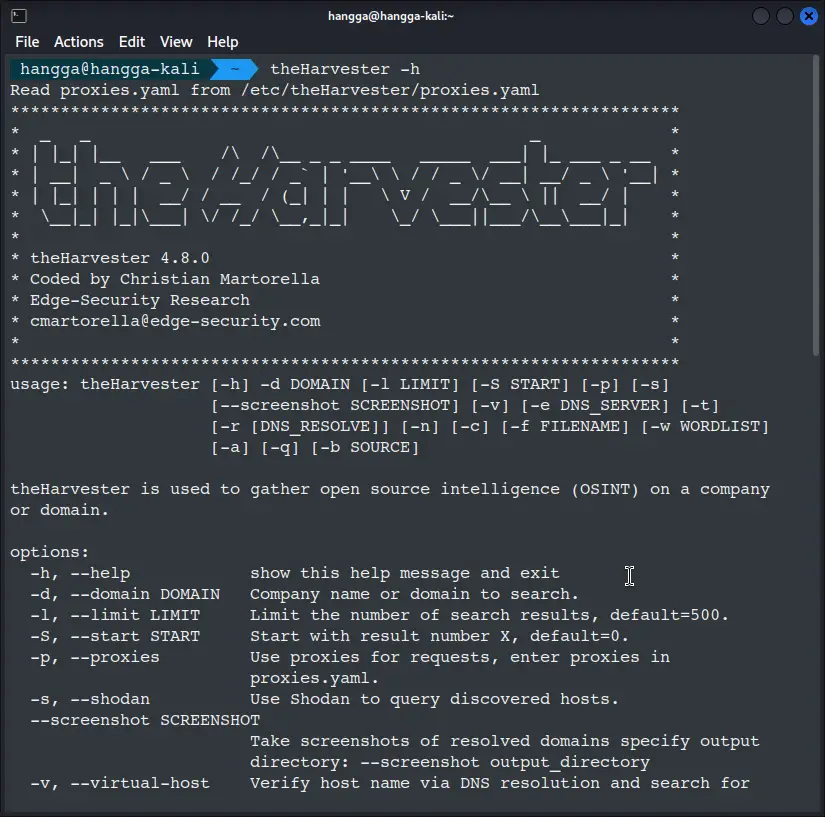
The presence of authentication-related parameters does not, by itself, demonstrate an authentication vulnerability. Figure 3: PenTesting 101: Using TheHarvester for OSINT and Reconnaissance From an attacker's point of view, publicly available information can assist in building an understanding of an organization's external attack surface.
Therefore, the results represent a preliminary reconnaissance dataset rather than a complete security assessment . Sensitive or unnecessary infrastructure details should be blurred/redacted before public publication. A hostname, IP address, email address, or URL discovered through OSINT requires further authorized validation before any security weakness can be established.
The exercise demonstrated how theHarvester 4.10.1 can collect publicly available information from multiple OSINT sources. The main learning outcome was understanding how publicly available information can contribute to an organization's digital footprint and how reconnaissance findings should be carefully interpreted. This exercise strengthened my practical understanding of Footprinting, OSINT, Passive Reconnaissance, and Information Exposure .
Tool: theHarvester 4.10.1 Target: microsoft.com Assessment Type: OSINT / Passive Reconnaissance Platform: Kali Linux Primary Evidence: theHarvester reconnaissance output As part of my cybersecurity and ethical hacking lab activities, I performed an Open-Source Intelligence (OSINT) and passive reconnaissance exercise using theHarvester 4.10.1.
2. System Architecture & Core Working Principles This project documents a practical domain reconnaissance exercise performed with theHarvester 4.10.1 as part of the Networkwalks W2-PM4 cybersecurity assignment. The exercise focused on collecting publicly available information associated with the domain microsoft.com and documenting the limitations encountered during multi-source reconnaissance.
Authorization and Ethics: This repository is for cybersecurity education and authorized security assessment only. Do not use these techniques against systems or data outside an approved scope. These values are reproduced as tool output from the training exercise and are not independently verified. Reconnaissance helps security professionals understand what information may be publicly discoverable about an organization. Publicly discoverable infrastructure information can contribute to external attack-surface analysis.
The findings in this project are reconnaissance observations, not confirmed vulnerabilities . Adio Kabiru Network Engineer | Cybersecurity | Telecommunications Engineer | Network Security Engineer #Cybersecurity #NetworkSecurity #theHarvester #Reconnaissance #KaliLinux #OSINT #EthicalHacking In the foundational preliminary stages of any professional penetration test, authorized Red Team engagement, or corporate threat intelligence investigation, the analyst’s primary objective is to define the target’s entire attack surface. You cannot attack, or defend, corporate infrastructure that you do not know exists.
During this crucial reconnaissance phase, elite intelligence analysts hunt for two highly valuable pieces of actionable intelligence: Attempting to gather this data manually by endlessly clicking through Google search results, reading hundreds of LinkedIn profiles, and querying DNS servers by hand is an impossible task. It is too slow and prone to severe human error.
Written efficiently in Python, theHarvester is a powerful command-line reconnaissance aggregator. It rapidly queries public search engines, breach databases, and corporate security APIs to compile a unified, structured report of a target’s global public footprint in mere seconds. In this tutorial, we will break down the philosophy of passive reconnaissance, manually install theHarvester from its raw source code, configure advanced third-party API keys, and execute complex real-world domain and email harvesting campaigns.
To understand why theHarvester is so valuable, you must understand the critical boundary between strict Passive and Active reconnaissance. When you ask theHarvester to find deeply hidden subdomains for target-company.com , the tool does not send a single network packet to target-company.com . Instead, it securely connects to Google, Bing, Shodan, and public global SSL Certificate Transparency Logs. It asks those third-party global databases, “What do you already know about this specific target?” Because the target’s physical servers are never touched, the target has no idea that you are mapping their corporate infrastructure. This makes theHarvester an indispensable tool for stealthy operations and early-stage OSINT gathering.
While theHarvester is pre-installed on security distributions like Kali Linux and Parrot OS, professional analysts frequently install it directly from the source repository to ensure they have the latest API modules and bug fixes. We will install the tool in an isolated Python Virtual Environment on a standard Ubuntu/Debian Linux system. This prevents the tool’s complex dependencies from conflicting with your host operating system.
Open your terminal and ensure Git and the Python virtual environment modules are installed: Securely download the official source code from the author’s official GitHub repository: Create an isolated environment folder named venv and activate it. Your terminal prompt will change, indicating you are securely operating inside the sandbox.
3. Software Implementation, Frameworks & Protocols theHarvester relies on dozens of libraries for web scraping and API interaction. Install them flawlessly using the provided requirements file: Out of the box, theHarvester works perfectly with free, unauthenticated global sources like Google, Bing, DuckDuckGo, and Yahoo. However, the true power of the tool is unlocked when you integrate it with global enterprise security APIs.
To configure your global API keys, you must edit the api-keys.yaml file located in the root directory of theHarvester directory. Carefully paste your unique API keys into the YAML file, ensuring you respect the strict Python indentation formatting, securely save the file, and exit the text editor. theHarvester is efficiently controlled via specific command-line flags. The core foundational syntax requires a specific target domain ( -d ) and a specific data source ( -b ).
Let’s execute a series of targeted reconnaissance campaigns, moving seamlessly from basic email harvesting to complex infrastructure global mapping. You are tasked with building a targeted phishing list for an authorized Red Team engagement against target-company.com . You need valid employee emails fast.
The Mechanics: theHarvester will scrape 1,000 pages of Google and Bing looking for the @target-company.com string. It will simultaneously query the Hunter.io API and scrape public LinkedIn profiles to extract employee names and accurately infer their email addresses based on the corporate naming convention (e.g., first.last@ ). The client wants you to specifically test their external perimeter. They provided their main website, but you need to discover the hidden staging servers they forgot to specify.
The Mechanics: This intentionally ignores standard global search engines. It heavily queries crt.sh (Certificate Transparency logs). Every time the target company buys a secure SSL certificate for a new server (e.g., dev-api.target-company.com ), it is permanently logged inside a global public database. theHarvester seamlessly pulls these logs, discovering subdomains that have never been linked publicly. The -v flag actively checks if those subdomains are currently actively online.
You want to know absolutely everything the internet knows about the specific target, and you want it correctly saved to a highly structured report for the client. The Mechanics: This command queries every single module built into the tool. It will take several minutes to run, as it perfectly respects API rate limits. Once complete, it will generate /reports/target_recon.html and /reports/target_recon.xml .
Data is useless if it is not highly actionable. The XML output generated by the -f flag is specifically designed to be flawlessly ingested by larger intelligence frameworks. If you carefully read our Maltego Community Edition Guide , you know that visual link analysis is crucial. You can write a simple Python script to parse theHarvester’s XML output and automatically generate a CSV file that Maltego can import. This instantly translates your terminal output into a massive, interactive visual graph of the target’s entire corporate structure.
Once theHarvester generates a list of 50 active subdomains, the passive phase of the investigation is over. You take that list of subdomains and feed it directly into an active vulnerability scanner like Nikto or a port scanner like Nmap to begin the exploitation phase of the engagement. If you are a corporate security administrator, it is terrifying to realize how easily an attacker can map your entire organization with a single Python script. To defend against automated reconnaissance, you must aggressively manage your public footprint.
theHarvester is a popular open-source intelligence (OSINT) tool designed to gather emails, subdomains, hosts, employee names, and open ports from various public sources like search engines and PGP key servers. Yes, theHarvester comes pre-installed on Kali Linux. You can launch it directly from the terminal by typing theHarvester . However, it is recommended to update it regularly or pull the latest version from GitHub to ensure API integrations are current.
You can find emails associated with a domain by running a basic command like theHarvester -d example.com -b google,linkedin,bing . This tells the tool to search for example.com across Google, LinkedIn, and Bing. If theHarvester returns no results, you may be hitting rate limits from search engines (like Google blocking automated scraping). You can bypass this by using different data sources (e.g., Baidu, DuckDuckGo), configuring API keys for premium sources (like Hunter.io), or using a proxy.
By default, theHarvester is a passive reconnaissance tool, meaning it only searches public databases and search engines without touching the target’s servers. However, it does have active features (like DNS brute-forcing and port scanning) which must be explicitly enabled via command-line flags. 4. Practical Deployment, Analysis & Case Studies theHarvester represents the perfect synergy of automation and open-source intelligence. By chaining together dozens of disparate databases, search engines, and enterprise APIs, it reduces hours of tedious manual reconnaissance into a few seconds of terminal output. Mastering this tool is an absolute requirement for any modern penetration tester or threat intelligence analyst. Ensure your API keys are valid, tune your search limits appropriately, and always use the output as a launchpad for deeper, targeted analysis.
Systems Engineer & Tech Educator with 8+ years of experience in Linux Administration, Cloud Computing, and Cybersecurity. Founder of FreeTechLearner, dedicated to creating practical tutorials that help students and professionals build real-world skills. Ever wonder how security pros find those hidden entry points before the real testing even begins? It all starts with what we call reconnaissance—the art of gathering intelligence. Think of it like casing a building before a security audit; you need to know the doors, windows, and air vents first.
In this digital age, one of the go-to tools for this initial legwork is TheHarvester . At its heart, TheHarvester is a Python script that doesn't try to do anything fancy. Its job is straightforward: to scour publicly available information and collect things like email addresses, subdomains, IPs, and URLs. It looks in all the usual places, from standard search engines to specialized databases like Shodan , which is essentially a search engine for internet-connected devices.
We did something like this by fingerprinting with WhatWeb in an earlier tutorial. But TheHarvester is a different tool with more diverse information. If you're not using Kali Linux, you can easily install TheHarvester from its GitHub repository . Let's use TheHarvester to discover information about our target, vulnweb.com . We'll start with a broad search using the google and duckduckgo sources.
If you're seeing the error The following engines are not supported: {'google'} , don't worry—you're not alone. This is a frequent problem that stems from how TheHarvester interacts with public search engines, particularly Google. The short answer: Google has made its search engine increasingly difficult to scrape programmatically. In the case of our example domain, vulnweb.com , this means we might miss some results that could be indexed on Google, but it's not the end of the world.
You can use -b all to run all modules. The unsupported ones will be gracefully skipped, and the supported ones will run. The output is actually huge, spanning over 600 lines. You can view the complete output in this GitHub gist . Don't let these alarm you. The "Server disconnected" and similar exceptions are TheHarvester's way of telling you that certain data sources were unavailable or timed out—this is completely normal during reconnaissance. The tool gracefully skips these and moves on to working sources.
This reveals the Autonomous System Number, essentially telling us which major network provider hosts this infrastructure (in this case, AS16509 is Amazon.com, Inc.). This is your target list! Each URL represents a potential entry point. Notice we've found: Only two IP addresses serving all this content? This suggests virtual hosting where multiple domains share the same server—valuable for understanding the infrastructure setup.
This massive list of 610 hosts reveals the true scale of the environment. You can see patterns emerging: For a test site like vulnweb.com , this makes sense. But in a real engagement, missing email addresses might mean you need different reconnaissance approaches. So what's next with this intelligence? Your penetration testing roadmap becomes clear: In just minutes, TheHarvester has transformed an unknown domain into a mapped-out territory ready for deeper security testing.
5. Performance Evaluation & Extended Technical Observations The real power of TheHarvester comes from using multiple data sources. Let's run a more comprehensive scan using bing , linkedin , and threatcrowd . For the most thorough reconnaissance, you can use nearly all sources with the -b all flag.
TheHarvester is a cornerstone tool for any penetration tester or security researcher. By following this guide, you can effectively use it to map out the digital footprint of your target and lay the groundwork for a successful security assessment. Software engineer since 2008. Security researcher, seasonal pentester, and creator of WebSlurp [webslurp.github.io] theHarvester is an open-source OSINT (Open-Source Intelligence) tool designed for gathering emails, subdomains, IPs, and URLs using passive techniques. It's often used during the initial stages of penetration testing or red teaming to build a profile of a target domain.
theHarvester -d example.com -c -w subdomains.txt Performs brute-force against DNS using a wordlist. theHarvester -d example.com -c -w subdomains.txt -f result_output Exports results for later review. theHarvester -d example.com -c -w subdomains.txt --screenshot screenshots/ Visual capture of exposed interfaces. theHarvester -d example.com -l 50 -c -w subdomains.txt Quick scan with up to 50 results.
theHarvester -d example.com -b all -c -w subdomains.txt -q Pulls from all supported sources. theHarvester -d example.com -c -n -w subdomains.txt Combines brute-forcing with DNS resolution. theHarvester -d example.com -r resolvers.txt -c -w subdomains.txt Useful for avoiding DNS filtering. theHarvester -d example.com --screenshot screenshots/ -c -w subdomains.txt -f full_results Complete visual and structured data dump.
theHarvester -d example.com -l 1000 -c -w subdomains.txt Deep dive for high-value domains. theHarvester -d example.com -a -c -w endpoints.txt Comprehensive endpoint enumeration. theHarvester -d example.com -b rapiddns -c -w subdomains.txt Great for passive DNS visibility. theHarvester -d example.com -b yahoo -c -w subdomains.txt -f yahoo_report Useful fallback when Google limits are reached.
theHarvester -d example.com -b crtsh -c -w subdomains.txt --screenshot screenshots/ Enumerates cert transparency logs. theHarvester -d example.com -S 100 -l 200 -c -w subdomains.txt Skips first 100, fetches next 200 results. theHarvester -d example.com -b all -c -w subdomains.txt -q Suppresses warnings — useful for automation. theHarvester -d example.com -c -w /usr/share/seclists/Discovery/DNS/namelist.txt Use extensive or customized wordlists.
Harvested Online Documentation & Reference Sources • https://github.com/whitebirdman/Footprinting-Reconnaissance-with-theHarvester • https://github.com/Kayfactorial/NETWORKWALKS-B083-WK2-PM4-CYBERSECURITY-theHarvester • https://www.freetechlearner.com/blog/cybersecurity/theharvester-tutorial-email-and-domain-reconnaissance • https://linuxhandbook.com/using-theharvester/ • https://grb889.github.io/klc89/theHarvester_OSINT_Guide/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Theharvester Wrapper Tool For Automated Reconnaissance.
[*] Metasploit Scan Running on Target Subnet for Theharvester Wrapper Tool For Automated Reconnaissance... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |