Complete Technical Paper Content — Threat Intelligence Dashboard Using Python And Streamlit
Overview & System Context
Threat Intelligence Dashboard Using Python And Streamlit: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~2241 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A full-stack analytics solution designed to monitor, analyze, and respond to cybersecurity threats across global networks. This project processes over 200,000+ threat logs to uncover patterns in attack types, severity levels, response actions, and geographic distribution—empowering SOC teams with predictive insights and real-time dashboards.
Cybersecurity operations demand rapid, data-driven decision-making. This project delivers an end-to-end threat intelligence platform that enables: A comprehensive Streamlit-based cybersecurity dashboard providing real-time insights into security threats, system performance, and data integrity. This interactive dashboard offers a user-friendly interface for monitoring and analyzing security metrics.
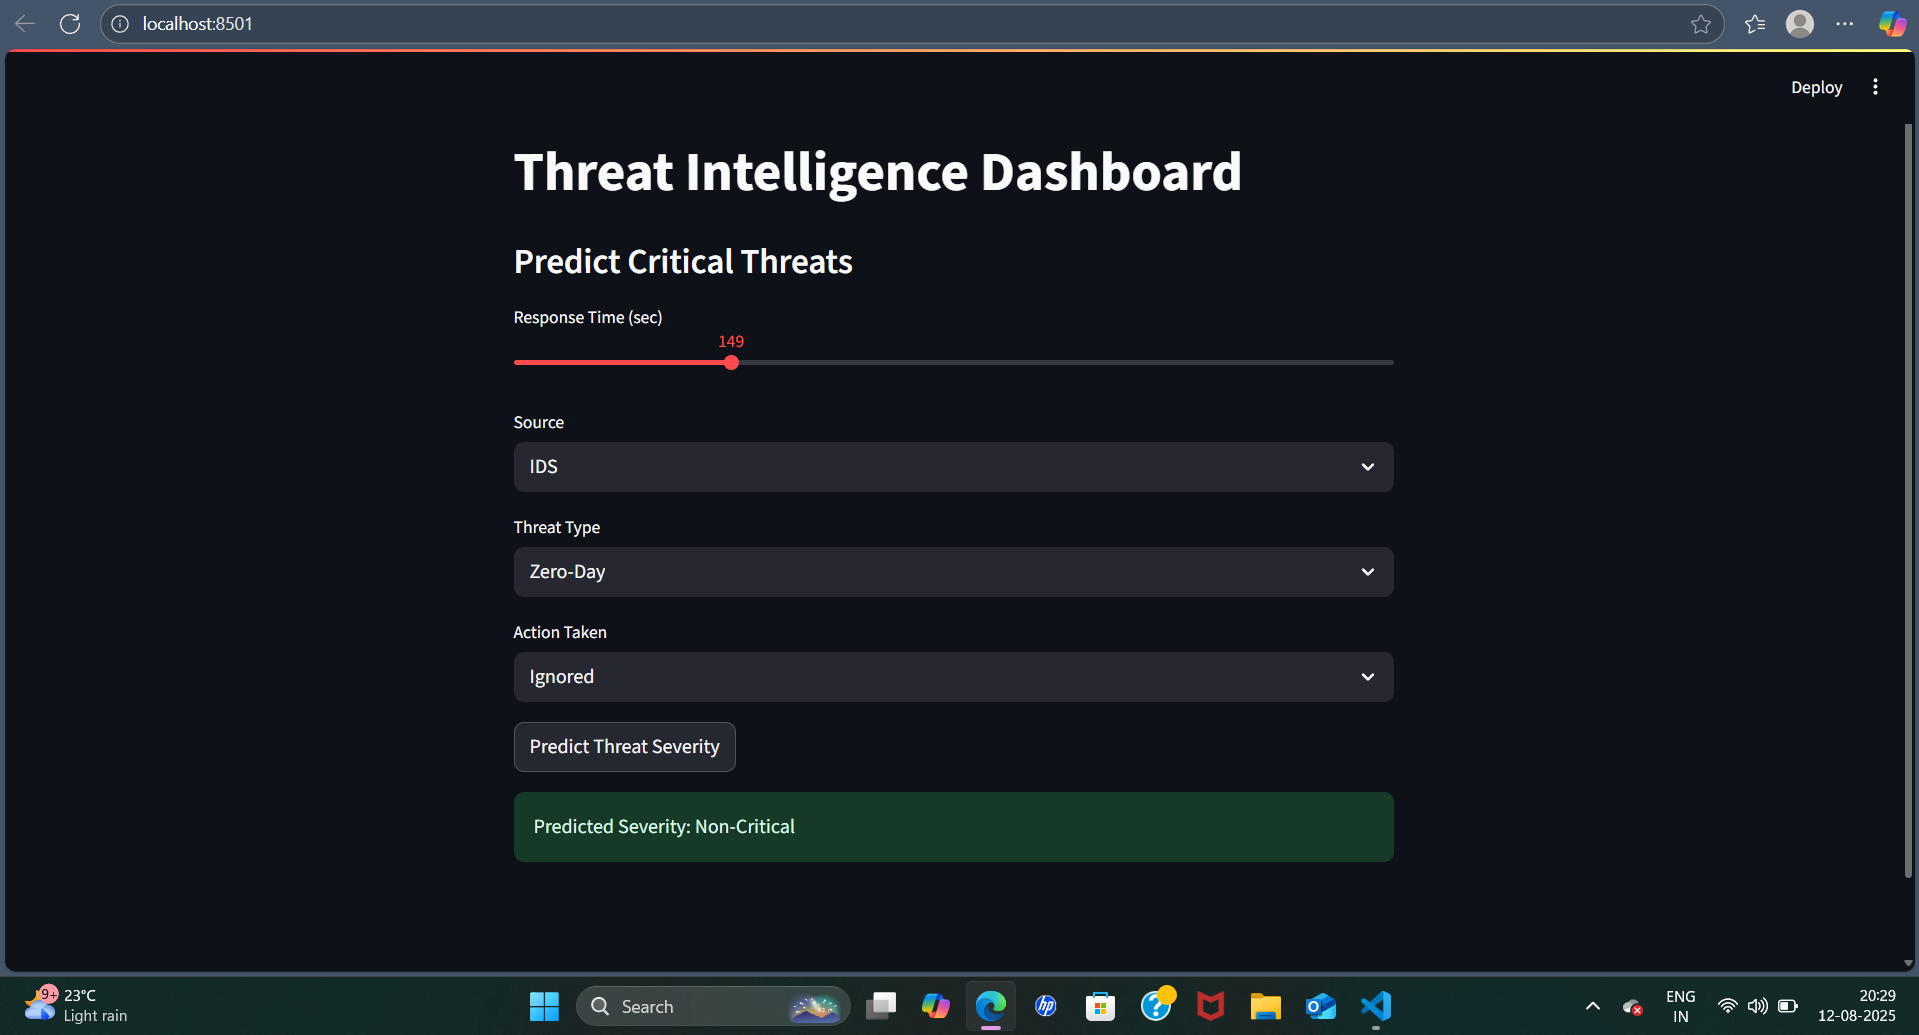
The dashboard currently runs on simulated data that mimics real-world cybersecurity incidents. It can be connected to actual data sources like: Figure 1: II Threat Intelligence Dashboard | Threat-Intelligence-Dashboard- A comprehensive Streamlit-based cybersecurity dashboard providing real-time insights into security threats, system performance, and data integrity. This interactive dashboard offers a user-friendly interface for monitoring and analyzing security metrics.
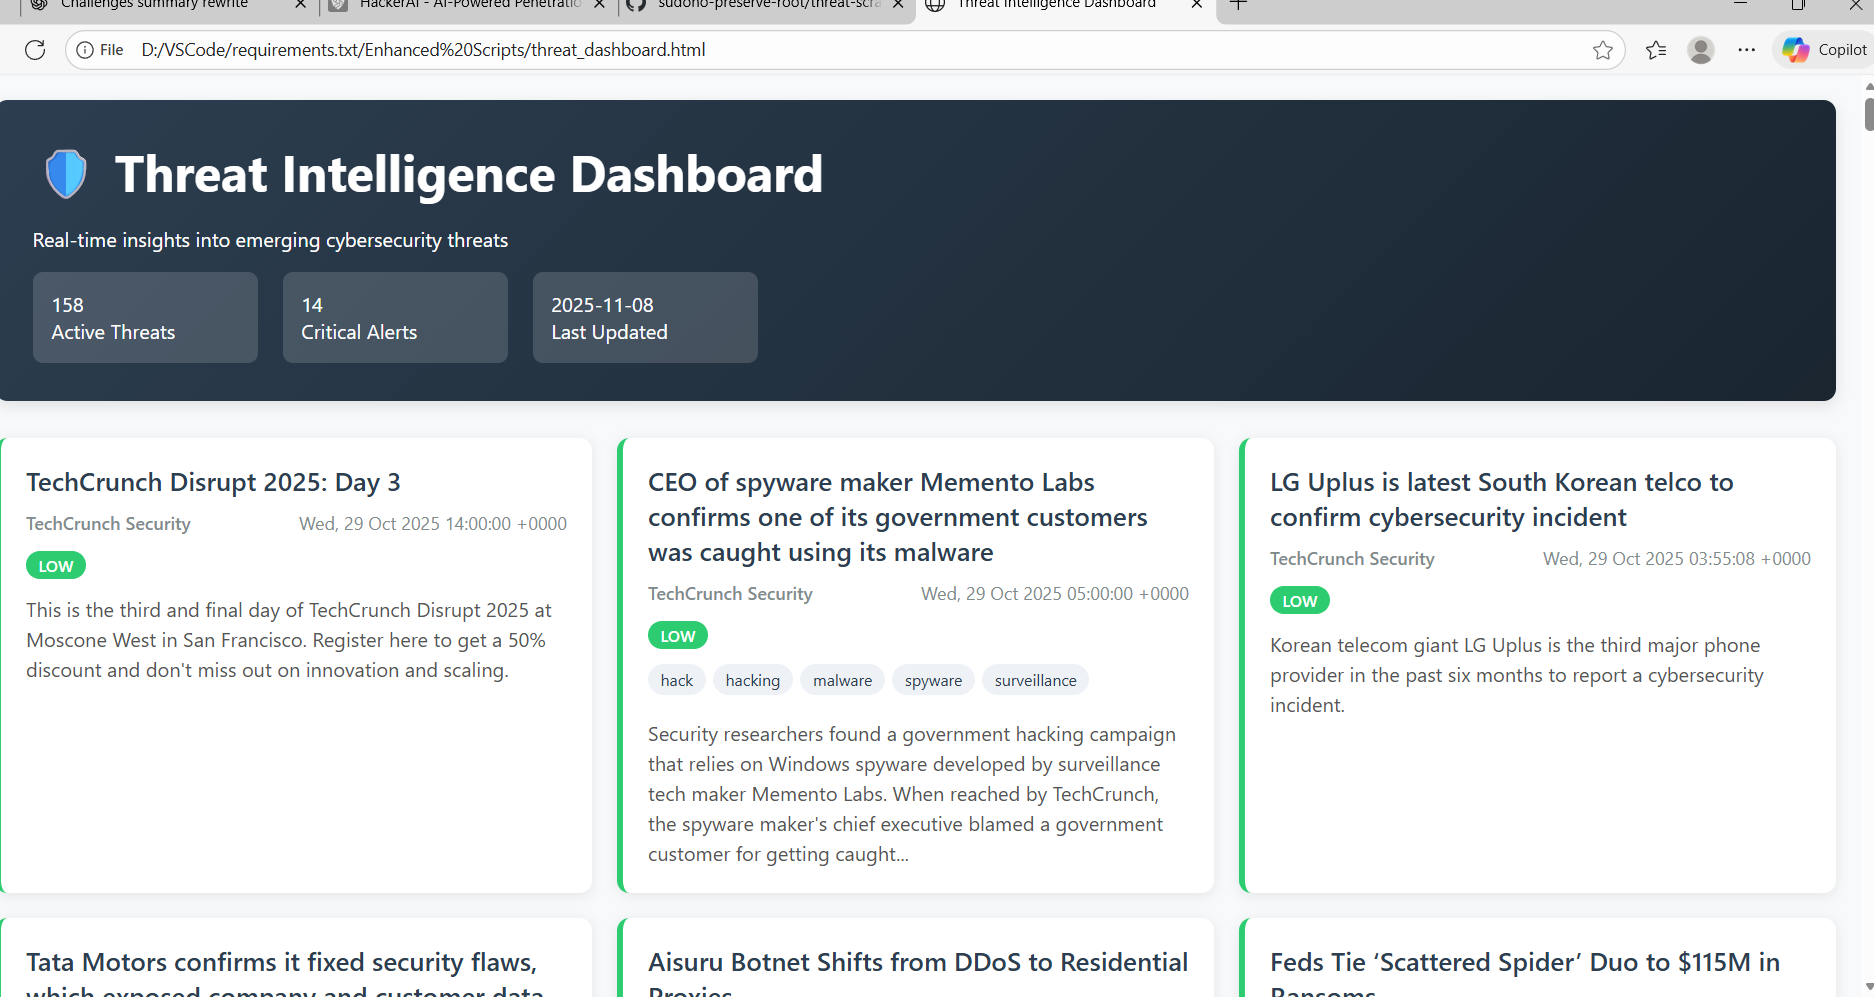
A comprehensive Streamlit-based cybersecurity dashboard providing real-time insights into security threats, system performance, and data integrity. This interactive dashboard offers a user-friendly interface for monitoring and analyzing security metrics. The dashboard currently runs on simulated data that mimics real-world cybersecurity incidents. It can be connected to actual data sources like: Streamlit is an open-source Python framework for data scientists and AI/ML engineers to deliver dynamic data apps with only a few lines of code. Build and deploy powerful data apps in minutes. Let's get started! Figure 2: Threat Intelligence Dashboard | Devpost Learn about our APIs, with actionable explanations of specific functions and features.
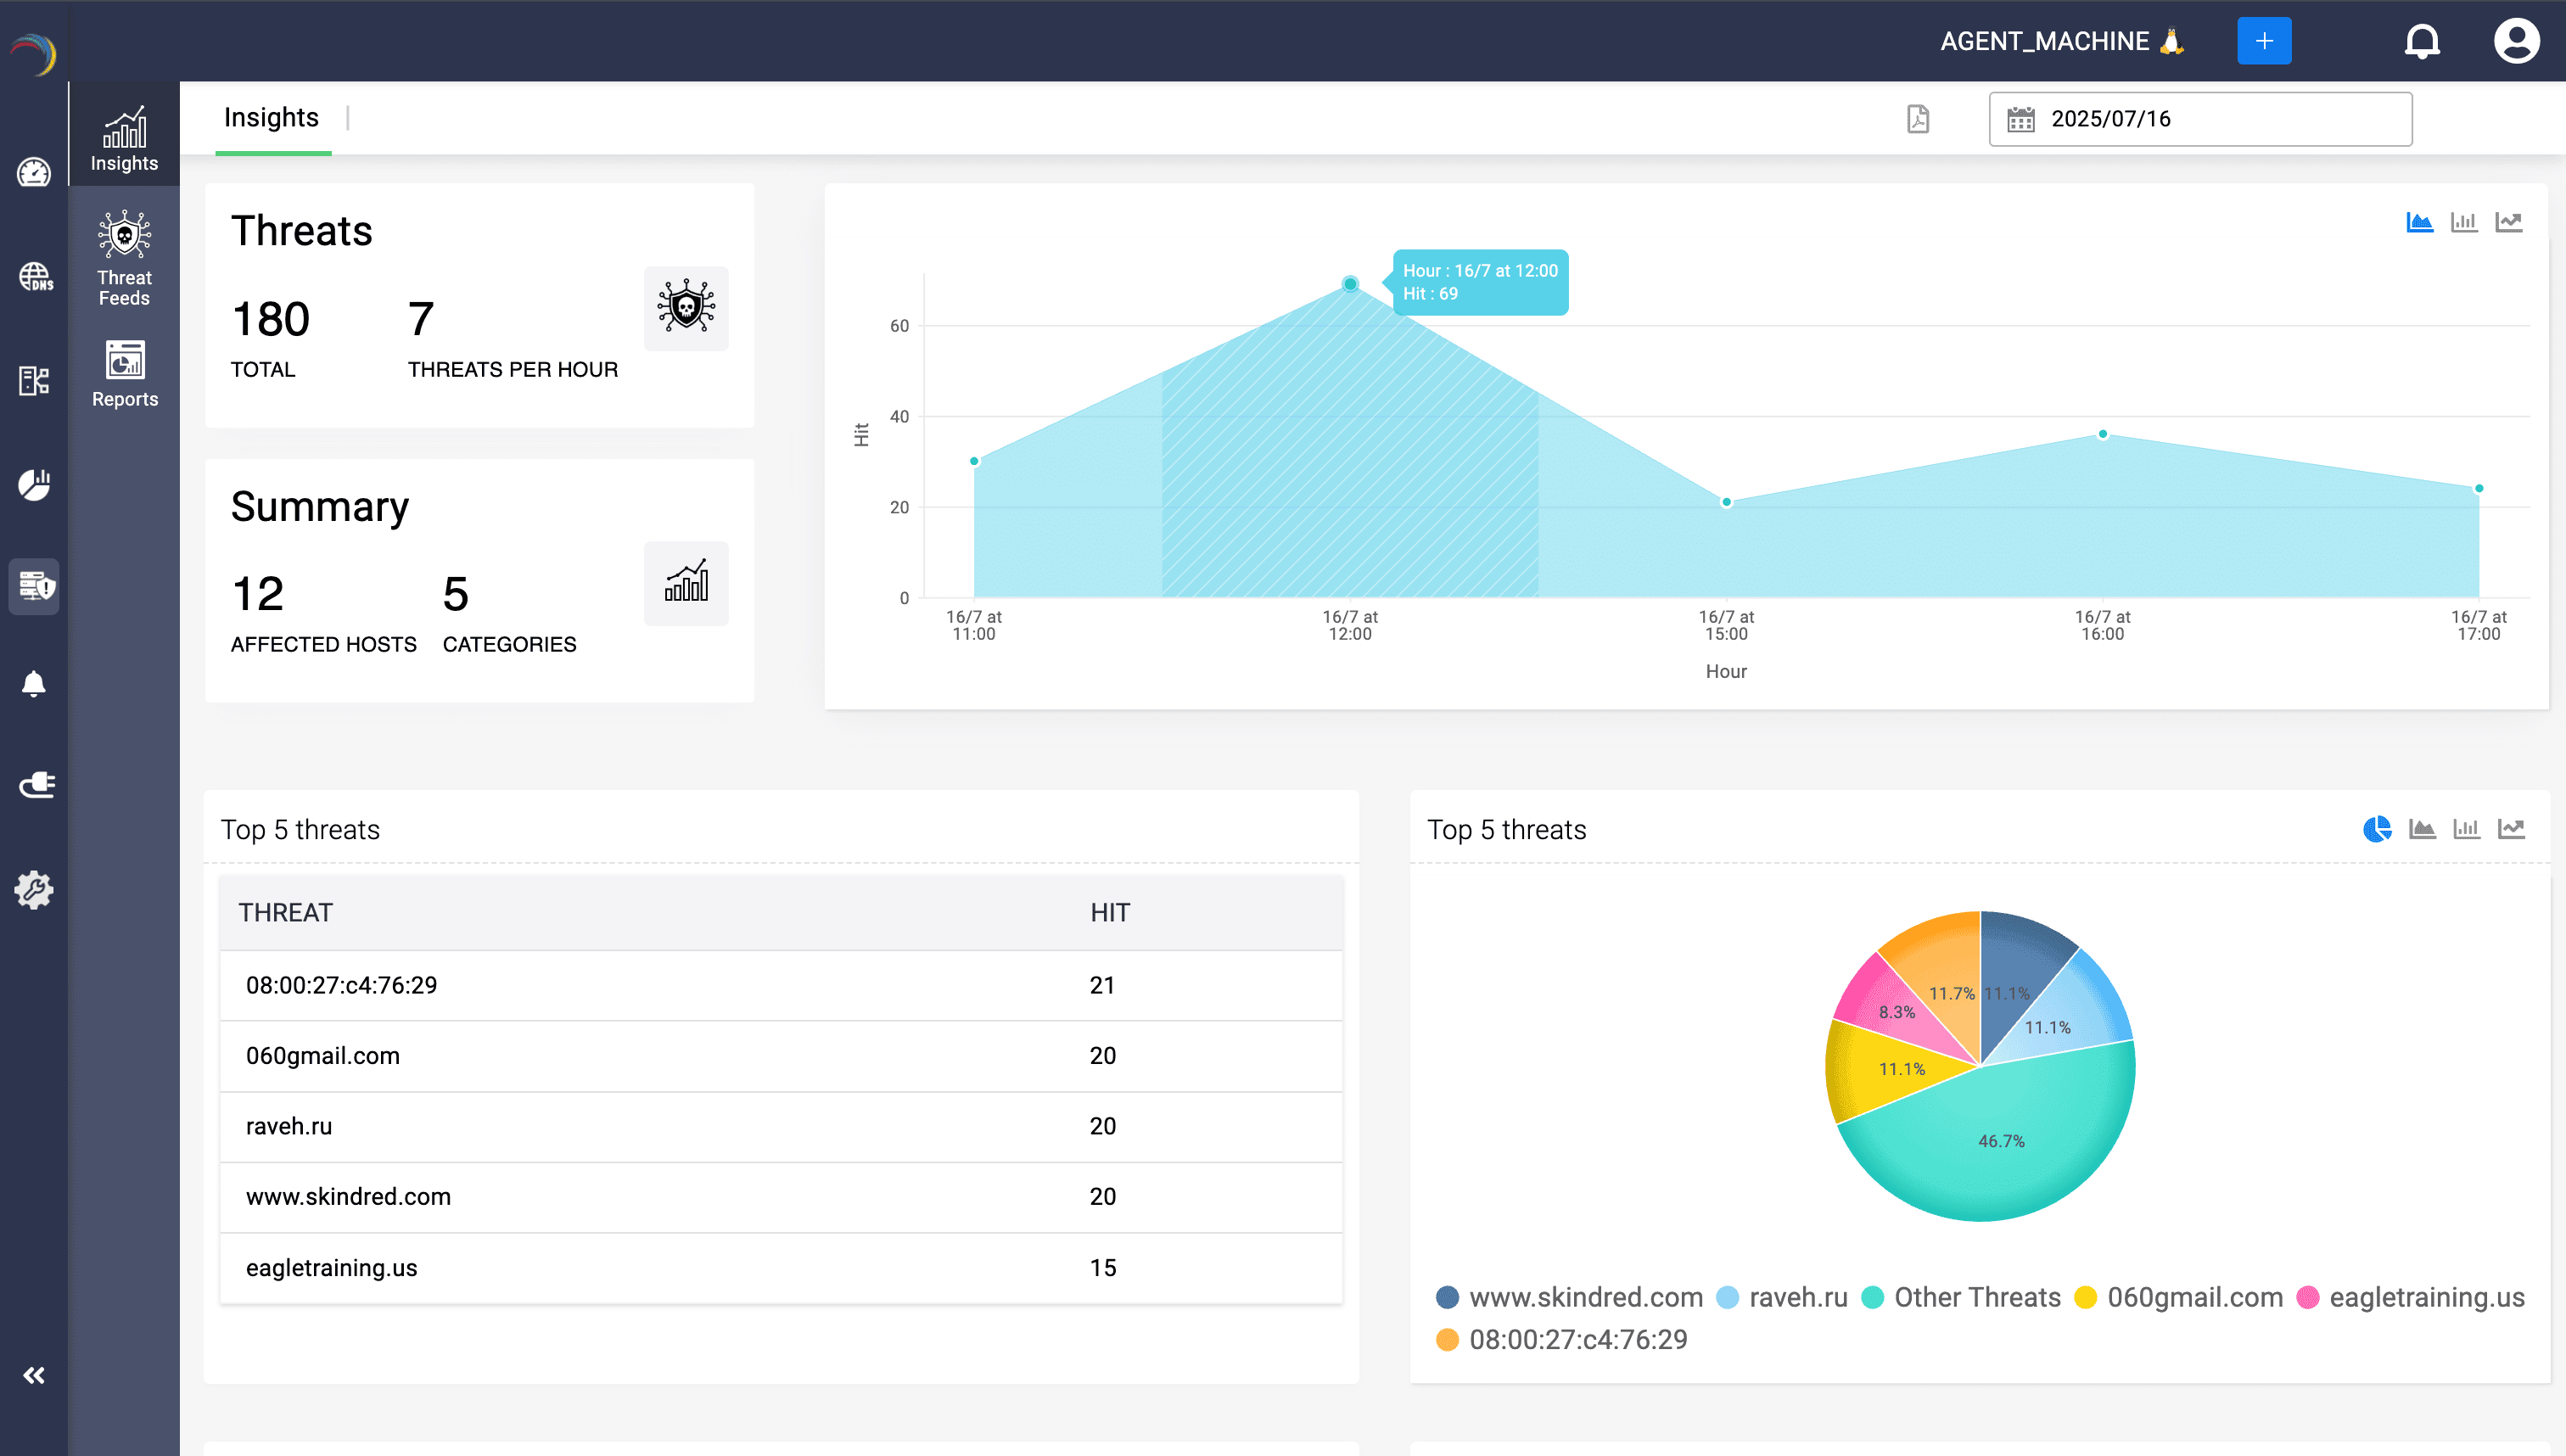
Get started with Streamlit! Set up your development environment and learn the fundamental concepts, and start coding! Develop your Streamlit app! Our API reference explains each Streamlit function with examples. Dive deep into all of our features with conceptual guides. Try out our step-by-step tutorials. Deploy your Streamlit app! Streamlit Community Cloud our free platform for deploying and sharing Streamlit apps. Streamlit in Snowflake is an enterprise-class solution where you can house your data and apps in one, unified, global system. Explore all your options! Figure 3: Threat intelligence dashboard 2. System Architecture & Core Working Principles Knowledge base is a self-serve library of tips, tricks, and articles that answer your questions about creating and deploying Streamlit apps.
Set position="left" or position="right" on st.dialog to open it as a full-height side drawer. Use the alt parameter to give images, media, charts, maps, and dataframes an accessible name for screen readers. st.echarts_chart renders Apache ECharts options with Streamlit theming. Pass a dict, a JSON string, or a pyecharts chart. Use async / await and popular async libraries directly in your Streamlit apps. The caching decorators work with async def functions too.
Set parallel=True on st.fragment to run independent fragments concurrently during full-app reruns. Refresh expired cached values in the background while your app continues serving the previous value. Streamlit is more than just a way to make data apps, it's also a community of creators that share their apps and ideas and help each other make their work better. Please come join us on the community forum. We love to hear your questions, ideas, and help you work through your bugs — stop by today! A threat intelligence dashboard should answer two questions: what is being exploited right now, and which indicators deserve attention today. This walkthrough builds a small one that runs on a laptop with Python’s standard library and SQLite. It ingests the CISA Known Exploited Vulnerabilities (KEV) catalog, enriches it with EPSS scores, ingests indicator feeds in the ThreatFox export shape, and serves a dashboard on localhost. The focus is on the parts that make or break a pipeline like this: deduplication, indicator aging, TLP handling, false positives and feed rate limits. It is defensive tooling: it only consumes and displays public intelligence.
The full platforms are real options. As of early October 2026, MISP’s latest GitHub release is v2.5.48, OpenCTI’s Community Edition is Apache 2.0 (its Enterprise Edition features ship in the same repository under a separate Filigran licence), and OpenSearch’s newest Docker tag is 3.9.0. OpenSearch (Apache 2.0) is the choice if you want an Elasticsearch-style store without licence tiers. But each platform brings a database, a cache or a broker, and one SQLite file is enough for a single analyst or small team. The schema below maps cleanly onto OpenSearch later.
“Real time” here means polling cadence: KEV changes a few times a week, and the page re-queries the API every 30 seconds. The project is five files: ti.py (storage, fetching, ingest, CLI), sample_feed.py , server.py , allowlist.txt and a static/ folder with the page.
3. Software Implementation, Frameworks & Protocols The dedup key is UNIQUE (ioc_type, value) . Everything else follows from it: a second report of the same indicator becomes an upsert, and a separate indicator_sources table records which feeds reported it, so corroboration is a count rather than a duplicate row. feed_state remembers each feed’s validators and the earliest time we are allowed to fetch it again.
TTL_DAYS is policy, not fact: infrastructure indicators go stale quickly because hosting gets reassigned, while file hashes keep their meaning, so tune these to your tolerance for noise. Three behaviours keep you out of trouble with feed operators: conditional requests, a minimum interval and obeying Retry-After . The next block implements all three.
I checked this three ways. A second kev run inside the hour printed “next fetch allowed in 3563s, skipping”. A run with --force sent the stored validators and got “not modified”. And a throwaway local stub that always answered 429 with Retry-After: 120 made fetch_feed return nothing and schedule the next attempt 120 seconds out. The 429 path was exercised against the stub only.
KEV entries are not immutable. dueDate and knownRansomwareCampaignUse can change after an entry is first published (361 of the 1,734 entries were flagged “Known” when I ran this), so the upsert must update those columns instead of ignoring conflicts. EPSS scores refresh daily, so after the first fill only entries added in the last 30 days are re-queried, in batches of 100 with a one second pause.
The first run fetched the catalog and enriched all 1,734 CVEs in about 38 seconds of wall time, almost all of it the pauses between 18 EPSS batches. Normalize before you key. C2-Alpha.Sample.Example. and c2-alpha.sample.example are the same domain, and hxxp:// is just a defanged http:// . The code below lowercases domains and hashes, lowercases only the scheme and host of URLs (paths are case sensitive), and drops fragments.
The upsert encodes the merge rules in one statement. First seen takes the minimum, last seen the maximum, confidence the maximum, and TLP the more restrictive of the two labels (TLP 2.0 order: CLEAR, GREEN, AMBER, AMBER+STRICT, RED). The sightings counter only increases when a report carries a newer last_seen , which makes re-ingesting the same file idempotent. Expiry is last_seen plus the type’s TTL, so a fresh sighting extends an indicator’s life.
Aging is computed at query time rather than by a cleanup job. The dashboard’s effective confidence decays linearly from the reported value to zero across the indicator’s life: confidence * remaining_life / total_life . An indicator reported at 89 that is a third of the way through its 30 day life ranks at about 58. Nothing is deleted until you run prune . Suppressed rows are kept so you can audit what was hidden. Note that the allowlist applies to domain indicators only.
Malware is regularly served from legitimate platforms, so a URL on raw.githubusercontent.com must stay visible even though the domain itself is allowlisted. This generator emits ThreatFox-shaped JSON with timestamps relative to now, so the aging behaviour is visible on any day. It includes a duplicate with different casing, an expired domain, a private IP, an allowlisted domain, a URL on an allowlisted host, a half-aged indicator and an empty record; --internal emits a second feed overlapping one domain. Hostnames use the reserved .example TLD, so nothing points at real infrastructure.
The server uses only the standard library. It binds to 127.0.0.1 , opens SQLite read-only (WAL mode lets it read while an ingest writes), validates max_tlp against the known labels instead of interpolating user input, and sends a strict Content-Security-Policy. The SQL fragments that get formatted into queries are built from constants in the code, never from request data.
4. Practical Deployment, Analysis & Case Studies Feed content is attacker-influenced, so the page builds every cell with textContent , never innerHTML , and shows indicators defanged so a stray click cannot fetch a payload. The two IOC ingests printed this, and re-running the first one printed the same counts without creating duplicates: Open http://127.0.0.1:8080/ . After the steps above the tiles showed 1,734 KEV entries, 18 active indicators, 1 expired and 3 suppressed. At the default CLEAR level the AMBER indicators are hidden; switching the selector to AMBER raised the active count to 20, and c2-alpha[.]sample[.]example appeared with TLP AMBER, confidence 90 (the higher of its two reports), two sources and an effective score of 87. The console showed no CSP violations in the one browser I used.
Stop the server and delete ti.db , ti.db-wal and ti.db-shm ; nothing else was installed. To scale up, keep the same normalization and key rules but index into OpenSearch using a hash of type and value as the document ID, which gives you the same upsert-based dedup. Not covered in this walkthrough, and not run by me: the authenticated abuse.ch feeds, OpenSearch, MISP, OpenCTI, Grafana, scheduling under cron or systemd, and any Python version other than 3.12.4.
A full-stack analytics solution designed to monitor, analyze, and respond to cybersecurity threats across global networks. This project processes over 200,000+ threat logs to uncover patterns in attack types, severity levels, response actions, and geographic distribution—empowering SOC teams with predictive insights and real-time dashboards. Cybersecurity operations demand rapid, data-driven decision-making. This project delivers an end-to-end threat intelligence platform that enables: Analyzed 200K+ global threat logs to uncover patterns in attack types, severity, and response actions. Built predictive models and deployed a Streamlit dashboard with SQL integration. Visualized insights using Power BI to support SOC decision-making as a Data Analyst.
A modern cybersecurity dashboard built using Python , Streamlit , Machine Learning , and Threat Intelligence Analytics . This project helps monitor cyber threats, visualize attack trends, detect anomalies, and predict threat severity using AI models. Uses Isolation Forest Algorithm to identify suspicious threat activities and anomalies. An interactive Cyber Security Data Analytics Dashboard built using Python , Streamlit , and Machine Learning to analyze cyber attack datasets, visualize threat intelligence, detect anomalies, and generate actionable security insights.
The Cyber Attack Analysis & Threat Intelligence Platform is a modern Streamlit-based dashboard that transforms raw cybersecurity incident logs into a complete Security Operations Center (SOC) Command Center . 5. Performance Evaluation & Extended Technical Observations The dashboard gracefully handles missing columns and skips unsupported visualizations automatically.
An interactive Cyber Security Data Analytics Dashboard built with Python and Streamlit to analyze cyber attack data, visualize threat patterns, identify security insights, and support data-driven cybersecurity decision-making. Streamlit turns Python scripts into shareable web apps in minutes — no HTML, CSS, or JavaScript required. For data analysts, it's the fastest way to move from a Jupyter notebook to a live, interactive dashboard that stakeholders can actually use.
Power BI and Tableau are excellent BI tools, but they have a hard ceiling: if your stakeholder wants something that Power BI can't do — custom ML predictions, dynamic SQL queries, API integrations — you're stuck. Streamlit removes that ceiling. If you can write it in Python, you can put it in a Streamlit app. The key insight is that Streamlit re-runs your entire script top to bottom whenever a user interacts with a widget. This sounds inefficient but is actually elegant — your app logic stays in pure Python, with no callback hell, no state management boilerplate, and no JavaScript.
Streamlit is not a replacement for Power BI or Tableau — it's what you reach for when your analysis needs to become a product: a live tool that non-analysts can interact with, not just a static report they read once. That's a fully functional file explorer in 12 lines of Python. Streamlit handles the HTTP server, file upload UI, and data rendering automatically.
Streamlit integrates natively with SQLAlchemy, which means you can connect directly to PostgreSQL, BigQuery, or any other database your team uses: Streamlit 1.30+ includes st.chat_message and st.chat_input components that make it trivial to add LLM-powered chat to any data app: Streamlit Cloud offers free hosting for public GitHub repositories. Deployment takes 3 steps: Your app is live at yourusername-appname.streamlit.app in under 2 minutes. For private data, use Streamlit Community Cloud with private repos, or self-host on a VPS with Docker.
Excited to share my latest project: AI-Driven Threat Intelligence Dashboard! I built a real-time dashboard that turns raw threat data into actionable insights — like a SOC co-pilot. Here’s what I did: I Key Highlights & Steps: Collected and generated threat data (IPs, attack types, risk scores). Implemented AI-based risk analysis to classify threats into High / Medium / Low severity. Created a professional dashboard UI using Streamlit, showing real-time threat metrics and tables. Designed the interface with a dark hacker-style theme, giving a real SOC look and feel. Simulated real-world cybersecurity workflows for ransomware, malware, phishing, and C2 infrastructure threats. Ensured the project is fully offline-capable, so it works anywhere for learning and demos. I Skills & Tools Used: Python | Streamlit | JSON | AI logic for risk prioritization | Data visualization | Cybersecurity concepts This project helped me understand SOC operations, threat prioritization, and cybersecurity analytics in a practical way. #CyberSecurity #AI #ThreatIntelligence #SOC #Python #DataVisualization #SOCAnalyst #RealTimeMonitoring #CyberDefense Harvested Online Documentation & Reference Sources • https://aneshraj-d96.github.io/Threat-Intelligence-Dashboard-/ • https://github.com/nelsonfoster-216/streamlit-cybersecurity-dashboard • https://github.com/nelsonfoster-216/streamlit-cybersecurity-dashboard/blob/master/README.md • https://docs.streamlit.io/ • https://codezup.com/building-a-real-time-threat-intelligence-dashboard-with-open-source-tools/ • https://github.com/aneshraj-d96/Threat-Intelligence-Dashboard- • https://github.com/codebyRamzi/threat-intelligence-dashboard • https://github.com/dhanush8m/cyber-security-data-analytics-dashboard • https://isachenko-andrii.github.io/articles/2026-07-20-streamlit-for-data-analysts.html • https://www.linkedin.com/posts/abhishek-kumar-52609829b_cybersecurity-ai-threatintelligence-activity-7419764466650861 568-NiPu
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Threat Intelligence Dashboard Using Python And Streamlit.
[*] Metasploit Scan Running on Target Subnet for Threat Intelligence Dashboard Using Python And Streamlit... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |