Complete Technical Paper Content — Threshold Cryptography Based Secure Secret Sharing Scheme
Overview & System Context
Threshold Cryptography Based Secure Secret Sharing Scheme: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9521 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Secret sharing (also called secret splitting) refers to methods for distributing a secret among a group, in such a way that no individual holds any intelligible information about the secret, but when a sufficient number of individuals combine their 'shares', the secret may be reconstructed. Whereas insecure secret sharing allows an attacker to gain more information with each share, secure secret sharing is 'all or nothing' (where 'all' means the necessary number of shares). In one type of secret sharing scheme there is one dealer and n players. The dealer gives a share of the secret to the players, but only when specific conditions are fulfilled will the players be able to reconstruct the secret from their shares. The dealer accomplishes this by giving each player a share in such a way that any group of t (for threshold) or more players can together reconstruct the secret but no group of fewer than t players can. Such a system is called a (t, n)-threshold scheme (sometimes it is written as an (n, t)-threshold scheme). Secret sharing was invented independently by Adi Shamir and George Blakley in 1979.
Each share of the secret must be at least as large as the secret itself. This result is based in information theory, but can be understood intuitively. Given t − 1 shares, no information whatsoever can be determined about the secret. Thus, the final share must contain as much information as the secret itself. There is sometimes a workaround for this limitation by first compressing the secret before sharing it, but this is often not possible because many secrets (keys for example) look like high-quality random data and thus are hard to compress. All secret-sharing schemes use random bits for constructing the shares. Otherwise, with a deterministic scheme, a player could deduce information about the secret by brute-forcing all possible secrets and running the deterministic scheme. To distribute a one-bit secret shares with a threshold of t shares, t − 1 random bits are needed. To distribute a secret of b bits, entropy of (t − 1) × b bits is necessary.
Encode the secret as a binary number s of any length. For each player i, where i is one fewer than the total number of players, give a random binary number pi of the same length as s. To the player without a share, give the share calculated as pn = s ⊕ p1 ⊕ p2 ⊕ ... ⊕ pn−1, where ⊕ denotes bitwise exclusive or. The secret is the bitwise exclusive-or of all the players' numbers (pi, for 1 ≤ i ≤ n). Instead, (1) can be performed using the binary operation in any group. For example, take the cyclic group of integers with addition modulo 232, which corresponds to 32-bit integers with addition defined with the binary overflow being discarded. The secret s can be partitioned into a vector of M 32-bit integers, which we call vsecret. Then (n − 1) of the players are each given a vector of M 32-bit integers that is drawn independently from a uniform probability distribution, with player i receiving vi. The remaining player is given vn = vsecret − v1 − v2 − ... − vn−1. The secret vector can then be recovered by summing across all the players' vectors.
In this scheme, any t out of n shares may be used to recover the secret. The system relies on the idea that one can construct a unique polynomial of degree t − 1, such that each of the t points lies on the polynomial. It takes two points to define a straight line, three points to fully define a quadratic, four points to define a cubic curve, and so on. That is, it takes t points to define a polynomial of degree t − 1. The method is to create a polynomial of degree t − 1 with the secret as the first coefficient and the remaining coefficients picked at random. Next find n points on the curve and give one to each of the players. When at least t out of the n players reveal their points, there is sufficient information to fit a (t − 1)th degree polynomial to them, the first coefficient being the secret.
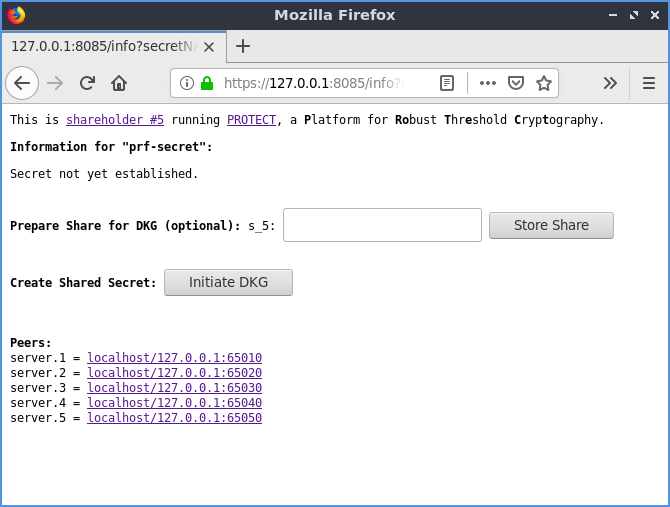
Figure 1: GitHub - jasonkresch/protect: A Platform for Robust Threshold ... Two nonparallel lines in the same plane intersect at exactly one point. Three nonparallel planes in space intersect at exactly one point. More generally, any n nonparallel (n − 1)-dimensional hyperplanes intersect at a specific point. The secret may be encoded as any single coordinate of the point of intersection. If the secret is encoded using all the coordinates, even if they are random, then an insider (someone in possession of one or more of the (n − 1)-dimensional hyperplanes) gains information about the secret since he knows it must lie on his plane. If an insider can gain any more knowledge about the secret than an outsider can, then the system no longer has information theoretic security. If only one of the n coordinates is used, then the insider knows no more than an outsider (i.e., that the secret must lie on the x-axis for a 2-dimensional system). Each player is given enough information to define a hyperplane; the secret is recovered by calculating the planes' point of intersection and then taking a specified coordinate of that intersection. Blakley's scheme is less space-efficient than Shamir's; while Shamir's shares are each only as large as the original secret, Blakley's shares are t times larger, where t is the threshold number of players. Blakley's scheme can be tightened by adding restrictions on which planes are usable as shares. The resulting scheme is equivalent to Shamir's polynomial system.
The Chinese remainder theorem can also be used in secret sharing, for it provides us with a method to uniquely determine a number S modulo k many pairwise coprime integers m 1 , m 2 , . . . , m k {\displaystyle m_{1},m_{2},...,m_{k}} , given that S < ∏ i = 1 k m i {\displaystyle S<\prod _{i=1}^{k}m_{i}} . There are two secret sharing schemes that make use of the Chinese remainder theorem, Mignotte's and Asmuth-Bloom's Schemes. They are threshold secret sharing schemes, in which the shares are generated by reduction modulo the integers m i {\displaystyle m_{i}} , and the secret is recovered by essentially solving the system of congruences using the Chinese remainder theorem.
If the players store their shares on insecure computer servers, an attacker could crack in and steal the shares. If it is not practical to change the secret, the uncompromised (Shamir-style) shares can be renewed. The dealer generates a new random polynomial with constant term zero and calculates for each remaining player a new ordered pair, where the x-coordinates of the old and new pairs are the same. Each player then adds the old and new y-coordinates to each other and keeps the result as the new y-coordinate of the secret. All of the non-updated shares the attacker accumulated become useless. An attacker can only recover the secret if he can find enough other non-updated shares to reach the threshold. This situation should not happen because the players deleted their old shares. Additionally, an attacker cannot recover any information about the original secret from the update files because they contain only random information. The dealer can change the threshold number while distributing updates, but must always remain vigilant of players keeping expired shares.
A player might lie about his own share to gain access to other shares. A verifiable secret sharing (VSS) scheme allows players to be certain that no other players are lying about the contents of their shares, up to a reasonable probability of error. Such schemes cannot be computed conventionally; the players must collectively add and multiply numbers without any individual's knowing what exactly is being added and multiplied. Tal Rabin and Michael Ben-Or devised a multiparty computing (MPC) system that allows players to detect dishonesty on the part of the dealer or on part of up to one third of the threshold number of players, even if those players are coordinated by an "adaptive" attacker who can change strategies in realtime depending on what information has been revealed.
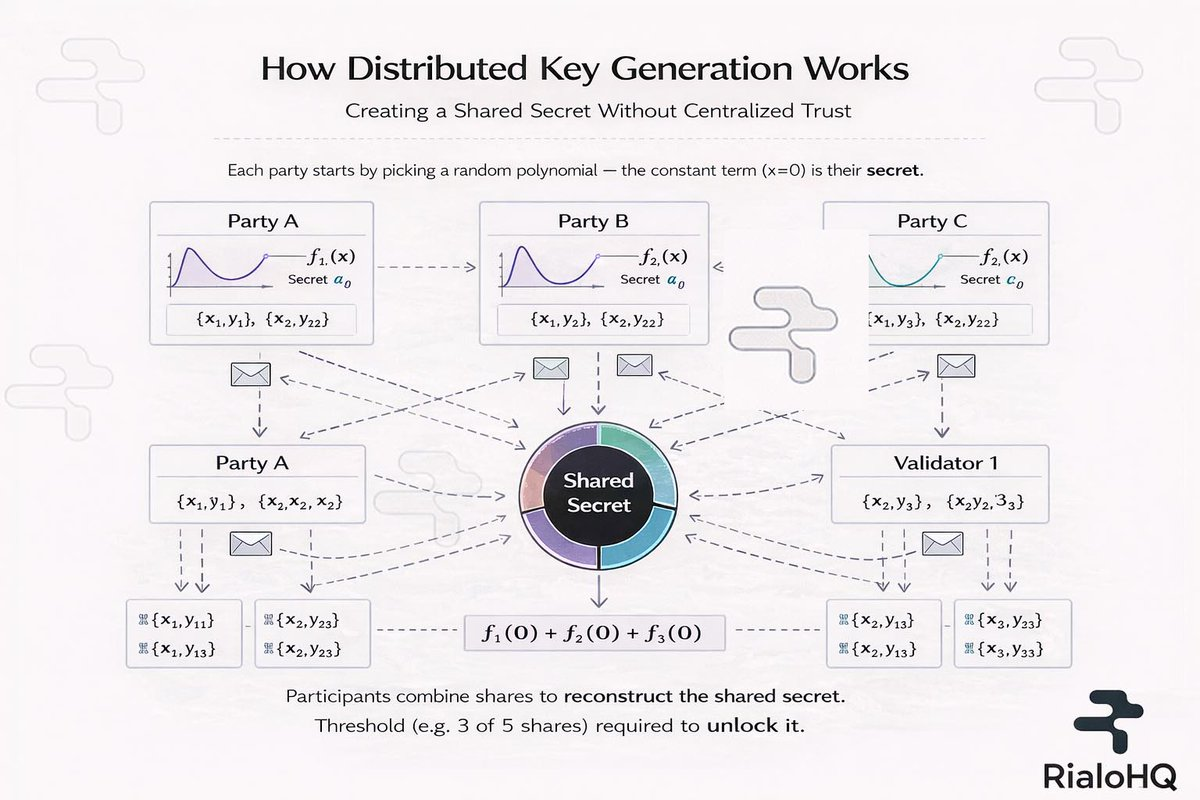
Figure 2: Here's the interesting thing about threshold cryptography that nobody ... Public-key cryptography, or asymmetric cryptography, is the field of cryptographic systems that use pairs of related keys. Each key pair consists of a public key and a corresponding private key. Key pairs are generated with algorithms based on mathematical problems termed one-way functions. Security of public-key cryptography depends on keeping the private key secret; the public key can be openly distributed without compromising security. There are many kinds of public-key cryptosystems, with different security goals, including digital signature, Diffie–Hellman key exchange, public-key key encapsulation, and public-key encryption. Public key algorithms are fundamental security primitives in modern cryptosystems, including applications and protocols that offer assurance of the confidentiality and authenticity of electronic communications and data storage. They underpin numerous Internet standards, such as Transport Layer Security (TLS), SSH, S/MIME, and PGP. Compared to symmetric cryptography, public-key cryptography can be too slow for many purposes, so these protocols often combine symmetric cryptography with public-key cryptography in hybrid cryptosystems.
In a digital signature system, a sender can use a private key together with a message to create a signature. Anyone with the corresponding public key can verify whether the signature matches the message, but a forger who does not know the private key cannot generate any message/signature pair that will pass verification with the public key.For example, a software publisher can create a signature key pair and include the public key in software installed on computers. Later, the publisher can distribute an update to the software signed using the private key, and any computer receiving an update can confirm it is genuine by verifying the signature using the public key. As long as the software publisher keeps the private key secret, even if a forger can distribute malicious updates to computers, they cannot convince the computers that any malicious updates are genuine. In a public-key encryption system, anyone with a public key can encrypt a message, yielding a ciphertext, but only those who know the corresponding private key can decrypt the ciphertext to obtain the original message.For example, a journalist can publish the public key of an encryption key pair on a website so that sources can send secret messages to the news organization in ciphertext. Only the journalist who knows the corresponding private key can decrypt the ciphertexts to obtain the sources' messages—an eavesdropper reading email on its way to the journalist cannot decrypt the ciphertexts.However, public-key encryption does not conceal metadata like what computer a source used to send a message, when they sent it, or how long it is. Public-key encryption on its own also does not tell the recipient anything about who sent a message—it just conceals the content of the message. Applications built on public-key cryptography include authenticating web servers with TLS, digital cash, password-authenticated key agreement, authenticating and concealing email content with OpenPGP or S/MIME, and time-stamping services and non-repudiation protocols. One important issue is confidence or proof that a particular public key is authentic, i.e., that it is correct and belongs to the person or entity claimed, and has not been tampered with or replaced by some (perhaps malicious) third party. There are several possible approaches to addressing this issue, including: A public key infrastructure (PKI), in which one or more third parties, known as certificate authorities, certify ownership of key pairs. TLS relies upon this. This implies that the PKI system (software, hardware, and management) can be trusted by all involved. A web of trust decentralizes authentication by using individual endorsements of links between a user and their public key. PGP uses this approach, in addition to lookup in the domain name system (DNS). The DKIM system for digitally signing emails also uses this approach.
I judged it most important for military use ... if you can share your key rapidly and electronically, you have a major advantage over your opponent. Only at the end of the evolution from Berners-Lee designing an open internet architecture for CERN, its adaptation and adoption for the Arpanet ... did public key cryptography realise its full potential. These discoveries were not publicly acknowledged until the research was declassified by the British government in 1997.
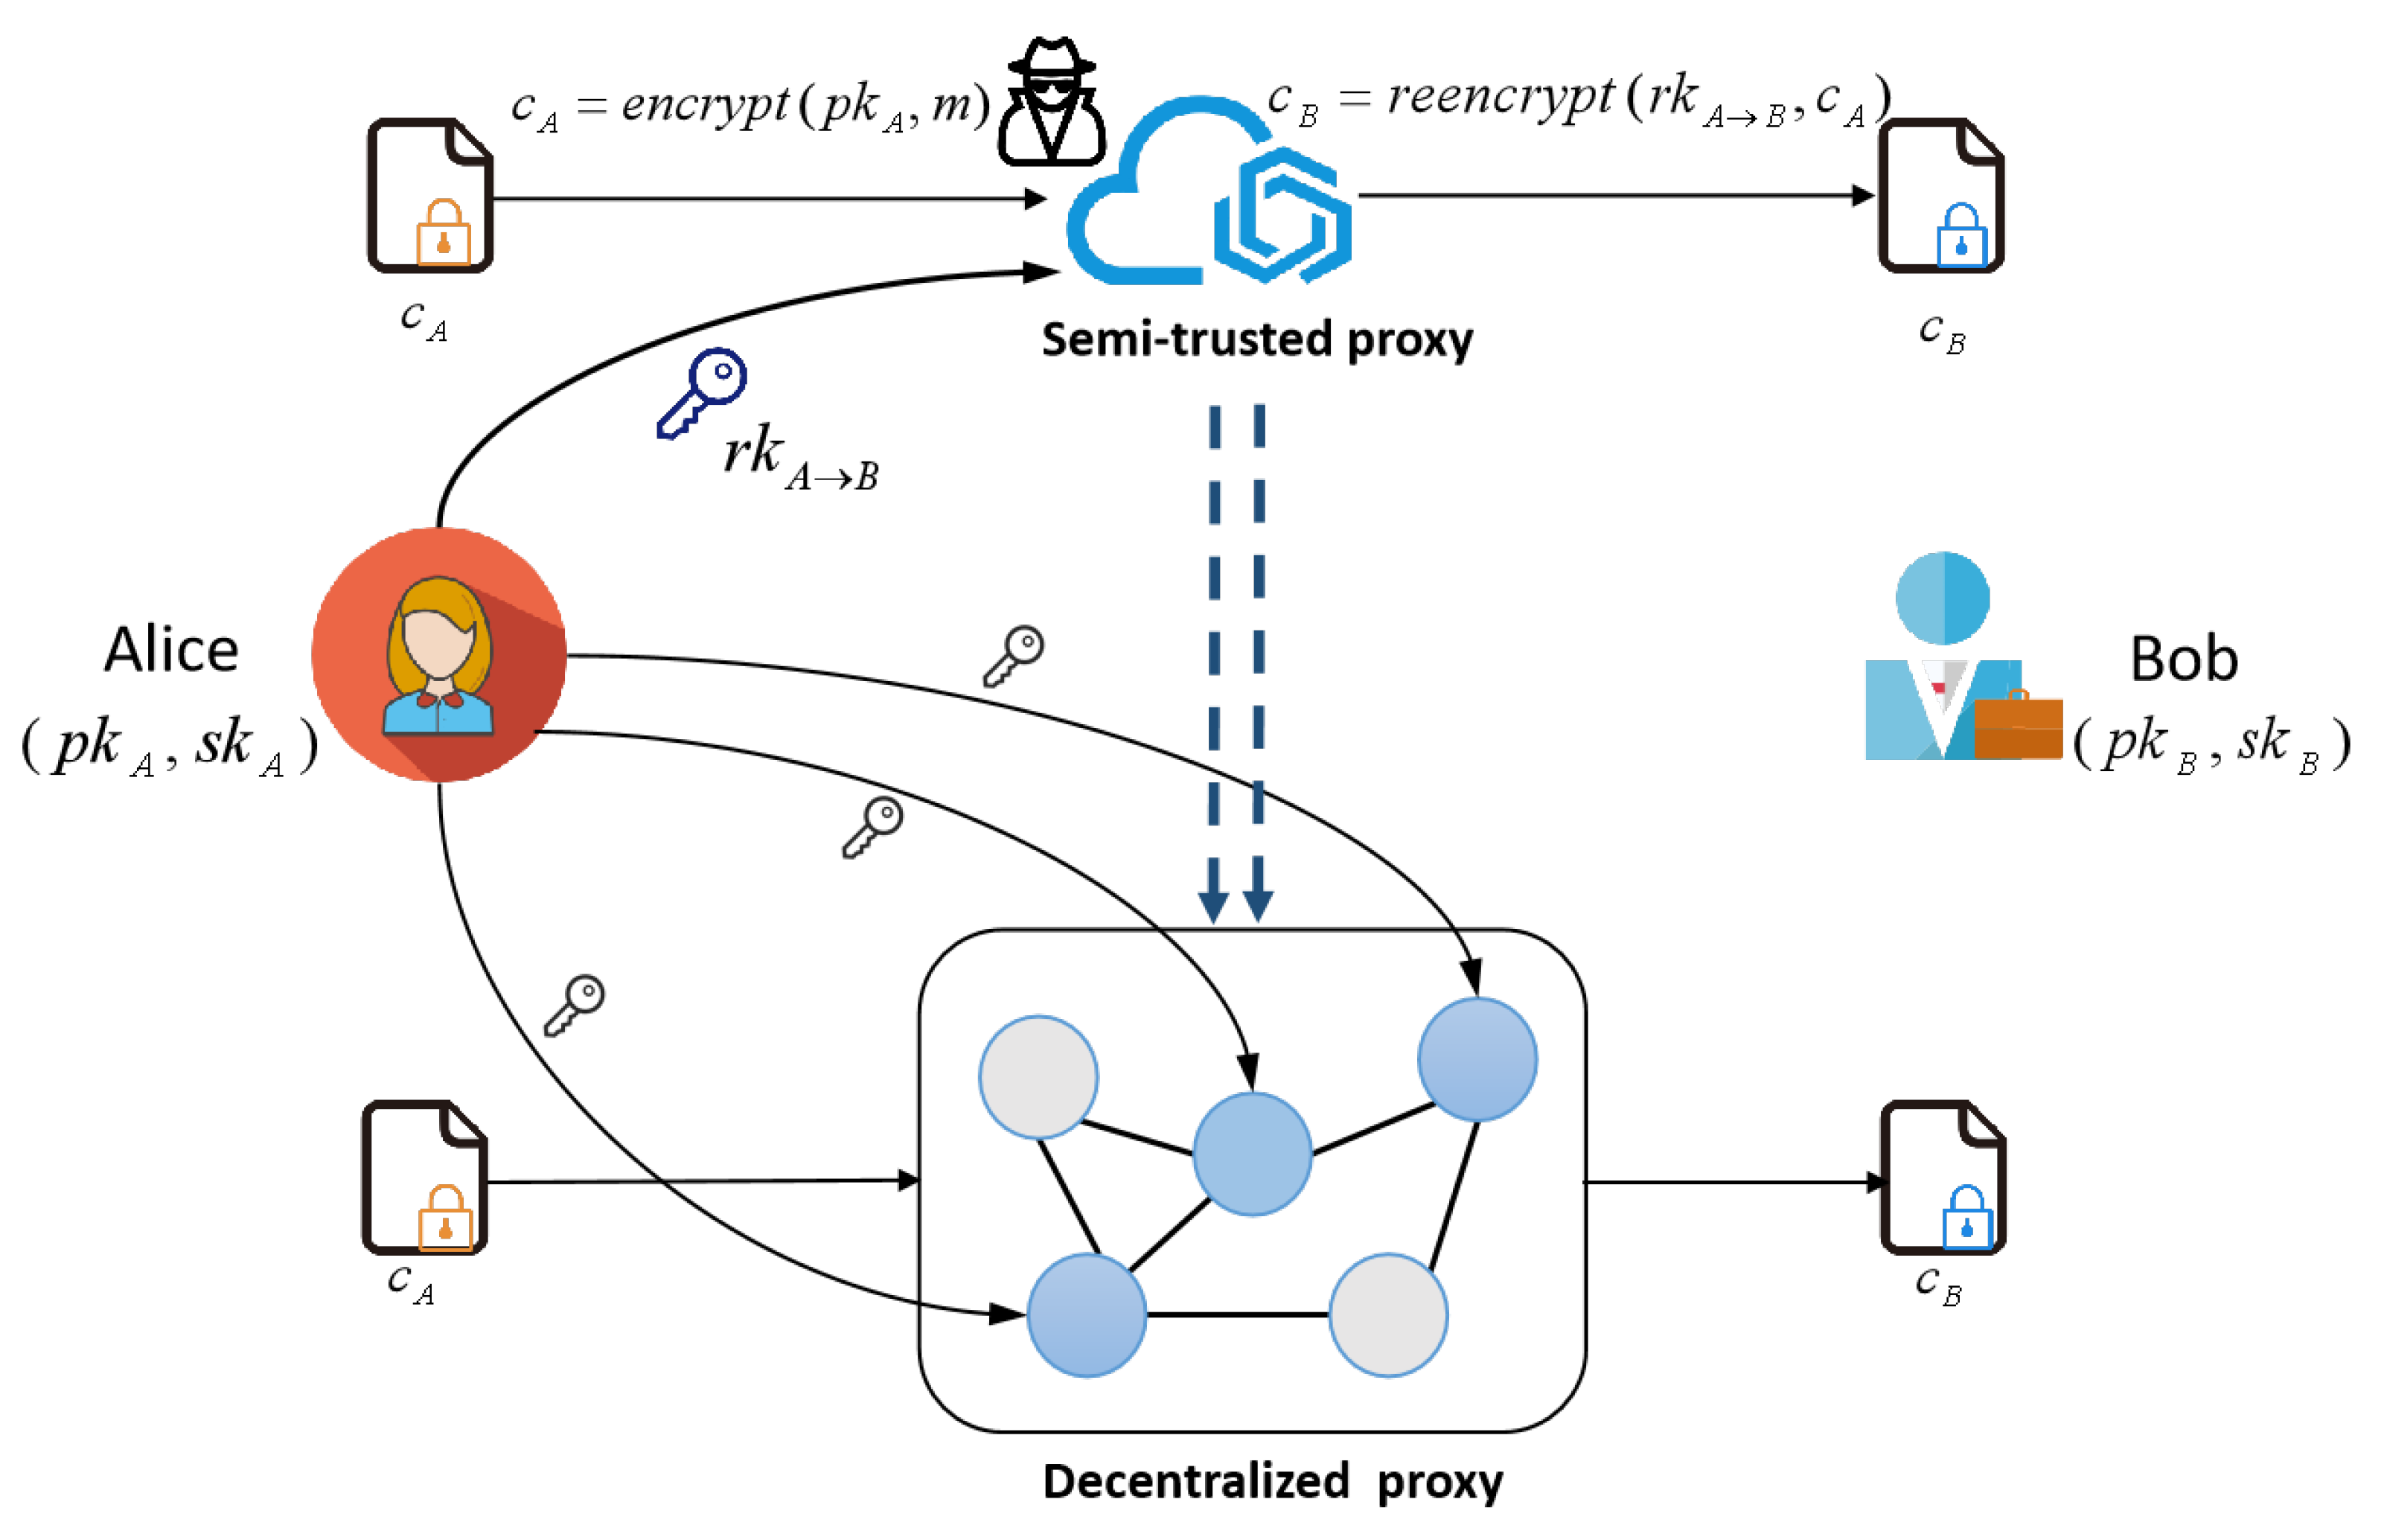
Figure 3: A Threshold Proxy Re-Encryption Scheme for Secure IoT Data Sharing ... Diffie–Hellman key exchange protocol DSS (Digital Signature Standard), which incorporates the Digital Signature Algorithm ElGamal Elliptic-curve cryptography Elliptic Curve Digital Signature Algorithm (ECDSA) Elliptic-curve Diffie–Hellman (ECDH) Ed25519 and Ed448 (EdDSA) X25519 and X448 (ECDH/EdDH) Various password-authenticated key agreement techniques Paillier cryptosystem RSA encryption algorithm (PKCS#1) Cramer–Shoup cryptosystem YAK authenticated key agreement protocol Examples of asymmetric key algorithms not yet widely adopted include: NTRUEncrypt cryptosystem Kyber McEliece cryptosystem Examples of notable – yet insecure – asymmetric key algorithms include: Merkle–Hellman knapsack cryptosystem Examples of protocols using asymmetric key algorithms include: S/MIME GPG, an implementation of OpenPGP, and an Internet Standard EMV, EMV Certificate Authority IPsec PGP ZRTP, a secure VoIP protocol Transport Layer Security standardized by IETF and its predecessor Secure Socket Layer SILC SSH Bitcoin Off-the-Record Messaging SM2 (China, elliptic curve) SM9 (China, identity-based) GOST R 34.10-2012 (Russia, elliptic curve signatures) EC-KCDSA (South Korea, elliptic curve signatures) DSTU 4145 (Ukraine, elliptic curve) Post-quantum cryptography (PQC), sometimes referred to as quantum-proof, quantum-safe, or quantum-resistant, is the development of cryptographic algorithms (usually public-key algorithms) that are currently thought, but not proven, to be secure against a cryptanalytic attack by a quantum computer. Most widely used public-key algorithms rely on the difficulty of one of three mathematical problems: the integer factorization problem, the discrete logarithm problem, or the elliptic-curve discrete logarithm problem. All of these problems could be easily solved on a sufficiently powerful quantum computer running Shor's algorithm or possibly alternatives. As of 2026, quantum computers lack the processing power to break widely used cryptographic algorithms; however, because of the length of time required for migration to quantum-safe cryptography, cryptographers are already designing new algorithms to prepare for Y2Q or "Q-Day", the day when current algorithms will be vulnerable to quantum computing attacks. Mosca's theorem provides the risk analysis framework that helps organizations identify how quickly they need to start migrating. Their work has gained attention from academics and industry through the PQCrypto conference series hosted since 2006, several workshops on Quantum Safe Cryptography hosted by the European Telecommunications Standards Institute (ETSI), and the Institute for Quantum Computing. The rumoured existence of widespread harvest now, decrypt later programs has also been seen as a motivation for the early introduction of post-quantum algorithms, as data recorded now may still remain sensitive many years into the future. In contrast to the threat quantum computing poses to current public-key algorithms, most current symmetric cryptographic algorithms and hash functions are considered to be relatively secure against attacks by quantum computers. While the quantum Grover's algorithm does speed up attacks against symmetric ciphers, doubling the key size can effectively counteract these attacks. Thus post-quantum symmetric cryptography does not need to differ significantly from current symmetric cryptography. In 2024, the U.S. National Institute of Standards and Technology (NIST) released final versions of its first three Post-Quantum Cryptography Standards.
This approach includes cryptographic systems such as learning with errors, ring learning with errors (ring-LWE), the ring learning with errors key exchange and the ring learning with errors signature, the older NTRU or GGH encryption schemes, and the newer NTRU signature and BLISS signatures. Some of these schemes like NTRU encryption have been studied for many years without anyone finding a feasible attack. Others like the ring-LWE algorithms have proofs that their security reduces to a worst-case problem. The Post-Quantum Cryptography Study Group sponsored by the European Commission suggested that the Stehle–Steinfeld variant of NTRU be studied for standardization rather than the NTRU algorithm. At that time, NTRU was still patented. Studies have indicated that NTRU may have more secure properties than other lattice based algorithms. Two lattice-based algorithms, ML-KEM (commonly known as Kyber) and ML-DSA (commonly known as Dilithium) were among the first post-quantum algorithms standardised by NIST.
This includes cryptographic systems such as the Unbalanced Oil and Vinegar signature scheme which is based on the difficulty of solving systems of multivariate equations. Various attempts to build secure multivariate equation encryption schemes have been broken, notably the Rainbow signature. This includes cryptographic systems such as Lamport signatures, the Merkle signature scheme, the XMSS, the SPHINCS, the WOTS and the SPHINCS+ schemes. Hash based digital signatures were invented in the late 1970s by Ralph Merkle and have been studied ever since as an interesting alternative to number-theoretic digital signatures like RSA and DSA. Their primary drawback is that for any hash-based public key, there is a limit on the number of signatures that can be signed using the corresponding set of private keys. This fact reduced interest in these signatures until interest was revived due to the desire for cryptography that was resistant to attack by quantum computers. There appear to be no patents on the Merkle signature scheme and there exist many non-patented hash functions that could be used with these schemes. The stateful hash-based signature scheme XMSS developed by a team of researchers under the direction of Johannes Buchmann is described in RFC 8391. Note that all the above schemes are one-time or bounded-time signatures. Moni Naor and Moti Yung invented UOWHF hashing in 1989 and designed a signature based on hashing (the Naor-Yung scheme) which can be unlimited-time in use (the first such signature that does not require trapdoor properties).
In some versions of Ring-LWE there is a security reduction to the shortest-vector problem (SVP) in a lattice as a lower bound on the security. The SVP is known to be NP-hard. Specific ring-LWE systems that have provable security reductions include a variant of Lyubashevsky's ring-LWE signatures defined in a paper by Güneysu, Lyubashevsky, and Pöppelmann. The GLYPH signature scheme is a variant of the Güneysu, Lyubashevsky, and Pöppelmann (GLP) signature which takes into account research results that have come after the publication of the GLP signature in 2012. Another Ring-LWE signature is Ring-TESLA. There also exists a "derandomized variant" of LWE, called Learning with Rounding (LWR), which yields "improved speedup (by eliminating sampling small errors from a Gaussian-like distribution with deterministic errors) and bandwidth". While LWE uses the addition of a small error to conceal the lower bits, LWR uses rounding for the same purpose.
Unbalanced Oil and Vinegar signature schemes are asymmetric cryptographic primitives based on multivariate polynomials over a finite field I F {\displaystyle \mathbb {F} } I. Bulygin, Petzoldt, and Buchmann have shown a reduction of generic multivariate quadratic UOV systems to the NP-Hard multivariate quadratic equation solving problem. In 2005, Luis Garcia proved that there was a security reduction of Merkle Hash Tree signatures to the security of the underlying hash function. Garcia showed in his paper that if computationally one-way hash functions exist then the Merkle Hash Tree signature is provably secure. Therefore, use of a hash function with a provable reduction of security to a known hard problem would have a provable security reduction of the Merkle tree signature to that known hard problem. The Post-Quantum Cryptography Study Group sponsored by the European Commission has recommended use of the Merkle signature scheme for long term security protection against quantum computers.
The McEliece Encryption System has a security reduction to the syndrome decoding problem (SDP). The SDP is known to be NP-hard. The Post-Quantum Cryptography Study Group sponsored by the European Commission has recommended the use of this cryptography for long term protection against attack by a quantum computer. 2. System Architecture & Core Working Principles Security is related to the problem of constructing an isogeny between two supersingular curves with the same number of points. The most recent published investigation of the difficulty of this problem, by Delfs and Galbraith, indicates that this problem is as hard as the inventors of the key exchange suggest that it is. There is no security reduction to a known NP-hard problem.
A practical consideration on a choice among post-quantum cryptographic algorithms is the effort required to send public keys over the internet. From this point of view, the Ring-LWE, NTRU, and SIDH algorithms provide key sizes conveniently under 1 kB, hash-signature public keys come in under 5 kB, and MDPC-based McEliece takes about 1 kB. On the other hand, Goppa-based McEliece requires a nearly 1 MB key.
The fundamental idea of using LWE and Ring LWE for key exchange was proposed and filed at the University of Cincinnati in 2011 by Jintai Ding. The basic idea comes from the associativity of matrix multiplications, and the errors are used to provide the security. The paper appeared in 2012 after a provisional patent application was filed in 2012. In 2014, Peikert presented a key transport scheme following the same basic idea of Ding's, where the new idea of sending an additional 1 bit signal for rounding in Ding's construction is also used. For somewhat greater than 128 bits of security, Singh presents a set of parameters which have 6956-bit public keys for the Peikert's scheme. The corresponding private key would be roughly 14,000 bits. In 2015, an authenticated key exchange with provable forward security following the same basic idea of Ding's was presented at Eurocrypt 2015, which is an extension of the HMQV construction in Crypto2005. The parameters for different security levels from 80 bits to 350 bits, along with the corresponding key sizes are provided in the paper.
For 128 bits of security in NTRU, ntruhps2048509 with n = 509 and q = 2048 was selected in the NIST submission in September 2020. This results in a public key of 699 bytes and a corresponding private key of 935 bytes. In order to get 128 bits of security for hash based signatures to sign 1 million messages using the fractal Merkle tree method of Naor Shenhav and Wool the public and private key sizes are roughly 36,000 bits in length.
For 128 bits of security in a McEliece scheme, The European Commission's Post-Quantum Cryptography Study group recommends using a binary Goppa code of length at least n = 6960 and dimension at least k = 5413, and capable of correcting t = 119 errors. With these parameters the public key for the McEliece system will be a systematic generator matrix whose non-identity part takes k × (n − k) = 8373911 bits. The corresponding private key, which consists of the code support with n = 6960 elements from GF(213) and a generator polynomial of with t = 119 coefficients from GF(213), will be 92,027 bits in length. The group is also investigating the use of Quasi-cyclic MDPC codes of length at least n = 216 + 6 = 65542 and dimension at least k = 215 + 3 = 32771, and capable of correcting t = 264 errors. With these parameters the public key for the McEliece system will be the first row of a systematic generator matrix whose non-identity part takes k = 32771 bits. The private key, a quasi-cyclic parity-check matrix with d = 274 nonzero entries on a column (or twice as much on a row), takes no more than d × 16 = 4384 bits when represented as the coordinates of the nonzero entries on the first row. Barreto et al.
recommend using a binary Goppa code of length at least n = 3307 and dimension at least k = 2515, and capable of correcting t = 66 errors. With these parameters the public key for the McEliece system will be a systematic generator matrix whose non-identity part takes k × (n − k) = 1991880 bits. The corresponding private key, which consists of the code support with n = 3307 elements from GF(212) and a generator polynomial of t = 66 coefficients from GF(212), will be 40,476 bits in length.
For 128 bits of security in the supersingular isogeny Diffie–Hellman (SIDH) method, De Feo, Jao and Plut recommend using a supersingular curve modulo of a 768-bit prime. If one uses elliptic curve point compression, the public key will need to be no more than 8x768 or 6144 bits in length. A March 2016 paper by authors Azarderakhsh, Jao, Kalach, Koziel, and Leonardi showed how to cut the number of bits transmitted in half, which was further improved by authors Costello, Jao, Longa, Naehrig, Renes and Urbanik resulting in a compressed-key version of the SIDH protocol with public keys only 2640 bits in size. This makes the number of bits transmitted roughly equivalent to the non-quantum secure RSA and Diffie–Hellman at the same classical security level.
Older supported versions that have been removed because of the progression of the NIST Post-Quantum Cryptography Standardization Project are: Google has maintained the use of "hybrid encryption" in its use of post-quantum cryptography: whenever a relatively new post-quantum scheme is used, it is combined with a more proven, non-PQ scheme. This is to ensure that the data are not compromised even if the relatively new PQ algorithm turns out to be vulnerable to non-quantum attacks before Y2Q. This type of scheme is used in its 2016 and 2019 tests for post-quantum TLS, and in its 2023 FIDO2 key. One of the algorithms used in the 2019 test, SIKE, was broken in 2022, but the non-PQ X25519 layer (already used widely in TLS) still protected the data.
Apple's PQ3 and Signal's PQXDH are also hybrid. The NSA and GCHQ argue against hybrid encryption, claiming that it adds complexity to implementation and transition. Daniel J. Bernstein, who supports hybrid encryption, argues that the claims are bogus. This is a potential security issue, you are being redirected to https://csrc.nist.gov .
Official websites use .gov A .gov website belongs to an official government organization in the United States. Secure .gov websites use HTTPS A lock ( ) or https:// means you’ve safely connected to the .gov website. Share sensitive information only on official, secure websites. The multi-party paradigm of threshold cryptography enables threshold schemes , which apply principles of secure multiparty computation (MPC) to achieve protocols that enable a secure distribution of trust in the operation of cryptographic primitives.
Threshold schemes can be applied to NIST standardized primitives/schemes, and beyond. The technical scope of the MPTC-project includes threshold schemes (for signatures, public-key encryption/decryption, ciphers, hashing, fully-homomorphic encryption (FHE) , and key-generation), as well as auxiliary techniques (such as zero-knowledge proofs (ZKP) and other gadgets).
Note: The old " single-device track" about masked circuits for block-ciphers has become a separate project . Each NIST-organized workshop has a dedicated webpage with detailed information. These events are also listed in the " Events " page associated with the MPTC project. So far, the main publications in the project are in the form of NIST Internal Reports (NISTIR), elaborated internally at NIST and made publicly available for comments and consultation.
The MPTC project intends to drive an open and transparent process (see IR 7977 ), welcoming and considering feedback from the community of stakeholders, including researchers and practitioners in academia, industry and government. The project has received useful community feedback about the multi-party threshold setting, including the references listed below: To receive announcements pertinent to opportunities for collaboration, feedback, and workshops, consider subscribing to the MPTC-forum . The messages are publicly available at https://groups.google.com/a/list.nist.gov/g/mptc-forum An earlier related call for focused feedback on criteria for threshold schemes ( Call 2021a ) solicited anticipated comments on the following topics: scope of proposals; security idealization; security vs. adversary types; system model; threshold profiles; building blocks.
The NIST reports on threshold schemes have benefited from public comments, as described in: Standardization setting: [2019] I1.2 (TC readiness); [2020] 2a1 (MPC settings), 2a2 (composability); [2023] 1a1 (diversity). Threshold ECDSA: [2019] I4.2 , I.5.1 ( a , b , c ); [2020] 3a2 , 3a3 , 3c1 , 3c2 ; [2023] 1b3 , 1b4 . Threshold Schnorr/EdDSA: [2019] II4 ; [2020] 1b2 (MPC-based), 1b3 (prob.), 1c1 ; [2023] 1b2 (prob.).
Gadgets / building blocks: [2020]: 2b2 + 2c1 (garbled circuits), OT ( 2b1 ), PCG ( 2a3 ), PVSS ( 1a2 ); [2023] 3a1 (auth garbling), 3a2 (stacked garbling), 3a3 (garbled lookup tables), 3a4 (VOLE), 3c2 (AONT), 3c3 (VORF), 3c5 (networking). 3. Software Implementation, Frameworks & Protocols Platforms/frameworks/endeavors: [2019] I1.3 , II4.3 ; [2020] 3b3 (frameworks), 2c2 , 2c3 , 2c4 , 2c5 (MPC Alliance); [2023] 1a2 (SPDZ), [2024] 3a5 (MPC Alliance).
Theory: [2019] II4.1 (multi-signatures); [2023] 2b3 (random-oracle); [2024] 3a2 (tutorial) Others applications/comments: [2019] II4.4 ; [2020] 1b1 , 1c4 ; [2023] 1a3 , 2b1 (TLS). NIST standards related: [2019] I2.1 (approach), I6.1 (validation) I2.2 (PQC & EC); [2023] 2c1 & 2c2 (PQC), 2c3 (LWC), 2c4 (Validation), 2a0 (PEC tools), 3a0 (gadgets).
Intros about the threshold-crypto project or call: [2019] I1.1 , [2020] 1a1 ; [2023] 101 . - For NTCW 2019, indices are Xyz, with X in {I, II} (day), y in {1,…,5} (session in the day), z in {1,2,3}. - For MPTS 2020 and MPTS 2023, indices are xyz, with x in {0, 1,2,3} (day), y in {a,b,c,d} (session in the day), z in {0,…,5}. Security and Privacy: digital signatures , encryption , key management , message authentication , post-quantum cryptography , secure hashing Multi-Party Threshold Cryptography (MPTC) Project [email protected] Luís T. A. N. Brandão - NIST/Strativia [email protected] Michael Davidson - NIST René Peralta - NIST Dustin Moody - NIST Security and Privacy: digital signatures , encryption , key management , message authentication , post-quantum cryptography , secure hashing Automated Cryptographic Validation Testing | NCCoE Cryptographic Module Validation Program Cryptographic Standards and Guidelines Lightweight Cryptography Post-Quantum Cryptography Privacy-Enhancing Cryptography Threshold cryptography is a powerful and well-known technique with many applications to systems relying on distributed trust.
It has recently emerged also as a solution to challenges in blockchain: frontrunning prevention, managing wallet keys, and generating randomness. This work presents Thetacrypt , a versatile library for integrating many threshold schemes into one codebase. It offers a way to easily build distributed systems using threshold cryptography and is agnostic to their implementation language. The architecture of Thetacrypt supports diverse protocols uniformly. The library currently includes six cryptographic schemes that span ciphers, signatures, and randomness generation. The library additionally contains a flexible adapter to an underlying networking layer that provides peer-to-peer communication and a total-order broadcast channel; the latter can be implemented by distributed ledgers, for instance. Thetacrypt serves as a controlled testbed for evaluating the performance of multiple threshold-cryptographic schemes under consistent conditions, showing how the traditional micro benchmarking approach neglects the distributed nature of the protocols and its relevance when considering system performance.
Distributing cryptographic capabilities within a group of nodes is a well-known technique in resilient systems that goes back to the 1990s [ 16 ] . Based on secret sharing , the field of threshold cryptography addresses public-key cryptosystems in which only the collaboration of sufficiently many nodes may produce the cryptographic result. Private keys are protected from leaking to a minority of corrupted nodes, even if they collude, provided most remain intact. Threshold cryptography is an essential and promising technology for securing distributed systems, especially in the recent era of blockchain networks. The renewed interest in the technology is confirmed also by the ongoing NIST effort [ 35 ] to standardize them.
The tension between (static) cryptographic schemes and (dynamic) distributed algorithms makes threshold cryptography inherently complex to build. We believe that this has hampered its widespread deployment so far. Implementing cryptographic primitives is difficult in the first place because a minor mistake may compromise the security of an entire solution built on the implementation. It has therefore become common practice to standardize cryptographic libraries and to use them in a modular way across many applications; OpenSSL is the most prominent example of this development. Vulnerabilities originating from custom implementations can be reduced, optimizations within a common library, such as eliminating side-channel leakage and using hardware instructions, benefit many applications, and the scrutiny placed on a reusable codebase is amortized across many uses.
Implementing distributed cryptography poses the same technical challenges as implementing ordinary cryptosystems, but with the additional concern of handling the communication among nodes in a distributed network. Several widely used platforms that integrate threshold cryptosystems with a distributed network have recently emerged, such as the Internet Computer [ 9 ] developed by DFINITY [ 19 ] , which provides a blockchain-like public computing infrastructure, or DRAND [ 17 ] , a distributed randomness beacon that produces verifiable and unbiased randomness used by many secure services on the Internet. Moreover, Partisia Blockchain [ 36 ] provides private computation as a service using threshold cryptography. Distributed cryptography is also a prominent method to manage the private keys of cryptocurrency wallets in a resilient way [ 18 , 31 ] .
However, all these solutions realize threshold cryptosystems within their platforms and only for their target applications. Therefore, such cryptographic implementations are specific to the needs of particular deployments and domains. In particular, they cannot easily be decoupled from the underlying communication tools, but a network transport is necessary in distributed cryptography.
To remedy this situation, this work shows how to make threshold cryptography modular and to simplify its deployment. Our goal is to decouple distributed cryptography from particular applications, such that it can easily be composed with and integrated into diverse distributed protocols. Blockchain platforms offer today significant communication, coordination, and synchronization capabilities; because of their maturity, threshold-cryptographic implementations may rely on them as a black box. This allows us to focus only on the implementation of the cryptographic schemes. Several research questions arise in this context: How does one structure a common framework that encompasses multiple types of distributed cryptosystems, such as signatures, encryption, and randomness generation? How can threshold cryptography be integrated with a diverse set of distributed protocols in a modular way? What are the precise assumptions on the communication primitives and which are the interfaces for connecting to existing distributed platforms? To answer these questions, we present Thetacrypt , a distributed service for threshold cryptography. It contains implementations of the most prominent distributed cryptographic schemes and organizes them into a hierarchy according to their types and implementations.
Moreover, Thetacrypt’s modular design allows easy integration of the threshold-cryptographic algorithms with diverse distributed applications. Since Thetacrypt does not depend on a particular networking infrastructure, it may be incorporated with existing platforms that already provide the communication means to execute distributed protocols. For completeness, however, Thetacrypt also comes with its own, minimal communication layer, such that it may be deployed as a standalone service.
Thetacrypt takes care of the challenges related to correctly implementing the cryptographic primitives and handles complex, multi-round distributed schemes modularly. In this way, threshold cryptography becomes a separate component in distributed applications: it improves overall security and offers higher flexibility for application developers. To our knowledge, Thetacrypt is the first system to treat threshold cryptography as a modular component that can be integrated flexibly with multiple applications.
This work describes the structure of Thetacrypt and motivates the need for and applicability of such technology. The codebase presents a layered and modular architecture, favoring easy extensibility and different utilization modes. At a high level, it presents two different APIs that let distributed applications integrate threshold cryptography either as a black box, ignoring protocols’ cryptographic details, or in a more granular way, using it as a library of primitives and relying on the assumption of a shared secret. At its core, Thetacrypt operates on a management code that executes tasks through a common interface shared by all implemented protocols. This interface permits easy and efficient integration of new protocols in the future. The cryptographic core is also modular, functioning as a self-contained library for direct access by specific applications.
Language-agnostic interfaces for peer-to-peer and total order broadcast communication have been designed at the network layer to facilitate easy integration with a hosting platform. 4. Practical Deployment, Analysis & Case Studies We use our design as a common testbed to fairly compare implemented schemes and evaluate them under different deployment scenarios. We study how the system’s performance varies with the number of nodes, network configuration, and schemes’ cryptographic characteristics. Our results show that in small deployments, the execution time of a threshold protocol is primarily influenced by the cryptographic assumptions of the scheme. However, as the number of nodes increases, this parameter gets overshadowed by the network latency. Further, we introduce novel metrics to quantify performance imbalances among the nodes in threshold-based protocols and analyze the impact on the overall system. These metrics reveal that the trade-off between computationally intensive local processing and network latency contributes to a more balanced system. This perspective complements the traditional micro-benchmarking approach of single cryptographic primitives, providing a more comprehensive view of threshold cryptography performance.
The rest of the paper is structured as follows: Section 2 reviews threshold cryptography and also highlights practical applications of distributed cryptography in the blockchain space. Section 3 summarizes current approaches with their limitations and then describes the architecture of Thetacrypt; this section also gives the details of the implemented protocols and schemes. In Section 4 , we evaluate the performance of the service with varying numbers of nodes and different deployments. Finally, Section 5 explores related work in the literature and Section 6 concludes the paper.
Fault tolerance refers to the ability of a system to remain operational even in the presence of faulty components; it is often implemented through replication across a diverse set of nodes or parties that comprise the system. This work considers the Byzantine [ 30 ] fault model, where a fraction of the nodes may behave maliciously, and therefore aims at achieving Byzantine Fault Tolerance (BFT) .
BFT protocols are today widely used in blockchain systems. The nodes maintaining a blockchain, called validators here, produce the chain together and must agree on the order of transactions and the state of the ledger. To do so, they run a consensus protocol for every new block, implementing total-order broadcast (TOB) [ 41 ] . The operational model varies according to the assumptions on the network delay and the fraction of Byzantine nodes, which resolves into different blockchain constructions. A wide range of blockchain consensus protocols and implementations exist today [ 24 ] .
When applied to cryptosystems, fault tolerance means that control over a cryptographic system is distributed among many parties, such that the confidentiality and integrity of the service remains intact despite failure or misbehavior of a subset of the parties. This means that a set of n n parties collaborate to jointly compute a cryptographic operation based on a private key. A sufficient number or threshold of them, specifically ( t + 1 ) (t+1) or more among the n n parties, are needed to carry out an operation successfully. On the other hand, any t t or fewer parties must not learn anything about the private key. These schemes leverage the concept of secret sharing and constitute the general approach of threshold cryptography [ 16 ] .
Threshold cryptography is an active area of research and industrial development, and the Multi-Party Threshold Cryptography project of NIST is currently standardizing threshold-cryptographic protocols [ 35 ] . Threshold schemes require a setup phase for the initial distribution of the cryptographic material to the parties. This can either be done by a centralized, trusted dealer or through a distributed key-generation protocol [ 37 , 27 ] , which is run by the parties themselves. The second approach is more secure but arguably also more complex. A threshold cryptosystem ideally produces the same cryptographic outputs or consumes the same inputs as the corresponding centralized schemes.
The communication requirement is also a crucial factor. Non-interactive protocols [ 44 , 5 , 3 , 43 , 8 ] require one round of communication, allowing asynchronous execution, while interactive protocols [ 10 , 29 , 40 , 26 , 25 ] require multiple rounds, demanding a certain level of coordination. A typical interface for a non-interactive threshold scheme provides three algorithms: one for generating the share of the partial local cryptographic operation, one to verify partial results, and one to combine the partial results and to assemble the final result.
In Thetacrypt the most relevant kinds of threshold cryptographic schemes are implemented: This is a public-key encryption scheme with a distributed decryption algorithm, where only sufficiently many parties can decrypt a ciphertext. Of particular practical interest are non-interactive schemes that are provably secure against chosen-ciphertext attacks (CCA) [ 34 ] .
This is a public-key digital signature scheme, in which the signing algorithm is distributed. Any group of parties large enough can jointly create a valid signature, while a strictly smaller group cannot. Desirable properties are unforgeability [ 28 ] , a computationally bounded adversary has a negligible advantage in forging a valid signature, and robustness [ 6 , 27 ] , the protocol will produce the correct output despite misbehavior of faulty parties.
A threshold-random function produces cryptographically secure pseudorandom values based on a shared secret held by the parties. Any group smaller than the threshold cannot distinguish such outputs from truly random values, i.e., its outputs are pseudorandom . Many schemes characterize this large category: coin-tossing schemes [ 8 ] , distributed verifiable random functions (DVRFs) [ 22 ] , and, more generally, distributed randomness beacons (DRBs) [ 11 , 15 ] .
The widespread adoption of distributed systems and blockchain-based solutions has renewed interest in practical deployments of threshold cryptography. Many current projects integrate threshold schemes with blockchains. For example, threshold cryptography can be used to prevent front-running , where faulty nodes see incoming transactions before these transactions become committed and are executed [ 14 ] . By encrypting transactions with a service-wide key and letting the nodes decrypt them jointly after deciding on their order, this attack can be mitigated [ 39 , 7 , 20 ] .
Another prominent application today concerns randomness generation . Trustworthy, i.e., reliable, non-predictable, and unbiased random values are a key ingredient in many blockchain networks (e.g., for consensus) and applications running on them (e.g., for games). The Internet Computer [ 9 ] , for instance, uses distributed threshold-cryptographic randomness for its consensus [ 8 ] .
In high-security contexts, key management often involves multi-factor control, sometimes managed with hardware-security modules (HSMs), but more recently done entirely in software through threshold cryptography. Moreover, multiple commercial solutions deploy threshold cryptography for managing cryptocurrency wallets today [ 18 , 31 ] . Despite their practical appeal, threshold-cryptographic schemes come in a wide variety of forms, use diverse communication assumptions, and systems using them often provide an ad-hoc treatment of their features. In particular, the necessary communication among the parties is specialized to the deployment platform, even though the principal requirement (that each party obtains the same sequence of messages) is the same across many deployments.
This level of specialization and integration with specific platforms hampers the wide-spread adoption of threshold cryptography. If common interfaces for the cryptographic schemes and modular assumptions about the communication platforms were available, a unified view on threshold cryptographic schemes could emerge and accelerate the adoption of this promising technology.
System implementers generally want to rely on robust libraries that provide basic cryptographic operations and, from there, develop more complex protocols. Since writing cryptographic code is complex and requires sophisticated knowledge, multiple client applications can benefit like this from the work put into a common library. Compared to the usual algorithms found in cryptographic libraries, threshold cryptography additionally requires the integration and implementation of distributed protocols that handle the communication between the involved parties. However, no common, general framework for threshold cryptography exists so far. This has led to the development of many proprietary implementations in different platforms, which are tailored to and optimized for the specific needs of their target environments. Consequently, such solutions often result in cryptographic software modules deeply intertwined with a target system’s codebase, making it difficult to port them to other platforms.
The goal of Thetacrypt is to overcome this limitation by providing a general framework that is composable with many distributed platforms. Our solution can be flexibly integrated into different systems without enforcing constraints on a specific network or adversarial model, instead inheriting them from the underlying platform. Moreover, it is highly modular and introduces customizable interfaces to fit multiple deployment configurations.
Thetacrypt operates as a distributed service on a set of nodes that are connected together over a network. The network is assumed to provide reliable communication among every pair of nodes, and optionally offer a total-order broadcast primitive among all nodes. No assumptions are made about the network delay. Each node runs a stateful Thetacrypt instance in a dedicated process. Applications invoke the service at one node through a remote procedure call (RPC) in a client-server interaction.
The intended deployment of Thetacrypt is in the form of a distributed service coupled with a distributed application that accesses Thetacrypt’s operations. The natural setup consists of a fault-tolerant replicated service with as many independent nodes as there are Thetacrypt nodes and with a compatible failure assumption. For instance, one service node may be grouped together with a Thetacrypt node into the same security domain or hosted on the same physical machine. In this way, n n physical nodes can host a service node and a Thetacrypt node each, and up to t t of the physical nodes may fail or be corrupted. Every node of the service then issues requests to the Thetacrypt instance locally, and the RPC requests can be authenticated by exploiting the common security context such that only the service node in the same security domain is allowed to issue requests to the Thetacrypt node.
In this deployment, the distributed application is also responsible for maintaining the service semantics of Thetacrypt: namely, that each instance receives valid inputs, that these inputs respect any particular ordering requirements of the threshold scheme, and that the assumptions of multi-round interactive cryptographic protocols are satisfied. The envisaged deployment mode of Thetacrypt involves integration with a blockchain network that embodies the state-machine replication paradigm. In this setting, each node executes an application with deterministic operations, concurrently to the other nodes, and invokes Thetacrypt to obtain service-wide cryptographic results. If integrated with a blockchain platform, applications using Thetacrypt would typically be smart contracts that access it through specific API calls from the blockchain validator node. Figure 1 illustrates this deployment and shows how the Thetacrypt module ( Θ \Theta ) integrates with the blockchain stack.
Thetacrypt itself encompasses three layers, as shown in Fig. 2 . We first give an overview of all layers and describe them in more detail in the following sections. 5. Performance Evaluation & Extended Technical Observations Starting from the top, the service layer defines the programming interface with two RPC endpoints accessible by the application. The scheme API provides direct access to the cryptographic primitives, while the protocol API abstracts the execution of threshold protocols.
As the name says, the core layer below contains the main logic of Thetacrypt. It is grouped into three modules. The orchestration module manages concurrent threads, each performing a threshold cryptographic protocol execution. This module keeps track of the creation, progression, and termination of the protocol instances, communicates with the service layer to return results, and dispatches protocol messages to and from the communication layer. The protocols module implements interfaces to access both non-interactive and interactive (multi-round) threshold protocols, abstracting the logic of the protocol away from the particular schemes. Finally, at the heart of Thetacrypt, the schemes module provides the cryptographic primitives for the threshold schemes. This module is self-contained and might also be imported as a library directly by other projects.
Finally, the network layer handles the communication among the nodes through a dedicated network manager module . This module configures the communication and contains the methods to optionally access an underlying network. Specifically, the manager relies on two primary communication methodologies. The peer-to-peer (P2P) communication module abstracts internode communication, and the total-order broadcast (TOB) module abstracts the integration with an existing replicated service and its total-order broadcast protocol since some cryptographic schemes may depend on it.
The service layer exposes the service interface, two RPC endpoints, to an application that integrates threshold cryptographic capabilities into its logic. The protocol API encapsulates the translation logic from the public API to the internal protocols implemented in the core layer. Additionally, the layer provides the scheme API endpoint, allowing the application to access the cryptographic primitives of the schemes module directly. This interface is beneficial for applications that require low-level access to cryptographic operations, bypassing the atomic execution of a threshold protocol but requiring more control over when and how the operations are performed. Currently, the service layer is implemented as a gRPC service [ 12 ] . The gRPC framework allows the definition of a service interface using Protocol Buffers [ 13 ] , a serialization toolset that provides a language-agnostic interface. The design’s modularity allows the layer to support additional interface formats easily.
The core layer represents the main part of Thetacrypt, connecting the cryptographic primitives, the logic behind the protocols, and the management code used to handle key material and execution. At this level, the primary objective is to distinguish between local computation, characterized by cryptographic operations, and internode communication, required by the distributed nature of threshold schemes. Those two distinct tasks are decoupled: the protocols module is responsible for the overall execution logic and the schemes module is responsible for the cryptographic details. This design allows for easy integration of additional cryptographic protocols.
For instance, to extend the cryptographic suite with an additional signature scheme, one should work in the schemes module providing just the necessary cryptographic primitives, and add the scheme to the list of signature schemes available; the protocol module will automatically support the new scheme. On the other hand, to design a new algorithm that takes advantage of the many primitives already present in the suite, one should work exclusively in the protocol module , and, if necessary, extend the schemes module with the required primitives.
The orchestration module is responsible for the management and concurrent execution of multiple protocol instances. It provides the execution environment for the general protocol interface. We identify commonalities in threshold cryptographic protocols and design the Threshold Round Interface (TRI) to integrate multiple protocols into a common architecture. The TRI handles the progression of round-based protocols, the finalization of the cryptographic results, operations that compute locally, and computing steps in response to messages received over the network. We refer to a round as the local computation performed by one party in response to receiving a message over the network until the party produces a result or a message that may be sent to other parties. This pattern is independent of the number of rounds and suitable for multi-round protocols. We present the functions defining the template and how they must be used to correctly execute a generic threshold cryptografic protocol.
A function do_round() triggers the local computation dictated by the protocol in a particular round. Produces as output a protocol message that encapsulates an output of the current round to be forwarded to other parties through the network. Each message indicates whether it is to be transported to other parties using P2P communication or broadcast to all using TOB. This function represents the entry point of the protocol execution. Thus, it is called at the beginning of the protocol (first round) and at the beginning of each new round.
Upon receiving a message from the network, every party needs to update the state of the protocol and check the conditions for termination or progression. The function update(message) triggers the update of the current state of the protocol, recording the received message. Based on the new state, the protocol tests the condition for termination or else the condition to move to a new round. If these are not satisfied, it shall wait for further messages.
The termination conditions are defined by the function is_ready_to_finalize() . If satisfied, the protocol can finalize the computation by executing the finalize() function (see below). The condition for progression is provided by the function is_ready_for_next_round() . Typically, this will check if a certain threshold of valid messages has been received from the other parties. If satisfied, the protocol advances to the next round, executing the do_round() function again.
Finally, the function finalize() contains the operation to compute the result locally (e.g., assembling partial operations received by a threshold of parties) and give it back to the management code of the orchestration module. Each specific protocol implementation needs to incorporate such state-machine logic describing protocol steps. It should clearly define the operations that determine a round, the conditions to transition through multiple phases, and how to react to inputs from the network and produce the correct outputs for other parties. Finally, locally compute the final result. The actual cryptographic primitives are provided by the schemes module .
The schemes module performs all cryptographic calculations for the threshold schemes implemented in Thetacrypt. It provides an easy-to-use API and represents the cryptographic core of the service. The main approach in the choice of the schemes implemented is related to their importance in the literature, and substantiated security proof. Table 1 presents an overview of the implemented schemes.
We will give a brief description of the different kinds of protocols offered, mentioning which schemes from the literature we implemented and their main characteristics. SG02: The threshold cryptosystem proposed by Shoup and Gennaro [ 44 ] is the first non-interactive protocol provably secure against CCA. It relies on the Discrete Logarithm problem. Our implementation relies on the Decisional Diffie-Hellman construction (TDH2 in the paper), which is an ElGamal-based [ 23 ] scheme with zero-knowledge proof (ZKP) of language membership to ensure the security of the scheme in the threshold setting. We apply a hybrid approach [ 1 , 2 ] to encrypt a symmetric key under the threshold key and the actual plaintext under the symmetric key. As a symmetric encryption scheme, we use the ChaCha20Poly1305, a stream cipher with a message authentication code.
BZ03: The scheme by Baek and Zheng [ 3 ] shares the desirable properties of SG02, but it is based on groups that satisfy the Gap Diffie-Hellman problem and requires pairing-friendly elliptic curves. Using pairings allows for an efficient ciphertext verification, without the need for ZKP. The implementation uses the same hybrid approach as SG02. SH00: The first construction of a non-interactive robust threshold signature scheme based on RSA is presented and analyzed by Shoup [ 43 ] . The signature share generation and the verification algorithm use a ZKP for correctness. We provide an implementation of the scheme based on different sizes of the RSA modulus: namely 512 512 , 1024 1024 , 2048 2048 , and 4096 4096 .
KG20: The signature scheme introduced by Komlo and Goldberg [ 29 ] , known as FROST, provides an optimized protocol for threshold Schnorr signatures [ 42 ] . Due to its randomized nature, the signing algorithm is an interactive protocol: the parties first jointly calculate a random nonce (first round) and then sign (second round). FROST introduces a pre-computation phase that performs the first round in advance for a batch of nonces. This is possible because the nonce is independent of the message to be signed. If precomputations are available, the signing algorithm only needs one round of interaction. In our implementation is possible to run a pre-computation phase to speed up the signing process as well as to run the protocol in a two-rounds fashion. FROST is the first multi-round protocol to have been implemented in Thetacrypt, and served as a model and test case for the proposed design. Incidentally, FROST is not robust, i.e., actively deviating parties may cause the signature protocol to abort.
BLS04: The signature scheme proposed by Boneh et al. [ 5 ] provides a novel construction that produces short signatures compared to RSA and DSA signatures with approximately the same level of security. The scheme uses pairings, thus assuming the Gap Diffie-Hellman problem, which provides, thanks to the bilinear mapping property, an efficient and deterministic verification algorithm. The key homomorphism makes the scheme directly threshold-friendly, both for the generation and verification of signature shares.
CKS05: The coin-tossing scheme of Cachin et al. [ 8 ] produces pseudorandom bit strings. Essentially, the scheme is a distributed function mapping a string to the coin value. The paper proposes two constructions, one from any distributed threshold signature scheme with unique signatures (such as the RSA-based SH00), and the other based on the Diffie-Hellman problem. Both constructions are proved secure in the random-oracle model. Thetacrypt incorporates the second construction, based on the Diffie-Hellman problem. It is worth noting that every share of a coin comes with a ZKP for validity, which is a proof of equality of discrete logarithms that ensures the correctness of the share.
For non-interactive schemes, we provide a higher-level interface that groups the schemes in the categories of signature , cipher , and randomness . In this way, at the protocol level, and then at the service level, we reduce the complexity of the APIs and parametrize them just with the scheme type and the arithmetic group needed for it. In the implementation, for the elliptic-curve arithmetic, we use MIRACL Core, a multi-lingual and architecturally agnostic cryptographic library [ 33 ] .
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Secret%20sharing • https://en.wikipedia.org/wiki/Public-key%20cryptography • https://en.wikipedia.org/wiki/Post-quantum%20cryptography • https://csrc.nist.gov/projects/threshold-cryptography • https://arxiv.org/html/2502.03247v1
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Threshold Cryptography Based Secure Secret Sharing Scheme.
[*] Metasploit Scan Running on Target Subnet for Threshold Cryptography Based Secure Secret Sharing Scheme... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |