Complete Technical Paper Content — Usb Forensic Investigation Tool For Windows Systems
Overview & System Context
Usb Forensic Investigation Tool For Windows Systems: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9544 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background During the 1980s, most digital forensic investigations consisted of "live analysis", examining digital media directly using non-specialist tools. In the 1990s, several freeware and other proprietary tools (both hardware and software) were created to allow investigations to take place without modifying media. This first set of tools mainly focused on computer forensics, although in recent years similar tools have evolved for the field of mobile device forensics. This list includes notable examples of digital forensic tools.
Memory forensics tools are used to acquire or analyze a computer's volatile memory (RAM). They are often used in incident response situations to preserve evidence in memory that would be lost when a system is shut down, and to quickly detect stealthy malware by directly examining the operating system and other running software in memory. Mobile forensics tools tend to consist of both a hardware and software component. Mobile phones come with a diverse range of connectors, the hardware devices support a number of different cables and perform the same role as a write blocker in computer devices.
Software forensics is the science of analyzing software source code or binary code to determine whether intellectual property infringement or theft occurred. It is the centerpiece of lawsuits, trials, and settlements when companies are in dispute over issues involving software patents, copyrights, and trade secrets. Software forensics tools can compare code to determine correlation, a measure that can be used to guide a software forensics expert.
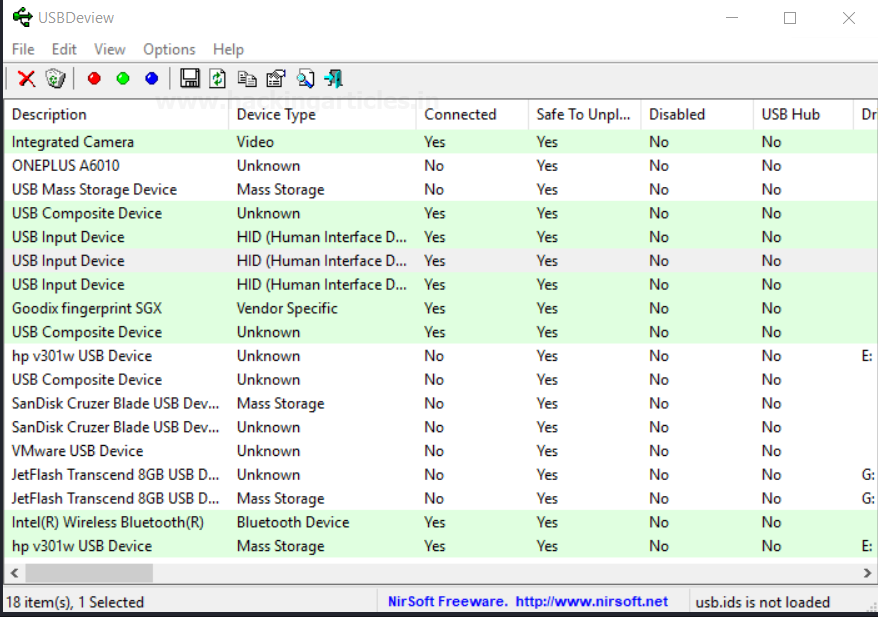
Figure 1: USB Forensics: Detection & Investigation - Hacking Articles Mobile device forensics is a branch of digital forensics relating to recovery of digital evidence or data from a mobile device under forensically sound conditions. The phrase mobile device usually refers to mobile phones; however, it can also relate to any digital device that has both internal memory and communication ability, including PDA devices, GPS devices and tablet computers. Mobile devices can be used to save several types of personal information such as contacts, photos, calendars and notes, SMS and MMS messages. Smartphones may additionally contain video, email, web browsing information, location information, and social networking messages and contacts. There is growing demand for mobile forensics due to several reasons and some of the prominent reasons are: Use of mobile phones to store and transmit personal and corporate information Use of mobile phones in online transactions Use of mobile phone devices by criminals Mobile device forensics can be particularly challenging on a number of levels: Evidential and technical challenges exist. For example, cell site analysis following from the use of a mobile phone usage coverage is not an exact science. Consequently, whilst it is possible to determine roughly the cell site zone from which a call was made or received, it is not yet possible to say with any degree of certainty that a mobile phone call emanated from a specific location e.g. a residential address.
To remain competitive, original equipment manufacturers frequently change mobile phone form factors, operating system file structures, data storage, services, peripherals, and even pin connectors and cables. As a result, forensic examiners must use a different forensic process compared to computer forensics. Storage capacity continues to grow thanks to demand for more powerful "mini computer" type devices. Not only the types of data but also the way mobile devices are used constantly evolve.
Hibernation behavior in which processes are suspended when the device is powered off or idle, but at the same time remaining active. As a result of these challenges, a wide variety of tools exists to extract evidence from mobile devices; no one tool or method can acquire all the evidence from all devices. It is therefore recommended that forensic examiners, especially those wishing to qualify as expert witnesses in court, undergo extensive training in order to understand how each tool and method acquires evidence; how it maintains standards for forensic soundness; and how it meets legal requirements such as the Daubert standard or Frye standard.
The forensics process for mobile devices broadly matches other branches of digital forensics; however, some particular concerns apply. Generally, the process can be broken down into three main categories: seizure, acquisition, and examination/analysis. Other aspects of the computer forensic process, such as intake, validation, documentation/reporting, and archiving still apply.
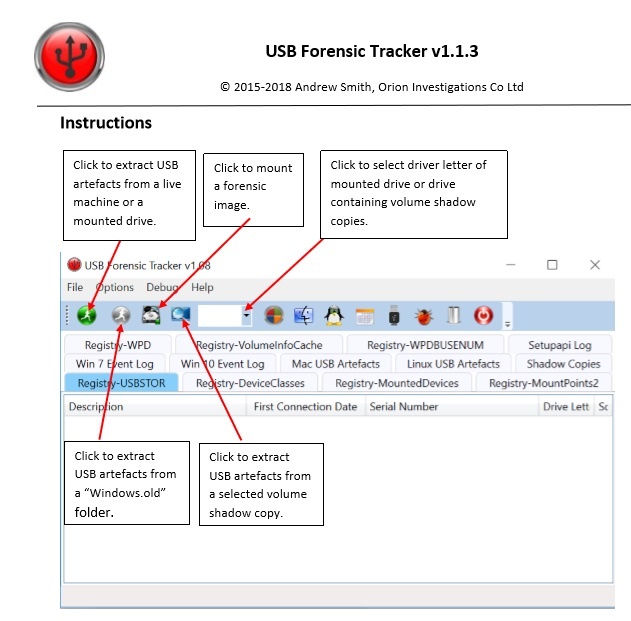
Figure 2: Digital Forensics Examiner: Digital Forensics:USB Forensic Tracker (USBFT) The second step in the forensic process is acquisition, in this case usually referring to retrieval of material from a device (as compared to the bit-copy imaging used in computer forensics). Due to the proprietary nature of mobiles it is often not possible to acquire data with it powered down; most mobile device acquisition is performed live. With more advanced smartphones using advanced memory management, connecting it to a recharger and putting it into a faraday cage may not be good practice. The mobile device would recognize the network disconnection and therefore it would change its status information that can trigger the memory manager to write data. Most acquisition tools for mobile devices are commercial in nature and consist of a hardware and software component, often automated.
Early investigations consisted of live manual analysis of mobile devices; with examiners photographing or writing down useful material for use as evidence. Without forensic photography equipment such as Fernico ZRT, EDEC Eclipse, or Project-a-Phone, this had the disadvantage of risking the modification of the device content, as well as leaving many parts of the proprietary operating system inaccessible. In recent years a number of hardware/software tools have emerged to recover logical and physical evidence from mobile devices. Most tools consist of both hardware and software portions. The hardware includes a number of cables to connect the mobile device to the acquisition machine; the software exists to extract the evidence and, occasionally, even to analyze it. Most recently, mobile device forensic tools have been developed for the field.
This is in response both to military units' demand for fast and accurate anti-terrorism intelligence, and to law enforcement demand for forensic previewing capabilities at a crime scene, search warrant execution, or exigent circumstances. Such mobile forensic tools are often ruggedized for harsh environments (e.g. the battlefield) and rough treatment (e.g. being dropped or submerged in water). Generally, because it is impossible for any one tool to capture all evidence from all mobile devices, mobile forensic professionals recommend that examiners establish entire toolkits consisting of a mix of commercial, open-source, broad support, and narrow support forensic tools, together with accessories such as battery chargers, Faraday bags or other signal disruption equipment, and so forth.
Desoldering the chips is done carefully and slowly, so that the heat does not destroy the chip or data. Before the chip is desoldered the PCB is baked in an oven to eliminate remaining water. This prevents the so-called popcorn effect, at which the remaining water would blow the chip package at desoldering. There are mainly three methods to melt the solder: hot air, infrared light, and steam-phasing. The infrared light technology works with a focused infrared light beam onto a specific integrated circuit and is used for small chips. The hot air and steam methods cannot focus as much as the infrared technique.
The first is to use a stencil. The stencil is chip-dependent and must fit exactly. Then the tin-solder is put on the stencil. After cooling the tin the stencil is removed and if necessary a second cleaning step is done. The second method is laser re-balling. Here the stencil is programmed into the re-balling unit. A bondhead (looks like a tube/needle) is automatically loaded with one tin ball from a solder ball singulation tank. The ball is then heated by a laser, such that the tin-solder ball becomes fluid and flows onto the cleaned chip. Instantly after melting the ball the laser turns off and a new ball falls into the bondhead. While reloading, the bondhead of the re-balling unit changes the position to the next pin. A third method makes the entire re-balling process unnecessary. The chip is connected to an adapter with Y-shaped springs or spring-loaded pogo pins. The Y-shaped springs need to have a ball onto the pin to establish an electric connection, but the pogo pins can be used directly on the pads on the chip without the balls. The advantage of forensic desoldering is that the device does not need to be functional and that a copy without any changes to the original data can be made. The disadvantage is that the re-balling devices are expensive, so this process is very costly and there are some risks of total data loss. Hence, forensic desoldering should only be done by experienced laboratories.
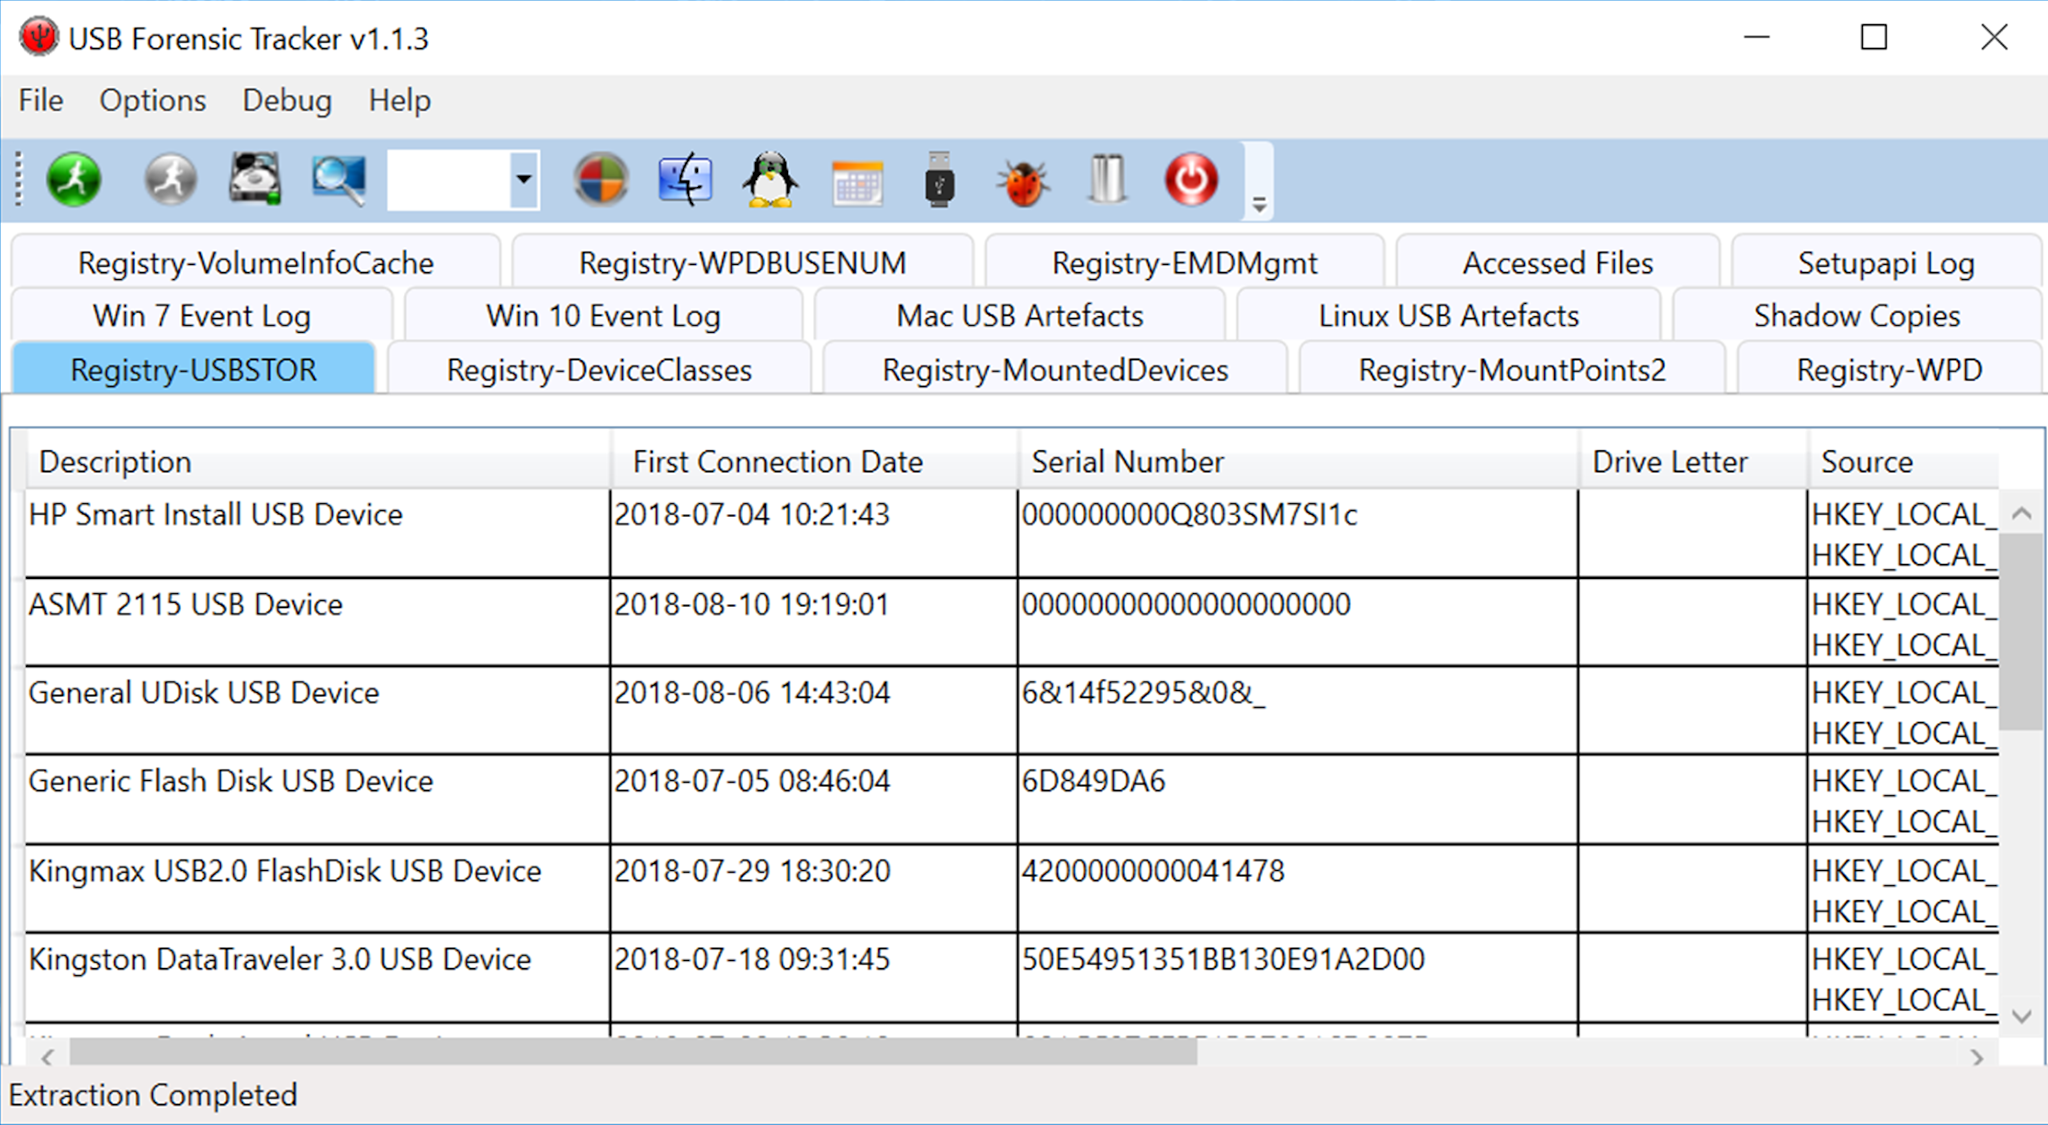
Figure 3: Digital Forensics Examiner: Digital Forensics: Computer Forensics Tools Computer forensics (also known as computer forensic science) is a branch of digital forensic science pertaining to evidence found in computers and digital storage media. The goal of computer forensics is to examine digital media in a forensically sound manner with the aim of identifying, preserving, recovering, analyzing, and presenting facts and opinions about the digital information. Although it is most often associated with the investigation of a wide variety of computer crime, computer forensics may also be used in civil proceedings. The discipline involves similar techniques and principles to data recovery, but with additional guidelines and practices designed to create a legal audit trail. Evidence from computer forensics investigations is usually subjected to the same guidelines and practices as other digital evidence. It has been used in a number of high-profile cases and is accepted as reliable within U.S. and European court systems.
BTK Killer: Dennis Rader was convicted of a string of serial killings over sixteen years. Towards the end of this period, Rader sent letters to the police on a floppy disk. Metadata within the documents implicated an author named "Dennis" at "Christ Lutheran Church," helping lead to Rader's arrest. Joseph Edward Duncan: A spreadsheet recovered from Duncan's computer contained evidence showing him planning his crimes. Prosecutors used this to demonstrate premeditation and secure the death penalty. Sharon Lopatka: Hundreds of emails on Lopatka's computer led investigators to her killer, Robert Glass.
Corcoran Group: In this case, computer forensics confirmed parties' duties to preserve digital evidence when litigation had commenced or was reasonably anticipated. Hard drives were analyzed, though the expert found no evidence of deletion, and evidence showed that the defendants intentionally destroyed emails. Dr. Conrad Murray: Dr. Conrad Murray, the doctor of Michael Jackson, was convicted partially by digital evidence, including medical documentation showing lethal amounts of propofol. Mark Twitchell, also known as the "Dexter Killer," Twitchell was convicted with the help of a deleted document recovered from his laptop titled "SKConfessions." This file, which detailed his criminal activities, served as a key piece of evidence in the case.
Computer forensic investigations typically follow the standard digital forensic process, consisting of four phases: acquisition, examination, analysis, and reporting. Investigations are usually performed on static data (i.e., acquired images) rather than "live" systems. This differs from early forensic practices, when a lack of specialized tools often required investigators to work on live data.
Cross-drive analysis This technique correlates information found on multiple hard drives and can be used to identify social networks or detect anomalies. Live analysis The examination of computers from within the operating system using forensic or existing sysadmin tools to extract evidence. This technique is particularly useful for dealing with encrypting file systems where encryption keys can be retrieved, or for imaging the logical hard drive volume (a live acquisition) before shutting down the computer. Live analysis is also beneficial when examining networked systems or cloud-based devices that cannot be accessed physically. Deleted files A common forensic technique involves recovering deleted files. Most operating systems and file systems do not erase the physical file data, allowing investigators to reconstruct it from the physical disk sectors.
Forensic software can "carve" files by searching for known file headers and reconstructing deleted data. Stochastic forensics This method leverages the stochastic properties of a system to investigate activities without traditional digital artifacts, often useful in cases of data theft. Steganography Steganography involves concealing data within another file, such as hiding illegal content within an image. Forensic investigators detect steganography by comparing file hashes, as any hidden data will alter the hash value of the file.
Numerous open-source and commercial tools exist for computer forensics. Common forensic analysis includes manual reviews of media, Windows registry analysis, password cracking, keyword searches, and the extraction of emails and images. Tools such as Autopsy (software), Belkasoft Evidence Center X, Forensic Toolkit (FTK), and EnCase are widely used in digital forensics.
In digital investigations, USB devices often become silent carriers of critical evidence. From data theft and intellectual property leaks to malware infections and insider threats, external storage devices can play a pivotal role. Understanding how to trace USB activity on Windows systems is therefore essential for digital forensic professionals. This article explores where Windows stores USB artifacts, what information can be recovered, and why proper analysis matters in real-world investigations.
In corporate environments, unauthorized USB usage can indicate data exfiltration. In criminal investigations, it may establish access, intent, or timeline correlations. 2. System Architecture & Core Working Principles Windows maintains multiple forensic artifacts that help reconstruct USB usage history. No single artifact provides the full picture; correlation is critical.
The serial number is especially important for uniquely identifying a specific USB device. When only the suspect computer is available, investigators look for copied file traces, such as: Timeline analysis tools can help correlate multiple artifacts into a coherent event sequence. An experienced examiner understands these limitations and looks for indirect indicators when primary artifacts are missing.
Technical accuracy alone is insufficient. Findings must be presented in a way that judges and legal professionals can understand. USB forensics on Windows systems provides powerful insights into device usage, user behavior, and potential data movement. By carefully analyzing registry entries, logs, file system metadata, and user artifacts, investigators can reconstruct events with high confidence.
In insider threat cases and data breach investigations, tracing external device usage can become the decisive factor that establishes intent, access, and timeline alignment. For digital forensic professionals, mastering USB artifact analysis is not optional — it is a core investigative skill. Cyberstalking & Digital Harassment: Forensic Evidence Collection In today’s digital world, cyberstalking and digital harassment have become serious and increasingly reported cybercrimes. Moreover, the widespread use of smartphones, social media ...
An employee on the way out who copies client folders to a personal USB drive, a workstation infected after a thumb drive found in a parking lot is plugged in: in both cases, the investigator’s first question is the same. Which device was connected, when, and by whom? USB devices are part of everyday life for users: flash drives, external hard drives, smartphones, and memory card readers.
They are also vectors for data exfiltration and infection, as shown by the Raspberry Robin worm, which spreads using USB drives . Each time a device is connected, Windows identifies the hardware, loads its drivers, and keeps a lot of information to recognize it faster the next time. In this new part of the Windows forensic series, we will look at where Windows stores USB device history (Registry, driver installation log, event logs). We will see how to correlate these traces to link a device to a user, then how to save time with NirSoft’s USBDeview and USBDriveLog.
If you missed the previous episodes, you can find them on the dedicated forensic page . By cross-referencing the different artifacts presented in this article, it is possible to identify: Native Windows USB artifacts mainly show that a device was recognized or mounted by the system. They do not automatically provide the full list of files copied to or from the media.
That gap can be filled by the EDR, which provides more precise visibility into files read, created, or copied when removable media monitoring is enabled. However, the absence of an EDR does not prevent you from reconstructing part of the activity by correlating Windows artifacts. When a USB device is connected, several exchanges occur between the hardware and the system to identify it, load its driver, and, if it is a storage device, mount its volume. Each of these steps leaves a trace in the Registry.
Identifying Storage Devices with USBSTOR USB storage devices are listed under the following key: HKLM\SYSTEM\ControlSet00#\Enum\USBSTOR\{ID de classe de périphérique}\{Sous-clés} The first level of subkeys follows the format Disk&Ven_
Determining the First Installation The following log records device and driver installation operations: %SystemRoot%\inf\Setupapi.dev.log By searching for the serial number or device instance identifier, it is possible to find the section corresponding to its installation. The associated date generally represents the first known installation of the device on that Windows installation. However, it should not be considered absolute proof of the very first connection, because the log may be rotated, truncated, or affected by a device reinstallation. Warning: the timestamps in setupapi.dev.log are expressed in the system’s local time, whereas Registry properties and event logs are in UTC. Be sure to align time zones when building the timeline. Linking a Device to a User When a volume is mounted in a user session, a trace is recorded in that user’s NTUSER.DAT hive at the following location: HKEY_USERS\{USER}\Software\Microsoft\Windows\CurrentVersion\Explorer\MountPoints2\{GUID du volume} The subkeys can contain a volume GUID or the path to a network share (in the form ##server#share ). The presence of a volume GUID in a user hive establishes that the volume was mounted in the context of that user’s profile. The Full Correlation Chain No single key can answer the question “ which user plugged in which drive? ” on its own. It is the sequence of artifacts that provides the answer: MountPoints2 (user hive) provides the volume GUID mounted in the user’s session MountedDevices links that GUID to the instance path , and therefore to the device serial number USBSTOR provides the manufacturer, model , and timestamps associated with that serial number setupapi.dev.log completes the picture with the first installation date USB Traces in Event Logs Event logs complement the Registry with one advantage: they can retain multiple connections of the same device, whereas the Registry keeps only the latest one. The DriverFrameworks-UserMode Log The following log can also provide information, provided it had been enabled beforehand (it is disabled by default): Microsoft-Windows-DriverFrameworks-UserMode/Operational These logs can contain information about volumes, their capacity, model, serial number, as well as connection and disconnection times. Analyzing USB Devices with USBDeview Tool Overview To make it easier to correlate this information, we will use USBDeview, a free portable tool developed by Nir Sofer (NirSoft). It lists currently connected USB devices as well as previously used ones, and works from Windows 2000 to Windows 11, on 32-bit and 64-bit systems. The current version is 3.10. Official website: USBDeview on nirsoft.net Running USBDeview Once the archive has been downloaded and extracted, launch the tool as administrator . This is essential: the Install Time , First Install Time , Connect Time , and Disconnect Time columns read the properties subkey seen above, which is accessible only with elevation. Without them, you only get the Registry Time 1 and Registry Time 2 columns, derived from the key last-write timestamps, whose meaning NirSoft says varies from one system to another. The tool provides, among other things: The device name and description Its type Its serial number (for storage devices) Its Vendor ID and Product ID Its drive letter, when it can be determined (USBDeview does not detect it for USB hard drives) Its installation, first installation, last connection, and last removal dates Its connected or disconnected state By double-clicking a device, we can view the details of its properties. Completing the Picture with USBDriveLog USBDeview makes inventorying easier, but it does not provide the history of all connections. For Windows 10 and Windows 11, USBDriveLog, from the same publisher, uses the Microsoft-Windows-Partition/Diagnostic and Microsoft-Windows-Storsvc/Diagnostic logs to list each connection with the model, serial number, capacity, and connection and removal times. It can read logs from an external disk through Choose Data Source (F7), by pointing to the Windows\System32\winevt\Logs folder of the analyzed image. You can download it using the following link: Official website: USBDriveLog on nirsoft.net Conclusion USB device analysis relies on correlating several artifacts: USBSTOR and its properties to identify the device and date its connections, MountedDevices and MountPoints2 to link it to a volume and a user, setupapi.dev.log for the first installation, and event logs for connection history. USBDeview and USBDriveLog speed up this work, as long as you understand where their data comes from and use them on copies. These traces prove that a device was plugged in, not what was copied. To go further, you need to cross-reference them with LNK files, Jump Lists, and ShellBags, or have removable media auditing in place. In an enterprise environment, a device whose manufacturer or model is not part of the authorized inventory is a good starting point for a deeper investigation. For further reading: GPO: managing USB devices allowed to connect to a Windows PC or server How to block USB drives with a GPO Forensic Windows - Part 14: Exploring Shadow Copies (VSS) Mehdi Dakhama Consultant and trainer Consultant and expert trainer in Windows Server and Azure Cloud. Cybersecurity researcher. See Full Bio The first level of subkeys follows the format Disk&Ven_
3. Software Implementation, Frameworks & Protocols Identifying the Vendor ID and Product ID The manufacturer and product USB identifiers are visible under the following key: HKLM\SYSTEM\ControlSet00#\Enum\USB The subkeys follow this format: VID_XXXX&PID_YYYY VID corresponds to the Vendor ID, the manufacturer identifier assigned by the USB-IF PID corresponds to the Product ID, the product identifier defined by the manufacturer The instance subkey under VID_XXXX&PID_YYYY reuses the serial number: this is what makes it possible to link a USB entry to the corresponding USBSTOR entry. Recovering the Volume Name Additional information about portable devices is stored under the following key: HKLM\SOFTWARE\Microsoft\Windows Portable Devices\Devices The name of each subkey reuses the device instance identifier (with its serial number), and the FriendlyName value usually contains the volume name as it appeared in File Explorer. Linking the Device to a Drive Letter and a Volume The mapping between volumes and drive letters is stored in: HKLM\SYSTEM\MountedDevices This key contains two types of values: \DosDevices\E: (and similar): the assigned drive letter \??\Volume{GUID} : the volume GUID For a removable USB device, the associated binary data usually corresponds to a Unicode string containing the device instance path, for example _??_USBSTOR#Disk&Ven_...&Prod_...#
Determining the First Installation The following log records device and driver installation operations: %SystemRoot%\inf\Setupapi.dev.log By searching for the serial number or device instance identifier, it is possible to find the section corresponding to its installation. The associated date generally represents the first known installation of the device on that Windows installation. However, it should not be considered absolute proof of the very first connection, because the log may be rotated, truncated, or affected by a device reinstallation. Warning: the timestamps in setupapi.dev.log are expressed in the system’s local time, whereas Registry properties and event logs are in UTC. Be sure to align time zones when building the timeline. Linking a Device to a User When a volume is mounted in a user session, a trace is recorded in that user’s NTUSER.DAT hive at the following location: HKEY_USERS\{USER}\Software\Microsoft\Windows\CurrentVersion\Explorer\MountPoints2\{GUID du volume} The subkeys can contain a volume GUID or the path to a network share (in the form ##server#share ). The presence of a volume GUID in a user hive establishes that the volume was mounted in the context of that user’s profile. The Full Correlation Chain No single key can answer the question “ which user plugged in which drive? ” on its own. It is the sequence of artifacts that provides the answer: MountPoints2 (user hive) provides the volume GUID mounted in the user’s session MountedDevices links that GUID to the instance path , and therefore to the device serial number USBSTOR provides the manufacturer, model , and timestamps associated with that serial number setupapi.dev.log completes the picture with the first installation date USB Traces in Event Logs Event logs complement the Registry with one advantage: they can retain multiple connections of the same device, whereas the Registry keeps only the latest one. The DriverFrameworks-UserMode Log The following log can also provide information, provided it had been enabled beforehand (it is disabled by default): Microsoft-Windows-DriverFrameworks-UserMode/Operational These logs can contain information about volumes, their capacity, model, serial number, as well as connection and disconnection times. Analyzing USB Devices with USBDeview Tool Overview To make it easier to correlate this information, we will use USBDeview, a free portable tool developed by Nir Sofer (NirSoft). It lists currently connected USB devices as well as previously used ones, and works from Windows 2000 to Windows 11, on 32-bit and 64-bit systems. The current version is 3.10. Official website: USBDeview on nirsoft.net Running USBDeview Once the archive has been downloaded and extracted, launch the tool as administrator . This is essential: the Install Time , First Install Time , Connect Time , and Disconnect Time columns read the properties subkey seen above, which is accessible only with elevation. Without them, you only get the Registry Time 1 and Registry Time 2 columns, derived from the key last-write timestamps, whose meaning NirSoft says varies from one system to another. The tool provides, among other things: The device name and description Its type Its serial number (for storage devices) Its Vendor ID and Product ID Its drive letter, when it can be determined (USBDeview does not detect it for USB hard drives) Its installation, first installation, last connection, and last removal dates Its connected or disconnected state By double-clicking a device, we can view the details of its properties. Completing the Picture with USBDriveLog USBDeview makes inventorying easier, but it does not provide the history of all connections. For Windows 10 and Windows 11, USBDriveLog, from the same publisher, uses the Microsoft-Windows-Partition/Diagnostic and Microsoft-Windows-Storsvc/Diagnostic logs to list each connection with the model, serial number, capacity, and connection and removal times. It can read logs from an external disk through Choose Data Source (F7), by pointing to the Windows\System32\winevt\Logs folder of the analyzed image. You can download it using the following link: Official website: USBDriveLog on nirsoft.net Conclusion USB device analysis relies on correlating several artifacts: USBSTOR and its properties to identify the device and date its connections, MountedDevices and MountPoints2 to link it to a volume and a user, setupapi.dev.log for the first installation, and event logs for connection history. USBDeview and USBDriveLog speed up this work, as long as you understand where their data comes from and use them on copies. These traces prove that a device was plugged in, not what was copied. To go further, you need to cross-reference them with LNK files, Jump Lists, and ShellBags, or have removable media auditing in place. In an enterprise environment, a device whose manufacturer or model is not part of the authorized inventory is a good starting point for a deeper investigation. For further reading: GPO: managing USB devices allowed to connect to a Windows PC or server How to block USB drives with a GPO Forensic Windows - Part 14: Exploring Shadow Copies (VSS) Mehdi Dakhama Consultant and trainer Consultant and expert trainer in Windows Server and Azure Cloud. Cybersecurity researcher. See Full Bio The instance subkey under VID_XXXX&PID_YYYY reuses the serial number: this is what makes it possible to link a USB entry to the corresponding USBSTOR entry.
Recovering the Volume Name Additional information about portable devices is stored under the following key: HKLM\SOFTWARE\Microsoft\Windows Portable Devices\Devices The name of each subkey reuses the device instance identifier (with its serial number), and the FriendlyName value usually contains the volume name as it appeared in File Explorer. Linking the Device to a Drive Letter and a Volume The mapping between volumes and drive letters is stored in: HKLM\SYSTEM\MountedDevices This key contains two types of values: \DosDevices\E: (and similar): the assigned drive letter \??\Volume{GUID} : the volume GUID For a removable USB device, the associated binary data usually corresponds to a Unicode string containing the device instance path, for example _??_USBSTOR#Disk&Ven_...&Prod_...#
Warning: the timestamps in setupapi.dev.log are expressed in the system’s local time, whereas Registry properties and event logs are in UTC. Be sure to align time zones when building the timeline. Linking a Device to a User When a volume is mounted in a user session, a trace is recorded in that user’s NTUSER.DAT hive at the following location: HKEY_USERS\{USER}\Software\Microsoft\Windows\CurrentVersion\Explorer\MountPoints2\{GUID du volume} The subkeys can contain a volume GUID or the path to a network share (in the form ##server#share ). The presence of a volume GUID in a user hive establishes that the volume was mounted in the context of that user’s profile. The Full Correlation Chain No single key can answer the question “ which user plugged in which drive? ” on its own. It is the sequence of artifacts that provides the answer: MountPoints2 (user hive) provides the volume GUID mounted in the user’s session MountedDevices links that GUID to the instance path , and therefore to the device serial number USBSTOR provides the manufacturer, model , and timestamps associated with that serial number setupapi.dev.log completes the picture with the first installation date USB Traces in Event Logs Event logs complement the Registry with one advantage: they can retain multiple connections of the same device, whereas the Registry keeps only the latest one. The DriverFrameworks-UserMode Log The following log can also provide information, provided it had been enabled beforehand (it is disabled by default): Microsoft-Windows-DriverFrameworks-UserMode/Operational These logs can contain information about volumes, their capacity, model, serial number, as well as connection and disconnection times. Analyzing USB Devices with USBDeview Tool Overview To make it easier to correlate this information, we will use USBDeview, a free portable tool developed by Nir Sofer (NirSoft). It lists currently connected USB devices as well as previously used ones, and works from Windows 2000 to Windows 11, on 32-bit and 64-bit systems. The current version is 3.10. Official website: USBDeview on nirsoft.net Running USBDeview Once the archive has been downloaded and extracted, launch the tool as administrator . This is essential: the Install Time , First Install Time , Connect Time , and Disconnect Time columns read the properties subkey seen above, which is accessible only with elevation. Without them, you only get the Registry Time 1 and Registry Time 2 columns, derived from the key last-write timestamps, whose meaning NirSoft says varies from one system to another. The tool provides, among other things: The device name and description Its type Its serial number (for storage devices) Its Vendor ID and Product ID Its drive letter, when it can be determined (USBDeview does not detect it for USB hard drives) Its installation, first installation, last connection, and last removal dates Its connected or disconnected state By double-clicking a device, we can view the details of its properties. Completing the Picture with USBDriveLog USBDeview makes inventorying easier, but it does not provide the history of all connections. For Windows 10 and Windows 11, USBDriveLog, from the same publisher, uses the Microsoft-Windows-Partition/Diagnostic and Microsoft-Windows-Storsvc/Diagnostic logs to list each connection with the model, serial number, capacity, and connection and removal times. It can read logs from an external disk through Choose Data Source (F7), by pointing to the Windows\System32\winevt\Logs folder of the analyzed image. You can download it using the following link: Official website: USBDriveLog on nirsoft.net Conclusion USB device analysis relies on correlating several artifacts: USBSTOR and its properties to identify the device and date its connections, MountedDevices and MountPoints2 to link it to a volume and a user, setupapi.dev.log for the first installation, and event logs for connection history. USBDeview and USBDriveLog speed up this work, as long as you understand where their data comes from and use them on copies. These traces prove that a device was plugged in, not what was copied. To go further, you need to cross-reference them with LNK files, Jump Lists, and ShellBags, or have removable media auditing in place. In an enterprise environment, a device whose manufacturer or model is not part of the authorized inventory is a good starting point for a deeper investigation. For further reading: GPO: managing USB devices allowed to connect to a Windows PC or server How to block USB drives with a GPO Forensic Windows - Part 14: Exploring Shadow Copies (VSS) Mehdi Dakhama Consultant and trainer Consultant and expert trainer in Windows Server and Azure Cloud. Cybersecurity researcher. See Full Bio The name of each subkey reuses the device instance identifier (with its serial number), and the FriendlyName value usually contains the volume name as it appeared in File Explorer.
For a removable USB device, the associated binary data usually corresponds to a Unicode string containing the device instance path, for example _??_USBSTOR#Disk&Ven_...&Prod_...#
By searching for the serial number or device instance identifier, it is possible to find the section corresponding to its installation. The associated date generally represents the first known installation of the device on that Windows installation. However, it should not be considered absolute proof of the very first connection, because the log may be rotated, truncated, or affected by a device reinstallation.
Warning: the timestamps in setupapi.dev.log are expressed in the system’s local time, whereas Registry properties and event logs are in UTC. Be sure to align time zones when building the timeline. When a volume is mounted in a user session, a trace is recorded in that user’s NTUSER.DAT hive at the following location: The subkeys can contain a volume GUID or the path to a network share (in the form ##server#share ). The presence of a volume GUID in a user hive establishes that the volume was mounted in the context of that user’s profile.
No single key can answer the question “ which user plugged in which drive? ” on its own. It is the sequence of artifacts that provides the answer: Event logs complement the Registry with one advantage: they can retain multiple connections of the same device, whereas the Registry keeps only the latest one.
The following log can also provide information, provided it had been enabled beforehand (it is disabled by default): These logs can contain information about volumes, their capacity, model, serial number, as well as connection and disconnection times. To make it easier to correlate this information, we will use USBDeview, a free portable tool developed by Nir Sofer (NirSoft). It lists currently connected USB devices as well as previously used ones, and works from Windows 2000 to Windows 11, on 32-bit and 64-bit systems. The current version is 3.10.
Once the archive has been downloaded and extracted, launch the tool as administrator . This is essential: the Install Time , First Install Time , Connect Time , and Disconnect Time columns read the properties subkey seen above, which is accessible only with elevation. Without them, you only get the Registry Time 1 and Registry Time 2 columns, derived from the key last-write timestamps, whose meaning NirSoft says varies from one system to another.
The tool provides, among other things: The device name and description Its type Its serial number (for storage devices) Its Vendor ID and Product ID Its drive letter, when it can be determined (USBDeview does not detect it for USB hard drives) Its installation, first installation, last connection, and last removal dates Its connected or disconnected state By double-clicking a device, we can view the details of its properties. Completing the Picture with USBDriveLog USBDeview makes inventorying easier, but it does not provide the history of all connections. For Windows 10 and Windows 11, USBDriveLog, from the same publisher, uses the Microsoft-Windows-Partition/Diagnostic and Microsoft-Windows-Storsvc/Diagnostic logs to list each connection with the model, serial number, capacity, and connection and removal times. It can read logs from an external disk through Choose Data Source (F7), by pointing to the Windows\System32\winevt\Logs folder of the analyzed image. You can download it using the following link: Official website: USBDriveLog on nirsoft.net Conclusion USB device analysis relies on correlating several artifacts: USBSTOR and its properties to identify the device and date its connections, MountedDevices and MountPoints2 to link it to a volume and a user, setupapi.dev.log for the first installation, and event logs for connection history.
USBDeview and USBDriveLog speed up this work, as long as you understand where their data comes from and use them on copies. These traces prove that a device was plugged in, not what was copied. To go further, you need to cross-reference them with LNK files, Jump Lists, and ShellBags, or have removable media auditing in place. In an enterprise environment, a device whose manufacturer or model is not part of the authorized inventory is a good starting point for a deeper investigation.
For further reading: GPO: managing USB devices allowed to connect to a Windows PC or server How to block USB drives with a GPO Forensic Windows - Part 14: Exploring Shadow Copies (VSS) Mehdi Dakhama Consultant and trainer Consultant and expert trainer in Windows Server and Azure Cloud. Cybersecurity researcher. See Full Bio Completing the Picture with USBDriveLog USBDeview makes inventorying easier, but it does not provide the history of all connections.
For Windows 10 and Windows 11, USBDriveLog, from the same publisher, uses the Microsoft-Windows-Partition/Diagnostic and Microsoft-Windows-Storsvc/Diagnostic logs to list each connection with the model, serial number, capacity, and connection and removal times. It can read logs from an external disk through Choose Data Source (F7), by pointing to the Windows\System32\winevt\Logs folder of the analyzed image. You can download it using the following link: Official website: USBDriveLog on nirsoft.net Conclusion USB device analysis relies on correlating several artifacts: USBSTOR and its properties to identify the device and date its connections, MountedDevices and MountPoints2 to link it to a volume and a user, setupapi.dev.log for the first installation, and event logs for connection history. USBDeview and USBDriveLog speed up this work, as long as you understand where their data comes from and use them on copies. These traces prove that a device was plugged in, not what was copied. To go further, you need to cross-reference them with LNK files, Jump Lists, and ShellBags, or have removable media auditing in place. In an enterprise environment, a device whose manufacturer or model is not part of the authorized inventory is a good starting point for a deeper investigation. For further reading: GPO: managing USB devices allowed to connect to a Windows PC or server How to block USB drives with a GPO Forensic Windows - Part 14: Exploring Shadow Copies (VSS) Mehdi Dakhama Consultant and trainer Consultant and expert trainer in Windows Server and Azure Cloud. Cybersecurity researcher. See Full Bio USBDeview makes inventorying easier, but it does not provide the history of all connections. For Windows 10 and Windows 11, USBDriveLog, from the same publisher, uses the Microsoft-Windows-Partition/Diagnostic and Microsoft-Windows-Storsvc/Diagnostic logs to list each connection with the model, serial number, capacity, and connection and removal times.
It can read logs from an external disk through Choose Data Source (F7), by pointing to the Windows\System32\winevt\Logs folder of the analyzed image. You can download it using the following link: 4. Practical Deployment, Analysis & Case Studies USB device analysis relies on correlating several artifacts: USBSTOR and its properties to identify the device and date its connections, MountedDevices and MountPoints2 to link it to a volume and a user, setupapi.dev.log for the first installation, and event logs for connection history. USBDeview and USBDriveLog speed up this work, as long as you understand where their data comes from and use them on copies.
These traces prove that a device was plugged in, not what was copied. To go further, you need to cross-reference them with LNK files, Jump Lists, and ShellBags, or have removable media auditing in place. In an enterprise environment, a device whose manufacturer or model is not part of the authorized inventory is a good starting point for a deeper investigation. Mehdi Dakhama Consultant and trainer Consultant and expert trainer in Windows Server and Azure Cloud. Cybersecurity researcher. See Full Bio Every removable mass-storage device that has ever been attached to a Windows host leaves a durable fingerprint in the registry. Long after the USB stick is unplugged and carried out the door, the SYSTEM hive retains the vendor, product, revision, serial number and last-connection timestamp of that device. For a digital forensics and incident response (DFIR) practitioner, this artifact answers one of the most common questions in a data-exfiltration or insider-threat investigation: which removable devices touched this machine, and when.
The canonical source for USB device history is the USBSTOR enumeration key under the current control set, supplemented by the MountedDevices key that maps a device to the drive letter it received. Together these keys let an examiner reconstruct a per-device timeline of attachment events, correlate a serial number across multiple hosts, and tie a specific physical device to a window of suspicious file activity.
This article approaches USB device history from the perspective of a senior examiner working a removable-media exfiltration case. We cover the registry provenance of the artifact, the real on-disk path Forenza reads, every normalized field the Forenza USB parser surfaces, the device-naming convention that lets you decode a class key into vendor and product, a realistic parsed record, the forensic significance of each field, detection priorities mapped to MITRE ATT&CK, Sigma and KQL detection scaffolding, the Forenza DFIR Query Language (DQL) equivalents, correlation with neighbouring artifacts, the noise model that trips up naive USB hunting, and the three Forenza collection paths.
The discussion assumes a modern Windows release (Windows 10 / 11 client, Windows Server 2016 onward). The USBSTOR sub-key layout and the vendor / product / revision naming convention have been stable since Windows XP, with the Properties timestamp subkeys gaining richer values on Windows 8 and later. We call out version-dependent behaviour explicitly where it matters.
USB history is a configuration-and-inventory artifact, not an event-log record. It does not stream in real time. It is a point-in-time snapshot of what the kernel Plug and Play (PnP) manager has enumerated and persisted, which means absence of a device in the registry is meaningful only when you understand how and when the enumeration is written. The USB devices artifact is the set of registry keys Windows maintains to remember every USB mass-storage device that has been mounted. The primary key is SYSTEMCurrentControlSetEnumUSBSTOR . Beneath it, Windows creates one sub-key per device class (a vendor / product / revision tuple), and beneath each class key, one leaf sub-key per physical device instance, named by the device serial number.
The companion key SYSTEMMountedDevices records the binary signature and the drive letter or volume GUID assigned to each mounted volume, including removable volumes. By cross-referencing the ParentIdPrefix value of a USBSTOR instance against the MountedDevices binary blobs, an examiner can determine which drive letter a given USB device received when it was last attached.
Forenza reads the SYSTEM hive directly and parses the USBSTOR enumeration into structured records. The parser decodes the class-key naming convention into discrete vendor, product and revision fields, captures the per-instance serial number, and surfaces the friendly name, the parent ID prefix and the hardware ID list. The last-connection timestamp is derived from the registry key last-write time of the instance sub-key, which the PnP manager updates on each attachment.
Because the artifact is registry-resident, it survives reboots, user logoff and even deletion of the files that were copied to the device. It is one of the most reliable physical-device-to-host bindings available to an examiner, and it is frequently the linchpin of an insider-threat or intellectual-property-theft timeline. Forenza resolves CurrentControlSet at parse time by reading the SelectCurrent value inside the SYSTEM hive, so an offline hive (where CurrentControlSet is a runtime-only symbolic link) is handled correctly by mapping to the concrete ControlSet001 or ControlSet002 key. This detail matters because offline triage and image-mode triage never see the live symbolic link.
When a USB mass-storage device is attached, the Windows PnP manager enumerates the device through the USB and storage driver stack. The USBSTOR.SYS driver claims the device and the PnP manager writes a class key under USBSTOR describing the device hardware (vendor, product, revision), then a per-instance key named by the serial number reported in the device descriptor. If the device does not report a unique serial number, Windows synthesises one with a second character of & , which is itself a forensic tell.
On first attachment, Windows records the FriendlyName , the ParentIdPrefix (which links the storage device to its volume), and the HardwareID multi-string. On each subsequent attachment, the PnP manager touches the instance key, updating its last-write timestamp. This last-write time is the value Forenza surfaces as the last-connection time. Richer first-install, first-connect and last-removal timestamps are stored in the Properties subkeys under each instance on Windows 8 and later, keyed by well-known property GUIDs.
The MountedDevices key is written by the mount manager when a volume is mounted. For a removable device, the binary value records the disk signature or the USB instance path, and the value name encodes the drive letter (for example DosDevicesE: ) or a volume GUID. This is what lets an examiner answer not just “was this device attached” but “what drive letter did it get”.
The fields below are the normalized field names the Forenza USB parser emits per device instance, as decoded from the USBSTOR class key and instance sub-key. JSON marshalling lower-cases every field name; the DQL accessors later in this article use these exact lower-cased names. The parser also emits a per-run summary carrying hive_source (the resolved hive classification, typically HKLM), entry_count (the number of device instances found) and source_path (the hive path that was read). These summary fields are useful for confirming coverage before reasoning about the absence of a device.
The single most important parsing rule for this artifact is the class-key naming convention. The USBSTOR class sub-key encodes the device type plus three ampersand-delimited tokens. Decoding it correctly is what turns an opaque key name into an attributable device. The JSON below is a representative Forenza USB device record. It depicts a Kingston DataTraveler stick with a hardware-reported serial number, last connected on 30 May 2026, that received drive letter E: at its last mount. Field ordering follows the parser output.
5. Performance Evaluation & Extended Technical Observations An examiner reads this record as: a Kingston DataTraveler 3.0 with a genuine (non-synthesised) serial was first seen on this host on 12 May and last attached on 30 May at 17:48 UTC. The parentidprefix is the pivot value used to resolve the drive letter from MountedDevices. The hardware ID list confirms the device class for cross-host matching.
USB device history is the most durable physical-device-to-host binding in the Windows registry. The serial number is, for devices that report one, globally unique, which means the same serial appearing in the USBSTOR key of two different hosts is strong evidence that the same physical device touched both machines. This is the foundation of removable-media exfiltration attribution and of mapping an insider’s device across the estate.
The lastconnectedat timestamp, combined with file-system timestamps and shellbag or LNK evidence, lets an examiner align a device attachment with a window of file copying. A USB stick attached at 17:48 followed by a burst of LNK creation pointing at E: and a spike in $UsnJrnl activity is the classic exfiltration signature. The parentidprefix to drive-letter resolution closes the loop by proving the device was the E: volume the user opened.
The artifact also carries negative-evidence value. A class key with a serial whose second character is & tells the examiner the device firmware did not report a unique serial, which both weakens attribution and is itself characteristic of cheap or deliberately anonymous devices. Absence of any USBSTOR instances on a host where exfiltration is suspected pushes the investigation toward network or cloud egress instead of removable media.
USB history is a registry artifact, so live-stream detection depends on the source that carries device-arrival telemetry. On hosts with Sysmon and PnP auditing, device arrivals also surface as event records, and the registry parse provides the durable backstop. The Sigma rule below targets the event-log surface for a newly-enumerated USB mass-storage device, which a SIEM can join against an approved-device allowlist.
For Microsoft Sentinel the equivalent KQL surfaces newly-seen USB device class strings per host by comparing the current day against a 30-day baseline. The query alerts only when a host enumerates a USBSTOR device class it has not seen before. Forenza ships its own SQL-derived DFIR Query Language (DQL), designed and developed in-house by the Forenza team, for incident-response queries against parsed artifact records and the unified timeline. Queries target the artifact_results table (per-case parsed records) or evidence_unified_timeline (cross-artifact correlation) and use JSONB field accessors ( normalized->>'field_name' ) against the canonical normalized column populated by the parser. DQL is submitted to POST /api/v1/query/run and executes server-side under tenant-scoped row-level security.
The first DQL example enumerates every USB device instance parsed for a case, ordered by last-connection time. This is the workhorse query an examiner opens an exfiltration case with: The second DQL example is the cross-host device-reuse hunt. The same physical serial number appearing in the USBSTOR records of more than one host across the tenant is strong evidence a single device was carried between machines: The third DQL example surfaces devices with OS-synthesised serial numbers (second character is & ), which are both attribution-weak and characteristic of anonymous or low-cost hardware. These warrant a closer look on sensitive hosts: The response carries columns , rows , row_count , execution_ms and a routing flag. Queries against artifact_results are always routed server-side under the tenant’s row-level security policy.
To register a recurring detection rather than a one-shot query, wrap the same DQL in a detection-rule definition and POST it to the detection service. The rule fires on every newly persisted USB device record matching the predicate and lands a row in findings at the configured severity: Forenza captures USB device history through three operator-facing collection paths: the web interface driving a deployed live agent, the standalone offline collector binary for hosts where an agent cannot be installed, and image-mode triage against a previously acquired disk image. All three paths feed the same parser pipeline, persist identical rows into artifact_results , and surface USB records to the same UI and DQL queries. The choice is operational, not analytical.
The web UI is the everyday collection path for incident response on agent-managed hosts. The operator never leaves the browser. When the suspect host has no Forenza agent (an isolated DMZ server, an OT operator console, a third-party-managed laptop, an air-gapped environment, or a host where deploying the agent would tip off an adversary), the standalone forenza-collector binary takes its place. The collector is a single-file, no-dependencies executable built per platform (Windows, Linux, macOS) and signed by the Forenza release pipeline. Operators carry it on a USB stick, a removable forensic drive, or a network-share path along with their incident-response kit.
When the source artefact is a disk image already in evidence storage (E01, EX01, raw .dd / .img , VHDX, VMDK, AFF4-Logical, multi-segment EWF), Forenza skips both the agent and the offline collector and reads the bytes directly from the image. The operator creates the case with Disk Image as the workspace mode at step 1 of Path 1, attaches the relevant evidence_packages row in step 2 (instead of an agent-managed host), then proceeds identically through steps 3 to 8.
Under the hood, Forenza’s accessor chain resolves the artifact path inside the image: file:// opens the container, ewf:// or vhdx:// or vmdk:// decodes the disk format, volume:// with a partition index reaches the Windows volume, and ntfs:// mounts the NTFS filesystem read-only so the path resolver can locate Windows/System32/config/SYSTEM . The same registry analyzer used in live mode and offline-collector mode consumes the hive bytes and produces identical artifact_results rows.
The USB DQL detection rules above run unchanged against image-derived data, which is exactly the property that lets the same Forenza tenancy host both live and post-mortem investigations side by side. Live agent telemetry is one investigation surface, but offline triage of the SYSTEM hive from a collected disk is equally important and often the only option in post-mortem work. The hive lives at %SystemRoot%System32configSYSTEM on a modern Windows host. It is a binary registry hive and can be parsed with any hive-aware tooling; Forenza’s registry analyzer reads it directly without mounting it into a live registry. The USBSTOR enumeration sits under the current control set, which on an offline hive must be resolved by reading SelectCurrent rather than relying on the runtime CurrentControlSet symbolic link.
When parsing offline, two cross-references complete the picture. The MountedDevices key, in the same hive, maps the device to its drive letter through the ParentIdPrefix value, so collect and decode it alongside USBSTOR. The plaintext setupapi.dev.log on the system volume independently records the first-install timestamp of each device driver and is invaluable for corroborating the registry-derived first-install time, especially on builds where the instance Properties subkeys are sparse.
For hosts where USBSTOR keys appear to have been scrubbed by a privacy tool, recovery from disk-level artifacts is sometimes possible. Volume Shadow Copies preserve historical SYSTEM hive states that may still contain a device cleaned from the current hive, and registry transaction logs ( SYSTEM.LOG1 / SYSTEM.LOG2 ) can hold uncommitted key writes. Always confirm coverage by comparing the device population across every recoverable hive state before concluding that a device was never present.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/List%20of%20digital%20forensics%20tools • https://en.wikipedia.org/wiki/Mobile%20device%20forensics • https://en.wikipedia.org/wiki/Computer%20forensics • https://hawkeyeforensic.com/usb-forensics-on-windows-systems/ • https://www.it-connect.tech/forensic-windows-part-15-tracing-usb-device-history/ • https://forenza.io/system-config-usb-devices/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Usb Forensic Investigation Tool For Windows Systems.
[*] Metasploit Scan Running on Target Subnet for Usb Forensic Investigation Tool For Windows Systems... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |