Complete Technical Paper Content — Usb Rubber Ducky Attack Detection And Prevention Tool
Overview & System Context
Usb Rubber Ducky Attack Detection And Prevention Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8533 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This guide covers USB Rubber Ducky™ hardware mark I (2011) and II (2022), as well as DuckyScript™ version 1.0 (2011) and 3.0 (2022).
The e-book PDF generated by this document may not format correctly on all devices. For the most-to-date version, please see https://docs.hak5.org DO NOT FLASH . The limited warranty does not cover damage caused by firmware flash. Flashing legacy or third-party firmware will render the device irrecoverable. The new USB Rubber Ducky is architected in conjunction with Payload Studio such that firmware flashing will never be required. Disregard articles related to the old USB Rubber Ducky and rely solely on the official documentation here at docs.hak5.org .
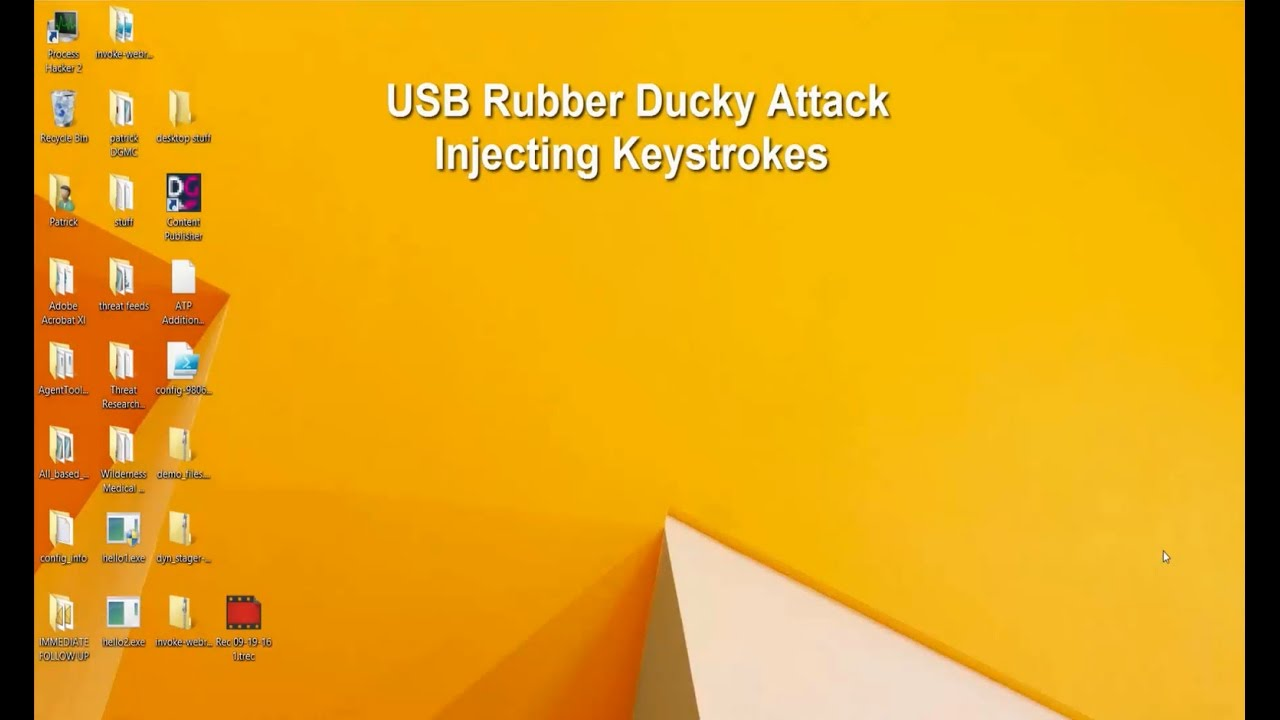
Hak5 introduced Keystroke Injection in 2010 with the USB Rubber Ducky™. This technique, developed by Hak5 founder Darren Kitchen, was his tool of choice for automating mundane tasks at his IT job — fixing printers, network shares and the like. Figure 1: Detecting a Rubber Ducky USB Attack with Digital Guardian Advanced ...
Today the USB Rubber Ducky is a hacker culture icon, synonymous with the keystroke injection technique it pioneered. It’s found its way into the hearts and toolkits of Cybersecurity and IT pros the world over — including many movies and TV shows! Core to its success is its simple language, DuckyScript™. Originally just three commands, it could be learned by anyone—regardless of experience—in minutes.
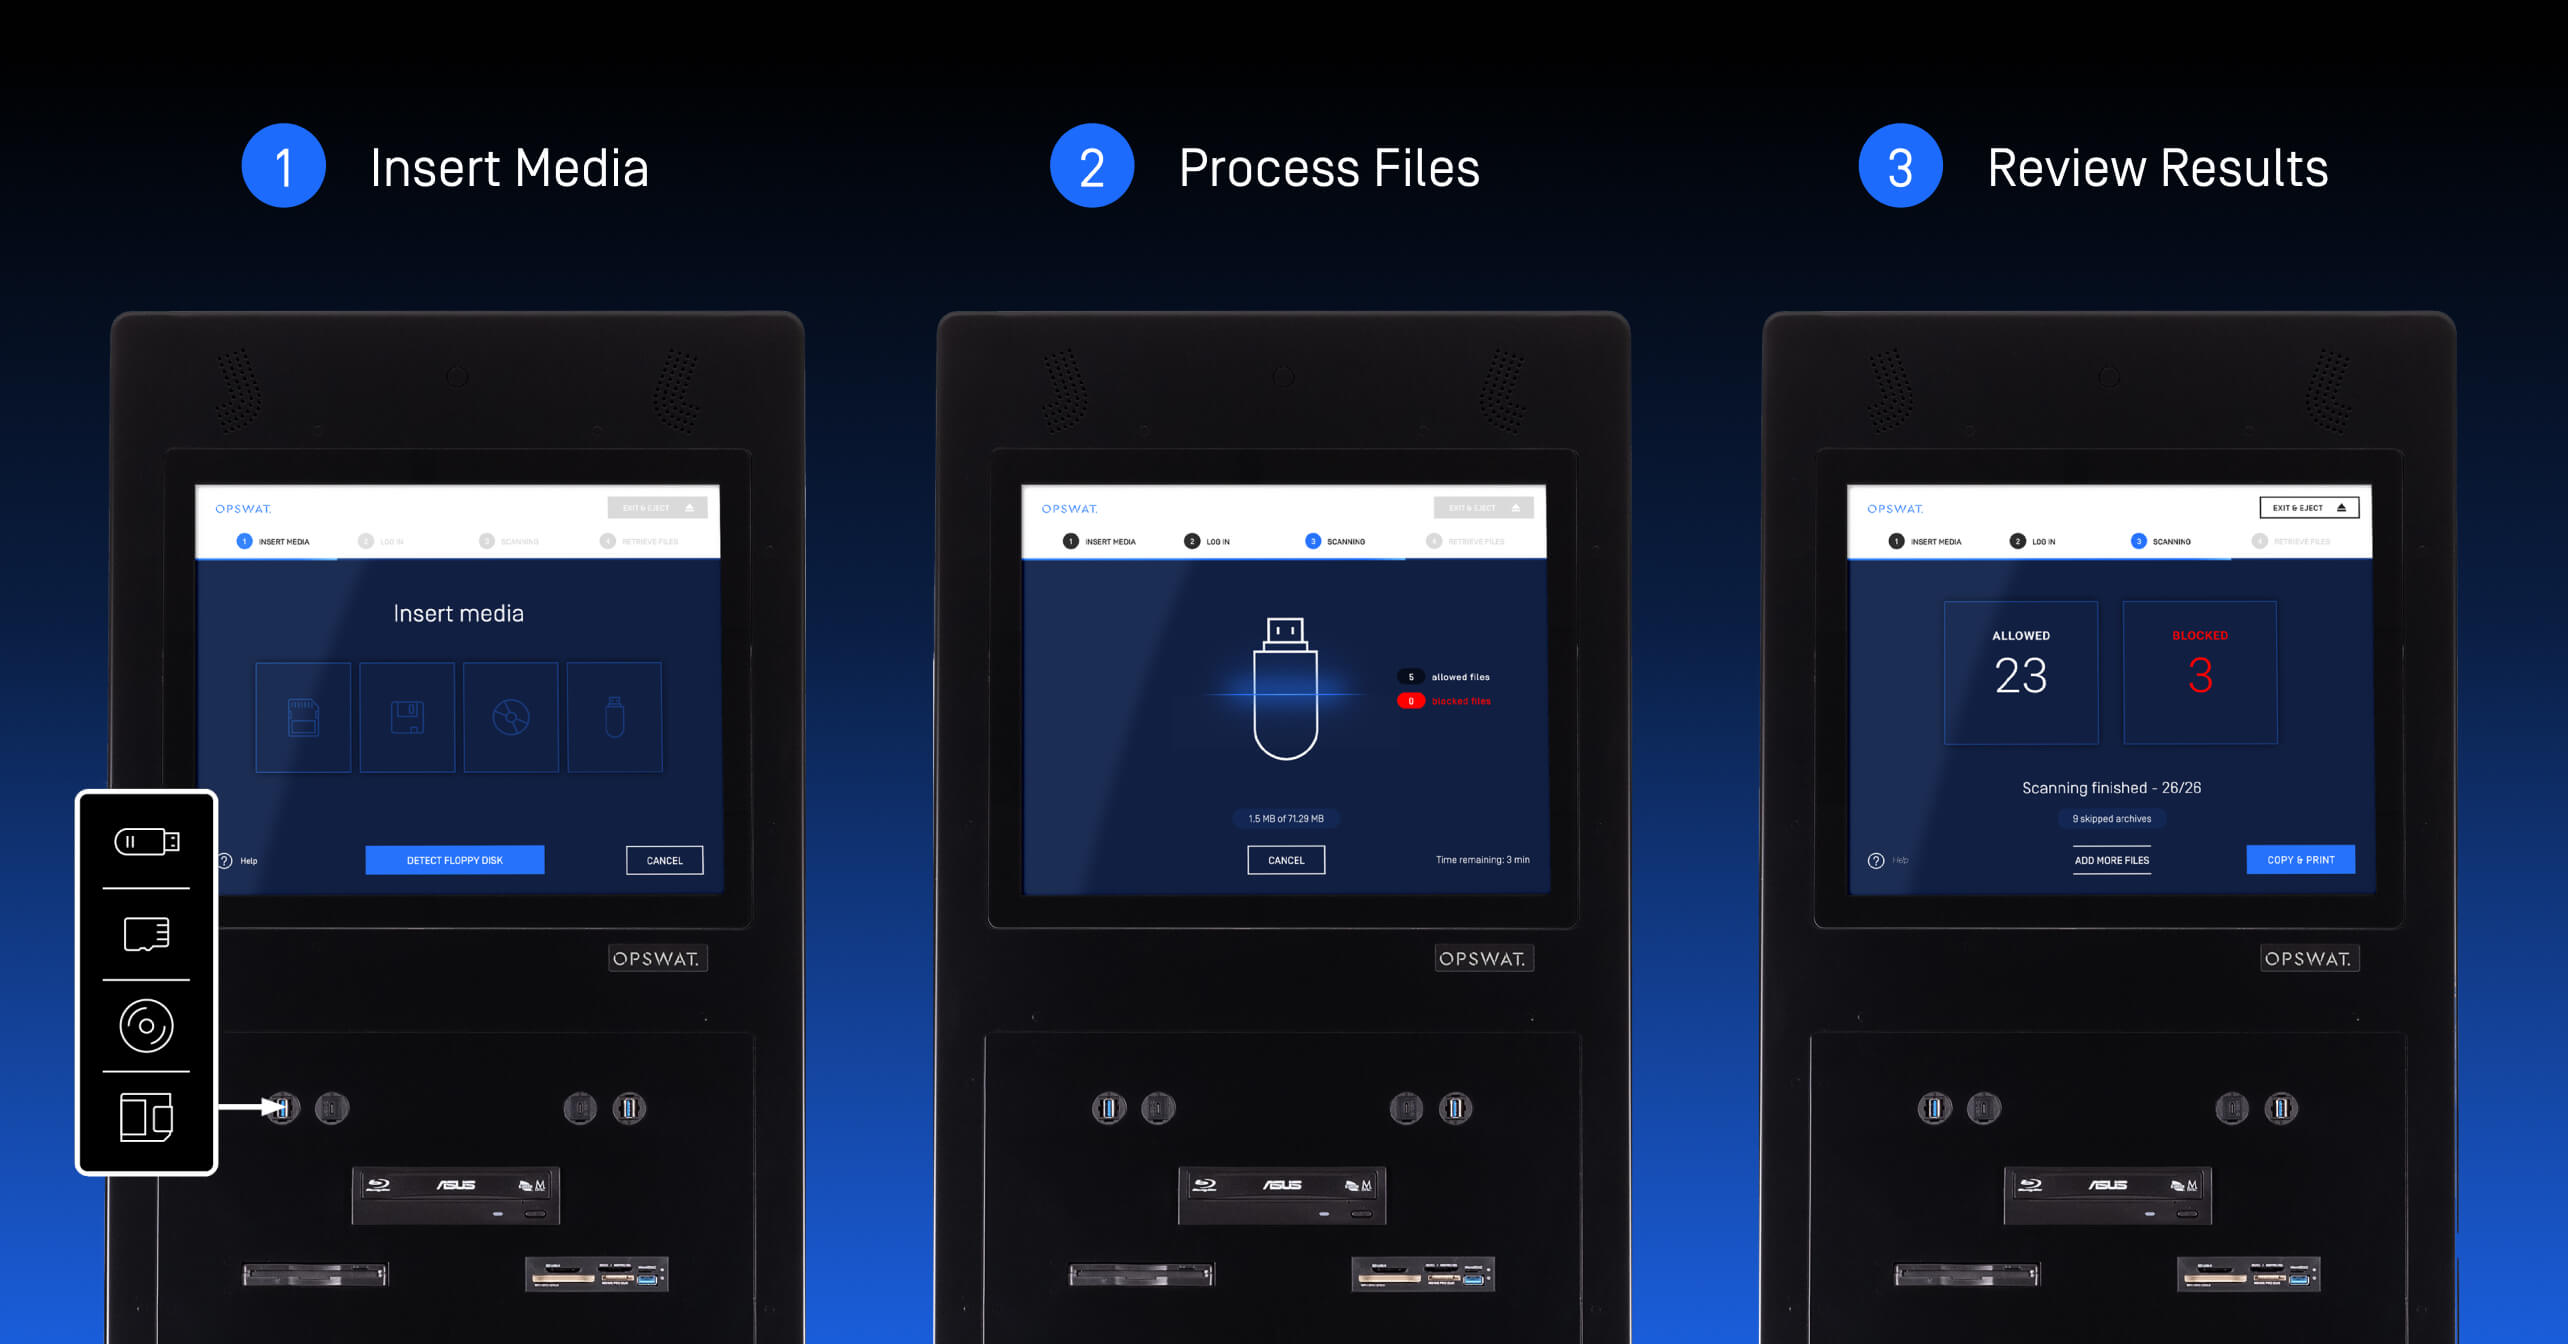
Now in version 3.0, DuckyScript is a feature rich structured programming language. It’s capable of the most complex attacks, all while keeping it simple. Following this guide you will learn and build on your knowledge — from keystroke injection to variables, flow control logic and advanced features. As you do, you’ll unlock ever more creative potential from your USB Rubber Ducky! Quack on! Figure 2: The Danger of a USB Device and Keystroke Injection Attack - OPSWAT DuckyScript 1.0, developed by Hak5 in 2010, is a macro scripting language. It sequentially processes one of two actions: keystroke injection (type a set of keys), and delay (momentarily pause). These actions, written in what is known as a payload, instruct the USB Rubber Ducky on what to do. Either type, or pause.
Over the years the DuckyScript language has evolved to include device specific commands. With the introduction of the Bash Bunny in 2017, DuckyScript was coupled with the shell scripting language BASH. Leveraging the Linux base, these DuckyScript payloads allowed the device to perform multi-vector USB attacks. Similarly, DuckyScript was included in the Shark Jack to probe Ethernet networks. The Key Croc uses DuckyScript 2.0 to execute a myriad of hotplug attacks based on live keylogging data. Even third party tools designed in partnership with Hak5 licensed DuckyScript — notably the O.MG Platform of malicious cables and adapters by Mischief Gadgets.
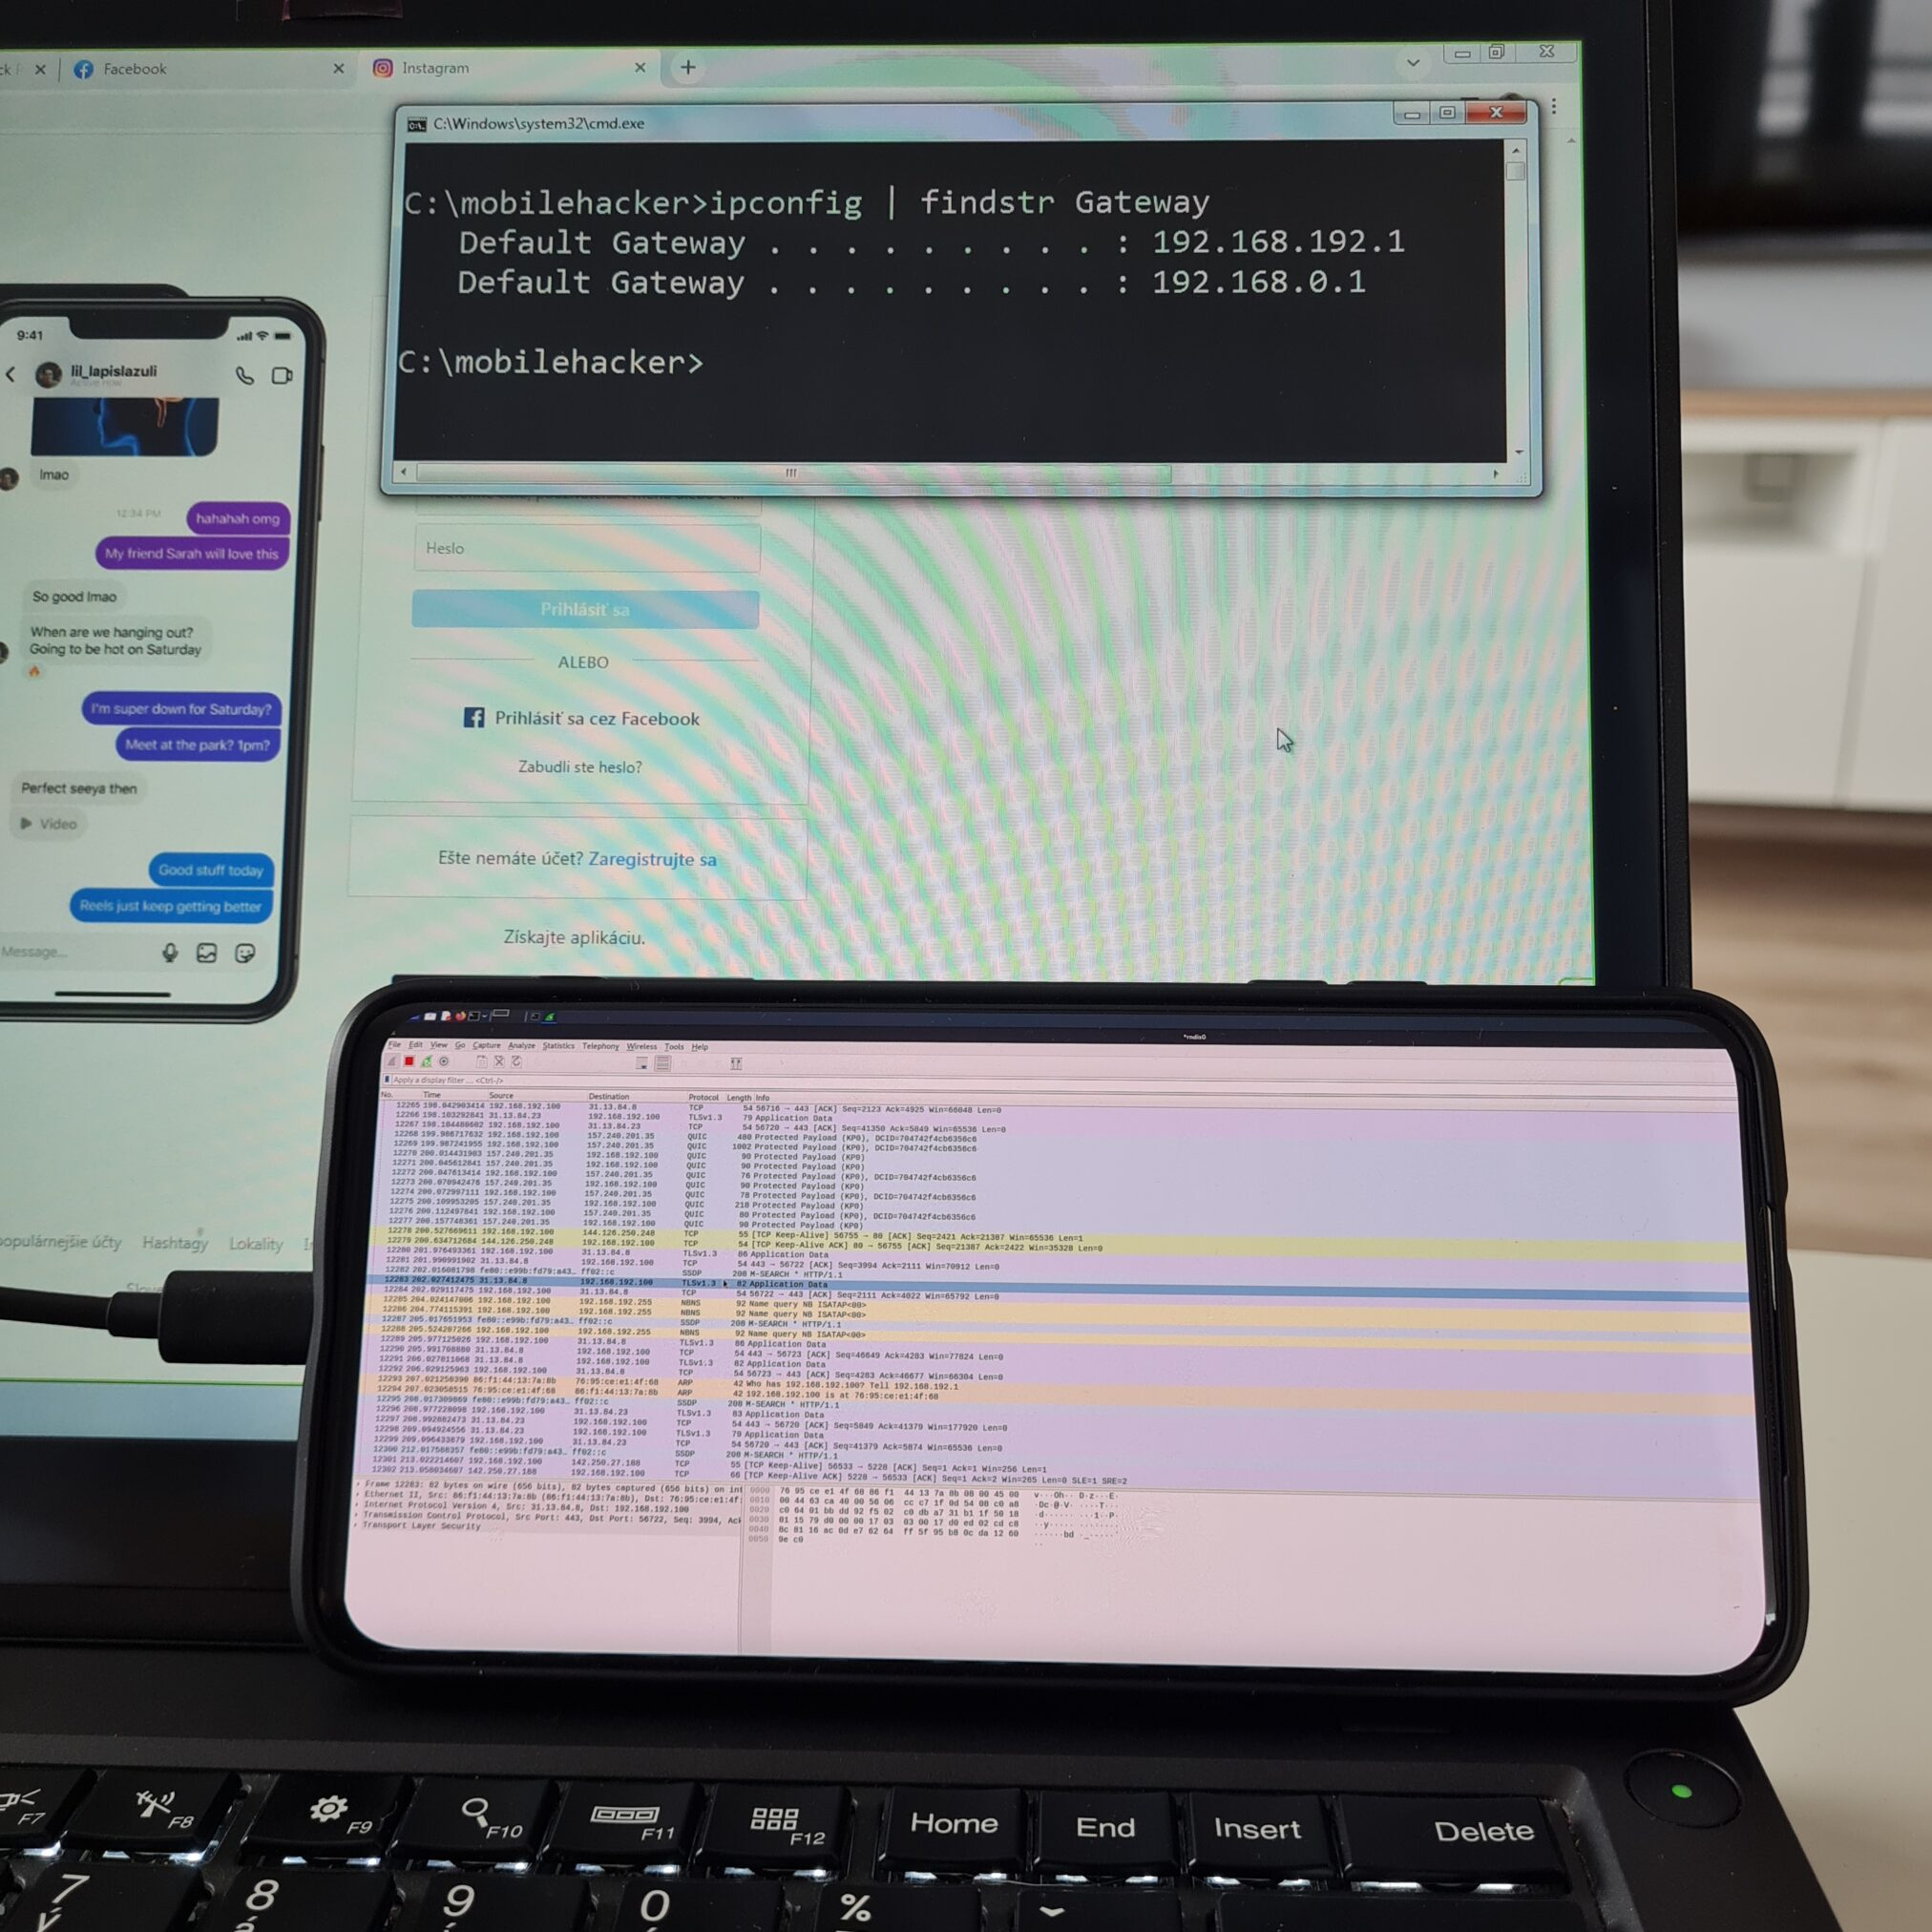
DuckyScript 3.0 is a feature rich, structured programming language. It includes all of the previously available commands and features of the original DuckyScript. Figure 3: NetHunter Hacker VI: Ultimate guide to HID attacks using Rubber Ducky ... Additionally, DuckyScript 3.0 introduces control flow constructs (if/then/else), repetition (while loops), functions, extensions.
Plus, DuckyScript 3.0 includes many features specific to keystroke injection attack/automation, such as HID & Storage attack modes, Keystroke Reflection, jitter and randomization to name a few. This documentation will cover the basics, then introduce each of the new features such that they build upon one another. USB Rubber Ducky and DuckyScript are subject to the Hak5 license agreement (https://hak5.org/license) DuckyScript is the intellectual property of Hak5 LLC for the sole benefit of Hak5 LLC and its licensees. To inquire about obtaining a license to use this material in your own project, contact us . Please report counterfeits and brand abuse to legal@hak5.org.
This material is for education, authorized auditing and analysis purposes where permitted subject to local and international laws. Users are solely responsible for compliance. Hak5 LLC claims no responsibility for unauthorized or unlawful use. Hak5 LLC products and technology are only available to BIS recognized license exception ENC favorable treatment countries pursuant to US 15 CFR Supplement No 3 to Part 740.
The USB Rubber Ducky is a discreet penetration testing device designed to operate covertly by masquerading as a standard USB keyboard. Its versatility lies in its capability to execute predefined scripts upon connection, enabling security professionals to evaluate and potentially exploit USB vulnerabilities. This device is an essential tool in USB security assessments, allowing for the simulation of various attack scenarios, providing a comprehensive evaluation of USB security.
Testing the Rubber Ducky is a necessary step in understanding how this USB device works and ensuring it is used responsibly. This process helps evaluate its potential impact and uncover any security risks it might pose. The functionalities listed below highlight potential risks associated with a Rubber Ducky: The Rubber Ducky can be programmed to mimic a keyboard and execute predefined scripts once connected to a computer.
This allows it to automate a sequence of keystrokes, potentially performing malicious actions. The Rubber Ducky can carry and execute payloads that exploit vulnerabilities in the target system. This might include downloading and executing malware, creating backdoors, or initiating other malicious activities. The device can be programmed to capture sensitive information such as usernames and passwords by simulating keyboard input. This information can then be exfiltrated or used for unauthorized access.
A Rubber Ducky can be used to launch network-based attacks once connected to a system. It might attempt to exploit vulnerabilities, perform privilege escalation, or establish unauthorized connections. The Rubber Ducky can be programmed to collect and exfiltrate sensitive data from the target system. This could include documents, credentials, or other confidential information.
By emulating a keyboard, the Rubber Ducky can trick the system into thinking it is a legitimate input device, enabling it to bypass certain security measures. Since the Rubber Ducky supports scripting languages, it can execute malicious scripts on the target system. This can be used to manipulate files, change system settings, or disrupt normal operations.
Mitigating the risks associated with Rubber Ducky and similar USB-based attacks involves a combination of technical measures, security practices, and user awareness. To protect against potential harm from devices like Rubber Ducky, it is essential for individuals and organizations to implement security measures such as: Deploying endpoint security solutions can monitor and control USB device usage on networks. These solutions can help detect and prevent unauthorized devices, including Rubber Ducky, from interacting with the system.
Implementing device authentication mechanisms ensures that only authorized USB devices can connect to host systems. This can involve using digital signatures or certificates to verify the legitimacy of connected devices. Physical access to USB ports should be restricted, particularly in sensitive environments. Measures such as USB port locks can be utilized to prevent unauthorized physical access, reducing the risk of connecting malicious devices.
Users should be made aware of the potential risks associated with connecting unknown USB devices. It is advisable to foster a security-conscious mindset and recommend against the use of untrusted USB devices or obtaining them from unreliable sources. Establish and enforce security policies regarding the use of USB devices within an organization. Clearly define acceptable use and implement controls to prevent unauthorized devices from connecting to company systems.
The use of behavioral analysis tools is recommended for identifying unusual or suspicious behavior, especially related to keyboard input. This approach assists in detecting and preventing automated script execution by devices like Rubber Ducky. Ensuring the operating systems, antivirus software, and security solutions are regularly updated is essential to address known vulnerabilities. Up-to-date systems provide protection against potential exploits that may be attempted by malicious devices.
Implementing network segmentation to isolate critical systems from less secure areas is recommended. This practice helps contain the impact of a potential breach and prevents lateral movement by malicious devices. Encrypting sensitive data is advised to safeguard it from unauthorized access, even in the event of an attempted interception or exfiltration by a malicious device. This adds an additional layer of security to protect critical data.
Regular security audits and penetration testing should be conducted to identify and address vulnerabilities in the network and systems. Simulating USB-based attacks helps assess the effectiveness of implemented security measures. Maintaining a whitelist of approved USB devices and permitting connections exclusively from devices on the list is advisable. This practice helps prevent unauthorized devices, including Rubber Ducky, from interacting with the system.
Implementing physical security measures, such as securing the physical location of computers and servers, is crucial. This helps prevent unauthorized individuals from gaining physical access and connecting malicious devices. By adopting a combination of these mitigation strategies, individuals and organizations can enhance their defenses against USB-based attacks, including those involving devices like Rubber Ducky. The key is to implement a multi-layered approach that includes technical controls, user education, and regular security assessments.
In penetration testing and automation scenarios, the USB Rubber Ducky utilizes Ducky Script commands to simulate keyboard actions. These commands allow security professionals to automate sequences of keystrokes for various testing purposes. Below are some fundamental Ducky Script commands: - DELAY [time]: Delays the specified time in milliseconds before executing the next command. Example: `DELAY 500`.
- REM [comment]: Adds a comment to the script, which is ignored during execution. Example: `REM This is a comment`. - STRING [text]: Types the specified text as if it were being entered via a keyboard. Example: `STRING Open Notepad ENTER` (opens Notepad). 2. System Architecture & Core Working Principles - SPACE: Simulates pressing the Spacebar key. Example: `STRING Hello SPACE World ENTER` (types "Hello World").
- CTRL [key]: Simulates holding down the Ctrl key. Example: `CTRL c` (copies selected text). - ALT [key]: Simulates holding down the Alt key. Example: `ALT F4` (closes the active window). - GUI [key]: Simulates pressing the GUI (Windows) key. Example: `GUI r` (opens the Run dialog). - REPEAT [number]: Repeats the next command or sequence of commands a specified number of times. Example: `REPEAT 3 { STRING Hello ENTER }` (prints "Hello" three times).
- DELAY [time]: Delays the specified time in milliseconds before executing the next command. Example: `DELAY 500`. Create a payload script using the Ducky Script language. This script outlines actions for the Rubber Ducky to execute upon connecting to a target system. Use a DuckEncoder tool to convert the script into an "injection.bin" file. For instance, using a Bash command with DuckEncoder: java -jar duckencoder.jar -i script.txt -o injection.bin Alternatively, tools like [Payload Studio (available on ( https://payloadstudio.hak5.org/community/ )] can be used for this conversion.
Transfer the resulting "injection.bin" file onto the USB Rubber Ducky for execution. This can be done by connecting the Rubber Ducky to a computer and treating it as a USB storage device to copy the binary file onto it. Insert the USB Rubber Ducky into the target system. Upon connection, it will execute the predefined payload script, simulating keyboard inputs.
Observe the impact of the script on the target system. Effectiveness of security measures can be assessed by monitoring the simulated sequence of actions triggered by the USB Rubber Ducky. USB Rubber Ducky detection cannot rely on blocking USB storage, because the device is not storage — it registers as a HID keyboard and types. Antivirus sees nothing, because there is no malicious file, only keystrokes. The detectable pattern is behavioral: a new keyboard enumerates and, within a second or two, a Run dialog or PowerShell launches and types faster than any human. This guide ships the Sigma rules for that pattern and the layered hardening that blocks the payload even when the keystrokes land.
A Rubber Ducky (or any BadUSB device — Bash Bunny, a malicious cable, a Flipper Zero in BadUSB mode ) is a hardware addition: MITRE ATT&CK T1200 — Hardware Additions , with the injected commands mapping to T1059.001 — PowerShell . A USB Rubber Ducky is a keystroke-injection tool shaped like a flash drive. When plugged in, it announces itself to the operating system as a keyboard and “types” a pre-programmed payload at machine speed — opening a Run dialog, launching PowerShell, and executing commands in the few seconds it takes to walk past an unlocked machine. Because the OS trusts keyboards implicitly, there is no permission prompt.
This is why it defeats the obvious controls. Blocking USB storage does nothing to a keyboard. Antivirus has no file to scan. The attack is the typing, so the defense has to model the typing — and what it spawns, the same way command injection detection watches what a process spawns rather than the input string alone. The defining fingerprint is timing and sequence : a keyboard appears and a scripting host runs almost immediately. No human plugs in a keyboard and launches PowerShell in under two seconds.
The detection chains a new HID keyboard to the process activity that follows it within seconds. Correlate that with the device-arrival event for high fidelity — a HID keyboard enumerating (Windows Event ID 6416 / DriverFrameworks-UserMode, or your EDR’s device-add telemetry) seconds before the shell launch. The correlation above depends on a device-arrival event, and on a default Windows install that event is not being recorded.
This is the step that quietly makes the whole detection theoretical. Enable Audit PnP Activity first. Without Event ID 6416 you have the second half of the correlation and not the first, which reduces a high-fidelity chained detection to a generic “a shell launched from Explorer” rule that fires constantly on developer workstations. That is the version most teams end up disabling, and they conclude the detection does not work when what failed was the telemetry.
The registry and SetupAPI sources are worth knowing separately. They are not alerting sources — they are what you interrogate on a host after the fact, and they persist long after the event log has rolled. During an investigation they answer “what has ever been plugged into this machine,” which is frequently the question that matters. Read the first rule above carefully and you will notice it carries a timeframe: 5s while selecting on a single condition. That is not a correlation — a timeframe is only meaningful alongside a count or a second event to join against, and a Sigma rule with one selection and a timeframe fires exactly as though the timeframe were absent.
Either way, the thing to internalise is that the detection is the join , and each half on its own is noise. A new keyboard is noise; a shell from Explorer is noise; a new keyboard followed by a shell in under two seconds is an attack. Publishing the halves separately and calling it a detection is a common way to ship coverage that does not exist. A USB device reports its own vendor ID and product ID . There is no attestation and no verification — the device says what it is, and the host believes it. A keystroke-injection device can therefore present the VID and PID of whatever keyboard your allowlist permits, and many purpose-built tools support exactly this because it is trivially achievable.
Serial numbers, exposed via the device instance ID, are somewhat better and are also self-reported. A device that clones the identity of a keyboard already enrolled in your allowlist is indistinguishable from that keyboard at the enumeration layer. The theoretically ideal detection is the typing itself. Human keystrokes arrive with substantial and irregular gaps; injected input is frequently orders of magnitude faster and unnaturally regular. Distinguishing them is straightforward when you have the data.
The problem is that you almost certainly do not. Inter-keystroke timing is not in any Windows event log — capturing it requires input-level instrumentation, which is what a keylogger is, with all the privacy, legal, and works-council consequences that implies. Some EDR products expose a derived version of this signal; most environments have no access to it at all. It is also evadable. Adding randomised delays between keystrokes is a one-line change in most injection tooling, and it costs the attacker a few seconds of dwell time.
This is why the process-and-timing correlation remains the practical detection. It uses telemetry you can actually collect, it does not require input surveillance, and it keys on the sequence the attack needs rather than on a characteristic the attacker can tune away. macOS has a genuine built-in mitigation. When an unrecognised keyboard is attached, macOS prompts to identify it before accepting input, which interrupts a walk-past attack directly. It is not absolute — a device impersonating an already-trusted keyboard, or a machine where somebody dismisses the prompt reflexively, gets through — but it is meaningfully more than Windows offers out of the box, and it is one of the few places the default configuration is on the defender’s side.
Linux has USBGuard , a policy framework that authorises devices by attribute before the kernel binds a driver. It is capable, it is genuinely effective, and it requires deliberate policy authoring — which means it protects servers and hardened workstations where somebody did that work and nothing else. For both, the endpoint telemetry story is weaker than Windows: fewer standard events, more reliance on your EDR’s device visibility. If your estate is mixed, verify what device-arrival telemetry you actually receive per platform rather than assuming the Windows pipeline generalises.
Point 7 is worth dwelling on. The 2016 study “Users Really Do Plug In USB Drives They Find” demonstrated that dropped-drive attacks work at scale — the overwhelming majority of drives left in a public area were picked up, and files were opened on a large fraction of them. The control that addresses that is not a Sigma rule. It is telling people, plainly and repeatedly, that found hardware goes to the security team unplugged, and making that the path of least resistance rather than a policy nobody has read.
Items 9 and 10 are prerequisites rather than improvements: without them the detection cannot fire and the investigation has no transcript, and both are single Group Policy settings. If you do nothing else from this list, turn those two on and confirm the events appear — a detection built on telemetry you never enabled looks identical to one that simply never matched. USB Rubber Ducky detection is behavioral, not signature-based: a HID keyboard enumerates and a script host launches faster than a human could type. Detect that correlation, and layer USB device control with application allowlisting so the payload fails even when the keystrokes succeed. The same HID-injection threat at firmware scale is BadUSB — controls for engineering teams . Continue with Flipper Zero NFC risk and WiFi deauthentication detection , or browse the full Hardware Security pillar.
Disclosure: Some links below are affiliate links. If you buy through them, darkpwn may earn a commission at no extra cost to you. We only recommend training and tools we actually use in our own lab, and affiliate links never influence editorial coverage. A Rubber Ducky registers as a HID keyboard, so you cannot block it by USB mass-storage policy. Detect the behavior instead: a new HID keyboard device enumerating immediately followed by rapid scripted input — a Run dialog, PowerShell, or a command shell launching within seconds of the device attaching, faster than a human types.
The Ducky injects keystrokes; it runs no file of its own, so there is nothing for signature-based antivirus to scan. The payload is whatever the typed commands do. Detection must focus on the input behavior and the processes the keystrokes spawn, not on a malicious file. Layer controls: USB device control that allowlists approved HID devices, application allowlisting (AppLocker/WDAC) to block the payloads keystrokes try to run, disabling the Run dialog and constrained-language PowerShell via policy, and screen-lock discipline so an unattended unlocked machine is not available.
The device itself maps to T1200 (Hardware Additions); the keystroke-injected commands typically map to T1059.001 (PowerShell) or other Command and Scripting Interpreter sub-techniques depending on the payload. BadUSB controls that survive contact with engineering teams — USB device control, HID allowlisting, USBGuard and WDAC, plus detection that does not block real work.
Evil twin access point defenses for blue teams — detect rogue APs with a WIDS, why 802.1X server-cert validation and WPA3 matter, plus a captive-portal DNS signal. A WiFi deauthentication detection guide — spot deauth floods with a WIDS, why 802.11w PMF and WPA3 help (and where they fall short, CVE-2023-21061), plus hardening.
TL;DR. Two USB Rubber Ducky payloads (Windows and Linux) are dissected step by step. Every action is mapped to a MITRE ATT&CK technique. Four academic detection approaches are evaluated. Practical mitigations are listed at the end. Useful for SOC analysts, red teamers, and anyone studying for Security+ or SC-200 who wants a real-world example of credential dumping, defence evasion, and indicator removal in one chain.
A USB Human Interface Device (HID) attack abuses the implicit trust an operating system gives to keyboards and mice. A device like the Hak5 Rubber Ducky looks like a keyboard to the host. The OS plugs it in, no questions asked. The "keyboard" then types attacker-controlled commands at machine speed, hundreds of keystrokes per second, executing a payload before any human could intervene.
3. Software Implementation, Frameworks & Protocols This repo walks through exactly what a Ducky payload does, why it works, and what defenders can do about it. Two virtual machines, one Windows target and one Linux target. The Ducky payload was loaded onto a USB device and triggered against each VM in turn. All actions and resulting telemetry were logged for analysis.
Full payload scripts are in /payloads/windows_ducky.txt and /payloads/linux_ducky.txt . Monitors typing rhythm, speed and inter-key timing. A Ducky injects keystrokes at machine-perfect intervals, a pattern no human produces. Useful as a first-line behavioural detection. Limits: requires per-user baselines, offers no protection on shared workstations, can be evaded by Duckies that randomise delays.
Source: Barbhuiya et al. (2012), International Symposium on Cyberspace Safety and Security . Builds a graph from process-creation, registry and file events triggered after a USB device is connected. Compares the graph against known-good patterns. Strong against multi-stage payloads like the ones in this repo, where the action chain itself is the signal.
Captures USB descriptor traffic at the physical layer and feeds it into a machine-learning classifier. Detects malicious devices regardless of payload obfuscation. Effective but requires dedicated hardware, limiting deployment outside high-security environments. Source: Denney et al. (2019), Conference on Security and Privacy in Wireless and Mobile Networks .
Combines signature-based and anomaly-based detection with a random-forest classifier. Trades single-method blind spots for higher coverage at the cost of complexity. This repo is for educational and defensive research only . The payloads are documented so analysts can learn to recognise the pattern and write detections. Running them against systems you do not own is illegal and unethical.
Muhammad Suhaib MSc Cyber Security (Distinction), University of the West of England CompTIA Security+ LinkedIn · suhaibkhan916@gmail.com USB Rubber Ducky HID attack analysis with every action mapped to MITRE ATT&CK, plus four detection approaches compared TL;DR. Two USB Rubber Ducky payloads (Windows and Linux) are dissected step by step. Every action is mapped to a MITRE ATT&CK technique. Four academic detection approaches are evaluated. Practical mitigations are listed at the end.
Useful for SOC analysts, red teamers, and anyone studying for Security+ or SC-200 who wants a real-world example of credential dumping, defence evasion, and indicator removal in one chain. A USB Human Interface Device (HID) attack abuses the implicit trust an operating system gives to keyboards and mice. A device like the Hak5 Rubber Ducky looks like a keyboard to the host. The OS plugs it in, no questions asked. The "keyboard" then types attacker-controlled commands at machine speed, hundreds of keystrokes per second, executing a payload before any human could intervene.
This repo walks through exactly what a Ducky payload does, why it works, and what defenders can do about it. Two virtual machines, one Windows target and one Linux target. The Ducky payload was loaded onto a USB device and triggered against each VM in turn. All actions and resulting telemetry were logged for analysis. Full payload scripts are in /payloads/windows_ducky.txt and /payloads/linux_ducky.txt .
Monitors typing rhythm, speed and inter-key timing. A Ducky injects keystrokes at machine-perfect intervals, a pattern no human produces. Useful as a first-line behavioural detection. Limits: requires per-user baselines, offers no protection on shared workstations, can be evaded by Duckies that randomise delays.
Source: Barbhuiya et al. (2012), International Symposium on Cyberspace Safety and Security . Builds a graph from process-creation, registry and file events triggered after a USB device is connected. Compares the graph against known-good patterns. Strong against multi-stage payloads like the ones in this repo, where the action chain itself is the signal.
Captures USB descriptor traffic at the physical layer and feeds it into a machine-learning classifier. Detects malicious devices regardless of payload obfuscation. Effective but requires dedicated hardware, limiting deployment outside high-security environments. Source: Denney et al. (2019), Conference on Security and Privacy in Wireless and Mobile Networks .
Combines signature-based and anomaly-based detection with a random-forest classifier. Trades single-method blind spots for higher coverage at the cost of complexity. This repo is for educational and defensive research only . The payloads are documented so analysts can learn to recognise the pattern and write detections. Running them against systems you do not own is illegal and unethical.
Muhammad Suhaib MSc Cyber Security (Distinction), University of the West of England CompTIA Security+ LinkedIn · suhaibkhan916@gmail.com This article serves as documentation for using the Rubber Ducky Detector developed by students of the FH Campus Wien. The Rubber Ducky Detector is a program running on a Raspberry Pi 4 Model B 8GB using RasPi OS that helps diminish attacks conducted with hotplug attack tools like the Hak5 Rubber Ducky . The Rubber Ducky is visually indistinguishable from a regular USB Stick, and pretends to be a Human Interface Device (HID) able to mimick keystrokes. The keystrokes can be pre-programmed in a custom payload. For further reference, see the detailed documentation for Hak5 Rubber Ducky .
The Rubber Ducky Detector is designed to run on an isolated system and provides a point where users can check unknown USB devices for maliciousness safely. After plugging in a device, the program checks if it is a Rubber Ducky. In case it is a legitimate USB drive, the Rubber Ducky Detector additionally checks for malicious file extensions and references the ClamAV anti virus library to check for infected files.
For the official distribution only , complete the setup process, open a terminal and clone the repository with the command The installer script installs all required dependencies automatically and offers optional configuration of the touchscreen and an autostart functionality. If permission to run the script is denied, make the script executable by entering the command After completing setup, enter the ducky-detector directory and compile the program by entering the command To scan a device, press 'OK' to initiate the process. After that , insert the USB drive, and press 'OK' again. If the connected device is an HID, the tool will cancel the scanning process and warn the user.
After passing the first check, the program will check for additional partitions on the device, and warn users if multiple partitions or file systems are detected. Press 'Details' for further information. If The Periphery Scan is complted and no critical Interface was detected, the Rubber Ducky Detector will check for malicious hidden partitions on the USB Stick. If the If all periphery scans are passed, the Rubber Ducky Detector analyses the file extensions of all files contained on the USB drive, and check for extensions with possible malicious consequences like executables. Press 'Details' for further information.
To scan the device for malware, a ClamAV Engine is created that subsequently accesses an online database to downloads signatures. It then checks the files against these signatures to detect infected files. Press 'Details' for further information. The project is hosted on GitLab . The GUI has recently been updated to be easily editable by using the tool Glade . The GUI is optimized for a small touchscreen, but can easily be edited and upscaled by using Glade. To edit, open the duckyDetector.glade file in Glade. To view applied changes in the actual running program, no recompilation is necessary as the application pulls the data from the Glade file at runtime.
The USB Rubber Ducky has been a potent threat for more than 15 years—innocent on the surface but paddling fast underwater. Tired of performing repetitive tasks in his IT job in 2010, Hak5 Founder Darren Kitchen took a creative route to efficiency. Using USB hardware modified to pose as a standard keyboard, Kitchen used scripting and keystroke injection to automatically send commands to the servers and printers he was administering.
The idea quickly morphed into the USB Rubber Ducky, the first commercially available keystroke injector. Despite looking like an innocent USB flash drive, the Ducky could inject 1,000 words per minute, automatically firing when plugged in. “You plug it in, and it acts like a keyboard,” explained Kieran Human, ThreatLocker Special Projects Engineer and head of Rubber Ducky labs at Zero Trust World.
“Anything you can do with a keyboard, this can do. It can open PowerShell, delete files, exfiltrate data, or encrypt it. You don’t even need elevated privileges to fire any of this stuff off, because you’re technically not executing scripts. You (or, more correctly, the Ducky) are just typing.” Because the device identifies itself as a standard human interface device (HID), the operating system grants it the same level of trust and access as a user’s actual keyboard.
No admin rights required, no suspicious binaries dropped, no obvious malware signatures created. 4. Practical Deployment, Analysis & Case Studies “You just create the PowerShell script and then run it. It could be literally anything. You can use it for any repetitive task; we had 500 computers that had to get connected to the internet, and instead of having to go to each one manually, I made a script that opened PowerShell and connected them automatically and did a few other fixes.” “In my lab sessions, I’ve put together a script that will take screenshots of your computer every 10 seconds, or one that copies your clipboard every minute and uploads it. There is another one that will detect if you copy a Bitcoin address and then switch it with a fake one. I’ve even managed to put ransomware on a Ducky. One major endpoint detection and response (EDR) vendor initially detected it, but after I split it up and made a couple of changes, they couldn’t see it. I ran it across multiple EDRs, the big EDRs you hear about, and none of them detect it. It’s straight ransomware.” This is the uncomfortable truth: Behavioral security tools are trained to detect malware, not a user typing at lightning speed.
And since blocking keyboards is not generally an option, the Rubber Ducky cannot be stopped conventionally. In the years since the product first reached the market, it has evolved significantly, making detection even more difficult. That is true post-attachment, with modern iterations of the Ducky platform able to slow typing to human speed and cadence, avoiding behavioral detection.
And it is true of the physical form of the Rubber Ducky, too. Though many versions remain packaged in the familiar USB flash drive shell, some now hide in the limited space usually afforded to e-marker chips in USB cables. The only practical defensive strategies for stopping Rubber Ducky attacks involve removing the ability of the scripts to do any damage, reducing the attack surface, and containing the blast radius through microsegmentation.
“Even if you need access to PowerShell,” explained Human, “using Ringfencing properly means it can’t access all your files, and it can’t access the internet. If you don’t need PowerShell, block it with Application Allowlisting. The whole point is that even if the Ducky gets a command through, the application it launches shouldn’t be allowed to do anything it isn’t allowed to do.” Even though a Rubber Ducky masquerades as a genuine keyboard, ThreatLocker can neutralize what it attempts to do after the keystrokes land.
Ducky payloads rely heavily on PowerShell, the command prompt, and other script interpreters. Allowlisting ensures that only approved applications can run. If an endpoint does not need PowerShell, block it entirely; if it does, restrict its use. Ringfencing isolates applications from one another and from sensitive data. A Rubber Ducky script may successfully launch PowerShell, but ThreatLocker prevents it from reading user documents, connecting to remote repositories, executing unapproved binaries, or exfiltrating content that is outside its permission boundary.
The payload may “run,” but it becomes functionally toothless. Many Ducky scripts rely on outside sources. Even if a Ducky attempts to download a full malicious script from an attacker’s server, which is a common tactic to evade detection, ThreatLocker can block outbound traffic from tools that should not have internet access. While Rubber Duckies tend to use only minimal storage, many attackers pair HID devices with the capacity of traditional USB drives. ThreatLocker can enforce device-level restrictions to prevent data exfiltration or the execution of unwanted files.
Most Rubber Ducky payloads never drop files and are therefore invisible to traditional EDR signature-based detection. Policy-based enforcement stops the behavior, not the specific file. Get more cybersecurity insights from Cyber Hero Frontline , a magazine by ThreatLocker. Try ThreatLocker free for 30 days and experience full Zero Trust protection in your own environment.
Schedule a customized demo and explore how ThreatLocker aligns with your security goals. Just starting to explore our platform? Find out what ThreatLocker is, how it works, and how it’s different. In a world where cyber threats are evolving every day, the USB Rubber Ducky stands out as a particularly insidious tool for launching attacks on IT infrastructure . This inconspicuous gadget, posing as a regular flash drive, can take control of a computer system in seconds, bypassing standard security measures. With a growing number of incidents involving such devices, organizations must be prepared to fend off increasingly sophisticated attacks. In this article, we take a comprehensive approach to protecting against the USB Rubber Ducky threat, combining technical with organizational and training aspects.
USB Rubber Ducky is an advanced penetration tool that externally resembles an ordinary USB flash drive. It was created by Hak5 as a tool for penetration testing and security audits. The device uses a microprocessor with its own operating system to emulate a USB keyboard. Unlike standard USB flash drives, Rubber Ducky can execute complex sequences of commands, simulating rapid keyboard input. This functionality makes it particularly dangerous in the wrong hands.
It is worth noting that despite its original purpose for educational and testing purposes, the USB Rubber Ducky is often used by cybercriminals to launch attacks against organizations of all sizes. ðIII Read the complete guide: SOC : Security Operations Center - what it is, how it works, how to choose The USB Rubber Ducky uses the HID (Human Interface Device) protocol, which is recognized by operating systems as an input device by default, just like a keyboard or mouse. This allows it to bypass many of the standard security features used with regular USB media.
Once connected to a computer, the device immediately begins executing pre-programmed commands. The speed of operation is impressive - it can enter hundreds of characters per second, making manual user intervention virtually impossible. The operating system treats all commands as legitimate user actions because they come from a âIItrustedâII input device. This makes it so that traditional malware security systems may not detect the threat.
In addition, scripts executed by USB Rubber Ducky can be encrypted and hidden from standard analysis tools, making them difficult to detect and analyze. USB Rubber Ducky can pose a serious security threat to organizations on multiple levels. In the hands of an attacker, it can be used to quickly execute malicious scripts that can steal credentials, install backdoors or create new administrative accounts.
Particularly dangerous is the fact that an attack can be carried out in a matter of seconds, often without the userâIIs knowledge. An attacker can take advantage of a moment of inattention by an employee or physical access to an unsecured workstation. WhatâIIs more, the USB Rubber Ducky can be used to bypass security features such as firewalls and intrusion detection systems, as it operates at the operating system level as a legitimate input device.
The threat is all the more serious because the device can be used to launch multi-stage attacks, where the initial script creates a gateway for the attackerâIIs later, more complex actions. The main difference between a USB Rubber Ducky and a standard flash drive lies in the way the device communicates with the operating system. A regular USB flash drive is recognized as a storage device, while the Rubber Ducky presents itself as a keyboard.
This fundamental difference allows USB Rubber Ducky to work even in environments where standard USB media are blocked by security policies. The system sees it as an HID device, which is usually allowed to be used. Another major difference is that Rubber Ducky has its own processor and memory, which allow it to perform complex operations independently of the host system. This makes it possible to launch more sophisticated attacks than ordinary malicious pendrives.
Traditional methods of securing USB ports often focus on blocking access to storage and controlling data transfer. However, in the case of USB Rubber Ducky, these safeguards prove insufficient, as the device is not detected as a storage medium. Standard antivirus software may not detect the threat because from its perspective, all actions look like legitimate keyboard command input. This makes traditional malware detection systems virtually useless in this case.
In addition, the speed of USB Rubber Ducky means that even if the system detects suspicious activity, it may be too late to respond effectively. Traditional monitoring and alerting mechanisms may not be able to keep up with the pace of malicious commands. The problem is exacerbated by the fact that many organizations focus on network and software security, neglecting the physical aspects of security, such as controlling access to USB ports.
Recognizing a USB Rubber Ducky attack requires special vigilance and knowledge of the characteristic signs. One of the first signs may be unusual keyboard activity, especially when no one is physically entering commands at a given position. Watch out for sudden command line openings, rapid command sequences or unexpected changes in system configuration. The system may show signs of slowdown associated with executing a large number of commands in a short period of time.
System monitoring should catch suspicious activities, such as creating new user accounts, modifying the Windows registry or attempting to establish unauthorized network connections. Special attention should be paid to activities performed with administrator privileges. It is also important to monitor physical USB ports for unauthorized device connections. Every new HID device should be verified for legitimacy of its use.
Effective protection against USB Rubber Ducky attacks requires a multi-level approach to security. A basic element is the implementation of physical access control to USB ports by blocking or disabling them where they are not needed. It is crucial to implement advanced USB device management systems that can recognize and control different types of HID devices. These systems should be able to whitelist allowed devices and block all others.
Software that monitors keyboard activity and detects unusual command input patterns should also be used. SIEM (Security Information and Event Management) systems should be configured to detect suspicious command sequences and quickly alert the security team. Consider implementing endpoint protection solutions that can detect and block suspicious scripts and automatic command execution, even if they come from HID devices.
Securing USB ports in a corporate environment requires a comprehensive approach combining technical solutions with appropriate procedures. The first step is to audit all available USB ports and determine which ones are actually necessary for operation. 5. Performance Evaluation & Extended Technical Observations An Endpoint Detection and Response (EDR) device management system should be implemented to centrally manage access to USB ports. The system should allow you to specify in detail what types of devices can be connected to which ports.
ItâIIs a good idea to use physical locks on USB ports in vulnerable areas, such as workstations in public spaces or computers running critical systems. In addition, special caps or covers can be used to prevent physical access to unused ports. Configuring Windows to protect against USB Rubber Ducky attacks should include several key aspects. First of all, Group Policy capabilities should be used to control access to USB devices and configure security policies. This is especially important in the context of the previously discussed threats related to automatic recognition of HID devices.
It is important to enable and properly configure Windows Defender Device Guard and Credential Guard, which can help prevent the execution of unauthorized scripts and protect credentials. Advanced auditing features for USB device connection events should also be activated. These mechanisms are the first line of defense against malicious USB devices. The system should be configured to require elevated privileges to perform potentially dangerous operations, even if they come from HID devices. It is also worth considering implementing third-party solutions that support native Windows security mechanisms. This is especially important for organizations handling sensitive data or subject to industry regulations.
Regularly updating the system and applying the latest security patches is key to maintaining effective protection against new variants of attacks. It is also worth considering the implementation of WSUS (Windows Server Update Services) in larger organizations, which will allow for controlled and systematic management of security updates. Choosing the right USB monitoring tools is crucial for effective protection against attacks. It is worth considering the implementation of specialized solutions like USB Device Monitoring, which offer detailed insight into USB device activity on the corporate network.
SIEM systems should be configured to collect and analyze logs related to USB device activity. Particular attention should be paid to tools that offer the ability to detect anomalous behavior of HID devices and respond quickly to suspicious activity. It is also worth deploying endpoint monitoring solutions that can detect and block suspicious scripts and automatic command execution. These tools should be able to produce detailed reports and alerts in real time.
Creating an effective USB security policy requires a systematic approach and consideration of the specifics of the organization. The policy should clearly define the rules for the use of USB devices, the procedures for their authorization and the consequences of violating the established rules. It is crucial to define processes for verifying and registering USB devices used in the organization. It is necessary to determine which departments and positions require access to USB ports and what types of devices are allowed on a case-by-case basis.
The policy should also include procedures for responding to incidents of unauthorized use of USB devices and guidelines for regular security training and audits. It is important that the document be updated regularly in response to new threats and the changing needs of the organization. Employee training is a key component of Rubber DuckyâIIs USB attack protection system. Employees must understand the nature of the threat and be able to recognize potential attack attempts. Training should be regular and tailored to different levels of technical expertise.
The training program should include practical threat demonstrations and attack scenarios so that employees can better understand how such devices work. Employees should also be taught proper procedures for reporting suspicious incidents and responding to potential threats. It is important to build awareness that security is the responsibility of all members of the organization. Employees should understand why certain restrictions and procedures are necessary to keep IT infrastructure secure.
The response to a detected USB Rubber Ducky attack must be swift and coordinated. The first step should be to immediately disconnect the suspected device and isolate the infected system from the corporate network to prevent the threat from spreading. The security team should immediately begin analyzing system and network logs to determine the extent of a potential security breach. It is critical to document all activities and collect digital evidence that may be needed in a later investigation.
Security incident management procedures should be activated, including notifying the appropriate people in the organization and, if necessary, external security experts. In parallel, a quick audit of other systems should be conducted for similar signs of compromise. Regular testing of security effectiveness is essential to maintain a high level of protection against USB Rubber Ducky attacks.
Organizations should conduct controlled penetration tests using similar devices to test the effectiveness of implemented protection mechanisms. Tests should include a variety of attack scenarios, including attempts to use different variants of scripts and security bypass techniques. It is important that the tests be conducted in a secure, isolated environment that does not compromise the production IT infrastructure.
It is also important to verify the effectiveness of incident detection and response procedures. Simulated attacks make it possible to assess how quickly and effectively the security team is able to detect and stop a potential threat. The contingency plan should be a comprehensive document outlining the exact procedures to be followed in the event of a successful USB Rubber Ducky attack. It should include clearly defined roles and responsibilities of individual team members and precise instructions for next steps. In the context of the previously discussed threats, it is particularly important to consider the specifics of attacks using HID devices.
A key component of the plan is to define procedures for isolating and recovering infected systems. Detailed instructions should be prepared for creating and restoring backups, as well as procedures for verifying the integrity of systems after an attack. The plan should address various attack scenarios, including those using the advanced security bypass techniques discussed in earlier sections.
The plan should also include communication aspects, specifying who and how various stakeholder groups should be informed of the situation. It is important that it also include guidelines for external communication, especially if customers or business partners may be affected by the attack. In this context, it is important to keep in mind the legal requirements for reporting security incidents to the appropriate authorities.
Regular review and updating of the emergency plan is essential to maintain its effectiveness. It is worth conducting periodic drills and simulations so that the team is well prepared to implement procedures in an emergency. These drills should be correlated with the employee training program mentioned earlier in this article. Protecting against USB Rubber Ducky threats requires a comprehensive approach combining technical solutions, organizational procedures and employee awareness. An effective defense strategy must take into account all the aspects discussed in the article: from the proper configuration of systems, to monitoring and access control, to training and incident response procedures.
Keep in mind that security is an ongoing process, requiring regular knowledge updates and adapting security to new threats. Organizations that take a proactive approach to protecting themselves from USB Rubber Ducky attacks will be better prepared for todayâIIs cyber security challenges. The USB Rubber Ducky v2 is an essential tool in the Hak5 pentesting ecosystem, engineered for stealth, efficiency, and full operational reliability.
This guide covers USB Rubber Ducky™ hardware mark I (2011) and II (2022), as well as DuckyScript™ version 1.0 (2011) and 3.0 (2022). [!WARNING] The e-book PDF generated by this document may not format correctly on all devices. For the most-to-date version, please see https://docs.hak5.org [!CAUTION] DO NOT FLASH . The limited warranty does not cover damage caused by firmware flash. Flashing legacy or third-party firmware will render the device irrecoverable. The new USB Rubber Ducky is architected in conjunction with Payload Studio such that firmware flashing will never be required. Disregard articles related to the old USB Rubber Ducky and rely solely on the official documentation here at docs.hak5.org .
Hak5 introduced Keystroke Injection in 2010 with the USB Rubber Ducky™. This technique, developed by Hak5 founder Darren Kitchen, was his tool of choice for automating mundane tasks at his IT job — fixing printers, network shares and the like. Today the USB Rubber Ducky is a hacker culture icon, synonymous with the keystroke injection technique it pioneered. It’s found its way into the hearts and toolkits of Cybersecurity and IT pros the world over — including many movies and TV shows! Core to its success is its simple language, DuckyScript™. Originally just three commands, it could be learned by anyone—regardless of experience—in minutes.
Now in version 3.0, DuckyScript is a feature rich structured programming language. It’s capable of the most complex attacks, all while keeping it simple. Following this guide you will learn and build on your knowledge — from keystroke injection to variables, flow control logic and advanced features. As you do, you’ll unlock ever more creative potential from your USB Rubber Ducky! Quack on! DuckyScript 1.0, developed by Hak5 in 2010, is a macro scripting language. It sequentially processes one of two actions: keystroke injection (type a set of keys), and delay (momentarily pause). These actions, written in what is known as a payload, instruct the USB Rubber Ducky on what to do. Either type, or pause.
Over the years the DuckyScript language has evolved to include device specific commands. With the introduction of the Bash Bunny in 2017, DuckyScript was coupled with the shell scripting language BASH. Leveraging the Linux base, these DuckyScript payloads allowed the device to perform multi-vector USB attacks. Similarly, DuckyScript was included in the Shark Jack to probe Ethernet networks. The Key Croc uses DuckyScript 2.0 to execute a myriad of hotplug attacks based on live keylogging data. Even third party tools designed in partnership with Hak5 licensed DuckyScript — notably the O.MG Platform of malicious cables and adapters by Mischief Gadgets.
DuckyScript 3.0 is a feature rich, structured programming language. It includes all of the previously available commands and features of the original DuckyScript. Additionally, DuckyScript 3.0 introduces control flow constructs (if/then/else), repetition (while loops), functions, extensions. Plus, DuckyScript 3.0 includes many features specific to keystroke injection attack/automation, such as HID & Storage attack modes, Keystroke Reflection, jitter and randomization to name a few.
This documentation will cover the basics, then introduce each of the new features such that they build upon one another. USB Rubber Ducky and DuckyScript are subject to the Hak5 license agreement ( https://hak5.org/license ) DuckyScript is the intellectual property of Hak5 LLC for the sole benefit of Hak5 LLC and its licensees. To inquire about obtaining a license to use this material in your own project, contact us . Please report counterfeits and brand abuse to legal@hak5.org .
This material is for education, authorized auditing and analysis purposes where permitted subject to local and international laws. Users are solely responsible for compliance. Hak5 LLC claims no responsibility for unauthorized or unlawful use. Harvested Online Documentation & Reference Sources • https://documentation.hak5.org/hak5-usb-rubber-ducky • https://wiki.elvis.science/index.php?title=USB_Rubber_Ducky:_Threats_and_Mitigation • https://darkpwn.com/posts/usb-rubber-ducky-detection-patterns/ • https://github.com/suhaibkhan916/usb-hid-attack-detection-mitre • https://github.com/suhaibkhan916/usb-hid-attack-detection-mitre/blob/main/README.md • https://wiki.elvis.science/index.php?title=Rubber_Ducky_Detector • https://www.threatlocker.com/blog/usb-rubber-ducky-attacks-explained-keystroke-injection-evasion-and-defense • https://nflo.tech/knowledge-base/usb-rubber-ducky-how-to-defend-against-it-safety-rules/ • https://doc.yupitek.com/hak5/products/usb-rubber-ducky/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Usb Rubber Ducky Attack Detection And Prevention Tool.
[*] Metasploit Scan Running on Target Subnet for Usb Rubber Ducky Attack Detection And Prevention Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |