Complete Technical Paper Content — Video Steganography For Secure Communication In Python
Overview & System Context
Video Steganography For Secure Communication In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7695 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background An anonymous P2P communication system is a peer-to-peer distributed application in which the nodes, which are used to share resources, or participants are anonymous or pseudonymous. Anonymity of participants is usually achieved by special routing overlay networks that hide the physical location of each node from other participants. Interest in anonymous P2P systems has increased in recent years for many reasons, ranging from the desire to share files without revealing one's network identity and risking litigation to distrust in governments, concerns over mass surveillance and data retention, and lawsuits against bloggers.
Censorship at the local, organizational, or national level Personal privacy preferences such as preventing tracking or data mining activities The material or its distribution is considered illegal or incriminating by possible eavesdroppers Material is legal but socially deplored, embarrassing or problematic in the individual's social world Fear of retribution (against whistleblowers, unofficial leaks, and activists who do not believe in restrictions on information nor knowledge) A particularly open view on legal and illegal content is given in The Philosophy Behind Freenet. Governments are also interested in anonymous P2P technology. The United States Navy funded the original onion routing research that led to the development of the Tor network, which was later funded by the Electronic Frontier Foundation and is now developed by the non-profit organization The Tor Project, Inc.
Anonymous blogging is one widespread use of anonymous networks. While anonymous blogging is possible on the non-anonymous internet to some degree too, a provider hosting the blog in question might be forced to disclose the blogger's IP address (as when Google revealed an anonymous blogger's identity). Anonymous networks provide a better degree of anonymity. Flogs (anonymous blogs) in Freenet, Syndie and other blogging tools in I2P and Osiris sps are some examples of anonymous blogging technologies. One argument for anonymous blogging is a delicate nature of work situation. Sometimes a blogger writing under their real name faces a choice between either staying silent or causing a harm to themselves, their colleagues or the company they work for. Another reason is risk of lawsuits. Some bloggers have faced multimillion-dollar lawsuits (although they were later dropped completely); anonymous blogging provides protection against such risks.
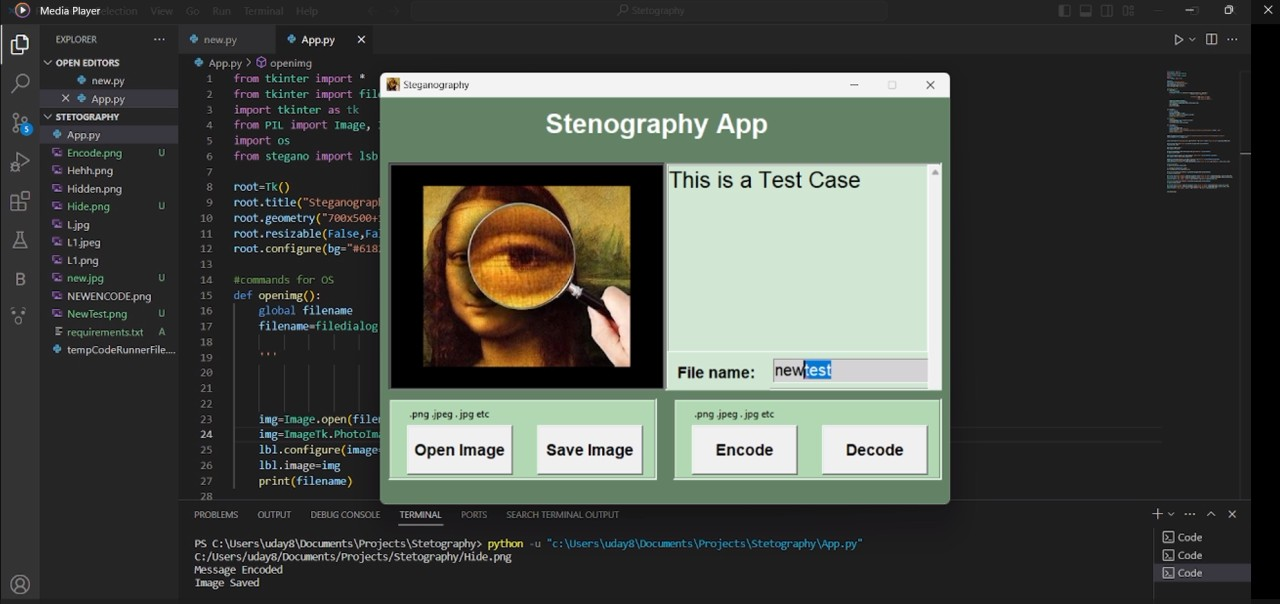
Like conventional P2P networks, anonymous P2P networks can implement either opennet or darknet (often named friend-to-friend) network type. This describes how a node on the network selects peer nodes: Figure 1: Introducing Steganography App with Python and Tkinter | Uday Singh ... In opennet network, peer nodes are discovered automatically. There is no configuration required but little control available over which nodes become peers. In a darknet network, users manually establish connections with nodes run by people they know. Darknet typically needs more effort to set up but a node only has trusted nodes as peers. Some networks like Freenet support both network types simultaneously (a node can have some manually added darknet peer nodes and some automatically selected opennet peers) . In a friend-to-friend (or F2F) network, users only make direct connections with people they know. Many F2F networks support indirect anonymous or pseudonymous communication between users who do not know or trust one another. For example, a node in a friend-to-friend overlay can automatically forward a file (or a request for a file) anonymously between two "friends", without telling either of them the other's name or IP address. These "friends" can in turn forward the same file (or request) to their own "friends", and so on. Users in a friend-to-friend network cannot find out who else is participating beyond their own circle of friends, so F2F networks can grow in size without compromising their users' anonymity. Some friend-to-friend networks allow the user to control what kind of files can be exchanged with "friends" within the node, in order to stop them from exchanging files that user disapproves of. Advantages and disadvantages of opennet compared to darknet are disputed, see friend-to-friend article for summary.
Syncthing – a free, open-source peer-to-peer file synchronization application. It can sync files between devices. Data security and data safety are built into the design of the software. Resilio Sync – a proprietary alternative to Syncthing Filetopia – not anonymous but encrypted friend-to-friend. File sharing, chat, internal mail service OneSwarm – a backwards compatible BitTorrent client with privacy-preserving sharing options, aims to create a large F2F network. Retroshare – filesharing, serverless email, instant messaging, VoIP, chatrooms, and decentralized forums.
anoNet – extensible IP anonymizer with steganography support (in development) Crowds – Reiter and Rubin's system for "blending into a crowd" has a known attack P2PRIV – Peer-to-Peer diRect and anonymous dIstribution oVerlay – anonymity via virtual links parallelization – currently in development and has significant, unsolved problems in a real world environment Phantom Anonymity Protocol – a fully decentralized high-throughput anonymization network (no longer in development) Race (Resilient Anonymous Communication for Everyone) – A project by DARPA to build an anonymous, attack-resilient mobile communication system that can reside completely within a network environment, capable of avoiding large-scale compromise by preventing compromised information from being useful for identifying any of the system nodes because all such information is encrypted on the nodes at all times, even during computation; and preventing communications compromise by virtue of obfuscating communication protocols.
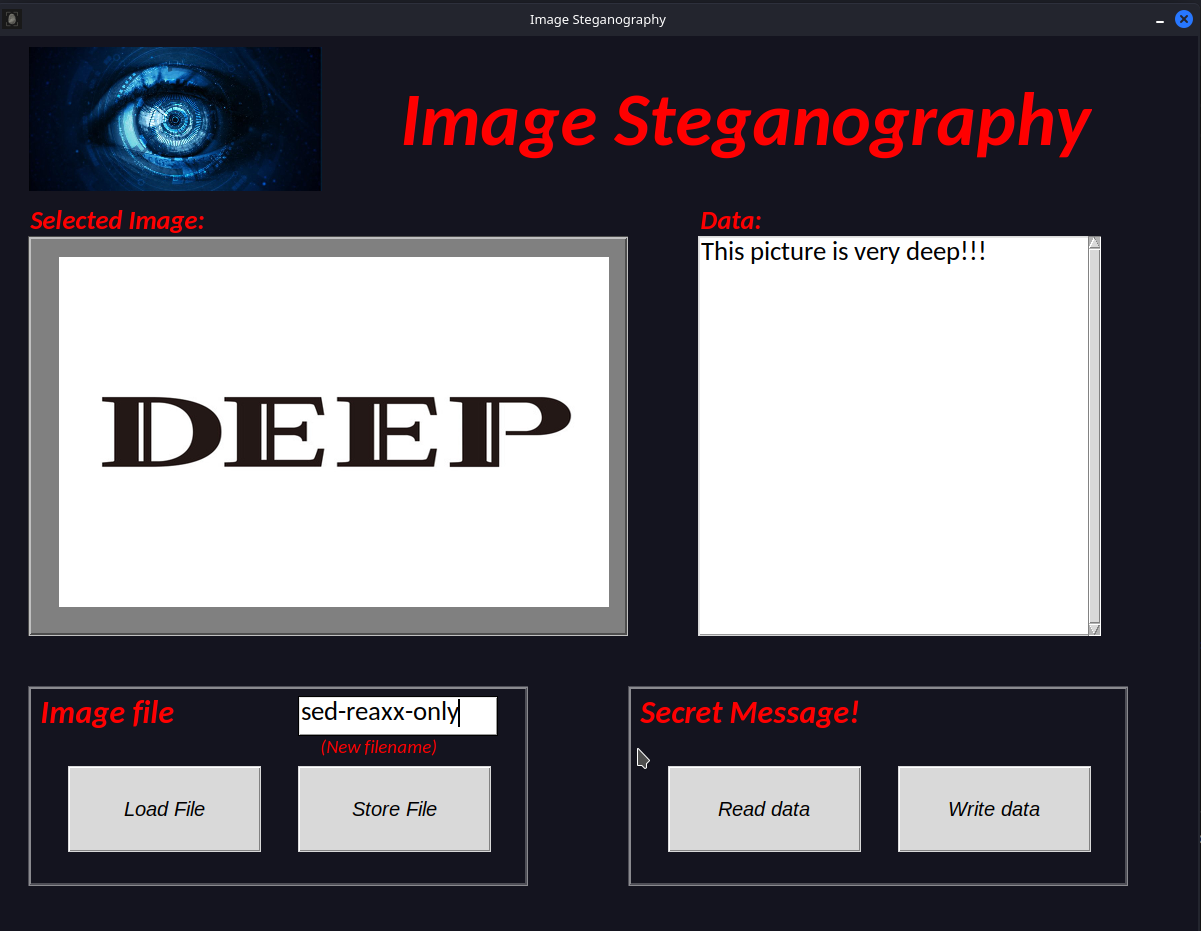
Figure 2: GitHub - adithya-subramani/Image-Steganography-with-GUI: A simple image ... Invisible IRC Project – anonymous IRC, inspired by Freenet, which later became I2P (Invisible Internet Project). Mnet (formerly MojoNation) – a distributed file system Digital video essentially consists of two types of data: a sequence of images (frames) and an audio track. To apply steganography to video, it is essential to understand how these data are stored and how different formats and compression methods affect informationIhiding techniques.
With respect to frames, some video formats store each image independently and without any loss of information. This is the case for formats such as FFV1, HuffYUV, Apple ProRes 4444 (in its lossless variants), or UT Video. These formats are particularly suitable for steganography because they allow direct pixelIlevel modification of each frame using techniques similar to those used on uncompressed images, such as inserting bits in the LSB.
By contrast, most popular video formats use lossy compression to reduce file size. This is the case with H.264, H.265/HEVC, VP9, AV1, and other codecs widely used on streaming platforms and social networks. These compression algorithms apply complex transforms (such as DCT, quantization, and interIframe prediction) that significantly alter the original data. Consequently, steganographic techniques that rely on preserving exact pixel values—like least significant bit modification—become more challenging, because pixelIdomain hidden data would be lost during compression.
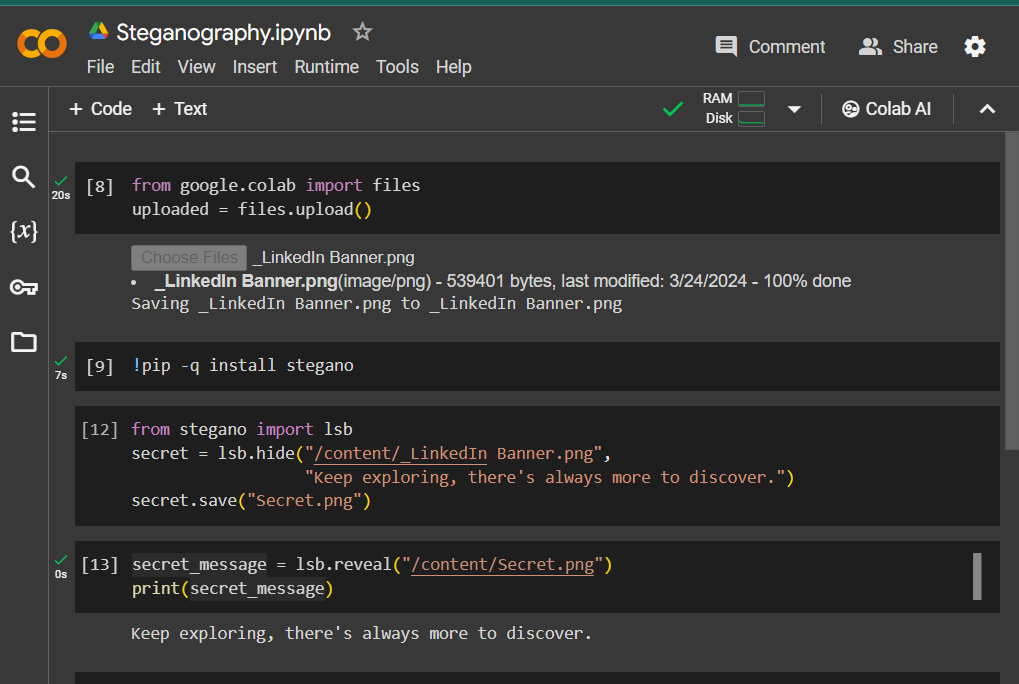
Figure 3: Image Steganography using Python – THE NUCLEAR GEEKS A similar situation occurs with audio. Some video formats include audio tracks in uncompressed or lossless formats such as PCM, WAV, or FLAC. These allow LSB techniques to be applied without risking the hidden information. However, other formats such as AAC, MP3, or Opus apply lossy compression and discard parts of the audio spectrum considered imperceptible. This implies an irreversible loss of data, which also affects any embedded message.
In summary, the feasibility of applying techniques like LSB to video depends on the type of compression used in both the video and audio tracks. Lossless formats provide a much more controlled and reliable environment for data hiding, whereas lossy formats require more sophisticated approaches. This section addresses hiding information in lossless videos, which means working with files in which the video and/or audio track is stored without lossy compression. This is fundamental for applying steganography techniques such as least significant bit (LSB) modification, because lossy compression processes remove or alter significant parts of the original data, destroying any hidden information in the process.
For video, you must use a codec that stores frames losslessly, such as FFV1, HuffYUV, or lossless variants of Apple ProRes or UT Video. For audio, you should use codecs such as PCM (typically stored as WAV) or FLAC, which preserve the fidelity of the original samples and are therefore suitable for LSBIbased embedding. Fortunately, ffmpeg—a powerful and versatile tool—allows you to transcode any video file to a lossless format by explicitly selecting the desired video and audio codecs. Below are some ffmpeg examples for generating files compatible with LSBIbased steganography: A fundamental aspect of working with video is understanding the difference between codecs and containers . While codecs (such as ffv1, h264, aac, etc.) are responsible for encoding and compressing audio and video streams, containers (such as .avi, .mov, .mkv, etc.) define how those streams are grouped, organized, and synchronized within a single file.
The container determines the file extension, not the codec itself. For example, the same video compressed with the ffv1 codec can be stored in an .avi, .mov, or .mkv container, and the internal video stream remains exactly the same. However, some containers offer better compatibility with certain codecs or better support for features such as multiple audio tracks, subtitles, or metadata.
Table 1 shows the most common containers, their extensions, and typically compatible codecs. Table 1 lists some of the most common containers along with the video and audio codecs they typically use. For steganography, the .avi, .mov, and .mkv containers are especially useful because they allow lossless codecs like ffv1, huffyuv, or pcm_s16le. Conversely, containers like .mp4, while very popular, are oriented toward lossy compression and are not recommended when working with LSB steganography.
Note that lossless formats generate significantly larger files. However, they are essential when applying LSBIbased techniques, such as LSB matching , to preserve the integrity of hidden data and ensure it can be extracted. In the following sections, we will see how to embed information in video by altering both the images and the audio. We will address them separately, though of course both can be done at the same time.
This section shows how to hide information in the frames of a video that uses a lossless compression codec. When working with lossless video, each frame can be treated as an independent image that preserves all its original pixel values. This allows us to apply techniques similar to those used with uncompressed images, such as least significant bit (LSB) modification. To access video frames and manipulate them directly from Python, we will use the PyAV library. PyAV provides a highIlevel interface for working with video and audio streams based on the popular ffmpeg tool. With PyAV, we can decode the video, extract frames one by one, modify their pixels, and reIencode them if we want to generate a new file with hidden information.
The key to this approach is that, by keeping compression lossless, the changes made to the frame pixels will not be altered by encoding, ensuring that the embedded information can be accurately recovered. In the following example, we use PyAV to extract the video’s frames sequentially. As an example of how to insert information, we modify the pixel at position $(0,0)$ by increasing it by one (avoiding overflow using min ). We use the first color channel—i.e., red.
However, the RGB image is a conversion from the YUV format used by the FFV1 codec. This is undesirable, since the YUVItoIRGB conversion will affect the byte LSBs and destroy the message. Therefore, we will not work with RGB but with YUV. Although many tools and libraries (such as FFmpeg or PyAV) use the term YUV to refer to formats like yuv444p or yuv420p, these names actually refer to a digital color encoding based on the YCbCr color space, which we described earlier. The term YUV comes from the analog world and was defined as a color encoding model used in television. In practice, when we manipulate data in formats like yuv444p, we are working with Y (luminance), Cb (blue difference), and Cr (red difference) components, but using the traditional YUV nomenclature for historical convenience. Thus, we can use YUV as a practical synonym for YCbCr since that is the common term in digital video libraries and formats.
Although we have modified the video sample, we still need to store it. This implies not only reIencoding the video but also the audio, as we do not want to lose it in the process. In the next section we will see how to embed information in the audio channel, and afterwards we will perform the complete process. This section shows how to hide information in the audio of a video that uses a lossless compression codec. When working with lossless audio, each sample is stored exactly, which allows direct manipulation of its values without them being altered by encoding. This enables techniques similar to those used in uncompressed audio files (e.g., .wav), including least significant bit (LSB) modification.
To access the audio samples of a video from Python, we will use the PyAV library. PyAV provides a highIlevel interface for working with video and audio streams based on ffmpeg. With PyAV, we can decode the audio stream, access the samples as NumPy arrays, modify them, and reIencode them to generate a new file with hidden information. The key to this approach is that, by keeping compression lossless, the changes made to audio samples will not be altered by encoding, ensuring that the embedded information can be accurately recovered.
In the following example, we use PyAV to access a video’s audio samples. As an example of how to insert information, we modify the first sample of the first channel by increasing its value by one. Note that we bound the maximum sample value to avoid overflow. 2. System Architecture & Core Working Principles As in the previous section, we still need to save the result. To do so, we must not only reIencode the audio but also copy the video. We will see the complete process in the next section.
In the previous sections we saw how to modify the images and the audio samples that make up a video to hide information. However, we have not yet reIencoded the video to save the result. To store the changes, we need to create an output container into which we will insert the images and audio samples. The following code implements message embedding in both the video frames and the audio stream using the LSB matching technique. The implementation is based on the PyAV library, which allows access to uncompressed frame and audio data.
The process begins by opening the input and output containers with the open_containers function, which initializes the objects needed to read and write multimedia data. Next, setup_streams configures the output container’s video and audio streams, copying essential parameters such as video resolution, number of audio channels, and channel layout. The video stream is encoded with the lossless FFV1 codec, while the audio is kept as uncompressed PCM.
The message to hide is converted into a bit sequence by message_to_bits , which turns each character into its 8Ibit binary representation, thereby generating a list of zeros and ones. The process_video_frame and process_audio_frame functions then iterate through the video frames and audio sample blocks, respectively. In each iteration, one bit of the message is embedded into the least significant bit (LSB) of the corresponding datum: a pixel in the Y channel for video or an audio sample.
Value changes are made using the LSB matching technique implemented in lsb_matching . This function checks whether the current value already contains the desired bit. If not, it adjusts the value by one unit up or down. When both directions are possible, the adjustment direction is chosen randomly; if the value is at one of the range extremes, the modification is forced inward.
Throughout the embedding process, explicit counters track the current position within the bit sequence for both video and audio. Once all message bits have been inserted, the remaining data are processed without alteration. Finally, the modified frames and blocks are encoded and written to the output container using PyAV’s encoding and multiplexing functions. Temporal synchronization is preserved by assigning pts and time_base , ensuring that the resulting file is perfectly playable.
This approach makes it possible to embed complete messages in both the visual and audio components of a media file effectively and with minimal detectability. This code provides the tools needed to modify frame LSBs and embed messages that will not be lost when saving the video. In the previous section we saw how to hide information in a video’s image frames and audio samples. Next we show how to extract this information.
The following code implements the extraction of hidden messages from the video and audio channels embedded with the code from the previous section. The main function, extract , coordinates the extraction process. Based on the expected number of bytes in the hidden message, it computes the total number of bits to recover from both video and audio. The input file is processed twice—once for each stream—by the functions extract_bits_from_video and extract_bits_from_audio .
extract_bits_from_video opens the file and accesses the first video stream. It then decodes the frames and converts each into a yuv444p representation. It iterates over the pixels of the luminance (Y) channel, extracting the least significant bit of each value and accumulating it in a list until the desired number of bits is reached. Similarly, extract_bits_from_audio accesses the audio stream of the same file. As it decodes the blocks of samples, it flattens them into a oneIdimensional array and extracts each sample’s LSB, storing these bits in a list until the specified length is reached.
Once both bit sequences have been obtained, bits_to_message decodes them. It groups the bits into chunks of 8 and converts them to their corresponding decimal values, thereby reconstructing the original message bytes. The result is interpreted as a UTFI8 string, ignoring any incomplete trailing bytes. This approach reliably recovers messages previously hidden in the visual and audio data of the file. To extract precisely, it is essential to know the exact message length in bytes. In more advanced applications, this length could be embedded as a header at the beginning of the message, as described in the image and video chapters.
Up to now we have seen how it is possible to embed information in videos that use lossless compression codecs, since the original data—both images and audio—are preserved intact. This allows working directly with pixel and sample values without risking that the encoding process will destroy the hidden information. However, when working with videos encoded with lossy compression—such as those using H.264, H.265/HEVC, VP9, or AV1—the situation changes dramatically. These algorithms apply transforms such as the Discrete Cosine Transform (DCT) on pixel blocks followed by quantization processes that remove information considered irrelevant from a perceptual standpoint. For audio, codecs such as MP3, AAC, or Opus use transforms like the MDCT (Modified Discrete Cosine Transform) to achieve compression, again with irreversible information loss.
From a steganographic point of view, the ideal would be to access the transformed coefficients (DCT or MDCT) before quantization—or even after it—to directly modify those values that will be retained in the encoded file. This would allow techniques similar to those used in JPEG steganography, where messages are embedded in the frequency domain. Unfortunately, within the Python ecosystem there are currently no libraries that provide straightforward, direct access to these coefficients in lossyIcompressed video or audio. Unlike JPEG images—where tools such as pythonIjpegItoolbox allow working with DCT coefficients—there are no equivalent tools for video streams encoded with H.264 or for MP3/AAC audio tracks.
Although the PyAV library is very powerful, it operates at a higher level and exposes already decoded data—that is, after transforms and quantization have been applied. As a result, any modification you make to PCM or RGB data will be discarded if you subsequently reIencode using a lossy codec, destroying the hidden message. This is a significant limitation for those who wish to apply robust steganography directly to compressed videos. To access the transformed coefficients, one would need to modify FFmpeg’s source code or use specific C/C++ libraries that interact with the codecs’ internal decoders—beyond the scope of this book.
In conclusion, while Python lacks tools for directly manipulating DCT or MDCT coefficients in lossyIcompressed streams, robust video steganographic techniques should be applied to lossless media, or developed in languages and environments closer to the codec’s encoding level. This remains an open and relevant research direction for future work on hiding and analyzing information in compressed audiovisual content.
A Python-based Steganography System that allows secure hiding and extraction of confidential data inside images, videos, and audio files using a graphical user interface (GUI). This project demonstrates how multimedia files can be used for secure data communication without noticeable changes in quality.
Multi-format steganography system using Python for secure hiding and extraction of data in images, videos, and audio files. The Secure Communication System Using Steganography is a Client-Server based application developed in Python that enables secure transmission of confidential information between two connected systems. The project combines networking and steganography techniques to conceal secret messages within multimedia files such as images, audio files, and videos before transmitting them over a network.
Unlike traditional communication systems where messages are transmitted directly, this system hides the existence of the message itself by embedding it into a carrier file using Least Significant Bit (LSB) steganography. The encoded file is then transmitted from the sender (Client) to the receiver (Server), where the hidden information can be extracted and decoded. The system supports Text-in-Image, Image-in-Image, Text-in-Audio, and Text-in-Video steganography operations through a user-friendly graphical interface developed using Tkinter.
In conventional communication systems, transmitted data can be intercepted, monitored, or attacked by unauthorized users. Although encryption secures the contents of a message, it still reveals the existence of communication. This project addresses the problem by hiding secret information inside multimedia files using steganography techniques. The encoded files are then transmitted through a Client-Server communication channel, making the communication more secure and difficult to detect.
The project follows a Client-Server Architecture consisting of two independent systems connected through a network. Both systems execute the same application and can function as sender or receiver when required. 3. Software Implementation, Frameworks & Protocols The Secure Communication System Using Steganography successfully combines multimedia steganography techniques with Client-Server networking to provide a secure communication platform. By concealing information within images, audio files, and videos before transmission, the system enhances confidentiality and minimizes the risk of unauthorized interception. The project demonstrates the practical implementation of steganography and secure network communication using Python and serves as an effective solution for covert information exchange between two connected systems.
StegoForge is a complex Python framework, but you shouldn't have to deal with broken environments when doing active forensics. We have compiled zero-dependency, native executables that automatically resolve their own AI and Media requirements. The Concept in Plain English: Steganography is the art of hiding secrets in plain sight. StegoForge takes your secret message or file and mathematically weaves it into the pixels of a normal photo, the soundwaves of a song, or the frames of a video. To the rest of the world, it just looks like a regular meme or MP3 track. To you, it's an invisible vault.
StegoForge is a modular, enterprise-grade steganography toolkit engineered for the full lifecycle of covert data: from embedding payloads into images, audio, video, and active network protocols, to deploying machine-learning steganalysis to forcibly extract anomalies from suspicious carrier files. Built for security researchers, CTF players, and digital forensics practitioners, it doesn't try to be one thing. It executes the entire forensic spectrum seamlessly.
Note on ML Architecture : StegoForge implements true Machine Learning steganalysis. The very first time you boot the engine, it will silently interface with HuggingFace to download the ONNX CNN weights directly into your ~/.stegoforge/models cache. Don't want to memorize terminal commands? Just run the tool on its own to access the interactive CLI! The menu features a cinematic startup sequence, grouped method selection, and guided transitions between Encoding, Decoding, and Forensics.
If you prefer raw terminal throughput, the CLI supports hyper-specific routing for all modules. Social survivability targets currently supported via Reed-Solomon wrapping: twitter , instagram , telegram , discord , whatsapp , signal . Strictly Educational Disclaimer: StegoForge was engineered strictly for digital forensics research, Capture The Flag (CTF) competitions, and lawful offensive security testing. Concealing illegal content, orchestrating unauthorized data exfiltration, or attempting to evade lawful surveillance is universally illegal. The author accepts zero liability for any misuse of this technology.
Contributing: Pull requests are heavily welcomed. Please ensure new encoding methods implement the BaseEncoder interface and contain robust PyTest coverage. For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation .
This project implements video steganography, allowing you to hide secret messages within video files. It consists of two main components: an encoder to hide messages and a decoder to extract them. The encoder hides the message by modifying the least significant bit of each color channel in the video frames. It adds a 32-bit zero sequence as an end marker.
The decoder extracts the least significant bits from the video frames and reconstructs the hidden message. It stops when it encounters the 32-bit zero sequence end marker. Contributions, issues, and feature requests are welcome. Feel free to check issues page if you want to contribute. Video Steganography Tool User Guide. This python script allows user to hide secret text file on media files such as image, audio, and video.
The purpose of this repository is to explore both the relationships between discrete cosine transform (DCT) coefficients as well as the variation in DCT coefficients across popular video codecs with a focus on improving and optimizing DCT-based steganographic systems. The primary focus of this repository is on variation histograms and correlation heatmaps (explained below).
Video Steganography Tool User Guide. This python script allows user to hide secret text file on media files such as image, audio, and video. This book is an introduction to steganography designed specifically for programmers with knowledge of Python who want to take their first steps in this discipline. Throughout its chapters, we explore the theoretical foundations of steganography, how it differs from other techniques such as cryptography and watermarking, and its relationship with steganalysis—the discipline in charge of detecting and extracting hidden information.
Unlike more academic or mathematically dense texts, this book takes a practical and accessible approach. No prior experience in computer security or advanced knowledge of signal processing is required, although some familiarity with Python programming will be very helpful. We present detailed examples and step-by-step explanations that let readers apply the concepts in practice through code.
One of the main goals of this book is to show how steganography can be implemented in different digital media , such as images, audio files, video, and text. Through concrete examples, we explore various information-hiding techniques, from the simplest ones—like modifying least significant bits ( LSB )—to more advanced methods based on mathematical transforms and modern techniques used today.
Beyond implementation, we also analyze tools and strategies used in steganalysis , enabling readers not only to learn how to hide information, but also to understand some of the methods used to detect it. This provides a more complete and balanced view of the discipline. Throughout the book, Python code takes center stage, allowing each technique to be understood from a practical and applicable standpoint. We use popular libraries for image and signal processing, as well as specific tools that make experimentation and learning easier.
In short, this book is an ideal starting point for any programmer who wants to get into the fascinating world of steganography in a practical and effective way. Beyond theory, the goal is for the reader to finish with a clear understanding of how to implement steganographic techniques in Python, with examples that can serve as a basis for future research or applications in the field of information security.
Python has become one of the most powerful and versatile tools for developing applications in the field of steganography. Its popularity and effectiveness stem from several reasons that make it especially suitable for this discipline. The simplicity and readability of Python code are notable. Python is known for its clear and concise syntax, which makes writing and understanding code easier. This is crucial in steganography, where algorithms can be complex and require readable code to facilitate review and maintenance.
In addition, Python offers a wide range of tools and libraries that simplify the development of steganography techniques. Libraries such as NumPy and SciPy provide a solid foundation for data processing and analysis, which is essential for developing steganographic algorithms. These tools provide robust functions that accelerate development and allow you to focus on implementing steganography algorithms.
However, in some cases, the existing tools do not cover all the specific needs of the field. For this reason, the author of this book has developed some libraries needed for image steganography that were not available in the Python ecosystem. One of these libraries is python-jpeg-toolbox, which allows access to low-level information in JPEG images, essential for working with steganography in this format. Another is PySTC, a library created to facilitate the use of Syndrome Trellis Codes (STC) in steganography, an advanced technique that allows embedding information while minimizing the number of modifications made. Both libraries are used throughout this book to illustrate and put into practice various steganography techniques.
The Python community is one of the largest and most active in the programming world. This means there are a great many resources available—from tutorials and documentation to discussion forums and open-source projects. The availability of these resources makes it easier to solve problems and continuously improve steganography techniques. Python is a high-level language that is compatible with multiple operating systems, including Windows, macOS, and Linux.
This is fundamental for developing steganography applications that must work in different environments. In addition, Python can easily interact with other languages and technologies, allowing steganography techniques to be integrated into larger and more diverse systems. In steganography, it is important not only to embed data but also to analyze and detect that data. Python offers powerful tools for data analysis and visualization, which are essential for steganalysis and for evaluating the effectiveness of hiding techniques.
Thanks to its simplicity and the availability of existing tools, Python enables rapid prototyping. This is especially valuable in research and development of new steganography techniques, where the ability to test and refine ideas quickly can lead to significant discoveries and improvements. 4. Practical Deployment, Analysis & Case Studies Python has been widely adopted in both academia and industry. This adoption ensures that techniques and tools developed in Python are relevant and applicable in real-world contexts. It also facilitates collaboration between researchers and professionals working in the field of steganography.
In summary, Python is the ideal choice for developing steganography applications due to its simplicity, versatility, and the vast ecosystem of available tools. These characteristics not only allow complex algorithms to be implemented efficiently but also ensure that applications are robust, maintainable, and easy to extend. In the study of steganography , it is common to encounter terms that may seem similar but actually have different purposes and applications. Concepts such as cryptography , watermarking , and steganalysis are closely related to hiding and protecting information, but they differ in their focus and functionality. This chapter aims to clarify these differences, providing a solid foundation for understanding how each technique operates, where they are similar, and where they differ within the field of information security.
Steganography and steganalysis represent two opposing approaches within information security. While steganography focuses on hiding information within a carrier medium so that its presence is not detected, steganalysis aims to detect and possibly extract these hidden messages. Steganography seeks discretion. Its purpose is not to encrypt the information but to hide it so that it appears nonexistent. This is achieved through various techniques, such as modifying the least significant bits (LSB) in images and audio, inserting data in the frequency domain through mathematical transforms, or hiding information in metadata and communication protocols.
Steganalysis, on the other hand, is responsible for detecting and analyzing files for subtle alterations that may reveal the presence of hidden information. It relies on statistical methods, machine learning, and signal processing techniques to identify irregularities in the suspected file. Some strategies include looking for anomalies in the distribution of pixel values or analyzing patterns in image encoding.
As steganography advances, more sophisticated hiding techniques emerge that challenge the capabilities of steganalysis. Likewise, detection methods evolve to counter new forms of concealment. This ongoing struggle makes both fields dynamic disciplines within computer security. Applications of steganography range from hiding malware, data exfiltration, and covert communication in criminal activities to secure communication in censored environments. Meanwhile, steganalysis is used in forensic investigations, cybersecurity, and in detecting malware that employs hiding techniques.
Steganography and steganalysis are intrinsically linked in continuous competition. While one seeks to hide information imperceptibly, the other develops advanced techniques to expose its existence. Both play a crucial role in information security and will continue to evolve with technological advances. Cryptography and steganography are two information security disciplines that, while sharing the goal of protecting data, differ in their focus and fundamental purpose. Whereas cryptography focuses on transforming information to make it unreadable to unauthorized third parties, steganography seeks to hide the very existence of the information within another medium.
Cryptography uses mathematical algorithms to encrypt data so that only those with the proper key can decrypt it. Its strength lies in the mathematical soundness of algorithms such as AES, RSA, or ECC, which ensure security even if an attacker intercepts the encrypted message. However, the main weakness of cryptography is that, although it protects the content of the message, it does not hide its existence. If an attacker detects encrypted communication, they may suspect that sensitive information is being transmitted and attempt to break the encryption using brute-force attacks, cryptanalysis, or social engineering. In addition, they may infer that two parties are communicating and therefore that a relationship exists between them.
In contrast, steganography does not alter the content of the message but hides it within another carrier medium, such as images, audio files, videos, or digital documents. Its goal is for the information to go unnoticed, preventing an attacker from even suspecting its existence. A steganographic message, if well implemented, can look like an innocuous file that arouses no suspicion. However, its potential weakness is that, once discovered and extracted, the security of the message may be compromised if the hidden information is in plaintext or only minimally protected.
Cryptography and steganography are not mutually exclusive and, in fact, can be combined to increase the security of a communication. A message can first be encrypted and then hidden inside a digital file so that, even if the hidden message is discovered, the attacker would still have to decrypt its content. This combination offers an additional layer of security, mitigating the weaknesses of both techniques.
In terms of applications, cryptography is widely used in secure communications, online banking, data storage, and privacy protection on networks. Steganography, for its part, has applications in communication in censored environments and hiding information in digital files. However, both technologies can be used for malicious purposes, such as hiding malware or covert communication of illegal activities.
Steganography and watermarking are techniques that involve inserting information inside digital files such as images, audio, and videos. Due to this similarity, they are often confused, but their purpose and application are fundamentally different. The main objective of steganography is to hide information imperceptibly so that its existence goes completely unnoticed. The goal is that no one suspects that there are hidden data within the carrier file. For this reason, the information inserted in a file by steganography must be undetectable.
Watermarking, on the other hand, is not designed to hide information but to embed it within the file for a specific purpose, such as copyright protection, authentication, or integrity verification. Unlike steganography, where the hidden message is generally arbitrary and intended for a specific recipient, in watermarking the inserted information is usually related to the identity of the content or its owner.
One essential property of watermarking is imperceptibility , since in most of its applications the goal is to protect a digital file without degrading its quality. If an image, video, or audio file suffered perceptible alterations due to the watermark, its usefulness would be compromised. For this reason, watermarking techniques are designed to insert information without affecting the perception of the original content.
Another key difference is robustness against modifications . Depending on the application, a watermark may be robust or fragile. Robust watermarking must withstand transformations such as compression, editing, or manipulation attacks, ensuring that the mark remains even if the file is copied or modified. This type of watermarking is used to verify the intellectual property of a file. In contrast, fragile watermarking is designed to disappear or change with the slightest modification to the file, allowing any attempt at tampering or forgery to be detected. This type of mark is used to verify the authenticity and integrity of the content.
Technically, steganography and watermarking can share similar data insertion methods, such as modifying least significant bits (LSB) or manipulating in the frequency domain using techniques such as the Discrete Cosine Transform (DCT) or the Discrete Wavelet Transform (DWT). However, steganography prioritizes the undetectability of the message, whereas watermarking usually balances imperceptibility and robustness depending on its purpose.
In terms of security, detection of a watermark does not imply that the file has been compromised, since its purpose is not concealment but content protection. In contrast, in steganography, if a third party detects the presence of a hidden message, its purpose is immediately compromised, since its effectiveness lies in avoiding any suspicion. This book is oriented toward developing steganography tools that are functional and resistant to detection techniques. For this reason, we do not include methods that, although historically used to hide information, present known vulnerabilities and can be easily detected through forensic analysis or steganalytic attacks.
One excluded technique is EOF (End of File) -based steganography, which consists of adding hidden data at the end of a file without modifying its original content. Although this technique is extremely simple to implement, it is also trivial to detect, since the additional data remain outside the normal structure of the file and can be identified through manual inspection or automated tools. Due to this weakness, its use in practical applications is limited and it will not be covered in this book.
Another commonly used but highly insecure method is steganography in metadata , where the hidden information is stored in the metadata fields of image, audio, or document files. Although this technique does not alter the visible content of the file, metadata can be easily inspected with standard tools, making this technique unreliable in scenarios where effective concealment of information is crucial.
The use of drawn text is another method that, although creative, proves insecure in practice. In this technique, hidden messages are represented within an image using drawn characters or subtle patterns that can only be interpreted by the recipient. However, this type of concealment is highly dependent on the visual content and can be easily detected using specialized filters.
Another image steganography technique not covered in this book is hiding data in the alpha channel of images with transparency. In this method, information is embedded in areas where the alpha channel is completely transparent, so that the modified pixels do not affect the visible appearance of the image. However, this technique is extremely easy to detect, since it is enough to force the alpha channel to be displayed as opaque to reveal possible modifications. Because of this fundamental weakness, its use in practical steganography is limited and it will not be addressed here.
Although this book studies techniques based on modifying the least significant bits of the pixels of an image, it does not use LSB replacement as a general embedding method. This method, which consists of directly replacing a pixel’s least significant bit with a bit of the hidden message, is highly vulnerable to so-called structural attacks [ Fridrich:2001:rs , Dumitrescu:2003:spa , Ker:2005:sstructural ], which analyze the statistical characteristics of the image to detect artificial alterations. Instead, we use LSB matching , which is more difficult to detect through statistical analysis.
In conclusion, this book focuses on steganography methods that offer a higher degree of security and resistance to detection techniques. The techniques mentioned above have been excluded due to their vulnerability to forensic analysis and their limited applicability in real-world scenarios. Throughout the chapters, we explore more advanced and resilient approaches, with practical examples in Python that allow readers to develop secure tools for hiding information.
Throughout this book, we will use several Python libraries to implement and test steganography techniques. To make installation easier and to ensure that the code runs smoothly, we will use Python’s package manager: pip . This manager allows you to install and update libraries easily and is the recommended option for handling dependencies in Python. In this chapter, we explain how to install the fundamental libraries we will use.
To install NumPy , which provides support for multidimensional arrays and advanced mathematical operations, run the following command in your terminal: To install SciPy , an extension of NumPy that provides tools for signal processing, optimization, and other advanced scientific operations, use: To install Matplotlib , a visualization library that allows you to plot data, including audio file waveforms: To install reedsolo , a library that implements Reed–Solomon error-correcting codes, use: To install PyDWT , a library that performs the Discrete Wavelet Transform (DWT) on images and signals, use: 5. Performance Evaluation & Extended Technical Observations To install imageio , a library for reading and writing images in multiple formats, use: To install PySTC , a library that implements Syndrome Trellis Codes (STC) for efficient steganography, use: To install python-jpeg-toolbox , a library that provides access to the DCT coefficients of JPEG images (as well as other low-level information), use: To install Numba , a library that speeds up Python functions using just-in-time compilation, use: To install PyAV , a library that provides access to audio and video data using FFmpeg from Python, use: To install Scapy , a tool for creating, manipulating, and analyzing network packets in Python, use: To intercept packets and manipulate them from user space, you also need the NetfilterQueue library. This library acts as a bridge between Linux’s Netfilter queue system (kernel) and Python. Install it with: In addition to installing the library, make sure the nf_netlink_queue kernel module is available. In most modern Linux distributions, it can be loaded automatically when first used. If it is not present, you can check for it with: Both Scapy and NetfilterQueue require administrator privileges, so it is common to run scripts with sudo .
To make learning easier and to let readers try the examples without having to write the code manually, all the examples used in this book are available in the following GitHub repository: This repository contains the source code for each example, organized by chapters and sections. In this way, users can copy and paste the code directly into their development environments instead of writing it from scratch. In addition, access to the repository’s files allows faster exploration of the examples and makes it easy to modify them for tests and experiments.
We recommend cloning the repository to have local access to all files. To do this, run the following command in your terminal: This command downloads a complete copy of the repository to the user’s machine, allowing structured access to all examples. It is also possible to download files individually from the GitHub web interface. A project named "STEGANOGRAPHY TOOLS " that provide 4 types of Steganography { Image, Text, Audio, Video } that hides User's Text message in the desired cover file using the tool and can send it to the receiver who can extract the Hidden message using the same tool .
To provide the stego community with C/C++ implementations of selected feature extractors mainly targeted at H.264 steganography. AES 256 & RSA encrypted video steganography. SRU Hackathon 2022 - Cybersecurity Winners A Advance Steganography Tool made with Python The Program Supports Hiding Secret Text data into an innocent looking cover file like : .mp4, .wav, .png, .jpeg, .txt through the use of Steganography Theory.
Improved way of securing data using combined Steganography and Cryptographic techniques Program that uses steganography and cryptography to hide a video file within another video file without noticeably effecting the appearance of the video. Networking component to securely send encoded files over a network. This is a final year project created by CSIT students for 7th semester. It is a simple website that can hide text inside videos or images.
Dissertation for master of Security and Applied Logic at FMI, UniBuc (Video Steganography - Topic) This project "STEGANOGRAPHY TOOLS" showcases algorithms to hide text message in four different cover file (Text, Image, Audio, Video) and transfer it to the receiver who can extract the hidden message from these files with the same tools. A Advance Steganography Tool made with Python The Program Supports Hiding Secret Text data into an innocent looking cover file like : .mp4, .wav, .png, .jpeg, .txt through the use of Steganography Theory Exploit Google Photos Unlimited Storage. Hide files inside videos with AES-256-CBC. Extract them back out—Encrypt them in between.
Audio and Video Steganography using Chaotic Theory and LFSR.
Find more details at https://drive.google.com/file/d/1ZmZvVDXN34kxMxThAaVP9b9u6D12i1HZ/view .
I am thrilled to delve into the captivating realm of video steganography, driven by a fervent interest in concealing secret image data within cover videos. My project involves a meticulous process of selecting specific frames and applying the tried-and-true LSB techniques to seamlessly embed information. To associate your repository with the video-steganography topic, visit your repo's landing page and select "manage topics." A secure video steganography tool for embedding and extracting hidden messages in video files.
Securely hide text in video files Extract hidden messages Lossless encoding & decoding Lightweight and fast Python
Implementation
Embed a secret message into a video Send the video securely Extract the message using a key A secure video steganography tool for embedding and extracting hidden messages in video files. Securely hide text in video files Extract hidden messages Lossless encoding & decoding Lightweight and fast Python
Implementation Synonym
Embed a secret message into a video Send the video securely Extract the message using a key A secure video steganography tool for embedding and extracting hidden messages in video files. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Anonymous%20P2P • https://daniellerch.me/stego/books/stegopython/video-en/ • https://github.com/BismaRiaz398/steganography • https://github.com/Aashritha-MB/Multimedia-Steganography • https://pypi.org/project/stegoforge/ • https://github.com/PappuWalker/Video_Steganography • https://github.com/nguyencuong1002/Video-Steganography • https://daniellerch.me/stego/books/stegopython/intro-en/ • https://github.com/topics/video-steganography • https://github.com/LeonardKachi/video-steganography-deployment/blob/main/README.md
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Video Steganography For Secure Communication In Python.
[*] Metasploit Scan Running on Target Subnet for Video Steganography For Secure Communication In Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |