Complete Technical Paper Content — Virtual Desktop Security Monitor
Overview & System Context
Virtual Desktop Security Monitor: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9542 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Remote desktop software is software for remote administration of computers, allowing a desktop environment to be displayed on a computer, known as the client, other than the one on which it is running − the server. While commonly found in the context of personal computers, the concept also applies to other forms of computers, such as smartphones and dedicated servers. Remote desktop applications have varying features. Some allow attaching to an existing user's session and "remote controlling", either displaying the remote control session or blanking the screen.
Apple Remote Desktop Protocol (ARD) – Original protocol for Apple Remote Desktop on macOS machines. Appliance Link Protocol (ALP) – a Sun Microsystems-specific protocol featuring audio (play and record), remote printing, remote USB, accelerated video HP Remote Graphics Software (RGS) – a proprietary protocol designed by Hewlett-Packard specifically for high end workstation remoting and collaboration. Independent Computing Architecture (ICA) – a proprietary protocol designed by Citrix Systems NX technology (NX) a proprietary protocol designed by NoMachine with open-source derivatives available from other forked projects. PC-over-IP (PCoIP) – a proprietary protocol used by VMware (licensed from Teradici) Remote Desktop Protocol (RDP) – a Windows-specific protocol featuring audio and remote printing Remote Framebuffer protocol (RFB) – A framebuffer level cross-platform protocol that VNC is based on. Simple Protocol for Independent Computing Environments (SPICE) – remote-display system built for virtual environments by Qumranet, now Red Hat Xpra – a protocol originally developed for forwarding X11 application seamlessly with audio, video, remote printing, etc. – extended to support Windows and macOS servers X Window System (X11) – a well-established cross-platform protocol mainly used for displaying local applications; X11 is network-transparent Wake-on-LAN – a standard protocol for remotely waking up computers that are in low-power mode (turned off, but still have access to a power source).
In computing, virtualization (or virtualisation in Commonwealth English; see spelling differences) abbreviated as v12n, is a series of technologies that allows dividing of physical computing resources into a series of virtual machines, operating systems, processes or containers. Virtualization began in the 1960s with IBM CP/CMS. The control program CP provided each user with a simulated stand-alone System/360 computer. In hardware virtualization, the host machine is the machine that is used by the virtualization and the guest machine is the virtual machine. The words host and guest are used to distinguish the software that runs on the physical machine from the software that runs on the virtual machine. The software or firmware that creates a virtual machine on the host hardware is called a hypervisor or virtual machine monitor. Hardware virtualization is not the same as hardware emulation. Hardware-assisted virtualization facilitates building a virtual machine monitor and allows guest OSes to be run in isolation. Desktop virtualization is the concept of separating the logical desktop from the physical machine. Operating system-level virtualization, also known as containerization, refers to an operating system feature in which the kernel allows the existence of multiple isolated user-space instances. The usual goal of virtualization is to centralize administrative tasks while improving scalability and overall hardware-resource utilization.
equivalence: a program running under the virtual machine monitor (VMM) should exhibit a behavior essentially identical to that demonstrated when running on an equivalent machine directly resource control (also called safety): the VMM must be in complete control of the virtualized resources efficiency: a statistically dominant fraction of machine instructions must be executed without VMM intervention This made it difficult to implement a virtual machine monitor for this type of processor.
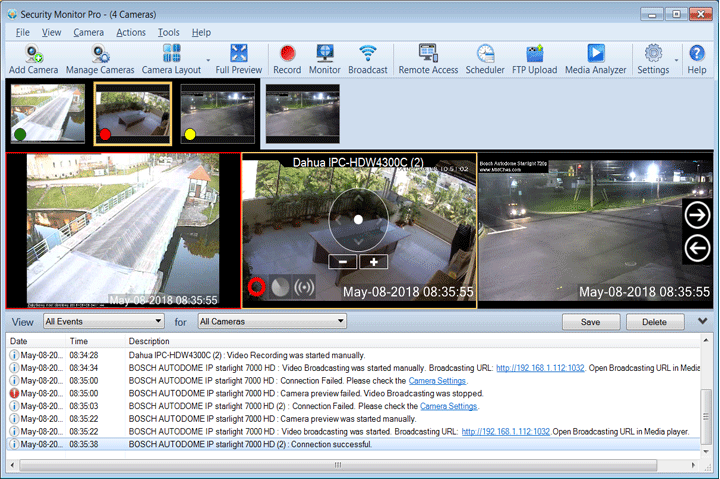
Specific limitations included the inability to trap on some privileged instructions. Therefore, to compensate for these architectural limitations, designers accomplished virtualization of the x86 architecture through two methods: full virtualization or paravirtualization. Both create the illusion of physical hardware to achieve the goal of operating system independence from the hardware but present some trade-offs in performance and complexity. Full virtualization was not fully available on the x86 platform prior to 2005. Many platform hypervisors for the x86 platform came very close and claimed full virtualization (such as Adeos, Mac-on-Linux, Parallels Desktop for Mac, Parallels Workstation, VMware Workstation, VMware Server (formerly GSX Server), VirtualBox, Win4BSD, and Win4Lin Pro). In 2005 and 2006, Intel and AMD (working independently) created new processor extensions to the x86 architecture called Intel VT-x and AMD-V, respectively. On the Itanium architecture, hardware-assisted virtualization is known as VT-i. The first generation of x86 processors to support these extensions were released in late 2005 early 2006: Figure 1: Download Security Monitor Pro 6.22 Free Trial On November 13, 2005, Intel released two models of Pentium 4 (Model 662 and 672) as the first Intel processors to support VT-x. On May 23, 2006, AMD released the Athlon 64 ("Orleans"), the Athlon 64 X2 ("Windsor") and the Athlon 64 FX ("Windsor") as the first AMD processors to support this technology.
Full virtualization – Almost complete virtualization of the actual hardware to allow software environments, including a guest operating system and its apps, to run unmodified. Paravirtualization – The guest apps are executed in their own isolated domains, as if they are running on a separate system, but a hardware environment is not simulated. Guest programs need to be specifically modified to run in this environment. Hybrid virtualization – Mostly full virtualization but utilizes paravirtualization drivers to increase virtual machine performance.
Full virtualization employs techniques that pools physical computer resources into one or more instances; each running a virtual environment where any software or operating system capable of execution on the raw hardware can be run in the virtual machine. Two common full virtualization techniques are typically used: (a) binary translation and (b) hardware-assisted full virtualization. Binary translation automatically modifies the software on-the-fly to replace instructions that "pierce the virtual machine" with a different, virtual machine safe sequence of instructions. Hardware-assisted virtualization allows guest operating systems to be run in isolation with virtually no modification to the (guest) operating system. Full virtualization requires that every salient feature of the hardware be reflected into one of several virtual machines – including the full instruction set, input/output operations, interrupts, memory access, and whatever other elements are used by the software that runs on the bare machine, and that is intended to run in a virtual machine. This approach was pioneered in 1966 with the IBM CP-40 and CP-67, predecessors of the VM family.
Some hypervisors perform binary translation between guest and host, either between differing instruction set architectures or between a guest and host using the same instruction set. The hypervisor may be designed to interpret a guest's machine code directly or generate machine code for the host's architecture in a form of dynamic binary translation. Most common hypervisors, including ones that use hardware to assist virtualization, perform binary translation of some instructions relating to hardware access. In such a case, the hypervisor will trap the instruction and perform the functions to emulate the required devices. Hypervisors that perform binary translation may also be designed to substitute instructions within the guest context to aid security or performance.
Figure 2: Smartnet - CyberSecurity Dashboard Design :: Behance Desktop virtualization separates the logical desktop from the physical machine. One form of desktop virtualization, virtual desktop infrastructure (VDI), can be thought of as a more advanced form of hardware virtualization. Rather than interacting with a host computer directly via a keyboard, mouse, and monitor, the user interacts with the host computer using another desktop computer or a mobile device by means of a network connection, such as a LAN, Wireless LAN or even the Internet. In addition, the host computer in this scenario becomes a server computer capable of hosting multiple virtual machines at the same time for multiple users. Companies like HP and IBM provide a hybrid VDI model with a range of virtualization software and delivery models to improve upon the limitations of distributed client computing. Selected client environments move workloads from PCs and other devices to data center servers, creating well-managed virtual clients, with applications and client operating environments hosted on servers and storage in the data center. For users, this means they can access their desktop from any location, without being tied to a single client device. Since the resources are centralized, users moving between work locations can still access the same client environment with their applications and data. For IT administrators, this means a more centralized, efficient client environment that is easier to maintain and able to more quickly respond to the changing needs of the user and business. Another form, session virtualization, allows multiple users to connect and log into a shared but powerful computer over the network and use it simultaneously. Each is given a desktop and a personal folder in which they store their files. With multiseat configuration, session virtualization can be accomplished using a single PC with multiple monitors, keyboards, and mice connected. Thin clients, which are seen in desktop virtualization, are simple and/or cheap computers that are primarily designed to connect to the network. They may lack significant hard disk storage space, RAM or even processing power, but many organizations are beginning to look at the cost benefits of eliminating "thick client" desktops that are packed with software (and require software licensing fees) and making more strategic investments. Desktop virtualization simplifies software versioning and patch management, where the new image is simply updated on the server, and the desktop gets the updated version when it reboots. It also enables centralized control over what applications the user is allowed to have access to on the workstation. Moving virtualized desktops into the cloud creates hosted virtual desktops (HVDs), in which the desktop images are centrally managed and maintained by a specialist hosting firm. Benefits include scalability and the reduction of capital expenditure, which is replaced by a monthly operational cost.
Operating system-level virtualization, also known as containerization, refers to an operating system feature in which the kernel allows the existence of multiple isolated user-space instances. Such instances, called containers, partitions, virtual environments (VEs) or jails (FreeBSD jail or chroot jail), may look like (physical) computers from the point of view of programs running in them. A computer program running on an ordinary operating system can see all resources (connected devices, files and folders, network shares, CPU power, quantifiable hardware capabilities) of that computer. However, programs running inside a container can only see the container's contents and devices assigned to the container. This provides many of the benefits that virtual machines have such as standardization and scalability, while using less resources as the kernel is shared between containers. Containerization started gaining prominence in 2014, with the introduction of Docker.
sharing a computer system among multiple users; isolating users from each other (and from the control program); emulating new hardware to achieve improved reliability, security, and productivity. A common goal of virtualization is to centralize administrative tasks while improving scalability and overall hardware-resource utilization. With virtualization, several operating systems can be run in parallel on a single central processing unit (CPU). This parallelism tends to reduce overhead costs and differs from multitasking, which involves running several programs on the same OS. Using virtualization, an enterprise can better manage updates and rapid changes to the operating system and applications without disrupting the user. Ultimately, virtualization dramatically improves the efficiency and availability of resources and applications in an organization. Instead of relying on the old model of "one server, one application" that leads to underutilized resources, virtual resources are dynamically applied to meet business needs without any excess fat". Virtual machines running proprietary operating systems require licensing, regardless of the host machine's operating system. For example, installing Microsoft Windows into a VM guest requires its licensing requirements to be satisfied.
An Introduction to Virtualization Archived 2020-10-22 at the Wayback Machine, January 2004, by Amit Singh Figure 3: Wide banner of security CCTV cameras and guard monitoring screen hud UI ... Remote Desktop Protocol (RDP) is a proprietary protocol developed by Microsoft Corporation which provides a user with a graphical interface to connect to another computer over a network connection. The user employs RDP client software for this purpose, while the other computer must run RDP server software. Several clients exist for most versions of Microsoft Windows (including Windows Mobile but the support has ended), Linux (for example Remmina, Vinagre or rdesktop), Unix, macOS, iOS, Android, and other operating systems. RDP servers are built into the server and professional editions of Windows operating systems but not home editions; an RDP server for Unix and OS X also exists (for example xrdp). By default, the server listens on TCP port 3389 and UDP port 3389. Microsoft currently refers to their official RDP client software as Remote Desktop Connection, formerly "Terminal Services Client". The protocol is an extension of the ITU-T T.128 application sharing protocol. Microsoft makes some specifications public on their website.
Every server and professional version of Microsoft Windows from Windows XP onward includes an installed Remote Desktop Connection (RDC) ("Terminal Services") client (mstsc.exe) whose version is determined by that of the operating system or by the last applied Windows Service Pack. The Terminal Services server is supported as an official feature on Windows NT 4.0 Terminal Server Edition, released in 1998, Windows 2000 Server, all editions of Windows XP except Windows XP Home Edition, Windows Server 2003, Windows Home Server, on Windows Fundamentals for Legacy PCs, in Windows Vista Ultimate, Enterprise and Business editions, Windows Server 2008 and Windows Server 2008 R2 and on Windows 7 Professional and above. The home versions of Windows do not support RDP. Microsoft provides the client required for connecting to newer RDP versions for downlevel operating systems. Since the server improvements are not available downlevel, the features introduced with each newer RDP version only work on downlevel operating systems when connecting to a higher version RDP server from these older operating systems, and not when using the RDP server in the older operating system.
Seamless Windows: remote applications can run on a client machine that is served by a Remote Desktop connection. It is available since RDP 6. Remote Programs: application publishing with client-side file-type associations. Terminal Services Gateway: enables the ability to use a front-end IIS server to accept connections (over port 443) for back-end Terminal Services servers via an HTTPS connection, similar to how RPC over https allows Outlook clients to connect to a back-end Exchange 2003 server. Requires Windows Server 2008. Network Level Authentication Support for remoting the Aero Glass Theme (or Composed Desktop), including ClearType font-smoothing technology. Support for remoting Windows Presentation Foundation applications: compatible clients that have .NET Framework 3.0 support can display full Windows Presentation Foundation effects on a local machine. Rewrite of device redirection to be more general-purpose, allowing a greater variety of devices to be accessed. Fully configurable and scriptable via Windows Management Instrumentation. Improved bandwidth tuning for RDP clients. Support for Transport Layer Security (TLS) 1.0 on both server and client ends (can be negotiated if both parties agree, but not mandatory in a default configuration of any version of Windows). Multiple monitor support for allowing one session to use multiple monitors on the client (disables desktop composition) Release 7.1 of RDP in 2010 introduced the following feature: RemoteFX: RemoteFX provides virtualized GPU support and host-side encoding; it ships as part of Windows Server 2008 R2 SP1. The latest version of RDP supports Transport Layer Security (TLS) version 1.1, 1.2 and 1.3 to protect RDP traffic.
Since the release of Remote Desktop Connection, there have been several additional Remote Desktop Protocol clients created by both Microsoft and other parties including Microsoft Remote Desktop, rdesktop, and FreeRDP. Dieser Inhalt ist eine maschinelle Übersetzung, die dynamisch erstellt wurde. (Haftungsausschluss) Cet article a été traduit automatiquement de manière dynamique. (Clause de non responsabilité) Questo contenuto è stato tradotto dinamicamente con traduzione automatica. (Esclusione di responsabilità)) Citrix Virtual Apps and Desktops™ are virtualization solutions that give IT control of virtual machines, applications, licensing, and security while providing anywhere access for any device.
Citrix Virtual Apps and Desktops share a unified architecture called FlexCast Management Architecture (FMA). FMA’s key features are the ability to run multiple versions of Citrix Virtual Apps or Citrix Virtual Desktops™ from a single site and integrated provisioning. This illustration shows the key components in a typical deployment, which is called a site.
The Delivery Controller is the central management component of a site. Each site has one or more Delivery Controllers. It is installed on at least one server in the data center. For site reliability and availability, install Controllers on more than one server. If your deployment includes a hypervisor or other service, the Controller services communicate with it to: The Controller’s Broker Service tracks which users are logged on and where, what session resources the users have, and if users need to reconnect to existing applications. The Broker Service runs PowerShell cmdlets and communicates with a broker agent on the VDAs over TCP port 80. It does not have the option to use TCP port 443.
The Monitor Service collects historical data and places it in the monitoring database. This service uses TCP port 80 or 443. The Controller manages the state of desktops, starting and stopping them based on demand and administrative configuration. At least one Microsoft SQL Server database is required for every site to store configuration and session information. This database stores the data collected and managed by the services that make up the Controller. Install the database within your data center, and ensure it has a persistent connection to the Controller.
The site also uses a configuration logging database and a monitoring database. By default, those databases are installed in the same location as the site database, but you can change this. The VDA is installed on each physical or virtual machine in your site that you make available to users. Those machines deliver applications or desktops. The VDA enables the machine to register with the Controller, which in turn allows the machine and the resources it is hosting to be made available to users. VDAs establish and manage the connection between the machine and the user device. VDAs also verify that a Citrix® license is available for the user or session, and apply policies that are configured for the session.
The VDA communicates session information to the Broker Service in the Controller through the broker agent in the VDA. The broker agent hosts multiple plug-ins and collects real-time data. It communicates with the Controller over TCP port 80. The word “VDA” is often used to refer to the agent and the machine on which it is installed. VDAs are available for single-session and multi-session Windows operating systems. VDAs for multi-session Windows operating systems allow multiple users to connect to the server at a time. VDAs for single-session Windows operating systems allow only one user to connect to the desktop at a time. Linux VDAs are also available.
StoreFront authenticates users and manages stores of desktops and applications that users access. It can host your enterprise application store, which gives users self-service access to the desktops and applications that you make available to them. It also keeps track of users’ application subscriptions, shortcut names, and other data. This helps ensure that users have a consistent experience across multiple devices.
Installed on user devices and other endpoints (such as virtual desktops), Citrix Workspace app provides users with quick, secure, self-service access to documents, applications, and desktops. Citrix Workspace app provides on-demand access to Windows, web, and Software as a Service (SaaS) applications. For devices that can’t install the device-specific Citrix Workspace app software, Citrix Workspace app for HTML5 provides a connection through an HTML5-compatible web browser.
Web Studio is a web-based management console that lets you configure and manage your on-premises Citrix Virtual Apps and Desktops deployment. Citrix Secure Private Access on-premises solution enhances an organization’s overall security and compliance posture with the ability to easily deliver Zero Trust Network Access to browser-based apps (internal web apps and SaaS apps) using StoreFront as a unified access portal to web and SaaS apps, along with virtual apps and desktops as an integrated part of Citrix Workspace. The solution is compatible with existing releases of NetScaler and StoreFront without any changes to the versions. For details, see Secure Private Access for on-premises .
Director is a web-based tool that enables IT support and help desk teams to monitor an environment, troubleshoot issues before they become system-critical, and perform support tasks for end users. You can use one Director deployment to connect to and monitor multiple Citrix Virtual Apps or Citrix Virtual Desktops sites. Real-time session data from the Broker Service in the Controller, which includes data the Broker Service gets from the broker agent in the VDA.
Director uses the ICA® performance and heuristics data captured by the Citrix Gateway device to build analytics from the data and then presents it to the administrators. 2. System Architecture & Core Working Principles You can also view and interact with a user’s sessions through Director, using Windows Remote Assistance.
The License Server manages your Citrix product licenses. It communicates with the Controller to manage licensing for each user’s session and with Studio to allocate license files. A site must have at least one license server to store and manage your license files. The hypervisor or other service hosts the virtual machines in your site. These can be the VMs you use to host applications and desktops, and VMs you use to host the Citrix Virtual Apps and Desktops components. A hypervisor is installed on a host computer dedicated entirely to running the hypervisor and hosting virtual machines.
Although many deployments require a hypervisor, you don’t need one to provide Remote PC Access. A hypervisor is also not required when you are using Provisioning Services (PVS) to provision VMs. The following components can also be included in Citrix Virtual Apps and Desktops deployments. For more information, see their documentation.
Citrix Provisioning (formerly Provisioning Services) is an optional component that is available with some editions. It provides an alternative to MCS for provisioning virtual machines. Whereas MCS creates copies of a master image, PVS streams the master image to user devices. PVS doesn’t require a hypervisor to do this, so you can use it to host physical machines. PVS communicates with the Controller to provide users with resources.
When users connect from outside the corporate firewall, Citrix Virtual Apps and Desktops can use Citrix Gateway (formerly Access Gateway and NetScaler® Gateway) technology to secure these connections with TLS. The Citrix Gateway or VPX virtual appliance is an SSL VPN appliance that is deployed in the demilitarized zone (DMZ). It provides a single secure point of access through the corporate firewall.
In deployments where virtual desktops are delivered to users at remote locations such as branch offices, Citrix SD-WAN technology can be employed to optimize performance. Repeaters accelerate performance across WANs. With repeaters in the network, users in the branch office experience LAN-like performance over the WAN. Citrix SD-WAN can prioritize different parts of the user experience so that, for example, the user experience does not degrade in the branch location when a large file or print job is sent over the network. HDX™ WAN optimization provides tokenized compression and data deduplication, dramatically reducing bandwidth requirements and improving performance.
A site is made up of machines with dedicated roles that allow for scalability, high availability, and failover, and provide a solution that is secure by design. A site consists of VDA-installed servers and desktop machines, and the Delivery Controller, which manages access. The VDA enables users to connect to desktops and applications. It is installed on virtual machines in the data center for most delivery methods, but it can also be installed on physical PCs for Remote PC Access.
The Controller is made up of independent Windows services that manage resources, applications, and desktops, and optimize and balance user connections. Each site has one or more Controllers. Because sessions are affected by latency, bandwidth, and network reliability, place all Controllers on the same LAN, if possible. Users never directly access the Controller. The VDA serves as an intermediary between users and the Controller. When users log on using StoreFront, their credentials pass through to the Broker Service on the Controller. The Broker Service then obtains profiles and available resources based on the policies set for them.
To start a session, the user connects either through Citrix Workspace app installed on the user’s device, or a StoreFront website. The user selects the physical or virtual desktop or virtual application that is needed. The user’s credentials move through this pathway to access the Controller, which determines which resources are needed by communicating with a Broker Service. Citrix recommends that administrators place an SSL certificate on StoreFront to encrypt the credentials coming from Citrix Workspace app.
The Broker Service determines which desktops and applications the user is allowed to access. After the credentials are verified, information about available applications or desktops is sent back to the user through the StoreFront-Citrix Workspace app pathway. When the user selects applications or desktops from this list, that information goes back down the pathway to the Controller. The Controller then determines the proper VDA to host the specific applications or desktop.
The Controller sends a message to the VDA with the user’s credentials, and then sends all the data about the user and the connection to the VDA. The VDA accepts the connection and sends the information back through the same pathways to Citrix Workspace app. A set of required parameters is collected on StoreFront. These parameters are then sent to Citrix Workspace app either as part of the Citrix-Workspace-app-StoreFront protocol conversation, or converted to an Independent Computing Architecture (ICA) file and downloaded. As long as the site was properly set up, the credentials remain encrypted throughout this process.
The ICA file is copied to the user’s device and establishes a direct connection between the device and the ICA stack running on the VDA. This connection bypasses the management infrastructure (Citrix Workspace app, StoreFront, and Controller). The connection between Citrix Workspace app and the VDA uses the Citrix Gateway Protocol (CGP). If a connection is lost, the Session Reliability feature enables the user to reconnect to the VDA rather than having to relaunch through the management infrastructure. Session Reliability can be enabled or disabled in Citrix policies.
After the client connects to the VDA, the VDA notifies the Controller that the user is logged on. The Controller then sends this information to the site database and starts logging data in the monitoring database. Every Citrix Virtual Apps and Desktops session produces data that IT can access through Studio or Director. Using Studio, administrators can access real-time data from the Broker Agent to manage sites. Director accesses the same data plus historical data stored in the monitoring database. It also accesses HDX data from NetScaler Gateway for help desk support and troubleshooting.
Within the Controller, the Broker Service reports session data for every session on the machine providing real-time data. The Monitor Service also tracks the real-time data and stores it as historical data in the monitoring database. Studio communicates only with the Broker Service. It accesses only real-time data. Director communicates with the Broker Service (through a plug-in in the Broker Agent) to access the site database.
You set up the machines that deliver applications and desktops with machine catalogs. Then, you create delivery groups that specify the applications and desktops that will be available (using machines in the catalogs), and which users can access them. Optionally, you can then create application groups to manage collections of applications. Machine catalogs are collections of virtual or physical machines that you manage as a single entity. These machines, and the application or virtual desktops on them, are the resources you provide to your users. All the machines in a catalog have the same operating system and the same VDA installed. They also have the same applications or virtual desktops.
Typically, you create a master image and use it to create identical VMs in the catalog. For VMs you can specify the provisioning method for the machines in that catalog: Citrix tools (Citrix Provisioning or MCS) or other tools. Alternatively, you can use your own existing images. In that case, you must manage target devices on an individual basis or collectively using third-party electronic software distribution (ESD) tools.
For more information, see Citrix Virtual Apps and Desktops Image Management and Create machine catalogs . Delivery groups specify which users can access which applications, desktops, or both on which machines. Delivery groups contain machines from your machine catalogs, and Active Directory users who have access to your site. You might assign users to your delivery groups by their Active Directory group, because Active Directory groups and delivery groups are ways to group users with similar requirements.
Each delivery group can contain machines from more than one catalog, and each catalog can contribute machines to more than one delivery group. However, each individual machine can only belong to one delivery group at a time. You define which resources users in the delivery group can access. For example, to deliver different applications to different users, you might install all the applications on the master image for one catalog and create enough machines in that catalog to distribute among several delivery groups. You can then configure each delivery group to deliver a different subset of applications that are installed on the machines.
Application groups provide application management and resource control advantages over using more delivery groups. Using the tag restriction feature, you can use your existing machines for more than one publishing task, saving the costs associated with deployment and managing more machines. A tag restriction can be thought of as subdividing (or partitioning) the machines in a delivery group. Application groups can also be helpful when isolating and troubleshooting a subset of machines in a delivery group.
You agree to hold this documentation confidential pursuant to the terms of your Citrix Beta/Tech Preview Agreement. The development, release and timing of any features or functionality described in the Preview documentation remains at our sole discretion and are subject to change without notice or consultation. The documentation is for informational purposes only and is not a commitment, promise or legal obligation to deliver any material, code or functionality and should not be relied upon in making Citrix product purchase decisions.
Access to this page requires authorization. You can try signing in or changing directories . Migrating user desktops to the cloud helps improve employee productivity so that employees can work from anywhere on a high-security cloud-based virtual desktop infrastructure. Azure provides several virtual desktop solutions to meet different organizational needs: Azure Virtual Desktop : A desktop and application virtualization service that runs on Azure. It provides multisession Windows desktops and published applications, with simplified management and scaling.
Windows 365 : A cloud-based service that automatically creates Cloud PCs for your users. Windows 365 assigns each Cloud PC to an individual user as their dedicated Windows device. Windows 365 is evolving to include developer-focused capabilities that Microsoft Dev Box previously offered. It provides a single platform for cloud desktops across information workers and developers. For more information, see Dev Box capabilities unified into Windows 365 .
Omnissa Horizon Cloud on Microsoft Azure : An Omnissa service that simplifies the delivery of virtual desktops and applications on Azure by extending Azure Virtual Desktop. 3. Software Implementation, Frameworks & Protocols Citrix DaaS : A desktop and app virtualization service that you can use to provision Windows desktops and apps on Azure with Citrix and Azure Virtual Desktop.
This section outlines virtual desktop architecture on Azure and shows how the key stages of a virtual desktop solution journey connect from initial learning through production deployment. The architecture includes hub-and-spoke virtual networks with connectivity via Azure ExpressRoute, identity components with Microsoft Entra ID and Active Directory Domain Services (AD DS), Azure Virtual Desktop host pools with session hosts, endpoint devices, storage solutions (Azure Files and Azure NetApp Files), and monitoring with Log Analytics.
The previous diagram demonstrates a typical basic or baseline virtual desktop implementation. For real-world solutions that you can build in Azure, see Virtual desktop architectures . The articles in this section include fully developed architectures that you can deploy in Azure and expand to production-grade solutions and guides. These articles can help you decide how to use virtual desktop technologies in Azure. Solution ideas demonstrate implementation patterns and possibilities to consider as you plan your virtual desktop proof-of-concept (POC) development.
The following production-ready architectures demonstrate end-to-end virtual desktop solutions that you can deploy and customize: Technology choices: The following articles help you evaluate and select the best virtual desktop technologies for your workload requirements: Azure Virtual Desktop landing zone design guide : Plan and design your Azure Virtual Desktop deployment aligned with Azure landing zone principles.
Windows 365 Azure network connection : Design and implement Windows 365 Azure network connections to integrate Cloud PCs with your existing network infrastructure. Multiregion BCDR for Azure Virtual Desktop : Design a multiregion BCDR strategy for Azure Virtual Desktop to provide high availability and resilience.
Microsoft Learn provides free online training resources for Azure virtual desktop technologies. The platform offers videos, tutorials, and interactive labs for specific products and services, along with learning paths organized by job role. The following resources provide foundational knowledge for virtual desktop implementations on Azure. Azure Virtual Desktop: Use the following resources to build core Azure Virtual Desktop knowledge.
Deliver remote desktops and apps by using Azure Virtual Desktop : Learn the fundamentals of planning and deploying Azure Virtual Desktop . Implement an Azure Virtual Desktop infrastructure : Develop skills for implementing and managing Azure Virtual Desktop infrastructure.
Monitor and maintain an Azure Virtual Desktop infrastructure : Learn how to monitor, maintain, and optimize Azure Virtual Desktop environments. Examine Windows 365 : Learn the basics of Windows 365 Cloud PCs, including editions, architecture, life cycle, and how they integrate with your environment. Windows 365 provides single-user virtual desktops as an alternative to the multisession model in Azure Virtual Desktop.
Organizations that start their cloud adoption can use the Cloud Adoption Framework for Azure to access proven guidance that accelerates cloud adoption. Azure Virtual Desktop planning : Plan your Azure Virtual Desktop migration or deployment. Azure Virtual Desktop Azure landing zone review : Review your Azure landing zone readiness for Azure Virtual Desktop.
To help ensure the quality of your virtual desktop solution on Azure, follow the Azure Well-Architected Framework . The Well-Architected Framework provides prescriptive guidance for organizations that seek architectural excellence and describes how to design, provision, and monitor cost-optimized Azure solutions. To implement virtual desktop solutions, focus on security, performance, and cost management. The following resources provide guidance about best practices for your Azure Virtual Desktop environment: Security recommendations for Azure Virtual Desktop : Follow security recommendations to protect your Azure Virtual Desktop environment.
Azure security baseline for Azure Virtual Desktop : Apply the Microsoft cloud security benchmark to Azure Virtual Desktop. Session host VM sizing guidelines : Select the appropriate VM sizes for your session host workloads. Peripheral and resource redirection over the Remote Desktop Protocol (RDP) : Learn which local devices and peripherals users can access in their Azure Virtual Desktop remote sessions, including redirection methods and supported resource types.
Create and assign an autoscale scaling plan for Azure Virtual Desktop : Use the native autoscale feature to automatically scale session host VMs in and out based on scaling schedules. This approach optimizes costs and performance for pooled and personal host pools. Workload deployment on Azure marks a significant milestone, and day-2 operations become critical.
Turn on Insights to monitor Azure Virtual Desktop : Use Azure Virtual Desktop Insights to track the health, performance, and usage of your Azure Virtual Desktop environment. Create and assign an autoscale scaling plan for Azure Virtual Desktop : Use the native autoscale feature to automatically scale session host VMs in and out based on a scaling schedule. This approach optimizes costs and performance.
Session host VM sizing guidelines : Select the appropriate VM sizes for your session host workloads. Set up device redirection : Set up which local devices users can access in their remote sessions. Monitor and maintain an Azure Virtual Desktop infrastructure : Learn how to plan for DR, set up automation, and optimize session host capacity for Azure Virtual Desktop .
BCDR for Azure Virtual Desktop : Design a multiregion BCDR strategy for Azure Virtual Desktop to provide high availability and resilience. Azure virtual desktop services evolve to address modern data challenges. Stay informed about the latest updates and features .
What's new in Azure Virtual Desktop : Learn about new features and improvements in Azure Virtual Desktop . What's new in Windows 365 Enterprise and Frontline : Stay updated on Windows 365 Cloud PC features, including virtual desktop capabilities for information workers and developers. The virtual desktop category covers a range of solutions. The following resources can help you discover more about Azure.
Supported identities and authentication methods : Learn how Azure Virtual Desktop authentication works. Microsoft Entra joined session hosts in Azure Virtual Desktop : Deploy session hosts that use Microsoft Entra ID for authentication. 4. Practical Deployment, Analysis & Case Studies Compare self-managed Active Directory Domain Services, Microsoft Entra ID, and managed Microsoft Entra Domain Services : Compare identity solutions to determine the right fit for your virtual desktop environment.
FSLogix supports roaming profiles in remote computing environments like Azure Virtual Desktop. It stores a complete user profile in a single container. At sign-in, FSLogix dynamically attaches this container to the computing environment: FSLogix configuration examples : Review configuration examples for FSLogix profile containers. FSLogix profile containers and Azure Files : Use Azure Files as a storage solution for FSLogix profile containers.
Storage options for FSLogix profile containers in Azure Virtual Desktop : Compare storage options for FSLogix profile containers. Azure Virtual Desktop network connectivity : Review a high-level overview of the network connections that Azure Virtual Desktop uses.
RDP Shortpath for Azure Virtual Desktop : Set up RDP Shortpath to establish a direct User Datagram Protocol (UDP)-based transport between a client and session host. Most organizations need a hybrid approach to virtual desktops because they integrate cloud-based virtual desktops with on-premises infrastructure. Azure Virtual Desktop supports hybrid deployment scenarios that extend virtual desktop capabilities to on-premises environments. To connect environments, organizations must choose a hybrid network architecture .
To help you ramp up quickly, the following articles compare Azure virtual desktop options to other cloud services. Dieser Inhalt ist eine maschinelle Übersetzung, die dynamisch erstellt wurde. (Haftungsausschluss) Cet article a été traduit automatiquement de manière dynamique. (Clause de non responsabilité) Questo contenuto è stato tradotto dinamicamente con traduzione automatica. (Esclusione di responsabilità)) This document applies to Citrix DaaS (formerly Citrix Virtual Apps and Desktops service) hosted in Citrix Cloud. This information includes Citrix Virtual Apps Essentials and Citrix Virtual Desktops Essentials.
Citrix Cloud manages the operation of the control plane for Citrix DaaS environments. The control plane includes the Delivery Controllers, management consoles, SQL database, license server, and optionally StoreFront™ and Citrix Gateway. The Virtual Delivery Agents (VDAs) hosting the apps and desktops remain under the customer’s control in the data center of their choice, either cloud or on-premises. These components are connected to the cloud service using an agent called the Citrix Cloud Connector. If customers elect to use Citrix® StoreFront Cloud, they can also choose to use the Citrix Gateway Service instead of running Citrix Gateway within their data center. The following diagram illustrates Citrix DaaS and its security boundaries.
Visit the Citrix Trust Center for more information regarding Citrix Cloud Certifications, and check back frequently for updates. The use of Citrix Managed Azure Capacity with various Citrix DaaS™ editions and Universal Hybrid Multi-Cloud has not been evaluated for Citrix SOC 2 (Type 1 or 2), ISO 27001, HIPAA, or other cloud compliance requirements. Citrix DaaS does not host the VDAs, so the customer’s application data and images required for provisioning are always hosted in the customer setup. The control plane has access to metadata, such as user names, machine names, and application shortcuts, restricting access to the customer’s Intellectual Property from the control plane.
Data flowing between the cloud and customer premises uses secure TLS connections over port 443. Citrix DaaS stores only the metadata needed for the brokering and monitoring of the customer’s applications and desktops. Sensitive information, including images, user profiles, and other application data remains on the customer premises or in their public cloud vendor’s subscription.
The capabilities of Citrix DaaS vary by edition. For example, Citrix Virtual Apps Essentials™ supports only Citrix Gateway service and Citrix® StoreFront Cloud. Consult that product documentation to learn more about supported features. Citrix DaaS provides several options for securing ICA traffic in transit. The following are the options available: It is recommended to use Secure HDX instead. Secure ICA was deprecated with the release of Citrix Virtual Apps and Desktops 2402.
When using HDX Direct in Internal only mode, traffic is encrypted as shown in the following diagram. When using HDX Direct in Internal and External mode, traffic is encrypted as shown in the following diagram. When using VDA TLS/DTLS encryption, traffic is encrypted as shown in the following diagram. When using the Gateway Service without Rendezvous, the traffic between the VDA and the Cloud Connector is not TLS encrypted, because the Cloud Connector does not support connecting to the VDA with network-level encryption.
Citrix recommends that users consult the published best practices documentation for deploying Citrix Gateway applications and VDAs within their environments. All connections from Citrix Cloud Connectors to DaaS and other Citrix Cloud services use HTTPS with TLS 1.2. If you use on-premise StoreFront or NetScaler Gateways, it is recommended that you enable HTTPS and disable HTTP on the connector. For more information, see HTTPS Configuration .
In addition to the ports described at Inbound and outbound ports configuration , Cloud Connectors have the following network access requirements: Traffic between the VDAs and Cloud Connectors is encrypted using Kerberos message-level security. You can use Security Keys to ensure that only authorized StoreFront servers and Citrix Gateway appliances are able to connect to DaaS via the cloud connectors. This is especially important if you have enabled XML trust .
You can provide client access via either Citrix hosted Citrix® StoreFront Cloud or by hosting your own StoreFront deployment. Users can connect to their store using either Citrix Workspace app or a web browser. For security recommendations for Citrix Workspace app, see the documentation for each platform. Citrix® StoreFront Cloud is a Citrix managed service that enables client apps to access DaaS resources without needing any on-premises infrastructure. For supported versions of Citrix Workspace app and other requirements, see Citrix® StoreFront Cloud System Requirements . For information on security, see Citrix® StoreFront Cloud security overview .
As an alternative to Citrix® StoreFront Cloud, you can provide client access by deploying Citrix® StoreFront in your local environment. This offers greater security configuration options and flexibility for deployment architecture, including the ability to maintain user credentials on-premises. The StoreFront server can be hosted behind a Citrix Gateway to provide secure remote access, enforce multifactor authentication, and add other security features. For more information see Secure your StoreFront deployment .
If the user authenticated to StoreFront with their active directory credentials, when a user launches an application, StoreFront passes the credentials to the Cloud Connector. By default the Cloud Connector encrypts user credentials using AES encryption and a random one-time key generated for each launch. The key is never passed into the cloud, and returned only to Citrix Workspace app. The Citrix Workspace app then passes this key to the VDA to decrypt the user password during session launch for a single sign-on experience. The flow is shown in the following figure.
It is important that you configure HTTPS between the client, gateway, storefront and connector to ensure that the password is always encrypted within your network. With the default behavior, as Citrix Cloud does not have access to the credentials, it is unable to forward the credentials to other Cloud Connectors or Connector Appliances for validation. This is required if you use multiple domains without trust relationships. You can disable this behavior and allow credentials to be uploaded to Citrix cloud so that it can forward them to other cloud connectors and Connector Appliances for validation. To configure this use the DaaS PowerShell SDK cmdlet Set-Brokersite with parameter CredentialForwardingToCloudAllowed .
It is recommended that you configure StoreFront to connect to the Cloud Connectors using HTTPS to ensure all communication is encrypted. This requires that you have enabled HTTPS for XML service and STA . To Configure StoreFront to connect using HTTPS, see Add resource feeds for Citrix Desktops as a Service and Add Citrix Gateway appliance . 5. Performance Evaluation & Extended Technical Observations By default, when StoreFront connects to DaaS for actions such as enumeration and launch, StoreFront must pass through the user’s Active Directory credentials so that DaaS can authenticate the user and check the user’s group membership. However when using other authentication methods such as domain pass-through, smart cards or SAML, StoreFront does not have the active directory password. In this case you must enable “XML Trust”. With XML trust enabled, DaaS allows StoreFront to perform actions on behalf of a user such as enumerating and launching applications without validating the user’s password.
Before enabling XML trust, use Security Keys or another mechanism such as firewalls or IPsec to ensure that only trusted StoreFront servers are able to connect to the Cloud Connectors. To enable XML trust in Studio, go to Settings > Site settings and turn on Enable XML trust . To use the Citrix DaaS SDK to check the XML trust current value, run Get-BrokerSite and inspect the value of TrustRequestsSentToTheXMLServicePort .
To use the Citrix DaaS SDK to enable or disable XML trust, run Set-BrokerSite with parameter TrustRequestsSentToTheXMLServicePort .
Using the Citrix Gateway service avoids the need to deploy Citrix Gateway within customer data centers. All TLS connections between the Cloud Connector and Citrix Cloud are initiated from the Cloud Connector to the Citrix Cloud. No in-bound firewall port mapping is required. You can use an on-premise NetScaler gateway to provide access to resources. The Gateway must be able to reach cloud connectors to redeem STA tickets. It is recommended you configure the gateway to connect to the Cloud Connectors using HTTPS, see HTTPS for XML service and STA . If you have enabled Security keys then you must configure the gateway to include the keys.
Citrix Trust Center : The trust center has documentation about standards and certifications that are important in maintaining a secure and compliant IT environment. Secure Deployment Guide for the Citrix Cloud Platform : This guide provides an overview of security best practices when using Citrix Cloud and describes the information Citrix Cloud collects and manages. This guide also contains links to comprehensive information about the Citrix Cloud Connector.
This document is intended to provide the reader with an introduction to and overview of the security functionality of Citrix Cloud; and to define the division of responsibility between Citrix and customers with regard to securing the Citrix Cloud deployment. It is not intended to serve as a configuration and administration guidance manual for Citrix Cloud or any of its components or services.
You agree to hold this documentation confidential pursuant to the terms of your Citrix Beta/Tech Preview Agreement. The development, release and timing of any features or functionality described in the Preview documentation remains at our sole discretion and are subject to change without notice or consultation. The documentation is for informational purposes only and is not a commitment, promise or legal obligation to deliver any material, code or functionality and should not be relied upon in making Citrix product purchase decisions.
Access to this page requires authorization. You can try signing in or changing directories . Azure Virtual Desktop is a managed virtual desktop service that includes many security capabilities for keeping your organization safe. The architecture of Azure Virtual Desktop comprises many components that make up the service connecting users to their desktops and apps.
Azure Virtual Desktop has many built-in advanced security features, such as Reverse Connect where no inbound network ports are required to be open, which reduces the risk involved with having remote desktops accessible from anywhere. The service also benefits from many other security features of Azure, such as multifactor authentication and conditional access. This article describes steps you can take as an administrator to keep your Azure Virtual Desktop deployments secure, whether you provide desktops and apps to users in your organization or to external users.
Before Azure Virtual Desktop, on-premises virtualization solutions like Remote Desktop Services require granting users access to roles like Gateway, Broker, Web Access, and so on. These roles had to be fully redundant and able to handle peak capacity. Administrators would install these roles as part of the Windows Server operating system, and they had to be domain-joined with specific ports accessible to public connections. To keep deployments secure, administrators had to constantly make sure everything in the infrastructure was maintained and up-to-date.
In most cloud services, however, there's a shared set of security responsibilities between Microsoft and the customer or partner. For Azure Virtual Desktop, most components are Microsoft-managed, but session hosts and some supporting services and components are customer-managed or partner-managed. To learn more about the Microsoft-managed components of Azure Virtual Desktop, see Azure Virtual Desktop service architecture and resilience .
While some components come already secured for your environment, you'll need to configure other areas yourself to fit your organization's or customer's security needs. Here are the components of which you're responsible for the security in your Azure Virtual Desktop deployment: Security boundaries separate the code and data of security domains with different levels of trust. For example, there's usually a security boundary between kernel mode and user mode. Most Microsoft software and services depend on multiple security boundaries to isolate devices on networks, virtual machines (VMs), and applications on devices. The following table lists each security boundary for Windows and what they do for overall security.
You'll also need to make certain choices about security boundaries on a case-by-case basis. For example, if a user in your organization needs local administrator privileges to install apps, you'll need to give them a personal desktop instead of a shared session host. We don't recommend giving users local administrator privileges in multi-session pooled scenarios because these users can cross security boundaries for sessions or NTFS data permissions, shut down multi-session VMs, or do other things that could interrupt service or cause data losses.
Users from the same organization, like knowledge workers with apps that don't require administrator privileges, are great candidates for multi-session session hosts like Windows 11 Enterprise multi-session. These session hosts reduce costs for your organization because multiple users can share a single VM, with only the overhead costs of a VM per user. With user profile management products like FSLogix, users can be assigned any VM in a host pool without noticing any service interruptions. This feature also lets you optimize costs by doing things like shutting down VMs during off-peak hours.
If your situation requires users from different organizations to connect to your deployment, we recommend you have a separate tenant for identity services like Active Directory and Microsoft Entra ID. We also recommend you have a separate subscription for those users for hosting Azure resources like Azure Virtual Desktop and VMs. In many cases, using multi-session is an acceptable way to reduce costs, but whether we recommend it depends on the trust level between users with simultaneous access to a shared multi-session instance. Typically, users that belong to the same organization have a sufficient and agreed-upon trust relationship. For example, a department or workgroup where people collaborate and can access each otherâIIs personal information is an organization with a high trust level.
Windows uses security boundaries and controls to ensure user processes and data are isolated between sessions. However, Windows still provides access to the instance the user is working on. Multi-session deployments would benefit from a security in depth strategy that adds more security boundaries that prevent users within and outside of the organization from getting unauthorized access to other users' personal information.
Unauthorized data access happens because of an error in the configuration process by the system admin, such as an undisclosed security vulnerability or a known vulnerability that hasn't been patched out yet. We don't recommend granting users that work for different or competing companies access to the same multi-session environment. These scenarios have several security boundaries that can be attacked or abused, like network, kernel, process, user, or sessions. A single security vulnerability could cause unauthorized data and credential theft, personal information leaks, identity theft, and other issues. Virtualized environment providers are responsible for offering well-designed systems with multiple strong security boundaries and extra safety features enabled wherever possible.
Reducing these potential threats requires a fault-proof configuration, patch management design process, and regular patch deployment schedules. It's better to follow the principles of defense in depth and keep environments separate. Azure Virtual Desktop is a service under Azure. To maximize the safety of your Azure Virtual Desktop deployment, you should make sure to secure the surrounding Azure infrastructure and management plane as well. To secure your infrastructure, consider how Azure Virtual Desktop fits into your larger Azure ecosystem. To learn more about the Azure ecosystem, see Azure security best practices and patterns .
Today's threat landscape requires designs with security approaches in mind. Ideally, you'll want to build a series of security mechanisms and controls layered throughout your computer network to protect your data and network from being compromised or attacked. This type of security design is what the United States Cybersecurity and Infrastructure Security Agency (CISA) calls defense in depth .
The following sections contain recommendations for securing an Azure Virtual Desktop deployment. Secure Score provides recommendations and best practice advice for improving your overall security. These recommendations are prioritized to help you pick which ones are most important, and the Quick Fix options help you address potential vulnerabilities quickly. These recommendations also update over time, keeping you up to date on the best ways to maintain your environmentâIIs security. To learn more, see Improve your Secure Score in Microsoft Defender for Cloud .
Requiring multifactor authentication for all users and admins in Azure Virtual Desktop improves the security of your entire deployment. To learn more, see Enable Microsoft Entra multifactor authentication for Azure Virtual Desktop . Enabling Conditional Access lets you manage risks before you grant users access to your Azure Virtual Desktop environment. When deciding which users to grant access to, we recommend you also consider who the user is, how they sign in, and which device they're using.
Enabling audit log collection lets you view user and admin activity related to Azure Virtual Desktop. Some examples of key audit logs are: Monitor your Azure Virtual Desktop service's usage and availability with Azure Monitor . Consider creating service health alerts for the Azure Virtual Desktop service to receive notifications whenever there's a service impacting event.
Encrypt your session hosts with managed disk encryption options to protect stored data from unauthorized access. Session hosts are virtual machines that run inside an Azure subscription and virtual network. Your Azure Virtual Desktop deployment's overall security depends on the security controls you put on your session hosts. This section describes best practices for keeping your session hosts secure.
To protect your deployment from known malicious software, we recommend enabling endpoint protection on all session hosts. You can use either Windows Defender Antivirus or a third-party program. For more information, see Deployment guide for Windows Defender Antivirus in a VDI environment . For profile solutions like FSLogix or other solutions that mount virtual hard disk files, we recommend excluding those file extensions. For more information on FSLogix exclusions, see Configure Antivirus file and folder exclusions .
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Remote%20desktop%20software • https://en.wikipedia.org/wiki/Virtualization • https://en.wikipedia.org/wiki/Remote%20Desktop%20Protocol • https://docs.citrix.com/en-us/citrix-virtual-apps-desktops/technical-overview.html • https://learn.microsoft.com/en-us/azure/architecture/virtual-desktop/virtual-desktop-get-started • https://docs.citrix.com/en-us/citrix-daas/secure.html • https://learn.microsoft.com/en-us/azure/virtual-desktop/security-recommendations
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Virtual Desktop Security Monitor.
[*] Metasploit Scan Running on Target Subnet for Virtual Desktop Security Monitor... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |