Complete Technical Paper Content — Virtual Private Network Client Server Implementation In C
Overview & System Context
Virtual Private Network Client Server Implementation In C: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8683 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A content delivery network (CDN) or content distribution network is a geographically distributed network of proxy servers and corresponding data centers. CDNs provide high availability and performance by distributing content geographically closer to end users, and arose in the late 1990s to alleviate the performance bottlenecks of the Internet as it was becoming a critical medium. Since then, CDNs have grown to serve a large portion of Internet content, including text, graphics and scripts, downloadable objects (media files, software, and documents), applications (e-commerce, portals), live streaming media, on-demand streaming media, and social media services. CDNs are a layer in the internet ecosystem. Content owners such as media companies and e-commerce vendors pay CDN operators to deliver their content to their end users. In turn, a CDN pays Internet service providers (ISPs), carriers, and network operators for hosting its servers in their data centers. CDN is an umbrella term spanning different types of content delivery services: video streaming, software downloads, web and mobile content acceleration, licensed/managed CDN, transparent caching, and services to measure CDN performance, load balancing, Multi CDN switching, analytics, and cloud intelligence. CDN vendors may cross over into other industries like security, DDoS protection and web application firewalls (WAF), and WAN optimization. Content delivery service providers include Akamai Technologies, Cloudflare, Amazon CloudFront, Qwilt (Cisco), Fastly, CDN77, BunnyCDN, EdgeNext, and Google Cloud CDN.
Content Provider Origin Server: the web server providing the source content CDN entry point(s): the servers within the CDN that fetch the content from the origin CDN Origin Shield: the CDN service helping to protect the origin server in case of heavy traffic CDN Edge Servers: the CDN servers serving the content request from the clients CDN footprint: the geographic areas where the CDN Edge Servers can effectively serve clients' requests CDN selector: in the context of multi-CDN, a decision-making service to choose among multiple CDNs CDN offloading: in the context of Peer-to-Peer CDN, a mechanism to help deliver the content between clients who are consuming it, in addition to CDN Edge Server delivery In peer-to-peer (P2P) content-delivery networks, clients provide resources as well as use them. This means that, unlike client–server systems, the content-centric networks can actually perform better as more users begin to access the content (especially with protocols such as Bittorrent that require users to share). This property is one of the major advantages of using P2P networks because it makes the setup and running costs very small for the original content distributor. To incentivize peers to participate in the P2P network, web3 and blockchain technologies can be used: participating nodes receive crypto tokens in exchange for their involvement.
In June 2011, StreamingMedia.com reported that a group of TSPs had founded an Operator Carrier Exchange (OCX) to interconnect their networks and compete more directly against large traditional CDNs like Akamai and Limelight Networks, which have extensive PoPs worldwide. This way, telcos are building a Federated CDN offering, which is more interesting for a content provider willing to deliver its content to the aggregated audience of this federation. The IETF has standardized a framework and a request-routing interface for interconnecting CDNs, so that a request handled by one CDN can be redirected to another. It is likely that in the near future, other telco CDN federations will be created. They will grow by enrollment of new telcos joining the federation and bringing network presence and their Internet subscriber bases to the existing ones. The Open Caching specification by Streaming Video Technology Alliance defines a set of APIs that allows a Content Provider to deliver its content using several CDNs in a consistent way, seeing each CDN provider the same way through these APIs.
Figure 1: Virtual Private Network (VPN) Lab CI_virtual private network lab-CSDNII Traditionally, CDNs have used the IP of the client's recursive DNS resolver to geo-locate the client. While this is a sound approach in many situations, this leads to poor client performance if the client uses a non-local recursive DNS resolver that is far away. For instance, a CDN may route requests from a client in India to its edge server in Singapore, if that client uses a public DNS resolver in Singapore, causing poor performance for that client. Indeed, a recent study showed that in many countries where public DNS resolvers are in popular use, the median distance between the clients and their recursive DNS resolvers can be as high as a thousand miles. In August 2011, a global consortium of leading Internet service providers led by Google announced their official implementation of the edns-client-subnet IETF Internet Draft, which is intended to accurately localize DNS resolution responses. The initiative involves a limited number of leading DNS service providers, such as Google Public DNS, and CDN service providers as well. With the edns-client-subnet EDNS0 option, CDNs can now utilize the IP address of the requesting client's subnet when resolving DNS requests. This approach, called end-user mapping, has been adopted by CDNs, and it has been shown to drastically reduce the round-trip latencies and improve performance for clients who use public DNS or other non-local resolvers. However, the use of EDNS0 also has drawbacks as it decreases the effectiveness of caching resolutions at the recursive resolvers, increases the total DNS resolution traffic, and raises a privacy concern of exposing the client's subnet.
A Content Delivery Network (CDN) for the fast serving of images. Image manipulation and optimization, either on-the-fly through URL directives, in batch mode (through manual upload of images) or fully automatic (or a combination of these). Device Detection (also known as Device Intelligence), i.e. the ability to determine the properties of the requesting browser and/or device through analysis of the User-Agent string, HTTP Accept headers, Client-Hints or JavaScript. The following table summarizes the current situation with the main software CDNs in this space: The Network Time Protocol (NTP) is a networking protocol for clock synchronization between computer systems over packet-switched, variable-latency data networks. In operation since before 1985, NTP is one of the oldest Internet protocols in current use. NTP was designed by David L. Mills of the University of Delaware. NTP is intended to synchronize participating computers to within a few milliseconds of Coordinated Universal Time (UTC). It uses the intersection algorithm, a modified version of Marzullo's algorithm, to select accurate time servers and is designed to mitigate the effects of variable network latency. NTP can usually maintain time to within tens of milliseconds over the public Internet, and can achieve better than one millisecond accuracy in local area networks under ideal conditions. Asymmetric routes and network congestion can cause errors of 100 ms or more. The protocol is usually described in terms of a client–server model, but can as easily be used in peer-to-peer relationships where both peers consider the other to be a potential time source. Implementations send and receive timestamps using the User Datagram Protocol (UDP); the service is normally on port number 123, and in some modes both sides use this port number. They can also use broadcasting or multicasting, where clients passively listen to time updates after an initial round-trip calibrating exchange. NTP supplies a warning of any impending leap second adjustment, but no information about local time zones or daylight saving time is transmitted. The current protocol is version 4 (NTPv4), which is backward compatible with version 3.
A typical NTP client regularly polls one or more NTP servers. The client must compute its time offset and round-trip delay. Time offset θ is the positive or negative (client time > server time) difference in absolute time between the two clocks. It is defined by Figure 2: Virtual Private Network (VPN) Lab CI_virtual private network lab-CSDNII θ = ( t 1 − t 0 ) + ( t 2 − t 3 ) 2 , {\displaystyle \theta ={\frac {(t_{1}-t_{0})+(t_{2}-t_{3})}{2}},} 2. System Architecture & Core Working Principles δ = ( t 3 − t 0 ) − ( t 2 − t 1 ) , {\displaystyle \delta ={(t_{3}-t_{0})-(t_{2}-t_{1})},} t0 is the client's timestamp of the request packet transmission, t1 is the server's timestamp of the request packet reception, t2 is the server's timestamp of the response packet transmission and t3 is the client's timestamp of the response packet reception. To derive the expression for the offset, note that for the request packet, t 0 + θ + δ / 2 = t 1 {\displaystyle t_{0}+\theta +\delta /2=t_{1}} t 3 + θ − δ / 2 = t 2 {\displaystyle t_{3}+\theta -\delta /2=t_{2}} Figure 3: Virtual Private Network (VPN) Lab CI_virtual private network lab-CSDNII Solving for θ yields the definition of the time offset. The values for θ and δ are passed through filters and subjected to statistical analysis ("mitigation"). Outliers are discarded and an estimate of time offset is derived from the best three remaining candidates. The clock frequency is then adjusted to reduce the offset gradually ("discipline"), creating a feedback loop.
Accurate synchronization is achieved when both the incoming and outgoing routes between the client and the server have symmetrical nominal delay. If the routes do not have a common nominal delay, a systematic bias exists of half the difference between the forward and backward travel times. A number of approaches have been proposed to measure asymmetry, but among practical implementations only chrony seems to have one included.
In 1979, network time synchronization technology was used in what was possibly the first public demonstration of Internet services running over a trans-Atlantic satellite network, at the National Computer Conference in New York. The technology was later described in the 1981 Internet Engineering Note (IEN) 173 and a public protocol was developed from it that was documented in RFC 778. The technology was first deployed in a local area network as part of the Hello routing protocol and implemented in the Fuzzball router, an experimental operating system used in network prototyping, where it ran for many years. Other related network tools were available both then and now. They include the Daytime and Time protocols for recording the time of events, as well as the ICMP Timestamp messages and IP Timestamp option (RFC 781). More complete synchronization systems, although lacking NTP's data analysis and clock disciplining algorithms, include the Unix daemon timed, which uses an election algorithm to appoint a server for all the clients; and the Digital Time Synchronization Service (DTSS), which uses a hierarchy of servers similar to the NTP stratum model. In 1985, NTP version 0 (NTPv0) was implemented in both Fuzzball and Unix, and the NTP packet header and round-trip delay and offset calculations, which have persisted into NTPv4, were documented in RFC 958. Despite the relatively slow computers and networks available at the time, accuracy of better than 100 milliseconds was usually obtained on Atlantic spanning links, with accuracy of tens of milliseconds on Ethernet networks. In 1988, a much more complete specification of the NTPv1 protocol, with associated algorithms, was published in RFC 1059. It drew on the experimental results and clock filter algorithm documented in RFC 956 and was the first version to describe the client–server and peer-to-peer modes. In 1991, the NTPv1 architecture, protocol and algorithms were brought to the attention of a wider engineering community with the publication of an article by David L. Mills in with pseudocode to describe its operation. It introduced a management protocol and cryptographic authentication scheme which have both survived into NTPv4, along with the bulk of the algorithm. However the design of NTPv2 was criticized for lacking formal correctness by the DTSS community, and the clock selection procedure was modified to incorporate Marzullo's algorithm for NTPv3 onwards. In 1992, RFC 1305 defined NTPv3. The RFC included an analysis of all sources of error, from the reference clock down to the final client, which enabled the calculation of a metric that helps choose the best server where several candidates appear to disagree. Broadcast mode was introduced. In subsequent years, as new features were added and algorithm improvements were made, it became apparent that a new protocol version was required. In 2010, RFC 5905 was published containing a proposed specification for NTPv4. Following the retirement of Mills from the University of Delaware, the reference implementation is currently maintained as an open source project led by Harlan Stenn. On the IANA side, an ntp (Network Time Protocols) work group is in charge of reviewing proposed drafts. The protocol has significantly progressed since NTPv4. As of 2022, three RFC documents describing updates to the protocol have been published, not counting the numerous peripheral standards such as Network Time Security. Mills had mentioned plans for a "NTPv5" on his page, but one was never published. An unrelated draft termed "NTPv5" by M. Lichvar of chrony was initiated in 2020 and includes security, accuracy, and scaling changes.
As NTP replaced the old Time Protocol, some use cases nevertheless found the full protocol too complicated. In 1992, Simple Network Time Protocol (SNTP) was defined to fill this niche. The SNTPv3 standard describes a way to use NTPv3 such that no storage of state over an extended period is needed. The topology becomes essentially the same as with the Time Protocol, as only one server is used. In 1996, SNTP was updated to SNTPv4, with some features of the then-in-development NTPv4.
SNTPv4 was merged into the main NTPv4 standard in 2010. SNTP is fully interoperable with NTP since it does not define a new protocol, as it utilizes the same packet format and port as NTP, ensuring compatibility with NTP servers. However, client/server will lack the complex algorithms required to filter network jitter, analyze clock drift, or cross-reference multiple time sources. This makes it suitable for IoT devices and basic hardware that require "good enough" time without the overhead of a full NTP application stack. An SNTP client typically operates by querying a single server and applying the received time directly to the local clock. However, the simple algorithms provide times of reduced accuracy and thus it is inadvisable to sync time from an SNTP source. However, RFC 5905 notes that because the additional complexity of the full on-wire protocol is minimal, full implementation is encouraged even for simple clients.
NTP uses a hierarchical, semi-layered system of time sources. Each level of this hierarchy is termed a stratum and is assigned a number starting with zero for the reference clock at the top. A server synchronized to a stratum n server runs at stratum n + 1. The number represents the distance from the reference clock and is used to prevent cyclical dependencies in the hierarchy. Stratum is not always an indication of quality or reliability; it is common to find stratum 3 time sources that are higher quality than some stratum 2 time sources. Brief descriptions of strata 0, 1, 2 and 3 are provided below.
Stratum 0 These are high-precision timekeeping devices such as atomic clocks, GNSS (including GPS) or other radio clocks, or PTP-synchronized clocks. They generate a very accurate pulse per second signal that triggers an interrupt and timestamp on a connected computer. Stratum 0 devices are also known as reference clocks. NTP servers cannot advertise themselves as stratum 0; a stratum field set to 0 in an NTP message indicates an unspecified stratum. Stratum 1 These are computers whose system time is synchronized to within a few microseconds of their attached stratum 0 devices. Stratum 1 servers may peer with other stratum 1 servers for sanity check and backup. They are also referred to as primary time servers. Stratum 2 These are computers that are synchronized over a network to stratum 1 servers. Often a stratum 2 computer queries several stratum 1 servers. Stratum 2 computers may also peer with other stratum 2 computers to provide more stable and robust time for all devices in the peer group. Stratum 3 These are computers that are synchronized to stratum 2 servers. They employ the same algorithms for peering and data sampling as stratum 2, and can themselves act as servers for stratum 4 computers, and so on. The upper limit for stratum is 15; stratum 16 is used to indicate that a device is unsynchronized. The NTP algorithms on each computer interact to construct a Bellman–Ford shortest-path spanning tree, to minimize the accumulated round-trip delay to the stratum 1 servers for all the clients. In addition to stratum, the protocol is able to identify the synchronization source for each server in terms of a reference identifier (refid).
3. Software Implementation, Frameworks & Protocols For servers on stratum 2 and below, the refid is an encoded form of the upstream time server's IP address. For IPv4, this is simply the 32-bit address; for IPv6, it would be the first 32 bits of the MD5 hash of the source address. Refids serve to detect and prevent timing loops to the first degree. The refid field is filled with status words in the case of kiss-o'-death (KoD) packets, which tell the client to stop sending requests so that the server can rest. Some examples are INIT (initialization), STEP (step time change), and RATE (client requesting too fast). The program output may additionally use codes not transmitted in the packet to indicate error, such as XFAC to indicate a network disconnection. The IANA maintains a registry for refid source names and KoD codes. Informal assignments can still appear.
chrony is an independent NTP implementation mainly sponsored by Red Hat, who uses it as the default time program in their distributions. Being written from scratch, chrony has a simpler codebase allowing for better security and lower resource consumption. It does not however, compromise on accuracy, instead syncing faster and better than the reference ntpd in many circumstances. It is versatile enough for ordinary computers, which are unstable, go into sleep mode or have intermittent connection to the Internet. It is also designed for virtual machines, a more unstable environment. chrony has been evaluated as "trustworthy", with only a few incidents. It is able to achieve improved precision on LAN connections, using hardware timestamping on the network adapter. Support for Network Time Security (NTS) was added on version 4.0. chrony is available under GNU General Public License version 2, was created by Richard Curnow in 1997 and is currently maintained by Miroslav Lichvar.
ntpd-rs is a security-focused implementation of the NTP protocol, founded by the Internet Security Research Group as part of their Prossimo initiative for the creation of memory-safe Internet infrastructure. ntpd-rs is implemented in Rust programming language which offers memory safety guarantees in addition to the real-time computing capabilities which are required for an NTP implementation. ntpd-rs is used in security-sensitive environments such as the Let's Encrypt non-profit Certificate Authority. Support for NTS is available. ntpd-rs is part of the "Pendulum" project which also includes a Precision Time Protocol implementation "statime". Both projects are available under Apache and MIT software licenses.
Because adjusting system time is generally a privileged operation, part or all of NTP code has to be run with some privileges in order to support its core functionality. Only a few other security problems have been identified in the reference implementation of the NTP codebase, but those that appeared in 2009, such as arbitrary code execution and denial-of-service attacks, were cause for significant concern. The protocol has been undergoing revision and review throughout its history. The codebase for the reference implementation has undergone security audits from several sources for several years. A stack buffer overflow exploit was discovered and patched in 2014. Apple was concerned enough about this vulnerability that it used its auto-update capability for the first time. On systems using the reference implementation, which is running with root user's credential, this could allow unlimited access. Some other implementations, such as OpenNTPD, have smaller code base and adopted other mitigation measures like privilege separation, are not subject to this flaw. A 2017 security audit of three NTP implementations, conducted on behalf of the Linux Foundation's Core Infrastructure Initiative, suggested that both NTP and NTPsec were more problematic than chrony from a security standpoint. NTP servers can be susceptible to man-in-the-middle attacks unless packets are cryptographically signed for authentication. The computational overhead involved can make this impractical on busy servers, particularly during denial of service attacks. NTP message spoofing from a man-in-the-middle attack can be used to alter clocks on client computers and allow a number of attacks based on bypassing of cryptographic key expiration. Some of the services affected by fake NTP messages identified are TLS, DNSSEC, various caching schemes (such as DNS cache), Border Gateway Protocol (BGP), Bitcoin and a number of persistent login schemes. NTP has been used in distributed denial of service attacks. A small query is sent to an NTP server with the return IP address spoofed to be the target address. Similar to the DNS amplification attack, the server responds with a much larger reply that allows an attacker to substantially increase the amount of data being sent to the target. To avoid participating in an attack, NTP server software can be upgraded or servers can be configured to ignore external queries.
LI (Leap Indicator): 2 bits Warning of leap second insertion or deletion: 0 = no warning 1 = last minute has 61 seconds 2 = last minute has 59 seconds 3 = unknown (clock unsynchronized) VN (Version Number): 3 bits NTP version number, typically 4. Mode: 3 bits Association mode: 0 = reserved 1 = symmetric active 2 = symmetric passive 3 = client 4 = server 5 = broadcast 6 = control 7 = private Stratum: 8 bits Indicates the distance from the reference clock. 0 = invalid 1 = primary server 2–15 = secondary 16 = unsynchronized Poll: 8 bits Maximum interval between successive messages, in logI(seconds). Typical range is 6 to 10. Precision: 8 bits Signed logI(seconds) of system clock precision (e.g., –18 ≈ 1 microsecond). Root Delay: 32 bits Total round-trip delay to the reference clock, in NTP short format. Root Dispersion: 32 bits Total dispersion to the reference clock, in NTP short format. Reference ID: 32 bits Identifies the specific server or reference clock; interpretation depends on Stratum. Reference Timestamp: 64 bits Time when the system clock was last set or corrected, in NTP timestamp format. Origin Timestamp (org): 64 bits Time at the client when the request departed, in NTP timestamp format. Receive Timestamp (rec): 64 bits The local time, in timestamp format, when the latest NTP message arrived. Transmit Timestamp (xmt): 64 bits Time at the server when the response left, in NTP timestamp format. Extension Field: variable Optional field(s) for NTP extensions (see , Section 7.5). Key Identifier: 32 bits Unsigned integer designating an MD5 key shared by the client and server. Message Digest (MD5): 128 bits MD5 hash covering the packet header and extension fields, used for authentication.
Option code: 42 Minimum length: 4 octets Length: must be a multiple of 4 Content: a sequence of 32-bit IPv4 addresses, each address represents one NTP server Examples: 42|2|192.0.2.1|192.0.2.2 Standard time: EST (UTC−5) Daylight saving time: EDT (UTC−4) DST starts: second Sunday in March at 02:00 DST ends: first Sunday in November at 02:00 The semantics and string formats are identical to those used in DHCPv4; only the binary encoding differs due to protocol differences between DHCPv4 and DHCPv6.
DHCP provides IP configuration and time zone information. NTP synchronises the system clock to UTC. The operating system applies the configured time zone to present local time to users and applications. This separation keeps NTP simple and avoids embedding region-specific political and legal time rules into the time synchronisation protocol. 4. Practical Deployment, Analysis & Case Studies An intranet is a computer network for sharing information, easier communication, collaboration tools, operational systems, and other computing services within an organization, usually to the exclusion of access by outsiders. The term is used in contrast to public networks, such as the Internet, but uses the same technology based on the Internet protocol suite. An organization-wide intranet can constitute a focal point of internal communication and collaboration, and provide a single starting point to access internal and external resources. In its simplest form, an intranet is established with the technologies for local area networks (LANs) and wide area networks (WANs). Many modern intranets have search engines, user profiles, blogs, mobile apps with notifications, and events planning within their infrastructure. An intranet is sometimes contrasted to an extranet. While an intranet is generally restricted to employees of the organization, extranets may also be accessed by customers, suppliers, or other approved parties. Extranets extend a private network onto the Internet with special provisions for authentication, authorization and accounting (AAA protocol).
Intranets can help users locate and view information faster and use applications relevant to their roles and responsibilities. With a web browser interface, users can access data held in any database the organization wants to make available at any time and — subject to security provisions — from anywhere within company workstations, increasing employees' ability to perform their jobs faster, more accurately, and with confidence that they have the right information. It also helps improve services provided to users. Using hypermedia and web technology, intranets allow for the synchronized sharing of corporate knowledge, such as employee manuals, benefits documents, company policies, business standards, news feeds, and training, all of which can be accessed throughout a company using common internet standards. Intranets are also used as a platform for deploying applications to support business operations across the inter-networked enterprise. Information is easily accessible to all authorised users, enabling collaboration. Being able to communicate in real-time through integrated third-party tools, such as an instant messenger, promotes the sharing of ideas and removes blockages to communication to help boost a business's productivity. Intranets can serve as powerful tools for communicating (such as through chat, email and/or blogs) within a given organization about vertically strategic initiatives that have a global reach throughout said organization. The type of information that can easily be conveyed is the purpose of the initiative and what it is aiming to achieve, who is driving it, results achieved to date, and whom to speak to for more information. By providing this information on the intranet, staff can keep up-to-date with the strategic focus of their organization. For example, when Nestlé had a number of food processing plants in Scandinavia, their central support system had to deal with a number of queries every day.
When Nestlé decided to invest in an intranet, they quickly realized the savings. Gerry McGovern says that the savings from the reduction in query calls was substantially greater than the investment in the intranet. Users can view information and data via a web browser rather than maintaining physical documents such as procedure manuals, internal phone list and requisition forms. This can potentially save the business money on printing, duplicating documents, and the environment, as well as document maintenance overhead. For example, the HRM company PeopleSoft "derived significant cost savings by shifting HR processes to the intranet". McGovern goes on to say the manual cost of enrolling in benefits was found to be US$109.48 per enrollment. "Shifting this process to the intranet reduced the cost per enrollment to $21.79; a saving of 80 percent".
Another company that saved money on expense reports was Cisco. "In 1996, Cisco processed 54,000 reports and the amount of dollars processed was USD19 million". Many companies dictate computer specifications which, in turn, may allow Intranet developers to write applications that only have to work on one browser such that there are no cross-browser compatibility issues. Being able to specifically address one's "viewer" is a great advantage. Since intranets are user-specific (requiring database/network authentication prior to access), users know exactly who they are interfacing with and can personalize their intranet based on role (job title, department) or individual ("Congratulations Jane, on your 3rd year with our company!"). Since "involvement in decision making" is one of the main drivers of employee engagement, offering tools (like forums or surveys) that foster peer-to-peer collaboration and employee participation can make employees feel more valued and involved.
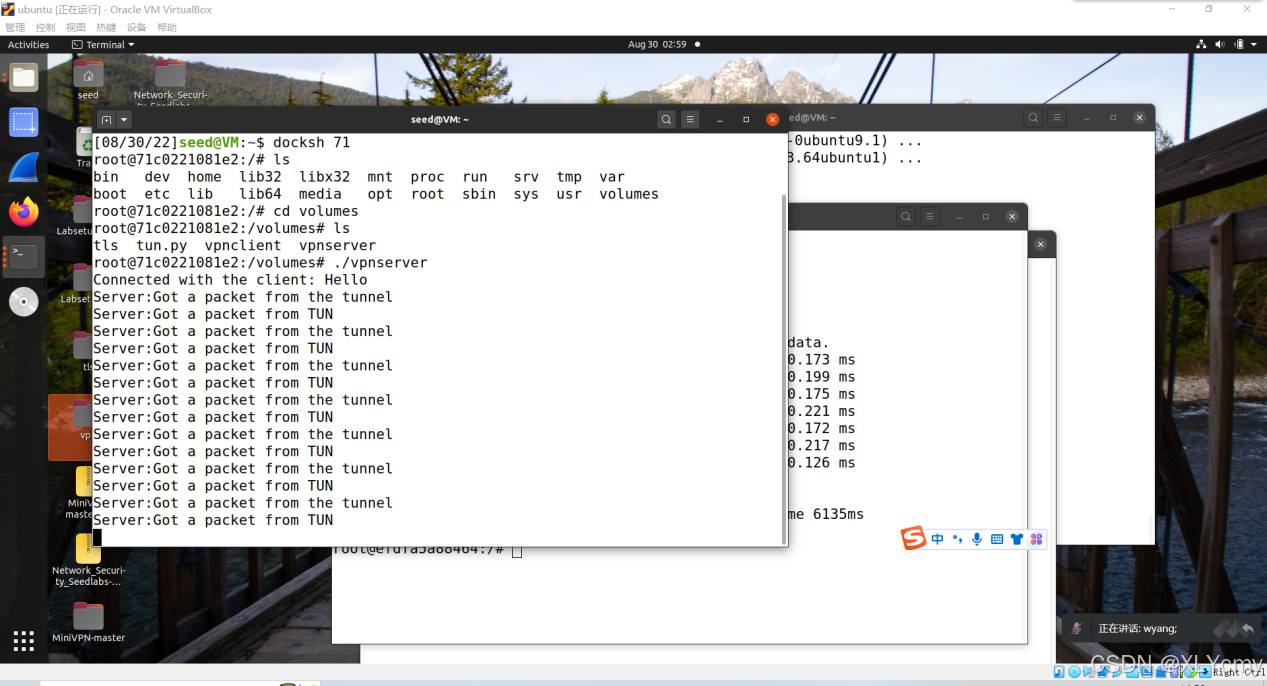
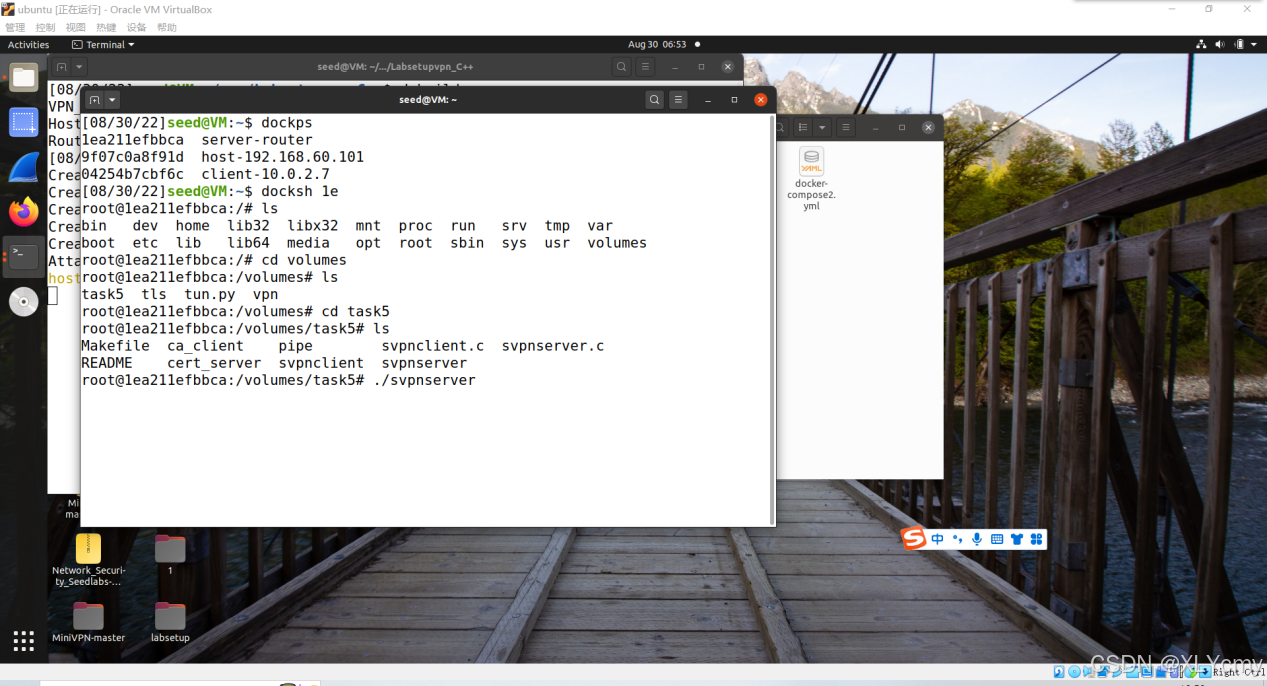
All R1(client) traffic flows through tun0. R1 reaches the R2(server) through its gw specifically. R2 reaches R1 through R2 gw specifically. All traffic with source address of tunnel not destined for tunnel, send to external interface and masqurade. r1 with vpn client process running, able to establish connection with r2 vpn server through tunneling.
r1 sends all its traffic to r2 (vpn server) which masqurades all traffic not belong to vpn subnet, out external interface, to host and out - can browse the web. Example of frame protocols encapsulation (using wireshark) visible on external interface and tun0: Frame IP packet with internal addresses of client/server udp datagram udpencap - udp encapsulated packet esp - encapsulating security payload - IP packet encapsulated (not encrypted).
TCP meltdown happens when TCP VPN tunnel transporting another tcp traffic, if packet lost or damaged and packet retransmission required, internal tcp asks for retransmission, the same can happen on the outer TCP which can also experience packet loss, the inner TCP can treat the packets on the outer layer as retransmitted packets leading to delay, and issues.
5. Performance Evaluation & Extended Technical Observations As UDP is stateless protocol as oppose to TCP which is connection oriented and have connect protocol initiated with listen / accept, UDP doesnt need to listen for connections, as datagrams can come in any order from any source. Raw sockets cannot be binded to port, as port related to TCP and UDP protocols. We work here at low level where concept of port is not known. So it can only read() and write() bytes from and to. Read raw bytes from tun and Write to.
tap - kernel process ethernet frames based on mac. tun - kernel process IP packets, routing decisions based on destination IP. TUN is a virtual device which is used for point-to-point connections at layer 3. After interface configuration and adjusting the routing table accordingly for the point to point connection: When process sends data, the packet will be passed to kernel which will check the route path for this packet in routing table.
This packet related to point to point connection, kernel will send the packet through tun0 which will read the data, encapsulate it within another packet, and send back to kernel, this time it will route the packet outside the physical interface. Client calls SetRouting to set its routing table accordingly after which it will enter a loop. Prerequisites - Socket Programming in C/C++ , TCP and UDP server using select , UDP Server-Client implementation in C If we are creating a connection between client and server using TCP then it has a few functionalities like, TCP is suited for applications that require high reliability, and transmission time is relatively less critical. It is used by other protocols like HTTP, HTTPs, FTP, SMTP, Telnet. TCP rearranges data packets in the order specified. There is absolute guarantee that the data transferred remains intact and arrives in the same order in which it was sent. TCP does Flow Control and requires three packets to set up a socket connection before any user data can be sent. TCP handles reliability and congestion control. It also does error checking and error recovery. Erroneous packets are retransmitted from the source to the destination.
This eBook requires no passwords or activation to read. We customize your eBook by discreetly watermarking it with your name, making it uniquely yours. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Content%20delivery%20network • https://en.wikipedia.org/wiki/Network%20Time%20Protocol • https://en.wikipedia.org/wiki/Intranet • https://github.com/YanShtein/C_vpn_client_server • https://www.geeksforgeeks.org/c/tcp-server-client-implementation-in-c/ • https://www.ciscopress.com/store/ccnp-security-virtual-private-networks-svpn-300-730-9780136634867
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Virtual Private Network Client Server Implementation In C.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |