Complete Technical Paper Content — Visual Cryptography For Secret Image Sharing In Python
Overview & System Context
Visual Cryptography For Secret Image Sharing In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~6755 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Visual cryptography is a cryptographic technique which allows visual information (pictures, text, etc.) to be encrypted in such a way that the decrypted information appears as a visual image. One of the best-known techniques has been credited to Moni Naor and Adi Shamir, who developed it in 1994. They demonstrated a visual secret sharing scheme, where a binary image was broken up into n shares so that only someone with all n shares could decrypt the image, while any n − 1 shares revealed no information about the original image. Each share was printed on a separate transparency, and decryption was performed by overlaying the shares. When all n shares were overlaid, the original image would appear. There are several generalizations of the basic scheme including k-out-of-n visual cryptography, and using opaque sheets but illuminating them by multiple sets of identical illumination patterns under the recording of only one single-pixel detector, which exposed the image. Using a similar idea, transparencies can be used to implement a one-time pad encryption, where one transparency is a shared random pad, and another transparency acts as the ciphertext. Normally, there is an expansion of space requirement in visual cryptography. But if one of the two shares is structured recursively, the efficiency of visual cryptography can be increased to 100%. Some antecedents of visual cryptography are in patents from the 1960s. Other antecedents are in the work on perception and secure communication. Visual cryptography can be used to protect biometric templates in which decryption does not require any complex computations.
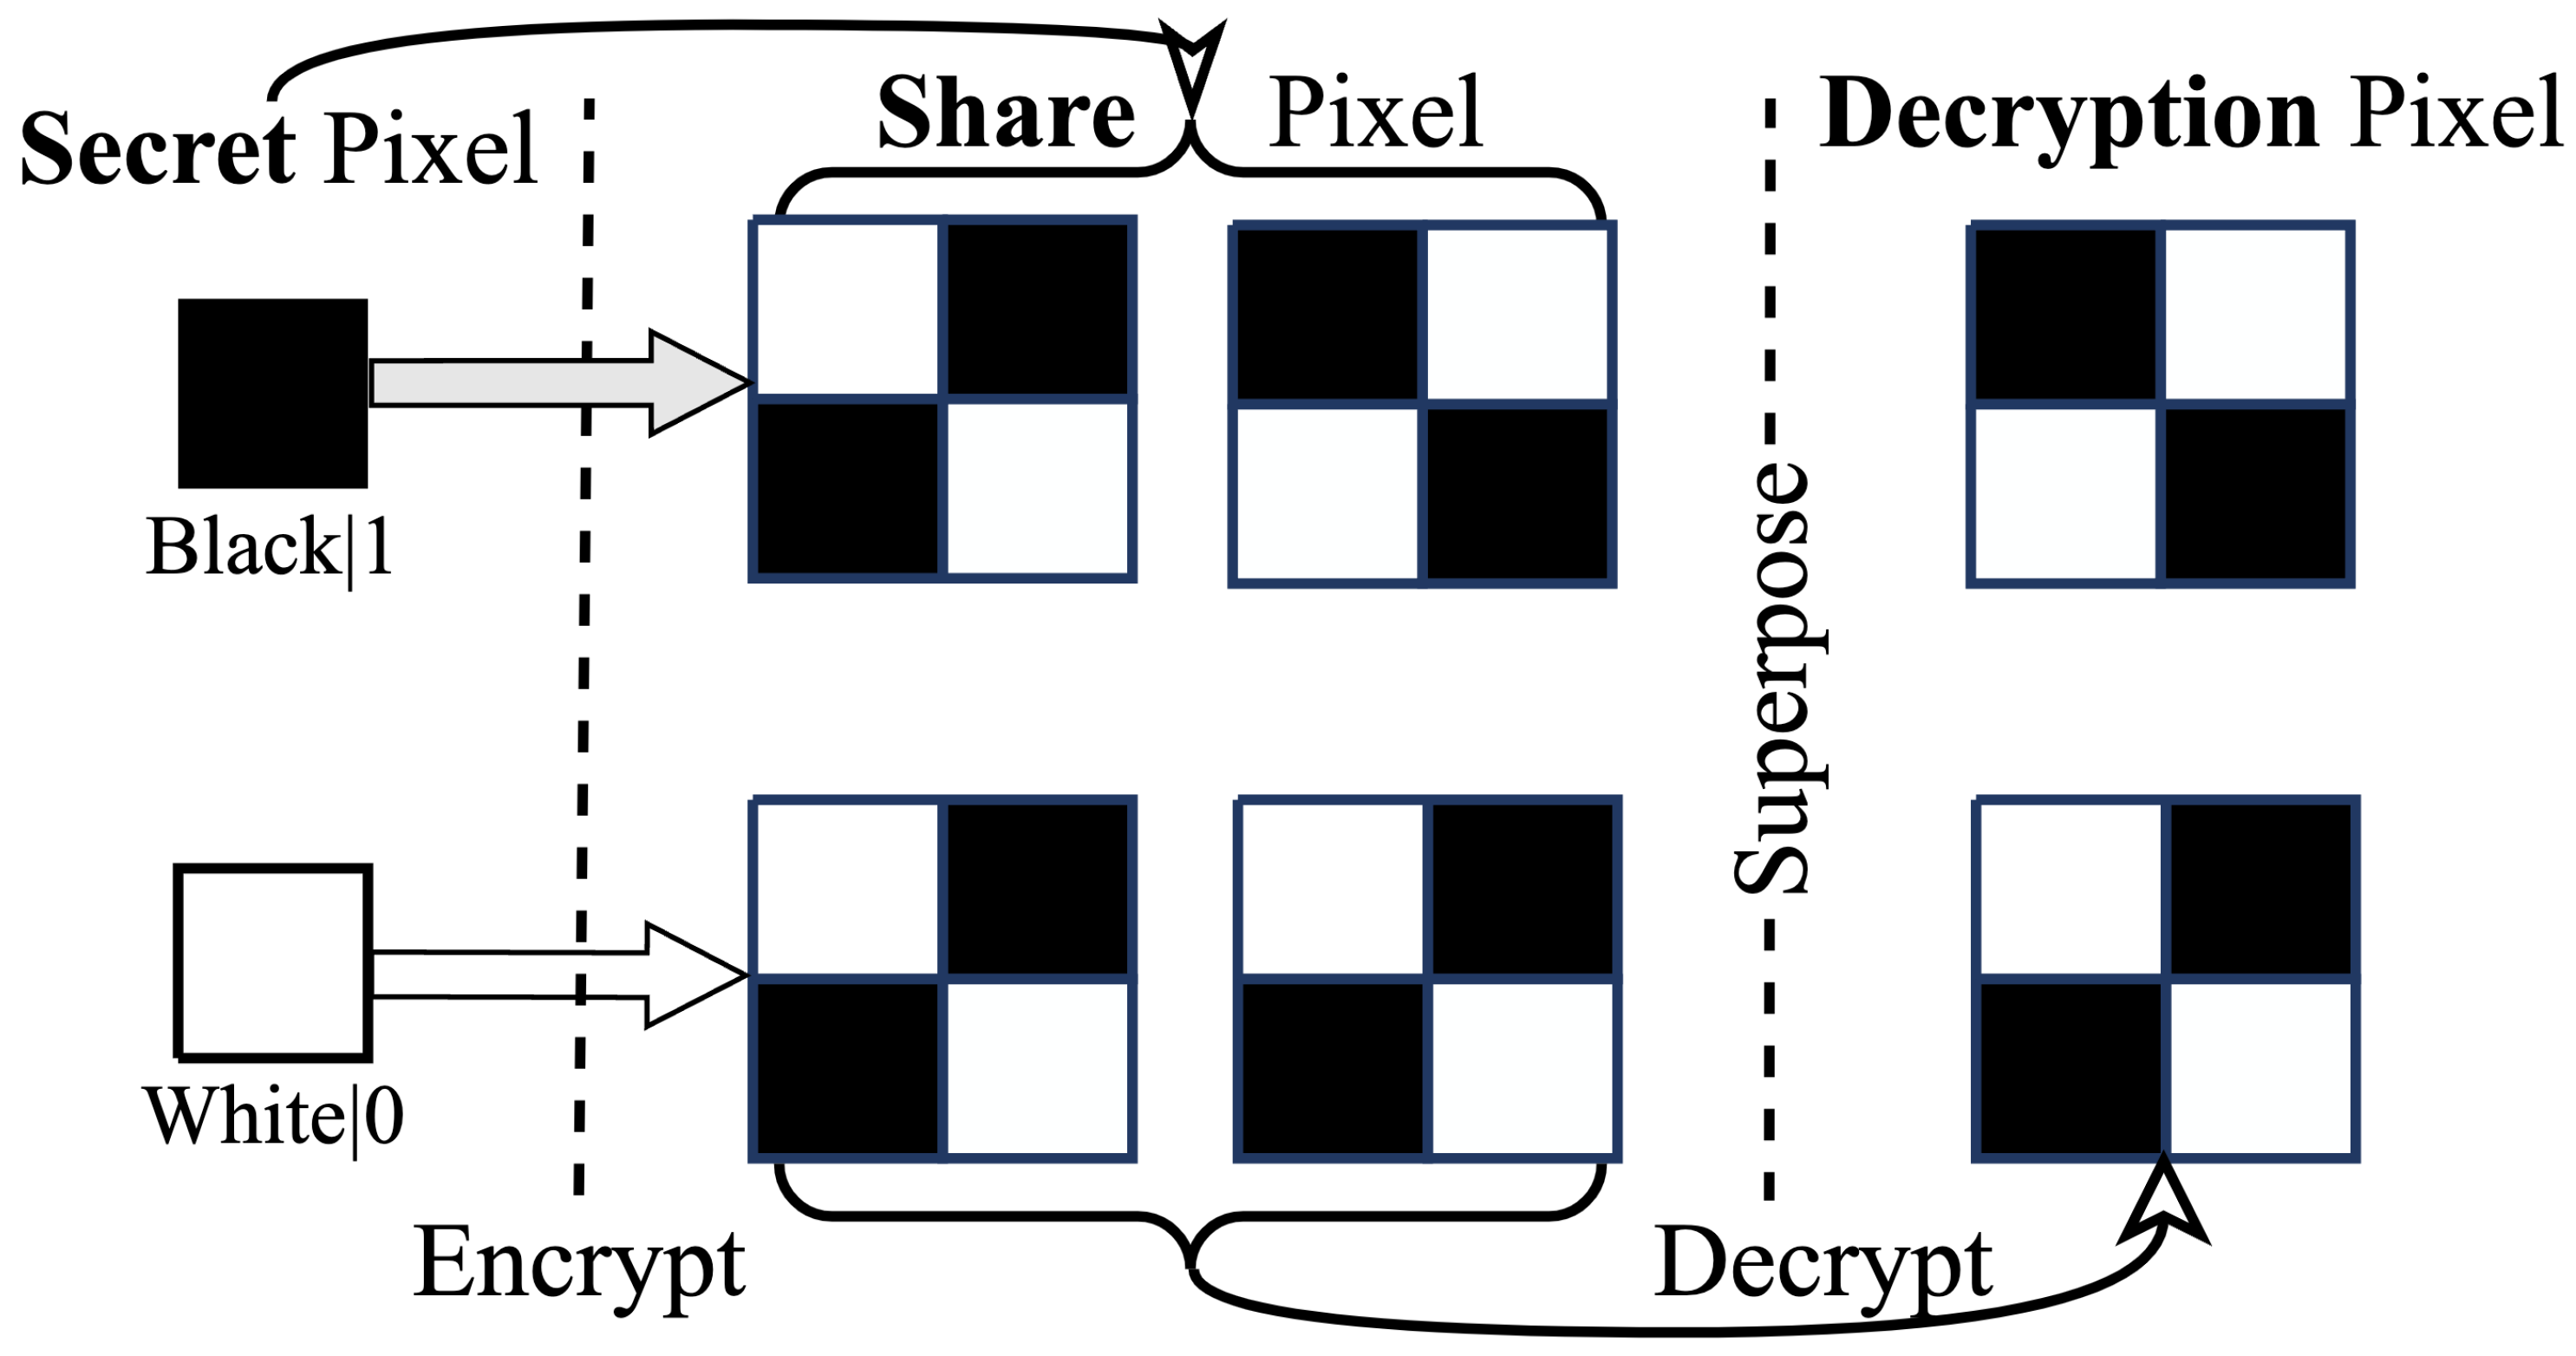
In this example, the binary image has been split into two component images. Each component image has a pair of pixels for every pixel in the original image. These pixel pairs are shaded black or white according to the following rule: if the original image pixel was black, the pixel pairs in the component images must be complementary; randomly shade one II, and the other II. When these complementary pairs are overlapped, they will appear dark gray. On the other hand, if the original image pixel was white, the pixel pairs in the component images must match: both II or both II. When these matching pairs are overlapped, they will appear light gray. So, when the two component images are superimposed, the original image appears. However, without the other component, a component image reveals no information about the original image; it is indistinguishable from a random pattern of II / II pairs. Moreover, if you have one component image, you can use the shading rules above to produce a counterfeit component image that combines with it to produce any image at all.
Sharing a secret with an arbitrary number of people, n, such that at least 2 of them are required to decode the secret is one form of the visual secret sharing scheme presented by Moni Naor and Adi Shamir in 1994. In this scheme we have a secret image which is encoded into n shares printed on transparencies. The shares appear random and contain no decipherable information about the underlying secret image, however if any 2 of the shares are stacked on top of one another the secret image becomes decipherable by the human eye. Every pixel from the secret image is encoded into multiple subpixels in each share image using a matrix to determine the color of the pixels. In the (2, n) case, a white pixel in the secret image is encoded using a matrix from the following set, where each row gives the subpixel pattern for one of the components: {all permutations of the columns of} : C 0 = [ 1 0 . . . 0 1 0 . . . 0 . . . 1 0 . . . 0 ] . {\displaystyle \mathbf {C_{0}=} {\begin{bmatrix}1&0&...&0\\1&0&...&0\\...\\1&0&...&0\end{bmatrix}}.} While a black pixel in the secret image is encoded using a matrix from the following set: {all permutations of the columns of} : C 1 = [ 1 0 .
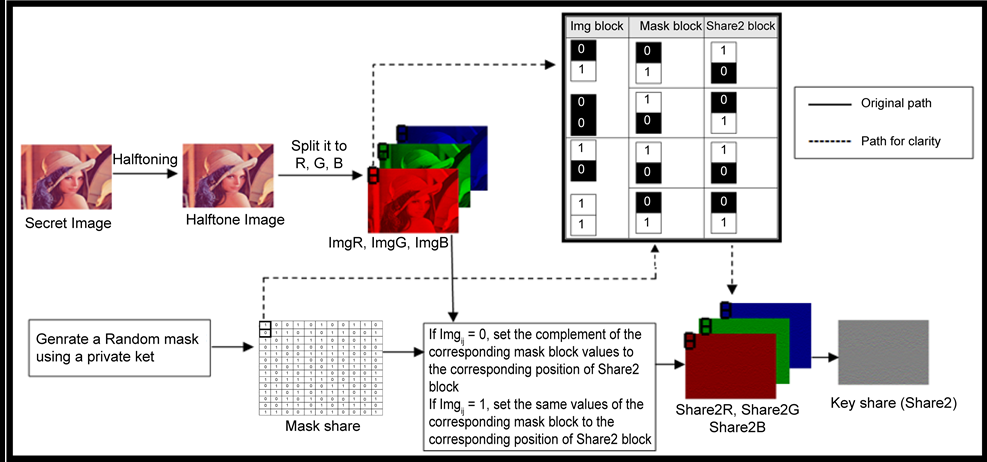
{\displaystyle \mathbf {C_{1}=} {\begin{bmatrix}1&0&...&0\\0&1&...&0\\...\\0&0&...&1\end{bmatrix}}.} Figure 1: A Secure Visual Cryptography Scheme Using Private Key with Invariant ...
For instance in the (2,2) sharing case (the secret is split into 2 shares and both shares are required to decode the secret) we use complementary matrices to share a black pixel and identical matrices to share a white pixel. Stacking the shares we have all the subpixels associated with the black pixel now black while 50% of the subpixels associated with the white pixel remain white.
2×2 subpixels can also encode a binary image in each component image. For example, each white pixel of each component image could be represented by two black subpixels, while each black pixel represented by three black subpixels. When overlaid, each white pixel of the secret image is represented by three black subpixels, while each black pixel is represented by all four subpixels black. Each corresponding pixel in the component images is randomly rotated to avoid orientation leaking information about the secret image.
CUDA (Compute Unified Device Architecture) is a proprietary parallel computing platform and application programming interface (API) developed by Nvidia that allows software to use certain types of graphics processing units (GPUs) for accelerated general-purpose processing, significantly broadening their utility in artificial intelligence, scientific and high-performance computing. CUDA was created in 2004 and was officially released in 2007. When introduced, the name was an acronym for Compute Unified Device Architecture, but Nvidia later dropped the initial meaning of the acronym and now rarely expands it. CUDA is both a software layer that manages data, giving direct access to the GPU and CPU as necessary, and a library of APIs that enable parallel computation. In addition to drivers and runtime kernels, the CUDA platform includes compilers, libraries and developer tools to help programmers. CUDA is written in the C programming language, but is designed to work with other programming languages including C++, Fortran, Python and Julia. This accessibility makes it easier for specialists in parallel programming to use GPU resources, in contrast to prior APIs like Direct3D and OpenGL, which require advanced skills in graphics programming. CUDA-powered GPUs support programming frameworks such as OpenMP, OpenACC and OpenCL.
The graphics processing unit (GPU) is a specialized processor. It addresses the demands of real-time high-resolution, compute-intensive tasks such as 3D graphics. By 2012, GPUs had evolved into highly parallel multi-core systems allowing efficient manipulation of large blocks of data. This design is more effective than general-purpose central processing unit (CPUs) for algorithms in situations where processing large blocks of data is done in parallel, such as: Figure 2: Integrating Visual Cryptography for Efficient and Secure Image Sharing ...
cryptographic hash functions machine learning molecular dynamics simulations physics engines The CUDA platform is accessible to software developers through CUDA-accelerated libraries, compiler directives such as OpenACC, and extensions to industry-standard programming languages including C, C++, Fortran and Python. C/C++ programmers can use 'CUDA C/C++', compiled to PTX with nvcc (Nvidia's LLVM-based C/C++ compiler) or by clang itself.
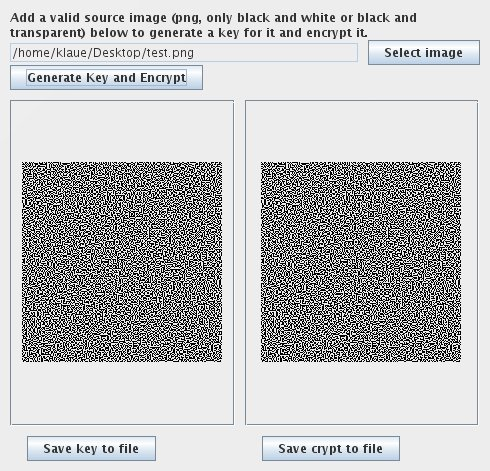
Fortran programmers can use 'CUDA Fortran', compiled with the PGI CUDA Fortran compiler from The Portland Group. Python programmers can use the cuPyNumeric library to accelerate applications on Nvidia GPUs. In addition to libraries, compiler directives, CUDA C/C++ and CUDA Fortran, the CUDA platform supports other computational interfaces, including the Khronos Group's OpenCL, Microsoft's DirectCompute, OpenGL Compute Shader and C++ AMP. Third party wrappers are also available for Python, Perl, Fortran, Java, Ruby, Lua, Common Lisp, Haskell, R, MATLAB, IDL, Julia, and native support in Mathematica. In the computer game industry, GPUs are used for graphics rendering, and for game physics calculations (physical effects such as debris, smoke, fire, fluids); examples include PhysX and Bullet. CUDA has also been used to accelerate non-graphical applications in computational biology, cryptography and other fields by an order of magnitude or more. CUDA provides both a low level API (CUDA Driver API, non single-source) and a higher level API (CUDA Runtime API, single-source). The initial CUDA SDK was made public on 15 February 2007, for Microsoft Windows and Linux. Mac OS X support was later added in version 2.0, which supersedes the beta released February 14, 2008. CUDA works with all Nvidia GPUs from the G8x series onwards, including GeForce, Quadro and the Tesla line. CUDA is compatible with most standard operating systems. CUDA 8.0 comes with the following libraries (for compilation & runtime, in alphabetical order): cuBLAS – CUDA Basic Linear Algebra Subroutines library CUDART – CUDA Runtime library cuFFT – CUDA Fast Fourier Transform library cuRAND – CUDA Random Number Generation library cuSOLVER – CUDA based collection of dense and sparse direct solvers cuSPARSE – CUDA Sparse Matrix library NPP – NVIDIA Performance Primitives library nvGRAPH – NVIDIA Graph Analytics library NVML – NVIDIA Management Library NVRTC – NVIDIA Runtime Compilation library for CUDA C++ CUDA 8.0 comes with these other software components: nView – NVIDIA nView Desktop Management Software NVWMI – NVIDIA Enterprise Management Toolkit GameWorks PhysX – is a multi-platform game physics engine CUDA 9.0–9.2 comes with these other components: Figure 3: Visual Cryptography | Applications | Double Helix CUTLASS 1.0 – custom linear algebra algorithms, NVIDIA Video Decoder was deprecated in CUDA 9.2; it is now available in NVIDIA Video Codec SDK CUDA 10 comes with these other components: 2. System Architecture & Core Working Principles nvJPEG – Hybrid (CPU and GPU) JPEG processing CUDA 11.0–11.8 comes with these other components: CUB is new one of more supported C++ libraries MIG multi instance GPU support nvJPEG2000 – JPEG 2000 encoder and decoder Scattered reads – code can read from arbitrary addresses in memory Unified virtual memory (CUDA 4.0 and above) Unified memory (CUDA 6.0 and above) Shared memory – CUDA exposes a fast shared memory region that can be shared among threads. This can be used as a user-managed cache, enabling higher bandwidth than is possible using texture lookups.
Faster downloads and readbacks to and from the GPU Full support for integer and bitwise operations, including integer texture lookups Below is an example given in Python that computes the product of two arrays on the GPU. The unofficial Python language bindings can be obtained from PyCUDA.
Additional Python bindings to simplify matrix multiplication operations can be found in the program pycublas. Note: CUDA SDK 10.2 is the last official release for macOS, as support will not be available for macOS in newer releases. CUDA compute capability by version with associated GPU semiconductors and GPU card models (separated by their various application areas): Note: Any missing lines or empty entries do reflect some lack of information on that exact item.
Note: Any missing lines or empty entries do reflect some lack of information on that exact item. oneAPI is an initiative based in open standards, created to support software development for multiple hardware architectures. The oneAPI libraries must implement open specifications that are discussed publicly by the Special Interest Groups, offering the possibility for any developer or organization to implement their own versions of oneAPI libraries. Originally made by Intel, other hardware adopters include Fujitsu and Huawei.
ROCm is an open source software stack for graphics processing unit (GPU) programming from Advanced Micro Devices (AMD). Telegram (also known as Telegram Messenger) is a Russian-Emirati cloud-based, cross-platform social media and instant messaging (IM) service. It launched for iOS on 14 August 2013 and Android on 20 October 2013. It allows users to exchange messages, share media and files, and hold private and group voice or video calls as well as public livestreams. It is available for Android, iOS, Windows, macOS, Linux, Wear OS, watchOS and web browsers. Telegram offers end-to-end encryption in voice and video calls, and optionally in private chats if both participants use a mobile device. Telegram also has social networking features, allowing users to post stories, create public groups with up to 200,000 members, and share one-way updates to unlimited audiences in so-called channels. Telegram was founded in 2013 by Pavel and Nikolai Durov. Its servers are distributed worldwide with several data centers, and its headquarters are in Dubai, United Arab Emirates. It was the most downloaded app worldwide in January 2021, with a billion downloads globally as of late August 2021. As of 2024, registration to Telegram requires either a phone number and a smartphone or one of a limited number of non-fungible tokens (NFTs) issued in 2022. As of March 2025, Telegram has more than 1 billion monthly active users, with India as the country with the most users.
On 3 August 2026, Telegram became unavailable for download from the iPhone and iPad App Store. The removal lasted several hours, during which people who had already installed Telegram could continue using it. Telegram subsequently announced that the application had returned to the store. An Apple spokesperson said that the company's review had found content violating its strict guidelines against child sexual abuse material (CSAM). Apple said that Telegram was restored on the same day after its developer removed the content and banned the user who had posted it. Apple did not publicly give further details about the original report, the location of the material on Telegram, or why the entire application was removed before Telegram was contacted. Telegram criticized Apple's decision to remove the entire application because of material posted by one user. Telegram spokesperson Remi Vaughn said Apple had been wrong to disrupt legitimate communication by the service's users over the actions of a single person. Responding to Apple's explanation on X, Telegram questioned whether Apple would apply the same standard equally to all other applications in the App Store. Telegram also linked to its safety overview, which states that the service removes many groups, channels, and pieces of content that violate its terms of service. Telegram said it had blocked more than 337,900 groups and channels associated with CSAM during 2026 by the time of the incident. That figure has not been independently audited. Epic Games chief executive Tim Sweeney questioned how large-scale communication services could operate if a single user's illegal post was sufficient for an entire application to be removed. He also questioned whether Apple would apply the same standard to its own iMessage service. On 4 August, Telegram founder Pavel Durov alleged that the prohibited material had been deliberately placed in a public group by a person engaged in what he called "takedown extortion". According to Durov, such attackers demand payment from the administrators of online communities and threaten to plant illegal material and report it to application-store operators if payment is refused.
Durov said the person responsible for the incident had inserted AI-modified illegal material by editing an older message in an active group. He said this made the material difficult for ordinary group members to notice and report. Durov also criticized Apple, saying it removed Telegram before contacting the company. He argued that the decision created a systemic risk for any application hosting user-generated content, because coordinated attackers could attempt to cause the removal of legitimate applications or online communities by planting prohibited material. Apple did not confirm Durov's account of the incident.
To use Telegram, a user must sign up with their phone number or an anonymous +888 number purchased from the Fragment blockchain platform. Changing the phone number in the app will automatically reassign the user's account to that number without exporting data or notifying their contacts. Phone numbers are hidden by default, with only a user's contacts able to see them. Sign-ups can be done only on an Android or iOS device. Messages users send and receive are tied to their numbers and custom usernames, not the device. Telegram content is synced between users' logged-in devices automatically through cloud storage, except for device-specific secret chats. By default, any account that is inactive for 6 months is deleted, but the period can be shortened or extended up to 18 months. Telegram allows groups, bots and channels with a verified social media or Wikipedia page to be verified, but not individual user accounts. Messages can contain formatted text, media, files up to 2 GB (4 GB with Premium), locations, and audio or video messages recorded in-app. Telegram messages in private chats can be edited for up to 48 hours; an "edited" icon indicates changes. Messages may also be deleted for both sides without a trace. Users may delete messages and whole chats for both themselves and other participants. Chats can be exported to preserve them via Telegram's Desktop client, but the saved data cannot be imported back into the user's account. Users can import chat history, including both messages and media, from WhatsApp, Line, and KakaoTalk due to data portability, making a new chat to hold the messages or adding them to an existing one. As users can be logged into many devices at once, starting to type a message on one of them will create a "cloud draft" that syncs with others, so that typing can be started on a phone and finished on a laptop, for example. Any message can be translated by opening the context menu. Premium users can translate a whole chat with one click. Users can hide the translate button for messages written in specific languages.
Reactions can be used to respond to a message with emoji. Premium users have access to more reaction choices and can leave more reactions per message. Reactions are always on in private chats and can be enabled by admins in groups and channels. Specific reactions can be allowed or excluded. Reaction emoji play an animation with special effects. Users can also send stickers, which can be static, animated or video. Sticker packs are made by Telegram designers as well as regular users and can be shared via links. They use the WebP or WebM format and do not require special software to create or upload. Some stickers feature full-screen effects that play out when first sent or when tapped. Users can schedule messages to send at a particular time or when their conversation partner comes online, as well as choose to send a message "without sound" without a notification. Messages from private chats can be forwarded, with an option to hide the original sender's identity or to hide captions from media messages. Forwarded messages also maintain reply formatting, able to show which messages in a thread are replying to others. Any user can also send a message to a special "Saved Messages" chat as a form of bookmarking them. The contents of the chat are only visible to the user.
3. Software Implementation, Frameworks & Protocols Chats can be sorted into folders to organize them with preset options like "Unread" and "Muted" or custom separations such as "Work" and "Family". Premium users have the ability to set any chat folder as the default screen in the app while regular users will always see the full chat list when first opening the app. Users have the option to start a one-on-one, end-to-end-encrypted "Secret Chat", which remains accessible only on the device on which it started and self-destructs upon logging out. Secret Chats restrict screenshotting by Android devices and warn when one is taken on an iOS device, while also hiding the chat contents from the final image. Secret Chats support perfect forward secrecy and switch encryption keys after a key has been used 100 times or a week has passed. Secret Chats are available only on Android, iOS, and macOS clients.
Both in Secret and regular chats, messages can self-destruct after they are read, disappearing for all parties after a period set by the user, ranging from one day to one year. In April 2021, the Payments 2.0 upgrade enabled bot payments within any chat, using third-party services such as Sberbank, Tranzoo, Payme, CLICK, LiqPay and ECOMMPAY to process the credit card information. Bots are also commonly used for businesses to communicate with customers as the bot APIs integrate with communication platforms so that Telegram messages can be sent and received in an omnichannelinbox. These platforms also enable businesses to add Telegram chat widget to their websites and gives them the option to automate conversations or let human agents reply. Examples of platforms providing Telegram bot integration include respond.io, Manychat and Trengo. In February 2018, Telegram launched its social login feature, Telegram Login. It features a website widget that can be embedded into websites, allowing users to sign into a third party website with their Telegram account. The gateway sends the user's Telegram name, username, and profile picture to the website owner, while the user's phone number remains hidden. The gateway is integrated with a bot, which is linked with the developer's specific website domain. In June 2021, an update introduced a new bot menu where users can browse and send commands while in a chat with a bot. In April 2022, bots gained support for customized interfaces and inline page loading. Interfaces can be adjusted to match the app's theme even if it changes while interacting with the bot. In October 2024, Telegram added increased messaging limits for bots, allowing bots to send up to 1000 messages per second to their users. Messages beyond the free limit of 30 per second are paid for using Telegram Stars. Telegram introduced affiliate programs in December 2024 that allow developers to create an affiliate program for their bot or mini app. Any Telegram user can join the affiliate program and be rewarded for referring others to the bot or mini app by receiving a commission from purchases made by the people they referred.
People can use their Telegram accounts to author articles on Telegraph – a minimalistic text editor and publisher. While articles on Telegraph can be published anonymously, tying them to one's account allows one to check their view count and edit them later. Telegraph natively supports Instant View, a feature which lets users read full articles in the chat with no load time and without opening an external browser. When an article is first published, the URL is generated automatically from its title. Non-Latin characters are transliterated, spaces are replaced with hyphens, and the date of publication is added to the address. For example, an article titled "Telegraph (blog platform)" published on 17 November would receive the URL /Telegraph-blog-platform-11-17. Text formatting options are also minimal: two levels of headings, single-level lists, bold, italics, quotes, and hyperlinks are supported. Authors could upload images and videos to the page, with a limit of 5 MB, however, it has been disabled since September 2024. When an author adds links to YouTube, Vimeo, or Twitter, the service allows you to embed their content directly in the article. In February 2018, Telegram launched their social login feature to its users, named Telegram Login. It features a website widget that could be embedded into websites, allowing users to sign into a third party website with their Telegram account. The gateway sends users' Telegram name, username, and profile picture to the website owner, while users' phone number remains hidden. The gateway is integrated with a bot, which is linked with the developer's specific website domain. In July 2018, Telegram introduced their online authorization and identity-management system, Telegram Passport, for platforms that require real-life identification. It asks users to upload their own official documents such as passport, identity card, driver license, etc. When an online service requires such identification documents and verification, it forwards the information to the platform with the user's permission. Telegram stated that it does not have access to the data, while the platform will share the information only with the authorized recipient. However, the service was criticised for being vulnerable to online brute-force attacks. In December 2020, Telegram launched a Bugs and Suggestions platform, where users can submit bug reports and suggestion cards for new features. Others can then vote and comment on the cards. In October 2024, Telegram launched a verification platform, called Telegram Gateway, allowing third-party services to authenticate their users by sending verification codes via Telegram.
For encrypted chats (branded as Secret Chats), Telegram uses a custom-built symmetric encryption scheme called MTProto. The protocol was developed by Nikolai Durov and other developers at Telegram and, as of version 2.0, is based on 256-bit symmetric AES encryption, 2048-bit RSA encryption and Diffie–Hellman key exchange. MTProto 1.0 was deprecated in favor of MTProto 2.0 in December 2017, which was deployed in Telegram clients as of v4.6. Version 2.0 was proven formally correct in December 2020 by a team from the University of Udine, Italy. The team reviewed the protocol after realizing that they could only find in-depth verifications done of version 1.0, where most criticisms were levied. They used ProVerif, a verifier based on the symbolic Dolev-Yao model. In the published paper, they "provide a fully automated proof of the soundness of MTProto 2.0’s protocols for authentication, normal chat, end-to-end encrypted chat, and re-keying mechanisms with respect to several security properties, including authentication, integrity, confidentiality and perfect forward secrecy...MTProto 2.0 is assumed to be a perfect authenticated encryption scheme (IND-CCA and INT-CTXT)." However, the team also stated that because all communication, including plaintext and ciphertext, passes through Telegram servers, and because the server is responsible for choosing Diffie–Hellman parameters, the "server should not be considered as trusted." They also concluded that a man-in-the-middle attack is possible if users fail to check the fingerprints of their shared keys. Finally, they qualified their conclusion with the caveat that "properties need to be formally proved in order to deem MTProto 2.0 definitely secure. This proof cannot be done in a symbolic model like ProVerif's, but it can be achieved in a computational model, using tools like CryptoVerif or EasyCrypt." In 2017, in an attempt to monetize Telegram without advertising, the company began the development of a blockchain platform dubbed either "The Open Network" or "Telegram Open Network" (TON) and its native cryptocurrency "Gram". The project was announced in mid-December 2017 and its 132-page technical paper became available in January 2018. The codebase behind TON was developed by Pavel Durov's brother Nikolai Durov, the core developer of Telegram's MTProto protocol. In January 2018, a 23-page white paper and a detailed 132-page technical paper for TON blockchain became available. Durov planned to power TON with the existing Telegram user base, and turn it into the largest blockchain and a platform for apps and services akin to a decentralized WeChat, Google Play, and App Store. Besides, the TON had the potential to become a decentralized alternative to Visa and MasterCard due to its ability to scale and support millions of transactions per second. In January and February 2018, the company ran a private sale of futures contracts for Grams, raising around $1.7 billion. No public offering took place. The development of TON took place in a completely isolated manner, and the release was postponed several times. The test network was launched in January 2019. The launch of the TON main network was scheduled for 31 October. On 30 October, the U.S. Securities and Exchange Commission obtained a temporary restrictive order to prevent the distribution of Grams to initial purchasers; the regulator considered the legal scheme employed by Telegram as an unregistered securities offering with initial buyers acting as underwriters. The judge hearing the Telegram v. SEC case, P. Kevin Castel, ultimately agreed with the SEC's argument and kept the restrictions on Gram distribution in force. The ban applied to non-U.S.-based purchasers as well, because Telegram could not prevent the re-sale of Grams to U.S. citizens on a secondary market, as the anonymity of users was one of the key features of TON. Following that, Durov announced the end of Telegram's active involvement with TON. On 26 June, the judge approved the settlement between Telegram and SEC. The company agreed to pay an $18.5 million penalty and return $1.22 billion to Gram purchasers. In March 2021, Telegram launched a bonds offering to cover the debt and fund further growth of the app.
In 2016, cryptography experts criticized how, unless modified, Telegram's default general security model stores all contacts, messages and media together with their decryption keys on its servers continuously and does not enable end-to-end encryption for messages. Durov has argued that this is because it helps to avoid third-party unsecured backups, and to allow users to access messages and files from any device. Criticisms were also aimed at Telegram's use of a custom-designed encryption protocol. In December 2020, a study titled "Automated Symbolic Verification of Telegram's MTProto 2.0" was published, confirming the security of the updated MTProto 2.0 and reviewing it while pointing out several theoretical vulnerabilities. The paper provides "fully automated proof of the soundness of MTProto 2.0's authentication, normal chat, end-to-end encrypted chat, and re-keying mechanisms with respect to several security properties, including authentication, integrity, confidentiality and perfect forward secrecy" and "proves the formal correctness of MTProto 2.0". This partially addresses the concern about the lack of scrutiny while confirming the formal security of the protocol's latest version. As of 2014, the desktop clients, excluding the macOS client, do not feature options for end-to-end encrypted messages. When the user assigns a local password in the desktop application, data is also locally encrypted. Telegram has defended the lack of ubiquitous end-to-end encryption by saying that online-backups that do not use client-side encryption are "the most secure solution currently possible". Security researcher Moxie Marlinspike, founder of the competing Signal messenger, and commenters on Hacker News criticized a 2013 contest to break its cryptography for being rigged or framed in Telegram's favor and said that Telegram's statements on the value of these contests as proof of the cryptography's quality are misleading.
This was because the cryptography contest could not be won even with completely broken algorithms such as MD2 (hash function) used as key stream extractor, and primitives such as the Dual EC DRBG that is known to be backdoored. Telegram has been blocked temporarily or permanently by some governments including Iran, China, Brazil, and Pakistan. The Russian government blocked Telegram for several years before lifting the ban in 2020. The company's founder has said he wants the app to have an anti-censorship tool for Iran and China similar to the app's role in fighting censorship in Russia. On 19 April 2024, Apple removed Telegram from the App Store in China. In September 2024, Ukraine banned the usage of Telegram by government officials, military personnel, and key workers on official devices, citing fears of Russian espionage.
The National Security and Defense Council of Ukraine enforced the restrictions following evidence reported to them by Kyrylo Budanov, showing Russia's ability to access messages and user data on the platform. Andriy Kovalenko, head of the security council's centre on countering disinformation, clarified that the ban was limited to official devices and did not extend to personal phones. In February 2026, Russia restricted Telegram, as officials said the platform failed to protect personal data and curb criminal content. Durov responded that Telegram remained committed to protecting freedom of speech and user privacy, and accused Russian authorities of directing users toward a state-backed platform, presumably Max. Over the summer of 2026, the share of active Russian-language channels posting links to Max doubled, reaching about one in fifty by August.
Telegram was the main subject surrounding the 2019 Puerto Rico riots that ended up in the resignation of then-Governor Ricardo Rosselló. Hundreds of pages of a group chat between Rosselló and members of his staff were leaked. The messages were considered vulgar, racist, and homophobic, with members of the chat discussing how they would use the media to target potential political opponents.
On 24 August 2024, Pavel Durov, who is both a French and UAE citizen, was arrested in France by French authorities. On 28 August he was charged with a wide array of crimes, including complicity in managing an online platform to enable illegal transactions; complicity in crimes such as enabling the distribution of child sexual abuse material; drug trafficking and fraud; and refusal to cooperate with law enforcement authorities. Durov posted bail of five million Euros, was barred from leaving France, and was released on condition he report to a French police station twice weekly. The case would be handled by a special magistrate with investigative and prosecutorial powers.
In June 2026, the Government of India temporarily blocked access to Telegram ahead of a re-conducted National Eligibility-cum-Entrance Test (NEET) examination, citing concerns that the platform had been used to distribute leaked examination papers. Telegram challenged the restriction before the Delhi High Court, arguing that the ban would affect millions of legitimate users while doing little to prevent examination fraud. Telegram CEO Pavel Durov criticized the decision, saying that the company had removed hundreds of channels associated with leaked examination materials and scams in India. At the time of the restriction, Telegram reported having more than 150 million active users in India. In October 2026, 404 Media reported that a letter included in US federal court records showed Telegram had provided US authorities with a user's account ID, phone number and IP address, along with the time of the account's last login. The letter, dated 4 September 2026, described the disclosure as voluntary and stated that Telegram was not conceding that it was subject to US jurisdiction or that the request had been properly served. The filing containing the letter was submitted to the court on 15 October 2026.
VisualCrypto is an open-source Python-based toolkit with a web interface designed for Visual Secret Sharing (VSS) , a cryptographic technique that splits a secret image into multiple shares. Each share appears as random noise and reveals no information on its own, but when combined, they reconstruct the original image. This repository primarily focuses on (2,2)-VSS schemes , where a secret image is split into two shares, both of which are required to reveal the hidden content.
If you’d like to implement a new Visual Secret Sharing algorithm or improve existing features, please check out our Contribution Guide . 4. Practical Deployment, Analysis & Case Studies VisualCrypto is an open-source Python-based toolkit with a web interface designed for Visual Secret Sharing (VSS) , a cryptographic technique that splits a secret image into multiple shares. Each share appears as random noise and reveals no information on its own, but when combined, they reconstruct the original image.
This repository primarily focuses on (2,2)-VSS schemes , where a secret image is split into two shares, both of which are required to reveal the hidden content. VisualCrypto was initially developed as part of a bachelor thesis that made use of Visual Cryptography (VC) and Random Grid (RG) schemes . During the research, several cryptographic schemes were implemented based on official academic papers, primarily to generate images for the thesis. Rather than letting all the code go unused, it was refined and expanded into a publicly available toolkit, making these techniques more accessible to a broader audience.
One of the key motivations behind VisualCrypto is the lack of a widely recognized and comprehensive library for Visual Secret Sharing schemes. While individual implementations exist, there is no unified software that allows users to easily apply, compare, and experiment with different VSS techniques. By making VisualCrypto open-source, the goal is to provide researchers, developers, and cryptography enthusiasts with a well-documented, reliable, and extensible platform for working with various schemes from scientific literature.
A Python-based Visual Cryptography System that securely converts an image into two encrypted visual shares. The original image can be reconstructed only by combining both shares. Visual Cryptography is a cryptographic technique that allows a secret image to be divided into multiple shares. In this project, the original image is converted into two pixel-based encrypted shares. Individually, the shares do not reveal the original image. The original image is reconstructed by manually selecting and combining both shares.
This guide provides instructions for setting up and using the VisualCrypto repository. Ensure the input image and output directories are correctly set in the script: image_path = '../images/test.png' output_path = '../images/output/' Run the script: python3 vc_grayscale_halftone.py The generated shares and reconstructed images will be stored in scripts/images/output/ .
The repository includes a Flask-based web application for a more user-friendly interaction. Before running the application, you need to set the PYTHONPATH environment variable. This ensures that Python can correctly locate the project directory and its dependencies. Without this step, launching the web application may result in ModuleNotFoundError or import issues.
To set the PYTHONPATH , use the following command, replacing
Visual cryptography is a fascinating field of cryptography that encodes an image into multiple shares. These shares are seemingly random images, but when stacked together, the original image is reconstructed. This tool is designed to teach and explore these concepts interactively. Visual Cryptography is a cryptographic technique that allows the encoding of a secret image into multiple shares. Each share appears as random noise, and no single share reveals any information about the original image. However, when all shares are stacked together, the original image is reconstructed without requiring any computer or mathematical computation. This method is useful for secure image sharing and authentication.
This project is licensed under the MIT License. See the LICENSE file in the repository for more details. An educational Python tool demonstrating visual cryptography techniques through interactive simulations. The internet has become an essential part of our lives, but with its rapid growth, protecting sensitive information has become increasingly important. Cryptography is the key to ensuring data security, but as the demand for secrecy and copyright protection rises, new techniques like Visual Cryptography have emerged.
In this article, we will explore how Visual Cryptography works, focusing on a methodology that combines data hiding and encryption techniques. We will dive into the algorithms behind the process, step-by-step, and discuss its applications, advantages, and potential limitations. By the end of this article, you'll have a clearer understanding of how this innovative cryptographic technique can be used to protect sensitive information.
The word cryptography is derived from two Greek words, which mean “secret writing” . Cryptography is the process of scrambling the original text by rearranging and substituting the original text, arranging it in a seemingly unreadable format for others. Cryptography is an effective way to protect the information that is transmitting through the network communication path.
Visual cryptography is a cryptographic technique which allows visual information (pictures, text, etc.) to be encrypted in such a way that decryption can be done just by sight reading. Visual cryptography, degree associated rising cryptography technology, uses the characteristics of human vision to rewrite encrypted photos. Visual cryptography provides secured digital transmission that is used just for merely the once. Numerous guidance like military maps and business identifications are transmitted over the internet. Whereas pattern secret photos, security problems ought to be compelled to be taken into thought as a result of hackers may utilize weak link over the communication network to steal info that they need.To touch upon the protection problems with secret photos, varied image secret sharing schemes are developed. anyone will use it for coding with none science information and any computations. Proposed Methodology: The proposed work is basically a framework design with two modules: 2. Visual Cryptography using Multi-layer Multi-shares method. An input image is accepted as a cover image for the secret image to be hidden.
Algorithm: Data Hiding Algorithm Input: Any image. Output: Other Image Hidden by Input Image. 2.1 Proposed Image Encryption Method Algorithm: Image Encryption. Input: Hided Image. Output: Encrypted Image. 2.2 Proposed Image Decryption Method Algorithm: Image Decryption. Input: Final Encrypted Image. Output: Decrypted Image.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Visual%20cryptography • https://en.wikipedia.org/wiki/CUDA • https://en.wikipedia.org/wiki/Telegram%20%28software%29 • https://github.com/coduri/VisualCrypto • https://coduri.github.io/VisualCrypto/ • https://github.com/aquibSC/Visual-Cryptography-System-Project • https://coduri.github.io/VisualCrypto/pages/getting_started/ • https://github.com/dipeshrayg/2026-05-13-visual-cryptography-tool • https://www.geeksforgeeks.org/computer-networks/visual-cryptography-introduction/ • https://github.com/yarstann/visualcrypto
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Visual Cryptography For Secret Image Sharing In Python.
[*] Metasploit Scan Running on Target Subnet for Visual Cryptography For Secret Image Sharing In Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |