Complete Technical Paper Content — Voip Call Forensic Analysis And Reconstruction Tool
Overview & System Context
Voip Call Forensic Analysis And Reconstruction Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9173 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Digital forensics (sometimes known as digital forensic science) is a branch of forensic science encompassing the recovery, investigation, examination, and analysis of material found in digital devices, often in relation to mobile devices and computer crime. The term "digital forensics" was originally used as a synonym for computer forensics but has been expanded to cover investigation of all devices capable of storing digital data. With roots in the personal computing revolution of the late 1970s and early 1980s, the discipline evolved in a haphazard manner during the 1990s, and it was not until the early 21st century that national policies emerged. Digital forensics investigations have a variety of applications. The most common is to support or refute a hypothesis before criminal or civil courts. Criminal cases involve the alleged breaking of laws that are defined by legislation and enforced by the police and prosecuted by the state, such as murder, theft, and assault against the person. Civil cases, on the other hand, deal with protecting the rights and property of individuals (often associated with family disputes), but may also be concerned with contractual disputes between commercial entities where a form of digital forensics referred to as electronic discovery (ediscovery) may be involved. Forensics may also feature in the private sector, such as during internal corporate investigations or intrusion investigations (a special probe into the nature and extent of an unauthorized network intrusion). The technical aspect of an investigation is divided into several sub-branches related to the type of digital devices involved: computer forensics, network forensics, forensic data analysis, and mobile device forensics. The typical forensic process encompasses the seizure, forensic imaging (acquisition), and analysis of digital media, followed with the production of a report of the collected evidence. As well as identifying direct evidence of a crime, digital forensics can be used to attribute evidence to specific suspects, confirm alibis or statements, determine intent, identify sources (for example, in copyright cases), or authenticate documents. Investigations are much broader in scope than other areas of forensic analysis (where the usual aim is to provide answers to a series of simpler questions), often involving complex time-lines or hypotheses.
Seizing, preserving, and analyzing evidence stored on a computer is the greatest forensic challenge facing law enforcement in the 1990s. Although most forensic tests, such as fingerprinting and DNA testing, are performed by specially trained experts the task of collecting and analyzing computer evidence is often assigned to patrol officers and detectives. Through cyberspace, enemies will target industry, academia, government, as well as the military in the air, land, maritime, and space domains. In much the same way that airpower transformed the battlefield of World War II, cyberspace has fractured the physical barriers that shield a nation from attacks on its commerce and communication. The field of digital forensics still faces unresolved issues. A 2009 paper, "Digital Forensic Research: The Good, the Bad and the Unaddressed" by Peterson and Shenoi, identified a bias towards Windows operating systems in digital forensics research. In 2010, Simson Garfinkel identified issues facing digital investigations in the future, including the increasing size of digital media, the wide availability of encryption to consumers, a growing variety of operating systems and file formats, an increasing number of individuals owning multiple devices, and legal limitations on investigators. The paper also identified continued training issues, as well as the prohibitively high cost of entering the field. Additionally, since 2024 there has been an integration of Artificial Intelligence (AI) and Machine Learning (ML) which has poised to amplify the efficiency as well as the precision behind digital forensics investigations During the 1980s, very few specialized digital forensic tools existed. Consequently, investigators often performed live analysis on media, examining computers from within the operating system using existing sysadmin tools to extract evidence. This practice carried the risk of modifying data on the disk, either inadvertently or otherwise, which led to claims of evidence tampering. A number of tools were created during the early 1990s to address the problem. The need for such software was first recognized in 1989 at the Federal Law Enforcement Training Center, resulting in the creation of IMDUMP (by Michael White) and in 1990, SafeBack (developed by Sydex). Similar software was developed in other countries; DIBS (a hardware and software solution) was released commercially in the UK in 1991, and Rob McKemmish released Fixed Disk Image free to Australian law enforcement. These tools allowed examiners to create an exact copy of a piece of digital media to work on, leaving the original disk intact for verification. By the end of the 1990s, as demand for digital evidence grew, more advanced commercial tools such as EnCase and FTK were developed, allowing analysts to examine copies of media without using any live forensics. More recently, a trend towards "live memory forensics" has grown, resulting in the availability of tools such as WindowsSCOPE. More recently, the same progression of tool development has occurred for mobile devices; initially investigators accessed data directly on the device, but soon specialist tools such as XRY or Radio Tactics Aceso appeared.
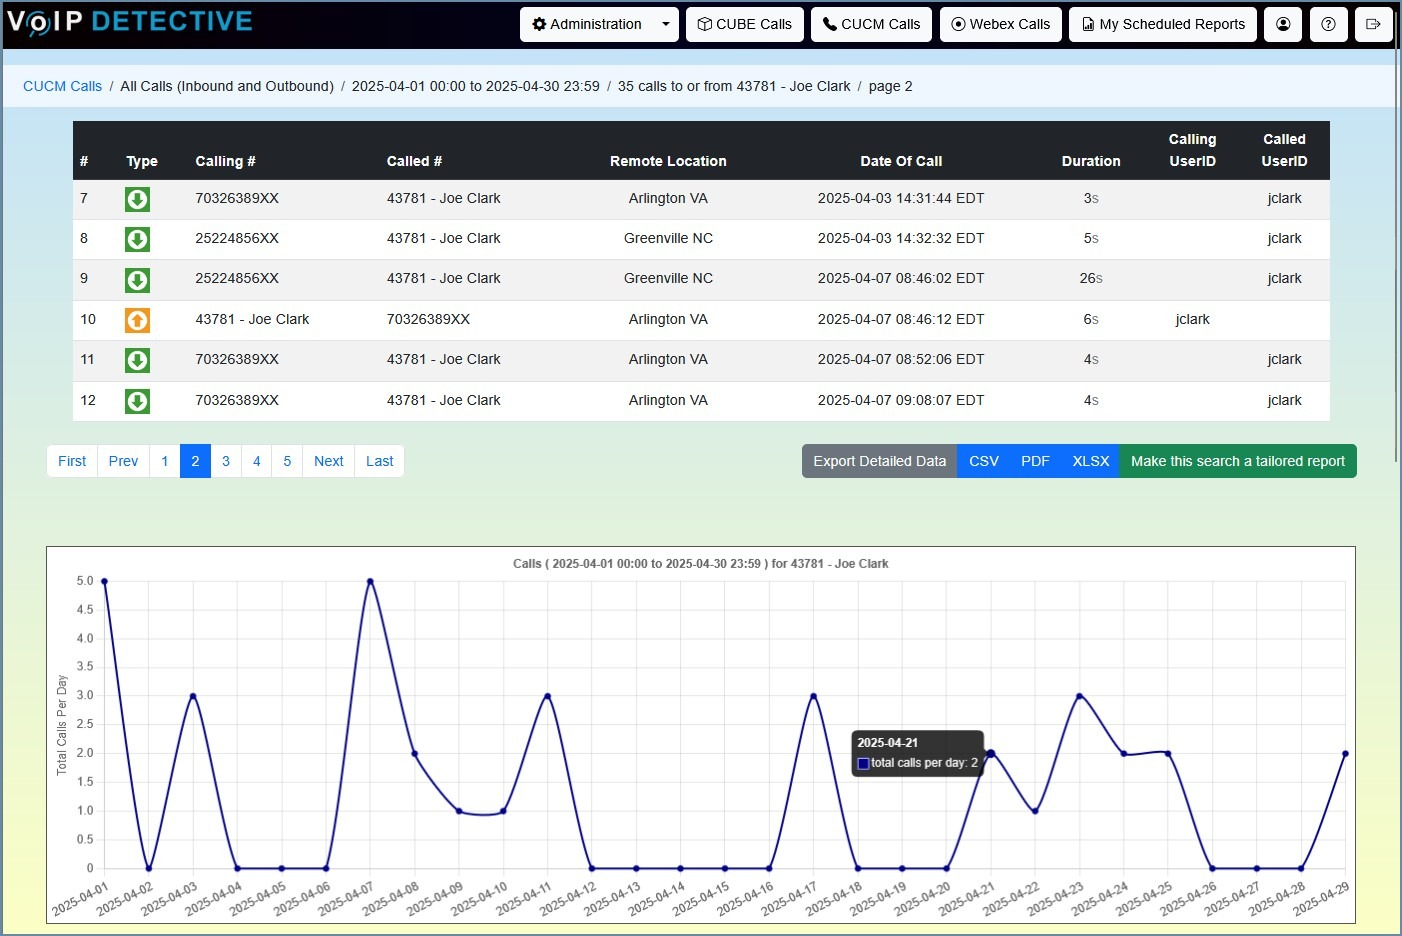
Police forces have begun implementing risk-based triage systems to manage the overwhelming demand for digital forensic services. Figure 1: CUCM Reporting - VoIP Detective acquisition or imaging of exhibits, analysis, and reporting. Acquisition does not normally involve capturing an image of the computer's volatile memory (RAM) unless this is done as part of an incident response investigation. Typically the task involves creating an exact sector level duplicate (or "forensic duplicate") of the media, often using a write blocking device to prevent modification of the original. However, the growth in size of storage media and developments such as cloud computing have led to more use of 'live' acquisitions whereby a 'logical' copy of the data is acquired rather than a complete image of the physical storage device. Both acquired image (or logical copy) and original media/data are hashed (using an algorithm such as SHA-1 or MD5) and the values compared to verify the copy is accurate. An alternative (and patented) approach (that has been dubbed 'hybrid forensics' or 'distributed forensics') combines digital forensics and ediscovery processes. This approach has been embodied in a commercial tool called ISEEK that was presented together with test results at a conference in 2017.
During the analysis phase an investigator recovers evidence material using a number of different methodologies and tools. In evidence related to the suspected crime." In 2006, forensics researcher Brian Carrier described an "intuitive procedure" in which obvious evidence is first identified and then "exhaustive searches are conducted to start filling in the holes." The actual process of analysis can vary between investigations, but common methodologies include conducting keyword searches across the digital media (within files as well as unallocated and slack space), recovering deleted files and extraction of registry information (for example to list user accounts, or attached USB devices). The evidence recovered is analyzed to reconstruct events or actions and to reach conclusions, work that can often be performed by less specialized staff. When an investigation is complete the data is presented, usually in the form of a written report, in lay persons' terms.
Digital forensics is commonly used in both criminal law and private investigation. Traditionally it has been associated with criminal law, where evidence is collected to support or oppose a hypothesis before the courts. As with other areas of forensics this is often a part of a wider investigation spanning a number of disciplines. In some cases, the collected evidence is used as a form of intelligence gathering, used for other purposes than court proceedings (for example to locate, identify or halt other crimes). As a result, intelligence gathering is sometimes held to a less strict forensic standard. In civil litigation or corporate matters, digital forensics forms part of the electronic discovery (or eDiscovery) process. Forensic procedures are similar to those used in criminal investigations, often with different legal requirements and limitations. Outside of the courts digital forensics can form a part of internal corporate investigations. A common example might be following unauthorized network intrusion. A specialist forensic examination, into the nature and extent of the attack, is performed as a damage limitation exercise, both to establish the extent of any intrusion and in an attempt to identify the attacker. Such attacks were commonly conducted over phone lines during the 1980s, but in the modern era are usually propagated over the Internet. The main focus of digital forensics investigations is to recover objective evidence of a criminal activity (termed actus reus in legal parlance).
However, the diverse range of data held in digital devices can help with other areas of inquiry. Attribution Meta data and other logs can be used to attribute actions to an individual. For example, personal documents on a computer drive might identify its owner. Alibis and statements Information provided by those involved can be cross checked with digital evidence. For example, during the investigation into the Soham murders the offender's alibi was disproved when mobile phone records of the person he claimed to be with showed she was out of town at the time. Intent As well as finding objective evidence of a crime being committed, investigations can also be used to prove the intent (known by the legal term mens rea). For example, the Internet history of convicted killer Neil Entwistle included references to a site discussing How to kill people. Evaluation of source File artifacts and meta-data can be used to identify the origin of a particular piece of data; for example, older versions of Microsoft Word embedded a Global Unique Identifier into files which identified the computer it had been created on. Proving whether a file was produced on the digital device being examined or obtained from elsewhere (e.g., the Internet) can be very important. Document authentication Related to "Evaluation of source," meta data associated with digital documents can be easily modified (for example, by changing the computer clock you can affect the creation date of a file). Document authentication relates to detecting and identifying falsification of such details.
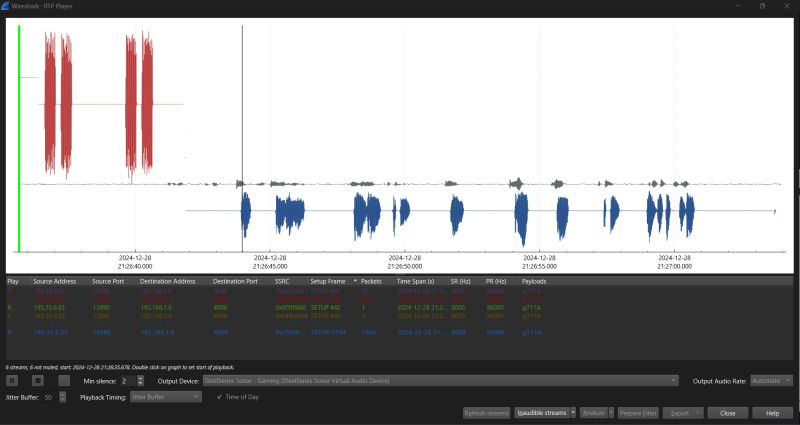
When used in a court of law, digital evidence falls under the same legal guidelines as other forms of evidence, as courts do not usually require more stringent guidelines. In the United States, the Federal Rules of Evidence are used to evaluate the admissibility of digital evidence. The United Kingdom PACE and Civil Evidence acts have similar guidelines and many other countries have their own laws. US federal laws restrict seizures to items with only obvious evidential value. This is acknowledged as not always being possible to establish with digital media prior to an examination. Laws dealing with digital evidence are concerned with two issues: Figure 2: IIProject Overview: Real-Time VoIP Traffic Interception, Analysis, and ...
2. System Architecture & Core Working Principles Integrity - it's ensuring that the act of seizing and acquiring digital media does not modify the evidence (either the original or the copy). Authenticity - refers to the ability to confirm the integrity of information; for example that the imaged media matches the original evidence. The ease with which digital media can be modified means that documenting the chain of custody from the crime scene, through analysis and, ultimately, to the court, (a form of audit trail) is important to establish the authenticity of evidence. Attorneys have argued that because digital evidence can theoretically be altered it undermines the reliability of the evidence. US judges are beginning to reject this theory, in the case US v. Bonallo the court ruled that "the fact that it is possible to alter data contained in a computer is plainly insufficient to establish untrustworthiness." In the United Kingdom, guidelines such as those issued by ACPO are followed to help document the authenticity and integrity of evidence. Digital investigators, particularly in criminal investigations, have to ensure that conclusions are based upon factual evidence and their own expert knowledge. In the US, for example, Federal Rules of Evidence state that a qualified expert may testify "in the form of an opinion or otherwise" so long as: (1) the testimony is based upon sufficient facts or data, (2) the testimony is the product of reliable principles and methods, and (3) the witness has applied the principles and methods reliably to the facts of the case. The sub-branches of digital forensics may each have their own specific guidelines for the conduct of investigations and the handling of evidence. For example, mobile phones may be required to be placed in a Faraday shield during seizure or acquisition to prevent further radio traffic to the device. In the UK forensic examination of computers in criminal matters is subject to ACPO guidelines. There are also international approaches to providing guidance on how to handle electronic evidence. The "Electronic Evidence Guide" by the Council of Europe offers a framework for law enforcement and judicial authorities in countries who seek to set up or enhance their own guidelines for the identification and handling of electronic evidence.
The goal of computer forensics is to explain the current state of a digital artifact; such as a computer system, storage medium or electronic document. The discipline usually covers computers, embedded systems (digital devices with rudimentary computing power and onboard memory) and static memory (such as USB pen drives). Computer forensics can deal with a broad range of information; from logs (such as internet history) through to the actual files on the drive. In 2007, prosecutors used a spreadsheet recovered from the computer of Joseph Edward Duncan to show premeditation and secure the death penalty. Sharon Lopatka's killer was identified in 2006 after email messages from him detailing torture and death fantasies were found on her computer.
Mobile device forensics is a sub-branch of digital forensics relating to recovery of digital evidence or data from a mobile device. It differs from Computer forensics in that a mobile device will have an inbuilt communication system (e.g. GSM) and, usually, proprietary storage mechanisms. Investigations usually focus on simple data such as call data and communications (SMS/Email) rather than in-depth recovery of deleted data. SMS data from a mobile device investigation helped to exonerate Patrick Lumumba in the murder of Meredith Kercher. Mobile devices are also useful for providing location information; either from inbuilt GPS/location tracking or via cell site logs, which track the devices within their range. Such information was used to track down the kidnappers of Thomas Onofri in 2006.
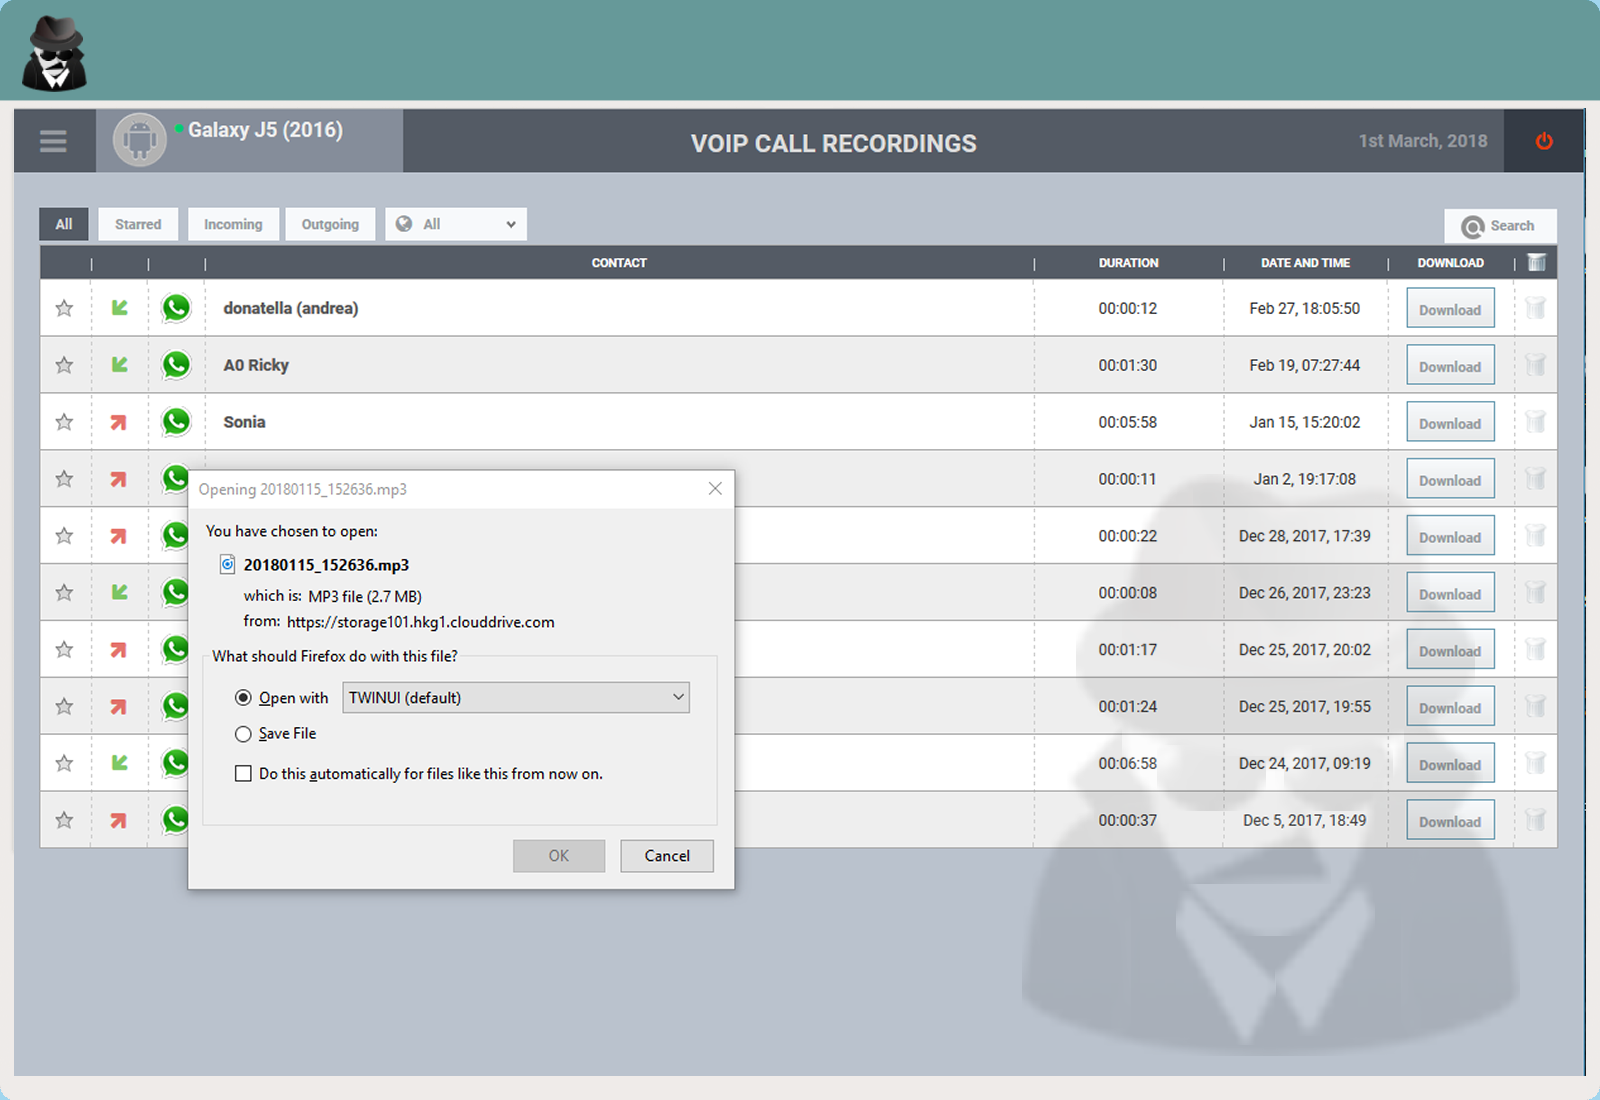
Figure 3: Spy4M Dashboard demo - Mobile Spy Software - VOIP Recordings Network forensics is concerned with the monitoring and analysis of computer network traffic, both local and WAN/internet, for the purposes of information gathering, evidence collection, or intrusion detection. Traffic is usually intercepted at the packet level, and either stored for later analysis or filtered in real-time. Unlike other areas of digital forensics network data is often volatile and rarely logged, making the discipline often reactionary. In 2000, the FBI lured computer hackers Aleksey Ivanov and Gorshkov to the United States for a fake job interview. By monitoring network traffic from the pair's computers, the FBI identified passwords allowing them to collect evidence directly from Russian-based computers.
Forensic Data Analysis is a branch of digital forensics. It examines structured data with the aim to discover and analyze patterns of fraudulent activities resulting from financial crime. Database forensics is a branch of digital forensics relating to the forensic study of databases and their metadata. Investigations use database contents, log files and in-RAM data to build a timeline or recover relevant information.
IoT forensics is a branch of Digital forensics that has the goal of identifying and extracting digital information from devices belonging to the Internet of things field, to be used for forensics investigations as potential source of evidence. 3. Software Implementation, Frameworks & Protocols Computer and network surveillance is the monitoring of computer activity and data stored locally on a computer or data being transferred over computer networks such as the Internet. This monitoring is often carried out covertly and may be completed by governments, corporations, criminal organizations, or individuals. It may or may not be legal and may or may not require authorization from a court or other independent government agencies. Computer and network surveillance programs are widespread today, and almost all Internet traffic can be monitored. Surveillance allows governments and other agencies to maintain social control, recognize and monitor threats or any suspicious or abnormal activity, and prevent and investigate criminal activities. With the advent of programs such as the Total Information Awareness program, technologies such as high-speed surveillance computers and biometrics software, and laws such as the Communications Assistance For Law Enforcement Act, governments now possess an unprecedented ability to monitor the activities of citizens. Many civil rights and privacy groups, such as Reporters Without Borders, the Electronic Frontier Foundation, and the American Civil Liberties Union, have expressed concern that increasing surveillance of citizens will result in a mass surveillance society, with limited political and/or personal freedoms. Such fear has led to numerous lawsuits such as Hepting v. AT&T. The hacktivist group Anonymous has hacked into government websites in protest of what it considers "draconian surveillance".
The vast majority of computer surveillance involves the monitoring of personal data and traffic on the Internet. For example, in the United States, the Communications Assistance For Law Enforcement Act mandates that all phone calls and broadband internet traffic (emails, web traffic, instant messaging, etc.) be available for unimpeded, real-time monitoring by Federal law enforcement agencies. Packet capture (also known as "packet sniffing") is the monitoring of data traffic on a network. Data sent between computers over the Internet or between any networks takes the form of small chunks called packets, which are routed to their destination and assembled back into a complete message. A packet capture appliance intercepts these packets, so that they may be examined and analyzed. Computer technology is needed to perform traffic analysis and sift through intercepted data to look for important/useful information. Under the Communications Assistance For Law Enforcement Act, all U.S. telecommunications providers are required to install such packet capture technology so that Federal law enforcement and intelligence agencies are able to intercept all of their customers' broadband Internet and voice over Internet protocol (VoIP) traffic. These technologies can be used both by the intelligence and for illegal activities. There is far too much data gathered by these packet sniffers for human investigators to manually search through. Thus, automated Internet surveillance computers sift through the vast amount of intercepted Internet traffic, filtering out, and reporting to investigators those bits of information which are "interesting", for example, the use of certain words or phrases, visiting certain types of web sites, or communicating via email or chat with a certain individual or group. Billions of dollars per year are spent by agencies such as the Information Awareness Office, NSA, and the FBI, for the development, purchase, implementation, and operation of systems which intercept and analyze this data, extracting only the information that is useful to law enforcement and intelligence agencies. Similar systems are now used by Iranian Security dept. to more easily distinguish between peaceful citizens and terrorists. All of the technology has been allegedly installed by German Siemens and Finnish Nokia. The Internet's rapid development has become a primary form of communication. More people are potentially subject to Internet surveillance. There are advantages and disadvantages to network monitoring. For instance, systems described as "Web 2.0" have greatly impacted modern society. Tim O' Reilly, who first explained the concept of "Web 2.0", stated that Web 2.0 provides communication platforms that are "user generated", with self-produced content, motivating more people to communicate with friends online. However, Internet surveillance also has a disadvantage. One researcher from Uppsala University said "Web 2.0 surveillance is directed at large user groups who help to hegemonically produce and reproduce surveillance by providing user-generated (self-produced) content. We can characterize Web 2.0 surveillance as mass self-surveillance". Surveillance companies monitor people while they are focused on work or entertainment. Yet, employers themselves also monitor their employees. They do so in order to protect the company's assets and to control public communications but most importantly, to make sure that their employees are actively working and being productive. This can emotionally affect people; this is because it can cause emotions like jealousy. A research group states "...we set out to test the prediction that feelings of jealousy lead to 'creeping' on a partner through Facebook, and that women are particularly likely to engage in partner monitoring in response to jealousy". The study shows that women can become jealous of other people when they are in an online group. Virtual assistants have become socially integrated into many people's lives. Currently, virtual assistants such as Amazon's Alexa or Apple's Siri cannot call 911 or local services. They are constantly listening for command and recording parts of conversations that will help improve algorithms. If the law enforcement is able to be called using a virtual assistant, the law enforcement would then be able to have access to all the information saved for the device.
The device is connected to the home's internet, because of this law enforcement would be the exact location of the individual calling for law enforcement. While the virtual assistance devices are popular, many debates the lack of privacy. The devices are listening to every conversation the owner is having. Even if the owner is not talking to a virtual assistant, the device is still listening to the conversation in hopes that the owner will need assistance, as well as to gather data.
Corporate surveillance of computer activity is very common. The data collected is most often used for marketing purposes or sold to other corporations, but is also regularly shared with government agencies. It can be used as a form of business intelligence, which enables the corporation to better tailor their products and/or services to be desirable by their customers. The data can also be sold to other corporations so that they can use it for the aforementioned purpose, or it can be used for direct marketing purposes, such as targeted advertisements, where ads are targeted to the user of the search engine by analyzing their search history and emails (if they use free webmail services), which are kept in a database. Such type of surveillance is also used to establish business purposes of monitoring, which may include the following: Preventing misuse of resources. Companies can discourage unproductive personal activities such as online shopping or web surfing on company time. Monitoring employee performance is one way to reduce unnecessary network traffic and reduce the consumption of network bandwidth. Promoting adherence to policies. Online surveillance is one means of verifying employee observance of company networking policies. Preventing lawsuits. Firms can be held liable for discrimination or employee harassment in the workplace. Organizations can also be involved in infringement suits through employees that distribute copyrighted material over corporate networks. Safeguarding records. Federal legislation requires organizations to protect personal information. Monitoring can determine the extent of compliance with company policies and programs overseeing information security. Monitoring may also deter unlawful appropriation of personal information, and potential spam or viruses.
Safeguarding company assets. The protection of intellectual property, trade secrets, and business strategies is a major concern. The ease of information transmission and storage makes it imperative to monitor employee actions as part of a broader policy. The second component of prevention is determining the ownership of technology resources. The ownership of the firm's networks, servers, computers, files, and e-mail should be explicitly stated. There should be a distinction between an employee's personal electronic devices, which should be limited and proscribed, and those owned by the firm. For instance, Google Search stores identifying information for each web search. An IP address and the search phrase used are stored in a database for up to 18 months. Google also scans the content of emails of users of its Gmail webmail service in order to create targeted advertising based on what people are talking about in their personal email correspondences. Google is, by far, the largest Internet advertising agency—millions of sites place Google's advertising banners and links on their websites in order to earn money from visitors who click on the ads. Each page containing Google advertisements adds, reads, and modifies "cookies" on each visitor's computer. These cookies track the user across all of these sites and gather information about their web surfing habits, keeping track of which sites they visit, and what they do when they are on these sites. This information, along with the information from their email accounts, and search engine histories, is stored by Google to use to build a profile of the user to deliver better-targeted advertising. The United States government often gains access to these databases, either by producing a warrant for it, or by simply asking. The Department of Homeland Security has openly stated that it uses data collected from consumer credit and direct marketing agencies for augmenting the profiles of individuals that it is monitoring.
In addition to monitoring information sent over a computer network, there is also a way to examine data stored on a computer's hard drive, and to monitor the activities of a person using the computer. A surveillance program installed on a computer can search the contents of the hard drive for suspicious data, can monitor computer use, collect passwords, and/or report back activities in real-time to its operator through the Internet connection. A keylogger is an example of this type of program. Normal keylogging programs store their data on the local hard drive, but some are programmed to automatically transmit data over the network to a remote computer or Web server. There are multiple ways of installing such software. The most common is remote installation, using a backdoor created by a computer virus or trojan. This tactic has the advantage of potentially subjecting multiple computers to surveillance. Viruses often spread to thousands or millions of computers, and leave "backdoors" which are accessible over a network connection, and enable an intruder to remotely install software and execute commands. These viruses and trojans are sometimes developed by government agencies, such as CIPAV and Magic Lantern. More often, however, viruses created by other people or spyware installed by marketing agencies can be used to gain access through the security breaches that they create. Another method is "cracking" into the computer to gain access over a network. An attacker can then install surveillance software remotely. Servers and computers with permanent broadband connections are most vulnerable to this type of attack. Another source of security cracking is employees giving out information or users using brute force tactics to guess their password. One can also physically place surveillance software on a computer by gaining entry to the place where the computer is stored and install it from a compact disc, floppy disk, or thumbdrive. This method shares a disadvantage with hardware devices in that it requires physical access to the computer.
One well-known worm that uses this method of spreading itself is Stuxnet. The purpose of the SSNA algorithms program is to extend techniques of social network analysis to assist with distinguishing potential terrorist cells from legitimate groups of people ... In order to be successful SSNA will require information on the social interactions of the majority of people around the globe. Since the Defense Department cannot easily distinguish between peaceful citizens and terrorists, it will be necessary for them to gather data on innocent civilians as well as on potential terrorists.
Surveillance and censorship are different. Surveillance can be performed without censorship, but it is harder to engage in censorship without some forms of surveillance. And even when surveillance does not lead directly to censorship, the widespread knowledge or belief that a person, their computer, or their use of the Internet is under surveillance can lead to self-censorship. In March 2013 Reporters Without Borders issued a Special report on Internet surveillance that examines the use of technology that monitors online activity and intercepts electronic communication in order to arrest journalists, citizen-journalists, and dissidents. The report includes a list of "State Enemies of the Internet", Bahrain, China, Iran, Syria, and Vietnam, countries whose governments are involved in active, intrusive surveillance of news providers, resulting in grave violations of freedom of information and human rights. Computer and network surveillance is on the increase in these countries. The report also includes a second list of "Corporate Enemies of the Internet", including Amesys (France), Blue Coat Systems (U.S.), Gamma (UK and Germany), Hacking Team (Italy), and Trovicor (Germany), companies that sell products that are liable to be used by governments to violate human rights and freedom of information. Neither list is exhaustive and they are likely to be expanded in the future. Protection of sources is no longer just a matter of journalistic ethics. Journalists should equip themselves with a "digital survival kit" if they are exchanging sensitive information online, storing it on a computer hard-drive or mobile phone. Individuals associated with high-profile rights organizations, dissident groups, protest groups, or reform groups are urged to take extra precautions to protect their online identities.
Anonymizer, a software system that attempts to make network activity untraceable Computer surveillance in the workplace Cyber spying Datacasting, a means of broadcasting files and Web pages using radio waves, allowing receivers near total immunity from traditional network surveillance techniques. Differential privacy, a method to maximize the accuracy of queries from statistical databases while minimizing the chances of violating the privacy of individuals. ECHELON, a signals intelligence (SIGINT) collection and analysis network operated on behalf of Australia, Canada, New Zealand, the United Kingdom, and the United States, also known as AUSCANNZUKUS and Five Eyes GhostNet, a large-scale cyber spying operation discovered in March 2009 List of government surveillance projects Internet censorship and surveillance by country Mass surveillance China's Golden Shield Project Mass surveillance in Australia Mass surveillance in China Mass surveillance in East Germany Mass surveillance in India Mass surveillance in North Korea Mass surveillance in the United Kingdom Mass surveillance in the United States Surveillance 4. Practical Deployment, Analysis & Case Studies Surveillance by the United States government: 2013 mass surveillance disclosures, reports about NSA and its international partners' mass surveillance of foreign nationals and U.S. citizens Bullrun (code name), a highly classified NSA program to preserve its ability to eavesdrop on encrypted communications by influencing and weakening encryption standards, by obtaining master encryption keys, and by gaining access to data before or after it is encrypted either by agreement, by force of law, or by computer network exploitation (hacking) Carnivore, a U.S. Federal Bureau of Investigation system to monitor email and electronic communications COINTELPRO, a series of covert, and at times illegal, projects conducted by the FBI aimed at U.S. domestic political organizations Communications Assistance For Law Enforcement Act Computer and Internet Protocol Address Verifier (CIPAV), a data gathering tool used by the U.S. Federal Bureau of Investigation (FBI) Dropmire, a secret surveillance program by the NSA aimed at surveillance of foreign embassies and diplomatic staff, including those of NATO allies Magic Lantern, keystroke logging software developed by the U.S. Federal Bureau of Investigation Mass surveillance in the United States NSA call database, a database containing metadata for hundreds of billions of telephone calls made in the U.S. NSA warrantless surveillance (2001–07) NSA whistleblowers: William Binney, Thomas Andrews Drake, Mark Klein, Edward Snowden, Thomas Tamm, Russ Tice Spying on United Nations leaders by United States diplomats Stellar Wind (code name), code name for information collected under the President's Surveillance Program Tailored Access Operations, NSA's hacking program Terrorist Surveillance Program, an NSA electronic surveillance program Total Information Awareness, a project of the Defense Advanced Research Projects Agency (DARPA) TEMPEST, codename for studies of unintentional intelligence-bearing signals which, if intercepted and analyzed, may disclose the information transmitted, received, handled, or otherwise processed by any information-processing equipment The practice of mass surveillance in the United States, which entails the pervasive surveillance of virtually all Americans' communications, dates back to wartime monitoring and censorship of international communications from, to, or which passed through the United States. After the First and Second World Wars, mass surveillance continued throughout the Cold War period, via programs such as the Black Chamber and Project SHAMROCK. President Harry S. Truman established the National Security Agency (NSA) in 1952 for the purposes of collecting, processing, and monitoring intelligence data. The formation of the international UKUSA surveillance agreement of 1946 evolved into the ECHELON collaboration by 1955 of five English-speaking nations, also known as the Five Eyes, and focused on interception of electronic communications, with substantial increases in domestic surveillance capabilities. The formation and growth of federal law-enforcement and intelligence agencies such as the FBI, CIA, and NSA institutionalized surveillance used to also silence political dissent, as evidenced by COINTELPRO projects which targeted various organizations and individuals. During the Civil Rights Movement era, many individuals put under surveillance orders were first labelled as integrationists, then deemed subversive, and sometimes suspected to be supportive of the communist model of the United States' rival at the time, the Soviet Union. Other targeted individuals and groups included Native American activists, African American and Chicano liberation movement activists, and anti-war protesters. When the Citizens' Commission to Investigate the FBI published stolen FBI documents revealing abuse of intelligence programs in 1971, Senator Frank Church began an investigation into the programs that become known as the Church Committee. The committee sought to investigate intelligence abuses throughout the 1970s.
Following a report provided by the committee outlining egregious abuse, in 1976 Congress established the Senate Select Committee on Intelligence. It would later be joined by the Foreign Intelligence Surveillance Court in 1978. The institutions worked to limit the power of the agencies, ensuring that surveillance activities remained within the rule of law. Following the attacks of September 11, 2001, domestic and international mass surveillance capabilities grew immensely. Congress passed the Patriot Act to strengthen security and intelligence efforts. The act granted the President broad powers on the war against terror, including the power to bypass the FISA Court for surveillance orders in cases of national security. Additionally, mass surveillance activities were conducted alongside various other surveillance programs under the head of President's Surveillance Program. Contemporary mass surveillance relies upon annual presidential executive orders declaring a continued State of National Emergency, first signed by George W. Bush on September 14, 2001 and then continued on an annual basis during the presidencies of Barack Obama, Joe Biden, and Donald Trump. The FISA Amendments Act of 2008 authorized the PRISM surveillance program. Political commentators have criticized these acts, orders, and resulting database network of fusion centers as forming an American police state that institutionalized the illegal COINTELPRO tactics used to assassinate dissenters and leaders from the 1950s onwards. Under pressure from the public, the warrantless wiretapping program was allegedly ended in January 2007. Additional surveillance agencies, such as the DHS and the position of Director of National Intelligence, have greatly escalated mass surveillance since 2001. A series of media reports in 2013 revealed more recent programs and techniques employed by the US intelligence community. Many details about the surveillance activities conducted in the United States were revealed in the disclosure by Edward Snowden in June 2013. Regarded as one of the biggest media leaks in the United States, it presented extensive details about the surveillance programs of the NSA, that involved interception of Internet data and telephonic calls from over a billion users, across various countries. Advances in computer and information technology allow the creation of huge national databases that facilitate mass surveillance in the United States by DHS managed fusion centers, the CIA's Terrorist Threat Integration Center (TTIC) program, and the FBI's Terrorist Screening Database (TSDB).
First Lady Eleanor Roosevelt – A vocal critic of Hoover who likened the FBI to an 'American Gestapo' for its Index lists. Roosevelt also spoke out against anti-Japanese prejudice during the second world war, and was later a delegate to the United Nations and instrumental in creating the Universal Declaration of Human Rights. The 3,000-page FBI dossier on Eleanor Roosevelt reveals Hoover's close monitoring of her activities and writings, and contains retaliatory charges against her for suspected Communist activities. Frank Sinatra – His 1,300 page FBI dossier, dating from 1943, contains allegations about Sinatra's possible ties to the American Communist Party. The FBI spent several decades tracking Sinatra and his associates.
Marilyn Monroe – Her FBI dossier begins in 1955 and continues up until the months before her death. It focuses mostly on her travels and associations, searching for signs of leftist views and possible ties to communism. Monroe's FBI dossier is "heavily censored", but a "reprocessed" version has been released by the FBI to the public. John Lennon – In 1971, shortly after Lennon arrived in the United States on a visa to meet up with anti-war activists, the FBI placed Lennon under surveillance, and the U.S. government tried to deport him from the country. At that time, opposition to the Vietnam War had reached a peak and Lennon often showed up at political rallies to sing his anti-war anthem "Give Peace a Chance". The U.S. government argued that Lennon's 300 page FBI dossier was particularly sensitive because its release may "lead to foreign diplomatic, economic and military retaliation against the United States", and therefore only approved a "heavily censored" version. Albert Einstein, who supported the anti-war movement and opposed nuclear proliferation, was a member of numerous civil rights groups including the National Association for the Advancement of Colored People (See Albert Einstein's political views). As a result of his political views, Einstein was subjected to telephone tapping, and his mail was searched by the U.S. Federal Bureau of Investigation (FBI) as part of a secret government campaign that aimed to link him with a Soviet espionage ring in order to first discredit him, and then deport him (unsuccessfully) from the United States. Martin Luther King Jr., a leader of the Civil Rights Movement, was the target of an intensive campaign by the FBI to "neutralize" him as an effective civil rights activist. An FBI memo recognized King to be the "most dangerous and effective Negro leader in the country.", and the agency wanted to discredit him by collecting evidence to (unsuccessfully) prove that he had been influenced by communism. Daniel Ellsberg, who leaked the Pentagon Papers to the media in 1971, experienced one of the most spectacular episodes of government surveillance and character assassination. The White House tried to steal his medical records and other possibly detrimental information by sending a special unit to break into the office of Ellsberg's psychiatrist. These activities were later uncovered during the course of investigation as the Watergate scandal slowly unfolded, which eventually led to the resignation of President Richard Nixon. 1967–73: The now-defunct Project MINARET was created to spy on U.S. citizens. At the request of the U.S. Army, those who protested against the Vietnam War were put on the NSA's "watch list".
Over 26,000 individuals were at one point catalogued on an FBI list of persons to be rounded up in the event of a "national emergency". Over 500,000 domestic intelligence files were kept at the FBI headquarters, of which 65,000 were opened in 1972 alone. At least 130,000 first class letters were opened and photographed by the FBI from 1940 to 1966. A quarter of a million first class letters were opened and photographed by the CIA from 1953 to 1973. Millions of private telegrams sent from, or to, through the United States were obtained by the National Security Agency (NSA), under a secret arrangement with U.S.
telegraph companies, from 1947 to 1975. Over 100,000 Americans have been indexed in U.S. Army intelligence files. About 300,000 individuals were indexed in a CIA computer system during the course of Operation CHAOS. Intelligence files on more than 11,000 individuals and groups were created by the Internal Revenue Service (IRS), with tax investigations "done on the basis of political rather than tax criteria". In response to the committee's findings, the United States Congress passed the Foreign Intelligence Surveillance Act in 1978, which led to the establishment of the United States Foreign Intelligence Surveillance Court, which was authorized to issue surveillance warrants. Several decades later in 2013, the presiding judge of the FISA Court, Reggie Walton, told The Washington Post that the court only has a limited ability to supervise the government's surveillance, and is therefore "forced" to rely upon the accuracy of the information that is provided by federal agents. On August 17, 1975 Senator Frank Church stated on NBC's "Meet the Press" without mentioning the name of the NSA about this agency: In the need to develop a capacity to know what potential enemies are doing, the United States government has perfected a technological capability that enables us to monitor the messages that go through the air. Now, that is necessary and important to the United States as we look abroad at enemies or potential enemies. We must know, at the same time, that capability at any time could be turned around on the American people, and no American would have any privacy left such is the capability to monitor everything — telephone conversations, telegrams, it doesn't matter. There would be no place to hide. If this government ever became a tyrant, if a dictator ever took charge in this country, the technological capacity that the intelligence community has given the government could enable it to impose total tyranny, and there would be no way to fight back because the most careful effort to combine in resistance to the government, no matter how privately it was done, is within the reach of the government to know. Such is the capability of this technology.
I don't want to see this country ever go across the bridge. I know the capacity that is there to make tyranny total in America, and we must see to it that this agency and all agencies that possess this technology operate within the law and under proper supervision so that we never cross over that abyss. That is the abyss from which there is no return. In 1988 an article titled "Somebody's listening" by Duncan Campbell in the New Statesman described the signals-intelligence gathering activities of a program code-named "ECHELON". The program was engaged by English-speaking World War II Allied countries – Australia, Canada, New Zealand, the United Kingdom and the United States (collectively known as AUSCANNZUKUS). It was created by the five countries to monitor the military and diplomatic communications of the Soviet Union and of its Eastern Bloc allies during the Cold War in the early 1960s. By the 1990s the ECHELON system could intercept satellite transmissions, public switched telephone network (PSTN) communications (including most Internet traffic), and transmissions carried by microwave. The New Zealand journalist Nicky Hager provided a detailed description of ECHELON in his 1996 book Secret Power. While some member governments denied the existence of ECHELON, a report by a committee of the European Parliament in 2001 confirmed the program's use and warned Europeans about its reach and effects. The European Parliament stated in its report that the term "ECHELON" occurred in a number of contexts, but that the evidence presented indicated it was a signals-intelligence collection system capable of interception and content-inspection of telephone calls, fax, e-mail and other data-traffic globally. James Bamford further described the capabilities of ECHELON in Body of Secrets (2002) about the National Security Agency. Intelligence monitoring of citizens, and their communications, in the area covered by the AUSCANNZUKUS security agreement have, over the years, caused considerable public concern.
We will come together to strengthen our intelligence capabilities to know the plans of terrorists before they act and to find them before they strike. 5. Performance Evaluation & Extended Technical Observations In the aftermath of the September 2001 attacks on the World Trade Center and the Pentagon, bulk domestic spying in the United States increased dramatically. The desire to prevent future attacks of this scale led to the passage of the Patriot Act.
Later acts include the Protect America Act (which removes the warrant requirement for government surveillance of foreign targets) and the FISA Amendments Act (which relaxed some of the original FISA court requirements). Follow-on legislation have amended and reauthorized the post-9/11 surveillance authorities. The USA FREEDOM Act of 2015 limited certain bulk collection authorized under the USA PATRIOT Act. Subsequent legislation reauthorized Section 702 of the Foreign Intelligence Surveillance Act, which allows for warrantless surveillance of non-U.S. persons located outside the United States and will sunset in April 2026 if not reauthorized by Congress. In 2002, "Total Information Awareness" was established by the U.S. government in order to "revolutionize the ability of the United States to detect, classify and identify foreign terrorists". In 2005, a report about President Bush's President's Surveillance Program appeared in The New York Times. According to reporters James Risen and Eric Lichtblau, the actual publication of their report was delayed for a year because "The White House asked The New York Times not to publish this article". Also in 2005, the existence of STELLARWIND was revealed by Thomas Tamm. In 2006, Mark Klein revealed the existence of Room 641A that he had wired back in 2003. In 2008, Babak Pasdar, a computer security expert, and CEO of Bat Blue publicly revealed the existence of the "Quantico circuit", that he and his team found in 2003. He described it as a backdoor to the federal government in the systems of an unnamed wireless provider; the company was later independently identified as Verizon.
The NSA's database of American's phone calls was made public in 2006 by USA Today journalist Leslie Cauley in an article titled, "NSA has massive database of Americans' phone calls." The article cites anonymous sources that described the program's reach on American citizens: ... it means that the government has detailed records of calls they made — across town or across the country — to family members, co-workers, business contacts and others. The three telecommunications companies are working under contract with the NSA, which launched the program in 2001 shortly after the Sept. 11 terrorist attacks. In 2009, The New York Times cited several anonymous intelligence officials alleging that "the N.S.A. made Americans targets in eavesdropping operations based on insufficient evidence tying them to terrorism" and "the N.S.A. tried to wiretap a member of Congress without a warrant".
On 6 June 2013, Britain's The Guardian newspaper began publishing a series of revelations by an unnamed American whistleblower, revealed several days later to be former CIA and NSA-contracted systems analyst Edward Snowden. Snowden gave a cache of internal documents in support of his claims to two journalists: Glenn Greenwald and Laura Poitras, Greenwald later estimated that the cache contains 15,000–20,000 documents, some very large and very detailed, and some very small. This was one of the largest news leaks in the modern history of the United States. In over two months of publications, it became clear that the NSA operates a complex web of spying programs which allow it to intercept internet and telephone conversations from over a billion users from dozens of countries around the world. Specific revelations have been made about China, the European Union, Latin America, Iran and Pakistan, and Australia and New Zealand, however the published documentation reveals that many of the programs indiscriminately collect bulk information directly from central servers and internet backbones, which almost invariably carry and reroute information from distant countries. Due to this central server and backbone monitoring, many of the programs overlap and interrelate among one another. These programs are often done with the assistance of US entities such as the United States Department of Justice and the FBI, are sanctioned by US laws such as the FISA Amendments Act, and the necessary court orders for them are signed by the secret Foreign Intelligence Surveillance Court. In addition to this, many of the NSA's programs are directly aided by national and foreign intelligence services, Britain's GCHQ and Australia's DSD, as well as by large private telecommunications and Internet corporations, such as Verizon, Telstra, Google and Facebook. On 9 June 2013, Edward Snowden told The Guardian: They (the NSA) can use the system to go back in time and scrutinize every decision you've ever made, every friend you've ever discussed something with, and attack you on that basis to sort of derive suspicion from an innocent life and paint anyone in the context of a wrongdoer. The US government has aggressively sought to dismiss and challenge Fourth Amendment cases raised: Hepting v. AT&T, Jewel v. NSA, Clapper v. Amnesty International, Al-Haramain Islamic Foundation v. Obama, and Center for Constitutional Rights v. Bush. The government has also granted retroactive immunity to ISPs and telecoms participating in domestic surveillance. The US district court judge for the District of Columbia, Richard Leon, declared on December 16, 2013 that the mass collection of metadata of Americans' telephone records by the National Security Agency probably violates the Fourth Amendment prohibition of unreasonable searches and seizures.
Given the limited record before me at this point in the litigation – most notably, the utter lack of evidence that a terrorist attack has ever been prevented because searching the NSA database was faster than other investigative tactics – I have serious doubts about the efficacy of the metadata collection program as a means of conducting time-sensitive investigations in cases involving imminent threats of terrorism. "Plaintiffs have a substantial likelihood of showing that their privacy interests outweigh the government's interest in collecting and analysing bulk telephony metadata and therefore the NSA's bulk collection program is indeed an unreasonable search under the fourth amendment," he wrote. "The Fourth Amendment typically requires 'a neutral and detached authority be interposed between the police and the public,' and it is offended by 'general warrants' and laws that allow searches to be conducted 'indiscriminately and without regard to their connections with a crime under investigation,'" he wrote. He added: I cannot imagine a more 'indiscriminate' and 'arbitrary invasion' than this systematic and high-tech collection and retention of personal data on virtually every single citizen for purposes of querying and analyzing it without prior judicial approval. Surely such a program infringes on 'that degree of privacy' that the founders enshrined in the Fourth Amendment. Indeed I have little doubt that the author of our Constitution, James Madison, who cautioned us to beware 'the abridgement of freedom of the people by gradual and silent encroachments by those in power,' would be aghast. Leon granted the request for a preliminary injunction that blocks the collection of phone data for two private plaintiffs (Larry Klayman, a conservative lawyer, and Charles Strange, father of a cryptologist killed in Afghanistan when his helicopter was shot down in 2011) and ordered the government to destroy any of their records that have been gathered. But the judge stayed action on his ruling pending a government appeal, recognizing in his 68-page opinion the "significant national security interests at stake in this case and the novelty of the constitutional issues." The second Trump administration has sought state data and consolidated historically isolated federal data. The Justice Department has sought state voter data. The Department of Government Efficiency has collected data seeking access to IRS, Social Security, Selective Service, Medicare, Health and Human Services, Securities and Exchange Commission, National Labor Relations Board, and student data. DHS has expanded its surveillance particularly to enable the administration's immigration priorities. This follows from DHS's earlier use of databases in the 2010s to profile Latino Americans and contribute to "self-deportation" techniques or physical deportations by way of the DHS gang databases.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Digital%20forensics • https://en.wikipedia.org/wiki/Computer%20and%20network%20surveillance • https://en.wikipedia.org/wiki/Mass%20surveillance%20in%20the%20United%20States
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Voip Call Forensic Analysis And Reconstruction Tool.
[*] Metasploit Scan Running on Target Subnet for Voip Call Forensic Analysis And Reconstruction Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |