Complete Technical Paper Content — Vulnerability Management Dashboard
Overview & System Context
Vulnerability Management Dashboard: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9548 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Network management software is software used to provision, discover, monitor, and maintain computer networks.
WordPress (WP, or WordPress.org) is a web content management system. It was originally created as a tool to publish blogs but has evolved to support publishing other web content, including more traditional websites, mailing lists, Internet forums, media galleries, membership sites, learning management systems, and online stores. Available as free and open-source software, WordPress is among the most popular content management systems – it was used by 22.52% of the top one million websites as of December 2024. WordPress is written in the PHP programming language and paired with a MySQL or MariaDB database. Features include a plugin architecture and a template system, known as "themes". Since 2018, WordPress has included a block-based editor ("Gutenberg"). To function, WordPress has to be installed on a web server, either as part of an Internet hosting service or on a personal computer. WordPress was first released on May 27, 2003, by its founders, American developer Matt Mullenweg and English developer Mike Little. The WordPress Foundation owns WordPress, WordPress projects, and other related trademarks.
"WordPress is a factory that makes webpages" is a core analogy designed to clarify the functions of WordPress: it stores content and enables a user to create and publish webpages, requiring nothing beyond a domain and a hosting service. WordPress has a web template system using a template processor. Its architecture is a front controller, routing all requests for non-static URIs to a single PHP file that parses the URI and identifies the target page. This allows support for more human-readable permalinks.
The December 2018 release of WordPress 5.0, "Bebo", is named in homage to the pioneering Cuban jazz musician Bebo Valdés. It included a new default editor "Gutenberg" – a block-based editor; that allows users to modify their displayed content in a much more user-friendly way than prior iterations. Blocks are abstract units of markup that, composed together, form the content or layout of a web page. Past content that was created on WordPress pages is listed under what is referred to as a Classic Block. Before Gutenberg, there were several block-based editors available as WordPress plugins, e.g. Elementor.
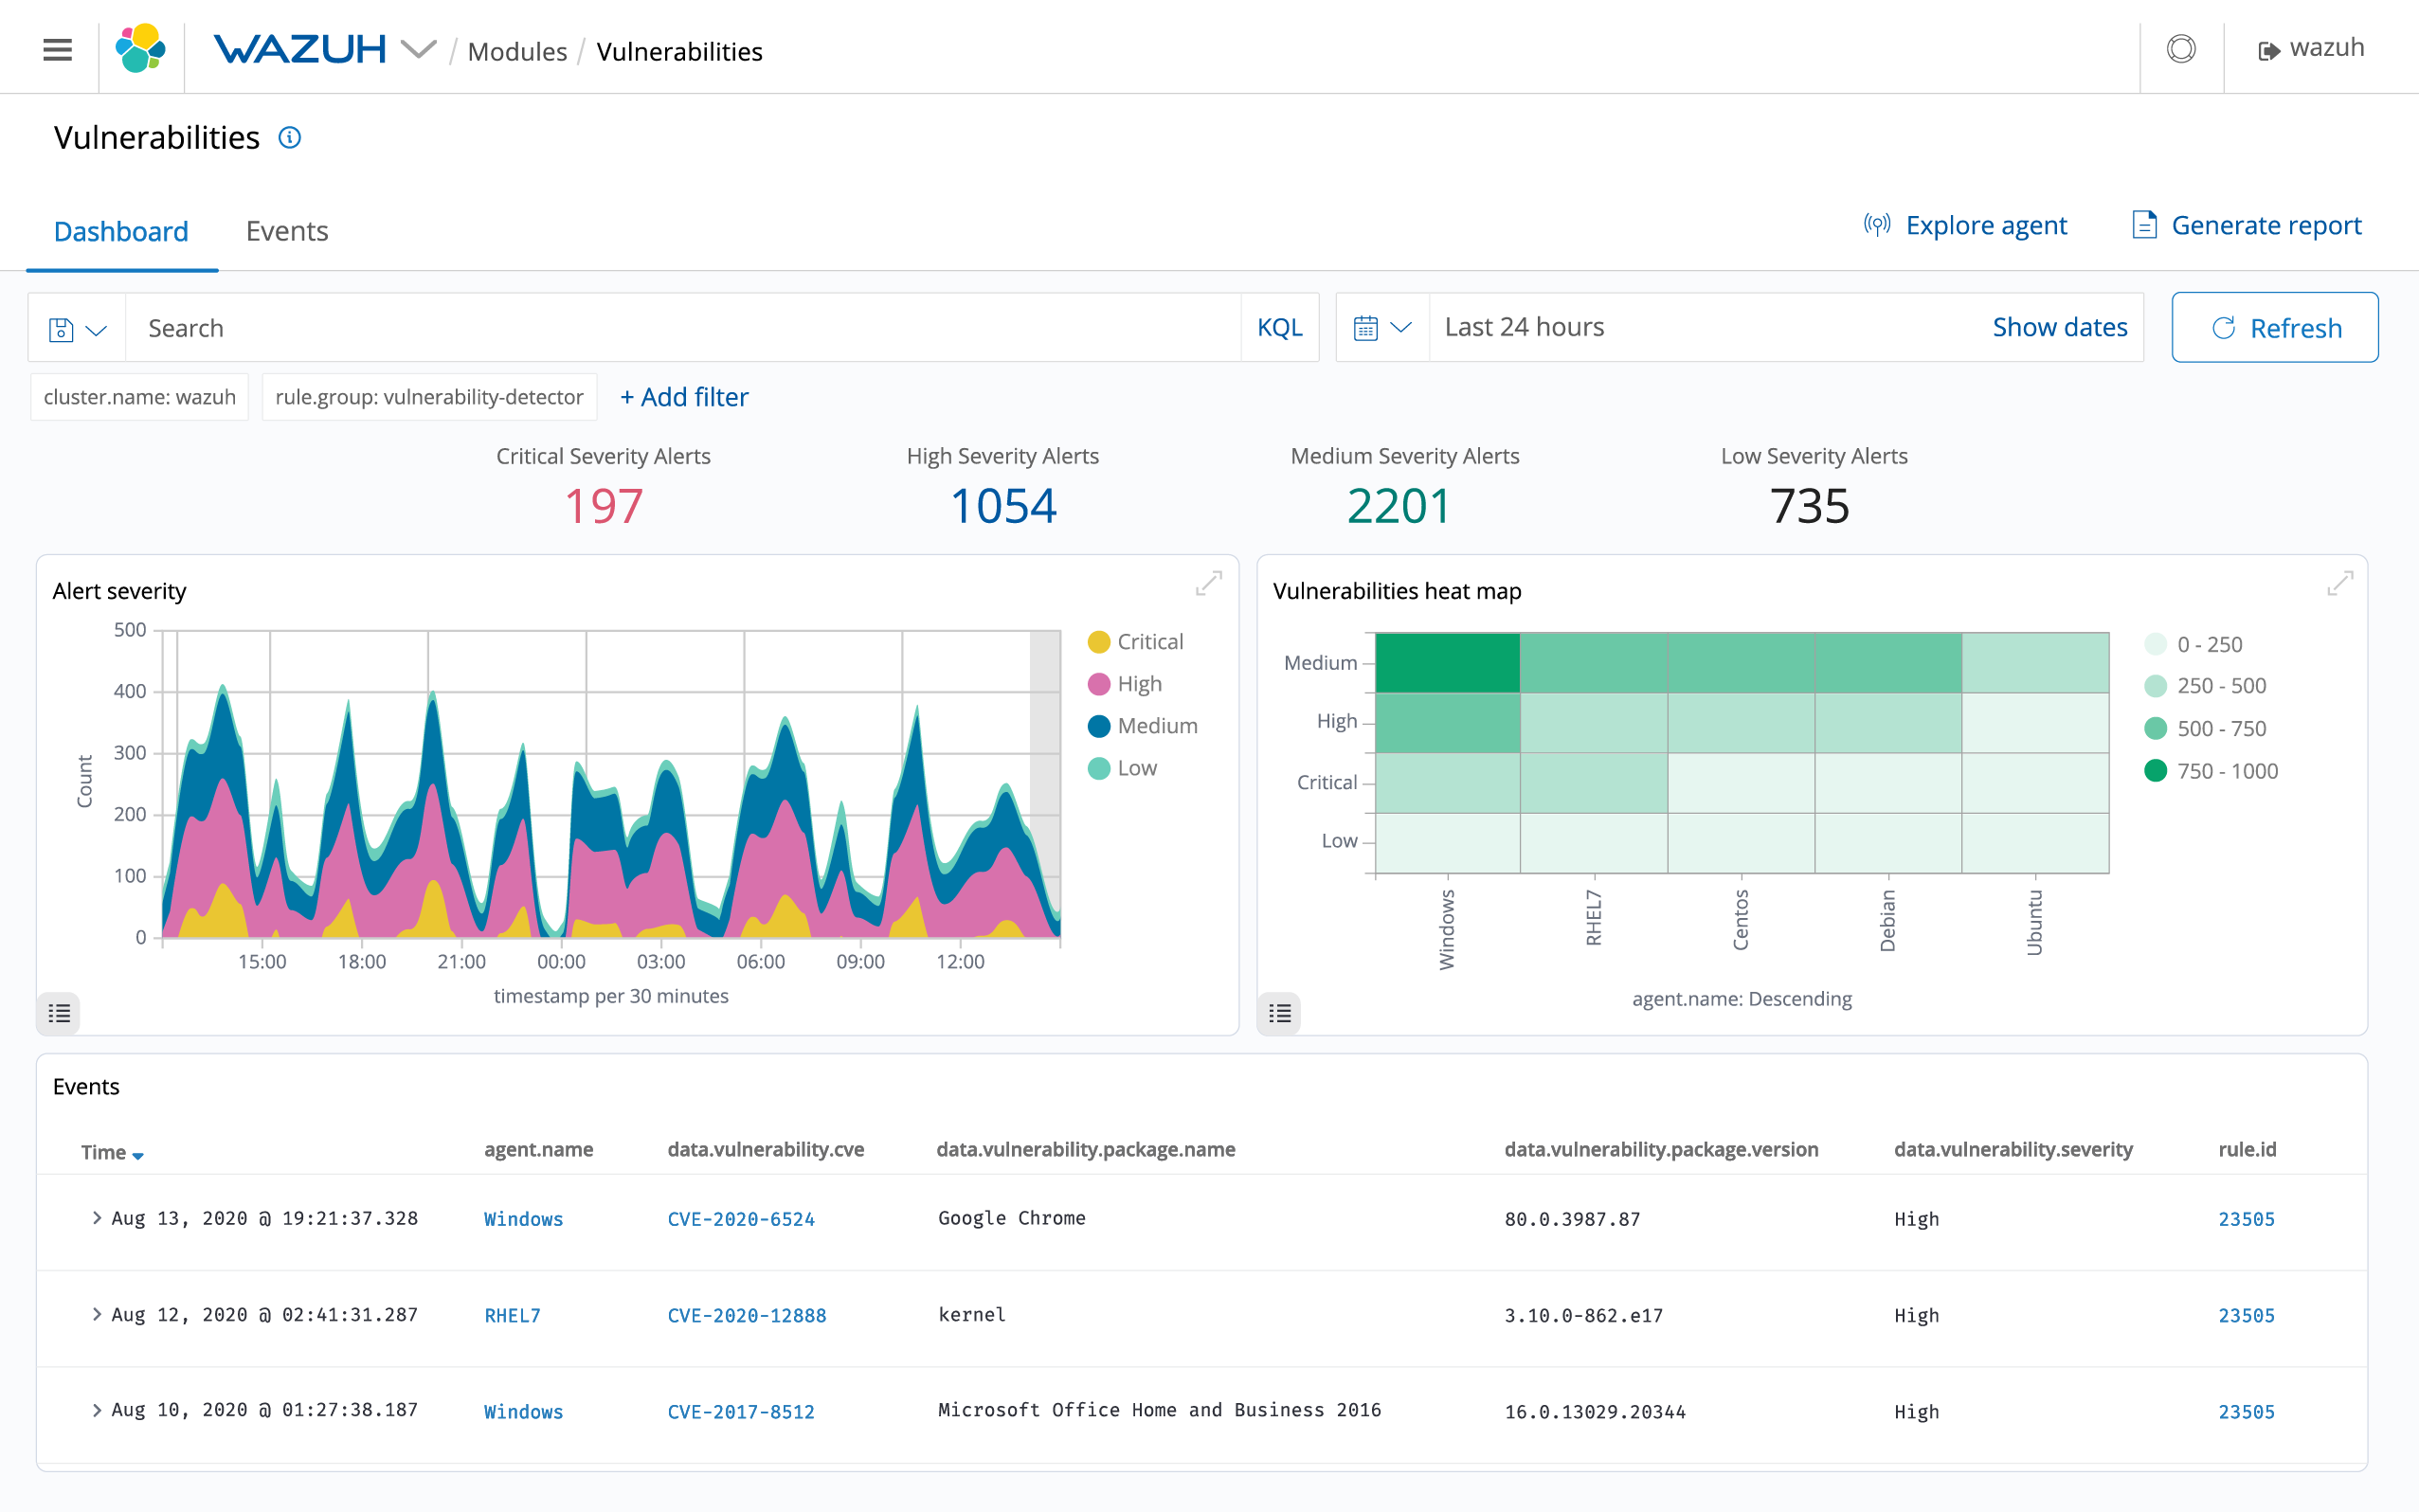
Following the release of Gutenberg, comparisons were made between it and those existing plugins. Figure 1: Open Source vulnerability scanning tool : r/selfhosted Many security issues have been uncovered and patched in the software, particularly in 2007, 2008, and 2015. A cumulative list of WordPress security vulnerabilities, not all of which have been corrected in the version current at any time, is maintained by SecurityScorecard. In January 2007, many high-profile search engine optimization (SEO) blogs, as well as many low-profile commercial blogs featuring AdSense, were targeted and attacked with a WordPress exploit. A separate vulnerability on one of the project site's web servers allowed an attacker to introduce exploitable code in the form of a back door to some downloads of WordPress 2.1.1. The 2.1.2 release addressed this issue; an advisory released at the time advised all users to upgrade immediately. In May 2007, a study revealed that 98% of WordPress blogs being run were exploitable because they were running outdated and unsupported versions of the software. To help mitigate this problem, WordPress made updating the software a much easier, "one-click" automated process in version 2.7 (released in December 2008). However, the filesystem security settings required to enable the update process can be an additional risk. In a June 2007 interview, Stefan Esser, the founder of the PHP Security Response Team, spoke critically of WordPress' security track record, citing problems with the application's architecture that made it unnecessarily difficult to write code that is secure from SQL injection vulnerabilities, as well as some other problems. In June 2013, it was found that some of the 50 most downloaded WordPress plugins were vulnerable to common Web attacks such as SQL injection and XSS. A separate inspection of the top 10 e-commerce plugins showed that seven of them were vulnerable. To promote better security and to streamline the update experience overall, automatic background updates were introduced in WordPress 3.7. Individual installations of WordPress can be protected with security plugins that prevent user enumeration, hide resources, and thwart probes. Users can also protect their WordPress installations by taking steps such as keeping all WordPress installations, themes, and plugins updated, using only trusted themes and plugins, and editing the site's .htaccess configuration file if supported by the webserver to prevent many types of SQL injection attacks and block unauthorized access to sensitive files. It is especially important to keep WordPress plugins updated because would-be hackers can easily list all the plugins a site uses and then run scans searching for any vulnerabilities against those plugins. If vulnerabilities are found, they may be exploited to allow hackers to, for example, upload their files (such as a web shell) that collect sensitive information. Developers can also use tools to analyze potential vulnerabilities, including Jetpack Protect, WPScan, WordPress Auditor, and WordPress Sploit Framework developed by 0pc0deFR. These types of tools research known vulnerabilities, such as CSRF, LFI, RFI, XSS, SQL injection, and user enumeration. However, not all vulnerabilities can be detected by tools, so it is advisable to check the code of plugins, themes, and other add-ins from other developers. In March 2015, it was reported that the Yoast SEO plugin was vulnerable to SQL injection, allowing attackers to potentially execute arbitrary SQL commands. The issue was fixed in version 1.7.4 of the plugin. In January 2017, security auditors at Sucuri identified a vulnerability in the WordPress REST API that would allow any unauthenticated user to modify any post or page within a site running WordPress 4.7 or greater. The auditors quietly notified WordPress developers, and within six days WordPress released a high-priority patch to version 4.7.2, which addressed the problem.
As of WordPress 6.0, the minimum PHP version requirement is PHP 5.6, which was released on August 28, 2014, and which has been unsupported by the PHP Group and not received any security patches since December 31, 2018. Thus, WordPress recommends using PHP version 7.4 or greater. In the absence of specific alterations to their default formatting code, WordPress-based websites use the canvas element to detect whether the browser can correctly render emoji. Because Tor Browser does not currently discriminate between this legitimate use of the Canvas API and an effort to perform canvas fingerprinting, it warns that the website is attempting to 'extract HTML5 canvas image data. Ongoing efforts seek workarounds to reassure privacy advocates while retaining the ability to check for proper emoji rendering capability.
WordCamps are casual, locally organized conferences covering everything related to WordPress. The first such event was WordCamp 2006 in August 2006 in San Francisco, which lasted one day and had over 500 attendees. The first WordCamp outside San Francisco was held in Beijing in September 2007. Since then, there have been over 1,022 WordCamps in over 75 cities in 65 countries around the world. WordCamp San Francisco 2014 was the last official annual conference of WordPress developers and users taking place in San Francisco, having now been replaced with WordCamp US. First ran in 2013 as WordCamp Europe, regional WordCamps in other geographical regions are held to connect people who are not already active in their local communities and inspire attendees to start user communities in their hometowns. In 2019, the Nordic region had its own WordCamp Nordic. The first WordCamp Asia was to be held in 2020, but cancelled due to the COVID-19 pandemic.
WordPress hosting services typically offer one-click WordPress installations, automated updates and backups, and security features to safeguard against common threats. Many also provide support and are configured for optimal performance with the CMS. There are two primary types of WordPress hosting: shared WordPress hosting and managed WordPress hosting. Shared WordPress hosting is a budget-friendly option where multiple websites reside on a single server, sharing resources.
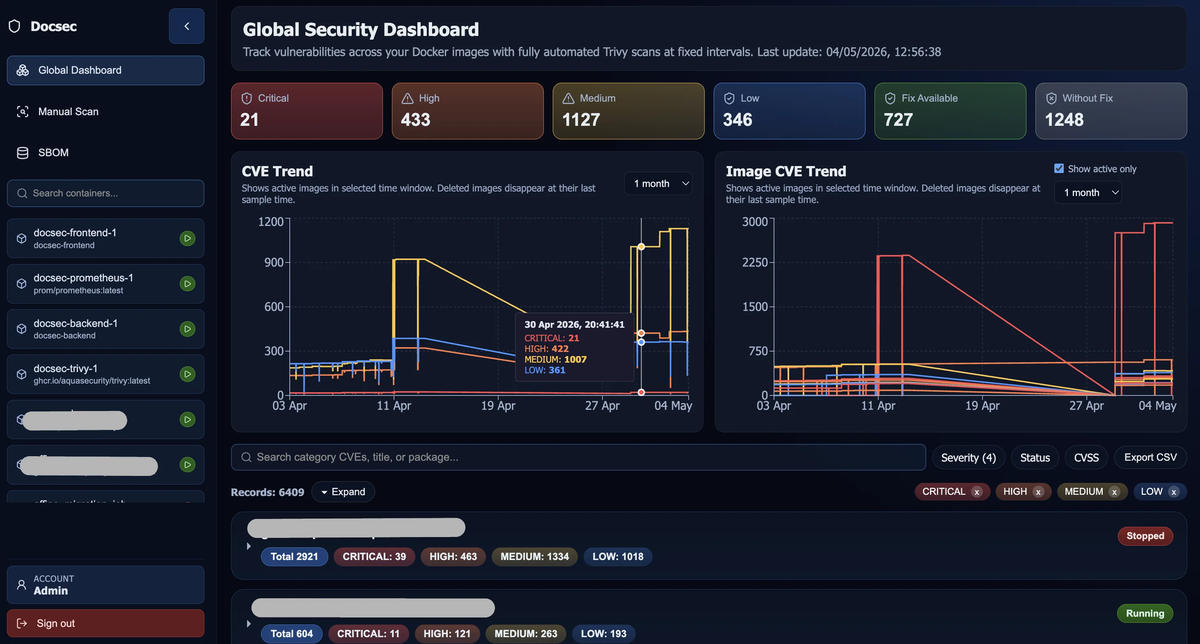
Managed WordPress hosting includes comprehensive management of a WordPress site, including technical support, security, performance optimization, and often higher server resources, but comes at a higher price. Figure 2: DOCSEC: Container Image Vulnerability Management Platform Real-time Adaptive Security is the network security model necessary to accommodate the emergence of multiple perimeters and moving parts on the network, and increasingly advanced threats targeting enterprises. Adaptive security can watch a network for malicious traffic and behavioral anomalies, ferret out end point vulnerabilities, identify real-time changes to systems, automatically enforce end point protections and access rules, block malicious traffic, follow a compliance dashboard while providing audit data, and more. Among the key features of an adaptive security infrastructure are security platforms that share and correlate information rather than point solutions, so the heuristics system could communicate its suspicions to the firewall. Other features include finer-grained controls, automation (in addition to human intervention), on-demand security services, security as a service, and integration of security and management data. Rather than adding security to custom applications after they go operational, security models would be created at the design phase of an app. A major change with this model of real-time adaptive security is shifting authorization management and policy to an on-demand service that contains details and policy enforcement that matches compliance and can adapt to the user's situation when he or she is trying to access an application, for instance.
Access to this page requires authorization. You can try signing in or changing directories . The Vulnerability Management section in the Microsoft Defender portal is now located under Exposure management . With this change, you can now consume and manage security exposure data and vulnerability data in a unified location, to enhance your existing Vulnerability Management features. Learn more .
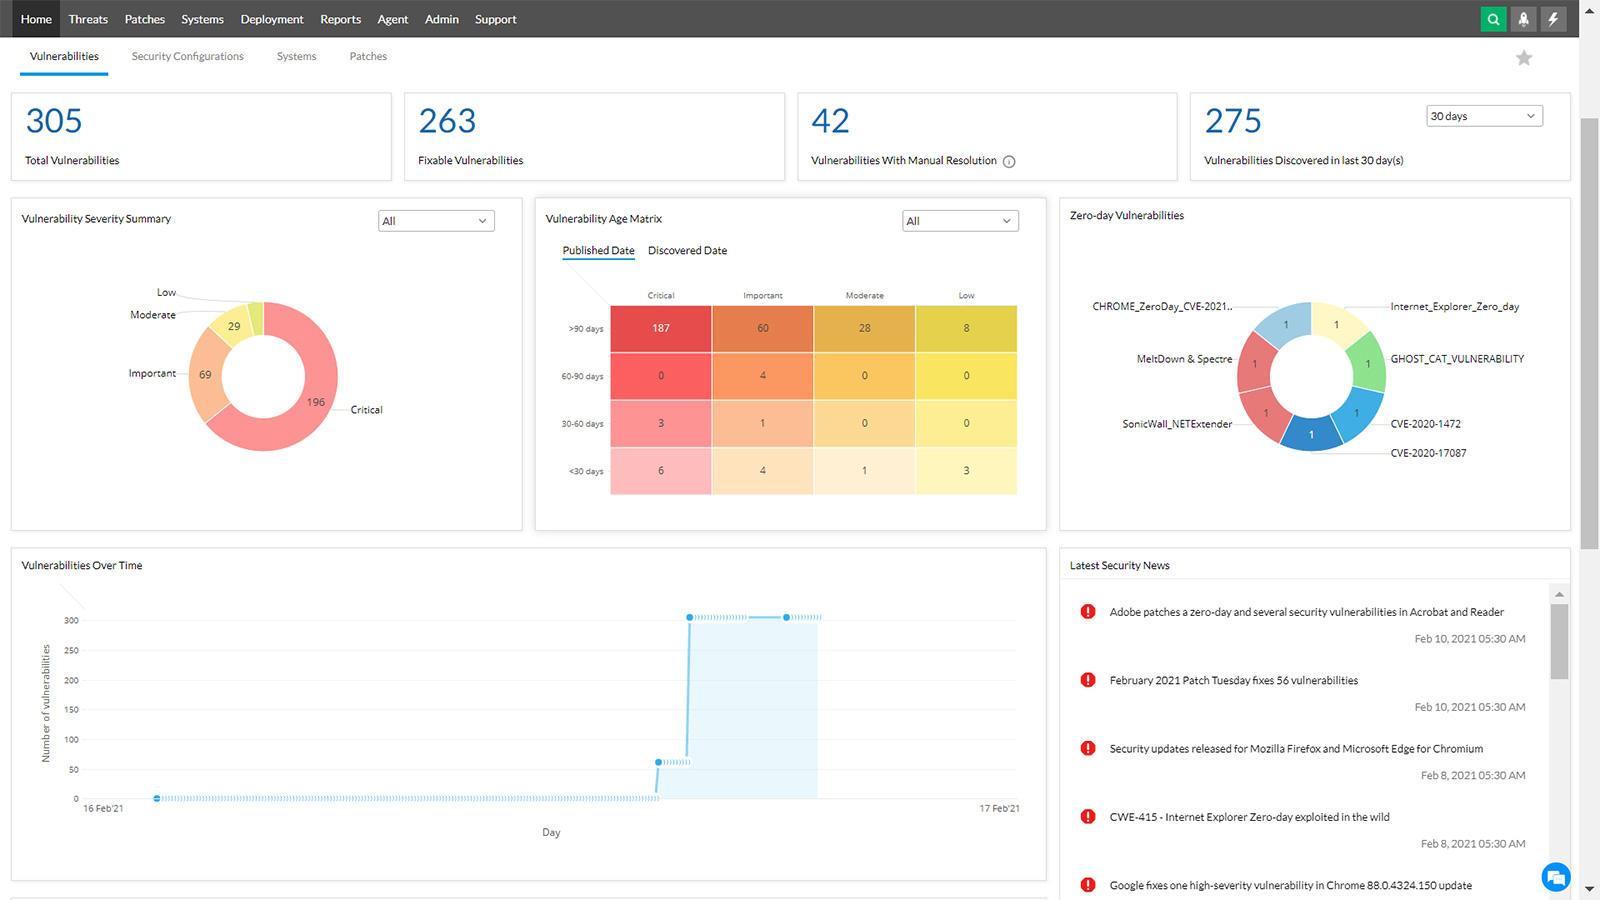
These changes are relevant for Preview customers ( Microsoft Defender XDR + Microsoft Defender for Identity preview option). Figure 3: Product showcase: ManageEngine Vulnerability Manager Plus - Help Net ... In this article, you'll learn about the Microsoft Defender Vulnerability Management overview page and how it can help you understand and manage your organization's security exposure.
Did you know you can try all the features in Microsoft Defender Vulnerability Management for free? Find out how to sign up for a free trial . This section describes the Microsoft Defender Vulnerability Management experience for customers using the Microsoft Defender XDR + Microsoft Defender for Identity preview. This experience is part of the integration of Microsoft Defender Vulnerability Management into Microsoft Security Exposure Management. Learn more .
You can use the Exposure management > Vulnerability management > Overview page in the Microsoft Defender portal to: You can view misconfiguration and secure score information in the Exposure management > Recommendations page. You can use the Endpoints > Defender Vulnerability Management > Dashboard in the Microsoft Defender portal to: Devices that aren't active in the last 30 days aren't factored in on the data that reflects your organization's vulnerability management exposure score and Microsoft Secure Score for Devices. In addition, CVEs marked as "won't fix" are not shown in the Microsoft Defender portal, and they're not included in vulnerability recommendations or scoring.
This section describes the Microsoft Defender Vulnerability Management experience for customers using the Microsoft Defender XDR + Microsoft Defender for Identity preview. This experience is part of the integration of Microsoft Defender Vulnerability Management into Microsoft Security Exposure Management. Learn more . Reduce cyber risk with continuous vulnerability discovery and assessment, risk-based prioritization, and remediation.
Building purposeful dashboards in Kibana that simplify vulnerability management, meet stakeholder requirements, and provide a modular framework for evolving cyber security maturity. Easily my lesser appreciated love within Vulnerability Management is dashboarding. If you’re working with any sort of reasonably-sized environment with a mix of workstations, servers, operational technology, and network devices, then any sort of vulnerability scanning will bring in large amounts of data, and typically not a great way to visualise it within the proprietary tools performing the scanning.
VM Scanning software like Tenable and Qualys provide ‘good enough’ solutions, but if you’re looking for more flexibility over data presentation, interactivity, improved readability, better user adoption, and more effective prioritisation; then investing in custom dashboarding may be the solution that you need. This post got a little longer than I thought it would. I’ve included a TL;DR at the bottom, and there’s a helpful Table of Contents to the left-hand side if you’d like to skip around! Consider the reason for creating the dashboard. What questions are being asked by the business, internal stakeholders, or yourself that you’d like to get a simple answer to? Questions could be: A dashboard can answer one or many of these questions, but if an excessive amount of filtering is needed to get to the answer, you may need to consider separate dashboards that more effectively present the needed information.
I’m putting this principle above your own outcomes as I think this is the most effective way to enact change in the business. Unless you’re a one-stop security shop in your org, you’ll need other experts and owners in the business to support patching and back improvements to security culture. Understand what these stakeholders want out of this service. Their requirements are likely to be much simpler than yours.
They may not want to peruse the data with a fine comb, but instead see a simple list of “things to do,” whether that’s upgrades, patching, decommissioning, uninstalling etc. Create an environment that works for them and presents the data in the way that they want it, i.e.: a Windows Server manager may want to see overall patch compliance across all Windows Servers; a Linux engineer may want a per-device breakdown of critical, exploitable vulnerabilities that have lapsed the patch policy requirements.
Understand that every team and individual has their own metrics for success, and building a platform that enables them to enact change and demonstrate success within their own area creates a positive feedback loop for security. Ask what you hope to achieve through the creation and distribution of this dashboard. What are your team’s Key Performance Indicators (KPIs)? How will this dashboard enable either your team or other stakeholders to start contributing to the broader organisational objectives surrounding security and vulnerability management? Some objectives to consider: 2. System Architecture & Core Working Principles Reducing number of active vulnerabilities that are not compliant to internal policy, i.e. critical vulnerabilities patched within 30 days, high within 60 days, medium within 90 days… etc.
Removing vulnerabilities that are not compliant to accredited standard guidelines, i.e. PCI DSS, ISO27001, Cyber Essentials+ etc. Patch all vulnerabilities that have an exploit available, that are remotely exploitable, and are present on internet-facing devices.
Understand in your objectives that there’s a difference between security compliance and being secure. Security compliance is a requirement; good security posture is your goal. These concepts are often not related. Dashboards should rarely be single-use. A dashboard used once is not a dashboard; it’s a report. While the interactivity of a dashboard for one-off events may be helpful, the strategic goal should always be to encourage and incentivise regular reviews of the content.
To better achieve this, you need to ensure that data is dynamic and as current as possible. Be consistent with your scan frequency. If Tenable scans occur daily, then ensure the information in your dashboard is updated daily. If the scans occur in the background every 4 hours, you better be updating that data every 4 hours, or at least setting expectations for regular updates.
If you follow the other principles listed and create something that answers key business questions, provides a solution to your stakeholders, and positively benefits your own KPIs, then regular reviews should be your indicator of success. If you are struggling to get that level of adoption, re-visit the other principles and consider where the failing is in the process. To effectively demonstrate an example dashboard, I had to follow a few steps to ensure I wasn’t compromising security and still creating a live-like demo environment. I’ll be using Elasticsearch for data analytics and aggregation as I already have an environment ready to go; I’ll be generating dummy data with help from ChatGPT using Faker , and then building the dashboard with Kibana .
See the Appendix for the prompt used to generate the data if you’d like to follow my steps. 120 devices in scope with a mix of technologies between Windows 10, Windows Servers, RHEL, and some Cisco kit. There are 5 managers in scope with different device responsibilities (i.e. Alice manages all the Win10 environment, Bob manages RHEL, Carlos manages Windows Servers, but Diana and Evan own a mix of both).
The vulnerability data is randomly generated and doesn’t represent any real vulnerabilities, but is instead a random distribution of made up CVEs, severities, solutions, and EPSS scores. Use filters to draw distinctions between vulnerabilities that are still within your Service Level Agreement (SLA), and vulnerabilities that have lapsed from their required remediation date. Here’s a very simple (and not recommended) example of Criticals being fixed within 30 days, Highs within 60 days, Mediums within 90 days, and Lows within 365 days. Adjust the values to your organisation’s policy.
Kibana allows you to add buttons that filter on-click. Add a button that applies the non-compliance filter to the entire dashboard with one click to make it simple for stakeholders. As any changes we make to the filter apply to the entire dashboard, the stakeholder viewing can then see which vulnerabilities have lapsed SLA and which to focus on first, either based on security improvement or vulnerability reduction, or even on a per-device basis.
By creating a historic data index, you can compare point-in-time data to see how data is trending. Vulnerabilities History index takes a snapshot every 24h of the current vulnerability posture from the rolling index. This then allows point-in-time comparisons of data to see how the organisation is performing. You can use the SLA metrics above to show changes in vulnerabilities for both the total and the non-compliant vulnerabilities: If you are conducting wide discovery scans that fingerprint the device OS, it can be useful to have an ‘Other’ category that isn’t one of your standard operating systems. This draws attention to anything on the network that isn’t part of your strategic deployment, or that you haven’t accounted for properly in your view.
This is a really simple way to draw out the potentially high-impact and highly exploitable vulnerabilities in your network, especially when used in conjunction with the other filters available in the dashboard. The table below organises the CVEs by their EPSS rating and allows the user to navigate to the NVD page through a context menu. If you’re filtering by device, OS, or owner, this can help to bring attention to the most exploitable vulnerabilities in scope.
Remember that just because something is highly exploitable, doesn’t mean that you are exposed - further checks will have to be conducted and could also be built into your filters to increase accuracy. It may be beneficial to patch by solution rather than vulnerability. This can call out how many devices would benefit from the fix and how many vulnerabilities would be remediated. Good for compliance and KPIs.
If you instead wanted to focus on security benefits, you can filter the data to show the Maximum EPSS score that would be remediated if the solution was applied. The above is a great example of showing that while more vulnerabilities would be remediated by applying the first solution, there is actually a more exploitable vulnerability that would be resolved by applying the third solution, mitigating the higher risk of exploit from 53 devices. The specific CVEs are shown on the left-hand side which can then be investigated further.
Another thing I’ve used the EPSS score for here is to provide an ‘Asset Exposure Rating’. This is simply a cumulative total of all EPSS scores affecting a device. As EPSS is represented as a decimal, by adding all of these scores together you can create a really simple way to call out potentially high exposure devices. This can be most effective when applied to internet-facing infrastructure or with more granular filtering of CVSS vectors (see External Attack Surface - Priority Patching dashboard below).
I use the above dashboard as a template to create other dashboards that highlight vulnerabilities and compliance issues in other business areas. Here’s a few more ideas for dashboards that might be of some use. Here’s one I use for what I call ‘Priority Patching’, where I focus on web-facing devices that are affected by exploitable vulnerabilities with a Network attack vector, using CVSS vectors to filter the data: Filter below allows for more granular filtering against the CVSS vector and gives more control over the type of vulnerabilities that are shown that are most suited to your environment.
This dashboard element looks at Software by installs, their vulnerabilities, and a heatmap of contribution to the vulnerability total. This can help to identify software that is significantly out of date or contributing a large amount of vulnerabilities to the total; thus better informing business decisions around approved software, End-User Device Management, and patching procedures.
This dashboard uses a custom tag for ‘PCIDSS’ that would group all of the assets that are in scope for PCI DSS compliance. Further filters in the dashboard would enable the reported vulnerabilities to only show if they go outside of compliance of recommended PCI standards, i.e. the PCI standard typically only asks for Critical and High vulnerabilities to be remediated on the internal network by default, but Critical, High, and Medium on the external network: 3. Software Implementation, Frameworks & Protocols If that was as lot of writing and you have too many vulnerabilities to fix to read in detail, here’s the short version; Create a clean, readable, dashboard that can be changed easily with simple filters for multiple stakeholder needs - use the one above as a starting point if you need some inspiration.
Consider iterative improvements to make the above easier. Better tagging, better ownership information, more data ingested etc. See my other post on using Elastic as a SIEM if you’d like to explore more. I set out to create a better framework for independent vulnerability dashboarding. Searching for solutions and guidance to this problem presents you with companies that are offering you a pre-built template, but not the principles behind what makes these successful, and often not the granular control that I want to have in this area.
My personal experience has been entirely with Elasticsearch and Kibana, but the same may very well be achievable with other vendors in this space. This post is here to provide a framework rather than a tutorial for Kibana, so hopefully you can take my experience and apply it to your own environment. Here is ChatGPT’s simple interpretation of the conversation to generate the dummy data: I need to generate 8,567 records of dummy vulnerability data for testing purposes, formatted for Elasticsearch bulk import.
Here are the details and requirements: 24 Windows Server devices, managed by Carlos. 70% of them should be Windows Server 2019 and 30% should be Windows Server 2016 . 30 Linux Servers , with 80% running RHEL 9.4 and 20% running RHEL 9.3 . Managed by Bob, Diana, or Evan.
3 Cisco Routers , with host.os.name as "Cisco 4000 Series Integrated" . Managed by either Diana or Evan. 148 unique CVEs in total. Each CVE should have a consistent solution , severity , EPSS score , and vulnerability.published date. Solution should be randomly assigned but remain consistent for each CVE. Possible solutions are: Each line should have an index action line ( {"index": {}} ) followed by the actual document on the next line, with no extra newlines between.
Some issues with data generation here that could be improved upon. I didn’t stipulate enough solutions and they shouldn’t be distributed so evenly. Due to generating fake data, I couldn’t simulate vuln patching and vuln discovery over time to better emulate the ebbs and flows of a normal vulnerability environment, thus the historic data elements aren’t shown to be working here. I also left it a little too long to write this post so there’s quite a lot of ‘vulnerabilities’ that are out of compliance :) A Power BI reporting suite for vulnerability management, featuring executive-level risk posture views and operational drilldowns for remediation teams. Built from mock scan data spanning one year of weekly scans to demonstrate data modeling, DAX calculations, and cybersecurity reporting in Power BI.
Star schema design with fact and dimension tables for scalable analytics. This structure enables efficient querying and provides the foundation for all dashboard visualizations and calculations. Audience: CISOs, Senior Management Purpose: High-level snapshot of organizational exposure Metrics: Total open vulnerabilities, Critical %, Exploitable %, Average CVSS (open), Assets with critical vulns Executives quickly see exposure, risk concentration, and whether remediation efforts are reducing backlog.
Audience: Infrastructure / Remediation Teams Purpose: Identify assets carrying the most risk Metrics: Assets with open vulnerabilities, Average risk score per asset (CVSS-weighted), Assets with critical vulnerabilities, Assets past SLA Operations teams identify hotspots -- assets with both high severity and many vulnerabilities.
Audience: Security Analysts, Incident Responders Purpose: Investigate specific CVEs across the estate Analysts can pivot to a single CVE (e.g., Log4Shell) and instantly see scope, affected assets, and remediation guidance. Audience: Executives and Governance Teams Purpose: Long-term risk posture and remediation velocity analysis Metrics: New vulnerabilities (this month), Closed vulnerabilities (this month), Net change (backlog growth or reduction), Average remediation time (days) Audience: Risk/Compliance, Operations Managers Purpose: Track remediation performance vs SLA targets Metrics: SLA compliance % (within defined thresholds per severity), Critical/High past SLA counts, Average remediation time, Vulnerabilities closed in last 30 days Accountability dashboard highlighting where SLA targets are being missed, broken down by severity and business unit.
Audience: Vulnerability Management Engineers Purpose: Validate scanner health and plugin effectiveness Metrics: Total scans, Unique assets scanned, Average scan coverage %, Top plugin (by findings) Detects blind spots -- ensures scanning is consistent, plugins are firing as expected, and failures are investigated. Dashboards are built from generated mock data for demonstration purposes. Some visualizations may reflect artifacts of the synthetic data rather than real-world patterns.
4. Practical Deployment, Analysis & Case Studies A comprehensive Power BI reporting suite designed for vulnerability management, featuring executive-level risk posture views and operational drilldowns for remediation teams. A vulnerability management dashboard is a useful way of organizing vulnerability data to make it as insightful and actionable as possible.
In this article, we have made suggestions for how you can build an effective vulnerability management dashboard, to ensure your team can make timely, data-driven decisions for your organization. A vulnerability management dashboard is a dynamic interface for displaying data, metrics, and insights for a vulnerability management program , in one place.
The most effective vulnerability reporting dashboards are dynamic, to ensure teams have the most current information at all times. This also saves teams the time it takes to manually create updated versions; time that could be better spent on more valuable remediation activities. A vulnerability management dashboard helps teams make sense of their vulnerability data and organize it in ways that are insightful and actionable.
With the help of a vulnerability reporting dashboard , teams can make data-led decisions at a glance, which are backed up by the most important and current information. This helps teams take the best course of action when planning and executing remediation. A vulnerability management dashboard can also aid IT security leaders in evaluating their vulnerability management programs against a vulnerability management maturity model , making it easier to identify what is working well and where the program needs to develop further.
Ultimately, a dynamic vulnerability management dashboard ensures teams are continuously aware of the status of their most important assets and critical issues, to keep their organizations secure. There is no single way to create an effective vulnerability management dashboard, as the choice of metrics and presentation need to be tailored to the readers and the goals of the organization.
We made some suggestions for creating an insightful vulnerability management dashboard below. The Rootshell Platform is our vendor-agnostic platform that helps you implement modern and effective vulnerability management programs, reducing mean-time-to-remediate by up to 61%. Rootshell automatically generates insightful vulnerability reporting dashboards for your data, including: As well as generating vulnerability management dashboards, Rootshell helps you executive the most effective threat and vulnerability managemen t : There is no single way to create an effective vulnerability management dashboard, as the choice of metrics and presentation need to be tailored to the readers and the goals of the organization.
We made some suggestions for creating an insightful vulnerability management dashboard below. Traditional vulnerability management can feel like a never-ending game of whack-a-mole. You patch one critical issue, and three more pop up, leaving your team feeling burnt out and perpetually behind. A modern dashboard changes the game entirely. By integrating real-world threat intelligence, it helps you move beyond simple CVSS scores to understand which vulnerabilities pose a genuine, immediate threat to your organization. This shift allows you to build a proactive security program focused on what attackers are actually exploiting. The Ultimate CISO Dashboard (viewing all vulnerabilities in a single place) is the foundation for this approach, giving you the context to prioritize effectively.
Let's be honest: as a security leader, you're constantly swimming in data from dozens of tools. Vulnerability scanners, firewalls, and endpoint detection systems all generate a flood of alerts and metrics. A CISO dashboard cuts through that noise. Think of it as your security program's command center. It’s a centralized tool that pulls all your critical security data into one place, translating complex technical details into clear, visual insights that are easy to understand at a glance.
The real value isn't just having data in one spot; it's about communication and strategy. Your board and executive team don't speak in CVEs or firewall rule numbers. They want to understand risk in terms of business impact. A well-designed dashboard helps you bridge that gap. It allows you to answer their toughest questions with confidence: Are we secure? Where are our biggest risks? Is our security investment paying off? It transforms your role from a technical manager into a strategic business partner, equipping you to lead conversations about risk, investment, and overall security posture with data-driven clarity.
A CISO dashboard’s main job is to create a single source of truth. Instead of juggling spreadsheets and logging into multiple platforms to piece together a report, you get a consolidated view of your entire security landscape. This centralized hub aggregates data from across your security stack, presenting key performance indicators (KPIs) and metrics in an easily digestible format. This gives you and your stakeholders a clear, up-to-the-minute snapshot of your organization's security health.
This approach saves an incredible amount of time and reduces the risk of human error. More importantly, it provides a unified view of cyber risks that everyone from the security operations center to the boardroom can understand. When everyone is looking at the same data, presented consistently, you can have more productive conversations about where to focus resources and how to measure success.
A great dashboard does more than just display data—it drives action. By visualizing trends and highlighting critical risks, it helps you move from a reactive to a proactive security posture. You can quickly recognize emerging threats, analyze the effectiveness of your existing security controls, and optimize your defenses before a minor issue becomes a major breach. This is where the dashboard becomes a strategic tool for your entire team.
It helps you prioritize your team's efforts based on what poses the greatest threat to your business, not just what has the highest CVSS score. When integrated into your regular decision-making process, the dashboard aligns your cybersecurity initiatives directly with business objectives. It fosters accountability by making security performance transparent and measurable, ensuring that every action taken is a step toward strengthening your overall resilience.
A great CISO dashboard does more than just display data; it tells a story about your organization's security posture. It should cut through the noise of endless alerts and spreadsheets to give you a clear, actionable picture of your cyber risk. When you're evaluating options or building your own, there are a few non-negotiable features that separate a truly useful dashboard from a simple reporting tool. These capabilities are what transform a dashboard from a passive monitor into an active command center for your entire security program, helping you make smarter, faster decisions.
Your security landscape changes by the minute, and your dashboard needs to keep up. A static, once-a-week report just won’t cut it. You need a real-time overview of your security and compliance status so you can spot critical issues the moment they arise. This means no more digging through different data sources or waiting for a team member to compile a report. An effective dashboard presents the most essential information front and center, allowing you to see your entire attack surface at a glance and immediately identify threats that require your attention. It’s about having a live pulse on your organization's security health.
If your team is chasing every "critical" vulnerability, you're likely burning out without actually reducing risk. A top-tier dashboard helps you move beyond basic severity scores. It should incorporate threat intelligence to highlight which vulnerabilities are actively being exploited in the wild. This approach to vulnerability and threat prioritization allows you to focus on the issues that pose a clear and present danger to your business. By concentrating on the most significant threats first, you can prevent alert fatigue and apply your resources where they’ll have the greatest impact, strategically addressing high-risk exposures instead of just high-severity scores.
A CISO dashboard shouldn't create another data silo. Its real power comes from its ability to act as a central hub, consolidating information from all the different tools in your security ecosystem. Whether it's data from your security monitoring platforms, compliance tools, or IT operations, the dashboard needs to pull it all together. This integration provides a comprehensive, executive-level view of your risk, performance, and overall readiness. A platform that offers a unified view of all your cyber risks in one place is what enables you to make truly informed, data-driven decisions without toggling between a dozen different screens.
Presenting to the board requires you to translate complex security metrics into clear business impact. Your dashboard is your best friend here. It should be able to generate concise, visually compelling reports that resonate with an executive audience. These reports need to go beyond technical jargon and instead focus on key performance indicators, compliance with relevant frameworks, and how your security posture stacks up against industry peers. This feature is vital for strategic discussions, helping you demonstrate the value of your security program and secure the buy-in you need for critical initiatives. It turns your data into a powerful tool for communication.
Let’s be honest: traditional vulnerability management can feel like a never-ending game of whack-a-mole. You patch one issue, and three more pop up. A CISO dashboard changes the game entirely. Instead of just reacting to an endless list of alerts, it gives you the context and clarity to build a truly strategic security program. It helps you see the bigger picture, connect the dots between vulnerabilities, assets, and active threats, and finally get ahead of attackers. This shift transforms your entire approach, moving your team from a constant state of defense to one of confident, proactive control.
A proactive security posture starts with knowing what to focus on. Instead of treating every vulnerability as a top priority, a CISO dashboard helps you pinpoint which issues pose the most significant risk to your business. By correlating threat intelligence with your unique asset inventory, it shows you which parts of your system are most likely to be targeted by attackers. This allows you to move beyond CVSS scores and make smarter decisions with effective vulnerability and threat prioritization . You can allocate your team’s time and resources to the vulnerabilities that matter most, strengthening your defenses where they’re needed and preventing incidents before they happen.
When a security incident occurs, every second counts. A CISO dashboard brings order to the chaos by providing a single source of truth for your response team. It offers real-time visibility into active incidents, clearly distinguishing high-priority threats from lower-level noise so your team can focus their efforts immediately. The dashboard can also track key metrics like how long it takes to resolve issues, helping you measure and improve your response processes over time. Some platforms even provide recommended actions, guiding your team with clear, actionable steps to contain threats and remediate vulnerabilities faster. This clarity ensures a coordinated, efficient response that minimizes damage and downtime.
Preparing for an audit can be a stressful, time-consuming process of gathering data from dozens of different tools. A CISO dashboard simplifies this by consolidating all your security and compliance information in one place. It gives you a continuous, real-time view of your compliance posture against frameworks like NIST, ISO, or PCI DSS. The dashboard can also maintain a complete inventory of your IT assets through total attack surface management , ensuring you have a comprehensive picture for auditors. Instead of scrambling for reports, you can confidently demonstrate due diligence and show exactly how security issues are being identified and resolved. This turns audit preparation from a frantic, periodic event into a calm, everyday state of readiness.
A great dashboard isn't just a collection of charts; it's a story about your security program's health and effectiveness. The right metrics cut through the noise, turning raw data into clear, actionable insights that guide your strategy and prove your team's value. Tracking the right key performance indicators (KPIs) helps you communicate risk to the board, justify security investments, and make smarter, faster decisions. It’s about focusing on the data points that truly reflect your security posture and your ability to defend against real-world threats. These metrics should give you an at-a-glance understanding of where you stand, where you’re going, and what needs your immediate attention. A well-designed dashboard provides a unified view of your cyber risks, helping you focus on the imminent threats that matter most instead of getting lost in a sea of alerts. It transforms security from a reactive guessing game into a confident, data-driven operation, ensuring your team's efforts are aligned with the organization's most critical business objectives.
5. Performance Evaluation & Extended Technical Observations This is a foundational metric, but its value goes beyond a simple number. Tracking your critical vulnerability count shows your immediate risk level, but monitoring the trend over time is what really tells the story. Is the number going down? Are you patching faster than new critical vulnerabilities are discovered? This data helps you understand the effectiveness of your vulnerability management program and prioritize remediation efforts where they matter most. A dashboard that clearly visualizes this trend allows you to see if your strategies are working and helps you allocate resources to address the most significant risks before they can be exploited. It’s the first step in moving toward proactive vulnerability and threat prioritization .
How quickly can your team neutralize a threat? That’s the question MTTD and MTTR answer. These metrics are a direct reflection of your incident response team's efficiency and the effectiveness of your security tools. Mean Time to Detect (MTTD) measures the time it takes to discover a potential security threat, while Mean Time to Remediate (MTTR) tracks how long it takes to fix it. A consistently low MTTR demonstrates a mature, well-oiled security operation. Your CISO dashboard should display these metrics prominently, as they are crucial for assessing your team’s readiness and identifying bottlenecks in your response processes. They provide a clear measure of your ability to recover from an incident.
You can't protect what you can't see. This metric is all about visibility. It answers a critical question: How much of our digital environment is actually being monitored for threats? Your dashboard should clearly show your attack surface coverage, highlighting any unmonitored assets, shadow IT, or other exposure gaps. Understanding these blind spots is essential for proactive risk management and preventing attackers from finding an unguarded entry point. By tracking this KPI, you can make a compelling case for the resources needed to achieve Total Attack Surface Management and ensure your defenses are comprehensive, leaving no part of your organization vulnerable.
Static vulnerability data isn't enough. To truly understand your risk, you need context. This is where integrating threat intelligence and breach simulation data becomes a game-changer. Your dashboard should show which vulnerabilities are actively being exploited in the wild, allowing you to prioritize threats that pose an immediate danger. Insights from breach and attack simulations test whether your security controls are actually working as intended against real-world attack scenarios.
This approach to adversarial exposure validation helps you analyze the efficacy of your security configurations and optimize your defenses based on proven performance, not just assumptions. The data in your security stack is only as good as your ability to understand it. A massive spreadsheet of vulnerabilities is just noise, but the right visualization can turn that noise into a clear signal. A great CISO dashboard doesn't just present data; it tells a story, guiding you toward the most critical issues and helping you make faster, more confident decisions. The goal is to see the big picture at a glance without losing the details that matter. When you can clearly see where your risks lie, you can allocate resources more effectively and build a stronger security posture.
Effective visuals transform complex security metrics into straightforward, actionable insights. They help you quickly identify patterns, communicate risk to non-technical stakeholders, and prove the value of your security investments. This is where a dashboard becomes more than just a reporting tool—it becomes a communication bridge between your security team and the boardroom. Instead of getting lost in the weeds of technical jargon, you can present a clear, compelling picture of the organization's risk landscape. This visual approach is key to moving from simply managing vulnerabilities to truly managing your threat exposure and making strategic, data-backed decisions that protect the entire organization.
Imagine trying to find the most critical asset in a list of thousands. A heat map makes this simple. By using color gradients—like red for high-risk and green for low-risk—heat maps give you an immediate visual summary of your entire attack surface . You can instantly see which business units, applications, or geographic locations are most exposed. This allows you to move beyond raw vulnerability counts and see risk in the context of your business. A well-designed dashboard helps you recognize critical risks and vulnerabilities, enabling you to direct your remediation resources to the areas that pose the greatest threat to your organization.
Are your security efforts actually working? Charts and graphs are the best way to answer that question. Line charts can track your mean time to remediate (MTTR) over months, while bar charts can compare vulnerability counts across different departments. These visuals are essential for identifying patterns and measuring progress against your key performance indicators (KPIs). This historical context is crucial for strategic planning and for communicating your team’s performance to the board. A dashboard that simplifies the tracking of these KPIs makes it much easier to demonstrate business value and secure the resources you need to strengthen your defenses.
In cybersecurity, timing is everything. You can’t afford to wait for a weekly report to learn about a critical threat. Real-time alerts and dynamic widgets on your dashboard act as an early warning system, notifying you of emerging threats, newly discovered high-severity vulnerabilities, or unusual activity on your network the moment it happens. This allows your team to shift from a reactive to a proactive stance. With real-time information and context , you can transform how you report on cybersecurity to leadership, especially during a potential incident. It provides the immediate awareness needed to contain threats before they cause significant damage.
A great CISO dashboard is more than just a collection of charts; it’s a strategic tool that can transform your security program. But getting there isn’t always a straight line. Implementation comes with its own set of challenges, from wrangling data to getting your team on board. The good news is that these hurdles are common, and with the right approach, you can clear them easily. Let’s walk through how to solve the most frequent implementation roadblocks so you can build a dashboard that delivers real value from day one.
Your security stack is likely a mix of different tools, each with its own data and reporting. The first hurdle is getting them all to talk to each other. A powerful CISO dashboard acts as a central hub, pulling in data from your security monitoring, compliance platforms, and IT operations tools. The goal is to create a single, unified view of your security posture. Without seamless integration, you’ll spend more time wrangling data than analyzing it. A platform that offers a unified view of cyber risks is essential for breaking down these data silos and getting a clear, complete picture of your environment.
It’s easy to get lost in a sea of alerts and vulnerability counts. The real challenge is moving beyond simple counts and severities to a risk-based narrative that tells you what actually matters. Point-in-time reports often lack the context needed to prioritize vulnerabilities effectively . Your dashboard shouldn't just show you that you have vulnerabilities; it should show you which ones pose a genuine threat to your business. This means focusing on vulnerabilities that are actively exploited or are on critical assets. A great dashboard cuts through the noise, helping you focus your team’s limited time and resources on the risks that require immediate attention.
A dashboard can have all the data in the world, but if it’s clunky or confusing, your team won’t use it. Adoption is everything. A great user experience is non-negotiable. Your dashboard should make it easy to pull data from multiple systems into a single trusted view and present metrics in clear, executive-friendly formats. When the interface is intuitive and the data is updated in real-time, the dashboard becomes a strategic tool that your entire team relies on. It stops being "just another screen" and becomes the central point for aligning security efforts with business objectives, strengthening accountability across the organization.
Communicating cyber risk to the board can feel like speaking a different language. A CISO dashboard is your translator. It turns complex security metrics into clear visualizations that demonstrate business impact. You can use it to track KPIs, share insights on your security posture, and lead conversations about where investment is needed most. When you can clearly show how security initiatives reduce business risk, you’re no longer just talking about technical details; you’re talking about protecting the bottom line. This makes your dashboard a critical guide for CISO board presentations and helps secure the buy-in you need to move your security program forward.
A CISO dashboard is more than just a collection of charts; it’s a strategic tool that should tell you a story about your security posture. But without the right context, that story can be misleading. Simply tracking the number of vulnerabilities is like counting the number of doors in a fortress without knowing which ones are unlocked or which ones attackers are actively trying to pick. This is where threat intelligence and breach simulation come in. They provide the critical context needed to move from simply managing vulnerabilities to actively managing your threat exposure.
By integrating real-world threat data and continuously testing your defenses, you can transform your dashboard from a passive reporting tool into an active command center. It allows you to see your organization through an attacker's eyes, understanding not just where your weaknesses are, but which ones are most likely to be exploited. This intelligence, sourced from expert teams like HiveForce Labs , helps you answer the most important questions: What are attackers doing right now? Are our security controls prepared to stop them? And where should we focus our limited resources for the biggest impact? This approach ensures your security efforts are always aligned with the current threat landscape, not just a generic list of best practices.
Let's be honest, your team is probably drowning in vulnerability alerts. Trying to patch everything at once is a recipe for burnout and inefficiency. The key is to focus on what truly matters. High-quality threat intelligence helps you cut through the noise by identifying which vulnerabilities are being actively exploited in the wild. A great CISO dashboard visualizes this by using a priority rating that goes beyond a simple CVSS score. It highlights the weaknesses that pose an immediate and credible threat to your organization. This allows your team to stop chasing every single alert and instead concentrate their efforts on the vulnerabilities that attackers are using today, dramatically reducing your real-world risk.
Having security controls in place is one thing, but knowing they’ll work under pressure is another. This is where Breach and Attack Simulation (BAS) becomes a game-changer. BAS platforms continuously and safely simulate real-world attack techniques against your security infrastructure. Think of it as a fire drill for your cyber defenses. Your CISO dashboard should display the results of these simulations, showing you exactly where your controls held up and where they failed. This provides concrete evidence of your security efficacy, helping you validate your adversarial exposure and make data-driven decisions to strengthen weak points before an actual attacker finds them.
When you combine threat intelligence with BAS insights, your remediation strategy becomes incredibly focused and effective. You know which vulnerabilities are being targeted and you know if your current defenses can stop those attacks. A CISO dashboard should bring this information together to guide your remediation efforts. Instead of just giving you a list of problems, it should highlight the most efficient path to fixing the highest-priority exposures. This helps your team focus on the fixes that will have the greatest impact on your security posture. By using a unified platform , you can ensure your resources are spent on closing the gaps that matter most, not just the ones that are easiest to find.
A CISO dashboard is more than just a collection of charts and graphs; it’s a strategic asset that can transform how your organization views and manages security. But simply having a dashboard isn’t enough. To make it truly effective, you need to treat it as a dynamic tool for communication, decision-making, and continuous improvement. It’s about turning raw data into a clear story that resonates with everyone from your security analysts to the board of directors. By focusing on alignment, optimization, and proving value, you can ensure your dashboard becomes an indispensable part of your security program.
This means moving beyond a "set it and forget it" mentality. The most powerful dashboards are living, breathing resources that evolve with your organization and the threat landscape. They provide the clarity needed to not only identify critical risks but also to analyze the effectiveness of your security controls and optimize your defenses. When your dashboard is woven into the fabric of executive decision-making, it stops being a simple reporting tool and becomes a cornerstone of your strategy, aligning cybersecurity with core business objectives and strengthening accountability across the entire organization.
A great dashboard starts with great conversations. Before you even think about which widgets to use, you need to understand what your stakeholders actually want to see. The metrics that matter to your board are very different from the granular data your SOC team needs. Your goal is to create a centralized view that gives leaders confidence in your security posture while providing your team with the actionable insights they need to do their jobs.
Start by defining clear requirements. Sit down with executives, department heads, and your security team to identify the key performance indicators (KPIs) that demonstrate business value. This alignment is crucial. When your dashboard clearly communicates how security efforts are protecting the business, it becomes much easier to secure the resources you need to strengthen defenses and meet compliance goals. Don’t build a dashboard in a silo; build it as a collaborative tool that answers the most important questions for each audience.
Think of your dashboard as a garden, not a statue. It requires regular attention to stay relevant and useful. The threat landscape is constantly changing, and your business priorities will shift over time. Your dashboard needs to reflect these changes. Schedule regular reviews—quarterly is a good starting point—to assess what’s working, what’s not, and what new information needs to be included.
A well-designed dashboard helps you move through a cycle of continuous improvement: you recognize critical risks and vulnerabilities, analyze the effectiveness of your security configurations, and optimize your defenses based on what you’ve learned. This process turns your dashboard from a passive reporting tool into an active defense mechanism. By integrating a comprehensive solution like the Uni5 Xposure Platform , you can feed your dashboard with the real-time, unified data needed to keep your view sharp and your strategy effective.
Ultimately, your CISO dashboard needs to answer one critical question: "Is our security investment paying off?" This is where you connect security metrics to business value. The dashboard is your primary tool for board presentations, providing a centralized guide to your organization's cyber risk posture, threat landscape, and compliance status. It’s how you demonstrate the return on investment (ROI) for your security program.
To do this, focus on tracking the right cybersecurity KPIs . These are the specific metrics that measure the effectiveness of your defenses and your team’s preparedness. Instead of just showing the number of vulnerabilities, show the trend line decreasing over time. Highlight improvements in your Mean Time to Remediate (MTTR) for critical threats. By visualizing these outcomes, you can clearly demonstrate how your team’s efforts are reducing risk and protecting the bottom line.
How is a CISO dashboard different from the dashboards already in my other security tools? Think of it this way: your individual security tools each give you a detailed view of one part of the puzzle, like your network traffic or endpoint alerts. A CISO dashboard is what pulls all those puzzle pieces together to show you the complete picture. It integrates data from across your entire security stack to provide a single, unified view of your risk. This allows you to see how a vulnerability on a critical server connects to a threat that your intelligence feed is tracking, giving you the full story instead of just isolated facts.
My team is already overwhelmed with data. Won't a dashboard just add to the noise? It’s a fair question, but a great dashboard is designed to do the exact opposite. Its primary job isn't to show you more data, but to show you the right data by filtering out the noise. By correlating information about your assets with real-world threat intelligence, it highlights the handful of issues that pose a genuine, immediate threat to your business. It transforms that overwhelming flood of alerts into a clear, prioritized action plan for your team.
You mention prioritizing by risk, not just severity. What does that actually mean in practice? A severity score, like a CVSS rating, tells you how dangerous a vulnerability could be in a theoretical, worst-case scenario. A risk-based approach tells you how likely that scenario is to actually happen to you. It adds critical context, answering questions like, "Are attackers actively exploiting this vulnerability right now?" and "Does this vulnerability exist on a system that’s essential to our business?" This focus helps you address clear and present dangers first, rather than spending resources on problems that are only theoretical.
What's the most effective way to use a dashboard to communicate with the board? The goal is to tell a clear story about progress and business impact. Instead of getting bogged down in the total number of vulnerabilities, use trend charts to show how your team is consistently reducing the number of critical risks over time. Metrics like Mean Time to Remediate (MTTR) are also incredibly powerful because they demonstrate your team's efficiency and resilience in a way anyone can understand.
These visuals prove the value of your security program and show that their investment is paying off. I'm convinced I need one, but where do I even start? The best place to start is with people, not platforms. Before you look at any technology, have conversations with your key stakeholders, from the executive team down to your security analysts. Your goal is to understand what questions they need answered to feel confident about the organization's security posture. Defining these requirements first ensures that you build or buy a dashboard that solves real business problems and provides genuine value from day one.
Let's be direct: a high CVSS score doesn't mean a vulnerability is a top priority for your organization. Attackers don't care about theoretical scores; they care about clear, exploitable pathways to your critical assets. If your vulnerability management dashboard is only showing you generic severity ratings, it's not giving you the full picture. You're missing the crucial context of which vulnerabilities are actively being used in attacks right now and whether your existing security controls would stop them.
By enriching your dashboard with threat intelligence and using Breach and Attack Simulation (BAS) to validate your exposures, you can finally start prioritizing threats based on actual, measurable risk to your business, not just a number. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Network%20management%20software • https://en.wikipedia.org/wiki/WordPress • https://en.wikipedia.org/wiki/Real-time%20adaptive%20security • https://learn.microsoft.com/en-us/defender-vulnerability-management/tvm-dashboard-insights • https://learn.microsoft.com/en-us/defender-vulnerability-management/ • https://www.watsecurity.com/p/effective-vulnerability-dashboarding • https://github.com/NullSpace-BitCradle/Vuln_Mgmt_Dashboards • https://www.rootshellsecurity.net/vulnerability-management-dashboard/ • https://www.hivepro.com/blog/ultimate-ciso-dashboard-guide • https://www.hivepro.com/blog/vulnerability-management-dashboard-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Vulnerability Management Dashboard.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Vulnerability Management Dashboard... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |