Complete Technical Paper Content — Wear Os Smartwatch Security Analysis And Data Leakage
Overview & System Context
Wear Os Smartwatch Security Analysis And Data Leakage: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8654 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background HarmonyOS (HMOS) (Chinese: IIIIII; pinyin: Hóngméng CIozuò XìtIng; trans. "Vast Mist") is a distributed operating system developed by Huawei for smartphones, tablets, smart TVs, smart watches, personal computers and other smart devices. It has a microkernel design with a single framework: the operating system selects suitable kernels from the abstraction layer in the case of devices that use diverse resources. The latest stable version is HarmonyOS 6; it was released on 25 November 2025. From 2019 to 2024, versions 1 to 4.3 (4.5 TV) of the operating system were built by integrating the Android Open Source Project (AOSP) with OpenHarmony, allowing it to support both HarmonyOS and Android apps. The current iteration of HarmonyOS became known as HarmonyOS NEXT (later it was renamed HarmonyOS 5 in launched of Pura X). HarmonyOS NEXT was announced on August 4, 2023, and officially launched on October 22, 2024. It also replaced the OpenHarmony multi-kernel system with its own HongMeng Kernel at its core and removed all Android code. Since version 5, HarmonyOS only supports apps in its native "App" format. HarmonyOS 5.x+ both discards the common Unix-like Linux kernel and replaces the previous multiple-kernel, kernel agnostic system from OpenHarmony with its own bespoke HarmonyOS microkernel as a single framework. HarmonyOS was officially launched by Huawei, and first used in Honor smart TVs, in August 2019. It was later used in Huawei wireless routers, IoT in 2020, followed by smartphones, tablets and smartwatches from June 2021. In May 2025, the first notebook with HarmonyOS was launched by Huawei, featuring "HarmonyOS PC", i.e. HarmonyOS 5 for the personal computer form factor. On November 19, 2025, the first 2-in-1 with HarmonyOS 5.1 was launched by Huawei, with MatePad Edge supporting both tablet mode and full desktop counterpart in line with Huawei MateBook PC line.
On 9 August 2019, three months after the Entity List ban, Huawei publicly unveiled HarmonyOS, which Huawei said it had been working on since 2012, at its inaugural developers' conference in Dongguan. Huawei described HarmonyOS as a free, microkernel-based distributed operating system for various types of hardware. The company focused primarily on IoT devices, including smart TVs, wearable devices, and in-car entertainment systems, and did not explicitly position HarmonyOS as a mobile OS. HarmonyOS 2.0 launched at the Huawei Developer Conference on 10 September 2020. Huawei announced it intended to ship the operating system on its smartphones in 2021. The first developer beta of HarmonyOS 2.0 was launched on 16 December 2020. Huawei also released the DevEco Studio IDE, which is based on IntelliJ IDEA, and a cloud emulator for developers in early access. Huawei officially released HarmonyOS 2.0 and launched new devices shipping with the OS in June 2021, and started rolling out system upgrades to Huawei's older phones for users gradually. On July 27, 2022, Huawei launched HarmonyOS 3, providing an improved experience across multiple devices such as smartphones, tablets, printers, cars and TVs. It also launched Petal Chuxing, a ride-hailing app running on the new version of the operating system. On 29 June 2023, Huawei launched the first developer beta of HarmonyOS 4. On 4 August 2023, Huawei officially announced and released HarmonyOS 4 as a public beta. On 9 August, it rolled the operating system out on 34 different existing Huawei smartphone and tablet devices—albeit as a public beta build. Alongside HarmonyOS 4, Huawei also announced the launch of HarmonyOS NEXT, which is a "pure" HarmonyOS version, without Android libraries and therefore incompatible with Android apps post-software convergence. On 18 January 2024, Huawei announced commercialisation of HarmonyOS NEXT with a Galaxy stable version rollout beginning in Q4 2024 based on OpenHarmony 5.0 (API 12) version after OpenHarmony 4.1 (API 11) based Q2 Developer Beta after release of public developer access of HarmonyOS NEXT Developer Preview 1 that has been in the hands of closed cooperative developers partners since August 2023 debut. The new system of upcoming HarmonyOS 5 version that replaced HarmonyOS multi-kernel dual-frame system convergence for unified system stack of the unified app ecosystem for commercial Huawei consumer devices. On March 11, 2024, Huawei announced the early recruitment for the new test experience version of Huawei HarmonyOS 4 firmware update, which included improvements to performance and user experiences. HarmonyOS version 4.0.0.200 (C00E200R2P7) of the firmware was gradually rolled out on March 12, 2024. On April 11, 2024, it was reported that Huawei opened the registration and rolled out the public beta of HarmonyOS 4.2 for 24 devices. On the same day, the company announced its incoming HarmonyOS 5.0 operating system version of Galaxy Edition version under the HarmonyOS NEXT system, which would first be released as an open beta program for developers and users at its annual Huawei Developer Conference in June 2024. The commercial consumer release with upcoming other devices, like the Mate 70 flagship, would follow in Q4. On April 18, 2024, Huawei Pura 70 flagship series lineup received the HarmonyOS 4.2.0.137 update, after release. On April 17, 2024, Huawei's chairman Eric Xu revealed plans to push the native HarmonyOS NEXT system for next gen HarmonyOS in global markets as the company's focus at Huawei's Analyst Summit 2024 (HAS 2024) to the Chinese and international press. On May 17, 2024, during the HarmonyOS Developer Day (HDD) event, Huawei announced a HarmonyOS upgrade with the new HarmonyOS NEXT base beginning commercial use by September with over 800 million devices and 4,000 apps in use. A total of 5,000 apps was targeted for launch. On June 21, 2024, during the Huawei Developer Conference (HDC) keynote, Huawei announced HarmonyOS NEXT Developer Beta for registered developers and 3,000 pioneer users on limited models such as the Huawei Mate 60 Series, Huawei Mate X5 Series and Huawei MatePad Pro 13.2 tablet. The consumer beta version was expected to be released in August 2024, while the stable build would be made available in Q4 2024. During the conference, Huawei formally announced the in-house Cangjie programming language for the new native system, alongside the release of the Developer Preview Beta recruitment program. On October 22, 2024, at the Huawei HarmonyOS Next event, it was officially revealed as "Native" HarmonyOS NEXT brand transitioning to HarmonyOS 5, incorporated as HarmonyOS 5.0.0 version, for public beta with 2025 expansions. Ahead of flagship devices with stable builds factory on November 26, 2024. Subsequent HarmonyOS NEXT releases of HarmonyOS 5 iterations, starting with version 5.0.1, launched on May 19, 2025, with the MateBook Pro and Fold PCs launch after the Huawei Pura X, the first phone to launch with full pre-installation of HarmonyOS 5 on March 20, 2025. The beta program was also launched for 14 devices. On July 23, 2025, Huawei launched HarmonyOS 5.1 for 30+ compatible devices after the launch of Huawei Watch 5 on May 16, 2025, and the Pura 80 series on June 11, 2025. On October 22, 2025, Huawei announced HarmonyOS 6 with consumer beta launch after releasing Developer Beta builds since June 20, 2025 at HDC 2025. The Mate 80 series, alongside Mate X7 devices, became the first to launch with HarmonyOS 6 preinstalled on November 25, 2025, with official stable version rollout on eligible models such as the Mate 70 series on the same day in mainland China's markets.
For HarmonyOS computer system side powered with Kirin X series silicon custom AArch64 PC chips, there is a virtual machine application on HarmonyOS called Oseasy and KaiMaster/Armor Master built on Huawei's openEuler virtualisation technology stack StratoVirt that enables users to run Windows 11 ARM in a virtual environment on Huawei MateBook PCs and MatePad Edge.
HiSH, Harmonix, Termony third-party console applications by open source HarmonyOS developer community based on harmony-qemu FOSS project built for pure single framework OpenHarmony-based HarmonyOS platform that supports QEMU virtualization adaptations natively that can enable users to run full Linux console applications and commands alongside the integration of HarmonyOS computer's default HiShell system terminal.
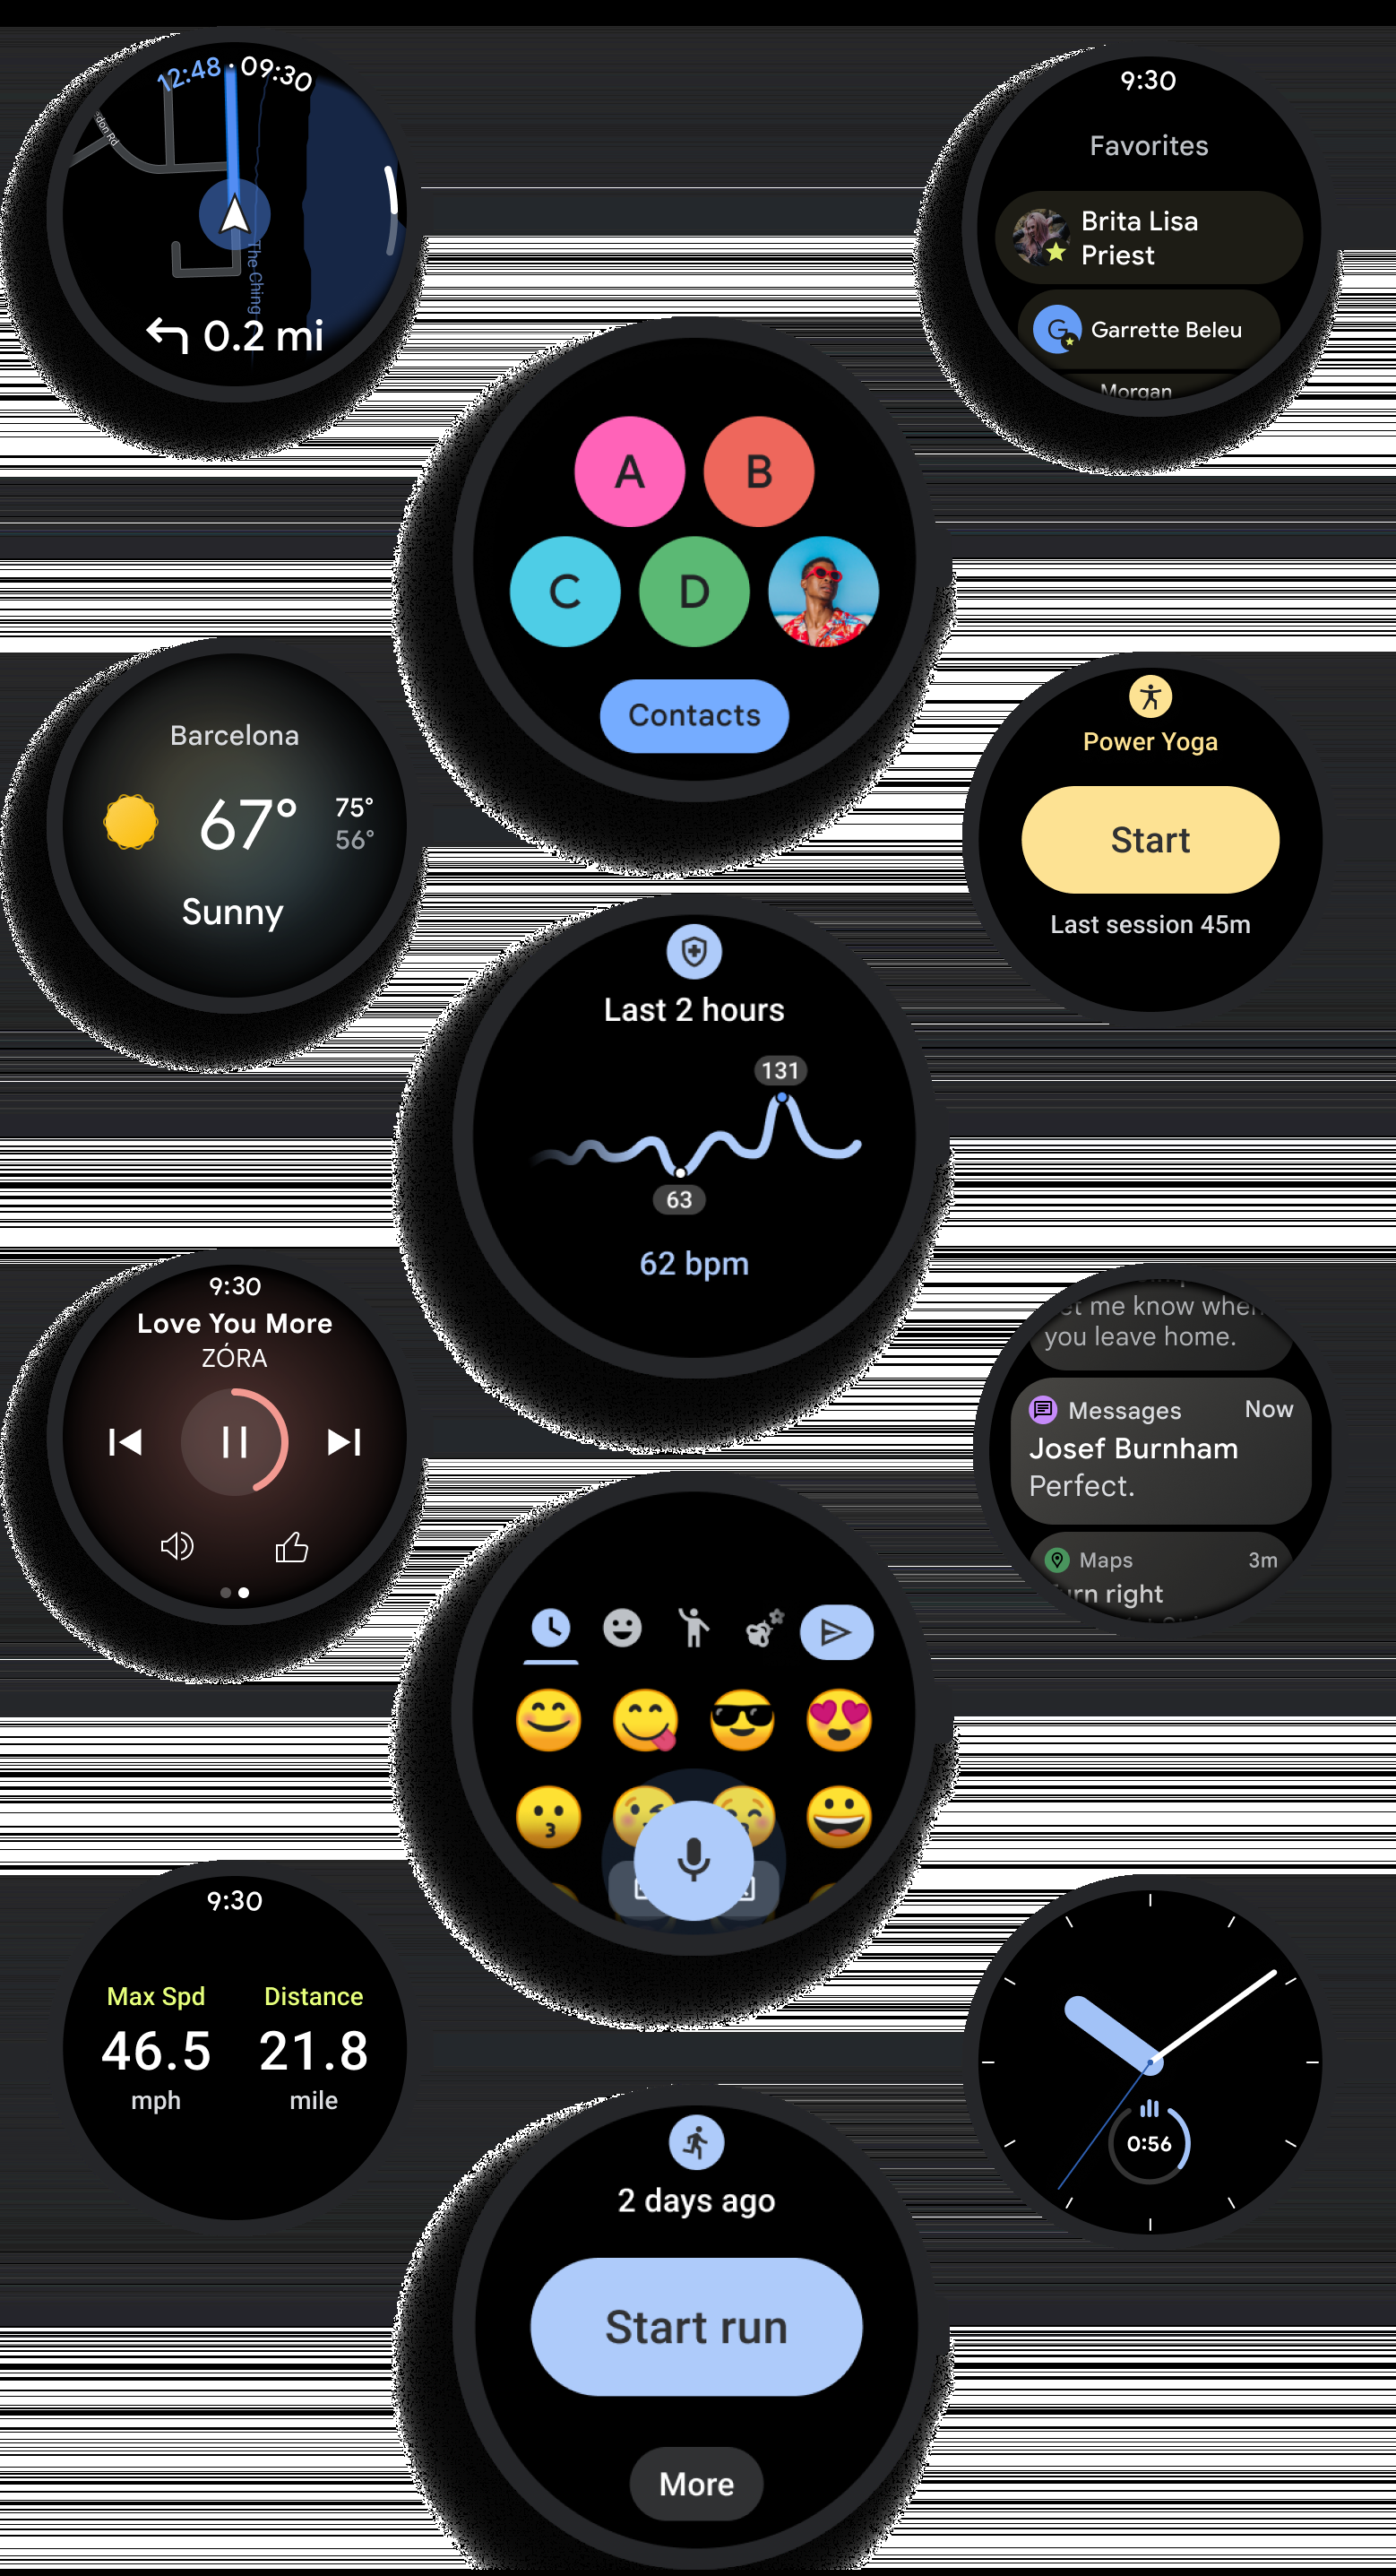
Figure 1: Wear | UI Design | Android Developers Huawei stated that HarmonyOS would initially be used on devices targeting the Chinese market. The company's former subsidiary brand, Honor, unveiled the Honor Vision line of smart TVs as the first consumer electronics devices to run HarmonyOS in August 2019. The HarmonyOS 2.0 beta launched on 16 December 2020 and supported the P30 series, P40 series, Mate 30 series, Mate 40 series, P50 series, and the MatePad Pro. Stable HarmonyOS 2.0 was released for smartphones and tablets as updates for the P40 and Mate X2 in June 2021. New Huawei Watch, MatePad Pro and PixLab X1 desktop printer models shipping with HarmonyOS were also unveiled at the time. In October 2021, HarmonyOS 2.0 had over 150 million users. On November 25, 2025, at a Huawei press conference for the Mate 80 series and Mate X7 flagship products, it was announced that devices running HarmonyOS 5 and HarmonyOS 6 has passed 27 million in activations altogether with an install base growing at 100,000 per day.
When it launched the operating system, Huawei stated that HarmonyOS plans to become a microkernel-based, distributed OS that was completely different from Android and iOS in terms of target market towards Internet of things. A Huawei spokesperson subsequently stated that HarmonyOS supported multiple kernels and used a Linux kernel if a device had a large amount of RAM, and that the company had taken advantage of a large number of third-party open-source resources, including Linux kernel with POSIX-like APIs on OpenHarmony base, as a foundation to accelerate the development of its unified system stack as a future-proof, microkernel-based, and distributed OS running on multiple devices. At its launch as an operating system for smartphones in 2021, HarmonyOS was, however, rumored by Ars Technica to be a "rebranded version of Android and EMUI" with nearly "identical code bases". Following the release of the HarmonyOS 2.0 beta, Ars Technica and XDA Developers suggested that "the smartphone version of the OS had been forked from Android 10". Ars Technica alleged that it resembled the existing EMUI software used on Huawei devices, but with all references to "Android" replaced by "HarmonyOS". It was also noted that the DevEco Studio software based on JetBrains open source IntelliJ IDEA IDE "shared components and tool chains" with Android Studio. When testing the new MatePad Pro in June 2021, Android Authority and The Verge similarly observed similarities in "behavior", including that it was possible to install apps from Android APK files on the HarmonyOS-based tablet, and to run the Android 10 easter egg apk app, reaffirming earlier rumor mills. In December 2022, some Chinese users discovered that, after switching the language to English in HarmonyOS 3.0, the "System" app would display as "Android System," which once again sparked controversy. Huawei subsequently released an urgent patch to remove the reference to Android.
In terms of architecture, HarmonyOS has close relationship with OpenEuler, which is a community edition of EulerOS, as they have implemented the sharing of kernel technology as revealed by Deng Taihua, President of Huawei's Computing Product Line. The sharing is reportedly to be strengthened in the future in the areas of the distributed software bus, system security, app framework, device driver framework and new programming language.
OpenHarmony is an open-source version of HarmonyOS donated by Huawei to the OpenAtom Foundation, built around its unique multiple-kernel architecture of the distributed operating system, sharing some principles from Huawei LiteOS lineage. It supports devices running a mini system such as printers, speakers, smartwatches and any other smart device with memory as small as 128 KB, or running a standard system with memory greater than 128 MB. The open-source operating system contains the basic capabilities of HarmonyOS and does not depend on the Android Open Source Project (AOSP) code.
Figure 2: Wearables Library On August 4, 2023, at Huawei Developers Conference 2023 (HDC), Huawei officially announced HarmonyOS NEXT (HarmonyOS 5), the next iteration system version of HarmonyOS, supporting only native APP apps via Ark Compiler, and ending the support for Android apk apps. Built on a custom version of OpenHarmony, HarmonyOS NEXT proprietary system has the HarmonyOS microkernel at its core with a single framework currently since HarmonyOS 5 version and up, departing from the common Linux kernel and replaced multi-kernel HarmonyOS. Among the first batch of over 200 developers, McDonald's and KFC in China became two of the first multinational food companies to adopt HarmonyOS Next.
The @ohos.router routing library implements page transitions, which must be declared in the main_pages.json file before being invoked. Effective in 2026, to align with our trunk stable development model and ensure platform stability for the ecosystem, we will publish source code to AOSP in Q2 and Q4. For building and contributing to AOSP, use android-latest-release . The android-latest-release manifest branch will always reference the most recent release pushed to AOSP. For more information, see Changes to AOSP .
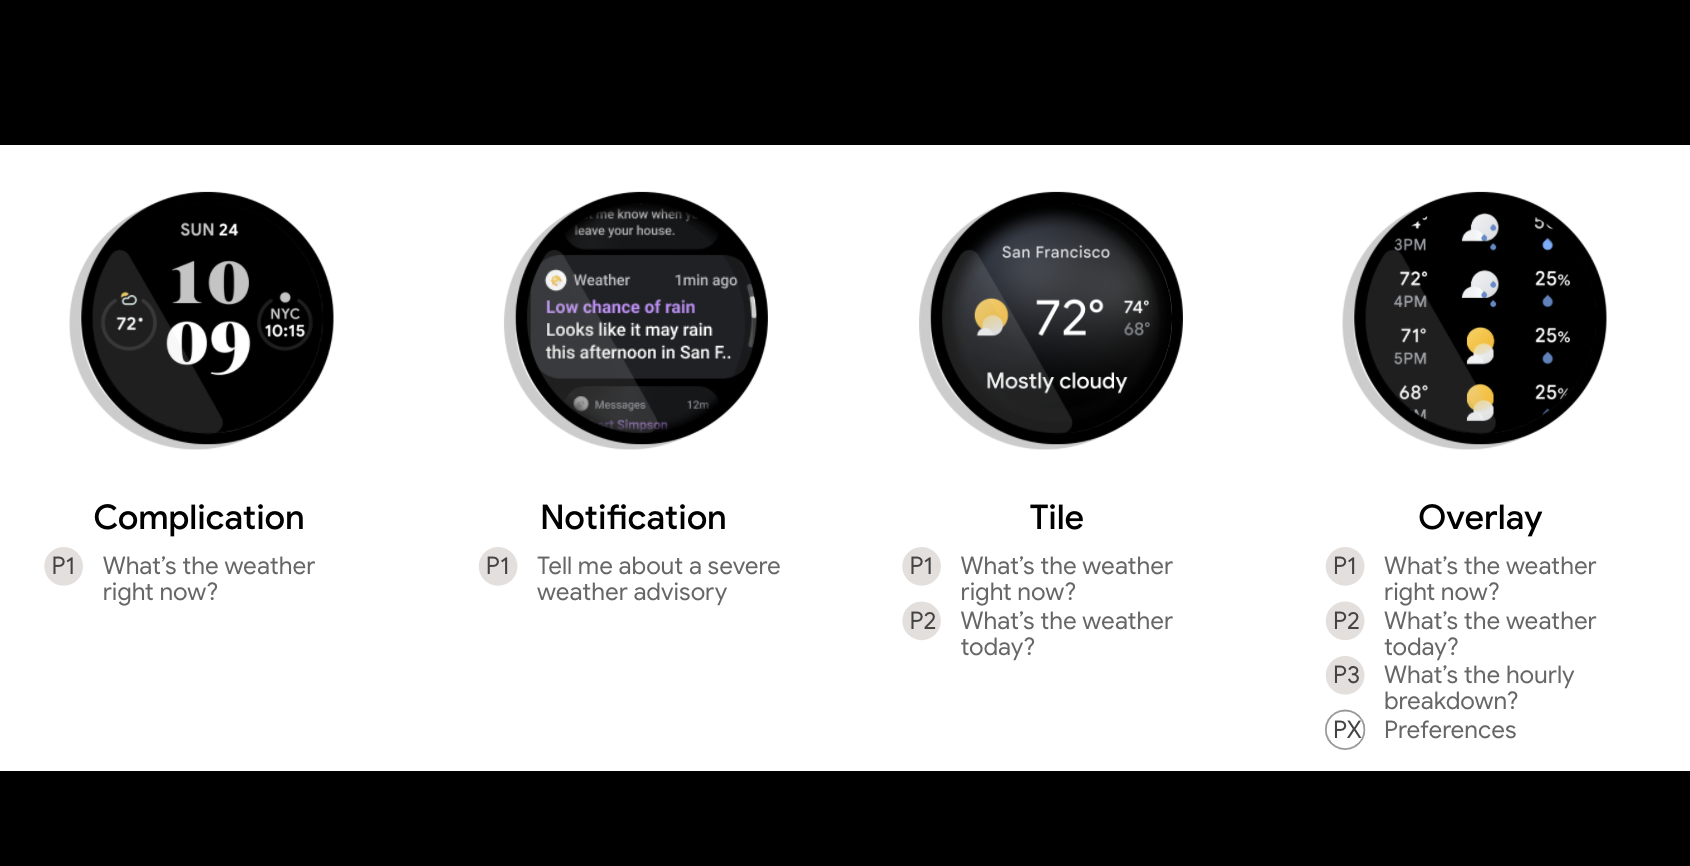
The Wear OS Security Bulletin contains details of security vulnerabilities affecting the Wear OS platform. The full Wear OS update comprises the security patch level of 2026-09-05 or later from the September 2026 Android Security Bulletin in addition to all issues in this bulletin. Figure 3: Wear OS user interfaces | Android Developers The most severe of these issues is a high security vulnerability in the System component that could lead to local escalation of privilege with no additional execution privileges needed. User interaction is needed for exploitation. The severity assessment is based on the effect that exploiting the vulnerability would possibly have on an affected device, assuming the platform and service mitigations are turned off for development purposes or if successfully bypassed.
In the sections below, we provide details for each of the security vulnerabilities that apply to the 2026-09-01 patch level. Vulnerabilities are grouped under the component they affect. Issues are described in the tables below and include CVE ID, associated references, type of vulnerability , severity , and updated AOSP versions (where applicable). When available, we link the public change that addressed the issue to the bug ID, like the AOSP change list. When multiple changes relate to a single bug, additional references are linked to numbers following the bug ID. Devices with Android 10 and later may receive security updates as well as Google Play system updates .
The vulnerability in this section could lead to local information disclosure with no additional execution privileges needed. User interaction is not needed for exploitation. The vulnerability in this section could lead to local escalation of privilege with no additional execution privileges needed. User interaction is needed for exploitation.
To learn how to check a device's security patch level, read the instructions on the Google device update schedule . For some devices on Android 10 or later, the Google Play system update will have a date string that matches the 2026-09-01 security patch level. Please see this article for more details on how to install security updates. 2. System Architecture & Core Working Principles Entries in the Type column of the vulnerability details table reference the classification of the security vulnerability.
Entries under the References column of the vulnerability details table may contain a prefix identifying the organization to which the reference value belongs. Issues that are not publicly available have an * next to the corresponding reference ID. The update for that issue is generally contained in the latest binary drivers for Pixel devices available from the Google Developer site .
5. Why are security vulnerabilities split between this bulletin and device / partner security bulletins, such as the Pixel bulletin? Security vulnerabilities that are documented in this security bulletin are required to declare the latest security patch level on Android devices. Additional security vulnerabilities that are documented in the device / partner security bulletins are not required for declaring a security patch level. Android device and chipset manufacturers may also publish security vulnerability details specific to their products, such as Google , Huawei , LGE , Motorola , Nokia , or Samsung .
Content and code samples on this page are subject to the licenses described in the Content License . Java and OpenJDK are trademarks or registered trademarks of Oracle and/or its affiliates. Official websites use .gov A .gov website belongs to an official government organization in the United States. Secure .gov websites use HTTPS A lock ( ) or https:// means you've safely connected to the .gov website. Share sensitive information only on official, secure websites.
Received 2023 Mar 11; Revised 2023 May 14; Accepted 2023 Jun 5; Collection date 2023 Jun. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Wearable devices are starting to gain popularity, which means that a large portion of the population is starting to acquire these products. This kind of technology comes with a lot of advantages, as it simplifies different tasks people do daily. However, as they recollect sensitive data, they are starting to be targets for cybercriminals. The number of attacks on wearable devices forces manufacturers to improve the security of these devices to protect them. Many vulnerabilities have appeared in communication protocols, specifically Bluetooth. We focus on understanding the Bluetooth protocol and what countermeasures have been applied during their updated versions to solve the most common security problems. We have performed a passive attack on six different smartwatches to discover their vulnerabilities during the pairing process.
Furthermore, we have developed a proposal of requirements needed for maximum security of wearable devices, as well as the minimum requirements needed to have a secure pairing process between two devices via Bluetooth. Keywords: Bluetooth, BLE, cybersecurity, secure connections, smartwatch, sniffer, wearable Internet of Things technologies are evolving and taking part in our daily routines without us even noticing [ 1 ]. The continuous growth and acceptance of these devices are going out of proportion, as the new normal shows a person owning multiple IoT devices. It is projected that by the year 2025, there will be over 75 billion connected devices [ 2 ]. Furthermore, just five years later, by 2030, it is expected that there will be 124 billion IoT devices [ 3 ].
IoT reaches different scopes; they can be medicine, education, industry, entertainment, sports, clothes, smart cities, agriculture, and many others. See Figure 1 . Technology recollects a big amount of data, including personal information, routines, and health records, to simplify the diverse tasks that we accomplish daily. However, having that great collection of records could be counterproductive, if someone else uses it to gain something. This opens the door for cybercriminals, who understand the value of these types of sensitive data.
IoT device cyberattacks are deemed to be of high risk, particularly when handling people’s health data, as they can lead to physical harm and endanger lives. Vulnerabilities not only impact device functionality, but also people’s health [ 4 ]. These devices are anticipated to have high demand in the market, and manufacturers strive to optimize their components for cost reduction and focus on providing minimum functionality, disregarding fundamental security needs. Furthermore, a considerable number of device manufacturers do not provide software updates or security patches to mitigate or prevent damage after an attack.
Researchers have reported that over 68,000 medical devices were identified in Shodan to be exposed and therefore accessed on the public internet. Some of the devices were Magnetic Resonance Imaging (MRI) machines, infusion pumps, and pacemaker systems. These devices had default configuration settings. Researchers were able to extract some information related to office numbers, employee names, default credentials, software versions, operating systems, and more [ 5 ]. In some cases, the attackers did not realize what devices they were infecting. If they had acknowledged it, they would have been able to get a lot of sensitive information and could have caused damage to the hospital’s IT infrastructure.
Doctors are now able to program implantable cardioverter-defibrillators (ICD) to monitor a patient’s heart condition. These devices can send the right level of electrical shock to get the heart beating properly [ 6 ]. It was found out how attackers could cause a malfunction in these devices provoking a dangerous shock in the patient. The COVID-19 pandemic has made IoT technologies increasingly valuable as they provide numerous benefits such as communication, work, staying updated on daily events, learning, entertainment, health monitoring, and promoting a healthy lifestyle [ 7 ]. By reducing medical costs and encouraging healthy habits, IoT devices have become more popular due to the growing demand from people worldwide. Given the importance of monitoring individuals’ health to prevent potential consequences, IoT technologies can play a crucial role in detection, especially in situations where continuous monitoring is necessary to prevent putting a larger group of people at risk [ 8 , 9 ].
3. Software Implementation, Frameworks & Protocols Data privacy will be a very important point that will have to be established because if it gets compromised, it will cause individuals to reject this type of technology. The increase in devices also makes these gadgets a target for an attacker. Thus, it will be a great challenge to have the necessary protection for each person’s data. Different strategies started to appear involving COVID-19 and smart devices. Effective contact tracing adds importance to the user’s privacy. Trying to identify individuals who have been exposed to an infected person during the contagious window while preserving our privacy [ 10 ].
Wearable devices include a large list of possible attacks [ 11 ]. While there are multiple ways to mitigate these threats, the continuous advance of these technologies also introduces some challenges to countermeasure these vulnerabilities [ 12 , 13 ]. Likewise, wearable devices, similar to smartwatches, come with a great number of limitations that must be addressed [ 14 , 15 ] to increase public acceptance of this kind of technology. As these types of devices are gaining popularity, for this project, we have focused on a cybersecurity analysis of smartwatches due to the diverse amount of data they obtain as they are worn all day. These devices recollect data such as location, messages, phone calls, and medical information such as heart rate.
Some types of smartwatches also collect temperature and oxygen saturation (SpO2); the multiple uses they have, as they can be used to track exercise activities and sleeping activity; and the acceptance they have received in the latter years by the public, as we see every day more smartwatch consumers. Furthermore, even when a smartwatch is not formally considered a medical device, today’s wearable devices are more than just human activity trackers. Several types of research have shown that smartwatch users are taking their activity notifications seriously as a tool for health management. Even more, there has been a phenomenon of users feeling stress or anxiety about health readings from smartwatches and other digital wellness tools [ 16 ]. A study of young people showed that they track and monitor their bodies and health behaviors as a common practice [ 17 , 18 , 19 ].
Concerns have arisen regarding the lack of comprehension related to data security and privacy, as well as the vulnerability of these trackers to various attacks. With the increasing prevalence of personal health data disclosure and breaches in wearable devices, it is essential to further investigate the security and privacy challenges associated with these devices to provide a better, more secure, and private user experience. Users should be aware that these devices may present data inaccuracies and should be considered only as a tool rather than something entirely accurate for making health decisions.
This paper focuses on the vulnerabilities of smartwatches during their pairing via Bluetooth with other devices. Bluetooth has been a victim of different attacks for many years. In Section 2 , we present several studies in which the authors describe vulnerabilities and various types of attacks on different smartwatches, as well as providing proposals to manufacturers and users for mitigating these threats. Section 3 describes the Bluetooth protocol, and how it has been evolving. We have also included the security recommendations proposed by the Bluetooth guide [ 20 ]. Section 3 also exhibits the difference between pairing methods on Bluetooth devices, exposing the weakest and the safest methods. Section 4 describes how the cybersecurity analysis has been developed as well as our findings on the smartwatches that have been tested. Section 5 presents a proposal for maximum-security requirements and a proposal for the minimum requirements needed for security, which have been made with the most necessary security features while pairing two devices via Bluetooth. Section 6 expresses the conclusions gathered during this project and our future work.
The literature shows multiple concerns already found in different IoT devices [ 21 ]. Now, to understand how big these concerns are, vulnerabilities must be covered due to the increasing use of this kind of technology and the sensitive information they gather. A key is to maintain confidentiality, integrity, and availability, also known as the CIA triad; this represents a fundamental concept in cybersecurity. There has been a lot of research, and the most common types of attacks that have been made on IoT devices can be seen in the systematic review in Table 1 .
The large number of attacks that exist on IoT devices gives us an idea of the importance of establishing security countermeasures against these threats [ 24 ]. The consequences that they can have on a person’s lifestyle and health could be devastating. Devices’ sensitive data could be at risk with a technique in which data is being sent through devices and because they have poor authentication methods for devices that handle such an important type of data, raising question marks about confidentiality.
Other types of attacks have the objective of changing data information, making the users’ data that was recollected hard to trust. This way, it damages the integrity part of the IoT device. Several IoT devices are now used for medical purposes, recollecting real-time information. If they are not available at every moment of the day, not only are they not fulfilling their purpose, but they could be putting a user’s life in danger by not registering, what might be, for some users, life and death cases.
As can be seen, the biggest fundamentals in cybersecurity have been exposed by these types of technologies. Correcting these problems would be the following step to take to guarantee confidentiality, integrity, and availability. However, numerous other issues appear when trying to apply new forms of security to IoT devices, as shown in Table 2 . In this paper, we are focused on the Design Constraints. One of the main technologies used in the IoT for device communication is Bluetooth. Bluetooth is everywhere: in speakers, headphones, refrigerators, cars, wearables, medical devices, and more. IoT is about small devices and multiple sensors. Bluetooth is a suitable technology that provides IoT features that can be applied to a wide range of potential IoT applications. Manufacturers need to understand how to implement secure architectures to protect users’ sensitive information while considering the challenges and limitations of the IoT.
However, Bluetooth communication has been the target of multiple types of attacks for years as cybercriminals exploit the vulnerabilities this technology has had in earlier versions. These communication protocols have been updated to protect devices against eavesdropping and man-in-the-middle attacks. The literature shows multiple researchers finding weaknesses in wearable devices [ 29 , 30 , 31 , 32 ]. They talk about different attacks on several IoT devices that communicate via Bluetooth, as well as they give countermeasures and recommendations to users for safer use of this technology. Furthermore, other research includes studies that found vulnerabilities in some devices [ 33 ]. One of them is an attack on a smartwatch, where the PIN that secures its communication with a smartphone was exploited while performing a brute-force attack. In the pairing process, this smartwatch had one of the least secure mechanisms, which shows that smartwatches are prone to attacks [ 34 ]. With respect to threats, one article divides them into two categories: passive adversary and active adversary, where the first, the attacker eavedrops on the connection and tries to find LTK or other information, but he can not manipulate the message, and in the second, the attacker can inject, modify, and block the message transmitted, enabling the ability to create his own messages and send them to the victim’s device [ 35 ].
Other research focuses on wearable devices, such as a Fitbit smartwatch, and how they can be targets of man-in-the-middle attacks. The attack consists of using two fake devices, one that disguises itself as a smart device and another one as a mobile app that connects to the Fitbit device; it also adds that Fitbit collects a lot of sensitive data, and it proposes to educate the users to be aware of what happens when doing an incorrect use of the device [ 36 ]. Another research project highlights a couple of vulnerabilities in some wearable devices, such as the smartwatch Fitbit Inspire, which has a serious threat known as the Link Layer Length Overflow. It means that an attacker acting as a central device can make the peripheral devices suffer instabilities until they finally crash [ 37 ].
More studies have concluded that it is important to teach users about the correct use of this technology because most of the recommendations always go to the manufacturers. They propose some guidelines to instruct about wearable devices [ 38 ] and state the need for standards in the wearable industry [ 36 ]. Another piece of research worries about the data these devices obtain; for example, the users’ location, which exposes them to different types of attacks. Furthermore, it proposes the constant change of the MAC address to avoid any type of targeting [ 39 ]. A group of researchers also mentions the vulnerabilities of the MAC address in Fitbit devices, as they recollect the MAC addresses of nearby Fitbit devices, and while Fitbit offers a reasonable level of security, they also gather extraneous data about users [ 40 ].
In one paper, they make passive attacks on wearable devices using Bluetooth sniffers and HCI snoop logs and capture an encryption key in plain text [ 41 ]. While another article shows the use of Bluetooth and describes an attack where it forces a key renegotiation using eavesdropping techniques [ 42 ]. Other works show the potential risks the devices are exposed to when manufacturers do not follow the recommendations of the Bluetooth Special Interest Group, as it happens more often than it should [ 43 , 44 ]. While various research projects include tests on different devices, the literature does not show a way to compare the security levels of these devices. To the best of our knowledge, there is no existence of measurement to identify when an IoT device is secure or what characteristics can be considered to categorize if an IoT device is safe or not.
We proposed a novel model of Security Requirements on smartwatches in order to categorize if a device is safe or not based on the Bluetooth guide [ 20 ]. We performed an analysis of six smartwatches to evaluate their security requirements and showed the comparison. Bluetooth is used for short-range radio-frequency communication. As mentioned before, vulnerabilities can be found in IoT devices, and this could be discovered through the Bluetooth protocol. The most common attacks are man-in-the-middle (MITM), where an attacker can obtain the keys that are exchanged between devices and, once obtained, eavesdrop on communications [ 45 ].
The earliest days of Bluetooth introduced Bluetooth Basic Rate (BR), Enhanced Data Rate (EDR), and High Speed (HS) models. Bluetooth 1.1 and 1.2 versions could only work with BR because they are only capable of supporting up to 1 megabit per second (Mbps). EDR improves in Bluetooth version 2.0, where it gets data rates up to 3.0 Mbps. HS arrives during Bluetooth 3.0, supporting faster data rates up to 24 Mbps. However, devices that support higher data rates are also able to support lower data rates from earlier Bluetooth specifications. When referring to these versions of Bluetooth, they are commonly known as Bluetooth Classic. See Figure 2 .
4. Practical Deployment, Analysis & Case Studies Bluetooth Low-Energy (BLE) was established in the Bluetooth 4.0 specification; later, an update was made in versions 4.1 and 4.2. It is useful for wearable medical devices and sensors because it was primarily made for devices that use a coin-cell battery. It reduces power consumption and memory requirements. Basically, it is designed to operate in sleep mode and wake up only when the connection is initiated. This improves efficiency when discovering devices and during connection procedures and results in packets with shorter lengths, while services and protocols are simpler.
Since Bluetooth 4.0 devices can support both Bluetooth Classic and BLE, this is known as the dual mode. Cellphones work as a perfect example, where they might use Bluetooth Classic when connected to earphones and have the necessity to have constant data streaming while also using BLE when connected to a smart wristband that tracks your activity while doing exercises, and you only need the data exchange when you synchronize your devices to check your results.
Authentication, using the Bluetooth address to verify the identity of each device during the communication stage. Confidentiality, guaranteeing that only authorized devices have access to data, avoiding any type of eavesdropping. Authorization, verifying that a device is authorized to use the service before allowing it to do it, guaranteeing that only this device can use the service and no other device can.
Message integrity, when information is exchanged between two Bluetooth devices, it has to be secure and nothing can be modified. Pairing/bonding, the generated keys are shared and stored for future use, to create trust between two Bluetooth devices. To understand the importance of the keys that are exchanged once two devices start pairing, we have to understand the Bluetooth protocols and the security levels to avoid eavesdropping during this process. We are going to discuss these security levels and modes for each Bluetooth specification, first Bluetooth Classic and later Bluetooth Low-Energy.
Bluetooth includes four security modes; mode 1 has no security, mode 2 has authentication and encryption in the controller, and mode 3 has it in the physical link. These three modes only existed in the prior Bluetooth 2.1 version. In this article, we only test communication between devices that have a Bluetooth version higher than the Bluetooth 2.1 version. For these devices, it is mandatory to work with security mode 4.
Security Mode 4 is a service-level enforced security mode; it uses secure simple pairing (SSP) and it uses Elliptic-curve Diffie–Hellman (ECDH) key agreement for link key generation. This helps protect against eavesdropping and man-in-the-middle attacks. The ECDH that is used could be the elliptic curve 192 or 256. For authentication and encryption, a secret symmetric key is necessary, and it is known as the link key. Security mode 4 includes five security levels. Starting from security level 0 and ending at security level 4: (i) Level 0 has no security and is only allowed for service discovery protocols; (ii) Level 1, also does not require security; (iii) Level 2 requires an unauthenticated link key; (iv) Level 3 requires an authenticated link key, and; (v) Level 4 requires authenticating the link key using secure connections. The secure connections pairing protocol was introduced in Bluetooth 4.1 and it uses the ECDH 256, improving from the ECDH 192 that was used prior.
This section meticulously explains BLE, to understand how it is possible to protect against the most common attacks on this technology. Bluetooth 4.0, 4.1, and 4.2 count cryptographic keys to improve security in the devices, these keys are named Identity Resolving Key (IRK), to support low-energy private device addresses, and Connections Signature Resolving Key (CSRK), to assist data signing. When pairing BLE devices, a Long-Term Key (LTK) is generated, which is important for authentication and encryption (known as the link key in Bluetooth Classic). This could result in two different methods. During the first method, one device generates the LTK and sends it to the other device in a secure manner; this is known as low-energy Legacy Pairing.
Furthermore, it is important to notice that for this method, all the keys are distributed in a secure process during the pairing stage. In the second method, both devices create the key without the need to share it through the link. This method is called low-energy Secure Connections. Meanwhile, the LTK is generated, while the IRK and the CSRK are created and distributed securely. An important difference between these methods is that low-energy Legacy Pairing does not include Elliptic-curve Diffie–Hellman (ECDH) encryption, which makes it vulnerable to eavesdropping attacks and allows attackers to potentially find the LTK. In contrast, Low-energy Secure Connections can countermeasure this threat. We will provide a more detailed review of these pairing methods later in this paper.
Low-energy Security includes two modes. Security Mode 1 has four levels related to encryption. Level 1 does not require encryption and authentication. Level 2 asks for unauthenticated pairing with encryption. Level 3 needs authenticated pairing with encryption. Level 4 uses the Secure Connections method previously discussed in this section, as it asks for an authenticated link key using low-energy Secure Connections pairing with encryption. Security Mode 2 requires data signing in both of its levels, with the sole difference that level 1 only needs unauthenticated pairing while level 2 asks for authenticated pairing. Because encryption is a great security asset, using Security Mode 1 Level 3 or 4 is strongly recommended over other options.
In this section, we give a more detailed explanation of the low-energy pairing methods and describe the phases that occurred during the pairing methods. Starting with low-energy Legacy Pairing. Phases: Phase 1, once explore the input/output capabilities and security requirements in the devices, they will establish an agreement on a Temporary Key (TK).
Phase 2, they proceed to create a Short Term Key (STK) using random values that are being exchanged and the TK. This STK establishes an encrypted link between devices. Phase 3, it assures a safe key transport for all the keys mentioned earlier in this article (LTK, IRK, CSRK). Low-energy Secure Connections work in a different manner. Even though phase 1 works the same way as legacy pairing, in phase 2, the LTK is generated without the need for the STK. This LTK is useful in phase 3, and the LTK encrypts the links, and a key agreement is made to distribute the IRK and CSRK securely instead of using a key transport.
5. Performance Evaluation & Extended Technical Observations During the pairing process between two devices, one of four different pairing processes can be applied. These pairing processes are: (a) Out of Band for Bluetooth Standard or BLE; (b) Numeric Comparison; (c) Passkey Entry 4 or 6 digits; and (d) Just Works. The input/output capabilities of devices play an important role in determining what processes can be utilized.
The out-of-band (OOB) process requires two devices that have OOB technology, such as near-field communication (NFC). One device sends the other a 128-bit number, which is the TK, using OOB technology. Using low-energy Legacy Pairing provides one-in-a-million protection against MITM attacks to guess the TK. However, this protection comes from the OOB technology that the device uses, because if someone is capable of eavesdropping on the OOB, they will obtain the TK values.
For low-energy Secure Connections, the device address is sent through the OOB. Even if an eavesdropper can obtain it, this does not give them any value in decrypting the data. Numeric comparison is an option available only for low-energy Secure Connections. This method is not available for low-energy Legacy Pairing. The process involves two devices displaying a 6-digit number on their respective screens, and the user enters one of two options: (i) YES, if both displays show the same 6-digit number; (ii) NO, if the numbers are different.
The previous 6-digit number is not used to generate the link key to avoid eavesdropping. Even if an unauthorized person captures this 6-digit number, it will not be useful for any further pairing process. Additionally, it has protection against MITM attacks, as the user must confirm if the 6-digit number is or is not the same on both devices before proceeding. This guarantees that no other device can initiate the pairing process.
Another method is passkey entry, which requires that both devices have a keyboard input or at least one of them has a display output. This method works with low-energy Legacy Pairing. A passkey is given on one device and entered on the other, and then a TK is generated using the passkey. The passkey is required to have six numeric digits, which would give an entropy of twenty bits that ensures the complexity of deciphering the given key. Low-energy Secure Connections pairing works differently. After the devices exchange public keys, the six numeric digits passkey is generated, and once it is entered into the device, it starts sending a hash of each bit of the passkey. This procedure is repeated twenty times to complete the twenty bits of the passkey. Furthermore, the public keys were sent during the previous step. This method offers protection against MITM attacks. When using a passkey of six digits, it gives an attacker a one-in-a-million chance to guess the correct passkey.
The last method is the least secure one, and it is used due to the limitations in the input/output capabilities of the devices. For low-energy Legacy Pairing the key is always the same and is set to all zeros, leaving the pairing exposed to eavesdropping and MITM attacks. In the low-energy Secure Connections method, the pairing process follows the same steps as in the numeric comparison process, but the user is unable to see the 6-digit number. This is because the devices involved in this procedure cannot display the number, which in turn makes it impossible to perform the final commitment checks.
These four pairing methods are not exclusive to Bluetooth Low-Energy; they can also be found in Bluetooth Classic, working slightly differently due to the IRK and CSRK being exclusive to BLE. Only the LTK is set to be created, but it is known as the link key. The association models (out of band, numeric comparison, and passkey entry) provide authenticated link keys; meanwhile, the link key is unauthenticated during the Just Works pairing model for Bluetooth Classic. The risk of an attack is determined by the version of Bluetooth and the pairing method used. See Figure 3 .
In this paper, we consider a passive attacker who does not interfere with the pairing process and only eavesdrops on the exchanged communication packets. This adversary is also called an honest-but-curious or passive global attacker because he or she can see all the traffic communication in the system. For this project, we aimed to exploit the vulnerabilities of the Bluetooth protocol in wearable devices due to the increase in use that they are showing in the general public. We chose to study various types of smartwatches from different brands. The limitations they might have in hardware and their input/output capabilities gave us reasons to believe that they could be unable to follow every step of the Bluetooth protocol guidelines [ 20 ].
For the experiment, we used six smartwatches. We carefully selected six devices that we believe would provide a good representation of the current market. We acknowledge that there are many other devices available, but we believe that our selection provides a useful and informative sample for our research purposes. See Figure 4 : Smartwatches used in the attack; ( a ) Amazfit GTS 2 mini; ( b ) Fitbit Versa 2; ( c ) Apple Watch Series 2 Aluminum; ( d ) Fitbit Versa 3; ( e ) Garmin vivoactive 3; ( f ) W27 Pro.
Smartwatches are under consideration for medical diagnosis. For example, in 2018, the Food and Drug Administration (FDA) cleared the Apple Watch Series 4 and named it a class 2 medical device [ 46 ] because of its ability to identify atrial fibrillation (AF). This shows that manufacturers are designing smartwatches that can obtain sensitive data, and because no standard has to be followed to design these devices, they create a world of possibilities for cybercriminals. We tested six different smartwatches; all of them include the heart rate detection function, while others also include blood oxygen saturation (SpO2) detection. These features could encourage the user to seek medical advice when necessary and could save multiple lives; for these reasons, it is important to guarantee the confidentiality, integrity, and availability of these data for smartwatch users.
To test the security features during the Bluetooth pairing process of these devices, we implemented a passive sniffing attack where we captured the traffic sent between devices. We used two Bluefruit LE Sniffer - Bluetooth Low-Energy (BLE 4.0)-nRF51822-Firmware Version 2, designed by adafruit. It allowed us to listen to only BLE devices and capture their traffic. It is recommended to use at least two sniffers, ideally three, because the packets are sent through 40 frequency channels (3 for advertising and 37 for data), and normally one packet is sent over different channels, and only one sniffer could capture them all, causing loss of information. Once we obtained it, we started analyzing the data packets using wireshark, an open-source packet analyzer. We made our attacks in a Dell-Inspiron laptop 14 serie 7000, intel core i7 with Kali Linux. See Figure 5 .
First, all the packets were captured while pairing a smartwatch and a smartphone, we noticed all packets sent over the Attribute Protocol (ATT) were missing; normally all the data exchange is here, whether encrypted or unencrypted. We found that once the smartwatches bonded with a smartphone, the sniffer stopped capturing data from the devices because their connection was encrypted thanks to the key exchange or agreement they had during pairing. We explored other ways to analyze the pairing process between our devices. Except for the Apple Watch Series 2, all the devices were paired with a Samsung Galaxy S20. This smartphone has Bluetooth 5.0 dual mode, which allows it to connect to devices with BLE and Bluetooth Classic. It also has the feature to generate a Bluetooth host controller interface (HCI) snoop log, which gives us the option to obtain records of the Bluetooth data that our smartphone is generating while pairing with other devices.
There are two ways to obtain the HCI log, and it depends on the smartphone and its operating system. For the one we selected, we had to generate a bug report. To do this, we activated the developer mode and extracted all the activity and bugs from the smartphone during a previous period of time. The report was stored in a .txt file extension on our device. However, this file contained information that was not useful for our purpose, so we used the btsnooz python script to extract only the captured Bluetooth information.
The other way to obtain the bug report is also by enabling developer mode, activating the Bluetooth HCI snoop log option, and finally rebooting the smartphone. This is supposed to automatically generate the report more easily. Nevertheless, in our case, this file was never generated. We tried other devices, such as a Xiaomi Mi9T smartphone and a Huawei MatePad tablet, but had no success with either of them. We believe that this method is no longer available.
With our analysis, we were able to find that the way different smartwatches work during pairing and the lack of standardization for wearable design show multiple differences inside the security scope. Table 3 includes the devices that were analyzed during this project and their features. We show the Bluetooth version of each device and whether their pairing method is in the Bluetooth Classic mode or the BLE mode.
For the Fitbit Versa 3 smartwatch, we discovered that it uses Bluetooth dual mode, as it has a feature that enables users to make and receive calls called Versa 3 Controls. To use this feature, the smartwatch must first be paired with the user’s smartphone via BLE. Once this is done, another pairing must be initiated via Bluetooth Classic between the smartphone and Versa 3 Controls to utilize the phone’s features for making and receiving calls. For this device, we decided to separate this feature and list it as another device due to the requirement of performing another pairing process to use it. Although it is one physical device, we are now counting it as two different smartwatches, one pairing via BLE and the other via Bluetooth Classic. Therefore, we have analyzed an extra device, resulting in a total of seven smartwatches being tested. For the Garmin, we found that besides showing the 6-digit number on both devices during the pairing process, when we analyzed the data packets in Wireshark, we noticed that the pairing authentication was performed repeatedly, much more than the other smartwatches, as shown in Figure 6 . This is because it uses the LE Secure Connections method, in which each device computes a confirmation value and sends it to the other device; then this second device also computes its own confirmation value and sends it to the first device, iterating for each k bit of the passkey. Table 3 also shows the pairing association model these devices use; sometimes they include more than one model. The reason is to be able to pair to smartphones with different input/output capabilities. These parameters are shown in the data traffic within the Security Manager Protocol when both devices share I/O capabilities when sending the pairing request. Some of these association models are less secure than others.
We can see the security modes and their respective levels previously discussed in this paper. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/HarmonyOS • https://source.android.com/docs/security/bulletin/wear/2026/2026-09-01 • https://pmc.ncbi.nlm.nih.gov/articles/PMC10301545/ • https://source.android.com/docs/security/bulletin/wear/2026/2026-04-01
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Wear Os Smartwatch Security Analysis And Data Leakage.
[*] Metasploit Scan Running on Target Subnet for Wear Os Smartwatch Security Analysis And Data Leakage... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |