Complete Technical Paper Content — Web Application Firewall Implementation Using Python
Overview & System Context
Web Application Firewall Implementation Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8433 Words · Real Software Screenshots: 1 1. Executive Overview & Technical Background A Web application firewall (WAF) is a specific form of application firewall that filters, monitors, and blocks HTTP traffic to and from a web service. By inspecting HTTP traffic, it can prevent attacks exploiting a Web application's known vulnerabilities, such as SQL injection, cross-site scripting (XSS), file inclusion, and improper system configuration. Financial institutions often utilize WAFs to help in the mitigation of Web application zero-day vulnerabilities, as well as hard-to-patch bugs or weaknesses through custom attack signature strings.
Dedicated Web application firewalls entered the market in the late 1990s during a time when web server attacks were becoming more prevalent. Early WAF products, from Kavado and Gilian technologies, tried to solve the increasing amount of attacks on Web applications in the late 1990s. In 2002, the open-source project ModSecurity was formed in order to make WAF technology more accessible. They finalized a core rule set for protecting Web applications, based on OASIS Web Application Security Technical Committee’s (WAS TC) vulnerability work. In 2003, they expanded and standardized rules through the Open Web Application Security Project’s (OWASP) Top 10 List, an annual ranking for Web security vulnerabilities. This list would become the industry standard for Web application security compliance. Since then, the market has continued to grow and evolve, especially focusing on credit card fraud prevention. With the development of the Payment Card Industry Data Security Standard (PCI DSS), a standardization of control over cardholder data, security has become more regulated in this sector.
An application firewall is a form of firewall that controls input/output or system calls of an application or service. It operates by monitoring and blocking communications based on a configured policy, generally with predefined rule sets to choose from. The two primary categories of application firewalls are network-based and host-based. Network-based application firewalls operate at the application layer of a TCP/IP stack and can understand certain applications and protocols such as File Transfer Protocol (FTP), Domain Name System (DNS), or Hypertext Transfer Protocol (HTTP).
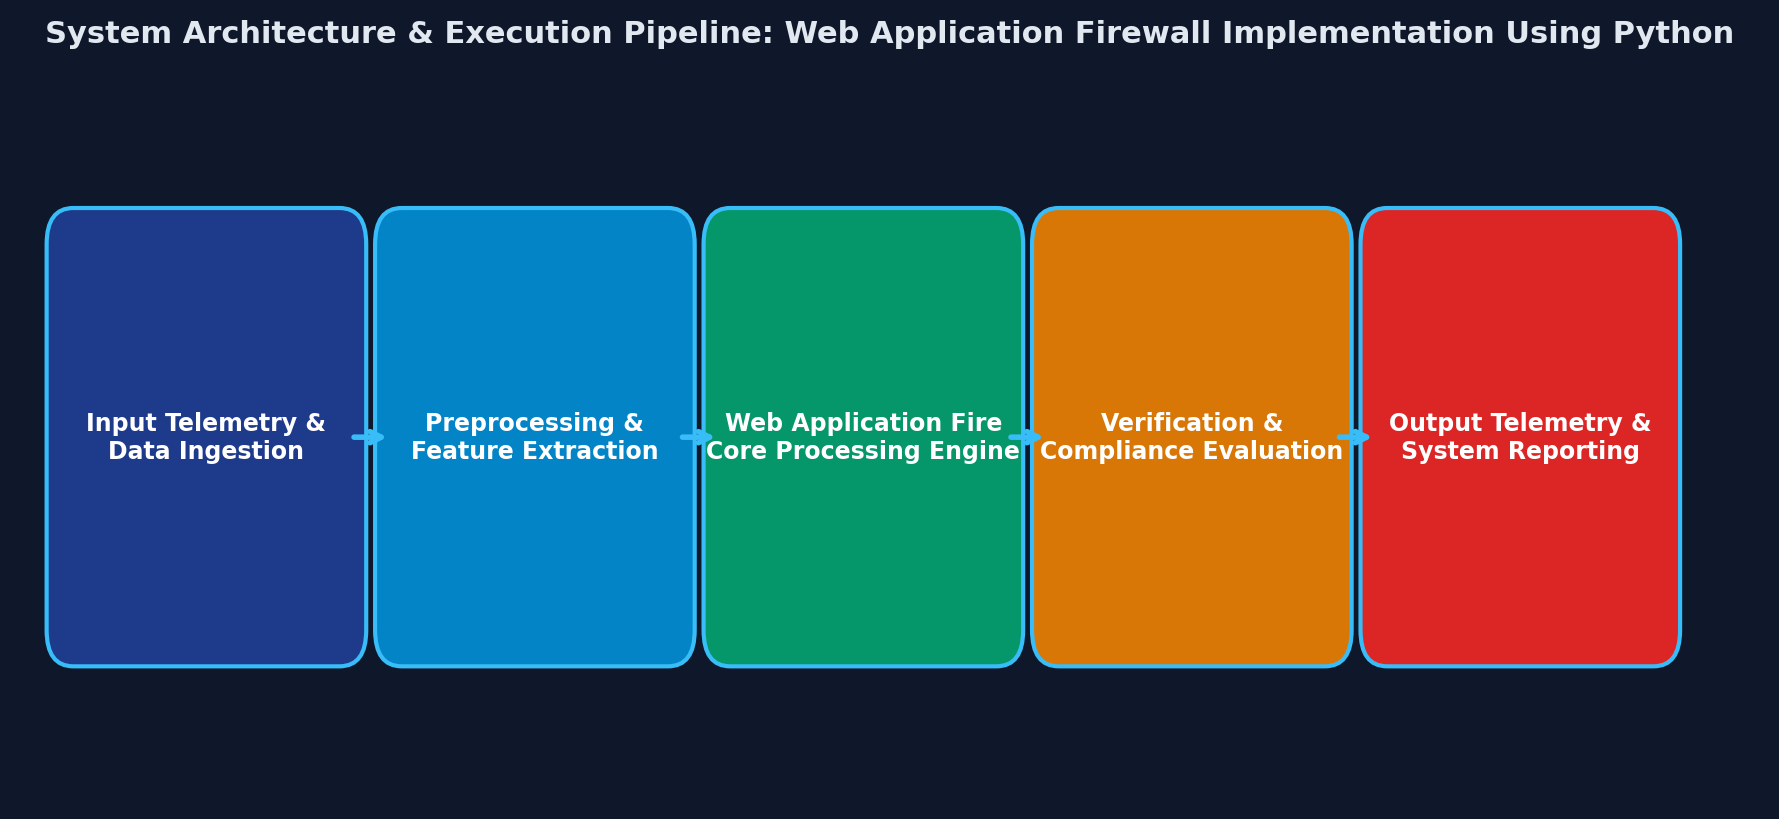
This allows it to identify unwanted applications or services using a non standard port or detect if an allowed protocol is being abused. Modern versions of network-based application firewalls can include the following technologies: Figure 1: Figure 1: Verified System Architecture & Pipeline Workflow Encryption offloading Intrusion prevention system Data loss prevention Web application firewalls (WAF) are a specialized version of a network-based appliance that acts as a reverse proxy, inspecting traffic before being forwarded to an associated server.
AppArmor Little Snitch Kerio Control — a commercial product from Kerio Technologies ModSecurity — also works under Windows, Mac OS X, Oracle Solaris and other versions of Unix. ModSecurity is designed to work with the Web servers IIS, Apache2 and NGINX. OpenSnitch Portmaster — an activity monitoring application by Safing. It is also available for Microsoft Windows. Systrace Zorp firewall Cisco Firepower Threat Defense Check Point Fortinet FortiGate Series Juniper Networks SRX Series Palo Alto Networks SonicWALL TZ/NSA/SuperMassive Series A10 Networks Web Application Firewall Barracuda Networks Web Application Firewall/Load Balancer ADC Citrix NetScaler F5 Networks BIG-IP Application Security Manager Fortinet FortiWeb Series KEMP Technologies Imperva Application security (AppSec) includes all tasks that introduce a secure software development life cycle to development teams. Its final goal is to improve security practices and, through that, to find, fix and preferably prevent security issues within applications. It encompasses the whole application life cycle from requirements analysis, design, implementation, verification as well as maintenance. Web application security is a branch of information security that deals specifically with the security of websites, web applications, and web services. At a high level, web application security draws on the principles of application security but applies them specifically to the internet and web systems. The application security also concentrates on mobile apps and their security which includes iOS and Android Applications. Web Application Security Tools are specialized tools for working with HTTP traffic, e.g., Web application firewalls.
Design review. Before code is written the application's architecture and design can be reviewed for security problems. A common technique in this phase is the creation of a threat model. White-box testing, or code review. Critical examination of internal structure, architecture, design, etc. Black-box testing. Tests functionality rather than internal structure. Automated Tooling. Many security tools can be automated through inclusion into the development or testing environment. Examples of those are automated DAST/SAST tools that are integrated into code editor or CI/CD platforms. Coordinated vulnerability platforms. These are hacker-powered application security solutions offered by many websites and software developers by which individuals can receive recognition and compensation for reporting bugs.
Broken access control Cryptographic failures Injection Insecure design Security misconfiguration Vulnerable and outdated components Identification and authentification failures Software and data integrity failures Security logging and monitoring failures* Server-side request forgery (SSRF)* Implement access control Use cryptography the proper way Validate all input & handle exceptions Address security from the start Secure by default configurations Keep your components secure Implement digital identity Use browser security features Implement security logging and monitoring Stop server-side request forgery Static application security testing (SAST) analyzes source code for security vulnerabilities during an application's development. Compared to DAST, SAST can be utilized even before the application is in an executable state. As SAST has access to the full source code it is a white-box approach. This can yield more detailed results but can result in many false positives that need to be manually verified. Dynamic application security testing (DAST, often called vulnerability scanners) automatically detects vulnerabilities by crawling and analyzing websites. This method is highly scalable, easily integrated and quick. DAST tools are well suited for dealing with low-level attacks such as injection flaws but are not well suited to detect high-level flaws, e.g., logic or business logic flaws. Fuzzing tools are commonly used for input testing. Industry application security research highlights increasing risks related to insecure APIs, client-side code tampering, and runtime exploitation, reinforcing the importance of comprehensive dynamic and runtime security testing. Interactive application security testing (IAST) assesses applications from within using software instrumentation. This combines the strengths of both SAST and DAST methods as well as providing access to code, HTTP traffic, library information, backend connections and configuration information. Some IAST products require the application to be attacked, while others can be used during normal quality assurance testing. Runtime application self-protection augments existing applications to provide intrusion detection and prevention from within an application runtime. Dependency scanners (also called software composition analysis) try to detect the usage of software components with known vulnerabilities. These tools can either work on-demand, e.g., during the source code build process, or periodically.
Web Application Firewall (WAF) provides centralized protection of your web applications from common exploits and vulnerabilities. You can deploy WAF on Azure Application Gateway or WAF on Azure Front Door Service. Use Web Application Firewall (WAF) to protect applications from malicious and unwanted internet traffic. WAF can protect any internet facing endpoint, providing consistent rule enforcement across a customer's application.
Learn about Oracle Cloud Infrastructure Oracle Cloud Infrastructure Web Application Firewall, a regional-based and edge enforcement service that's attached to an enforcement point, such as a load balancer or a web application domain name. WAF protects applications from malicious and unwanted internet traffic. WAF can protect any internet facing endpoint, providing consistent rule enforcement across a customer's applications.
WAF provides you with the ability to create and manage rules for internet threats including Cross-Site Scripting (XSS), SQL Injection, and other OWASP-defined vulnerabilities. Access rules can limit based on geography or the signature of the request. Edge policy is a global solution. To use this solution, allowlist Oracle nodes throughout the world and use DNS to point your application to the CNAME that we provide.
You can convert an Edge policy to a WAF policy and vice a versa, by manually recreating the settings and policy. No automated method or tool exists for this conversion. WAF is a Payment Card Industry (PCI) compliant, global security service that protects applications from malicious and unwanted internet traffic.
Each service in Oracle Cloud Infrastructure integrates with IAM for authentication and authorization, for all interfaces (the Console, SDK or CLI, and REST API). An administrator in your organization needs to set up groups , compartments , and policies that control which users can access which services, which resources, and the type of access. These policies control who can create users, create and manage the cloud network, launch instances, create buckets, download objects, and similar tasks. For more information, see Getting Started with Policies . For specific details about writing policies for each of the different services, see Policy Reference .
If you're a regular user (not an administrator) who needs to use the Oracle Cloud Infrastructure resources that your company owns, contact your administrator to set up a user ID for you. The administrator can confirm which compartment or compartments you should be using. You can create automation based on state changes for Oracle Cloud Infrastructure resources by using event types, rules, and actions. For more information, see Overview of Events .
Apply tags to resources to help organize them according to your business needs. You can apply tags when you create a resource, and you can update a resource later to add, revise, or remove tags. For general information about applying tags, see Resource Tags . For information about how to secure WAF, including security information and recommendations, see Securing Web Application Firewall .
This section provides a reference implementation architecture diagram for the components deployed with this solution. Deploying this solution with the default parameters deploys the following components in your AWS account. CloudFormation template deploys AWS WAF and other AWS resources to protect your web application from common attacks. At the core of the design is an AWS WAF web ACL, which acts as the central inspection and decision point for all incoming requests to a web application. During initial configuration of the CloudFormation stack, the user defines which protective components to activate. Each component operates independently and adds different rules to the web ACL.
The components of this solution can be grouped into the following areas of protection. AWS Managed Rules (A) - This component contains AWS Managed Rules IP reputation rule groups , baseline rule groups , and use-case specific rule groups . These rule groups protect against exploitation of common application vulnerabilities or other unwanted traffic, including those described in OWASP publications, without having to write your own rules.
Manual IP lists (B and C) - These components create two AWS WAF rules. With these rules, you can manually insert IP addresses that you want to allow or deny. You can configure IP retention and remove expired IP addresses on allowed or denied IP sets using Amazon EventBridge rules and Amazon DynamoDB . For more information, refer to Configure IP retention on Allowed and Denied AWS WAF IP sets .
SQL Injection (D) and XSS (E) - These components configure two AWS WAF rules that are designed to protect against common SQL injection or cross-site scripting (XSS) patterns in the URI, query string, or body of a request. HTTP Flood (F) - This component protects against attacks that consist of a large number of requests from a particular IP address, such as a web-layer DDoS attack or a brute-force login attempt. With this rule, you set a quota that defines the maximum number of incoming requests allowed from a single IP address within a default five-minute period (configurable with the Athena Query Run Time Schedule parameter). After this threshold is breached, additional requests from the IP address are temporarily blocked. You can implement this rule by using an AWS WAF rate-based rule, or by processing AWS WAF logs using a Lambda function or Athena query. For more information about the tradeoffs related to HTTP flood mitigation options, refer to Log parser options .
Scanner and Probe (G) - This component parses application access logs searching for suspicious behavior, such as an abnormal amount of errors generated by an origin. Then it blocks those suspicious source IP addresses for a customer-defined period of time. You can implement this rule using a Lambda function or Athena query. For more information about the tradeoffs related to scanner and probe mitigation options, refer to Log parser options .
IP Reputation Lists (H) - This component is the IP Lists Parser Lambda function that checks third-party IP reputation lists hourly for new ranges to block. These lists include the Spamhaus DonâIIt Route Or Peer (DROP) and Extended DROP (EDROP) lists, the Proofpoint Emerging Threats IP list, and the Tor exit node list. Bad Bot (I) - This component enhances bad bot detection by monitoring direct connections to an Application Load Balancer (ALB) or Amazon CloudFront, in addition to the honeypot mechanism. If a bot bypasses the honeypot and attempts to interact with ALB or CloudFront, the system analyzes request patterns and logs to identify malicious activity. When a bad bot is detected, its IP address is extracted and added to an AWS WAF block list to prevent further access. Bad bot detection operates through a structured logic chain, ensuring comprehensive threat coverage: HTTP Flood Protection Lambda Log Parser âII Collects bad bot IPs from log entries during flood analysis.
Scanner & Probe Protection Lambda Log Parser âII Identifies bad bot IPs from scanner-related log entries. HTTP Flood Protection Athena Log Parser âII Extracts bad bot IPs from Athena logs, using partitions across query run. Scanner & Probe Protection Athena Log Parser âII Retrieves bad bot IPs from scanner-related Athena logs, using the same partitioning strategy.
Fallback Detection âII If both HTTP Flood Protection and Scanner & Probe Protection are disabled, the system relies on the Log Lambda parser, which logs bot activity based on WAF label filters . Each of the three custom Lambda functions in this solution publish runtime metrics to CloudWatch. For more information on these Lambda functions, refer to Component details .
2. System Architecture & Core Working Principles Get automatic protection from vulnerabilities and the flexibility to create custom rules. The Cloudflare Web Application Firewall (Cloudflare WAF) checks incoming web and API requests and filters undesired traffic based on sets of rules called rulesets. The WAF uses the Rules language , a flexible expression syntax that lets you filter traffic by request properties such as IP address, URL path, headers, and body content.
Compare requests with an application-specific expected structure. Review profile detections before mitigating violations with Custom Rules. Create your own custom rules to protect your website and your APIs from malicious incoming traffic. Use advanced features like WAF attack score and malicious uploads detection in your custom rules.
Define rate limits for incoming requests matching an expression, and the action to take when those rate limits are reached. Enable the pre-configured managed rulesets to get immediate protection. These rulesets are regularly updated , offering advanced zero-day vulnerability protections, and you can adjust their behavior. Review mitigated requests (rule matches) using an intuitive interface. Tailor your security configurations based on sampled logs.
Displays information about all incoming HTTP requests, including those not affected by security measures. This is a summary of available features per Cloudflare plan. Refer to the documentation of individual features for more details. Cloudflare DDoS protection secures websites, applications, and entire networks while ensuring the performance of legitimate traffic is not compromised.
Client-side security (formerly known as Page Shield) is a comprehensive client-side security solution to ensure the safety of your website visitors' browser environment. Cloudflare bot solutions identify and mitigate automated traffic to protect your domain from bad bots. For additional protection against distributed denial of service (DDoS) attacks, AWS also offers AWS Shield Advanced . AWS Shield Advanced provides expanded DDoS attack protection for your Amazon CloudFront distributions, Amazon Route 53 hosted zones, and Elastic Load Balancing load balancers. AWS Shield Advanced incurs additional charges. For more information, see the AWS Shield documentation .
AWS Firewall Manager simplifies your AWS WAF administration and maintenance tasks across multiple accounts and resources. With AWS Firewall Manager, you set up your firewall rules just once. The service automatically applies your rules across your accounts and resources, even as you add new resources. For more information, see the AWS Firewall Manager documentation .
For more information about choosing the right protection service, see Which should I choose ? A Web Application Firewall (WAF) is a security solution that monitors, filters, and blocks HTTP traffic to and from web applications. Unlike traditional network firewalls, WAFs focus on application-layer attacks and can protect against sophisticated threats.
There are several types of WAF solutions available, each with its own advantages and deployment models. WAFs provide protection against a wide range of web application attacks and vulnerabilities. Implementing a WAF requires careful planning and configuration to ensure optimal protection without impacting application performance.
Evaluate your current security posture, identify critical applications, and determine the appropriate WAF solution based on your requirements and budget. Deploy the WAF in your environment and configure initial rules based on your application stack and security requirements. Test the WAF with various attack scenarios and fine-tune rules to minimize false positives while maintaining security.
Continuously monitor WAF performance, update rules based on new threats, and maintain the system for optimal protection. Effective WAF configuration requires understanding of rule types and their application to different attack scenarios. WAF implementation must balance security with performance to ensure your applications remain responsive and available. Continuous monitoring and analysis of WAF logs and performance metrics are essential for maintaining effective protection.
Implementing a WAF is a crucial step in protecting your web applications from modern threats. Proper configuration and ongoing maintenance ensure optimal protection and performance. Use our security scanning platform to identify vulnerabilities and get expert recommendations for WAF implementation. Learn how to effectively scan websites for security vulnerabilities and implement robust security measures.
Essential SSL/TLS configuration practices to ensure secure communication and protect user data. WAFs have become one of the key cornerstones of modern application security. With present-day SaaS applications owned by third-party suppliers on largely invisible infrastructure, a WAF allows for network-level visibility and control to be wrested back to the organization itself. However, implementation is one of the biggest WAF challenges , and a major responsibility.
After selecting a WAF tool , an organization is faced with the daunting process of implementation. In order to establish best practices, it’s important to first map out how most implementations work. The effectiveness of a web application firewall depends heavily on how well it’s positioned, configured, managed, and monitored. The specific application will have already been selected before the buying process, and therefore will have an ideal design. A reliable way to validate your setup is by starting with a passive web application firewall deployment. In this mode, the WAF observes and logs traffic without actively blocking any requests.
From there, a WAF needs to be loaded with rules. These rules can follow a few different styles: allowlist and blocklist settings allow an organization to specify precisely which traffic sources are allowed or denied. Rate limiting is another approach, allowing policies to set thresholds on the number of requests that can be made within any one time. Geo-blocking does the same with locations: collectively, these allow a WAF to identify and block suspicious traffic. Getting to this stage demands efficient implementation.
With WAFs becoming such cornerstones of modern security, an efficient implementation process can give organizations a major head start. Before integrating any device or virtual instance into a network, it’s essential to ensure two key steps are completed: thorough documentation of the network infrastructure and proper hardening of the system being deployed.
Hardening involves applying the latest security patches and configuring the system to align with established security policies and best practices. This includes disabling unnecessary services, enforcing strong authentication controls, and securing network access. These measures help reduce the attack surface and ensure the new component doesn’t introduce vulnerabilities into the environment.
Once your requirements are clearly defined, the next step is choosing the right application for your initial WAF deployment. For those new to Web Application Firewalls, it’s advisable to begin with a non-essential application whenever feasible. This strategy provides a safer environment to learn the ins and outs of the WAF, fine-tune its settings, and gain operational experience – all while minimizing potential disruptions to critical business operations.
It’s also wise to select an application that the security team is highly familiar with. Familiarity with normal traffic patterns enables you to more effectively monitor the impact of WAF implementation, detect anomalies, and adjust the WAF configuration best practices that are being followed. After selecting your target application, the recommended next step is to deploy your WAF in a staging environment. This setup provides a safe space to test configurations and functionality without disrupting live traffic or impacting users.
There are two common methods for creating a WAF-enabled staging environment, depending on your organization’s practices: Once the staging environment is up and running, it’s critical to restrict access to a designated group of authorized developers. A basic way of enforcing this isolation is via IP-based restrictions, where the WAF blocks any traffic not originating from your organization’s known public IP addresses. While straightforward, this method lacks user authentication and can become cumbersome if remote access is needed – unless developers use a VPN to connect to the internal network.
Application-level authorization, on the other hand, implements authentication within the application itself, and allows the WAF to look at more general identity markers, such as the role of each user. This is a basic form of Role-Based Access Control (RBAC), and allows for a more flexible and scalable rule architecture. Managed rule sets are pre-configured collections of WAF rules designed to address common web application threats such as SQL injection , cross-site scripting (XSS), and bot traffic. Offered by most WAF vendors, these rules streamline deployment and provide immediate protection.
Stress testing them is important, however – not all managed rules are going to be ideal for every application. Get it wrong, and rules can begin alerting on and outright blocking legitimate users’ traffic. A key part of rule implementation is testing their performance – which is why a staging environment is so useful. Deploying these new rules in block mode allows a security team to see precisely how those rules are interacting with an application’s traffic. This ensures your operations team becomes familiar with how WAF rules function before moving into a live environment.
3. Software Implementation, Frameworks & Protocols When implementing within production environments, however, it’s best to enable new rules in count mode. This approach allows you to monitor rule activity and detect false positives without impacting users. Once you’re confident in the rule’s behavior, it’s possible to transition to block mode – helping avoid unintended disruptions caused by misconfigured rules.
When an application request aligns with a managed rule set, the WAF can then attach a label to that request. These labels persist as the request continues through the rule evaluation process, allowing it to reach custom exception rules that act on these labels. This approach allows you to bypass specific rules for traffic patterns known to be safe, and therefore reduce false positives. This is also why monitoring mode is so vital for early implementation – it’s how analysts can see which labels are applied.
Integrating WAF with security infrastructure is a critical best practice for effective implementation and ongoing security monitoring. Logs allow WAF policy choices to be integrated into other tools, and show how the WAF is interacting with incoming traffic – highlighting blocked requests, rule matches, anomalies, and potential attack patterns. Without this insight, monitoring WAF performance is far more difficult.
Integrating WAF logs into a Security Information and Event Management (SIEM) platform allows for broader threat analysis across the environment. Whether using a cloud-native SIEM or a third-party solution, feeding WAF data into this system ensures that external-facing applications are included in security investigations and incident response workflows. Check Point’s cloud-based WAF – Check Point – intelligently learns application structures and behaviors, automatically enforcing data protection policies and content rules around it. To achieve this, Check Point applies two layers of artificial intelligence to all requests, one assessing the request’s associated APIs, and the other comparing each request against the application’s baseline of usual behavior. Read more about Check Point WAF with our solution brief . Implementation is made super-simple, as the WAF is based on WAF-as-a-Service architecture. As it doesn’t demand heavy agent integration, Check Point offers rapid routing after a one-time DNS configuration.
Welcome to the Ultimate Web Application Firewall (WAF) Guide — your practical, big-picture resource for understanding how WAFs work, why they matter, and how to deploy, tune, and test them effectively. This guide breaks down WAF types, core features, integration tips, common pitfalls, and real-world best practices. You’ll find links scattered throughout, but you’ll also find them and many more resources at the bottom of the page.
This post is regularly updated to keep up with the latest tools, threats, and tuning strategies — so bookmark it and check back often! A well-configured WAF can defend your apps against many common web attacks. Here are a few real-world examples: These attacks are mapped to the OWASP Top 10 , an industry standard for critical web application security risks. ( Imperva WAF ) A network firewall protects your infrastructure by blocking unwanted IP addresses, ports, or protocols ( Layer 3/4 ), and some firewalls partly block Layer 7 traffic with web filters. A WAF , on the other hand, inspects the actual HTTP payloads at Layer 7, understanding the structure of web requests and responses. ( Fortinet WAF ) Key point: They work best together — the network firewall sets the broad perimeter defense, while the WAF catches web-specific attacks.
A WAF can help absorb some Layer 7 DDoS attacks by filtering suspicious requests before they reach your application server. But for large-scale volumetric DDoS (network-layer floods), you’ll still need robust network-level protection or a dedicated DDoS mitigation service . A WAF is your web app’s bouncer. It checks every request coming in and blocks the shady ones before they hit your server.
In a secure architecture, a network firewall , a WAF , and sometimes a secure web gateway each add a layer to your defense in depth. Not all WAFs are the same — and understanding the different types helps you choose the right protection for your stack. A Web Application Firewall can be deployed in cloud-managed , on-premises , hybrid , or open source modes — each with trade-offs for control, cost, and ease of use.
A cloud-managed WAF is hosted and operated by a third-party vendor on their globally distributed edge network. Examples include Cloudflare WAF , AWS WAF , and Akamai Kona Site Defender . You simply route your traffic through the provider’s network, and they inspect and filter malicious traffic before it reaches your servers. These services come with pre-configured managed rule sets, DDoS mitigation, bot protection, and automatic updates.
Best for: Startups, SaaS, small teams, or businesses that want security without large operational overhead. An on-premises WAF lives inside your data center or private cloud and is fully managed by your security team. Popular examples include F5 BIG-IP ASM , Fortinet FortiWeb , and Imperva SecureSphere . Here, your WAF can be tightly integrated with other network security appliances like traditional firewalls, intrusion prevention systems (IPS), and SIEM solutions.
Best for: Enterprises, financial services, healthcare, or any high-compliance environment with complex apps and sensitive data. A hybrid WAF combines elements of both on-premises and cloud-based models. For example, you might run a local WAF appliance for day-to-day traffic inspection, but burst overflow traffic or offload DDoS scrubbing to a cloud WAF like Cloudflare or AWS.
This is increasingly popular because it balances local control with global scalability. Best for: Large enterprises with seasonal spikes or global apps with critical workloads. An open source WAF gives you full transparency and flexibility over your web traffic protection. The most well-known is ModSecurity , often deployed with the OWASP Core Rule Set (CRS) .
These WAFs are DIY by nature — you install and configure them yourself, whether on Apache, NGINX, or other platforms. Best for: Security-conscious teams with hands-on skills, those on tight budgets, or companies wanting maximum customization. Pro Tip: Many vendors now blur the lines with WAF-as-a-Service offerings. Pick the mix that fits your risk appetite, traffic patterns, and compliance needs.
Now that you know what a WAF is and the different deployment types, let’s look at real-world solutions you can actually deploy. These run at the vendor’s edge or CDN and are fully managed. Perfect for fast, low-maintenance protection. When in doubt, start simple: test a free tier of a cloud WAF, learn how it works, then level up to more advanced configurations as your threat model matures.
When you understand how a Web Application Firewall is deployed, you can pick the right architecture for your network and risk profile. This is the most common setup. The WAF sits between your users and your web server, acting as a gatekeeper. All HTTP(S) traffic passes through the WAF first.
Pros: I Full request and response inspection I Easy to combine with caching or CDN features I Protects your true server IP from exposure In an inline setup, the WAF sits directly in the data path, inspecting packets without changing the source or destination IPs. An out-of-band WAF inspects copies of traffic (mirror/span port) and then injects TCP resets or other signals to stop malicious connections.
A solid Web Application Firewall does far more than simply block obvious threats. The best WAFs combine multiple detection methods and protective layers to handle both known and unknown attacks — without disrupting legitimate user traffic. Rulesets are the backbone of every WAF. These are pre-configured patterns that identify malicious requests. A common baseline is the open-source OWASP ModSecurity Core Rule Set (CRS) , which covers well-known threats like XSS, SQL Injection, Local File Inclusion (LFI), Remote File Inclusion (RFI), and more.
I Pro tip: Always start with your WAF in monitoring mode (also called detection or transparent mode) before enabling blocking. This helps you spot false positives without affecting users. Signature-based blocking isn’t enough anymore. Modern WAFs add behavioral and anomaly detection to catch new or evolving threats.
Some solutions include machine learning algorithms to reduce manual tuning and improve accuracy over time. A well-rounded WAF should offer more than just rulesets and anomaly detection. Look for: I Bot protection: Stops malicious bots, scrapers, and credential stuffing attacks by analyzing user agents, IP reputation, and request patterns. I DDoS mitigation: Many WAFs provide basic Layer 7 DDoS protection or integrate with upstream DDoS solutions to handle massive floods of malicious requests. I Custom rules & exceptions: You should be able to write your own custom logic to handle edge cases specific to your app. I Logging & detailed reporting: Attack logs, threat reports, and event correlation help you investigate incidents and tune your policies for better accuracy.
If your WAF is too strict, you’ll block real customers — if it’s too loose, you’ll miss attacks. Smart WAF management is all about balance: 4. Practical Deployment, Analysis & Case Studies Your WAF is not a “set it and forget it” solution — treat it like a living system that needs regular updates, tuning, and monitoring.
Tuning your Web Application Firewall is where the real security magic happens — and where many companies struggle. An out-of-the-box ruleset like OWASP CRS is a great start, but every app is unique. Without tuning, you’ll either miss real threats or frustrate users with false positives. A WAF that’s too strict blocks legitimate users. Too lenient, and attackers slip through. Tuning adjusts your rules to your specific application logic, traffic patterns, and business needs.
Before you enforce blocking, run your WAF in Detection Only mode. This logs what would be blocked, so you can: I Example: Many modern apps use JSON payloads or special headers that older rulesets may flag as unusual. Whenever your app changes (new endpoints, new frameworks, new third-party integrations), revisit your WAF. Many cloud-managed WAFs include automatic learning or auto-tuning. Use these features to reduce manual workload, but always validate changes — automated learning can sometimes introduce new gaps.
Your Web Application Firewall rarely works alone. To protect modern apps, you need to integrate your WAF smoothly into your delivery and security stack. Done well, you’ll boost performance, coverage, and manageability. Most cloud-managed WAFs double as Content Delivery Networks (CDNs) or bundle CDN-like capabilities out of the box. This means they can cache static assets, filter malicious requests, and absorb DDoS attacks right at the edge — without needing extra devices.
I Example: Cloudflare and Fastly are classic examples of WAFs that combine CDN, WAF, and DDoS features in one integrated service. This “all-in-one edge security” is why cloud WAFs are so popular for distributed apps. Modern apps rely heavily on APIs — and APIs are prime targets. Some WAFs, especially open-source options like ModSecurity or integrated platforms like AWS WAF with API Gateway, let you secure web traffic and API traffic together.
Key point: Many cloud WAFs provide basic API security features, but serious API traffic often runs through a dedicated gateway like Kong or NGINX Plus. Pairing your WAF with a gateway means you get robust routing, authentication, rate limiting, and the WAF inspects payloads for injections and other attacks. I Example: Use NGINX Plus or Kong Gateway with a tuned ModSecurity ruleset for full control. Remember: on-prem WAF appliances usually focus more on web traffic than APIs — so combining them with a separate API Gateway is best practice.
An on-premises WAF appliance like F5 BIG-IP ASM or Fortinet FortiWeb often comes with built-in load balancing capabilities. This is why physical WAFs are popular in data centers and enterprise networks — you get inspection, balancing, and failover in one box. I Example: F5 BIG-IP is both a load balancer and a WAF module in one — with advanced tuning and custom policies for each service. This consolidation reduces hardware sprawl and simplifies management.
Most WAFs are deployed as a reverse proxy , sitting between clients and your origin servers. This means they: I Tip: Reverse proxy mode helps ensure all inbound web traffic is inspected — but be mindful of latency and single points of failure. Many modern WAFs blur these lines intentionally to simplify operations — but you should still test integrations carefully to avoid misconfigurations or performance bottlenecks.
With smart integration, your WAF becomes an efficient multi-purpose shield — not a single-purpose bottleneck. Even with the best Web Application Firewall, poor configuration or neglect can leave you wide open. Let’s look at common pitfalls security teams make with WAFs — so you can avoid them. Too many teams deploy a WAF once and assume it’s bulletproof forever. Why it’s a problem: New vulnerabilities, app updates, or rule changes can lead to blind spots or break functionality. Fix: Review your WAF rules and logs regularly.
Automate updates where possible. Rolling out new rules or updates straight to production is asking for trouble. Why it’s a problem: Legitimate user requests can get blocked, leading to user frustration and revenue loss. Fix: Always test in a staging environment that mirrors live traffic. Whitelisting too much traffic can punch big holes in your security. Why it’s a problem: Attackers may exploit trusted paths to bypass protections. Fix: Keep exceptions tightly scoped and document who approved them.
A WAF can generate thousands of alerts. Many teams tune them out — or worse, don’t monitor them at all. Why it’s a problem: Real attacks slip through unnoticed. Fix: Integrate WAF logs into your SIEM or monitoring stack and build actionable alerts. Some teams see the WAF as a standalone shield. Why it’s a problem: Overlaps or gaps can happen with other tools like reverse proxies, CDNs, or DDoS solutions. Fix: Review your full traffic path and clarify where each control sits.
Regularly run simulated attacks — like SQL injection or XSS tests — to verify your WAF is working as intended. Tools like OWASP ZAP , Burp Suite , or even custom payloads can help you find weaknesses. Your Web Application Firewall is only as good as its configuration — so you need to test it safely and thoroughly. Always run tests in a controlled lab, staging, or dev environment , never on live production, and handle any malware or payloads with care.
Run WAF tests in CI/CD where possible. Always monitor logs and tune rulesets. A basic test scenario might include setting up a test page vulnerable to XSS, running an automated scan with ZAP or Burp, verifying that the WAF blocks the payload, and checking logs for alerts. Always contain malware samples safely and never test on live production. Web3 apps and decentralized platforms still rely on traditional web frontends, admin portals, and APIs — and that means they’re just as exposed to Layer 7 attacks as any other modern web app.
A Web Application Firewall plays an important role in protecting the web-facing components of your Web3 stack: Good Practice: Pair your WAF deployment with regular smart contract audits — the WAF handles the frontend Layer 7 threats, while audits ensure the on-chain code is secure. Tip: Don’t overlook rate limiting and geo-blocking for your Web3 APIs. A tuned WAF can help stop resource exhaustion and API abuse.
A curated list of trusted references, vendor docs, and testing tools to help you plan, deploy, tune, and test WAFs the right way. Modern web apps face relentless threats — but with the right Web Application Firewall , tuned rules, and testing approach, you’re already ahead of 90% of attackers. In this guide, you learned: I Got questions? Drop them in the comments — I read every one. I Stay updated: Check back regularly, this guide will be updated frequently, I try and upload every Friday.
Web Application Firewalls (WAFs) are critical components in modern cybersecurity, protecting web applications from threats like SQL injection, cross-site scripting (XSS), and other OWASP Top Ten vulnerabilities. In the context of DevSecOps, WAFs bridge development, security, and operations by embedding security controls into the software development lifecycle (SDLC). This tutorial provides a detailed exploration of WAFs, covering their concepts, architecture, setup, use cases, benefits, limitations, and best practices, tailored for DevSecOps practitioners.
A WAF is a security solution that monitors, filters, and blocks HTTP/HTTPS traffic to and from web applications based on predefined rules. Positioned between the client and the web server, it inspects requests and responses to detect and mitigate malicious activities. WAFs emerged in the late 1990s as web applications became prime targets for cyberattacks. Early solutions focused on basic request filtering, evolving into sophisticated systems with machine learning and behavioral analysis by the 2010s. The rise of DevSecOps in the 2010s emphasized integrating WAFs into CI/CD pipelines, aligning security with agile development.
DevSecOps integrates security into every phase of the SDLC, and WAFs play a pivotal role by: Understanding WAFs requires familiarity with essential terms and their integration into DevSecOps workflows. WAFs operate as a protective layer, analyzing HTTP traffic and applying security rules. Arrows depict bidirectional traffic flow through the WAF, with a logging module capturing events for analysis.
This section outlines the prerequisites and a step-by-step guide to set up ModSecurity, an open-source WAF, with Nginx. WAFs are indispensable in DevSecOps, providing robust protection for web applications while aligning with agile and secure development practices. As threats evolve, WAFs are incorporating AI-driven anomaly detection and deeper cloud integrations. Future trends include serverless WAFs and enhanced automation in CI/CD pipelines.
#Automation #CareerGrowth #CICD #CI_CD #CloudAutomation #CloudComputing #CloudDevOps #CloudNative #DataScience #DevOps #DevOpsAutomation #DevOpsCareer #DevOpsCareers #DevOpsSkills #DevOpsTools #DevOpsTraining #DevSecOps #EnterpriseDevOps #InfrastructureAsCode #ITTraining #Kubernetes #MachineLearning #Microservices #Observability #SiteReliabilityEngineering #SoftwareDelivery #SoftwareDevelopment #SRE #TechSkills #TechTraining 5. Performance Evaluation & Extended Technical Observations With two decades of industry experience and market data showing that nearly half of breaches begin with web applications, we manually tested three leading WAFs (Cloudflare, Imperva, Barracuda) against real attack traffic by creating a test site and targeting it with common web threats, broken access control, injection, and vulnerable and outdated components.
See a summary of our benchmark findings , a key features comparison of 10 leading WAF solutions: Ranking : Tools are ranked according to their average mitigation rate aggregated across all tested attack vectors: injection, broken-access, and vulnerable & outdated components. Disclaimer : The benchmark results are based on Cloudflare’s free tier, along with the trial versions of Imperva and Barracuda.
We use Cloudflare’s free plan for basic protection against external threats. Although configuration options are limited, the free plan remains a reliable, zero-cost alternative to paid WAF solutions for basic traffic filtering. Performs well in mitigating Broken Access Control and Security Misconfiguration attacks. We evaluated the trial version of Imperva App Protection. The solution provides layered traffic and security telemetry, including: Imperva performed best among the three platforms we experienced in stopping attacks on outdated or vulnerable components, with a 93% success rate.
Trial version of Barracuda Application Protection is utilized in our benchmark. Barracuda’s WAF offers a clear, easy-to-use dashboard. It gives quick access to event data, faster than other tools we tested. The platform outperforms other three platforms in the injection attacks with a 91% mitigation rate. To compare these tools, we used OWASP ZAP, a testing tool that simulates attacks on websites. We created a test site and targeted it with common web threats. These threats come from the OWASP Top 10, a list of the most serious web application security risks. 1 We chose one of the most common attacks: broken access control, injection, and vulnerable and outdated components. They include: The effectiveness of the WAF was evaluated based on whether the WAF solutions successfully identified the malicious payload and blocked the request, typically returning an HTTP 403 Forbidden status code, verified through the WAF provider’s security event logs/dashboard. The ability of each tool to detect and block these threats was evaluated based on its mitigation rate.
The benchmark highlights differences in how each WAF handles various attack types. Barracuda achieved the highest injection mitigation rate (91%), reflecting its focus on low-latency detection and detailed threat analytics. Imperva performed best against vulnerable and outdated components (93%), benefiting from layered traffic monitoring and comprehensive attack telemetry. Cloudflare , tested on its free plan, showed solid overall mitigation (86–87%) but has limited customization and analytics compared with the other two.
These differences stem from each platform’s design priorities, dashboard capabilities, and inspection methods: Barracuda emphasizes fast, granular detection; Imperva emphasizes comprehensive monitoring and analysis; Cloudflare emphasizes basic, zero-cost protection with fewer configuration options. FortiWeb is a web application firewall that protects critical web applications and APIs from both common and advanced threats, including bots, DDoS attacks, and zero-day exploits. It uses machine learning to detect unusual behavior, reduce false alarms, and cut down on manual work. FortiWeb also helps with API security by automatically discovering them and applying tailored protection policies without slowing down legitimate traffic.
Azure Web Application Firewall provides built-in defenses against attacks at both the app and network edge. It uses regularly updated rule sets to detect threats, reduce false positives, and support compliance needs. With easy deployment, centralized management, and detailed security logs, it helps teams monitor risks and maintain secure operations. Imperva Web Application Firewall defends against attacks like SQL injection and cross-site scripting, while keeping false alarms low. It works across cloud, on-premises, and hybrid setups, adapting to both new and older systems. Built-in machine learning and global threat updates help teams spot and respond to real threats faster.
Cloudflare WAF protects web applications from threats, including zero-day attacks, by using global threat intelligence and machine learning. It can automatically block emerging threats in real time and offers easy setup with minimal management. The WAF uses both managed and custom rules to defend against common attacks like SQL injection, malware uploads, and credential stuffing.
AWS WAF helps protect your web applications from common online threats by filtering traffic before it reaches your system. It comes with preconfigured rules to block attacks like SQL injection, cross-site scripting, or large volumes of requests from a single source. You can also set up custom rules and monitor suspicious activity using built-in tools like IP reputation checks and traffic analysis.
It launched an AI Activity Dashboard in February 2026 with rule packs that classify AI scrapers, AI tools, and AI agents separately. 2 Fastly Next-Gen WAF protects web apps and APIs from both common and complex threats, like bots, account takeovers, and API abuse. It works wherever your apps are, on the edge, in the cloud, or on-prem, without needing a lot of setup or tuning.
With clear reporting, fast alerts, and flexible deployment options, it helps teams spot and stop attacks quickly. Radware Cloud WAF adjusts to changing threats in real time and offers simple, clear insights into unusual activity. It supports a wide range of setups, including hybrid and cloud environments, and keeps protections up to date without adding extra work for in-house teams.
Barracuda Web Application Firewall helps protect websites, APIs, and mobile apps from common and advanced cyber threats. It integrates with cloud services, provides bot protection, and adapts easily to rapidly changing DevOps environments. With clear dashboards and built-in automation tools, it also simplifies security tasks and gives teams better control over app traffic and access.
As one of the web application firewall solutions, F5 BIG-IP Advanced WAF uses behavioral analytics and machine learning to detect and respond to threats, including application-layer attacks and automated bots. It supports modern API protocols and helps manage security through flexible deployment and integration with DevOps workflows. Sensitive data is protected at the application layer, and configurations can be automated using declarative APIs.
HAProxy Enterprise WAF claims to offer reliable protection against common application attacks like SQLi and XSS. It uses machine learning and threat intelligence to detect threats with minimal impact on performance. The system is designed for easy management and low latency, helping organizations maintain security without complex configurations. Rate limiting is a key feature in many WAF solutions used to manage how often a client, such as a user, bot, or application, can send requests to a server. It helps protect web applications from being overwhelmed by malicious or accidental spikes in traffic.
By setting limits on the number of HTTP requests that can be made within a given time frame, WAF solutions can delay or block traffic that exhibits abnormal behavior. This makes it harder for bad actors to succeed without disrupting legitimate traffic. Example in action: An online service uses a cloud-based WAF to restrict each IP to 20 requests per minute. A second rule limits traffic per user-agent header to 500 requests per hour. This dual-layer approach blocks scraping bots and prevents service degradation while allowing real users to browse freely.
While rate limiting handles how often requests are made, zero-day protection focuses on what’s inside those requests. Zero-day threats exploit web application vulnerabilities that haven’t been patched or even discovered yet. These are especially dangerous because traditional security tools may not recognize the attack pattern. Modern WAF systems use an adaptive security engine that inspects web requests in real time. These engines learn from evolving threats and can block suspicious behavior even if the specific threat is new.
Blocking is one of the most basic but powerful WAF features. It automatically stops traffic that matches known attack patterns or violates set rules. Blocking helps prevent known threats from reaching your app. It reduces the risk of damage or data loss. Custom rules let security teams set up their own conditions to allow or block traffic. You can write rules based on IP addresses, URLs, request methods, or even keywords in the request.
Most WAFs offer built-in protection against the OWASP Top 10, a list of the most serious web application risks. The current version is the OWASP Top 10:2025, released in November 2025 at the Global AppSec Conference and finalized in January 2026. 3 The most current version includes: By covering these threats, WAFs help reduce the most common security gaps in web apps.
Web Application Firewalls (WAFs) provide web application security by detecting and blocking malicious traffic in real time. They work in two main ways: 4 This method relies on known attack patterns, or “signatures.” When a request matches one of these patterns, the WAF blocks it. This is fast and effective against known threats like SQL injection or cross-site scripting.
This approach uses machine learning to understand what “normal” traffic looks like. It then flags anything unusual, even if it’s a new or unknown type of attack. Techniques include classification algorithms, neural networks, and decision trees. Many modern WAFs use both methods together. This helps catch both known and new (zero-day) attacks. Hybrid models offer: A web application firewall (WAF) is a security tool placed in front of web applications. It checks incoming and outgoing web traffic (HTTP) to detect and block harmful activity. A WAF works independently of the web app itself and can be either software or hardware. It protects web apps from attacks by applying security rules, especially when the app has weak or outdated code.
A WAF (Web Application Firewall) filters HTTP traffic to block attacks like SQL injection and cross-site scripting. A WAAP (Web Application and API Protection) is a broader platform that provides DDoS protection, bot management, and API security from a single console. Most vendors sold as “WAFs” in 2026 are actually WAAPs. If your applications use APIs or face AI bot traffic (most do), a WAAP is closer to what you need.
Modern WAFs treat AI bots as a distinct category, separate from older scrapers. Detection relies on a mix of declared user agents (GPTBot, ClaudeBot), TLS fingerprints, and behavioral scoring, since well-funded crawlers can rotate IPs and mimic human browsing patterns. Controls range from blocking specific crawlers to per-prompt inspection for applications that expose LLM endpoints. Ask vendors whether they distinguish between AI scrapers (training data), AI tools (search and retrieval), and AI agents (autonomous task completion). Each calls for a different response.
Pick the format that matches where you're publishing. Pasting the link version into your CMS preserves the backlink. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Web%20application%20firewall • https://en.wikipedia.org/wiki/Application%20firewall • https://en.wikipedia.org/wiki/Application%20security • https://learn.microsoft.com/en-us/azure/web-application-firewall/ • https://docs.oracle.com/en-us/iaas/Content/WAF/home.htm • https://docs.oracle.com/en-us/iaas/Content/WAF/Concepts/overview.htm • https://docs.aws.amazon.com/solutions/latest/security-automations-for-aws-waf/architecture-overview.html • https://developers.cloudflare.com/waf/ • https://docs.aws.amazon.com/waf/ • https://pentesterr.com/blog/web-application-firewall-guide
Extracted Research Figures & Simulation Topologies
Total 1 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Web Application Firewall Implementation Using Python.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Web Application Firewall Implementation Using Python... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |