Complete Technical Paper Content — Web Application Vulnerability Scanner Using Python Source Code
Overview & System Context
Web Application Vulnerability Scanner Using Python Source Code: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9507 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Safely simulate real-world attacks against your internal and external infrastructure with a 30-day snapshot-in-time subscription. Confirm which vulnerabilities are actually exploitable, prioritize the fixes that matter, and prove the fix worked, all inside your test window.
Purpose-built to safely exploit, not just enumerate. Attack surface discovery, production-safe playbooks, prioritized findings, and audit-ready reports in one secure portal, as a 30-day snapshot-in-time subscription. Kick off a full internal or external run in minutes, no installer or field engineer required. A defined 30-day window to test, remediate, and retest so you get a clean snapshot in time of your security posture.
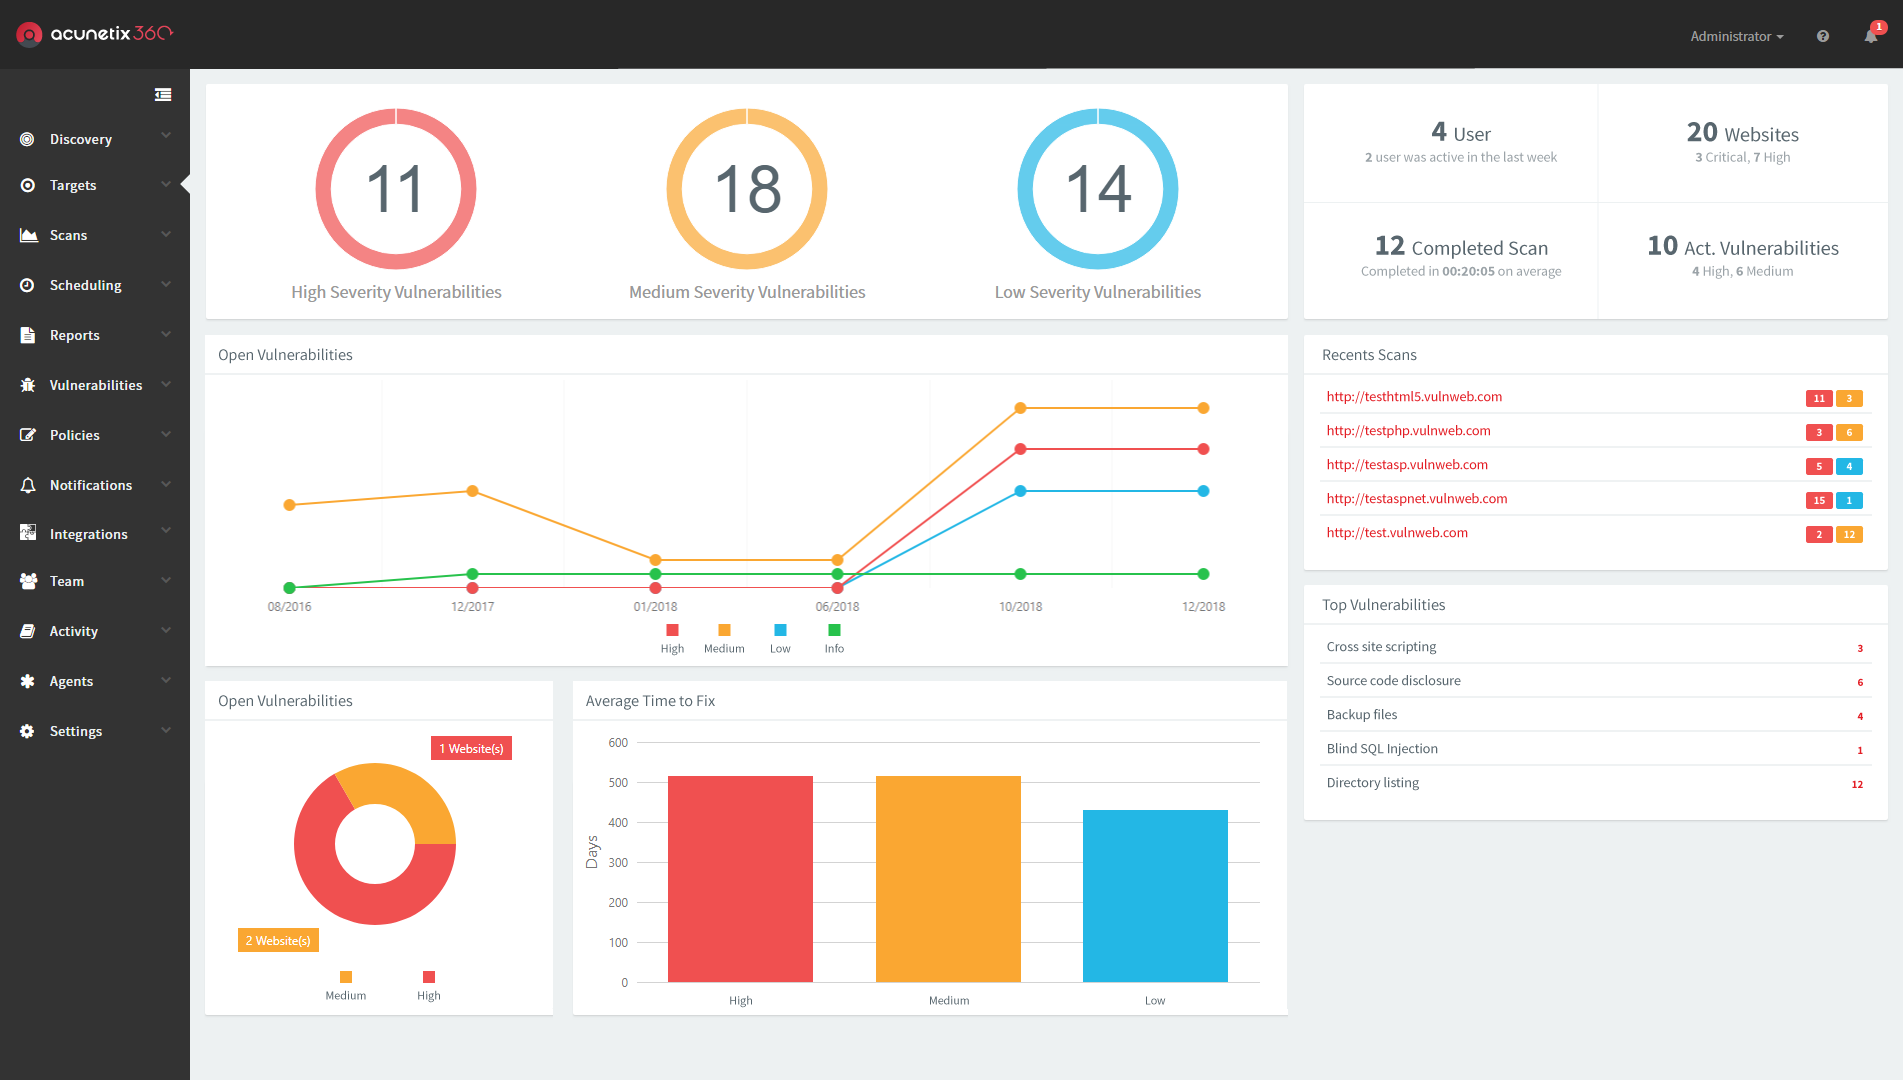
Figure 1: 13 Best Web Application Vulnerability Scanners for 2026 Production-safe playbooks confirm exploitability so your team stops chasing false positives. Perimeter, internal network, Active Directory, cloud, and web applications from one platform. Every finding is tagged to the ATT&CK tactic and technique attackers use in the real world.
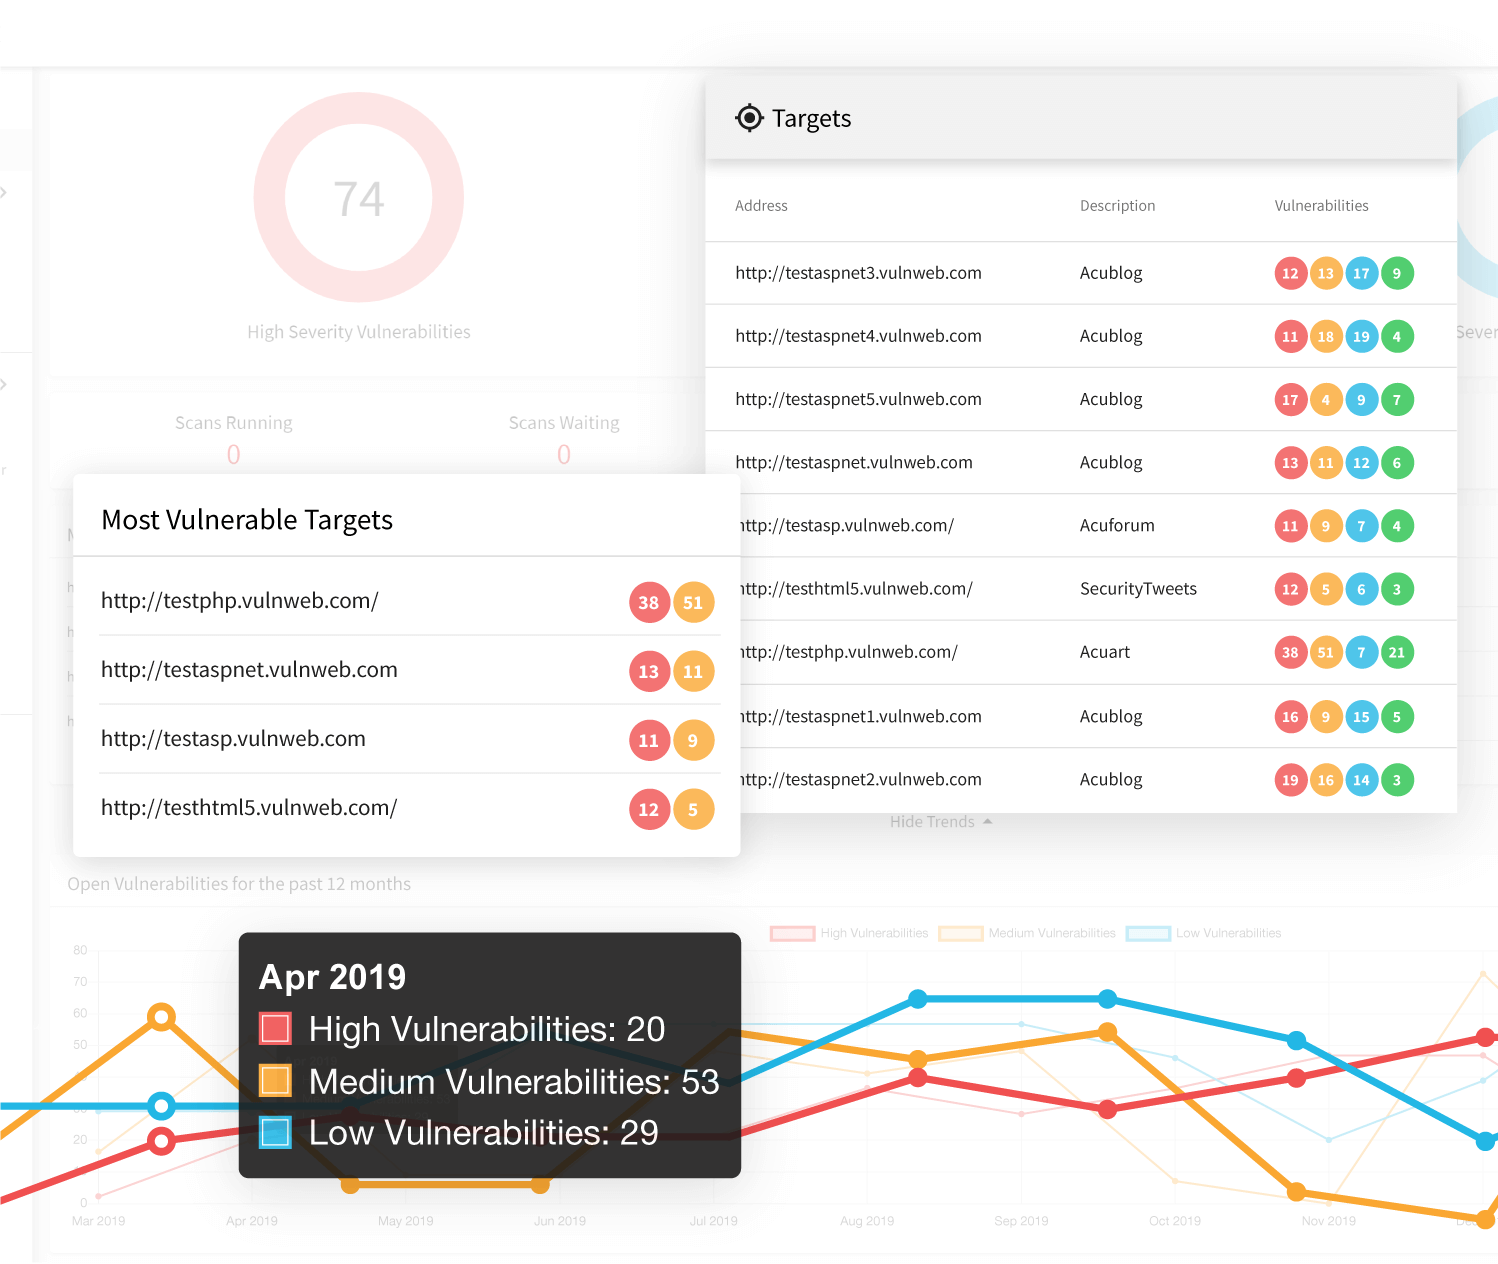
Fix a vulnerability and re-run the exact scenario any time inside your 30-day subscription to prove the fix. Figure 2: Vulnerability Scanner – Automated Web App Security Testing Executive summary, technical detail with proof-of-exploit, and remediation guidance in every report. Our SOC engineers are available around the clock for questions about your automated pen test.
No installers, no field engineers, no six-week wait. Launch on demand or on a schedule and get results while your coffee is still warm. Define internal and external targets, exclusions, and testing windows in the portal. No agents required for external testing; a lightweight collector handles internal segments.
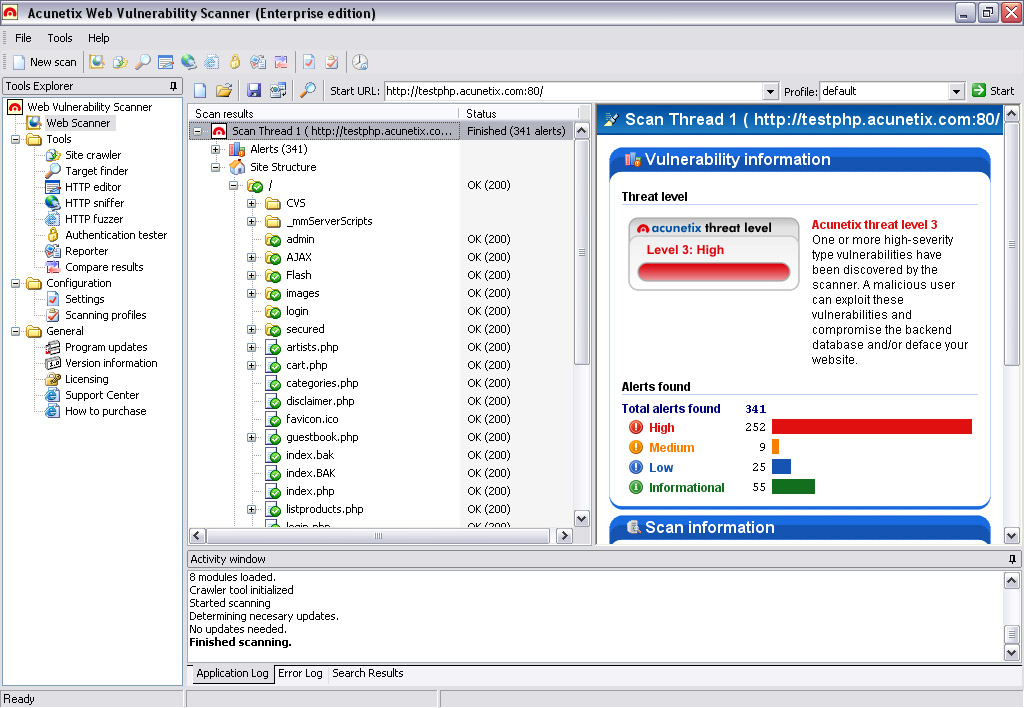
Figure 3: Acunetix Web Vulnerability Scanner 4.0 - Help Net Security The platform enumerates your in-scope attack surface, IPs, subdomains, services, and cloud assets, at the start of your 30-day subscription. Production-safe playbooks mapped to MITRE ATT&CK attempt real exploitation, credential reuse, and privilege escalation to confirm what an attacker could actually do.
Findings are ranked by exploitability and blast radius, with fix guidance, example configurations, and AI-drafted remediation steps. Re-run the exact scenario to confirm the fix, then export executive and technical reports with proof-of-exploit evidence for auditors.
Real breaches rarely stop at the perimeter. Our platform runs both sides of the fence: outside-in against your public attack surface, and inside-out from a foothold to see how far an intruder could reach. Perimeter services, exposed applications, subdomains, and shadow assets you did not know were public. Lateral movement, privilege escalation, Kerberoasting, credential reuse, and misconfigured shares from an assumed-breach starting point.
Authentication flaws, injection, access control, and business-logic weak points on your public and internal apps. IAM misconfigurations, over-permissive roles, and exposed storage across AWS, Azure, and Google Cloud. Web application penetration testing is included as a capability of our automated pen test. We test behind the login, follow real user sessions, and exercise your supported APIs so the flaws only authenticated users can reach do not stay hidden.
Testing behind the login with valid credentials, so flaws that only appear to signed-in users are found and proven. Exercise the REST and service endpoints behind your app to catch broken authorization, injection, and data exposure. Sessions, tokens, and multi-step flows are maintained through the run so deep application paths stay in scope. Checks for logic abuse such as privilege jumps, forced browsing, and workflow bypasses that signature scanners miss.
Every confirmed finding ships with technical evidence, executive reporting, and step-by-step remediation guidance. Fix an application finding and re-run the same test inside your 30-day window to confirm the issue is closed. Prove control effectiveness continuously for PCI DSS, HIPAA, SOC 2, ISO 27001, and cyber insurance renewals. Catch exploitable regressions the same week they ship instead of during an annual test.
Get real attacker perspective on your environment without hiring or contracting a full test crew. Validate that internet-facing systems in the cardholder data environment cannot be exploited between quarterly ASV scans. Every run produces an executive summary, technical detail with proof-of-exploit evidence, remediation guidance, and retest confirmation. Reports support PCI DSS 4.0.1 Requirement 11.4, HIPAA Security Rule, SOC 2 CC7, ISO 27001 A.12.6, and cyber-insurance renewals. Pair with PCI ASV Scanning and SIEM & Endpoint Protection for a full detect, validate, and prove cycle.
Recurring exploit validation to satisfy risk-analysis and continuous-monitoring controls. Add the Clone Systems AI assistant to any plan. It explains findings in plain English, drafts remediation for your exact stack, and ranks confirmed exploits by real business impact so your team fixes what matters first. Automated pen testing pairs cleanly with expert-led engagements, external ASV scanning, and 24/7 managed detection.
Expert-led engagements for business-logic flaws and creative attack chains automation cannot find. Quarterly external vulnerability scanning by a PCI SSC Approved Scanning Vendor since 2007. 24/7 SOC monitoring so exploits confirmed here are also detected in real time in production. Same-day onboarding, production-safe playbooks, retests inside your 30-day subscription, and audit-ready reports. Talk to a security specialist and get scoping guidance for your environment.
Author: Bhavya Bhalla Institution: Thapar Institute of Engineering and Technology Project Type: Cybersecurity Internship - Elevate Labs This project implements a comprehensive web vulnerability assessment platform that automates the detection of common web application security vulnerabilities. The system combines industry-standard security testing methodologies with a professional web interface suitable for client demonstrations and security assessments.
Python 3.9+ III Flask Web Framework III BeautifulSoup4 (HTML Parsing) III Requests (HTTP Client) III Threading (Concurrent Processing) III JSON Reporting System HTML5 + CSS3 + Vanilla JavaScript III Responsive Design III Real-time API Communication III Progressive Web App Features III Professional UI/UX OWASP Testing Framework III Top 10 Vulnerability Coverage III Automated Payload Injection III Error Pattern Recognition III Security Header Validation Clone Repository git clone https://github.com/yourusername/web-vulnerability-scanner.git cd web-vulnerability-scanner Setup Environment python -m venv venv source venv/bin/activate # Windows: venv\Scripts\activate pip install -r requirements.txt Test against public vulnerable application python src/vulnerability_scanner.py --target http://testphp.vulnweb.com/ POST /api/scan # Start new scan GET /api/scan/{id}/status # Check scan progress GET /api/scan/{id}/report # Get detailed report GET /api/scans # List all scans GET /api/scan/{id}/download # Download report file SQL Injection Detection: { "type": "SQL Injection", "severity": "Critical", "url": " https://target.com/login.php ", "payload": "' OR 1=1--", "description": "SQL Injection vulnerability detected...", "recommendation": "Use parameterized queries..." } XSS Detection: { "type": "Cross-Site Scripting (XSS)", "severity": "High", "url": " https://target.com/search.php ", "payload": "", "description": "Reflected XSS vulnerability found...", "recommendation": "Implement input validation..." } Crawling Configuration MAX_CRAWL_DEPTH = 2 # Website exploration depth MAX_LINKS_PER_PAGE = 10 # Links to follow per page REQUEST_TIMEOUT = 10 # HTTP request timeout (seconds) Payload Configuration XSS_PAYLOADS = [...] # Custom XSS attack vectors SQL_PAYLOADS = [...] # Custom SQL injection payloads http://testphp.vulnweb.com/ # Public test site http://demo.testfire.net/ # IBM Security AppScan demo https://xss-game.appspot.com/ # Google XSS challenge web-vulnerability-scanner/ III src/ I III vulnerability_scanner.py # Core scanning engine I III flask_app.py # Web application server III templates/ I III index.html # Dashboard interface III static/ I III style.css # Custom styling III reports/ I III *.json # Generated scan reports III tests/ I III test_scanner.py # Unit tests III docs/ I III api_documentation.md # API reference III requirements.txt # Python dependencies III README.md # Project documentation III .gitignore # Git ignore rules III LICENSE # Project license Bhavya Bhalla I Email: bhavyabhalla19@gmail.com I LinkedIn: linkedin.com/in/bhavya-bhalla-235300258 I GitHub: github.com/bhavya-bhalla Institution: Thapar Institute of Engineering and Technology Course: B.E. Computer Engineering (2022-2026) CGPA: 7.20/10.0 "Bridging technical security expertise with business impact through innovative vulnerability assessment solutions." 2. System Architecture & Core Working Principles Professional web vulnerability assessment platform with automated XSS and SQL injection detection. Built with Python/Flask featuring real-time scanning dashboard and comprehensive security reporting.
VulnerabilityHub follows a modern three-tier architecture, designed for scalability and maintainability. It separates the presentation layer (Frontend) from the business logic (Backend API) and data persistence (Database). It handles user authentication, scan management, built-in insights visualizations, and administration interfaces. Key Responsibilities : - XML Parsing (Greenbone/OpenVAS reports) - Business Logic (Disputes, Notifications, Imports) - Background Tasks (Email sending, File processing) - Audit Logging (Comprehensive tracking of actions) - Virus Scanning : Integrated with ClamAV to scan all uploaded files. - Greenbone Integration : An optional GMP connector imports reviewed targets Insights Overview : Built-in charts surface vulnerability trends, prioritization signals, and forecasts directly in the application.
Metrics Endpoint : The backend exposes Prometheus-compatible application metrics for external scraping. For detailed diagrams of system interactions (Scan Upload, Dispute Resolution, etc.), please refer to Data Flows . Audit Logging : Every critical action (create/update/delete, file access) is logged to the audit_logs table. See Audit Logging . Input Validation : Strict typing with Pydantic prevents injection and data corruption.
Network Isolation : Database and internal services are not exposed publicly in production environments. A web application vulnerability scanner helps identify security weaknesses in live web applications and APIs before attackers can exploit them. At MSSP Security, we believe automated scanning is essential for reducing manual effort, prioritizing real risks, and supporting continuous application security.
Effective scanners detect issues such as SQL injection, cross-site scripting, misconfigurations, and outdated components, while working alongside secure coding, manual testing, and ongoing monitoring. Want to learn how web application vulnerability scanners work and how to choose the right solution? Keep reading. Together, these practices create a stronger, more effective web application security strategy that keeps pace with evolving threats.
In our work with MSSPs, we often explain web app scanning like this: it’s a piece of software that acts as an ethical attacker. It crawls a live app or API, mapping pages, following links, testing forms, and sending controlled payloads to find the same weaknesses a real attacker would look for. We’ve found the platforms that work best use proof-based detection. They don’t just guess; they confirm the flaw exists before raising an alert. This is vital, because dynamic testing, as OWASP points out, catches runtime problems that static code reviews can miss.
The real value, in our view, comes from making this a continuous process, not a yearly box-ticking exercise. A scanner constantly re-evaluates an application as it changes, checking new code, updated third-party libraries, authentication flows, and cloud deployments. This ongoing assessment is non-negotiable now. Before any testing begins, a scanner has to do its groundwork. It crawls everything: websites, APIs, and JavaScript-heavy single-page apps, to build a complete inventory of the attack surface.
Then it runs a mix of active and passive security checks, finishing with reports that include solid evidence for developers to fix. Modern tools don’t just blindly request every URL. They use intelligent discovery. A good scanner has a security-focused crawler that can follow complex application workflows, handle authenticated sessions, and find hidden endpoints across websites, REST APIs, GraphQL, and SPAs.
Once the map is built, dynamic application security testing (DAST) starts. The tool sends controlled payloads to simulate attacks, checking for SQL injection, cross-site scripting, CSRF, SSRF, XXE, broken authentication, and IDOR vulnerabilities. It watches the application’s responses for signs of success. The goal isn’t to flood teams with alerts. Leading scanners now prioritize validated findings, backing them up with request/response pairs, screenshots, or out-of-band verification to cut down on false positives.
“The design of a WVS includes three core components as per the usage scenario. First, the crawler module grabs the content of the web pages. Second, the attacker module is designated for launching the attacks. Third, the analysis module highlights vulnerabilities.” – IEEE Access Our experience auditing these tools for MSSPs shows that the workflow of intelligent discovery, proof-based active testing, and thorough passive analysis is what separates a useful security asset from a noisy one.
A scanner’s job is to combine intelligent crawling, passive inspection, and active attack simulation against a live application. This combination of techniques reflects modern vulnerability scanner technology designed to identify security weaknesses with greater accuracy while reducing unnecessary alerts. This approach starts with discovery, and frankly, that’s where many organizations are weakest. Industry surveys indicate low visibility into app inventories.
We see this all the time in our audits: forgotten staging systems, legacy APIs, and temporary cloud deployments left exposed long after a project ends. This lack of visibility is why automated discovery is now essential. Modern web environments have outgrown simple HTML parsing.
If your scanner relies on basic GET and POST requests, it is essentially blind to modern frontends. In our SOC pipeline, we mandate engine testing that handles asynchronous DOM rendering natively. The typical workflow breaks down into five stages, illustrating how vulnerability scanners work in modern environments: For enterprise environments, risk-based vulnerability prioritization is a game-changer. It helps security teams focus on what’s actually exploitable instead of just counting total flaws.
Modern scanners cover the OWASP Top 10 and a lot more. In our work with MSSPs, clients often start by looking for the obvious risks like SQL injection or cross-site scripting. A mature security posture, however, goes much further, evaluating authentication, authorization, APIs, and cloud-native deployments. Beyond that, advanced scanners are adding support for containerized apps, cloud-native architectures, headless CMS platforms, microservices, and even specific platforms like WordPress.
It’s important to remember automation has limits. Business logic flaws, race conditions, and complex authorization chains are still tough for any scanner to catch reliably. These areas require experienced analysts and periodic manual penetration testing to uncover. Each testing approach identifies different classes of security issues and fits a different phase of the software lifecycle.
We generally recommend treating these approaches as complementary instead of competing. A DAST tool validates the application’s behavior from the outside, while SAST identifies coding flaws earlier in development and IAST combines runtime insight with code awareness. That figure reinforces why relying on only one testing method rarely provides sufficient coverage.
“With each technique, we found unique vulnerabilities not found using the other techniques.” – Elder, S., et al. Accuracy matters far more than the number of reported vulnerabilities. From our experience at MSSP Security, organizations gain more value from scanners that produce actionable findings than platforms that generate thousands of unverified alerts. Security teams should evaluate how well a solution handles authentication, modern frameworks, reporting, and automation.
Automated scanners cannot replace experienced security professionals. They excel at identifying repeatable technical weaknesses but struggle with complex business logic, chained authorization issues, and application-specific workflows. Even today, automation alone cannot identify every meaningful security risk. That said, automation dramatically reduces repetitive work and allows specialists to focus on higher-value security analysis.
Careful planning protects both application stability and scan quality. We encourage organizations to define scope before running any production-safe scanner. Production environments often require rate limiting, maintenance windows, stakeholder approval, and carefully tuned scan profiles. Continuous scanning improves security without unnecessarily slowing development. Modern organizations increasingly integrate a CI/CD security scanner, pipeline security scanner, GitHub Actions security scan, GitLab CI vulnerability scan, Jenkins security plugin, and command-line vulnerability scanner into automated release pipelines.
This approach enables faster feedback while giving developers enough context to fix issues before deployment. The best web application vulnerability scanner matches your technology stack, security maturity, compliance requirements, and operational workflow. Organizations comparing platforms such as Nessus, Qualys, and Rapid7 should evaluate detection accuracy, authentication support, automation capabilities, and reporting based on their own operational requirements.
When we work with organizations through MSSP Security, the discussion rarely starts with features alone. Instead, we first examine application architecture, authentication complexity, regulatory obligations, and internal security resources. That practical assessment usually produces better long-term outcomes than selecting a platform based solely on marketing claims.
Organizations with compliance obligations should also evaluate PCI DSS web scanner, ISO 27001 vulnerability scanner, and SOC 2 web app scanner capabilities alongside reporting and remediation workflows. Modern DevSecOps practices integrate vulnerability scanning directly into the CI/CD pipeline so security checks occur automatically during every build and deployment. Instead of waiting until an application reaches production, the scanner evaluates code, dependencies, and application behavior early in the development lifecycle.
This approach helps teams identify vulnerabilities sooner, reduce remediation costs, and ensure that only builds meeting predefined security requirements progress to deployment, making security a continuous part of software delivery rather than a final checkpoint. What is the difference between a web application vulnerability scanner and a DAST tool? A web application vulnerability scanner automatically examines running websites and APIs for known security weaknesses. A DAST tool, which stands for dynamic application security testing, analyzes applications from the outside while they are running instead of reviewing source code. Many solutions combine automated vulnerability assessment, crawl and scan tool functionality, and proof-based vulnerability detection to produce reliable findings with fewer false positives.
A web app security scanner can detect many common security issues, including SQL injection, cross-site scripting, broken authentication, security misconfiguration, outdated components, insecure deserialization, IDOR, SSRF, XXE, and CSRF vulnerabilities. Features such as an OWASP Top 10 scanner, SQL injection scanner, cross-site scripting detector, XSS vulnerability scanner, and CSRF detection tool help identify these risks before they become serious security incidents.
Yes. Modern scanners often include an API security scanner that supports both REST API vulnerability scanner and GraphQL security scanner capabilities. Many tools also use a headless browser scanner to evaluate single-page applications through SPA vulnerability scanner and JavaScript-heavy app scanner features. An authenticated vulnerability scan can assess protected areas, while an unauthenticated web scan evaluates publicly accessible pages.
Organizations often integrate scanning into software delivery by using a CI/CD security scanner, DevSecOps integration tool, or pipeline security scanner. Many platforms also support GitHub Actions security scan, GitLab CI vulnerability scan, Jenkins security plugin, and a REST API for scanner automation. Compliance scanning tool features help organizations verify security controls for PCI DSS, ISO 27001, and SOC 2 requirements.
Organizations can improve scan accuracy by enabling features such as a false positive reduction scanner, exploit evidence scanner, out-of-band detection tool, authenticated vulnerability scan, and session handling scanner. A production-safe scanner, read-only scan mode, destructive scan prevention, and risk-based vulnerability prioritization also help security teams identify verified vulnerabilities without disrupting production environments.
Web application threats don’t stay the same, and waiting until the end of development often leaves gaps that are harder to fix. Regular vulnerability scanning helps you catch real security issues sooner, giving your team more time to respond before they become costly problems. Making automated scanning part of your daily workflow is a simple way to strengthen long-term security. If your organization needs additional expertise, MSSP Security’s consulting services help MSSPs streamline operations, reduce tool sprawl, optimize security stacks, and improve service quality through vendor-neutral recommendations, technology assessments, proof-of-concept support, and actionable guidance backed by more than 15 years of experience and 48,000+ completed projects.
Web applications are prime targets for cyberattacks. Regular vulnerability scanning helps identify security weaknesses before attackers exploit them. Automated security scanning is essential for: 3. Software Implementation, Frameworks & Protocols Select an automated web application security scanner like SecuraProbe. Consider factors like deployment options (SaaS vs on-premise), pricing, and integration capabilities.
Sign up for a free trial account. Most platforms offer free trials with credits. Get your API key from the dashboard for programmatic access. Determine which web application you want to scan. This could be a production site, staging environment, or local development server accessible via URL.
If your application requires login, configure authentication in the scanner. This may include form-based auth, HTTP basic auth, or API token authentication. Configure scan settings including scan depth, vulnerability types to test, excluded URLs, and scan schedule. Choose between quick, standard, or deep scan profiles.
Initiate the scan through the web interface, API, or CLI. The scanner will automatically crawl your application and test for vulnerabilities. Monitor the scan progress in real-time. Most scanners provide progress indicators and estimated completion time. Once complete, review the security report. Examine identified vulnerabilities, their severity (critical, high, medium, low), and affected endpoints.
Prioritize vulnerabilities based on severity and business impact. Focus on critical and high-severity issues first, especially those affecting sensitive data or authentication. Fix vulnerabilities using the remediation guidance provided in the report. Common fixes include input validation, secure coding practices, and security configuration updates.
Run another scan after implementing fixes to verify that vulnerabilities have been resolved. This confirms your remediation efforts were successful. Configure automated scheduled scans or integrate scanning into your CI/CD pipeline for continuous security monitoring as your application evolves.
Fast scans (5-10 minutes) for rapid feedback during development. Ideal for quick checks before commits. Balanced scans (15-30 minutes) for regular security testing. Good for scheduled scans and CI/CD integration. Comprehensive scans (1-4 hours) for thorough security audits. Best for pre-production and compliance scans. Specialized scans for REST and GraphQL APIs. Tests API endpoints, authentication, and OWASP API Top 10.
Set up automated scheduled scans to catch new vulnerabilities as your application evolves. Scan staging or preview environments rather than production to avoid impacting live users. Focus on fixing critical and high-severity vulnerabilities first, especially those affecting sensitive data. SecuraProbe makes it easy to scan web applications for vulnerabilities. Get started with our free trial and scan your first application in minutes.
Vulnerability scanning is a fundamental cybersecurity practice for automating security testing. Especially in application security, it’s crucial to have a good vulnerability scanner that can automatically probe your app and API attack surface for security weaknesses and help your teams plug any identified vulnerabilities before they turn into data breaches or worse. This article discusses vulnerability scanning tools relevant to securing modern web applications, so we’re not talking about network security scanners that find network vulnerabilities such as open ports or exposed operating system services. When pointed at a website or application, network scanners can only identify a handful of external application security issues like web server misconfigurations or outdated server software, making up a tiny proportion of what a dedicated web vulnerability scanner can find.
Web vulnerability scanners are used to automatically test running applications for security vulnerabilities. This approach is called dynamic application security testing, or DAST, and since web applications make up the vast majority of today’s business software, web security scanners are also called DAST tools . At the most basic level, a web vulnerability scanner interacts with a website, application, or API in similar ways that a human user or interfacing external system would. However, instead of simulating valid and expected operations, the tool simulates (safely) the actions of an attacker who is trying to find security flaws and exploit them to extract sensitive data or gain unauthorized access. You can think of a DAST scanner as an automatic penetration tester who works extremely fast, never gets tired, and has a wider arsenal of tricks than any individual tester.
Vulnerability scanning examines web applications from the outside without requiring source code access or any knowledge of their internal workings, so it’s also referred to as black-box security testing. Professional DAST tools are extremely versatile and can cover many use cases across information security and application security, from vulnerability assessments and automated penetration testing to dynamic testing at multiple points in the software development lifecycle.
There are many vulnerability scanners out there, and each one will be slightly different in how it does things and what functionality it provides besides actual scanning, but there are three broad stages to any web application scanning process: There are many ways to categorize vulnerability scans (see Types of vulnerability scans below), but the general process is for the scanner to send HTTP requests to a target URL, inserting test values (payloads) into identified parameters and then observing how the application reacts. In the most basic case, this could mean trying out various form values to see if the application is vulnerable to an injection attack like SQL injection or cross-site scripting (XSS). For each parameter on each page, a good scanner will test for multiple vulnerabilities, often trying out multiple payloads for each one. This gives you a way to safely and extremely quickly simulate cyberattacks and imitate the potential actions of malicious hackers trying to compromise your systems.
To add an extra layer of complexity, practically all web-facing business apps require authentication to access any valuable functionality, so authenticating the scanner is another prerequisite step in the vulnerability scanning process. Fully automated vulnerability scanning requires automated authentication, which is only possible with more advanced DAST tools. When it comes to vulnerabilities, terminology can get a little fuzzy. Strictly speaking, CWEs are potential weaknesses, while CVEs are reported vulnerabilities in specific products. The Common Weakness Enumeration (CWE) catalog lists software and hardware security weaknesses that could result in vulnerabilities if implemented in production. The Common Vulnerabilities and Exposures (CVE) database lists confirmed and publicly reported security defects.
In practice, it’s common to call any identified security weaknesses a vulnerability, especially when talking about security issues that have been verified and confirmed, whether manually or automatically. Any decent vulnerability scanner should be able to find both CWEs (security weaknesses in code that could result in new vulnerabilities) and CVEs (known vulnerable products and components), as well as security issues such as misconfigurations that don’t directly result from insecure code. Each class of security flaws requires a different approach to identify as many real issues as possible while avoiding false positives.
The ability to automatically find new vulnerabilities is what makes DAST tools unique among vulnerability scanners. The scanner needs to have an extensive collection of active security checks that allow it to probe for weaknesses (Invicti DAST has over a thousand), but it also needs smart and reliable ways of identifying vulnerable behaviors triggered by its mock attacks. Some vulnerabilities may be identified directly in server responses to test requests, while others will require indirect or out-of-band observation.
Application behaviors in response to testing can be ambiguous, so finding a way to automatically verify findings has been the holy grail of vulnerability scanning. The Invicti platform uses proof-based scanning to safely exploit many common vulnerabilities and extract proof that the issue is real and remotely exploitable. This clearly shows which vulnerabilities are definitely not false positives and can go straight to remediation.
Finding CVEs is a bit different because a CVE corresponds to a piece of software with a known vulnerability, so you’re looking for that component rather than probing for weak spots. To find a CVE, the vulnerability scanner needs two things: a list of vulnerable components to look out for and a way to identify application components for checking. The Invicti platform has its own vulnerability database, updated weekly with the latest CVEs, and a fingerprinter that lets it efficiently identify components to check against the database. This dynamic SCA functionality is augmented by tech stack analysis to flag outdated products.
Last but not least are passive security checks to find such crucial gaps as missing security headers and other misconfigurations. Having an automated scanner to check things like CSP rules or HSTS headers across thousands of pages is invaluable to save time and sanity on manual verification. Some CVEs have their own additional active security checks on the Invicti platform, which is extremely useful for verifying whether a reported vulnerability is actually exploitable in your specific environment.
There are several ways to categorize web vulnerability scans, but it’s worth keeping in mind that different types of scans don’t have to require separate tools. In fact, as application environments keep growing while also becoming more complex and technologically diverse, AppSec tool consolidation is becoming a major trend. An application security platform such as Invicti’s internally uses many different tools and processes to present a unified picture of your application and its security posture.
As already mentioned, the core original purpose of a web vulnerability scanner is to actively probe websites, applications, and APIs to try and uncover new vulnerabilities. Active scanning is the most difficult but also the most valuable part of application security testing, giving you a realistic security assessment of your applications in their runtime state. Passive checks, on the other hand, are used to detect many misconfigurations as well as identify vulnerable or outdated open-source libraries, application frameworks, and tech stack components.
A closely related way to categorize vulnerability scans is by what they are looking for: suspicious behaviors or known patterns (signatures). Heuristic scanners perform security checks and analyze application reactions to detect vulnerable behaviors that may never have been observed before. A signature-based scanner, on the other hand, looks for known vulnerabilities by comparing against its internal database. What used to be separate tools can now be combined and integrated into modern AppSec platforms, as with Invicti’s combination of a heuristic scanner with dynamic SCA and outdated component analysis.
In past decades, internal and external scanning would have referred to literally scanning the internal corporate network behind a firewall versus externally scanning its outer perimeter. Today, especially in the context of application security, internal vulnerability scanning more often refers to automated testing performed while an application is still in internal development, with external scanning corresponding to testing at the production stage. Again, what used to require different scanners for each role can now be done on a single AppSec platform that integrates at multiple points into the CI/CD pipeline and general DevOps workflow.
A decent vulnerability scanner can detect hundreds of weaknesses (CWEs) and thousands of known vulnerabilities (CVEs). The most common classes of new vulnerabilities found during scanning include the following: Running a vulnerability scan is only the beginning. After all, the main reason you scan for vulnerabilities is to find and remediate security issues that could get you hacked if left untouched—but the actual steps you need to take can vary hugely depending on the tool, your environment, and your workflow.
Ad-hoc scanning with an inaccurate tool will typically require your security team to manually go through all the results to weed out false positives and only then triage and assign confirmed vulnerabilities for remediation. In such ad-hoc workflows, security engineers need to manually send security tickets to developers, clarify the required mitigation, monitor resolution, retest fixes, and more. This places a huge burden on the security team while also making it a potential release bottleneck when the process cannot keep up with development schedules.
To avoid these headaches, the recommended practice is to have a vulnerability management program and process, based on a reliable AppSec solution and deeply integrated into the software development lifecycle. Using the Invicti platform as an example, you can plug the vulnerability scanner directly into your Jira or other issue tracker and have developers receive automatic tickets when specific criteria are met, for example for confirmed high or critical vulnerabilities. Each vulnerability report includes full technical information and detailed remediation guidance—and thanks to proof-based scanning, everyone is confident that confirmed issues are not false positives but real vulnerabilities that need fixing.
Vulnerability scanners have evolved from basic pentesting tools to critical AppSec solutions that can run in continuous processes to help organizations take a more proactive approach to security. On the information security side, automated DAST can deliver real-time insights into your security posture, support remediation efforts, and help with risk management and compliance. At the same time, automated dynamic security testing in the development pipeline can greatly improve software security while also removing the process bottlenecks traditionally associated with security testing.
Vulnerability scanning is foundational to web application and API security—and an industry-grade DAST platform is the way to build it into your AppSec program. See how Invicti can help you level up your application security. Note: This guide is based on OffSec PEN-200 (OSCP) training materials, adapted and rephrased for educational purposes. Vulnerability scanning identifies the attack surface of software, systems, or networks. These tools range from simple scripts targeting specific flaws to comprehensive commercial platforms detecting thousands of vulnerabilities. Automated scanners establish a security baseline quickly, but manual analysis remains essential for thorough coverage.
Common Scanner Types: - Network vulnerability scanners - Web application scanners - Database scanners - Configuration auditors Despite implementation differences, most vulnerability scanners follow a standard four-step process: Determines if targets are online and responding using: - ICMP echo requests (ping) - TCP SYN/ACK packets - ARP requests (local networks) Identifies open ports and accessible services: - TCP Connect/SYN scans - UDP scans - Service-specific probes Fingerprints services and operating systems through: - Banner grabbing - Protocol analysis - TCP/IP stack fingerprinting Correlates findings with vulnerability databases: - NVD (National Vulnerability Database) : NIST-maintained repository - CVE (Common Vulnerabilities and Exposures) : Standardized identifiers - Vendor databases : Security vendor-specific data Commercial scanners often attempt partial or full exploitation to confirm vulnerabilities. While this reduces false positives, it risks service instability and should be used cautiously in production environments.
CVE identifiers follow the format: CVE-YYYY-NNNNN - YYYY : Publication year - NNNNN : Unique identifier Causes: - Incorrect service version detection - Backported patches (security fixes on older versions) - Security configurations preventing exploitation - Network filtering Example: Scanner: CVE-YYYY-12345 detected on
Example: Scanner: No vulnerabilities found Reality: Service vulnerable to CVE-YYYY-67890 Strengths: - Discovers complex logical vulnerabilities - Identifies business logic flaws - Adapts to unique configurations - Follows attack chains Weaknesses: - Time-consuming and resource-intensive - Cognitive limits with large datasets - Not scalable for enterprise networks - Requires deep expertise Strengths: - Fast baseline establishment - Handles large networks efficiently - Consistent and repeatable - Covers known vulnerabilities comprehensively Weaknesses: - Generates false positives/negatives - Misses logical flaws - Can disrupt systems - Requires proper configuration Combine both methods: 1. Run automated scan for baseline 2. Review automated findings 3. Manually verify high-severity issues 4. Perform manual testing on critical systems 5. Generate comprehensive report Key Principle: Understand your tools' inner workings, limitations, and proper configuration.
Targets: - DMZ systems - Web applications - Public-facing services (VPN, mail servers) - Cloud infrastructure Considerations: - Companies often have undiscovered exposed systems - Geographical restrictions may apply - Firewall rules affect accessibility Focus Areas: - Lateral movement opportunities - Privilege escalation vectors - Network segmentation - Trust relationships Detects: - Remote service vulnerabilities - SSL/TLS issues - Web application flaws (limited) - Exposed configurations Limitations: Cannot detect local issues like missing patches, file permissions, or local privilege escalation vulnerabilities.
Detects: - Missing patches - Vulnerable software versions - Configuration issues - Security policy violations - Local vulnerabilities External scans take longer due to network hops and latency. Plan accordingly: - Single host: Minutes to hours - Small network (<50 hosts): Hours - Medium network (50-500 hosts): Hours to days - Enterprise (500+ hosts): Days to weeks External Issues: - Geographical IP filtering - WAF/DDoS protection - Cloud security groups - IP whitelisting Internal Issues: - ICMP filtering causing false offline reports - Firewall rules between subnets - IPS blocking scanner traffic - VLAN segmentation Network devices may throttle traffic based on: - Packets per second - Concurrent connections - Bandwidth usage Potential Impacts: - Service crashes - Performance degradation - Resource exhaustion - Unplanned reboots High-Risk Systems: - Production environments - Critical infrastructure (SCADA/ICS) - Legacy systems - Medical devices Best Practices: 1. Coordinate with system owners 2. Use safe-checks mode 3. Test non-critical systems first 4. Monitor during scans 5. Have rollback procedures 6. Schedule maintenance windows Q: Scanner detects a Linux vulnerability on a Windows server. False positive or negative? Q: Scanner detects wrong FTP version with no vulnerabilities, but actual version is vulnerable. False positive or negative? Key Points: 1. Scanners follow four steps: host discovery, port scanning, service detection, database matching 2. CVE identifies vulnerabilities; CVSS rates severity (0-10) 3. False positives waste time; false negatives are dangerous 4. Combine automated and manual testing for best coverage 5. External/internal and authenticated/unauthenticated scans serve different purposes 6. Consider duration, visibility, rate limiting, and system impact 7. Always coordinate with stakeholders and have contingency plans Let me state the conclusion first. Vulnerability assessment splits into "horizontal holes you can comprehensively crush with tools" and "vertical risks you can plug only with a design review." And the most cost-effective is this order — first sweep the horizontal holes with free official tools, and route to humans only the vertical risks whose correctness machines can't judge.
"I want to outsource vulnerability assessment, but I don't know what and how much I can do myself," "I hear the word OWASP but don't know the concrete how-to" — this article runs through, end to end, the "range you can do yourself" that precedes that, with a hands-on faithful to the OWASP official methods. SCAISASTIsecret scanningIDAST (ZAP)ICI integration, all shown with actually-working code.
Let me note the most important thing first. No automated tool guarantees "completely safe." Even with a perfect scan, the access-control (authorization) flaw that causes the most leaks can slip right through. This article draws, as honestly as possible, the boundary — how far is free and automatable, and where on does the professional's audit realm begin. This article's target readers : individual developers / startup developers / those in a position to make technology choices, on modern web stacks like Next.js / Supabase. The code examples use Next.js (App Router) as the subject, but the assessment thinking and tools are framework-independent.
Before the technology, be sure to pin down law and ethics first. Skip this and a well-intentioned assessment can become an illegal act. Uphold just this one line and everything henceforth is a legitimate procedure for "diagnosing your own app, safely, yourself." Those who want to systematically grasp the boundary of law and ethics, read alongside White Hackers and the Law [Definitive Edition] (the Unauthorized Access Act, active cyber defense, the correct way to report a vulnerability).
To judge the validity of an estimate or proposal for a commission, let me pin down the difference from nearby words. Vulnerability Assessment is the activity of "comprehensively and repeatedly surfacing whether known vulnerability patterns are left." The portion automatable with tools is large, which is exactly why it's the realm you should do yourself first. On the other hand, a penetration test or audit requires "human creativity / design understanding," so it's high-cost and can be run only at limited frequency.
"What an audit is / when it's needed / the cost feel" is detailed in a separate article, What a security audit looks at — the range where automation suffices, and the range an audit is needed . This article, before that, goes all-in on "implementing auto-assessment." The world standard of vulnerability assessment is published free by OWASP (Open Worldwide Application Security Project) .
What to reference in practice is 3 official documents with different roles. Using them distinctly without conflating is the first step to systematizing assessment. Use them in the flow "size it up with Top 10 → move your hands with WSTG → measure pass/fail with ASVS." OWASP Top 10:2025 , whose official version came out in January 2026, is the latest "TOP 10 most-critical web-app risks" analyzing over 175,000 CVEs and 248 CWEs. Let me correctly grasp the changes from the 2021 edition.
Web Security Testing Guide v4.2 is the official handbook comprehensively covering actual test procedures. If Top 10 is "what," WSTG shows "how," in the following 12 categories (4.1–4.12). Of these, most of 4.1–4.4I4.6–4.9I4.11I4.12 are coverable by automation. On the other hand, 4.5 (authorization) and 4.10 (business logic) are extremely hard to mechanize — these 2 are the "vertical risk" handled in the article's latter half. When designing an assessment, it's organized to think of color-coding "the range automation can paint" and "the range painted by hand" on top of this map first.
ASVS (Application Security Verification Standard) 5.0 (published May 2025) is the "checklist of achievement criteria" organizing about 350 verification requirements into 17 chapters. Apply it in stages at 3 levels. In practice, it's effective to build it into the acceptance criteria (Definition of Done) like "our product targets satisfying ASVS L2." Divide roles: assessment is the work of "finding holes," ASVS the yardstick of "measuring whether they're plugged." [Latest, official caution] The standard DAST tool "ZAP" is no longer an OWASP project. ZAP (Zed Attack Proxy) , described later, was long called "OWASP ZAP," but left OWASP in 2023, and since September 2024 development continues under the Checkmarx regime ("ZAP by Checkmarx"). The license remains OSS (Apache-2.0-equivalent) and free , with features and community operation maintained. The Docker image name owasp/zap2docker-stable from old articles is also discontinued , and it's now ghcr.io/zaproxy/zaproxy:stable . Get this wrong and it won't run.
Auto-doable vulnerability assessment decomposes into 4 kinds of tools that observe different targets. The table mapping which part of OWASP Top 10:2025 each crushes is below. This mapping is the "map" I most want you to take home from this article. Line up the 4 "in order of fast / shallow" and the order to build into CI comes into view.
Running "the fast and cheap first" in this order is the DevSecOps standard. Below, per layer, I show actually-working commands and code. The cheapest and most effective is here. Even if your code is perfect, if a known CVE sleeps inside node_modules , it's a hole. Now that A03 (supply chain) was promoted in 2025, it's top priority.
Set the --audit-level threshold to moderate and you can "auto-block a PR that mixed in a moderate-or-higher vulnerability." This alone plugs most of A03. Detecting and stopping there doesn't make operations run. Enable GitHub Dependabot and it auto-generates fix PRs against vulnerable dependencies. Just place this one file in the repository.
A cost-efficiency hint : SCA suffices with the free ecosystem standard ( npm audit + Dependabot). You needn't include SCA in a paid vulnerability assessment. Settle this with automation, and route the human budget to §9's vertical risk — that's the right answer. SAST (Static Application Security Testing) tracks the data flow without running the code , detecting paths like unsanitized input flowing into SQL or dangerouslySetInnerHTML . It's a layer strong on SQLiIcommand injectionIpath traversalIopen redirectIDOM XSS (A05).
p/owasp-top-ten is a rule collection corresponding to each OWASP Top 10 category , with rules tagged for "what corresponds to which risk." It's directly usable when reporting assessment results mapped to the Top 10. SAST sees "structural flaws." For example, the following Next.js Route Handler string-concatenates user input into SQL , and Semgrep warns with high confidence (A05 / WSTG 4.7).
The point is to root-cure the SAST warning with the design of "parameterization + type validation at the boundary." Not ad-hoc escaping, but always validate / neutralize at the trust boundary (values coming from outside the system) — this is OWASP's consistent philosophy, and it lowers A05IA07IA10 together. SAST tends to over-detect. Suppress, with a reason comment attached, the spots you've judged definitely safe. Unbridled suppression is forbidden — if you can't explain "why it's safe" in one line, that's not suppression but un-addressed.
A misplaced NEXT_PUBLIC_ , a committed .env , a hardcode during debugging — an API key or DB connection string leaking into the repository is a typical accident. This becomes the entrance to A02 (misconfiguration) and A03 (supply chain). Root-cure by design : the proper path is a structure where a secret "can't be written" into code in the first place. Make a server-only secret touchable only by server components / Route Handlers via process.env , and separate it at the type level from values reaching the client ( NEXT_PUBLIC_* ). The design of validating the env boundary with Zod is covered in the separate article Design to prevent environment-variable leakage .
7. Hands-On { DAST — Diagnose a "Running App" from the Attacker's Viewpoint with ZAP (A01/A05/A02) Here is assessment's flower, DAST (Dynamic Application Security Testing). Where SAST reads the source, DAST sends HTTP requests to an actually-running app and judges vulnerabilities by externally-visible behavior. It's a layer strong on reflected XSSIopen redirectISQLi (boolean/error inference)Imissing security headersISSRF.
5. Performance Evaluation & Extended Technical Observations The free standard is ZAP (Zed Attack Proxy) . As noted, it's now under the Checkmarx regime but OSS / free is maintained. Using it with Docker is the most reproducible, with 3 kinds of scan used distinctly. Against local or staging, diagnose deeply with a full scan that actually sends attack payloads. Never fire it at production (§0).
An API with no screen can't be traversed by a spider. Feed it an OpenAPI(Swagger)/GraphQL definition and assess the endpoints comprehensively. The baseline / full scripts are handy, but for an app needing authentication or when you want to finely control the scan procedure , use the Automation Framework that ZAP officially is switching to recommending. Because you write the scan plan declaratively in one zap.yaml , reproducibility, readability, and version-controllability are on a different level.
A pitfall of SPA (React/Next.js) assessment : an app where client rendering is the main can't have its links traversed by the conventional spider, and coverage plummets. Always combine spiderAjax (the Ajax spider). Misjudging "ZAP finds nothing = safe" without knowing this is the most frequent mistake of self-taught DAST. Bundle the 4 layers so far into one pipeline with GitHub Actions , and aggregate the results into GitHub Code Scanning as SARIF. With this, vulnerabilities are "auto-visualized/blocked on every PR," becoming an assessment gate of production-operation quality with observabilityIresilienceIidempotency.
The point is separating the frequency, "static = every PR, dynamic = nightly/pre-release." DAST is slow and needs a deploy, so it's heavy for every PR. Running the fast ones at high frequency and the slow ones at low frequency achieves both feedback speed and cost. The SAST/secret results aggregate into GitHub's "Security" tab via SARIF, becoming a mechanism that permanently prevents regression (the same hole mixed back in).
If you want to deep-dive CI integration on a SARIF premise, see the separate article Building security assessment into CI (SARIF × GitHub Actions) . By here, most of OWASP Top 10:2025's A02–A05IA08IA10 are auto-plugged. But — even if every scan is green, that's not "safe." There are vulnerabilities automated tools fundamentally can't find. They are A01 (access control)'s core = authorization and A06/business logic (WSTG 4.5 / 4.10).
Look at the following code. It's syntactically perfect , and neither SAST nor DAST warns. Yet it's a serious IDOR (Broken Object Level Authorization). The reason a tool can't warn is clear. The knowledge that " invoice should be filtered by userId " depends on the "meaning" of your business rules (who owns what, and which operations are allowed). A scanner doesn't know your data model, so it can't judge this omission as an "omission." This contrasts with SQL injection being "the same structural flaw in any app." This object-level authorization flaw (IDOR/BOLA) has been 1st ever since the first edition of the OWASP API Security Top 10 too — not "a rare advanced attack" but "the most ordinary leak." The detection of IDOR/authorization in Next.js × Supabase, and multi-layer defense with RLS (row-level security), is concretely covered in the separate article Detecting IDORIauthorization flaws (doubling up with RLS) .
Once you know "the how-to," finally it's important to land it into a sustainable operation. A one-off assessment goes stale with next week's deploy. I recommend the following frequency design. The way to think about cost : in the table above, everything down to the 5th row can be internalized with free tools. What you should pay for is the bottom row, only the audit of vertical risk that machines can't judge. Do everything by hand and cost balloons; leave everything to tools and the most serious authorization slips through. "Sweep horizontal for free → only vertical paid" is the cheapest, safest budget allocation.
If the following apply, it's the juncture to consider a manual audit of vertical risk while basing it on auto-assessment. Summary — Maximize "the Range You Can Do Yourself," and Ask Humans Only for What's Beyond Vulnerability assessment isn't "something to dump wholesale on a professional." Horizontal holes can be swept by the developer themselves with free official tools. On top of that, use money and human time only on the vertical risk machines can't judge — this is the most rational way to fight, securing production-quality security on a limited budget.
I myself have designed and implemented a B2B SaaS that won the Minister of Economy, Trade and Industry Award, and a payment foundation that achieved 0 double charges in production, with one person × generative AI. I've landed the workflow of "defend fast and cheap with automation, keep the design judgments in human hands," solidified in that process, into all the code in this article. First, from the single command npx semgrep scan --config=auto , try diagnosing your app today.
Developer of a METI Minister's Award–winning product. With TypeScript + Python + AWS, I deliver SaaS, industry DX, and production-grade generative AI (RAG) end to end — from requirements to infrastructure and operations — single-handedly. Many of the measures here can be mechanically detected and hardened with a single middleware file and static analysis. With the free, MIT-licensed Aegis, you can scan your current project from one command. The vertical risks that need design, I also take on as an audit.
Available for both project-based (contract) and advisory engagements. Start with a free 30-minute consult. Next.js × Supabase Application Security Complete Guide — Protecting Authorization and RLS with Vulnerability Detection and Defense in Depth The overall picture of security for AI-mass-produced Next.js × Supabase apps. We divide it into automatable horizontal controls (CSP, rate limiting, CSRF, Zod validation), injection detected by static analysis (SQLi/SSRF/XSS), and vertical risks only design can close (authorization/IDOR, RLS, tenant isolation), and systematize how to protect with 3 detection layers and defense in depth.
A security checklist before real customer data goes into your SaaS — tenant isolation, keys, backups, and breach reporting What a SaaS or web app team should verify before onboarding its first customers or migrating production data: two-tenant IDOR tests, key rotation, restore drills, PII-free logging, and Japan's breach-report duty to the PPC, each with the reason it has to happen before real data.
Can You Run a Security Assessment With Only a Production Environment? — Splitting Zero-Touch Review, Read-Only Checks, and Tests That Need Staging No staging, only production? You can still run a security assessment. Split methods into review that never touches production, read-only checks against it, and tests that need staging or written agreement — with a decision table, a rules-of-engagement checklist, safe test accounts, and why backups are no undo button.
When Supabase RLS authenticates but doesn't authorize — how auth.role() = 'authenticated' leaks every row, and how to scope by owner You enabled RLS and wrote a policy, yet every logged-in user can read every row — because auth.role() = 'authenticated' and auth.uid() is not null only prove a session exists, never that the row belongs to the caller. This explains the 'authenticates but doesn't authorize' policy pattern found in 9.2% of the RLS-shipping repos in a scan of 1,000 public Supabase repos, how to tell it apart from a legitimate shared table, and how to fix it to owner scope — with real SQL.
Vercel Security Configuration Checklist: Environment Variables, Deployment Protection, Git Integration and the Next.js Boundary A configuration audit checklist for teams running Next.js on Vercel: Config/Secret env vars, Deployment Protection defaults, Git Fork Protection, Server Action auth, caching and Cron, checked against the docs as of October 2026.
Does the app you built with AI need a human security review? — who needs one, who doesn't, and what it costs, when to do it and how to ask Should you pay a person to review the app you built with Claude Code, Cursor or Lovable? A decision table based on the data you hold, what an AI self-check covers and what it can't, when in the launch cycle to ask, typical prices and what drives them, and how to get a review without handing over keys or customer data.
Implementing Statutory Calculations in TypeScript: Japan's Unemployment Benefit Logic as Pure Functions, Revision Tables, and Tests Built from Official Worked Examples A design guide to implementing Japan's unemployment insurance (basic allowance) calculation as pure TypeScript functions: why the official formulas are rewritten as integer ratios, how to hold caps that change every August, how to turn the government's published worked examples into test fixtures, and how to keep user input out of analytics — using code from a live app.
This documentation provides an in-depth exploration of vulnerability scanning techniques essential for penetration testing and the OSCP certification. Content is derived from OffSec PEN-200 courseware, rephrased and organized for practical application. The industry-standard port scanner with powerful NSE scripting capabilities for lightweight vulnerability detection.
Professional vulnerability scanner with extensive plugin library covering 67,000+ CVEs. Open-source vulnerability assessment framework with 50,000+ Network Vulnerability Tests (NVTs). Mohamed Trigui is a cybersecurity enthusiast completing a Master's in Cybersecurity at Illinois Tech. Currently preparing for OSCP certification through hands-on practice on Hack The Box and developing custom security tools.
Current Projects: - Replicating vulnerabilities on Linux and writing Lua patches - Developing Nmap NSE scripts for zero-day reconnaissance - Writing HTB machine walkthroughs and exploit documentation This guide is for educational purposes only . Always obtain proper authorization before scanning any systems. Unauthorized vulnerability scanning is illegal and unethical.
Content is derived from OffSec PEN-200 (OSCP) training materials, rephrased and adapted for educational purposes. All credit for the original methodology and techniques goes to Offensive Security. This documentation is provided as-is for educational purposes. When using these techniques: Vulnerability scanning is the process of automatically probing systems, networks, and applications to identify known security weaknesses before an attacker finds them first. If you're building or maturing a scanning program, this guide covers what you actually need: scan types, scheduling, prioritization beyond CVSS scores, remediation workflows, and the Apple-specific considerations most security guides skip entirely.
A vulnerability scanner compares the software versions, configurations, and open services on your assets against a database of known vulnerabilities, typically sourced from the National Vulnerability Database (NVD) and vendor-specific advisories. The scanner fingerprints each asset, maps what it finds to Common Vulnerabilities and Exposures (CVE) records, and produces a prioritized list of findings.
What it does not do: exploit those vulnerabilities. That distinction matters. Scanning tells you a door might be unlocked. Penetration testing tries to walk through it. Both have a place in a mature security program, but they answer different questions. A scan gives you broad, repeatable coverage across your entire fleet. A pen test gives you adversarial depth on a subset of targets.
The output of a vulnerability scan feeds your vulnerability management program, which is the broader process of tracking, prioritizing, and remediating findings over time. Unauthenticated scans probe assets from the outside, the same view an attacker without credentials would have. They catch exposed services, open ports, and unpatched network-facing software. Useful for external attack surface coverage, but they miss a large portion of vulnerabilities that only exist once you're logged in.
Authenticated scans use credentials (SSH keys, API tokens, domain accounts) to log into systems and inspect installed software, registry entries, configuration files, and kernel versions. For endpoint fleets, authenticated scanning consistently catches two to three times more vulnerabilities than unauthenticated scanning. If you're running unauthenticated scans on your endpoints and calling it done, you have significant blind spots.
Internal scans run from inside your network perimeter and cover your full asset inventory. External scans simulate what an internet-facing attacker sees. You need both. Compliance frameworks like PCI DSS 11.3 explicitly require external scanning by an Approved Scanning Vendor (ASV) on a quarterly basis, separate from your internal scan cadence. Active scanning sends probes directly to target assets. Passive scanning monitors network traffic to infer what assets exist and what software they're running without touching them. Passive scanning is useful for discovering assets that active scans miss (IoT devices, shadow IT), but it produces less detail. Most enterprise programs use active scanning as the primary method and passive as a supplement for asset discovery.
Agent-based scanning deploys a lightweight agent on each endpoint that continuously reports vulnerability state without requiring network-based probes. Agentless scanning relies on network access or temporary credentials. For remote Mac workforces where devices are rarely on the corporate network, agent-based scanning is the only reliable option. An agentless scanner scheduled to run at 2 AM will miss laptops that are closed and off VPN.
You cannot scan what you don't know exists. A credible vulnerability scanning program starts with an accurate, continuously updated asset inventory. This means every managed device, server, container, and cloud instance. For endpoint fleets, hardware inventory management is the foundation. Your MDM platform should be your authoritative source of truth for managed devices, feeding asset lists directly into your scanner. When those two systems aren't connected, you end up with scan coverage gaps and stale inventory data that makes your vulnerability reports unreliable.
The CIS Controls v8 lists basic asset inventory as Control 1 for a reason. Every other control, including vulnerability management (Control 7), depends on knowing what's in scope. Harvested Online Documentation & Reference Sources • https://www.bing.com/aclick?ld=e8BJ1XIhcozHdGZ-5b9alSZDVUCUzs5z7C3ILee2OKoMbCv_X5ed9jpQYZk3TtbHWctqQO etmb_NTIHtbW9QV7SgU30Ev2jDCdFkT4c8dg5TVkcD_h5LwoHlvOKh8bzPE_6o5PeVvwZqKSRUbrM4mGR0Hcp3P9qqxicB qmJdoDKwySP3Ho_B5Xt3X43KYFVvZaIvy4GA&u=aHR0cHMlM2ElMmYlMmZ3d3cuY2xvbmUtc3lzdGVtcy5jb20lMmZhdXRv bWF0ZWQtcGVuZXRyYXRpb24tdGVzdGluZy1zZXJ2aWNlJTNmbXNjbGtpZCUzZGU0NTk4OTYzZjg0ZjE4MDg3NmVmZTNi NzEyM2NiNjI5JTI2dXRtX3NvdXJjZSUzZGJpbmclMjZ1dG1fbWVkaXVtJTNkY3BjJTI2dXRtX2NhbXBhaWduJTNkUGVuJTI1M jBUZXN0JTI1MjBDaGVjayUyNTIwdGhlJTI1MjBCb3glMjUyMC0lMjUyMFNlYXJjaCUyNTIwLSUyNTIwMSUyNTIwV2VlayUyNT IwJTI1MjQyMDAlMjZ1dG1fdGVybSUzZHdlYnNpdGUlMjUyMHBlbmV0cmF0aW9uJTI1MjB0ZXN0aW5nJTI2dXRtX2NvbnRlb nQlM2RXZWIlMjUyMEFwcCUyNTIwQ2xvdWQlMjUyMGFuZCUyNTIwU2FhUyUyNTIwUGVuJTI1MjBUZXN0&rlid=e4598963f 84f180876efe3b7123cb629 • https://github.com/bhavya-bhalla/web-vulnerability-scanner • https://vulnerabilityhub.readthedocs.io/en/latest/development/architecture.html • https://msspsecurity.com/web-application-vulnerability-scanners/ • https://www.securaprobe.com/blog/how-to-scan-web-application-for-vulnerabilities • https://www.invicti.com/blog/web-security/what-is-vulnerability-scanning-how-vulnerability-scanners-work • https://medtrigui.github.io/vulnerability-scanning/vulnerability-scanning-theory/ • https://tomodahinata.com/en/blog/web-application-vulnerability-assessment-owasp-zap-sast-dast-guide • https://medtrigui.github.io/vulnerability-scanning/ • https://www.iru.com/endpoint/vulnerability-management/vulnerability-scanning
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Web Application Vulnerability Scanner Using Python Source Code.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Web Application Vulnerability Scanner Using Python Source Code... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |