Complete Technical Paper Content — Web Cache Poisoning Detection Tool Using Python
Overview & System Context
Web Cache Poisoning Detection Tool Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9506 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Cache poisoning refers to a computer security vulnerability where invalid entries can be placed into a cache, which are then assumed to be valid when later used. Two common varieties are DNS cache poisoning and ARP cache poisoning. Web cache poisoning involves the poisoning of web caches (which has led to security issues in programming languages, including all Python versions at the time in 2021, and expedited security updates). Attacks on other, more specific, caches also exist.
In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection. Web caches exist to improve performance: they store responses to frequently requested URLs and serve subsequent requests from cache rather than the origin server. The security assumption is that all requests with the same cache key should receive the same response. Web cache poisoning breaks this assumption by exploiting headers or parameters that the origin server uses to generate the response but that the cache does not include in the cache key.
The research by James Kettle at PortSwigger documented this vulnerability class extensively in 2018 and 2019, demonstrating that it affected major internet services at scale. The impact of cache poisoning is multiplicative: a single malicious request can poison a cache entry that is subsequently served to thousands of users, delivering XSS payloads, open redirects, or malicious script imports with no per-victim interaction required.
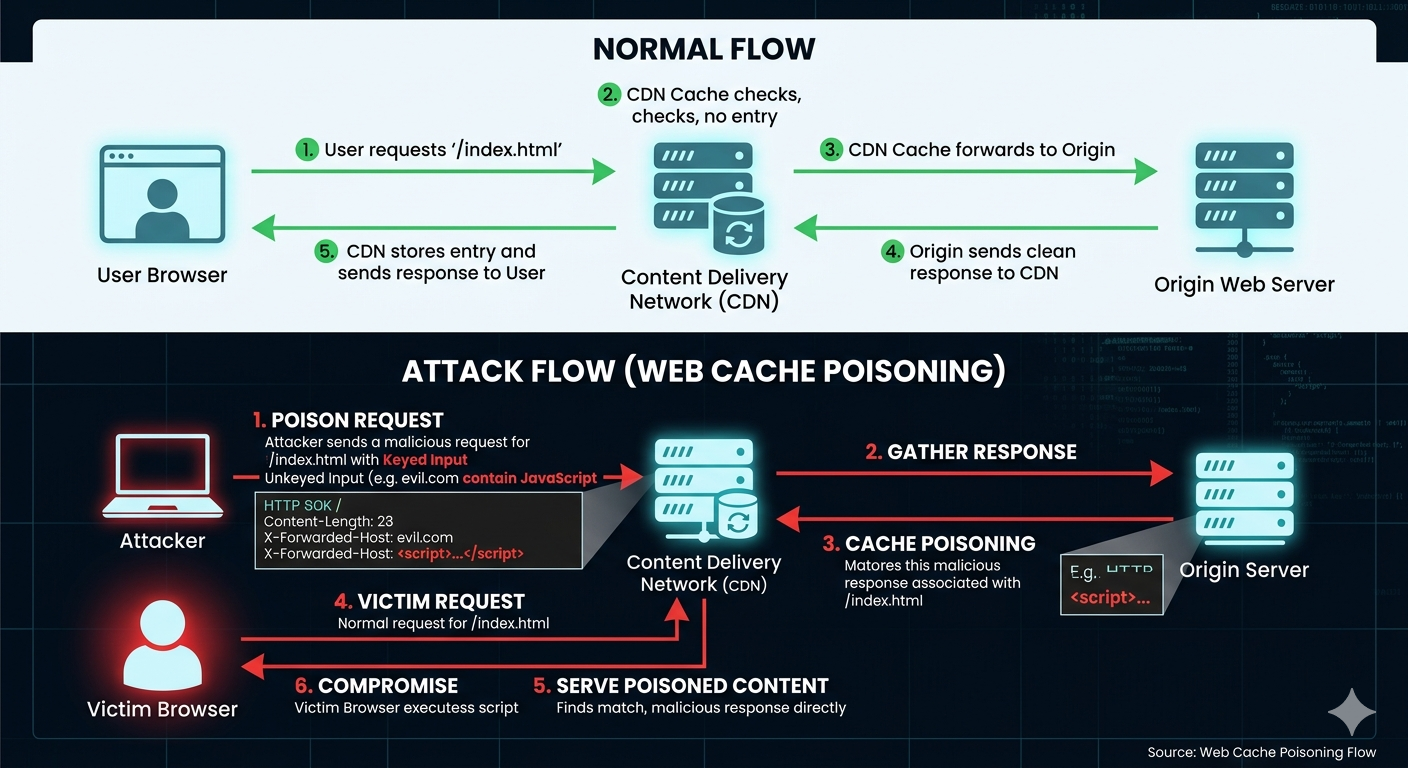
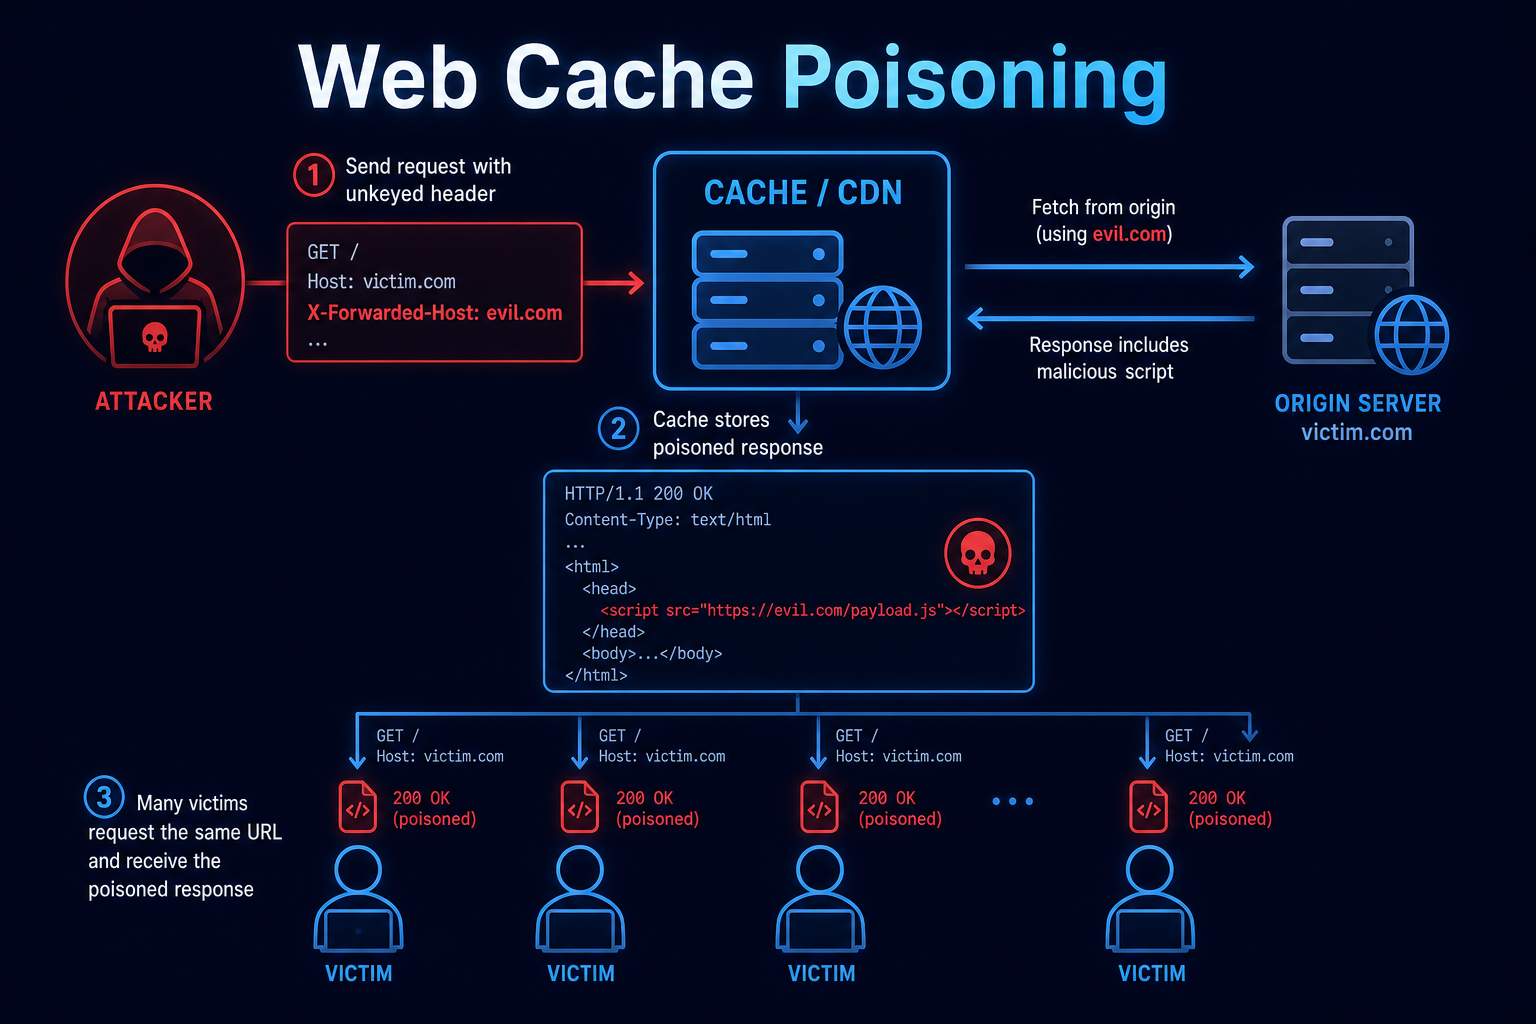
Figure 1: Web Cache Poisoning - IvanTran Cache poisoning manifests in several distinct forms depending on which unkeyed input the attacker exploits and how the origin server uses that input to generate responses. Understanding each variant helps security teams prioritize what to test and which cache configurations to audit first. The four main vectors are Host header injection via X-Forwarded-Host, parameter cloaking through stripped query strings, request smuggling-based poisoning, and fat GET body injection. Each requires a slightly different detection approach and a targeted remediation at either the cache key configuration or the origin server request handling layer.
The most impactful cache poisoning variant. Many web frameworks (Django, Rails, Spring, Laravel) use the X-Forwarded-Host header (set by proxies) to construct absolute URLs in responses: redirect headers, canonical URL meta tags, script src attributes, and API endpoints in JavaScript. If a CDN strips X-Forwarded-Host from the cache key but forwards it to the origin, an attacker can supply X-Forwarded-Host: attacker.com, receive a response with . The CDN caches this page using a cache key based only on the URL path ( /products/laptop ), but the origin server uses the X-Forwarded-Host header to determine the domain for script imports. This creates a vulnerability.
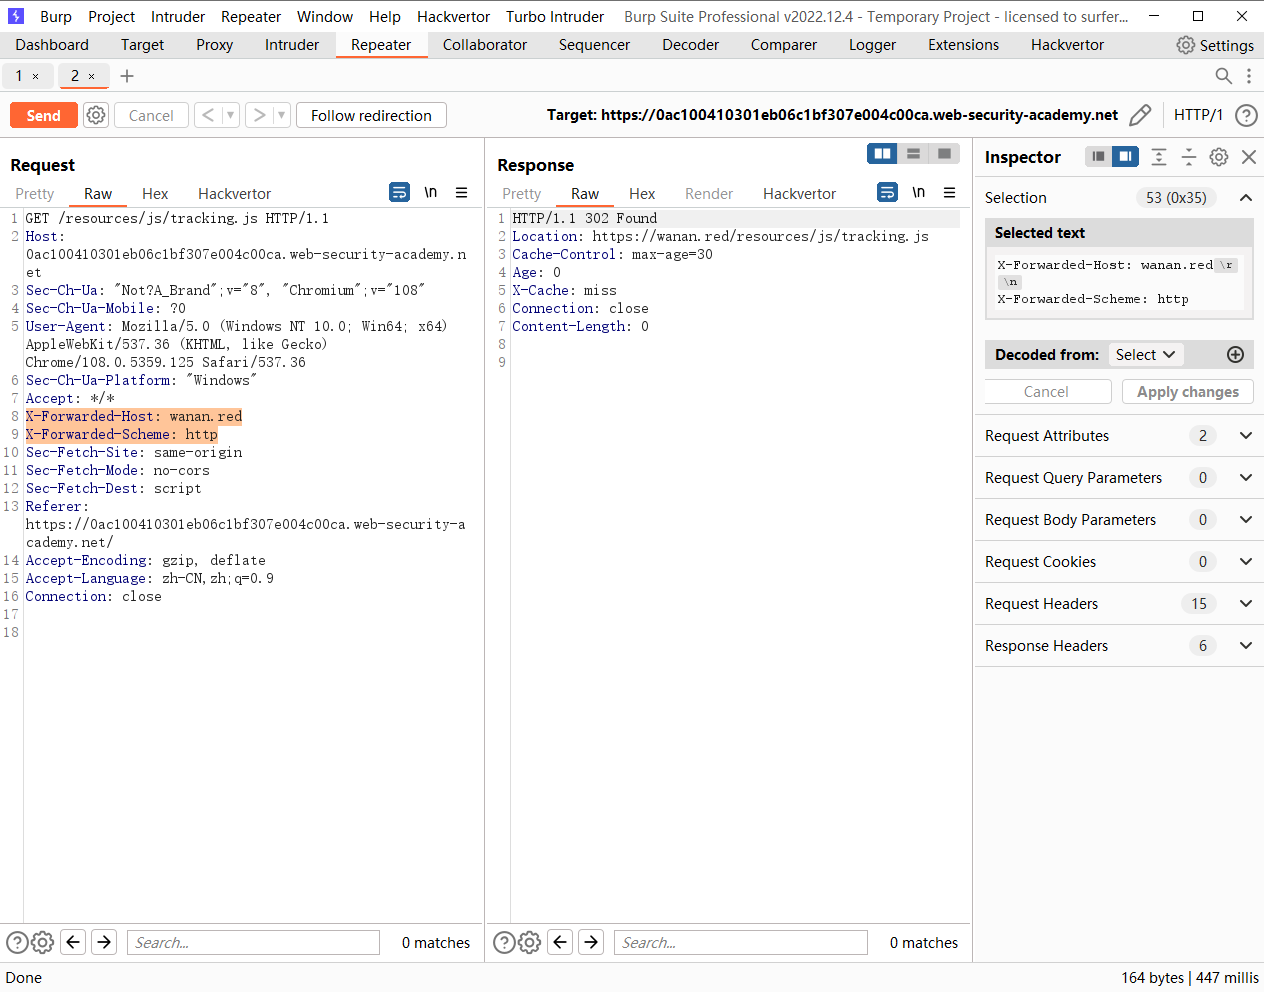
This response is cached by the CDN with a cache key based only on /products/laptop . Subsequent users will receive this cached version. An attacker identifies that the X-Forwarded-Host header is not included in the cache key but IS processed by the server. The attacker crafts a request with a malicious domain: The server used the X-Forwarded-Host: attacker-analytics .com header to replace the domain in the analytics script import. Since X-Forwarded -Host is not included in the cache key (only /products/laptop is), this poisoned response is cached and will be served to all subsequent users requesting the same URL.
When legitimate users visit https://example.com/products/laptop after the cache poisoning, they receive the cached poisoned response: Notice the X-Cache: HIT header—the response is served directly from cache. The poisoned response is now served to all users without modification. Their browsers execute the script from https://attacker-analytics.com/scripts/analytics.js , which is under the attacker’s control.
The poisoned cache entry remains active for the entire max-age=3600 (1 hour) period. During this time: This demonstrates how the cache key ( /products/laptop ) is identical for both requests, but the responses are completely different because the origin server processed the unkeyed X-Forwarded-Host header differently. This scenario illustrates how a single malicious request can compromise thousands of users through a single point of cache poisoning vulnerability.
The most prevalent attack vector exploits HTTP headers that influence response content but aren’t included in cache keys. The following table presents common vulnerable headers, their legitimate purposes, and exploitation techniques: Beyond simple header injection, sophisticated attackers exploit how caches normalize and construct cache keys. The following table details common cache key implementation flaws: CPDoS attacks target service availability rather than data integrity by poisoning caches with error responses. The following table details CPDoS attack techniques: A single successful cache poisoning attack can affect thousands to millions of users simultaneously, making this attack class one of the most impactful vulnerabilities in modern web security. The difficulty in detecting and remediating these attacks—combined with the widespread use of caching infrastructure—necessitates comprehensive prevention strategies at multiple layers.
HTTP headers occupy a paradoxical position in web caching architecture: they simultaneously enable sophisticated performance optimization through intelligent cache management and create security vulnerabilities that attackers ruthlessly exploit. Understanding this dual nature is essential for implementing effective cache security. Headers serve as the primary mechanism through which servers communicate caching intentions to intermediary systems, browsers, and CDNs. Simultaneously, unkeyed headers or improperly configured headers become the primary attack surface for cache poisoning exploits. The tension between flexibility (allowing diverse caching strategies) and security (preventing malicious content distribution) runs throughout HTTP header handling, forcing security teams to carefully balance performance optimization with vulnerability mitigation. Different stakeholders—application developers, cache administrators, CDN operators, and security teams—often have conflicting incentives regarding header configuration, leading to security misconfigurations that persist in production environments.
The Cache-Control header serves as the primary mechanism for explicitly directing caching behavior across all layers of web infrastructure. This header contains directives that apply globally to all intermediary caches and browsers, making it the foundational element of any cache security strategy. The max-age=3600 directive specifies the caching duration in seconds, instructing all caches that the response remains valid for exactly 3600 seconds before requiring revalidation. The public directive explicitly indicates that the response is shareable across multiple users and can be stored in shared caches (CDNs, proxies), not just browser caches. The private directive restricts caching to single-user browser caches and explicitly prevents storage in shared caches—this is critical for sensitive content like user profiles or account data. The no-cache directive does not disable caching as commonly misunderstood; instead, it requires that cached responses must be revalidated with the origin server before serving, using mechanisms like ETags or Last-Modified headers. The no-store directive actually disables caching entirely, instructing all caches to never store the response, which is necessary for highly sensitive data. The must-revalidate directive forces cache revalidation after expiration, preventing stale content from being served to users after the max-age timeout expires.
When properly configured, these Cache-Control directives provide the foundation for cache security. However, the reality of production environments reveals systematic failures in implementation: many applications fail to set appropriate Cache-Control directives or use overly permissive settings like Cache-Control: public, max-age=86400 for content that shouldn’t be cached at all. This permissive default behavior allows aggressive caching by intermediary proxies and CDNs, expanding the potential impact of cache poisoning attacks. Furthermore, different caching systems interpret Cache-Control directives differently—some strictly adhere to directives while others use Cache-Control as a guideline that can be overridden by CDN-specific configurations. Organizations must audit their applications to identify which content is being cached when it shouldn’t be, and which Cache-Control directives are actually being respected by their caching infrastructure.
The Vary header serves a critical security function by explicitly instructing caches which request headers to include in cache key generation. When a server responds with Vary: X-Forwarded-Host, Accept-Language , it tells the caching system: “This response varies based on these request headers, so you must treat requests with different values for these headers as different cache entries.” The caching layer must then incorporate these headers into the cache key, preventing a request with X-Forwarded-Host: attacker.com from poisoning the cache for requests with X-Forwarded-Host: example.com . When properly implemented, Vary headers eliminate entire categories of cache poisoning vulnerabilities by ensuring that unkeyed inputs are never truly unkeyed—they’re explicitly included in cache key generation. The header acts as a communication bridge between developers (who understand what inputs affect responses) and cache systems (which must decide what inputs constitute different cache entries).
However, Vary header implementation in real-world systems reveals alarming security gaps. Applications often use specific headers to generate responses without specifying those headers in Vary directives, creating vulnerabilities. For example, an application might reflect the X-Forwarded-Host header into resource URLs without including Vary: X-Forwarded-Host in the response, leaving the vulnerability open for exploitation. Caches configured to ignore Vary headers—whether due to misunderstanding or performance optimization—bypass this security mechanism entirely, continuing to process requests as if the Vary directive doesn’t exist. CDN configurations frequently override Vary directives with their own cache key rules, potentially removing headers from the cache key that the application intended to include. Some CDNs only include a limited set of headers in cache keys by default, requiring explicit configuration to include additional headers. This fragmentation between what applications expect (based on Vary headers) and what caches actually do (based on their configuration) creates security gaps. Security teams must verify that their CDN provider actually respects Vary headers and is configured to include all relevant headers in cache key generation. Misconfiguration here is a critical vulnerability that enables cache poisoning despite application-level attempts to prevent it.
Hop-by-hop headers represent a specialized category of headers intended exclusively for single-hop transport-level communication between adjacent nodes in a connection chain. Headers like Connection , Keep-Alive , Transfer-Encoding , Upgrade , Proxy-Authenticate , and Proxy-Authorization should never traverse multiple hops and should never be cached. These headers control aspects of the current connection (such as whether to keep the connection alive) rather than describing the response itself. HTTP specifications explicitly prohibit caching these headers—they should be stripped by intermediaries and never forwarded to downstream systems. However, vulnerabilities in cache implementations have allowed these headers to escape their intended isolation, enabling attackers to smuggle malicious responses through these header channels. A sophisticated attacker might craft requests that manipulate hop-by-hop headers in ways that cause discrepancies between how the cache interprets the message and how the origin server interprets it. For example, by manipulating Transfer-Encoding or Content-Length headers, an attacker can cause a request to be interpreted as ending at a different point by the cache versus the origin server (a form of HTTP request smuggling). This can result in cache poisoning where the cache stores one portion of a response while the origin server intended something different. Researchers have discovered specific vulnerabilities in major CDNs (like Akamai) where hop-by-hop headers could be exploited to poison responses for entire geographic regions.
Beyond headers that control when responses are cached, certain request headers influence whether servers reuse cached content or generate fresh responses. The If-Modified-Since header allows clients to ask: “Please send me the full response only if the resource has been modified since this date; otherwise, send me a 304 Not Modified response.” The If-None-Match header performs the same function using ETags—cryptographic identifiers representing specific versions of resources. These conditional request headers enable efficient cache revalidation where clients avoid re-downloading unchanged content. However, mishandling these headers enables attacks where attackers manipulate these conditions to force generation of responses that wouldn’t normally be generated or to prevent caching of responses that should be cached. The Accept-Encoding header influences whether responses are gzip-compressed, and different encodings might be cached separately. An attacker might manipulate this header to cause the server to generate uncompressed responses that reflect unescaped user input, bypassing security filters that typically work on the compressed stream.
Implementing cache security through HTTP headers requires coordination across multiple configuration layers. Applications must set appropriate Cache-Control directives that accurately reflect content sensitivity—using private for user-specific content, no-store for highly sensitive data, and thoughtful max-age values that balance performance with security. The Vary header must explicitly enumerate all request headers that influence response generation. Developers must audit their code to identify every header that affects response content and ensure it appears in Vary directives. CDN configurations must be reviewed and adjusted to include all relevant headers in cache key generation, potentially overriding default behavior. Many CDNs allow fine-grained cache key configuration where specific headers can be explicitly included or excluded. Organizations should review CDN documentation for their specific provider (Cloudflare, Akamai, Fastly, AWS CloudFront) and adjust configurations accordingly. Content Security Policy headers mitigate the impact of JavaScript injection attacks from cache poisoning: Content-Security-Policy: script-src 'self' https://trusted-cdn.example.com prevents execution of scripts from unexpected sources even if cache poisoning injects script tags. Strict-Transport-Security headers enforce HTTPS-only communication, preventing man-in-the-middle attacks that could further compromise cache security. X-Frame-Options: DENY prevents clickjacking attacks where cached pages are loaded in frames. X-Content-Type-Options: nosniff prevents MIME type sniffing that could cause browsers to execute content with unintended handling. Organizations should implement these security headers comprehensively and verify their deployment across all responses.
Modern HTTP protocols introduce additional complexity to header handling and cache management. HTTP/2 uses header compression (HPACK) and multiplexing, changing how headers are transmitted and potentially affecting how caches interpret headers. Some cache implementations incorrectly handle HTTP/2 pseudo-headers ( :method , :scheme , :authority , :path ), potentially creating vulnerabilities. HTTP/3 over QUIC introduces further changes to header handling and encryption. Different caching systems handle these modern protocols differently, and vulnerabilities may exist in how headers are parsed and processed. Security teams must test cache poisoning vectors specifically against HTTP/2 and HTTP/3 traffic, as vulnerabilities that don’t exist in HTTP/1.1 may be present in newer protocol versions.
Preventing web cache poisoning demands a layered defense strategy spanning cache/server configuration, secure software development, operational vigilance, and automated controls. Each preventive technique can be reinforced with clear, practical examples for real-world deployments. Sensitive endpoints—such as login pages, personal profiles, transaction details, and admin consoles—should never be cached by intermediary servers or CDNs. For these URLs, always configure the response headers as: For example, in a Python Flask application handling authentication, you can inject the following header to every login response: This ensures browsers and proxies always retrieve a fresh response, preventing persistent cache poisoning for critical resources.
Cache keys must include all headers that impact how the server generates a response. Audit CDN and proxy configurations to ensure headers like X-Forwarded-Host or Accept-Language are part of cache key construction. For instance, in Cloudflare’s rules editor, you must explicitly require X-Forwarded-Host as part of the cache key for resources that use it. On Fastly, custom VCL logic can add necessary headers to cache key computations.
This signals to caches which request-header variations must receive unique cached entries, closing common poisoning vectors. Validate all incoming header and user data, strictly limiting allowed values, and always escape output before reflecting data in HTTP responses. For example, when accepting a domain name from the X-Forwarded-Host header, use a whitelist and regular expressions: This effectively blocks malicious scripts or payloads from poisoning cacheable content. For server-side templates, use languages with built-in autoescaping (like Jinja2 for Python).
Enforce HTTPS-only connections with HSTS to prevent attackers from exploiting insecure connections for cache poisoning. For Nginx, configure: This guarantees browsers never access the application over HTTP, blocking a crucial attack surface. If poisoned content loads a malicious script, the browser blocks its execution, neutralizing the attack’s impact.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Cache%20poisoning • https://www.decryptiondigest.com/blog/web-cache-poisoning-detection-defense-guide • https://github.com/0xShakhawat/web-cache-poisoning • https://securitycipher.com/docs/security/vulnerability-explain/web-cache-poisoning/ • https://pentest-tools.com/blog/web-cache-poisoning • https://denizhalil.com/2026/01/26/web-cache-poisoning-attacks-prevention-guide/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Web Cache Poisoning Detection Tool Using Python.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Web Cache Poisoning Detection Tool Using Python... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |