Complete Technical Paper Content — Web Crawler For Security Vulnerability Scanning In Python
Overview & System Context
Web Crawler For Security Vulnerability Scanning In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4513 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A web shell is a shell-like interface that facilitates remote access to a web server, commonly exploited for cyberattacks. Unlike traditional shells, it is accessed via a web browser, making it a versatile tool for malicious activities. Web shells can be coded in any programming language supported by a server, with PHP being the most prevalent due to its widespread use in web applications. Other languages, such as Active Server Pages, ASP.NET, Python, Perl, Ruby, and Unix shell scripts, are also employed. Attackers identify vulnerabilities often in web server application using network monitoring tools, which can be exploited to deploy a web shell. Once installed, a web shell allows attackers to execute shell commands, perform privilege escalation, and manage files by uploading, deleting, downloading, or executing them on the server.
Data theft Infecting visitors through watering hole attacks Website defacement by altering files with malicious intent Launching DDoS attacks Relaying commands to inaccessible network segments Serving as a command and control hub, such as in botnet systems or to compromise external networks Web shells enable hackers to extract data, corrupt systems, and deploy more damaging malware. The threat intensifies when compromised servers are used to infiltrate additional systems. They are also employed in cyber espionage targeting sectors like government, finance, and defense. A notable example is the "China Chopper" web shell.
SQL injection Flaws in applications and services (e.g., web server software like NGINX or content management systems like WordPress) File processing and upload vulnerabilities (mitigated by restricting file types) Remote file inclusion (RFI) and local file inclusion (LFI) vulnerabilities Remote code execution Exposed administration interfaces Attackers may also spoof the Content-Type header during file uploads to bypass weak file validation, enabling shell deployment.
With a filename of example.php, the command to display the /etc/passwd file could be: https://example.com/example.php?x=cat%20%2Fetc%2Fpasswd This executes the command cat /etc/passwd. Such risks can be mitigated by disabling PHP shell functions to prevent arbitrary command execution.
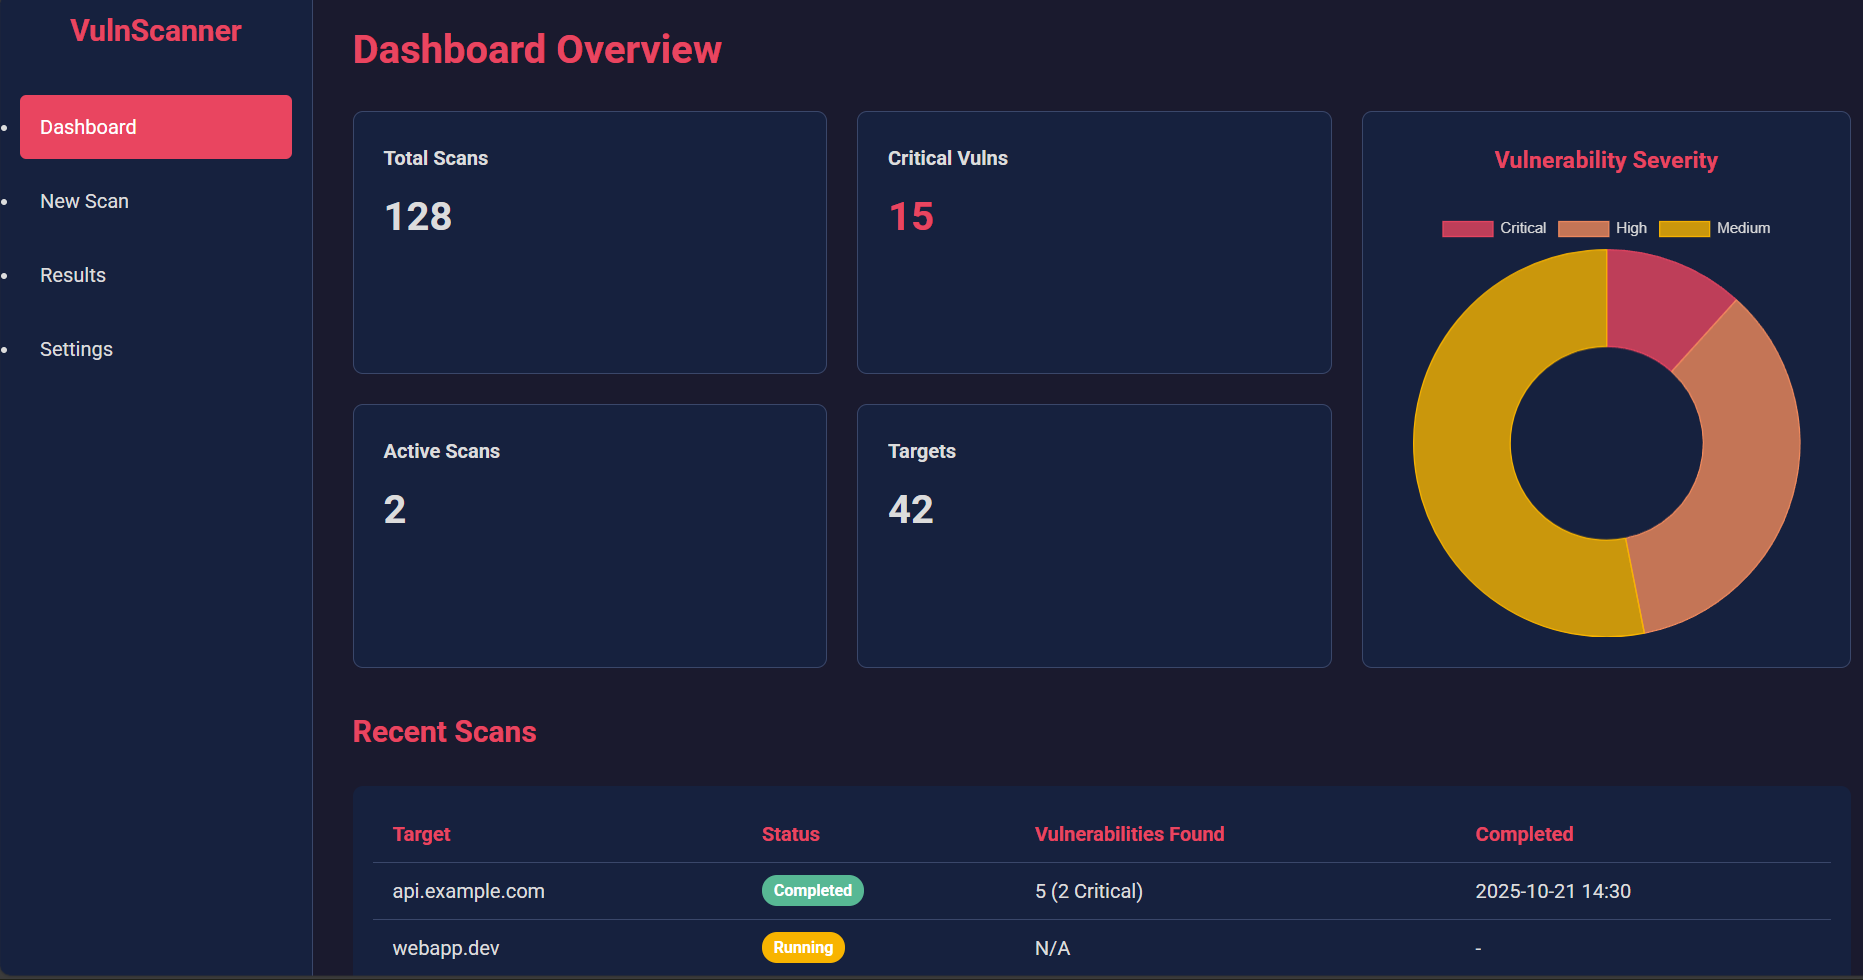
Figure 1: Swatantra Trivedi – Cybersecurity Portfolio Regularly updating applications and the host server's operating system to patch known bugs Implementing a demilitarized zone (DMZ) between web-facing servers and internal networks Securing web server configurations Closing unused ports and services Validating user input to limit local and remote file inclusion vulnerabilities Using a reverse proxy to restrict administrative URLs to legitimate sources Conducting frequent vulnerability scans (though ineffective against zero-day attacks) Deploying a firewall Disabling directory browsing Avoiding default passwords Unusually high web server activity from downloading/uploading Files with abnormal timestamps (e.g., newer than last modification) Unknown files on the server Suspicious references (e.g., cmd.exe or eval) Unusual connections in server logs For instance, a PNG file with POST parameters or dubious logins between DMZ servers and internal subnets may signal a web shell. Web shells may include disguised login forms, such as fake error pages. Attackers can modify the .htaccess file (on Apache HTTP Server) to redirect search engine queries to malware or spam pages, often tailoring content based on user-agent detection. Identifying the shell may require altering the crawler's user-agent, after which it can be easily removed.
Analyzing server logs can pinpoint the web shell's location, as legitimate users typically have diverse user-agents and referers, while attacker access is more uniform. Burp Suite is a proprietary software tool for security assessment and penetration testing of web applications. It was initially developed in 2003–2006 by Dafydd Stuttard to automate his own security testing needs, after realizing the capabilities of automatable web tools like Selenium. Stuttard created the company PortSwigger to flagship Burp Suite's development. A community, professional, and enterprise version of this product are available. Notable capabilities in this suite include features to proxy web-crawls (Burp Proxy), log HTTP requests/responses (Burp Logger and HTTP History), capture/intercept in-motion HTTP requests (Burp Intercept), and aggregate reports which indicate weaknesses (Burp Scanner). This software uses a built-in database containing known-unsafe syntax patterns and keywords to search within captured HTTP requests/responses. Burp Suite possesses several penetration-type functionalities. A few built-in PoC services include tests for HTTP downgrade, interaction with tool-hosted external sandbox servers (Burp Collaborator), and analysis for pseudorandomization strength (Burp Sequencer). This tool permits integration of user-defined functionalities through download of open-source plugins (such as Java Deserialization Scanner and Autorize).
Burp Proxy and Interceptor: Like other web application security scanners, one of the primary functionalities behind Burp Suite is its capability to act as a proxy server for client-side HTTP requests. Penetration testers can intercept web servers' default HTTP requests variables (attributes, body parameters, cookies, headers) in real-time and edit these values on-the-fly. Burp Site Map: BurpSuite operates similarly to the OWASP ZAP software, wherein target URLs' site maps can be captured either through automatic or manual web-crawling. When users crawl through a web application, HTTP requests become sent to a web proxy in Burp Suite's software. Once HTTP requests/responses are captured, these endpoints can be investigated manually or audited automatically through features in Burp Suite's Professional edition. Burp Logger and HTTP History: Retains a list of HTTP requests/responses captured during web-crawling (and automated scanning for Professional edition).
Burp Repeater: Repeats captured HTTP requests, allowing custom changes to request variables. Customized HTTP requests can be sent in quick succession and can be used to exploit race condition vulnerabilities. Burp Decoder: Automates text decoding. Decoded text can then be edited and re-encoded, allowing for enhanced customization in web requests. Currently, Burp can encode and decode in HTML, URL, Base64, ASCII hex, Hex, Octal, Binary, and GZIP. Burp's “smart decode” will automatically detect encoded data and recursively decode it as much as it can. Burp Sequencer: Analyzes an application-generated token variable across repeated HTTP requests to determine pseudorandomness predictability strength.
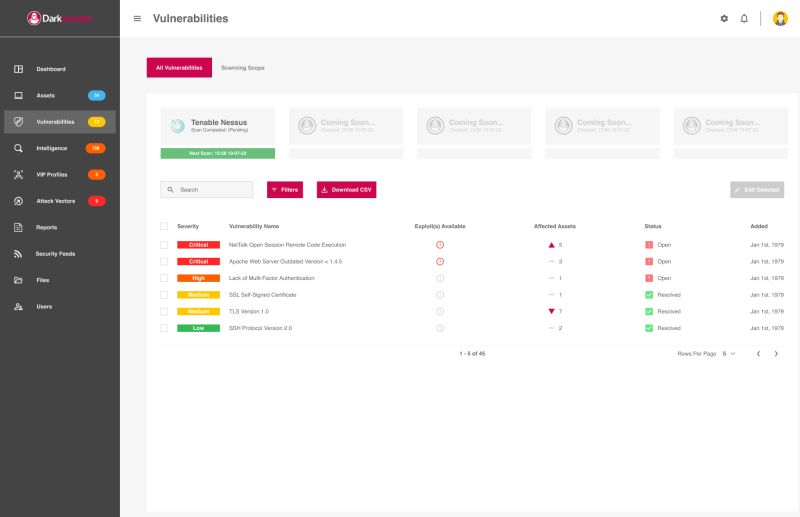
Burp Comparer: Allows users to compare content found between two different HTTP requests or HTTP responses. Burp Extender: See the Burp Extender section below; certain Burp Suite plugins are limited to only interact with Professional edition. Figure 2: RELEASE 1.8 IS HERE: VULNERABILITY SCANNING & ENHANCED DARK WEB CRAWLER ...
Burp Scanner: Automates report auditing and/or web crawling for HTTP captured requests/responses. Uses internal rules to audit contents from intercepted HTTP responses in order to search for vulnerable response values. Capacitates users to customize scanners' speeds and findings coverage. Burp Dashboard: Displays findings results and categorizes issues based on severity. Detailed descriptions and remediation steps may be provided based on what type of finding. Burp Intruder: Similarly to Burp Repeater at a broader extent, grants users the means to send multiple parallel HTTP requests with changes to specified request variables. Burp Collaborator: Simulates C2 Server hosting to attempt external service interaction and Out-of-Band attacks. Burp Organizer: Allows users to curate selected HTTP requests/responses into a saved collection. Burp Infiltrator: An IAST agent scripted to automate interactive/runtime scanning and communicate results through the Burp Collaborator feature. Burp Clickbandit: A tool to concept proof to test clickjacking attacks against web applications' front-end HTML and JavaScript files. File Saving: Professional edition allows users to save their projects as ".burp" files.
Honeypots are security devices whose value lie in being probed and compromised. Traditional honeypots are servers (or devices that expose server services) that wait passively to be attacked. Client Honeypots are active security devices in search of malicious servers that attack clients. The client honeypot poses as a client and interacts with the server to examine whether an attack has occurred. Often the focus of client honeypots is on web browsers, but any client that interacts with servers can be part of a client honeypot (for example ftp, email, ssh, etc.). There are several terms that are used to describe client honeypots. Besides client honeypot, which is the generic classification, honeyclient is the other term that is generally used and accepted. However, there is a subtlety here, as "honeyclient" is actually a homograph that could also refer to the first known open source client honeypot implementation (see below), although this should be clear from the context.
HoneyMonkey [3] is a web browser based (IE) high interaction client honeypot implemented by Microsoft in 2005. It is not available for download. HoneyMonkey is state based and detects attacks on clients by monitoring files, registry, and processes. A unique characteristic of HoneyMonkey is its layered approach to interacting with servers in order to identify zero-day exploits. HoneyMonkey initially crawls the web with a vulnerable configuration. Once an attack has been identified, the server is reexamined with a fully patched configuration. If the attack is still detected, one can conclude that the attack utilizes an exploit for which no patch has been publicly released yet and therefore is quite dangerous.
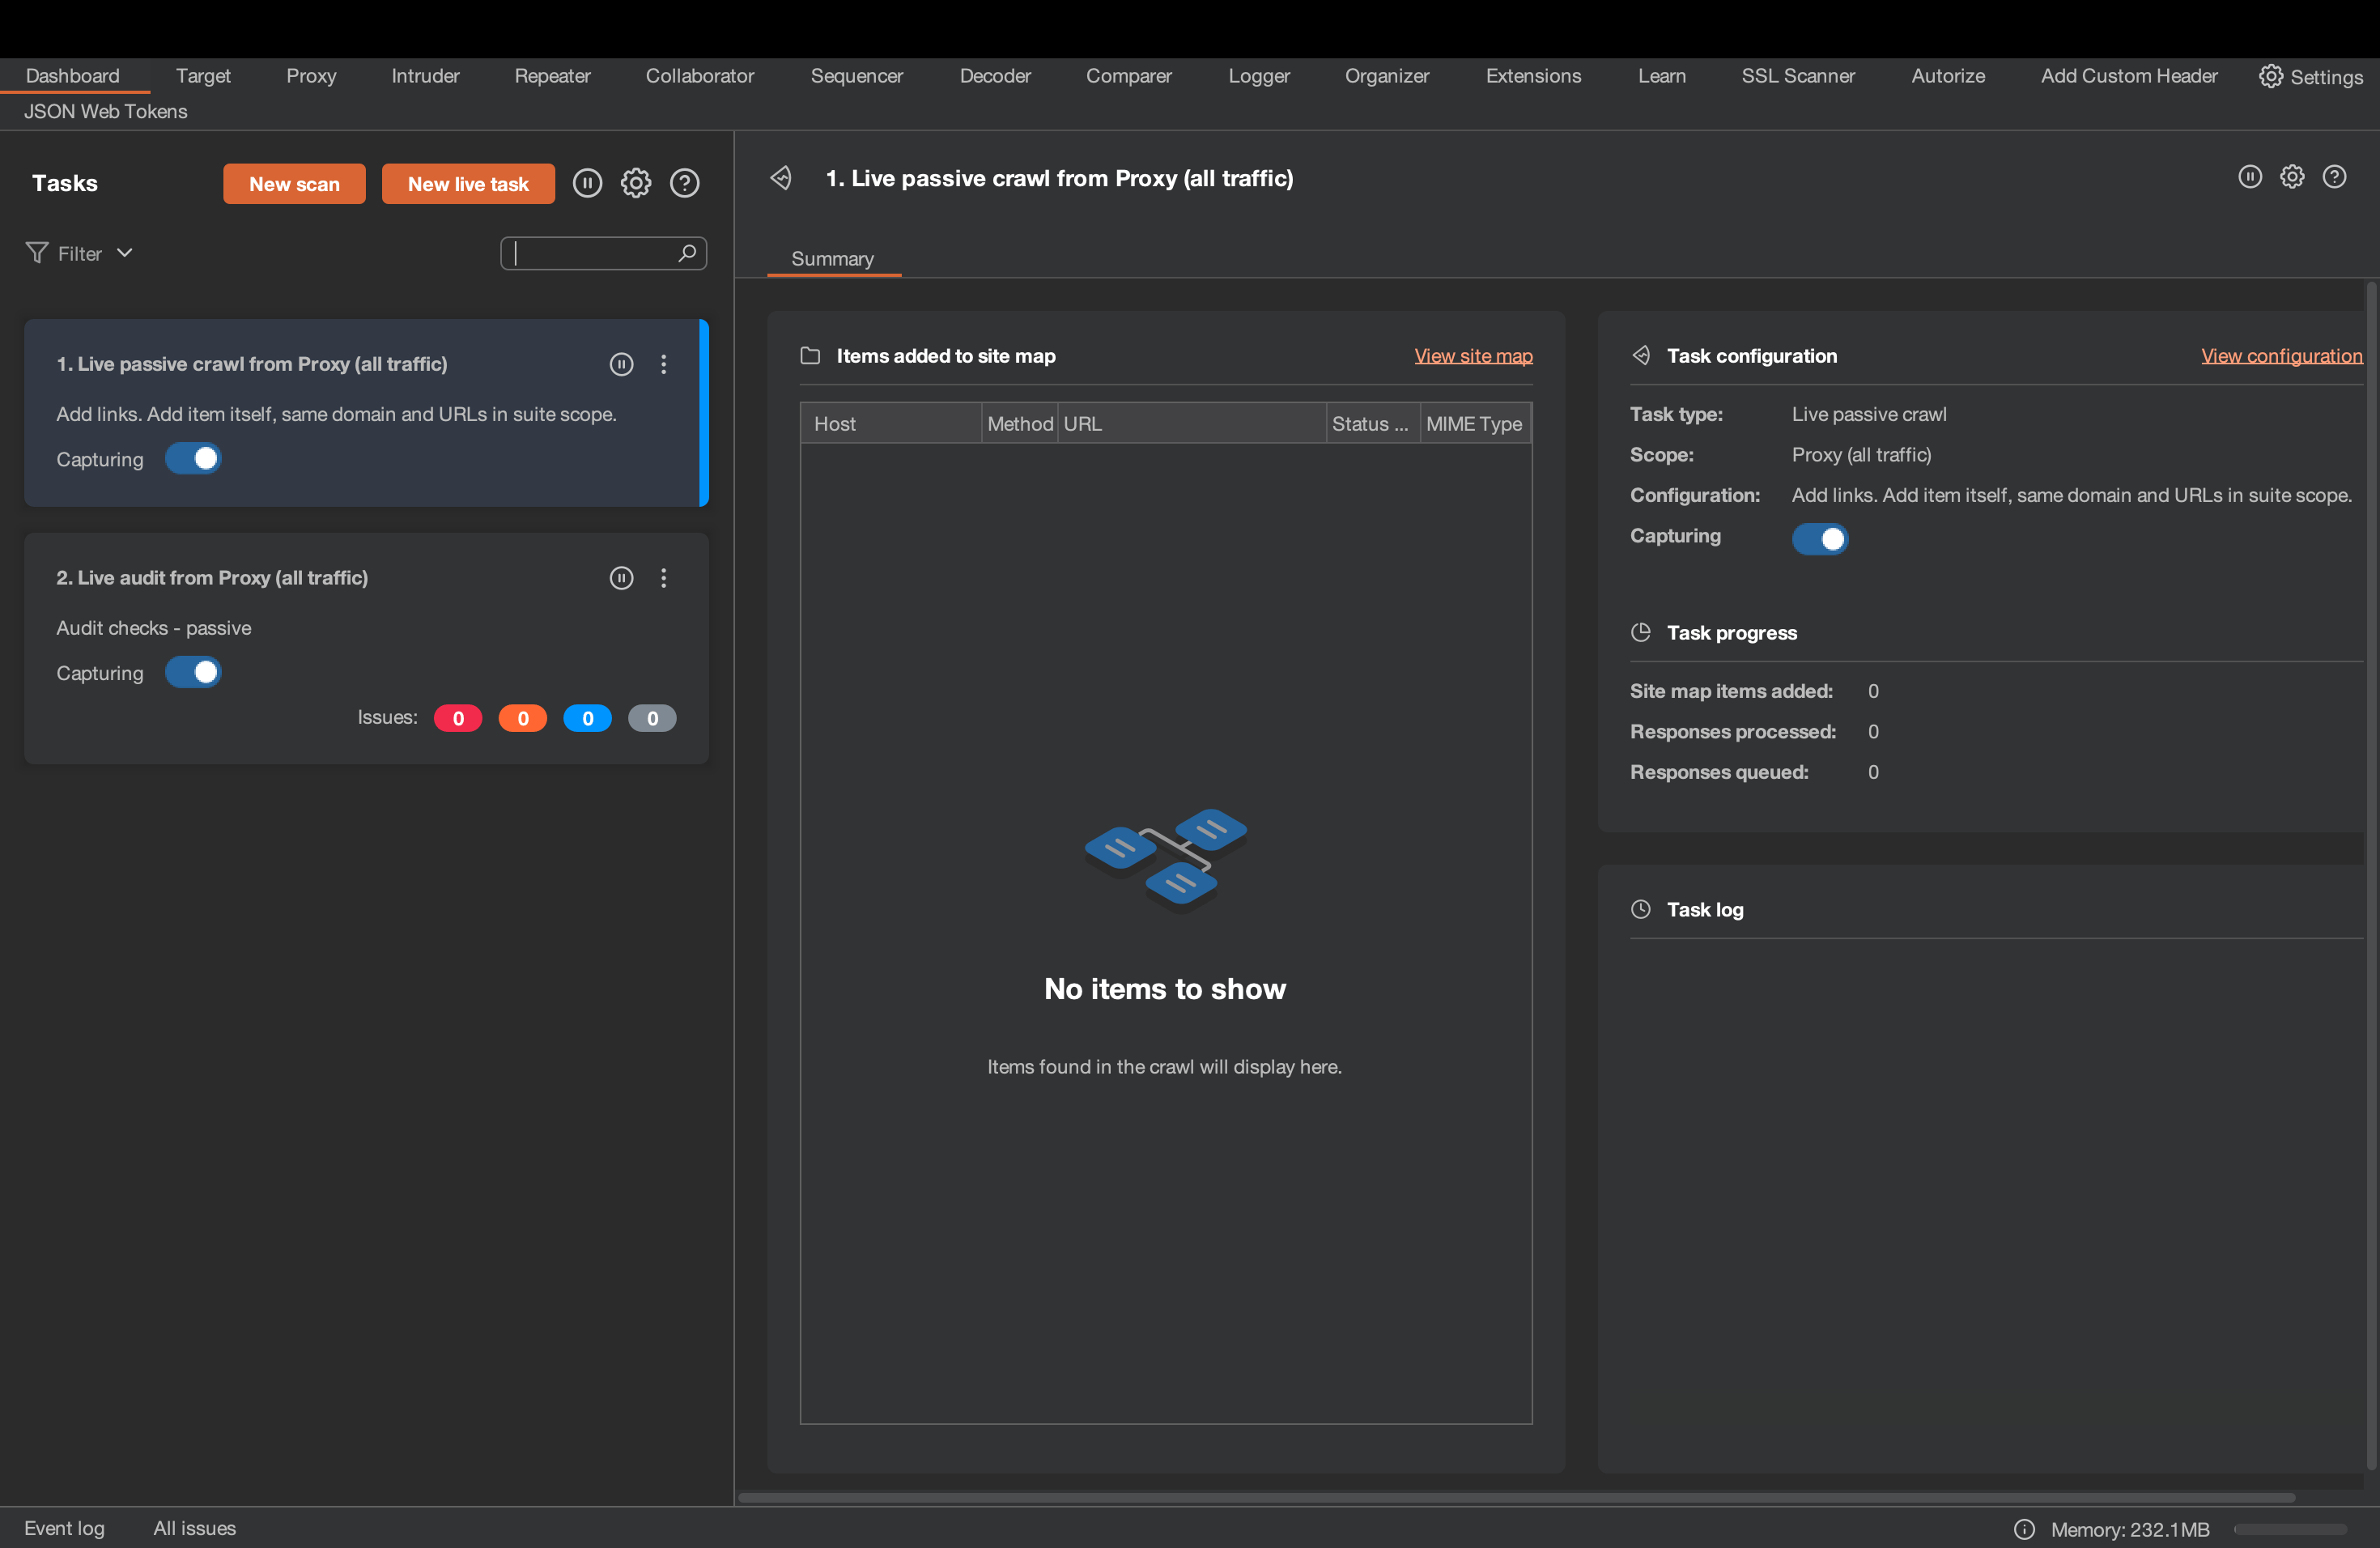
In the rapidly evolving digital landscape, web security is paramount. A Web Application Security Scanner plays a crucial role in identifying vulnerabilities . This article provides an introduction to build a simple scanner using Python, focusing on system design, architecture , design patterns , and data modeling. Figure 3: 13 Best Web Application Vulnerability Scanners for 2026 Modular Architecture Our scanner adopts a modular approach, ensuring scalability and maintainability. Key components include: The SQL Injection Module exemplifies the application of our design principles in a real-world context.
Performance Optimization : Implementing asynchronous scanning and efficient data handling to manage performance. False Positive Reduction : Employing advanced algorithms and heuristics to minimize false positives. Continuous Updates : Keeping the scanner updated with the latest vulnerability signatures and detection logic. Unit Testing : Ensuring reliability and correctness of individual modules. Integration Testing : Verifying the seamless functioning of modules within the system.
Real-world Testing : Using known vulnerable applications like OWASP WebGoat to test the scanner's effectiveness. User Documentation : Detailed guides on setup, configuration, and report interpretation. Deployment Strategy : Packaging the application for ease of installation and use, considering containerization for better environment control. Permission-Based Testing : Emphasizing the need for authorization before scanning any web application. Legal Compliance : Adhering to legal requirements and ethical standards in the deployment and use of the scanner.
Building a Web Application Security Scanner is a complex yet rewarding endeavor. This project not only bolsters your Python and software design skills but also deepens your understanding of web application vulnerabilities . As the threat landscape evolves, the scanner must adapt, incorporating the latest in vulnerability detection and software architecture trends. This tool, when fully realized, becomes an indispensable part of any developer's or security analyst's toolkit , providing insights and foresight in the crucial domain of web security.
Author: Bhavya Bhalla Institution: Thapar Institute of Engineering and Technology Project Type: Cybersecurity Internship - Elevate Labs This project implements a comprehensive web vulnerability assessment platform that automates the detection of common web application security vulnerabilities. The system combines industry-standard security testing methodologies with a professional web interface suitable for client demonstrations and security assessments.
Python 3.9+ III Flask Web Framework III BeautifulSoup4 (HTML Parsing) III Requests (HTTP Client) III Threading (Concurrent Processing) III JSON Reporting System HTML5 + CSS3 + Vanilla JavaScript III Responsive Design III Real-time API Communication III Progressive Web App Features III Professional UI/UX 2. System Architecture & Core Working Principles OWASP Testing Framework III Top 10 Vulnerability Coverage III Automated Payload Injection III Error Pattern Recognition III Security Header Validation Clone Repository git clone https://github.com/yourusername/web-vulnerability-scanner.git cd web-vulnerability-scanner Setup Environment python -m venv venv source venv/bin/activate # Windows: venv\Scripts\activate pip install -r requirements.txt Test against public vulnerable application python src/vulnerability_scanner.py --target http://testphp.vulnweb.com/ POST /api/scan # Start new scan GET /api/scan/{id}/status # Check scan progress GET /api/scan/{id}/report # Get detailed report GET /api/scans # List all scans GET /api/scan/{id}/download # Download report file SQL Injection Detection: { "type": "SQL Injection", "severity": "Critical", "url": " https://target.com/login.php ", "payload": "' OR 1=1--", "description": "SQL Injection vulnerability detected...", "recommendation": "Use parameterized queries..." } XSS Detection: { "type": "Cross-Site Scripting (XSS)", "severity": "High", "url": " https://target.com/search.php ", "payload": "", "description": "Reflected XSS vulnerability found...", "recommendation": "Implement input validation..." } Crawling Configuration MAX_CRAWL_DEPTH = 2 # Website exploration depth MAX_LINKS_PER_PAGE = 10 # Links to follow per page REQUEST_TIMEOUT = 10 # HTTP request timeout (seconds) Payload Configuration XSS_PAYLOADS = [...] # Custom XSS attack vectors SQL_PAYLOADS = [...] # Custom SQL injection payloads http://testphp.vulnweb.com/ # Public test site http://demo.testfire.net/ # IBM Security AppScan demo https://xss-game.appspot.com/ # Google XSS challenge web-vulnerability-scanner/ III src/ I III vulnerability_scanner.py # Core scanning engine I III flask_app.py # Web application server III templates/ I III index.html # Dashboard interface III static/ I III style.css # Custom styling III reports/ I III *.json # Generated scan reports III tests/ I III test_scanner.py # Unit tests III docs/ I III api_documentation.md # API reference III requirements.txt # Python dependencies III README.md # Project documentation III .gitignore # Git ignore rules III LICENSE # Project license Bhavya Bhalla I Email: bhavyabhalla19@gmail.com I LinkedIn: linkedin.com/in/bhavya-bhalla-235300258 I GitHub: github.com/bhavya-bhalla Institution: Thapar Institute of Engineering and Technology Course: B.E. Computer Engineering (2022-2026) CGPA: 7.20/10.0 "Bridging technical security expertise with business impact through innovative vulnerability assessment solutions." Professional web vulnerability assessment platform with automated XSS and SQL injection detection. Built with Python/Flask featuring real-time scanning dashboard and comprehensive security reporting.
This is a comprehensive web application vulnerability scanner developed in Python. Designed as a portfolio piece for cybersecurity, it combines robust backend scanning logic with an interactive and modern graphical user interface. It demonstrates core concepts of web interaction, intelligent crawling, and essential vulnerability detection. This tool is developed for educational purposes, learning, and authorized security testing ONLY. DO NOT use this scanner on any website or system without explicit, written permission from the owner. Unauthorized scanning can lead to legal consequences and severe reputational damage. Always ensure you have proper authorization before initiating any security testing.
Create and Activate a Virtual Environment: It's highly recommended to use a virtual environment to manage project dependencies. Install Dependencies: Once your virtual environment is active, install all required Python libraries listed in requirements.txt . This is the primary way to interact with the scanner, providing a user-friendly graphical interface.
Building a modular vulnerability scanner in Python — from crawlers and fingerprinting to SQL injection detection and report generation. 3. Software Implementation, Frameworks & Protocols To understand web security, you have to learn how automated scanners work. I built VulnScanner , a modular vulnerability scanner in Python, to run penetration testing experiments on local labs. Here is a breakdown of how the scanner is architected.
This project taught me the importance of input validation, sanitized database queries (prepared statements), and the utility of automated testing tools in modern secure development pipelines. I recently completed my MSIT Capstone project at the University of the People an automated web vulnerability scanner built with Python and OWASP ZAP. Here's what I built, how it works, and what I found. The Problem Most web security tools like OWASP ZAP are powerful but complex. A developer without a cybersecurity background struggles to configure them correctly. My goal was to wrap ZAP's API into a simple Python CLI tool that anyone can run with a single command. How It Works The scanner has four modules: URL Seeder manually seeds known endpoints into ZAP's site tree before scanning. This is critical for Angular SPAs like OWASP Juice Shop where the traditional spider misses hash-based routes. Spider crawls all discoverable URLs from the seeded endpoints. Active Scanner injects attack payloads (SQL injection strings, XSS vectors) against every discovered endpoint. Report Generator produces a timestamped JSON report with a risk summary.
Running a scan is one command: bashpython scanner.py --spider --scan --alerts --report What I Found Testing against OWASP Juice Shop, the scanner identified 122 security alerts including: I 1 High SQL Injection at /rest/products/search?q=apple' I 70 Medium CORS misconfigurations, missing CSP headers I 23 Low Application error disclosures, timestamp leakage I 28 Informational Modern web app indicators The Interesting Problem Initially the scanner only found 1 alert. The issue? Juice Shop is an Angular SPA with hash-based routing. The ZAP spider couldn't discover routes like /#/login because they're rendered client-side. The fix was implementing a URL seeder that manually requests all known endpoints through the ZAP proxy before spidering. After that fix — 122 alerts.
The Code The full source code is available on GitHub: I https://github.com/JAAFAR12781/zap-vulnerability-scanner What's Next I'm planning to add AJAX spider support for deeper SPA coverage and HTML report generation for non-technical stakeholders. If you're building web apps and haven't run a vulnerability scan yet this tool makes it easy to get started. If you’re serious about bug bounties, penetration testing, or ethical hacking, learning how to build your own web vulnerability scanner is one of the most powerful skills you can develop.
Professionals understand how scanners work internally. Advanced hackers build their own. In this step-by-step guide, you’ll learn how to make a web vulnerability scanner using Python — designed for learning, lab environments, and authorized testing only. Instead of manually testing every page, a scanner automates reconnaissance and testing.
This knowledge alone makes you better than someone who just presses “Scan” in a GUI tool. In this article, you are going to learn to create a basic security tool that can be helpful in identifying common vulnerabilities in web applications. I have two goals here. The first is to empower you with the skills to develop tools that can help enhance the overall security posture of your websites. The second is to help you practice some Python programming.
In this guide, you will be building a Python-based security scanner that can detect XSS, SQL injection, and sensitive PII (Personally Identifiable Information). Generally, we can categorize web security vulnerabilities into the following buckets (for even more buckets, check the OWASP Top 10 ): SQL injection : A technique where attackers are able to insert malicious SQL code into SQL queries through unvalidated inputs, allowing them to modify / read database contents.
Cross-Site Scripting (XSS) : A technique where attackers inject malicious JavaScript in trusted websites. This allows them to execute the JavaScript code in the context of the browser and steal sensitive information or perform unauthorized operations. Sensitive information exposure : A security issue where an application unintentionally reveals sensitive data like passwords, API keys and so on through logs, insecure storage, and other vulnerabilities.
Common security misconfigurations : Security issues that occurs due to improper configuration of web servers – like default credentials for administrator accounts, enabled debug mode, publicly available administrator dashboards with weak credentials, and so on. Basic authentication weaknesses : Security issues that occur due to lapses in password policies, user authentication processes, improper session management, and so on.
4. Practical Deployment, Analysis & Case Studies This class will serve as our main class that will handle the web security scanning functionality. It will track our visited pages and also store our findings. We have the normalize_url function that we’ll use to ensure that you don’t rescan URLs that have already been seen before.
This function will essentially remove the HTTP GET parameters from the URL. For example, https://example.com/page?id=1 will become https://example.com/page after normalizing it. The first step in our scanner is to implement a web crawler that will discover pages and URLs in a given target application. Make sure you’re writing these functions in our WebSecurityScanner class.
This crawl function helps us perform a depth-first crawl of a website. It will explore all pages of a website while staying within the specified domain. For example, if you plan to use this scanner on https://google.com , the function will first get all the URLs and then one-by-one check if they belong to the specified domain (that is, google.com ). If so, it will recursively continue to scan the seen URL up to a specified depth which is supplied with the depth parameter as an argument to the function. We also have some exception handling to make sure we handle errors smoothly and report any errors during crawling.
Now let’s finally get to the juicy part and implement our security checks. We’ll start first with SQL Injection. This function essentially performs basic SQL injection checks by testing the URL against common SQL injection payloads and looking for error messages that might hint at a security vulnerability. Based on the error message received after performing a simple GET request on the URL, we check whether that message is a database error or not. If it is, we use the report_vulnerability function to report that as a security issue in our final report that this script will generate. For the sake of this example, we are selecting a few commonly tested SQL injection payloads, but you can extend this to test even more.
This function, just like the SQL injection tester, uses a set of common XSS payloads and applies the same idea. But the key difference here is that we are looking for our injected payload to appear unmodified in our response rather than looking for an error message. If you are able to see our injected payload, most likely it will be executed in the context of the victim’s browser as a reflected XSS attack.
This function uses a set of predefined Regex patterns to search for PII like emails, phone numbers, SSNs, and API keys (that are prefixed with api-key-
Let’s finally stitch everything together by defining the scan and report_vulnerability function in the WebSecurityScanner class: This code defines our scan function which will essentially invoke the crawl function and recursively start crawling the website. With multithreading, we will apply all three security checks on the visited URLs. We have also defined the report_vulnerability function which will effectively print our vulnerability to the console and also store them in our vulnerabilities array.
The target URL will be supplied as a system argument and we will get the summary of URLs scanned and vulnerabilities found at the end of our scan. Now let’s discuss how you can extend the scanner and add more features. Here are some ideas to extend this basic security scanner into something even more advanced: Add configuration options for scan intensity and scope of searching (specifying the depth of scans through a CLI argument).
Adding authentication support for testing URLs that require session-based authentication. Now you know how to build a basic security scanner! This scanner demonstrates a few core concepts of Web Security. Keep in mind that this tutorial should only be used for educational purposes. There are several professionally designed enterprise-grade applications like Burp Suite and OWASP Zap that can check for hundreds of security vulnerabilities at a much larger scale.
5. Performance Evaluation & Extended Technical Observations I hope you learned the basics of web security and a bit of Python programming as well. Learn to code for free. freeCodeCamp's open source curriculum has helped more than 40,000 people get jobs as developers. Get started This project is a web crawler and vulnerability scanner tool developed by Rohit Ajariwal. The tool is designed to crawl a website and scan for common web application vulnerabilities, including SQL injection, XSS, command injection, file inclusion, directory traversal, HTML injection, CSRF, LFI, RFI, LDAP injection, XXE, SSRF, unvalidated redirects, and clickjacking.
Vulnerabilities Tested SQL Injection: Tests for SQL injection vulnerabilities using various payloads. XSS (Cross-Site Scripting): Tests for XSS vulnerabilities using different XSS payloads. Command Injection: Tests for command injection vulnerabilities by injecting OS command payloads. File Inclusion: Tests for local and remote file inclusion vulnerabilities. Directory Traversal: Tests for directory traversal vulnerabilities. HTML Injection: Tests for HTML injection vulnerabilities. CSRF (Cross-Site Request Forgery): Tests for CSRF vulnerabilities. LFI (Local File Inclusion): Tests for local file inclusion vulnerabilities. RFI (Remote File Inclusion): Tests for remote file inclusion vulnerabilities. LDAP Injection: Tests for LDAP injection vulnerabilities. XXE (XML External Entity): Tests for XXE vulnerabilities. SSRF (Server-Side Request Forgery): Tests for SSRF vulnerabilities. Unvalidated Redirects: Tests for unvalidated redirects. Clickjacking: Tests for clickjacking vulnerabilities. Logging All identified vulnerabilities are logged in the vulnerability_scanner.log file.
License This project is licensed under the MIT License - see the LICENSE file for details. Contributing Contributions are welcome! Please feel free to submit a Pull Request or open an issue. Individual Vulnerability Test Methods Each of these methods uses specific payloads to test for vulnerabilities like SQL Injection, XSS, Command Injection, etc. Here's an example for SQL Injection: This script is a basic web crawler and vulnerability scanner that can identify several common web application vulnerabilities by submitting payloads to forms on the target website and analyzing the responses.
The OWASP Benchmark Project is a Python test suite designed to verify the speed and accuracy of vulnerability detection tools. It is a fully runnable open source web application that can be analyzed by any type of Application Security Testing (AST) tool, including SAST, DAST (like ZAP ), and IAST tools. The intent is that all the vulnerabilities deliberately included in and scored by the Benchmark are actually exploitable so it's a fair test for any kind of application vulnerability detection tool.
The Benchmark project also includes scorecard generators for numerous open source and commercial AST tools, and the set of supported tools is growing all the time. This scoring capability is implemented in the BenchmarkUtils project, which is at: https://github.com/OWASP/BenchmarkUtils . The project documentation is all on the OWASP site at the OWASP Benchmark project pages. Please refer to that site for all the project details.
This is a preliminary initial release we are calling v0.1. Over the next several months we plan to improve/upgrade this project to get to a full v1.0 release when we have sufficient vulnerability coverage implemented. Note that all the releases that are available here: https://github.com/OWASP/BenchmarkPython/releases , are historical. The latest release is always available live by simply cloning or pulling the head of this repository (i.e., git pull).
ACKNOWLEDGEMENTS: The OWASP Benchmark project would like to thank the contributions of AppSecAI ( https://www.appsecai.io ) and their team members Theo Cartsonis and Jessica Salawu for doing the bulk of the development work to produce this first release of the Benchmark for Python test suite. The OWASP Benchmark for Python is a test suite designed to verify the accuracy of Python software vulnerability detection tools. A fully runnable web app written in Python, it supports analysis by Static (SAST), Dynamic (DAST), and Runtime (IAST) tools that support Python. For more details, see the OWASP Benchmark Project home page.
arXivLabs is a framework that allows collaborators to develop and share new arXiv features directly on our website. Both individuals and organizations that work with arXivLabs have embraced and accepted our values of openness, community, excellence, and user data privacy. arXiv is committed to these values and only works with partners that adhere to them.
Have an idea for a project that will add value for arXiv's community? Learn more about arXivLabs . This is a Python-based Web Vulnerability Scanner that analyzes websites for potential security threats, including: The tool automatically scans key pages, extracts forms and links, injects payloads, and reports vulnerabilities found. This project is intended for educational and ethical security research purposes only. Unauthorized use is strictly prohibited.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Web%20shell • https://en.wikipedia.org/wiki/Burp%20Suite • https://en.wikipedia.org/wiki/Client%20honeypot • https://dev.to/aissageek/building-a-simple-web-application-security-scanner-in-python-4g5f • https://github.com/bhavya-bhalla/web-vulnerability-scanner • https://github.com/Tabbi109/WebVulnScanner • https://saheerkhan.app/blog/web-vulnerability-scanning-python • https://dev.to/jaafar12781/how-i-built-an-automated-web-vulnerability-scanner-with-python-and-owasp-zap-l35 • https://spyboy.blog/2026/03/09/how-to-make-a-web-vulnerability-scanner-using-python-step-by-step-guide/ • https://www.freecodecamp.org/news/build-a-web-application-security-scanner-with-python
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Web Crawler For Security Vulnerability Scanning In Python.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Web Crawler For Security Vulnerability Scanning In Python... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |