Complete Technical Paper Content — Wifi Evil Twin Attack Detection Tool In Python
Overview & System Context
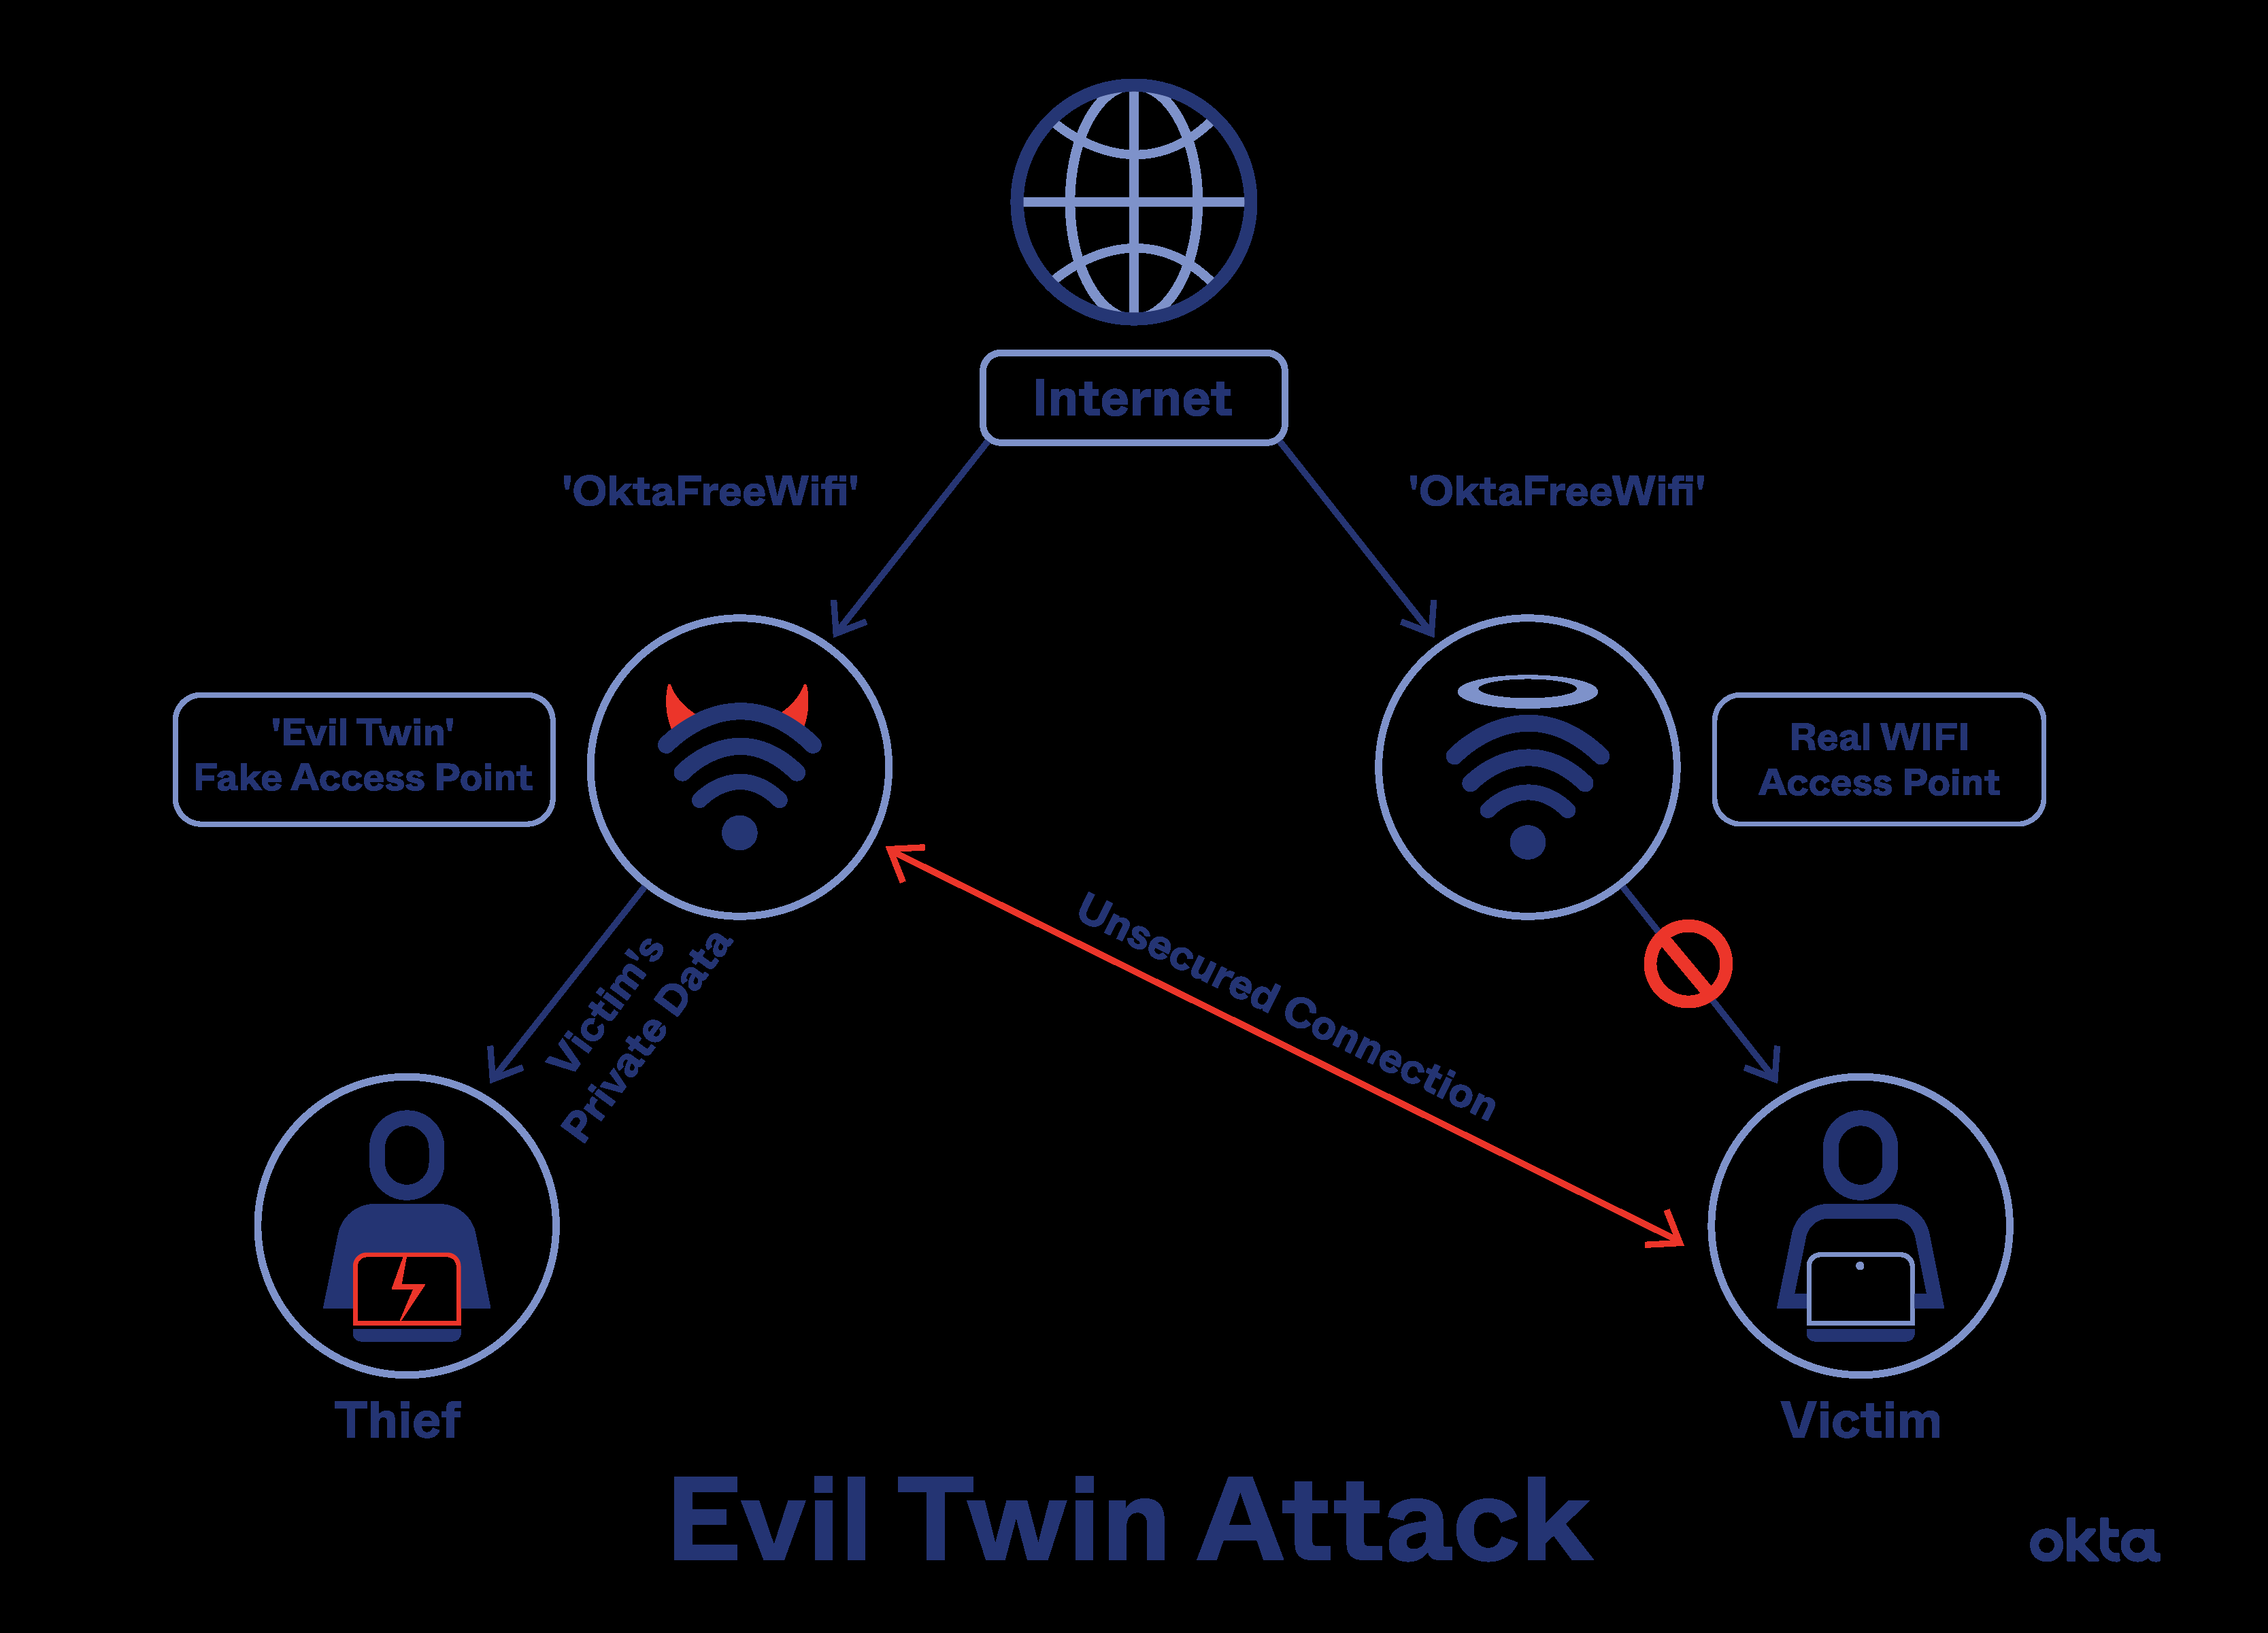
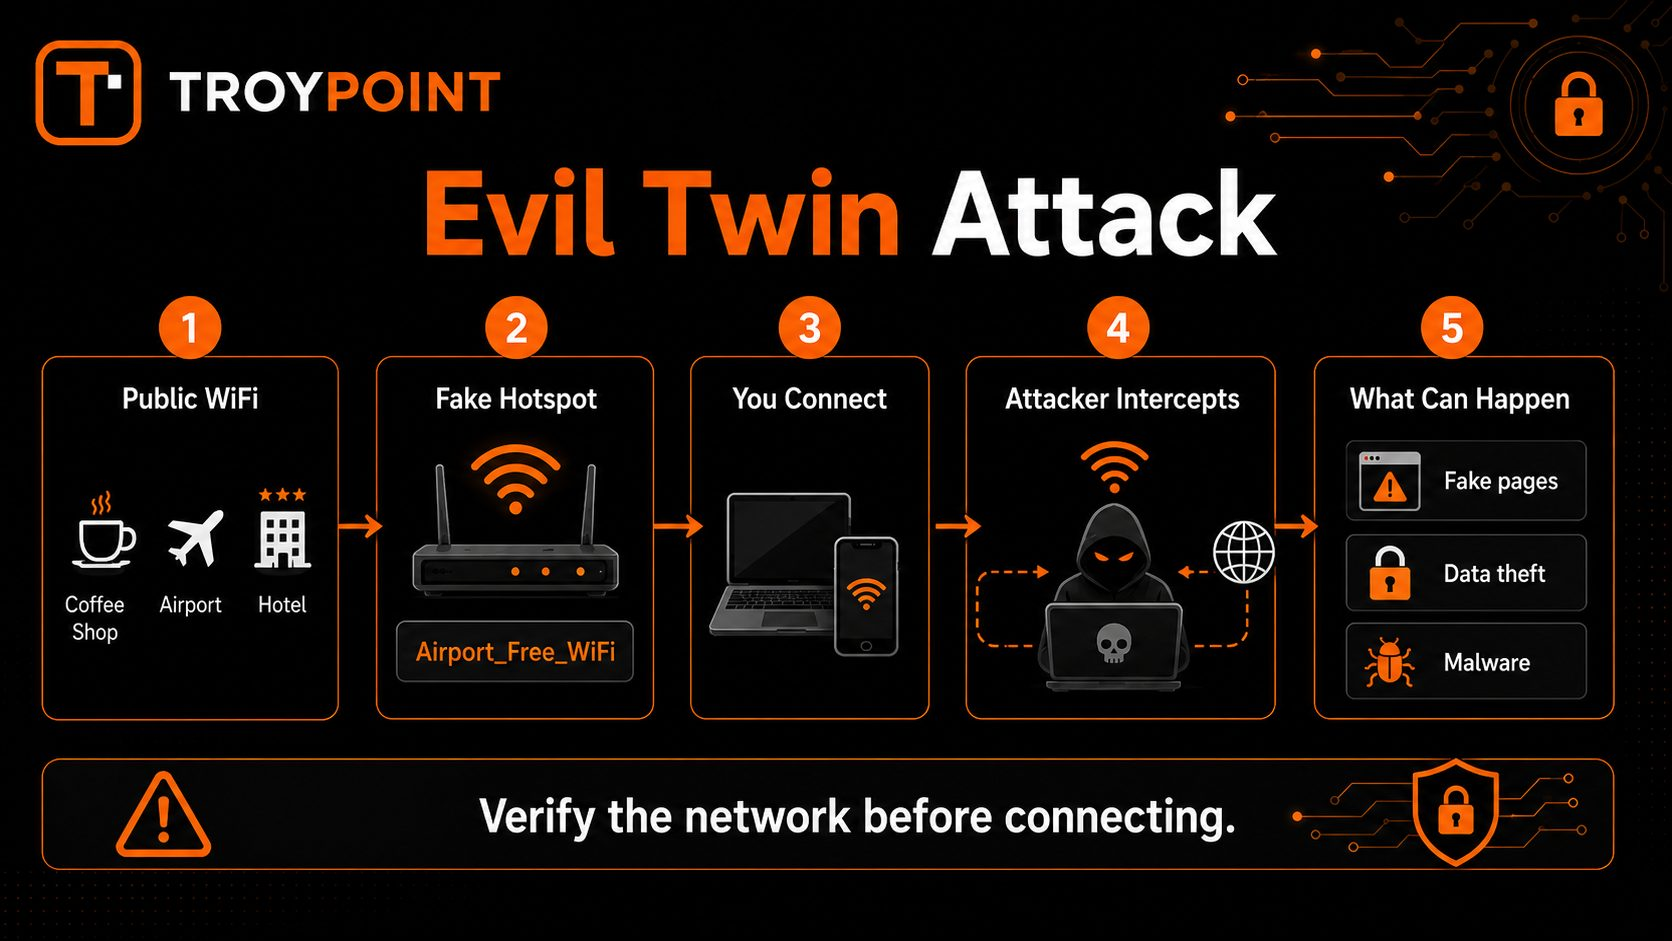
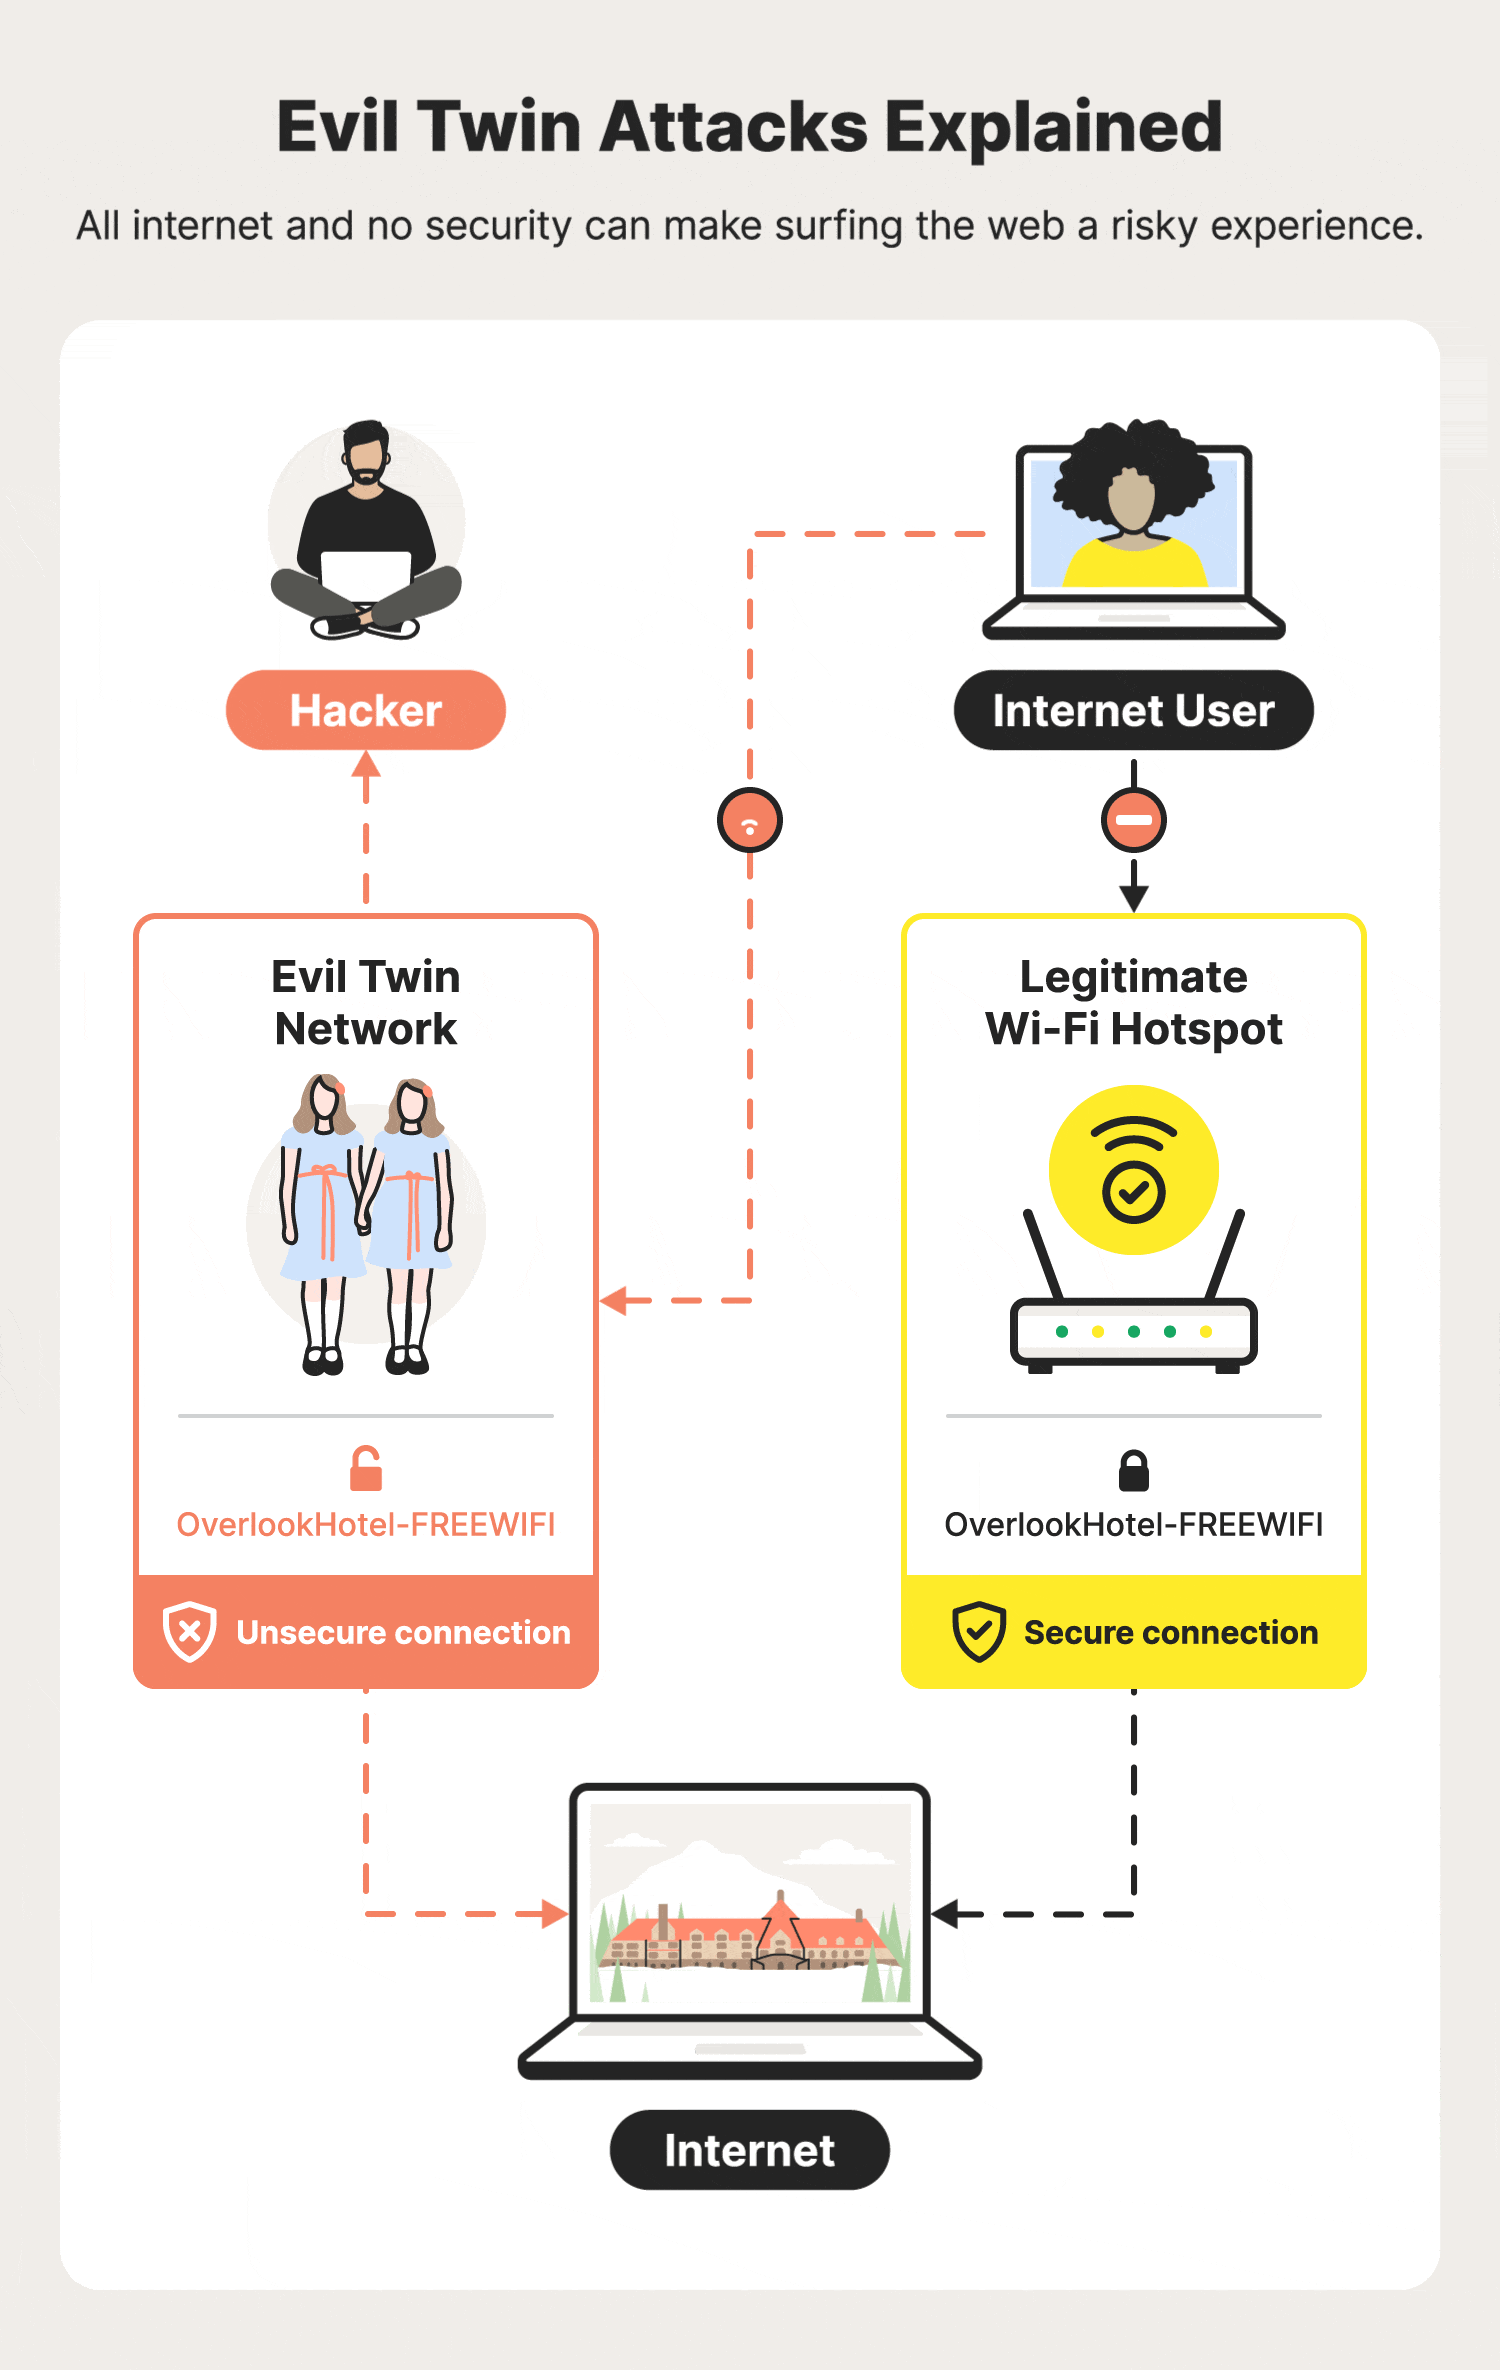
Wifi Evil Twin Attack Detection Tool In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~6116 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background An Evil Twin is a fake Wi-Fi network set up to trick people into connecting to it, thinking it’s a legitimate network, like one in a coffee shop or airport. Hackers create this network to steal personal information, such as passwords, credit card details, or emails, from those who connect. It works because it looks exactly like a real network, even using the same name. Once someone joins, their data can be monitored or stolen. It’s like sitting next to someone who secretly spies on everything you’re doing online.
Existing security measures for Wi-Fi networks often struggle to effectively detect and mitigate these sophisticated attacks. Traditional approaches rely heavily on signature-based detection and static rules, which lack adaptability and real-time effectiveness in open Wi-Fi settings. While machine learning (ML) has shown promise for enhancing network security, most current ML-based models remain theoretical and demonstrate high accuracy with offline datasets yet fail to deliver practical solutions in real-time scenarios.
The system starts by preparing a dataset to ensure the data is clean and relevant. Once ready, machine learning (ML) techniques are used to train a model. The goal is to choose the model that performs the best with high accuracy. Next, a packet capture tool collects Wi-Fi data in monitor mode to gather detailed network information. This data is saved and converted into JSON format, making it easier to work with. The JSON data is then turned into a CSV file, which is sent to the trained ML model for predictions. Finally, the model's results are shared with the user, offering useful insights or recommendations.
Figure 1: Evil Twin Attack: Fake WiFi Access Point Vulnerabilities | Okta AWID2 dataset , a wireless intrusion detection evaluation dataset developed by the University of the Aegean. Reference : C. Kolias, G. Kambourakis, A. Stavrou and S. Gritzalis, "Intrusion Detection in 802.11 Networks: Empirical This research addresses a significant gap in the work of Asaduzzaman, Majib, and Rahman (2020), who proposed a Wi-Fi frame analysis-based detection scheme and achieved 91.24% accuracy using a J48 decision tree model.
However, their approach remains theoretical and limited in scope. In contrast, this study goes beyond theoretical models by leveraging various machine learning algorithms to provide a practical, real-time solution for improving accuracy. This research not only offers a robust solution for real-world deployment but also enhances detection accuracy beyond the 91.24% achieved by prior study.
Figure 2: 5 Ways to Protect Your Privacy on WiFi (2026 Guide) Reference : M. Asaduzzaman, M. S. Majib and M. M. Rahman, "Wi-Fi Frame Classification and Feature Selection Analysis in 10.1109/TENSYMP50017.2020.9231042. The Research-Evil_Twin_Detection.ipynb notebook provides a detailed walkthrough of the preprocessing steps, model training, results, and analysis. Below is a summary of the key steps and findings: Raspap is a simple yet powerful web-based interface that makes managing wireless access points (AP) on a Raspberry Pi easy. With RaspAP, you can quickly set up your Raspberry Pi as a Wi-Fi hotspot, allowing other devices to connect to your Pi over the network. It's designed to be lightweight, easy to install, and simple to use.
Whether you're setting up a Raspberry Pi for personal or professional use, RaspAP offers an intuitive web interface to manage your wireless network settings, including SSID, password, and IP address configurations. It’s perfect for scenarios where you need a portable Wi-Fi hotspot, such as IoT projects, secure networks, or development environments. Source Code Figure 3: What is an evil twin attack? + how to avoid them - Norton This project uses RaspAP as the backend while replacing its original frontend with a custom setup named Netaegis. Netaegis is our Research project product name.
Our goal is to detect and prevent evil twin WiIFi with steps you can run in the field. You need admin access to your WLAN, a capture tool like Wireshark or tshark, and authority to test in a lab or maintenance window. We assume enterprise WPA3 or mixed deployments with Protected Management Frames available. You will learn how to establish baselines, analyze beacons, enforce safeguards, and validate that detection works. The workflow blends planning, environment setup, ordered execution, and checks that measure success. Early paragraphs show you how to detect beacons that do not match expected BSSID lists, then later steps help prevent recurrence. Throughout, we balance thoroughness with low noise and practical on-call operations.
Start by defining scope so detection and prevention map to business risk, not guesswork. List production SSIDs, each authorized BSSID per building, and channels used. A simple rule of thumb is one authoritative inventory per site with last verified date and approver. Include sensitive zones such as executive floors where attackers might position an evil twin near entrances. The tradeoff is granularity versus maintenance cost, so draft an update cadence that fits change windows. Scope must cover guest, IoT, and internal SSIDs because attackers often mimic the least protected name. This plan clarifies what you intend to detect, how you will prevent spoofing, and where you will not act to avoid false alarms.
Create a baseline of RF metrics to make later anomalies stand out clearly. Capture beacon frames for each SSID in representative areas and record BSSID, channel, security suite, and average RSSI. For office floors, a ten to fifteen minute walk per quadrant usually yields stable numbers. Include notes on structural materials like glass or concrete that skew signal propagation. The limitation is that people and devices change the RF picture, so repeat baselines after major rearrangements.
Baselines help you detect an evil twin because a sudden SSID match with a new BSSID or a stronger nearby signal at an odd channel becomes obvious. Document where the baseline storage lives and who maintains it. Align stakeholders early to prevent accidental disruption when you enforce protections. Notify help desk, facilities, and security operations that you will adjust PMF settings and monitor for spoofed SSIDs. Share a rollback plan that defines measurable exit criteria such as connection failure rates below a safe threshold. A practical example is scheduling PMF required for internal SSIDs during a low traffic window and watching authentication success. The risk is user impact from legacy clients that do not support PMF. Mitigate by piloting on a small segment before broad changes. This alignment ensures your detect and prevent steps can proceed without surprises while maintaining trust with operations teams.
Choose tooling that can see management frames and export structured lists. Wireshark and tshark read beacon fields, and many enterprise controllers expose neighbor reports through APIs. Start with a simple approach that matches SSID to known BSSID values. Maintain an allowlist per SSID that includes MAC OUI notes and channel allocations. The tradeoff is complexity when you add multiple sources, so begin with one authoritative list from the controller if available. Prepare a staging laptop with a dual band adapter that supports monitor mode. This setup allows you to capture nearby advertisements and compare them against your inventory without connecting to unknown access points.
Configure your WLAN for robust posture before testing to prevent accidental exposure. Set Protected Management Frames to required for internal SSIDs and capable for guest while you evaluate client compatibility. Disable transition modes that allow downgrade from WPA3 where feasible because an evil twin often exploits weaker association paths. A balanced configuration protects users while keeping doors open for controlled evaluation. If you need a reference for layered controls across authentication suites, consult a comprehensive map of modern standards in this guide on best practices for WPA3 and WPA4 security . These preparations reduce the chance that testing introduces fresh risk during normal operations.
2. System Architecture & Core Working Principles Draft a small comparison for capture flags so operators pick consistent parameters. Use a monitor channel aligned to your target SSID where practical and narrow the capture to management frames to limit noise. Keep timestamps and RSSI fields enabled because they help correlate with physical locations later. The tradeoff is missing distant beacons if your channel choice is too narrow, so repeat per channel plan in larger venues. A predictable capture profile lets your team repeat results and spot deviations confidently. The table below shows common flags that keep beacon captures tidy while preserving fields needed for evil twin checks.
Run detection in a tight loop that compares live beacons to your allowlist while you stand near likely lure points. A practical path is to walk from building entrances to elevators and common areas with a laptop in monitor mode. Look for your SSID advertised by unknown BSSIDs, unusually strong RSSI compared to baseline, or unexpected channels. Decide thresholds up front such as unknown BSSID and RSSI at least 8 dB stronger than the nearest authorized AP in the same spot. This reduces noise from distant neighbors using similar names. When you confirm a suspect, record time, channel, and signal then notify operations. Apply preventive controls only after confirming repeatability across two passes.
Use a minimal tshark command to list unique BSSIDs for a specified SSID, which makes rogues obvious without sifting through full captures. The snippet below prints SSID, BSSID, and signal strength so you can quickly note unknown transmitters. Expect to see your known BSSIDs alongside any imposters that advertise the same SSID in range. If the list includes unexpected BSSIDs near your baseline areas, mark them for follow up and containment. The method trades deep detail for speed, which is ideal for on-site checks and follow up analysis later on full pcap files.
Apply containment and prevention after confirming a rogue pattern. Enable PMF required for sensitive SSIDs and disable overly permissive options like open authentication for production names. Consider broadcast SSID changes only with communication, because renaming disrupts users and can cause shadow settings to linger. If you use a wireless intrusion prevention system, review its tuning guidance to avoid deauth storms or noisy signatures. For a deeper view into sensors and containment approaches, see the practical overview on tuning WIDS and WIPS for low noise response . These steps prevent easy reappearance by forcing clients to reject unauthenticated management frames and reducing unsafe associations.
Prove detection quality by recreating the scenario in a controlled lab that mirrors production channels. Use a test AP advertising your SSID with a distinct BSSID and position it near a normal coverage zone. Run the same capture procedure and confirm the rogue appears as unknown with the expected RSSI relationship. Validation fails if your thresholds miss the twin or flag legitimate APs due to overlapping small cells. Adjust channel selection and walking paths to remove blind spots near stairwells and elevator shafts. This process verifies that your workflow can detect an evil twin consistently without swamping responders with false positives.
Verify prevention by forcing common client behaviors and observing the results. Attempt to associate with the rogue BSSID from a test device and ensure PMF blocks management frame abuse. Check that enterprise authentication rejects imposters without tearing down good sessions on nearby legitimate APs. Document pass or fail alongside client OS versions to capture compatibility reality. The tradeoff is time spent chasing edge behavior on older handhelds, which may never meet policy.
Decide whether to segment those devices or retire them. These checks give evidence that prevention steps do more good than harm and that users stay connected to trusted infrastructure. Record outcomes in the baseline inventory so future sweeps can measure drift. Add confirmed rogue locations, observed channels, and timestamps to help correlate with building access logs if investigation continues. Save filtered beacon lists as artifacts for audit trails, keeping file names consistent with site codes and dates. The overhead is storage and cataloging effort, which pays back when a similar alert reappears months later. With a durable record, your team can act quickly on recurring patterns instead of repeating early analysis. This closes the loop on detect and prevent work by making validation durable and repeatable across site visits.
Address false positives by separating neighbor SSIDs from true impersonation. Some nearby networks might share your SSID string in public spaces, which confuses naive checks. Tighten criteria to match SSID plus OUIs that your hardware actually uses or expected RSN capabilities for WPA3. A practical threshold is unknown BSSID with a strong RSSI and mismatched OUI or RSN suite. The tradeoff is missing a sophisticated adversary that spoofs OUIs, so keep multiple signals in play. When alerts still spike, reduce monitoring radius around building edges where neighbors dominate and prioritize interior floors where your clients operate most.
Handle intermittent detections by correlating with time and channel. Attackers sometimes move or rotate channels to evade simple checks. Compare detections that occur within a short window and share ESSID but differ in channel hop patterns. If patterns cluster around shift changes or lunchtime peaks, station a responder at entrances to inspect devices. The limitation is manpower and schedule coverage. To compensate, automate correlation in your SIEM using key fields like SSID, BSSID, and channel over time windows. This narrows responders to meaningful signals without inspecting every transient advertisement that passes by.
Reduce user impact from enforced protections by staging changes and measuring client outcomes. Start with guest or IoT segments that have limited blast radius before moving PMF required into internal SSIDs. Track authentication success, roaming performance, and help desk tickets for at least one business cycle. Roll back only when both objective metrics and operator sentiment point to degradation. For advanced adversarial risks such as spoofed management frames and deauthentication, align mitigation with guidance on validating PMF modes for attack resistance . Ongoing tuning keeps detect and prevent measures stable while your environment evolves.
Extend your coverage by integrating beacon checks with continuous telemetry from your WLAN controller and facility floor maps. Automate allowlist refresh on change windows and schedule roaming walk tests quarterly. Consider expanding detections to include anomalies in RSN information elements and channel utilization near sensitive spaces. The tradeoff is alert fatigue, so stage one additional signal at a time and revisit thresholds. For teams standing up broader monitoring, explore how to correlate WiIFi signals with security tooling so investigations move faster with fewer manual sweeps. Incremental improvements keep evil twin detection resilient as layouts change and user density shifts.
Strengthen responder readiness with playbooks that pair evidence with actions under time pressure. Define who validates a suspected rogue, who approves containment, and how to communicate with impacted users if brief disruption is expected. Keep one reversible change per step so rollback remains straightforward. A short runbook that includes known safe test areas and escalation contacts prevents drift during on-call events. When your process is mature, add scenario drills to rehearse realistic detection and prevention timelines. Over time, your organization will spot spoofed SSIDs earlier and apply controls with confidence and minimal disruption.
Broaden security posture by adding adjacent controls that close common gaps. Review hotspot policies around open networks and educate users on preferred connection profiles to avoid unsafe associations. If your environment includes campus deployments, maintain a living diagram of authorized radios per building to anchor field checks. Pair periodic sweeps with data from authentication failures to triangulate suspicious behavior that aligns with evil twin tactics. As your next research step, consider a field guide that explains sensors, detections, containment, and tuning strategies to keep responses effective without excess noise. Continuous care keeps detect and prevent measures aligned with real conditions.
An evil twin advertises your SSID but is controlled by an attacker and placed to lure your clients. A neighbor AP with a common name is unrelated and usually on other channels. Confirm by checking unknown BSSIDs, channel plan mismatches, and stronger local RSSI. PMF blocks unprotected management frame tricks such as deauthentication and association abuse, which reduces attack options. It does not prevent a client from seeing a spoofed SSID. Combine PMF with allowlists, monitoring, and user profiles to avoid unsafe associations.
Beacon captures are passive and generally safe during business hours if you only listen. Containment or configuration changes should occur in maintenance windows with a rollback plan. Communicate timing and impact to operations and support teams prior to changes. Tighten criteria to SSID plus expected OUI and RSN suites. Focus on unknown BSSIDs that are significantly stronger than nearby authorized APs in the same location. Limit monitoring near building edges and prioritize interior areas where clients operate.
Save filtered lists with SSID, BSSID, channel, RSSI, timestamps, and approximate location. Store notes on walking paths and environmental factors that influenced signal strength. Use consistent filenames with site codes and dates to speed correlation and audits. The increasing number of devices that connect over-the-air to the internet over-the-air and the wide availability of WiFi access points provide many opportunities for attackers to exploit users. By tricking users to connect to rogue access points , hackers gain full control over the users' network connection, which allows them to sniff and alter traffic, redirect users to malicious sites, and launch other attacks over the network..
3. Software Implementation, Frameworks & Protocols To protect users and teach them to avoid risky online behaviors, security auditors and researchers must evaluate users' security practices and understand the reasons they connect to WiFi access points without being confident they are safe. There are a significant number of tools that can conduct WiFi audits, but no single tool can test the many different attack scenarios and none of the tools integrate well with one another.
The Evil-Twin Framework (ETF) aims to fix these problems in the WiFi auditing process by enabling auditors to examine multiple scenarios and integrate multiple tools. This article describes the framework and its functionalities, then provides some examples to show how it can be used. The ETF framework was written in Python because the development language is very easy to read and make contributions to.
In addition, many of the ETF's libraries, such as Scapy , were already developed for Python, making it easy to use them for ETF. The ETF architecture (Figure 1) is divided into different modules that interact with each other. The framework's settings are all written in a single configuration file. The user can verify and edit the settings through the user interface via the ConfigurationManager class. Other modules can only read these settings and run according to them.
The ETF supports multiple user interfaces that interact with the framework. The current default interface is an interactive console, similar to the one on Metasploit . A graphical user interface (GUI) and a command line interface (CLI) are under development for desktop/browser use, and mobile interfaces may be an option in the future. The user can edit the settings in the configuration file using the interactive console (and eventually with the GUI). The user interface can interact with every other module that exists in the framework.
The WiFi module ( AirCommunicator ) was built to support a wide range of WiFi capabilities and attacks. The framework identifies three basic pillars of Wi-Fi communication: packet sniffing , custom packet injection , and access point creation . The three main WiFi communication modules are AirScanner , AirInjector , and AirHost , which are responsible for packet sniffing, packet injection, and access point creation, respectively. The three classes are wrapped inside the main WiFi module, AirCommunicator, which reads the configuration file before starting the services. Any type of WiFi attack can be built using one or more of these core features.
To enable man-in-the-middle (MITM) attacks, which are a common way to attack WiFi clients, the framework has an integrated module called ETFITM (Evil-Twin Framework-in-the-Middle). This module is responsible for the creation of a web proxy used to intercept and manipulate HTTP/HTTPS traffic. There are many other tools that can leverage the MITM position created by the ETF. Through its extensibility, ETF can support them—and, instead of having to call them separately, you can add the tools to the framework just by extending the Spawner class. This enables a developer or security auditor to call the program with a preconfigured argument string from within the framework.
The other way to extend the framework is through plugins. There are two categories of plugins: WiFi plugins and MITM plugins . MITM plugins are scripts that can run while the MITM proxy is active. The proxy passes the HTTP(S) requests and responses through to the plugins where they can be logged or manipulated. WiFi plugins follow a more complex flow of execution but still expose a fairly simple API to contributors who wish to develop and use their own plugins. WiFi plugins can be further divided into three categories, one for each of the core WiFi communication modules.
Each of the core modules has certain events that trigger the execution of a plugin. For instance, AirScanner has three defined events to which a response can be programmed. The events usually correspond to a setup phase before the service starts running, a mid-execution phase while the service is running, and a teardown or cleanup phase after a service finishes. Since Python allows multiple inheritance, one plugin can subclass more than one plugin class.
Figure 1 above is a summary of the framework's architecture. Lines pointing away from the ConfigurationManager mean that the module reads information from it and lines pointing towards it mean that the module can write/edit configurations. There are a variety of ways ETF can conduct penetration testing on WiFi network security or work on end users' awareness of WiFi security. The following examples describe some of the framework's pen-testing functionalities, such as access point and client detection, WPA and WEP access point attacks, and evil twin access point creation.
These examples were devised using ETF with WiFi cards that allow WiFi traffic capture. They also utilize the following abbreviations for ETF setup commands: In a real testing scenario, make sure to replace these abbreviations with the correct information. This scenario (Figure 2) takes two aspects into consideration: the de-authentication attack and the possibility of catching a 4-way WPA handshake. The scenario starts with a running WPA/WPA2-enabled access point with one connected client device (in this case, a smartphone). The goal is to de-authenticate the client with a general de-authentication attack then capture the WPA handshake once it tries to reconnect. The reconnection will be done manually immediately after being de-authenticated.
The consideration in this example is the ETF's reliability. The goal is to find out if the tools can consistently capture the WPA handshake. The scenario will be performed multiple times with each tool to check its reliability when capturing the WPA handshake. There is more than one way to capture a WPA handshake using the ETF. One way is to use a combination of the AirScanner and AirInjector modules; another way is to just use the AirInjector. The following scenario uses a combination of both modules.
The ETF launches the AirScanner module and analyzes the IEEE 802.11 frames to find a WPA handshake. Then the AirInjector can launch a de-authentication attack to force a reconnection. The following steps must be done to accomplish this on the ETF: This simple set of commands enables the ETF to perform an efficient and successful de-authentication attack on every test run. The ETF can also capture the WPA handshake on every test run. The following code makes it possible to observe the ETF's successful execution.
4. Practical Deployment, Analysis & Case Studies The next scenario (Figure 3) will also focus on the Address Resolution Protocol (ARP) replay attack's efficiency and the speed of capturing the WEP data packets containing the initialization vectors (IVs). The same network may require a different number of caught IVs to be cracked, so the limit for this scenario is 50,000 IVs. If the network is cracked during the first test with less than 50,000 IVs, that number will be the new limit for the following tests on the network. The cracking tool to be used will be aircrack -ng .
The test scenario starts with an access point using WEP encryption and an offline client that knows the key—the key for testing purposes is 12345, but it can be a larger and more complex key. Once the client connects to the WEP access point, it will send out a gratuitous ARP packet; this is the packet that's meant to be captured and replayed. The test ends once the limit of packets containing IVs is captured.
ETF uses Python's Scapy library for packet sniffing and injection. To minimize known performance problems in Scapy, ETF tweaks some of its low-level libraries to significantly speed packet injection. For this specific scenario, the ETF uses tcpdump as a background process instead of Scapy for more efficient packet sniffing, while Scapy is used to identify the encrypted ARP packet.
This scenario requires the following commands and operations to be performed on the ETF: After executing these commands, ETF correctly identifies the encrypted ARP packet, then successfully performs an ARP replay attack, which cracks the network. The scenario in Figure 4 creates multiple access points with the same SSID. This technique discovers the encryption type of a network that was probed for but out of reach. By launching multiple access points with all security settings, the client will automatically connect to the one that matches the security settings of the locally cached access point information.
Using the ETF, it is possible to configure the hostapd configuration file then launch the program in the background. Hostapd supports launching multiple access points on the same wireless card by configuring virtual interfaces, and since it supports all types of security configurations, a complete catch-all honeypot can be set up. For the WEP and WPA(2)-PSK networks, a default password is used, and for the WPA(2)-EAP, an " accept all " policy is configured.
For this scenario, the following commands and operations must be performed on the ETF: With these commands, the ETF can launch a complete catch-all honeypot with all types of security configurations. ETF also automatically launches the DHCP and DNS servers that allow clients to stay connected to the internet. ETF offers a better, faster, and more complete solution to create catch-all honeypots. The following code enables the successful execution of the ETF to be observed.
These scenarios use common and well-known attacks to help validate the ETF's capabilities for testing WiFi networks and clients. The results also validate that the framework's architecture enables new attack vectors and features to be developed on top of it while taking advantage of the platform's existing capabilities. This should accelerate development of new WiFi penetration-testing tools, since a lot of the code is already written. Furthermore, the fact that complementary WiFi technologies are all integrated in a single tool will make WiFi pen-testing simpler and more efficient.
The ETF's goal is not to replace existing tools but to complement them and offer a broader choice to security auditors when conducting WiFi pen-testing and improving user awareness. The ETF is an open source project available on GitHub and community contributions to its development are welcomed. Following are some of the ways you can help.
One of the limitations of current WiFi pen-testing is the inability to log important events during tests. This makes reporting identified vulnerabilities both more difficult and less accurate. The framework could implement a logger that can be accessed by every class to create a pen-testing session report. The ETF tool's capabilities cover many aspects of WiFi pen-testing. On one hand, it facilitates the phases of WiFi reconnaissance, vulnerability discovery, and attack. On the other hand, it doesn't offer a feature that facilitates the reporting phase. Adding the concept of a session and a session reporting feature, such as the logging of important events during a session, would greatly increase the value of the tool for real pen-testing scenarios.
Another valuable contribution would be extending the framework to facilitate WiFi fuzzing. The IEEE 802.11 protocol is very complex, and considering there are multiple implementations of it, both on the client and access point side, it's safe to assume these implementations contain bugs and even security flaws. These bugs could be discovered by fuzzing IEEE 802.11 protocol frames. Since Scapy allows custom packet creation and injection, a fuzzer can be implemented through it.
An evil twin attack does not require expensive hardware or advanced cryptography. A $30 USB adapter, a Raspberry Pi running hostapd-wpe, and five minutes in a parking garage is enough to intercept credentials from employees who connect automatically. Here is how these attacks work in 2026, what they leave behind in pcap, and how to build detection that actually catches them.
The core mechanic has not changed since 2004: broadcast a SSID that matches a legitimate network, convince a client device to associate, intercept or relay traffic. What has changed is the tooling, the scale of automation, and the way attackers handle WPA3 environments. The most common variant in enterprise environments today does not attempt to crack WPA2 at all. Instead, the attacker broadcasts an open or WPA2-Personal twin of the corporate guest SSID, intercepts the association, and serves a convincing captive portal - frequently a pixel-perfect clone of the organization's SSO login page. Employees on mobile devices, conditioned to enter credentials on captive portals, comply. Tools like Wifiphisher and airgeddon automate the entire flow: deauth the client from the real AP, serve the fake portal, harvest credentials, and exfiltrate over LTE. The attacker is gone before anyone notices.
KARMA exploits the 802.11 probe request mechanism. When a client has previously joined a network, it periodically broadcasts that SSID in probe requests. A KARMA responder - implemented in hostapd-wpe , the WiFi Pineapple Mark VII , and the Hak5 Signal Owl - answers every probe request, claiming to be whatever network the client is looking for. In a conference room or hotel lobby, a single KARMA device can harvest association attempts from dozens of client devices simultaneously. In enterprise environments, the threat is highest in common areas where employees use personal devices that carry home and coffee-shop SSIDs in their preferred network lists.
5. Performance Evaluation & Extended Technical Observations WPA3-SAE (Dragonfly) eliminates the offline-crackable four-way handshake. Attackers have adapted: they broadcast a WPA2-only twin of the same SSID. If the AP is running WPA3 Transition Mode (mixed WPA2/WPA3) and the client's supplicant does not enforce WPA3, the client may associate with the WPA2 twin. The attacker captures a standard PMKID or EAPOL handshake and attacks it offline. The countermeasure - Transition Disable , specified in IEEE 802.11-2020 - instructs clients to stop connecting to WPA2 variants of the same SSID after successfully authenticating via WPA3 once. However, as of early 2026, fewer than 40% of enterprise APs have Transition Disable enabled in their default profiles.
WPA3 Transition Mode is not WPA3 security. If your APs advertise both WPA2 and WPA3 on the same SSID and you have not enabled Transition Disable, your clients can be downgraded by any attacker with a $30 USB adapter. Audit this before assuming WPA3 deployment equals WPA3 protection. You do not need a dedicated WIDS sensor to find evil twin indicators. A 15-minute passive capture with a monitor-mode adapter gives you enough data to identify several high-confidence signals. Here is what to look for.
A legitimate AP has one BSSID per radio. If your capture shows the same BSSID appearing on channel 6 and channel 11 simultaneously - or the same BSSID advertising different capabilities in successive beacon frames - that is a near-certain evil twin. Legitimate channel changes involve disassociation and reassociation, not simultaneous multi-channel presence. 802.11 beacons are transmitted at a fixed interval, typically 100 TUs (102.4 ms). A legitimate AP's beacon interval is consistent. An evil twin running on a laptop or Pi under load will show jitter - inter-beacon intervals varying by more than 5-10 ms - because the host OS is not a real-time system. Look for standard deviation in beacon intervals greater than 8 ms as a soft indicator, especially combined with other signals.
If a BSSID your sensors have been tracking at a stable -65 dBm suddenly appears at -45 dBm from the same sensor, something physically moved closer or a second transmitter appeared. Cross-reference against the AP's known MAC OUI: a Cisco or Aruba OUI at -65 dBm and a Realtek or Ralink OUI at -45 dBm claiming the same BSSID is a clear compromise signal.
A KARMA device responds to directed probe requests for any SSID. In pcap this appears as a single BSSID sending probe responses advertising dozens of different SSIDs within a short window - no legitimate AP does this. Filter on wlan.fc.type_subtype == 0x05 (probe response) grouped by BSSID and count distinct SSIDs per BSSID per minute. More than three is suspicious; more than ten is definitive.
Purpose-built Wireless Intrusion Detection Systems give you continuous monitoring rather than point-in-time captures. Here is how the main options compare for enterprise deployments. Kismet is the strongest open-source option for teams who cannot justify a $30k WIDS budget. A Raspberry Pi 4 with an Alfa AWUS036AXML adapter makes a capable passive sensor. Kismet logs to JSON and SQLite, which you can query directly or feed into a SIEM. Its default alert set covers BSSIDSPOOFED , CHANNELCHANGE , APSPOOF , and PROBENOJOIN - all relevant to evil twin detection. The operational cost is sensor management and alert tuning; in a noisy RF environment expect to spend time filtering false positives from co-channel neighbors.
Both platforms use your existing AP infrastructure as distributed sensors. Aruba AirWave's Rogue AP Detection classifies every detected BSSID as Authorized, Rogue, or Interfering based on OUI whitelists, wired-side MAC correlation, and RF fingerprinting. Cisco Catalyst Center's Rogue Management adds automatic containment - sending deauth frames to clients of confirmed rogues - which is aggressive but effective in controlled environments. Both platforms cost significantly more than open-source alternatives but integrate directly into existing change-management workflows and generate audit-ready reports.
Containment requires careful scoping. Aruba and Cisco's automatic deauth-based rogue containment is effective but can interfere with neighboring networks operating on the same channel. Verify your legal authorization covers containment actions before enabling it, particularly in multi-tenant buildings. When you upload a pcap from a site survey or continuous sensor to the wifiaudit.io API, the analysis engine runs a dedicated rogue AP detection module in addition to the standard credential-security checks. Specifically, the report surfaces: Each finding maps to a remediation recommendation and a severity score. The PDF output is structured to satisfy NIS2 Article 21(2)(i) requirements for network security monitoring documentation and maps to ISO 27001:2022 Annex A 8.20 (network security).
Detection is necessary but not sufficient. These controls reduce the attack surface before an evil twin can operate effectively: A rogue AP is any unauthorized access point connected to or broadcasting near your network - could be an employee's mobile hotspot or a forgotten device in a conference room. An evil twin is a deliberate attack: an adversary broadcasts the same SSID and a cloned or spoofed BSSID as a legitimate AP to lure clients into associating with attacker-controlled hardware and interposing on their traffic.
WPA3-only networks are significantly harder to evil-twin because SAE (Dragonfly) does not expose an offline-crackable handshake. However, attackers in 2026 commonly use downgrade attacks: they broadcast a WPA2-only evil twin of the same SSID. Legacy clients or misconfigured supplicants may associate with the weaker network. The fix is to enforce WPA3-only in client profiles and enable Transition Disable on APs that support it.
Kismet detects SSID/BSSID conflicts and logs beacon anomalies by default. It will alert on a BSSID seen on two channels simultaneously and on new APs advertising a known SSID from an unexpected OUI. However, Kismet requires dedicated sensor hardware and tuning to reduce false positives in dense RF environments. For point-in-time audits, uploading a pcap to the wifiaudit.io API gives you a structured, reportable result without maintaining persistent sensor infrastructure.
A classic evil twin targets a specific known SSID. KARMA-style attacks exploit the 802.11 probe request mechanism: clients broadcast the SSIDs of networks they have previously joined. A KARMA responder answers every probe request, claiming to be whatever network the client is looking for. Tools like hostapd-wpe and the built-in KARMA mode in WiFi Pineapple automate this. Detection focuses on an AP responding to probe requests for many different SSIDs simultaneously - a strong anomaly signal clearly visible in pcap.
Upload a pcap from your next site survey and get a structured rogue AP and evil twin detection report in minutes. No WIDS infrastructure required. Harvested Online Documentation & Reference Sources • https://github.com/kirula0626/Evil-Twin-Detection-using-Machine-Learning • https://pulsegeek.com/articles/detect-and-prevent-evil-twin-wi-fi-step-by-step/ • https://opensource.com/article/19/1/evil-twin-framework • https://wifiaudit.io/blog/evil-twin-detection • https://github.com/31-santhosh/evil-twin-detector-windows
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Wifi Evil Twin Attack Detection Tool In Python.
[*] Metasploit Scan Running on Target Subnet for Wifi Evil Twin Attack Detection Tool In Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |