Complete Technical Paper Content — Wireless Intrusion Detection System Using Raspberry Pi
Overview & System Context
Wireless Intrusion Detection System Using Raspberry Pi: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5317 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A real-time CLI + web Wi-Fi and LAN threat monitor for Raspberry Pi. Displays a live dashboard (uses TMUX) showing all activity: deauth attacks, probe floods, nearby access points, connected devices, management frame activity, and active LAN threat detection (ARP scanning, ARP poisoning/MITM, port scanning, DHCP starvation).
A Wi-Fi adapter in monitor mode cannot simultaneously be associated with an access point. It just listens to raw 802.11 frames. If you put your only adapter into monitor mode, you lose your network connection and can no longer scan for IPs, run arp-scan, or get security metadata from NetworkManager. You need one adapter locked to your home network (wlan0) and a second one free to sniff the air (wlan1).
Not all Wi-Fi adapters support monitor mode. Many cheap adapters advertise it but the Linux driver does not implement it. The following chipsets are well-tested on Raspberry Pi OS: You should see monitor in the list. If it is not there, the driver does not support it and the dongle will not work for WIDS. Figure 1: GitHub - flatmarstheory/Wi-Fi-Intrusion-Detection-System: Raspberry Pi ...
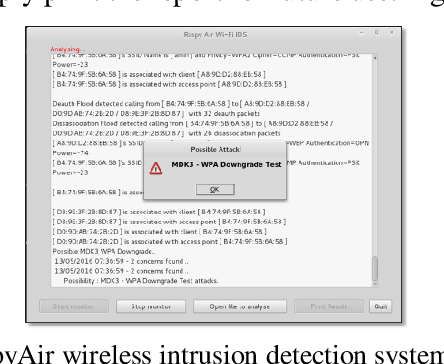
Use Raspberry Pi Imager ( https://www.raspberrypi.com/software/ ) to flash to your SD card. In Imager, before flashing, click the gear icon (I) or press Ctrl+Shift+X to open advanced options: Replace 192.168.1.X with your Pi's actual IP. Accept the host key fingerprint when prompted. Now you can SSH without a password. You should then disable password authentication on the Pi for security: Figure 2: Figure 1 from RaspyAir: Personal Wireless Intrusion Detection ...
During tshark installation you will be asked whether non-root users should be able to capture packets. Select Yes (but WIDS runs as root anyway). The --break-system-packages flag is required on Raspberry Pi OS Bookworm (Debian 12) and later, which use externally managed Python environments.
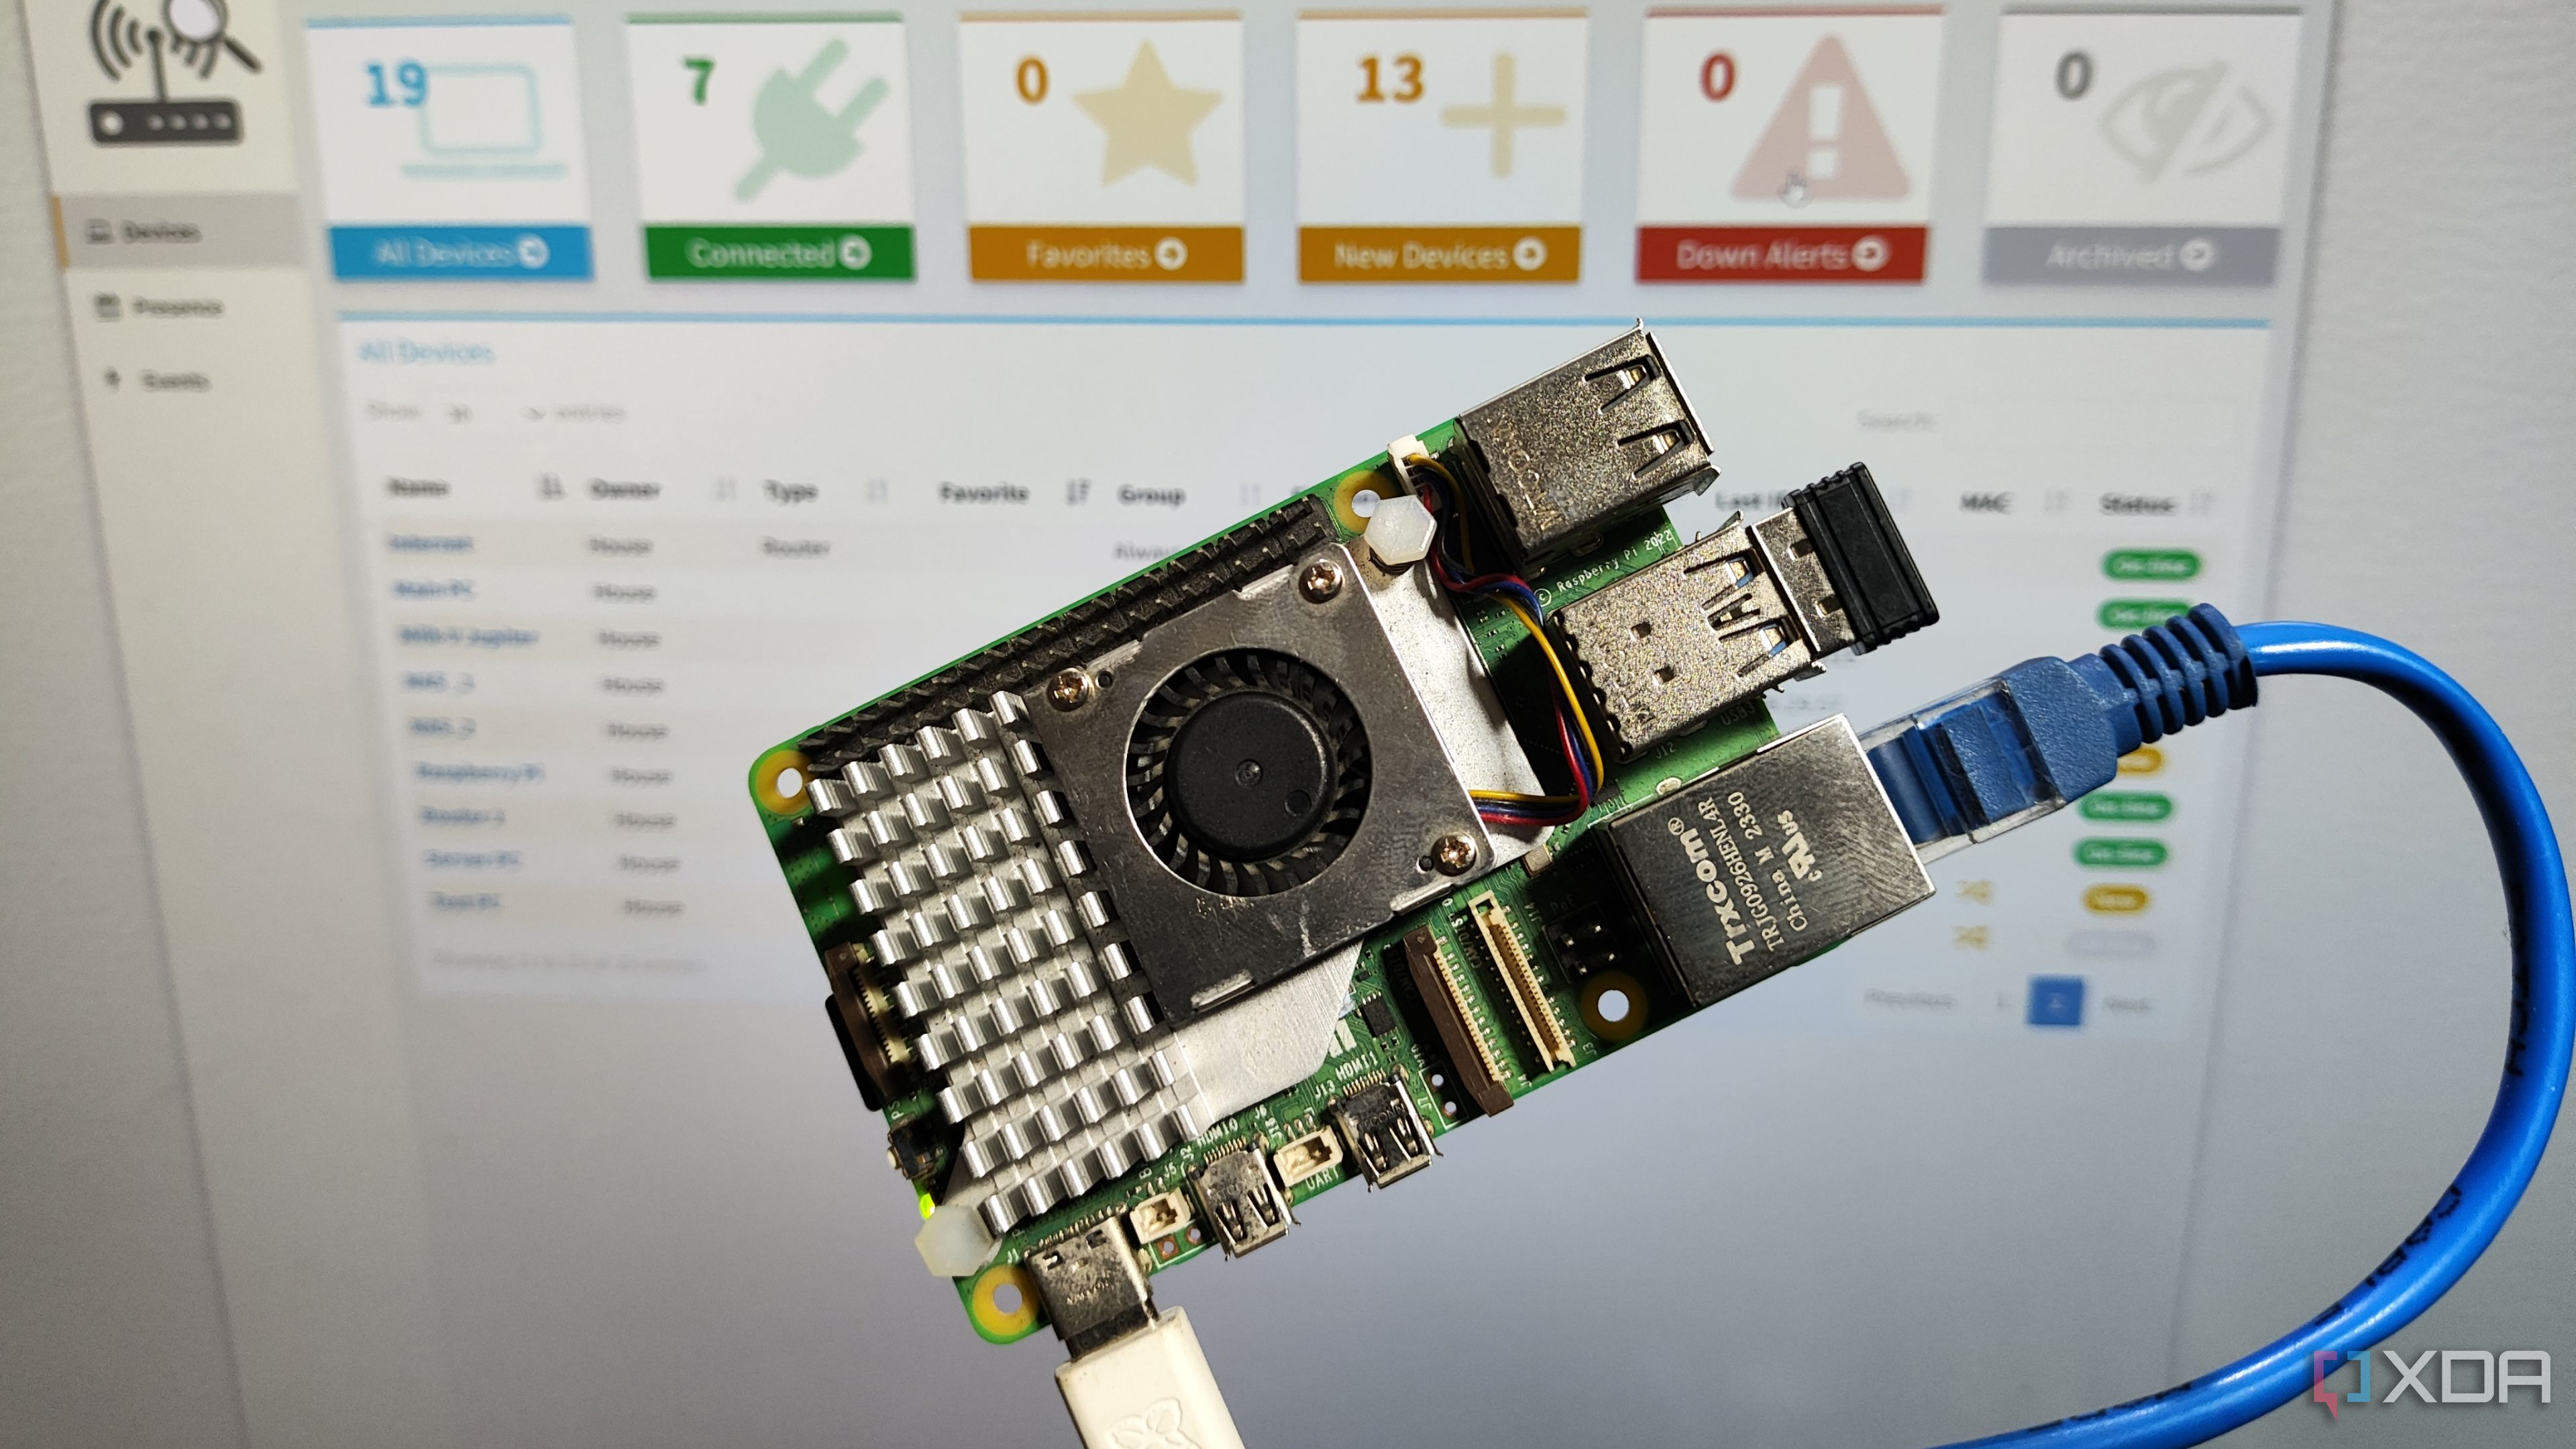
Do not put your Wi-Fi password in wids.py directly. Instead, create a local config file that is excluded from git: wlan0 is typically the built-in RPi Wi-Fi. wlan1 is the USB dongle. Confirm which is which: Figure 3: Turn your Raspberry Pi into an intrusion detection system with Pi.Alert This shows each interface with its PHY (physical radio), MAC address, and current mode.
If your interfaces are named differently (e.g. wlx00c0ca... ), update monitor_iface and scan_iface in the config accordingly. Running WIDS as a service means it starts automatically on boot and restarts if it crashes. WIDS runs inside a tmux session so you can attach and detach from the dashboard. Create the service wrapper: WIDS runs inside a tmux session. tmux is a terminal multiplexer — it keeps the dashboard running in the background even when you disconnect your SSH session.
APs are sorted strongest signal first. APs on the same channel as your home AP get live RSSI from beacons. APs on other channels get estimated RSSI from nmcli (updated every 60 seconds). Devices actively on your LAN right now, discovered via arp-scan . Shows IP address, MAC, and vendor. Refreshes every dashboard cycle (~1 second) but arp-scan itself takes a few seconds so there is slight lag.
Log rotation is not built in. To prevent disk fill on long-running deployments, set up logrotate: Look for the dongle's USB vendor/product ID in lsusb and any kernel messages about loading firmware. If the dongle is listed but monitor mode fails, the driver may not support it — see Recommended Wi-Fi Dongles . The nmcli scan thread has not run yet (it waits 5 seconds on startup) or wlan0 is not connected. Check: If nmcli dev wifi list returns nothing, wlan0 is not scanning. Ensure NetworkManager is managing it: Expected behaviour for APs on channels other than your home AP's channel. wlan1 in monitor mode is locked to a single channel — it only receives beacons from APs on that channel. APs on other channels get estimated signal from nmcli (shown after the first 60-second scan cycle). This is a hardware limitation, not a bug.
A critical capture process (management frame reader or EAPOL reader) has exited. Check the logs: Common cause: wlan1 was disconnected, NetworkManager grabbed it back out of monitor mode, or another process bound to the interface. The reader will auto-restart every 5 seconds. WIDS ignores ARP traffic originating from the Pi itself, but if your home IP changed (e.g. after DHCP renewal) the cached own_ips set will be stale. Restart the service: If wlan0 shows type monitor , something has flipped it into monitor mode (unlikely but possible). WIDS will detect this and skip the LAN monitor with a LAN_SKIP alert until it is resolved.
On a RPi 3B+ with a busy network, CPU can reach 30–40% during peak probe activity. This is normal. If it consistently exceeds 80%, reduce the dashboard refresh rate in CFG: The service may still be starting. Wait 15–20 seconds after boot then try wids-attach again. If it consistently fails, check: A lightweight, passive, edge-based Intrusion Detection System (IDS) designed for WiFi-connected IoT networks using Raspberry Pi 5 and Suricata.
The system passively monitors WiFi traffic, detects common network reconnaissance activities using signature-based detection rules, records security events in structured JSON format, and processes relevant alerts through a Python-based alerting service. The increasing use of IoT devices has expanded the attack surface of wireless networks. Many small IoT environments do not use dedicated intrusion detection infrastructure because traditional enterprise security solutions can introduce additional cost, complexity, and hardware requirements.
2. System Architecture & Core Working Principles This project explores a lightweight security monitoring approach that operates directly at the network edge. The proposed system uses a Raspberry Pi 5 running Ubuntu 24.04 LTS together with Suricata as the intrusion detection engine. Network traffic is monitored passively through the WiFi interface, while Suricata analyzes packets using signature-based detection rules.
Detected security events are recorded in structured JSON logs and processed by a Python-based alerting service. High-severity events can generate summarized email notifications for the network administrator. WiFi-Based Intrusion Detection System for IoT Networks using Raspberry Pi and Suricata Raspberry Pi Wi-Fi intrusion detection stack with Scapy capture, FastAPI automation, and a Svelte operations console.
PiGuard is a wireless intrusion detection system that runs on Raspberry Pi. It monitors Wi-Fi traffic for deauth attacks, SSID spoofing, and rogue access points. The system includes a Scapy-based packet capture engine, FastAPI control plane, and a Svelte dashboard. The project required combining 802.11 packet capture with resource-constrained embedded systems. I learned how to optimize SQLite for high-throughput writes on limited hardware and how to design REST APIs that support both UI interactions and automation scripts.
This project is a Raspberry Pi-based Intrusion Detection System (IDS) that utilizes a Long Short-Term Memory (LSTM) neural network to detect network intrusions. The IDS is trained on the CSE-CIC-IDS 2018 dataset and is capable of identifying malicious activities in a network. Intrusion detection is a critical aspect of cybersecurity, and this project provides a lightweight yet efficient IDS that can be deployed on a Raspberry Pi. By leveraging LSTM-based neural networks, this system detects anomalous patterns in network traffic and classifies them as malicious or benign.
Activate the Pre-configured Virtual Environment The project comes with a pre-configured Python virtual environment. Activate it using the following command: Prepare the Raspberry Pi Ensure the Raspberry Pi is connected to your network. The app.py script and model.keras file must be present on the Raspberry Pi.
Use the simulate.py script to generate synthetic network traffic. Ensure the Raspberry Pi is running the IDS ( app.py ) and connected to the same network. Simulating Network Traffic on Local Device {and make sure to edit the ip address of the rasberry pi in the script!} The Raspberry Pi serves as the deployment platform for the Intrusion Detection System. Its role includes: Processing Network Traffic: The Raspberry Pi monitors and processes incoming network traffic for intrusion detection.
Lightweight Deployment: The Raspberry Pi’s low power consumption and compact size make it ideal for continuous IDS deployment in small networks. Running the IDS Model: The app.py script runs the pre-trained LSTM model ( model.keras ) on the Raspberry Pi to classify traffic as benign or malicious.
Real-Time Detection: By deploying the IDS on the Raspberry Pi, network traffic is analyzed in real-time for immediate detection of malicious activities. To test and evaluate the IDS, the simulate.py script is used to simulate network traffic from a local device. This ensures that: Traffic Diversity: Simulated traffic includes both benign and malicious samples to test the accuracy of the IDS.
Evaluation of the Model: It allows thorough evaluation of the IDS performance without requiring actual malicious activities. Seamless Testing: By simulating network traffic from a local device, developers can test the IDS remotely without affecting live networks. This project uses the CSE-CIC-IDS 2018 dataset, which is widely used for intrusion detection system training and evaluation.
It contains a diverse set of network traffic samples labeled as benign or malicious. For more information on the dataset, visit CSE-CIC-IDS 2018 Dataset . Contributions are welcome! If you'd like to contribute, please fork the repository, make your changes, and submit a pull request.
Raspberry Pi-based Intrusion Detection System is a lightweight and efficient security solution leveraging machine learning and network traffic analysis to detect potential intrusions on a Raspberry Pi network. This system utilizes advanced algorithms, including LSTM neural networks, to provide real-time threat detection and enhance network security This is a project that has been well documented all over the internet. Lots of people enjoy building their own Intrusion Detection/Prevention System for their home network and many choose to use a Raspberry Pi. The idea occurred to me as a colleague and I were discussing his home-built router using OpnSense. Fortunately, great minds think alike, and I was able to find a LOT of stories and examples online of how to build a NIDS.
My main inspiration came from this Reddit post . While the versions are slightly dated the premise is the same. I’ll provide a step by step here of what I did not only to help you, but also so I don’t forget the next time I need to troubleshoot this, or build another. I went with Raspberry Pi Lite 64-bit. Unless you plan on dual purposing this device you don’t “need” a GUI. Command line is good enough considering it’s going to sit there and monitor/report on traffic.
You can use the Raspberry Pi Imager tool to quickly and accurately format and install a new SD card with the OS of your choice. Network : For the purposes of installing and configuring the myriad of modules and packages you will be downloading, you’ll need to decide if you want to use Wi-Fi or a wired network. If you choose Wi-Fi, you’ll need to do the following first: For me, the radio was disabled. So when I ran raspi-config and nothing was there, I had to go back and actually turn it on.
Then run raspi-config to connect to your Wi-Fi network. Sudo : I acknowledge there are ways to add a user to the sudoers group, etc. You configure your device’s security in whichever way works best for you. Since this device is physically plugged into my network in my home in a secured location, I’m ok with running the following command for all of the remaining commands below This effectively elevates you to root for this session, eliminating the need to type sudo before every command. This is not recommended for regular use in Linux. It is ultimately your choice. It’s not hard to perma-elevate yourself then accidentally wipe the disk you’re working on, for example. Use caution and pay attention! 3. Software Implementation, Frameworks & Protocols If there are any other customizations you want to make do those first. For example, if you’re using a screen and you don’t want it to auto-blank (that’s a default now), make sure you turn that off in raspi-config. Also if you want to auto-login on startup/restart, don’t forget to set that in raspi-config as well.
I chose Suricata as my IDS platform, because Snort didn’t have a package that would work on ARM processors. They’re all good in my opinion, and Snort was my first thought. But so far Suricata is just as good and highly customizable. This will download Suricata. At the time of this post 8.0 was the latest version. Please make sure you’re getting the latest version in the future.
Extract the compressed download and switch directories so you’re in the folder you just extracted Assuming there are no errors (and believe me there were PLENTY along the way for me) you now have Suricata installed! Here are some of the pitfalls I encountered: Wrong version of Rust . This required me to uninstall Rust, install Rustup and let it install the latest version (at the time of this post, it was 1.88) Permission issues . Many guides will tell you to create a user, add the user to a group, then give the group access to the Suricata folder. There’s a lot more than that, and when I tried to do this I ended up needing to wipe the SD card and start over – twice. Most likely my inexperience with Linux, but exercise caution anyway.
Suricata uses a rules file to compare traffic against and determine if there’s a threat. This file should have updated on its own when you ran the installer, but for good measure I ran it again Next I created a service to run Suricata for me, that way I can ensure if the device restarts it will start on its own. Start off by creating the file and opening the editor It takes around 20-30 seconds to get going, so run the status line after a short bit to give it time. If you see “running”, you’re good! If not, the errors should tell you what needs to be addressed.
Suricata’s log files can get very big very fast, depending on your traffic in and out of your home network. It’s recommended to not keep logging on the same disk as the OS I had a Sandisk 120GB SSD among the parts I’ve collected over many years, so I got an adapter that converts it to USB, so I could connect it to the Pi and mount it to the OS for log storage. 120GB should be plenty to handle long-term storage.
To get the Pi to recognize this as attached storage, first create a directory for the drive (example) You’re looking for the drive that starts with /dev and has the size you know should be there. Depending on how you formatted the drive there could be more than one volume present, so you may see something like this In this case I wanted /dev/sda2, because that’s where my main partition and volume were. Now it’s time to mount the disk to the directory you just created That’s it! However, you’ve successfully mounted it for this session. To make the drive auto-mount at every reboot, there’s a few more steps. We’re going to start with getting the UUID of the drive You’re looking for the line with your Device UUID, like so (not the PARTUUID, just the UUID) Next, edit your fstab file like so, adding the line below the command to an empty row in the file (just make sure you use your UUID and directory you made when you mounted the drive above) All three except suricata.log can fill up quick and take up a good deal of space depending on your network traffic. You can change where Suricata writes log files with the following Look for the line that says “default-log-dir” and you can point to your new external drive path. You’ll need to restart the service you created if you created one.
You can set things up so your log files are compressed regularly and only keep n number of days’ worth of log files. There’s a lot of ways to customize this, I’ll share what I chose to do. I wanted to keep 7 days’ worth of all log files and compress them after each day. To do this, start out by creating a logrotate file just for Suricata Put the following into the file and save (make sure you update your log path to whatever you set yours to above) This will effectively take the current log files, compress them, rename them by appending an incremental digit to the end of the filename, not worry if it’s in the middle of writing (not a big deal to me), run at midnight each day, only keep 7 days of log files, don’t run if the log file is empty, and after the rotation restart the service. Very simple yet thorough! For redundancy and quick visibility, I wanted to copy my log files up to my OneDrive, more of a quick cloud backup but also for doing some analysis and reporting later on. This was easily accomplished by using rclone. Installation is simple: Then just follow the instructions to set up a remote connection. Here’s the guide for OneDrive . Note if you chose the headless install of Raspberry Pi (Debian Bookworm Lite) you’ll need to install rclone on another machine in order to authenticate. It is possible to download rclone to Windows, ru nthe command-line file, authenticate and have it give you a token you then copy/paste into your RPi when you’re setting up the remote connection.
To regularly copy these files up, just add an entry to CRON like so. This will run every hour and copy the contents of the log path to my OneDrive/Documents/Network/Suricata folder. The parm “–local-no-check-updated” ensures if data is being written to the file at the time to copy anyway. Omitting this parm could cause the command to break with “access denied”. The last thing I wanted to do was somehow get notifications when a new alert was generated. I explored sending email and leveraging an email-SMS gateway, but Verizon stopped providing an email-SMS gateway for non-business customers years ago. Fortunately there are plenty of open-source SMS gateways available. So I settled on using textbee.dev . This free solution provides what amounts to a workaround SMS gateway by turning your phone into the gateway. You install an app on the phone, register it with their API, then make API calls and the app will send an SMS text on your behalf. Pretty smart! Since we covered the SMS gateway, next is the script to monitor the log file. Suricata has hundreds of rules and you can add your own if you like, too. I commented some out that were adding bloat to my logs that I wasn’t concerned about. I decided basically I wanted to know about moderate or high threats. Suricata classifies these as 1 or 2. You can get the list of classifications in /etc/suricata/classification.config. So to get the list of high threats I ran the following Each row has a comma-separated series of values, the middle has the value that gets written to fast.log. Example: Next I wrote the Python script that checks the path and calls the API. Note recently the Raspberry Pi OS releases have prevented installing/using pip and related libraries, citing “externally managed environment”, so you may need to create a virtual environment to work out of. Here’s an example: Make sure you update the path to your fast.log file, also your textbee API key and device ID. Now we need a way to run this regularly to check the log file. That’s easily accomplished with an entry in CRON (just update the path to your script file and put in your script file name).
And there you have it. A fully functional IDS on my home network that keeps 7 days of logs and notifies me by text message when a threat is detected! I’ll be doing more with this, including doing some Power BI analysis and adding on an IPS solution to drop threats and notify the intended recipient of the attempted threat. For now, I’m happy it works! Feel free to share other ideas, maybe things that worked for you, better ways of doing things, etc. I’m always open to new ideas and different perspectives.
4. Practical Deployment, Analysis & Case Studies The Raspberry Pi project is designed to enhance your network security by using the capabilities of a Raspberry Pi device. This project aims to create a cost-effective and efficient solution for monitoring incoming network traffic for potential threats. Packet Sniffing: Utilizes the sniffing capabilities of Scapy library to capture and analyze network packets.
Rule-Based Analysis: Implements Snort-like rule-based analysis to identify potential threats within the network traffic. User Notifications: Provides pop-up notifications to alert users of detected malicious packets. Logging: Logs detected events into a dedicated log file for future reference and analysis. -Enhances network security without the need for expensive hardware or software solutions. -Provides monitoring and notifications, enabling proactive threat mitigation. -Offers flexibility for customization and adaptation to specific network environments.
PiGuard is a WiIFi intrusion detection system (WIDS) designed for home networks and Raspberry Pi enthusiasts. It detects deauthentication attacks and rogue access points in real time, provides a clean web interface, and is perfect for learning about network security. Wi-Fi intrusion detection system for Raspberry Pi that detects deauth attacks and rogue access points with real-time web monitoring.
Everything is connected to wireless these days. In my case I found that I have LOTS of devices after running a simple nmap command on my home network : I have a Raspberry 4 with Ubuntu (focal) installed and decided to use the well-known Kismet to find out. And by that I mean that you should not be trying to eavesdrop or infiltrate a wireless network that is not yours . It is relatively easy to detect if a new unknown client joined your wireless network, and it is also illegal.
So do the right thing – use this tutorial to learn and not to break into someone else's network, OK? I will jump a little ahead to show you a small issue with the Raspberry 4 integrated Wireless interface. The Raspberry PI 4 onboard wireless card will not work out of the box as the firmware doesn't support monitor mode. There are works to support this . Instead, I took the easy way out and ordered an external Wi-Fi dongle from CanaKit .
The CanaKit wireless card worked out of the box, and we'll see it shortly. But first let's install and play around with Kismet. I know I will always set up my Ralink Technology, Corp. RT5370 Wireless Adapter in monitor mode, but I need to be careful as Ubuntu can swap wlan0 and wlan1 (The Broadcom adapter I want to skip is a PCI device). Now we need to find out what device was mapped to the Ralink adapter. With a little bit of help of the Ubuntu community I found than the Ralink adapter uses the rt2800usb driver 5370 Ralink Technology a wireless network and device detector, sniffer, wardriving tool, and WIDS (wireless intrusion detection) framework.
The version that comes with the Ubuntu RaspberryPI by default is from 2016, way too old . Instead, get an updated binary as explained here (I have Ubuntu focal, check with lsb_release --all ). Kismet needs elevated privileges to run. And deals with possibly hostile data. So running with minimized permissions is the safest approach.
The right way to set it up is by using a Unix group and set user id ( SUID ) binary. My user is 'josevnz' so I did this: I will enable SSL for my Kismet installation by using a self-signed certificate . I will use for that the Cloudflare CFSSL tools: Next step is to create the self-signed certificates. There is a lot of boilerplate steps here, so I will show you how you can jump through them (but please read the man pages to see what each command does): Here we put the name and IP address of the machine that will run our Kismet web application: Kismet has a really nice feature: it can use a file that overrides some defaults, without the need to edit multiple files. In this case my installation will override the SSL settings, Wifi interface, and log location. So time to update our /etc/rc.local file: Now let's log on for the first time to the web interface (In my case http://raspberripi.home:2501 ) After a little time, Kismet will populate the main Dashboard with the list of wireless networks and devices it can detect. You will be surprised not just how many neighboring devices are out there but how many you have in your own house.
In my example, the wireless devices around me look pretty normal, except one that doesn't have a name: The web interface provides all sorts of useful information, but is there an easy way to filter all the mac addresses on my networks? The developer documentation contains examples of how to extend Kismet, specifically the one related to the official Kismet REST-API in Python .
But it seems to be missing a feature to use API keys, instead of user/password. And the interaction with the end points doesn't seem to be complicated, so I will write my (less rich feature) wrapper. 5. Performance Evaluation & Extended Technical Observations You can download and install the code for a small application I wrote ( kismet_home to illustrate how to work with Kismet (also has a copy of this tutorial) like this: And then run the unit tests/ integration tests and even the third party vulnerability scanner: First I'll write a generic HTTP client I can use to query or send commands to Kismet, that is the KismetWorker class: check_session : It checks if your API KEY is valid. If not it will throw an exception.
check_system_status : Validates if the administrator (you most likely) defined an administrator for the Kismet server. If not, then all the API queries will fail. get_alert_by_hash : If you know the identifier (hash) of an alert, you can retrieve the details of that event only. get_alert_definitions : Get all the alert definitions. Kismet supports a wide range of alerts and a user will definitely be interested to find out what type of alerts they are.
I also wrote a class that requires admin privileges. I use it to define a custom alert type and to send alerts using that type to Kismet, as part of the integration tests. Right now I don't have much use of sending custom alerts to Kismet in real life, but that may change in the future, so here is the code: Getting the data is just part of the story. We need to normalize it, so it can be used by the final scripts.
Kismet contains a lot of details about the alerts, but we do not require to show the user those details (think about the nice view you get with the web application). Instead we do a few transformations using the following class with static methods: process_alerts : Changes numeric alerts for more descriptive types and also returns dictionaries for the types and severity meaning of those alerts.
pretty_timestamp : Converts the numeric timestamp into something we can use for comparisons and display If you run the integration tests with the admin role enabled, you will see than one or more (depending how many times you ran the test) alerts were added to the Web UI: As a reminder, you can see how this is used by looking at the code here . Showing a sample run of all the integration tests against my installation (this one without publishing alerts, so some tests are skipped): Details like this won't be hardcoded inside the scripts, but instead they will reside on an external configuration file: The following classes handle all the access details (using a Reader and a Writer class for each type of operation): The first time you set up your kismet_home installation, you can create the configuration files like this: Please note the use of the virtual environment here. This will allow us to keep the application's libraries self-contained.
Or showing all the alerts received so far, with anonymous MAC address (great for screenshots like this): How you can generate these tables with ease? There is a dedicated class for the text user interface (TUI): This is not a long-running application. Instead, is a snapshot of all the alerts. If you wanted, for example, to forward these alerts by email or to a framework like grafana , you are better off using Websockets and one of the methods that retrieves only the last changes.
The layout is crude, and there is plenty of room for improvement. But our little tui is displaying relevant information without too many distractions How to write a simple Bash script to set up the correct Wireless interface in monitor mode, after the RaspBerryPI reboots How to add an API KEY with read-only access to use it instead of the legacy user/ password schema for authentication and authorization How to add unit and integration tests to the code to make sure everything works and new code changes do not break existing functionality Please leave your comments on the git repository and report any bugs. But more important get Kismet, get the code of this tutorial, and start securing your home wireless infrastructure in no time.
Learn to code for free. freeCodeCamp's open source curriculum has helped more than 40,000 people get jobs as developers. Get started An IDS, or an intrusion detection system, is a popular security tool that scans a network 24/7 and alerts you the moment it detects something fishy – like unauthorized devices attempting to connect to your system. Thankfully, you don’t have to shell out thousands of dollars just to detect intruders on your network. So long as you have a Raspberry Pi, you can build your own network monitoring server with the help of Pi.Alert.
Pi.Alert is a fairly lightweight tool, so you can install it on pretty much any Raspberry Pi SBC. The same holds for the microSD card, though you’ll need to configure a couple of things on the software front. For example, you’ll need an OS pre-installed on your Raspberry Pi. I’ve put together this guide using the GUI version of Raspberry Pi OS , but you can just as easily use the CLI variant – or even an ultra-light distro such as DietPi – if you’re rocking some of the low-power boards.
Since Pi.Alert requires an SMTP server, you’ll want to configure that before attempting to install this tool. Unfortunately, configuring an SMTP server is well beyond the scope of this article, though I plan to work on a detailed guide for that in the future. While establishing an IDS may sound complicated, developer pucherot provides an installation script that simplifies the Pi.Alert setup procedure.
If you followed all the steps properly, the Pi.Alert homepage should appear, and you’ll be able to view the IPv4 address, MAC address, and other details of the systems connected to your home network. If you’ve properly configured the email setting, Pi.Alert will notify you when a known device goes offline or another system attempts to access your network. Harvested Online Documentation & Reference Sources • https://github.com/sumdher/RaspberryPi_intrusion_detection • https://github.com/SHRAVANTHIK1999/wifi-based-ids-iot-suricata • https://mardigiorgio.github.io/projects/piguard/ • https://github.com/B3TA-BLOCKER/Raspberry-Pi-based-Intrusion-Detection-System • https://eric.oszakiewski.net/code/home-nids-using-raspberry-pi-5/ • https://github.com/BotezDaniel/FinalYearProject • https://github.com/mardigiorgio/PiGuard • https://www.freecodecamp.org/news/wireless-security-using-raspberry-pi-4-kismet-and-python • https://www.xda-developers.com/turn-your-raspberry-pi-into-an-intrusion-detection-system/ • https://github.com/flatmarstheory/Wi-Fi-Intrusion-Detection-System
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Wireless Intrusion Detection System Using Raspberry Pi.
[*] Metasploit Scan Running on Target Subnet for Wireless Intrusion Detection System Using Raspberry Pi... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |