Complete Technical Paper Content — Wireless Network Vulnerability Scanner Using Scapy
Overview & System Context
Wireless Network Vulnerability Scanner Using Scapy: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8022 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Imagine you’re sitting at your desk, wondering exactly which devices are lurking on your local network. Is that new smart TV actually connected? Did someone unauthorized join your Wi-Fi? Instead of guessing, you can write a script that instantly reveals every device’s IP and MAC address—right from your terminal. With Python and the powerful Scapy library, building a network scanner is not just possible; it’s surprisingly simple, and you can get it running today.
Scapy is a Python library designed for packet manipulation. It lets you craft, send, and analyze network packets at a low level, making it ideal for tasks like network scanning, intrusion detection, and protocol analysis [1][2]. Unlike higher-level tools that abstract away the details, Scapy gives you full control—perfect for learning how networks actually work. Before writing code, you need Scapy installed. It’s not included in Python by default, so you’ll add it via pip.
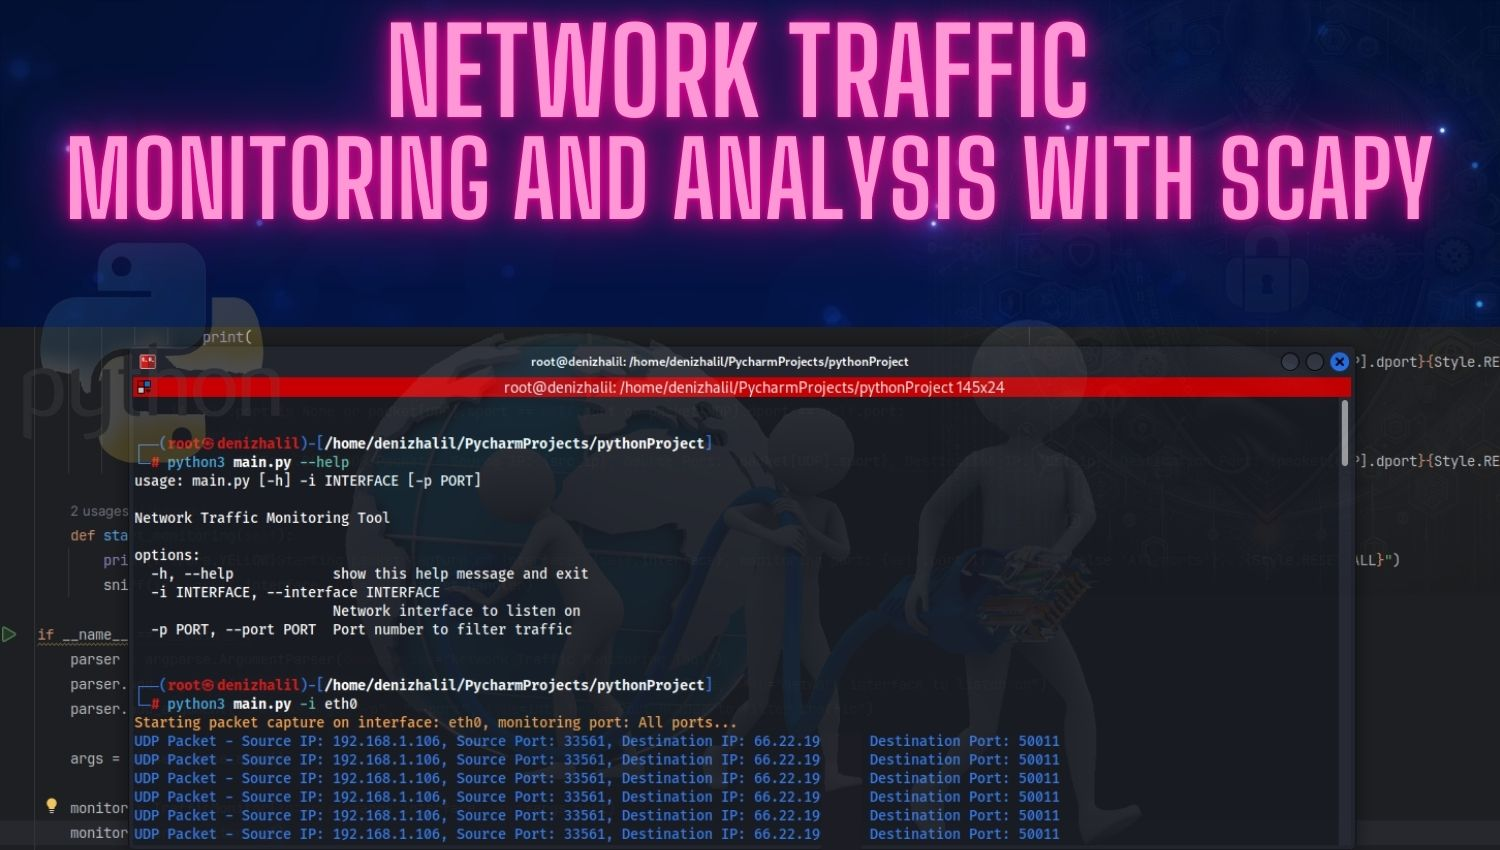
On Windows, you must also install Npcap and enable WinPcap API-compatible mode during installation [3]. Then run: Figure 1: Network Traffic Monitoring with Scapy: A Beginner's Guide - DenizHalil ... This approach ensures your scanner project doesn’t interfere with other Python packages [7]. The most effective way to discover devices on a local network is through ARP (Address Resolution Protocol) scanning . ARP is used to map IP addresses to MAC addresses. When you send an ARP request to the entire network (broadcast), every device that receives it replies with its IP and MAC—giving you a live inventory [1][2].
Let’s build a complete, working scanner. This script will scan your local network (e.g., 192.168.1.0/24 ) and list all active devices. Note: This script requires network access privileges. On Linux, run it with sudo . On Windows, ensure Npcap is installed correctly [3].
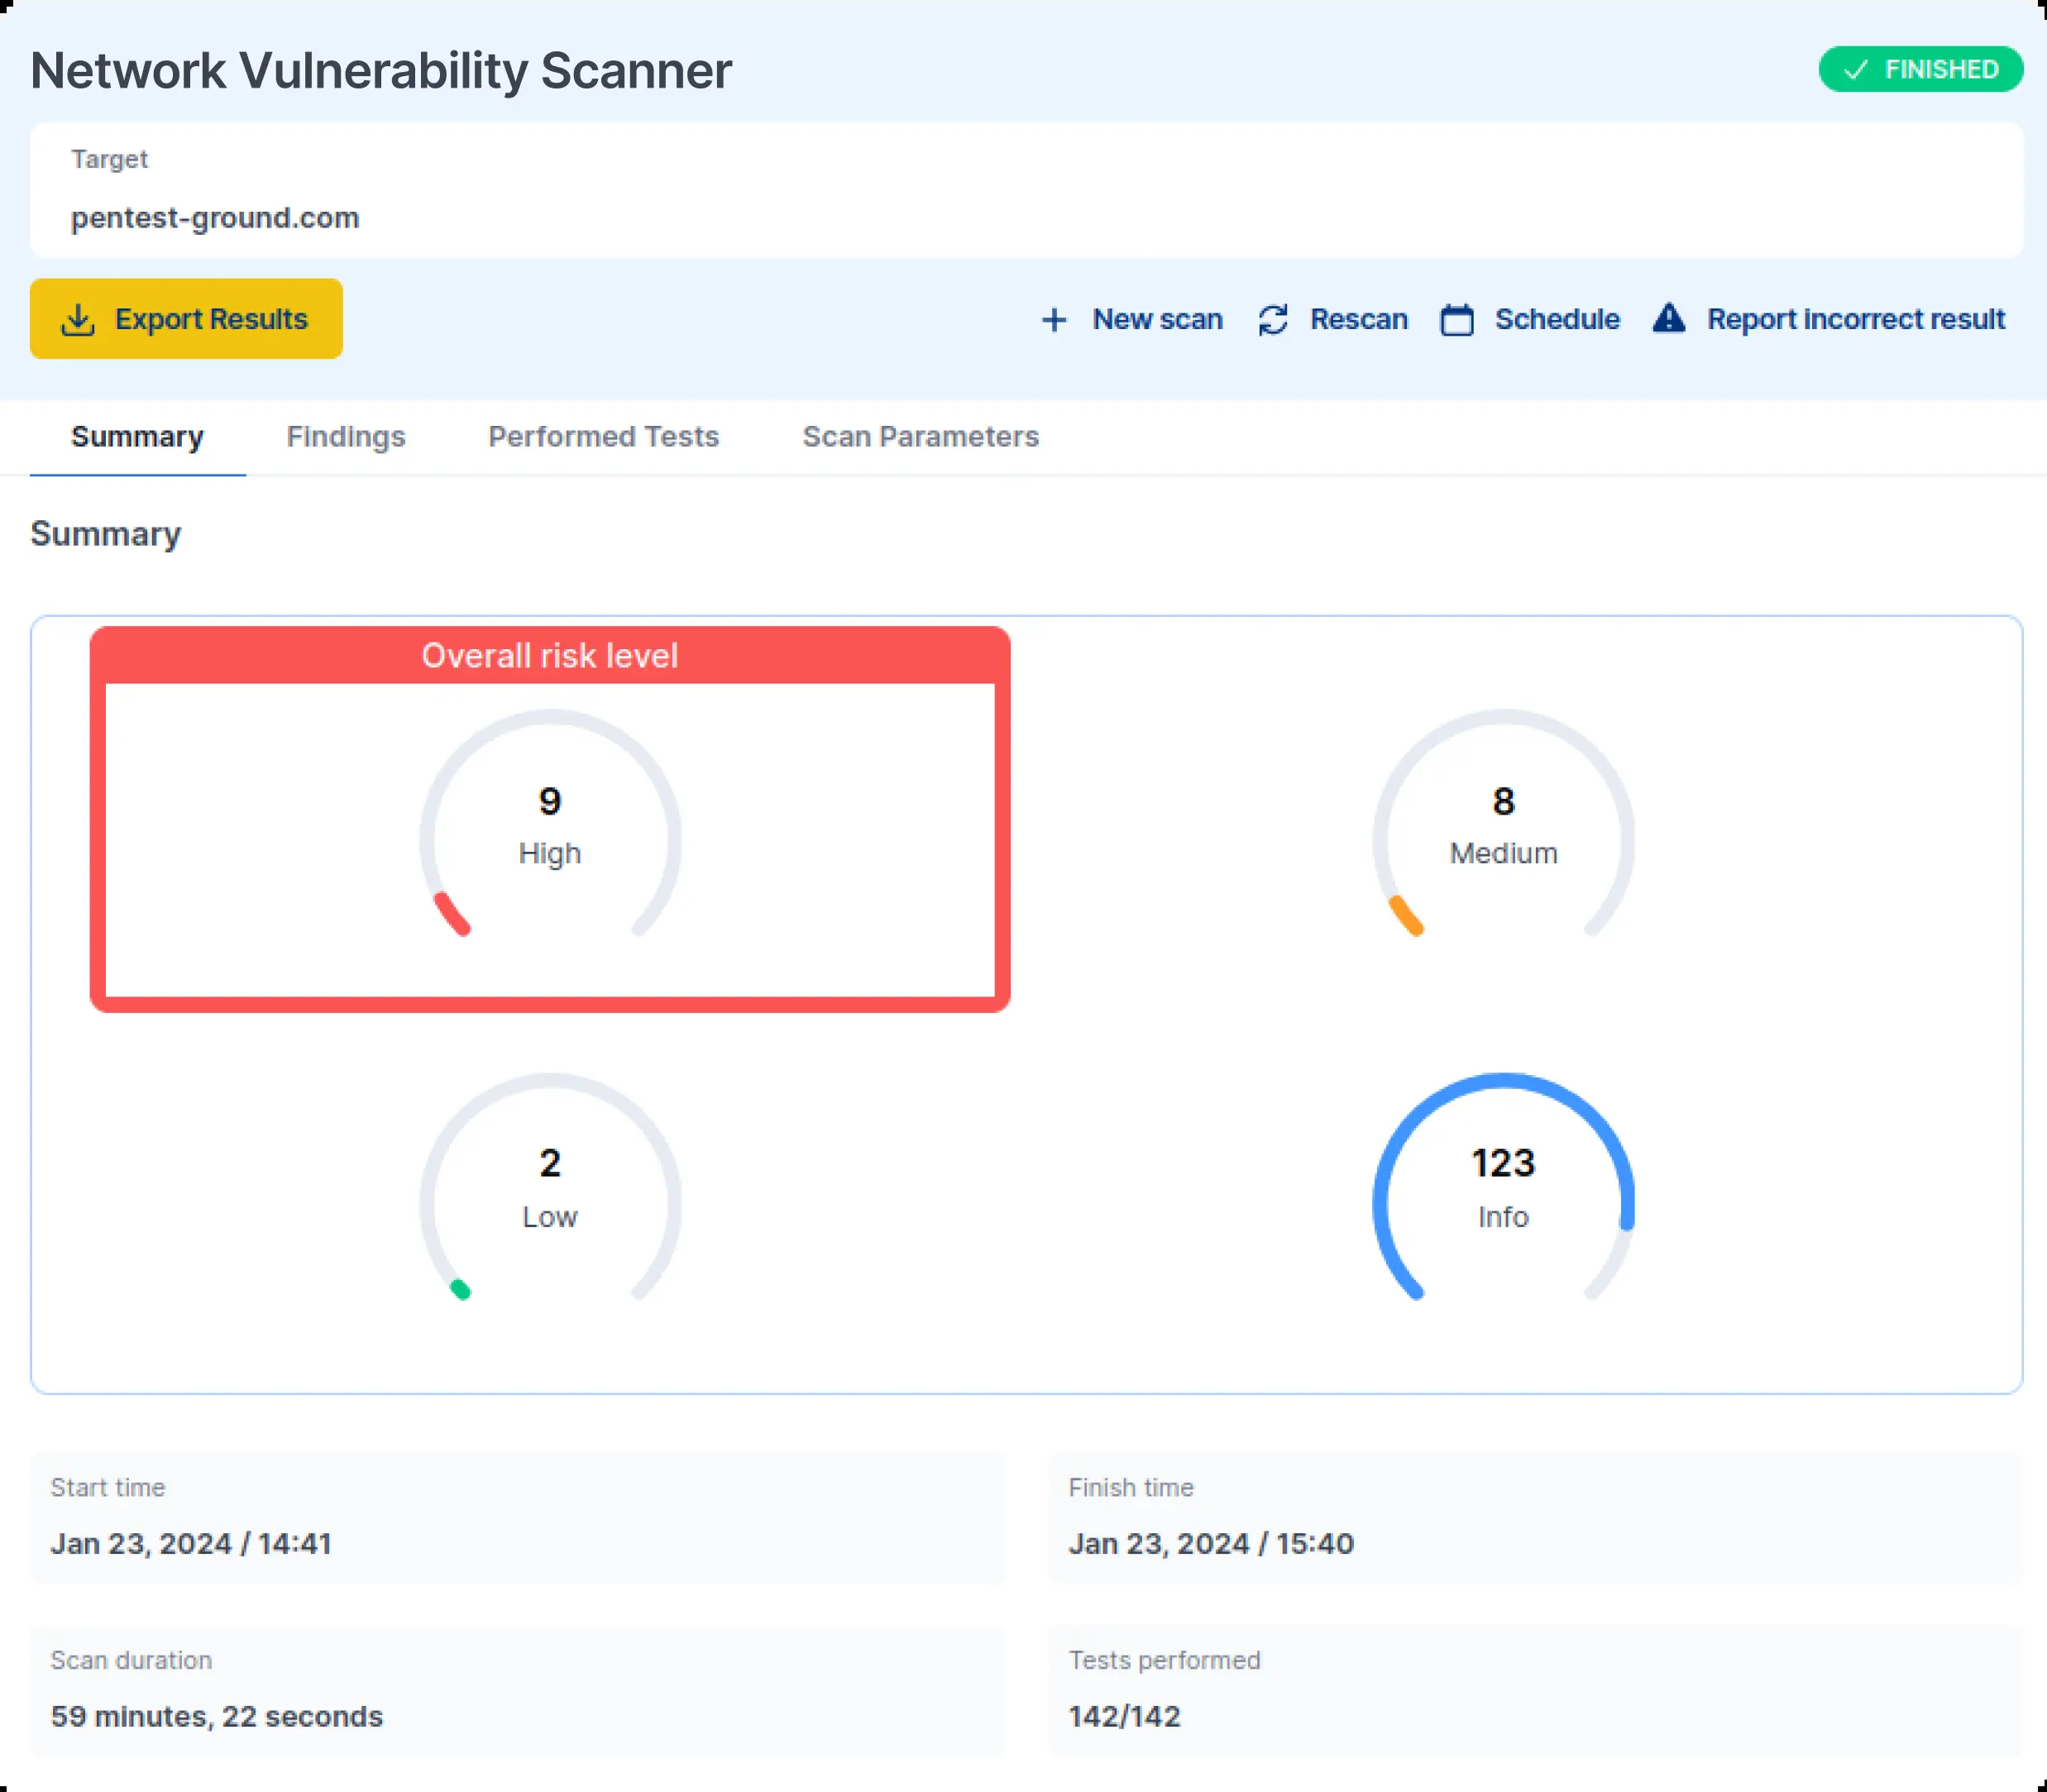
Figure 2: Online Network Vulnerability Scanner - free scans and report The example above uses a hardcoded IP range. To make it useful TODAY, adapt it to your actual network: Look for your IPv4 address and subnet (e.g., 192.168.1.100/24 ). Use the first three octets + /24 as your target. Scapy also supports TCP, UDP, and custom protocol crafting—making it a foundation for advanced network security tools [11].
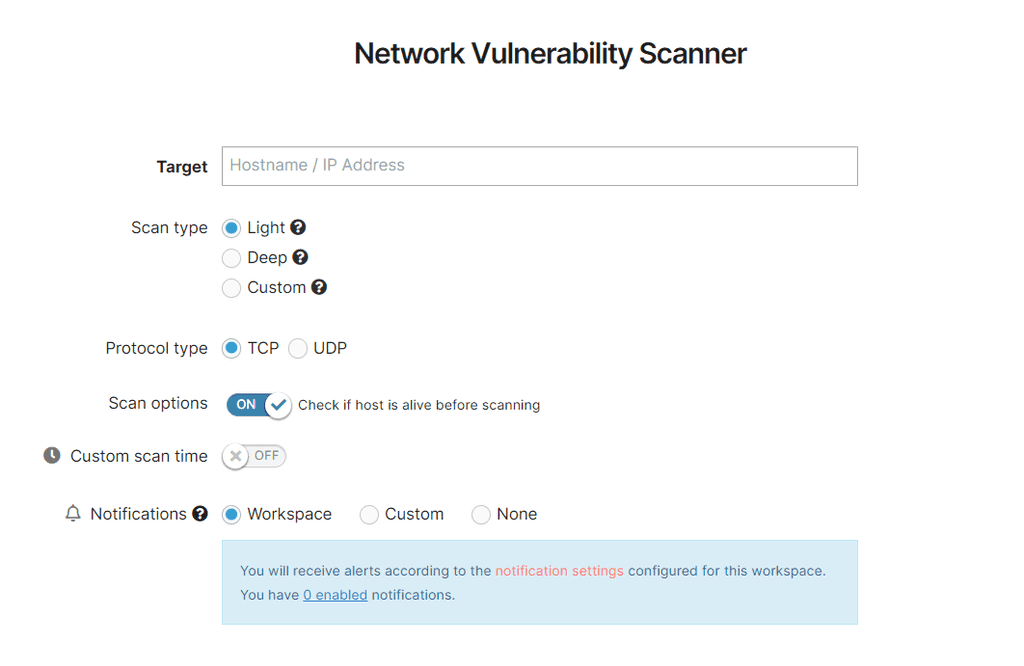
You now have a fully functional network scanner that reveals every device on your local network—no guesswork, no third-party tools. Just Python, Scapy, and a few lines of code. Figure 3: Network Vulnerability Scanner Documentation | Pentest-Tools.com Tools ... Try running it on your home network tonight. See what’s connected. Spot the unknown. And if you find something interesting (or suspicious), share your findings in the comments below.
Your call to action: Fork this script, customize it for your network, and push it to GitHub. Tag it with #python , #scapy , and #networksecurity . Let’s build a community of developers who understand their networks deeply. If you found this helpful, consider buying me a coffee I — it keeps these articles coming! Network scanning identifies active devices on a network by sending requests and analyzing their responses. Scapy can automate this process by creating and sending network packets. Scapy is a Python-based packet manipulation library that can construct, send, receive and analyze network packets. A It creates an ARP packet. The pdst field specifies the IP address or network range for which ARP requests are generated.
This method creates an Ethernet frame. The broadcast MAC address can be used to send the frame to all devices on the local network. This method is particularly useful before building the scanner because it shows the fields available for a Scapy packet. In the field of cybersecurity, capturing and analyzing network traffic is a crucial task. With Scapy, a powerful packet manipulation tool in Python, you can capture, analyze, and manipulate network packets in real-time. I created a wireless network tool called PySniffer that enables you to capture, analyze, and crack wireless network traffic.
PySniffer is a tool that I created using the Python programming language and the Scapy library. The name PySniffer is a combination of two words: “Py,” which is short for Python, and “Sniffer,” which is a term used to describe a tool that monitors network traffic. I came up with the idea for PySniffer when I first learned about the Scapy library. Scapy is a powerful packet manipulation tool that can be used for network analysis, penetration testing, and more. I realized that by using Scapy, I could create a tool that would allow me to sniff wireless network traffic and analyze it for security purposes.
Step 1: Installing Scapy The first step was to install the Scapy library. Scapy is a powerful packet manipulation tool that allows you to capture, analyze, and manipulate network packets in real-time. You can install Scapy using pip with the following command: pip install scapy Step 2: Define the handle_packet() Function The handle_packet() function is responsible for handling packets that are captured by Scapy. This function takes a packet argument, which is a Scapy packet object.
Inside the handle_packet() function, we can access various packet attributes using Scapy’s built-in packet fields. For example, we can check if the packet has a Dot11 layer (which is the layer used for Wi-Fi packets) using the packet.haslayer(Dot11) method. Step 3: Define the sniff_wireless() Function The sniff_wireless() function is responsible for sniffing wireless network traffic.
This function takes an interface argument, which is the name of the wireless interface to use for sniffing. Inside the sniff_wireless() function, we can use the sniff() function from Scapy to start sniffing wireless network traffic. We can pass in the iface argument to specify the wireless interface to use, and the prn argument to specify the callback function to be called for each packet that is captured.
Step 4: Define the crack_wep() Function The crack_wep() function is responsible for cracking WEP encryption. This function takes five arguments: interface, bssid, channel, ssid, and wep_key. Inside the crack_wep() function, we first set some Scapy configuration variables (conf.iface and conf.monitor) to prepare for packet sniffing. We then use the os.system() function to set the wireless interface to the correct channel.
Next, we create an ARP request packet using the ARP() function from Scapy. This packet is used to send a request to the access point with the specified bssid to obtain its MAC address. We then create a broadcast packet using the Ether() function from Scapy. This packet is used to send the ARP request to all devices on the network.
We use the srp() function from Scapy to send the broadcast packet and wait for a response. If we receive a response, we check if the response is an ARP response and if the source IP address is the router’s IP address. If these conditions are met, we print the WEP key and return. python pysniffer.py crack INTERFACE BSSID CHANNEL SSID WEP_KEY Replace INTERFACE, BSSID, CHANNEL, SSID, and WEP_KEY with the appropriate values for the network you want to target.
PySniffer is a powerful tool that can help you secure your wireless network by monitoring the traffic that is passing through it. Whether you are a network administrator, a security professional, or just a curious user, PySniffer can help you better understand your network and keep it secure. You can also find this tool my Github. Thanks for reading! Scapy is a powerful Python library used for network packet manipulation and analysis. In this guide, we will explore how to build network scanners using Python and Scapy to perform tasks like network discovery, packet sniffing, and vulnerability assessment.
The first step is to install Scapy. Scapy can be installed via pip and may require additional dependencies depending on your operating system. Scapy can be used to create a simple network scanner to discover active hosts in a network. This involves sending ARP requests and monitoring responses. See also Python Debugging Techniques: Master Print Debugging, Logging, and PDB Packet sniffing involves capturing network packets in real-time. Scapy provides functionalities to filter and analyze these packets. See also Django Model Relationships: ForeignKey, ManyToMany, OneToOne Explained You can also use Scapy to assess vulnerabilities, such as inspecting packets for anomalies or testing networks for susceptibility to specific attack vectors.
Scapy is a versatile tool for network analysis and security testing. With Python and Scapy, you can build custom network scanners tailored to your specific requirements, ranging from basic network discovery to complex security assessments. See also What are the max and min values of integer in Python? Gain insights into Python Scapy for network security. Delve into creating, manipulating, and analyzing network packets. Learn about port scanning, honeypots, and custom vulnerability scanners.
I am a freelance consultant and content creator with a focus on blockchain and cybersecurity. I have developed and taught many courses exploring and explaining various aspects of cybersecurity and have written hundreds of articles on the subject. These are high-quality courses. Trust me the price is worth it for the content quality. Educative came at the right time in my career. I'm understanding topics better than with any book or online video tutorial I've done. Truly made for developers.
Thanks 2. System Architecture & Core Working Principles Just finished my first full #ML course: Machine learning for Software Engineers from Educative, Inc. ... Highly recommend! You guys are the gold standard of crash-courses... Narrow enough that it doesn't need years of study or a full blown book to get the gist, but broad enough that an afternoon of Googling doesn't cut it.
I spend my days and nights on Educative. It is indispensable. It is such a unique and reader-friendly site Your courses are simply awesome, the depth they go into and the breadth of coverage is so good that I don't have to refer to 10 different websites looking for interview topics and content. Gain insights into JWT, OAuth2, and OpenID Connect. Learn about HTTPS, encryption, and handshake techniques, and explore foundational concepts in web API security for enhanced application protection.
Learn web app vulnerabilities, penetration testing with Kali Linux, and security tools using Python, web technologies, and network management. Learn about security techniques, e.g., patching, cryptography, and phishing prevention. Explore practices to make systems resistant to defend against attacks.
Learn networking essentials for software engineers: client-server models, Python sockets, CLI tools, key protocols, and hands-on distributed processing. This Python script was developed as part of learning the fundamentals of network security. It uses the Scapy library to capture wireless network traffic and discover available Wi-Fi networks (SSIDs) in the vicinity.
The script is designed to capture and analyze Beacon Frames—which broadcast network identity—by running the network card in Monitor Mode. II How It Works Packet Capture: The script listens to the specified wireless interface. Filtering: It filters the captured packets to include only the Dot11Beacon frames (which announce network ID).
Information Extraction: It extracts the Network Name (SSID) and the BSSID (MAC Address) from each Beacon frame. Unique Listing: It lists the detected networks without duplication and prints them to the console. II Prerequisites and Requirements For this script to function correctly, a Linux-based operating system (e.g., Kali Linux) and Root (Sudo) access are required.
Network Card: A wireless network adapter that supports Monitor Mode (e.g., cards with Realtek RTL8812AU chipsets) is necessary. pip install scapy I Usage Steps (For Kali Linux) Switch Interface to Monitor Mode: (Assuming your interface name is wlan0) sudo airmon-ng start wlan0 Note: This command will give you a new interface name, such as wlan0mon. Update the iface parameter in your code with this new name.
sudo python3 wifi_scanner.py Superuser permissions are required to start packet capturing. sudo airmon-ng stop wlan0mon I Cybersecurity Focus This tool serves as a fundamental application for developing Passive Network Reconnaissance skills and understanding the basic operating principles of wireless network cards. This Python script was developed as part of learning the fundamentals of network security. It uses the Scapy library to capture wireless network traffic and discover available Wi-Fi networks (SSIDs) in the vicinity.
Building a WiFi scanner in Python can be done using the Scapy library, which is a powerful packet manipulation tool. However, before you proceed, you should be aware that scanning networks without permission may be illegal or unethical. Ensure you have the right to scan the network you're working on and that you're in compliance with all relevant laws and regulations.
Ensure Proper Permissions : You need to run your script with administrative privileges to perform network scanning because Scapy needs to send and listen to packets on the network interfaces. Remember, this script is for educational purposes and should be used responsibly and ethically. vue.js pywinauto coturn gunicorn devise seaborn gnu-findutils geoserver code-sharing web-scraping The idea for this post came about from just wanting to play around with Scapy . Not having spent any time on it before, it was high time to see what this excellent packet crafting tool was all about. There was no well-defined end goal here, only a desire to dissect some packets. In the end (about 20 hours later), what came out of it is essentially a Wi-Fi network reconnaissance tool. As such, it almost feels obligatory to have a disclaimer stating that the content provided here is for educational purposes only, if it wasn’t for the fact that the tool is harmless (besides exposing networks with weak security that is…).
What does the Wi-Fi scanner tool do? It uses the Scapy sniff module to capture wireless frames, and analyses their contents to display a list of wireless networks and their properties. It displays BSSID, SSID, RSSI, frequency on which the frame was received, as well as the cipher & AKM suites which give us the configured security level. The last parameter is the age of the beacon, the entries are aged out after 30 seconds, but this is configurable. Each entry is updated in real time, then the results are sorted by RSSI and displayed using varying colours from strongest to weakest.
A few words on the lab environment. Here we have a Debian Buster VM (Raspberry Pi Desktop) running on a Windows 10 host using VMware Workstation 15 Player. The wireless adapter is a tp-link Archer T9UH using the freely available aircrack-ng drivers. Getting a combination of hardware and software suitable for this task (i.e. wireless sniffing) can be a hassle, as can getting it running even after you find a combination that works. For a bit more on this see an earlier post titled Wireless Capture Analysis . As Python (3) comes pre-installed on Debian the only additional software is Scapy itself, easily added using pip3 install scapy .
All of the required information is available by looking into the various frame headers of the beacon frame, or layers, as they are referred to in Scapy. The link below shows a Scapy dump of all available layers from a captured beacon frame. RSSI and frequency are in the RadioTap header/layer, and give us the parameters of the frame as it was received . The RadioTap header is added by the driver of the interface performing the capture.
The BSSID can be found in the 802.11-FCS layer (or Frame Control Field in 802.11 parlance), and corresponds to the transmitting station’s MAC address. Recall that 802.11 communication uses up to four MAC addresses for each frame, depending on the type of transmission. Address 2 (a ddr2) represents the TA or Transmitter Address. For a Beacon frame this is the radio MAC address of the transmitting AP, exactly what we are looking for.
For the SSID value we have to look at the Dot11Beacon layer, or specifically, the Information Element immediately following the Dot11Beacon layer. This also doesn’t quite correspond to the way that (say) Wireshark would decode the information, the IE order is different, but it doesn’t really affect anything from a scripting point of view. Last but not least, the network security information can be found in the RSN Information Element. Scapy presents this as two layers, RSNCipherSuite and AKMSuite, and also decodes the value for each as a decimal number. The tables below show the possible values for Cipher and AKM suites, representing the configured network encryption and authentication types respectively.
To capture wireless frames the network interface needs to be in monitor mode. This can be achieved with the following commands: There are some caveats however, as there are a number of system services that can interfere with the scanning/sniffing process and should be disabled. The airmon-ng tool is very useful here and will provide a list of services that may need to be disabled.
After some testing though, it seems that the dhcpcd and wpa_supplicant services are the real culprits here (at least in this case). Particularly the dhcpcd service, as it appears to initiate periodic channel scans (!?) about once every second, which means you may miss traffic if trying to capture only a single channel. In this case we are not capturing all traffic, only beacons, so it’s not as much of a problem. However, if you do want to scan a single channel, it is best to disable the dhcpcd service, and possibly the wpa_supplicant service too.
Scanning can also be performed while cycling through all channels, allowing for a wider view of available networks. For this, instead of writing code to change channels periodically, we can just use the channel scanning ‘feature’ of dhcpcd , and simply leave the dhcpcd service enabled. Welcome to the Scapy Network Security Tools repository! This repository contains 10 powerful tools designed for network analysis, penetration testing, and security testing. Each tool leverages Python and Scapy to manipulate or inspect network traffic, helping you to better understand network behavior, identify vulnerabilities, and test security mechanisms.
Whether you're a cybersecurity professional, network administrator, or just curious about how network protocols work, these tools provide valuable insights into network traffic and vulnerabilities. I’m Deniz Halil , a cybersecurity specialist, author, and software developer with a deep passion for network security, ethical hacking, and programming. On my website, you’ll find a wealth of content including projects, articles, and tutorials focused on Python, networking, and cybersecurity.
For more Python-related projects, be sure to visit the Python Projects category on my website: Python Projects on DenizHalil.com In addition to building network tools, I’ve authored several books aimed at teaching network analysis, Python programming, and ethical hacking. If you’re interested in furthering your knowledge in these areas, check out my books: These books are designed to guide you from beginner to advanced levels, equipping you with the tools and knowledge to become proficient in network analysis and cybersecurity.
If you found these tools and resources useful, please consider supporting my work by buying me a coffee. Your support will help me continue creating open-source tools, writing more books, and sharing free educational content with the community. 3. Software Implementation, Frameworks & Protocols Important : These tools are provided for educational purposes only. They are designed to help users understand network security concepts and perform penetration testing in authorized environments. Do not use these tools on any network without explicit permission from the network owner. Unauthorized usage of these tools may be illegal and could result in severe consequences.
The author assumes no responsibility or liability for any misuse of the tools provided in this repository. Use them responsibly and always ensure you have proper authorization before conducting any network security testing. A collection of 10 network security tools using Scapy for traffic analysis, penetration testing, and network manipulation. Ideal for cybersecurity professionals and enthusiasts.
Professional WiFi packet analyzer with live 3D network topology visualization, real-time protocol analysis, and interactive dashboard. Complete Django-Scapy implementation with WebSocket streaming, ideal for cybersecurity final year project. Django 4.2 | Python 3.8+ | Scapy 2.5 | Django Channels | Django REST Framework | Three.js | WebSocket | JavaScript ES6+ | HTML5 | CSS3 | SQLite | ASGI | OrbitControls | Glassmorphism UI | BPF Filters This comprehensive WiFi packet sniffer represents a cutting-edge final year project that combines network security, real-time data visualization, and modern web technologies. Built with Django and Scapy, this professional-grade packet analyzer provides deep insights into network traffic patterns, protocol distributions, and security vulnerabilities through an intuitive 3D visualization interface.
Perfect for computer science and cybersecurity students seeking a challenging final year project, this implementation demonstrates advanced concepts in network programming, packet analysis, real-time communication, and 3D graphics rendering. The project includes complete source code, detailed documentation, and ready-to-deploy configurations. The packet capture system leverages Scapy library to intercept and analyze network traffic across multiple wireless interfaces. The implementation supports monitor mode operation, enabling comprehensive packet collection including encrypted traffic metadata. Advanced Berkeley Packet Filter integration allows precise traffic filtering based on protocols, ports, IP addresses, and custom packet characteristics.
The capture engine operates asynchronously to ensure zero packet loss during high-traffic scenarios, processing thousands of packets per second while maintaining system stability. Each captured packet undergoes immediate classification, extracting critical information such as source-destination pairs, protocol types, payload sizes, and timing information. Experience network traffic like never before with the Three.js-powered 3D visualization engine. The network topology renderer displays active nodes as glowing spheres positioned in three-dimensional space, with animated particle streams representing packet flows between communicating devices. This visual representation helps identify traffic patterns, detect anomalies, and understand network behavior at a glance.
The visualization includes dynamic camera controls allowing users to orbit, zoom, and pan through the network graph. Auto-rotation features provide continuous monitoring perspectives, while protocol-specific color coding enables instant identification of different traffic types. Smooth animations and particle effects create an engaging, informative display of network activity.
The comprehensive analytics dashboard provides real-time statistics across multiple protocol categories including TCP, UDP, ICMP, ARP, DNS, HTTP, and HTTPS. A 3D bar chart visualization dynamically updates to reflect protocol distribution, offering immediate insights into network composition and traffic patterns. Statistical analysis includes packet count tracking, bandwidth utilization calculations, protocol percentage distributions, and temporal traffic analysis. The dashboard employs glassmorphism design principles with a cybersecurity-themed interface featuring cyber green, neon blue, and alert pink color schemes that enhance readability while maintaining professional aesthetics.
Built on Django Channels, the WebSocket implementation ensures instantaneous packet data delivery from backend to frontend. As packets are captured, they are immediately serialized and transmitted through persistent WebSocket connections, enabling real-time dashboard updates without polling overhead or refresh delays. The streaming architecture supports multiple concurrent client connections, allowing team collaboration and remote monitoring capabilities. Connection status indicators provide continuous feedback on stream health, while automatic reconnection logic ensures uninterrupted operation during network fluctuations.
Implement sophisticated packet filtering using BPF syntax to isolate specific traffic types. Filter by protocol, port numbers, IP ranges, packet sizes, or combine multiple conditions for precise traffic analysis. The filtering system operates at kernel level for maximum performance, processing filter expressions before packet capture to minimize processing overhead. Historical packet search functionality allows users to query captured data using protocol types, time ranges, source-destination pairs, and custom attributes. Results are displayed with full packet details including headers, payloads, and decoded protocol information.
The Django-based backend implements a robust Model-View-Controller architecture with REST API endpoints for packet capture control, interface management, and data retrieval. Django Channels extends the framework with ASGI support, enabling WebSocket communication alongside traditional HTTP request handling. Database models efficiently store packet metadata, capture sessions, and statistical summaries using optimized SQLite schemas. The capture module implements thread-safe packet processing with queuing mechanisms to handle high-throughput scenarios without blocking the web server.
The responsive single-page application combines modern JavaScript ES6+ features with Three.js for 3D rendering. Custom modules handle WebSocket communication, real-time DOM updates, chart animations, and user interactions. CSS3 implements glassmorphism effects, gradient backgrounds, and smooth transitions that create a polished, professional interface.
Orbitron and Rajdhani fonts from Google Fonts provide a technical, futuristic aesthetic matching the cybersecurity theme. Responsive design ensures optimal viewing across desktop monitors, tablets, and mobile devices. Security professionals utilize packet sniffers to identify vulnerabilities, detect intrusions, and analyze suspicious traffic patterns. This tool enables comprehensive network monitoring for security assessments, penetration testing, and incident response scenarios.
Network administrators diagnose connectivity issues, identify bandwidth bottlenecks, and optimize traffic routing by analyzing packet flows. The visualization features help pinpoint communication failures and unusual traffic patterns affecting network performance. Cybersecurity students and researchers use packet analysis tools to understand network protocols, study attack vectors, and develop defensive strategies. This project provides hands-on experience with professional-grade network analysis techniques and tools.
Software developers creating network protocols or networked applications benefit from packet-level inspection capabilities. The tool helps verify correct protocol implementation, debug communication issues, and optimize data transmission strategies. The project runs on Windows, Linux, and macOS operating systems with Python 3.8 or higher. Administrator or root privileges are required for packet capture operations. Compatible wireless network interfaces supporting monitor mode are necessary for WiFi traffic capture.
Recommended hardware includes multi-core processor for handling high packet volumes, minimum 8GB RAM for smooth operation, and modern graphics card for optimal 3D visualization performance. The application supports both development and production deployment configurations. The modular architecture allows easy customization and feature additions. Students can extend functionality by implementing packet payload analysis, adding machine learning-based anomaly detection, integrating with threat intelligence feeds, developing custom protocol decoders, or creating additional visualization modes.
The codebase follows Django best practices and clean code principles, making it accessible for developers to understand, modify, and enhance according to specific requirements or research objectives. This WiFi packet sniffer project stands out as an exceptional final year project choice due to its combination of practical utility, technical depth, and visual appeal. The implementation demonstrates mastery of advanced programming concepts while producing a functional, professional-grade tool applicable to real-world scenarios.
The project showcases skills highly valued in the software industry including backend development, frontend engineering, network programming, real-time systems, and data visualization. The comprehensive documentation and clean codebase facilitate easy understanding and presentation during project demonstrations and vivas. With complete source code, detailed setup instructions, and professional UI design, students can focus on understanding the core concepts and customizing features rather than struggling with basic implementation details. The project is fully documented and ready for immediate deployment and demonstration. For students interested in related security projects, explore our network security vulnerability scanner or phishing website detection systems.
This project emphasizes responsible use of network monitoring tools. Students receive guidance on legal frameworks governing packet capture, ethical hacking principles, and proper authorization requirements. The project includes prominent disclaimers and educational content about lawful use cases including personal network monitoring, authorized security testing, and research applications.
Understanding these ethical dimensions is crucial for cybersecurity professionals and forms an important component of the learning experience. The project documentation explicitly covers legal boundaries and responsible disclosure practices. We'll install and configure the project on your PC via remote session (Google Meet, Zoom, or AnyDesk). Want to know exactly how the setup works? Review our detailed step-by-step process before scheduling your session.
A sophisticated web-based steganography application that uses LSB algorithm to hide confidential text messages within PNG and BMP images. Perfect for final year projects in cryptography, information security, and image processing domains. A powerful Django-based web application that scans websites for common security vulnerabilities including SQL Injection, Cross-Site Scripting (XSS), and Cross-Site Request Forgery (CSRF).
PhishGuard is an advanced AI-powered phishing email detection system built with Python, Flask, and Scikit-learn that analyzes email content in real-time to identify and flag potential phishing attempts with high accuracy. Advanced cybersecurity final year project with Django that detects keyloggers in real-time using behavioral analysis, heuristic algorithms, and process monitoring. Complete source code, documentation, and setup support included.
Professional-grade Django-based network vulnerability assessment platform with automated port scanning, CVE detection, service enumeration, and comprehensive PDF reporting system for cybersecurity final year projects. Enterprise-grade honeypot monitoring system that simulates vulnerable network services to detect zero-day attacks, malware patterns, and cyber threats in real-time with GeoIP tracking, automated threat scoring, and comprehensive security analytics.
He explained the project clearly and thoroughly. He was very supportive throughout the process and was always available to help when needed. His guidance and assistance made it easier to understand the project and complete tasks effectively. I had a very good experience with CodeAj Marketplace. The team is professional and supportive, especially Ajay Pandit sir who guides clearly throughout the project. The work was completed neatly and according to requirements. A great place for learning and project development. Highly recommended for students and developers.
4. Practical Deployment, Analysis & Case Studies Excellent explanation! Concepts are explained in a very simple and understandable way. It really helped me a lot in improving my knowledge. Great work! Codeaj was really helpful with my project, especially during the customization part. He didn't just do the work but also took the time to explain everything, from the project structure and database to the code itself. It was a huge help, especially for students trying to understand how everything fits together. I really appreciated his support and the way he made things easier to follow.
Working with CodeAj Marketplace has been such a positive experience. The projects delivered are original, carefully crafted from scratch, and tailored to meet expectations with impressive attention to detail. What really makes him stand out is his willingness to go the extra mile — not just in creating outstanding work, but also in helping others understand how everything functions. He explains things clearly, addresses questions patiently, and ensures the whole process feels like a learning journey instead of just a handover. On top of the technical expertise, his calm and approachable personality makes communication effortless. No unnecessary stress, just smooth collaboration and genuine support. I truly value the dedication he brings to his work and would highly recommend him to anyone in search of high-quality, authentic projects.
I purchased a project from him recently and I have to say it's one of the best decisions I've made. The project was absolutely beautiful, built completely from scratch with no shortcuts, and perfectly matched what I wanted. What makes him stand out is not just his ability to create anything we ask for, no matter how complex, but also the way he helps us understand every part of it. He patiently explains the process, clears doubts, and makes sure we actually learn from the project instead of just using it.
On top of his skills, his personality is amazing — he's calm, chill, and very friendly to talk to. There's no stress when working with him, only smooth communication and genuine support. I truly appreciate the effort he puts in and would highly recommend him to anyone looking for original, high-quality projects. I received my project from CodeAJ Marketplace on time, and the work was very neat and well-presented. The team maintained good communication and delivered everything as promised. I appreciate their timely completion and professional approach.
I sincerely thank Mr. Ajay Pandit for his constant support and valuable guidance throughout the project. His timely advice, encouragement, and expertise greatly contributed to the successful completion of the work. I'm truly grateful for his mentorship. I had an outstanding experience with CodeAj while developing my mobile app. Their team was incredibly cooperative, ensuring every customization I requested was implemented flawlessly. The service was top-notch, and the final product exceeded my expectations. Highly recommend CodeAj for anyone seeking professional and reliable app development services! 11/10 I would like to sincerely thank Ajay Pandit for providing me with the project. His guidance and explanation of the system's architecture, modules, and AI integration were extremely helpful in understanding the project thoroughly. Ajay's support played a key role in helping me implement the hotel booking and payment module effectively. His willingness to clarify concepts and walk me through complex logic made the learning process smooth and insightful. I truly appreciate his mentorship and the time he dedicated to ensuring I was well-prepared for both the development and presentation of this project.
I had a great experience with the project I purchased. It was well-structured and met all my expectations. The team was responsive and supportive throughout, addressing all my queries promptly. Highly recommended for anyone looking for quality projects and good service. I'm really thankful to Codeaj for helping me with my project explanation and guiding me throughout. Your support made everything much easier and clearer.
The project he made was wonderful, and the way he patiently listened, understood all my ideas and presented them so well in the project, was amazing. I would highly recommend him to everyone. I would like to sincerely thank Ajay Pandit for providing me with the project. His guidance and explanation of the system's architecture, modules, and AI integration were extremely helpful in understanding the project thoroughly.
Too good experience, I love their projects and they are available for you to help, they are incredible good. Must avail their services. I am happy customer. The team was very supportive and their explanation was very good, they are clarifying each and every doubts with lots of patience. Highly recommended for quality projects.
Thank you, CodeAj Bro, for supporting the Doctor Appointment System project. Your guidance during the project setup, installation, and report creation was very helpful and greatly appreciated. One of the best Software Developer provide the best setup environment for project, good explain skills, and good technical skills, step by step explain project through google meet and budgetly price project Available.
Thank you so much for your excellent work on our project! Your kindness and clear explanations made the entire process smooth and enjoyable. Highly recommend! Really very supportive, helpful and kind, loving nature. Available for any time for any query, highly recommend to get projects from him.
Awesome projects. They support on setting up the project after purchasing. Completely legal one. Affordable projects too. Code AJ guide team are very formal, friendly to setup project step by step and explain each question I Thank you codeAj, Best site to get your project done quickly, with fast responses and instant clarification of any project-related doubts.
They provide very good service and code also running condition and they fulfill all the queries it's very helpful. Really helpful, makes things easy to understand and very kind nature, you can look forward to get help from here. I recently purchased this project online and I am very satisfied with it. The project was well-designed, properly organized, and included all the necessary files and documentation. The source code was clean, easy to understand, and worked as expected. A special appreciation for the project explanation and setup session. The session was detailed and easy to understand, covering both the project implementation and the complete setup process. All my questions were answered clearly, which helped me understand the project much better. Thanks for giving your time.
Complete guidance including full-stack development, documentation, presentation coaching & 24/7 support until successful submission. A professional-grade, Python-powered project that captures raw network packets in real time , dissects every protocol layer (Ethernet → IP → TCP/UDP/ICMP/DNS/ARP/HTTP/TLS), maps live hosts and open ports across a subnet, visualises traffic flow on an interactive dashboard and raises intrusion alerts — making it one of the most impactful network security final year projects for BE, MTech and PhD scholars.
Modern networks carry enormous volumes of traffic spanning diverse protocols, and the ability to capture, decode and analyse packets in real time is foundational to network security, performance engineering and forensic investigation. This project implements a dual-mode network tool that combines a passive packet sniffer with an active network scanner into a unified Python application.
Using Python's Scapy library and raw socket access, the sniffer places the selected network interface into promiscuous mode and intercepts all frames traversing the wire or wireless medium. Each captured frame is dissected layer by layer — from the Ethernet (Layer 2) MAC header through the IPv4/IPv6 (Layer 3) network header to the TCP/UDP/ICMP (Layer 4) transport header — and, where applicable, up to application-layer protocols such as DNS, HTTP, HTTPS/TLS, FTP, SMTP and ARP.
Packet metadata — source/destination IP, ports, protocol, payload length, TTL, TCP flags, sequence numbers and timestamps — is extracted and written to both a rotating log file and a live in-memory dataframe for real-time analytics. The scanner module dispatches ICMP ping sweeps and ARP requests to discover all reachable hosts on a user-specified subnet (e.g. 192.168.1.0/24). For each live host, a TCP SYN port scan (optionally full-connect or UDP) probes a configurable port range to identify open services. Results are matched against a service-name database (analogous to Nmap's nmap-services) to label ports (HTTP, SSH, FTP, RDP, MySQL, etc.). OS fingerprinting heuristics based on TTL values and TCP window size provide a probabilistic OS estimate without requiring root/administrator-level raw-socket privileges for the connect scan fallback.
A lightweight rule engine monitors the live packet stream for known attack signatures: ARP spoofing (duplicate IP-to-MAC mappings), SYN flood (high SYN rate without ACK), port scan detection (sequential port probes from a single source), DNS amplification patterns and ICMP ping storms . Alerts are raised in the console, logged to a structured JSON alert file and, optionally, pushed to a Telegram bot or email endpoint for remote notification.
A Tkinter or Streamlit GUI provides live visualisation: a scrollable packet table, protocol distribution pie chart, top-talkers bar chart, bandwidth timeline, and a host-discovery map rendered as an interactive network graph with NetworkX and Matplotlib. The dashboard refreshes every second via a background thread without blocking the capture engine. The project is built entirely in Python 3 and uses best-in-class networking, data analysis and visualisation libraries — no third-party paid software required.
A modular pipeline from raw NIC capture to parsed packets, analytics engine and GUI dashboard — running concurrently via Python threads. Students gain direct, byte-level understanding of how Ethernet frames, IP datagrams, TCP segments, DNS queries and ARP replies are structured — knowledge that no textbook exercise can replicate. Every viva question about OSI layers can be answered from first-hand implementation experience.
Python, Scapy, Wireshark, Nmap and all supporting libraries are free and open-source. The project runs on any Linux, macOS or Windows machine with a standard NIC, eliminating hardware procurement barriers for students. The live Streamlit / Tkinter dashboard displaying scrolling packet tables, protocol pie charts and a NetworkX host graph provides striking visual evidence during demos and viva presentations — far more compelling than static screenshots or printed reports.
Combining a passive sniffer (zero network footprint) with an active Nmap-based scanner gives the project dual academic value — covering both network monitoring and security auditing domains, which broadens its applicability across CSE, ECE, IT and cybersecurity syllabi. Built-in ARP spoofing, SYN flood and port scan detectors give the project a tangible security use case, directly mapping to IDS/IPS concepts taught in network security courses and making it relevant for IEEE publication in security-focused journals and conferences.
All captures can be saved as standard .pcap files and cross-validated in Wireshark, providing independent verification of the tool's accuracy and demonstrating Wireshark proficiency — a highly sought skill in network engineering roles. The modular architecture supports extensions: ML-based traffic classification (Random Forest / CNN on flow features), encrypted traffic fingerprinting via TLS SNI, federated anomaly detection across edge nodes, and 5G N6 interface monitoring — each a publishable research direction.
Runs on Linux (recommended for raw sockets), macOS and Windows (with Npcap/WinPcap). The sniffer engine uses fewer than 150 lines of core code, making it easy to read, explain and customise — ideal for viva where code walkthrough questions are common. Skills demonstrated — packet capture, protocol analysis, port scanning, network mapping, PCAP forensics and security alerting — are directly relevant to roles in network engineering, SOC analyst, penetration testing, cloud security and DevSecOps, boosting placement prospects.
We deliver IEEE-format project report covering problem statement, literature review, system design (DFD, ER, flow diagrams), implementation, results (packet tables, scan reports, alert logs, Wireshark comparison), conclusion, references and a 25-slide PPT with 60+ viva Q&A covering OSI, TCP/IP, ARP, DNS, IDS concepts. A representative excerpt showing the core packet capture loop, protocol dissection logic and live output — exactly as it appears on a Linux terminal during a real capture session.
5. Performance Evaluation & Extended Technical Observations This is a Python tool for capturing, analyzing, and cracking wireless network traffic using the Scapy library. The tool provides two main functions: sniff_wireless(): Sniffs wireless network traffic and extracts the SSID, BSSID, and channel of each wireless network beacon frame.
crack_wep(): Cracks WEP encryption using an ARP injection attack and a specified WEP key. This tool is intended for educational purposes only and should not be used for malicious activities. Always ensure that you have permission to perform security testing on a network before doing so. Replace INTERFACE, BSSID, CHANNEL, SSID, and WEP_KEY with the appropriate values for the network you want to target.
PySniffer is a Python tool for capturing, analyzing, and cracking wireless network traffic using the Scapy library. The tool provides a simple and easy-to-use interface for wireless security testing and education. Have you ever wanted to build a tool to display nearby wireless networks along with their MAC address and some other useful information? Well, in this tutorial, we are going to build a Wi-Fi scanner using the Scapy library in Python.
If you're in this field for a while, you might have seen the airodump-ng utility that sniffs, captures, and decodes 802.11 frames to display nearby wireless networks in a nice format, in this tutorial, we will do a similar one. To get started, you need to install Scapy , I have cloned the development version, you can also install it using pip : Note: This tutorial assumes you are using any Unix-based environment, it is also suggested you use Kali Linux .
After that, we gonna use pandas just for printing in a nice format (you can change that obviously): Now the code of this tutorial won't work if you do not enable monitor mode in your network interface, please install aircrack-ng (comes pre-installed on Kali) and run the following command: So I've set the BSSID (MAC address of the access point) as the index of each row, as it is unique for every device.
If you're familiar with Scapy , then you know for sure that we are going to use the sniff() function, which takes the callback function that is executed whenever a packet is sniffed, let's implement this function: This callback makes sure that the sniffed packet has a beacon layer on it, if it is the case, then it will extract the BSSID , SSID (name of access point), signal, and some stats. Scapy's Dot11Beacon class has the awesome network_stats() function that extracts some useful information from the network, such as the channel, rates, and encryption type. Finally, we add these information to the dataframe with the BSSID as the index.
You will encounter some networks that don't have the SSID ( ssid equals to "" ), this is an indicator that it's a hidden network. In hidden networks, the access point leaves the info field blank to hide the discovery of the network name, you will still find them using this tutorial's script, but without a network name. Now we need a way to visualize this dataframe. Since we're going to use sniff() function (which blocks and start sniffing in the main thread), we need to use a separate thread to print the content of networks dataframe, the below code does that: Now, if you execute this, you will notice not all nearby networks are available. That's because we're listening on one WLAN channel only. We can use the iwconfig command to change the channel. Here is the Python function for it: Great, so this will change channels incrementally from 1 to 14 every 0.5 seconds, spawning the daemon thread that runs this function: Note: Channels 12 and 13 are allowed in low-power mode, while channel 14 is banned and only allowed in Japan.
Note that we set the daemon attribute of the thread to True , so this thread will end whenever the program exits. Check this tutorial for more information about daemon threads. Alright, in this tutorial, we wrote a simple Wi-Fi scanner using the Scapy library that sniffs and decodes beacon frames which are transmitted every time by access points. They serve to announce the presence of a wireless network.
Finally, we have an Ethical Hacking with Python EBook where we build over 20 hacking tools scripts from scratch using Python. Make sure to check it out if you're interested! Scan, analyse and improve your Wi-Fi in Python: best channel, security checkup, site survey and reports. Get every module of WiFi Analyzer Pro , plus tests, the README guide and free updates, for $12.
Learn how you can extract Wi-Fi passwords that are saved in your machine (either Windows or Linux) using Python without installing any third-party library. Learn how to use Scapy library in Python to perform a TCP SYN Flooding attack, which is a form of denial of service attacks. Forcing devices to disconnect from a network by sending deauthentication frames continuously using Scapy library in Python, this is called deauthentication attack.
Got a coding query or need some guidance before you comment? Check out this Python Code Assistant for expert advice and handy tips. It's like having a coding tutor right in your fingertips! Ready to take Python coding to a new level? Explore our Python Code Generator . The perfect tool to get your code up and running in no time. Start now! A network scanner is an important element for a network administrator as well as a penetration tester. It allows the user to map the network to find devices that are connected to the same network.
In this tutorial, you will learn how to build a simple network scanner using Scapy ibrary in Python. Back to the point, there are many ways out there to scan computers in a single network, but we are going to use one of the popular ways which is using ARP requests. The network scanner will send the ARP request indicating who has some specific IP address, let's say "192.168.1.1" , the owner of that IP address ( the target ) will automatically respond saying that he is "192.168.1.1" , with that response, the MAC address will also be included in the packet, this allows us to successfully retrieve all network users' IP and MAC addresses simultaneously when we send a broadcast packet (sending a packet to all the devices in the network).
Note that you can change the MAC address of your machine, so keep that in mind while retrieving the MAC addresses, as they may change from one time to another if you're in a public network. Note: In case you are not familiar with the notation "/24" or "/16" after the IP address, it is basically an IP range here, for example, "192.168.1.1/24" is a range from "192.168.1.0" to "192.168.1.255" , please read more about CIDR Notation .
Now we have created these packets, we need to send them using srp() function which sends and receives packets at layer 2, we set the timeout to 3 so the script won't get stuck: result now is a list of pairs that is of the format (sent_packet, received_packet) , let's iterate over them: Alright, we are done with this tutorial. See how you can extend this and make it more convenient to replace other scanning tools.
Finally, we have an Ethical Hacking with Python EBook , where we build more than 35 hacking tools and scripts from scratch using Python. Check it out here if you're interested! Why juggle between languages when you can convert? Check out our Code Converter . Try it out today! Learn how to write a port scanner in Python using sockets, starting with a simple port scanner and then diving deeper to a threaded version of a port scanner that is reliable for use.
Building a Wi-Fi scanner in Python using Scapy that finds and displays available nearby wireless networks and their MAC address, dBm signal, channel and encryption type. Learn how to use Scapy library in Python to perform a TCP SYN Flooding attack, which is a form of denial of service attacks. Harvested Online Documentation & Reference Sources • https://dev.to/qingluan/build-a-network-scanner-with-python-and-scapy-aff • https://scapy.readthedocs.io/ • https://www.geeksforgeeks.org/python/network-scanning-using-scapy-module-python/ • https://dev.to/sainsec/pysniffer-a-wireless-network-tool-3bhb • https://pythoneo.com/building-network-scanners-with-scapy/ • https://www.educative.io/courses/python-scapy-for-network-security • https://github.com/Tarek-Talab/WIFI-Scanner • https://www.iditect.com/programming/python-example/how-to-build-a-wifi-scanner-in-python-using-scapy.html • https://netpacket.net/2020/08/building-a-wi-fi-scanner-with-scapy/ • https://github.com/HalilDeniz/Scapy-Network-Security-Tools
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Wireless Network Vulnerability Scanner Using Scapy.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Wireless Network Vulnerability Scanner Using Scapy... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |