Complete Technical Paper Content — Wireless Sensor Network Security Against Wormhole Attack
Overview & System Context
Wireless Sensor Network Security Against Wormhole Attack: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4651 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Wireless sensor networks (WSNs) refer to networks of spatially dispersed and dedicated sensors that monitor and record the physical conditions of the environment and forward the collected data to a central location. WSNs can measure environmental conditions such as temperature, sound, pollution levels, humidity and wind. These are similar to wireless ad hoc networks in the sense that they rely on wireless connectivity and spontaneous formation of networks so that sensor data can be transported wirelessly. WSNs monitor physical conditions, such as temperature, sound, and pressure. Modern networks are bi-directional, both collecting data and enabling control of sensor activity. The development of these networks was motivated by military applications such as battlefield surveillance. Such networks are used in industrial and consumer applications, such as industrial process monitoring and control and machine health monitoring and agriculture. A WSN is built of "nodes" – from a few to hundreds or thousands, where each node is connected to other sensors. Each such node typically has several parts: a radio transceiver with an internal antenna or connection to an external antenna, a microcontroller, an electronic circuit for interfacing with the sensors and an energy source, usually a battery or an embedded form of energy harvesting. A sensor node might vary in size from a shoebox to (theoretically) a grain of dust, although microscopic dimensions have yet to be realized. Sensor node cost is similarly variable, ranging from a few to hundreds of dollars, depending on node sophistication.
Size and cost constraints constrain resources such as energy, memory, computational speed and communications bandwidth. The topology of a WSN can vary from a simple star network to an advanced multi-hop wireless mesh network. Propagation can employ routing or flooding. In computer science and telecommunications, wireless sensor networks are an active research area supporting many workshops and conferences, including the International Workshop on Embedded Networked Sensors (EmNetS), International Conference on Information Processing in Sensor Networks (IPSN), SenSys, MobiCom and European Conference on Wireless Sensor Networks (EWSN). As of 2010, wireless sensor networks had deployed approximately 120 million remote units worldwide.
Wireless sensor networks also are used for the collection of data for monitoring of environmental information. This can be as simple as monitoring the temperature in a fridge or the level of water in overflow tanks in nuclear power plants. The statistical information can then be used to show how systems have been working. The advantage of WSNs over conventional loggers is the "live" data feed that is possible.
WSN can be used to monitor the condition of civil infrastructure and related geo-physical processes close to real time, and over long periods through data logging, using appropriately interfaced sensors. Power consumption constraints for nodes using batteries or energy harvesting. Examples of suppliers are ReVibe Energy and Perpetuum Ability to cope with node failures (resilience) Some mobility of nodes (for highly mobile nodes see MWSNs) Heterogeneity of nodes Homogeneity of nodes Scalability to large scale of deployment Ability to withstand harsh environmental conditions Ease of use Cross-layer optimization Cross-layer is becoming an important studying area for wireless communications. In addition, the traditional layered approach presents three main problems: Figure 1: Wormhole Attack Detection in Wireless Network Coding Traditional layered approach cannot share different information among different layers, which leads to each layer not having complete information. The traditional layered approach cannot guarantee the optimization of the entire network. The traditional layered approach does not have the ability to adapt to the environmental change. Because of the interference between the different users, access conflicts, fading, and the change of environment in the wireless sensor networks, traditional layered approach for wired networks is not applicable to wireless networks. So the cross-layer can be used to make the optimal modulation to improve the transmission performance, such as data rate, energy efficiency, quality of service (QoS), etc.
Sensor nodes can be imagined as small computers which are extremely basic in terms of their interfaces and their components. They usually consist of a processing unit with limited computational power and limited memory, sensors or MEMS (including specific conditioning circuitry), a communication device (usually radio transceivers or alternatively optical), and a power source usually in the form of a battery. Other possible inclusions are energy harvesting modules, secondary ASICs, and possibly secondary communication interface (e.g. RS-232 or USB). The base stations are one or more components of the WSN with much more computational, energy and communication resources. They act as a gateway between sensor nodes and the end user as they typically forward data from the WSN on to a server. Other special components in routing based networks are routers, designed to compute, calculate and distribute the routing tables.
One major challenge in a WSN is to produce low cost and tiny sensor nodes. There are an increasing number of small companies producing WSN hardware and the commercial situation can be compared to home computing in the 1970s. Many of the nodes are still in the research and development stage, particularly their software. Also inherent to sensor network adoption is the use of very low power methods for radio communication and data acquisition. In many applications, a WSN communicates with a local area network or wide area network through a gateway. The Gateway acts as a bridge between the WSN and the other network. This enables data to be stored and processed by devices with more resources, for example, in a remotely located server. A wireless wide area network used primarily for low-power devices is known as a Low-Power Wide-Area Network (LPWAN).
Increased lifespan Robustness and fault tolerance Self-configuration Lifetime maximization: Energy/Power Consumption of the sensing device should be minimized and sensor nodes should be energy efficient since their limited energy resource determines their lifetime. To conserve power, wireless sensor nodes normally power off both the radio transmitter and the radio receiver when not in use.
Sensor nodes are prone to failure, For better collection of data, To provide nodes with backup in case of failure of the central node. There is also no centralised body to allocate the resources and they have to be self organized. As for the distributed filtering over distributed sensor network. the general setup is to observe the underlying process through a group of sensors organized according to a given network topology, which renders the individual observer estimates the system state based not only on its own measurement but also on its neighbors'.
Figure 2: Wormhole Attack Detection in Wireless Network Coding The data gathered from wireless sensor networks is usually saved in the form of numerical data in a central base station. Additionally, the Open Geospatial Consortium (OGC) is specifying standards for interoperability interfaces and metadata encodings that enable real time integration of heterogeneous sensor webs into the Internet, allowing any individual to monitor or control wireless sensor networks through a web browser.
Adrian Perrig (born 1972) is a Swiss computer science researcher and professor at ETH Zurich, leading the Network Security research group. His research focuses on networking and systems security, and specifically on the design of a secure next-generation internet architecture. Jean-Pierre Hubaux is a Swiss-Belgian computer scientist specialised in security and privacy. He is a professor of computer science at EPFL (École Polytechnique Fédérale de Lausanne) and is the head of the Laboratory for Data Security at EPFL's School of Computer and Communication Sciences.
2. System Architecture & Core Working Principles Official websites use .gov A .gov website belongs to an official government organization in the United States. Secure .gov websites use HTTPS A lock ( ) or https:// means you've safely connected to the .gov website. Share sensitive information only on official, secure websites.
Retraction in: PeerJ Comput Sci. 2024 Mar 22;10:e1449/retraction See also: PMC Retraction Policy unrestricted use, distribution, reproduction and adaptation in any medium and for any purpose provided that it is properly attributed. For attribution, the original author(s), title, publication source (PeerJ Computer Science) and either DOI or URL of the article must be cited.
Figure 3: Wormhole Attack in Wireless Sensor Network Projects - YouTube Wireless sensor networks (WSNs) are networks formed by organizing and combining tens of thousands of sensor nodes freely through wireless communication technology. WSNs are commonly affected by various attacks, such as identity theft, black holes, wormholes, protocol spoofing, etc . As one of the more severe threats, wormholes create passive attacks that are hard to detect and eliminate. Since WSN is often used in the tactical network field, a planned secure network is essential for military applications with high security. Guard nodes are traffic monitoring nodes used to supervise neighbors’ data communication around the tactical networks. Therefore, this work proposes a Quality of Service (QoS) security mechanism to select multiple dual-layer guard nodes at different paths of the WSN based on the path qualities to detect wormholes. The entire network’s links are categorized into high, normal, and low priority levels. As such, this study aimed to confirm the security of high priority nodes and links in the tactical network, avoid excessive overhead, and provide random security facilities to all nodes. The proposed measures of the QoS-based security provision, including link cluster formation, guard node selection, authenticated guard node identification, and intrusion detection, ensure economic and efficient network communication with different quality levels.
Keywords: Tactical network, WSN, Passive attack, Wormhole, QoS, Protocols, Intrusion, Secure routing and neighbor monitoring Wireless security networks (WSNs) are a type of sensor network that deploys multiple wireless sensor nodes around vast geographical regions. Each sensor node in the network can be manufactured with multiple sensors and transceivers that observe environmental objects, such as heat, moisture, pressure, etc . These sensor nodes and other gateway systems are implemented into tactical networks to increase security. However, despite the secure environment, the network is still vulnerable to different attacks that harm its functions and, thus, requires new techniques to enhance security further. Guard nodes provide a security technique that employs separate nodes with other tactical nodes to supervise neighbours’ activities.
These nodes must be optimally selected from any part of the tactical WSN. to maintain data transmission quality. In this work, guard nodes were chosen for detecting wormhole attacks raised in the tactical WSN. A wormhole attack is a passive attack that creates a separate unauthorized link between two communicating nodes, subsequently causing the legitimate nodes to send data through this link. Thus, the data are intercepted, and the corresponding nodes are compromised. In a tactical WSN, the guard node selection should be based on current link qualities and priorities to ensure dedicated security benefits. However, in data communication, QoS in security depends on its availability, reliability, and serviceability. This work analyzed the specific characteristics, limitations, and QoS factors of tactical WSNs. Specifically, guard nodes were selected for monitoring purposes by analysing the quality metrics of each node.
Because selecting multiple guard nodes helps to protect the links and nodes from wormhole attacks. The principle of QoS is to ensure the security of all links and guard node activities. At the same time, the priority-based security provision is achieved using this effective guard node selection process. To develop QoS-based guard nodes and establish secure monitoring to eliminate wormholes, supervised monitoring nodes (SMNs) are improved with quality control techniques. Ji, Chen & Zhong (2015) analysed wormhole attackers and the complexity of intrusion detection, focusing on QoS and security difficulties.
Results showed that such attacks do not concentrate on network availability, communication reliability, or security in WSN. Therefore, the prior wormhole attack detection and performance estimation was the target of the research. In this work, guard node-based security was combined with QoS for a WSN as a protective measure against wormhole attacks due to inadequate resources and composite interactions of WSN operations. This proposed measure is pertinent for developing secured and QoS-provisioned data transmission.
This presented work suggests the selection of multiple guard nodes to protect the tactical WSN from wormhole attacks. Each node in the network is equipped with wormhole detection procedures and alarm units and can be requested to act as a guard node. At the same time, the guard node uses wormhole detection procedures to detect attacks from the nearest hops. In addition, the proposed system ensures link quality, priority, and QoS levels of each node to provide guard node-based security. The rest of this article is organized as follows. The second section presents related works. The third section describes QoS-based guard node selection procedures, followed by discussions on QoS attainments, secure guard node authentication, and wormhole detection procedures. The fourth section explains the results of implementing the proposed QWDGN. The fifth section provides concluding remarks.
3. Software Implementation, Frameworks & Protocols Various detection techniques have been proposed to protect tactical WSNs against attacks. Precisely, the wormhole attack detection techniques follow either rule-based, feature-based, or signature-based identification. Karthigadevi, Balamurali & Venkatesulu (2018a) proposed a transmission round time-oriented wormhole attack detection algorithm in wired networks. In this approach, the authors analysed traffic attributes using an enhanced interior gateway routing protocol then implemented the proposed mechanism in cisco-based networks. Lakshmi & Yadav (2019) discussed effective wormhole detection strategies in wireless mesh networks containing more links than other networks. The authors concentrated on mesh network links in which wormholes were created to misuse the network resources. The authors further investigated the performance rates of attack detection algorithms against a large number of wormhole links.
Ji, Chen & Zhong (2015) established a distributed-level coding system, DAWN, to protect the network resources against multiple wormhole attacker nodes. The proposed system was designed to monitor local, and global network services, communication synchronization patterns, and wormhole attacks by controlling network coding protocols. Both Khan & Lavagno (2012) and Perillo & Heinzelman (2005) analysed proactive and reactive protocols for WSN security, focusing on support for data communication, security problems, and the necessary solutions.
Tun & Maw (2008) and Kurmi, Verma & Soni (2017a) proposed wormhole attack detection strategies in WSNs to protect the nodes. In these works, wormhole attacks were first created by multiple attackers among legitimate nodes, then detected using the proposed algorithms based on the node signatures and transmission patterns. However, the proposed strategies suffer from a limited number of nodes. In the same way, Kumhar & Ukani (2015) proposed QoS support protocols for WSNs to build reliable security in the proposed system. Moreover, Wang et al. (2010) devised a QoS-based efficient routing approach using MAC optimization for cross-layer activities between MAC and routing protocol procedures. The authors claim that this design performs better in WSN, whereby the MAC and IP data sequences can be customized to obey QoS requirements. Further, the authors suggest that the QoS-based routing strategy offers less delay and smaller packet loss compared to other methods.
Previous studies have proposed diverse viewpoints and principles of QoS. For instance, Dutta & Dunkels (2012) investigated QoS measurements and optimal power consumption using QoS procedures and policies with the Gur prototype, and found that node dimension, deployment, coverage, and liveliness of each node constrain QoS. Dissimilar to other works, this work developed QoS as a provision to guard node selection procedures. The researchers matched the requirements of both QoS and security in a single view to building an efficient guard node-based Intrusion Detection System (IDS). Since tactical WSNs are prone to different types of wormhole attacks, Roy & Khan (2020) aimed to establish security against wormhole attacks without compromising the quality performance of the network. The latter authors incorporated security policies and a QoS strategy as a protective measure against wormhole attacks.
Similarly, Pazynyuk et al. (2008) investigated the challenges and needs of QoS-based security features by selecting guard nodes and using SMNs to maintain the optimal data loss rate, transmission rate, and delay with energy utilization. Because QoS and security concerns are not associated with the context of WSN, Karthigadevi, Balamurali & Venkatesulu (2018a) proposed different solutions against wormhole attacks. The authors emphasized the WSN environment, where both QoS and security attainments are required for successful operation. Tactical networks, such as those used in military target tracking applications, are expected to be more secured. Kurmi, Verma & Soni (2017) demonstrated the impact of the inclusion of certain security protocols on the rate of QoS and the effects of specific QoS parameters on the network’s security needs. All mentioned studies found notable correlations between QoS and security despite not being closely related notions.
Even though there are different routing and wormhole attack detection techniques, security and QoS maintenance are vital in WSNs ( Poonam & Preeti, 2014 ). In Fathi et al. (2021) the quality of service-based sensor location modelling is done, and the service pricing is determined based on that Sartori & Melen (2021) describes the usage of wireless sensor networks with mobile elements for designing a platform for the smart environment. In this manner, this presented work suggests security provisions against wormhole attacks ( Kaliyar et al., 2020 ; Karthigadevi, Balamurali & Venkatesulu, 2018a ) by considering link-wise QoS requirements and offering the flexibility of customized security metric allotments for different links in tactical WSNs. Specifically, QoS’ needs and security qualities are interrelated and secured, while security levels are ensured using Hash-based Authentication Codes (HMAC) computations. Herein, the communication parameters were optimized to enhance the security of QoS levels.
Based on the analysis, both the computation and communication overhead provide efficient security procedures and, thus, improved security for nominal computation overhead in the WSN. In the proposed QWDGN, security and QoS parameters were analyzed and correlated. First, security levels were determined with varying HMAC complexities and packet lengths, as given in Table 1 . Then, QoS and guard node characteristics were mapped for the selection procedures. In the next phase, the selected guard nodes were identified. In the end, the wormhole attack detection procedures were activated to ensure security in the tactical WSN.
Providing security in the selection process of guard nodes creates additional control messages and data exchanges. This can cause the packet length to increase, affecting the QoS assigned to the data transmission. Table 1 provides details of the various security levels. Discussion of related works focuses on the secured packets with the help of HMAC. As the size of HMAC increases, the packet length also increases, which affects data transmission. Thus, building guard node-based IDS with minimal cost of packet overhead is an important task. Only a few research works describe object or node-tracking mechanisms in WSNs.
Guard nodes contain the intrusion detection system (IDS) as the active agent to configure rules and procedures to validate node traffic. Since the IDS agent can be designed to monitor any violations in the tactical network, it was configured with wormhole attack patterns in this work. Guard nodes in the network can activate these IDS procedures to validate their behaviors and traffic patterns. Figure 1 shows a sample tactical WSN with various clusters in which several nodes can be grouped. Guard nodes must be selected based on link efficiency to keep QoS constraint. In addition, the supervising master nodes (SMNs) were configured to organize guard nodes’ activities and reports.
4. Practical Deployment, Analysis & Case Studies Figure 1 also illustrates the guard node selection process in the initial steps of the selection algorithm. In the network setup stage, secure cluster formation and guard node selection phases were incorporated with QoS constraints. The following section explains QoS-based guard node selection algorithms and QoS-based SMN configuration procedures.
As seen in Fig. 1 , the network setup displays four clusters, each containing members, cluster heads, and SMNs. Algorithm 1 represents the QoS-based cluster formation and cluster head election, assuming there are four classes of QoS requirements. QoS attributes, such as delay, bandwidth, jitter, energy, and throughput, are given reference values to classify clusters and node characteristics. Algorithm 1 (as shown in Fig. 2 ) requires a few additional steps for incorporating QoS requirements in each cluster. In this setup phase, quality measurements for all nodes and links are defined and updated in the base station and the cluster head. The quality definitions are provided in Table 2 , in which the dots specify the range or sequence of link quality.
Figure 3 shows the clusters and cluster node links. Using these nodes and QoS requirements, the guard nodes must be selected, while SMNs need to be configured to monitor the nodes. Figure 4 displays the creation of wormhole nodes and links (grey nodes) in different clusters, in which the short wormhole are affected by Node 1 and Node 6 from Cluster 2. Besides Nodes 1 and 6 from Cluster 2, Nodes H and K from Cluster 3 are also affected by short wormhole attackers. A single wormhole attacker can use high transmission energy to entice the neighbour nodes to send their data to the attacker. This creates a wormhole between Nodes 1 and 2 and between Nodes L and M, presenting the first case of vulnerability creation. In comparison, Nodes 7, 15, 14, 13, and 12 from Clusters 0 and 1 are influenced by the longest wormholes, which affect the entire link.
According to the QoS requirements and security needs, the proposed QWDGN provides controllable security complexities. For example, level 0 requires high priority of QoS but allows minimal security overhead, thus, QoS and security levels are indirectly proportional. Yet, this lack of security is not allowable in the best QoS links. In Cluster 1, the affected nodes include Nodes B, C, G, and the cluster head. All wormhole attackers collect packets from their victims and then misuse or divert the collected information. Otherwise, they may alter the received data and send false information to other network nodes. These attacks create extensive issues for low, medium, and high-priority links.
Due to the complex nature of WSNs, identifying guard nodes and maintaining the availability of nodes are complicated tasks. Therefore, in addition to the optimal guard node selection algorithms, this presented study performed the secure cluster head identification and trust evaluation procedures, as reported in previous works. Algorithm 2 (as shown in Fig. 5 ) is responsible for validating each link in the network and then subsequently analyzing the priority vector details, which describe the priority levels of each link. From the initial level of analysis, the possible guard nodes are identified.
Once the list of optimal neighbours has been formed, they can share their monitor requests with the nodes to be monitored. Advanced Encryption Standard (AES) encrypts these requests at each guard node. This is explained in Algorithm 3 (as shown in Fig. 6 ). The nodes that receive valid permission from Node ‘i’ can monitor the guard node. Typically, the guard nodes are not selected from high priority QoS links, but rather from low priority links, which causes delays in sensitive data transmission. Also, the bandwidth of superior priority links is saved.
By using this approach, throughput is increased. For MP links, the guard nodes are selected based on the W weight vector, which may fractionally vary between 0 and 1. Once these guard nodes are selected successfully, they are under the control of SMNs. In this QoS-based security mechanism, the SMNs need to be configured in different manners. 5. Performance Evaluation & Extended Technical Observations SMN is the master node that acts as the authenticated cluster head and must be configured for maintaining the operation of guard nodes in wormhole detection. Guard nodes detect wormholes at their nearest hops, then raise alarms and send reports to their closest SMNs, which repeat the wormhole alert messages to all other members of the WSN cluster. Algorithm 4 (as shown in Fig. 7 ) gives the details of SMN configuration. Figure 8 illustrates the creation and utilization of guard nodes and SMNs, represented by shaded and bold line circles, respectively. The lines between circles indicate the monitoring processes between the grey nodes in the four clusters with several attackers (circles). In Cluster 0, Node 8 monitors Node 9, while Node 10 monitors Node 13. Assuming that Node 6 is sending data to any other node in a cluster, then that data transmission is monitored by two nodes.
The monitoring processes are dependent on QoS conditions. For example, if Node 3 withdraws its monitoring task on Node 6 to monitor Node 1, it is assumed that the association between Nodes 1 and 3 has higher priority than between Nodes 3 and 6. The same situation can occur for the operation of Node 5 and each cluster to maintain the network traffic requirements based on QoS metrics. Once this QoS-based intrusion detection is enabled in the respective guard node, the node executes its IDS agent module.
Usually, wormholes create separate attacker nodes at the transmitting ends (source and destination). The wormhole attackers generate a private unauthenticated link from the source to the destination to intercept the data. Since this attack is not openly active, it is rather complicated to be detected. However, the nodes’ signatures and traffic patterns help identify wormhole attackers in tactical WSN, which are implemented in the proposed QWDGN system. Algorithm 5 (as shown in Fig. 9 ) describes the procedure of wormhole detection.
At the end of this process, various wormholes can be detected. In this work, a secure Ad Hoc On-Demand Distance Vector (AOMDV) ( Fathi et al., 2021 ; Sartori & Melen, 2021 ) was used for a safe routing process, in which the transmission path is declined once the attackers are identified successfully. Then, the path is forever marked as vulnerable in the AOMDV routing table, thus ensuring secure routing.
Herein, the proposed QWDGN was verified using Network Simulator-3 (NS-3). The network was designed with the simulation characteristics, which are provided are in Table 2 . In this simulation, 300 tactical WSN nodes were created with an initial transmitting power of 0.5 Joules, then the tactical WSN area of 1000*1000 m was configured. Figure 10 shows the performance of the proposed QWDGN system at different security levels of links, where the link counts vary according to different HMAC lengths. For this performance analysis, three existing wormhole detection techniques, namely wormhole detection in static WSN (WSWSN), round-trip time (RTT) based wormhole detection (RTTWD), and AODV for wormhole detection (AWD), were included for comparison. In the WSWSN approach, several wormholes are simulated on a static WSN and are identified using signature-based procedures. However, this approach assumes that all nodes are preconfigured with predefined guard nodes ( Patel, Aggarwal & Chaubey, 2019 ).
Figures 11 and 12 present the details of the different wormhole detection methods, namely WSWSN, RTTWD, and AWD, compared with the proposed QWDGN system. Results show that QWDGN performs better than the other methods due to its dynamic QoS aware guard nodes and security aspects. Figure 13 illustrates the comparison of QoS-based overhead between our proposed strategy and the other methods. In this case, the different methods lack quality parameters of the sensitive tactical WSN, which increases the complexity of all QoS levels when developing security principles. Comparatively, our proposed QWDGN system ensures limited overhead in providing security features to all links.
The proposed QWDGN was designed and implemented to create a wormhole detecting guard node environment. The nodes were selected based on the required quality levels of each link, which were detained separately as priority based on QoS needs. In this environment, the selected guard nodes were dynamically switched to detect the wormholes considering QoS needs, while routing was carried out using secure AOMDV. According to the performance evaluation, the proposed strategy can produce a sufficient number of guard nodes and ensure security of the tactical WSN based on the QoS provision levels with 20% less overhead. Nevertheless, the main challenge of this proposed system is maintaining the availability of guard nodes against dynamic network changes. Thus, our strategy can be improved by using secure quality aware routing algorithms to minimize the latency by 20% and packet loss and implementing deep learning-based neural network techniques to increase the dynamic decision-making rate against wormholes.
Ke Zhang conceived and designed the experiments, performed the experiments, analyzed the data, performed the computation work, prepared figures and/or tables, authored or reviewed drafts of the article, and approved the final draft. This section collects any data citations, data availability statements, or supplementary materials included in this article. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Wireless%20sensor%20network • https://en.wikipedia.org/wiki/Adrian%20Perrig • https://en.wikipedia.org/wiki/Jean-Pierre%20Hubaux • https://pmc.ncbi.nlm.nih.gov/articles/PMC10495966/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
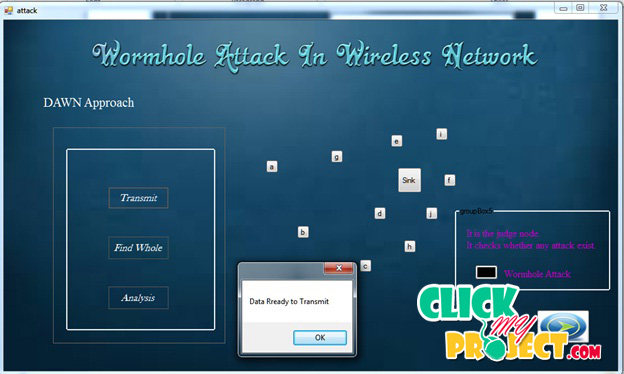
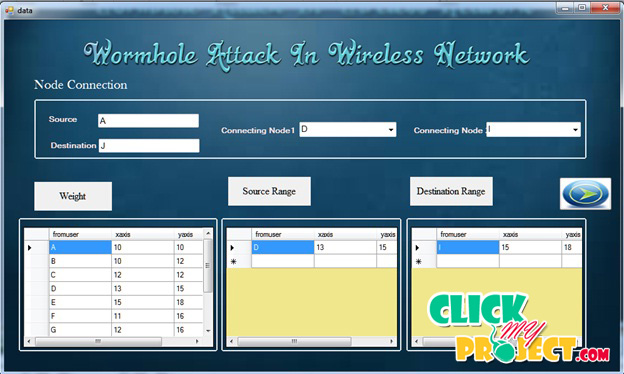
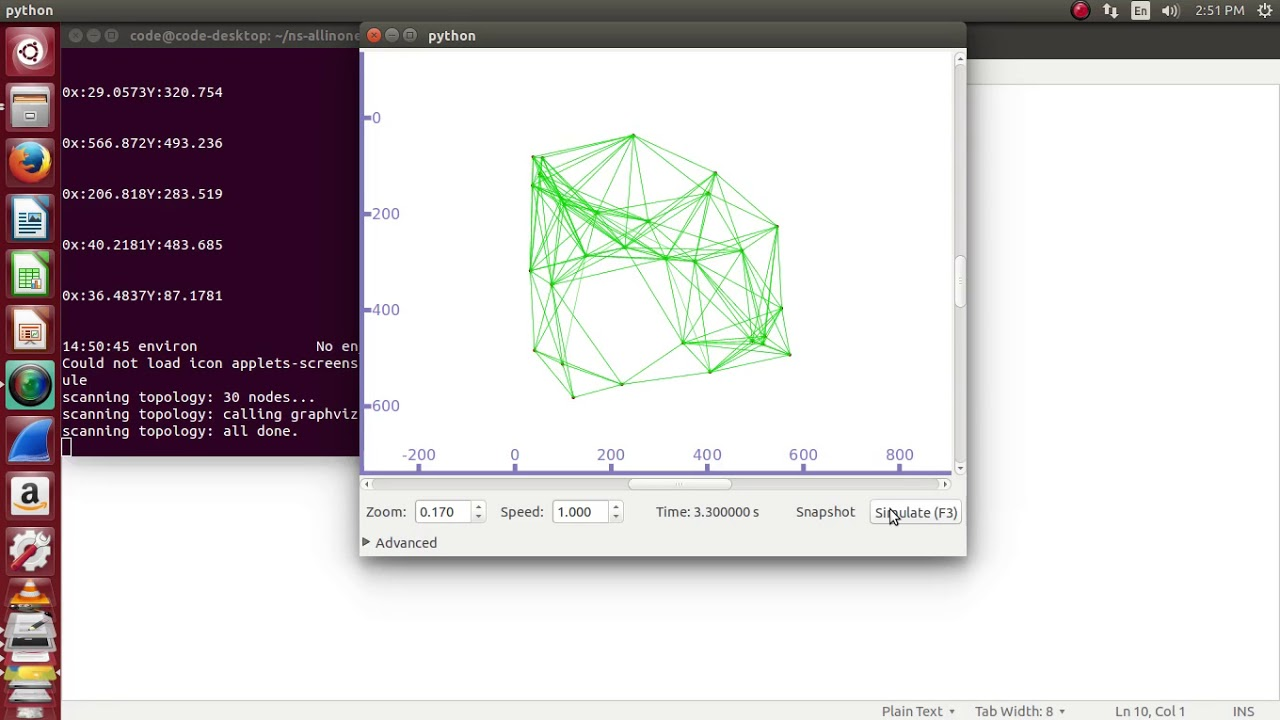
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Wireless Sensor Network Security Against Wormhole Attack.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |