Complete Technical Paper Content — Zero Knowledge Authentication For Banking Systems Project
Overview & System Context
Zero Knowledge Authentication For Banking Systems Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9523 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A password, sometimes called a passcode, is secret data, typically a string of characters, usually used to confirm a user's identity. Traditionally, passwords were expected to be memorized, but the large number of password-protected services that a typical individual accesses can make memorization of unique passwords for each service impractical. Using the terminology of the NIST Digital Identity Guidelines, the secret is held by a party called the claimant while the party verifying the identity of the claimant is called the verifier. When the claimant successfully demonstrates knowledge of the password to the verifier through an established authentication protocol, the verifier can infer the claimant's identity. In general, a password is a sequence of characters including letters, digits, or other symbols. If the permissible characters are constrained to be numeric, the corresponding secret is sometimes called a personal identification number (PIN). Despite its name, a password does not need to be an actual word; indeed, a non-word (in the dictionary sense) may be harder to guess, which is a desirable property of passwords. A memorized secret consisting of a sequence of words or other text separated by spaces is sometimes called a passphrase. A passphrase is similar to a password in usage, but the former is generally longer for added security.
The way in which they secure the passing round of the watchword for the night is as follows: from the tenth maniple of each class of infantry and cavalry, the maniple which is encamped at the lower end of the street, a man is chosen who is relieved from guard duty, and he attends every day at sunset at the tent of the tribune, and receiving from him the watchword—that is a wooden tablet with the word inscribed on it – takes his leave, and on returning to his quarters passes on the watchword and tablet before witnesses to the commander of the next maniple, who in turn passes it to the one next to him. All do the same until it reaches the first maniples, those encamped near the tents of the tribunes. These latter are obliged to deliver the tablet to the tribunes before dark. So that if all those issued are returned, the tribune knows that the watchword has been given to all the maniples, and has passed through all on its way back to him. If any one of them is missing, he makes inquiry at once, as he knows by the marks from what quarter the tablet has not returned, and whoever is responsible for the stoppage meets with the punishment he merits. Passwords in military use evolved to include not just a password, but a password and a counterpassword; for example in the opening days of the Battle of Normandy, paratroopers of the U.S. 101st Airborne Division used a password—flash—which was presented as a challenge, and answered with the correct response—thunder. The challenge and response were changed every three days. American paratroopers also famously used a device known as a "cricket" on D-Day in place of a password system as a temporarily unique method of identification; one metallic click given by the device in lieu of a password was to be met by two clicks in reply. Passwords have been used with computers since the earliest days of computing. The Compatible Time-Sharing System (CTSS), an operating system introduced at MIT in 1961, was the first computer system to implement password login. CTSS had a LOGIN command that requested a user password.
"After typing PASSWORD, the system turns off the printing mechanism, if possible, so that the user may type in his password with privacy." In the early 1970s, Robert Morris developed a system of storing login passwords in a hashed form as part of the Unix operating system. The system was based on a simulated Hagelin rotor crypto machine, and first appeared in 6th Edition Unix in 1974. A later version of his algorithm, known as crypt(3), used a 12-bit salt and invoked a modified form of the DES algorithm 25 times to reduce the risk of pre-computed dictionary attacks. In modern times, user names and passwords are commonly used by people during a log in process that controls access to protected computer operating systems, mobile phones, cable TV decoders, automated teller machines (ATMs), etc. A typical computer user has passwords for multiple purposes: logging into accounts, retrieving e-mail, accessing applications, databases, networks, websites, and even reading the morning newspaper online.
The name of a pet, child, family member, or significant other Anniversary dates and birthdays Birthplace Name of a favorite holiday Something related to a favorite sports team The word "password" The security of a password-protected system depends on several factors. The overall system must be designed for sound security, with protection against computer viruses, man-in-the-middle attacks and the like. Physical security issues are also a concern, from deterring shoulder surfing to more sophisticated physical threats such as video cameras and keyboard sniffers.
Passwords should be chosen so that they are hard for an attacker to guess and hard for an attacker to discover using any of the available automatic attack schemes. Nowadays, it is a common practice for computer systems to hide passwords as they are typed. The purpose of this measure is to prevent bystanders from reading the password; however, some argue that this practice may lead to mistakes and stress, encouraging users to choose weak passwords. As an alternative, users should have the option to show or hide passwords as they type them. Effective access control provisions may force extreme measures on criminals seeking to acquire a password or biometric token. Less extreme measures include extortion, rubber hose cryptanalysis, and side channel attack. Some specific password management issues that must be considered when thinking about, choosing, and handling a password follow.
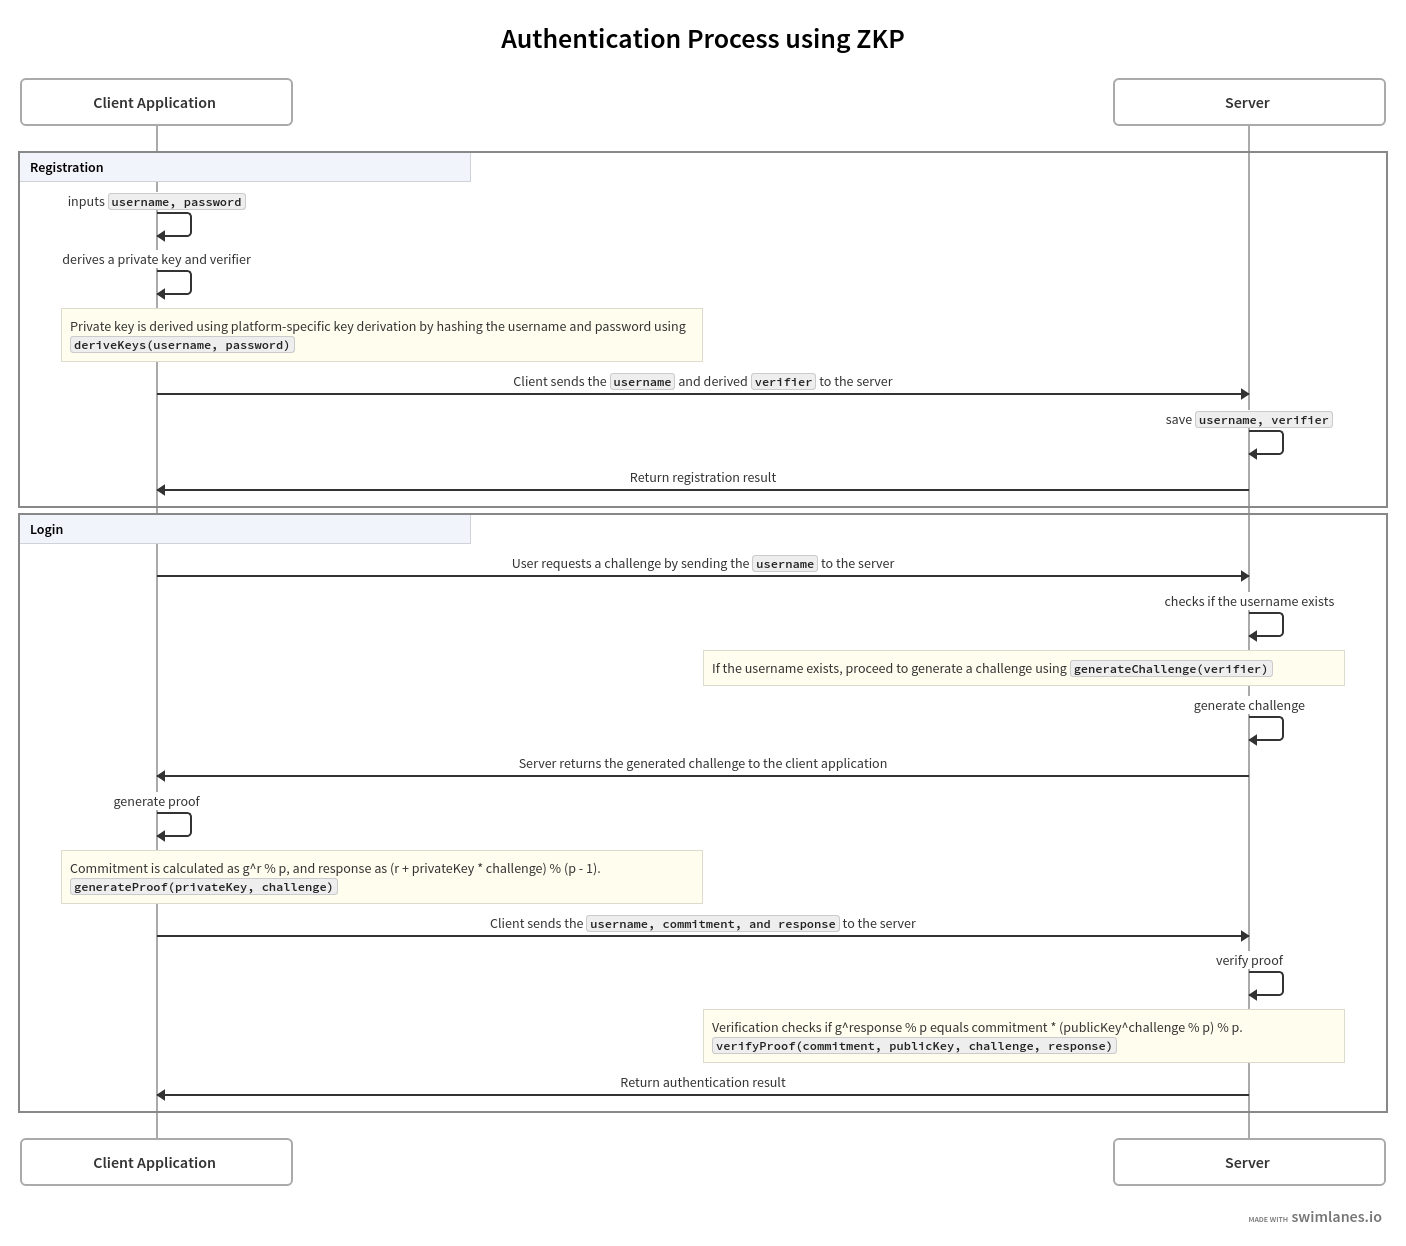
Figure 1: Zero-Knowledge Proof Authentication The risk of interception of passwords sent over the Internet can be reduced by, among other approaches, using cryptographic protection. The most widely used is the Transport Layer Security (TLS, previously called SSL) feature built into most current Internet browsers. Most browsers alert the user of a TLS/SSL-protected exchange with a server by displaying a closed lock icon, or some other sign, when TLS is in use. There are several other techniques in use.
Usually, a system must provide a way to change a password, either because a user believes the current password has been (or might have been) compromised, or as a precautionary measure. If a new password is passed to the system in unencrypted form, security can be lost (e.g., via wiretapping) before the new password can even be installed in the password database and if the new password is given to a compromised employee, little is gained. Some websites include the user-selected password in an unencrypted confirmation e-mail message, with the obvious increased vulnerability. Identity management systems are increasingly used to automate the issuance of replacements for lost passwords, a feature called self-service password reset.
The user's identity is verified by asking questions and comparing the answers to ones previously stored (i.e., when the account was opened). Some password reset questions ask for personal information that could be found on social media, such as mother's maiden name. As a result, some security experts recommend either making up one's own questions or giving false answers.
Not displaying the password on the display screen as it is being entered or obscuring it as it is typed by using asterisks (*) or bullets (•). Allowing passwords of adequate length. (Some legacy operating systems, including early versions of Unix and Windows, limited passwords to an 8 character maximum, reducing security.) Requiring users to re-enter their password after a period of inactivity (a semi log-off policy). Enforcing a password policy to increase password strength and security. Assigning randomly chosen passwords. Requiring minimum password lengths. Some systems require characters from various character classes in a password—for example, "must have at least one uppercase and at least one lowercase letter". However, all-lowercase passwords are more secure per keystroke than mixed capitalization passwords. Employ a password blacklist to block the use of weak, easily guessed passwords Providing an alternative to keyboard entry (e.g., spoken passwords, or biometric identifiers). Requiring more than one authentication system, such as two-factor authentication (something a user has and something the user knows). Using encrypted tunnels or password-authenticated key agreement to prevent access to transmitted passwords via network attacks Limiting the number of allowed failures within a given time period (to prevent repeated password guessing). After the limit is reached, further attempts will fail (including correct password attempts) until the beginning of the next time period. However, this is vulnerable to a form of denial of service attack. Introducing a delay between password submission attempts to slow down automated password guessing programs. Some of the more stringent policy enforcement measures can pose a risk of alienating users, possibly decreasing security as a result.
Multi-factor authentication schemes combine passwords (as "knowledge factors") with one or more other means of authentication to make authentication more secure and less vulnerable to compromised passwords. For example, a simple two-factor login might send a text message, e-mail, automated phone call, or similar alert whenever a login attempt is made, possibly supplying a code that must be entered in addition to a password. More sophisticated factors include such things as hardware tokens and biometric security.
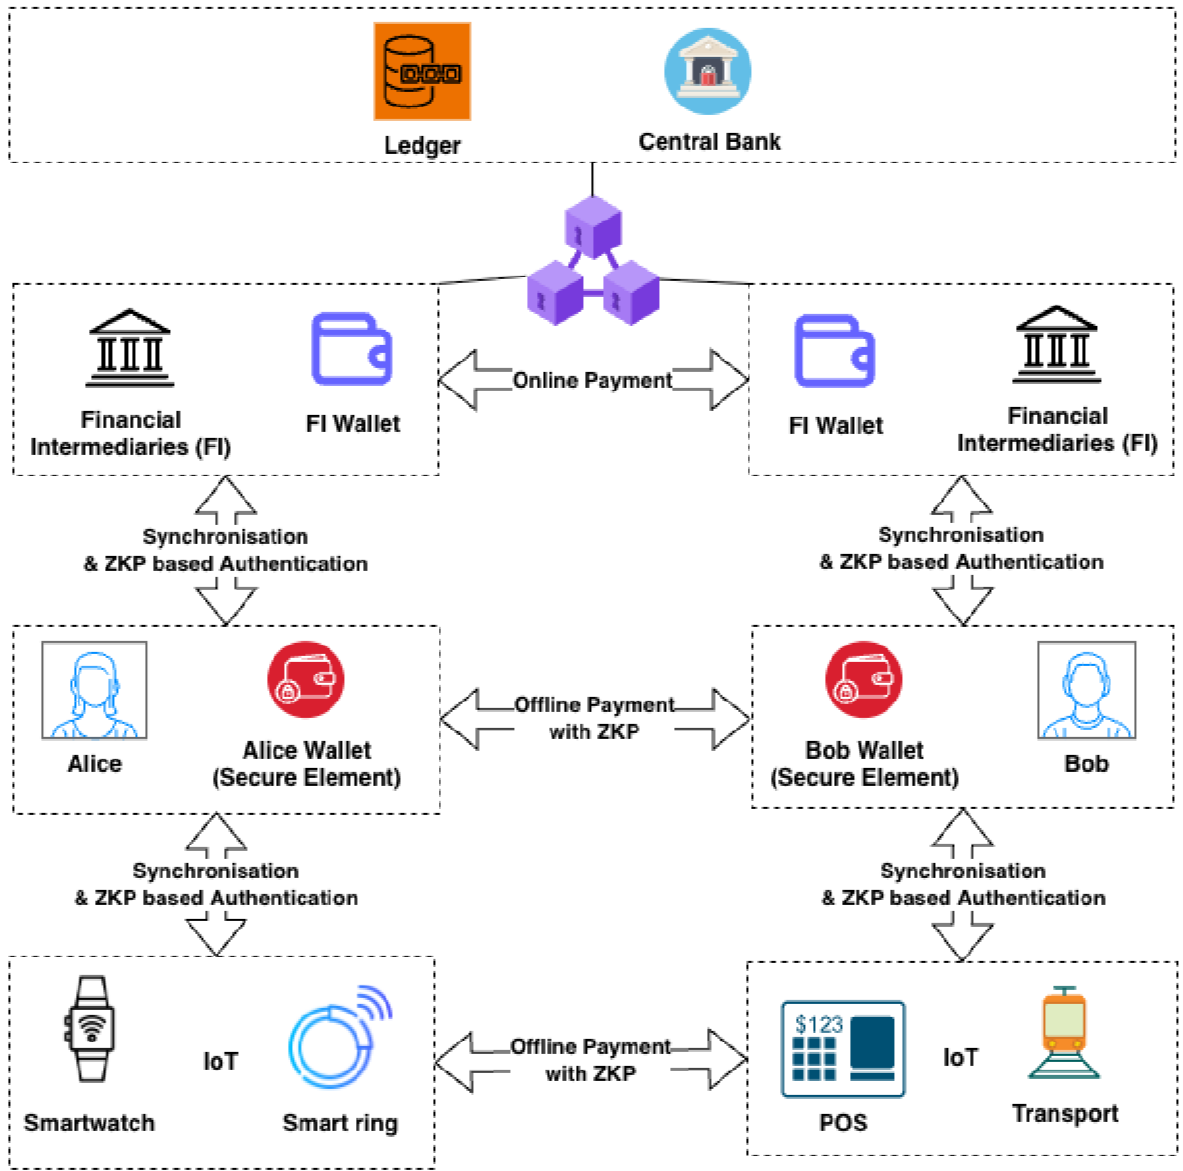
Figure 2: [II II] Zero-Knowledge Proof (ZKP) Authentication for Offline CBDC ... Most organizations specify a password policy that sets requirements for the composition and usage of passwords, typically dictating minimum length, required categories (e.g., upper and lower case, numbers, and special characters), and prohibited elements (e.g., use of one's own name, date of birth, address, telephone number). Some governments have national authentication frameworks that define requirements for user authentication to government services, including requirements for passwords. Many websites enforce standard rules such as minimum and maximum length, but also frequently include composition rules such as featuring at least one capital letter and at least one number/symbol. These latter, more specific rules were largely based on a 2003 report by the National Institute of Standards and Technology (NIST), authored by Bill Burr.
It originally proposed the practice of using numbers, obscure characters and capital letters and updating regularly. In a 2017 article in The Wall Street Journal, Burr reported he regrets these proposals and made a mistake when he recommended them. According to a 2017 rewrite of this NIST report, a number of websites have rules that actually have the opposite effect on the security of their users. This includes complex composition rules as well as forced password changes after certain periods of time. While these rules have long been widespread, they have also long been seen as annoying and ineffective by both users and cybersecurity experts. The NIST recommends people use longer phrases as passwords (and advises websites to raise the maximum password length) instead of hard-to-remember passwords with "illusory complexity" such as "pA55w+rd". A user prevented from using the password "password" may, if required to include a number and uppercase letter, simply choose "Password1". Combined with forced periodic password changes, this can lead to passwords that are difficult to remember but easy to crack. Paul Grassi, one of the 2017 NIST report's authors, further elaborated: "Everyone knows that an exclamation point is a 1, or an I, or the last character of a password. $ is an S or a 5. If we use these well-known tricks, we aren't fooling any adversary. We are simply fooling the database that stores passwords into thinking the user did something good." Pieris Tsokkis and Eliana Stavrou were able to identify some bad password construction strategies through their research and development of a password generator tool. They came up with eight categories of password construction strategies based on exposed password lists, password cracking tools, and online reports citing the most used passwords. These categories include user-related information, keyboard combinations and patterns, placement strategy, word processing, substitution, capitalization, append dates, and a combination of the previous categories.
Attempting to crack passwords by trying as many possibilities as time and money permit is a brute-force attack. A related method, rather more efficient in most cases, is a dictionary attack. In a dictionary attack, all words in one or more dictionaries are tested. Lists of common passwords are also typically tested. Password strength is the likelihood that a password cannot be guessed or discovered, and varies with the attack algorithm used. Cryptologists and computer scientists often refer to the strength or 'hardness' in terms of entropy. Passwords easily discovered are termed weak or vulnerable; passwords difficult or impossible to discover are considered strong. There are several programs available for password attack (or even auditing and recovery by systems personnel) such as L0phtCrack, John the Ripper, and Cain; some of which use password design vulnerabilities (as found in the Microsoft LANManager system) to increase efficiency. These programs are sometimes used by system administrators to detect weak passwords proposed by users. Studies of production computer systems have consistently shown that a large fraction of all user-chosen passwords are readily guessed automatically. For example, Columbia University found 22% of user passwords could be recovered with little effort. According to Bruce Schneier, examining data from a 2006 phishing attack, 55% of MySpace passwords would be crackable in 8 hours using a commercially available Password Recovery Toolkit capable of testing 200,000 passwords per second in 2006. He also reported that the single most common password was password1, confirming yet again the general lack of informed care in choosing passwords among users. (He nevertheless maintained, based on these data, that the general quality of passwords has improved over the years—for example, average length was up to eight characters from under seven in previous surveys, and less than 4% were dictionary words.) Single-use passwords. Having passwords that are only valid once makes a number of potential attacks ineffective. Most users find single-use passwords extremely inconvenient. They have, however, been widely implemented in personal online banking, where they are known as Transaction Authentication Numbers (TANs). As most home users only perform a small number of transactions each week, the single-use issue has not led to intolerable customer dissatisfaction in this case.
Time-synchronized one-time passwords are similar in some ways to single-use passwords, but the value to be entered is displayed on a small (generally pocketable) item and changes every minute or so. Passwordless authentication in which a user can log in to a computer system without entering (and having to remember) a password or any other knowledge-based secret. In most common implementations users are asked to enter their public identifier (username, phone number, email address etc.) and then complete the authentication process by providing a secure proof of identity through a registered device or token. Most of implementations rely on public-key cryptography infrastructure where the public key is provided during registration to the authenticating service (remote server, application or website) while the private key is kept on a user's device (PC, smartphone or an external security token) and can be accessed only by providing a biometric signature or another authentication factor which is not knowledge-based. PassWindow one-time passwords are used as single-use passwords, but the dynamic characters to be entered are visible only when a user superimposes a unique printed visual key over a server-generated challenge image shown on the user's screen. Access controls based on public-key cryptography e.g. ssh.
The necessary keys are usually too large to memorize (but see proposal Passmaze) and must be stored on a local computer, security token or portable memory device, such as a USB flash drive or even floppy disk. The private key may be stored on a cloud service provider, and activated by the use of a password or two-factor authentication. Biometric methods promise authentication based on unalterable personal characteristics, but as of 2008 have high error rates and require additional hardware to scan, for example, fingerprints, irises, etc. They have proven easy to spoof in some famous incidents testing commercially available systems, for example, the gummie fingerprint spoof demonstration, and, because these characteristics are unalterable, they cannot be changed if compromised; this is a highly important consideration in access control as a compromised access token is necessarily insecure. Single sign-on technology is claimed to eliminate the need for having multiple passwords. Such schemes do not relieve users and administrators from choosing reasonable single passwords, nor system designers or administrators from ensuring that private access control information passed among systems enabling single sign-on is secure against attack. As yet, no satisfactory standard has been developed. Envaulting technology is a password-free way to secure data on removable storage devices such as USB flash drives. Instead of user passwords, access control is based on the user's access to a network resource. Non-text-based passwords, such as graphical passwords or mouse-movement based passwords. Graphical passwords are an alternative means of authentication for log-in intended to be used in place of conventional password; they use images, graphics or colours instead of letters, digits or special characters. One system requires users to select a series of faces as a password, utilizing the human brain's ability to recall faces easily. In some implementations the user is required to pick from a series of images in the correct sequence to gain access. Another graphical password solution creates a one-time password using a randomly generated grid of images. Each time the user is required to authenticate, they look for the images that fit their pre-chosen categories and enter the randomly generated alphanumeric character that appears in the image to form the one-time password. So far, graphical passwords are promising, but are not widely used. Studies on this subject have been made to determine their usability in the real world. While some believe that graphical passwords would be harder to crack, others suggest that people will be just as likely to pick common images or sequences as they are to pick common passwords. 2D Key (2-Dimensional Key) is a 2D matrix-like key input method having the key styles of multiline passphrase, crossword, ASCII/Unicode art, with optional textual semantic noises, to create big password/key beyond 128 bits to realize the MePKC (Memorizable Public-Key Cryptography) using fully memorizable private key upon the current private key management technologies like encrypted private key, split private key, and roaming private key. Cognitive passwords use question and answer cue/response pairs to verify identity.
"The password is dead" is a recurring idea in computer security. The reasons given often include reference to the usability as well as security problems of passwords. It often accompanies arguments that the replacement of passwords by a more secure means of authentication is both necessary and imminent. This claim has been made by a number of people at least since 2004. Alternatives to passwords include biometrics, two-factor authentication or single sign-on, Microsoft's Cardspace, the Higgins project, the Liberty Alliance, NSTIC, the FIDO Alliance and various Identity 2.0 proposals. Bonneau et al.
systematically compared web passwords to other technical solutions that were alternatives. They reviewed these in respect of usability, deployability, and security. Their analysis showed that most alternatives do better than passwords on security, some do better and some worse with respect to usability, while every alternative does worse than passwords on deployability. This may be why over 20 years after this recurring idea started, passwords are still being used, despite attempts by technology businesses to change this. Some that highlight this, suggest that the problem is generally not with the system of using passwords and is instead an issue with how humans use and manage their passwords and that "in the age of disparate workforces, home WiFi networks and multiple devices, password use has continued to increase".
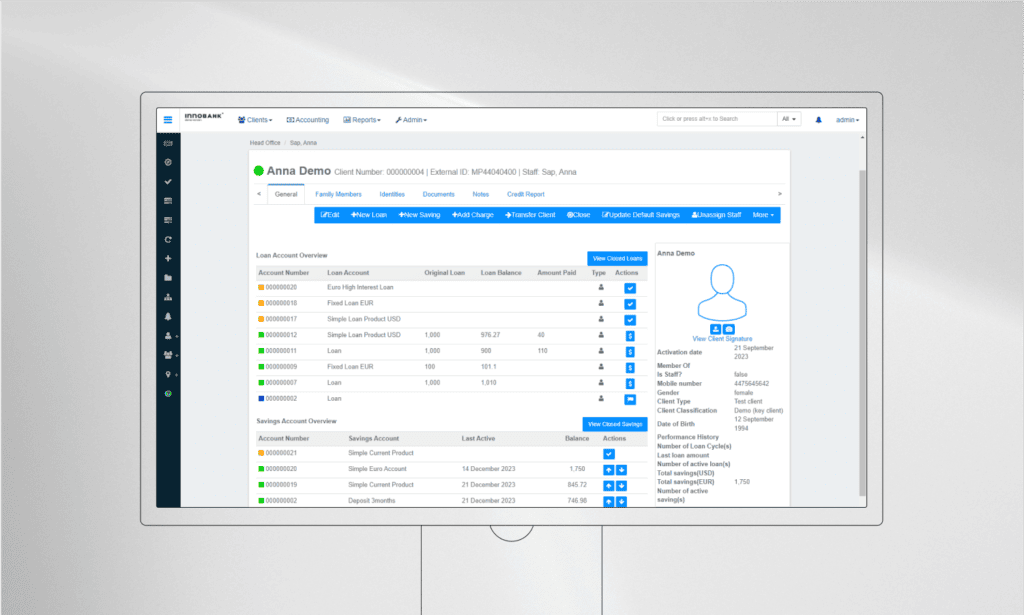
Figure 3: Core Banking System Implementation | Innowise In cryptography, a key-agreement protocol is a protocol whereby two (or more) parties generate a cryptographic key as a function of information provided by each honest party so that no party can predetermine the resulting value. In particular, all honest participants influence the outcome. A key-agreement protocol is a specialisation of a key-exchange protocol. At the completion of the protocol, all parties share the same key. A key-agreement protocol precludes undesired third parties from forcing a key choice on the agreeing parties. A secure key agreement can ensure confidentiality and data integrity in communications systems, ranging from simple messaging applications to complex banking transactions. Secure agreement is defined relative to a security model, for example the Universal Model. More generally, when evaluating protocols, it is important to state security goals and the security model. For example, it may be required for the session key to be authenticated. A protocol can be evaluated for success only in the context of its goals and attack model. An example of an adversarial model is the Dolev–Yao model. In many key exchange systems, one party generates the key, and sends that key to the other party; the other party has no influence on the key.
whether a pre-shared key already exists or not the method of generating the session key. The pre-shared key may be shared between the two parties, or each party may share a key with a trusted third party. If there is no secure channel (as may be established via a pre-shared key), it is impossible to create an authenticated session key. The session key may be generated via: key transport, key agreement and hybrid. If there is no trusted third party, then the cases of key transport and hybrid session key generation are indistinguishable. SKA is concerned with protocols in which the session key is established using only symmetric primitives.
Anonymous key exchange, like Diffie–Hellman, does not provide authentication of the parties, and is thus vulnerable to man-in-the-middle attacks. A wide variety of cryptographic authentication schemes and protocols have been developed to provide authenticated key agreement to prevent man-in-the-middle and related attacks. These methods generally mathematically bind the agreed key to other agreed-upon data, such as the following: Department of Artificial Intelligence & Machine Learning Dilkap Research Institute of Engineering & Management Studies Mamdapur, Neral, Karjat, Raigad 410101, Maharashtra, India
Abstract
Traditional banking systems rely on passwords, PINs, and centralized biometric storage, exposing users to phishing, SIM-swap attacks, and credential reuse vulnerabilities. This paper presents the ZKP Banking Interface, a pinless, context-aware financial authentication system built on Zero-Knowledge Proof (ZKP) technology. A unified ZK-SNARK circuit (Grotp6), implemented in Circom, encodes three simultaneous security factors: identity commitment, trusted network context, and transaction threshold logic using Poseidon hashing. Conditional biometric and puzzle challenges are enforced cryptographically for higher-risk scenarios.
Abstract Art
Proof generation and verification are fully automated within the browser using snarkJS and WebAssembly artifacts, eliminating manual proof handling. The system supports two verification modes: local (device-only privacy) and on-chain (public auditability via a Solidity smart contract on a Hardhat network). Experimental evaluation across five test scenarios confirms correct contextual policy enforcement, successful proof validation in both modes, and a smooth, practical banking user experience. The proposed system demonstrates that ZKP-based authentication can replace traditional credentials while maintaining strong privacy guarantees.
Abstract Definition
Keywords- Zero-Knowledge Proofs; Privacy-Preserving Banking; ZK-SNARKs; Grotp6; On-chain Verification; Smart Contracts; Circom; Context-Aware Security; Poseidon Hash; snarkJS Financial applications increasingly require authentication systems that are both secure and frictionless. Conventional methods such as passwords, PINs, OTPs, and static biometrics expose users to phishing, replay attacks, and credential theft, while simultaneously degrading user experience [1], [2].
Abstraction
Zero-Knowledge Proofs (ZKPs) offer a cryptographic alternative that allows a user to prove possession of a secret without revealing the secret itself. Applied to banking, ZKPs can enable a pinless, context-aware interface that verifies identity and transaction authorization while fully preserving user privacy. The proposed ZKP Banking Interface combines three independent security signals: identity, network context, and transaction threshold into a single Grotp6 proof. The circuit, implemented in Circom [3], uses Poseidon hashing to bind private inputs to public commitments. Private values never leave the device; only cryptographic proofs are transmitted.
Abstraction Tadc
Conditional logic within the circuit enforces adaptive security: untrusted networks trigger biometric verification; high-value transactions require a puzzle challenge. This yields a layered The system operates in two verification modes: (i) local mode, where the proof is verified in the client browser using snarkJS The ZKP Banking Interface comprises three cooperating layers, as shown in Fig. 1. The Frontend Interface (React + TypeScript) handles proof generation, local secret storage, and conditional authentication prompts.
Abstract Meaning
The ZKP Circuit (Circom, Grotp6) encodes identity commitment, trusted network context, and transaction threshold policy as cryptographic constraints. The Smart Contract (Solidity, Hardhat) stores public commitments and verifies proofs on-chain when the user selects on-chain verification mode. The core privacy guarantee is that private inputs : identity secret, biometric phrase, puzzle answer, and network ID never leave the user's device.
Abstract Noun
Only Poseidon hash commitments and the proof tuple (a, b, c) are ever transmitted, whether to localStorage in local mode or to the blockchain in on-chain mode. Fig. 2 shows the detailed interaction between components during a proof lifecycle. The user triggers a transaction from the frontend. The Circom circuit processes private and public inputs via snarkJS and WASM artifacts to produce a Grotp6 proof.
Abstract Painting
In local mode, the proof is verified in-browser. In on-chain mode, the proof and public signals are submitted via MetaMask to the ZKPBank smart contract on the Hardhat network, which validates the proof and emits a TransactionAuthorized event. 2. System Architecture & Core Working Principles The flowchart in Fig. 3 captures every decision point in the ZKP authentication pipeline.
Abstract Expressionism
It shows the two orthogonal risk signals evaluated simultaneously: network trust status and transaction amount versus the user-defined spending threshold. Step 2- Load Secrets: Identity secret, trusted network ID, biometric commitment, and puzzle commitment are loaded. If absent, the user is sent to the Security Center for enrollment. Step 3- Input Amount: User enters transaction amount and recipient address.
Abstracted Jax
Step 4- Network Check: Current network ID is hashed and compared to the trusted network hash. Step 5- Biometric Prompt: If network is untrusted, the user must supply their biometric passphrase; the frontend hashes it and passes it as a private circuit input. Step 8- Generate Proof: snarkjs.grotp6.fullProve() is invoked in-browser using WASM and ZKey artifacts.
Step 9- Verify Proof: Local mode verifies in-browser; on- chain mode submits proof to ZKPBank via MetaMask. Step 10- Update Dashboard: Context Halo, balance, and activity log are updated with result. The interface consists of seven screens across three navigation tabs: Dashboard, Activity, and Security Center. A Pre- Transaction Setup modal handles first-time onboarding. Screens are documented below in the order a user encounters them.
The enrollment modal (Fig. 4) is shown automatically on first launch or when any required context is missing. It captures: Trusted Network ID, the current network's simulated BSSID hash, scanned via Rescan Network; Biometric Enrollment a user passphrase that is keccak256- hashed locally and stored as biometricCommitment; the raw passphrase is discarded immediately. Status badges (Wallet / Network / Biometric / Puzzle / Threshold / Crypto) must all be active before the user can continue to the dashboard. The error state Blocking: wallet is shown when MetaMask is not yet connected.
The main dashboard (Fig. 5) is the primary interface for initiating transactions. It contains four panels. The Balance Overview (top left) shows on-chain ETH balance with mode, network, and threshold badges. The Send Funds panel (top right) accepts verification mode selection, recipient address, and transaction amount; the Generate Proof and Execute button triggers the full proof pipeline.
The Context Halo (bottom left) is a large circular visual indicator blue for TRUSTED, orange for UNTRUSTED that provides immediate security context feedback. The Account Status panel (bottom right) shows wallet address, biometric status, active network label, and wallet connection state.
The Secure Context Ready badge in the header confirms all five commitments are registered and ready. Local Proof (no blockchain) verifies entirely in-browser, requires no wallet, and incurs no gas cost this mode demonstrates pure device-side privacy. On-Chain Verification submits the proof to the ZKPBank smart contract, providing public auditability. Both modes use the identical Circom circuit; only the verification destination differs. When a transaction amount exceeding the spending threshold is entered, the status badge below the button immediately updates to High-Value Mode and queues the puzzle prompt.
In on-chain mode, after the proof is generated in-browser, MetaMask presents a transaction request (Fig. 7). The request shows: Network = Hardhat Local; Request from localhost:5173; Interacting with the ZKPBank contract address. The network fee (~$0.94 in test ETH) is the gas cost for the on-chain verifyProof call. The proof tuple (a, b, c) and public commitments are what get submitted not the identity secret, biometric phrase, or puzzle answer.
After successful on-chain verification (Fig. 8), the UI displays a success toast in the top-right corner: Profile Registered On-chain context is active, with the full transaction hash for external auditing. The balance is updated to reflect gas consumed. Dashboard badges confirm Mode: On-Chain, Network: trusted, and the current threshold.
If verification fails due to an incorrect biometric or puzzle input, a failure toast is shown and no gas is consumed, since the proof is rejected before submission. The Activity tab (Fig. 9) is a read-only audit ledger stored in localStorage. Each entry records the transaction amount (ETH), verification mode (chain or local), network state (trusted or untrusted), and timestamp. On-chain entries include the full transaction hash prefixed On-chain proof verified: 0x… No private data is stored in this log, only public proof receipts and transaction metadata.
The Security Center (Fig. 10) configures all device-bound secrets and context parameters used by the ZKP circuit. It allows the user to: switch verification mode; view and rescan the Trusted Network ID; use Network Simulation controls (Force Trusted, Force Untrusted, Auto Flip which alternates every 90 seconds for live demonstrations); re-enroll the biometric passphrase; and set the spending threshold in ETH.
Register On-Chain Context calls ZKPBank.registerUser() with all five public commitments. Table I summarises the five test scenarios used to validate contextual policy enforcement. Each scenario tests a distinct combination of network trust, transaction amount, and biometric correctness, confirming that the ZKP circuit enforces the correct adaptive policy independently of any UI- level logic.
Scenario E confirms that supplying an incorrect biometric passphrase violates the circuit constraint Poseidon(biometricSecret) == biometricCommitment. The snarkJS witness generation fails, no proof is produced, and the activity log records a rejected entry. No blockchain transaction is submitted and no gas is consumed. Table II maps every data item in the system to its storage location and whether it is ever transmitted. This table provides the evidential basis for the privacy claims made in the primary research paper.
3. Software Implementation, Frameworks & Protocols Table III lists all named UI components, their function, and the security behaviour they surface to the user. Blue = trusted network (no biometric required). Orange = untrusted (biometric required). Updates in real-time. Triggers the full proof pipeline: input collection, snarkjs.grotp6.fullProve(), then verification.
Amount threshold. No puzzle required. Biometric may still apply if network is untrusted. Untrusted network biometric passphrase must be entered; wrong input causes proof failure. All five commitments (identity, network, biometric, puzzle, threshold) are registered. Re-reads the current simulated BSSID and updates trusted network hash in localStorage.
Alternates network trust state every 90 seconds used in live demos of adaptive biometric triggering. This paper presented the ZKP Banking Interface, a pinless, context-aware banking authentication system built on Zero- Knowledge Proofs. The system verifies identity and transaction authorization without exposing private data, combining identity commitments, trusted network context, biometric confirmation, and transaction threshold logic in a single Grotp6 ZK-SNARK circuit. Proof generation and verification are fully automated in the browser, and dual verification modes offer both privacy-first local operation and publicly auditable on-chain validation.
Experimental results confirmed correct enforcement of all contextual security policies across five test scenarios, successful proof validation in both modes, and a smooth, intuitive user experience. The system demonstrates that ZKP- based authentication is a practical and viable alternative to traditional PIN/OTP workflows for financial applications. Future work directions include: (1) integration of AI-driven behavioral biometricstyping rhythm, mouse dynamics, and interaction patternsto generate additional trust signals; (2) hardware secure enclave support for storing secrets with device attestation; (3) Layer-2 deployment for reduced gas costs and faster on-chain confirmation; (4) real biometric API integration with liveness detection; and (5) federated learning models for behavioral baselines that preserve user privacy. These enhancements would advance the system toward a production-ready, multi-modal, privacy-preserving financial authentication platform.
We sincerely thank Prof. Akshata Laddha (Project Guide) and Prof. Amit Chakrawarti (Head of Department, AI & ML) for their continuous guidance and support. Gratitude is also extended to the developers of Circom, snarkJS, and the Ethereum ecosystem for providing the foundational open- source technologies that made this work possible. A. J. Menezes, P. C. van Oorschot, and S. A. Vanstone, Handbook of Applied Cryptography. Boca Raton, FL: CRC Press, 1996.
iden3, "Circom: A Circuit Compiler for ZK-SNARKs," GitHub Repository, 2022.
[Online]. Available: https://github.com/iden3/circom iden3, "snarkJS: JavaScript ZK-SNARK Library," GitHub Repository, 2022.
[Online]. Available: https://github.com/iden3/snarkjs A. K. Jain, A. Ross, and S. Prabhakar, "An introduction to biometric recognition," IEEE Trans. Circuits Syst. Video Technol., A. Das and N. Borisov, "Tracking the trackers: Measuring intrusiveness of web tracking," Proc. NDSS, 2019.
S. Nakamoto, "Bitcoin: A Peer-to-Peer Electronic Cash System," 2008. [Online]. Available: https://bitcoin.org/bitcoin.pdf J. Groth, "On the size of pairing-based non-interactive arguments," in Proc. Eurocrypt, 2016, pp. 305326. E. Ben-Sasson et al., "Zerocash: Decentralized anonymous payments from Bitcoin," in Proc. IEEE Symp. Security and Privacy, 2014, pp. 459474.
C. Garman, M. Green, and I. Miers, "Accountable privacy for decentralized anonymous payments," in Proc. Financial Cryptography, 2015. 21142132, 2018. This guide details an architecture where users perform KYC once with a trusted issuer and can then generate ZK proofs of their status to multiple service providers. It covers credential issuance, proof standardization (e.g., W3C VC-DM), revocation mechanisms, and maintaining audit trails for regulators. Integration with existing compliance databases is discussed.
Zero-knowledge proofs enable identity verification without exposing sensitive user data. This guide explains the core architecture for building a ZK-based KYC/AML system. Traditional KYC (Know Your Customer) and AML (Anti-Money Laundering) processes require users to submit sensitive personal documents—passports, driver's licenses, bank statements—to a centralized authority. This creates significant privacy risks and single points of failure. A zero-knowledge proof (ZKP) based architecture flips this model. Instead of sharing raw data, a user cryptographically proves they possess verified credentials that satisfy specific compliance rules, without revealing the credentials themselves. This enables privacy-preserving access to financial services and on-chain applications.
The core components of a ZK KYC system are the Issuer , Holder , and Verifier . The Issuer is a trusted entity (like a regulated bank or KYC provider) that attests to a user's identity. They issue a verifiable credential (VC) , a cryptographically signed statement containing claims (e.g., "is over 18", "country of residence"). The Holder (the user) stores this credential in a secure digital wallet. The Verifier (e.g., a DeFi protocol) requests proof that the Holder meets certain criteria. The Holder uses a ZK circuit to generate a proof from their VC, which the Verifier can check without learning any underlying data.
The technical heart of the system is the ZK circuit . Written in a domain-specific language like Circom or Noir , this circuit encodes the compliance logic. For example, a circuit could prove a user's birth date is before a certain threshold (proving age >= 18) or that their jurisdiction is not on a sanctions list, using only the hashed commitments from their VC. Popular libraries for implementing this include Semaphore for anonymous signaling and zkEmail for verifying information from email headers.
The proof is then verified on-chain by a smart contract, granting access. A critical design choice is the identity model . Systems can be built on semaphore-style group membership , where verified users join a Merkle tree and prove membership anonymously. Alternatively, they can use Sparse Merkle Trees (SMTs) for more granular, revocable credentials. Another key consideration is selective disclosure , allowing users to reveal only specific attributes (e.g., just their country, not their full ID number) while still proving the credential's validity. This is often implemented using BBS+ signatures or zk-SNARKs with predicate proofs .
For developers, the workflow involves: 1) Designing the credential schema and compliance rules, 2) Implementing the ZK circuit logic, 3) Creating issuer and verifier smart contracts (commonly on Ethereum , Polygon zkEVM , or zkSync Era ), and 4) Building the user wallet interface for proof generation. Off-chain components, like an issuer backend for credential signing and a proof relay to pay gas fees for users, are also essential. The goal is to create a seamless flow where compliance is a frictionless, private background check.
Before building a zero-knowledge KYC/AML system, you need a solid foundation in cryptography, smart contract development, and regulatory frameworks. 4. Practical Deployment, Analysis & Case Studies A zero-knowledge KYC/AML solution requires expertise in three core domains: cryptography , blockchain development , and compliance . You must understand the cryptographic primitives that make ZK proofs possible, such as zk-SNARKs (e.g., Groth16, Plonk) or zk-STARKs. Familiarity with elliptic curve pairings, hash functions, and commitment schemes is essential.
For development, proficiency in a ZK framework like Circom (for circuit design), SnarkJS (for proof generation), or StarkWare's Cairo is required. You'll also need experience with a smart contract language like Solidity to implement the verification logic on-chain. The system's architecture dictates its technical requirements. A typical ZK-KYC system involves an Issuer (a regulated entity that verifies user identity), a User (who generates a ZK proof of their verified status), and a Verifier (a dApp or service that checks the proof). The issuer runs a backend service to manage identity credentials, often using the W3C Verifiable Credentials data model. The user's client, likely a wallet, must have a ZK proving library integrated. The verifier is a smart contract with a verifyProof function. High computational resources are needed for the prover (user side) and gas-efficient verification is critical for the verifier contract.
You must define the precise compliance logic to encode into the ZK circuit. This involves mapping regulatory rules to programmable constraints. For example, a circuit could prove a user is over 18 without revealing their birthdate: circuit.isAdult = (today - birthDate) > 18 years . For AML, you might prove a user's jurisdiction is not on a sanctions list by having the issuer sign a credential for an approved country code, and the circuit proves knowledge of a valid signature for a code not in a banned set. These rules must be meticulously specified and audited, as the circuit becomes the immutable source of compliance truth.
Key development tools and libraries form the practical prerequisite stack. For Ethereum-based systems, use Circom 2.x and SnarkJS for circuit compilation and proof management. The circomlib library provides standard circuit templates. For testing, a local development network like Hardhat or Foundry is necessary to simulate on-chain verification. You will need to manage trusted setup ceremonies for zk-SNARK systems or configure a STARK prover. Understanding how to use IPFS or Ceramic for decentralized credential storage, and OAuth or SIWE (Sign-In with Ethereum) for initial authentication, rounds out the technical toolkit.
Finally, non-technical requirements are equally critical. You must establish legal frameworks with qualified issuers who can perform KYC checks under regulations like Travel Rule (FATF Recommendation 16) or MiCA . Data privacy laws like GDPR dictate how personal data is handled off-chain. The system design must incorporate revocation mechanisms for compromised credentials and consider upgrade paths for changing regulations. A successful ZK-KYC solution is not just a cryptographic protocol; it's a blend of robust code, secure infrastructure, and legally sound operational procedures.
Building a zero-knowledge KYC/AML solution requires integrating several key components to verify identity privately. This guide covers the essential building blocks for developers. This is the foundational component where a trusted entity (e.g., a licensed KYC provider) cryptographically attests to a user's verified identity. The attestation, often a signed credential or verifiable credential (VC) , contains claims like country of residence and age without revealing raw PII. Standards like W3C Verifiable Credentials or Iden3's core protocol provide the data model. The issuer's public key must be known and trusted by the verifying smart contract or service.
The core logic of the system is encoded in an arithmetic circuit. This circuit defines the proof statement: "I possess a valid credential from a trusted issuer, and the revealed data (e.g., 'over 18') is true, without showing the credential itself." Key design considerations include: Users generate a zero-knowledge proof (ZKP) locally using their private credential and the circuit. This proof cryptographically demonstrates the statement is true. Common proof systems include Groth16 , PLONK , or STARKs . The verification key and proof are then submitted on-chain. A verifier smart contract , which holds the trusted issuer's public key and verification key, can check the proof in a gas-efficient manner (often < 500k gas). This step enables trustless, automated compliance checks without exposing user data.
To go beyond binary checks, systems can compute a risk score or reputation without exposing underlying transaction history. This can be done using zk-SNARKs or zk-SNARKs to prove properties about private data sets. For example, proving that a user's total transaction volume over the last 30 days is below a threshold, or that no transactions were with sanctioned addresses, without revealing individual transactions. This requires designing circuits that aggregate private data according to compliance rules.
The user-facing application must securely manage private keys and credentials. This is typically a browser extension or mobile wallet that can: The first step in building a zero-knowledge KYC/AML system is defining the architecture for how credentials are issued, stored, and verified. This flow establishes trust and privacy.
A ZK KYC credential issuance flow begins when a user submits their identity documents (e.g., passport, driver's license) to a trusted Issuer . This entity, often a regulated compliance provider like Veriff or Onfido , performs the traditional verification checks. Their role is to cryptographically attest to specific user attributes—such as being over 18, a resident of a permitted jurisdiction, or not on a sanctions list—without revealing the underlying documents.
Once verified, the Issuer creates a verifiable credential (VC) . This is a signed data structure, often following the W3C VC Data Model , containing the attested claims. For a ZK system, this credential is then used as the private input to generate a zero-knowledge proof . The user's wallet (e.g., a browser extension or mobile app) runs a ZK circuit—a program defining the logic of the proof—to create a cryptographic proof that they possess a valid credential meeting certain criteria, without exposing the credential itself.
The core design decision is determining what claims are attested in the VC and encoded in the ZK circuit. You must balance regulatory requirements with user privacy. For example, a circuit could prove age >= 21 and country_code NOT IN [US-sanctioned countries] using only the hashes of the original data. The circuit is the single source of truth for what can be proven; changing logic requires redeploying it.
The issuance flow must also handle credential storage and key management . The VC and its associated private key material are stored securely on the user's device. Solutions like SpruceID's Kepler or Ceramic Network provide decentralized storage options where the user retains custody. The Issuer never sees the generated ZK proof, ensuring a privacy-preserving, user-centric model.
Finally, this design must integrate with the verification layer . The Issuer provides the public verification key for their circuit, and the verifying smart contract or service only needs this key and the proof. A well-designed flow results in a simple verification function, such as verifyProof(proof, verificationKey) → true/false , which can be executed on-chain with minimal gas cost, enabling private access to DeFi protocols or DAOs.
This step details how a user's client application generates a zero-knowledge proof to verify KYC/AML compliance without revealing the underlying sensitive data. After the user has submitted their identity documents to a trusted Issuer (e.g., a regulated financial institution) and received a signed ZK credential , the next step is proof generation. This occurs locally on the user's device using a ZK-SNARK or ZK-STARK proving system. The user's client—typically a web or mobile wallet—loads the credential and the specific circuit for the compliance rule they need to prove (e.g., "I am over 18" or "I am not on a sanctions list"). The circuit defines the computational logic that the proof will attest to.
The generation process requires the user to provide the necessary private inputs (witnesses) that satisfy the circuit's constraints. For an age-check circuit, the private input is the user's actual date of birth. The public inputs, known to the verifier, would be the current date and the minimum age threshold. The prover software cryptographically hashes the credential data, runs the computation defined by the circuit using these inputs, and generates a proof (often a few kilobytes in size). This proof cryptographically demonstrates that the user possesses a valid credential from a trusted issuer and that the hidden data within it satisfies the public rule.
Here is a simplified conceptual outline of the client-side code flow using a library like SnarkJS or Circom : Performance and user experience are critical considerations. Proof generation time and hardware requirements vary by circuit complexity. A simple age check may take 1-2 seconds in a browser, while a complex multi-rule check could take 10+ seconds. Optimizations include using WebAssembly for browsers, pre-fetching circuit artifacts, and employing recursive proofs to bundle multiple checks. The goal is to make this step nearly invisible to the end-user, ensuring the privacy-preserving verification does not come at the cost of usability.
Security in this step hinges on the integrity of the client-side code and the trusted setup of the circuit's proving/verification keys. Users must download the proving software and circuit files from a reputable source. Any compromise here could allow the generation of false proofs. Furthermore, the design must ensure that the private witness data (like the raw date of birth) is never transmitted or stored permanently after the proof is generated, adhering to the principle of data minimization .
Comparison of major zk-SNARK proof systems and associated circuit development frameworks for implementing KYC/AML logic. A functional ZK-KYC system must manage credential lifecycle and provide a transparent, immutable record of verification events for compliance.
Revocation is a critical mechanism for maintaining system integrity. When a user's KYC status changes—due to a sanctions update, account closure, or expired identity document—the credential must be invalidated without revealing the user's identity on-chain. The standard approach uses a revocation registry , often a Merkle tree where each leaf represents a credential's unique revocation nonce. The credential's validity proof must demonstrate that its nonce is not present in the current revocation root published to the blockchain. This allows for private, efficient batch updates where only the registry's root hash needs to be updated.
Implementing this requires careful architecture. For a registry using a sparse Merkle tree, the prover (user's wallet) needs access to the latest root and a Merkle proof of non-inclusion for their nonce. The verifier (smart contract or verifier service) checks the proof against the on-chain root. Libraries like @iden3/sparse-merkle-tree can manage this off-chain. A governance-controlled entity, or a decentralized oracle network, must have the sole authority to update the revocation root, ensuring only authorized status changes are processed.
Audit trails provide the necessary transparency for regulators and auditors. Every verification event should emit a zero-knowledge proof receipt to a public ledger. This receipt contains a hash of the proof's public inputs (verifier ID, timestamp, policy version) and the proof's validity, but no user-identifying data. This creates an immutable, pseudonymous log. For example, a smart contract for a DeFi protocol might record: event VerificationSubmitted(address indexed verifier, bytes32 proofHash, uint256 timestamp, bool isValid) .
To make audit trails useful, they must be queryable and linkable to specific compliance policies. Each verification request should reference a policy ID (e.g., a hash of the required credential schema and business rules). Auditors can then filter logs by verifier and policy ID to confirm that all accesses followed procedure. Tools like The Graph can index these events for easy querying. This design satisfies regulatory requirements for auditability while preserving user privacy through cryptographic commitments.
In practice, integrating these features looks like extending your credential issuance flow. After a user generates a ZK proof from their credential, your application's backend must fetch the latest revocation root and generate the non-inclusion proof. The full proof package—containing the ZK proof and the revocation proof—is then sent to the verifier. The verifier contract checks both before approving a transaction. This ensures real-time compliance without sacrificing the privacy guarantees that make ZK-KYC valuable.
This section details how to connect your ZK-KYC system to traditional compliance data sources like World-Check or local registries, enabling on-chain verification of off-chain credentials. A ZK-KYC system's utility depends on its connection to authoritative data sources. You cannot build a trusted compliance layer in a vacuum. The core challenge is to create a secure, automated bridge between off-chain Know Your Customer (KYC) and Anti-Money Laundering (AML) databases—such as Refinitiv World-Check, Dow Jones Risk & Compliance, or government business registries—and your on-chain verification protocol. This integration is typically handled by a trusted, permissioned oracle or a dedicated attestation service that has legal access to these databases.
5. Performance Evaluation & Extended Technical Observations The technical flow involves several key steps. First, the oracle service receives a user's verified identity data (e.g., from a previous KYC process). It then performs a check against the compliance database, querying for sanctions, politically exposed person (PEP) status, or adverse media. Crucially, the oracle does not send the raw query result on-chain. Instead, it generates a zero-knowledge proof attesting to a specific claim, such as "The provided identity is NOT on the OFAC SDN list as of block N." This proof, along with a public nullifier to prevent reuse, is submitted to your verifier smart contract.
Your smart contract's verification logic must be carefully designed. It needs to validate the ZK proof against a known verification key and check the attestation's recency using a block timestamp or oracle-provided timestamp proof. A common pattern is to mint a verifiable credential (VC) as an SBT (Soulbound Token) to the user's address upon successful verification. This token acts as a persistent, non-transferable proof of compliance status. The contract must also manage revocation, often by having the oracle periodically submit validity proofs or by checking a revocation registry.
For developers, integrating with an oracle like Chainlink Functions or Pyth for this purpose requires writing specific External Adapter code. Below is a simplified conceptual example of an adapter that requests a proof from a hypothetical ZK attestation service: Security considerations are paramount. You must trust the oracle's integrity and its access controls to the compliance data.
Using a decentralized oracle network (DON) with multiple nodes can reduce single points of failure. Furthermore, the privacy of the user's data is maintained only if the oracle's off-chain component correctly discards the query data after proof generation. The system's security is a chain: it relies on the oracle's honesty, the soundness of the ZK circuit, and the correct implementation of the verifier contract. Regular audits of all three components are non-negotiable for a production system.
In practice, projects like zkPass and Sismo are pioneering models for private verification of off-chain data. Their architectures demonstrate how to use zk-SNARKs or zk-STARKs to generate proofs about web2 data sources. The end goal is to create a seamless flow where a user's compliance status becomes a portable, reusable, and private asset across the decentralized ecosystem, without exposing their personal information or requiring re-submission of documents to every new application.
Practical tools and building blocks for designing a zero-knowledge KYC/AML system that preserves privacy while meeting compliance requirements. Each resource focuses on implementation details rather than theory. Most production zero-knowledge KYC systems rely on custom circuits that prove properties about identity data without revealing it. Circom is the dominant DSL for writing zk-SNARK circuits, while SnarkJS handles trusted setup, proof generation, and verification.
Polygon ID provides a full-stack framework for verifiable credentials + zero-knowledge proofs that can be used for KYC and AML gating. It is based on the iden3 protocol and supports selective disclosure by default. Polygon ID is already integrated with EVM chains and avoids designing circuits from scratch. Semaphore is a zero-knowledge protocol that enables anonymous membership proofs . It is useful when users must prove they passed KYC without revealing identity or reusing a static identifier.
Semaphore is often combined with off-chain KYC providers who add approved users to a Merkle tree, enabling privacy-preserving access control. zkMe offers a production-ready ZK-KYC SDK that abstracts circuit design and credential issuance. It targets applications that need compliance quickly without building cryptography in-house.
zkMe is commonly used by DeFi and NFT platforms that need privacy-preserving compliance with minimal cryptographic engineering. Beyond tools, correct architecture determines whether a ZK-KYC system is secure and auditable. Most production systems combine traditional AML checks off-chain with ZK proofs on-chain, satisfying regulators while preserving user privacy.
Common technical questions and implementation challenges when building zero-knowledge proof systems for KYC/AML compliance. The core primitive is a zero-knowledge Succinct Non-interactive Argument of Knowledge (zk-SNARK) . This allows a user (the prover) to cryptographically prove they possess certain verified credentials (like an ID hash or age) without revealing the underlying data. The system works by: Popular libraries for implementation include Circom for circuit writing and SnarkJS for proof generation/verification.
Mapping involves converting verified identity attributes into provable statements a circuit can understand. This is a multi-step process: For example, using Semaphore or Sismo , the circuit would verify a user holds a valid credential from a specific group (like verified citizens) without revealing which specific credential they hold.
Most zk-SNARKs require a trusted setup ceremony to generate the proving and verification keys. If the secret randomness ("toxic waste") used in this setup is compromised, an attacker could generate false proofs. This is a single point of failure for the entire system. A ZK proof is static data; without safeguards, it can be re-used (replayed) by anyone who obtains it. To prevent this, you must add uniqueness and context to the proof.
Failing to implement anti-replay allows users to bypass one-time access gates or voting mechanisms. On-chain verification gas costs are significant but predictable. A typical Groth16 zk-SNARK verification on Ethereum requires a fixed number of pairing operations and elliptic curve additions/multiplications. ZK credentials must have a mechanism to be invalidated if a user's status changes (e.g., sanction listing). Static proofs are insufficient.
Systems like Iden3 and Veramo provide frameworks for managing these stateful credentials. While a single ZK proof is private, correlation across multiple actions can deanonymize users. This is a system-level privacy leak. This guide has outlined the core components for building a privacy-preserving KYC/AML system. The next step is to move from theory to a practical implementation.
A production-ready ZK-KYC/AML solution requires integrating the cryptographic proof system with real-world identity verification and compliance logic. Key next steps include selecting a proving system like Circom or Halo2 , defining the precise compliance circuit (e.g., "user is over 18 AND is not on sanction list X"), and establishing a secure, decentralized attestation layer for credential issuance. The Verifiable Credentials (VCs) data model, as standardized by the W3C, is the recommended format for the underlying claims.
For developers, the implementation workflow involves several stages. First, design the circuit logic that enforces your AML rules without revealing the user's underlying data. Second, integrate with an identity provider's API to issue signed VCs upon successful KYC. Third, build the user-facing prover application that generates a ZK-SNARK proof from the VC. Finally, deploy the verifier contract, such as a Semaphore group or a custom Solidity verifier, on-chain. Tools like SnarkJS and Circomlib are essential for this development cycle.
The regulatory landscape for such systems is still evolving. Engaging with legal experts to ensure your circuit's logic aligns with jurisdictional requirements like the Travel Rule or FATF guidelines is critical. Furthermore, consider the system's trust assumptions: who is the issuer of the credential, and is their signing key secure? Exploring decentralized identifier (DID) methods and key rotation policies can help mitigate issuer-centric risks.
Looking ahead, the field is advancing rapidly. ZK-SNARKs are becoming more efficient with recursion and custom gates, while new paradigms like Proof of Innocence protocols offer alternative models for blacklist compliance. To continue your learning, explore resources like the ZKProof Community Standards , the 0xPARC crypto engineering tutorials , and the documentation for frameworks like zkEmail . Building a robust ZK-KYC system is a complex but solvable engineering challenge at the frontier of privacy and compliance.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Password • https://en.wikipedia.org/wiki/Key-agreement%20protocol • https://www.ijert.org/zkp-banking-interface-a-privacy-preserving-context-aware-authentication-system-using-zero-knowledge -proofs-ijertv15is030929 • https://chainscorelabs.com/guides/adoption-strategies-and-market-penetration/business-privacy-systems/how-to-design-a-z ero-knowledge-kyc-aml-solution • https://www.nukoe.com/blog/en-zkp-implementation-secure-passwordless-authentication-mh0dsxss
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Zero Knowledge Authentication For Banking Systems Project.
[*] Metasploit Scan Running on Target Subnet for Zero Knowledge Authentication For Banking Systems Project... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |