Complete Technical Paper Content — Zero Knowledge Proof Based Authentication Protocol
Overview & System Context
Zero Knowledge Proof Based Authentication Protocol: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9596 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In cryptography, a zero-knowledge proof (also known as a ZK proof or ZKP) is a protocol in which one party (the prover) can convince another party (the verifier) that some given statement is true, without conveying to the verifier any information beyond the mere fact of that statement's truth. The intuition behind the nontriviality of zero-knowledge proofs is that it is trivial to prove possession of the relevant information simply by revealing it; the hard part is to prove this possession without revealing this information (or any aspect of it whatsoever). In light of the fact that one should be able to generate a proof of some statement only when in possession of certain secret information connected to the statement, the verifier, even after having become convinced of the statement's truth by means of a zero-knowledge proof, should nonetheless remain unable to prove the statement to further third parties. Zero-knowledge proofs can be interactive, meaning that the prover and verifier exchange messages according to some protocol, or noninteractive, meaning that the verifier is convinced by a single prover message and no other communication is needed. In the standard model, interaction is required, except for trivial proofs of BPP problems. In the common random string and random oracle models, non-interactive zero-knowledge proofs exist. The Fiat–Shamir heuristic can be used to transform certain interactive zero-knowledge proofs into noninteractive ones.
Ali Baba cave is a story presenting the fundamental ideas of zero-knowledge proofs, first published in 1990 by Jean-Jacques Quisquater and others in their paper "How to Explain Zero-Knowledge Protocols to Your Children". The two parties in the zero-knowledge proof story are Peggy as the prover of the statement, and Victor, the verifier of the statement. In this story, Peggy has uncovered the secret word used to open a magic door in a cave. The cave is shaped like a ring, with the entrance on one side and the magic door blocking the opposite side. Victor wants to know whether Peggy knows the secret word; but Peggy does not want to reveal her knowledge (the secret word) to Victor or to reveal the fact of her knowledge to the world in general. They label the paths from the entrance A and B. First, Victor waits outside the cave as Peggy goes in. Peggy takes either path A or B; Victor is not allowed to see which path she takes. Then, Victor enters the cave and shouts the name of the path he wants her to use to return, either A or B, chosen at random. Providing she really does know the magic word, this is easy: she opens the door, if necessary, and returns along the desired path. However, suppose she did not know the word.
Then, she would only be able to return by the named path if Victor were to give the name of the same path by which she had entered. Since Victor would choose A or B at random, she would have a 50% chance of guessing correctly. If they were to repeat this trick many times, say 20 times, her chance of successfully anticipating all of Victor's requests would be reduced to 1 in 220, or roughly one in a million. Thus, if Peggy repeatedly appears at the exit Victor names, then he can conclude that it is extremely probable that Peggy does, in fact, know the secret word.
Completeness: if the statement is true, then an honest verifier (that is, one following the protocol properly) will be convinced of this fact by an honest prover. Soundness: if the statement is false, then no cheating prover can convince an honest verifier that it is true, except with some small probability. Zero-knowledge: if the statement is true, then no verifier learns anything other than the fact that the statement is true. In other words, just knowing the statement (not the secret) is sufficient to imagine a scenario showing that the prover knows the secret. This is formalized by showing that every verifier has some simulator that, given only the statement to be proven (and no access to the prover), can produce a transcript that "looks like" an interaction between an honest prover and the verifier in question. The first two of these are properties of more general interactive proof systems. The third is what makes the proof zero-knowledge. Zero-knowledge proofs are not proofs in the mathematical sense of the term because there is some small probability, the soundness error, that a cheating prover will be able to convince the verifier of a false statement. In other words, zero-knowledge proofs are probabilistic "proofs" rather than deterministic proofs.
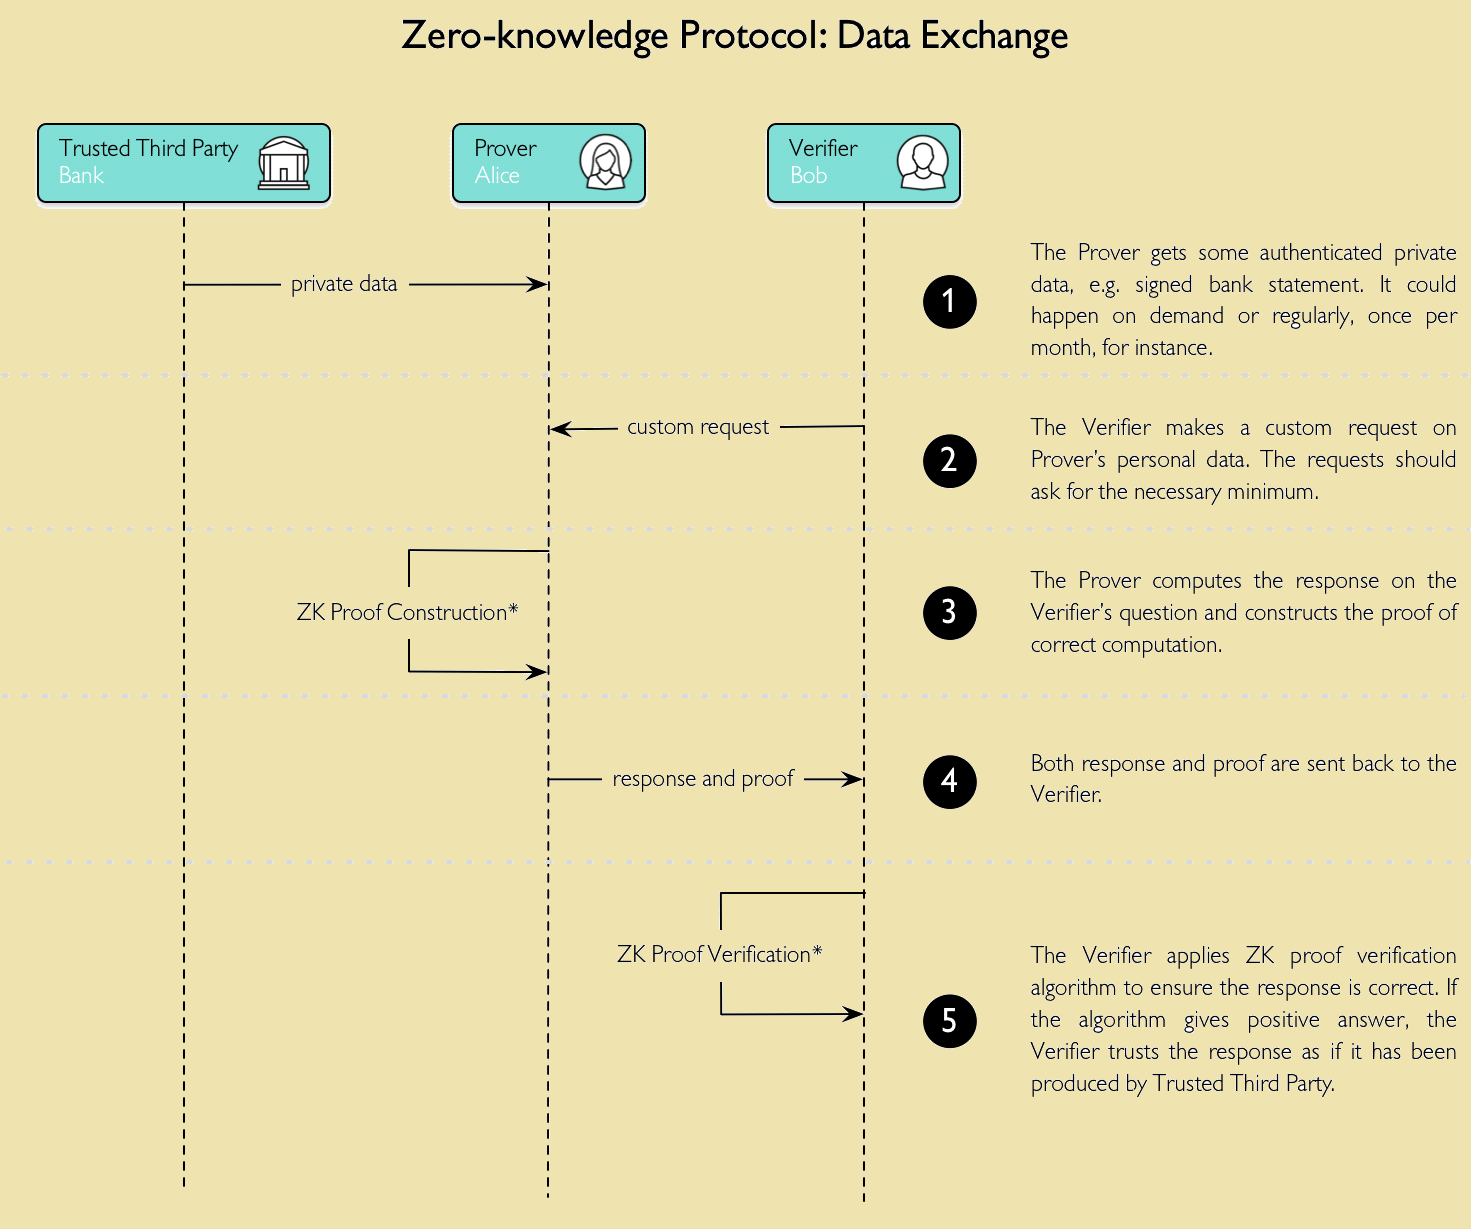
However, there are techniques to decrease the soundness error to negligibly small values (for example, guessing correctly on a hundred binary decisions has a 1/2100 soundness error. As the number of bits increases, the soundness error decreases toward zero). A formal definition of zero-knowledge must use some computational model, the most common one being that of a Turing machine. Let P, V, and S be Turing machines. An interactive proof system with (P,V) for a language L is zero-knowledge if for any probabilistic polynomial time (PPT) verifier V ^ {\displaystyle {\hat {V}}} there exists a PPT simulator S such that: ∀ x ∈ L , z ∈ { 0 , 1 } ∗ , View V ^ I [ P ( x ) ↔ V ^ ( x , z ) ] = S ( x , z ) , {\displaystyle \forall x\in L,z\in \{0,1\}^{*},\operatorname {View} _{\hat {V}}\left[P(x)\leftrightarrow {\hat {V}}(x,z)\right]=S(x,z),} Figure 1: Zero Knowledge Proof Protocol to Increase App Security where View V ^ {\displaystyle {\hat {V}}} [P(x)↔ V ^ {\displaystyle {\hat {V}}} (x,z)] is a record of the interactions between P(x) and V(x,z). The prover P is modeled as having unlimited computation power (in practice, P usually is a probabilistic Turing machine). Intuitively, the definition states that an interactive proof system (P,V) is zero-knowledge if for any verifier V ^ {\displaystyle {\hat {V}}} there exists an efficient simulator S (depending on V ^ {\displaystyle {\hat {V}}} ) that can reproduce the conversation between P and V ^ {\displaystyle {\hat {V}}} on any given input. The auxiliary string z in the definition plays the role of "prior knowledge" (including the random coins of V ^ {\displaystyle {\hat {V}}} ). The definition implies that V ^ {\displaystyle {\hat {V}}} cannot use any prior knowledge string z to mine information out of its conversation with P, because if S is also given this prior knowledge then it can reproduce the conversation between V ^ {\displaystyle {\hat {V}}} and P just as before. The definition given is that of perfect zero-knowledge. Computational zero-knowledge is obtained by requiring that the views of the verifier V ^ {\displaystyle {\hat {V}}} and the simulator are only computationally indistinguishable, given the auxiliary string.
At the beginning of each round, Peggy creates H, a graph which is isomorphic to G (that is, H is just like G except that all the vertices have different names). Since it is trivial to translate a Hamiltonian cycle between isomorphic graphs with known isomorphism, if Peggy knows a Hamiltonian cycle for G then she also must know one for H. Peggy commits to H. She could do so by using a cryptographic commitment scheme. Alternatively, she could number the vertices of H. Next, for each edge of H, on a small piece of paper, she writes down the two vertices that the edge joins. Then she puts all these pieces of paper face down on a table. The purpose of this commitment is that Peggy is not able to change H while, at the same time, Victor has no information about H. Victor then randomly chooses one of two questions to ask Peggy. He can either ask her to show the isomorphism between H and G (see graph isomorphism problem), or he can ask her to show a Hamiltonian cycle in H. If Peggy is asked to show that the two graphs are isomorphic, then she first uncovers all of H (e.g. by turning over all pieces of papers that she put on the table) and then provides the vertex translations that map G to H. Victor can verify that they are indeed isomorphic. If Peggy is asked to prove that she knows a Hamiltonian cycle in H, then she translates her Hamiltonian cycle in G onto H and only uncovers the edges on the Hamiltonian cycle. That is, Peggy only turns over exactly |V(G)| of the pieces of paper that correspond to the edges of the Hamiltonian cycle, while leaving the rest still face-down. This is enough for Victor to check that H does indeed contain a Hamiltonian cycle. It is important that the commitment to the graph be such that Victor can verify, in the second case, that the cycle is really made of edges from H. This can be done by, for example, committing to every edge (or lack thereof) separately.
We speak of perfect zero-knowledge if the distributions produced by the simulator and the proof protocol are distributed exactly the same. This is for instance the case in the first example above. Statistical zero-knowledge means that the distributions are not necessarily exactly the same, but they are statistically close, meaning that their statistical difference is a negligible function. We speak of computational zero-knowledge if no efficient algorithm can distinguish the two distributions.
Proof of knowledge: the knowledge is hidden in the exponent like in the example shown above. Witness-indistinguishable proof: verifiers cannot know which witness is used for producing the proof. Zero-knowledge proof schemes can be constructed from various cryptographic primitives, such as hash-based cryptography, pairing-based cryptography, multi-party computation, or lattice-based cryptography.
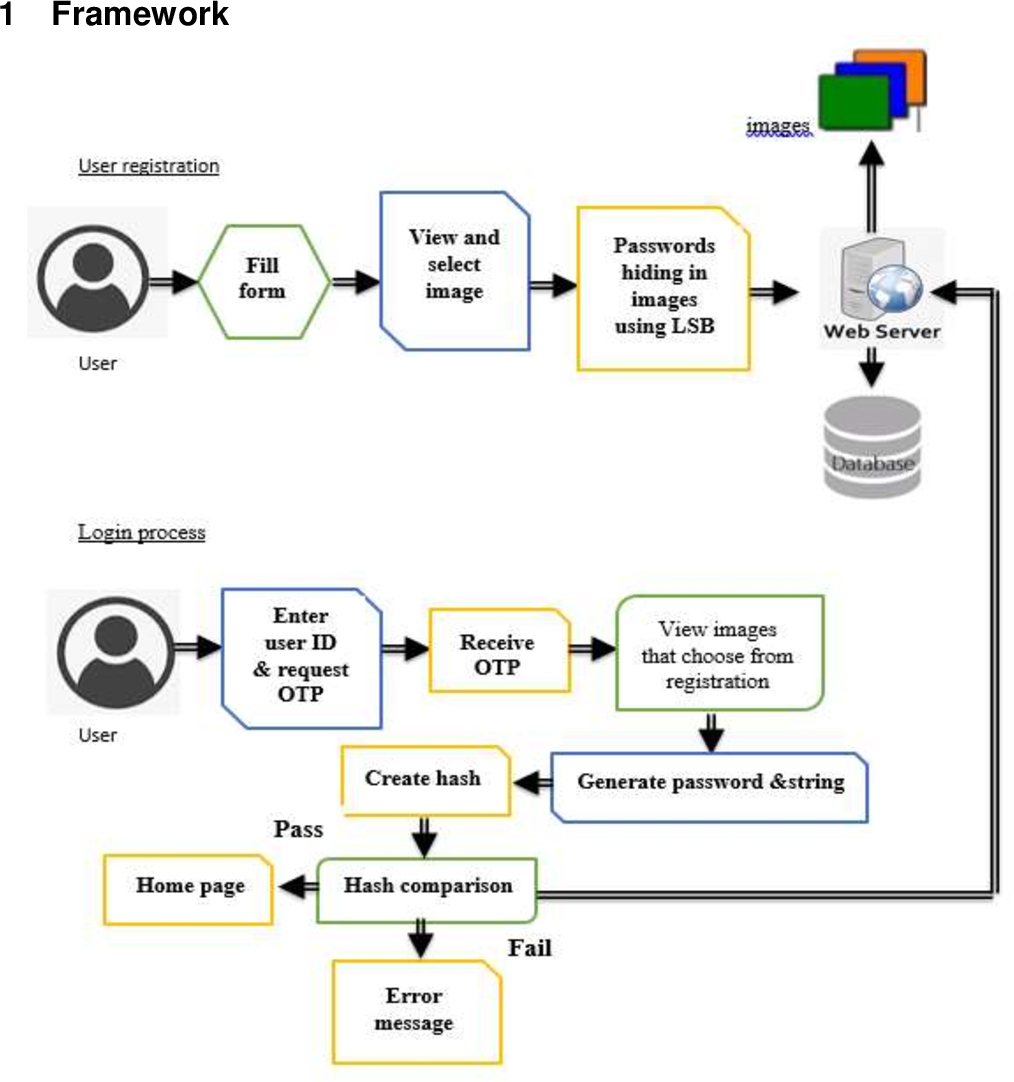
Figure 2: Figure 1 from DATA HIDING IN IMAGE BASED AUTHENTICATION USING ... Of particular interest is the case where this additional knowledge is essentially 0 and we show that [it] is possible to interactively prove that a number is quadratic non residue mod m releasing 0 additional knowledge. This is surprising as no efficient algorithm for deciding quadratic residuosity mod m is known when m's factorization is not given. Moreover, all known NP proofs for this problem exhibit the prime factorization of m. This indicates that adding interaction to the proving process, may decrease the amount of knowledge that must be communicated in order to prove a theorem.
The quadratic nonresidue problem has both an NP and a co-NP algorithm, and so lies in the intersection of NP and co-NP. This was also true of several other problems for which zero-knowledge proofs were subsequently discovered, such as an unpublished proof system by Oded Goldreich verifying that a two-prime modulus is not a Blum integer. Oded Goldreich, Silvio Micali, and Avi Wigderson took this one step further, showing that, assuming the existence of unbreakable encryption, one can create a zero-knowledge proof system for the NP-complete graph coloring problem with three colors. Since every problem in NP can be efficiently reduced to this problem, this means that, under this assumption, all problems in NP have zero-knowledge proofs. The reason for the assumption is that, as in the above example, their protocols require encryption. A commonly cited sufficient condition for the existence of unbreakable encryption is the existence of one-way functions, but it is conceivable that some physical means might also achieve it. On top of this, they also showed that the graph nonisomorphism problem, the complement of the graph isomorphism problem, has a zero-knowledge proof. This problem is in co-NP, but is not currently known to be in either NP or any practical class. More generally, Russell Impagliazzo and Moti Yung as well as Ben-Or et al. would go on to show that, also assuming one-way functions or unbreakable encryption, there are zero-knowledge proofs for all problems in IP = PSPACE, or in other words, anything that can be proven by an interactive proof system can be proven with zero knowledge. Not liking to make unnecessary assumptions, many theorists sought a way to eliminate the necessity of one way functions. One way this was done was with multi-prover interactive proof systems (see interactive proof system), which have multiple independent provers instead of only one, allowing the verifier to "cross-examine" the provers in isolation to avoid being misled. It can be shown that, without any intractability assumptions, all languages in NP have zero-knowledge proofs in such a system. It turns out that, in an Internet-like setting, where multiple protocols may be executed concurrently, building zero-knowledge proofs is more challenging. The line of research investigating concurrent zero-knowledge proofs was initiated by the work of Dwork, Naor, and Sahai. One particular development along these lines has been the development of witness-indistinguishable proof protocols. The property of witness-indistinguishability is related to that of zero-knowledge, yet witness-indistinguishable protocols do not suffer from the same problems of concurrent execution. Another variant of zero-knowledge proofs are non-interactive zero-knowledge proofs.
Blum, Feldman, and Micali showed that a common random string shared between the prover and the verifier is enough to achieve computational zero-knowledge without requiring interaction. Non-interactive zero-knowledge proofs are cryptographic primitives, where information between a prover and a verifier can be authenticated by the prover, without revealing any of the specific information beyond the validity of the statement itself. This makes direct communication between the prover and verifier unnecessary, effectively removing any intermediaries. The key advantage of non-interactive zero-knowledge proofs is that they can be used in situations where there is no possibility of interaction between the prover and verifier, such as in online transactions where the two parties are not able to communicate in real time. This makes non-interactive zero-knowledge proofs particularly useful in decentralized systems like blockchains, where transactions are verified by a network of nodes and there is no central authority to oversee the verification process.
Most non-interactive zero-knowledge proofs are based on mathematical constructs like elliptic curve cryptography or pairing-based cryptography, which allow for the creation of short and easily verifiable proofs of the truth of a statement. Unlike interactive zero-knowledge proofs, which require multiple rounds of interaction between the prover and verifier, non-interactive zero-knowledge proofs are designed to be efficient and can be used to verify a large number of statements simultaneously.
Blum, Feldman, and Micali showed in 1988 that a common reference string shared between the prover and the verifier is sufficient to achieve computational zero-knowledge without requiring interaction. Goldreich and Oren gave impossibility results for one shot zero-knowledge protocols in the standard model. In 2003, Shafi Goldwasser and Yael Tauman Kalai published an instance of an identification scheme for which any hash function will yield an insecure digital signature scheme.
The model influences the properties that can be obtained from a zero-knowledge protocol. Pass showed that in the common reference string model non-interactive zero-knowledge protocols do not preserve all of the properties of interactive zero-knowledge protocols; e.g., they do not preserve deniability. Non-interactive zero-knowledge proofs can also be obtained in the random oracle model using the Fiat–Shamir heuristic.
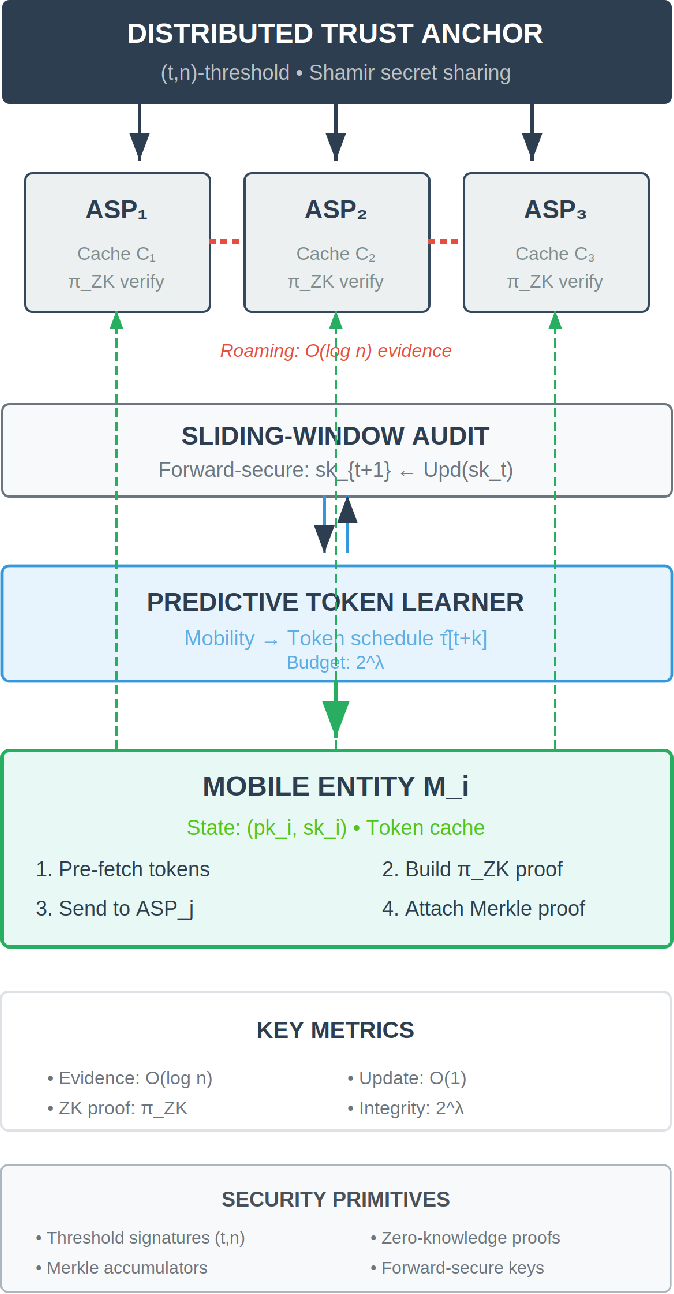
Figure 3: Figure 1 from AI-Enhanced Zero-Knowledge Authentication for High ... In 2012, Alessandro Chiesa et al developed the zk-SNARK protocol, an acronym for zero-knowledge succinct non-interactive argument of knowledge. The first widespread application of zk-SNARKs was in the Zerocash blockchain protocol, where zero-knowledge cryptography provides the computational backbone, by facilitating mathematical proofs that one party has possession of certain information without revealing what that information is. Zcash utilized zk-SNARKs to facilitate four distinct transaction types: private, shielding, deshielding, and public. This protocol allowed users to determine how much data was shared with the public ledger for each transaction. Ethereum zk-Rollups also utilize zk-SNARKs to increase scalability. In 2017, Bulletproofs was released, which enable proving that a committed value is in a range using a logarithmic (in the bit length of the range) number of field and group elements. Bulletproofs was later implemented into Mimblewimble protocol (the basis for Grin and Beam, and Litecoin via extension blocks) and Monero cryptocurrency. In 2018, the zk-STARK (zero-knowledge Scalable Transparent Argument of Knowledge) protocol was introduced by Eli Ben-Sasson, Iddo Bentov, Yinon Horesh, and Michael Riabzev, offering transparency (no trusted setup), quasi-linear proving time, and poly-logarithmic verification time. Zero-Knowledge Succinct Transparent Arguments of Knowledge are a type of cryptographic proof system that enables one party (the prover) to prove to another party (the verifier) that a certain statement is true, without revealing any additional information beyond the truth of the statement itself. zk-STARKs are succinct, meaning that they allow for the creation of short proofs that are easy to verify, and they are transparent, meaning that anyone can verify the proof without needing any secret information. Unlike the first generation of zk-SNARKs, zk-STARKs, by default, do not require a trusted setup, which makes them particularly useful for decentralized applications like blockchains. Additionally, zk-STARKs can be used to verify many statements at once, making them scalable and efficient. In 2019, HALO recursive zk-SNARKs without a trusted setup were presented. Pickles zk-SNARKs, based on the former construction, power Mina, the first succinctly verifiable blockchain. A list of zero-knowledge proof protocols and libraries is provided below along with comparisons based on transparency, universality, and plausible post-quantum security. A transparent protocol is one that does not require any trusted setup and uses public randomness. A universal protocol is one that does not require a separate trusted setup for each circuit. Finally, a plausibly post-quantum protocol is one that is not susceptible to known attacks involving quantum algorithms.
In cryptography, a zero-knowledge password proof (ZKPP) is a type of zero-knowledge proof that allows one party (the prover) to prove to another party (the verifier) that it knows a value of a password, without revealing anything other than the fact that it knows the password to the verifier. The term is defined in IEEE P1363.2, in reference to one of the benefits of using a password-authenticated key exchange (PAKE) protocol that is secure against off-line dictionary attacks. A ZKPP prevents any party from verifying guesses for the password without interacting with a party that knows it and, in the optimal case, provides exactly one guess in each interaction. A common use of a zero-knowledge password proof is in authentication systems where one party wants to prove its identity to a second party using a password but doesn't want the second party or anybody else to learn anything about the password. For example, apps can validate a password without processing it and a payment app can check the balance of an account without touching or learning anything about the amount.
Zero-Knowledge Proofs (ZKPs) provide a way for users to authenticate themselves without revealing sensitive data such as passwords. This process involves proving knowledge of a secret without directly sharing it. The authentication flow is composed of several steps, each ensuring that the user's credentials remain secure. Below is an overview of the ZKP authentication process, implemented using both Kotlin (for the mobile client) and JavaScript (for the frontend client).
These properties make ZKPs particularly useful in scenarios where privacy and security are paramount. The Schnorr protocol is a specific implementation of a zero-knowledge proof that allows a prover to demonstrate knowledge of a discrete logarithm. It is based on the hardness of the discrete logarithm problem, which is widely regarded as a secure foundation for cryptographic systems.
Let p be a large prime number, and g be a generator of a cyclic group G of order q (where q divides p-1 ). The prover has a secret key x (the discrete logarithm) and computes the public key y = g x mod p . The verifier generates a random challenge c (often using a cryptographic hash function) and sends it to the prover. 2. System Architecture & Core Working Principles Schnorr signatures provide a compact and efficient alternative to traditional signature schemes. They allow for signature aggregation, which can significantly reduce the size of blockchain transactions. This is particularly beneficial in environments where bandwidth and storage are limited.
The protocol can be used in authentication systems where users can prove their identity without revealing their credentials. This enhances security by minimizing the risk of credential theft. Many cryptocurrencies, including Bitcoin, are exploring the integration of Schnorr signatures to enhance privacy and scalability. By using Schnorr signatures, transactions can be aggregated, allowing multiple transactions to be combined into a single signature, thereby reducing the overall data size on the blockchain.
The Schnorr protocol can be utilized in various privacy-preserving applications, such as confidential transactions and secure voting systems, where it is crucial to prove knowledge of a secret without revealing the secret itself. Note: Make sure to set expiry or one time usage mechanism for generated challenge to prevent it to be reused This document describes the zkPass oracle protocol from a technical perspective. It presents the underlying cryptographic components and specifies the building blocks used to construct the zkPass protocol.
The zkPass protocol is meticulously designed to serve as a private data oracle, leveraging Vector Oblivious Linear Evaluation (VOLE) to create efficient commitments, commonly referred to as VOLE-Based Zero-Knowledge Proofs (VOLE-ZK). Specifically, beyond the use of SoftSpokenOT for Oblivious Transfer (OT), the security integrity of the zkPass protocol is intimately tied to the robustness of the VOLE-in-the-Head (VOLEitH) technique.
zkPass operates in a Hybrid Mode, which combines Proxy Mode and MPC Mode, allowing the protocol to adapt to various network conditions and server restrictions without compromising performance or security. This design ensures flexibility in data-sharing scenarios, whether a server supports direct client requests or has stricter security policies. While Transport Layer Security (TLS) provides secure access to private data, it doesn't allow users to prove to third parties that the data genuinely came from a specific website. Existing solutions either require unwanted trust assumptions or server modifications, effectively locking users' data at its source. The zkPass protocol addresses this issue by extending TLS into a Three-party TLS (3P-TLS) to prevent cheating and protect privacy, enabling secure data sharing without needing assistance or permission from the data holder.
The zkPass protocol involves three entities: the Prover ( P ), the Verifier ( V ), and the DataSource (TLS Server as S ). Departing from conventional methods, P utilizes their access token to directly pinpoint and extract their data from S . P then generates a Zero-Knowledge Proof (ZKP) for the V 's inspection. This procedure ensures that V remains oblivious to the P 's personal data.
To actualize this architecture, we integrate 3P-TLS, MPC , and Non-Interactive Zero Knowledge (NIZK) technologies. These two modes collectively form Hybrid Mode , providing zkPass with the flexibility to operate efficiently across various scenarios. Typically, the zkPass protocol operates efficiently in Proxy Mode. However, a small number of TLS servers do not support this mode, meaning they block the same account's requests originating from different IP addresses. In such cases, our protocol switches to operate in MPC Mode.
In Proxy Mode, we propose having V act as a proxy between P and S . In this setup, P communicates with S through V , which allows V to record the traffic for later verification. The modified protocol flow is designed to maintain security while improving efficiency. Three-Party Handshake: P , V , and S engage in a 3P-TLS handshake. This handshake establishes cryptographic parameters and ensures mutual authentication among the parties.
Prover's Key Share Commitment: After the handshake, P commits to her key share K p K_p K p I . This commitment prevents P from altering her key share later in the protocol. P must commit to her key share K p K_p K p I I before learning the complete session key K K K . This commitment binds P to her key share, ensuring she cannot manipulate the session to produce fraudulent proofs later on.
Verifier Reveals Key Share: V reveals his key share K v K_v K v I I to P . With both key shares, P computes the full session key K = K p + K v K=K_p+K_v K = K p I + K v I . Session Continuation: P uses the session key K K K to continue the TLS session with S . V , acting as a proxy, records all traffic between P and S .
Proof Generation: After the session concludes, P proves statements about the recorded session to V. To verify server identity, during the three-party handshake, V can verify S 's identity by checking the server's signature over a fresh nonce, as per standard TLS procedures. Verifier integrity and privacy are maintained because, under the assumption that TLS is secure, a malicious V cannot compromise the integrity and privacy of the TLS session between P and S . Ensuring Prover integrity requires certain network assumptions. V must maintain a reliable connection to S throughout the session and ensure that the P cannot tamper with the messages exchanged between V and S such as those executed through BGP hijacking. Since attacks like BGP are difficult to execute in practice and are already mitigated by ICP and CSP, these network assumptions are generally acceptable and can be considered negligible in practical scenarios.
The Proxy Mode in the zkPass protocol enhances efficiency and performance by simplifying the communication flow and eliminating the need for intensive cryptographic computations after the handshake phase. Since no complex cryptographic operations are required during the rest of the session, the protocol becomes faster and more efficient due to the reduced cryptographic workload. While this approach is more universal, it introduces an additional trust assumption for the proxy and requires not only a ZK solution that’s affordable for the client, but also special magic tricks to bypass the data source’s WAF.
3. Software Implementation, Frameworks & Protocols VOLEitH is the most suitable and client affordable ZKP Protocol for authorizing TLS. We have implemented the protocol using SoftSpokenOT[ROY22], VOLE-ZK[YSWW21] and Fiat-Shamir transform[FS87]. In order to construct the zkPass protocol, we introduce the VOLEitH to create an interactive argument system. This system is then made non-interactive using the Fiat-Shamir transform and its security is proven within the Random Oracle Model (ROM).
zkPass uses VOLE correlations over a finite field F 2 k F_{2^k} F 2 k I , to use as a form of linearly homomorphic commitment scheme. A VOLE correlation of length is defined by a random global key ∆ ∈ F 2 k ∆ ∈ F_{2^k} ∆ ∈ F 2 k I , a set of random bits u i ∈ F 2 k u_i ∈ F_{2^k} u i I ∈ F 2 k I , random VOLE tags v i ∈ F 2 k v_i ∈ F_{2^k} v i I ∈ F 2 k I and VOLE keys q i ∈ F 2 k q_i ∈ F_{2^k} q i I ∈ F 2 k I such that: The values u i u_i u i I and v i v_i v i I should be known only to P , while q i q_i q i I and ∆ ∆ ∆ should be given to V . A VOLE correlation can be seen as committing P to the random bits u i u_i u i I via a linearly homomorphic commitment scheme. The scheme is hiding, because the random v i v_i v i I mask u i u_i u i I in the V 's values q i q_i q i I , and the scheme is binding, because opening to a different value u i ′ u^′_i u i ′ I requires P to come up with a tag q i ′ = u i ′ ∗ ∆ + v i ′ q^′_i = u^′_i ∗ ∆ + v^′_i q i ′ I = u i ′ I ∗ ∆ + v i ′ I but then P would have successfully guessed ∆ = ( v i ′ − v i ) / ( u i ′ − u i ) ∆ = (v^′_i − v_i)/(u^′_i − u_i) ∆ = ( v i ′ I − v i I ) / ( u i ′ I − u i I ) , which can only happen with probability 2 − k 2^{−k} 2 − k .
A VOLE correlation can be created with a secure two-party protocol, in zkPass protocol, however, since we want to obtain ZKP that are publicly verifiable, we instead use the VOLEitH technique [BBD+23]. Here, P first generates its values u i u_i u i I , v i v_i v i I and commits to them using a special type of VOLE commitment. The commitment is set up such that V can later send to P the random key ∆ ∆ ∆ , after which, P can send an opening that allows V to learn its q i q_i q i I values, such that equation holds for ∆ ∆ ∆ , and nothing more. It is important that ∆ ∆ ∆ is only given to P after running the main steps of the ZKP, since as soon as ∆ ∆ ∆ is known, the binding property of the homomorphic commitments is trivially broken.
The main building block of our VOLEitH approach is the technique of committing to a vector of N pseudo-random seeds by deriving them from a tree of length-doubling PRGs. This is also known as the GGM construction, which builds a puncturable PRF from a PRG [GGM84, KPTZ13,BW13, BGI14]. We model this as an all-but-one vector commitment scheme, where P commits to N seeds by sending a single hash value, and can later open N − 1 of them with only O ( l o g N ) O(logN) O ( l o g N ) communication. To open all-but-one of the seeds, say all except index s d j sd_j s d j I , P takes the siblings of all nodes on the path from the root to leaf j j j (excluding the root node) and sends these to V , together with the commitment c o m j com_j co m j I . V can then reconstruct every s d i sd_i s d i I for i ≠ j i \ne j i I = j using the sibling nodes, and also has enough information to compute the hash value h h h and check the original commitment.
Then we start converting vector commitments to VOLE, to obtain our desired VOLE commitments, P starts by committing to τ all-but-one vector commitments. After send the vector commitments, the next step is to convert each vector commitment into a length- l l l , small-field VOLE correlation in F 2 k F_{2^k} F 2 k I , This involves first expanding each of the seeds s d 0 , . . . , s d N − 1 sd_0, . . . , sd_{N−1} s d 0 I , ... , s d N − 1 I (committed in the vector commitment) using a PRG, to obtain N N N strings r 0 , . . . , r N − 1 ∈ { 0 , 1 } l r_0, . . . , r_{N−1} ∈ \{0,1\}^l r 0 I , ... , r N − 1 I ∈ { 0 , 1 } l , and then computing in F 2 k F_{2^k} F 2 k I : To see how this can be used to get a VOLE correlation, consider a V who later learns seeds s d i sd_i s d i I for all i ≠ j i \ne j i I = j , for some index j ∈ 0 , . . . , N − 1 j∈ {0, . . . , N − 1} j ∈ 0 , ... , N − 1 (viewed as an F 2 k F_{2^k} F 2 k I element). V can compute: After doing this for each of the vector commitments, P has l l l small and independent VOLE correlations. Denote these as u i u_i u i I I V i V_i V i I for i = 0 , . . . , τ − 1 i = 0, . . . , τ − 1 i = 0 , ... , τ − 1 , where we now view V i V_i V i I as a matrix in { 0 , 1 } l ∗ k \{0, 1\}^{l∗k} { 0 , 1 } l ∗ k , instead of a vector in F 2 k F_{2^k} F 2 k I . V will eventually learn ( ∆ i , Q i ∆_i ,Q_i ∆ i I , Q i I ) such that: where δ 0 , . . . , δ k − 1 δ_0, ..., δ_{k−1} δ 0 I , ... , δ k − 1 I is the bit decomposition of ∆ ∆ ∆ .
After this P must send correction values so that the VOLEs can be fixed to use the same u u u value. Finally we make a VOLE Consistency Check to ensure that all u u u values are corrected in right ways. The VOLE-ZK is an interactive ZKP in the VOLE-hybrid model. It is based on the Line-Point Zero-Knowledge Paradigm[DIO21]. For the zkPass protocol, we use the QuickSilver protocol to prove boolean circuits satisfaction. As QuickSilver is an interactive proof system, it is described here as a protocol executed between two parties: P and V . And we will convert it into the NIZK eventually.
We have VOLE Commitments at last step, P first get χ i χ_i χ i I from Fiat-Shamir transformation and then P calculates the ∑ u i ∑ u_i ∑ u i I ∗ χ i χ_i χ i I and ∑ v i ∑ v_i ∑ v i I ∗ χ i χ_i χ i I for all the inputs and gates in circuit, and later get ∆ ∆ ∆ from Fiat-Shamir then open all the vector commits and ∑ u i ∑ u_i ∑ u i I ∗ χ i χ_i χ i I , ∑ v i ∑ v_i ∑ v i I ∗ χ i χ_i χ i I , to V , V reconstructs the GGM Trees to obtain VOLE instances and calculate ∑ q i ∑ q_i ∑ q i I ∗ χ i χ_i χ i I then check: ZK systems like SNARKs are less suitable for authorizing TLS data because they involve intensive cryptographic computations, such as large-scale exponentiations and complex pairing operations. These operations require substantial computational resources and memory, leading to time-consuming proof generation that is often unaffordable for clients.
Additionally, SNARKs typically require a trusted setup phase, which introduces potential security risks. While they may be acceptable for very small data sizes, they are inefficient and impractical for the typical data sizes found in TLS communications. In contrast, VOLE-ZKs are much more efficient. They naturally handle the linear computations, enabling fast and low-overhead, which makes them more suitable for authorizing TLS data. They avoid the need for a trusted setup and do not require large memory or extensive calculations for proof generation, making them affordable for clients. However, VOLE-ZK proofs are interactive, necessitating the verifier's continuous online presence and potentially introducing risks of collusion.
To overcome these challenges, the zkPass protocol employs the VOLEitH technique, transforming the VOLE-ZK protocol into a non-interactive form. This ensures swift and efficient proof generation directly in the browser and device, addressing the limitations of both traditional SNARKs and VOLE-ZKs. By doing so, zkPass combines the efficiency of VOLE-ZK proofs with the convenience of non-interactivity, making it a practical and secure solution for authorizing TLS data.
In MPC Mode, we have implemented the protocol using a hybrid approach that combines ZKP and MPC technologies for 3P-TLS. P and V work together as a single client to establish secure communication with S . They achieve this through a series of stages based on the elliptic curve Diffie-Hellman (ECDH) protocol, enhanced with MPC and OT techniques.
The first stage of the protocol is a three-party handshake between P , V , and S , where they work together to generate the pre-master key. P and V each receive a share of this key using Oblivious Linear Evaluation (OLE) based Multiplicative-to-Additive (MtA) or Additive-to-Multiplicative (AtM) schemes, which support additive homomorphism. The pre-master key is divided, with P and V each getting one half, while S retains the full key.
To ensure authenticity and prevent the client from impersonating fake websites, after the client and server exchange greetings, the server provides its certificate. During the key exchange phase, the server also signs the public key with its private key from the certificate. This allows V , within the client, to verify the certificate and signature, confirming the server's identity and establishing trust in the data source.
The second stage of the protocol is key derivation, where P and V work together using Garbled Circuit (GC) to generate two session keys from the pre-master key: the encryption key (enc_key) for data protection and the message authentication code key (mac_key) for data integrity. Notably, V only holds a share of the mac_key and has no access to the enc_key, ensuring that V cannot view P ’s private information. P also holds a share of the mac_key, giving access to identity-related data but without the ability to tamper with it. Any tampering can be detected by verifying the authenticity of messages using the mac_key.
4. Practical Deployment, Analysis & Case Studies The MPC algorithm in zkPass has been significantly optimized in several areas, including communication time, hash functions for the Garbler and Evaluator, OT operations, and memory copying. These improvements have increased efficiency by more than threefold. A new AES128 proof method has also been introduced, reducing the number of blocks by 300 times and speeding up Garbler/Evaluator execution by tenfold. zkPass uses Silent OT, minimizing offline network communication during OT generation. For GC, zkPass implements Three Halves Make a Whole and Stacked GC, which reduces the size of the Garbled Tables, leading to less communication and faster execution. Overall, these optimizations have greatly reduced the runtime of the entire MPC process, making zkPass much more efficient.
In the final stage of the zkPass protocol, the client creates a ZKP for public verification. After the 3P-TLS phase, the prover obtains the complete data and uses the VOLEitH process to generate a proof. Since this step is similar to the process used in proxy mode, we won’t go into the details here. The performance overhead of MPC Mode is significant, mainly due to the truth table (TT) in GC. Every block of application data must be encrypted using a TT, which greatly increases both computational and bandwidth requirements. For a single TLS session, there's a fixed cost of 20MB, plus 8MB per 1KB of outgoing data and 32KB per 1KB of incoming data. For a typical 1KB request and 100KB response, the prover would need to upload around 32MB, making this approach impractical for regular use.
Additionally, MPC Mode isn't necessarily more secure than Proxy Mode because it still relies on a "trusted notary", similar to a proxy. A malicious notary could cache session data and collude with a compromised client. Since the server's decrypted key is hidden for privacy, external verification is impossible, meaning collusion or manipulation could go unnoticed. While MPC mode reduces some trust assumptions, it doesn't fully eliminate them, so it isn't inherently more secure.
Given these issues, while MPC Mode provides some cryptographic advantages and may be useful for small requests, its high performance overhead and limited security benefits make it no better than a well-designed and decentralized proxy. Its resource demands and impracticality for everyday use restrict its real-world application. Therefore, we only reserve this mode as a backup for TLS servers that block requests from the same account when coming from different IP addresses.
The zkPass protocol distinguishes itself by combining advanced cryptographic techniques to achieve secure, efficient, and privacy-preserving data sharing. By extending TLS into a three-party protocol and integrating VOLEitH for Non-Interactive Zero-Knowledge (NIZK) proofs, zkPass effectively addresses both security and performance challenges. Its Hybrid Mode , which seamlessly switches between Proxy Mode and MPC Mode , allows the protocol to adapt to various network environments and server policies without compromising efficiency or security. Proxy Mode ensures high performance with minimal cryptographic overhead, while MPC Mode takes over when certain servers block requests from multiple IP addresses, maintaining privacy and security. The use of VOLEitH further enhances efficiency by avoiding the heavy computational and memory demands of traditional cryptographic systems like SNARKs.
Optimized cryptographic computations and communication flows make zkPass highly scalable, ensuring that the protocol remains practical for real-world applications without sacrificing security or speed. A zero-knowledge authentication protocol is a cryptographic interactive protocol in which an entity (prover) convinces another party ( verifier ) of its identity, or knowledge of a secret, without revealing any information about the secret itself. Such protocols rely fundamentally on zero-knowledge proofs ( ZKPs ), and their instantiations span a wide array of algebraic, combinatorial, and post-quantum structures, and have seen deployment in classical, quantum, and blockchain contexts. They are crucial for enhancing security and privacy of authentication in scenarios with strong adversarial models, stringent privacy requirements, and minimal trust assumptions.
Zero-knowledge authentication protocols are based on interactive (or non-interactive) proofs of knowledge satisfying three essential criteria: Security is typically based on well-studied computational hardness assumptions such as the discrete logarithm problem (for DLP-based schemes ( Yigit et al., 25 Aug 2025 , Serna, 2023 )), quadratic residuosity (for QRP-based proofs ( Povsic et al., 2022 )), syndrome decoding (code-based ( Aguilar et al., 2011 )), non-commutative algebraic problems such as the generalized symmetric decomposition problem (GSDP) ( Hecht, 2017 ), or quantum state estimation hardness (quantum protocols ( Carney, 2022 , Garcia-Cid et al., 2024 )).
Common adversary models include eavesdropping, replay, active man-in-the-middle (MitM), and impersonation, as well as specific concerns such as collusion (e.g., between verifier and third parties ( Naziri et al., 23 Aug 2025 )) and quantum attacks. Zero-knowledge authentication protocols manifest in multiple methodological classes, including: Protocols vary by interactivity, computational assumptions, zero-knowledge flavor (perfect, statistical, or computational), and whether they include fresh randomness per session or reuse public parameters.
From ( Aguilar et al., 2011 ), using double-circulant codes, cyclic shifts, and hashed commitments to minimize communication. Verification relies on the intractability of decoding random linear codes and soundness is bounded by ≈ X = [ x ] G X = [x]G X = [ x ] G 5 per round. PRZK-Bind ( Yigit et al., 25 Aug 2025 ) binds digital-twins to physical devices using PUF-derived secrets and Schnorr ZKPs over elliptic curves, achieving 0.02% FAR—10x better than attribute- or PUF-ECC–only schemes.
Adversaries may passively observe, actively interfere, or attempt to impersonate or replay sessions (e.g., ( Naziri et al., 23 Aug 2025 )), or in blockchain, mount Sybil or collusion attacks. [0609057]: "Concurrently Non-Malleable Zero Knowledge in the Authenticated Public-Key Model", ( Naziri et al., 23 Aug 2025 ): "ZAPS: A Zero-Knowledge Proof Protocol for Secure UAV Authentication with Flight Path Privacy", ( Yigit et al., 25 Aug 2025 ): "PRZK-Bind: A Physically Rooted Zero-Knowledge Authentication Protocol for Secure Digital Twin Binding in Smart Cities", ( Carney, 2022 ): "On Zero-Knowledge Proofs over the Quantum Internet", ( Lai et al., 2024 ): "BioZero: An Efficient and Privacy-Preserving Decentralized Biometric Authentication Protocol on Open Blockchain", ( Rasheed et al., 2019 ): "Adaptive Group-based Zero Knowledge Proof-Authentication Protocol (AGZKP-AP) in Vehicular Ad Hoc Networks", ( Garcia-Cid et al., 2024 ): "Experimental Implementation of A Quantum Zero-Knowledge Proof for User Authentication", ( Khernane et al., 2016 ): "BANZKP: a Secure Authentication Scheme Using Zero Knowledge Proof for WBANs", ( Ho et al., 2021 ): "An Anonymous On-Street Parking Authentication Scheme via Zero-Knowledge Set Membership Proof", ( Povsic et al., 2022 ): "Zero-Knowledge Authentication", ( Namazi et al., 2022 ): "zkFaith: Soonami's Zero-Knowledge Identity Protocol", ( Hecht, 2017 ): "Post-Quantum Cryptography: A Zero-Knowledge Authentication Protocol", ( Aguilar et al., 2011 ): "A new zero-knowledge code based identification scheme with reduced communication", ( Saluja et al., 2019 ): "Zero Knowledge Proof based authentication protocol using graph isomorphism", ( Serna, 2023 ): "Study of Zero-Knowledge protocols and Elliptic Curve Cryptography and their implementation in Smart Card environments using Java Card", ( Mosina et al., 2010 ): "Mean-Set Attack: Cryptanalysis of Sibert et al. Authentication Protocol", ( Chuat et al., 2019 ): "Zero-Knowledge User Authentication: An Old Idea Whose Time Has Come".
Get notified by email when new papers are published related to Zero-Knowledge Authentication Protocol . Zero-Knowledge Proofs (ZKPs) are a cryptographic primitive that allows a prover to demonstrate knowledge of a secret value to a verifier without revealing anything about the secret itself. ZKPs have shown to be an extremely powerful tool, as evidenced in both industry and academic settings. In recent years, the utilization of user data in practical applications has necessitated the rapid development of privacy-preserving techniques, including ZKPs. This has led to the creation of several robust open-source ZKP frameworks. However, there remains a significant gap in understanding the capabilities and real-world applications of these frameworks. Furthermore, identifying the most suitable frameworks for the developers’ specific applications and settings is a challenge, given the variety of options available. The primary goal of our work is to lower the barrier to entry for understanding and building applications with open-source ZKP frameworks.
5. Performance Evaluation & Extended Technical Observations In this work, we survey and evaluate 25 general-purpose, prominent ZKP frameworks. Recognizing that ZKPs have various constructions and underlying arithmetic schemes, our survey aims to provide a comprehensive overview of the ZKP landscape. These systems are assessed based on their usability and performance in SHA-256 and matrix multiplication experiments. Acknowledging that setting up a functional development environment can be challenging for these frameworks, we offer a fully open-source collection of Docker containers. These containers include a working development environment and are accompanied by documented code from our experiments. We conclude our work with a thorough analysis of the practical applications of ZKPs, recommendations for ZKP settings in different application scenarios, and a discussion on the future development of ZKP frameworks.
Privacy-preserving cryptographic methods have become increasingly vital as privacy and data security evolve into a higher priority in new applications. Zero-Knowledge Proofs (ZKPs) enable a prover I \mathcal{P} to prove to a verifier I \mathcal{V} that a statement is true, without revealing any information beyond the validity of the statement itself. While ZKPs are most prominently known to the general public in blockchain applications [ 48 , 57 , 45 , 55 ] , they have also been effectively applied in many other real-world domains, such as healthcare [ 129 , 118 , 67 ] , traditional finance [ 111 , 126 , 95 ] , and government [ 30 , 93 ] . ZKPs are an excellent solution for verifying data and computation in a secure fashion, however there are still many challenges before they can become a practical privacy-preserving solution.
Although introduced in the 1980s [ 75 ] , recent algorithmic and computing advances have garnered the evolution of ZKPs from a theoretical construct to a relatively practical cryptographic primitive. ZKPs have garnered the interest of researchers and developers as concerns over data privacy grow, which has caused significant improvements in both theory and implementation. The first significant milestone in the practical application of ZKPs was the development of zero-knowledge succinct non-interactive arguments of knowledge (zk-SNARKs) introduced by Ben-Sasson et. al [ 40 ] in 2013.
In the decade since the introduction of zk-SNARKs, the zero-knowledge landscape has evolved to include a diverse set of ZKP constructions, such as zk-STARKs [ 38 ] , which build off of zk-SNARKs and are discussed at length in this work. For many of the ZKP constructions that are available, there are several prominent frameworks, stemming from industry and academia, that allow developers to create their own ZKP applications. Despite the availability of these open-source frameworks and the demand of privacy-preservation in real-world systems, the implementation of ZKPs in practical applications has been limited. This can be attributed to three ongoing challenges: 1) performance; 2) usability; 3) accessibility.
These are the attributes that we evaluate the chosen open-source frameworks on in this work. The journey towards making ZKPs a de facto solution for privacy-preserving applications is hamstrung by the performance, due to the complexity of current accessible ZKP protocols. In this work, we hope to find the schemes with the best performance for each type of ZKP construction, evaluated over several metrics on CPU and we will discuss the next steps that can be taken towards practical ZKP adoption.
Usability and accessibility are common problems that face privacy-preserving technologies, especially those stemming from academia, and the ZK landscape is no different. Due to the surge of research that has been done in the ZK space, there has been a sudden increase in the number of available frameworks for developers. For a nascent developer of ZKP applications, especially one with little exposure to cryptography and ZK concepts, this can seem like a near-impossible field to navigate.
Even for experienced developers, these frameworks are often hard to use, due to their (mostly) poor documentation or reproducible examples. While this is understandable in academic settings, due to time and resource constraints, a significant step towards enabling practical ZKP usage is demystifying the currently existing frameworks and lowering the barrier of entry for experienced and unexperienced developers. Alongside this, it is also currently difficult for developers to decipher whether a framework is usable for their custom application, due to the different ZKP constructions available, each with different underlying arithmetic, security guarantees, and interaction/communication requirements.
While there is no arguing that the development of the open-source ZKP frameworks has significantly reduced the amount of necessary effort for building new applications, the field is still difficult to navigate. The available open source frameworks have been used to enable secure verification of computation, data, and identity in the domains of machine learning [ 143 ] , networking [ 80 ] , IP protection [ 119 ] , and many more. Although there has been this evident uptick in ZKP frameworks and applications, there is no overview of the ZK landscape that is both cryptographer and non-cryptographer friendly. Alongside this, it is hard to find a clear path for where ZKPs can be improved so they can be more broadly integrated into practical real-world applications.
This paper aims to provide users with a guide to ZKPs and the available ZKP frameworks, allowing readers to gain a high-level overview of the ZK landscape, while also providing new quantitative benchmarks and details for developers to choose the best ZKP framework for their application. To achieve this goal, we conduct an extensive survey of the ZK landscape, gathering several state-of-the-art frameworks representing the seminal ZKP constructions. We first evaluate these existing tools based on the usability and accessibility of their repositories for a non-experienced cryptographic application developer, highlighting their features and shortcomings from a design standpoint. We then evaluate a subset of the most accessible and usable frameworks, primarily those that expose a high-level API, based on their performance through an in-depth analysis of their runtime and communication complexity. Performance is measured over two custom benchmarks that represent commonly used functions in privacy-preserving computation: matrix multiplication and SHA-256 compression.
We provide a discussion of the different constructions at a high-level to guide developers in their choice of framework. Our experimental evaluation, insights, and recommendations should provide a general guide to developers on how to whittle down the available frameworks to ones that fit their application setting, bandwidth, and computational requirements. We conclude our work with a discussion on some of the cutting-edge applications that ZKPs have been utilized in, the challenges that ZKP applications currently face, and the future of ZKPs.
Unfortunately, many of the prominent works that provide open-source frameworks do not include a proper documentation or reproducible examples, thus hindering developers in integrating these frameworks into their applications. Alongside this, many of the frameworks require complex local environment build dependencies. To combat this hurdle, we provide a new open-source Github repository 1 1 1 https://github.com/ACESLabUCSD/ZeroKnowledgeFrameworksSurvey containing all the tools necessary to build a custom ZKP application with any framework discussed in this survey. Not only do we provide open-source Docker environments for each frameworks with reproducible documented examples, but we also include Docker containers for other helpful tools, such as circuit building and inspection tools. This repository is also well-documented and actively maintained to encourage users to immediately start building custom applications, rather than focusing on setup troubles.
The goal of this survey is to lower the barrier of entry to building ZKP applications by providing an in-depth overview of ZKPs, the existing constructions, the available open-source frameworks and their capabilities, and the usability, accessibility, and performance of each available framework. This paper is written so that a reader with no prior knowledge of ZKPs can garner a high-level understanding of the landscape, while experienced readers can sharpen their knowledge of the details of ZKPs and gain insights on the available tools for ZK-based application development. In short, our scientific contributions are: We present the first survey of open-source ZKP frameworks, spanning all ZKP constructions, with accompanying open-source environments for each framework, including benchmarks and documentation.
We perform extensive analysis of select open-source ZKP frameworks on scalability, runtime, and proof size on two benchmarks representing prominent domains of ZKPs in current practice. We provide a thorough analysis of the capabilities, usability, and accessibility of each open-source ZKP framework. Based on the insights of our work, we customize suggestions of frameworks for different use cases based on available compute power, developer experience, and application type. Finally, we provide novel insights on the current state of ZKP and the necessary path to further boost practicality.
To the best of our knowledge, this work is the first to systematically survey and benchmark open-source ZKP frameworks spanning all constructions for practical settings and realization. [ 56 , 127 ] have considered a very limited amount of frameworks, but their industry-led work is largely comparing different constructions to each other (zk-SNARK vs. zk-STARK), rather than comparing frameworks of the same construction to each other (zk-SNARK vs. zk-SNARK). While there are very interesting insights made, we believe that our work is much more objective, systematic and extensive, while also adding the element of usability and accessibility analysis. Another survey on ZKP frameworks has been conducted [ 124 ] , however this work only focuses on zk-SNARKs and does not look into the usability, accessibility, or performance of the chosen frameworks.
Also, the work is largely focused on the application of zk-SNARKs in the blockchain. While we believe that surveying zk-SNARKs is very important, we note that many zk-SNARK schemes are not post-quantum secure. As post-quantum security becomes a rapidly growing concern, our work purposefully inspects every available ZKP construction to provide insights into post-quantum secure frameworks, alongside more established zk-SNARK frameworks. We believe that limiting our work to zk-SNARKs would not be fully representative of the ZK landscape.
We model our paper after the seminal surveys in privacy-preserving technology centered around MPC [ 82 ] and FHE [ 131 ] . Like these works, we aim to provide as detailed of a description as we can surrounding the usability, accessibility, and performance of our chosen frameworks, while providing a digestible guide for developers choosing a tool for their ZK-based applications.
Zero-Knowledge Proofs (ZKPs) are a cryptographic primitive that allow a prover I \mathcal{P} to prove to a verifier I \mathcal{V} that they know a secret value w w , called the witness, without revealing anything about w w . I \mathcal{P} does this by showing that they know a secret value w w such that I \mathcal{F} evaluated at w w equals some public output y y . Formally, I \mathcal{P} sends a proof attesting that I I ( x , w ) = y \mathcal{F}(x;w)=y , where x x and y y are public inputs and outputs, respectively. ZKPs have three core attributes [ 73 ] : Soundness : I \mathcal{V} will find out, with a very high probability, if a I \mathcal{P} is dishonest if the statement is false.
Completeness : An honest I \mathcal{P} can convince I \mathcal{V} if the statement is true. Zero-Knowledge : If the statement is true, I \mathcal{V} will learn nothing about the I \mathcal{P} ’s private inputs - only that the statement is true. In the following sections, we discuss the evolution of ZKPs, the nuances of specific classes and schemes, and provide a detailed overview of the current ZK landscape.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Zero-knowledge%20proof • https://en.wikipedia.org/wiki/Non-interactive%20zero-knowledge%20proof • https://en.wikipedia.org/wiki/Zero-knowledge%20password%20proof • https://suwasto.github.io/kmpzkp/ • https://docs.zkpass.org/overview/technical-overview • https://www.emergentmind.com/topics/zero-knowledge-authentication-protocol • https://arxiv.org/html/2502.07063v1
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Zero Knowledge Proof Based Authentication Protocol.
[*] Metasploit Scan Running on Target Subnet for Zero Knowledge Proof Based Authentication Protocol... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |