Complete Technical Paper Content — Zero Trust Network Access Simulation System Project
Overview & System Context
Zero Trust Network Access Simulation System Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9513 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Identity threat detection and response (ITDR) is a cybersecurity discipline that includes tools and best practices to protect identity management infrastructure from attacks. ITDR can block and detect threats, verify administrator credentials, respond to various attacks, and restore normal operations. Common identity threats include phishing, stolen credentials, insider threats, and ransomware. ITDR adds an extra layer of security to identity and access management (IAM) systems. It helps secure accounts, permissions, and the identity infrastructure itself from compromise. With attackers targeting identity tools directly, ITDR is becoming more important in 2023 : according to Gartner, established IAM hygiene practices like privileged access management and identity governance are no longer enough. ITDR can be part of a zero trust security model. ITDR is especially relevant for multicloud infrastructures, which have gaps between cloud providers' distinct IAM implementations.
Closing these gaps and orchestrating identity across clouds is an ITDR focus. The market for zero-day exploits is commercial activity related to the trafficking of software exploits. Software vulnerabilities and "exploits" are used to get remote access to both stored information and information generated in real time. When most people use the same software, as is the case in most of countries today given the monopolistic nature of internet content and service providers, one specific vulnerability can be used against thousands if not millions of people. In this context, criminals have become interested in such vulnerabilities. A 2014 report from McAfee's Center for Strategic and International Studies estimates that the cost of cybercrime and cyberespionage is somewhere around $160 billion per year. Worldwide, countries have appointed public institutions to deal with this issue, but they will likely conflict with the interest of their own government to access people's information in order to prevent crime. As a result, both national security agencies and criminals hide certain software vulnerabilities from both users and the original developer. This type of vulnerability is known as a zero-day exploit.
Much has been said in academia and regular media about the regulation of zero-day exploits in the market. However, it is very difficult to reach a consensus because most definitions for zero-day exploits are rather vague or not applicable, as one can only define the use of certain software as malware after it has been used. In addition, there is a conflict of interest within the operations of the state that could prevent a regulation that can make mandatory the disclosure of zero-days. Governments face a trade-off between protecting their citizens' privacy through the reporting of vulnerabilities to private companies on one hand and undermining the communication technologies used by their targets—who also threaten the security of the public—on the other. The protection of national security through exploitation of software vulnerabilities unknown to both companies and the public is an ultimate resource for security agencies but also compromises the safety of every single user because any third party, including criminal organizations, could be making use of the same resource. Hence, only users and private firms have incentives to minimize the risks associated with zero-day exploits; the former to avoid an invasion of privacy and the latter to reduce the costs of data breaches. These include legal processes, costs related to the development of solutions to fix or "patch" the original vulnerability in the software and costs associated with the loss of confidence of clients in the product.
The value will not go to zero for two reasons: (1) the distribution of the patch is asymmetric and (2) developers could use the original bug to create a variant at a decreased cost. They are also atypical because they are time-sensitive commodities. Companies are updating their software on a regular basis and a patch is only useful during the lapse between versions; sometimes a vulnerability can be corrected without any external report. Third, even in confidential transactions, the use of the exploit itself can create a dysfunction on the user-end, exposing the vulnerability and leading to its loss of value. In this sense, exploits are non-excludable but they can or can not be non-rivalrous, as the more users use a zero day exploit after a certain point, the more visible its impact will be to the company in question. This could result in the company being more likely to patch the exploit, resulting in a limited period of time where the exploit is available for all users.
Classically, black markets—like illegal weapons or narcotics—require a huge network of trusted parties to perform the transactions of deal-making, document forgery, financial transfers and illicit transport, among others. As it is very difficult to enforce any legal agreement within these networks, many criminal organizations recruit members close to home. This proximity element increases the cost of transaction as more intermediaries are required for transnational transactions, decreasing the overall profit of the original seller. Zero-days, on the other hand, are virtual products and can be easily sold without intermediaries over the internet as available technologies are strong enough to provide anonymity at a very low cost.
Even if there is a need for intermediaries, "unwitting data mules" can be used to avoid any evidence of wrongdoing. This is why the black market is so lucrative compared to gray markets. Gray markets, which involve transactions with public institutions in charge of national security, usually require the use of third parties to hide the traces of their transactions. The Hacking Team archive, for example, contains alleged contracts with the Ecuadorian National Secretariat of Intelligence where they used two intermediaries: Robotec and Theola. In the same archive, it is said that third-party companies Cicom and Robotec negotiated the contracts on behalf of the FBI and DEA respectively. It is less likely that white markets face the same problem as it is not in their interest to hide the transaction, it is quite the opposite because companies actively promote the use of their new patches.
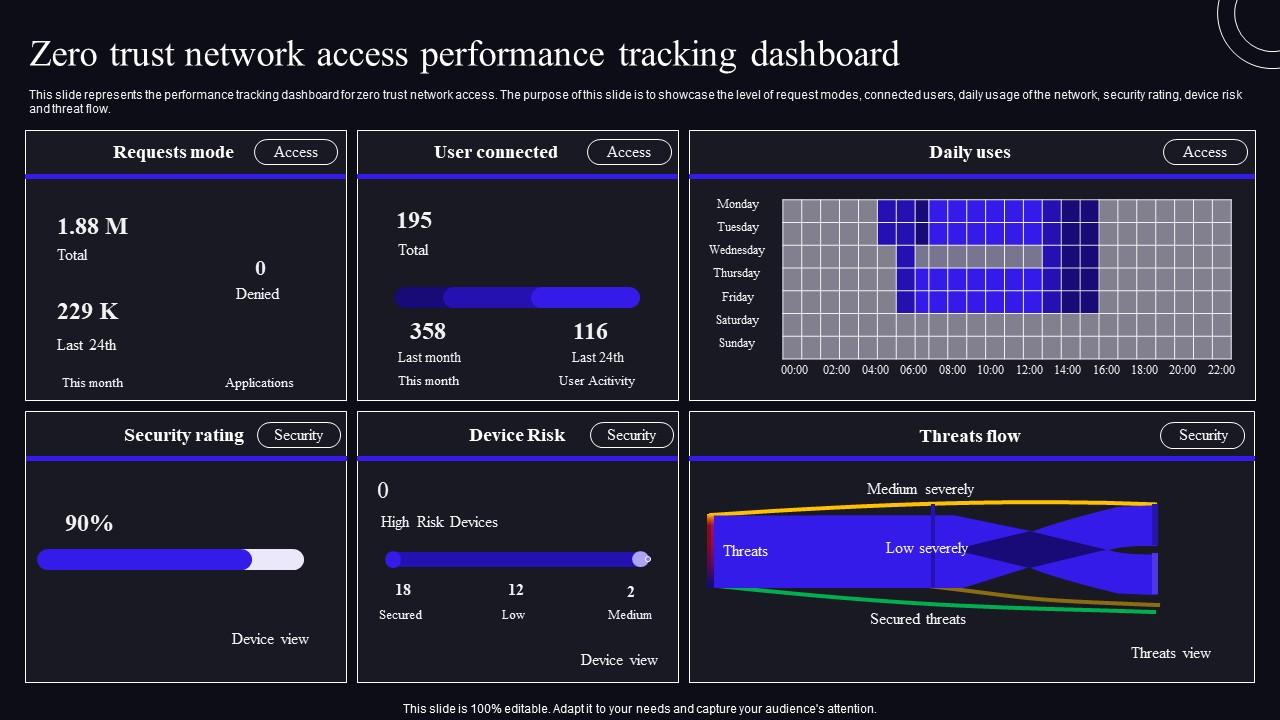
Figure 1: F1589 Zero Trust Network Access Performance Tracking Dashboard Zero ... Buyers follow standard technology purchasing practices around testing, delivery, and acceptance. Warranty and requirements negotiations become necessary in purchasing a product intrinsically predicated on the existence of information asymmetry between the buyer and the seller. Requirements—like targeted software configurations—are important to negotiate ahead of time because adding support for new targets might be impossible or not worth the effort. Likewise warranty provisions for buyers are common so they can minimize risk by parceling out payments over a set time frame and terminating payments early if the vulnerability is patched before that time frame is complete. Payments are typically made after a 0day exploit has been delivered and tested against requirements, necessitating sellers to trust buyers to act in good faith. Similarly, buyers purchasing exploits must trust the sellers not to expose the vulnerability or share it with others if it's sold on an exclusive basis.
Kentucky Route Zero is a 2013–2020 point-and-click adventure interactive fiction game developed by Cardboard Computer and published by Annapurna Interactive. The game follows the narrative of a truck driver named Conway and the strange people he meets as he tries to cross the mysterious Route Zero in Kentucky to make a final delivery for the antiques company he works for. The game received acclaim for its visual art, narrative, characterization, atmosphere, and themes, appearing on several best-of-the-decade lists. Kentucky Route Zero was first revealed in 2011 via the crowdfunding platform Kickstarter and is separated into five acts that were released sporadically throughout its development; the first releasing in January 2013 and the last releasing in January 2020. The game was developed for Linux, Windows, and macOS, with console ports for the Nintendo Switch, PlayStation 4, and Xbox One under the subtitle of "TV Edition", coinciding with the release of the final act.
The game was released for Android and iOS on December 13, 2022, in partnership with Netflix and was later released for PlayStation 5 and Xbox Series X/S in August 2023. Kentucky Route Zero is a point and click game that contains text-driven dialogue. There are no traditional puzzles or challenges, with the focus of the game being storytelling and atmosphere. The game has been described as an "interactive screenplay." The player controls Conway by clicking on the screen, either to guide him to another location, or interact with other characters and objects. The player also has the choice to choose Conway's dialogue, and occasionally the dialogue of other characters, during in-game conversations. The game is separated into various locations, between which Conway can travel using his truck. A map is shown when traveling on the road, and the player must guide the truck icon to the destination of their choosing, mostly areas where the player has been pointed or sent out to go. The player also takes control of other characters at certain times.
Conway arrives in the Equus Oils station and meets an old man named Joseph, who is the owner of the establishment. Joseph informs Conway that the only way to arrive at Dogwood Drive is by taking the mysterious Route Zero, and then tasks him to fix the circuit breaker to restore power in the station and use the computer to locate directions. Conway goes underneath the station and meets three people who are playing a strange game and ignore him completely. He is able to retrieve their lost 20-sided die but soon notices their disappearance afterwards, clearing a way to fix the electricity. When asking Joseph about the strange people who disappeared, he suggests Conway may have been hallucinating. Conway uses the computer to locate the directions of the Márquez Farm to talk to Weaver Márquez, who has a better understanding of the roads. As Conway leaves, Joseph tells him that he loaded a TV into the back of the truck to take to Weaver. Conway drives to the Márquez residence and meets Weaver. Weaver quizzically asks Conway a number of questions and Conway finally asks her about directions to Route Zero. She has Conway set up the TV and when Conway looks into the screen, he sees the vision of a strange farm and spaces out. When he wakes, Weaver informs him of her cousin Shannon who fixes TVs and gives him the directions to Route Zero, and suddenly disappears. When arriving at the destination, Conway finds the area to actually be an abandoned mine shaft called Elkhorn Mine. He locates Shannon Márquez, who has been exploring the mines in search of something she has lost. Conway decides to help Shannon travel deeper into the mine, and begins toying with a PA system to test the depth and length of the tunnels. Unfortunately, the sound waves cause a portion of the mine to collapse.
Conway injures his leg from falling rubble, and Shannon uses a track to help them travel through the mine. While exploring the mine, Shannon reveals the mine's tragic history, involving the deaths of many miners due to flooding. If the lamplight is turned off during the travel, ghostly visions of miners can be seen wandering the caves. Before exiting the mines, Shannon leaves Conway and travels a bit farther down the mine shaft, and comes across a heap of miner helmets. She comes back quickly without explaining anything. Conway and Shannon travel to Shannon's workshop, and then back to the Márquez Farm, where Shannon reveals that the Márquez family's debts had caused Weaver to flee. As Shannon attempts to fix the old TV, Conway looks in again. This time the picture of the farm begins to warp and separate, causing the screen to create an image of the opening to Route Zero and the truck driving down it.
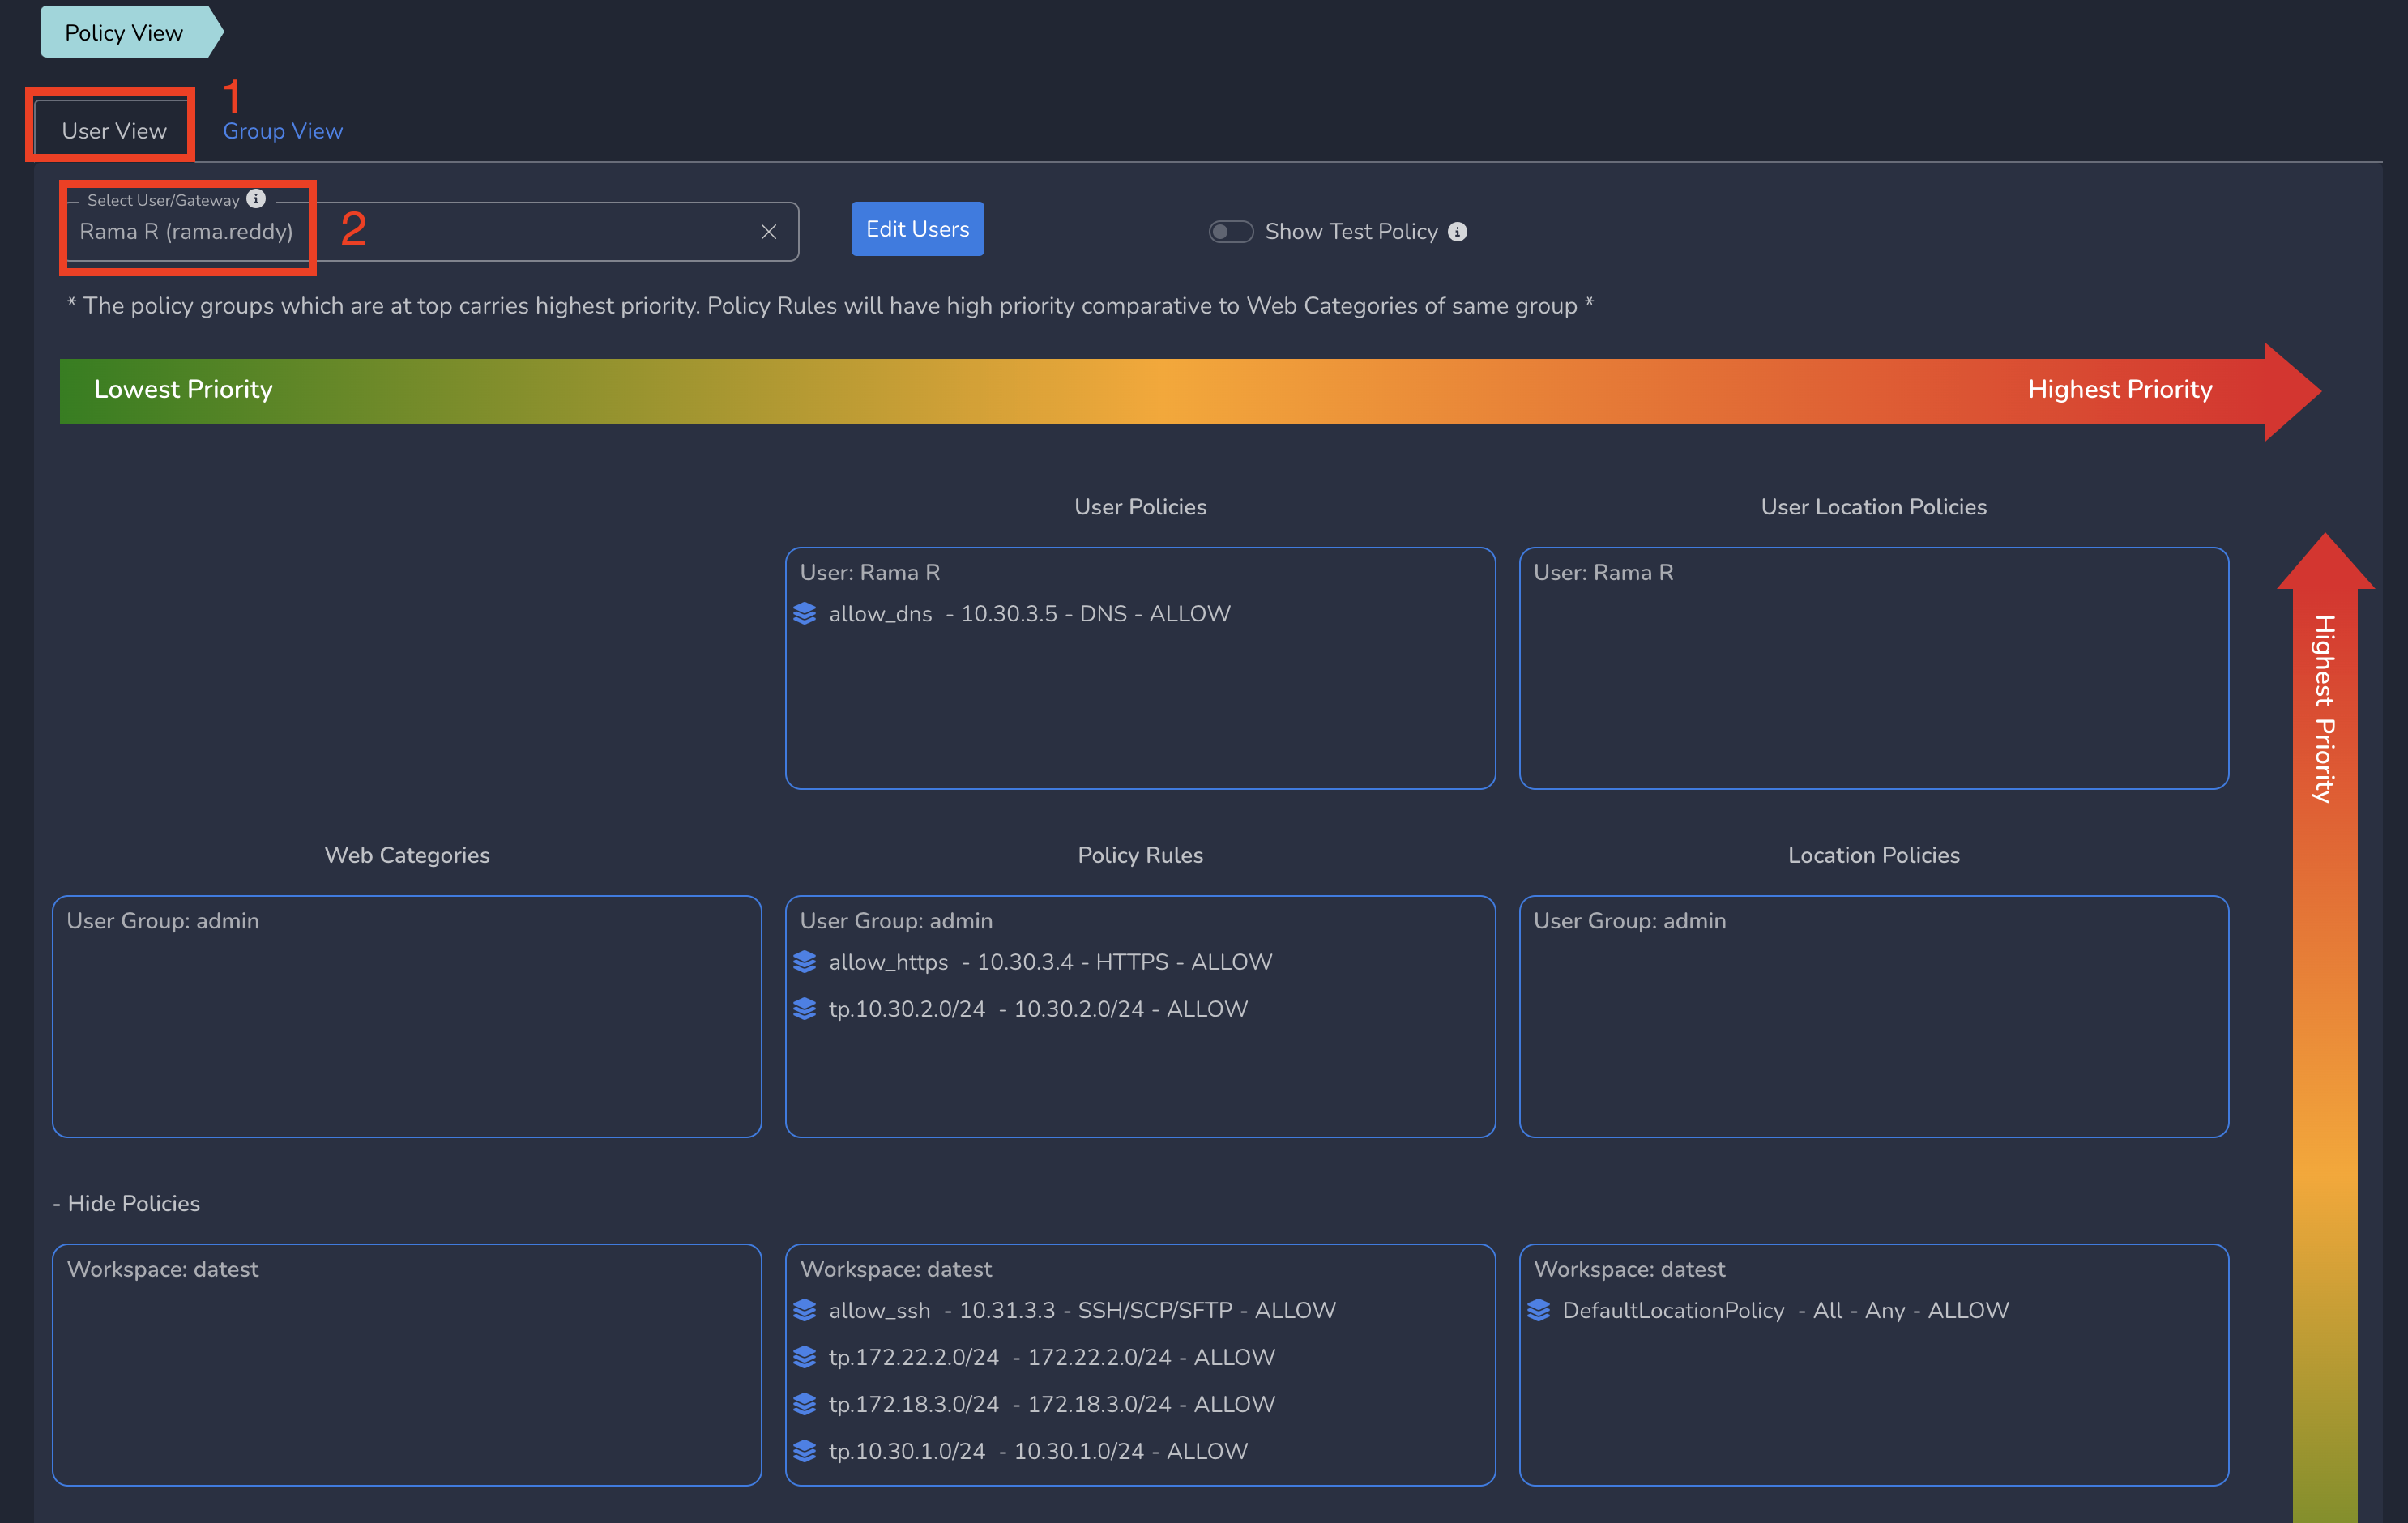
Figure 2: 3. Zero Trust Network Access Control for Private Applications | Exium ... Act II opens with a prelude in which Lula Chamberlain, an installation artist whose work is featured in the Kentucky Route Zero bonus content Limits & Demonstrations, receives a rejection notice from the Gaston Trust for Imagined Architecture. After reading this notice, Chamberlain sorts through a series of proposals for reclaiming spaces for purposes alternate to their current function, such as a proposal to reclaim a basketball court as a dog kennel. Following the prelude, the focus returns to Conway, Shannon, and Conway's dog. The three arrive at a six-story building known as the Bureau of Reclaimed Spaces. In the lobby they are told that in order to receive directions to Dogwood Drive they must first obtain an ingestion notice from within the Bureau. The receptionist suggests they seek out Lula Chamberlain, currently the Bureau's senior clerk. After a series of bureaucratic misdirections, the three manage to meet with Lula. She informs them that the directions to Dogwood Drive are at an off-site storage facility within an old church. Additionally she suggests Conway should seek out Doctor Truman for treatment of his injured leg. At the storage facility Conway chats about hobbies with the caretaker of the building and listens to a prerecorded sermon on the virtue of hard work while Shannon finds the record they are seeking. As they leave the building Conway collapses from his injury, hallucinating about Elkhorn Mine, and Shannon decides their first priority should be to find Doctor Truman and obtain treatment. Upon their return, the receptionist at the Bureau tells the group that Doctor Truman can be found at his house off the highway. The group leaves Route Zero and goes back above ground in search of Doctor Truman. Arriving at the site, the group discovers that the doctor's house has been torn down and replaced with a museum—the Museum of Dwellings. While searching the museum, they encounter a young boy named Ezra, who claims his brother is Julian, a giant eagle. Ezra tells them the Doctor now lives in the Forest, and offers to fly them using Julian. The group accepts and after traveling through the strange illusory forest, lands in the woods. As Conway's condition worsens, Shannon helps him continue, and finally locates Doctor Truman's house. Doctor Truman tells Conway his injury is severe but treatable, and prescribes him an anesthetic called Neurypnol TM. Act II ends as Conway succumbs to the drug, causing his vision to grow black and the walls of the house to pull away to reveal the forest beyond.
The Act opens with Conway dreaming of a previous conversation he had with Lysette. The two recall a tragic event involving Charlie, Lysette's son, and Lysette informs Conway of a new delivery to be made, which will be the last delivery of Lysette's antique shop. Conway awakens from the Neurypnol TM-induced sleep at Doctor Truman's house to find his injured leg replaced with a strange skeletal limb giving off a yellow glow. After returning to the Museum of Dwellings to find it closed for the night, Conway, Shannon and Ezra resume their search for Lula Chamberlain in Conway's truck. The three are quickly stopped again, however, after the truck's engine breaks down. While Shannon calls for a tow truck, two musicians, Johnny and Junebug, pass the group on a motorcycle with a sidecar, and after some discussion decide to help the group get the truck moving again in exchange for following them to the Lower Depths bar to watch their performance. The group agrees, traveling to the Lower Depths and talking with Harry, the bartender, who gives directions back to Route Zero. After their performance, Johnny and Junebug decide to accompany Conway, Shannon and Ezra on their travels. Upon returning to Route Zero, the group comes across a large cave dominated by a rock spire, known as the Hall of the Mountain King. There they find various types of vintage electronics in many states of disrepair, including a large amount set on fire. They come across an old man named Donald who appears fixated on a grand computer project involving a "mold computer" that is enhanced by black mold growing inside it, as well as a piece of software designed as a comprehensive simulation called Xanadu. Donald claims that Lula was one of the people who designed Xanadu along with him, and that she had left a long time ago, but that there may be a way to find her using Xanadu. However, as Xanadu is not working correctly after an apparent sabotage from creatures Donald calls the Strangers, the group must travel to the Place Where the Strangers Come From in order to seek out their help.
Conway and Shannon talk to the Strangers off-screen and, after returning with the solution, travel back with the group to the Hall of the Mountain King and fix Xanadu, using it to locate Lula. With Donald's help, she finds directions to Dogwood Drive, and tells the group to meet her at the Bureau of Reclaimed Spaces. After arriving at the Bureau, Conway receives Lula's directions, which involve taking a ferry from the Bureau down a river. While waiting for the ferry, Conway reveals what happened while he was talking with the Strangers - he and Shannon had gone via a hidden elevator to an underground whiskey distillery staffed by odd, indistinct glowing skeletons, identical in appearance to Conway's new leg. While at the factory, Conway is mistaken for a new hire as a shipping truck driver and coerced into taking a drink of a very expensive whiskey, and is subsequently roped into a job driving trucks for the distillery to pay it off. Act III ends with the ferry arriving.
Act IV takes place on and around The Mucky Mammoth tugboat ferry, as it goes around the underground river known as the Echo. Conway, Shannon, Ezra, Johnny, and Junebug continue downriver on the Echo with boat captain Cate, her assistant Will, and a passenger named Clara who plays the theremin. They make several short stops along the way - at a floating refueling station, a tiki bar called the Rum Colony, a waterside telephone booth, a psychological research facility called the Radvansky Center, and a cypress-covered island rich with edible mushrooms. Cate needs to deliver a package to a telephone exchange located in a flooded train tunnel, but the tugboat cannot pass through the area without disturbing a bat sanctuary, so Conway and Shannon agree to take a dinghy to reach the exchange station. They pass by a monument to the Elkhorn Mine disaster and then through the bat sanctuary. Conway, who has been drinking and whose behavior had become increasingly erratic, sees a boat full of glowing skeletons, similar to those at the whiskey distillery, and remarks that he's been seeing them repeatedly on the river journey. He tells Shannon he wants to take the job at the distillery and pass his delivery truck on to her; she is disturbed by his plan. Shannon delivers the package to Poppy, the lone remaining exchange operator, and when she turns around to re-board the dinghy, she finds that Conway has turned completely into a skeleton, and has boarded a skiff with two other skeletons, departing with them. Shannon continues down the river alone on the dinghy and rendezvouses with the rest of the Mucky Mammoth passengers and crew at Sam & Ida's, a seafood restaurant. They eat and converse with the proprietors, then travel to a neighborhood of houseboats, where Clara gives a performance on theremin. Their last stop is the Silo of Late Reflections, where Shannon, Clara, Johnny, Junebug, and Ezra all disembark and unload Conway's truck. There is no clear path to get the truck from the Silo up to the surface; nevertheless, Shannon resolves to continue trying to make Conway's delivery to Dogwood Drive.
Kentucky Route Zero has received positive reviews from critics. GameSpot referred to it as being "beautiful and mysterious enough to grip you," and IGN called it "a damn fine example of what makes the medium of video games so special." PC Gamer stated: "[It is a] powerfully evocative and beautiful subversion of point-and-click rote, but occasionally opaque and disorienting." The A.V. Club noted that "KRZ really is the masterpiece critics have been lauding it as for years" and that "anyone with an interest in storytelling, existential mysteries, and the way art can reflect our poor and hollowed world should play it." The Washington Post called it "one of the most important games of the [2010s]." It was nominated for the Games For Impact award at The Game Awards 2020 and for the 2021 Nebula Award for Best Game Writing. Kentucky Route Zero: TV Edition was nominated for the Narrative award and won the Original Property award at the 2021 BAFTA Games Awards.
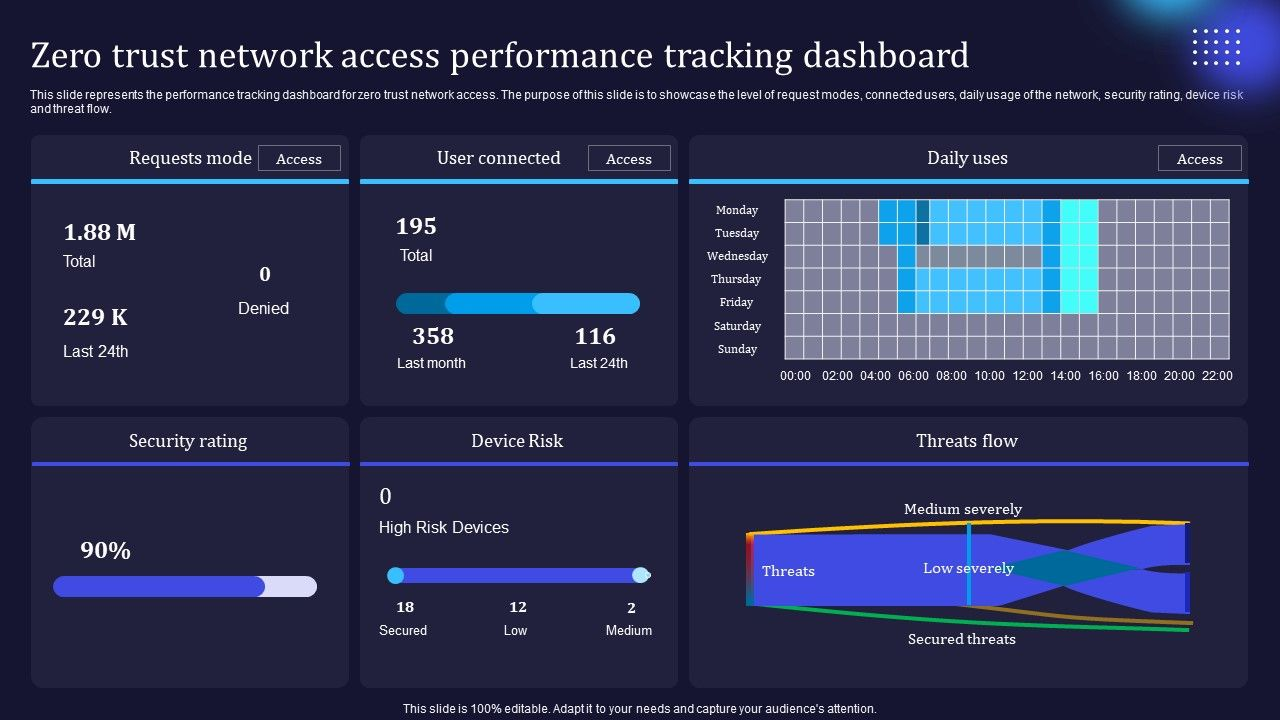
During the 24th Annual D.I.C.E. Awards, the Academy of Interactive Arts & Sciences nominated Kentucky Route Zero for Adventure Game of the Year, as well as Outstanding Achievement in Game Direction, in Story, and for an Independent Game. Figure 3: Zero Trust Model Zero Trust Network Access Performance Tracking Protecting enterprise data and resources has become increasingly challenging. Many users need access from anywhere, at any time, from any device to support the organizationâIIs mission. Data is created, stored, transmitted, and processed across different organizationsâII environments, which are distributed across on-premises and multiple clouds to meet ever-evolving business use cases. It is no longer feasible to simply protect data and resources at the perimeter of the enterprise environment or to assume that all users, devices, applications, and services within it can be trusted.
A ZTA enables secure authorized access to assetsâIImachines, applications and services running on them, and associated data and resourcesâIIwhether located on-premises or in the cloud, for a hybrid workforce and partners based on an organizationâIIs defined access policy. For each access request, ZTA explicitly verifies the context available at access timeâIIthis includes both static user profile information or non-person entity information, such as the requesterâIIs identity and role; and dynamic information such as geolocation, the requesting deviceâIIs health and credentials, the sensitivity of the resource, access pattern anomalies, and whether the request is warranted and in accordance with the organizationâIIs business process logic. If the defined policy is met, a secure session is created to protect all information transferred to and from the resource. A real-time, risk-based assessment of resource access and access pattern anomaly detection with continuous policy evaluation is performed to establish and maintain the access. A ZTA can also protect organizations from non-organizational resources that their users and applications may connect to, helping to stop threats originating from outside of the organizationâIIs control.
NCCoE has collaborated with ZTA technology providers to build numerous example ZTA solutions and demonstrate their ability to meet the tenets of ZTA described in NIST SP 800-207. The goal of the solutions is to enforce corporate security policy dynamically and in near-real-time to restrict access to authenticated, authorized users, devices, and non-person entities while flexibly supporting a complex set of business outcomes involving both remote and on-premises workforces, use of the cloud, partner collaboration, and support for contractors. The example solutions are designed to demonstrate the ability to protect against and detect attacks and malicious insiders. They showcase the ability of ZTA products to interoperate with existing enterprise and cloud technologies while trying to minimize the impact on end-user experience.
The project can help organizations plan how to evolve their existing enterprise environments to ZTA, starting with an assessment of their current resources, strengths, and weaknesses, and setting mile-stones along a path of continuous improvement, gradually bringing them closer to achieving the ZTA goals they have prioritized based on risk, cost, resources, and their unique mission. The goal is to enable organizations to thoughtfully apply ZTA controls that best protect their business while enabling them to operate as they need to.
Throughout this project, numerous challenges organizations may face in implementing ZTA have been identified, including the following: Perception that ZTA is suited only for large organizations and requires significant investment rather than understanding that ZTA is a set of guiding principles suitable for organizations of any size Concern that ZTA might negatively impact the operation of the environment or end-user experience Lack of resources to develop necessary policies and a pilot or proof-of-concept implementation needed to inform a transition plan Leveraging existing investments and balancing priorities while making progress toward a ZTA via modernization initiatives Lack of understanding regarding what additional skills and training administrators, security personnel, operators, end users, and policy decision-makers may require Lack of adequate asset inventory and management needed to fully understand the business applications, assets, and processes that need to be protected, with no clear understanding of the criticality of these resources Lack of adequate digital definition, management, and tracking of user roles across the organization needed to enforce fine-grained, need-to-know access policy for specific applications and services 2. System Architecture & Core Working Principles Lack of visibility of the organizationâIIs communications and usage patternsâIIlimited understanding of the transactions that occur between an organizationâIIs subjects, assets, applications, and services, and absence of the data necessary to identify these communications and their specific flows Lack of information regarding everything that encompasses the organizationâIIs attack surface. Organizations can usually address threats with traditional security tools in the layers that they currently manage and maintain such as networks and applications, but elements of a ZTA may extend beyond their normal purview. False assumptions are often made in understanding the health of a device as well as its exposure to supply chain risks.
Integrating various types of commercially available technologies of varying maturities, assessing capabilities, and identifying technology gaps to build a complete ZTA Lack of a standardized policy to distribute, manage, and enforce security policy, causing organizations to face either a fragmentary policy environment or non-interoperable components Lack of common understanding and language of ZTA across the community and within the organization, gauging the organizationâIIs ZTA maturity, determining which ZTA approach is most suitable for the business, and developing an implementation plan There is not a single ZTA that fits all. ZTAs need to be designed and implemented for each organization based on the organizationâIIs requirements and risk tolerance, as well as its existing invested technologies and environments.
Organizations participating in this project submitted their capabilities in response to an open call in the Federal Register for all sources of relevant security capabilities from academia and industry (vendors and integrators). Respondents with relevant capabilities or product components (identified as âIITechnology Partners/CollaboratorsâII herein) signed a CRADA to collaborate with NIST in a consortium to build example ZTA solutions.
Each of these technology partners and collaborators has described the relevant products and capabilities they bring to this ZTA effort in the following subsections. The NCCoE does not certify, validate, or endorse products or services. We demonstrate the capabilities that can be achieved by using participantsâII contributed technology. Your organizationâIIs information security experts should identify the products that will best integrate with your existing tools and IT system infrastructure. Your organization can adopt this solution or one that adheres to these guidelines entirely, or you can use this guide as a starting point for tailoring and implementing parts of a solution.
Appgate is the secure access company. It empowers how people work and connect by providing solutions purpose-built on zero trust security principles. This security approach enables fast, simple, and secure connections from any device and location to workloads across any IT infrastructure in cloud, on-premises, and hybrid environments. The Appgate SDP solution has been designed with the intent to provide all the critical elements of NIST SP 800-207. The Appgate SDP has a controller that offers policy administrator (PA) and policy engine (PE) functionality and gateways that offer policy enforcement point (PEP) functionality. Appgate SDP natively integrates with components via representational state transfer (REST) application programming interfaces (APIs) and metadata. By providing highly performant, scalable, secure, integrated, and cloaked zero trust access, Appgate SDP is able to ensure that the correct device and user (under the appropriate conditions at that moment in time) are connected. For more information about Appgate SDP, see How Appgate SDP Works .
AWS provides a platform in the cloud that hosts private and public sector agencies in most countries around the world. AWS offers more than 200 services which include compute, storage, networking, database, analytics, application services, deployment, management, developer, mobile, IoT, artificial intelligence (AI), security, and hybrid and enterprise applications. Additionally, AWS provides several security-related services and features such as Identity and Access Management (IAM), Virtual Private Cloud (VPC), PrivateLink, and Security Hub, allowing AWS customers to build and deliver their services worldwide with a high degree of confidence and assurance. AWSâIIs array of third-party applications provides complementary functionality that further extends the capabilities of the AWS environment. To learn more about security services and compliance on AWS, please visit Security, Identity, and Compliance on AWS .
The following subsections briefly list some AWS services relevant to ZTA that are being provided in support of this project, organized by category of service. IAM : AWS Identity and Access Management (IAM) provides fine-grained access control across all of AWS. With IAM, organizations can specify who can access which services and resources, and under which conditions. With IAM policies, organizations manage permissions to their workforce and systems to ensure least-privilege permissions.
Cognito : Amazon Cognito lets organizations add user sign-up, sign-in, and access control to web and mobile apps quickly and easily. Cognito scales to millions of users and supports sign-in with social identity providers, such as Apple, Facebook, Google, and Amazon, and enterprise identity providers via Security Assertion Markup Language (SAML) 2.0 and OpenID Connect.
VPC : Amazon Virtual Private Cloud (Amazon VPC) gives organizations full control over their virtual networking environment, including resource placement, connectivity, and security. A couple of key security features found in VPCs are network access control lists (ACLs) that act as firewalls for controlling traffic in and out of subnets, and security groups that act as host-based firewalls for controlling traffic to individual Amazon Elastic Compute Cloud (Amazon EC2) instances.
PrivateLink : AWS PrivateLink provides private connectivity between VPCs, AWS services, and on-premises networks without exposing traffic to the public internet. AWS PrivateLink makes it easy to connect services across different accounts and VPCs to significantly simplify network architecture. Network Firewall: AWS Network Firewall is a managed service that makes it easy to deploy essential network protections for all of an organizationâIIs Amazon VPCs.
Web Application Firewall : AWS WAF is a web application firewall (WAF) that helps protect web applications and APIs against common web exploits and bots that may affect availability, compromise security, or consume excessive resources. Route 53 : Amazon Route 53 is a highly available and scalable cloud Domain Name System (DNS) web service. It is designed to give developers and businesses an extremely reliable and cost-effective way to route end users to internet applications.
Amazon Route 53 is fully compliant with IPv6 as well. With Route 53 Resolver an organization can filter and regulate outbound DNS traffic for its VPC. EC2 : Amazon EC2 is a web service that provides secure, resizable compute capacity in the cloud. It is designed to make web-scale cloud computing easier for developers.
ECS : Amazon Elastic Container Service (Amazon ECS) is a fully managed container orchestration service that makes it easy to deploy, manage, and scale containerized applications. EKS : Amazon Elastic Kubernetes Service (Amazon EKS) is a managed container service to run and scale Kubernetes applications in the cloud or on-premises.
EBS : Amazon Elastic Block Store (Amazon EBS) is an easy-to-use, scalable, high-performance block-storage service designed for Amazon EC2. 3. Software Implementation, Frameworks & Protocols S3 : Amazon Simple Storage Service (Amazon S3) is an object storage service that offers scalability, data availability, security, and performance.
Systems Manager : AWS Systems Manager is the operations hub for AWS applications and resources, and it is broken into four core feature groups: Operations Management, Application Management, Change Management, and Node Management. Security Hub : AWS Security Hub is a cloud security posture management service that performs security best practice checks, aggregates alerts, and enables automated remediation.
CloudWatch : Amazon CloudWatch is a monitoring and observability service built for DevOps engineers, developers, site reliability engineers (SREs), IT managers, and product owners. CloudWatch provides data and actionable insights to monitor applications, respond to system-wide performance changes, and optimize resource utilization. CloudTrail : AWS CloudTrail monitors and records account activity across AWS infrastructures, giving organizations control over storage, analysis, and remediation actions.
GuardDuty : Amazon GuardDuty is a threat detection service that continuously monitors AWS accounts and workloads for malicious activity and delivers detailed security findings for visibility and remediation. Firewall Manager : AWS Firewall Manager is a security management service which allows organizations to centrally configure and manage firewall rules across their accounts and applications in AWS Organizations.
Cisco Systems, or Cisco, delivers collaboration, enterprise, and industrial networking and security solutions. The companyâIIs cybersecurity team, Cisco Secure, is one of the largest cloud and network security providers in the world. CiscoâIIs Talos Intelligence Group, the largest commercial threat intelligence team in the world, is comprised of world-class threat researchers, analysts, and engineers, and supported by unrivaled telemetry and sophisticated systems. The group feeds rapid and actionable threat intelligence to Cisco customers, products, and services to help identify new threats quickly and defend against them. Cisco solutions are built to work together and integrate into your environment, using the âIInetwork as a sensorâII and âIInetwork as an enforcerâII approach to both make your team more efficient and keep your enterprise secure. Learn more about Cisco at Cisco Security .
Duo is a PE, PA, and PEP for users and their devices. It delivers simple, safe access to all applications âII on-premises or in the cloud âII for any user, device, or location. It makes it easy to effectively implement and enforce security policies and processes, using strong authentication to reduce the risk of data breaches due to compromised credentials and access from unauthorized devices.
Cisco ISE is a network central PDP that includes both the PE and PA to help organizations provide secure access to users, their devices, and the non-user devices in their network environment. It simplifies the delivery of consistent and secure access control to PEPs across wired and wireless multi-vendor networks, as well as remote VPN connections. It controls switches, routers, and other network devices as PEPs, enabling granular control of every connection down to the individual port, delivering a dynamic, granular, and automated approach to policy enforcement that simplifies the delivery of highly secure, microsegmented network access control. ISE is tightly integrated with and enhances network and security devices, allowing it to transform the network from a simple conduit for data into an intuitive and adaptive security sensor and enforcer that acts to accelerate the time to detection and time to resolution of network threats.
Cisco Secure Endpoint addresses the full life cycle of the advanced malware problem before, during, and after an attack. It uses global threat intelligence to strengthen defenses, antivirus to block known malware, and static and dynamic file analysis to detect emerging malware, continuously monitoring file and system activity for emerging threats. When something new is detected, the solution provides a retrospective alert with the full recorded history of the file back to the point of entry, and the rich contextual information needed during a potential breach investigation to both prioritize remediation and create response plans.
As a policy input point, Secure Endpoint delivers deep visibility, context, and control to rapidly detect, contain, and remediate advanced threats if they evade front-line defenses. It can also eliminate malware with a few clicks and provide a cost-effective security solution without affecting operational efficiency. Cisco FTD is a threat-focused, next-generation firewall with unified management. It provides advanced threat protection before, during, and after attacks. By delivering comprehensive, unified policy management of firewall functions, application control, threat prevention, and advanced malware protection, from network to endpoint, it increases visibility and security posture while reducing risk.
Cisco Secure Network Analytics aggregates and analyzes network telemetry âII information generated by network devices âII to turn the network into a sensor. As a policy input point, it provides enterprise-wide network visibility and applies advanced security analytics to detect and respond to threats in real time. It delivers end-to-end network visibility on-premises, in private clouds, and in public clouds. Secure Network Analytics detects a wide range of network and data center issues ranging from command-and-control (C&C) attacks to ransomware, from distributed denial of service (DDoS) attacks to illicit cryptomining, and from malware to insider threats.
Secure Network Analytics can be deployed on-premises as a hardware appliance or virtual machine (VM), or cloud-delivered as a SaaS solution. It works with the entire Cisco router and switch portfolio as well as a wide variety of other security solutions. Cisco ETA helps illuminate the dark corners of encrypted traffic without decryption by using new types of data elements and enhanced NetFlow telemetry independent of protocol details. Cisco ETA can help detect malicious activity in encrypted traffic by applying advanced security analytics. At the same time, the integrity of the encrypted traffic is maintained because there is no need for bulk decryption.
Cisco SecureX is an extended detection and response (XDR) cloud-native integrated threat response platform within the Cisco Secure portfolio. Its open, extensible integrations connect to the infrastructure, providing unified visibility and simplicity in one location. It maximizes operational efficiency to secure the network, users and endpoints, cloud edge, and applications. Cisco SecureX radically reduces the dwell time and human-powered tasks involved with detecting, investigating, and remediating threats to counter attacks, or securing access and managing policy to stay compliant. The time savings and better collaboration involved with orchestrating and automating security across SecOps, ITOps, and NetOps teams help advance the security maturity level.
Cisco Endpoint Security Analytics (CESA) analyzes endpoint telemetry generated by the Network Visibility Module (NVM), which is built into the Cisco AnyConnect® Secure Mobility Client. CESA feeds Splunk Enterprise software to analyze NVM data provided by endpoints to uncover endpoint-specific security risks and breaches. This data includes information about data loss, unapproved applications and SaaS usage, security evasion, unknown malware, user behavior when not connected to the enterprise, endpoint asset inventory, and destination allowlists and denylists.
Cisco AnyConnect Secure Mobility Client is a unified endpoint software client compatible with several of todayâIIs major enterprise mobility platforms. It helps manage the security risks associated with extended networks. Built on foundational VPN technology, it extends beyond remote-access capabilities to offer user-friendly, network-based security including: Cisco network devices do more than move packets on the network; they provide a platform to improve user experience, unify management, automate tasks, analyze activity, and enhance security across the enterprise. In a zero-trust environment, Cisco switches, routers, and other devices provide continuous visibility using the âIInetwork as a sensorâII to monitor network activity, reporting 100% of NetFlow and other metadata. These devices act as PEPs utilizing a âIInetwork as an enforcerâII approach to microsegment network access control to each port and enable dynamic and automated policy enforcement. This policy enforcement simplifies the delivery of highly secure control across environments.
TodayâIIs networks include applications running in a hybrid multi-cloud environment that uses bare-metal, virtualized, cloud-based and container-based workloads. A key challenge is how to better secure applications and data without compromising agility. Cisco Secure Workload (formerly known as Cisco Tetration) is designed to address this security challenge by providing comprehensive workload protection by bringing security closer to applications and tailoring the security posture based on the application behavior. Secure Workload achieves this by using advanced machine learning and behavior analysis techniques. This platform provides a ready-to-use solution to support the following security use cases: Microsegmentation policies that allow implementation of a zero trust model: It enforces policies that allow only the traffic required for business purposes Detection of common vulnerabilities and exposures associated with the software packages installed on the resources Enforcement of policies that proactively quarantine servers when vulnerabilities are detected, blocking communication 4. Practical Deployment, Analysis & Case Studies DigiCert is a global provider of digital trust, enabling individuals and businesses to engage online with the confidence that their footprint in the digital world is secure. DigiCert® ONE, the platform for digital trust, provides organizations with centralized visibility and control over a broad range of public and private trust needs, securing websites, enterprise access and communication, software, identity, content, and devices. For more information, visit digicert.com .
DigiCert CertCentral is used to provision publicly trusted Transport Layer Security (TLS) server authentication certificates. CertCentral relies on DigiCertâIIs publicly trusted root certificates with excellent ubiquity to provide the necessary interoperability with the widest range of third-party products. DigiCert Enterprise PKI Manager is a digital certificate management solution for enterprise identity and access public key infrastructure (PKI) use cases. Enterprise PKI Manager simplifies and streamlines certificate lifecycle management for identity and access of users, devices, and applications, supporting a broad array of certificate types with automated workflows, preconfigured templates, multiple enrollment and authentication methods, and a rich ecosystem of integrated technology partners. It is part of the DigiCert family of products delivering digital trust solutions. Enterprise PKI Manager is built on DigiCert ONEâIIs modern, containerized architecture, delivering scalability capable of serving high volumes of certificates, supporting flexible deployment in cloud, on-premises, or hybrid deployment models, and enabling dynamic and rapid intermediate Certificate Authority (ICA) creation to meet the diverse needs of different business groups.
F5 empowers its customers to create, secure, and operate applications that deliver extraordinary digital experiences. Fueled by automation and AI-driven insights, these applications will naturally adapt based on their changing environmentâIIso companies can focus on their core business, boost speed to market, improve operations, and build trust with their customers. By enabling these adaptive applications, F5 with NGINX and F5 Distributed Cloud Services technologies offers a comprehensive suite of solutions for every digital organization.
The BIG-IP product family provides full proxy security, application intelligence, and scalability for application traffic. As the amount of traffic grows or shrinks, BIG-IP can be adjusted or it can request addition or removal of application servers. It provides rich application traffic programmability to further enhance application security and application traffic steering requirements. In addition, BIG-IPâIIs rich control plane programmability allows for integrations into on-premises orchestration engines, cloud automation/orchestration, and continuous integration/continuous delivery (CI/CD) pipelines, and the ability to deliver application security in a DevSecOps manner. All capabilities can be propagated as common policy throughout the enterprise regardless of whether an organization utilizes F5 hardware or a virtualized on-premises or cloud environment.
BIG-IP modules provide the ability to layer on additional capabilities. The modules being considered for this project are discussed in the subsections below. BIG-IP LTM is an enterprise-class load balancer providing granular layer 7 control, Secure Sockets Layer (SSL) offloading, and acceleration capabilities. It allows for massive scaling of traditional and modern apps across the enterprise and provides visibility into TLS-encrypted streams, TLS security enforcement, and Federal Information Processing Standards (FIPS) certified cryptography.
BIG-IP APM integrates and unifies secure user access to ensure the correct people have the correct access to the correct applicationsâIIanytime, anywhere, providing the ability to authenticate users into applications allowing for granular application access control and zero trust capabilities across the application landscape. BIG-IP APM sits in front of applications and APIs to enforce application authentication and access control for each user as part of zero trust.
BIG-IP WAF provides the flexibility to deploy WAF services closer to the apps so theyâIIre protected wherever they reside. It has the ability to virtually patch applications for security vulnerabilities such as the latest Common Vulnerabilities and Exposures (CVE) entry without application code changes. It also reduces unwanted application traffic, allowing the application to be more responsive to its intended users while providing complete visibility into the application traffic. WAF provides API security, protecting against web application security concerns. WAF provides secure communication and vetting of traffic to APIs and applications.
NGINX is a cloud-native, easy-to-use reverse proxy, load balancer, and API gateway. It integrates advanced monitoring, strengthens security controls, and orchestrates Kubernetes containers. NGINX Ingress Controller combines software load balancing with simplified configuration based on standard Kubernetes Ingress resources or custom NGINX Ingress resources to ensure that applications in a Kubernetes cluster are delivered reliably, securely, and at high velocity. It provides security to Kubernetes-based microservices and APIs using API gateway and WAF capabilities. The Ingress Controller protects application and API containers in the Kubernetes environment by enforcing security on all traffic entering the Kubernetes node.
NGINX Plus is an all-in-one load balancer, web server, content cache, WAF, and API gateway. NGINX Plus is built on NGINX Open Source. It is intended to reduce complexity and simplify management by consolidating several capabilities, including reverse proxy and TLS termination, into a single elastic ingress/egress tier. It acts as a webserver to server applications that are secured by the systemâIIs zero trust capabilities.
NGINX Service Mesh scales from open-source projects to a fully supported, secure, and scalable enterprise-grade solution. It provides a turnkey service-to-service solution featuring a unified data plane for ingress and egress Kubernetes management in a single configuration. NGINX Service Mesh provides for mutual TLS authentication (mTLS) enforcement, rate limiting, quality of service (QoS), and an API gateway to enforce security at each pod, securing pods from both north/south (N/S) and east/west (E/W) traffic and allowing for zero trust enforcement for all pod traffic.
Forescout delivers automated cybersecurity across the digital terrain. It empowers its customers to achieve continuous alignment of their security frameworks with their digital realities, across all asset types - IT, IoT, OT, and Internet of Medical Things (IoMT). Forescout enables organizations to manage cyber risk through automation and data-powered insights. The Forescout Platform provides complete asset visibility of connected devices, continuous compliance, network segmentation, network access control, and a strong foundation for zero trust. Forescout customers gain data-powered intelligence to accurately detect risks and quickly remediate cyberthreats without disruption of critical business assets. For more information, see About Forescout .
Forescout eyeSight delivers comprehensive device visibility across an organizationâIIs entire digital terrain - without disrupting critical business processes. It discovers every IP-connected device, auto-classifies it, and assesses its compliance posture and risk the instant the device connects to the network. For more information, see eyeSight . Forescout eyeControl provides flexible and frictionless network access control for heterogeneous enterprise networks. It enforces and automates zero trust security policies for least-privilege access on all managed and unmanaged assets across an organizationâIIs digital terrain. Policy-based controls can continuously enforce asset compliance, proactively reduce attack surfaces, and rapidly respond to incidents. For more information, see eyeControl .
Forescout eyeSegment accelerates zero trust segmentation. It simplifies the design, planning, and deployment of non-disruptive, dynamic segmentation across an organizationâIIs digital terrain to reduce attack surface and regulatory risk. For more information, see eyeSegment . Forescout eyeExtend automates security workflows across disparate products. It shares device context between the Forescout platform and other IT and security products, automates policy enforcement across disparate tools, and accelerates system-wide response to mitigate risks. For more information, see eyeExtend .
Google Cloud brings the best of GoogleâIIs innovative products and services to enable enterprises of all sizes to create new user experiences, transform their operations, and operate more efficiently. GoogleâIIs mission is to accelerate every organizationâIIs ability to digitally transform its business with the best infrastructure, platform, industry solutions, and expertise. Google Cloud helps customers protect their data using the same infrastructure and security services Google uses for its own operations, defending against the toughest threats. Google pioneered the zero trust model at the core of its services and operations, and it enables its customers to do the same with its broad portfolio of solutions.
BeyondCorp Enterprise (BCE) is a zero trust solution, built on the Google platform and global network, which provides customers with simple and secure access to applications and cloud resources and offers integrated threat and data protection. It leverages the Chrome Browser and the Google Cloud platform (GCP) to protect and monitor proxy traffic from an organizationâIIs network. It allows customers to enforce context-aware policies (using factors such as identity, device posturing, and other signal information) to authorize access to SaaS applications and resources hosted on Google Cloud, third-party clouds, or on-premises. This solution is built from GoogleâIIs own approach of shifting access controls from the network perimeter to individual users and devices, allowing for secure access without the need for a VPN.
Context-aware access proxy (identity-aware proxy): Globally deployed proxy built on the GCP that leverages identity, device, and contextual information to apply continuous authorization access decisions to applications and VMs deployed in real-time on GCP, other clouds, or on-premises data centers. Google Chrome: The Secure Enterprise Browser is a core component of the BeyondCorp zero trust offering. Chrome provides agentless zero trust access to web apps hosted on GCP, other clouds (e.g., AWS, Azure), or on-premises data centers.
Data loss prevention (DLP): DLP features help businesses prevent sensitive data from being leaked to unauthorized users. 5. Performance Evaluation & Extended Technical Observations Threat protection: Chrome Secure Enterprise Browser includes a number of features to protect users from malware, phishing, and other online threats.
Device posturing: Ability to collect detailed information from endpoint devices. This includes areas like OS version, encrypted state, processes, certificates, and many other areas that can be used as part of a least privilege access model. Advanced reporting: Deep visibility into web traffic and user actions within web applications and the data being transmitted between a device and application.
Legacy client application access (IAP TCP Forwarding): Software kit that enables zero trust access to non-HTTP, thick-client apps hosted in the GCP, other clouds, or on-premises data centers via an Identity-Aware Proxy (IAP). Chronicle Security Orchestration, Automation, and Response (SOAR): Cloud-based security platform that combines Google ChronicleâIIs threat detection and response capabilities with Google SOARâIIs automation and orchestration capabilities.
This integration allows organizations to quickly and easily automate security workflows, reducing the time it takes to respond to threats and improving their overall security posture. Leveraging machine learning to identify and prioritize threats allows for reducing the need for manual analysis. In addition, Chronicle SOAR automates common incident response tasks, such as triaging alerts, investigating incidents, and remediating vulnerabilities, providing a more cohesive ZTA strategy.
Data protection: Built-in Chrome browser capabilities to detect and prevent sensitive data loss, including prevention of copying, pasting, printing, and uploading/downloading of protected content in and out of the browser. Additional capabilities include preventing the accidental and intentional exfiltration of corporate data, and enforcing data protection policies across applications.
Advanced threat analytics: ChronicleâIIs security analytics platform helps organizations detect, investigate, and respond to threats. Chronicle collects and normalizes security telemetry from across an organizationâIIs infrastructure, including logs, network traffic, and application data. Chronicle then uses machine learning to identify and prioritize threats. Chronicle also provides tools for investigating threats and responding to incidents.
Threat protection: Built-in Chrome browser capabilities include filtering and blocking harmful or unauthorized URLs in real-time, identifying phishing sites and malicious content in real-time, stopping suspicious file and malware transfers, providing sandbox detonation capabilities, and protecting user credentials and passwords. BeyondCorp Alliance ecosystem integrations: A collection of integrations from BeyondCorp Alliance member partners that enable organizations to share signal information from EDR, MDM, enterprise mobility management (EMM), and other device or ecosystem endpoints to use in access policy decisions. (Members include Broadcom, Check Point, Citrix, CrowdStrike, InTune, Jamf, Lookout, and Palo Alto Networks.) Hybrid Network Endpoint Group (NEG): Private connectivity from Google Cloud to applications outside of Google Cloud (i.e., hosted by other clouds or on-premises data centers.) VPN interconnect: Private connectivity via an interconnect from Google Cloud to applications outside of Google Cloud (i.e., hosted by other clouds or on-premises data centers.) App connector: Secure internet-based connectivity from Google Cloud to applications outside of Google Cloud (i.e., hosted by other clouds or on-premises data centers via containerized network appliance.) Cloud Armor: Provides a WAF service that protects your HTTP(S)-based applications from common web attacks, including DDoS, cross-site scripting (XSS), and SQL injection. Cloud Armor is a regional service that can be used to protect applications running on GCP or on-premises.
Google Platform: GoogleâIIs public cloud computing services including data management, application development, storage, hybrid & multi-cloud, security, and AI and ML that run on Google infrastructure. Google Network: GoogleâIIs global backbone with 146 edge locations in over 200 countries and territories provides low-latency connections, integrated DDoS protection, elastic scaling, and private transit.
International Business Machines Corporation (IBM) is an American multinational technology corporation headquartered in Armonk, New York, with operations in over 171 countries. IBM produces and sells computer hardware, middleware, and software, and provides hosting and consulting services in areas ranging from mainframe computers to nanotechnology. IBM is also a major research organization, holding the record for most annual U.S. patents generated by a business (as of 2020) for 28 consecutive years. IBM has a large and diverse portfolio of products and services that range in the categories of cloud computing, AI, commerce, data and analytics, IoT, IT infrastructure, mobile, digital workplace, and cybersecurity.
IBM Security® Trusteer® solutions help detect fraud, authenticate users, and establish identity trust across a digital user journey. Trusteer uses cloud-based intelligence, AI, and ML to holistically identify new and existing users while improving the overall user experience by reducing the friction created with traditional forms of MFA. Within a ZTA, Trusteer acts as a risk engine that improves the efficacy of policy decisions enforced by various identity and access management solutions.
IBM Security QRadar® XDR suite provides a single unified workflow across an organizationâIIs security tools. Built on a unified cross-domain security platform, IBM Cloud Pak® for Security, the open architecture of QRadar XDR suite enables organizations to integrate their EDR, SIEM, network detection and response (NDR), security orchestration, automation, and response (SOAR), and threat intelligence solutions in support of a ZTA.
IBM Security QRadar SIEM helps security teams detect, prioritize, and respond to threats across the enterprise. As an integral part of an organizationâIIs XDR and zero trust strategies, it automatically aggregates and analyzes log and flow data from thousands of devices, endpoints, and apps across the network, providing single, prioritized alerts to speed incident analysis and remediation. QRadar SIEM is available for on-premises and cloud environments.
IBM Security QRadar SOAR is designed to help security teams respond to cyberthreats with confidence, automate with intelligence, and collaborate with consistency. It guides a team in resolving incidents by codifying established incident response processes into dynamic playbooks. The open and agnostic platform helps accelerate and orchestrate response by automating actions with intelligence and integrating with other security tools.
IBM Security QRadar XDR Connect is a cloud-native, open XDR solution that saves time by connecting tools, workflows, insights, and people. The solution adapts to a teamâIIs skills and needs, whether the user is an analyst looking for streamlined visibility and automated investigations or an experienced threat hunter looking for advanced threat detection. XDR Connect empowers organizations with tools that strengthen their zero trust model and enable them to be more productive.
Modernized, modular IBM Security Verify provides deep, AI-powered context for both consumer and workforce identity and access management. It protects users and apps, inside and outside the enterprise, with a low-friction, cloud-native, SaaS approach. Verify delivers critical features for supporting a zero trust strategy based on least privilege and continuous verification, including single sign-on (SSO), multi-factor and passwordless authentication, adaptive access, identity lifecycle management, and identity analytics.
IBM Security MaaS360® with Watson protects devices, apps, content, and data, which allows organizations to rapidly scale their hybrid workforce and BYOD initiatives. IBM Security MaaS360 can help build a zero trust strategy with modern device management. And with Watson, organizations can take advantage of contextual analytics via AI for actionable insights. IBM Security Guardium® Insights is a data security hub for the modern data source environment. It builds and automates compliance policy enforcement and streams and centralizes data activity across a multi-cloud ecosystem. It can apply advanced analytics to uncover data risk insights. Guardium Insights can complement and enhance existing Guardium Data Protection deployments or be installed on its own to help solve compliance and cloud data activity monitoring challenges. Built on a unified cross-domain security platform, IBM Cloud Pak for Security, Guardium Insights can deploy and scale in any data environment âII as well as integrate and share insights with major security tools such as IBM Security QRadar XDR, Splunk, ServiceNow, and more, in support of a ZTA.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Identity%20threat%20detection%20and%20response • https://en.wikipedia.org/wiki/Market%20for%20zero-day%20exploits • https://en.wikipedia.org/wiki/Kentucky%20Route%20Zero • https://pages.nist.gov/zero-trust-architecture/VolumeA/ProjectOverview.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Zero Trust Network Access Simulation System Project.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |