Complete Technical Paper Content — Zero Trust Network Architecture
Overview & System Context
Zero Trust Network Architecture: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9511 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Zero trust architecture (ZTA) is a design and implementation strategy of IT systems. The principle is that users and devices should not be trusted by default, even if they are connected to a privileged network such as a corporate LAN and even if they were previously verified. The principle is also known as perimeterless security or formerly de-perimeterization. ZTA is implemented by establishing identity verification, validating device compliance prior to granting access, and ensuring least privilege access to only explicitly-authorized resources. Most modern corporate networks consist of many interconnected zones, cloud services and infrastructure, connections to remote and mobile environments, and connections to non-conventional IT, such as IoT devices. The traditional approach by trusting users and devices within a notional "corporate perimeter" or via a VPN connection is commonly not sufficient in the complex environment of a corporate network. The zero trust approach advocates mutual authentication, including checking the identity and integrity of users and devices without respect to location, and providing access to applications and services based on the confidence of user and device identity and device status in combination with user authentication. The zero trust architecture has been proposed for use in specific areas such as supply chains. The principles of zero trust can be applied to data access, and to the management of data. This brings about zero trust data security where every request to access the data needs to be authenticated dynamically and ensure least privileged access to resources. In order to determine if access can be granted, policies can be applied based on the attributes of the data, who the user is, and the type of environment using attribute-based access control (ABAC). This zero trust data security approach can protect access to the data.
Using enhanced identity governance and policy-based access controls. Using micro-segmentation Using overlay networks or software-defined perimeters ZT is a security strategy (or approach), which is based on no implicit trust (i.e. zero trust) in the digital world, and is designed to detect and prevent breaches, while consistently (or better continuously) verifying all users, all devices, all layers (e.g. OSI layered model Recommendation ITU-T X.200...), all applications, across all locations in real time (run-time), and applying continuous integration and continuous delivery (CI/CD) pipeline security, resulting in preventative security from all attack vectors at all stages of the attacks: thus trust becomes explicit. The ZT-Kipling methodology moves beyond the foundational principles of Zero Trust Architecture (ZTA) by defining a set of five mandatory, iterative steps. This methodology treats ZT as a continual and iterative process.. The core of the methodology’s systematic nature lies in its integration of the Kipling Criteria: what, why, when, where, who, and how. This set of six questions is to be systematically applied and answered for each of the five iterative steps: Step 1 - Define the protected surface; Step 2 - Map the transaction flows; Step 3 - Build a Zero Trust Architecture (ZTA); Step 4 - Create Zero Trust policy; and Step 5 - Monitor and maintain. This entire process is repeated throughout the lifetime of a protected surface, which must be clearly defined in Step #1 of the methodology. TS 104 102 establishes the ZT-Kipling methodology as a systematic and cyclical governance framework for Zero Trust.
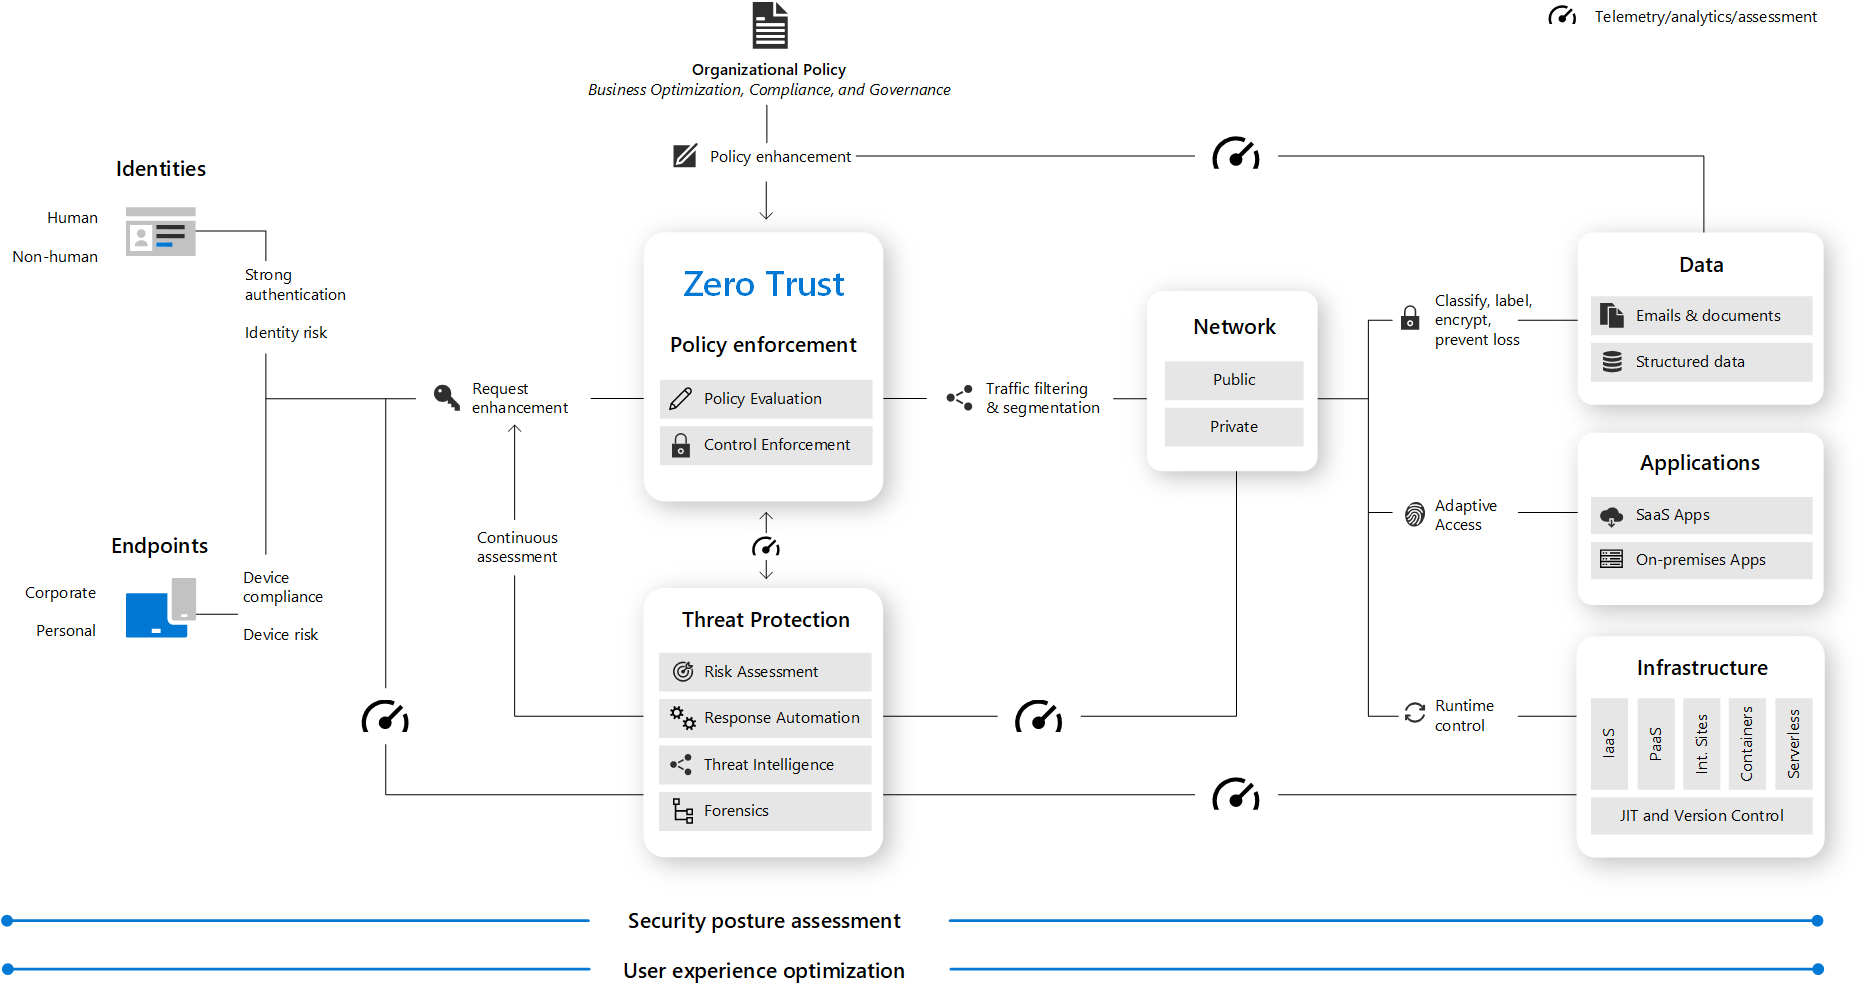
Figure 1: Microsoft Endpoint Manager Zero Trust at Kaitlyn Guest blog Single strong source of user identity User authentication Machine authentication Additional context, such as policy compliance and device health Authorization policies to access an application Access control policies within an application In the United States, Executive Order 14028 (May 2021) directed federal agencies to adopt zero trust architectures, and the Office of Management and Budget subsequently issued memorandum M-22-09 requiring agencies to meet specific zero trust security goals by the end of fiscal year 2024. In September 2025, the European Telecommunications Standards Institute (ETSI) Technical Committee CYBER (ETSI TC CYBER) published Technical Specification (TS) 104 102, which details the ZT-Kipling methodology to be used to achieve Zero Trust security posture.
BeyondCorp is an implementation of zero-trust computer security concepts creating a zero trust network. It is created by Google. the ability to allow their employees to work securely from any location. It reduces the risk of data breaches since data and applications are protected and users and devices are constantly being verified. The Zero Trust architecture is scalable and can be adapted to the changing needs of the businesses and their users. Especially relevant in today's work-from-home era, BeyondCorp allows employees to access enterprise resources securely from any location, without the need for traditional VPNs.
Perimeter 81 is an Israeli cloud and network security company that develops secure remote networks, based on the zero trust architecture, for organizations. Its technology replaces legacy security appliances like VPNs and firewalls. Since 2023, Perimeter 81 has been owned by the American-Israeli multinational cybersecurity company Check Point and renamed to "Harmony SASE.".
Figure 2: How To Implement Zero Trust Architecture (Reduce Security Risks) In June 2022 it completed a Series C financing round led by the USA's B Capital, with the participation of Insight Partners, Entree Capital, Toba Capital and ION Crossover Ventures. It has raised $100 million, at a $1b valuation, becoming a unicorn. The company has over 2,500 clients, among them Fortune 500 companies, as well as small and medium-sized enterprises. In August 2023, it was reported that the company would be acquired for $490 million by Check Point.
During my tenure on a defense program, the network perimeter was the primary security control. A VPN connection and a valid Active Directory credential meant you had broad access to internal systems. When a contractor's laptop was compromised in 2019, the lateral movement from one compromised endpoint to sensitive engineering databases took less than 48 hours. The perimeter model failed because it assumed that everything inside the network was trusted.
Zero trust is the architectural response to that failure. The core principle is straightforward: never trust, always verify. Every request (regardless of origin, network location, or previous authentication) is treated as potentially hostile until proven otherwise. This guide covers how to implement zero trust in practice, not just the theory. The US government formalized zero trust requirements in Executive Order 14028 (May 2021) and the subsequent CISA Zero Trust Maturity Model. By September 2024, all federal agencies were required to meet specific zero trust benchmarks.
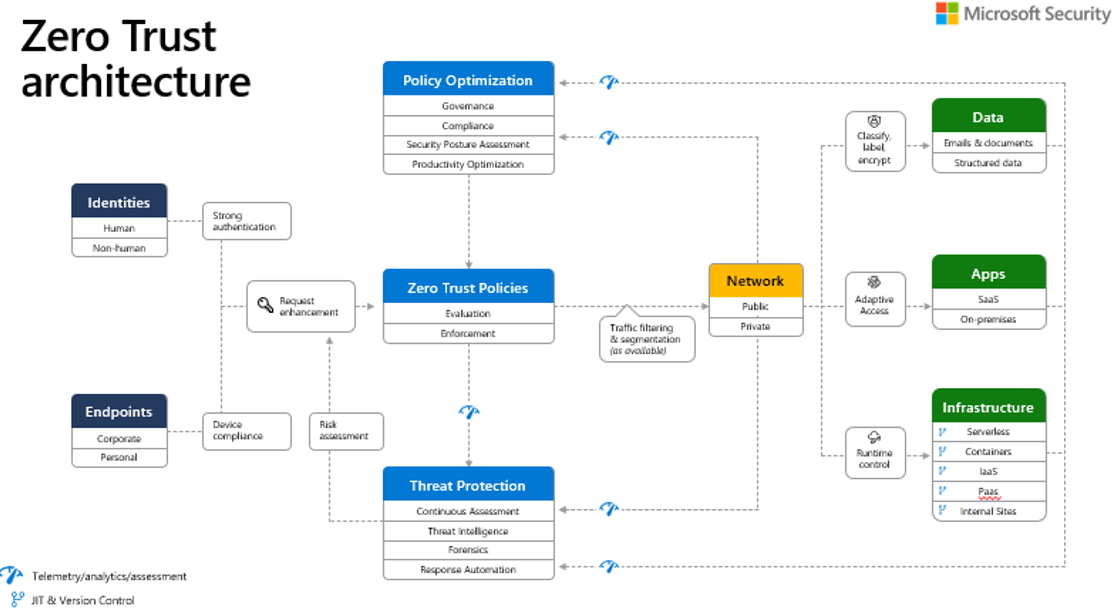
Enterprise adoption followed: Forrester Research estimates that 60% of large enterprises have active zero trust initiatives in 2026, up from 35% in 2023. Figure 3: Zero trust strategy defined CISA's Zero Trust Maturity Model defines seven pillars. Each requires specific technology and process changes: Identity is the new perimeter. Every user, service, and device must have a verified identity before accessing any resource.
Implementing zero trust is a multi-year journey. This 12-month plan covers the highest-impact changes first. Zero trust implementation has real costs. Here is a realistic breakdown for a mid-sized organization (200-500 employees): The ROI calculation: the average cost of a data breach in 2025 was $4.88 million (IBM/Ponemon). Organizations with mature zero trust architectures experienced breach costs that were $1.76 million lower than those without. The architecture pays for itself after preventing a single significant breach.
No. Firewalls remain part of defense-in-depth. Zero trust adds identity-based, application-aware controls on top of network-level controls. Think of it as adding more layers, not replacing existing ones. No. Small organizations can implement the core principles with affordable tools. Cloudflare Access (free tier for up to 50 users), Tailscale (free for personal use), and open-source EDR solutions make the foundational components accessible to organizations of any size.
Cloud-native architectures are well-suited to zero trust because they already rely on APIs, service identities, and software-defined networking. Kubernetes NetworkPolicies, IAM roles, and service mesh mTLS implement zero trust principles natively. See our CKA study guide for hands-on Kubernetes security practices. The (ISC)2 CCSP and CISSP cover zero trust concepts. The SANS SEC530 course focuses specifically on zero trust architecture. For cloud-specific implementation, AWS security certifications cover IAM, VPC security, and encryption that form the AWS implementation layer.
For a mid-sized organization: 12-24 months for a meaningful implementation covering all seven pillars. The identity and device pillars (Phase 1-2 above) typically take 6 months and deliver the highest immediate security improvement. Full maturity across all pillars is a 3-5 year journey for large enterprises. Start with an assessment of your current security posture against the CISA Zero Trust Maturity Model. Identify which pillar has the largest gap and prioritize it. For cloud-specific implementation, explore our free courses program which covers AWS IAM, VPC security, and container security. Browse the cloud security collection for structured learning paths on security architecture and implementation.
For career development in cloud security, see our cloud architect interview guide which includes security architecture questions that appear in senior-level interviews, and our DevOps vs SRE comparison for understanding how security responsibilities differ across infrastructure roles. *Sources: NIST SP 800-207 Zero Trust Architecture (2020), CISA Zero Trust Maturity Model v2.0 (2023), Executive Order 14028, IBM/Ponemon Cost of a Data Breach Report 2025, Forrester Zero Trust adoption survey (2025), Google BeyondCorp whitepaper, enterprise implementation data from the author's direct experience on defense and healthcare environments.* The rise of identity-driven threats, remote work environments and the move to hybrid environments have exposed the limitations of perimeter-based security. Zero Trust redefines the security architecture by continuously validating identity, context and risk before access is allowed.
CISAs Zero Trust Security Model outlines five pillars that organizations can focus on during a zero trust implementation. These components work together to enforce secure, policy-based access control across users, devices and enterprise resources. The workflow connects each core component into a continuous decision loop. An access request first passes through identity and access management to authenticate the user or workload. Device and endpoint security then provide posture and risk signals. The policy engine evaluates these inputs, which makes a real-time access decision based on defined policies and context.
Zero Trust network access enforces the decision by allowing only scoped, application-level access. Throughout the session, monitoring and analytics observe behavior and feed updated risk signals back to the policy engine, enabling ongoing revalidation and adaptive control. Zero trust is a progressive operating model one that organizations adopt over time as their environments, risks and capabilities evolve.
Most organizations begin their Zero Trust journey by strengthening the fundamentals. At this stage, the focus is on identity-first security. Users are authenticated more rigorously, while multi-factor authentication is introduced and access decisions begin to move away from implicit network trust. Visibility improves, but controls are still coarse-grained. What matters most here is clarity: Join security leaders who rely on the Think Newsletter for curated news on AI, cybersecurity, data and automation. Learn fast from expert tutorials and explainers—delivered directly to your inbox twice weekly. See the IBM Privacy Statement .
As maturity increases, organizations begin to apply Zero Trust principles consistently across environments. Access becomes more granular. Policies incorporate context such as device posture, location, behavior and workload identity. Trust decisions are no longer static—they adapt to risk in real time. This part is often the most challenging phase: Security decisions are automated and continuously evaluated. Identity, telemetry and threat intelligence work together to dynamically adjust access. Breaches are assumed and impact is contained through segmentation and least-privilege enforcement. In this stage, we can see certain benefits: Zero Trust is easy to understand, but hard to implement, as it requires architectural changes, not just technical controls. Let’s understand step by how to implement Zero Trust in practice.
The starting point for Zero Trust is clarity—on what truly needs protection and which legacy trust assumptions must be removed. Zero Trust is not deployed everywhere at once. It begins by defining a focused protect surface and applying explicit, policy-driven controls around it. Organizations should start where risk reduction is immediate whether that is identity, endpoints, critical applications, APIs or sensitive data. A clear starting point allows teams to design and validate controls without disrupting the broader environment.
This focus sets the foundation for success. Zero Trust is not about adding more security layers, but about deliberately replacing implicit trust with explicit, context-based access decisions that align with how modern environments operate. After defining Zero Trust goals, organizations must understand what they are protecting because policy-driven access decisions depend on accurate visibility.
Create a practical inventory of the identities of users, contractors and service accounts and the applications, APIs and data they access across cloud and on-premises environments. The objective is clarity, not perfection, revealing access paths, dependencies and trust relationships that influence risk. Classify assets by sensitivity, business criticality and compliance impact to distinguish high-value targets from lower-risk resources.
This foundation prevents overly broad policies and enables least privilege access aligned to real business risk. With the protected surface defined, Zero Trust makes identity the primary control point, replacing network location and VPN-based trust. Every request is verified through a centralized identity provider, with strong authentication and adaptive risk checks applied by default.
Access decisions also factor in device posture, including management status, endpoint health and OS currency. If a device becomes non-compliant, access is restricted or revoked. Together, identity and device context ensure that access remains precise, risk-aware and aligned with Zero Trust principles. A zero trust approach aims to wrap security around every user, every device, every connection — every time. Unify and integrate your security tools to protect your most valuable assets and proactively manage threats.
With identity and device context in place, Zero Trust uses centralized, context-aware policies to evaluate every access request. Decisions are attribute-based considering identity, device posture, request context and resource sensitivity and enforced consistently through a central policy engine. 2. System Architecture & Core Working Principles Access is applied at the resource layer through identity-aware proxies and cloud-native controls, eliminating broad network trust. Users and services can reach only what they are explicitly authorized to access, reducing lateral movement and limiting the blast radius.
Least privilege ensures that access is precise, temporary and purpose-driven. Users and services receive only the permissions required for a specific task, and only for the necessary duration. Broadly, standing privileges are replaced with just-in-time elevation, time-bound credentials and explicit permission boundaries defined through IAM policies. Privileges expire automatically once the task completes, limiting unnecessary exposure. By constraining access in scope and duration, least privilege prevents both accidental and intentional misuse without disrupting day-to-day operations.
In a Zero Trust model, access is never permanent. Every session is continuously evaluated and reassessed as the context changes. Real-time telemetry from identity, device, SIEM, UEBA, endpoint and threat systems feeds dynamic policy decisions. If risk rises, access can be challenged, restricted or revoked immediately. Every decision allowed or denied is logged to create a complete audit trail across users, devices and applications. Centralized monitoring correlates signals, flags high-risk behavior and triggers alerts. This continuous feedback loop transforms Zero Trust into a living system where trust adapts in real time.
Zero Trust is a phased architectural transition, not a one-time deployment. Implementation should begin with high-value targets, such as privileged accounts and sensitive applications, where strong identity and policy controls deliver immediate risk reduction. Controls then expand across devices, APIs and workloads, aligning enforcement with how the environment operates.
As maturity increases, real-time risk signals and adaptive policies enable continuous verification. This phased approach reduces complexity, minimizes disruption and allows Zero Trust to evolve into a resilient, operational security model over time. Zero Trust succeeds when implemented as a phased maturity journey, not a one-time deployment. Each phase builds on the last, increasing precision and reducing implicit trust. The journey begins with identity as the control plane. IBM Security® Verify authenticates users and services with SSO, MFA and risk-based access, replacing network location with verified identity.
Next, device context is added. Access decisions incorporate device posture signals, which ensures that the trusted identities on non-compliant devices are restricted through policy. With identity and device context established, least privilege is enforced. IBM Security Verify Access applies fine-grained authorization, replacing standing access with just-in-time, time-bound permissions. Enforcement then moves closer to the resource. Applications, APIs and workloads validate access directly, eliminating lateral movement and network-level trust.
Finally, Zero Trust becomes adaptive through continuous verification. Telemetry flows into IBM QRadar, enabling real-time risk detection and immediate access adjustment. Together, these phases create a continuous verification loop where trust is never assumed, access is precise and Zero Trust operates as a resilient security architecture.
Zero Trust is a modernization journey that embeds identity-first, policy-driven access to improve resilience, compliance and scalability. It replaces perimeter-based trust with “always verify” principles. Aligned with NIST, it reduces the attack surface through secure, context-aware access across on-premises, SaaS, mobile and IoT environments. By using ZTA and ZTNA, organizations enforce identity-based policies, enable micro segmentation and limit lateral movement. Automation and continuous monitoring strengthen security posture and real-time response.
As AI automation scales, identity becomes a control plane for AI trust, risk, and security. Without verified identities, agents can trigger runaway loops, deepfake scams, and unauthorized actions at machine speed. The global average cost of a data breach reached USD 4.99M while AI-driven attacks increased 56%. Explore the latest findings.
This e-book guides security and platform teams on how to reduce secret sprawl, prioritize remediation, and embed proper security hygiene to ultimately take a proactive approach to stopping secrets from entering production environments. Explore how IBM Verify and HashiCorp Vault work together to deliver runtime identity validation, scoped just-in-time access, continuous authorization at the point of use and unified audit evidence across identity, policy and credentials.
With the right foundations in place, organizations can innovate confidently, knowing their AI agents are acting with integrity, under the right level of human oversight. AI agents and services are creating identities faster than teams can manage. See why KuppingerCole named HashiCorp® an overall leader in non-human identity management and how zero trust, dynamic credentials and policy-based access control keep every identity in check.
Discover how IBM’s new IAM guide helps teams simplify identity sprawl, automate manual work and secure both human and non-human identities at scale. Learn how IBM leads in access management with secure authentication, SSO and adaptive access, recognized as a leader for the third year in a row.
Learn how integrated identity platforms simplify access across hybrid environments with smarter visibility, adaptive governance and AI-powered threat detection. See why IBM has been named a major player and gain insights for selecting the cybersecurity consulting services vendor that best fits your organization’s needs.
Learn how to maximize efficiency, reduce human bottlenecks and strengthen your security operations while staying ahead of evolving threats. This report explains how integrated security platforms reduce detection and containment times, lower costs and strengthen your overall defense posture. Learn how platformization helps security leaders maximize both protection and business value.
Protect secrets, manage machine identities and issue dynamic credentials for agentic AI and hybrid cloud. Verify identities, enforce least privilege and protect secrets across users, devices, workloads and hybrid cloud. Put your workforce and consumer IAM program on the road to success with skills, strategy and support from identity and security experts.
Discover how IBM Vault® and zero trust solutions simplify infrastructure while protecting data and identities across cloud, edge and AI environments. In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Zero trust is a security model built on the principle that no user, device, or network should be implicitly trusted based on location or prior authentication. Every access request is authenticated, authorized, and continuously validated regardless of whether it originates from inside the corporate network or outside it. Implementing zero trust is not a project with a completion date. It is a shift in security architecture that typically takes three to five years for an enterprise to implement fully across all five pillars: identity, devices, networks, applications and workloads, and data. The organizations that fail at zero trust treat it as a product purchase. The organizations that succeed treat it as a phased architectural transformation.
This guide covers the implementation sequence that produces the fastest risk reduction per dollar invested, the specific controls that constitute each zero trust pillar, and how to build a realistic roadmap without the false requirement of replacing existing infrastructure on day one. Identity is the highest-leverage starting point for zero trust implementation because 72% of breaches involve compromised credentials. Strengthening identity controls before addressing network or device controls produces the fastest per-dollar risk reduction of any zero trust pillar.
Phase one of identity zero trust implementation requires three controls. First, enforce MFA for all users on all applications, including on-premises applications federated through your IdP. MFA with phishing-resistant methods (FIDO2 hardware keys or passkeys) should be the standard for privileged accounts and all internet-facing applications. SMS-based MFA is better than no MFA but is vulnerable to SIM-swapping and should be phased out for high-risk accounts.
Second, implement conditional access policies that evaluate device health, user risk score, and location at authentication time. A valid credential entering from an unmanaged device or an anomalous location should trigger step-up authentication or be blocked entirely. Azure AD Conditional Access, Okta Adaptive MFA, and Ping Identity all provide this capability. Third, implement privileged access management. Privileged accounts (domain admins, cloud infrastructure admins, security tool admins) should use just-in-time access workflows, accounts have no standing privileges; access is granted for specific tasks, for defined time windows, with session recording. This limits blast radius when a privileged credential is compromised from 'full domain access indefinitely' to 'specific task for a defined period.' These three controls alone, universal MFA, conditional access, and PAM for privileged accounts, address the majority of credential-based attack paths that zero trust architecture is designed to eliminate.
Zero trust for devices requires that access decisions incorporate device health state. A valid user credential presenting from a compromised, unpatched, or unmanaged device should receive different access treatment than the same credential from a managed, healthy, compliant device. Device trust implementation requires four components. Device inventory: you cannot apply policy to devices you do not know about. A complete, current device inventory integrated with your IdP is a prerequisite. Device compliance policy: define what a compliant device looks like, current OS patch level, EDR agent installed and active, disk encryption enabled, screen lock enforced. These requirements are enforced through MDM platforms (Intune, Jamf, VMware Workspace ONE).
Certificate-based device authentication: issue device certificates from your organization's certificate authority to managed devices. Require this certificate as part of VPN or application access authentication. This prevents access from devices that are not enrolled in your MDM regardless of credential validity. Continuous device health evaluation: device compliance is not a one-time check at login. An EDR platform that continuously monitors device health should feed compliance signals back to your IdP so that a device that becomes non-compliant mid-session triggers a re-authentication requirement or session termination.
For BYOD environments, containerization (separating managed corporate applications from personal device data) and browser-based zero trust access (ZTNA clients that do not require full device enrollment) allow device trust policies that are more permissive for personal devices while still enforcing meaningful security requirements. Traditional network security models create a hard perimeter with soft interior: once an attacker is inside the network, lateral movement faces minimal friction. Microsegmentation replaces implicit interior trust with policy-based access controls that limit communication to approved flows.
Microsegmentation can be implemented at three layers. Network layer: VLAN segmentation with firewall rules controlling inter-VLAN traffic. This is the most common starting point and the easiest to implement with existing infrastructure. Application layer: firewall rules based on application identity rather than IP and port. This requires application-aware firewalls but produces more precise policy. Workload layer: host-based firewall policies or software-defined networking that control communication at the individual workload level, regardless of network segment.
Start with your highest-value assets. Segment your domain controllers into their own network zone with strict ingress and egress policy, only authentication traffic in, no lateral traffic out to workstations. Segment your backup infrastructure similarly. Segment POS systems, industrial control systems, and other sensitive device types with defined communication allowlists. 3. Software Implementation, Frameworks & Protocols Microsegmentation does not require ripping out existing network infrastructure. Most organizations implement it incrementally: start with the crown jewel systems, learn the actual communication patterns between systems using network flow data before writing rules, and expand coverage quarter by quarter. Writing microsegmentation policy without first mapping actual traffic flows is the most common mistake, it results in rules that break legitimate applications and immediate rollback of the entire initiative.
Zero trust roadmaps fail when they are too ambitious in year one, creating the impression that zero trust is unachievable, or too vague in year three and beyond, losing executive support when progress becomes invisible. A realistic four-year roadmap allocates effort across the five pillars in phases. Year one: universal MFA, conditional access, and privileged access management for identity (the fastest risk reduction); device inventory completion and MDM enrollment for managed endpoints. Year two: microsegmentation of crown jewel assets (domain controllers, backup infrastructure, critical servers); application inventory and single sign-on federation for all internal applications. Year three: ZTNA replacing legacy VPN for remote access; data classification and DLP policy for sensitive data categories. Year four: continuous compliance monitoring across all pillars; automated response to compliance violations.
Use the CISA Zero Trust Maturity Model (free download, updated 2023) as a self-assessment framework. It defines four maturity levels across each pillar and provides specific control requirements for advancing between levels. This framework is useful both for roadmap planning and for communicating progress to executive leadership with a standardized vocabulary. Universal MFA, conditional access, and PAM address the majority of credential-based attack paths before touching network or device controls.
Microsegmentation based on assumed communication patterns breaks legitimate applications. Use network flow data first. Any vendor claiming you can achieve zero trust by deploying their product is describing one component of one pillar. It provides standardized maturity levels across all five pillars and is free to download. Microsegmentation of domain controllers and backup infrastructure produces high impact even before enterprise-wide segmentation is complete.
Zero trust implementation is a phased architectural journey with a clear sequence: identity controls first (fastest risk reduction), device trust second (necessary for conditional access to function), network segmentation third (limits lateral movement blast radius), application access controls fourth (replaces perimeter-based application exposure), and data controls fifth (the hardest and most long-term pillar). Organizations that follow this sequence consistently reach meaningful zero trust maturity in three to four years. Organizations that treat zero trust as a product deployment never reach it at all.
Traditional VPN grants network-level access to a defined network segment after authenticating a user. Once connected, the user can reach any system on that network. ZTNA grants application-level access to specific applications after continuously validating user identity, device health, and contextual signals. There is no network-level access, only approved application-to-application communication. ZTNA is significantly harder to laterally move through after compromise because compromising a ZTNA-connected device gives an attacker access only to the applications that device is authorized to reach, not the network they are connected to.
No. Zero trust is a model implemented on top of existing infrastructure, not a replacement for it. Identity controls (MFA, conditional access, PAM) work with existing IdP infrastructure. Device compliance policies work with existing MDM platforms. Microsegmentation can be implemented on top of existing network infrastructure using VLAN and firewall controls before investing in software-defined networking. Most organizations reach meaningful zero trust maturity without a full infrastructure replacement by layering controls onto existing platforms in the sequence described above.
NIST SP 800-207 defines zero trust architecture as a security model based on seven tenets: all data sources and computing services are resources, all communication is secured regardless of network location, access to individual enterprise resources is granted on a per-session basis, access is determined by dynamic policy, the enterprise monitors and measures the integrity of all owned assets, authentication and authorization are dynamic and enforced before access is granted, and the enterprise collects information to improve security posture. The document is freely available and provides the foundational reference for most government and enterprise zero trust programs.
Cloud environments are a natural fit for zero trust because they eliminate the network perimeter assumption that traditional security is built on. In cloud environments, zero trust is implemented through: identity and access management using cloud IAM with least-privilege policies, workload identity (machine-to-machine authentication using service accounts and certificates rather than network location), security groups and VPCs for workload microsegmentation, and CSPM tools that continuously monitor cloud configuration compliance. Most cloud providers (AWS, Azure, GCP) provide native tools for each of these controls that integrate with enterprise identity platforms.
Frame zero trust as risk reduction for specific, named business risks rather than as a technology initiative. The most effective executive conversations connect zero trust controls to breach scenarios the organization has already experienced or that have impacted peers: 'After the Change Healthcare ransomware attack encrypted systems across a flat network, we ran a simulation of the same technique against our environment. Zero trust microsegmentation would have contained the blast radius to one segment. Here is what implementing it costs versus what a comparable incident cost Change Healthcare.' Quantify three to five scenarios with probability and estimated cost, then show how each zero trust control investment reduces expected loss. Executives respond to business risk language, not security maturity scores.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. Modern businesses face a wide variety of external and internal threats that require a complete approach to security. Organizations can improve their security posture by implementing the zero trust model to closely control how users gain access to sensitive data and critical assets.
Zero trust acknowledges that internal threats exist and must be mitigated to protect the business. Zero trust eliminates implicit trust, treats all access requests as potential security breaches, and takes necessary steps to protect the IT environment. The entire company must be involved in zero-trust adoption. Executive buy-in and strong cross-team support are essential for successful zero trust transformation. Zero trust offers a more effective security strategy than traditional security models.
The zero trust model is built on the precept of “Never Trust, Always Verify.” No implicit trust is granted based on network location or previous activity. The foundation of the zero trust architecture comprises the following core principles. The main objective of a company’s zero trust efforts is to ensure all access requests are verified at every step through the environment. These core principles support the strong system and data security required to protect business-critical resources.
Organizations must define their attack surface and build a security framework that protects their Data, Applications, Assets, and Services (DAAS). Teams must inventory and identify critical assets and sensitive data to accurately define the attack surface that needs to be defended. All external dependencies that interact with these assets and expand the attack surface must be included in this inventory.
Businesses can prioritize the identified assets when developing their zero trust strategy. They can focus on protecting critical assets first, then move on to the remaining infrastructure elements to improve their security posture across the organization while maintaining operations. Access management for users already inside the corporate network is an aspect of the zero trust security model. Teams should map all network traffic between users, applications, and data stores. The objective is to identify the most effective policy enforcement points for all critical data flows that protect resources while facilitating smooth business operations.
Zero trust security extends to network access attempts by remote workers and third parties trying to connect with on-premises or cloud resources. Companies should record and review connection patterns to determine whether security controls should be modified to protect business-critical systems and data better. Security teams must design the architecture to protect the defined attack surface. They should use a methodical approach when developing the zero trust architecture, addressing the following characteristics.
The key to the zero trust model is a reliable, centralized Identity and Access Management (IAM) platform that enforces multi-factor authentication (MFA) for all access requests. Strong identity verification is mandatory to support a zero trust approach. Users can only be granted access to a subset of the IT environment. Organizations must develop and implement role-based access controls (RBACs) for all users, aligned with their job functions. Attribute-based policies should be defined to control contextual access decisions.
Admin accounts require special consideration when developing IAM policies. These accounts provide privileged access that must be tightly controlled and restricted to specific systems and resources. Admin privileges should always be provided on a limited basis to minimize insider threats. Organizations can use the Kipling Method to build explicit, auditable, and secure access policies. The method defines the following criteria for every access policy based on six related questions. After each question is answered, the access request can be allowed to continue or terminated based on policy definitions.
Every job role or service should be granted least-privilege access for a given system or resources. Decision-makers should periodically review these privileges and make the necessary modifications to address changes in the environment or role. Zero Trust Network Access (ZTNA) enforces per-application and identity-verified access to IT resources. A ZTNA approach replaces the broad access enabled by traditional virtual private network (VPN) solutions with conditional access tied to user identity and device health and status.
A VPN typically enables users to access multiple internal systems once they are connected and verified. ZTNA’s application-level access connects a user only to the specific application they are authorized to use. The zero trust network approach reduces the blast radius if threat actors compromise credentials. Zero trust network access controls must be designed to ensure secure access for users and devices. Modern businesses often deploy a range of automated IoT devices and endpoint solutions to support remote work. Teams should implement policies to verify device health before granting access. Device health checks are essential for identifying outdated firmware or patching vulnerabilities that threat actors can exploit.
One method of preventing IoT devices from accessing unauthorized resources is to limit access to specific dedicated network segments. This type of control involves planning to ensure IoT-connected applications live on an appropriate segment. All IoT access attempts to other segments should be refused. Companies that engage managed service providers such as Atlantic.Net should expect them to provide complete edge security aligned with their zero-trust access policies.
Companies must implement a continuous monitoring solution to support a zero trust security posture. Teams should collect identity and network activity telemetry in real time and be prepared to address incidents that may indicate threats or malicious activity. Security teams should implement advanced anomaly detection solutions leveraging threat intelligence and behavioral analysis.
When potential incidents are detected, automated alerts should be generated to trigger recovery and mitigation playbooks. The immediate goal is to reduce the business impacts of an unauthorized incursion by locking down the rogue user or device. All monitoring logs should be retained and archived for use in forensic investigations and to provide audit evidence. Companies should deploy a policy engine to automate decisions and enforcement. Zero-trust security violations must be addressed in real time to protect the IT environment fully. Teams can evaluate unauthorized access attempts that were denied after the fact to determine if policies should be modified.
Organizations should define remediation workflows for non-compliant devices that fail health checks and result in denied access attempts. These devices should be serviced promptly to address their issues. Teams should strongly consider implementing policy-as-code to achieve more consistent deployments that comply with governance and compliance requirements.
Organizations must exercise effective governance to avoid control drift, which can undermine the viability of zero trust. Governance efforts should incorporate the following elements. Companies must implement zero trust to support any applicable compliance frameworks such as HIPAA or PCI DSS. Access controls for sensitive and regulated data should align with compliance standards. Teams must document policies and retain logs to provide evidence for compliance audits.
4. Practical Deployment, Analysis & Case Studies Businesses should consider attack surface reduction to be an ongoing process. Efforts to reduce entry points for threat actors should be security-focused. Teams should schedule attack surface reduction exercises and use the results to inform infrastructure changes that support a zero-trust architecture.
Companies should begin their zero trust journey by selecting a high-impact pilot case to validate controls and processes. Teams can collect and evaluate key KPIs to gauge the impact of zero trust principles on user access to sensitive data and on operational metrics. Once the organization is satisfied with the details of its zero trust strategy, security controls can be scaled across additional applications and cloud resources. Ideally, replicating the strict access controls across all critical assets can be done with minimal impact on business operations.
Organizations that implement zero trust typically proceed through the following stages as the process matures. Teams commonly measure many KPIs to evaluate the effectiveness of their zero trust environment, including: Companies should schedule quarterly reviews of the zero trust policy’s scope and controls. The review provides an opportunity to refine controls to better protect sensitive resources. Businesses in the early stages of zero trust adoption should plan to cover all remaining assets and services and reach the phase as soon as possible.
Robert is a regular contributor and blogger for Atlantic.Net living in Northeastern Pennsylvania who specializes in various information technology topics. He brings over 30 years of IT experience to the table with a focus on backup, disaster recovery, security, compliance, and the cloud. A new customer approached Atlantic.Net about moving two Windows servers from Rackspace to a ‘simpler, more cost-effective environment’ in one of our U.S. data centers. The organization wanted… A technology group approached Atlantic.Net about consolidating much of its infrastructure with a long-term hosting partner. Its environment spanned Amazon Web Services, Vultr, Cloudinary, and Rackspace, supporting websites,… Hermes vs OpenClaw vs Claude Code compares three AI agent platforms built for different workloads. Hermes Agent focuses on persistent memory, reusable skills, provider flexibility, messaging, and general… Zero Trust implementation is a step-by-step security initiative that eliminates default trust and validates every access request based on factors such as user identity, device health, workload, data sensitivity, and real-time risk. Begin by identifying your most critical assets and the pathways used to access them, then evaluate your organization’s maturity against the CISA Zero Trust pillars. Launch with a high-impact pilot, apply least-privilege access and continuous verification, and gradually extend the framework as results are validated. Rather than being a standalone product, Zero Trust is an ongoing security strategy that can be adopted incrementally without replacing your existing infrastructure all at once.
Zero Trust is everywhere: the media, your management, 160+ OEMs who propose some form of a Zero Trust solution , government standards and now Presidential mandates. The need is genuine, the question I propose is, “Are you ready?” Zero Trust is a security model based on maintaining strict access controls and not trusting anyone by default, even users already inside the network perimeter. It removes implied access and only grants trusted users the access they need to perform their job.
Zero Trust is a methodology, not a product ; there’s no single infrastructure implementation or architecture that delivers a complete Zero Trust solution on its own. As a reference model, NIST Special Publication 800-207 provides a standard Zero Trust conceptual framework that illustrates the components and functional capabilities of a typical Zero Trust Architecture (ZTA) . Beyond that federal standard, OEM-specific solutions and industry analyst architectures from firms like Forrester and Gartner offer their own approaches to the same underlying principles.
Red River Tip: Many organizations already have technologies that support Zero Trust but have yet to deploy, integrate, or manage them as part of a unified strategy. Red River’s approach starts by evaluating existing security capabilities, aligning them with Zero Trust requirements, and addressing only the gaps that need attention. This phased approach helps avoid unnecessary technology replacements while accelerating implementation with a stronger, more defensible security foundation.
Identity and Access Management (IAM) is a central component of Zero Trust because access decisions begin with verifying who or what is requesting access. Rather than assuming that an authenticated user or device should have broad access, Zero Trust evaluates identity and other contextual signals before granting access to a specific resource. Effective IAM provides the foundation for enforcing “never trust, always verify” access decisions. It also creates a foundation for extending Zero Trust controls across devices, applications, networks and data.
Implementing Zero Trust can be challenging because it affects identity, devices, applications, networks, data and day-to-day access processes. Organizations may also need to work around legacy systems, incomplete visibility and existing security tools that were not designed to operate as part of a unified Zero Trust strategy. Addressing these challenges early helps organizations build a practical Zero Trust implementation plan rather than attempting to apply every Zero Trust control across the environment at once.
Zero Trust Architecture rests on three foundational principles. Understanding each one individually helps clarify what a real implementation actually requires. Red River Tip: Focus on implementing one principle at a time. Strengthening identity verification and least-privilege access often delivers immediate security improvements while laying the foundation for broader Zero Trust adoption.
Implementing Zero Trust does not rely on a single framework. Instead, the most practical approach incorporates guidance from multiple sources, applying each where it is most relevant. There are many reasons to implement Zero Trust Architecture . The more practical question is how to begin . Here’s a five-step implementation framework, often achievable with the tools you already have: Beyond the five foundational steps above, most Zero Trust rollouts also move through four broader implementation phases: Red River Tip: Define measurable success criteria for each implementation phase, such as reducing privileged accounts, improving device compliance, or increasing policy coverage. Tracking progress makes it easier to demonstrate business value and prioritize the next phase.
Before rolling out any Zero Trust controls, map your risks. A risk assessment identifies which systems, data and workflows are most valuable to attackers and most damaging to lose, so implementation resources go toward the highest-impact areas first rather than being spread evenly across low-risk and high-risk systems alike. Ranking risks this way turns a vague “implement Zero Trust” mandate into a concrete, prioritized project plan.
Red River Tip: A risk-based approach helps organizations focus Zero Trust efforts where they will have the greatest impact. Prioritizing critical assets and high-risk access paths often delivers faster security improvements than attempting enterprise-wide changes all at once. Zero Trust is often described in terms of network and identity controls, but data-centric security is just as central to the model.
Three practices anchor this piece: Together, these controls mean that even a successful breach doesn’t automatically translate into a successful data theft. Traditional network security focuses on the perimeter, while a Zero Trust approach focuses just as much on what happens after someone is inside. Internal segmentation , sometimes called microsegmentation , breaks the network into small, isolated zones so a compromised device or account can’t move freely to reach everything else.
In practice, this might mean isolating finance systems from general office traffic, restricting IoT and OT devices to their own segments or requiring reauthentication to move between zones. The goal isn’t to make the network harder to use for real employees – it’s to make sure a single compromised credential doesn’t equal a compromised organization.
Most organizations now run a mix of on-premises infrastructure and cloud platforms , and Zero Trust has to extend across both. Applying Zero Trust to cloud environments generally involves: Rather than implementing every piece of Zero Trust at once, most organizations mature through three broad stages: Red River Tip: Zero Trust maturity is an ongoing journey rather than a one-time project. Organizations typically achieve the best results by expanding capabilities incrementally as operational processes and security controls mature.
Most organizations spend months in the Crawl stage and a year or more in Walk, while Run is best treated as an ongoing state rather than a finish line. Even with a well-defined Zero Trust implementation roadmap, organizations can encounter challenges that slow adoption or reduce the effectiveness of their Zero Trust strategy. Recognizing and avoiding these common mistakes can lead to a more successful Zero Trust implementation.
There are various methods to approach a Zero Trust implementation in terms of architecture, below are a few examples in the state what’s possible and key OEMs who are proponents of their specific approach: The Zero Trust Architecture and supported OEM solutions will continue to evolve over the next decade. It is my prediction that it will take the next three to five years before the components genuinely settle and services begin to consolidate.
There are simply too many moving parts, dynamic IT support components, shifting remote access requirements and evolving threat landscape areas that are moving faster than IT budgets can support. It will take a few in-production Zero Trust Architecture renditions before well-established best practices can be established. With that as a background, the 160+ OEM solutions plus the ongoing marketing and business pressure to move towards ZTA, the time is now to begin your Zero Trust journey. If you need help getting started, a managed service provider and security expert like Red River can create your customized Zero Trust plan, and help you monitor, manage and implement it.
Red River helps organizations plan, implement, and optimize Zero Trust initiatives through every stage of the journey, from initial assessment and architecture design to deployment and ongoing managed services. The organization’s documented Zero Trust framework combines workshops, a 77-question technology stack assessment, strategic roadmaps, and a multi-vendor lab to evaluate integrations and proof-of-concept scenarios.
Rather than requiring a large-scale infrastructure overhaul, Zero Trust implementation can begin by assessing critical assets, understanding access paths, evaluating existing capabilities, and prioritizing the most important security gaps. This phased approach enables organizations to make measurable progress while maximizing existing technology investments. 5. Performance Evaluation & Extended Technical Observations Zero Trust implementation is the process of rolling out “never trust, always verify” controls, covering identity, devices, network, applications and data, across an organization’s environment. It’s typically done through a phased roadmap rather than a single deployment.
Start with an asset and identity inventory , since you can’t protect what you haven’t mapped. Most organizations move through four phases: assessment , planning , phased deployment and ongoing optimization . Deployment usually starts with a pilot group on the highest-risk systems, then expands as policies get tuned based on what that pilot reveals. There’s no single blueprint, since every environment’s starting point looks different.
Common building blocks include multi-factor authentication , identity and access management , network segmentation tools , endpoint detection and response , data classification , DLP and centralized monitoring , most of which layer onto tools organizations already have rather than requiring a full technology overhaul. Most organizations spend several months on initial deployment and a year or more maturing to organization-wide coverage.
Full maturity is best treated as an ongoing program, not a fixed end date. Complexity, mapping every asset, identity and data flow across a hybrid environment before meaningful policies can even be written. Yes. Zero Trust is a methodology, not a product , so most organizations layer it onto existing identity providers, firewalls and endpoint tools.
Prioritize by risk. Rank systems by how sensitive their data is, how disruptive a compromise would be, and where existing vulnerabilities are greatest, then work down that list instead of trying to protect everything simultaneously. The most common mistakes: trying to implement everything at once, skipping employee communication and training, and treating Zero Trust as a one-time project instead of an ongoing program.
Costs vary widely. Many first steps, like enabling MFA or tightening access groups, cost little to nothing, while advanced tooling and dedicated staff add expense as the program matures. The five pillars are identity, devices, networks, applications and workloads, and data . Together, they provide a framework for applying Zero Trust controls across the IT environment.
Zero Trust applies continuous verification and least-privilege access to cloud services, applications, users, and workloads. It can be implemented across environments such as: Start by securing user identities with MFA , enforcing least-privilege access, verifying device health, and applying conditional access policies. Access should be evaluated based on identity, device, application, and real-time risk rather than network location alone.
Zero Trust is a security strategy focused on verifying access and enforcing least privilege, while SASE (Secure Access Service Edge) is an architecture that combines networking and security capabilities through cloud-delivered services. SASE can incorporate Zero Trust principles and technologies. Zero Trust protects applications and workloads by limiting access to authorized users and systems, enforcing least-privilege policies, and continuously evaluating access requests. Application segmentation, identity controls, encryption, and monitoring can also help limit the impact of a compromise.
MFA adds additional identity verification beyond a password and helps strengthen authentication. It is a foundational Zero Trust control, particularly for protecting sensitive systems, privileged accounts, and remote access. Implement Zero Trust security by identifying critical assets and access pathways, assessing security risks, and applying controls such as MFA, least-privilege access, device verification, network segmentation, and continuous monitoring . Start with a focused pilot, measure results, and gradually expand Zero Trust controls across the organization.
Zero trust network implementation involves applying continuous verification, least-privilege access, segmentation, and monitoring across network resources. It helps ensure that users and devices cannot access resources simply because they are connected to the network. Zero trust access requires every access request to be authenticated, authorized, and evaluated based on factors such as user identity, device health, resource sensitivity, and risk. Access is limited to the specific applications, systems, or data a user or device needs.
Corrin Jones is the Director of Digital Demand Generation. With over ten years of experience, she specializes in creating content and executing campaigns to drive growth and revenue. Connect with Corrin on LinkedIn . Zero Trust Architecture in System Design explores a security model focused on the principle of 'never trust, always verify.' This approach assumes that threats could exist both inside and outside the network, so it requires rigorous verification for every user and device trying to access resources. The article discusses how to design systems using Zero Trust principles to enhance security.
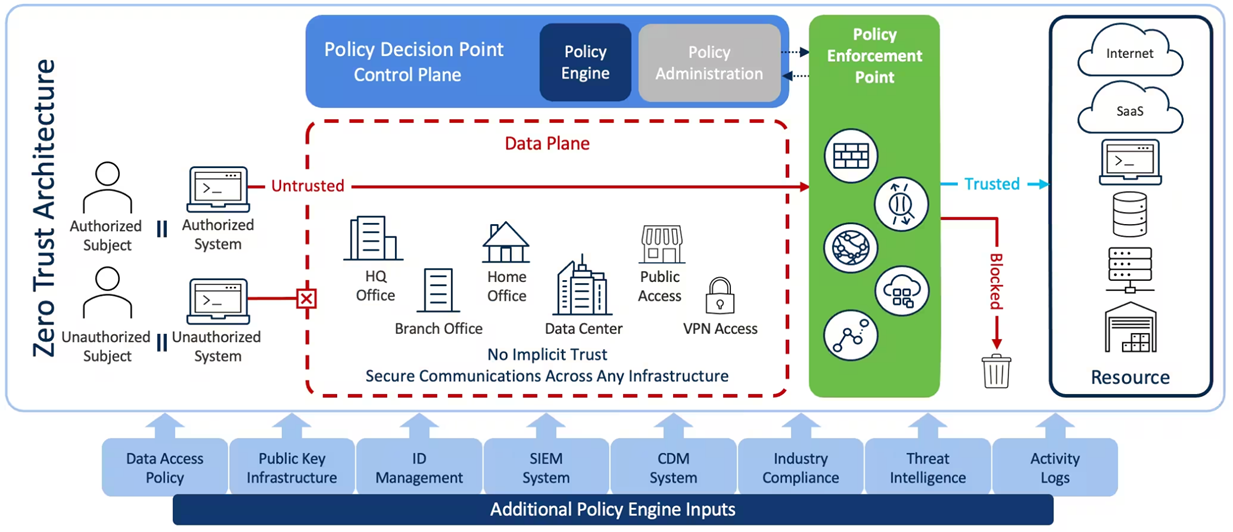
Zero Trust Architecture (ZTA) is a security model that assumes no user, device, or network is trusted by default, whether inside or outside the organization's network. Every access request must be authenticated, authorized, and continuously validated, applying the principle of least privilege. The model emphasizes microsegmentation, continuous monitoring, and strong identity verification to minimize security risks. This approach ensures secure communications and access control across any infrastructure, blocking unauthorized access and minimizing security risks.
The PEP is the component that enforces the decisions made by the Policy Engine. It acts as a gatekeeper, ensuring that only authorized users and devices can access the resources they request. If the access request is trusted, the PEP allows it; if not, it blocks it. This includes the various locations and methods through which data is accessed, such as corporate offices, remote work environments, data centers, and public access points. In a Zero Trust model, these environments are all considered untrusted by default, and secure communication is required across any infrastructure.
These are the various sources of information that feed into the Policy Engine to help it make informed decisions. They include: These are the assets that need protection, such as data, applications, and services, which could reside on-premises, in the cloud, or as part of SaaS offerings. The Zero Trust Architecture ensures that access to these resources is controlled and continuously monitored.
Implementing Zero Trust Architecture (ZTA) effectively requires adherence to several best practices that ensure robust security and adaptability to evolving threats. Here are some of the key best practices: Implementing Zero Trust Architecture (ZTA) comes with several challenges that organizations need to be aware of to ensure a successful deployment. Here are some of the key challenges: Zero Trust Architecture (ZTA) has been adopted by various organizations worldwide to enhance their security posture. Here are some real-world examples of how different organizations have implemented Zero Trust: Google pioneered the Zero Trust model with its BeyondCorp initiative. BeyondCorp eliminates the traditional notion of a privileged corporate network and instead requires all applications to be accessed in a secure, controlled manner, regardless of the user's location or device.
Microsoft has integrated Zero Trust principles into its own IT infrastructure, including how it secures access to corporate resources and services. Microsoft leverages its own Azure Active Directory (Azure AD) and Microsoft Endpoint Manager to enforce Zero Trust principles. IBM has embraced Zero Trust both in its product offerings and within its internal IT security framework. The company has incorporated Zero Trust principles into its cloud security solutions and consulting services. Internally, IBM uses a combination of identity management, risk-based conditional access, and continuous monitoring to enforce Zero Trust.
In conclusion, designing a Zero Trust Architecture is essential for modern cybersecurity. It shifts the focus from relying on perimeter defenses to continuously verifying every user, device, and connection within a network. By following best practices such as implementing least privilege access, continuous monitoring, and encryption, organizations can significantly enhance their security posture. However, challenges like integration with legacy systems and the complexity of implementation require careful planning and resources. Ultimately, adopting Zero Trust ensures stronger, more resilient defenses against evolving threats, making it a critical strategy for safeguarding digital environments.
Traditional network security relies on a simple assumption: everything inside the firewall is trusted, everything outside is not. This model fails when a compromised endpoint, a lateral-moving attacker, or an overly permissive VPN can access anything on the internal network. Zero trust replaces this with a straightforward principle: never trust, always verify. Every access request (regardless of source network) must be authenticated, authorized, and encrypted.
This isn't a product you buy. It's an architecture you build, incrementally, using the infrastructure you likely already have. The highest-impact first step is microsegmentation. Most flat networks allow any device to reach any other device. Microsegmentation breaks this by creating security zones with explicit allow rules. Traditional firewalls match on IP addresses. Zero trust matches on identity . This means integrating your firewall with your identity provider.
This eliminates the problem of static IP-based rules that break when devices move or IPs change. North-south traffic (in/out of the network) gets inspected by default. East-west traffic (between internal hosts) often flows uninspected. The goal isn't to inspect every packet, it's to ensure that a compromised web server can't reach your database server on a management port.
Zero trust isn't about buying the right product. It's about systematically reducing implicit trust in your network, one policy at a time. Five concrete Kubernetes security failures that show up repeatedly in production clusters, with real examples of what goes wrong and exactly how to fix each one.
The traditional perimeter-based security model assumed that everything inside the corporate network was trustworthy. That assumption has been thoroughly dismantled by cloud migration, remote work, supply chain attacks, and lateral movement techniques that let adversaries roam freely once they breach the perimeter. Zero trust architecture (ZTA) replaces implicit trust with continuous verification: never trust, always verify.
This guide provides a practical implementation roadmap for zero trust, with identity as the cornerstone. You will learn how to design, deploy, and operate a zero trust environment that protects your organization regardless of where users, devices, and workloads reside. Zero trust architecture is not a single product. It is a design philosophy implemented through the coordinated deployment of several components: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Zero%20trust%20architecture • https://en.wikipedia.org/wiki/BeyondCorp • https://en.wikipedia.org/wiki/Perimeter%2081 • https://www.citadelcloudmanagement.com/blog/zero-trust-architecture-complete-implementation-guide-2026 • https://www.ibm.com/think/topics/zero-trust-implementation • https://www.decryptiondigest.com/blog/how-to-implement-zero-trust-architecture • https://www.atlantic.net/cloud-platform/zero-trust-implementation-roadmap/ • https://redriver.com/security/implementing-zero-trust • https://www.geeksforgeeks.org/system-design/zero-trust-architecture-system-design/ • https://dkinfraedge.com/blog/zero-trust-network-architecture-practical-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Zero Trust Network Architecture.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |