Complete Technical Paper Content — Zigbee Wireless Network Vulnerability Scanning Tool
Overview & System Context
Zigbee Wireless Network Vulnerability Scanning Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9523 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Wireless security is the prevention of unauthorized access or damage to computers or data using Wireless networks, which include Wi-Fi networks. The term may also refer to protecting the wireless network itself from adversaries seeking to damage the confidentiality, integrity, or availability of the network. The most common type is Wi-Fi security, which includes Wired Equivalent Privacy (WEP) and Wi-Fi Protected Access (WPA). WEP is an old IEEE 802.11 standard from 1997. It is a notoriously weak security standard: the password it uses can often be cracked in a few minutes with a basic laptop computer and widely available software tools. WEP was superseded in 2003 by WPA, a quick alternative at the time to improve security over WEP. The current standard is WPA2; some hardware cannot support WPA2 without a firmware upgrade or replacement.
WPA2 uses an encryption device that encrypts the network with a 256-bit key; the longer key length improves security over WEP. Enterprises often enforce security using a certificate-based system to authenticate the connecting device, following the standard 802.11X. In January 2018, the Wi-Fi Alliance announced WPA3 as a replacement for WPA2. Certification began in June 2018, and WPA3 support has been mandatory for devices that bear the "Wi-Fi CERTIFIED™" logo since July 2020.
Many laptop computers have wireless cards pre-installed. The ability to enter a network while mobile has great benefits. However, wireless networking is prone to some security issues. Hackers have found wireless networks relatively easy to break into, and even use wireless technology to hack into wired networks. As a result, it is very important that enterprises define effective wireless security policies that guard against unauthorized access to important resources. Wireless Intrusion Prevention Systems (WIPS) or Wireless Intrusion Detection Systems (WIDS) are commonly used to enforce wireless security policies.
The risks to users of wireless technology have increased as the service has become more popular. There were relatively few dangers when wireless technology was first introduced. Hackers had not yet had time to latch on to the new technology, and wireless networks were not commonly found in the workplace. However, there are many security risks associated with the current wireless protocols and encryption methods, and in the carelessness and ignorance that exists at the user and corporate IT level. Hacking methods have become much more sophisticated and innovative with wireless access. Hacking has also become much easier and more accessible with easy-to-use Windows- or Linux-based tools being made available on the web at no charge. Some organizations that have no wireless access points installed do not feel that they need to address wireless security concerns. In-Stat MDR and META Group have estimated that 95% of all corporate laptop computers that were planned to be purchased in 2005 were equipped with wireless cards. Issues can arise in a supposedly non-wireless organization when a wireless laptop is plugged into the corporate network. A hacker could sit out in the parking lot and gather information from it through laptops and/or other devices, or even break in through this wireless card–equipped laptop and gain access to the wired network.
Wireless security is another aspect of computer security. Organizations may be particularly vulnerable to security breaches caused by rogue access points. If an employee adds a wireless interface to an unsecured port of a system, they may create a breach in network security that would allow access to confidential materials. Countermeasures like disabling open switchports during switch configuration and VLAN configuration to limit network access are available to protect the network and the information it contains, but such countermeasures must be applied uniformly to all network devices.
A man-in-the-middle attacker entices computers to log into a computer that is set up as a soft AP (Access Point). Once this is done, the hacker connects to a real access point through another wireless card offering a steady flow of traffic through the transparent hacking computer to the real network. The hacker can then sniff the traffic. One type of man-in-the-middle attack relies on security faults in challenge and handshake protocols to execute a "de-authentication attack". This attack forces AP-connected computers to drop their connections and reconnect with the hacker's soft AP (disconnects the user from the modem so they have to connect again using their password which one can extract from the recording of the event).
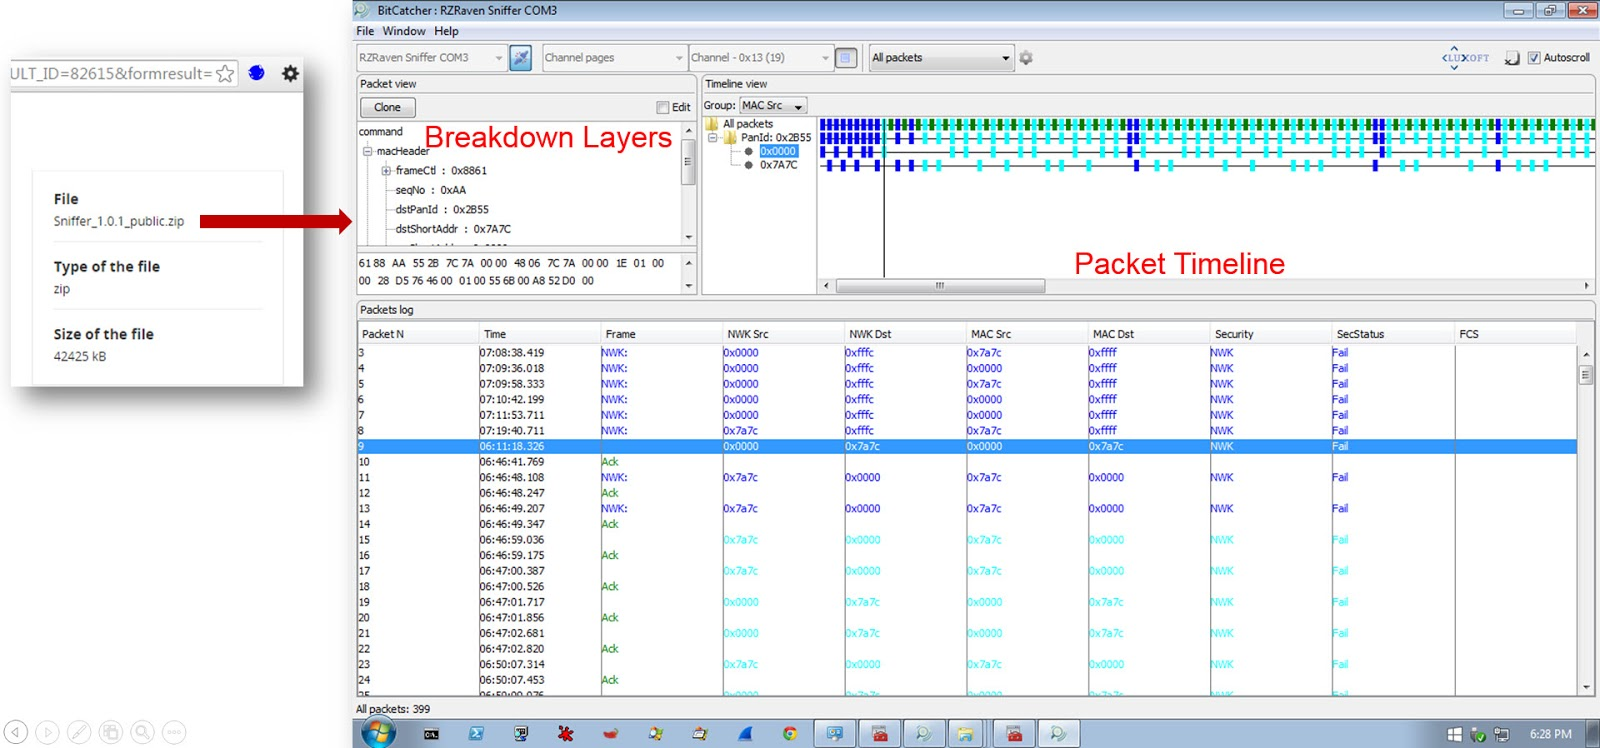
Man-in-the-middle attacks are enhanced by software such as LANjack and AirJack which automate multiple steps of the process, meaning what once required some skill can now be done by script kiddies. Hotspots are particularly vulnerable to any attack since there is little to no security on these networks. Figure 1: SecuritySynapse: Fun with Zigbee Wireless - Part III (Software) For closed networks (like home users and organizations) the most common way is to configure access restrictions in the access points. Those restrictions may include encryption and checks on MAC address. Wireless Intrusion Prevention Systems can provide wireless LAN security in this network model. For commercial providers, hotspots, and large organizations, the preferred solution is often to have an open and unencrypted, but completely isolated wireless network. The users will at first have no access to the Internet nor to any local network resources. Commercial providers usually forward all web traffic to a captive portal which provides for payment and/or authorization. Another solution is to require the users to connect securely to a privileged network using VPN. Wireless networks are less secure than wired ones; in many offices intruders can easily visit and hook up their own computer to the wired network without problems, gaining access to the network, and it is also often possible for remote intruders to gain access to the network through backdoors like Back Orifice. One general solution may be end-to-end encryption, with independent authentication on all resources that should not be available to the public. There is no ready-designed system to prevent fraudulent usage of wireless communication or to protect data and functions with wirelessly communicating computers and other entities. However, there is a system of qualifying the taken measures as a whole according to a common understanding of what shall be seen as state of the art. The system of qualifying is an international consensus as specified in ISO/IEC 15408.
A Wireless Intrusion Prevention System (WIPS) is a concept for the most robust way to counteract wireless security risks. However such a WIPS does not exist as a ready-designed solution to implement as a software package. A WIPS is typically implemented as an overlay to an existing Wireless LAN infrastructure, although it may be deployed standalone to enforce no-wireless policies within an organization. WIPS is considered so important to wireless security that in July 2009, the Payment Card Industry Security Standards Council published wireless guidelines for PCI DSS recommending the use of WIPS to automate wireless scanning and protection for large organizations. Several WIPS vendors were established in the early 2000s. AirDefense was founded in 2001 and later acquired by Motorola in 2008. Mojo Networks was founded in 2004 and later acquired by Arista Networks in 2018. With the rapid growth of Wireless LANs, WIPS became an important part of every organization's security posture.
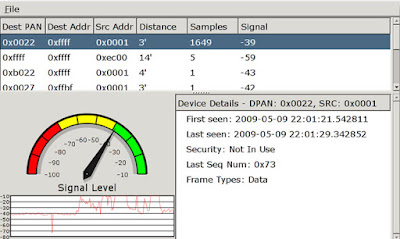
A simple but ineffective method to attempt to secure a wireless network is to hide the SSID (Service Set Identifier). This provides very little protection against anything but the most casual intrusion efforts. IEEE 802.1X is the IEEE Standard authentication mechanism for devices wishing to attach to a Wireless LAN. Figure 2: SecuritySynapse: Fun with Zigbee Wireless - Part IV (Passive attacks) The Wired Equivalent Privacy (WEP) encryption standard was the original encryption standard for wireless, but since 2004 with the ratification WPA2 the IEEE has declared it "deprecated", and while often supported, it is seldom or never the default on modern equipment. Concerns were raised about its security as early as 2001, dramatically demonstrated in 2005 by the FBI, yet in 2007 T.J. Maxx admitted a massive security breach due in part to a reliance on WEP and the Payment Card Industry took until 2008 to prohibit its use – and even then allowed existing use to continue until June 2010.
The Wi-Fi Protected Access (WPA and WPA2) security protocols were later created to address the problems with WEP. If a weak password, such as a dictionary word or short character string is used, WPA and WPA2 can be cracked. Using a long enough random password (e.g. 14 random letters) or passphrase (e.g. 5 randomly chosen words) makes pre-shared key WPA virtually uncrackable. The second generation of the WPA security protocol (WPA2) is based on the final IEEE 802.11i amendment to the 802.11 standard and is eligible for FIPS 140-2 compliance. With all those encryption schemes, any client in the network that knows the keys can read all the traffic. Wi-Fi Protected Access (WPA) is a software/firmware improvement over WEP. All regular WLAN equipment that worked with WEP are able to be simply upgraded and no new equipment needs to be bought. WPA is a trimmed-down version of the 802.11i security standard that was developed by the IEEE 802.11 to replace WEP. The TKIP encryption algorithm was developed for WPA to provide improvements to WEP that could be fielded as firmware upgrades to existing 802.11 devices. The WPA profile also provides optional support for the AES-CCMP algorithm that is the preferred algorithm in 802.11i and WPA2. WPA Enterprise provides RADIUS based authentication using 802.1X. WPA Personal uses a pre-shared Shared Key (PSK) to establish the security using an 8 to 63 character passphrase.
The PSK may also be entered as a 64-character hexadecimal string. Weak PSK passphrases can be broken using off-line dictionary attacks by capturing the messages in the four-way exchange when the client reconnects after being deauthenticated. Wireless suites such as aircrack-ng can crack a weak passphrase in less than a minute. Other WEP/WPA crackers are AirSnort and Auditor Security Collection. Still, WPA Personal is secure when used with ‘good’ passphrases or a full 64-character hexadecimal key. There was information, however, that Erik Tews (the man who created the fragmentation attack against WEP) was going to reveal a way of breaking the WPA TKIP implementation at Tokyo's PacSec security conference in November 2008, cracking the encryption on a packet in 12 to 15 minutes. Still, the announcement of this 'crack' was somewhat overblown by the media, because as of August, 2009, the best attack on WPA (the Beck-Tews attack) is only partially successful in that it only works on short data packets, it cannot decipher the WPA key, and it requires very specific WPA implementations in order to work.
This stands for Temporal Key Integrity Protocol and the acronym is pronounced as tee-kip. This is part of the IEEE 802.11i standard. TKIP implements per-packet key mixing with a re-keying system and also provides a message integrity check. These avoid the problems of WEP. This stands for the Lightweight Extensible Authentication Protocol. This protocol is based on 802.1X and helps minimize the original security flaws by using WEP and a sophisticated key management system. This EAP version is safer than EAP-MD5.
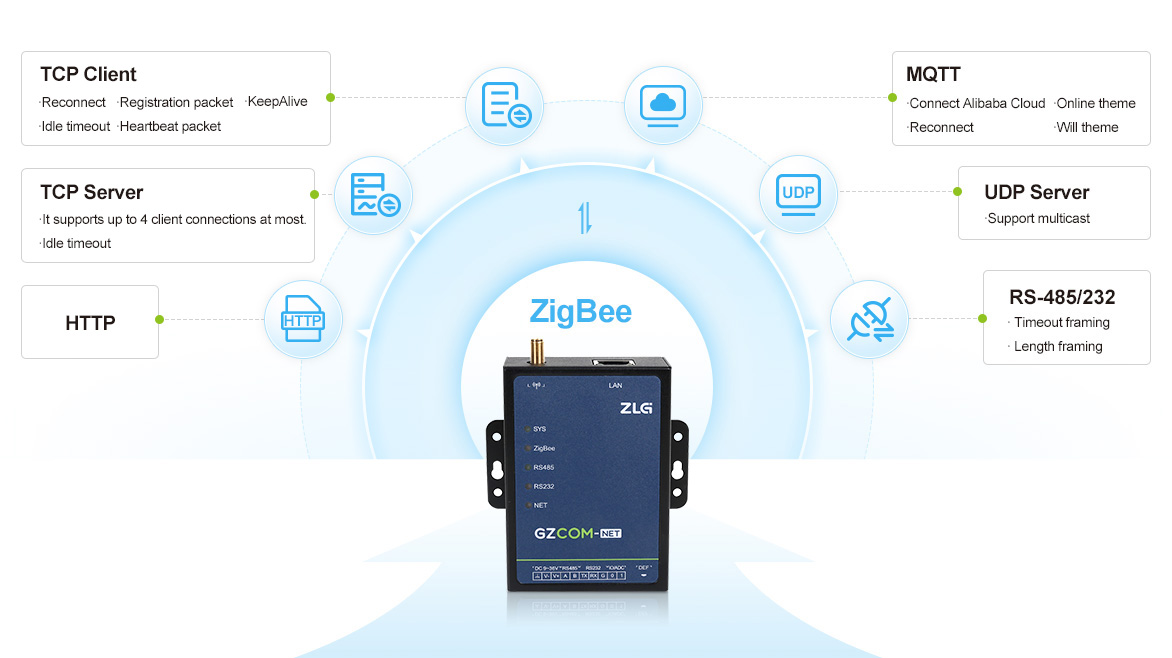
This also uses MAC address authentication. LEAP is not secure; THC-LeapCracker can be used to break Cisco's version of LEAP and be used against computers connected to an access point in the form of a dictionary attack. Anwrap and asleap are other crackers capable of breaking LEAP. PEAP Figure 3: Intelligent ZigBee data communication gateway GZCOM-NET - Guangzhou ...
This stands for Protected Extensible Authentication Protocol. This protocol allows for a secure transport of data, passwords, and encryption keys without the need for a certificate server. This was developed by Cisco, Microsoft, and RSA Security. Other EAPs There are other types of Extensible Authentication Protocol implementations that are based on the EAP framework. The framework that was established supports existing EAP types as well as future authentication methods.
EAP-TLS offers very good protection because of its mutual authentication. Both the client and the network are authenticated using certificates and per-session WEP keys. EAP-FAST also offers good protection. EAP-TTLS is another alternative made by Certicom and Funk Software. It is more convenient as one does not need to distribute certificates to users, yet offers slightly less protection than EAP-TLS.
WPA2 is a WiFi Alliance-branded version of the final 802.11i standard. The primary enhancement over WPA is the inclusion of the AES-CCMP algorithm as a mandatory feature. Both WPA and WPA2 support EAP authentication methods using RADIUS servers and preshared key (PSK). The number of WPA and WPA2 networks are increasing, while the number of WEP networks are decreasing, because of the security vulnerabilities in WEP. WPA2 has been found to have at least one security vulnerability, nicknamed Hole196. The vulnerability uses the WPA2 Group Temporal Key (GTK), which is a shared key among all users of the same BSSID, to launch attacks on other users of the same BSSID. It is named after page 196 of the IEEE 802.11i specification, where the vulnerability is discussed. In order for this exploit to be performed, the GTK must be known by the attacker.
This stands for WLAN Authentication and Privacy Infrastructure. This is a wireless security standard defined by the Chinese government. With an increasing number of mobile devices with 802.1X interfaces, security of such mobile devices becomes a concern. While open standards such as Kismet are targeted towards securing laptops, access point solutions should extend towards covering mobile devices also. Host-based solutions for mobile handsets and PDA's with 802.1X interface. Security within mobile devices falls under three categories: Protecting against ad hoc networks Connecting to rogue access points Mutual authentication schemes such as WPA2 as described above Wireless IPS solutions now offer wireless security for mobile devices. Mobile patient monitoring devices are becoming an integral part of the healthcare industry and these devices will eventually become the method of choice for accessing and implementing health checks for patients located in remote areas. For these types of patient monitoring systems, security and reliability are critical because they can influence the condition of patients and could leave medical professionals in the dark about the condition of the patient if compromised.
Aradial RADIUS Server Cisco Secure Access Control Software freeRADIUS (open-source) Funk Software Steel Belted RADIUS (Odyssey) Microsoft Internet Authentication Service Meetinghouse Data EAGIS SkyFriendz (free cloud solution based on freeRADIUS) Client software comes built-in with Windows XP and may be integrated into other OS's using any of the following software: AEGIS-client Cisco ACU-client Intel PROSet/Wireless Software Odyssey client Xsupplicant (open1X)-project Remote Authentication Dial In User Service (RADIUS) is an AAA (authentication, authorization and accounting) protocol used for remote network access. RADIUS, developed in 1991, was originally proprietary but then published in 1997 under ISOC documents RFC 2138 and RFC 2139. The idea is to have an inside server act as a gatekeeper by verifying identities through a username and password that is already pre-determined by the user. A RADIUS server can also be configured to enforce user policies and restrictions as well as record accounting information such as connection time for purposes such as billing.
The wireless network is after all confined to a small geographical area. A computer connected to the Internet and having improper configurations or other security problems can be exploited by anyone from anywhere in the world, while only clients in a small geographical range can exploit an open wireless access point. Thus the exposure is low with an open wireless access point, and the risks with having an open wireless network are small. However, one should be aware that an open wireless router will give access to the local network, often including access to file shares and printers. The only way to keep communication truly secure is to use end-to-end encryption. For example, when accessing an internet bank, one would almost always use strong encryption from the web browser and all the way to the bank – thus it should not be risky to do banking over an unencrypted wireless network. The argument that anyone can sniff the traffic applies to wired networks too, where system administrators and possible hackers have access to the links and can read the traffic. Also, anyone knowing the keys for an encrypted wireless network can gain access to the data being transferred over the network. If services like file shares, access to printers etc. are available on the local net, it is advisable to have authentication (i.e. by password) for accessing it (one should never assume that the private network is not accessible from the outside). Correctly set up, it should be safe to allow access to the local network to outsiders. With the most popular encryption algorithms today, a sniffer will usually be able to compute the network key in a few minutes. It is very common to pay a fixed monthly fee for the Internet connection, and not for the traffic – thus extra traffic will not be detrimental. Where Internet connections are plentiful and cheap, freeloaders will seldom be a prominent nuisance. On the other hand, in some countries including Germany, persons providing an open access point may be made (partially) liable for any illegal activity conducted via this access point. Also, many contracts with ISPs specify that the connection may not be shared with other persons.
978-3838372266 "The Evolution of 802.11 Wireless Security" (PDF). ITFFROC. 2010-04-18. Boyle, Randall, Panko, Raymond. Corporate Computer Security. Upper Saddle River, New Jersey. 2015 A MAC address (medium access control address or media access control address) is a unique identifier assigned to a network interface controller (NIC) for use as a network address in communications within a network segment. This use is common in most IEEE 802 networking technologies, including Ethernet, Wi-Fi, and Bluetooth. Within the Open Systems Interconnection (OSI) network model, MAC addresses are used in the medium access control protocol sublayer of the data link layer. As typically represented, MAC addresses are recognizable as six groups of two hexadecimal digits, separated by hyphens, colons, or without a separator. MAC addresses are primarily assigned by device manufacturers, and are therefore often referred to as the burned-in address, or as an Ethernet hardware address, hardware address, or physical address. The address can be stored in the interface hardware, such as in its read-only memory, or by a firmware mechanism. Many network interfaces, however, support changing their MAC addresses. The address typically includes a manufacturer's organizationally unique identifier (OUI). MAC addresses are formed according to the principles of two numbering spaces based on extended unique identifiers (EUIs) managed by the Institute of Electrical and Electronics Engineers (IEEE): EUI-48—which replaces the obsolete term MAC-48—and EUI-64. Network nodes with multiple network interfaces, such as routers and multilayer switches, must have a unique MAC address for each network interface in the same network. However, two network interfaces connected to two different networks can share the same MAC address.
The IEEE 802 MAC address originally comes from the Xerox Network Systems Ethernet addressing scheme. This 48-bit address space contains potentially 248 (over 281 trillion) possible MAC addresses. The IEEE manages the allocation of MAC addresses, originally known as MAC-48 and now called EUI-48 identifiers. The IEEE has a target lifetime of 100 years (until 2080) for applications using EUI-48 space and restricts applications accordingly. The IEEE encourages adoption of the more plentiful EUI-64 for non-Ethernet applications. The distinctions between EUI-48 and MAC-48 identifiers are in name and application only. MAC-48 was used to address hardware interfaces within existing 802-based networking applications; EUI-48 is now used for 802-based networking and is also used to identify other devices and software, for example Bluetooth. The IEEE now considers MAC-48 to be an obsolete term. EUI-48 is now used in all cases. In addition, the EUI-64 numbering system originally encompassed both MAC-48 and EUI-48 identifiers by a simple translation mechanism. These translations have since been deprecated. The Individual Address Block (IAB) is an inactive registry which has been replaced by the MA-S (MAC address block, small), previously named OUI-36, and has no overlaps in addresses with the IAB registry product as of January 1, 2014. The IAB uses an OUI from the MA-L (MAC address block, large) registry, previously called the OUI registry.
The term OUI is still in use, but the IEEE Registration Authority does not administer them. An OUI is concatenated with 12 additional IEEE-provided bits (for a total of 36 bits), leaving only 12 bits for the organisation owning the IAB to assign to its (up to 4096) individual devices. An IAB is ideal for organizations requiring not more than 4096 unique 48-bit numbers (EUI-48). Unlike an OUI, which allows the assignee to assign values in various number spaces (for example, EUI-48, EUI-64, and the various context-dependent identifier number spaces, as in SNAP or EDID), the Individual Address Block could only be used to assign EUI-48 identifiers. All other potential uses based on the OUI from which the IABs are allocated are reserved and remain the property of the IEEE Registration Authority. Between 2007 and September 2012, the OUI value 00:50:C2 was used for IAB assignments. After September 2012, the value 40:D8:55 was used. Owners of an already assigned IAB may continue to use it. The MA-S registry includes, for each registrant, both a 36-bit unique number used in some standards and a block of EUI-48 and EUI-64 identifiers (while the registrant of an IAB cannot assign an EUI-64). MA-S does not include assignment of an OUI. Additionally, the MA-M (MAC address block, medium) provides both 220 EUI-48 identifiers and 236 EUI-64 identifiers, the first 28 bits being assigned by IEEE. The first 24 bits of the assigned MA-M block are an OUI assigned to IEEE that will not be reassigned, so the MA-M does not include assignment of an OUI.
Packets sent to the broadcast address, all one bits, are received by all stations on a local area network. In hexadecimal the broadcast address would be FF:FF:FF:FF:FF:FF. A broadcast frame is flooded and is forwarded to and accepted by all other nodes. Packets sent to a multicast address are received by all stations on a LAN that have been configured to receive packets sent to that address. Functional addresses identify one or more Token Ring NICs that provide a particular service, defined in IEEE 802.5. These are all examples of group addresses, as opposed to individual addresses; the least significant bit of the first octet of a MAC address distinguishes individual addresses from group addresses. That bit is set to 0 in individual addresses and set to 1 in group addresses. Group addresses, like individual addresses, can be universally administered or locally administered.
IEEE 802 networks Ethernet 802.11 wireless networks (Wi-Fi) Bluetooth IEEE 802.5 Token Ring Fiber Distributed Data Interface (FDDI) Asynchronous Transfer Mode (ATM), switched virtual connections only, as part of an NSAP address Fibre Channel and Serial Attached SCSI (as part of a World Wide Name) The ITU-T G.hn standard, which provides a way to create a high-speed (up to 1 gigabit/s) local area network using existing home wiring (power lines, phone lines and coaxial cables).
The G.hn Application Protocol Convergence (APC) layer accepts Ethernet frames that use the EUI-48 format and encapsulates them into G.hn Medium Access Control Service Data Units (MSDUs). Every device that connects to an IEEE 802 network (such as Ethernet and Wi-Fi) has an EUI-48 address. Common networked consumer devices such as PCs, smartphones and tablet computers use EUI-48 addresses. EUI-64 identifiers are used in: IEEE 1394 (FireWire) InfiniBand IPv6 (Modified EUI-64 as the least-significant 64 bits of a unicast network address or link-local address when stateless address autoconfiguration is used.) IPv6 uses a modified EUI-64, treats MAC-48 as EUI-48 instead (as it is chosen from the same address pool) and inverts the local bit. This results in extending MAC addresses (such as IEEE 802 MAC address) to modified EUI-64 using only FF-FE (and never FF-FF) and with the local bit inverted. Zigbee / 802.15.4 / 6LoWPAN wireless personal-area networks IEEE 11073-20601 (IEEE 11073-20601 compliant medical devices) Z-Wave is a Wireless communications protocol used primarily for residential and commercial building automation. It is a mesh network using low-energy radio waves to communicate from device to device, allowing for wireless control of smart home devices, such as smart lights, security systems, thermostats, sensors, smart door locks, and garage door openers. Z-Wave Long Range (ZWLR) is a sub-GHz wireless communication protocol designed to extend smart home connectivity, offering a range of up to 1.5 miles. It enables direct hub-to-device communication, supports up to 4,000 nodes per network, and is designed for large properties and commercial, industrial, and outdoor use. Both technologies are managed and owned by the Z-Wave Alliance, with over 200 companies involved in the technology within the organization. Like other protocols and systems aimed at the residential, commercial, MDU and building markets, a Z-Wave system can be controlled from a smart phone, tablet, or computer, and locally through a smart speaker, wireless key fob, or wall-mounted panel with a Z-Wave gateway or central control device serving as both the hub or controller. Z-Wave provides the application layer interoperability between home control systems of different manufacturers that are a part of its alliance. There is a growing number of interoperable Z-Wave products; over 1,700 in 2017, over 2,600 by 2019, over 4,000 by 2022, and over 4,500 by 2026.
Most smart home networks leak more data than homeowners realize. I discovered this the hard way after setting up a Zigbee sniffer for the first time and watching unencrypted join requests fly across my neighbor’s network. Zigbee protocol security testing isn’t just academic anymore, it’s essential for understanding IoT vulnerabilities that affect millions of deployed devices. Whether you’re auditing enterprise IoT deployments or testing your own smart home setup, proper protocol analysis separates guesswork from actual security posture.
2. System Architecture & Core Working Principles The problem? Most security researchers treat Zigbee like Wi-Fi and wonder why their tools don’t work. Zigbee operates on IEEE 802.15.4, uses mesh networking, and has encryption quirks that make packet capture tricky even with dedicated hardware. This guide covers the actual process, hardware selection, capture setup, decryption workflows, and vulnerability patterns I’ve found in real deployments.
Smart home adoption exploded over the past three years. According to industry reports, over 300 million Zigbee devices shipped globally in 2024. That’s door locks, thermostats, medical sensors, and industrial controls all using the same protocol stack. The security model assumes proper implementation. In practice, I’ve found default link keys still active in production devices, unauthenticated pairing modes left open, and network keys transmitted in plaintext during commissioning. These aren’t theoretical they’re exploitation vectors I’ve demonstrated on consumer hardware.
Zigbee operates in the 2.4 GHz ISM band using 16 channels. Each channel is 5 MHz wide, and devices can hop between them for interference avoidance. This channel hopping complicates passive monitoring compared to single-channel protocols. You need hardware that can either track channel changes or capture across multiple channels simultaneously. The mesh topology means every device can route traffic. One compromised bulb becomes your pivot point into the entire network. I’ve used this in testing to reach door locks four hops away from my entry point. Traditional perimeter security doesn’t apply when your attack surface includes every $15 smart plug.
Zigbee sits on top of IEEE 802.15.4 for the physical and MAC layers. Above that, you get the Zigbee network layer (NWK) handling routing and security, and the application layer (APS) managing endpoints and clusters. Security happens at two layers. The NWK layer uses a network key shared by all devices for encrypting routing and control frames. The APS layer uses link keys for end-to-end encryption between specific device pairs. If you’re testing security, you need both keys to decrypt most traffic.
You have three realistic options for Zigbee packet capture. The TI CC2531 USB dongle is the budget choice at around £30. It works with the official TI packet sniffer software but locks you into Windows. I burned through two of these before upgrading because the firmware is finicky and capture drops are common under heavy traffic. The better option is a dedicated Zigbee Sniffer Kit built around newer silicon like the CC2652 or nRF52840. These handle multi-channel capture, have better sensitivity, and work with open-source tools. Your packet capture quality directly impacts your ability to decrypt traffic later. Dropped frames mean missing key exchanges.
For mobile testing, I pair a Flipper Zero with a CC1101 add-on board for Sub-GHz work, then use a separate Zigbee sniffer for 2.4 GHz. The Flipper handles replay attacks and basic RF analysis while the dedicated sniffer captures protocol-level traffic. This combo costs around £350 total but covers most wireless IoT testing scenarios. The capture software matters as much as the hardware. Wireshark with the Zigbee dissector plugins is standard. You’ll also want KillerBee (Python toolkit for 802.15.4/Zigbee) and zbstumbler for network discovery. Install all three before you start capturing.
Start with network discovery. Run zbstumbler in scanning mode to identify active Zigbee networks in range. You’ll see PAN IDs, channel numbers, and device counts. Pick your target network and lock your sniffer to that channel. The critical phase is capturing the network key exchange. New devices joining a Zigbee network receive the network key encrypted with a transport key during commissioning. If you catch this exchange, you can derive the network key and decrypt subsequent traffic.
I keep my sniffer running continuously during testing because you never know when a device will rejoin or a new device will pair. I caught a smart lock transmitting its network key in plaintext during a firmware update three hours into a capture session. Patience pays off. Raw Zigbee captures are encrypted. You need keys to make sense of the data. The default Zigbee Alliance link key (ZigBeeAlliance09) works surprisingly often. I’ve successfully decrypted traffic from major smart home brands using this default key because their devices never rotated it post-install.
Configure Wireshark’s Zigbee security settings before opening your capture file. Add known network keys and link keys to the decryption table. Enable the “Try to decrypt with network key” option. Reprocess the capture and watch previously garbled packets resolve into readable application commands. For hardened networks, you need to sniff the actual key exchange or extract keys from hardware. I’ve pulled network keys from smart bulbs using JTAG and SWD debug interfaces. The Raspberry Pi 5 makes an excellent debugging platform with OpenOCD for this work. You’re looking for keys stored in flash memory or transmitted during firmware updates.
The KillerBee toolkit includes zbdsniff for automated key extraction from captures. Point it at your pcap file and it’ll search for common transport key patterns and attempt decryption. This works best with full captures starting from network formation. After testing dozens of smart home deployments, certain patterns repeat. Unauthenticated pairing modes left active past initial setup are everywhere. I’ve joined live Zigbee networks without any authorization simply by sending a join request during the permitting period.
Install codes were supposed to fix this. They’re unique per-device keys derived from a code printed on the device label. In practice, many devices accept the default install code or ship with predictable variants. I’ve scripted install code generation based on MAC addresses and successfully commissioned devices without physical access. Touchlink commissioning is another common weakness. It’s supposed to require physical proximity (touching the device with a commissioning tool). The reality is touchlink requests work from several meters away. I’ve factory-reset and re-commissioned smart bulbs from outside buildings using this method.
Zigbee supports automatic network key rotation as a security mechanism. The coordinator can generate a new network key and distribute it to all devices, then switch to using the new key. This limits the impact of a compromised key. Most networks I’ve tested never rotate keys. Ever. I’ve captured the same network key in use on a corporate IoT deployment over an eight-month testing period. Once you have that key, you maintain access indefinitely unless someone physically resets every device.
The key distribution process itself has timing vulnerabilities. All devices must receive and acknowledge the new key before the coordinator switches to using it. If you jam this distribution, devices end up out of sync and the network fragments. I’ve caused denial-of-service conditions during key rotation on test networks by selectively jamming acknowledgment frames. My current setup uses a Zigbee Sniffer Kit for passive capture, a CC2531 running alternative firmware for injection attacks, and a Raspberry Pi 5 running Kali Linux as the analysis workstation. Total cost around £450 excluding the Pi if you already have one.
The Pi 5 handles Wireshark, KillerBee, and Scapy scripts without performance issues. I can capture on one USB sniffer while simultaneously injecting with another and analyzing in real-time. The 8GB RAM model prevents capture buffer overflows during extended sessions. For mobile testing, everything fits in a small backpack. A power bank keeps the Pi running for 4-6 hours. I use a small wireless keyboard for field work, but SSH from my phone works for most tasks. The entire kit draws under 15W so battery life isn’t a concern.
Storage matters more than you’d expect. A busy Zigbee network with 20+ devices generates 500MB-1GB of capture data per hour. I use a 256GB microSD card in the Pi and back up captures to cloud storage nightly. You’ll want those captures for offline analysis and report generation. Once you have decrypted traffic, the real analysis begins. I use Scapy to parse Zigbee frames and extract application-layer commands. This reveals what devices are actually doing—door lock states, thermostat setpoints, occupancy sensor data.
3. Software Implementation, Frameworks & Protocols Build a device database as you test. Note MAC addresses, device types, supported clusters, and command sequences. This knowledge transfers between deployments because many devices use identical chipsets and firmware. A Philips Hue bulb behaves the same everywhere.
Look for insecure defaults in cluster configurations. Many devices expose sensitive attributes with read/write access to any network member. I’ve changed smart lock PIN codes by writing to the door lock cluster without any additional authentication beyond network membership. With network access established, injection attacks become possible. Craft custom Zigbee frames using KillerBee’s kbstab tool or Scapy. Send commands directly to devices or impersonate trusted network members.
Replay attacks work better than they should. Many Zigbee implementations don’t properly validate frame counters or use nonces. I’ve replayed door unlock commands captured hours earlier and had them execute successfully. The devices had no mechanism to detect the replay. For testing replay resistance, capture a legitimate command frame, modify the timestamp, and retransmit it. If the device executes the command, you’ve found a vulnerability. Document the device model, firmware version, and cluster details for your report.
After breaking Zigbee security, let’s talk defense. Enable install codes if your coordinator supports them. This prevents unauthorized device joining even during commissioning periods. Document and securely store your install codes—you’ll need them for legitimate device additions. Implement network key rotation on a schedule. Quarterly rotation limits exposure from compromised keys. Test this in your lab first because poorly implemented rotation will fragment your network. Some devices handle key updates gracefully, others don’t.
Disable touchlink commissioning unless you specifically need it. Most controllers allow this as a configuration option. The convenience isn’t worth the security risk for most deployments. If you must use touchlink, do it with the coordinator’s antenna directly against the device to minimize range. Physical security matters for IoT devices. An attacker with physical access to a coordinator can extract network keys, flash malicious firmware, or simply steal the device. Secure your coordinator in a locked cabinet or equipment room. Treat it like network infrastructure.
Before you start testing, understand the legal boundaries. Testing your own network is legal everywhere. Testing a client’s network requires written authorization detailing scope, methods, and timeframes. Zigbee sniffing without authorization likely violates wiretapping laws in most jurisdictions. If you discover vulnerabilities during research, follow responsible disclosure practices. Contact the vendor first, give them 90 days to patch, then publish your findings. MITRE provides CVE IDs for IoT vulnerabilities if you need formal tracking.
Document everything during testing. Capture files, timestamps, device information, and command sequences all matter for reports and legal defense if questions arise later. I keep testing logs for at least two years after completing engagements. For more information on IoT security standards and testing frameworks, the [OWASP IoT Security Project](https://owasp.org/www-project-internet-of-things/) provides excellent resources. NIST also publishes guidelines for IoT device security that inform testing methodology.
What’s the difference between Zigbee and Z-Wave for security testing? Zigbee operates on 2.4 GHz with higher data rates but more interference, while Z-Wave uses sub-1 GHz frequencies with better range. Z-Wave networks are typically smaller and use proprietary encryption that’s harder to analyze without vendor cooperation. Your sniffer hardware differs completely between protocols.
Can I use a WiFi Pineapple to test Zigbee networks? No. WiFi Pineapple operates on 802.11 (WiFi) which is completely different from 802.15.4/Zigbee despite sharing the 2.4 GHz band. You need dedicated Zigbee sniffer hardware with proper radio chipsets. Mixing up these protocols is like trying to use an FM radio to listen to WiFi. How long does it take to capture a Zigbee network key? It depends entirely on network activity. If devices are actively joining or a key rotation happens, you might capture it in minutes. On a stable network with no changes, you could wait days. I usually combine passive capture with active triggering—factory resetting a test device to force a join sequence.
Is Flipper Zero enough for complete Zigbee testing? Not by itself. Flipper Zero excels at Sub-GHz (under 1 GHz) protocol work but has limited Zigbee capabilities. You need a dedicated Zigbee sniffer for proper 802.15.4 packet capture and decryption. Use them together—Flipper for general RF analysis and replay attacks, dedicated sniffer for protocol-level testing. Start with your own smart home deployment before touching client networks. Build a test environment with mixed device types and practice capturing keys, decrypting traffic, and documenting vulnerabilities. The experience translates directly to professional penetration testing.
The threat landscape keeps evolving as more critical infrastructure moves to Zigbee. Medical devices, industrial sensors, and building automation systems all present higher-stakes testing scenarios than smart bulbs. Your methodology stays the same but the impact analysis changes significantly. If you’re serious about IoT security research, proper tooling makes the difference between surface-level testing and deep protocol analysis. Explore our complete range of wireless security testing hardware to build a professional-grade lab.
We all encounter IoT and home automation in some form or another, from smart speakers to automated sensors that control water pumps. These services appear simple and straightforward to us, but many devices and protocols work together under the hood to deliver them. One of those protocols is Zigbee. Zigbee is a low-power wireless protocol (based on IEEE 802.15.4) used by many smart devices to talk to each other. It’s common in homes, but is also used in industrial environments where hundreds or thousands of sensors may coordinate to support a process.
There are many guides online about performing security assessments of Zigbee. Most focus on the Zigbee you see in home setups. They often skip the Zigbee used at industrial sites, what I call ‘non-public’ or ‘industrial’ Zigbee. In this blog, I will take you on a journey through Zigbee assessments. I’ll explain the basics of the protocol and map the attack surface likely to be found in deployments. I’ll also walk you through two realistic attack vectors that you might see in facilities, covering the technical details and common problems that show up in assessments. Finally, I will present practical ways to address these problems.
Zigbee is a wireless communication protocol designed for low-power applications in wireless sensor networks. Based on the IEEE 802.15.4 standard, it was created for short-range and low-power communication. Zigbee supports mesh networking, meaning devices can connect through each other to extend the network range. It operates on the 2.4 GHz frequency band and is widely used in smart homes, industrial automation, energy monitoring, and many other applications.
You may be wondering why there’s a need for Zigbee when Wi-Fi is everywhere? The answer depends on the application. In most home setups, Wi-Fi works well for connecting devices. But imagine you have a battery-powered sensor that isn’t connected to your home’s electricity. If it used Wi-Fi, its battery would drain quickly – maybe in just a few days – because Wi-Fi consumes much more power. In contrast, the Zigbee protocol allows for months or even years of uninterrupted work.
Now imagine an even more extreme case. You need to place sensors in a radiation zone where humans can’t go. You drop the sensors from a helicopter and they need to operate for months without a battery replacement. In this situation, power consumption becomes the top priority. Wi-Fi wouldn’t work, but Zigbee is built exactly for this kind of scenario. Also, Zigbee has a big advantage if the area is very large, covering thousands of square meters and requiring thousands of sensors: it supports thousands of nodes in a mesh network, while Wi-Fi is usually limited to hundreds at most.
There are lots more ins and outs, but these are the main reasons Zigbee is preferred for large-scale, low-power sensor networks. 4. Practical Deployment, Analysis & Case Studies Since both Zigbee and IEEE 802.15.4 define wireless communication, many people confuse the two. The difference between them, to put it simply, concerns the layers they support. IEEE 802.15.4 defines the physical (PHY) and media access control (MAC) layers, which basically determine how devices send and receive data over the air. Zigbee (as well as other protocols like Thread, WirelessHART, 6LoWPAN, and MiWi) builds on IEEE 802.15.4 by adding the network and application layers that define how devices form a network and communicate.
Zigbee operates in the 2.4 GHz wireless band, which it shares with Wi-Fi and Bluetooth. The Zigbee band includes 16 channels, each with a 2 MHz bandwidth and a 5 MHz gap between channels. This shared frequency means Zigbee networks can sometimes face interference from Wi-Fi or Bluetooth devices. However, Zigbee’s low power and adaptive channel selection help minimize these conflicts.
There are three main types of Zigbee devices, each of which plays a different role in the network. The coordinator can have child devices, which can be either Zigbee routers or Zigbee end devices. Zigbee end devices do not accept child devices unless they are configured as both a router and an endpoint simultaneously. Both addresses can be used in the MAC and network layers, unlike in TCP/IP, where the MAC address is used only in Layer 2 and the IP address in Layer 3.
Zigbee has many attack surfaces, such as protocol fuzzing and low-level radio attacks. In this post, however, I’ll focus on application-level attacks. Our test setup uses two attack vectors and is intentionally small to make the concepts clear. In our setup, a Zigbee coordinator is connected to a single device that functions as both a Zigbee endpoint and a router. The coordinator also has other interfaces (Ethernet, Bluetooth, Wi-Fi, LTE), while the endpoint has a relay attached that the coordinator can switch on or off over Zigbee. This relay can be triggered by events coming from any interface, for example, a Bluetooth command or an Ethernet message.
Our goal will be to take control of the relay and toggle its state (turn it off and on) using only the Zigbee interface. Because the other interfaces (Ethernet, Bluetooth, Wi-Fi, LTE) are out of scope, the attack must work by hijacking Zigbee communication. For the purposes of this research, we will attempt to hijack the communication between the endpoint and the coordinator. The two attack vectors we will test are: In this scenario, we assume the Zigbee network is already up and running and that both the coordinator and endpoint nodes are working normally. The coordinator has additional interfaces, such as Ethernet, and the system uses those interfaces to trigger the relay. For instance, a command comes in over Ethernet and the coordinator sends a Zigbee command to the endpoint to toggle the relay. Our goal is to toggle the relay by injecting simulated legitimate Zigbee packets, using only the Zigbee link.
The first step in any radio assessment is to sniff the wireless traffic so we can learn how the devices talk. For Zigbee, a common and simple tool is the nRF52840 USB dongle by Nordic Semiconductor. With the official nRF Sniffer for 802.15.4 firmware, the dongle can run in promiscuous mode to capture all 802.15.4/Zigbee traffic. Those captures can be opened in Wireshark with the appropriate dissector to inspect the frames.
Zigbee runs on one of the 16 channels that we mentioned earlier, so we must set the sniffer to the same channel that the network uses. One practical way to scan the channels is to change the sniffer channel manually in Wireshark and watch for Zigbee traffic. When we see traffic, we know we’ve found the right channel. After selecting the channel, we will be able to see the communication between the endpoint and the coordinator, though it will most likely be encrypted: In the “Info” column, we can see that Wireshark only identifies packets as Data or Command without specifying their exact type, and that’s because the traffic is encrypted.
Even when Zigbee payloads are encrypted, the network and MAC headers remain visible. That means we can usually read things like source and destination addresses, PAN ID, short and extended MAC addresses, and frame control fields. The application payload (i.e., the actual command to toggle the relay) is typically encrypted at the Zigbee network/application layer, so we won’t see it in clear text without encryption keys. Nevertheless, we can still learn enough from the headers.
Zigbee supports several key types and encryption models. In this post, we’ll keep it simple and look at a case involving only two security-related devices: a Zigbee coordinator and a device that is both an endpoint and a router. That way, we’ll only use a network encryption model, whereas with, say, mesh networks there can be various encryption models in use. The network encryption model is a common concept. The traffic that we sniffed earlier is typically encrypted using the network key. This key is a symmetric AES-128 key shared by all devices in a Zigbee network. It protects network-layer packets (hop-by-hop) such as routing and broadcast packets. Because every router on the path shares the network key, this encryption method is not considered end-to-end.
Depending on the specific implementation, Zigbee can use two approaches for application payloads: The link key provides end-to-end protection of the APS payload between the two devices. Because the network key could allow an attacker to read and forge many types of network traffic, it must be random and protected. Exposing the key effectively compromises the entire network.
When a new device joins, the coordinator (Trust Center) delivers the network key using a Transport Key command. That transport packet must be protected by a link key so the network key is not exposed in clear text. The link key authenticates the joining device and protects the key delivery. A common historical problem is the global default Trust Center link key, “ZigBeeAlliance09”. It was included in early versions of Zigbee (pre-3.0) to facilitate testing and interoperability. However, many vendors left it enabled on consumer devices, and that has caused major security issues. If an attacker knows this key, they can join devices and read or steal the network key.
Newer versions – Zigbee 3.0 and later – introduced installation codes and procedures to derive unique link keys for each device. An installation code is usually a factory-assigned secret (often encoded on the device label) that the Trust Center uses to derive a unique link key for the device in question. This helps avoid the problems caused by a single hard-coded global key. Unfortunately, many manufacturers still ignore these best practices. During real assessments, we often encounter devices that use default or hard-coded keys.
If an endpoint has already joined the network and communicates with the coordinator using the network key, there are two main options for decrypting traffic: After successful decryption, packet types and readable application commands will be visible, such as Link Status or on/off cluster commands: Now that we can read and potentially decrypt traffic, we need hardware and software to inject packets over the Zigbee link between the coordinator and the endpoint. To keep this practical and simple, I opted for cheap, widely available tools that are easy to set up.
5. Performance Evaluation & Extended Technical Observations For the hardware, I used the nRF52840 USB dongle, the same device we used for sniffing. It’s inexpensive, easy to find, and supports IEEE 802.15.4/Zigbee, so it can sniff and transmit. The dongle runs the firmware we can use. A good firmware platform is Zephyr RTOS . Zephyr has an IEEE 802.15.4 radio API that enables the device to receive raw frames, essentially enabling sniffer mode, as well as send raw frames as seen in the snippets below.
Using this API and other components, we created a transceiver implementation written in C, compiled it to firmware, and flashed it to the dongle. The firmware can expose a simple runtime interface, such as a USB serial port, which allows us to control the radio from a laptop. At runtime, the dongle listens on the serial port (for example, /dev/ttyACM1). Using a script, we can send it raw bytes, which the firmware will pass to the radio API and transmit to the channel. The following is an example of a tiny Python script to open the serial port: I used the Scapy tool with the 802.15.4/Zigbee extensions to build Zigbee packets. Scapy lets us assemble packets layer-by-layer – MAC → NWK → APS → ZCL – and then convert them to raw bytes to send to the dongle. We will talk about APS and ZCL in more detail later.
Before sending, the packet must be properly encrypted and signed so the endpoint accepts it. That means applying AES-CCM (AES-128 with MIC) using the network key (or the correct link key) and adhering to Zigbee’s rules for packet encryption and MIC calculation. This is how we implemented the encryption and MIC in Python (using a cryptographic library) after building the Scapy packet. We then sent the final bytes to the dongle.
Now that we know how to inject packets, the next question is what to inject. To toggle the relay, we simply need to send the same type of command that the coordinator already sends. The easiest way to find that command is to sniff the traffic and read the application payload. However, when we look at captures in Wireshark, we can see many packets under ZCL marked [Malformed Packet].
A “malformed” ZCL packet usually means Wireshark could not fully interpret the packet because the application layer is non-standard or lacks details Wireshark expects. To understand why this happens, let’s look at the Zigbee application layer. Putting all this together, in the standard home automation traffic we see APS pointing to the home automation profile, the On/Off cluster, and a destination endpoint (for example, endpoint 1). In ZCL, the byte 0x00 often means “Off”.
In many industrial setups, vendors use private profiles or custom application frameworks. That’s why Wireshark can’t decode the packets; the AF payload is custom, so the dissector doesn’t know the format. So how do we find the right bytes to toggle the switch when the application is private? Our strategy has two phases. With the legitimate payload at hand, we can now turn to creating our own packet. There are two ways to do that. First, we need to replay or duplicate the captured application payload exactly as it is. This works if there are no freshness checks like sequence numbers. Otherwise, we have to reverse-engineer the payload and adjust any counters or fields that prevent replay.
For instance, many applications include an application-level counter. If the device ignores packets with a lower application counter, we must locate and increment that counter when we craft our packet. Another important protective measure is the frame counter inside the Zigbee security header (in the network header security fields). The frame counter prevents replay attacks; the receiver expects the frame counter to increase with each new packet, and will reject packets with a lower or repeated counter.
If all of the above are handled correctly, we will be able to hijack the Zigbee communication and toggle the relay (turn it off and on) using only the Zigbee link. The goal of this attack vector is to force the Zigbee endpoint to leave its original coordinator’s network and join our spoofed network so that we can take control of the device. To do this, we must achieve two things: To better understand how to manipulate endpoint connections, let’s first describe the concept of a beacon frame. Beacon frames are periodic announcements sent by a coordinator and by routers. They advertise the presence of a network and provide join information, such as: When a device wants to join, it sends a beacon request across Zigbee channels and waits for beacon replies from nearby coordinators/routers. Even if the network is not beacon-enabled for regular synchronization, beacon frames are still used during the join/discovery process, so they are mandatory when a node tries to discover networks.
Note that beacon frames exist at both the Zigbee and IEEE 802.15.4 levels. The MAC layer carries the basic beacon structure that Zigbee then extends with network-specific fields. Now, we can force the endpoint to leave its network by abusing how Zigbee handles PAN conflicts. If a coordinator sees beacons from another coordinator using the same PAN ID and the same channel, it may trigger a PAN ID conflict resolution.
When that happens, the coordinator can instruct its nodes to change PAN ID and rejoin, which causes them to leave and then attempt to join again. That rejoin window gives us an opportunity to advertise a spoofed coordinator and capture the joining node. In the capture shown below, packet 7 is a beacon generated by our spoofed coordinator using the same PAN ID as the real network. As a result, the endpoint with the address 0xe8fa leaves the network (see packets 14–16).
After forcing the endpoint to leave its original network by sending a fake beacon, the next step is to make the endpoint choose our spoofed coordinator. At this point, we assume we already have the necessary keys (network and link keys) and understand how the application behaves. To impersonate the original coordinator, our spoofed coordinator must reply to any beacon request the endpoint sends. The beacon response must include the same Extended PAN ID (and other fields) that the endpoint expects. If the endpoint deems our beacon acceptable, it may attempt to join us.
If two coordinators advertise the same Extended PAN ID but one has a higher Update ID, some stacks will prefer the beacon with the higher Update ID. This is undefined behavior across implementations; it works on some stacks but not on others. In my experience, sometimes it works and sometimes it fails. There are lots of other similar quirks we can try during an assessment.
Even if the endpoint chooses our fake coordinator, the connection may be unstable. One main reason for that is the timing. The endpoint expects ACKs for the frames it sends to the coordinator, as well as fast responses regarding connection initiation packets. If our responder is implemented in Python on a laptop that receives packets, builds responses, and forwards them to a dongle, the round trip will be too slow. The endpoint will not receive timely ACKs or packets and will drop the connection.
In short, we’re not just faking a few packets; we’re trying to reimplement parts of Zigbee and IEEE 802.15.4 that must run quickly and reliably. This is usually too slow for production stacks when done in high-level, interpreted code. A practical fix is to run a real Zigbee coordinator stack directly on the dongle. For example, the nRF52840 dongle can act as a coordinator if flashed with the right Nordic SDK firmware (see Nordic’s network coordinator sample ). That provides the correct timing and ACK behavior needed for a stable connection.
However, that simple solution has one significant disadvantage. In industrial deployments we often run into incompatibilities. In my tests I compared beacons from the real coordinator and the Nordic coordinator firmware. Notable differences were visible in stack profile headers: The stack profile identifies the network profile type. Common values include 0x00, which is a network-specific (private) profile, and 0x02, which is a Zigbee Pro (public) profile.
If the endpoint expects a network-specific profile (i.e., it uses a private vendor profile) and we provide Zigbee Pro, the endpoint will refuse to join. Devices that only understand private profiles will not join public-profile networks, and vice versa. In my case, I could not change the Nordic firmware to match the proprietary stack profile, so the endpoint refused to join. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Wireless%20security • https://en.wikipedia.org/wiki/MAC%20address • https://en.wikipedia.org/wiki/Z-Wave • https://wai-works.com/blog/zigbee-protocol-security-testing-sniffer-hardware-guide/ • https://securelist.com/zigbee-protocol-security-assessment/118373/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Zigbee Wireless Network Vulnerability Scanning Tool.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Zigbee Wireless Network Vulnerability Scanning Tool... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |